This is the full developer documentation for Warp
# Warp products and getting started
Canonical page: [/](https://docs.warp.dev/)
> Warp combines a modern terminal, coding agents, cloud automation, and software factories for teams that build and ship software.
Warp is an [open-source](https://github.com/warpdotdev/warp) **Agentic Development Environment** that brings together terminal work, coding agents, and cloud automation. With Warp, you can work in a desktop terminal, use the Warp Agent in a local checkout or from any terminal, automate background work in the cloud, and run repeatable team workflows with Warp Factories.
## Warp
[Section titled “Warp”](#warp)
With the Warp desktop terminal, you can run commands, edit code, and work with agents in a local checkout.
* [Modern terminal editing](/terminal/editor/) - Edit commands, navigate blocks, manage tabs, and customize your terminal.
* [Code](/code/overview/) - Review agent changes and edit files alongside your terminal.
* [Agents](/agents/) - Start and steer coding agents in the Warp app.
## Warp Agent
[Section titled “Warp Agent”](#warp-agent)
The Warp Agent helps you investigate issues, edit code, run commands, and complete multi-step work. Use it in the Warp terminal or from the [Warp Agent CLI](/agents/cli/), which runs the same agent in any terminal.
## Automation Platform
[Section titled “”](#varswarp_automation_platform)
The Automation Platform runs cloud agents from triggers, schedules, integrations, and APIs. Use it for background work such as issue triage, pull request review, and recurring maintenance.
* [Cloud agents](/platform/) - Run background agent work in the cloud.
* [The Automation Platform](/platform/overview/) - Configure environments, integrations, orchestration, and shared agent settings.
## Warp Factories
[Section titled “Warp Factories”](#warp-factories)
Warp Factories is available in Early Access. A factory turns incoming engineering work into a repeatable, multi-stage workflow with specialized agents, review points, and measurable outcomes.
* [Warp Factories overview](/factories/) - Learn how a factory receives, routes, and tracks work.
* [Factory quickstart](/factories/quickstart/) - Create a factory and send it its first work item.
## How the products work together
[Section titled “How the products work together”](#how-the-products-work-together)
Start and steer interactive work in the Warp terminal with the Warp Agent. For work that starts from a schedule, integration, or API, the Automation Platform runs agents in the cloud. Warp Factories builds on the Automation Platform to turn incoming team work into a repeatable workflow with specialized agents and review stages.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Install Warp](/quickstart/) - Set up Warp and start coding.
* [Start an agent conversation](/agents/) - Work with the Warp Agent in a local checkout.
* [Run cloud agents](/platform/quickstart/) - Set up background automation.
* [Set up a factory](/factories/quickstart/) - Route engineering work through Warp Factories.
* [Privacy and security](/support-and-community/privacy-and-security/privacy/) - Review Warp’s data handling, privacy, and security practices.
# Page not found
Canonical page: [/404/](https://docs.warp.dev/404/)
> The page you are looking for does not exist or has moved.
The page you are looking for does not exist or has been moved. Use the search or navigation to find what you need.
[Go to the docs home](/)
# Agents overview
Canonical page: [/agents/](https://docs.warp.dev/agents/)
> The Warp Agent runs commands in a real terminal, carries your context across every surface, and works interactively or in the background.
The **Warp Agent** is Warp’s built-in coding agent. It works through multi-step tasks on its own, running commands in a real terminal and using the output to decide what to do next. You stay in the loop, approving actions and reviewing diffs before anything lands.
This page covers where to run the agent, the third-party CLI agents Warp supports, and the [Automation Platform](/platform/overview/), which runs and coordinates agents at scale.
***
## Where to use the Warp Agent
[Section titled “Where to use the Warp Agent”](#where-to-use-the-warp-agent)
You reach the same agent three ways. Which one you pick depends on where you’re working, not on what the agent can do.
* **In the Warp app** - The full experience, with code review, agent management, and the terminal beside your conversation.
* [**In any terminal, with the Warp Agent CLI**](/agents/cli/) - Run the `warp` command to start a conversation in any terminal emulator, over SSH, or on a machine where the Warp app isn’t installed.
* [**In the cloud, as a cloud agent**](/platform/) - Run the agent in the background from a trigger, a schedule, or an integration, without keeping a session open. Cloud agents run on the [Automation Platform](/platform/overview/), Warp’s platform for environments, triggers, orchestration, and observability.
***
## What makes the Warp Agent different
[Section titled “What makes the Warp Agent different”](#what-makes-the-warp-agent-different)
* **It works in a real terminal** - The agent runs shell commands, reads live output, and drives interactive programs like REPLs, database shells, and full-screen apps. See [Full terminal use](/agents/capabilities/full-terminal-use/).
* **Your context follows it everywhere** - [Rules](/agents/capabilities/rules/), [Skills](/agents/capabilities/skills/), [MCP servers](/agents/capabilities/mcp/), and [Codebase Context](/agents/capabilities/codebase-context/) apply the same way in the app, the CLI, and the cloud.
* **Interactive or delegated, and you can switch mid-task** - Steer a conversation while it runs, or [hand it off](/platform/handoff/) to a cloud agent and pick it back up locally when it’s done.
* **You approve before anything lands** - The agent asks before it runs commands, edits files, or calls MCP servers. Set how much it does on its own with [Agent Profiles and permissions](/agents/capabilities/agent-profiles-permissions/), and review generated changes in [interactive code review](/agents/local-agents/interactive-code-review/).
* **Many agents at once** - Run several conversations in parallel and track them in the [Agent Management Panel](/platform/managing-cloud-agents/), or use [orchestration](/platform/orchestration/) to have a parent agent spawn and coordinate children.

**Try this prompt** — [*open in Warp*](https://app.warp.dev/drive/prompt/Clone-and-install-Warps-themes-repository-PkK9Zw16SCD3JKzOUoGuj4)
```text
Detect my current operating system. Based on that, navigate to the appropriate Warp themes directory (e.g. ~/.warp/ on macOS).
Then, clone the official Warp themes repository using SSH (git@github.com:warpdotdev/themes.git) into that directory, following the structure and instructions provided in the repo's README. If SSH does not work, try HTTPS (https://github.com/warpdotdev/themes.git) or via the GitHub CLI (gh repo clone warpdotdev/themes).
```
***
## Third-party CLI agents
[Section titled “Third-party CLI agents”](#third-party-cli-agents)
Separately from the Warp Agent, Warp gives third-party CLI coding agents first-class support. Run Claude Code, Codex, OpenCode, and others inside Warp and get rich input, agent notifications, inline code review, and remote session control.
→ [Learn about third-party CLI agents](/agents/cli-agents/overview/)
***
## The platform behind the agent
[Section titled “The platform behind the agent”](#the-platform-behind-the-agent)
The [**Automation Platform**](/platform/overview/) is Warp’s programmable system for running and coordinating agents at scale. It provides the environments, triggers, integrations, orchestration, and observability that cloud agents run on, along with a CLI, API, and SDK for driving agents programmatically.
To automate an entire workflow rather than a single task, use [Warp Factories](/factories/). Built on the Automation Platform, a factory runs a team of cloud agents that triage, spec, implement, review, and verify work.
The Automation Platform tab covers the platform in full.
***
## Privacy and security
[Section titled “Privacy and security”](#privacy-and-security)
Warp is **SOC 2 compliant** and has **Zero Data Retention** policies with all contracted LLM providers. No customer AI data is retained, stored, or used for training.
You can disable Warp’s AI features entirely in **Settings** > **Agents** > **Warp Agent**.
→ [Read more about data privacy](https://www.warp.dev/privacy)
***
## Where to go next
[Section titled “Where to go next”](#where-to-go-next)
* [**Interacting with agents**](/agents/local-agents/interacting-with-agents/) - Conversations, context, code review, and voice in the Warp app.
* [**Agent capabilities**](/agents/capabilities/) - Planning, skills, rules, MCP servers, task lists, and model choice.
* [**Warp Agent CLI quickstart**](/agents/cli/quickstart/) - Install the CLI and run your first conversation.
* [**Cloud agents quickstart**](/platform/quickstart/) - Run your first agent in the cloud, or put one on a [schedule](/platform/triggers/scheduled-agents/). For a comparison of triggers across schedules, Slack, Linear, GitHub Actions, the CLI, and the API, see [Run unattended agents](/guides/agent-workflows/how-to-run-unattended-agents/).
* [**Agent FAQs**](/agents/getting-started/faqs/) - Models, privacy, credits, and limits.
***
## Open source
[Section titled “Open source”](#open-source)
Warp’s client is open source under [AGPL v3](https://github.com/warpdotdev/warp/blob/master/LICENSE-AGPL), so the editor and terminal that host your agents are fully auditable. See [Contributing to Warp](/support-and-community/community/contributing/).
# Agent Memory (Research Preview)
Canonical page: [/agents/agent-memory/](https://docs.warp.dev/agents/agent-memory/)
> Agent Memory gives agents in Warp persistent memory across supported harnesses, including the Warp Agent, Claude Code, and Codex.
Caution
Agent Memory is in **research preview** and is enabled per team for design partners. [Join the waitlist](https://www.warp.dev/oz/agent-memory#waitlist) to request access for your team.
Agent Memory is a persistent memory system that lives on Warp and is shared across every supported [agent harness](/platform/harnesses/), including the built-in Warp Agent, Claude Code, Codex, and others as they’re added. Agents read from and write to this memory system as they run, so durable facts, decisions, and outcomes from one conversation are available to the next — regardless of which harness, machine, or teammate triggers the work.
Memory creation and retrieval are asynchronous and run in the background, so they don’t consume tokens or add latency to the active task.
Watch this short preview to see Agent Memory in context.

[Join the Agent Memory waitlist](https://www.warp.dev/oz/agent-memory#waitlist).
## Key features
[Section titled “Key features”](#key-features)
* **Cross-harness memory** - One memory system is shared across the Warp Agent, Claude Code, Codex, and other harnesses as they’re added. Third-party harnesses are covered when they run as cloud agents.
* **Both local and cloud agents** - Supports interactive local agents in Warp and background cloud agents.
* **Asynchronous by design** - Memory creation runs after a conversation ends. Retrieval runs in the background during a run. Neither consumes tokens or adds latency to the active task.
* **Automatic memory creation from conversations** - When a conversation ends, Warp extracts durable facts, learnings, and outcomes and writes them as memories. New knowledge merges with existing memories or supersedes them on conflict.
* **Shareable stores** - Memory is organized into stores. A store can be attached to one or more agents, so the same knowledge is available wherever those agents run. To share knowledge across a team, attach a store to an agent the whole team uses.
* **Auto-memory for new agents** - New agents get a dedicated, agent-owned memory store by default, so they start building long-term memory from their first run. You can turn this off when you create the agent.
* **Per-agent access and instructions** - Attach stores to specific agents with read-only or read-write access. Per-store instructions tell each agent how and when to use the store.
* **Traceability** - Each memory records where it came from, so teams can trace a memory back to its source.
* **Auditability** - Every change to a memory is recorded so teams can inspect how a memory has changed over time.
## Where Agent Memory runs
[Section titled “Where Agent Memory runs”](#where-agent-memory-runs)
Agent Memory is part of Warp. Storage, memory creation, and retrieval all run on Warp alongside your agents. The same memory is accessible from any agent you run in Warp:
* The local Warp Agent.
* [Cloud agents](/platform/) triggered from the CLI, web app, [schedules](/platform/triggers/scheduled-agents/), or [integrations](/platform/integrations/).
* Third-party harnesses running as cloud agents: Claude Code, Codex, and others as they’re added. (Running third-party harnesses locally isn’t supported during the research preview.)
Memory stays bound to its owner (a user, an agent, or a team), independent of which harness reads or writes.
## Memory stores
[Section titled “Memory stores”](#memory-stores)
A memory store is a collection of memories. Stores are used by attaching them to agents: a store can be attached to a single agent or to several agents that need the same knowledge. To make knowledge available across a team, attach a store to an agent the whole team uses; there’s no separate step for sharing a store with individual teammates.
Stores differ by who owns them:
* **Personal stores** - Owned by a user. Hold memories about preferences, working notes, and individual patterns.
* **Agent stores** - Owned by an agent. A new agent gets one by default as its auto-memory store (see below).
* **Team stores** - Owned by a team. Hold shared knowledge like deployment runbooks, code review conventions, or on-call procedures. Attach a team store to any agent the team uses so everyone’s work draws on the same knowledge.
Teams can use multiple stores to keep contexts separate, and attach the same store to several agents when needed. For example, a code review agent can use a dedicated store of review patterns, while a repo-specific store of architectural decisions is attached to both the code review agent and a Sentry triage agent so both reason about the same codebase.
### Auto-memory for new agents
[Section titled “Auto-memory for new agents”](#auto-memory-for-new-agents)
When you create an agent in the Oz web app, **Auto-memory** is on by default. With it enabled, Warp creates a dedicated memory store owned by that agent and uses it as the agent’s default long-term memory: the agent reads relevant memories before it acts and writes durable facts, decisions, and preferences for future runs. Each agent has a single auto-memory store.
Auto-memory is different from automatic memory creation from conversations, described below: auto-memory is the store an agent gets by default, while automatic memory creation from conversations is how memories are written to a store after a conversation ends.
You can turn Auto-memory off when you create the agent, and you can attach existing team stores at the same time, each with its own access level and instructions.
## Automatic memory creation from conversations
[Section titled “Automatic memory creation from conversations”](#automatic-memory-creation-from-conversations)
When a conversation finishes, Warp extracts durable facts, learnings, and outcomes from the transcript and writes them as memories. Memory creation runs in the background after the conversation ends, so it doesn’t consume tokens or add latency during that run.
* **Memories evolve over time** - Agents update and supersede their own memories as new information arrives, including to resolve contradictions with prior memories.
You can also explicitly ask an agent to remember something during a conversation. Warp saves that memory to the appropriate store.
## How agents use memory
[Section titled “How agents use memory”](#how-agents-use-memory)
When an agent starts a task, Warp searches the stores the agent can access for relevant memories and injects them as context. The search runs in the background, so the agent only sees the memories returned. Agents can also retrieve additional memories on demand mid-conversation when they determine it’s relevant, similar to how they consult [Rules](/agents/capabilities/rules/) or [Codebase Context](/agents/capabilities/codebase-context/). You don’t need to write retrieval queries or pre-load memory.
## Attaching memory to your agents
[Section titled “Attaching memory to your agents”](#attaching-memory-to-your-agents)
Attach stores to agents with read-only or read-write access. Each attachment includes per-store instructions that tell the agent how and when to use the store. For example, use instructions like “Reference this store for team naming conventions” or “Write a new memory after each successful deployment.” Instructions are required on every attachment so the agent knows the purpose of each store.
## Coming soon
[Section titled “Coming soon”](#coming-soon)
These capabilities aren’t part of the research preview yet, but they’re on the way:
* **Programmatic API access** - Read and manage memories and stores through the [Warp Platform API](/factories/api-and-sdk/), in addition to managing them in the Oz web app.
* **Self-hosting support** - Run Agent Memory on a [self-hosted Automation Platform](/factories/self-hosting/) instance to meet security, privacy, and compliance requirements.
## Join the waitlist
[Section titled “Join the waitlist”](#join-the-waitlist)
Agent Memory is rolling out to design partner teams during research preview. [Join the waitlist](https://www.warp.dev/oz/agent-memory#waitlist) to request access.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Harnesses in the Automation Platform](/platform/harnesses/) - Run Warp Agent, Claude Code, or Codex as cloud agents with shared platform features.
* [Codebase Context](/agents/capabilities/codebase-context/) - Let agents understand your codebase through semantic indexing.
* [Rules](/agents/capabilities/rules/) - Define global and project-level guidelines that shape agent behavior.
* [Skills](/agents/capabilities/skills/) - Reusable, scoped instructions that teach agents how to perform specific tasks.
* [Agent profiles and permissions](/agents/capabilities/agent-profiles-permissions/) - Control what permissions and autonomy agents have.
# Capabilities overview
Canonical page: [/agents/capabilities/](https://docs.warp.dev/agents/capabilities/)
> Core capabilities and configuration options that shape how agents behave, what context they have access to, and how they execute tasks.
Agent capabilities are the core building blocks that define how agents operate, including the context sources agents can access, the rules that guide their behavior, the tools they can use, and the models they run on. Configure these capabilities to match your workflows and preferences.
## Capabilities in this section
[Section titled “Capabilities in this section”](#capabilities-in-this-section)
* [Slash Commands](/agents/capabilities/slash-commands/) - Quick actions and saved prompts accessible by typing `/` in Agent Mode.
* [Skills](/agents/capabilities/skills/) - Reusable, scoped instructions that teach agents how to perform specific tasks in your codebase.
* [Planning](/agents/capabilities/planning/) - Turn agent requests into organized, editable plans that execute step-by-step with full visibility.
* [Task Lists](/agents/capabilities/task-lists/) - Track complex workflows with automatic task lists that update progress in real time.
* [Rules](/agents/capabilities/rules/) - Define global and project-level guidelines that shape agent behavior and responses.
* [Full Terminal Use](/agents/capabilities/full-terminal-use/) - Let the agent drive interactive terminal apps, seeing live output and running commands.
* [Computer Use](/agents/capabilities/computer-use/) - Let agents interact with desktop environments by taking screenshots, clicking, typing, and controlling the GUI.
* [MCP](/agents/capabilities/mcp/) - Connect external data sources and tools to agents via the Model Context Protocol.
* [Codebase Context](/agents/capabilities/codebase-context/) - Let agents understand your codebase through semantic indexing of your Git-tracked files.
* [Agent Profiles & Permissions](/agents/capabilities/agent-profiles-permissions/) - Control what permissions and autonomy agents have to run commands and apply changes.
* [Web Search](/agents/capabilities/web-search/) - Allow agents to search the web for up-to-date information.
## Related
[Section titled “Related”](#related)
* [Inference & providers](/agents/inference/model-choice/) - Pick the model that powers your agents, bring your own API key, or connect a custom inference endpoint.
* [Agents overview](/agents/) - What the Warp Agent does, how to control it, and where to run it.
# Agent Notifications
Canonical page: [/agents/capabilities/agent-notifications/](https://docs.warp.dev/agents/capabilities/agent-notifications/)
> Warp surfaces notifications from coding agents, both in-app and via desktop alerts, so you know exactly when an agent needs your attention.
Warp delivers notifications from any supported coding agent so you always know when an agent finishes a task, encounters an error, or needs your input. Notifications work whether you’re in a different tab or a different app.

## Notification types
[Section titled “Notification types”](#notification-types)
Warp categorizes agent notifications by what happened:
* **Complete** - the agent finished its task successfully. You can review the output and continue working.
* **Request** - the agent is blocked and needs your input. This includes command approval, permission requests, and idle prompts where the agent is waiting for you.
* **Error** - the agent encountered an error that requires your attention.
## In-app notifications
[Section titled “In-app notifications”](#in-app-notifications)
When you’re working in Warp but not looking at the agent’s tab, Warp provides several visual signals.
### Toast notifications
[Section titled “Toast notifications”](#toast-notifications)
Floating toast notifications appear in the corner of the Warp window when an agent in another tab needs attention. Toasts auto-dismiss after a few seconds. Hover over a toast to pause the timer, or click it to jump directly to the agent’s session.
Up to two toasts are visible at a time. If additional notifications arrive, the oldest toast is replaced.
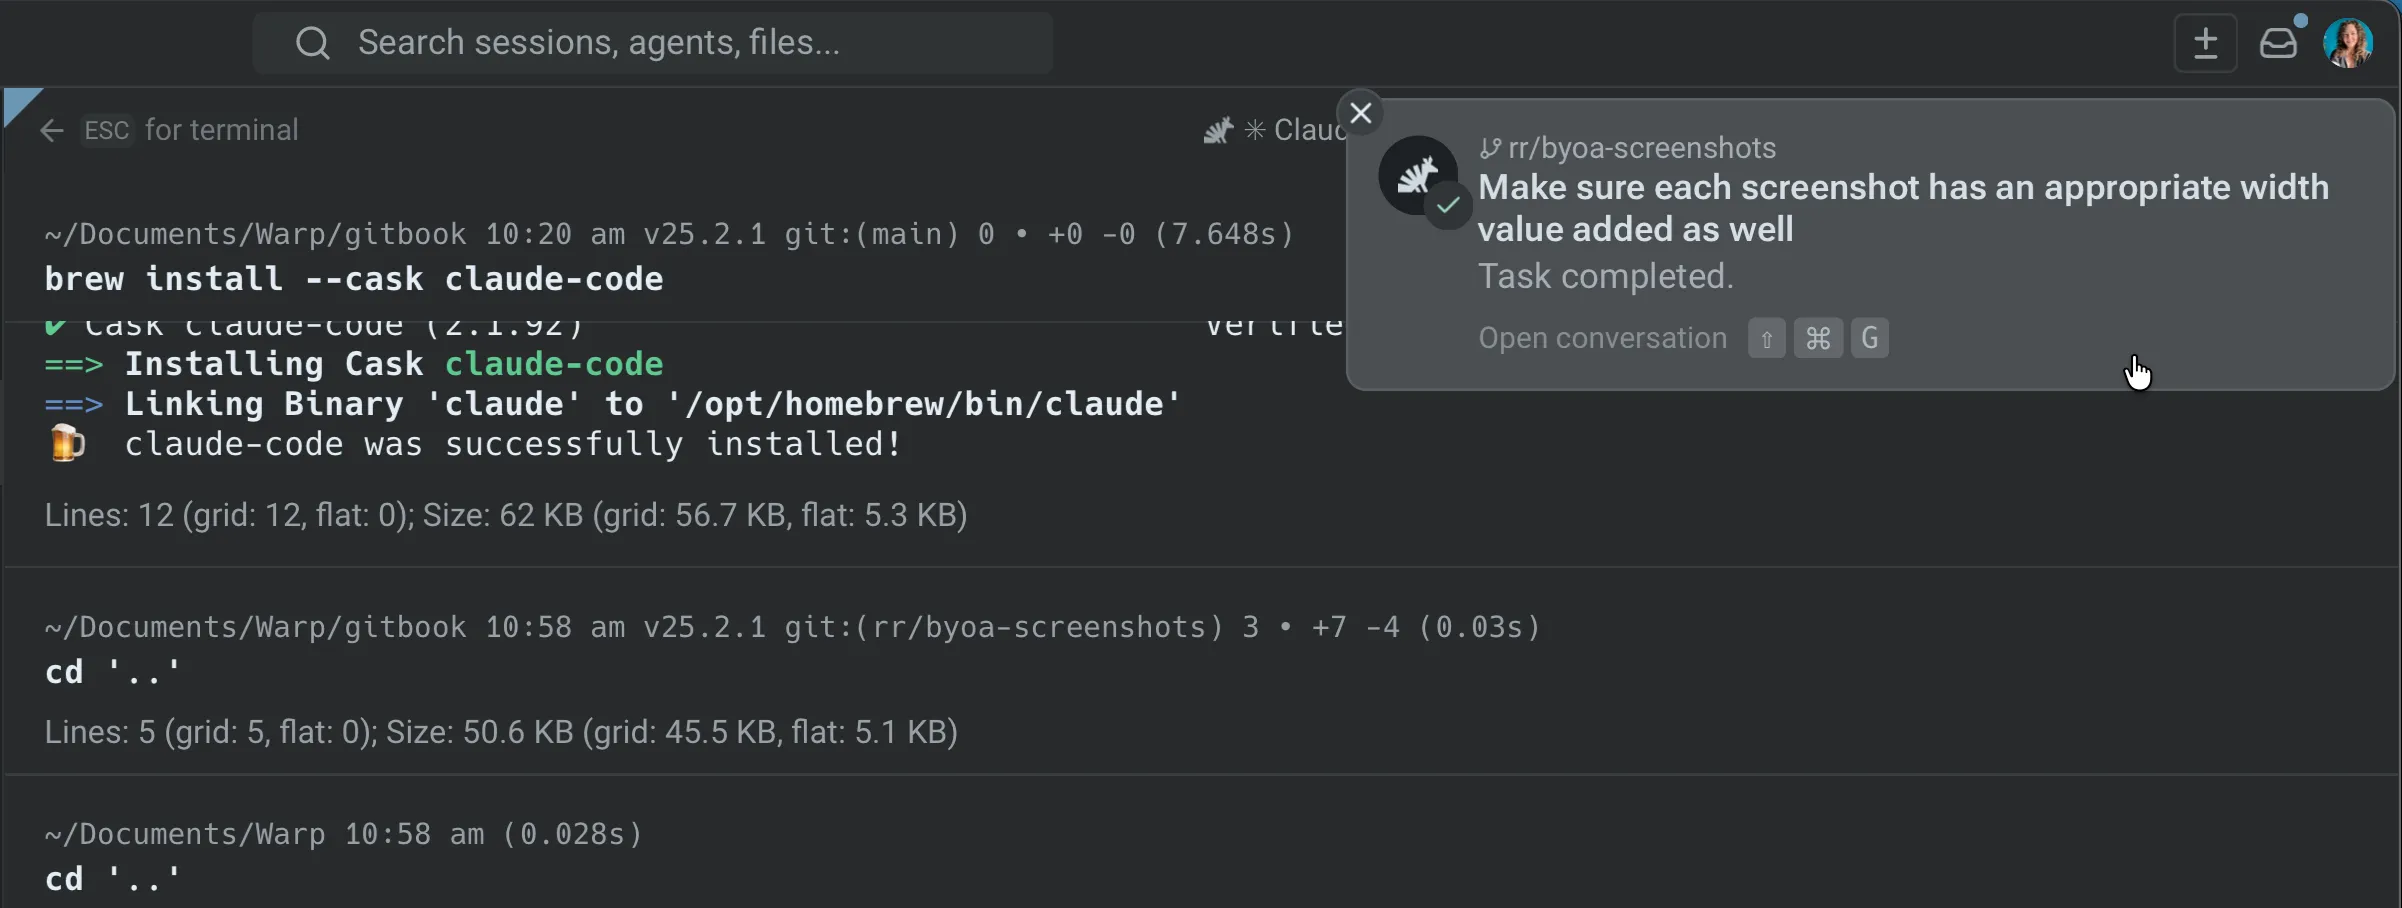
Agent task completion notification.
### Notification mailbox
[Section titled “Notification mailbox”](#notification-mailbox)
The notification mailbox is a sidebar panel that collects all agent notifications in one place. Open it from the bell icon in the top-right corner of Warp.
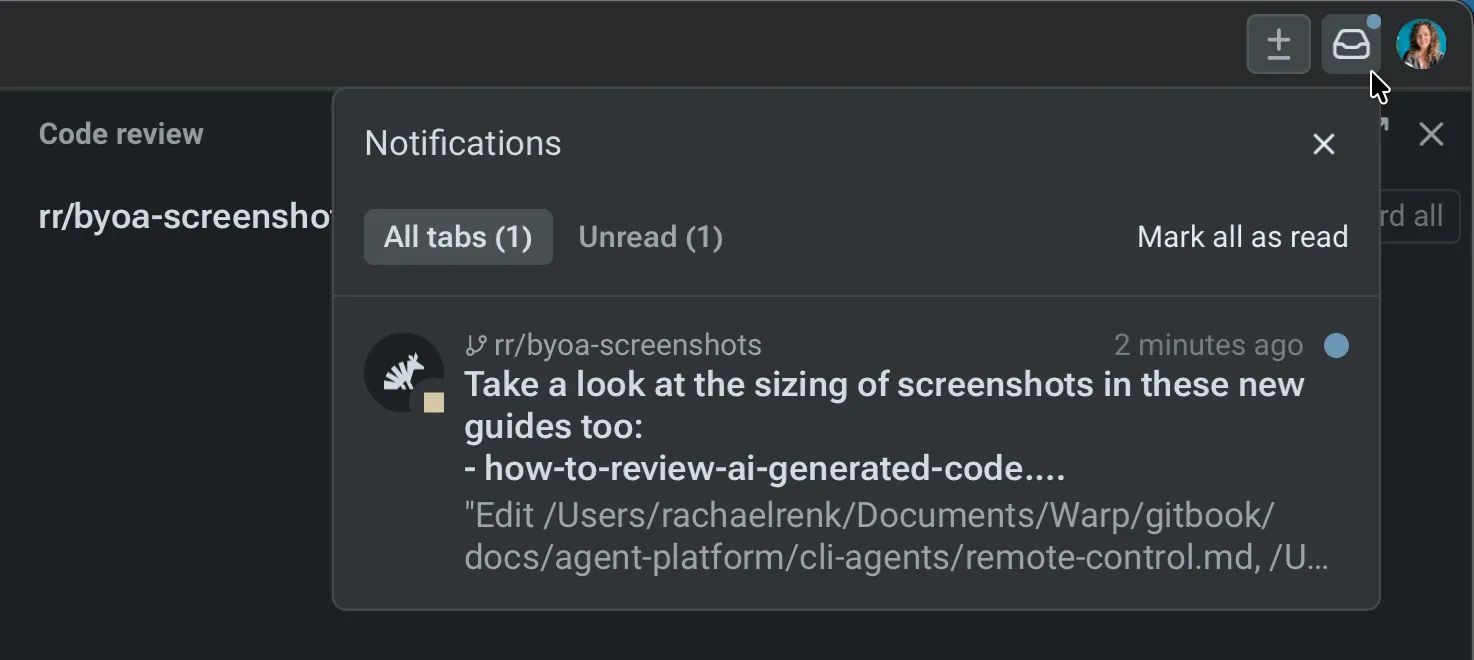
Agent notification mailbox.
The mailbox includes:
* **Filter tabs** - switch between **All tabs**, **Unread**, and **Errors** to find what needs attention. If there are no unreads or errors, those filters don’t appear.
* **Mark all as read** - clear all unread indicators at once
* **Click to navigate** - click any notification to jump directly to that agent’s tab
**Keyboard shortcuts:**
* `↑` / `↓` - select previous / next notification
* `Enter` - open the selected notification’s session
* `Shift+Tab` - cycle through filter tabs
* `Esc` - close the mailbox
### Tab status indicators
[Section titled “Tab status indicators”](#tab-status-indicators)
Each tab displays an icon reflecting its agent’s current state — working, blocked, completed, or errored. Tabs with unread notifications show an attention badge so you can spot which sessions need action, even with many tabs open.
Notifications are automatically marked as read when you navigate to the agent’s tab.
## Desktop notifications
[Section titled “Desktop notifications”](#desktop-notifications)
When Warp is in the background or minimized, agent notifications are delivered as native system-level desktop alerts. This ensures you’re aware of agent activity even while working in other apps.
Note
Desktop notifications require system permissions. If you’re not receiving them, check your OS notification settings for Warp. See [Desktop Notifications](/terminal/more-features/notifications/) for setup and troubleshooting.
## Supported agents
[Section titled “Supported agents”](#supported-agents)
Agent notifications currently work with:
* **Warp Agent** - supported out of the box. No setup required.
* **Claude Code** - full support via notification plugin.
* **Codex** - full support via native Codex configuration.
* **OpenCode** - full support via notification plugin.
## Setting up notifications
[Section titled “Setting up notifications”](#setting-up-notifications)
For the **Warp Agent**, notifications work out of the box — no setup needed.
For **third-party CLI agents**, each agent requires a one-time setup. The process varies by agent:
* **Claude Code** - one-click auto-install via a chip in Warp, or manual plugin commands. See [Claude Code setup](/agents/cli-agents/claude-code/#setting-up-notifications).
* **Codex** - add `notification_condition = "always"` under `[tui]` in `~/.codex/config.toml`, then restart Codex. See [Codex setup](/agents/cli-agents/codex/#setting-up-notifications).
* **OpenCode** - add `"@warp-dot-dev/opencode-warp"` to the `plugin` array in your OpenCode config. See [OpenCode setup](/agents/cli-agents/opencode/#setting-up-notifications).
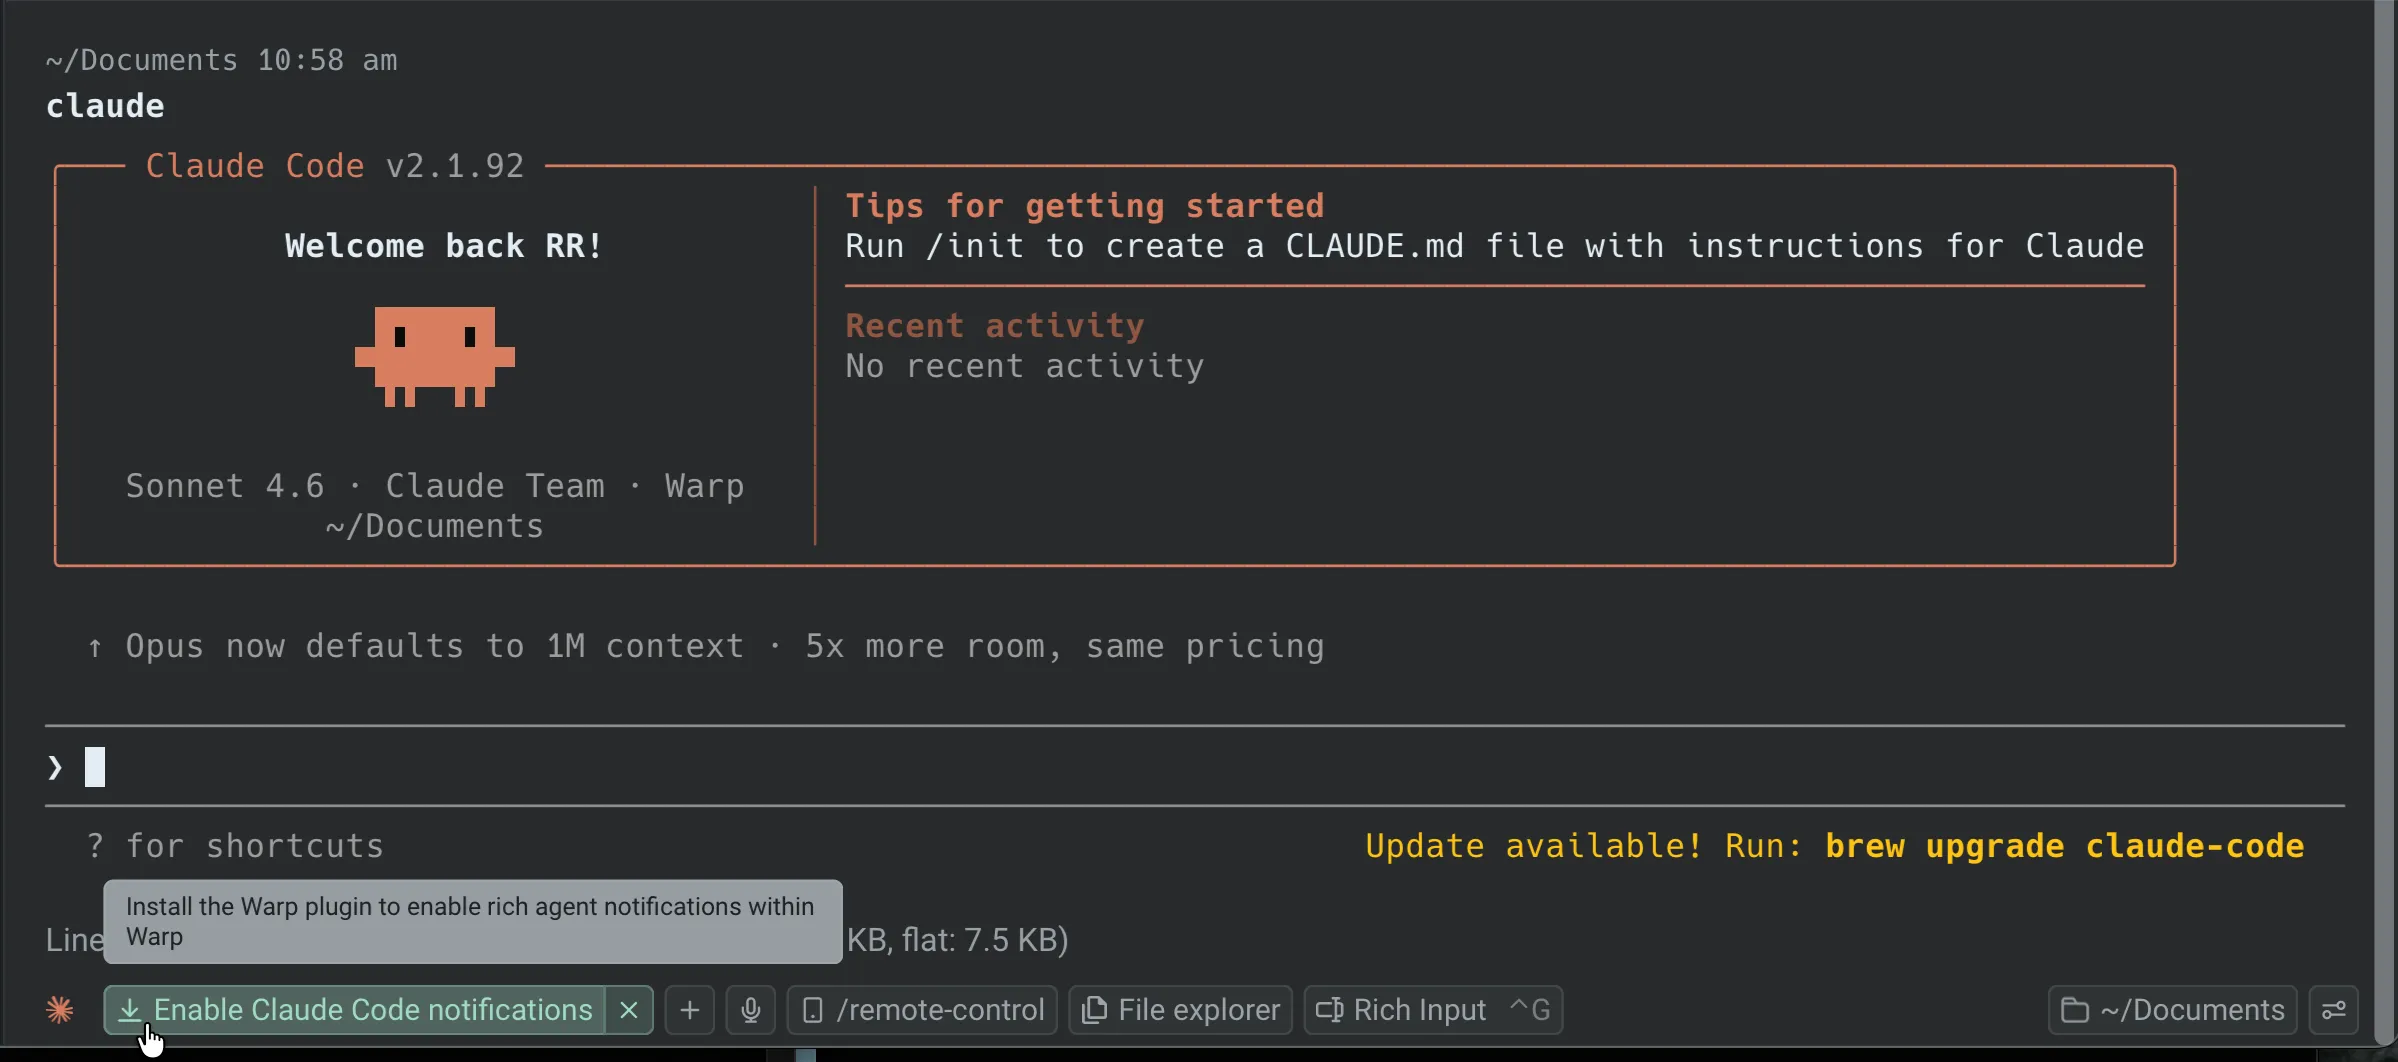
Notification plugin install chip.
If auto-install doesn’t work or you’re running an agent over SSH, Warp displays an installation-instructions chip in the terminal with setup steps you can follow directly.
## Notifications in orchestrated runs
[Section titled “Notifications in orchestrated runs”](#notifications-in-orchestrated-runs)
In a [multi-agent orchestration](/platform/orchestration/), the parent agent and each child agent are separate conversations. Today, in-app notifications fire on the parent’s conversation only: child agent conversations are excluded from the toast stream and the notification mailbox so the mailbox doesn’t get cluttered with per-child status churn.
That means:
* **Toasts and the mailbox** - watch the parent’s conversation for `Complete`, `Request`, and `Error` notifications.
* **Per-child state** - use the orchestration pill bar above the agent view header (in the Warp app) or the parent’s **Sub-agents** tab on the [Runs page](https://oz.warp.dev/runs) (in the Oz web app) to see each child’s live status. Both surfaces update as children transition through `INPROGRESS`, `SUCCEEDED`, `BLOCKED`, `FAILED`, `ERROR`, and `CANCELLED`.
* **Blocked children** - if a child blocks on user input (for example, a command approval request), open that child from the pill bar to resolve the block. The parent’s transcript also reflects the child’s `BLOCKED` state so the parent can wait, send a follow-up, or cancel the child.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Desktop Notifications](/terminal/more-features/notifications/) - configure system-level notification permissions and troubleshoot delivery
* [Managing Agents](/platform/managing-cloud-agents/) - monitor all agent conversations, filter by status, and inspect sessions
* [Multi-agent orchestration](/platform/orchestration/) - parent/child model, run state transitions, and the orchestration pill bar
* [Third-party CLI agents](/agents/cli-agents/overview/) - overview of supported CLI agents and Warp features
* [Claude Code](/agents/cli-agents/claude-code/) - setup and notification plugin installation
* [Codex](/agents/cli-agents/codex/) - setup and notification configuration
* [OpenCode](/agents/cli-agents/opencode/) - setup and notification plugin installation
# Profiles & Permissions
Canonical page: [/agents/capabilities/agent-profiles-permissions/](https://docs.warp.dev/agents/capabilities/agent-profiles-permissions/)
> Agent Profiles let you customize how your Agent behaves, from its models and autonomy to the tools and permissions it can use.
Agent Profiles let you configure how agents behave in different situations, including autonomy level, base model, tool access, and command permissions. Create multiple profiles for different workflows, control which commands run automatically, and set MCP server access rules per profile.
## Agent Profiles
[Section titled “Agent Profiles”](#agent-profiles)
Agent Profiles let you configure how your Agent behaves in different situations. Each profile defines the Agent’s autonomy, base models, and tool access. You can create multiple profiles and edit them directly in **Settings** > **Agents** > **Profiles**.
* **Default profile**: Every user starts with a default profile, you can edit it at any time, and new profiles will copy its settings as a starting point.
* **Other profiles**: Set up different profiles for different workflows (e.g., “Safe & cautious”, “YOLO mode”, etc.). Manage them in the Profiles settings menu.
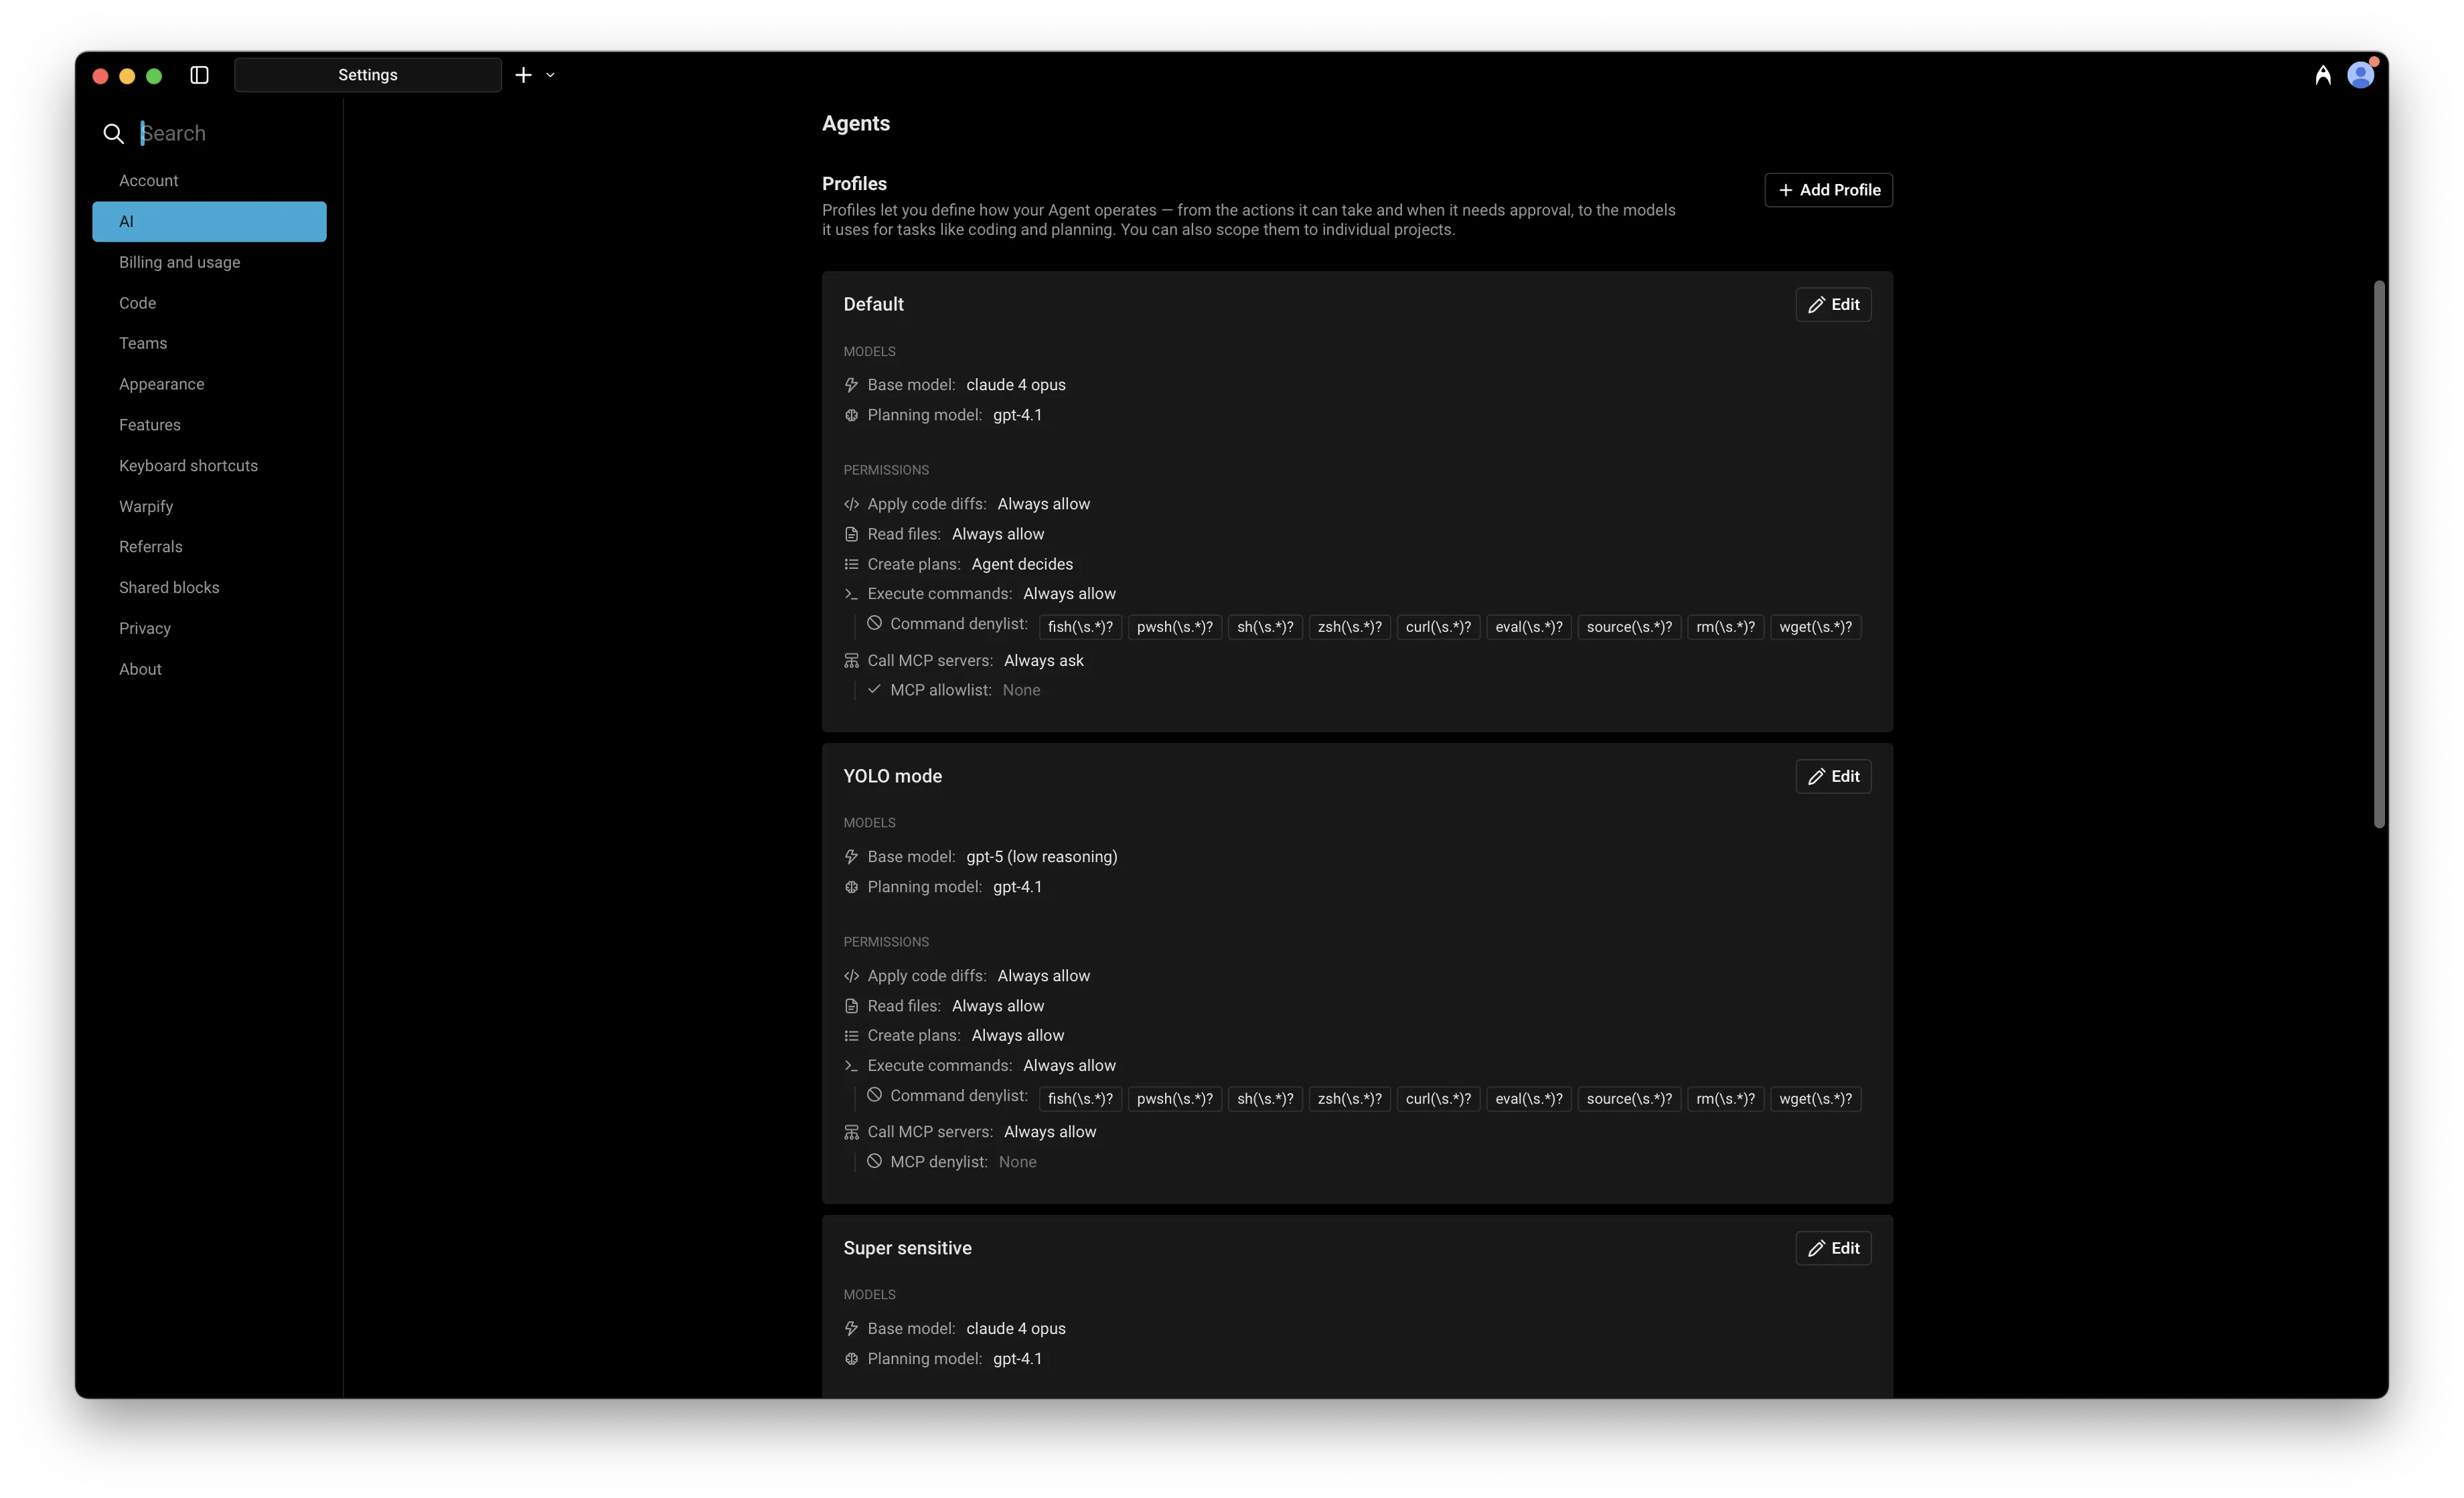
Agent Profile settings.
**In each Agent Profile, you can configure:**
* The name of the profile
* **Base model**: The core engine for your Agent. It handles most interactions and invokes other models when needed (e.g. for code generation). This model is also used for [Planning](/agents/capabilities/planning/) by default, though you can configure a separate planning model.
* Agent autonomy and permissions
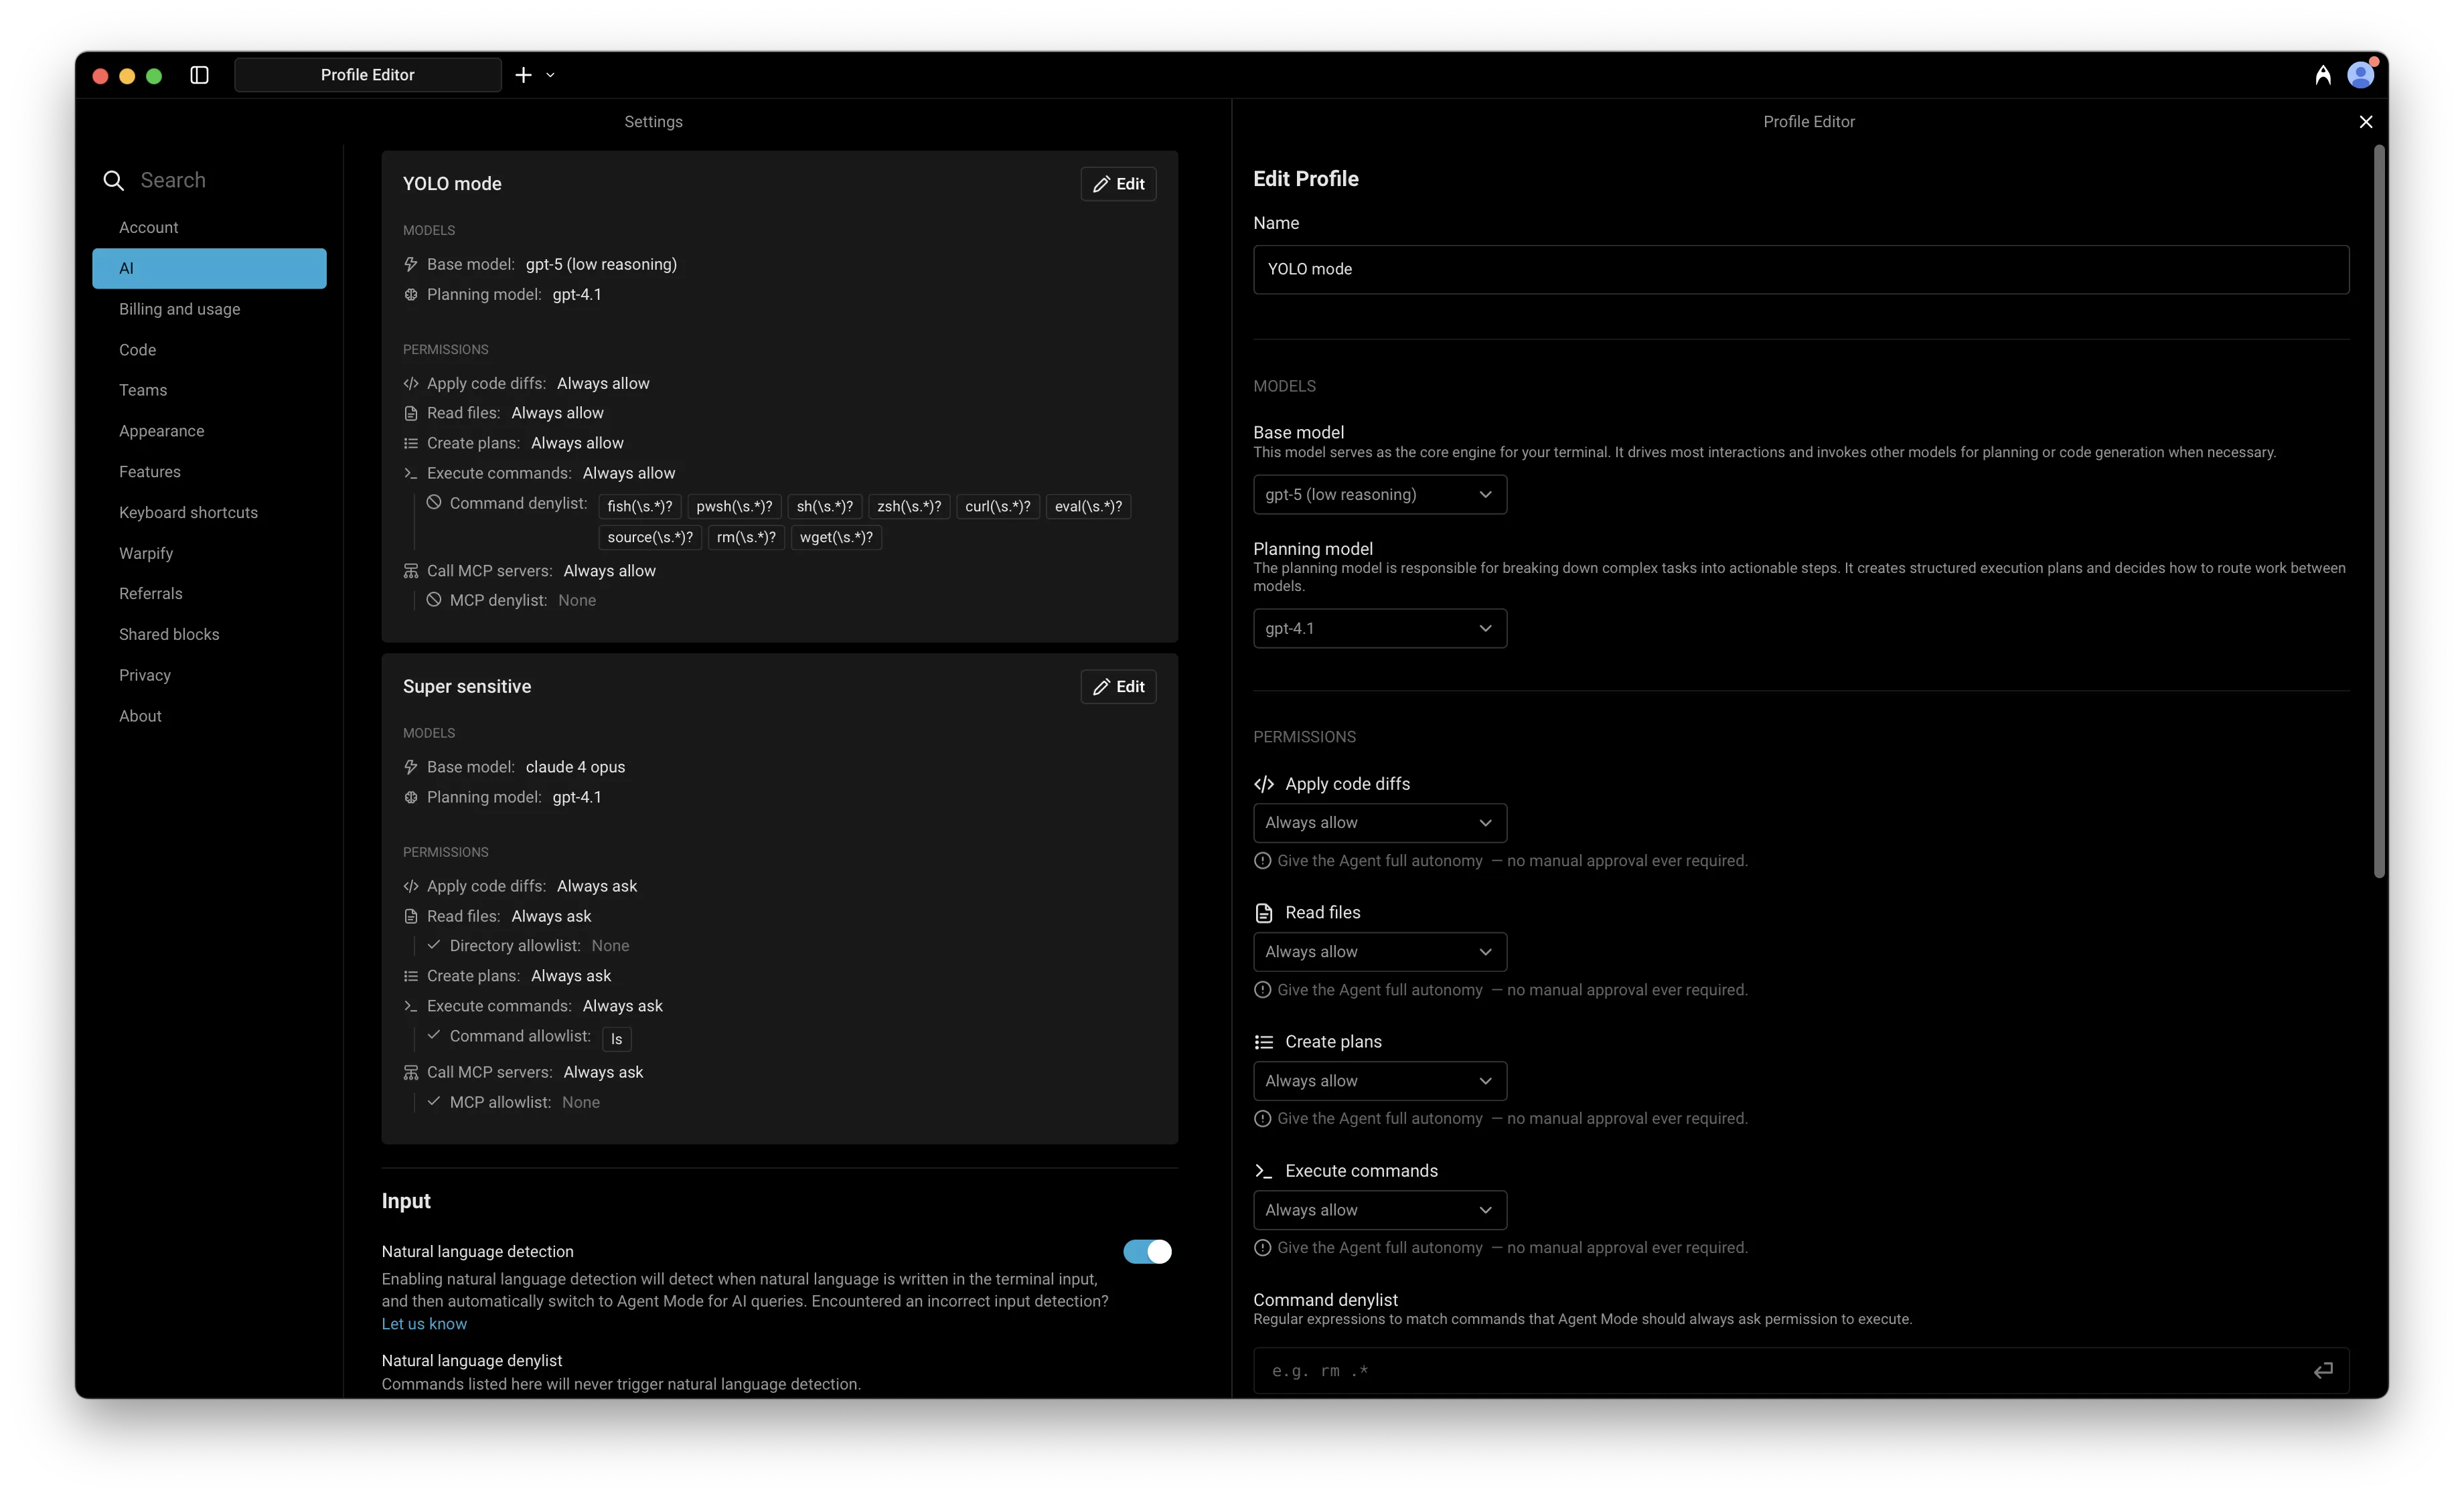
Editing an Agent Profile.
## Agent Permissions
[Section titled “Agent Permissions”](#agent-permissions)
Agent Permissions let you define how your Agent in a specific Profile operates — control its autonomy, choose what tools or MCP servers it can access, and set when it should act independently or ask for approval.
Caution
**Still getting approval prompts?** If the Agent keeps asking for permission to run certain commands (like `curl`, `rm`, or `wget`) even though you’ve set permissions to “Always allow,” check your **Command denylist** in **Settings** > **Agents** > **Profiles**. The denylist takes precedence over your other permission settings. Remove commands from the denylist to allow them to auto-execute, or use [Run until completion](#run-until-completion) to bypass the denylist for the current task.
You can control how much autonomy the Agent has when performing different types of actions under **Settings** > **Agents** > **Profiles** > **Permissions**. Agent permission types:
* Apply code diffs
* Read files
* Create plans
* Execute commands
* Interact with running commands (via [Full Terminal Use](/agents/capabilities/full-terminal-use/))
* Ask clarifying questions (via [Agent questions](/agents/local-agents/interacting-with-agents/agent-questions/))
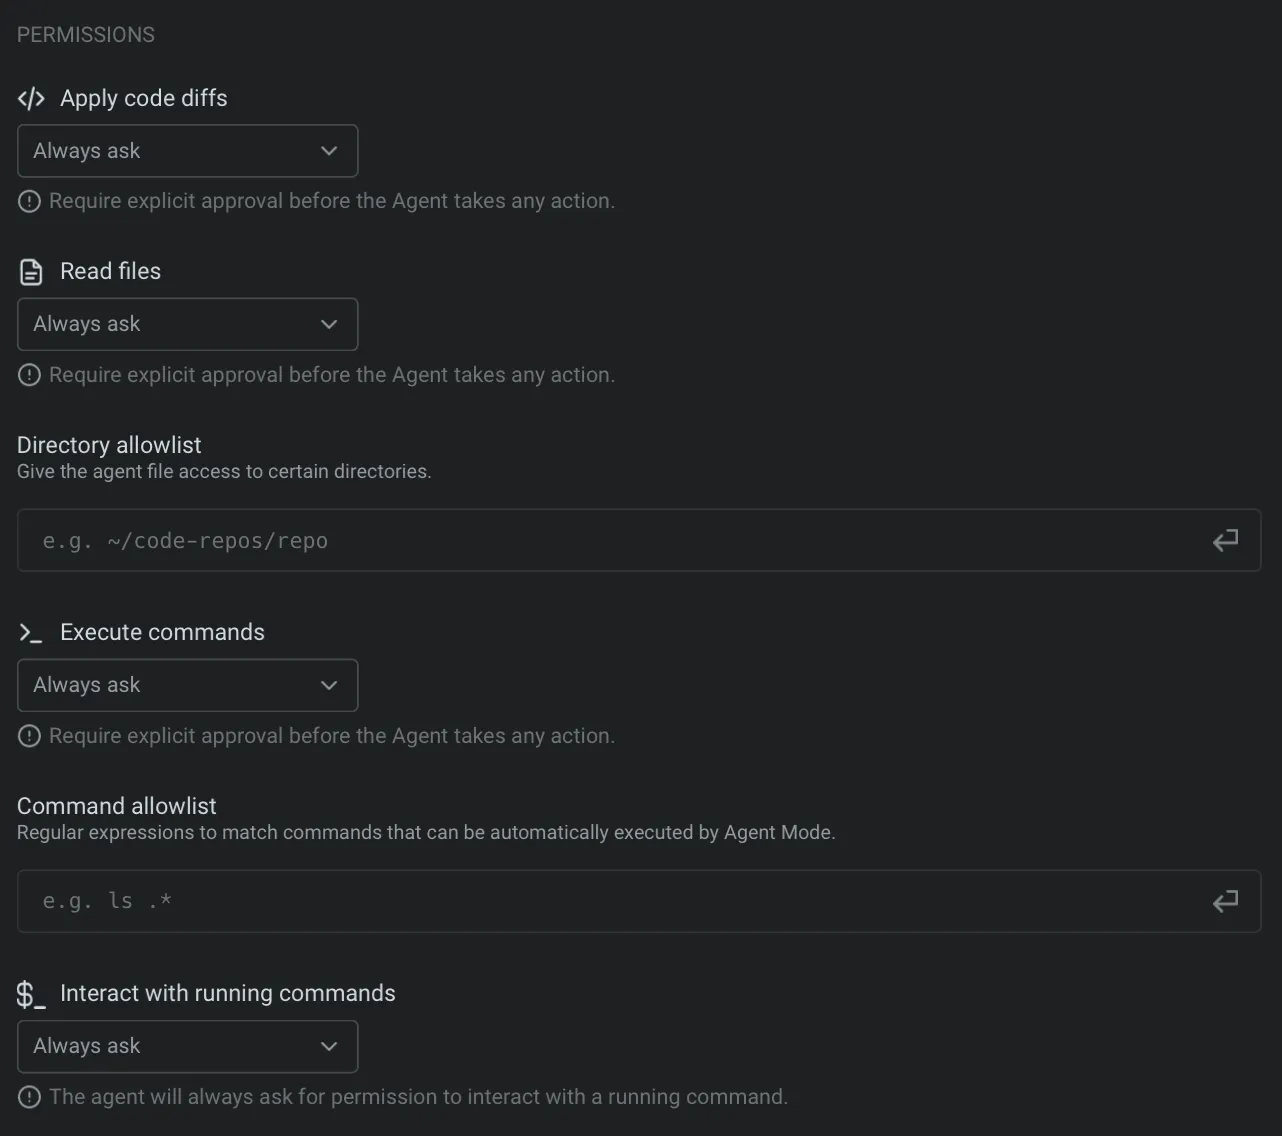
**Each permission has different levels of autonomy:**
| Autonomy level | Description |
| -------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Agent Decides | Agent will act autonomously when it’s confident, but prompt for approval when uncertain. This option balances speed with control, allowing the Agent to go ahead with common workflows while keeping you in the loop for more complex or risky steps. |
| Always ask | Agent will request explicit user approval before taking any action. Choose this for sensitive actions. |
| Always allow | Agent will perform the action without ever requesting explicit confirmation. Use this for tasks you fully trust the Agent to handle on its own. |
| Never | Agent will not ever take the action (i.e. Create plans). |
Note
For **Apply code diffs**, `Agent decides` currently behaves the same as `Always ask` — the Agent always prompts you to review diffs before applying them. Only `Always allow` skips the review prompt.
When all Agent permissions are set to **Always allow**, the Agent gains full autonomy (“YOLO mode”); however, any denylist rules will still override these settings.
### Ask questions
[Section titled “Ask questions”](#ask-questions)
The **Ask questions** permission controls whether the Agent can pause a conversation to ask you clarifying questions before continuing.
The available settings are:
* **Never ask** - The Agent does not pause for clarifying questions and continues with its best judgment.
* **Ask unless auto-approve** - The Agent can ask during normal conversations, but questions are skipped while auto-approve is on.
* **Always ask** - The Agent can pause for your answer even when auto-approve is on.
For the full user flow, see [Agent questions](/agents/local-agents/interacting-with-agents/agent-questions/).
### Command allowlist
[Section titled “Command allowlist”](#command-allowlist)
The Agent lets you define an allowlist of commands that run automatically without confirmation. It’s empty by default, but users often add read-only commands such as:
* `which .*` - Find executable locations
* `ls(\s.*)?` - List directory contents
* `grep(\s.*)?` - Search file contents
* `find .*` - Search for files
* `echo(\s.*)?` - Print text output
You can add your own regular expressions to this list in **Settings** > **Agents** > **Profiles** > **Command allowlist**. Commands in the allowlist will always auto-execute, even if they are not read-only operations.
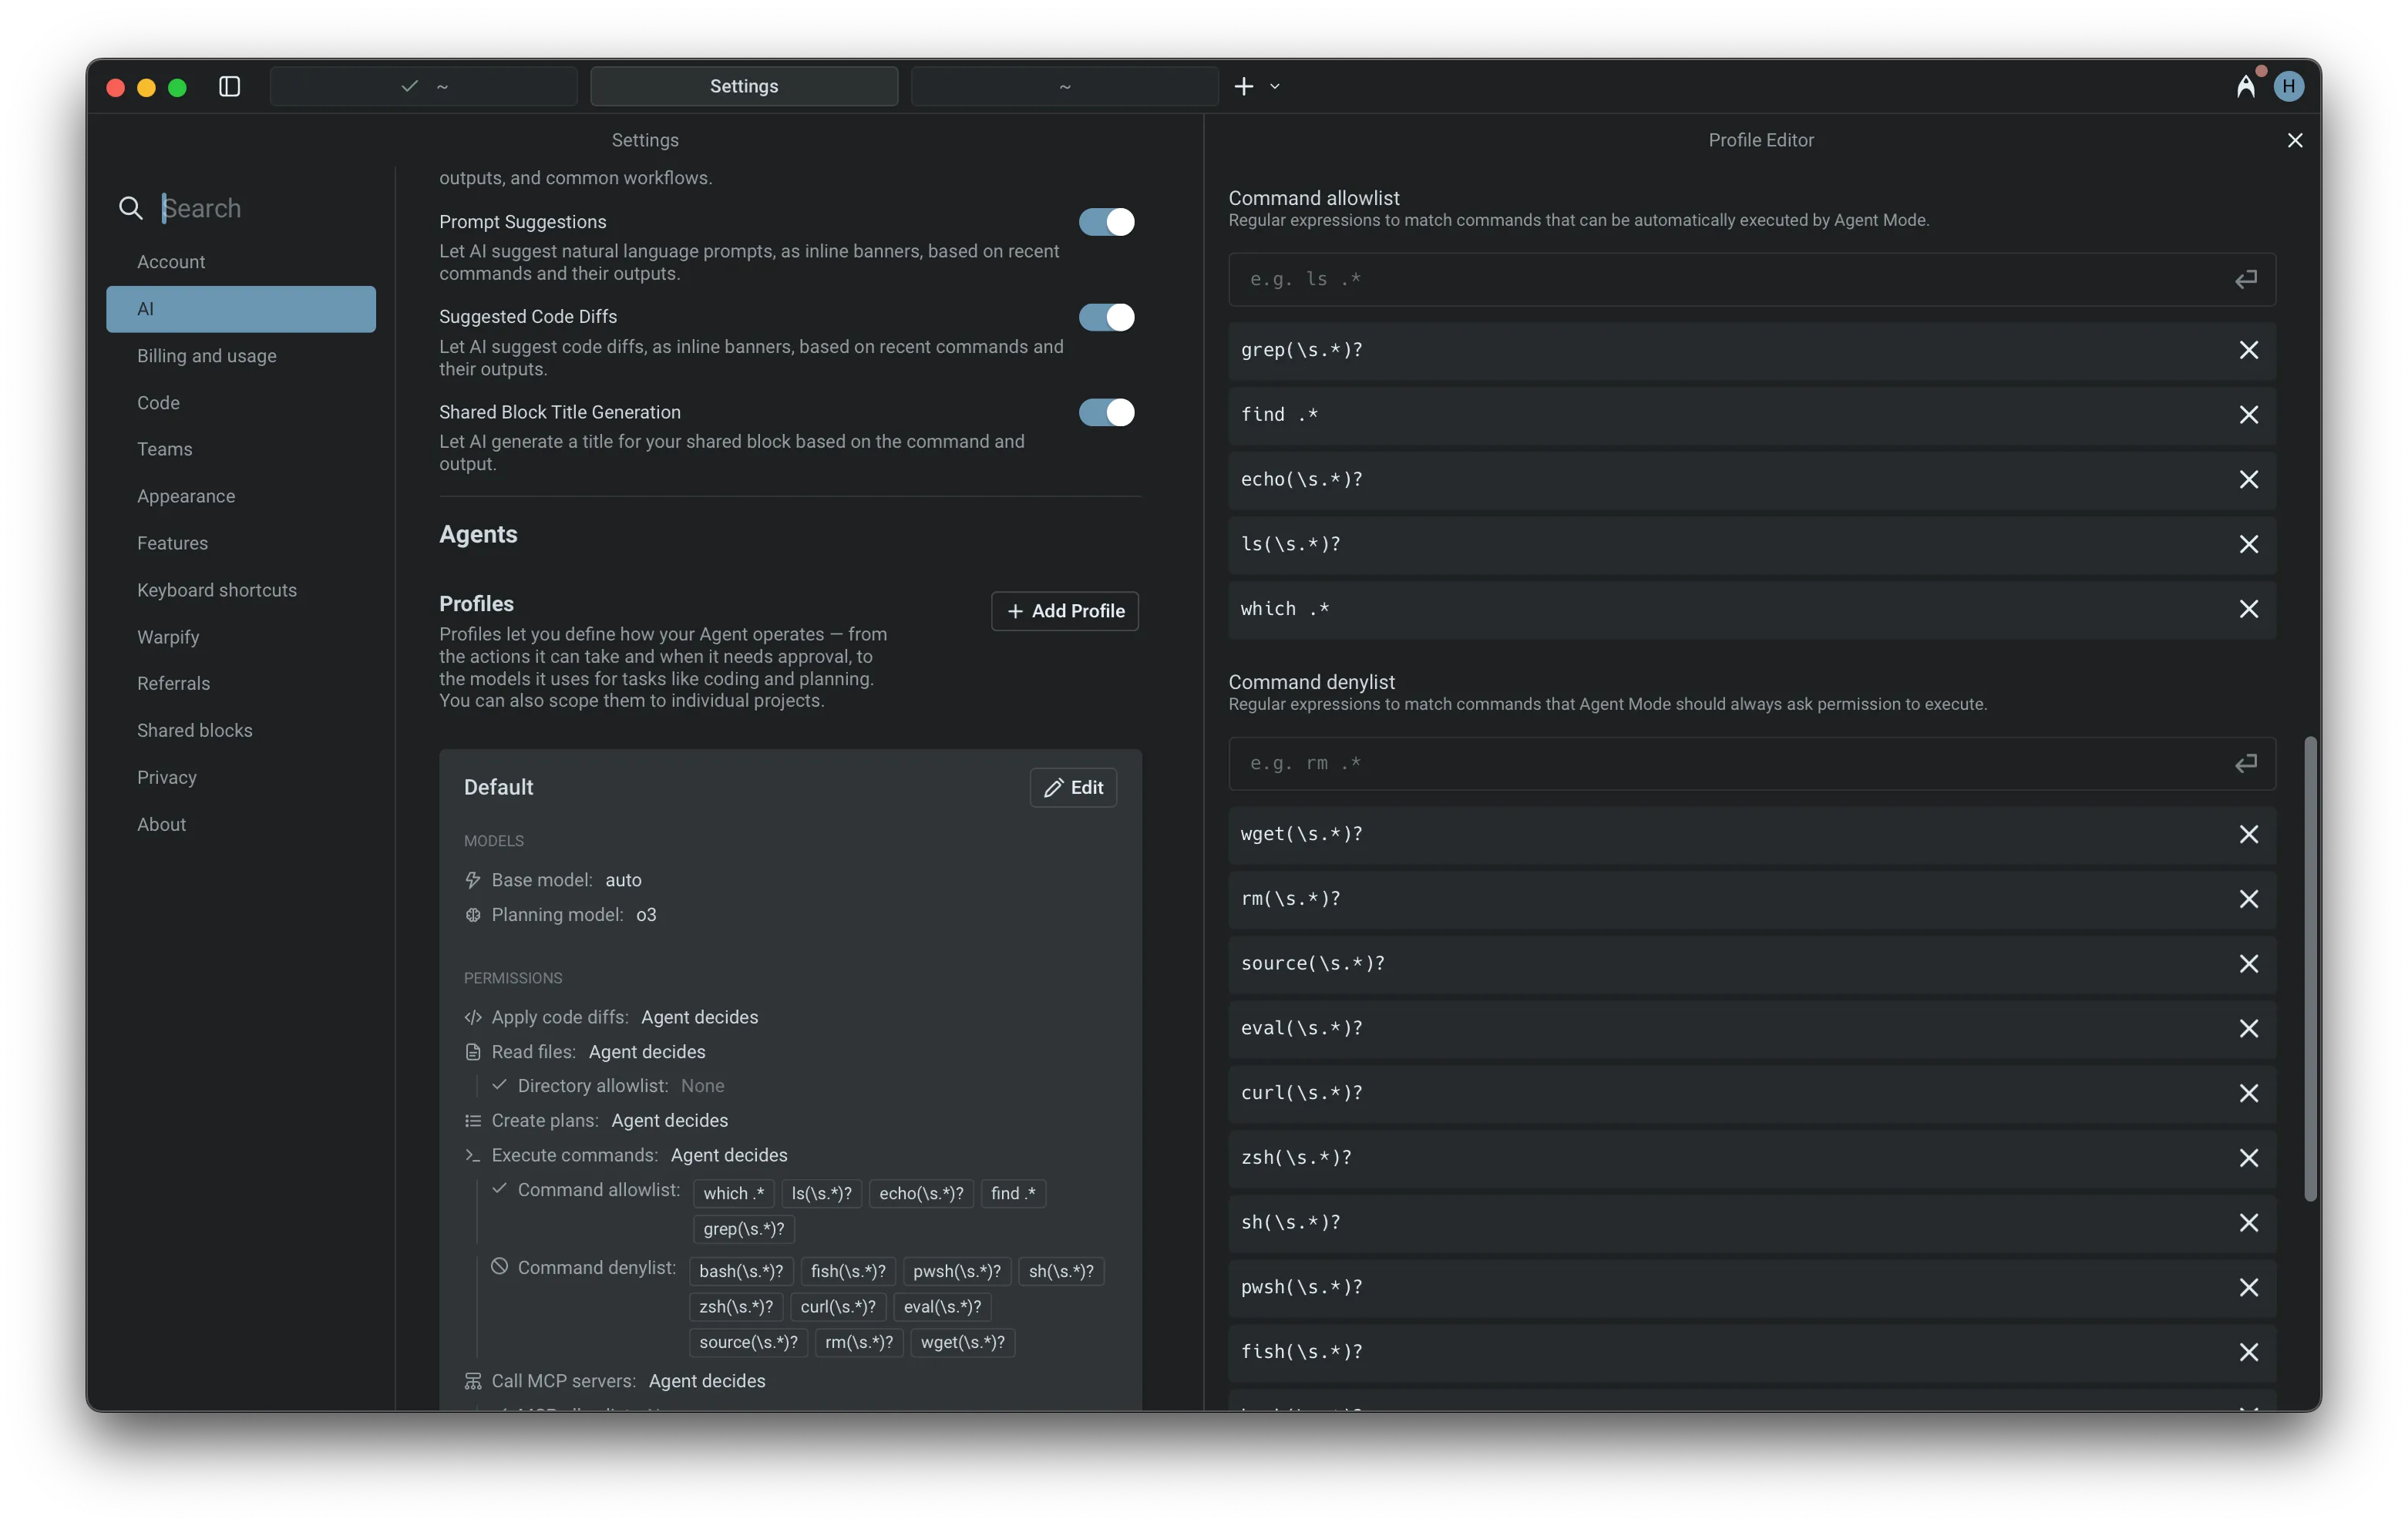
Command allowlist and denylists as part of an Agent Profile.
### Command denylist
[Section titled “Command denylist”](#command-denylist)
For safety, the Agent always prompts for confirmation before executing potentially risky commands. The default denylist includes several examples, such as:
* `wget(\s.*)?` - Network downloads
* `curl(\s.*)?` - Network requests
* `rm(\s.*)?` - File deletion
* `eval(\s.*)?` - Shell code execution
The denylist takes precedence over both the allowlist and `Agent decides`: if a command matches the denylist, the Agent asks for permission even when that action type is set to **Always allow**. Add your own regular expressions to this list in **Settings** > **Agents** > **Profiles** > **Command denylist**. The one exception is [Run until completion](#run-until-completion), which bypasses your denylist by default.
### MCP permissions
[Section titled “MCP permissions”](#mcp-permissions)
MCP servers let you extend the Agent with custom tools and data sources using standardized, plugin-like modules.
In this settings menu, you can configure which MCP servers the Agent is allowed to call:
* Use the MCP allowlist to give the Agent permission to call specific servers without asking.
* Use the MCP denylist to require approval before calling certain servers, even if they’re also in the allowlist.
* Or set the Agent to “decide” — it will act autonomously when confident, and ask for confirmation when uncertain.
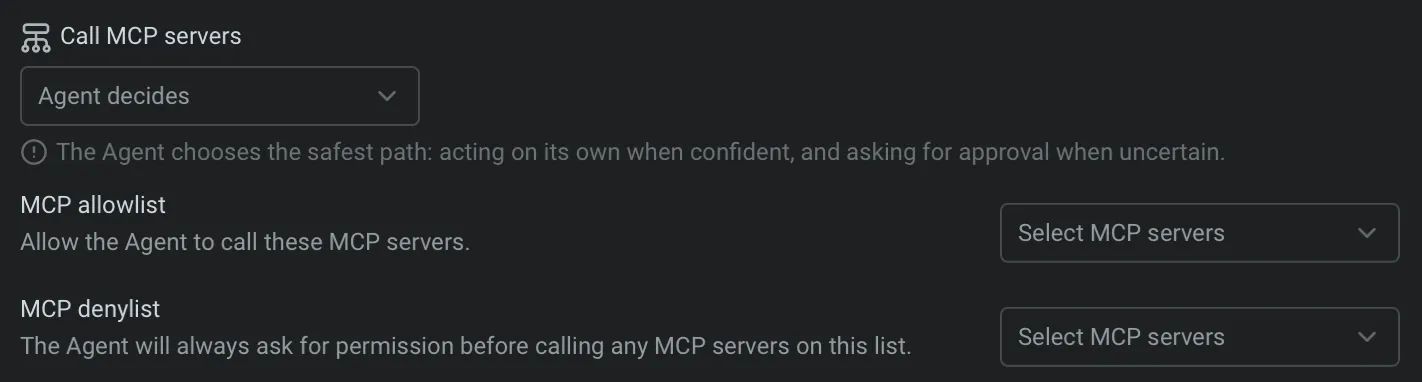
MCP server interaction settings in an Agent Profile.
Note
To learn how to build and configure your own MCP server, check out the [MCP feature docs](/agents/capabilities/mcp/).
## Run until completion
[Section titled “Run until completion”](#run-until-completion)
During an Agent interaction, you can give the Agent full autonomy for the current task. When auto-approve is on, every suggested command runs immediately until the task finishes, or you stop it with `Ctrl+C`.
* macOS
Auto-approve all Agent actions with: `⌘+Shift+I`
* Windows
Auto-approve all Agent actions with: `Ctrl+Shift+I`
* Linux
Auto-approve all Agent actions with: `Ctrl+Shift+I`
Auto-approve and take-over controls.
Caution
*Run until completion* is the purest form of “YOLO” mode: the Agent proceeds without asking for confirmation, and by default it also runs commands that match your command denylist.
To keep your denylist in force during *Run until completion*, turn off **Allow auto-approve to bypass command denylist** in **Settings** > **Agents** > **Warp Agent** > **Input**. Denylist rules your team enforces through the [Admin Panel](/enterprise/team-management/admin-panel/) always require approval and are never bypassed.
***
## Next steps
[Section titled “Next steps”](#next-steps)
Once you’ve configured how your agent operates, try giving it a larger task to plan and execute.
* **[Planning](/agents/capabilities/planning/)** - Break down complex tasks into structured, executable plans that the agent runs step by step.
* **[Code diffs](/agents/local-agents/code-diffs/)** - Review, refine, and apply code changes the agent generates.
* **[Interactive Code Review](/agents/local-agents/interactive-code-review/)** - Leave inline comments on agent-generated diffs and have the agent address your feedback.
# Codebase Context
Canonical page: [/agents/capabilities/codebase-context/](https://docs.warp.dev/agents/capabilities/codebase-context/)
> Warp indexes your Git-tracked codebase to help Agents understand your code and generate accurate, context-aware responses. No code is stored on Warp servers.
Codebase Context helps Agents understand your project by indexing your local codebase. This allows Agents to generate more accurate completions, suggest context-aware edits, and answer questions using real knowledge of your code.
## Get started
[Section titled “Get started”](#get-started)
Index a project and see the difference in agent responses in a few minutes.
Note
**Don’t have a project to try?** Clone a popular open-source repo to test out codebase indexing:
```bash
git clone https://github.com/vercel/next.js.git && cd next.js
```
1. **Open a project folder in Warp.** Navigate to a Git repository using `cd` or open a folder from the file tree. Warp automatically detects the Git repo and begins indexing.
2. **Verify indexing status.** In Warp, go to **Settings** > **Code** > **Indexing and projects** and check the status under “Initialized / indexed folders.” Once the status shows **Synced**, your codebase is ready.
3. **Ask the Agent a question about your code.** Start an Agent conversation (`⌘+Enter` on macOS, `Ctrl+Shift+Enter` on Windows/Linux) and try a prompt like:
* “Explain the architecture of this project”
* “What are the main entry points?”
* “Walk me through the most important modules”
4. **See the difference.** The Agent grounds its responses in actual files, functions, and line numbers from your codebase, producing more accurate and context-aware answers.
***
## Indexing your codebase
[Section titled “Indexing your codebase”](#indexing-your-codebase)
When you open a directory in Warp, we check if it is part of a Git repository. If it is, Warp begins indexing the source code to provide rich context for Agents. Warp also detects [Git worktree](/code/git-worktrees/) checkouts — each worktree is indexed as its own repository, so Agents always have accurate context for the branch you’re working on.
Note
Code indexed with Codebase Context is never stored on our servers. Codebase Context works with both local agent sessions and [cloud agent runs](/platform/). Without Codebase Context enabled, agents will still be able use terminal commands (i.e. `grep`, `sed`) to navigate your code.
Note
Codebase Context works in SSH sessions when [Warp’s SSH extension](/terminal/warpify/ssh/) is installed on the remote host — the remote repository is indexed directly on the remote machine. WSL sessions are not yet supported ([GitHub #6744](https://github.com/warpdotdev/Warp/issues/6744)).
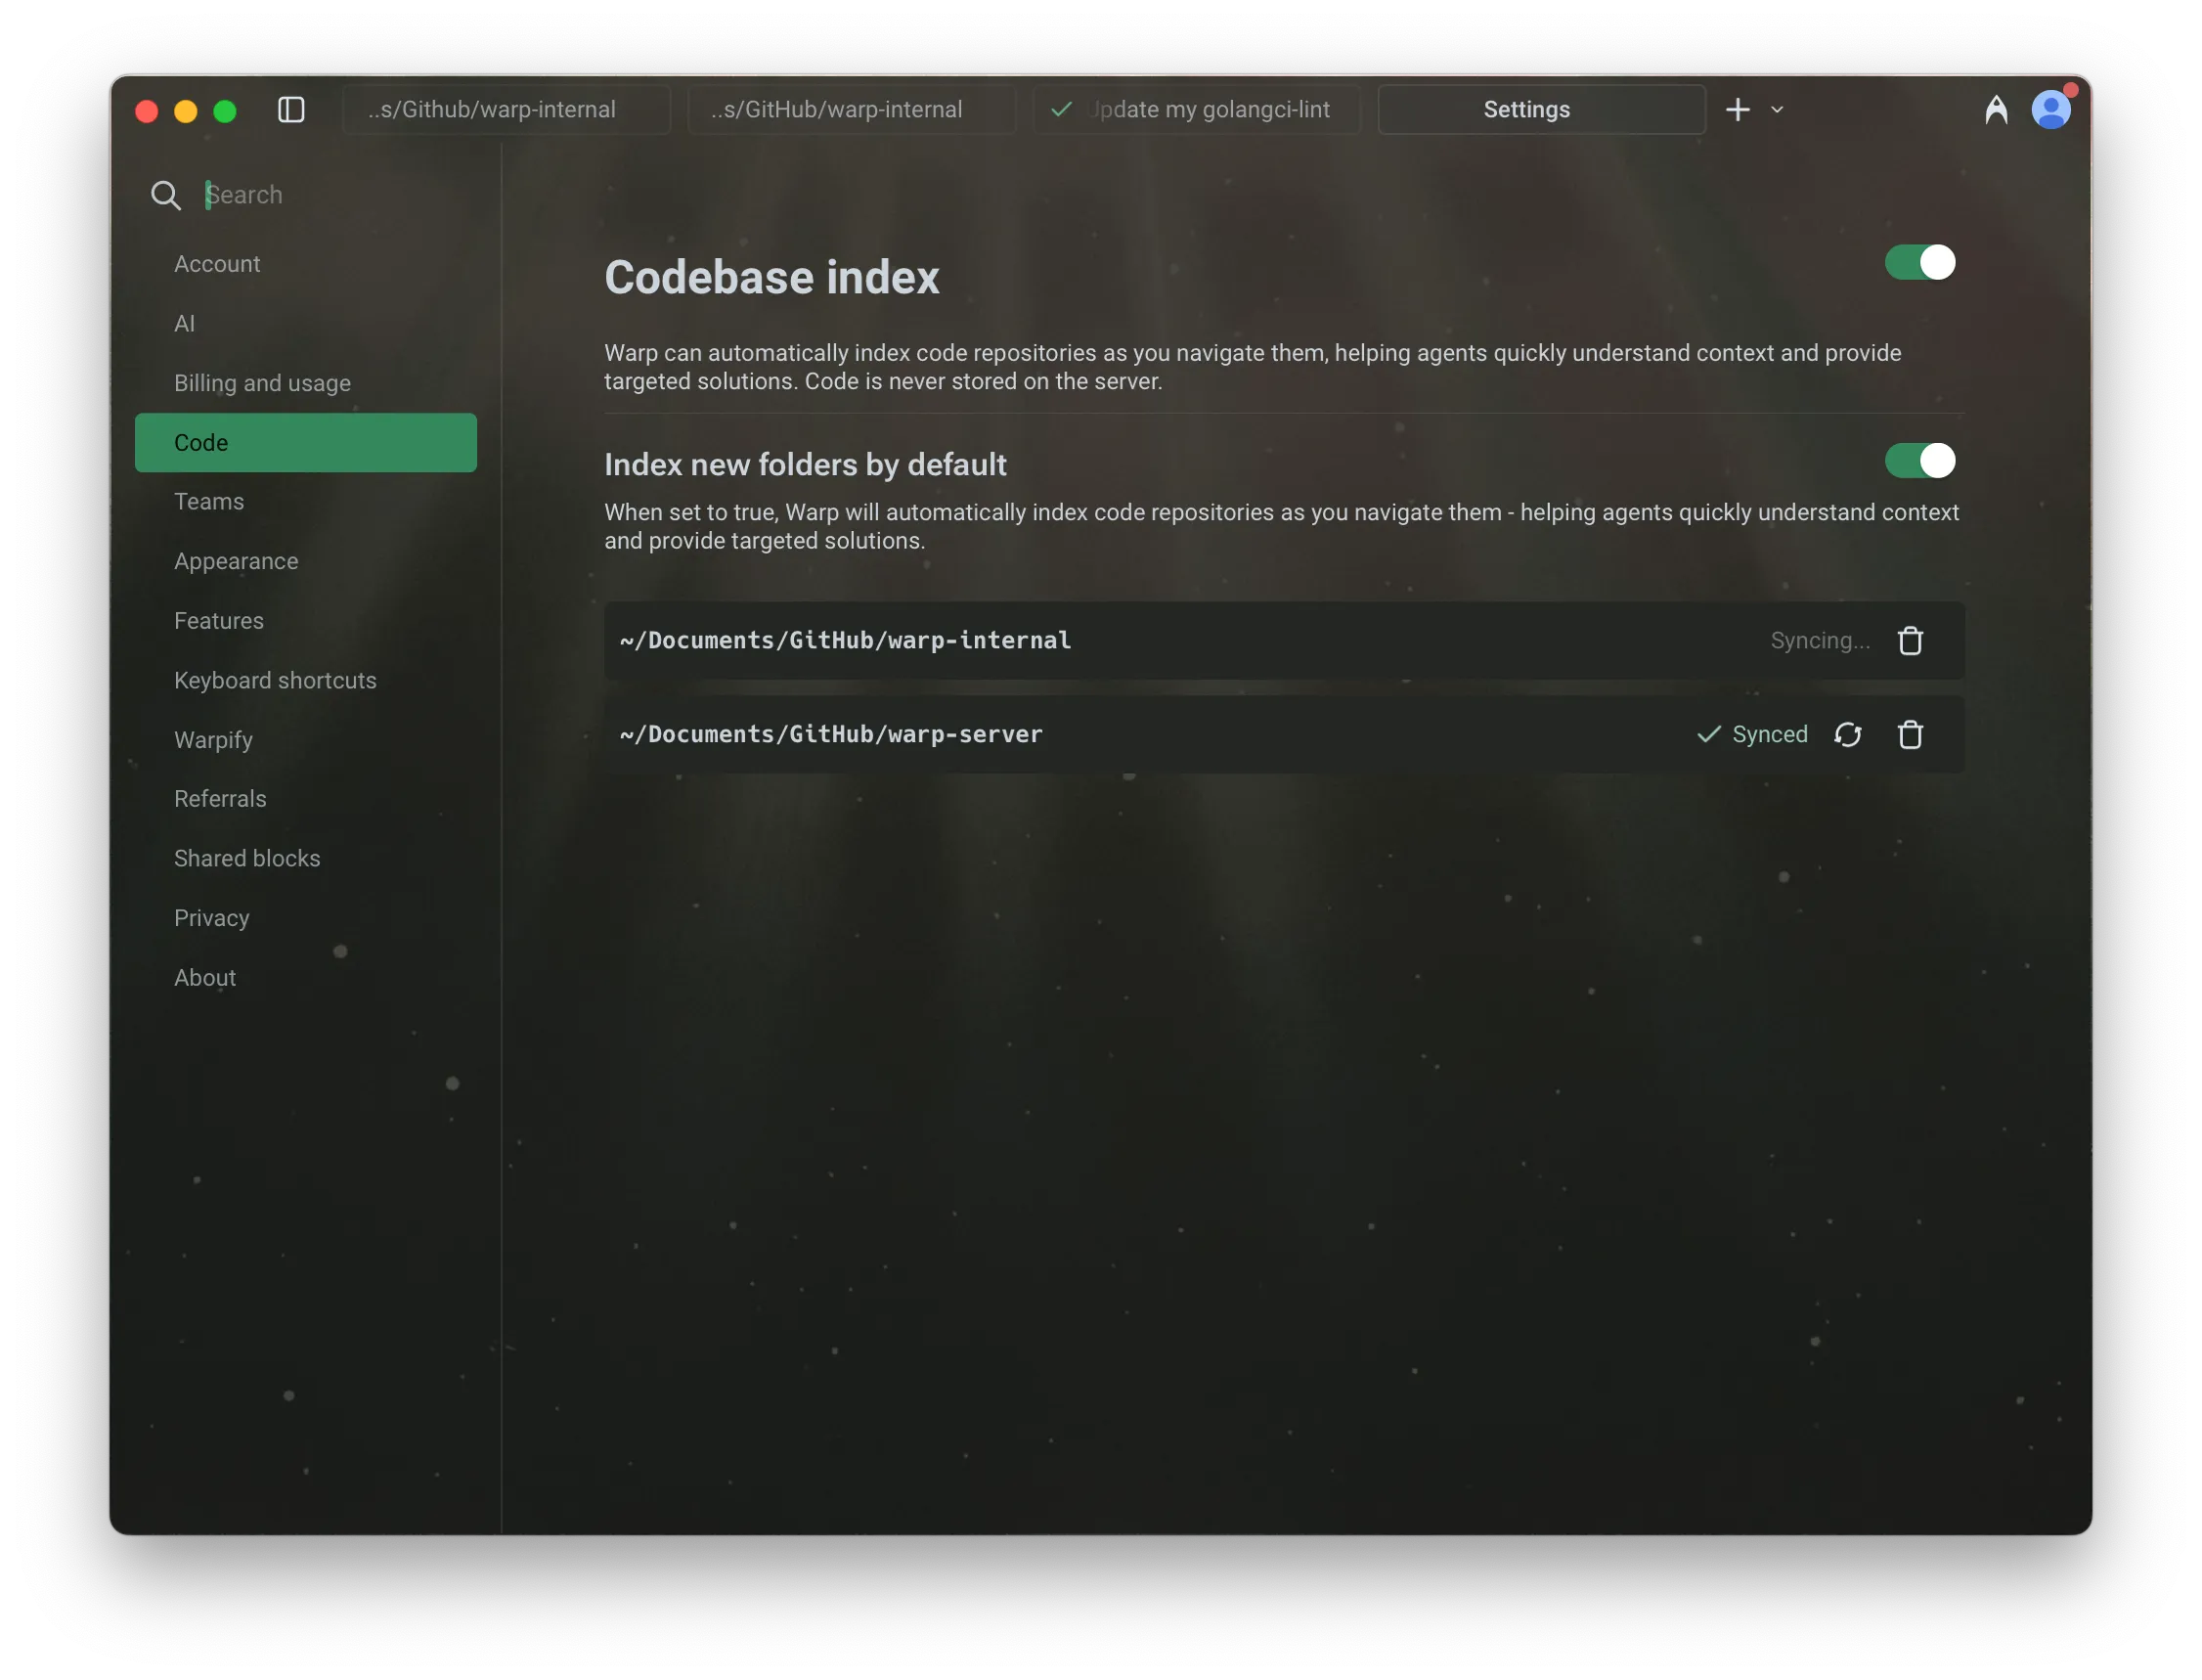
Codebase indexing settings.
**Codebase indexing intervals and triggers:**
* Initially when you have Codebase Context enabled.
* Warp automatically triggers a codebase index periodically.
* Whenever a new Agent conversation begins.
* When you click on the sync 🔄 button in **Settings** > **Code** > **Indexing and projects**.
**This embeddings index helps Agents:**
* Understand your project structure and reference relevant code
* Generate completions that match your style and patterns
* Suggest edits in the correct locations based on real context
For large projects, indexing may take a few minutes. Agents will not use Codebase Context until indexing is complete, but **agentic coding features remain fully available in the meantime**.
Note
You can view and manage your indexed codebases in **Settings** > **Code** > **Indexing and projects** under “Initialized / indexed folders”. You can also choose whether to automatically index new folders as you navigate them.

### Codebase indexing states
[Section titled “Codebase indexing states”](#codebase-indexing-states)
When viewing indexed codebases in Warp under **Settings** > **Code** > **Indexing and projects**, you may see different status indicators:
* **Synced** — Indexing is complete and the codebase is ready to be used as context.
* **Discovering files** – Warp is currently scanning and indexing files in the codebase.
* **Failed** – Indexing failed. Common reasons include unreadable `.git` directories or corrupted repositories. Try re-cloning the repo and syncing again.
* **Codebase too large** – The number of files in the codebase exceeds your current plan’s limit. You can either reduce the number of files being indexed using `.warpindexingignore`, or [contact sales](https://www.warp.dev/contact-sales) for support with larger codebases.
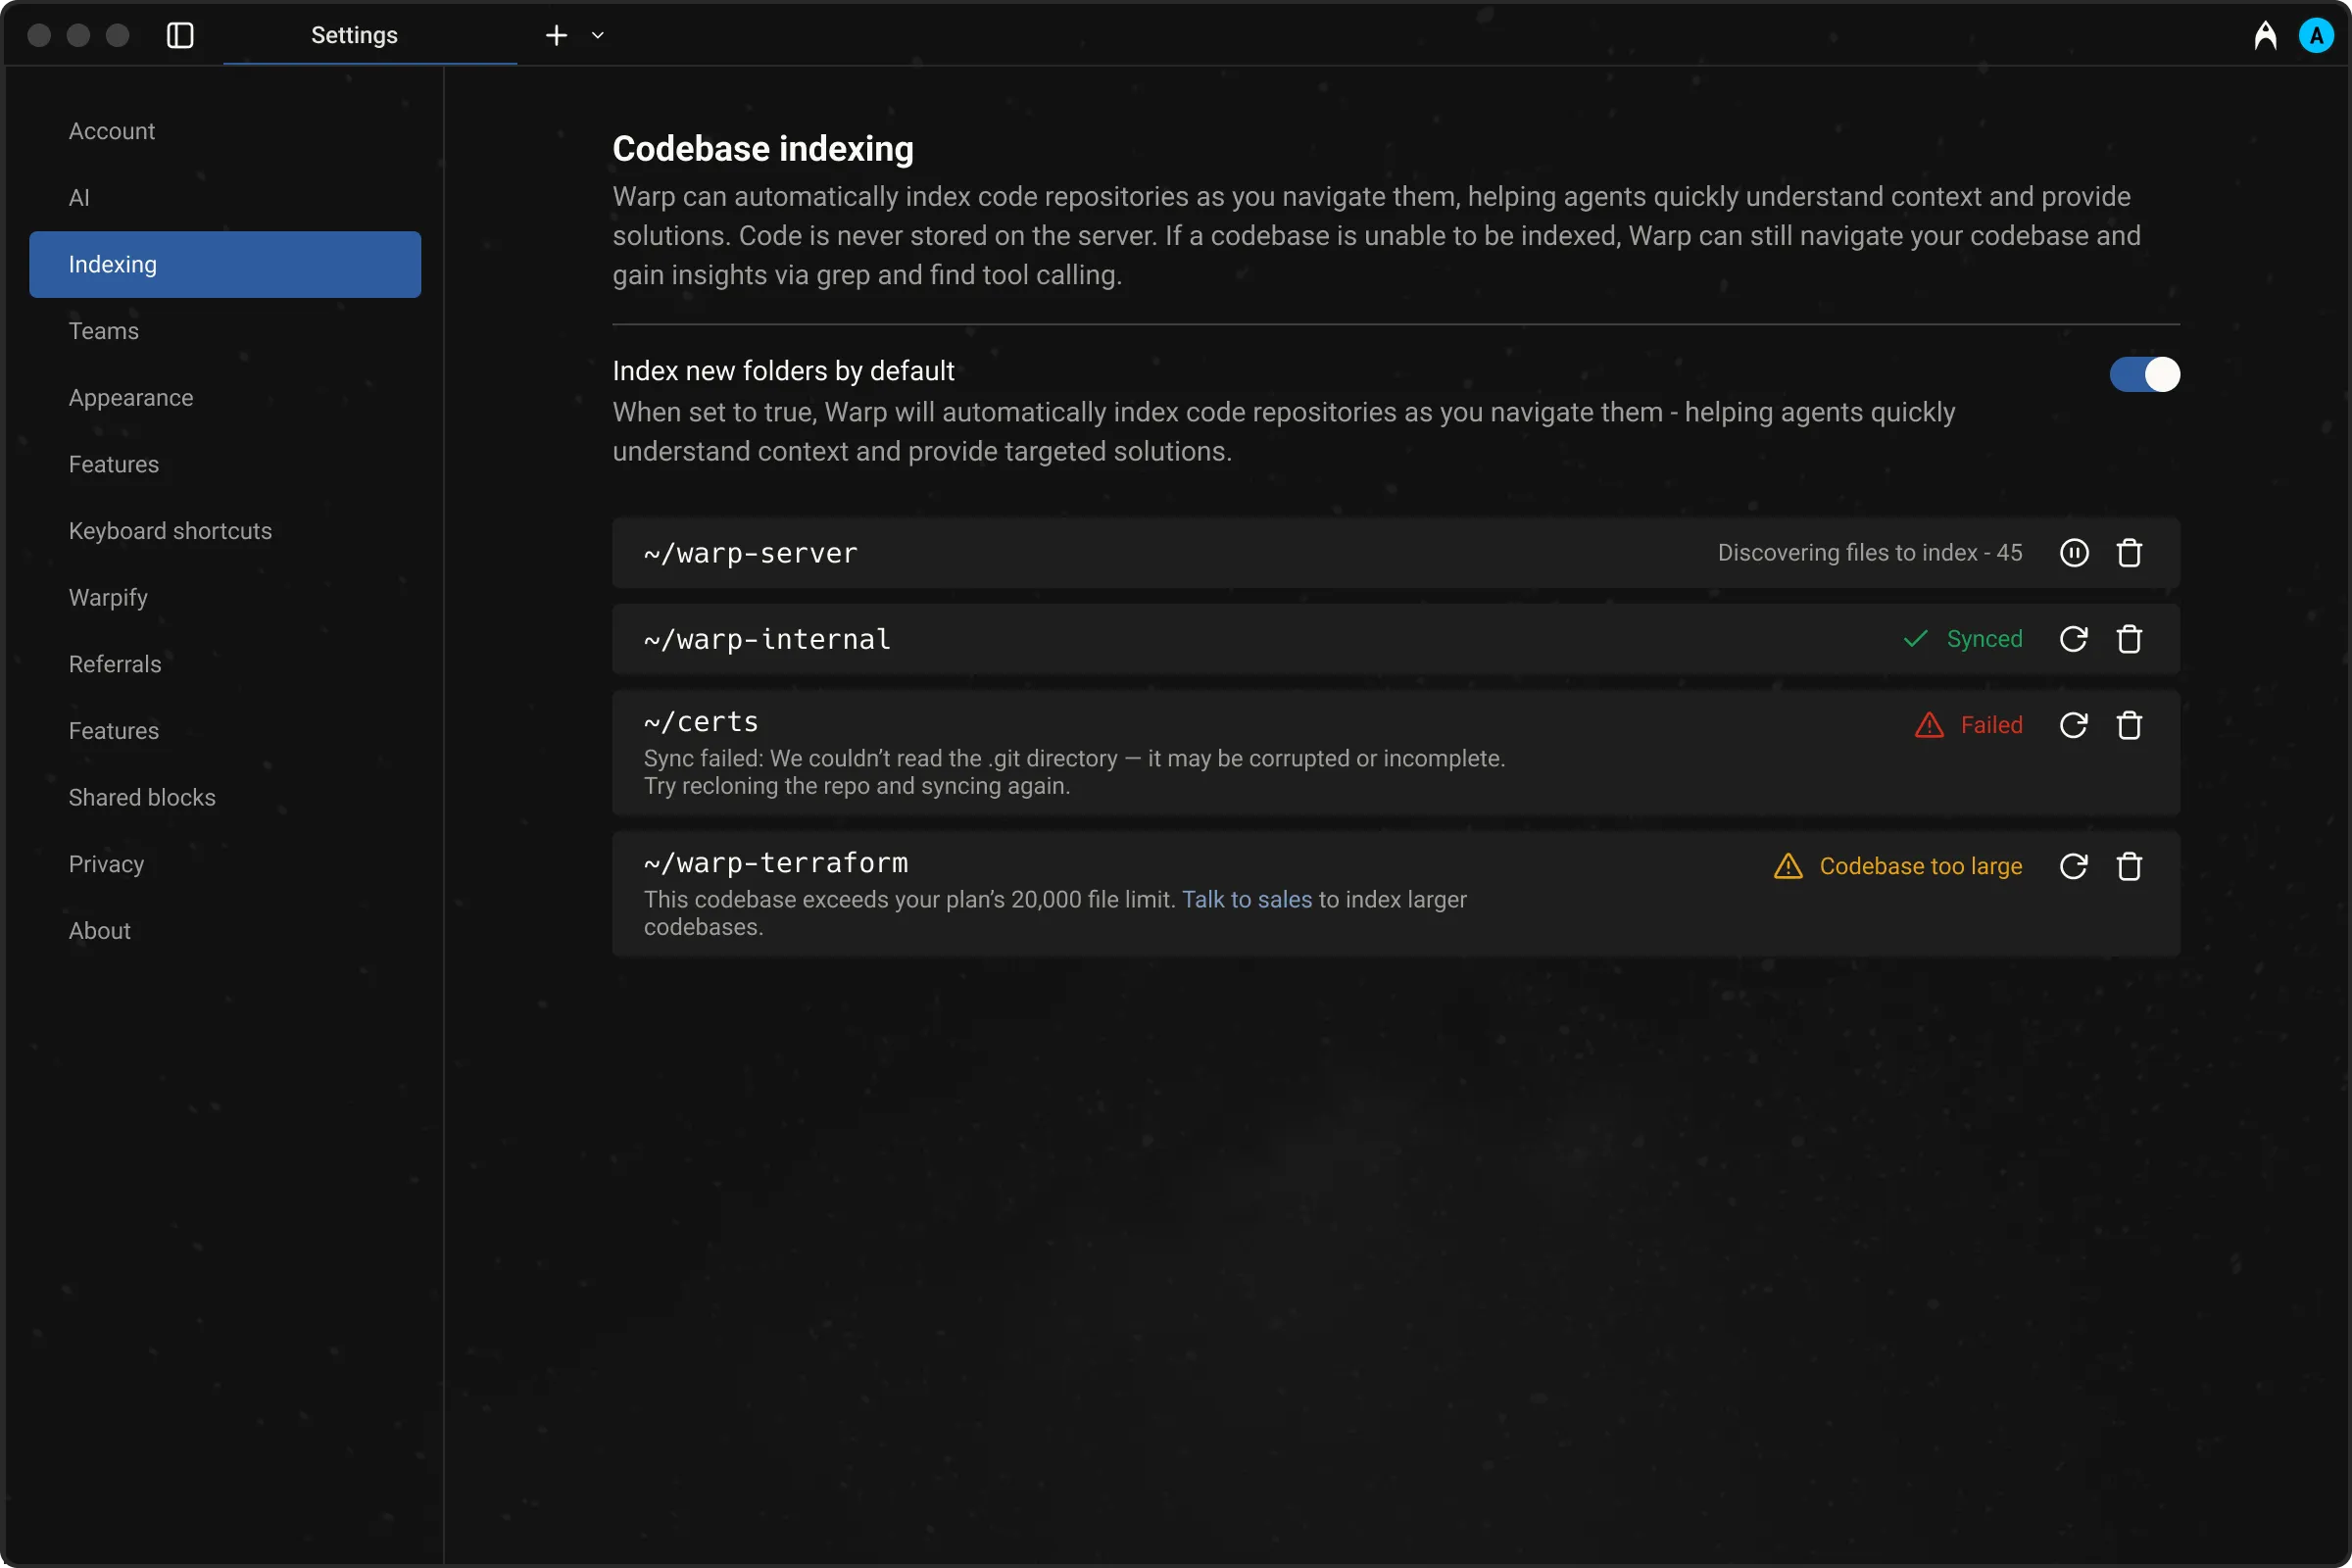
Codebase indexing status overview.
### When does codebase syncing happen?
[Section titled “When does codebase syncing happen?”](#when-does-codebase-syncing-happen)
Warp automatically triggers a codebase sync initially and periodically, when you click on the sync 🔄 button in **Settings** > **Code** > **Indexing and projects**, or when you start a new Agent conversation. However, if many files have changed or the network is slow, the sync may not complete before the Agent tries to access context.
Note
In large projects (e.g. after a branch switch), there may be a short delay where the Agent references stale or outdated files.
### File and codebase limits
[Section titled “File and codebase limits”](#file-and-codebase-limits)
The number of codebases you can index and the maximum number of files per repository vary by plan. The Free plan supports indexing **up to 5,000 files per repository**. Higher tiers support larger repositories and additional codebases.
For full details, visit our [pricing page](https://www.warp.dev/pricing).
### Ignore files
[Section titled “Ignore files”](#ignore-files)
For large codebases, Warp supports several ignore files to give you control over what gets indexed. This allows each developer to focus context on the parts of the codebase most relevant to their work.
Warp respects the following ignore files:
* `.gitignore`
* `.warpindexingignore`
* `.cursorignore`
* `.cursorindexingignore`
* `.codeiumignore`
Use these files to skip indexing of folders, generated files, or any content you don’t want agents to reference. This can improve performance and result quality.
Note
Files excluded by ignore rules **do not** count toward your codebase’s file limit.
## Codebase Context in cloud agent runs
[Section titled “Codebase Context in cloud agent runs”](#codebase-context-in-cloud-agent-runs)
Codebase Context is available in all [cloud agent runs](/platform/viewing-cloud-agent-runs/) — including runs triggered from the CLI, API/SDK, integrations (Slack, Linear, GitHub Actions), and schedules — as long as Codebase Context is enabled for your account.
**No additional configuration is needed.** If Codebase Context is enabled, cloud agents use it automatically.
## Multi-repo context
[Section titled “Multi-repo context”](#multi-repo-context)
Warp supports referencing context across multiple indexed repositories. Note that you don’t need to be inside a specific repo for agents to use its context.
**This is especially useful when:**
* Implementing a feature across multiple repos, such as full-stack work across client and server
* Using one repo as a reference while building in another, for example: “copy the implementation from repo A into my repo B”
Agents will only reference other repositories if they are already indexed. During cross-repo tasks, Warp’s Agents have access to the file paths of all indexed repos. It is more likely to use cross-repo context when you mention the exact name of the repo in your prompt.
## Demo: Explain my codebase with Warp
[Section titled “Demo: Explain my codebase with Warp”](#demo-explain-my-codebase-with-warp)
Here’s an example from [Warp Guides](/guides/), where Zach demonstrates how Warp uses Codebase Context to search for and use the relevant files as context:

***
## Next steps
[Section titled “Next steps”](#next-steps)
With your codebase indexed, you can browse your project directly in Warp and start letting agents take action on your code.
* **[File Tree](/code/code-editor/file-tree/)** - Browse your project structure in Warp’s sidebar and open files directly.
* **[Code editor](/code/code-editor/)** - Edit files with syntax highlighting, LSP support, and find-and-replace without leaving Warp.
* **[Agent profiles and permissions](/agents/capabilities/agent-profiles-permissions/)** - Configure how much autonomy the agent has when working with your code.
# Computer Use for agents
Canonical page: [/agents/capabilities/computer-use/](https://docs.warp.dev/agents/capabilities/computer-use/)
> Let agents interact with desktop GUIs in sandboxed cloud environments for automated UI testing and validation.
Computer Use enables agents to interact with desktop environments. The agent can see what’s displayed on screen, click and drag, type text, use keyboard shortcuts, and perform other GUI interactions—all within a secure, isolated sandbox.
A key use case is **testing UI changes** with a self-contained feedback loop, where the agent can verify that your code changes produce the expected visual and behavioral results without requiring manual testing.
## Capabilities
[Section titled “Capabilities”](#capabilities)
With Computer Use, agents can:
* **Take screenshots** - Capture and analyze the current display
* **Record video** - Capture sessions as annotated video recordings; see [Testing and recordings](/agents/capabilities/computer-use/testing-and-recordings/)
* **Interact with applications** - Click buttons, fill forms, navigate interfaces
* **Type and control keyboard** - Enter text and use keyboard shortcuts
* **Automate testing workflows** - Test UI changes end-to-end without manual intervention
* **Work with browser-based interfaces** - Test web apps and navigate the web
Computer Use is only available in Warp’s sandboxed cloud environments, not in local interactive terminal sessions.
## In this section
[Section titled “In this section”](#in-this-section)
* [Browser use](/agents/capabilities/computer-use/browser-use/) - Drive the bundled Chromium browser, visually or with scripted Playwright commands.
* [Testing and recordings](/agents/capabilities/computer-use/testing-and-recordings/) - Validate changes end-to-end and capture annotated video recordings as proof.
* [Screenshots and videos in pull requests](/agents/capabilities/computer-use/artifacts-in-prs/) - Attach captured screenshots and recordings to pull request descriptions automatically.
***
## Enabling Computer Use
[Section titled “Enabling Computer Use”](#enabling-computer-use)
Computer Use is **enabled by default** for cloud agent runs on Warp’s built-in harness: when a run’s configuration doesn’t specify a Computer Use setting, the agent runs with Computer Use available. Runs on [third-party harnesses](/platform/harnesses/) (Claude Code and Codex) default to Computer Use disabled because third-party harnesses don’t integrate with Warp’s Computer Use tooling. You can control Computer Use per run or per configuration through several entry points:
### Warp app settings
[Section titled “Warp app settings”](#warp-app-settings)
Runs started from the Warp app don’t use the server default: they always follow the app’s **Computer use in Cloud Agents** setting ([`cloud_agent_computer_use_enabled`](/terminal/settings/all-settings/)), which is off by default. To control Computer Use for [Cloud Agents](/platform/) started from the Warp app, navigate to **Settings** > **Agents** > **Warp Agent** > **Experimental** > **Computer use in Cloud Agents**.
### CLI
[Section titled “CLI”](#cli)
When running cloud agents with the [Oz CLI](/agents/cli/oz-cli/), use flags to control Computer Use per run:
```bash
oz agent run-cloud --computer-use --prompt ""
oz agent run-cloud --no-computer-use --prompt ""
```
### API
[Section titled “API”](#api)
When creating a cloud agent run with the [Warp Platform API](/factories/api-and-sdk/), the optional `config.computer_use_enabled` field controls Computer Use. When omitted, it defaults to `true` for runs on Warp’s built-in harness and `false` for runs on third-party harnesses. Set it to `false` to disable Computer Use for the run:
```json
{
"prompt": "Build a button component that matches this design, then test it in the browser",
"config": {
"computer_use_enabled": false,
"environment_id": "optional-environment-id"
}
}
```
For full API documentation, see the [Warp Platform API](/factories/api-and-sdk/) reference.
### Web app
[Section titled “Web app”](#web-app)
In the [Oz web app](https://oz.warp.dev), you can enable or disable Computer Use for:
* **New agent runs** - Configure Computer Use when starting a new agent run from the web app
* **Scheduled agent runs** - Enable Computer Use for [scheduled agents](/platform/triggers/scheduled-agents/) managed from the web app
* **Integrations** - Configure Computer Use for Slack, Linear, and other [integration-triggered agents](/platform/integrations/)
***
## How Computer Use works
[Section titled “How Computer Use works”](#how-computer-use-works)
### Setup and requirements
[Section titled “Setup and requirements”](#setup-and-requirements)
Computer Use runs in a containerized sandbox, allowing headless cloud environments to render and interact with graphical applications. The sandbox is fully isolated—it does not have access to your local machine, credentials, or sensitive data outside the sandbox environment.
Your cloud environment must include any desktop applications you want the agent to control in your [environment configuration](/platform/environments/). Browser-based tasks need no extra setup: every Computer Use environment includes a bundled Chromium browser. Learn more in [Browser use](/agents/capabilities/computer-use/browser-use/).
### Model selection
[Section titled “Model selection”](#model-selection)
Computer Use currently supports Anthropic Claude models. Warp uses an auto model selector to choose the best-suited model for each Computer Use task.
***
## Recording sessions
[Section titled “Recording sessions”](#recording-sessions)
Agents can record their Computer Use sessions as annotated video artifacts — capturing clicks, key presses, and cursor movement alongside the interaction, with idle time trimmed out. Recordings are captured entirely inside the sandbox and never include your local desktop or credentials.
For the recording pipeline, what the finished video contains, and where to find recordings, see [Testing and recordings](/agents/capabilities/computer-use/testing-and-recordings/). For how recordings and screenshots land on pull requests, see [Screenshots and videos in pull requests](/agents/capabilities/computer-use/artifacts-in-prs/).
***
## Security considerations
[Section titled “Security considerations”](#security-considerations)
Computer Use comes with unique security considerations. These risks are heightened when interacting with the internet.
To minimize risks when using Computer Use:
* **Avoid sensitive data** - Do not pass API keys, authentication tokens, or personal information to agents using Computer Use
* **Limit internet access** - If your environment has internet access, consider restricting to an allowlist of known-safe domains
* **Require human confirmation** - For tasks with real-world consequences (e.g., financial transactions, accepting legal terms), ask a human to confirm before the agent proceeds
* **Review agent actions** - Regularly review what agents are doing on your behalf, especially when testing new workflows
***
## Example workflows
[Section titled “Example workflows”](#example-workflows)
### Testing UI changes
[Section titled “Testing UI changes”](#testing-ui-changes)
Verify that code changes produce the expected visual results and behavior:
* **Build from mockups** - Receive a Figma design or mockup image, build the UI, and test it matches
* **Visual regression testing** - After code changes, verify UI renders correctly
* **Form and interaction testing** - Test form submissions, validation, error handling
* **Responsive design validation** - Test layout on different screen sizes
For complete end-to-end examples with demo recordings — validating UI changes, QA of critical flows, and bug reproduction — see [Testing and recordings](/agents/capabilities/computer-use/testing-and-recordings/).
### Browsing and web interaction
[Section titled “Browsing and web interaction”](#browsing-and-web-interaction)
Computer Use can also help with general web tasks: browsing websites, filling out and submitting forms, and navigating multi-step workflows in web applications. See [Browser use](/agents/capabilities/computer-use/browser-use/) for how agents drive the browser.
***
## Related capabilities
[Section titled “Related capabilities”](#related-capabilities)
* [Images as Context](/agents/local-agents/agent-context/images-as-context/) - Pass design mockups and screenshots as context
* [Full Terminal Use](/agents/capabilities/full-terminal-use/) - Let agents drive interactive terminal apps, see live output, and run commands
* [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/) - Open the cloud run transcript and artifacts after a Computer Use session finishes
# Screenshots and videos in pull requests
Canonical page: [/agents/capabilities/computer-use/artifacts-in-prs/](https://docs.warp.dev/agents/capabilities/computer-use/artifacts-in-prs/)
> Cloud agents automatically attach Computer Use screenshots and video recordings to pull request descriptions, giving reviewers visual proof without extra steps.
When a cloud agent run opens or updates a pull request, the screenshots and video recordings it captured with [Computer Use](/agents/capabilities/computer-use/) are attached to the PR description automatically. Reviewers get visual proof of the change — a rendered UI state, a recorded flow, a bug reproduction — without leaving the pull request.
## What gets attached
[Section titled “What gets attached”](#what-gets-attached)
* **Screenshots** - UI states the agent captures during its Computer Use session. Up to 10 screenshots are attached per pull request.
* **Video recordings** - Session recordings the agent produces. See [Testing and recordings](/agents/capabilities/computer-use/testing-and-recordings/) for how recordings are captured and processed.
Attachment is automatic: once a screenshot or recording artifact is associated with the run, the agent includes it the next time it creates or updates a pull request. You can encourage captures in your prompt — for example, “take screenshots of the before and after states” or “record the flow and attach it to the PR.”
## Attachment modes
[Section titled “Attachment modes”](#attachment-modes)
A team-level setting controls how artifacts are attached:
* **Link only (default)** - Screenshots and recordings are attached as links to the run’s page in the Oz web app. Artifacts stay private: opening a link requires access to the run.
* **Embed** - Screenshots render inline as images in the PR description, and recordings are attached as direct download links. To make this work, the attached artifacts are published at stable, publicly accessible URLs.
* **Disabled** - No screenshots or recordings are attached to pull requests.
Caution
In **Embed** mode, attached screenshots and recordings become publicly downloadable by anyone with the URL — including anyone who can read the PR description. Use **Link only** if your Computer Use sessions may capture content that shouldn’t leave your team.
### Changing the attachment mode
[Section titled “Changing the attachment mode”](#changing-the-attachment-mode)
Team admins control the attachment mode from the [Admin Panel](https://app.warp.dev/admin/):
1. In the Admin Panel sidebar, select your team under **Team admin**.
2. Click the **Platform** tab.
3. Under **Pull request artifact attachments**, choose **Disabled**, **Link only**, or **Embed**.

The Pull request artifact attachments setting in the Admin Panel.
## Where else artifacts appear
[Section titled “Where else artifacts appear”](#where-else-artifacts-appear)
Pull requests aren’t the only place captures end up:
* **In the conversation** - Screenshots and recordings appear as blocks in the agent’s conversation as they’re captured.
* **On the run page** - Open the run in the [Oz web app](/platform/oz-web-app/#runs) to view, play, or download all artifacts the run produced.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Computer Use](/agents/capabilities/computer-use/) - Control Computer Use and understand security considerations.
* [Testing and recordings](/agents/capabilities/computer-use/testing-and-recordings/) - How the recording pipeline works and what finished videos contain.
* [Admin Panel for teams](/enterprise/team-management/admin-panel/) - The full reference for team settings, including the Platform section.
* [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/) - Open and inspect cloud agent run transcripts.
* [Privacy](/support-and-community/privacy-and-security/privacy/) - Warp’s data handling policies, including how run artifacts are stored.
# Browser use for agents
Canonical page: [/agents/capabilities/computer-use/browser-use/](https://docs.warp.dev/agents/capabilities/computer-use/browser-use/)
> Computer Use environments include bundled Chromium and the Playwright CLI, so agents can test web apps and browse without extra setup.
Agents with [Computer Use](/agents/capabilities/computer-use/) enabled can drive a real browser inside their sandboxed cloud environment — opening web apps, exercising flows, filling forms, and verifying what renders on screen. Every Computer Use environment includes a browser out of the box, so browser-based tasks work without any changes to your [environment configuration](/platform/environments/).
## The bundled browser
[Section titled “The bundled browser”](#the-bundled-browser)
Computer Use environments ship with a bundled Chromium browser that runs on any environment base image — you don’t need to install Chrome, Firefox, or any browser dependencies yourself.
* **Available as `chromium`** - The browser is on the agent’s `PATH` as `chromium`, and the `CHROMIUM_BIN` and `BROWSER` environment variables point to it.
* **Your own browser wins** - If your environment’s base image already provides a browser, the agent uses that instead of the bundled one.
## Two ways to drive the browser
[Section titled “Two ways to drive the browser”](#two-ways-to-drive-the-browser)
Agents can interact with the browser in two complementary ways, and choose the right one for each task:
* **Visual interaction** - The agent takes screenshots, then clicks, types, and scrolls like a person would. This is the right mode for verifying what a user actually sees: layout, styling, visual regressions, and rendering issues.
* **Scripted control with Playwright** - Computer Use environments also bundle the Playwright CLI (`playwright-cli`), which lets the agent drive the browser through shell commands — navigating to URLs, clicking elements, filling forms, and reading page content — without taking a screenshot for every step. Scripted control is faster and more token-efficient for functional flows, like stepping through a multi-page form or asserting that an element exists.
You don’t need to tell the agent which mode to use, but you can steer it in your prompt — for example, “verify the layout visually” or “use Playwright to step through the signup flow.”
The bundled Playwright CLI drives the bundled Chromium rather than downloading its own browser build, so it works on base images that don’t provide Playwright’s system dependencies.
### Attaching to a running browser
[Section titled “Attaching to a running browser”](#attaching-to-a-running-browser)
For advanced workflows, the agent can attach the Playwright CLI to a browser it launched manually with a Chrome DevTools Protocol (CDP) endpoint:
```bash
chromium --remote-debugging-port=9222
playwright-cli attach --cdp=http://localhost:9222
```
This is useful when a task needs to set up specific browser state (for example, launching with custom flags) before scripted control takes over.
Caution
Browsing the open internet is where Computer Use risks are highest. Prefer non-root containers, which let Chromium run its own process sandbox properly, and consider restricting your environment’s internet access to an allowlist of known-safe domains. See the [security considerations for Computer Use](/agents/capabilities/computer-use/#security-considerations).
## Example workflows
[Section titled “Example workflows”](#example-workflows)
* **Test a web app end-to-end** - “Start the dev server, then walk through the checkout flow in the browser and verify each step works.”
* **Verify a UI change visually** - “Open the settings page and confirm the new toggle renders correctly in both light and dark mode.”
* **Automate a web task** - “Fill out the staging signup form with test data and confirm the verification email screen appears.”
## Related pages
[Section titled “Related pages”](#related-pages)
* [Computer Use](/agents/capabilities/computer-use/) - Control Computer Use and understand how the sandbox works.
* [Testing and recordings](/agents/capabilities/computer-use/testing-and-recordings/) - Record browser sessions as annotated videos for review.
* [Environments](/platform/environments/) - Configure the cloud environment your agents run in.
# Testing with Computer Use and video recordings
Canonical page: [/agents/capabilities/computer-use/testing-and-recordings/](https://docs.warp.dev/agents/capabilities/computer-use/testing-and-recordings/)
> Use Computer Use to test desktop UIs in a sandbox and capture annotated recordings for UI validation, end-to-end QA, and bug reproduction.
Agents don’t just write code; with [Computer Use](/agents/capabilities/computer-use/) enabled they can drive a real desktop GUI in an isolated sandbox, record everything they do, and hand you a trimmed, annotated video as concrete proof of the result.
This page explains when to use Computer Use with recordings, how the recording pipeline works, where your recordings end up, what the finished video contains, and how to handle common recording failures.
Here’s Warp engineer Varoon Kodithala to walk you through it.
[Testing with Computer Use and video recordings walkthrough](https://www.loom.com/embed/fb3190a2e4c442aba76e5145da019b20)
## When to use it
[Section titled “When to use it”](#when-to-use-it)
Computer Use with recordings fits a wide range of tasks. Three common examples:
* **UI change evidence** - After a code change lands, ask an agent to boot the app, exercise the affected surface, and record the session. You get a video showing the change works without running the app yourself.
* **End-to-end QA of existing flows** - Run an agent through a critical workflow (for example, Warp’s onboarding flow or a multi-step form) and capture the full interaction as a single clip for review or a regression archive.
* **Reproducing a bug** - Ask an agent to reproduce the exact steps from a bug report and record them. The resulting video is the definitive reproduction artifact: shareable, time-stamped, and independent of local environment differences.
You don’t need to ask the agent to record explicitly. Prompts like “test this change”, “verify the fix works”, or “produce evidence” naturally lead an agent with Computer Use enabled to start and stop a recording as part of its workflow.
## How it works
[Section titled “How it works”](#how-it-works)
1. **Confirm Computer Use is enabled.** Computer Use is enabled by default for cloud agent runs on Warp’s built-in harness, so no setup is needed unless it was turned off for your run. See the [Computer Use](/agents/capabilities/computer-use/#enabling-computer-use) page for how to control it via the Warp app, the Oz CLI, or the Automation Platform API.
2. **Agent starts recording.** Once Computer Use is active, the agent begins a screen capture inside the sandbox. The recording is gated by your session’s Computer Use approval. If you’ve already approved Computer Use for the run, recording starts automatically without a separate prompt.
3. **Agent exercises the UI.** The agent takes screenshots, clicks, types, scrolls, and drives the interface. Each successful interaction is tracked: when it started, when it finished, what actions it contained, and where the cursor moved.
4. **Agent stops and processes.** When the task is complete (or when the recording’s configured time or size limit is reached), the agent stops capture. Before upload, the recording is post-processed: idle and thinking gaps are cut, leaving only the windows where real interaction happened, and action overlays are burned in so the video is annotated.
5. **Artifact is published.** The processed video is uploaded as a run artifact, ready to view wherever the run’s artifacts appear.
## Where to find recordings
[Section titled “Where to find recordings”](#where-to-find-recordings)
### In Warp
[Section titled “In Warp”](#in-warp)
After the agent finishes its Computer Use session, any video recording appears as a block in the conversation. Clicking the block opens the full conversation view alongside the recording artifact. If the recording was produced by a cloud agent run, you can also access it by opening that run’s transcript as a [cloud-synced conversation](/platform/viewing-cloud-agent-runs/).
### In the web app
[Section titled “In the web app”](#in-the-web-app)
Cloud agent runs are listed on the [Runs page of the Oz web app](/platform/oz-web-app/#runs). Open a run to see its artifacts section, which lists any video recordings produced during that run. You can play the video directly from the run page or download it.
### On pull requests
[Section titled “On pull requests”](#on-pull-requests)
Recordings are also attached to the PR description when the agent opens or updates a pull request — see [Screenshots and videos in pull requests](/agents/capabilities/computer-use/artifacts-in-prs/).
## What’s in a recording
[Section titled “What’s in a recording”](#whats-in-a-recording)
The finished video is not raw screen capture. After the agent stops recording, Warp post-processes the video before uploading it:
* **Smart cut of idle and thinking time** - Gaps where the agent is planning, waiting on a network call, or idle between actions are removed. What remains are only the windows where real interaction happened, played back at normal speed. This makes recordings significantly shorter than the raw capture duration.
* **Action overlays** - Each interaction is burned into the video as overlay pills. Keyboard shortcuts (such as `Ctrl+C`, `Return`, or `Escape`) appear as labels on the frame where they were pressed, so non-visible keys like modifier chords show up clearly. Text typing is labeled “typing…” to avoid leaking sensitive input. Scroll events show a directional label.
* **Click ripples and drag trails** - Pointer events (mouse clicks, drags, and moves) are captured with their coordinates and burned into the video as click ripples and movement trails, so cursor activity is visible even when the cursor itself is small on screen.
* **Sandbox-only capture** - The recording is taken from inside the isolated sandbox environment. It never captures your local desktop, terminal, credentials, or anything outside the sandbox.
Note
Post-processing is best-effort: if the cut or overlay burn-in step fails for any reason, the original capture is uploaded without annotations. You still get a video, just without the smart cut or overlay pills.
## Example recordings
[Section titled “Example recordings”](#example-recordings)
### UI change evidence
[Section titled “UI change evidence”](#ui-change-evidence)
An agent validates a visual change, records the before-and-after behavior, and attaches the recording to the pull request for the reviewer.
Example prompt:
```text
Add a feature to tab groups where each new tab group is assigned a default color that differs from colors already in use. Disable it by default and expose it as a Setting users can toggle on. Once implemented, record a demo that first shows new tab groups getting no color while the setting is off, then enables the setting and shows new tab groups receiving sequential palette colors that cycle back to the start once the palette is exhausted.
```
The finished recording is attached to the pull request, giving a reviewer proof that both states behave correctly without building the change themselves.
[](/assets/agent-platform/tab-group-demo.mp4)
### End-to-end QA of an existing flow
[Section titled “End-to-end QA of an existing flow”](#end-to-end-qa-of-an-existing-flow)
An agent walks through a critical user journey, such as the “New run” creation flow in the Oz web app, capturing the complete interaction.
Example prompt:
```text
Build the Oz web app and walk through the entire "New run" creation flow end to end. Exercise every entrypoint into the flow: the primary New run button, the Command Palette, and any contextual entrypoints. Then step through each stage from opening the New run surface to submitting a run.
```
This gives you a reproducible, time-stamped clip of the flow that can be archived, diffed across releases, or shared with the team as a baseline.
[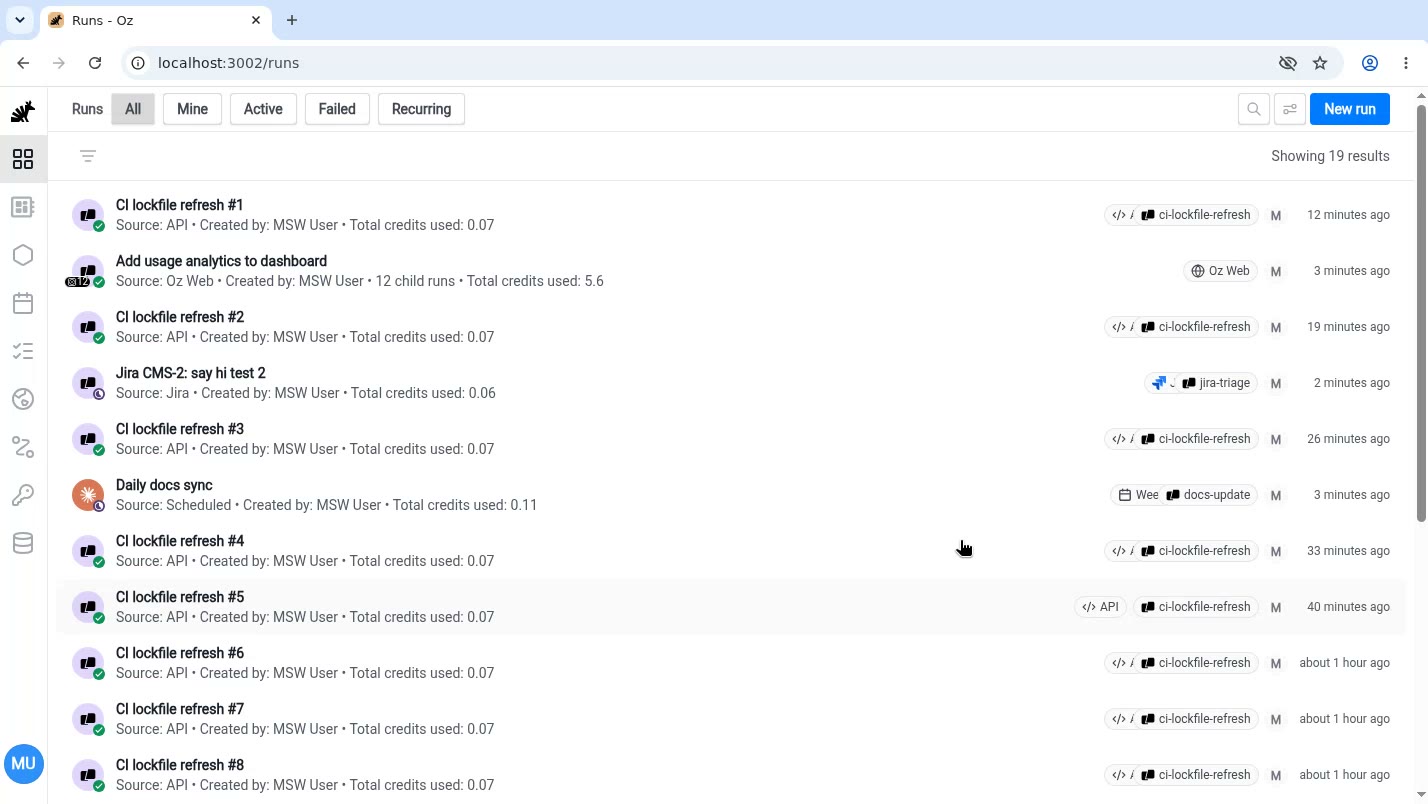](/assets/agent-platform/new-run-demo.mp4)
### Reproducing a bug
[Section titled “Reproducing a bug”](#reproducing-a-bug)
An agent follows the exact steps from a bug report and records them, producing a shareable reproduction artifact. This is a core part of Warp’s open-source workflow: when a user files a bug against [warpdotdev/warp](https://github.com/warpdotdev/warp), we spin off a cloud agent to reproduce and verify it before reviewing any contribution that claims to fix it.
Example prompt:
```text
Reproduce warpdotdev/warp#13480 ("ctrl+c does not set focus on prompt"): build warp-oss, select a command block, then press Ctrl+C. The block should be deselected and focus should return to the prompt. Record the session so it can be attached to the issue as reproduction proof.
```
In [warpdotdev/warp#13480](https://github.com/warpdotdev/warp/issues/13480), pressing Ctrl+C while a block is selected fails to return focus to the prompt: the block stays selected and its focus annotations linger. The agent reproduces the bug by driving a sandboxed Warp build and pressing Ctrl+C on a selected block on camera. Bug reproductions are one of the strongest use cases because the video is unambiguous: the recording either shows the bug or it doesn’t.
[](/assets/agent-platform/ctrl-c-bug.mp4)
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### Recording was cut short
[Section titled “Recording was cut short”](#recording-was-cut-short)
Each recording has a maximum duration of **10 minutes** and a maximum file size of **1 GiB**. When either limit is hit, the capture is stopped and finalized automatically.
If the conversation is cancelled while a recording is active, the recording is discarded rather than uploaded.
### Retry guidance
[Section titled “Retry guidance”](#retry-guidance)
Most recording failures are transient. If a recording fails or produces an unexpected result:
1. Check the agent’s output for the specific error message.
2. Retry the run; recording substrate errors typically clear on the next attempt.
3. If the failure repeats consistently across multiple runs, file an issue on the [open-source Warp client repository](https://github.com/warpdotdev/warp/issues) with the error message.
## Related
[Section titled “Related”](#related)
* [Computer Use](/agents/capabilities/computer-use/) - enable Computer Use, understand security considerations, and configure models for Computer Use sessions.
* [Screenshots and videos in pull requests](/agents/capabilities/computer-use/artifacts-in-prs/) - how captured artifacts are attached to PR descriptions and the team setting that controls it.
* [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/) - open and inspect cloud agent run transcripts in Warp or the browser.
* [Security considerations](/agents/capabilities/computer-use/#security-considerations) - understand the sandboxed environment and data isolation model.
* [Privacy](/support-and-community/privacy-and-security/privacy/) - Warp’s data handling policies, including how run artifacts are stored.
# Full Terminal Use
Canonical page: [/agents/capabilities/full-terminal-use/](https://docs.warp.dev/agents/capabilities/full-terminal-use/)
> Full Terminal Use means agents can interact with active terminal apps to monitor live output and run commands.
Full Terminal Use lets the Warp Agent operate directly inside interactive terminal applications like database shells, debuggers, text editors, and long-running servers. The agent can see the live terminal buffer, write commands, respond to prompts, and hand control back to you at any time.
The agent can see the live terminal buffer (terminal state), write to the PTY to run commands, respond to prompts, and continue working inside the running process while you stay in control.

## Overview
[Section titled “Overview”](#overview)
With Full Terminal Use, the Warp Agent can attach to interactive tools like `psql`, `vim`, `python`, `gdb`, `top`, or your dev server, read the terminal output as it changes, and interact with the application as if you were typing.
You can either ask the agent to start an interactive program, or you can start it yourself and then tag the agent in once the tool is already running. In both cases, the agent sees the same terminal buffer (and PTY session) you do and can act on it.
## How Full Terminal Use works
[Section titled “How Full Terminal Use works”](#how-full-terminal-use-works)
#### Start an interactive command
[Section titled “Start an interactive command”](#start-an-interactive-command)
You can either ask the agent to run an interactive command, or start one manually and then tag the agent in:
* **Ask the agent to start an interactive tool**
* Example:
* “Open a Postgres shell and help me inspect the orders table.”
* “Start the dev server and debug this 500 error.”
* **Or start the command yourself, then tag the agent in**
* Example:
* If you’ve already launched an interactive tool (for example `psql` or `npm run dev`), you can bring the agent into the running session using the **Use Agent** button in the terminal footer or via `Cmd+I`.
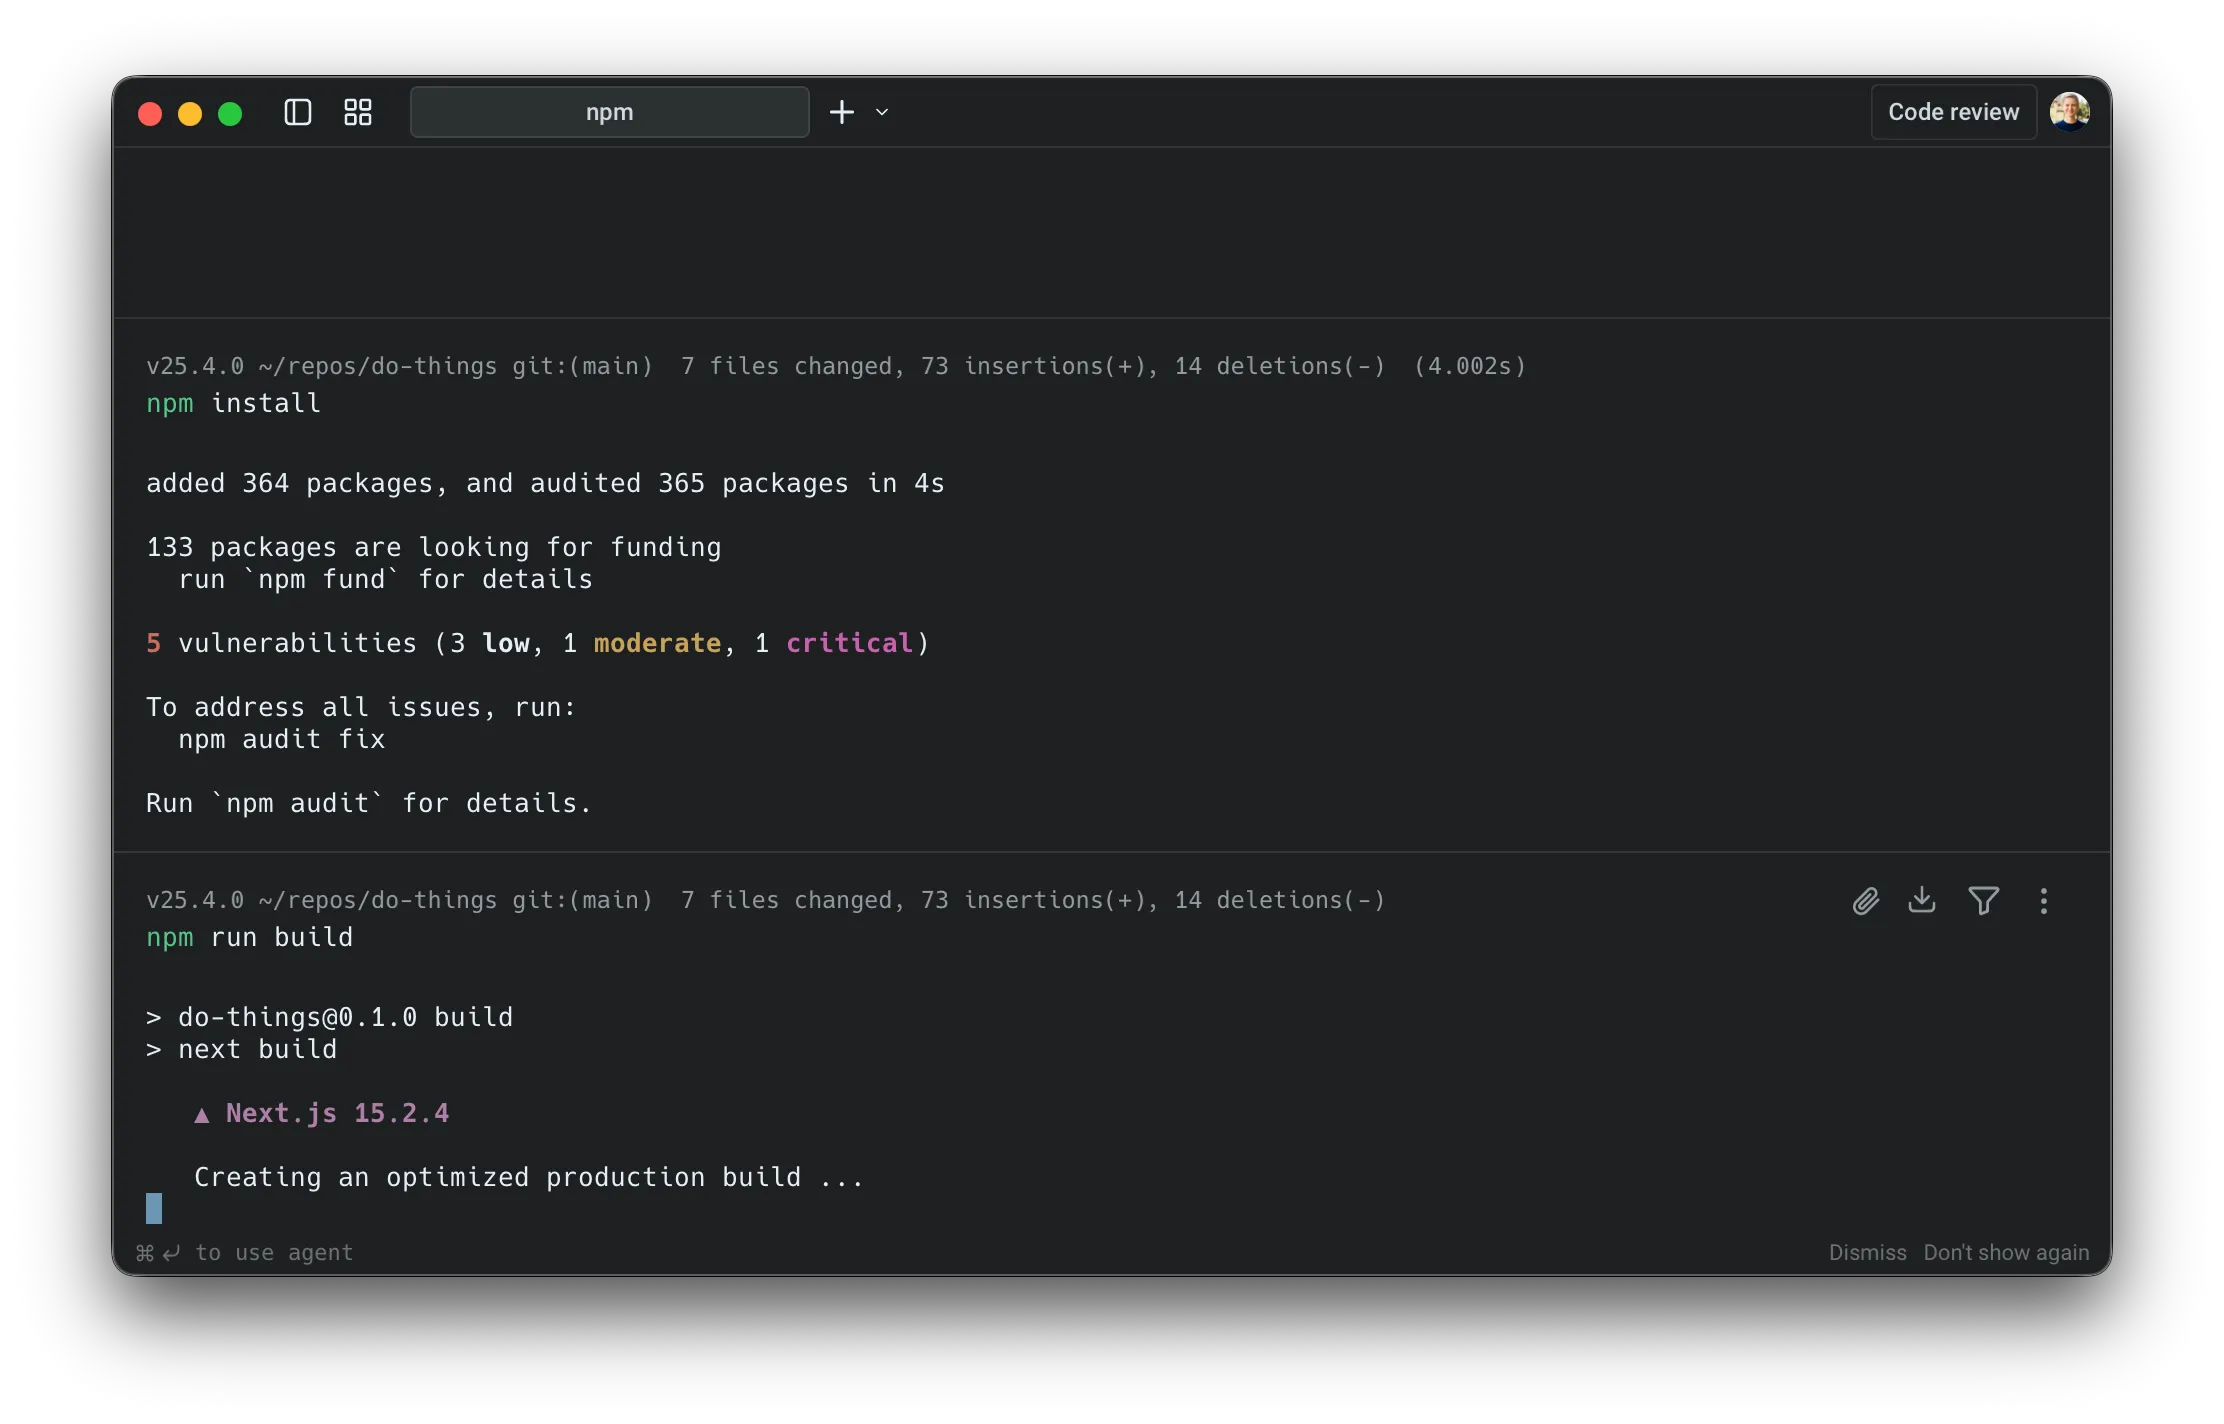
Option to tag the agent into a running command.
* Once the agent is tagged in, you can follow up with natural-language requests such as:
“Watch this process and help debug the error on the /session endpoint.”
* Warp then attaches the agent to the active PTY so it can see the current terminal buffer and propose actions inside the session.
[Tagging in the agent.](https://www.loom.com/embed/bcedc521071a4b6a9bbcf74b5156f903)
Running a build command.
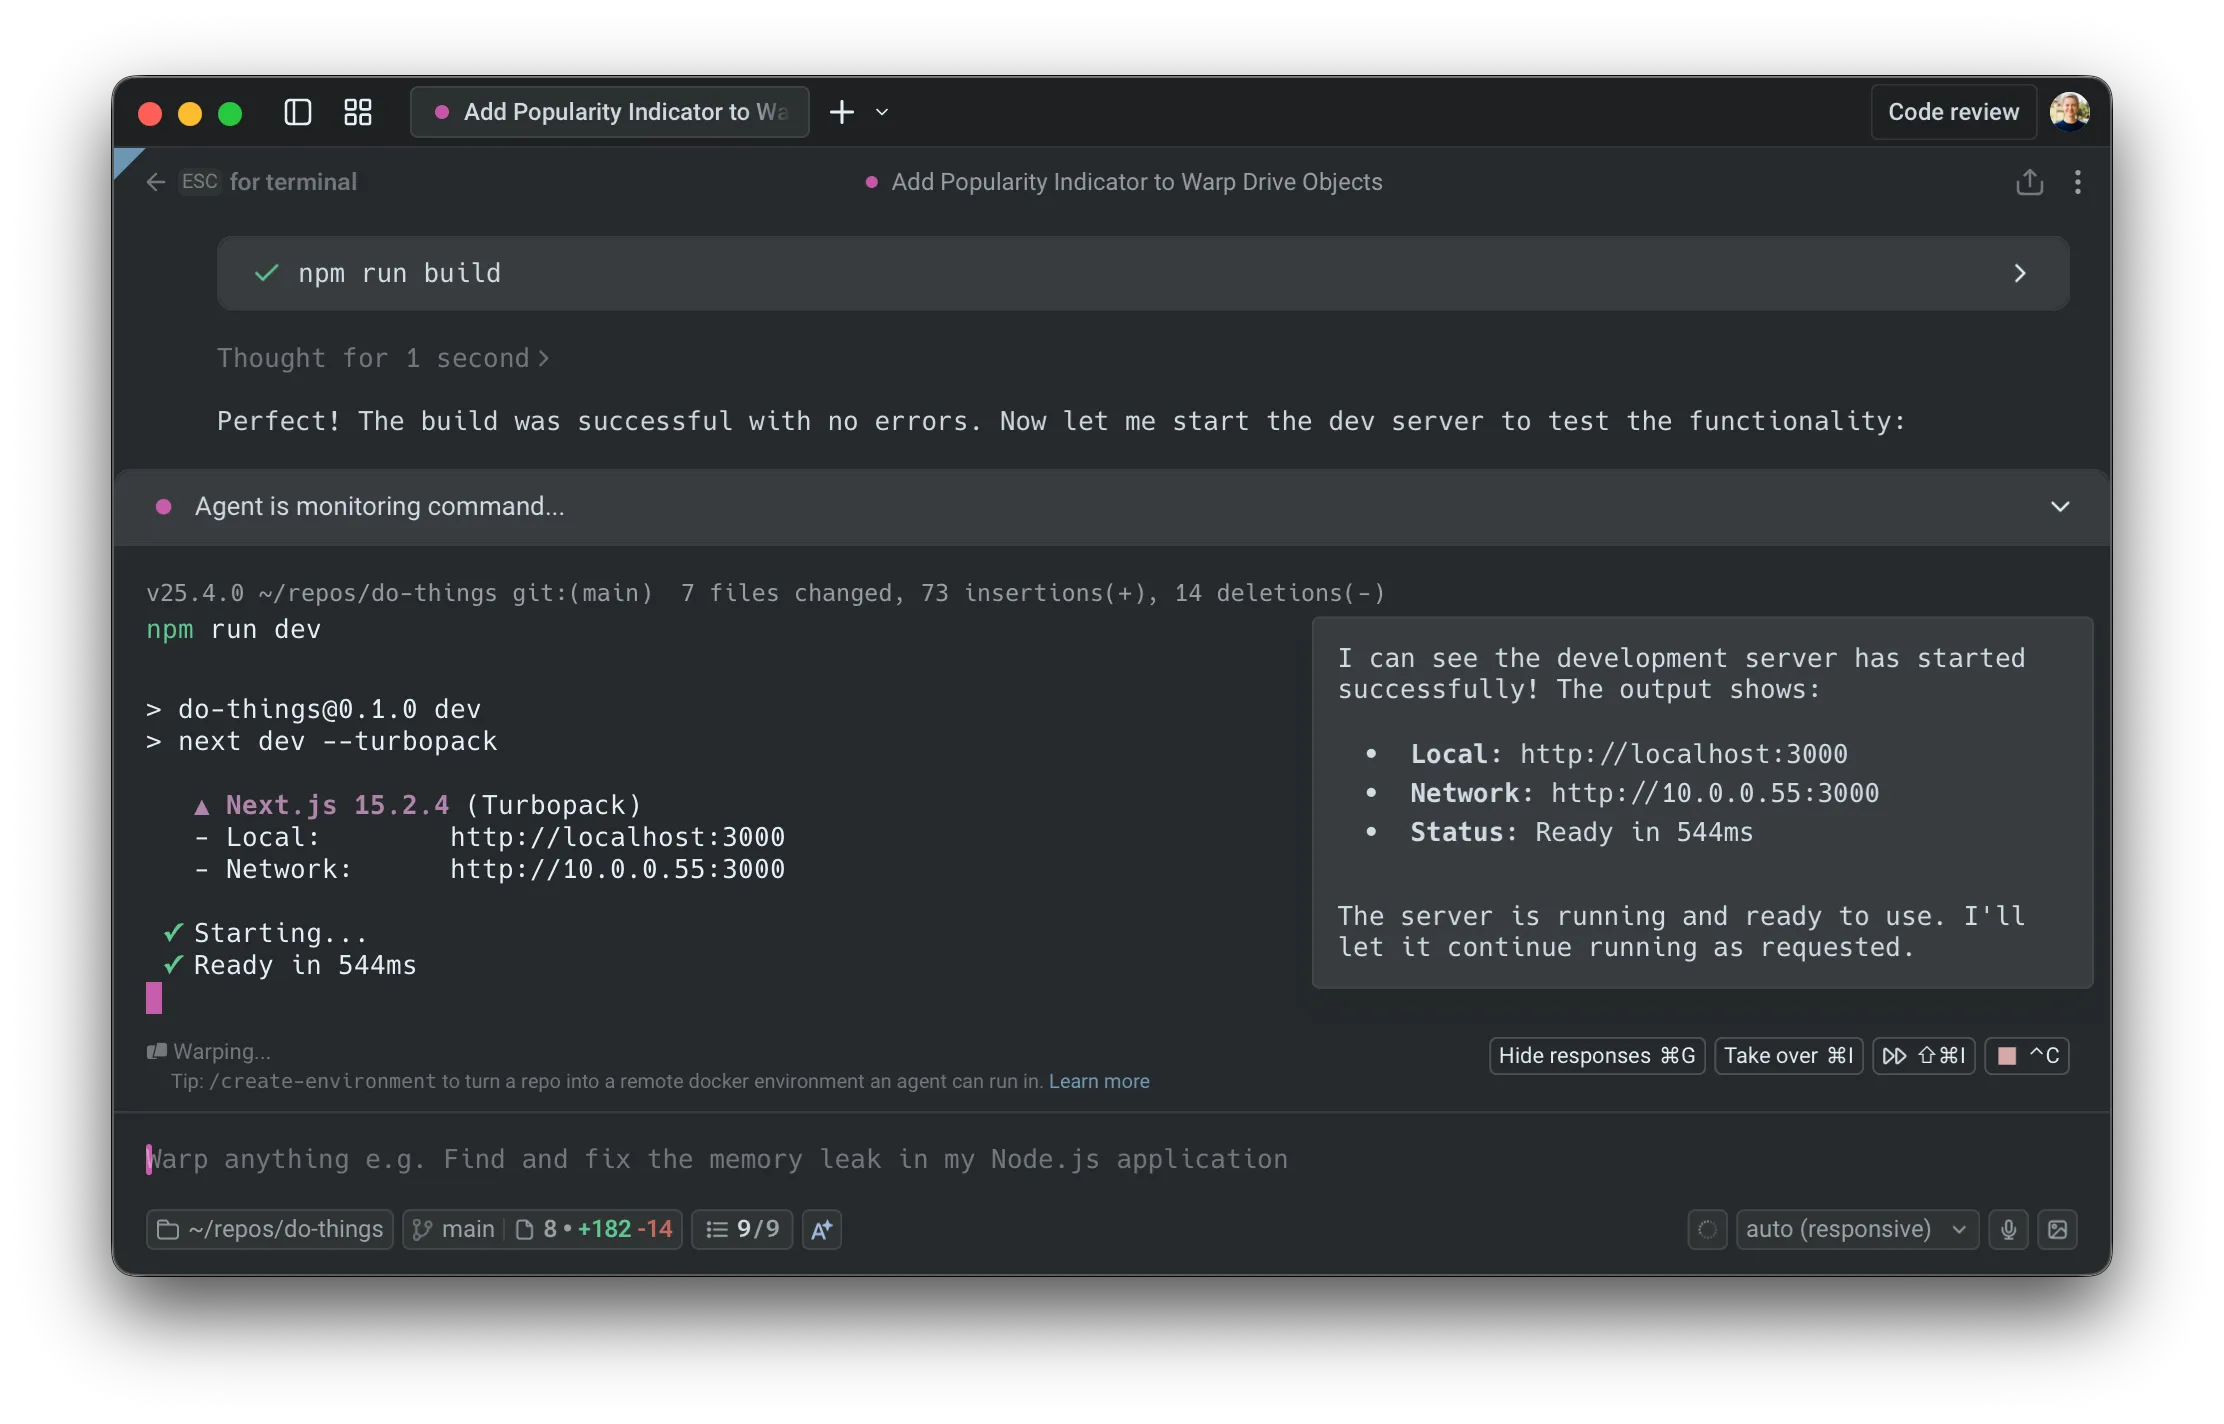
Tagging in the Agent to monitor the dev server.
Warp attaches the agent to the running command so it can see and control the terminal buffer.
#### Agents propose actions inside the session
[Section titled “Agents propose actions inside the session”](#agents-propose-actions-inside-the-session)
Once attached, you can continue using natural language and the agent turns your requests into concrete terminal actions. For example, in a Postgres shell:
* You: “Show me all the tables and describe the orders table.”
* Agent: proposes running commands like: `\dt` —> `\d+ orders`
In the UI, you’ll see a request to:
* Run a specific command
* Optionally enable auto-approval for similar commands in this session
#### Switching control between user and the agent
[Section titled “Switching control between user and the agent”](#switching-control-between-user-and-the-agent)
You can swap control at any time.
**Take over**
* Use the Takeover control to stop the agent from typing or performing any actions.
* The shell stays open, and you can type directly into the same session.
Option to take over from agent in the footer.
**Hand back control**
* When you’re ready for the agent to continue, click the control again.
* The agent resumes where you left off, with full access to the current terminal state.
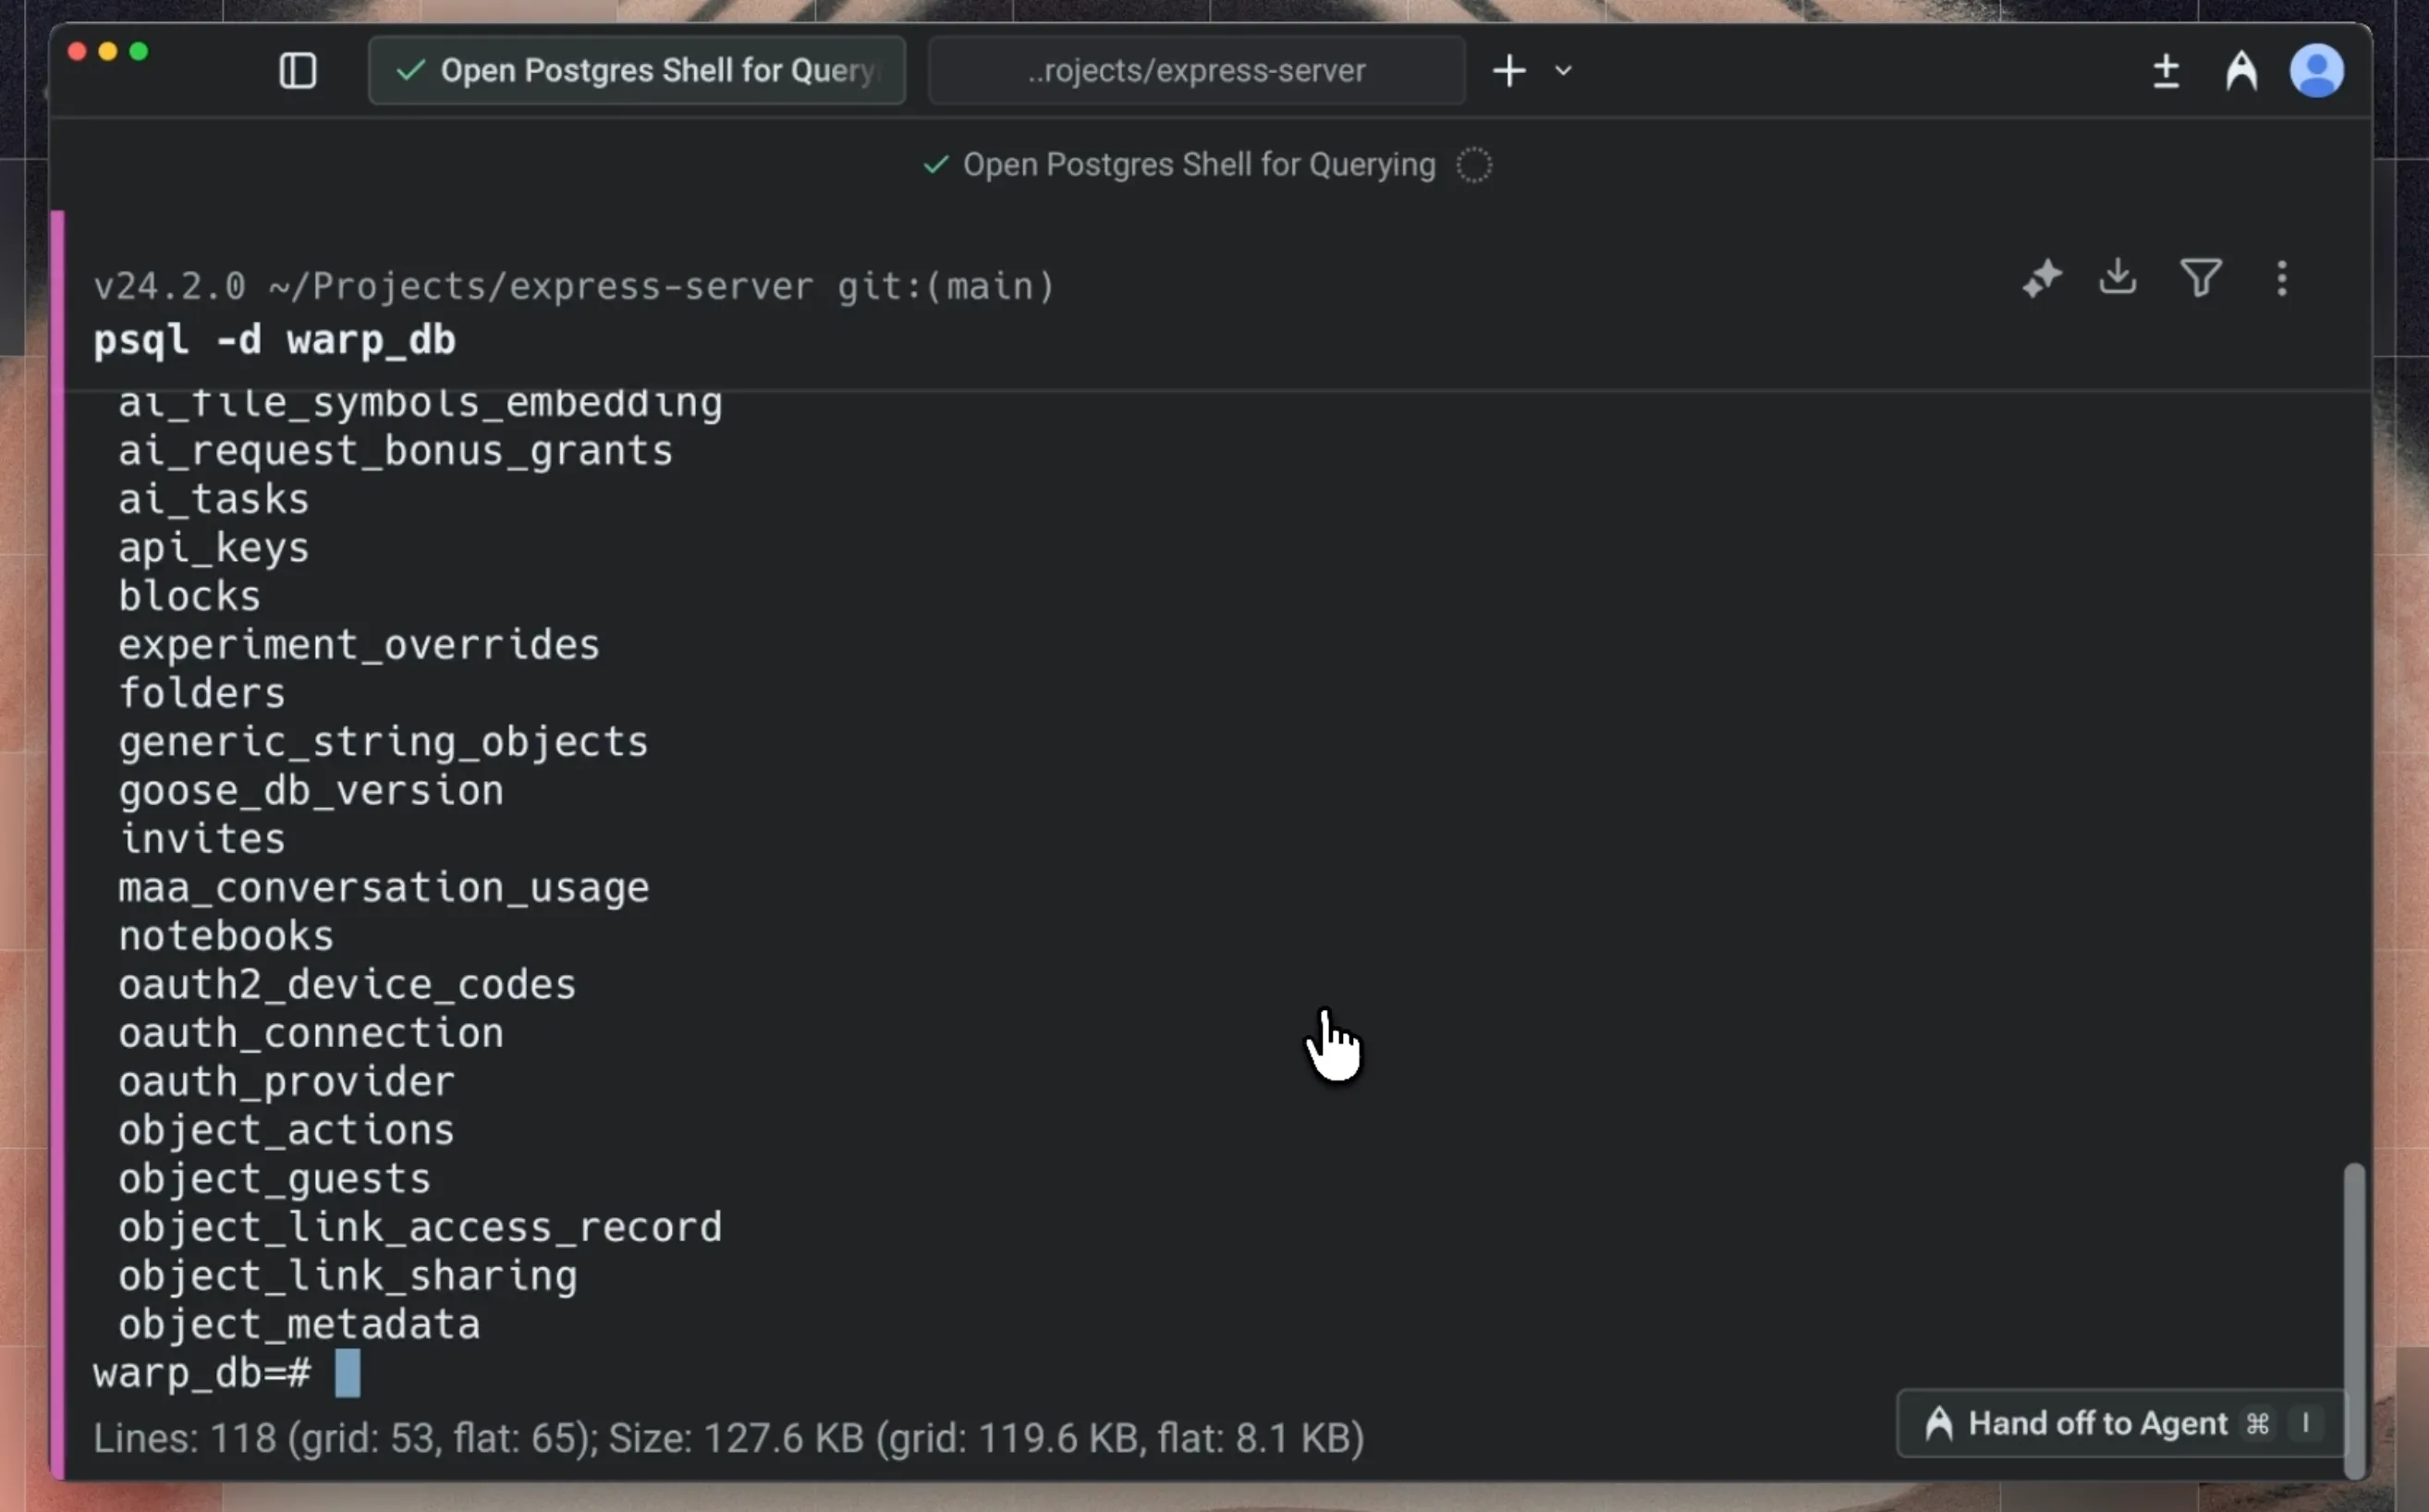
Option to hand-off to the agent in the conversation footer.
This makes it easy to:
* Let the agent do mechanical work (paging output, trying variants of a command)
* Step in for delicate or security-sensitive actions
* Then let the agent continue once the critical step is done
#### Prompts queue while the agent drives a command it started
[Section titled “Prompts queue while the agent drives a command it started”](#prompts-queue-while-the-agent-drives-a-command-it-started)
When the agent starts a long-running command itself, prompts you submit while it drives that command are queued by default instead of steering the agent mid-command. They appear in the queued prompts panel with a *(queued until the command finishes)* suffix, and Warp sends them to the agent automatically when the command finishes. This applies only to commands the agent started; if you start a command and tag the agent in, your prompts keep steering the agent immediately.
To steer the agent immediately during an agent-started command, toggle auto-queue off for the remainder of the command, or change the **Default long-running command submission mode** setting in the Warp app under **Settings** > **Agents** > **Warp Agent** > **Input**. For the full behavior, including the setting’s options and when it applies, see [Queueing during long-running commands](/agents/local-agents/interacting-with-agents/prompt-queueing/#queueing-during-long-running-commands).
#### Long-running commands in terminal vs agent view
[Section titled “Long-running commands in terminal vs agent view”](#long-running-commands-in-terminal-vs-agent-view)
The behavior differs based on where you start the long-running command:
* From terminal view
1. Run an interactive command (e.g., `python`, `psql`)
2. Press `⌘+Enter` (macOS) or `Ctrl+Shift+Enter` (Windows/Linux), or use `⌘+I` (macOS) / `Ctrl+I` (Windows/Linux), to tag in the agent
3. The input switches to Agent Mode with full controls
4. When you exit, an agent conversation block appears in your terminal block list
5. Click the block to reopen the full conversation with your LRC interaction context
* From agent view
1. The agent runs an interactive command as part of your conversation
2. Use `⌘+Enter` (macOS) or `Ctrl+Shift+Enter` (Windows/Linux) to tag in if the agent isn’t already interacting
3. The UI stays the same since you’re already in agent view
4. When you exit, the interaction remains part of your conversation. No separate block is created in the terminal block list
5. Commands run in agent view are automatically included as context
Note
You can also use `⌘+I` (macOS) or `Ctrl+I` (Windows/Linux) to toggle agent control in either view.
#### Showing and hiding agent responses
[Section titled “Showing and hiding agent responses”](#showing-and-hiding-agent-responses)
Warp gives you control over how much agent output appears in Full Terminal Use.
**Toggle visibility**
Use the `Hide responses` or `Show responses` button or `⌘+G` in the interactive command footer to switch between showing all agent output or hiding it from the terminal view.
Note that this only affects the agent’s messages and proposals; your terminal state and command output remain unchanged.
**Behavior when hidden**
* When agent responses are hidden, your own agent requests automatically dismiss after **4 seconds** to keep the terminal clear.
* You can also manually dismiss any user query at any time by hovering over it and clicking the X.
[Hiding and showing agent responses in Full Terminal Use demo](https://www.loom.com/embed/c639fb4ab33343a39037b2083c66858a)
***
### Configuring agent permissions and autonomy
[Section titled “Configuring agent permissions and autonomy”](#configuring-agent-permissions-and-autonomy)
You control how much autonomy the agent has when interacting with the terminal.
#### Session-level approvals
[Section titled “Session-level approvals”](#session-level-approvals)
Each time the agent wants to take an action inside an interactive shell, you’ll see the agent’s reasoning, a brief explanation, and the proposed command. From there you can:
* Allow the command once (for example by approving it or pressing `Enter`).
* Turn on auto-approval for similar commands in this session (for example with `⌘+Shift+I`).
* Refine the request with `Ctrl+C`, which clears the proposed action and lets you follow up with a different query.
* Take over manually with `⌘+I`, which stops the agent from issuing any further PTY writes until you hand control back.
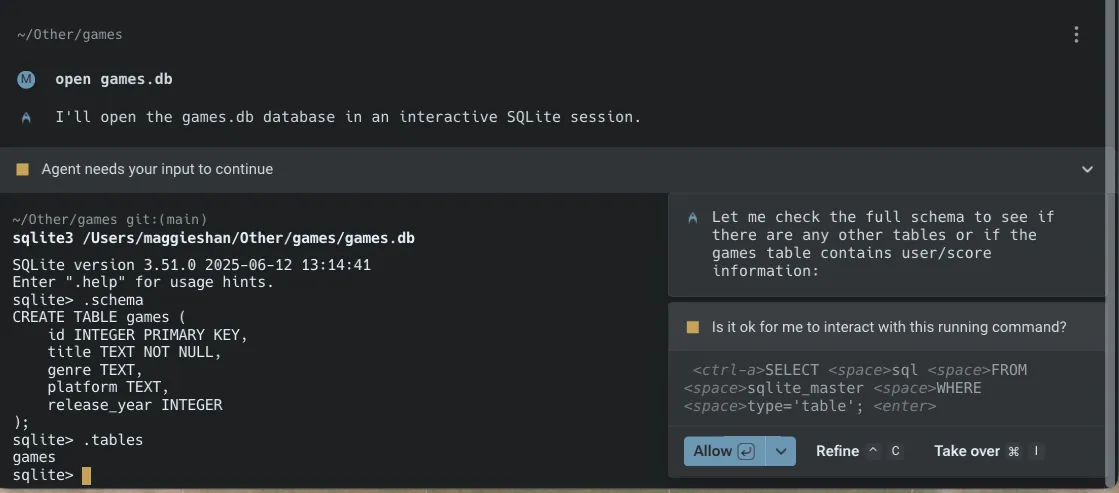
Allow, Refine, or Take over an agent response.
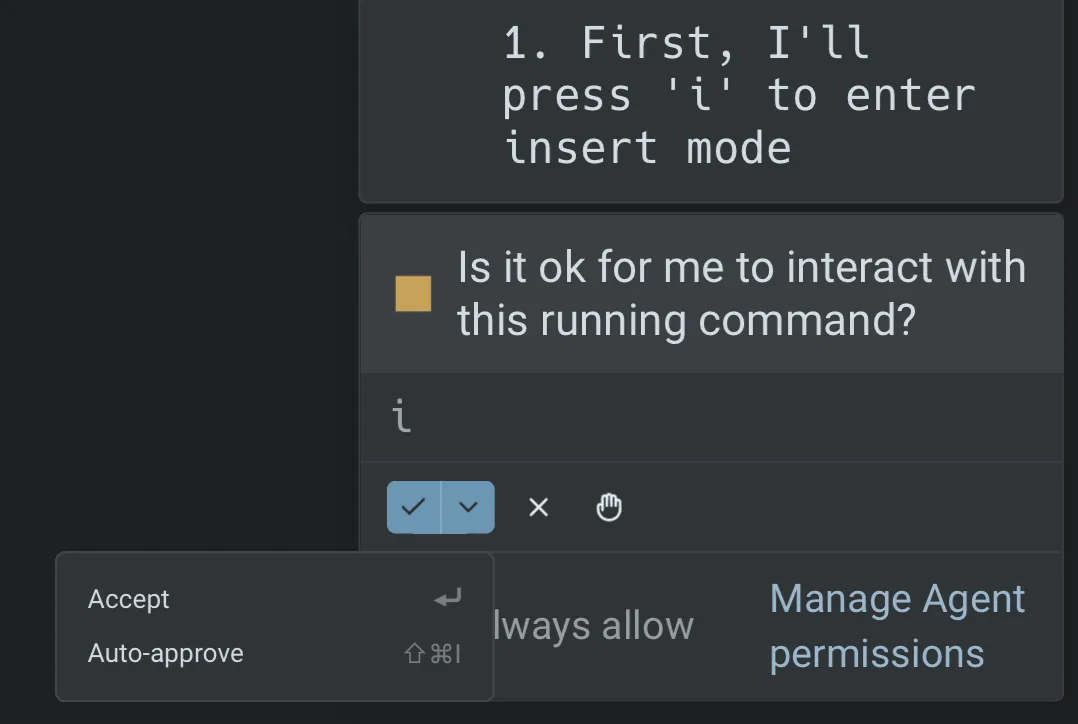
This lets you tighten or loosen control for the current task:
* For exploratory work, use **Always allow** to reduce friction.
* For production systems or sensitive operations, use **Allow once** and review each step.
#### Global permission settings
[Section titled “Global permission settings”](#global-permission-settings)
You can configure global defaults from your [Agent Profiles & Permissions](/agents/capabilities/agent-profiles-permissions/) settings:
* **Ask on first write**: The first write to a shell process requires approval. After that, all subsequent writes for that specific process/command will be approved.
* **Always ask**: Every write to the shell process from the agent requires your explicit approval.
* **Always allow**: The agent can write to the shell process without prompting you each time.
These settings apply to every session that uses Full Terminal Use. You can still override them on a per-session basis when prompted. For example, you can enable **auto-approval** for similar commands in the current session using the fast-forward control, or switch to a **different AI profile** with its own permission settings for that conversation.
Note
**Note**: All [Secret Redaction](/support-and-community/privacy-and-security/secret-redaction/) features still apply during Full Terminal Use, so sensitive values in your environment or output remain protected.
### Credits usage
[Section titled “Credits usage”](#credits-usage)
All AI interactions from Full Terminal Use consume [credits](/support-and-community/plans-and-billing/credits/), including understanding your natural language requests.
Credits are consumed in a similar way as other Warp actions that use the same model and a similar context size.
**Interactive sessions can consume more credits if:**
* The agent runs many commands in an interactive shell on your behalf.
* There is a significant amount of terminal output to read and summarize.
**To manage credit usage:**
* Use tighter scopes:
* “Describe just the orders table.” instead of “Explain the entire database.”
* Pause autonomy for high-volume tasks with copious terminal output:
* Take over manual control when running large batches or long logs.
* Use stricter permissions:
* Set global permissions to “Ask on first write” or “Always ask”, then approve only what you need.
Note
To learn more about what goes into a credit and how to get more value from AI usage in Warp, see: [*Getting the most out of credits in Warp*](https://www.warp.dev/blog/warp-ai-requests).
## Example workflows
[Section titled “Example workflows”](#example-workflows)
Here’s a demo from one of our engineers, Maggie, that walks through a couple of Full Terminal Use examples.
[Full Terminal Use example workflows demo](https://www.loom.com/embed/d47ee09153df417983df65a339a9d6f2)
Below are some common interactive tools where Full Terminal Use is particularly useful: database shells (Postgres, MySQL, SQLite), debuggers such as gdb, language-specific REPLs like python or node, text editors and file explorers, and long-running dev servers or monitoring tools such as top and htop.
| Tool | Example tasks | Agents can… |
| --------------------------------------------------------------------------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Database shells (REPLs)** e.g. `psql`, `mysql`, `sqlite`, etc. | * “List all tables and describe the users and orders tables.”
* “Create a new table to store archived user sessions.”
* “Show me all rows in orders from the last 30 days, grouped by status.”
* “Generate and run a query that finds the top 10 customers by revenue.” | - Navigate `\d`, `\dt`, `DESCRIBE`, etc.
- Write and execute SQL queries
- Summarize results in plain language |
| **Text editors** e.g. `vim`, `nano`, etc. | * “Open this file in vim and add a Markdown header and a boilerplate section.”
* “Insert a docstring above this function explaining what it does.”
* “Generate a CSS utility class block and insert it in this file.” | - Navigate within the editor using keystrokes
- Insert, edit, and delete text
- Save and quit when done |
| **Python REPLs** e.g. `python`, `ipython` | * “Start a Python REPL and define a function that calculates a moving average.”
* “Write a unit test for this function and run it.”
* “Plot x from 0 to 10 and y = sin(x).” | - Import modules
- Define functions and classes
- Run tests and small scripts
- Print or summarize results back to you |
| **Debuggers** e.g. `gdb`, `lldb`, language-specific debuggers | * “Start gdb for this binary and set a breakpoint on `handle_request`.”
* “Run until the breakpoint, then show the stack and local variables.”
* “Inspect this pointer and tell me if it looks invalid.” | - Issue debugger commands (break, run, next, continue, bt, etc.)
- Walk through execution step by step
- Summarize relevant state so you don’t have to remember every command |
| **Long-running servers and services** e.g. `npm run dev`, `uvicorn`, Rails servers, etc | * “Run the dev server and debug the internal server error on /session.”
* “Send a sample request to this endpoint and explain the failure.”
* “Kill the server once you identify the error and propose a code diff.” | - Watch server logs in real time
- Notice new errors as they appear
- Stop the server when appropriate
- Propose code changes (for example, via a diff) based on what it observes |
| **Version control workflows** e.g. `git rebase -i`, complex git commands | * “Interactively rebase master onto `feature-branch` to squash these commits into one.”
* “Resolve these merge conflicts and ensure tests pass.” | - Navigate interactive rebase prompts
- Edit commit messages
- Apply conflict resolutions you approve |
| **Cloud provider CLIs** e.g. `gcloud`, `aws`, `az`, etc. | * “Use gcloud to create a new Kubernetes cluster with these settings.”
* “Provision a new RDS instance for staging and show me the connection details.” | - Walk through multi-step CLI workflows
- Handle prompts and confirmations
- Summarize the resulting resources |
# Model Context Protocol (MCP)
Canonical page: [/agents/capabilities/mcp/](https://docs.warp.dev/agents/capabilities/mcp/)
> Configure MCP servers in the Warp app to extend local agents with custom tools and data sources through a standardized interface.
MCP servers extend Warp’s [local agents](/agents/local-agents/interacting-with-agents/) in a modular, flexible way by exposing custom tools or data sources through a standardized interface — essentially acting as plugins for Warp. Warp supports a variety of connection protocols, including Streamable HTTP and SSE, along with custom headers and environment variables.
MCP is an open source protocol. Check out the official [MCP documentation](https://modelcontextprotocol.io/introduction) for more detailed information on how this protocol is engineered.
Note
This page covers MCP servers for local agents in the Warp app. For help choosing between local, cloud, and shared MCP workflows, see [Connect developer tools to agents with MCP workflows](/guides/external-tools/using-mcp-servers-with-warp/). If you’re using cloud agents, see [MCP Servers for cloud agents](/platform/mcp/).
### How to access MCP Server settings
[Section titled “How to access MCP Server settings”](#how-to-access-mcp-server-settings)
You can navigate to the MCP servers page in any of the following ways:
* From the [Settings Page](warp://settings/mcp): **Settings** > **Agents** > **MCP servers**
* From [Warp Drive](/knowledge-and-collaboration/warp-drive/): under **Personal** > **MCP Servers**
* From the [Command Palette](/terminal/command-palette/): search for `Open MCP Servers`
* From the Warp app: **Settings** > **Agents** > **Warp Agent** > **Manage MCP servers**
This will show a list of all configured MCP servers, including which are currently running. If you close Warp with an MCP server running, it will run again on next start of Warp. MCP servers that are stopped will remain so on next launch of Warp.
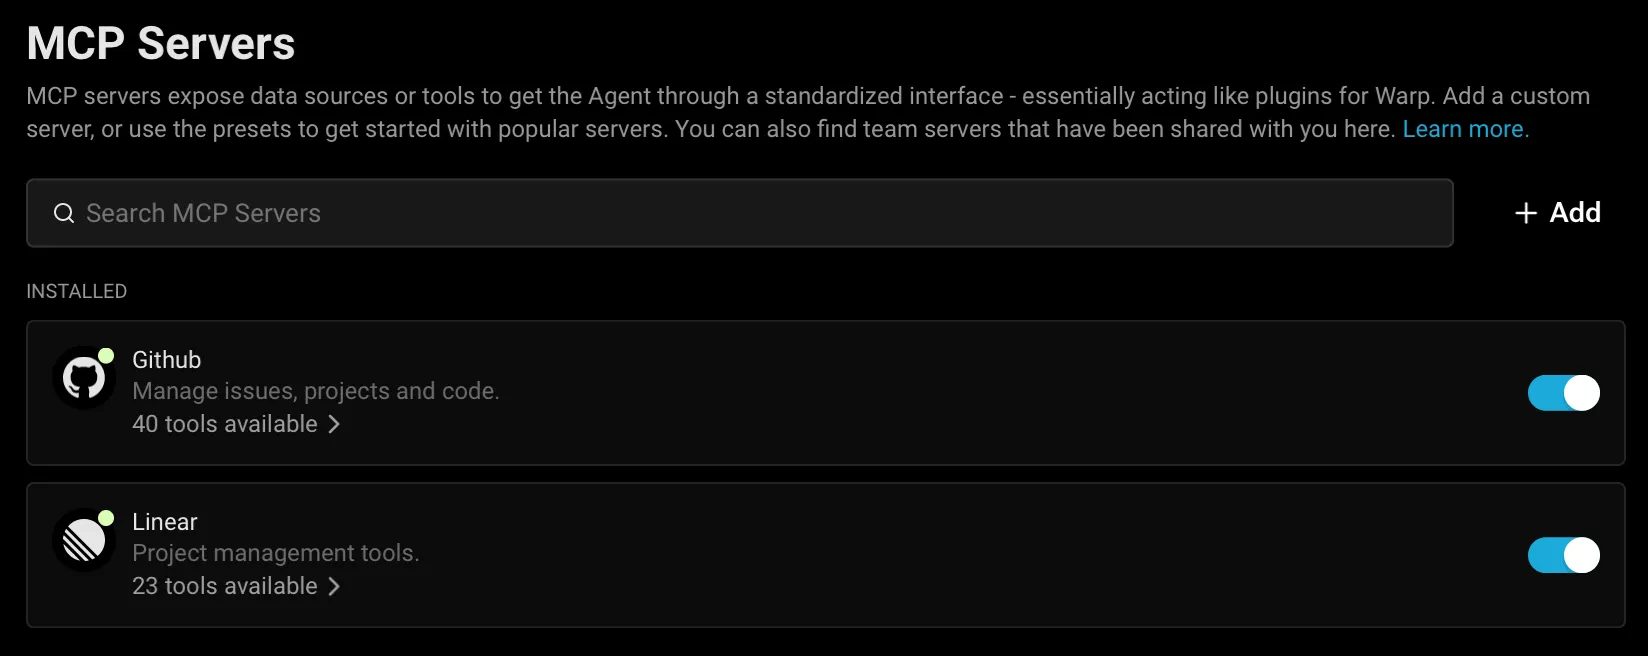
MCP servers page.
### Adding an MCP Server
[Section titled “Adding an MCP Server”](#adding-an-mcp-server)
To add a new MCP server, you can click the **+ Add** button. Configurations from most MCP clients can be directly copied and pasted.
MCP server types you can add:
* CLI Server (Command)
Provide a startup command. Warp will launch this command when starting up and shut it down on exit.
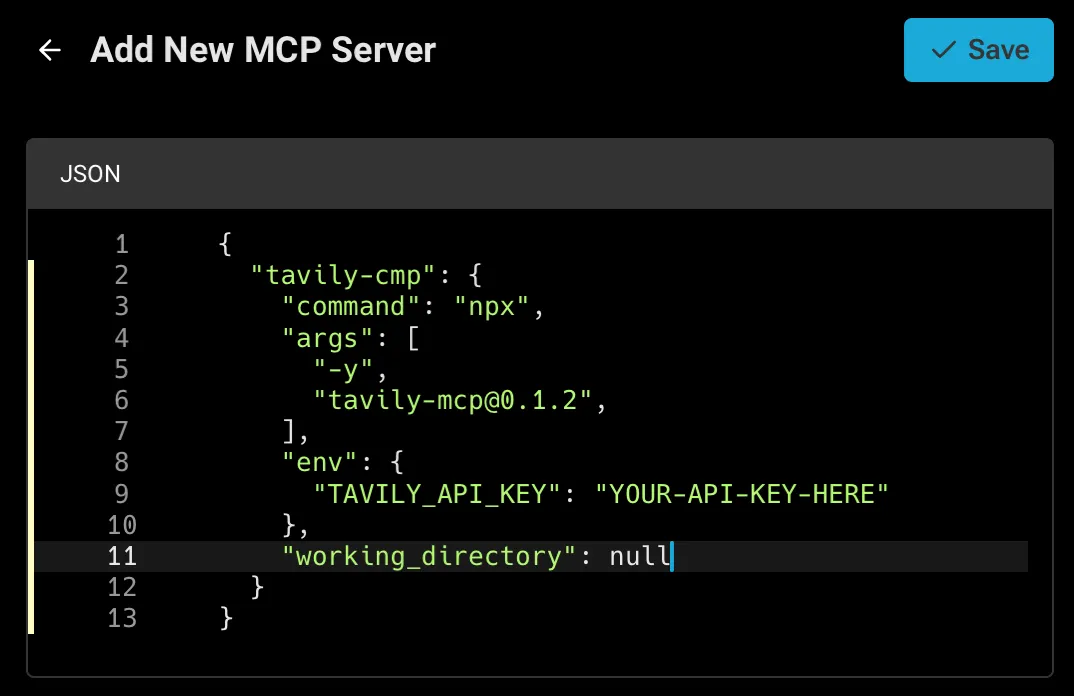
Adding a CLI MCP Server (Command).
Note
Always set `working_directory` explicitly when your MCP server command or args include relative paths. This ensures consistent and predictable behavior across machines and sessions.
**CLI Server (Command) MCP Configuration Properties**
| Property | Type | Required | Description |
| ------------------- | --------- | -------- | ----------------------------------------------------------------------------------- |
| `command` | string | Yes | The executable to launch (e.g., `npx`). |
| `args` | string\[] | Yes | Array of command-line arguments passed to `command` (e.g., module name, paths). |
| `env` | object | No | Key-value object of environment variables (e.g., API Tokens). |
| `working_directory` | string | No | Working directory path where the command is run, used for resolving relative paths. |
* Streamable HTTP or SSE Server (URL)
Provide a URL where Warp can reach an already-running MCP server that supports Server-Sent Events.
Adding an SSE MCP Server (URL).
**Streamable HTTP or SSE Server (URL) MCP Configuration Properties**
| Property | Type | Required | Description |
| --------- | ------ | -------- | ----------------------------------------------------------------- |
| `url` | string | Yes | The HTTP endpoint URL to connect to via Server-Sent Events (SSE). |
| `headers` | object | No | Key-value object of header variables (e.g., Authorization). |
### Adding multiple MCP servers
[Section titled “Adding multiple MCP servers”](#adding-multiple-mcp-servers)
Warp supports configuring **multiple MCP servers** using a JSON snippet. Each entry under `mcpServers` is keyed by a unique name (`filesystem`, `github`, `notes`, etc.). All servers defined in the example are added automatically — no manual setup required.
To add multiple MCP servers, you can click the **+ Add** button then paste in a JSON snippet like the example below:
```json
{
"mcpServers": {
"filesystem": {
"command": "npx",
"args": ["-y", "@modelcontextprotocol/server-filesystem", "/path/to/allowed/files"]
},
"notes": {
"command": "npx",
"args": ["-y", "@modelcontextprotocol/server-notes", "--notes-dir", "/Users/you/Documents/notes"]
},
"externalDocs": {
"url": "http://localhost:4000/mcp/stream",
"headers": {
"my-header": "my-header-value"
}
}
}
}
```
### File-based MCP servers
[Section titled “File-based MCP servers”](#file-based-mcp-servers)
Compared to manually adding a server in the Warp settings, file-based servers are defined in config files that Warp detects and can spawn automatically. They offer a few additional benefits:
* **Configurable directly with an agent** - Use the [bundled skill](#using-agent-add-mcp) `/agent-add-mcp` so the Warp Agent can add or update an MCP server without leaving the conversation.
* **Inherited across providers and repos** - Warp reads `.warp/.mcp.json` files and also picks up config from third-party agent providers (Claude Code, Codex, and others). The same server definition follows you across tools and repos.
#### Supported providers
[Section titled “Supported providers”](#supported-providers)
Warp reads MCP server definitions from the following providers:
| Provider | Global config | Project-scoped config | Auto-spawn |
| ------------ | ---------------------- | ------------------------------------ | --------------- |
| Warp | `~/.warp/.mcp.json` | `.warp/.mcp.json` at project root | On by default |
| Claude Code | `~/.claude.json` | `.mcp.json` at project root | Requires toggle |
| Codex | `~/.codex/config.toml` | `.codex/config.toml` at project root | Requires toggle |
| Other agents | `~/.agents/.mcp.json` | `.agents/.mcp.json` at project root | Requires toggle |
Global Warp servers auto-spawn by default. Global servers from all other providers auto-spawn only when **Auto-spawn servers from third-party agents** is enabled. Project-scoped servers from any provider require explicit approval.
For provider-specific setup, see the [Claude Code MCP docs](https://code.claude.com/docs/en/mcp#user-scope) and [Codex MCP docs](https://developers.openai.com/codex/mcp/#connect-codex-to-an-mcp-server).
#### Auto-spawn behavior
[Section titled “Auto-spawn behavior”](#auto-spawn-behavior)
Global Warp servers auto-spawn by default. Third-party agent servers require you to enable auto-spawn first.
To auto-spawn global servers from third-party agents:
1. In the Warp app, go to **Settings** > **Agents** > **MCP servers**.
2. Toggle **Auto-spawn servers from third-party agents** on.
File-based MCP server settings.
Project-scoped servers from any provider must be toggled on individually from the MCP servers page. These are session-scoped — after restarting Warp, toggle them on again if you still trust the repo.
#### Using `/agent-add-mcp`
[Section titled “Using /agent-add-mcp”](#using-agent-add-mcp)
The built-in `/agent-add-mcp` skill lets the Warp Agent create or update file-based MCP server definitions. Choose whether to save globally or in the current project — the skill writes the server definition to the matching file:
* **Global:** `~/.warp/.mcp.json`
* **Project-scoped:** `{repo_root}/.warp/.mcp.json`
[](/assets/agent-platform/file-based-mcp-demo.mp4)
The demo shows how to use `/agent-add-mcp` to add an MCP server, choose where Warp saves the file-based configuration, and review the generated `.warp/.mcp.json` file before using the server.
#### Security mitigations
[Section titled “Security mitigations”](#security-mitigations)
MCP config files can start local commands and send data to external tools. Warp adds approval gates around file-based MCP servers to reduce the risk of untrusted config changes:
* **Config edits require approval** - Warp prevents edits to MCP config files unless you explicitly approve the change. This keeps an agent or automation from silently adding a server that can run commands or access data.
* **Project-scoped servers never auto-spawn** - Warp detects project-scoped MCP config files in cloned repos, but requires you to start each server manually. This prevents a cloned repo from automatically starting an MCP server that runs arbitrary local commands.
Note
File-based servers that require OAuth show an authentication modal on their first spawn. Credentials are saved for future spawns, the same as manually configured MCP servers.
### Managing MCP servers
[Section titled “Managing MCP servers”](#managing-mcp-servers)
After MCP servers are registered in Warp, you can **Start** or **Stop** them from the MCP servers page. Each running server will have a list of available tools and resources.
You can rename and edit a server’s name, as well as delete the server. If you are a part of a Team, you can also share an MCP server with your teammates.
### Sharing MCP servers
[Section titled “Sharing MCP servers”](#sharing-mcp-servers)
MCP servers can be shared with your teammates by clicking the share icon. When sharing, sensitive values in the `env` configuration will be automatically scrubbed and replaced with variables.
Sharing an MCP Server.
Your teammates can find shared MCP servers under the `Shared` section of their MCP settings. When your teammates install your server configuration, they will be prompted to enter any scrubbed `env` values.
Warp also provides out-of-the-box MCP servers that can be installed by anyone. These can be found under the `Shared` section of your MCP settings.
### Authentication in MCP servers
[Section titled “Authentication in MCP servers”](#authentication-in-mcp-servers)
Most MCP servers require authentication to connect to external services. Warp supports the following methods:
* **Environment variables**: pass an API key or access token via the server’s environment variables.
* **OAuth login (one-click installation)**: simplifies configuration by handling authentication through your browser. Warp stores credentials securely on your device and reuses them for future sessions. Re-authentication is required when opening Warp on a new machine.
* Starting a server without existing credentials automatically opens a browser-based authentication flow.
* Credentials can be revoked at any time from the MCP Servers pane in Warp.
* **Custom Headers**: pass an Authentication Bearer token via the headers variable.
### Debugging MCP
[Section titled “Debugging MCP”](#debugging-mcp)
If you’re having trouble with an MCP server, you can check the logs for any errors or messages to help you diagnose the problem by clicking the **View Logs** button on a server from the MCP servers page.
Caution
If you choose to share your MCP server logs with anybody, **make sure to remove any sensitive information before sharing**, as they may contain API keys.
Many SSE based MCP servers will state that your URL should be treated like a password, and can be used with no additional authentication.
Note
Tip: We’ve noticed that some models often work better with MCP servers than others. If you’re having trouble calling or using an MCP server, try using a different model.
#### Debugging MCP authentication issues
[Section titled “Debugging MCP authentication issues”](#debugging-mcp-authentication-issues)
In some cases you may need to reset the auth token for some MCP servers. To do this, delete the local MCP auth files by running the following: `rm -rf ~/.mcp-auth`
Caution
Note this will delete all your MCP auth tokens stored locally so you will need to login and re-authenticate.
If the above doesn’t help and you need to reset or change authentication, you may need to switch to a CLI-based MCP server configuration and provide the token via environment variables. See the Sentry tab under [MCP server configuration examples](/agents/capabilities/mcp/#mcp-server-configuration-examples).
### Where MCP logs are stored
[Section titled “Where MCP logs are stored”](#where-mcp-logs-are-stored)
Warp saves the MCP logs locally on your computer. You can open the files directly and inspect the full contents in the following location:
* macOS
```bash
cd "$HOME/Library/Group Containers/2BBY89MBSN.dev.warp/Library/Application Support/dev.warp.Warp-Stable/mcp"
```
* Windows
```powershell
Set-Location $env:LOCALAPPDATA\warp\Warp\data\logs\mcp
```
* Linux
```bash
cd "${XDG_STATE_HOME:-$HOME/.local/state}/warp-terminal/mcp"
```
## MCP server configuration examples
[Section titled “MCP server configuration examples”](#mcp-server-configuration-examples)
Below are examples for popular Model Context Protocol (MCP) servers.
* **CLI Server (Command)** — local `npx` or `docker` command based MCP servers.
* **Streamable HTTP or SSE Server (URL)** — remote or locally hosted MCP endpoints.
### **Engineering & Ops**
[Section titled “Engineering & Ops”](#engineering--ops)
* GitHub
[GitHub MCP Docs](https://github.com/github/github-mcp-server)
**GitHub CLI Server (Command)**
```json
{
"GitHub": {
"command": "docker",
"args": ["run","-i","--rm","-e","GITHUB_PERSONAL_ACCESS_TOKEN","ghcr.io/github/github-mcp-server"],
"env": {
"GITHUB_PERSONAL_ACCESS_TOKEN": ""
}
}
}
```
**GitHub SSE Server (URL)**
```json
{
"GitHub": {
"url": "https://api.githubcopilot.com/mcp/"
}
}
```
* Sentry
[Sentry MCP Docs](https://docs.sentry.io/product/sentry-mcp/)
**Sentry CLI Server (Command)**
```json
{
"Sentry": {
"command": "npx",
"args": ["-y","mcp-remote@latest","https://mcp.sentry.dev/mcp"]
}
}
```
**Sentry Streamable HTTP Server (URL)**
```json
{
"Sentry": {
"url": "https://mcp.sentry.dev/mcp"
}
}
```
* Grafana
[Grafana MCP Docs](https://github.com/grafana/mcp-grafana)
**Grafana CLI Server (Command)**
```json
{
"Grafana": {
"command": "docker",
"args": ["run","--rm","-i","-e","GRAFANA_URL","-e","GRAFANA_API_KEY","mcp/grafana","-t","stdio","-debug"],
"env": {
"GRAFANA_URL": "http://localhost:3000",
"GRAFANA_API_KEY": ""
}
}
}
```
**Grafana SSE Server (URL)**
```json
{
"Grafana": {
"url": "https://your-mcp-host.com/api/mcp/grafana/sse"
}
}
```
* Linear
[Linear MCP Docs](https://linear.app/docs/mcp)
**Linear CLI Server (Command)**
```json
{
"Linear": {
"command": "npx",
"args": ["-y","mcp-remote","https://mcp.linear.app/mcp"]
}
}
```
**Linear Streamable HTTP Server (URL)**
```json
{
"Linear": {
"url": "https://mcp.linear.app/mcp"
}
}
```
* Chroma
**Chroma Package Search CLI Server (Command)**
1. Visit Chroma’s [Package Search](http://trychroma.com/package-search) page.
2. Click “Get API Key” to create or log into your Chroma account and issue an API key for Package Search.
3. After issuing your API key, click the “Other” tab and copy your API key.
4. Add the following to your Warp MCP config. Make sure to click “Start” on the server after adding.
More info in [Chroma’s Package Search MCP Docs](https://docs.trychroma.com/cloud/package-search/mcp)
```json
{
"package-search": {
"command": "npx",
"args": ["mcp-remote", "https://mcp.trychroma.com/package-search/v1", "--header", "x-chroma-token: ${X_CHROMA_TOKEN}"],
"env": {
"X_CHROMA_TOKEN": ""
}
}
}
```
### **Design & Collaboration**
[Section titled “Design & Collaboration”](#design--collaboration)
* Figma
**Figma Remote MCP Server (Recommended)**
The official Figma remote MCP server supports OAuth for simple, one-click setup.
1. In Warp, go to **Warp Drive** > **MCP Servers** > **+ Add** and paste the configuration below.
2. Warp will open a browser window to authenticate with Figma.
3. After approving access, credentials are stored securely on your device.
Note
Note: A Figma account with [Dev Mode](https://www.figma.com/dev-mode/) enabled is required.
```json
{
"Figma": {
"url": "https://mcp.figma.com/mcp"
}
}
```
**Figma Local MCP Server**
1. Enable the Official Figma MCP Server. [Figma MCP Docs](https://help.figma.com/hc/en-us/articles/32132100833559-Guide-to-the-Figma-MCP-server)
2. Open the [Figma desktop app](https://www.figma.com/downloads/) and make sure you’ve [updated to the latest version](https://help.figma.com/hc/en-us/articles/5601429983767-Guide-to-the-Figma-desktop-app#h_01HE5QD60DG6FEEDTZVJYM82QW).
3. Create or open a Figma Design file.
4. In the upper-left corner, open the Figma menu.
5. Under **Preferences**, select **Enable local MCP Server**.
6. Enter the following configuration into **Warp** > **Warp Drive** > **MCP Servers** > **+ Add**.
```json
{
"Figma (Local)": {
"url": "http://127.0.0.1:3845/mcp"
}
}
```
* Slack
[Slack MCP Docs](https://github.com/korotovsky/slack-mcp-server/)
**Slack CLI Server (Command)**
Enter the following configuration into **Warp** > **Warp Drive** > **MCP Servers** > **+ Add**.
```json
{
"Slack": {
"command": "npx",
"args": ["-y", "@modelcontextprotocol/server-slack"],
"env": {
"SLACK_BOT_TOKEN": "xoxb-",
"SLACK_APP_TOKEN": "xapp-",
"SLACK_TEAM_ID": "T",
"SLACK_CHANNEL_IDS": ", ",
"MCP_MODE": "stdio"
}
}
}
```
**Slack SSE Server (URL)**
Enter the following configuration into **Warp** > **Warp Drive** > **MCP Servers** > **+ Add**.
```json
{
"Slack": {
"url": "https://your-mcp-host.com/api/mcp/slack/sse"
}
}
```
* Atlassian
[Atlassian MCP Docs](https://support.atlassian.com/rovo/docs/setting-up-ides/)
**Atlassian CLI Server (Command)**
Enter the following configuration into **Warp** > **Warp Drive** > **MCP Servers** > **+ Add**.
```json
{
"Atlassian": {
"command": "npx",
"args": ["-y", "mcp-remote", "https://mcp.atlassian.com/v1/sse"]
}
}
```
* Notion
[Notion MCP Docs](https://developers.notion.com/docs/mcp)
**Notion CLI Server (Command)**
Enter the following configuration into **Warp** > **Warp Drive** > **MCP Servers** > **+ Add**.
```json
{
"Notion": {
"command": "npx",
"args": ["-y", "mcp-remote", "https://mcp.notion.com/mcp"]
}
}
```
**Notion SSE Server (URL)**
Enter the following configuration into **Warp** > **Warp Drive** > **MCP Servers** > **+ Add**.
```json
{
"Notion": {
"url": "https://mcp.notion.com/sse"
}
}
```
### MCP server demos
[Section titled “MCP server demos”](#mcp-server-demos)
[Warp Guides](/guides/) hosts a collection of demos and walkthroughs showing how MCP servers can extend your workflows. Each example highlights practical use cases you can try today:
* [**GitHub**](/guides/external-tools/github-mcp-summarizing-open-prs-and-creating-gh-issues/) — access repositories, issues, and pull requests through MCP.
* [**Sentry**](/guides/external-tools/sentry-mcp-fix-sentry-error-in-empower-website/) — surface error monitoring and alerts as agent-usable data.
* [**Linear**](/guides/external-tools/linear-mcp-retrieve-issue-data/) — integrate project management tasks and tickets.
* [**Puppeteer**](/guides/external-tools/puppeteer-mcp-scraping-amazon-web-reviews/) — run automated browser workflows via MCP.
* [**Context7**](/guides/external-tools/context7-mcp-update-astro-project-with-best-practices/) — experiment with external data integrations.
# Agent planning and execution
Canonical page: [/agents/capabilities/planning/](https://docs.warp.dev/agents/capabilities/planning/)
> Turn requests into structured, editable plans that agents execute step-by-step with version control.
Warp has native planning functionality that helps you break down complex engineering tasks into structured, executable steps. Planning is tightly integrated with Warp’s coding agent and provides a persistent plan editor, version history, selective execution, and deep links into your workspace.

***
### Creating a plan
[Section titled “Creating a plan”](#creating-a-plan)
You can generate a plan using the `/plan` [slash command](/agents/capabilities/slash-commands/) or by asking the agent in natural language.
Creating a plan with the /plan command.
The agent then creates a structured plan inside Warp’s native rich text editor, which is designed for long, multi-step workflows. The editor includes clean formatting, inline code blocks, and clickable file paths so you can open referenced files immediately in Warp (see below) or in your external editor.
### Reviewing and editing
[Section titled “Reviewing and editing”](#reviewing-and-editing)
Once a plan is generated, you can review it, reorganize steps, or refine details. You can edit the document manually or ask the agent to revise sections for you.
Plan editor in Warp.
Any update made by the agent **creates a new version**. Version history lets you compare past iterations and restore an older version if you want to revert your approach, preserving a clear decision trail as the plan evolves.
Access previous versions of your plan.
### Executing a plan
[Section titled “Executing a plan”](#executing-a-plan)
When you’re ready to start implementing, prompt the agent to run the plan. You can ask it to execute the full set of steps or only a specific section, such as “Implement phase 1 of the plan.”
Referencing a plan using @.
The agent applies changes incrementally and updates files as it proceeds. This makes it easy to validate early steps before moving forward, adjust the plan mid-run, or try alternative paths without committing to the full workflow.
If you revise the plan while the agent is running, you can notify it directly; the agent will adjust its execution based on your updates.
Prompt to update the agent’s plan during execution.
### Monitoring progress
[Section titled “Monitoring progress”](#monitoring-progress)
While the agent is running, you can reopen the plan at any time by selecting **View plan** in the input. You can also follow each change in real time through the [Code Review](/code/code-review/) panel and add comments or guidance using [Interactive Code Review](/agents/local-agents/interactive-code-review/).
Monitoring progress with the task list and plan view.
This gives you clear oversight, helps confirm expected behavior, and lets you intervene quickly if something needs correction.
### Saving and sharing
[Section titled “Saving and sharing”](#saving-and-sharing)
Warp automatically saves all plans in the *Plans* folder in [Warp Drive](/knowledge-and-collaboration/warp-drive/). You’ll see a confirmation when your plan is synced.
Plans are automatically synced to Warp Drive.
You can export any plan as Markdown, check it into your repository, or share a link—useful for GitHub PRs, design reviews, or async collaboration.
Different ways to share a plan.
Because plans persist in Warp Drive, you can return to them later, reuse them for new work, or treat them as documentation for ongoing projects. This is also naturally passed to the agent as context.
Plans are accessible directly from the Warp Drive side panel.
You can configure whether your plans will be automatically added and synced to Warp Drive in your [Agent Profiles & Permissions](/agents/capabilities/agent-profiles-permissions/) under **Settings** > **Agents** > **Profiles**.
### Using plans across conversations
[Section titled “Using plans across conversations”](#using-plans-across-conversations)
Plans are reusable across tasks and sessions. You can reference them in future prompts, continue where you left off, or build follow-up plans that rely on earlier work.
The **@plans** command helps you quickly search for and reopen previously saved plans, making planning a consistent part of your development workflow rather than a one-off step. See [attaching context with @ references](/agents/local-agents/agent-context/using-to-add-context/) for more ways to add files, folders, diffs, and saved objects to an agent conversation.
***
## Next steps
[Section titled “Next steps”](#next-steps)
As the agent executes your plan, you’ll review code changes and may want to scale work to the cloud.
* **[Interactive Code Review](/agents/local-agents/interactive-code-review/)** - Leave inline comments on agent-generated diffs and have the agent revise in one pass.
* **[Cloud Agents quickstart](/platform/quickstart/)** - Run agents in the cloud for longer tasks, background automation, or parallel work across repos.
# Rules for agents
Canonical page: [/agents/capabilities/rules/](https://docs.warp.dev/agents/capabilities/rules/)
> Create reusable Global or Project Rules to ensure agents follow your coding standards, project conventions, and personal preferences.
Warp’s **Rules** feature lets you create reusable guidelines that inform how agents respond to your prompts. Rules help tailor responses to match your coding standards, project conventions, and personal preferences, making agent interactions smarter and more consistent.
Warp supports two types of rules: **Global Rules** and **Project Rules**.

## Global Rules
[Section titled “Global Rules”](#global-rules)
Global Rules apply across all projects and contexts. They’re ideal for:
* Coding standards and best practices
* Workspace-wide guidelines
* Tool configurations or preferences you want applied everywhere
Warp may also suggest Global Rules based on your usage patterns to make future interactions smarter and more consistent.
## Project Rules
[Section titled “Project Rules”](#project-rules)
Project Rules live in your codebase and apply automatically when working within that project. They’re stored in an `AGENTS.md` file (or `WARP.md` for backwards compatibility) and can be:
* Placed in the root of your repository
* Added in subdirectories for more targeted guidance
Note
Warp uses `AGENTS.md` as the default project rules file. Existing `WARP.md` files are still fully supported—if you have `WARP.md`, it will continue to work as expected. You can also rename `WARP.md` to `AGENTS.md` at any time without additional changes.
If both `WARP.md` and `AGENTS.md` exist in the same directory, `WARP.md` takes priority.
Caution
The filename must be in **all caps** for Warp to recognize it (e.g., `AGENTS.md`, not `agents.md` or `Agents.md`). We recommend creating `AGENTS.md` for new projects.
**When you’re in a directory:**
* Warp automatically applies the `AGENTS.md` (or `WARP.md`) in the root and in the current directory.
* If you edit files in another subdirectory, Warp makes a best-effort attempt to include that subdirectory’s rules file as well.
Example project structure:
* project/
* api/
* AGENTS.md API-specific rules
* ui/
* AGENTS.md UI-specific rules
* AGENTS.md Project-wide rules
How Warp applies these Project Rules:
* **If the current directory is `ui/`**
* Automatically applied: `project/AGENTS.md` and `project/ui/AGENTS.md`
* Best effort: `project/api/AGENTS.md` if editing files there
* **If the current directory is `api/`**
* Automatically applied: `project/AGENTS.md` and `project/api/AGENTS.md`
* Best effort: `project/ui/AGENTS.md` if editing files there
### Rules precedence
[Section titled “Rules precedence”](#rules-precedence)
When multiple rules apply, Warp follows this order of precedence:
1. Rules in the current subdirectory’s project rules file
2. Rules in the root directory’s project rules file
3. Global Rules
This ensures the most specific, project-relevant rules take priority over broader ones.
***
## How to access Rules
[Section titled “How to access Rules”](#how-to-access-rules)
* From [Warp Drive](/knowledge-and-collaboration/warp-drive/): **Personal** > **Rules**
* From the [Command Palette](/terminal/command-palette/): search for “Open AI Rules”
* From the Settings panel: **Settings** > **Agents** > **Knowledge** > **Manage Rules**
* Here, you can manage both Global as well as Project Rules.
* From the Warp menu bar: **AI** > **Open Rules**
* From the Slash Commands menu: `/open-project-rules` to open Project Rules directly in Warp’s code editor
Project Rules UI open in a Rules pane.
## How to create, edit, or delete Rules
[Section titled “How to create, edit, or delete Rules”](#how-to-create-edit-or-delete-rules)
#### Global Rules
[Section titled “Global Rules”](#global-rules-1)
* **From Warp Drive Rules pane:** **Personal** > **Rules** > **Global**\
Add, edit, or delete any number of rules. Each rule can include:
* Name (optional)
* Description (what the rule does and when to apply it)
* **From the Slash Commands menu:** Use `/add-rule` to create a new Global Rule (automatically opens the Warp Drive Rules pane).
[Rules Demo (legacy) with just Global Rules. Project rules can also be found there.](https://www.loom.com/embed/3a49462c01e149cf9c040130cebe1184)
#### Project Rules
[Section titled “Project Rules”](#project-rules-1)
* **When in a directory, set up Project Rules with a slash command:** Use `/init` to:
* Begin indexing your codebase or display indexing status
* Generate an `AGENTS.md` file with initial context, or
* Link an existing Rules file to `AGENTS.md`
* Warp currently supports linking the following external Rules files: `CLAUDE.md`, `.cursorrules`, `AGENT.md`, `GEMINI.md`, `.clinerules`, `.windsurfrules`, `.github/copilot-instructions.md`
To view all Project Rules and open them in Warp, access it via the Warp Drive Rules pane: **Personal** > **Rules** > **Project-based**
### Rules as Agent context
[Section titled “Rules as Agent context”](#rules-as-agent-context)
When relevant, Agents automatically pull in applicable rules to guide their responses. Rules used in an interaction will appear in the conversation under **References** or marked as derived from a specific rule.
An agent response showing which rules were applied.
Rules listed as references in an agent conversation.
### Rules privacy
[Section titled “Rules privacy”](#rules-privacy)
See our [Privacy page](/support-and-community/privacy-and-security/privacy/) for more information on how we handle data with Rules.
# Skills for agents
Canonical page: [/agents/capabilities/skills/](https://docs.warp.dev/agents/capabilities/skills/)
> Create reusable instruction sets that teach agents specific tasks and share expertise across your team.
Skills allow you to create reusable, shareable instructions that agents can invoke when performing tasks. Instead of repeating detailed prompts, you can encapsulate common workflows, coding patterns, or domain expertise into skill files that agents automatically discover and use.
## Key features
[Section titled “Key features”](#key-features)
* **Reusable instructions** - Define a task once and let Agents use it whenever relevant
* **Project and global scopes** - Create skills specific to a project or available across all projects
* **Automatic discovery** - Agents are aware of all available skills and invoke them when appropriate
* **Simple markdown format** - Skills are just markdown files with a small amount of metadata
* **Supporting files** - Include scripts, templates, or other resources alongside your skill instructions
* **Slash command invocation** - Invoke any skill directly with `/{skill-name}`
* **Parameterized skills** - Use argument placeholders to create dynamic, reusable skill templates
## How Skills work
[Section titled “How Skills work”](#how-skills-work)
When you start an [Agent conversation](/agents/local-agents/interacting-with-agents/), the Agent receives a list of all available skills with their names and descriptions.
When the Agent determines that a skill would help accomplish your task, it loads the skill’s full instructions and follows them to complete the task.
Caution
Skill discovery is based on your current working directory. For Git repositories, Warp includes all skills from your current directory up through the repository root. If you’re working in project A, you won’t have access to skills from project B.
Note
Skills complement Rules, which provide persistent guidelines that Agents always follow. Use Rules for constraints and preferences; use Skills for specific task workflows.
### Skill name conflicts
[Section titled “Skill name conflicts”](#skill-name-conflicts)
If you have skills with the same name in multiple directories, Warp handles the conflict differently depending on how the skill is invoked:
* **Natural language** - The Agent receives a list of all in-scope skills including their names, descriptions, and file paths. The Agent can see all available options and chooses the appropriate skill based on its path.
* **Slash commands** - When multiple skills share the same name, Warp displays all matching skills in the menu. You select which one to use based on the description.
* **Background resolution** - When Warp resolves skill names automatically (without direct user selection), it prioritizes home directory (global) skills first, then skills from higher directories (closer to the repository root).
### Example interactions
[Section titled “Example interactions”](#example-interactions)
You can invoke skills in two ways:
**Using natural language** - Describe what you want to accomplish:
* “Use the deploy skill to push to staging”
* “Check the docs for broken links” (invokes a link-checking skill)
* “Create a DOCX file with my project’s README content”
* “Draft documentation for the new API endpoint based on this PR”
**Using slash commands** - Invoke a skill directly with `/{skill-name}`:
* `/deploy` - Invokes the deploy skill
* `/add-feature-flag` - Invokes the add-feature-flag skill
The Agent recognizes when your request matches a skill’s purpose, loads the skill instructions, and follows them to complete the task.
### Identify skill sources in conversation data
[Section titled “Identify skill sources in conversation data”](#identify-skill-sources-in-conversation-data)
The [Conversation API](/api) returns skill loads as `read_skill` actions. The action’s `input` identifies the skill source:
| Input field | Skill source |
| ------------------ | -------------------------------------------------------------------------------------------------------------------------------------------- |
| `bundled_skill_id` | A Warp-provided bundled reference when this field is present. |
| `skill_path` | The path used to resolve the skill. It can refer to a file-based skill or a path-referenced bundled skill, including one from a remote host. |
To measure usage of skills your team owns, exclude `read_skill` actions whose `input` contains `bundled_skill_id`. From the remaining actions, count only `skill_path` values under skill roots your team manages. Don’t classify other path-based entries as customer-owned because Warp-bundled skills can also use `skill_path`.
See the [bundled skill ID catalog](/factories/api-and-sdk/#skill-actions-in-conversation-data) for Warp-provided IDs and availability details.
## Skill file format
[Section titled “Skill file format”](#skill-file-format)
Skills are markdown files with YAML frontmatter. Each skill must have:
* **name** - A unique identifier for the skill (typically kebab-case)
* **description** - A brief explanation of what the skill does and when to use it
### Basic structure
[Section titled “Basic structure”](#basic-structure)
```markdown
---
name: your-skill-name
description: Brief description of what this skill does and when to use it
---
# Your Skill Name
## Instructions
Provide clear, step-by-step guidance for the agent.
You can use argument placeholders like $ARGUMENTS or $0 in the body (see [Skill arguments](#skill-arguments)).
## Examples
Show concrete examples of using this skill.
```
### Example skill file
[Section titled “Example skill file”](#example-skill-file)
Here’s a complete example of a skill that helps create feature flags:
```markdown
---
name: add-feature-flag
description: Add a new feature flag to the codebase with proper configuration and documentation
---
# Add Feature Flag
## Instructions
1. Ask the user for the feature flag name and default value
2. Add the flag definition to `config/feature_flags.yaml`
3. Create a helper function in `src/utils/flags.ts`
4. Update the feature flags documentation in `docs/FEATURE_FLAGS.md`
## Configuration Format
Feature flags should follow this format in the YAML file:
feature_name:
default: false
description: "What this flag controls"
owner: "team-name"
## Examples
- "Add a feature flag for the new checkout flow"
- "Create a flag to enable dark mode for beta users"
```
## Skill arguments
[Section titled “Skill arguments”](#skill-arguments)
Skills can include argument placeholders that are automatically substituted with values you provide when invoking the skill. This lets you create reusable, parameterized skill templates.
[Using Skill Arguments in Warp](https://www.loom.com/embed/4cb0a80e567c41788816cd9b5acbc7ed)
### Argument syntax
[Section titled “Argument syntax”](#argument-syntax)
Three placeholder formats are supported:
* **`$ARGUMENTS`** — Replaced with the full raw argument string (everything after the skill name).
* **`$ARGUMENTS[N]`** — Replaced with the Nth whitespace-separated argument (0-indexed). For example, `$ARGUMENTS[0]` is the first argument, `$ARGUMENTS[1]` is the second, etc.
* **`$N`** — Shorthand for `$ARGUMENTS[N]`. For example, `$0` is equivalent to `$ARGUMENTS[0]`.
### How argument substitution works
[Section titled “How argument substitution works”](#how-argument-substitution-works)
When you invoke a skill, any text you type after the skill name is treated as the argument string. The argument string is split on whitespace to produce individual indexed arguments.
**If the skill contains argument placeholders** (`$ARGUMENTS`, `$ARGUMENTS[N]`, or `$N`), the placeholders are replaced with the corresponding argument values before the skill instructions are sent to the agent.
**If the skill does not contain any argument placeholders**, the extra text you provide is passed to the agent as a separate user message alongside the skill instructions. This means you can always add context when invoking a skill, whether or not it uses argument placeholders.
Note
If a placeholder references an argument index that wasn’t provided (e.g. `$2` when only two arguments were given), the placeholder is left as-is in the skill content.
### Example: Skill with arguments
[Section titled “Example: Skill with arguments”](#example-skill-with-arguments)
Here’s a skill that uses arguments to explain a topic for a specific audience:
```markdown
---
name: explain-topic
description: Explain a topic for a specific audience in a given tone
---
# Explain Topic
Explain $0 for an audience of $1 professionals.
Use a $2 tone.
Full request: $ARGUMENTS
```
Invoking this skill with:
```plaintext
/explain-topic bears engineering fun
```
Produces the following instructions for the agent:
```plaintext
Explain bears for an audience of engineering professionals.
Use a fun tone.
Full request: bears engineering fun
```
### Example: Skill without arguments
[Section titled “Example: Skill without arguments”](#example-skill-without-arguments)
If a skill has no argument placeholders:
```markdown
---
name: greet
description: Greet the user with an Australian-style hello
---
# Greet
Greet the user warmly in an Australian style.
```
Invoking with extra text:
```plaintext
/greet say it in French
```
The skill instructions are sent first, then “say it in French” is passed as a follow-up user message. The agent sees both and can combine them — in this case, greeting in French with an Australian flair.
## Skill locations
[Section titled “Skill locations”](#skill-locations)
Skills can be stored at two levels: project-level (accessible only within that project) and user-level (accessible from any project).
### Project skills
[Section titled “Project skills”](#project-skills)
Project skills live in your repository and are available when you’re working in that project. We recommend storing them at your project root, but skills in subdirectories are also discovered when you’re working within that subdirectory. This is useful for monorepos with separate `./frontend` and `./backend` directories.
Store them in any of these directories:
* **`.agents/skills/`** (recommended)
* **`.warp/skills/`**
* **`.claude/skills/`**
* **`.codex/skills/`**
* **`.cursor/skills/`**
* **`.gemini/skills/`**
* **`.copilot/skills/`**
* **`.factory/skills/`**
* **`.github/skills/`**
* **`.opencode/skills/`**
Each skill must be in its own subdirectory with a `SKILL.md` file. Any supporting files (scripts, templates, configs) should be referenced in `SKILL.md` so the Agent knows they exist:
* your-project/
* .agents/
* skills/
* add-feature-flag/
* SKILL.md
* run-migrations/
* SKILL.md
* .claude/
* skills/
* review-code/
* SKILL.md
* .github/
* skills/
* create-release/
* SKILL.md
Note
Warp scans all supported skill directory names in your project root, allowing you to maintain skills compatible with multiple AI coding tools in the same repository.
### Root directory skills (global)
[Section titled “Root directory skills (global)”](#root-directory-skills-global)
Root directory skills are stored in your home directory and are available across all projects on your machine. These are useful for personal workflows, coding patterns, or procedures you use regardless of the specific project.
Store global skills in any of these directories in your home folder:
* **`~/.agents/skills/`** (recommended)
* **`~/.warp/skills/`**
* **`~/.claude/skills/`**
* **`~/.codex/skills/`**
* **`~/.cursor/skills/`**
* **`~/.gemini/skills/`**
* **`~/.copilot/skills/`**
* **`~/.factory/skills/`**
* **`~/.github/skills/`**
* **`~/.opencode/skills/`**
The directory structure is the same as project skills:
* `~/.agents/`
* skills/
* git-workflow/
* SKILL.md
* code-review/
* SKILL.md
### Project vs Root directory skills
[Section titled “Project vs Root directory skills”](#project-vs-root-directory-skills)
Understanding when to use each level:
**Project skills** are best for:
* Project-specific workflows (deployment, testing, migrations)
* Team-shared procedures and standards
* Repository-specific automation and tooling
* Domain-specific patterns for that codebase
**Root directory skills** are best for:
* Personal coding preferences and patterns
* General-purpose workflows used across all projects
* Cross-project automation (git workflows, documentation templates)
* Professional standards you apply everywhere
### Extra directories for cloud runs
[Section titled “Extra directories for cloud runs”](#extra-directories-for-cloud-runs)
[Cloud agents](/platform/) discover skills from the repositories in their [environment](/platform/environments/). To index skills that live outside those repositories — for example, skills baked into a custom Docker image — set the `WARP_SKILL_DIRS` environment variable. See [extra skill directories in cloud runs](/platform/skills-as-agents/#extra-skill-directories-in-cloud-runs).
## Creating skills
[Section titled “Creating skills”](#creating-skills)
### Step 1: Choose a location
[Section titled “Step 1: Choose a location”](#step-1-choose-a-location)
Decide whether your skill should be:
* **Project-specific** - Place it in one of your project’s skill directories (`.agents/skills/`, `.warp/skills/`, `.claude/skills/`, etc.)
* **Global** - Place it in one of your home directory’s skill folders (`~/.agents/skills/`, `~/.warp/skills/`, `~/.claude/skills/`, etc.)
### Step 2: Create the directory structure
[Section titled “Step 2: Create the directory structure”](#step-2-create-the-directory-structure)
Create a subdirectory for your skill with a descriptive name:
```bash
mkdir -p .agents/skills/my-new-skill
```
### Step 3: Write the skill file
[Section titled “Step 3: Write the skill file”](#step-3-write-the-skill-file)
Create `SKILL.md` in your skill directory:
```bash
touch .agents/skills/my-new-skill/SKILL.md
```
### Step 4: Add content
[Section titled “Step 4: Add content”](#step-4-add-content)
Write your skill with clear instructions:
```markdown
---
name: my-new-skill
description: One-line description of what this skill does
---
# My New Skill
## When to use
Explain the scenarios where this skill is helpful.
## Instructions
1. First step the Agent should take
2. Second step with specific details
3. Continue with clear, actionable steps
## Important notes
- Any constraints or requirements
- Common pitfalls to avoid
```
## Skills with supporting files
[Section titled “Skills with supporting files”](#skills-with-supporting-files)
Skills can include supporting files like scripts, templates, or configuration files. Place these files in the same directory as your `SKILL.md`:
* .agents/skills/
* check-broken-links/
* SKILL.md
* `check_links.py` Supporting script
* config.yaml Configuration file
In your skill instructions, reference these files using relative paths. For example, in your `SKILL.md`:
```plaintext
## Running the check
From the project root:
python3 .agents/skills/check-broken-links/check_links.py --internal-only
```
This pattern is useful for:
* **Automation scripts** - Python, shell, or Node scripts that perform complex tasks
* **Templates** - Boilerplate files the Agent can copy and customize
* **Configuration** - Default settings or schemas the skill references
## Managing skills
[Section titled “Managing skills”](#managing-skills)
### Viewing available skills
[Section titled “Viewing available skills”](#viewing-available-skills)
Ask the Agent what skills are available:
```plaintext
What skills do I have?
```
The Agent lists all discovered skills with their names and descriptions. This includes skills from all supported directories in both your current project and your home directory.
### Editing skills
[Section titled “Editing skills”](#editing-skills)
Use the [`/open-skill`](/agents/capabilities/slash-commands/) slash command to modify existing skills:
```plaintext
/open-skill
```
This opens an interactive menu where you can:
* Browse project and root directory skills
* See which directory each skill is located in
* Open the skill file in your editor
### Best practices
[Section titled “Best practices”](#best-practices)
* **Write clear descriptions** - The description is how Agents decide whether to use your skill
* **Be specific in instructions** - Include exact file paths, command syntax, and expected formats
* **Include examples** - Show concrete use cases to help Agents understand intent
* **Keep skills focused** - Each skill should do one thing well
* **Use consistent naming** - Follow a naming convention like `verb-noun` (e.g., `add-feature-flag`, `run-migrations`)
* **Version control your skills** - Commit project skills to your repo so the whole team benefits
## Pre-built skills
[Section titled “Pre-built skills”](#pre-built-skills)
Warp maintains a public collection of ready-to-use skills in the [warpdotdev/oz-skills](https://github.com/warpdotdev/oz-skills) repository. You can browse these skills for inspiration, copy them directly into your project’s `.agents/skills/` directory, or adapt them to fit your team’s workflows.
These same skills also appear as suggested agents in the [Oz web app](/platform/oz-web-app/), where you can run them directly in the cloud.
## Suggested skills from Agent Memory
[Section titled “Suggested skills from Agent Memory”](#suggested-skills-from-agent-memory)
Promoting recurring patterns from [Agent Memory](/agents/agent-memory/) into reviewable skill drafts is in design as part of the research preview. See the Agent Memory page for a current status.
## Invoking skills with a prompt
[Section titled “Invoking skills with a prompt”](#invoking-skills-with-a-prompt)
You can pass additional context or instructions to a skill when invoking it with a slash command.
**Using slash commands with a prompt:**
* `/deploy push the latest changes to staging` — Invokes the deploy skill with additional instructions to target staging
* `/code-review focus on error handling and edge cases` — Invokes the code-review skill with guidance on what to prioritize
This is useful when you want to reuse a skill’s workflow but tailor the execution to a specific situation without modifying the skill itself.
## Running agents from skills
[Section titled “Running agents from skills”](#running-agents-from-skills)
Skills can be used with both local and [cloud agents](/platform/) to create reusable, automated workflows. When running an agent via the CLI, web app, or API, you can specify a skill to provide the base instructions for the agent.
For a complete guide to running skill-based agents—including CLI usage, the Oz web app, scheduling, skill discovery, and API integration—see [Skills as Agents](/platform/skills-as-agents/).
## Related features
[Section titled “Related features”](#related-features)
* [**Rules**](/agents/capabilities/rules/) - Set persistent guidelines and constraints for Agent behavior
* [**MCP Servers**](/agents/capabilities/mcp/) - Expose external data sources and tools to Agents
* [**Cloud Agents**](/platform/) - Run Agents in the cloud on schedules or triggers
* [**Agent Profiles**](/agents/capabilities/agent-profiles-permissions/) - Control Agent permissions and autonomy
***
## Next steps
[Section titled “Next steps”](#next-steps)
Skills become even more powerful when you automate and share them.
* **[Scheduled Agents quickstart](/platform/triggers/scheduled-agents-quickstart/)** - Run a skill on a recurring cron schedule for tasks like weekly dependency checks or daily code cleanup.
* **[Integrations quickstart](/platform/integrations/quickstart/)** - Trigger skills from Slack or Linear so your team can invoke agent workflows from the tools they already use.
# Slash Commands
Canonical page: [/agents/capabilities/slash-commands/](https://docs.warp.dev/agents/capabilities/slash-commands/)
> Use Slash Commands in terminal mode or Agent Mode to quickly run built-in actions or saved prompts without leaving the input field.
Slash Commands are quick actions and saved prompts you can invoke by typing `/` in terminal mode or Agent Mode. They provide instant access to built-in actions like starting conversations, creating environments, switching models, opening static flows, and running saved prompts from Warp Drive.
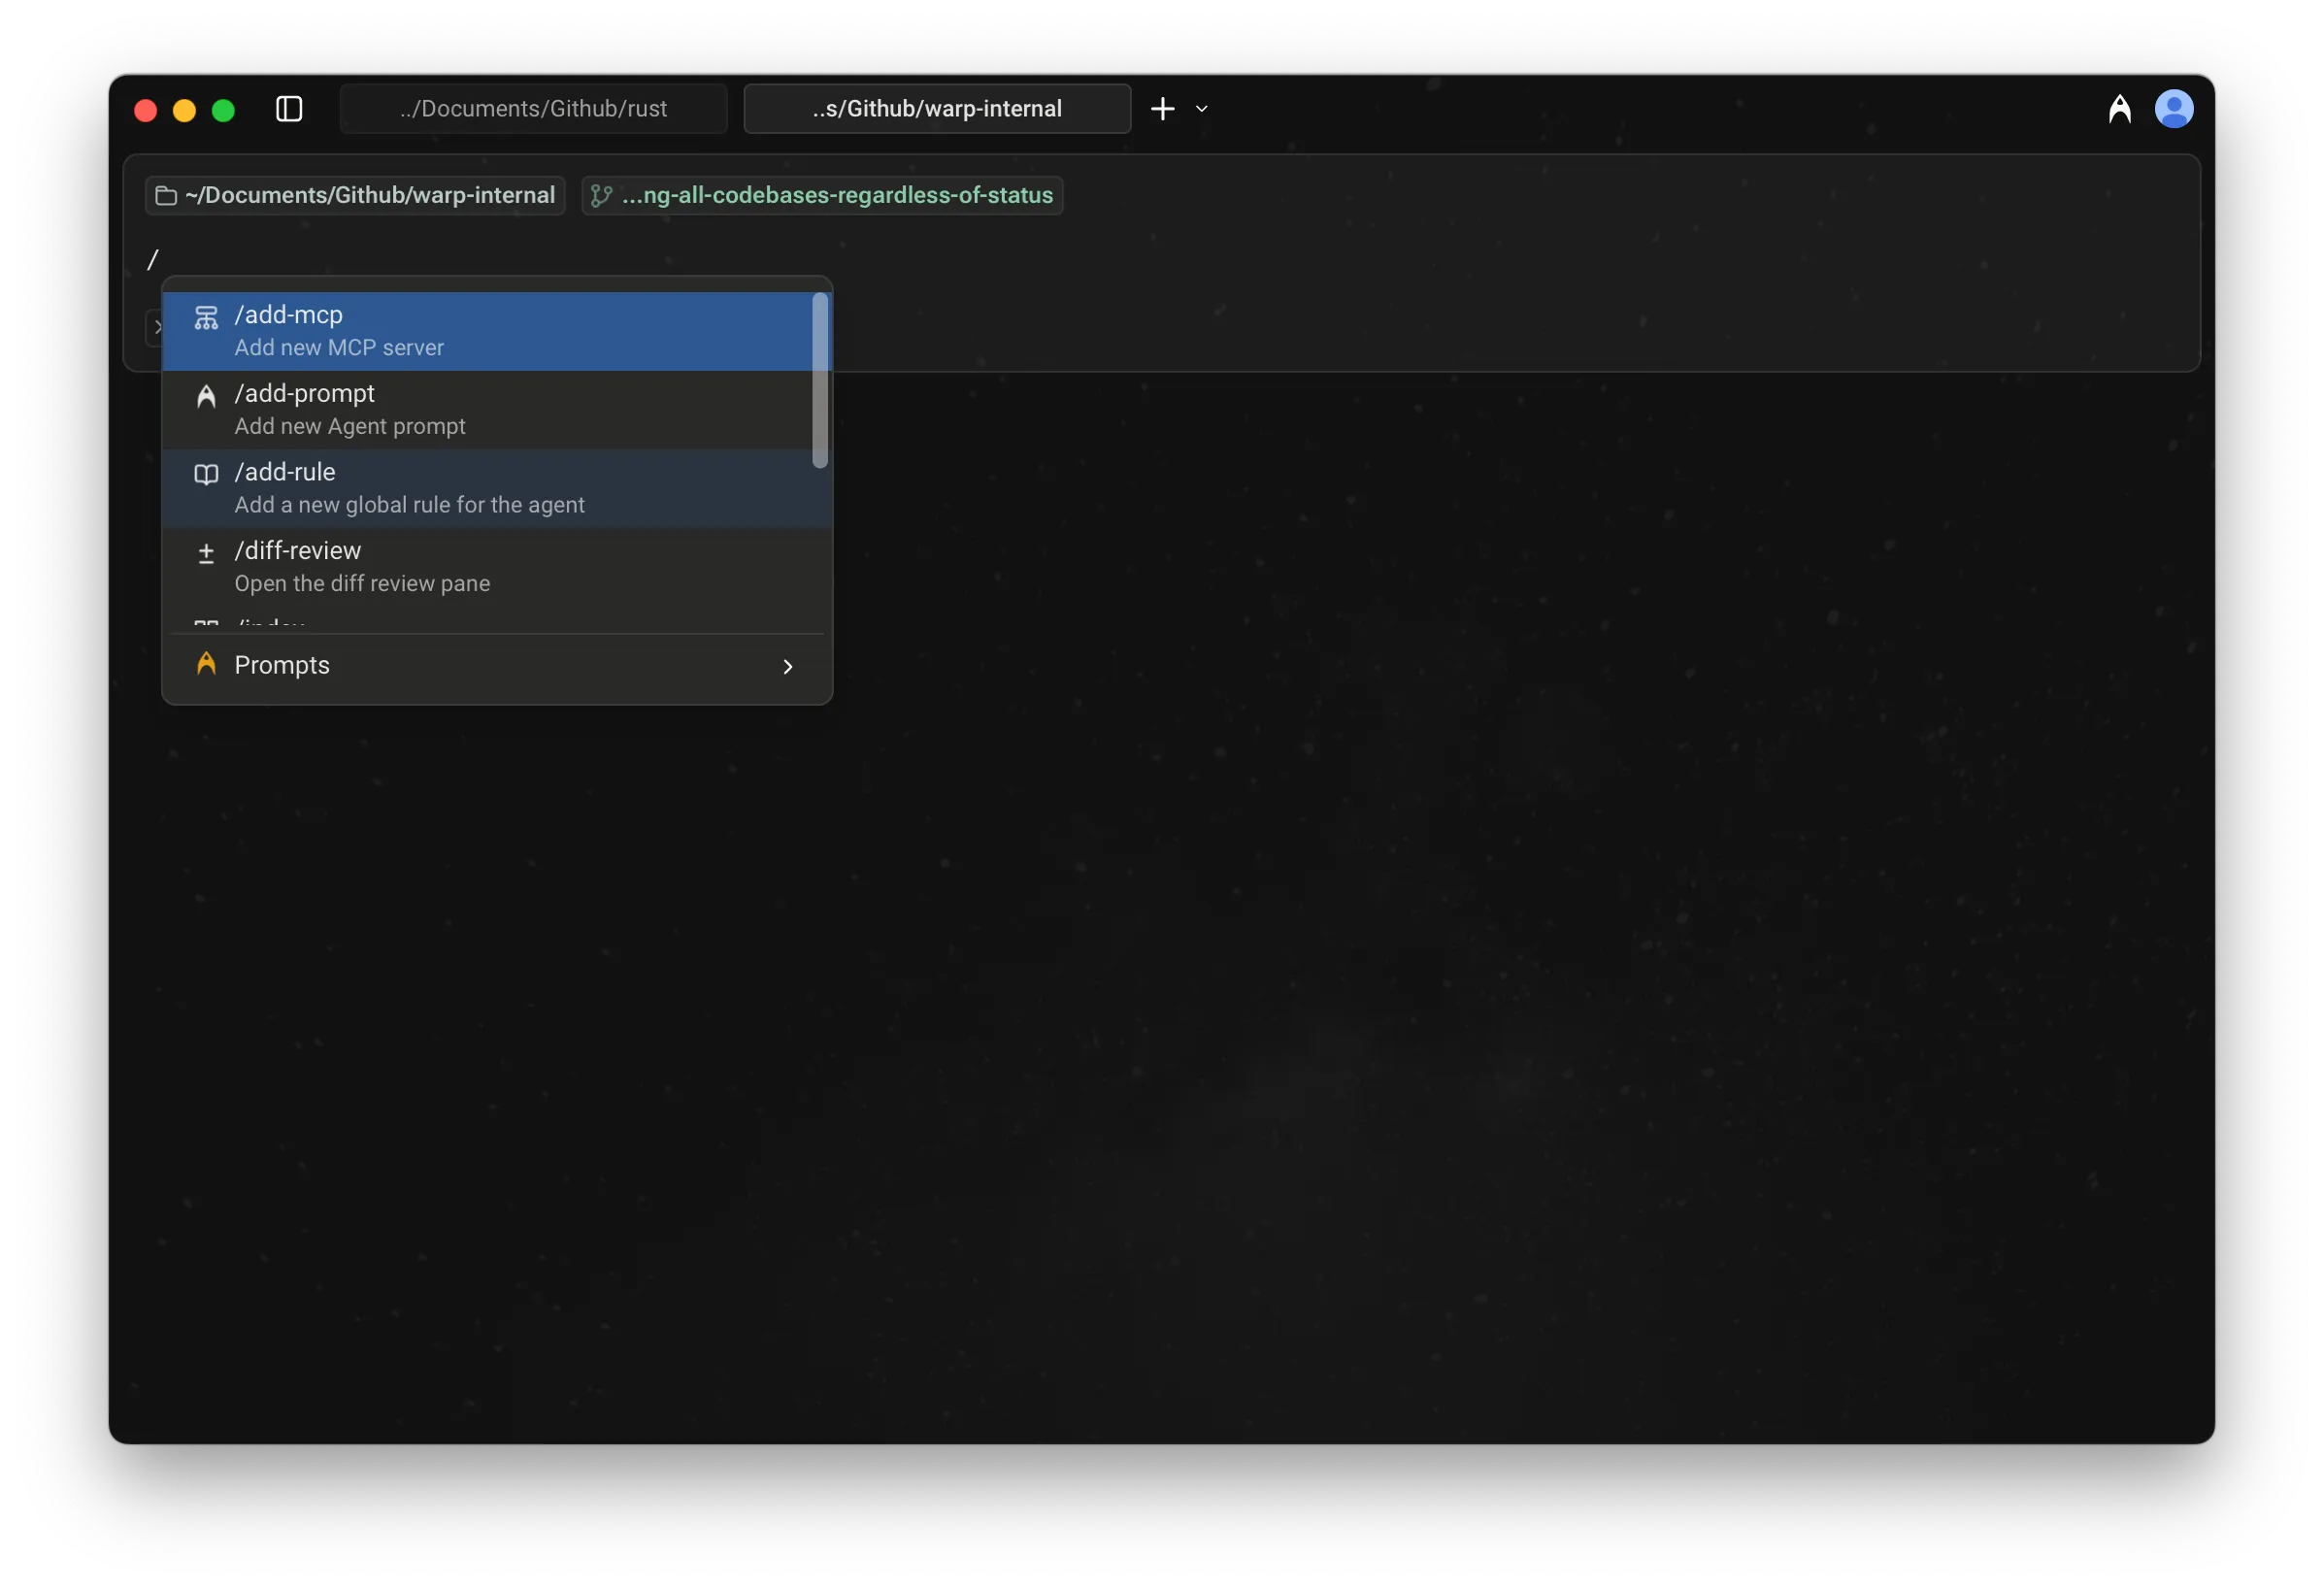
Slash Commands menu.
As you type, the menu filters results in real time, making it easy to find and run the command or prompt you need.
## Static slash commands
[Section titled “Static slash commands”](#static-slash-commands)
Warp currently supports the following built-in Slash Commands:
| Slash Command | Description |
| ---------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `/add-mcp` | Add a new [MCP server](/agents/capabilities/mcp/). |
| `/add-prompt` | Add a new [Agent Prompt](/knowledge-and-collaboration/warp-drive/prompts/) in Warp Drive. |
| `/add-rule` | Add a new [Global Rule](/agents/capabilities/rules/) for the Agent. |
| `/agent` | Start a new [agent conversation](/agents/local-agents/interacting-with-agents/). Optionally include a prompt to send immediately. |
| `/changelog` | Open the latest Warp [changelog](/changelog/). |
| `/cloud-agent` | Start a new [cloud agent conversation](/platform/). `*` |
| `/compact` | Free up context by summarizing conversation history. |
| `/compact-and` | Compact the current conversation and then send a follow-up prompt. |
| `/continue-locally` | Fork the current cloud agent conversation into a local Warp session. See [Handoff between local and cloud agents](/platform/handoff/). Available while a cloud agent conversation is active. |
| `/conversations` | Open [conversation history](/agents/local-agents/interacting-with-agents/). |
| `/copy-debugging-id` | Copy debugging information for the current conversation to your clipboard, so you can include it when [reporting an issue](/support-and-community/troubleshooting-and-support/sending-us-feedback/). Available while a conversation is active. |
| `/cost` | Toggle credit usage details in the current conversation. |
| `/create-environment` | Create a [Warp Environment](/platform/environments/) (Docker image + repos) via guided setup. `*` |
| `/create-new-project` | Have the Agent walk you through creating a new coding project. `*` |
| `/environment` | Switch the [environment](/platform/environments/) for the current cloud agent conversation. |
| `/export-to-clipboard` | Export the current conversation to clipboard in markdown format. |
| `/export-to-file` | Export the current conversation to a markdown file. |
| `/feedback` | Open the static feedback experience. See [Using `/feedback` in Warp](/support-and-community/troubleshooting-and-support/sending-us-feedback/#using-feedback-in-warp) for details. |
| `/fork` | [Forks the current conversation](/agents/local-agents/interacting-with-agents/conversation-forking/) into a new thread with the full context and history of the original. You can optionally include a prompt that will be sent immediately in the forked conversation. |
| `/fork-and-compact` | [Forks the current conversation](/agents/local-agents/interacting-with-agents/conversation-forking/) and automatically compacts the forked version. Useful when you want a fresh, summarized starting point that preserves relevant context while trimming the rest. |
| `/fork-from` | Open a searchable menu to [fork the conversation](/agents/local-agents/interacting-with-agents/conversation-forking/) from a specific query. Select a query to create a fork that includes everything up to that point. |
| `/handoff` | Hand the current local conversation off to a cloud agent, carrying its history and a snapshot of your uncommitted changes. See [Handoff from local to cloud](/platform/handoff/local-to-cloud/). You can optionally include a follow-up prompt. `*` |
| `/harness` | Switch the [harness](/platform/harnesses/) for the current cloud agent conversation. |
| `/host` | Switch the execution host for the current cloud agent conversation. |
| `/index` | Index the current codebase using [Codebase Context](/agents/capabilities/codebase-context/). |
| `/init` | Index the current codebase and generate an [AGENTS.md file](/agents/capabilities/rules/). `*` |
| `/model` | Switch the base agent model for the current conversation. |
| `/new` | Start a new [agent conversation](/agents/local-agents/interacting-with-agents/) (alias for `/agent`). |
| `/open-code-review` | Open the [code review](/code/code-review/) pane. |
| `/open-file` | Open a file for editing in Warp’s [code editor](/code/code-editor/). |
| `/open-mcp-servers` | View the status of your [MCP servers](/agents/capabilities/mcp/). |
| `/open-project-rules` | Open the [Project Rules](/agents/capabilities/rules/#project-rules) file (`AGENTS`). |
| `/open-repo` | Switch to another indexed repository. |
| `/open-rules` | View all of your global and project [rules](/agents/capabilities/rules/). |
| `/open-settings-file` | Open the Warp [settings file](/terminal/settings/) (`settings.toml`) in Warp’s code editor. |
| `/open-skill` | Open an interactive menu to browse and edit project or global [skills](/agents/capabilities/skills/). |
| `/orchestrate` | Break a task into subtasks and run them in parallel with multiple agents. See [Multi-agent orchestration](/platform/orchestration/). `*` |
| `/plan` | Prompt the Agent to research and create a [plan](/agents/capabilities/planning/) for a task. When the work benefits from parallel agents, the plan can include [multi-agent orchestration](/platform/orchestration/). |
| `/profile` | Switch the active [execution profile](/agents/capabilities/agent-profiles-permissions/). |
| `/prompts` | Search saved [prompts](/knowledge-and-collaboration/warp-drive/prompts/). |
| `/queue` | Queue a prompt to send after the agent finishes responding. See [Prompt Queueing](/agents/local-agents/interacting-with-agents/prompt-queueing/). |
| `/remote-control` | Publish the current third-party CLI agent session to the cloud so you can monitor and steer it from another device. See [Remote Control](/agents/cli-agents/remote-control/). |
| `/rename-conversation` | Rename the current conversation. |
| `/rename-tab` | Rename the current tab. Include the new tab name as an argument (for example, `/rename-tab deploy`). |
| `/rewind` | Rewind to a previous point in the conversation. |
| `/set-tab-color` | Set the color of the current tab. Takes a required color argument: `red`, `green`, `yellow`, `blue`, `magenta`, `cyan`, or `none` to clear it. See [Tab colors](/terminal/windows/tabs/#tab-colors). |
| `/skills` | Invoke a [skill](/agents/capabilities/skills/) from a searchable menu. |
| `/usage` | Open [billing and usage](/support-and-community/plans-and-billing/) settings. |
Caution
Slash commands marked with a `*` consume credits to complete the task.
#### Using Agent Prompts via Slash Commands
[Section titled “Using Agent Prompts via Slash Commands”](#using-agent-prompts-via-slash-commands)
In addition to static commands, the menu also shows [Agent Prompts](/knowledge-and-collaboration/warp-drive/prompts/) saved in your [Warp Drive](/knowledge-and-collaboration/warp-drive/).
* These prompts can be custom ones you’ve created or ones shared with you.
* As you type after `/`, prompts are filtered dynamically, so you can quickly run them without leaving the input field.
Slash Commands menu with filtered Agent Prompts.
### Tips
[Section titled “Tips”](#tips)
* **Context-aware:** Many Slash Commands use your current working directory or file selection as context.
* **Quick access:** Use `/` from terminal mode or Agent Mode to avoid navigating through menus.
### Example of using a Slash Command
[Section titled “Example of using a Slash Command”](#example-of-using-a-slash-command)
Below is an example interaction when `/init` is run:
The /init setup flow, step 1 of 2.
The /init setup flow, step 2 of 2.
# Agent Task Lists
Canonical page: [/agents/capabilities/task-lists/](https://docs.warp.dev/agents/capabilities/task-lists/)
> Track and manage complex Agent workflows with automatic task lists that break requests into clear, actionable steps and update progress in real time.
Task Lists let the Warp Agent automatically break down complex requests into clear, trackable steps. When a request requires multiple actions, the agent creates a structured list, executes each step in order, and tracks progress in real time. No configuration is needed—the agent detects and creates task lists automatically.
An example of a Task List in progress.
### How task lists work
[Section titled “How task lists work”](#how-task-lists-work)
1. **Automatic task creation** — For complex requests, the Agent generates a structured list of tasks to complete.
2. **Step-by-step execution** — The Agent works through each task in sequence, updating statuses in real time.
3. **Summary** — Once all tasks are complete, the Agent provides a concise summary of what was done, including outputs, results, and relevant context. If any tasks were skipped or couldn’t be completed, it explains why.
After each step is completed, there is also a completion marker in the Agent conversation.
Task completion markers in a conversation.
### Task statuses
[Section titled “Task statuses”](#task-statuses)
Each task in the list has a visual indicator so you can quickly see its progress.
| Status | Icon | Meaning |
| ------------ | ----------------- | ----------------------------------------------- |
| Current task | ● (filled circle) | The Agent is actively working on this task. |
| Completed | ✔︎ | The Agent has finished this task successfully. |
| Not started | ○ (empty circle) | The task is in the queue but work hasn’t begun. |
| Cancelled | ■ (filled square) | The task was stopped before completion. |
### Task list access
[Section titled “Task list access”](#task-list-access)
During any Agent conversation, a task list chip appears at the bottom-right of the screen (when input is pinned to the bottom; otherwise, it may appear along the right side).
* Click the chip to open the current task list.
* You can collapse or expand the view at any time without interrupting the Agent.
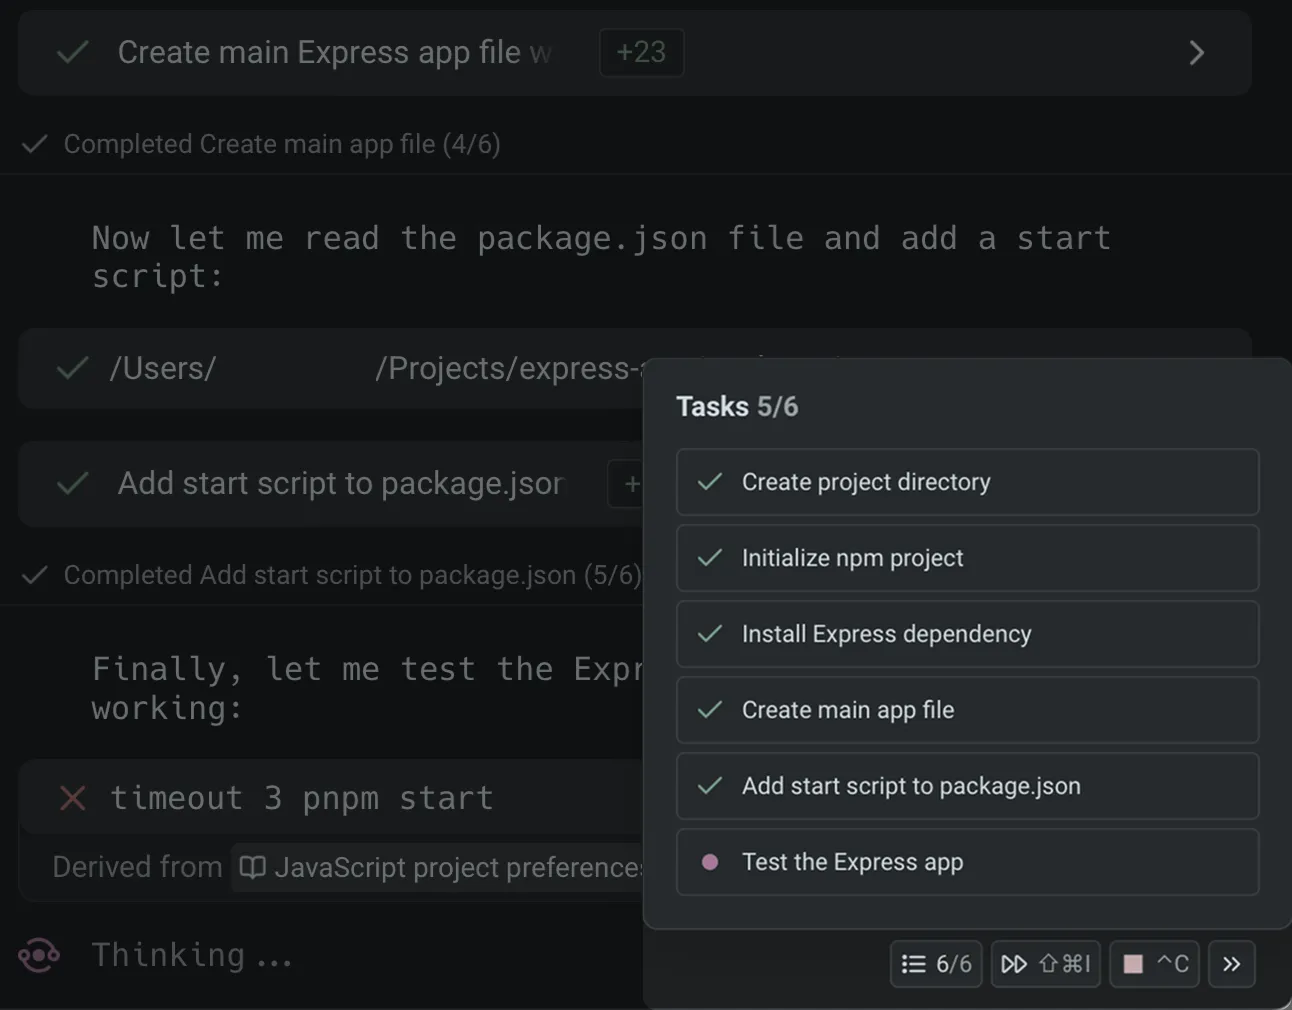
Task List chip in an agent conversation.
# Agent web search
Canonical page: [/agents/capabilities/web-search/](https://docs.warp.dev/agents/capabilities/web-search/)
> Warp’s web search lets agents pull in real-time information, documentation, and cited sources whenever it improves an answer.
Warp includes native web search for models that support first-party search tools. When enabled, agents can look up information in real time, consult documentation, retrieve current version numbers, and cite the sources used to generate responses.
[Web search in Warp](https://www.loom.com/embed/06a4ba98f2e0446d80cb37aa4c23848c)
This page covers how web search works, supported models, what you can expect inside Warp, configuration options, and how this differs from attaching URLs directly to a prompt.
***
### When the Agent uses web search
[Section titled “When the Agent uses web search”](#when-the-agent-uses-web-search)
Models initiate a web search when it improves the quality or accuracy of an answer. **Common scenarios include:**
* Retrieving official documentation or API references
* Getting the latest version of a library or tool
* Checking error messages, GitHub issues, or Stack Overflow discussions
* Looking up ongoing incidents or recent changes
* Answering questions where recency matters (e.g., “best approach in 2025 to…”)
Web searches are automatically triggered when the model considers them useful. You don’t need special syntax.
### How web search works in Warp
[Section titled “How web search works in Warp”](#how-web-search-works-in-warp)
**When a search occurs:**
1. Warp shows a “Searching the web…” indicator inside the conversation.
2. You can expand the search result to view:
* The query issued
* The pages retrieved
3. **The model reads results and produces a grounded response.**
* Claude models cite sources in the references footer.
* OpenAI models use inline citations and also show references in the footer.
### Supported and unsupported models
[Section titled “Supported and unsupported models”](#supported-and-unsupported-models)
Web search is available only for models that offer a native web search integration, that works in tandem with other custom tools.
**Models that support web search**
* Anthropic: `Claude Opus 5.5`, `Claude 4.6 Series`, `Claude 4.5 Series`, `Claude 4 Series`
* OpenAI:
* `GPT-6 Astra`, `GPT-6.1 Sol`, `GPT-6 Sol`, `GPT-6 Luna`
* `GPT-5.4`, `GPT-5.3 Codex`, `GPT-5.2 Codex`, `GPT-5.2`
Warp uses each vendor’s official tool:
* [Claude web search tool documentation](https://docs.claude.com/en/docs/agents-and-tools/tool-use/web-search-tool)
* [OpenAI web search tool documentation](https://developers.openai.com/api/docs/guides/tools-web-search)
Note
**Note**: We plan to add native web search for additional models as soon as their APIs fully support it. We’ll continue updating the list of search-capable models as vendors roll out broader tooling. We’re also exploring custom web search tools that’ll work across all models.
### Viewing search results
[Section titled “Viewing search results”](#viewing-search-results)
You can inspect the web search UI at any time:
* Expand the **Web Search** section in the agent response
* You can see:
* The list of pages fetched
* The text used to answer your question
* Citations and reference metadata
This makes it easy to verify accuracy, audit reasoning, and validate sources.
### Enabling or disabling web search
[Section titled “Enabling or disabling web search”](#enabling-or-disabling-web-search)
Web search is controlled per [Profiles & Permissions](/agents/capabilities/agent-profiles-permissions/).
To configure:
1. In the Warp app, navigate to **Settings** > **Agents** > **Profiles**.
2. Next to the agent profile, click **Edit**.
3. Scroll to **Call web tools** and toggle the setting on or off.
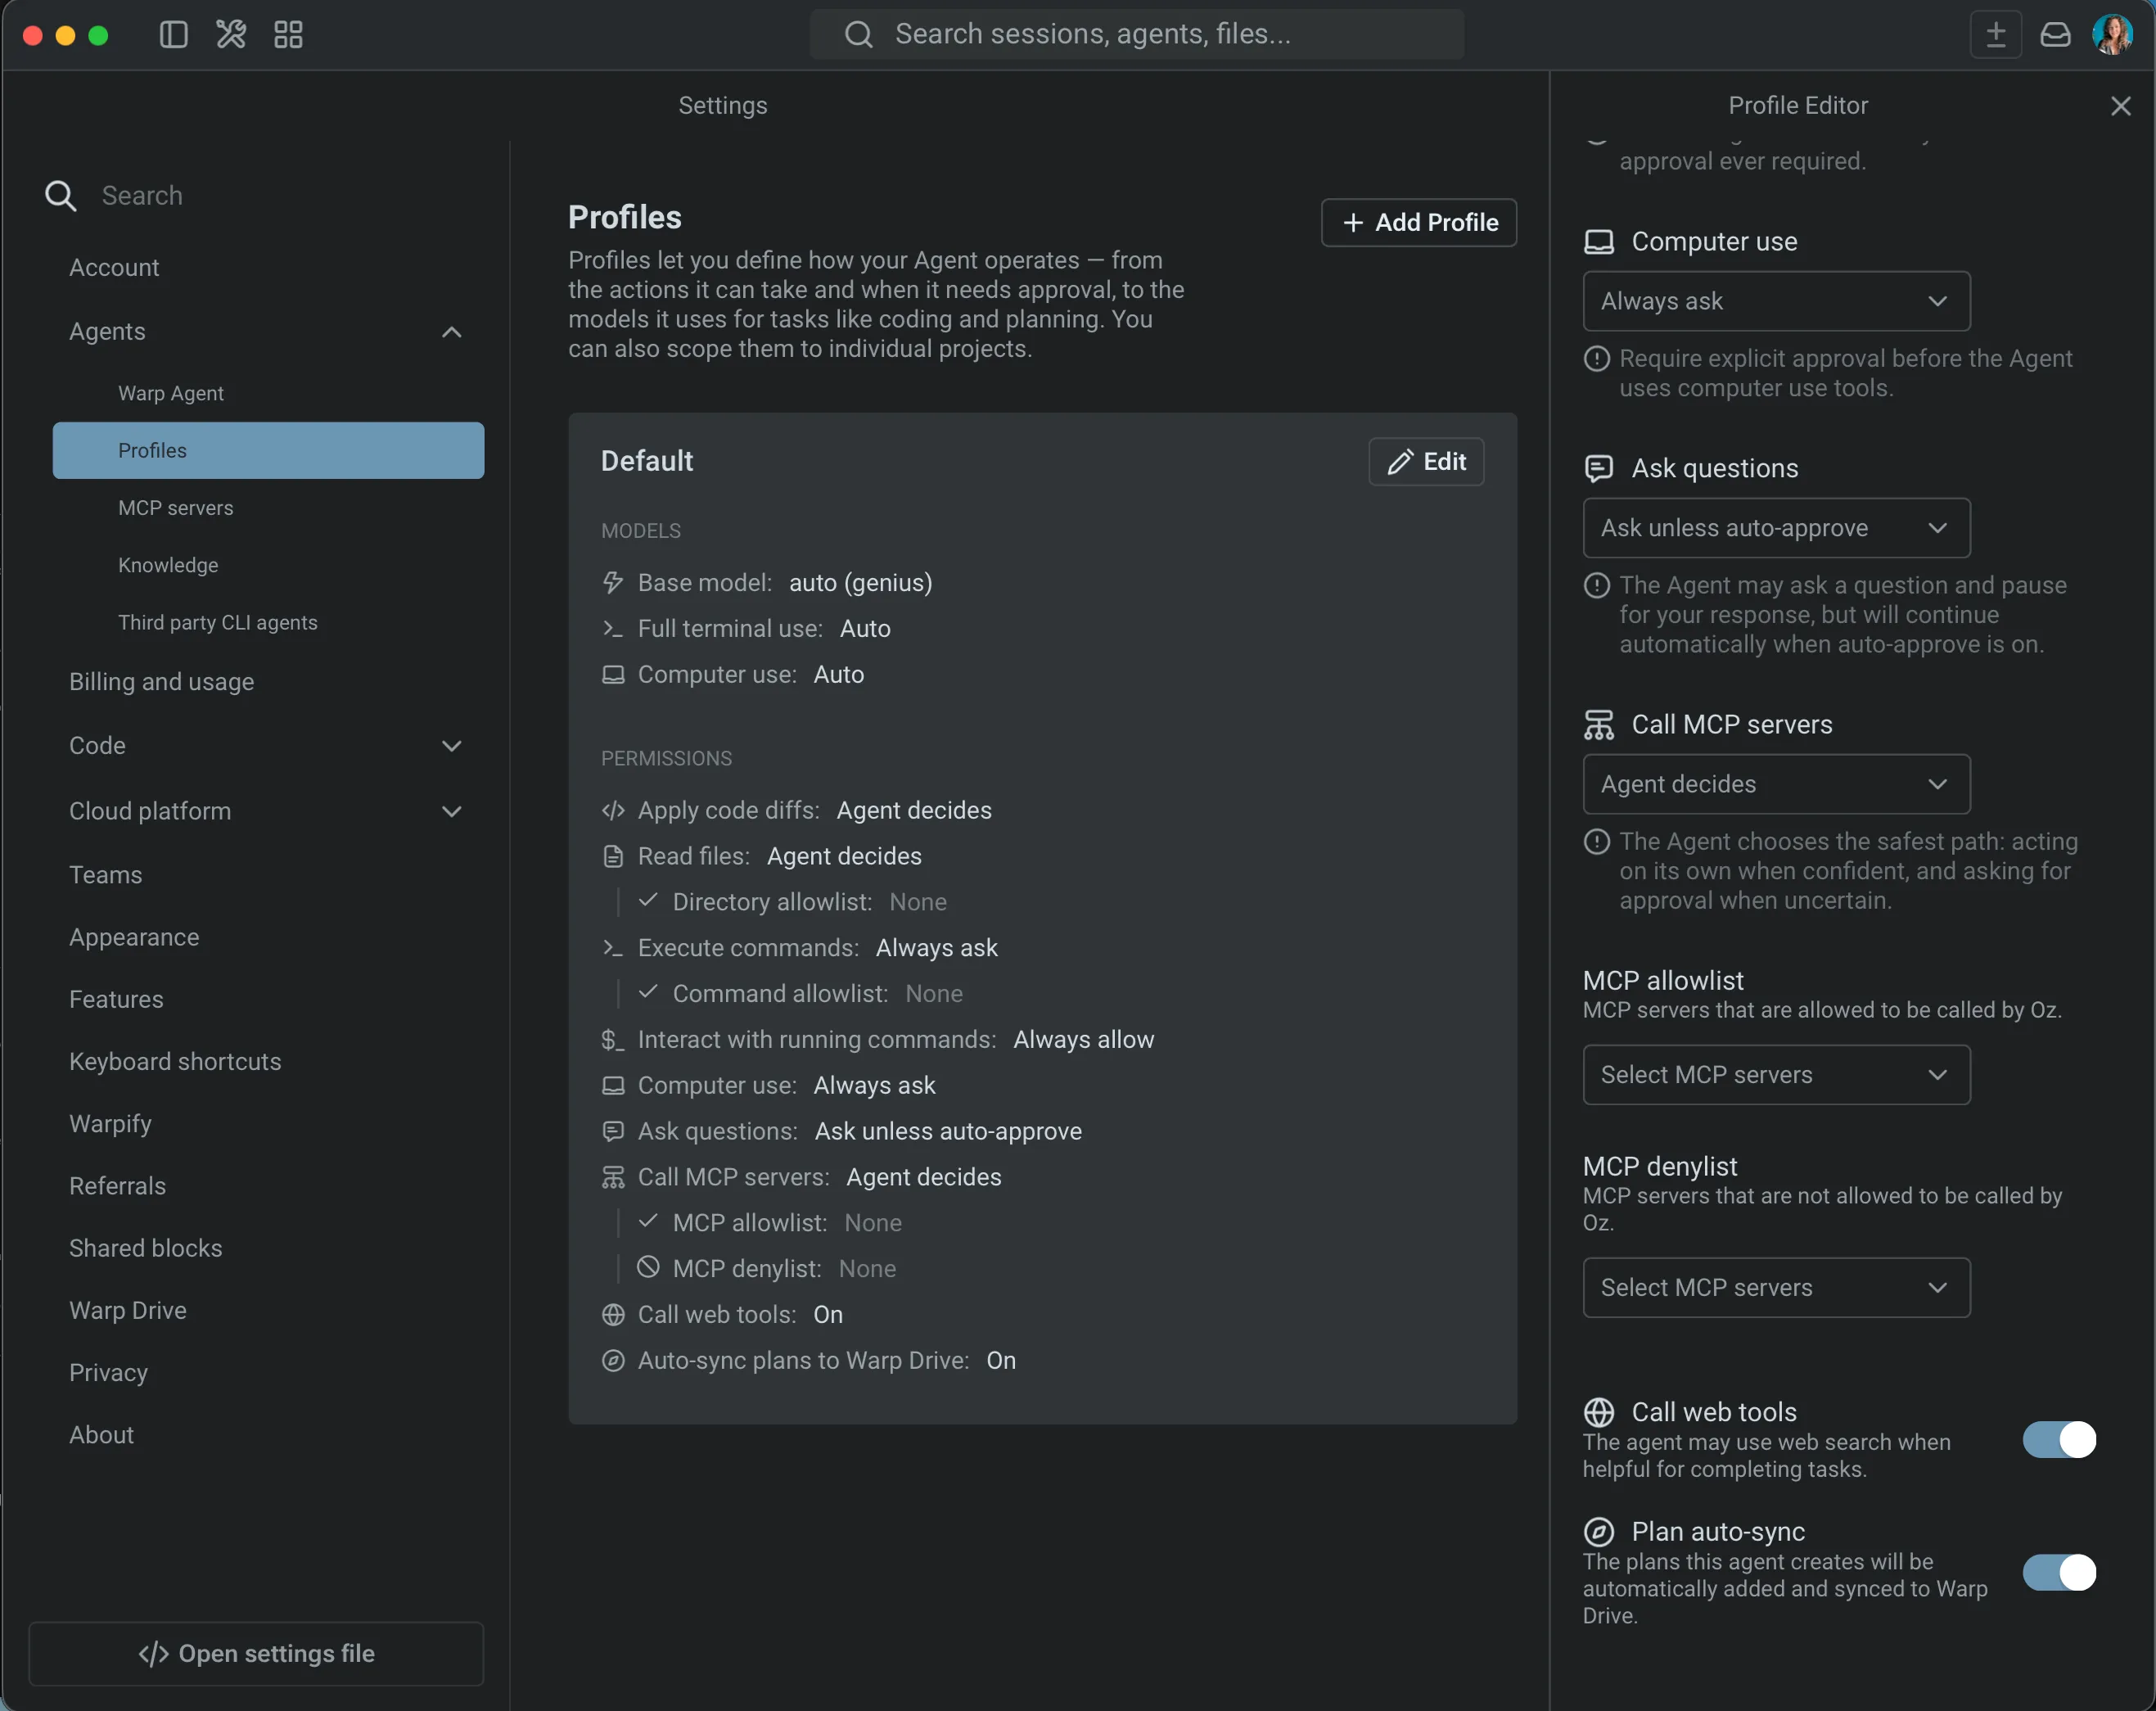
Disabling this prevents the agent from performing searches, even if a model would normally use them.
### Credit usage
[Section titled “Credit usage”](#credit-usage)
Web search incurs two types of credit usage:
1. A small fixed cost per search invocation
2. Additional cost proportional to retrieved content, since retrieved text is passed to the model
You’ll see these contributions itemized in the conversation’s credit usage footer, alongside model calls, planning calls, and other tool usage.
# Warp Agent CLI overview
Canonical page: [/agents/cli/](https://docs.warp.dev/agents/cli/)
> Run the Warp Agent in any terminal with the Warp Agent CLI. Prompt the agent, run shell commands, and hand work off to cloud agents.
The Warp Agent CLI brings the Warp Agent from the Warp app to the terminal you already use. Run the `warp` command to start an agent conversation. You can prompt the agent in natural language, review and approve its actions, and run shell commands in the same input, without changing your terminal setup.
## What is the Warp Agent CLI?
[Section titled “What is the Warp Agent CLI?”](#what-is-the-warp-agent-cli)
The Warp Agent CLI is a standalone terminal program that runs [the Warp Agent](/platform/harnesses/warp-agent/), the same agent that powers the Warp app. It renders conversations as a scrolling transcript in your terminal, with streaming responses, code diffs, tool calls, and permission requests you approve inline.
The CLI is also a native terminal multiplexer. It creates and maintains its own pseudoterminal (PTY), which lets you and the agent execute commands and interact with running processes through the same terminal, including prompts and full-screen terminal apps. Because it’s a regular command-line program, it works in any terminal emulator, including over SSH.
To get a working setup in a few minutes, follow the [quickstart](/agents/cli/quickstart/).
## Key features
[Section titled “Key features”](#key-features)
* **[Agent conversations](/agents/cli/agent-conversations/)** - Follow the agent’s work in a scrollable transcript with streamed responses, Markdown formatting, file-edit diffs, tool calls, plans, and task lists.
* **[Shell commands](/agents/cli/input-and-shell-commands/#shell-mode)** - Run shell commands from the same input you use to prompt the agent, including long-running and interactive ones.
* **[Permissions and profiles](/agents/cli/permissions-and-profiles/)** - Approve commands and file edits from inline request cards, or configure execution profiles and auto-approve.
* **[Persistent conversations](/agents/cli/agent-conversations/#managing-conversations)** - Conversations save to your Warp account, so you can exit and resume later or switch between them.
* **[Cloud handoff and orchestration](/agents/cli/cloud-and-orchestration/)** - Hand off a conversation to a cloud agent, continue cloud runs in the CLI, and coordinate multiple agents.
* **[Project context](/agents/cli/configuration/#project-context-and-rules)** - The agent automatically picks up your project’s rules (like `AGENTS.md`), skills, and MCP servers.
* **[Model choice](/agents/cli/models-and-usage/)** - Pick a model per conversation, bring your own provider API keys, and track credit usage.
* **[Customization](/agents/cli/configuration/)** - Configure themes, the statusline, and the start screen through a local settings file.
## How it relates to the Warp app and cloud agents
[Section titled “How it relates to the Warp app and cloud agents”](#how-it-relates-to-the-warp-app-and-cloud-agents)
* **The Warp app** - The CLI runs the same [Warp Agent](/platform/harnesses/warp-agent/) harness as the Warp app, so your account, plan, model access, rules, and skills work the same in both. The CLI doesn’t require the Warp app to be installed.
* **Automation Platform** - The Automation Platform is Warp’s programmable platform for running and coordinating agents at scale. The CLI connects to the same platform. Conversations sync to your Warp account, and you can hand work off to [cloud agents](/agents/cli/cloud-and-orchestration/) or continue a cloud run from your terminal.
## Checking your account, plan, and billing
[Section titled “Checking your account, plan, and billing”](#checking-your-account-plan-and-billing)
The CLI has slash commands for the account details you’d otherwise look up in the Warp app or the Oz web app.
* **Session and account status** - Run `/status` to open a read-only panel with the installed version, the current conversation’s name and ID, the working directory, and the organization and email you’re signed in as. Press `Esc` to close it. Include these details when you report a problem.
* **Upgrade your plan** - Run `/upgrade` to open Warp’s upgrade page in your browser.
* **Manage team billing** - Run `/manage-billing` to open your team’s billing page in your browser. The command is listed only when you administer billing for your team.
For how usage is metered as you work, see [models and usage](/agents/cli/models-and-usage/#usage-and-cost).
## Coming from the Warp app
[Section titled “Coming from the Warp app”](#coming-from-the-warp-app)
If you already use the Warp app, most of your setup carries over. Rules and skills are discovered from the same shared paths, and your saved Warp Drive prompts are available after you log in (other Warp Drive object types aren’t available in the CLI). To copy compatible settings and global MCP server configurations, run the bundled `/tui-migrate-setup` skill and follow the agent’s instructions. Credentials are never copied, so MCP servers that require authentication must be reauthenticated in the CLI.
## Next steps
[Section titled “Next steps”](#next-steps)
* [Quickstart](/agents/cli/quickstart/) - Install the CLI, log in, run your first prompt, and see the supported platforms.
* [Agent conversations](/agents/cli/agent-conversations/) - Learn how the transcript, diffs, and approvals work.
* [Input and shell commands](/agents/cli/input-and-shell-commands/) - Compose prompts and run shell commands from the same input.
* [Configuration](/agents/cli/configuration/) - Customize the CLI with the settings file.
* [Reference](/agents/cli/reference/) - Flags, slash commands, and keyboard shortcuts.
# Claude Code in Warp
Canonical page: [/agents/cli-agents/claude-code/](https://docs.warp.dev/agents/cli-agents/claude-code/)
> Set up Claude Code in Warp with full notification support, rich input, code review, and more.
Claude Code is Anthropic’s agentic coding tool that operates directly in your terminal. It understands your codebase, executes commands, edits files, and manages Git workflows — all through natural language. For full documentation, see the [official Claude Code docs](https://code.claude.com/docs).
Warp auto-detects Claude Code when you run it, giving you access to rich input controls, code review, agent notifications, and other integrated features. For a product overview, see [Claude Code in Warp](https://www.warp.dev/agents/claude-code).
For installation, authentication, project configuration, and productivity tips, see the [How to set up Claude Code](/guides/external-tools/how-to-set-up-claude-code/) guide.
Note
Claude Code is also available as a harness in the Automation Platform for cloud orchestration. See [Claude Code with the Automation Platform](/platform/harnesses/claude-code/).
## Setting up notifications
[Section titled “Setting up notifications”](#setting-up-notifications)
Warp supports agent notifications for Claude Code through a plugin. Once installed, Warp surfaces in-app and desktop alerts when Claude Code needs your input — such as command approval, code review, or error intervention.
### Auto-install
[Section titled “Auto-install”](#auto-install)
Each time you run Claude Code in Warp without the notification plugin installed, a notification chip appears offering one-click installation. Click the chip to install the plugin automatically. After installation, Warp immediately starts receiving notifications from Claude Code.
### Manual install
[Section titled “Manual install”](#manual-install)
Note
The notification plugin requires `jq`. Install it with your package manager (e.g., `brew install jq` on macOS) if it’s not already available.
If the auto-install chip doesn’t appear or fails to install the plugin, install it manually. From inside Claude Code, run:
```bash
/plugin marketplace add warpdotdev/claude-code-warp
/plugin install warp@claude-code-warp
```
Or from your terminal (outside of Claude Code):
```bash
claude plugin marketplace add warpdotdev/claude-code-warp
claude plugin install warp@claude-code-warp
```
After installing, restart Claude Code or run `/reload-plugins` to activate the plugin.
Note
If installation fails or you have an outdated version of the plugin, remove it first with `claude plugin marketplace remove claude-code-warp`, then re-run the install commands above.
### Installation instructions banner
[Section titled “Installation instructions banner”](#installation-instructions-banner)
If the auto-install chip doesn’t work, or if you’re running Claude Code over SSH or on a remote machine, Warp displays an installation instructions banner directly in the terminal. The banner shows step-by-step commands that you can run in place — no need to switch between tabs or copy-paste from external documentation.
For plugin source and updates, see the [claude-code-warp GitHub repository](https://github.com/warpdotdev/claude-code-warp).
## Supported Warp features
[Section titled “Supported Warp features”](#supported-warp-features)
Claude Code supports Warp’s full set of agent integration features:
* **Agent notifications** - Receive in-app and desktop alerts when Claude Code needs your attention. The notification UI displays your current git branch alongside agent status.
* **Rich input editor** - Press `Ctrl-G` to open an expanded input editor for composing longer prompts.
* **Code review** - Send inline review comments directly to the agent from Warp’s code review panel.
* **Attach code as context** - Select code and send it to the agent as context.
* **Vertical tabs with agent metadata** - Monitor Claude Code sessions with status indicators in Warp’s tab bar.
* **Tab Configs** - Save and restore Claude Code session configurations.
* **[Remote Control](/agents/cli-agents/remote-control/)** - Publish your Claude Code session so you can monitor and steer it from another device.
## Related pages
[Section titled “Related pages”](#related-pages)
* [How to set up Claude Code](/guides/external-tools/how-to-set-up-claude-code/) — step-by-step setup guide
* [Claude Code in Warp](https://www.warp.dev/agents/claude-code) — product overview
* [Third-party CLI agents overview](/agents/cli-agents/overview/) — supported CLI agent integrations
* [Remote Control](/agents/cli-agents/remote-control/) — publish a Claude Code session to monitor and steer it remotely
* [Claude Code with the Automation Platform](/platform/harnesses/claude-code/) — Claude Code as a cloud harness
* [OpenCode](/agents/cli-agents/opencode/) — OpenCode in Warp
* [Codex](/agents/cli-agents/codex/) — Codex in Warp
# Codex CLI in Warp
Canonical page: [/agents/cli-agents/codex/](https://docs.warp.dev/agents/cli-agents/codex/)
> Set up Codex in Warp with notification support, rich input, code review, and more.
Codex is OpenAI’s open-source coding agent that runs in your terminal. It can write and edit code, execute commands, and navigate your codebase through natural language. For full documentation, see the [Codex GitHub repository](https://github.com/openai/codex).
Warp auto-detects Codex when you run it, giving you access to rich input controls, code review, and other integrated features. For a product overview, see [Codex in Warp](https://www.warp.dev/agents/codex).
For installation, authentication, project configuration, and productivity tips, see the [How to set up Codex CLI](/guides/external-tools/how-to-set-up-codex-cli/) guide.
Note
Codex is also available as a harness in the Automation Platform for cloud orchestration. See [Codex with the Automation Platform](/platform/harnesses/codex/).
## Setting up notifications
[Section titled “Setting up notifications”](#setting-up-notifications)
Warp surfaces Codex activity as in-app and desktop alerts — such as when Codex completes a task, encounters an error, or needs your input. This is powered by the Warp plugin for Codex, published from the [warpdotdev/codex-warp](https://github.com/warpdotdev/codex-warp) plugin marketplace.
When Warp detects a Codex session without the plugin, it shows an install chip in the terminal. Click the chip to install the plugin, then restart Codex. Warp shows an update chip the same way when a newer plugin version is required.
To install the plugin yourself, add the marketplace and the plugin:
```bash
codex plugin marketplace add warpdotdev/codex-warp
codex plugin add warp@codex-warp
```
Restart Codex to activate the plugin. To update it later, upgrade the marketplace and reinstall the plugin:
```bash
codex plugin marketplace upgrade codex-warp
codex plugin add warp@codex-warp
```
Note
If you point `codex-warp` at a local (non-Git) marketplace source, Warp leaves that override alone and doesn’t offer plugin updates for it.
## Supported Warp features
[Section titled “Supported Warp features”](#supported-warp-features)
Codex supports Warp’s full set of agent integration features:
* **Agent notifications** - Receive in-app and desktop alerts when Codex needs your attention. Requires the Warp plugin for Codex (see [Setting up notifications](#setting-up-notifications)).
* **Rich input editor** - Press `Ctrl-G` to open an expanded input editor for composing longer prompts.
* **Code review** - Send inline review comments directly to the agent from Warp’s code review panel.
* **Attach code as context** - Select code and send it to the agent as context.
* **Vertical tabs with agent metadata** - Monitor Codex sessions with status indicators in Warp’s tab bar.
* **Tab Configs** - Save and restore Codex session configurations.
* **[Remote Control](/agents/cli-agents/remote-control/)** - Publish your Codex session so you can monitor and steer it from another device.
## Related pages
[Section titled “Related pages”](#related-pages)
* [How to set up Codex CLI](/guides/external-tools/how-to-set-up-codex-cli/) — step-by-step setup guide
* [Codex in Warp](https://www.warp.dev/agents/codex) — product overview
* [Third-party CLI agents overview](/agents/cli-agents/overview/) — supported CLI agent integrations
* [Codex with the Automation Platform](/platform/harnesses/codex/) — Codex as a cloud harness
* [Claude Code](/agents/cli-agents/claude-code/) — Claude Code in Warp
* [OpenCode](/agents/cli-agents/opencode/) — OpenCode in Warp
# OpenCode in Warp
Canonical page: [/agents/cli-agents/opencode/](https://docs.warp.dev/agents/cli-agents/opencode/)
> Set up OpenCode in Warp with notification support, rich input, code review, and more.
OpenCode is an open-source terminal-based coding agent. It connects to multiple LLM providers and supports tool use, file editing, and command execution from your terminal. For full documentation, see the [OpenCode docs](https://opencode.ai/docs).
Warp auto-detects OpenCode when you run it, giving you access to rich input controls, code review, agent notifications, and other integrated features. For a product overview, see [OpenCode in Warp](https://www.warp.dev/agents/opencode).
For installation, authentication, project configuration, and productivity tips, see the [How to set up OpenCode](/guides/external-tools/how-to-set-up-opencode/) guide.
## Setting up notifications
[Section titled “Setting up notifications”](#setting-up-notifications)
Warp supports agent notifications for OpenCode through a plugin. Once installed, Warp surfaces in-app and desktop alerts when OpenCode needs your input.
To set up the plugin, add `"@warp-dot-dev/opencode-warp"` to the `plugin` array in your `opencode.jsonc` configuration file (or `opencode.json` if you use plain JSON):
```json
{
"plugin": ["@warp-dot-dev/opencode-warp"]
}
```
If the plugin isn’t installed, Warp displays an installation chip in the terminal when you run OpenCode, with setup steps you can follow directly.
For plugin source and updates, see the [opencode-warp GitHub repository](https://github.com/warpdotdev/opencode-warp).
## Supported Warp features
[Section titled “Supported Warp features”](#supported-warp-features)
OpenCode supports Warp’s full set of agent integration features:
* **Agent notifications** - Receive in-app and desktop alerts when OpenCode needs your attention. The notification UI displays your current git branch alongside agent status.
* **Rich input editor** - Press `Ctrl-G` to open an expanded input editor for composing longer prompts.
* **Code review** - Send inline review comments directly to the agent from Warp’s code review panel.
* **Attach code as context** - Select code and send it to the agent as context.
* **Vertical tabs with agent metadata** - Monitor OpenCode sessions with status indicators in Warp’s tab bar.
* **Tab Configs** - Save and restore OpenCode session configurations.
* **[Remote Control](/agents/cli-agents/remote-control/)** - Publish your OpenCode session so you can monitor and steer it from another device.
## Related pages
[Section titled “Related pages”](#related-pages)
* [How to set up OpenCode](/guides/external-tools/how-to-set-up-opencode/) — step-by-step setup guide
* [OpenCode in Warp](https://www.warp.dev/agents/opencode) — product overview
* [Third-party CLI agents overview](/agents/cli-agents/overview/)
* [Claude Code](/agents/cli-agents/claude-code/)
* [Codex](/agents/cli-agents/codex/)
# Third-party CLI agents overview
Canonical page: [/agents/cli-agents/overview/](https://docs.warp.dev/agents/cli-agents/overview/)
> Warp provides first-class support for third-party CLI coding agents with a rich input editor, notifications, code review, and more.
Warp auto-detects supported CLI agents and enhances them with IDE-level features — a rich input editor, agent notifications, inline code review, [Remote Control](/agents/cli-agents/remote-control/), and more. Run your preferred coding agent inside Warp and get a better experience out of the box.
This feature set is also known as **universal agent support**.
Looking for Warp’s own CLI instead? The [Warp Agent CLI](/agents/cli/) runs the Warp Agent itself in any terminal. This page covers running third-party coding agents inside the Warp app.
Note
Claude Code and Codex are also supported as harnesses in the Automation Platform for [multi-agent orchestration](/platform/orchestration/). See [Harnesses in the Automation Platform](/platform/harnesses/).
## Supported agents
[Section titled “Supported agents”](#supported-agents)
Warp currently supports the following CLI coding agents:
* [**Claude Code**](/agents/cli-agents/claude-code/) — Anthropic’s CLI coding agent
* [**OpenAI Codex**](/agents/cli-agents/codex/) — OpenAI’s CLI coding agent
* [**OpenCode**](/agents/cli-agents/opencode/) — Open-source CLI coding agent
* **Amp** — Sourcegraph’s CLI coding agent
* **Auggie** — Augment Code’s CLI coding agent
* **Copilot CLI** — GitHub’s CLI coding agent
* **Cursor CLI** — Cursor’s CLI coding agent
* **Gemini CLI** — Google’s CLI coding agent
* **Droid** — Factory’s CLI coding agent
* **Pi** — Open-source CLI coding agent
* **Goose** — Block’s CLI coding agent
* **Antigravity** — the Antigravity CLI coding agent (invoked with `agy`)
* **Hermes** — Nous Research’s CLI coding agent
* **Mistral Vibe** — Mistral’s CLI coding agent
* **Grok Build** — xAI’s CLI coding agent (invoked with `grok`)
When you launch a supported agent inside Warp, the **agent toolbelt** appears automatically, giving you quick access to Warp’s enhanced features.
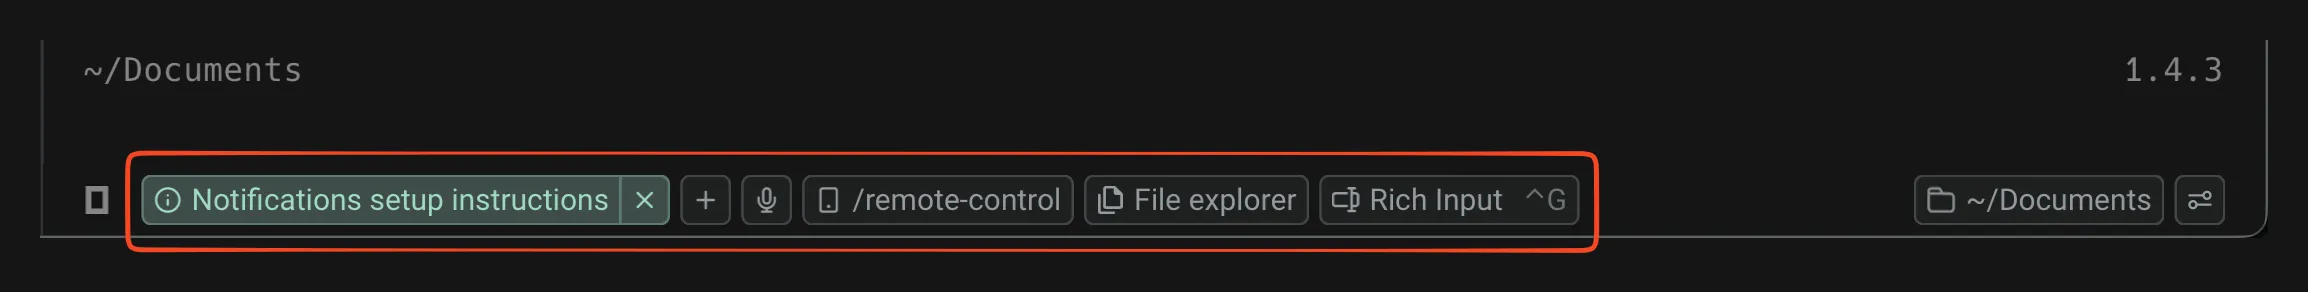
The agent toolbelt for CLI agents.
## Feature support
[Section titled “Feature support”](#feature-support)
Not every feature is available for every agent. The table below shows current support.
| Feature | Claude Code | Codex | OpenCode | Amp | Auggie | Copilot CLI | Cursor | Gemini CLI | Droid | Pi |
| ------------------------------------- | ----------- | ----- | -------- | --- | ------ | ----------- | ------ | ---------- | ----- | -- |
| Rich input editor (`Ctrl-G`) | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Agent notifications | ✓ | ✓ | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ | ✗ |
| Code review comments | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Attach code as context | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Vertical tabs + metadata | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Tab Configs | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Remote Control | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
**Goose**, **Antigravity** (`agy`), **Hermes**, **Mistral Vibe**, and **Grok Build** (`grok`) are also recognized. They get the same enhanced features as the agents above — rich input editor, code review comments, attach code as context, vertical tabs and metadata, Tab Configs, and Remote Control — but don’t support agent notifications yet.
Note
Agent notifications require a one-time setup. Claude Code and OpenCode use a Warp notification plugin. Codex uses a native config change. See the individual agent pages for setup instructions. Amp, Auggie, Copilot CLI, Cursor, Gemini CLI, Droid, Pi, Goose, Antigravity, Hermes, Mistral Vibe, and Grok Build don’t support notifications yet.
## Customizing the toolbelt
[Section titled “Customizing the toolbelt”](#customizing-the-toolbelt)
The chips and buttons on the CLI agent toolbelt can be reordered, hidden, or moved between the left and right sides. Your layout is saved and persists across app restarts.
In the Warp app, open the **Edit CLI agent toolbelt** modal in one of two ways:
* Right-click the input area while a supported CLI coding agent is running and select **Edit CLI agent toolbelt**.
* Go to **Settings** > **Agents** > **Third party CLI agents**, then click the **Toolbar layout** preview.
## Getting started
[Section titled “Getting started”](#getting-started)
Run a supported agent inside Warp — that’s it. Warp detects the agent automatically and activates the agent toolbelt with all available features.
For **agent notifications**, each agent requires a one-time setup — either a notification plugin or a config change. See the individual agent pages for instructions.
Note
If you don’t see the agent toolbelt, make sure you’re on the latest version of Warp.
***
## Related pages
[Section titled “Related pages”](#related-pages)
* [Remote Control](/agents/cli-agents/remote-control/) — publish a CLI agent session to monitor and steer it from another device
* [Cloud handoff and orchestration](/agents/cli/cloud-and-orchestration/) — hand off a Warp Agent CLI conversation to a cloud agent, or run multi-agent orchestration from the terminal
* [Agent Notifications](/agents/capabilities/agent-notifications/)
* [How to run multiple AI coding agents](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/) — run CLI agents in parallel with worktrees and cloud fan-out
* [Tabs](/terminal/windows/tabs/)
* [Tab Configs](/terminal/windows/tab-configs/)
# Remote Control
Canonical page: [/agents/cli-agents/remote-control/](https://docs.warp.dev/agents/cli-agents/remote-control/)
> Publish any third-party agent session to the cloud so you can monitor progress, steer the agent, and check in from your phone or another computer.
Remote Control lets you publish a running third-party agent session — such as Claude Code, Codex, or OpenCode — to the cloud with a single click. Once published, you can monitor progress, review output, and steer the agent from your phone, a web browser, or another computer without staying at the original machine. See [Third-party CLI agents](/agents/cli-agents/overview/) for the full list of supported agents.
This is especially useful for long-running agent tasks. Start a coding agent, publish the session, and check back whenever you want.

Note
Remote Control is built on top of [Agent Session Sharing](/agents/local-agents/session-sharing/). It uses the same underlying infrastructure to publish sessions and generate shareable links.
## Key capabilities
[Section titled “Key capabilities”](#key-capabilities)
* **One-click publish** - Click the `/remote-control` chip in the agent utility bar to publish instantly. The shareable link is copied to your clipboard automatically.
* **Monitor from anywhere** - Check on agent progress from a phone, tablet, or another computer — no install required for web viewers
* **Steer remotely** - Send input, approve commands, or redirect the agent without being at your original machine
* **Team access** - Share the link with teammates so they can observe or collaborate on the session
* **Persistent cloud access** - The session stays in sync while it’s active. New agent output and terminal activity appear for all viewers in real time. Syncing stops when you close or stop publishing the session.
## How it works
[Section titled “How it works”](#how-it-works)
When you publish a session through Remote Control, Warp uploads the session state to the cloud and generates a shareable link. The link stays live and in sync — any new agent output, tool use, or terminal activity appears for all connected viewers in real time. You control who can view and who can steer the agent.
Remote Control differs from standard [Agent Session Sharing](/agents/local-agents/session-sharing/) in its intent: Session Sharing is designed for live collaborative work (pair-programming, interactive debugging), while Remote Control is designed for async monitoring and steering when you’re away from your machine.
## Publishing a session
[Section titled “Publishing a session”](#publishing-a-session)
1. Start or resume a third-party agent session in Warp (for example, Claude Code or Codex).
2. Click the **`/remote-control`** chip in the agent utility bar. Warp publishes the session to the cloud and copies the shareable link to your clipboard.
The /remote-control chip in the agent utility bar.
3. A **Sharing link copied** toast notification confirms the link is on your clipboard, and the pane’s status icon changes to a red broadcast indicator to show that publishing is active.
4. Open the link on another device, or share it with a teammate.
To stop publishing, click the **Stop sharing** button in the agent utility bar. The status icon returns to its normal state, confirming the session is no longer accessible remotely.
## Accessing a remote session
[Section titled “Accessing a remote session”](#accessing-a-remote-session)
Published sessions are accessible from:
* **Web browser** - Open the shared link in any browser. No app install required.
* **Warp desktop app** - Paste the link into Warp on a different machine for the full desktop experience
* **Mobile** - Open the link on your phone or tablet browser to check on progress while away from your desk
The web experience mirrors the desktop view, showing complete agent activity including thinking steps, tool use, and terminal output.
## Permissions
[Section titled “Permissions”](#permissions)
When you publish a session, you control access:
* **View access** - Anyone with the link can watch the session, see agent output, and review terminal activity
* **Edit access** - You can grant viewers permission to send input, approve commands, or redirect the agent
Only you (the publisher) can revoke access or stop publishing the session.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Agent Session Sharing](/agents/local-agents/session-sharing/)
* [Third-party CLI agents](/agents/cli-agents/overview/)
* [Viewing Cloud Agent Runs](/platform/viewing-cloud-agent-runs/)
* [Handoff between local and cloud agents](/platform/handoff/) - Move work off your laptop into a cloud agent run when you need longer-running or unattended execution.
* [How to run multiple AI coding agents](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/) - Run parallel CLI agents locally, then monitor or fan work out further.
# Rich input editor
Canonical page: [/agents/cli-agents/rich-input/](https://docs.warp.dev/agents/cli-agents/rich-input/)
> Warp's rich input editor gives you IDE-style editing, voice input, context attachment, and slash commands for any supported CLI coding agent.
Warp’s rich input editor lets you write prompts for any CLI coding agent with the same editing experience you’d expect from an IDE — mouse support, context attachment, voice, and more. Press `Ctrl-G` (configurable) or click the **Rich Input** button in the agent utility bar to open it.

## Key capabilities
[Section titled “Key capabilities”](#key-capabilities)
* **IDE-style editing** - Click, select, and navigate your prompt with your mouse. Copy, cut, paste, undo, and word-level navigation all work. Write multi-line prompts with line breaks and soft wrapping. Vim keybindings are also supported. See [Modern text editing](/terminal/editor/) for the full list of shortcuts.
* **Rich context with @mentions** - Reference files, folders, and code symbols with `@` mentions. Attach images for visual context. Search for specific symbols directly from the editor. See [Agent Context](/agents/local-agents/agent-context/) for details.
* **Voice input** - Dictate prompts instead of typing. See [Voice](/agents/local-agents/interacting-with-agents/voice/) for details.
* **Slash commands and skills** - Access saved `/prompts`, `/skills`, and [Warp Drive](/knowledge-and-collaboration/warp-drive/) content with `/`. The editor shows skills specific to the running agent’s provider (e.g., Claude-specific skills when running Claude Code). See [Slash Commands](/agents/capabilities/slash-commands/) for details.
* **Agent toolbar** - Browse files, view code changes, and manage the agent session from the toolbar.
## How to open
[Section titled “How to open”](#how-to-open)
There are two ways to open the rich input editor:
1. **Keyboard shortcut** - Press `Ctrl-G` (configurable) while a supported agent is running in the active pane.
2. **Rich Input button** - Click the **Rich Input** button in the agent utility bar at the bottom of the pane.
The Rich Input button in the agent utility bar.
The rich input editor also auto-opens when an agent resumes from a blocked state (for example, after you approve a command). This requires the agent’s plugin to be supported and installed. Toggle **Auto show/hide based on agent status** in [Rich input settings](#rich-input-settings) to control this behavior.
When the rich input editor is active, Warp hides the cursor inside the CLI agent and moves focus to the editor input. Submit your prompt from here and it goes directly to the running agent.
The rich input editor.
## Rich input settings
[Section titled “Rich input settings”](#rich-input-settings)
In the Warp app, go to **Settings** > **Agents** > **Third party CLI agents** to configure the following:
* **Auto show/hide based on agent status** - Automatically open the rich input editor when the agent needs input, and hide it when the agent is working. Works with agents that have plugin support and the plugin installed (Claude Code and OpenCode).
* **Auto open on session start** - Automatically open the rich input editor when a CLI agent session starts.
* **Auto dismiss after submission** - Close the editor after you send a prompt.
* **Keyboard shortcut** - The default shortcut is `Ctrl-G`. Customize this in **Settings** > **Keyboard shortcuts**.
* **Disable the Rich Input button** - Right-click the agent utility bar and remove the **Rich Input** chip, or disable the footer entirely in **Settings** > **Agents** > **Third party CLI agents**.
Rich input settings in Warp.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Third-party CLI agents overview](/agents/cli-agents/overview/)
* [Remote Control](/agents/cli-agents/remote-control/)
* [Voice](/agents/local-agents/interacting-with-agents/voice/)
* [Slash Commands](/agents/capabilities/slash-commands/)
* [Agent Context](/agents/local-agents/agent-context/)
# Agent conversations in the Warp Agent CLI
Canonical page: [/agents/cli/agent-conversations/](https://docs.warp.dev/agents/cli/agent-conversations/)
> Read, manage, and resume agent conversations in the Warp Agent CLI, including streamed responses, tool calls, file diffs, plans, and task lists.
When you send the agent a prompt in the Warp Agent CLI, the conversation appears as a scrollable transcript directly in your terminal. Responses stream in as they’re generated, and everything the agent does renders inline: tool calls, file diffs, questions, task lists, and plans. Conversations persist as you work. You can start a new conversation, browse history, compact context, and [resume after exiting](#resuming-conversations).
## The conversation transcript
[Section titled “The conversation transcript”](#the-conversation-transcript)
The agent’s response streams into the transcript below your prompt as it’s generated. Press `Ctrl+C` once to stop a response that’s still in progress.
Responses render as formatted Markdown, including syntax-highlighted code blocks and tables. Be aware of a few terminal-specific caveats: Mermaid diagrams appear as their source in a code block, images show their alt text instead of rendering inline, and very long code blocks are truncated to keep the transcript responsive.
## Tool calls
[Section titled “Tool calls”](#tool-calls)
Every tool call the agent makes appears inline in the transcript, in the order it happens. Most render as a one-line status row with a state glyph and a label describing the action, like “reading a file” or “searching your codebase”.
Some tool calls render richer, interactive content:
* **[Shell commands](/agents/cli/input-and-shell-commands/#shell-mode)** - Commands run in your session, with output streamed into the transcript.
* **[File edits](#code-diffs)** - Expandable diffs with per-file headers.
* **[Questions](#agent-questions)** - Interactive option prompts.
* **[Plans](#planning)** - Inline plan documents.
When a tool call needs your approval before it runs, an approval card appears in place of the input. See [permissions in the CLI](/agents/cli/permissions-and-profiles/) to learn how approvals work.
## Code diffs
[Section titled “Code diffs”](#code-diffs)
When the agent edits files, the edit renders as a diff in the transcript:
* **Per-file sections** - Each edited file gets its own header showing the action taken and the lines added or removed.
* **Multi-file edits** - Each file’s section nests, indented, under one collapsible summary header (for example, `Edited 3 files`).
Diffs are fully expanded while the agent waits for your approval, then collapse to their headers once the edits are applied. Press `E` while the approval card is active to expand or collapse all diffs at once.
The CLI renders diffs inline rather than in a separate editor. For how agent-generated changes work in the Warp app, including refining a diff in natural language, see [Agent code diffs and review](/agents/local-agents/code-diffs/).
## Thinking blocks
[Section titled “Thinking blocks”](#thinking-blocks)
For models that expose their reasoning, the agent’s thinking streams into a collapsible section with the header `Thinking...`, which collapses to a single `Thought for` row once it finishes.
## Agent questions
[Section titled “Agent questions”](#agent-questions)
When the agent needs a decision from you mid-task, it asks a question with an interactive option list that temporarily replaces the input. Use the arrow keys to navigate between options, or press an option’s number on your keyboard to select it. **Other…** accepts a free-form answer when the listed options don’t fit.
Options the agent suggests as the best fit are labeled `(recommended)`. For multi-select questions, chosen options are marked with a check mark so you can select more than one. When the agent asks several questions at once, the card advances through them.
To control whether the agent pauses to ask questions, see [Agent questions](/agents/local-agents/interacting-with-agents/agent-questions/).
## Task lists
[Section titled “Task lists”](#task-lists)
For multi-step work, the agent tracks its progress with a task list rendered directly in the transcript under a `≡ Tasks` header. Each task row starts with a status glyph:
* `◌` - Pending
* `●` - In progress
* `✓` - Completed
Canceled tasks appear struck through. As the agent finishes tasks, compact confirmation rows (e.g., `✓ Completed (2/5)`) track progress without repeating the whole list.
Task lists in the CLI reflect the same agent behavior as in the Warp app. Learn more about [how task lists work](/agents/capabilities/task-lists/).
## Planning
[Section titled “Planning”](#planning)
To have the agent first research and produce a plan before making changes, use the `/plan` slash command followed by a description of your task. You can also ask for a plan in natural language.
The plan renders inline in the transcript as a formatted document with its own header row showing the plan’s status. An `Updated plan` entry appears when the agent revises it. Press `Ctrl+Shift+P` to expand or collapse the latest plan.
Planning in the CLI follows the same workflow as the Warp app. See [Planning](/agents/capabilities/planning/) to learn how to create, review, and execute plans.
## Selecting and copying output
[Section titled “Selecting and copying output”](#selecting-and-copying-output)
Select text anywhere in the transcript by clicking and dragging with the mouse. Releasing the mouse button copies the selection automatically.
To copy an entire conversation as Markdown, use the `/export-to-clipboard` slash command, or use `/export-to-file` to save it to a file.
Note
In local sessions, the CLI writes directly to your system clipboard. Over SSH, it copies through your terminal using OSC 52 escape sequences (including from inside tmux), so the text lands on your local clipboard. Terminals that disable OSC 52 may ignore the copy.
## Managing conversations
[Section titled “Managing conversations”](#managing-conversations)
The CLI saves every agent conversation as you work, so closing your terminal won’t lose your progress.
### Conversation persistence
[Section titled “Conversation persistence”](#conversation-persistence)
The CLI shows one conversation at a time. Opening a past conversation replaces the current transcript, and the previous one remains available in history. You can’t switch conversations while the current conversation is responding or a command is running. Finish or stop it with `Ctrl+C` first.
Conversations sync to your Warp account, so the same history is available in the Warp app and on your other devices. See [Cloud-synced conversations](/agents/local-agents/cloud-conversations/) for details about syncing, restoring, and sharing work.
### Starting a new conversation
[Section titled “Starting a new conversation”](#starting-a-new-conversation)
Use any of these slash commands to clear the transcript and start a fresh conversation:
* `/new`
* `/agent`
* `/clear`
Each command accepts an optional prompt. For example, `/new write tests for the parser` starts a new conversation and immediately sends that prompt to the agent. To keep the history but reduce its size instead, use [`/compact`](#compacting-context).
For guidance on when to start fresh rather than follow up, see [Interacting with agents](/agents/local-agents/interacting-with-agents/).
### Conversation history
[Section titled “Conversation history”](#conversation-history)
To browse and reopen past conversations, you can open the conversation menu in two ways:
* **`/conversations`** - Run the slash command from the input.
* **`←`** - Press the left arrow key when the input is empty and the cursor is at the start.
The menu lists your Warp Agent conversations, including conversations started in the Warp app and completed cloud agent runs tied to your account. Start typing to filter the list by title.
Caution
If the CLI can’t load conversation data from Warp’s servers, the menu shows conversations from your local device only and displays a warning. Conversations from other devices reappear once the connection recovers.
To continue a cloud agent run from the CLI, or to hand the current conversation off to a cloud agent, see [cloud handoff and orchestration](/agents/cli/cloud-and-orchestration/).
### Resuming conversations
[Section titled “Resuming conversations”](#resuming-conversations)
There are two ways to pick a past conversation back up:
* **The [conversation menu](#conversation-history)** `(recommended)` - From a running session, press `←` or run `/conversations`, then filter to the conversation you want.
* **`warp --resume`** - Reopens a specific conversation from your shell as the CLI starts, without going through the menu.
When you exit the CLI with a non-empty conversation, it prints the `--resume` command for that conversation:
```bash
To continue this conversation, run:
warp --resume YOUR_CONVERSATION_TOKEN
```
`YOUR_CONVERSATION_TOKEN` is a conversation identifier generated by Warp. For the complete list of command-line flags, see the [CLI reference](/agents/cli/reference/).
### Compacting context
[Section titled “Compacting context”](#compacting-context)
Long conversations eventually fill the model’s [context window](/agents/local-agents/interacting-with-agents/#context-window-management), which can degrade response quality. The `/compact` command frees up context by asking the agent to summarize the conversation history so far and carry only the summary forward.
* **`/compact`** - Summarizes the conversation history with default instructions.
* **`/compact `** - Adds custom summarization instructions. For example, `/compact keep the API design decisions` tells the agent what to preserve in the summary.
After compaction, a collapsed **Conversation summary** block appears in the transcript, and the conversation keeps working normally with the summary standing in for the compacted history.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Permissions and profiles](/agents/cli/permissions-and-profiles/) - Approve, reject, or auto-approve the agent’s tool calls.
* [Input and shell commands](/agents/cli/input-and-shell-commands/) - How commands the agent (or you) run appear in the transcript.
* [Cloud handoff and orchestration](/agents/cli/cloud-and-orchestration/) - Hand off conversations to cloud agents and resume cloud runs.
* [Warp Agent CLI reference](/agents/cli/reference/) - Command-line flags, slash commands, and keyboard shortcuts.
* [Planning](/agents/capabilities/planning/) - The full planning workflow.
* [Task lists](/agents/capabilities/task-lists/) - How agents create and update task lists.
* [Agent code diffs and review](/agents/local-agents/code-diffs/) - Reviewing and refining agent-generated changes.
* [Cloud-synced conversations](/agents/local-agents/cloud-conversations/) - How conversations sync, restore, and share across devices.
# Cloud handoff and orchestration in the Warp Agent CLI
Canonical page: [/agents/cli/cloud-and-orchestration/](https://docs.warp.dev/agents/cli/cloud-and-orchestration/)
> Hand off Warp Agent CLI conversations to cloud agents, resume cloud runs, and run multi-agent orchestration from your terminal.
The Warp Agent CLI connects your terminal sessions to the Automation Platform. You can hand off a local conversation to a cloud agent, pick a finished cloud run back up in your terminal, and coordinate multiple agents working in parallel, all without leaving the CLI.
## Hand off to a cloud agent
[Section titled “Hand off to a cloud agent”](#hand-off-to-a-cloud-agent)
Handoff promotes your Warp Agent CLI conversation into a cloud agent run. Use it when a task outgrows your machine: long-running work you don’t want to keep your laptop awake for, or work you want to check on later from another device. The [Handoff overview](/platform/handoff/) explains the feature across all Warp surfaces. This section covers the CLI flow.
The cloud agent receives the same context as a handoff from the Warp app:
* **Conversation history** - Warp forks the conversation, so the cloud agent sees the full transcript and your local conversation stays untouched.
* **Workspace changes** - Warp snapshots your uncommitted repository changes, including untracked files, and applies them in the cloud run.
* **Pending input** - The optional follow-up prompt and any images attached to the input move to the cloud run.
See [what carries over](/platform/handoff/#what-carries-over) for the full behavior, and [Handoff from local to cloud](/platform/handoff/local-to-cloud/) for prerequisites.
### Hand off a conversation
[Section titled “Hand off a conversation”](#hand-off-a-conversation)
1. In an active conversation, run `/handoff`, or `/handoff ` to give the cloud agent a follow-up prompt. The **Hand off to cloud** card replaces the input area while your transcript stays visible.
2. The card suggests your most recent environment (preferring one that contains the current repository) and preselects your conversation’s current model if it can run in the cloud. If the model is incompatible, it’s flagged so you can choose another before continuing.
3. To open the searchable environment and model selectors, press `Ctrl+E`.
4. From the card summary, press `Enter` to hand off. The card shows progress, then reports that the cloud run was created along with a link to the run.
Press `Ctrl+C` at any point before confirming to cancel the handoff. Your prompt and attachments return to the input.
From the created card:
* **`Enter`** - Opens the cloud run in your browser.
* **`C`** - Continues the conversation locally. The card collapses into a transcript banner with the run link, and the input reopens.
* **`N`** - Starts a new conversation.
Note
If you don’t have a cloud environment yet, the card prompts you to create one: `Enter` opens the [Environments page](https://oz.warp.dev/environments) in the Oz web app, and `R` refreshes the list after you create one.
Handoff needs the conversation in a state it can fork. You can’t hand off while a command is still running, or while the conversation has child agents that are in progress or blocked. Cancel the command or let the children finish first. Handing off an orchestrator forks only its own conversation. The orchestration and its child agents stay local.
## Resume cloud conversations
[Section titled “Resume cloud conversations”](#resume-cloud-conversations)
There are two ways to pick up a cloud agent’s work:
* **In the browser** - Open the run in the Oz web app to review its transcript and changes, steer it, or continue the conversation there. [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/) covers that flow.
* **In the CLI** - Pull a finished cloud run into your terminal. It appears in the conversation history alongside local conversations. Press `←` in an empty input, or run `/conversations`, to open the conversation list, then select the cloud run. Your next prompt continues the conversation locally.
Resuming in the CLI has two constraints:
* **The run must be finished** - Cloud runs that are still in progress or blocked can’t be opened in the CLI.
* **Warp Agent runs only** - Conversations that ran with a different harness, such as Claude Code or Codex, can’t be opened in the CLI.
You can also open a conversation directly at startup with `warp --resume `. See [managing conversations in the CLI](/agents/cli/agent-conversations/#managing-conversations) to learn more about conversation history and resume details.
## Multi-agent orchestration
[Section titled “Multi-agent orchestration”](#multi-agent-orchestration)
Orchestration lets one conversation spawn child agents that work in parallel, on your machine or in the cloud. The CLI runs the same parent/child model as the rest of the platform. [Multi-agent orchestration](/platform/orchestration/) covers the model, run states, and common patterns.
To start an orchestration, ask the agent to parallelize the work, for example “split this migration across three agents”.
You can also shape the configuration in your prompt. For example, ask for a specific model to manage token spend: keep the parent on a premium model while child agents handle research on a cheaper open-source model.
When the agent decides to spawn child agents, the CLI shows an approval card titled **Can I start additional agents for this task?** that summarizes the agents it wants to launch and the run-wide configuration.
By default, no child agents launch until you approve. The **Run orchestrated agents** permission in your profile controls this: **Always allow** skips the approval card, and **Never** blocks child agents entirely. See [Permissions and profiles](/agents/cli/permissions-and-profiles/).
From the approval card:
* **`Enter`** - Approves the request and launches the child agents.
* **`Ctrl+E`** - Edits the configuration first: where the agents run (on your machine or in the cloud) and which model they use. Cloud agents add pages for the harness, environment, and host, plus an API key page for harnesses that need one.
* **`Ctrl+C`** - Rejects the request.
After launch, a tab bar labeled **Agents:** appears above the session with one tab for the orchestrator and one tab per child agent. Messages between the parent and child agents appear in each agent’s transcript.

The Agents: tab bar with one child agent running and two finished.
* **Local child agents** - Each local child runs on your machine as its own session, starting in the parent’s working directory. Local children always run the Warp Agent.
* **Cloud child agents** - Each cloud child runs in a cloud [environment](/platform/environments/), and can run a different harness than the parent, such as Claude Code or Codex, chosen on the approval card’s harness page. A cloud child’s session shows the run’s live status and a link. Press `Enter` or click the link to open the run in the Oz web app. If a cloud child can’t start because GitHub authentication is required, its session shows the authentication link. Authenticate, then ask the agent to run the orchestration again.
Caution
Cloud child sessions in the CLI only show status. They don’t accept input. To send prompts to a cloud child or respond to its approvals, open the run in the Oz web app.
## Managing child agents
[Section titled “Managing child agents”](#managing-child-agents)
The **Agents:** tab bar is how you move around an orchestration.
* **Focus the tab bar** - Press `Shift+↑` from the input. The bar highlights the active conversation.
* **Switch agents** - `Tab` or `→` selects the next agent and `Shift+Tab` or `←` the previous one, wrapping across the orchestrator and all children. Switching keeps the bar focused so you can keep cycling.
* **Jump to an end** - `Shift+←` selects the first child and `Shift+→` selects the last one.
* **Return to the conversation** - `↓` moves focus back to the current session’s input. `Esc` jumps back to the orchestrator.
* **Use the mouse** - Tabs are clickable, and when there are more children than fit, arrows at the ends of the bar page through them without changing your selection.
Each agent keeps its own session. Transcript position, input drafts, and running work are all preserved while you view another agent, and child agents keep working in the background. Tabs reorder as statuses change, moving children that need attention, such as blocked ones, toward the front of the bar.
A focused local child behaves like a regular conversation. You can send it follow-up prompts and respond to its permission requests. If a child’s tab shows a blocked status, switch to that child to respond to its pending request.
### Kill a child agent
[Section titled “Kill a child agent”](#kill-a-child-agent)
`Ctrl+C` kills a child agent. It stops the child’s work, cancels the cloud run if the child is a cloud agent, and removes the child’s tab and conversation, returning you to the orchestrator.
* **From the tab bar** - With the tab bar focused and a child tab selected, a single `Ctrl+C` kills the selected child. The footer shows `Ctrl+C to kill sub-agent` as a reminder.
* **While viewing a child** - Press `Ctrl+C` twice. The first press arms a short confirmation window and the footer shows `ctrl-c again to kill child agent`. A second press within the window kills the child.
In the orchestrator’s own session, `Ctrl+C` keeps its usual behavior.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Handoff overview](/platform/handoff/) - Directions of handoff and what carries over in each.
* [Handoff from local to cloud](/platform/handoff/local-to-cloud/) - Prerequisites, the Warp app flow, and troubleshooting.
* [Multi-agent orchestration](/platform/orchestration/) - The parent/child model, run states, and orchestration patterns.
* [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/) - Open, inspect, and continue cloud runs in the Oz web app.
* [Agent conversations in the CLI](/agents/cli/agent-conversations/#managing-conversations) - Conversation history, `/conversations`, and `--resume`.
* [Environments](/platform/environments/) - Configure the repos, image, and setup commands cloud agents run with.
# Customizing the Warp Agent CLI
Canonical page: [/agents/cli/configuration/](https://docs.warp.dev/agents/cli/configuration/)
> Configure Warp Agent CLI themes, the statusline, and the start screen, and give the agent context from project rules, skills, and MCP servers.
The Warp Agent CLI keeps its configuration in a plain TOML settings file on your machine. You can change settings by editing the file directly, by running slash commands like `/theme` and `/statusline`, or by asking the agent to update a setting for you.
Beyond the CLI’s own settings, this page also covers the agent’s context, which includes the project rules, skills, and MCP servers the agent picks up as you work.
## The settings file
[Section titled “The settings file”](#the-settings-file)
The CLI reads its settings from a `settings.toml` file:
* **macOS** - `~/.warp_cli/settings.toml`
* **Linux** - `~/.config/warp-terminal/cli/settings.toml` (respects `$XDG_CONFIG_HOME`)
* **Windows** - `%LOCALAPPDATA%\warp\Warp\config\cli\settings.toml`
The file is created the first time you change a setting, and you can also create it yourself. Settings use dotted TOML sections. For example:
settings.toml
```toml
[appearance]
theme = "dark"
```
Note
CLI settings are local to your machine and are never synced to the cloud. They are also independent from the Warp app’s settings: the app and the CLI keep separate settings files, so changing one never affects the other.
## Edit settings
[Section titled “Edit settings”](#edit-settings)
Change settings any of these ways:
### Edit the file directly
[Section titled “Edit the file directly”](#edit-the-file-directly)
Open the settings file in your editor and change values directly. The CLI watches the file while it’s running and reloads most values as you save, so edits take effect without a restart. Theme edits are the exception: they apply the next time you run `/theme` or restart the CLI. If a value is invalid, the CLI logs the problem and uses the default for that setting instead. If the file can’t be parsed at all, the CLI starts with default settings.
### Use slash commands
[Section titled “Use slash commands”](#use-slash-commands)
Commands like `/theme` and `/statusline` open interactive panels for specific settings and save your choice to the settings file automatically. See [Themes](#themes) and [Statusline](#statusline).
### Ask the agent
[Section titled “Ask the agent”](#ask-the-agent)
Describe the change to the agent in your CLI session, in plain language. The CLI ships with a bundled skill and a schema of every available setting, which the agent uses to find the right key, validate the value, and update the settings file for you. Try prompts like:
* “Switch my theme to light.”
* “Add the time to my [statusline](#statusline).”
* “What CLI settings can I change?”
The agent’s edits follow the same hot-reload behavior as editing the file directly (see [Edit the file directly](#edit-the-file-directly)). For the full list of built-in skills, see [Bundled skills](#bundled-skills).
## Themes
[Section titled “Themes”](#themes)
The CLI renders with a light or dark color theme. Set it with the `/theme` slash command:
* **`/theme auto`** - Matches the host terminal’s background (default).
* **`/theme light`** - Always uses the light theme.
* **`/theme dark`** - Always uses the dark theme.
Running `/theme` applies the change immediately and persists it across sessions as the `theme` key under `[appearance]` in the settings file.
In auto mode, detection runs at startup, so if you switch your terminal’s colors while the CLI is running, restart it or set a theme explicitly.
## Statusline
[Section titled “Statusline”](#statusline)
The statusline is the row below the CLI’s input box that shows session information at a glance. By default it shows the auto-approve indicator, the active model, the working directory, the Git branch, and the Git diff status inside a repository, plus the Vim mode indicator when Vim mode is on. You can enable any of these items:
The statusline with credit usage, context window usage, and task list chips enabled.
* **Auto-approve indicator** - A clickable `▶▶` toggle for auto-approve, highlighted when it’s on.
* **Vim mode indicator** - The active Vim mode (such as `NOR` or `INS`), shown only when Vim mode is enabled.
* **Model** - The active model. Click it to open the model picker.
* **Working directory** - The current working directory.
* **Git branch** - The current branch, when the directory is a Git repository.
* **Git branch status** - The branch, plus how far it is ahead of or behind its upstream (for example, `master • ↑1`). Enabling this replaces the plain Git branch chip, rather than adding a second one.
* **Git diff status** - Files changed, with line additions and deletions.
* **GitHub pull request** - The pull request for the current branch. Click it to open the PR on GitHub.
* **Credit usage** - Credits used by the current conversation. Click it to switch between credits and provider cost.
* **Context window usage** - How much of the model’s context window the conversation has used.
* **Agent to-do list** - The agent’s progress through its current task list.
You can also add the date, the time (12- or 24-hour), and a voice input control.
Items only appear when they have something to show. For example, the Git items appear only inside a repository. In shell mode, the statusline always leads with a shell mode label.
### Customizing the statusline
[Section titled “Customizing the statusline”](#customizing-the-statusline)
Choose which items appear and in what order:
1. Run `/statusline`. The **Configure statusline** panel opens with every available item.
2. Select an item and press `Enter` to toggle its visibility.
3. Press `←` and `→` to move the highlighted item earlier or later in the row.
4. Press `Esc` to save and close. Press `Ctrl+C` to cancel without saving.
Your choices are saved to the settings file, so the layout persists across sessions. To start over, run `/reset-statusline`, which restores the default items and ordering.
## Start screen
[Section titled “Start screen”](#start-screen)
The start screen appears when you launch the CLI, showing a rotating ASCII object alongside sections for your account, the changelog, project info, and MCP servers. Customize it with the `appearance.zero_state` settings:
* **`object`** - The rotating object. Keep the built-in one, or point the setting at your own ASCII art file (a path relative to the CLI settings directory). Changing the setting reloads the object. Edits to the linked file take effect after a restart.
* **`rotation_period_seconds`** - Seconds per full rotation, from 1 through 60.
* **`show_signed_in_user`, `show_changelog`, `show_project_info`, `show_mcp`, `show_animation`** - Toggle individual start-screen sections.
* **`freeze_animation_when_unfocused`** - Stop repainting the animation while your terminal window is unfocused, so an idle start screen doesn’t use CPU in the background. Off by default, and applied as soon as you save the setting.
The fastest way to change these is to [ask the agent](#ask-the-agent), for example “use my own ASCII art for the start screen object”.
## Project context and rules
[Section titled “Project context and rules”](#project-context-and-rules)
The CLI gives its agent the same layered context system as the Warp app, combining your working directory, project rules, skills, and MCP servers, all scoped to the directory you’re working in.
The agent works in your session’s current directory. When you `cd`, project rules and skills re-scope to the new directory automatically.
Within a project, the CLI picks up the same rule files as the Warp app:
* **Project rules** - `AGENTS.md` (or `WARP.md`) files in your repository apply automatically, starting from the repository root and your current directory. See [Rules](/agents/capabilities/rules/) for the file format, nested rules in subdirectories, and precedence.
* **Global rules** - A rule file at `~/.agents/AGENTS.md` applies across all projects on your machine.
Because rules and skills come from the same shared locations, a repository already configured for agents in the Warp app (or any tool that reads `AGENTS.md`) works in the CLI immediately.
## Skills
[Section titled “Skills”](#skills)
[Skills](/agents/capabilities/skills/) are reusable instruction sets the agent can invoke to perform specific tasks. The CLI discovers the same skills as the Warp app. Project skills come from your repository’s skill directories (e.g., `.agents/skills/`), and personal skills come from your home directory (e.g., `~/.agents/skills/`), scoped to your current working directory.
Run `/skills` to browse every skill in scope. Selecting a skill inserts `/skill-name` into the input so you can add extra instructions before running it. Any text after the skill name is passed along, either as [skill arguments](/agents/capabilities/skills/#skill-arguments) or as additional context for the agent. You can also invoke a skill directly by typing `/` followed by its name, for example `/deploy push the latest changes to staging`.
### Bundled skills
[Section titled “Bundled skills”](#bundled-skills)
The CLI ships with built-in skills that appear in the skills menu alongside your own:
* **`/modify-settings`** - Updates CLI settings using the bundled settings schema to find and edit the right key. See [Ask the agent](#ask-the-agent).
* **`/tui-migrate-setup`** - Sets up the CLI from an existing Warp app installation. The agent copies compatible settings and global MCP server definitions from the app, and asks for approval before changing anything. Credentials and OAuth state are never copied, so MCP servers that require authentication prompt you to re-authenticate. Rules and skills don’t need migration: the CLI and the Warp app both discover them from the same file locations (see [Project context and rules](#project-context-and-rules) and [Skills](#skills)).
## MCP servers
[Section titled “MCP servers”](#mcp-servers)
[MCP servers](/agents/capabilities/mcp/) extend the agent with external tools and data sources. The CLI keeps its own MCP server configuration, separate from the Warp app’s, so each can run its own set of servers.
Servers are defined in a JSON config file using the same `mcpServers` format as [file-based MCP servers](/agents/capabilities/mcp/#file-based-mcp-servers) in the Warp app (on macOS, the file is `~/.warp_cli/.mcp.json`). Edit the file to add or remove servers. The CLI picks up changes automatically. Configured servers start automatically once you’re logged in.
Note
The CLI reads MCP servers from its global config file only. Project-scoped MCP config files in repositories are not detected. To copy global server definitions from the Warp app, use the `/tui-migrate-setup` bundled skill.
### Managing servers with `/mcp`
[Section titled “Managing servers with /mcp”](#managing-servers-with-mcp)
Type `/mcp` to open the MCP management view. The header shows the path to the config file the CLI is reading.
Each configured server is listed with its transport (`stdio` or `HTTP/SSE`) and current status, including the number of tools a running server exposes.
Press `Enter` on a server to start, stop, or retry it depending on its state. Failed rows show the error message. Servers awaiting authentication reopen the OAuth page in your browser, and servers with saved credentials show a **Log out** row that clears them.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Rules](/agents/capabilities/rules/) - Full guide to project and global rules.
* [Skills](/agents/capabilities/skills/) - Authoring skills, skill arguments, and skill locations.
* [MCP servers](/agents/capabilities/mcp/) - Config format, server examples, and authentication.
* [Codebase Context](/agents/capabilities/codebase-context/) - Codebase indexing in the Warp app.
* [Warp Agent CLI reference](/agents/cli/reference/) - Command-line flags, slash commands, and keyboard shortcuts.
# Input and shell commands in the Warp Agent CLI
Canonical page: [/agents/cli/input-and-shell-commands/](https://docs.warp.dev/agents/cli/input-and-shell-commands/)
> Compose prompts, edit input, and run shell commands in the Warp Agent CLI, including menus, history, completions, images, voice, and interactive commands.
The Warp Agent CLI is a full terminal as well as an agent. Every session runs a real shell, so you can run commands in the same place you prompt the agent. The input is a multiline editor that combines readline-style editing with inline menus for slash commands, history, and completions, plus mouse support, image attachments, and voice input. For the complete list of flags, slash commands, and keyboard shortcuts, see the [Warp Agent CLI reference](/agents/cli/reference/).
## Editing basics
[Section titled “Editing basics”](#editing-basics)
The input is a multiline editor.
* **Insert a newline** - Press `Ctrl+J`, or `Shift+Enter` in terminals that support distinguishing it. `Alt+Enter` also works.
* **Edit with readline-style keys** - The editor supports familiar bindings such as `Ctrl+A` and `Ctrl+E` (start and end of line), `Ctrl+W` (delete the previous word), `Ctrl+K` and `Ctrl+U` (delete to the end or start of the line), `Ctrl+Y` (reinsert the last deleted text), and `Ctrl+Z` (undo).
* **Use macOS Command shortcuts** - When the Kitty keyboard protocol is enabled in your terminal, the editor supports Command-modified shortcuts such as `⌘+X` to cut and `⌘+Shift+←` or `⌘+Shift+→` to extend the selection.
The full editing and selection table is in the [keyboard shortcuts reference](/agents/cli/reference/#keyboard-shortcuts).
Note
Core `Ctrl` and `Alt` bindings are cross-platform. Shortcuts that use `Alt` require some macOS terminals’ Option-as-Alt (Meta) setting. Command-modified shortcuts require a terminal with the Kitty keyboard protocol enabled.
### Vim mode
[Section titled “Vim mode”](#vim-mode)
If you prefer modal editing, run `/vim-mode` to toggle Vim keybindings in the input. The setting persists across sessions. Turn on the [statusline](/agents/cli/configuration/#statusline) Vim mode item to see the active mode (such as `NOR` or `INS`) while you type.
## Slash commands
[Section titled “Slash commands”](#slash-commands)
Type `/` at the start of an empty input to open the slash command menu. Entries for toggles and pickers show their current state, for example `/theme (currently auto: Dark)` or `/auto-approve (currently off)`.
When a command takes an argument, the input shows a ghost-text argument hint after the full command name, for example `/theme `.
Your [skills](/agents/cli/configuration/#skills) also appear in the slash command menu, so you can invoke a skill by typing `/` followed by its name.
The [slash commands reference](/agents/cli/reference/#slash-commands) lists every command.
## Input history
[Section titled “Input history”](#input-history)
Press `↑` with the cursor on the first row of the input to open the history menu.
* **What’s listed** - In Agent Mode, the menu combines your previous prompts and shell commands in one list, with commands marked by a `!` prefix. In [shell mode](#shell-mode), the menu lists commands only.
* **Preview** - Moving the selection previews each entry in the input and switches the input to the matching mode: recalled commands run as shell commands, and recalled prompts go to the agent.
* **Submit** - `Enter` runs the selection immediately. It doesn’t insert it for editing.
* **Dismiss** - `Esc` restores what you had typed. Pressing `↓` past the newest entry does the same.
## Tab completions
[Section titled “Tab completions”](#tab-completions)
In [shell mode](#shell-mode), press `Tab` to complete the command you’re typing, including file and directory paths.
* If exactly one completion matches, the CLI applies it immediately.
* If several completions match, the CLI inserts the longest shared prefix and opens a completion menu. Press `Tab` again to cycle through the suggestions.
## Selection and clipboard
[Section titled “Selection and clipboard”](#selection-and-clipboard)
* **Highlight to copy** - Finishing a mouse selection in the input or the [conversation transcript](/agents/cli/agent-conversations/) automatically copies it.
* **Keyboard selection** - Extend the selection with `Shift` plus the arrow keys, or select everything with `Ctrl+Shift+A`. Copy with `Ctrl+Shift+C` and cut with `Ctrl+X`.
* **Paste** - Press `Ctrl+V` or `Ctrl+Shift+V` (also `Alt+V` on Windows). Your terminal’s own paste shortcut works as well.
* **Click controls** - Interactive elements such as the **Voice** footer entry and the attachment bar controls respond to clicks.
Note
Copying works over SSH: on remote sessions the CLI writes the clipboard through the OSC 52 escape sequence (including tmux passthrough), so your local clipboard receives the text when your terminal supports OSC 52.
## Attach images
[Section titled “Attach images”](#attach-images)
Attach images to a prompt so the agent can analyze them:
* **Paste an image** - Copy an image to your clipboard and press `Ctrl+V`.
* **Paste or drop a file path** - Paste the path to an image file, or drag the file onto your terminal window to insert its path. Absolute paths, paths relative to the working directory, and `~` paths all resolve.
Supported formats are PNG, JPEG, GIF, and WebP. Attaching an image locks the input to Agent Mode, since images are sent to the agent rather than the shell.
Attached images appear in an attachment bar above the input. Press `Tab` to focus the bar, `Backspace` to remove the selected attachment, and `Esc` to return to the input.
## Voice input
[Section titled “Voice input”](#voice-input)
Dictate prompts instead of typing them:
Caution
Voice input isn’t currently included in the official Linux build. Linux support is planned.
1. Start listening with `Ctrl+S`, the `/voice` slash command, or by clicking **Voice** in the footer. The footer shows **Listening** while recording.
2. Press `Enter`, or click the footer entry again, to stop recording. The transcribed text lands in the input so you can review and edit it before submitting.
Press `Esc` while transcription is in progress to cancel it. `/voice` clears the input before recording, and `Ctrl+S` keeps what you’ve already typed.
Voice input in the CLI uses the same transcription service as the Warp app. See [voice input for agents](/agents/local-agents/interacting-with-agents/voice/) for microphone setup, privacy, and usage limits.
## Keyboard hints and the shortcuts menu
[Section titled “Keyboard hints and the shortcuts menu”](#keyboard-hints-and-the-shortcuts-menu)
The CLI shows its shortcuts in context, so you rarely need to memorize them:
* **Placeholder hints** - An empty input shows the key triggers for the current mode.
* **Shortcuts menu** - Type `?` in an empty input to open a shortcuts overview. Its contents adapt to what you’re doing: Agent Mode lists the menu triggers and input history, shell mode shows how to return to Agent Mode, and extra sections appear during multi-agent sessions or agent-controlled terminal use. Press `Esc`, or start typing, to close it.
## Shell mode
[Section titled “Shell mode”](#shell-mode)
The input is agent-first: by default, pressing `Enter` sends your text to the agent as a prompt. Use shell mode to run a command instead:
1. Press `!` at the start of the input. The prompt marker changes from `>` to `!`, and the statusline below the input shows **Shell mode**.
2. Run a command. The input returns to Agent Mode afterward.
To leave shell mode without running a command, press `Esc`, or press `Backspace` at the start of the input. Any text you typed stays in the input.
In shell mode, press `Tab` to complete commands and paths. See [Tab completions](#tab-completions).
Note
Running a shell command cancels the agent’s in-progress response, if there is one.
## Natural language detection
[Section titled “Natural language detection”](#natural-language-detection)
Out of the box, the CLI never guesses what your input is: everything goes to the agent unless you enter shell mode. To type commands directly without the `!` prefix, turn on natural language detection:
* **Toggle detection** - Run `/natural-language-detection` to turn detection on or off. The statusline confirms the change, and the setting persists across sessions.
* **Automatic classification** - With detection on, the CLI classifies your input as you type. When the input looks like a shell command (for example, `git status`), the input switches to shell mode, and `Enter` runs it as a command. Everything else is sent to the agent.
* **Ambiguous input** - Short or ambiguous input stays in Agent Mode, and a single word switches to shell mode only when it matches a command available in your shell.
The prompt marker and statusline always show the current mode before you press `Enter`. If detection classifies input differently than you intended, press `Esc` to switch back to Agent Mode, or press `!` at the start of the input to force shell mode.
## Long-running and interactive commands
[Section titled “Long-running and interactive commands”](#long-running-and-interactive-commands)
When a command keeps running, such as a dev server, a package install, or an interactive prompt, the CLI hands input over to it:
* **Input passthrough** - Keystrokes and pasted text are forwarded to the running process, so password requests, confirmation prompts, and other interactive programs work as they do in a plain terminal.
* **Type ahead** - If you start typing your next command before the current one finishes, the typed characters are carried into the input when the command completes, with the cursor at the end. This matches type-ahead behavior in shells like zsh and bash.
One command runs in the session at a time. If the terminal is already busy, for example while the agent is running a command of its own, submitting a shell command shows a notice in the statusline and keeps your text in the input.
## Full-screen terminal apps
[Section titled “Full-screen terminal apps”](#full-screen-terminal-apps)
Commands that switch the terminal to the alternate screen, such as `vim`, `htop`, or `less`, take over the whole CLI view:
* The app renders full-screen and receives keyboard, paste, scroll, and mouse input, so editors and other terminal UIs are fully usable inside the CLI.
* When the app exits, the transcript returns with your conversation intact.
## Stopping commands and exiting
[Section titled “Stopping commands and exiting”](#stopping-commands-and-exiting)
`Ctrl+C` performs one contextual action per press:
* **While a command is running** - `Ctrl+C` interrupts the running command, as in a plain terminal. It doesn’t exit the CLI.
* **While the agent is responding** - `Ctrl+C` cancels the in-progress response. Text in the input is preserved.
* **At an idle prompt** - `Ctrl+C` clears the input if it has text.
After a press at the prompt, the statusline shows `ctrl-c again to exit` for about one second. Press `Ctrl+C` a second time within that window to exit the CLI. This works even while the agent is responding. While a shell command is running, `Ctrl+C` keeps interrupting the command instead.
There are two other ways to exit:
* **`Ctrl+D`** - Exits immediately when the input is empty.
* **`/exit`** - Exits from the slash command menu.
When you exit, the CLI prints a command you can use to pick the conversation back up later. See [Managing conversations](/agents/cli/agent-conversations/#managing-conversations) for resuming and switching conversations.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Warp Agent CLI reference](/agents/cli/reference/) - Flags, environment variables, slash commands, and keyboard shortcuts.
* [Agent conversations in the Warp Agent CLI](/agents/cli/agent-conversations/) - The transcript, tool calls, diffs, and managing conversations.
# Models and usage in the Warp Agent CLI
Canonical page: [/agents/cli/models-and-usage/](https://docs.warp.dev/agents/cli/models-and-usage/)
> Choose models in the Warp Agent CLI, bring your own API key, and track credit usage and per-response cost.
The Warp Agent CLI gives you the same model options as the Warp app. You can pick the model that powers your conversations, bring your own provider API keys, route requests through custom model routers, and see what every response costs as you work.
## Choosing a model
[Section titled “Choosing a model”](#choosing-a-model)
Run `/model` to open the model picker. You can also click the model name in the [statusline](/agents/cli/configuration/#statusline) to open the same picker.
Models that your plan or your team’s settings don’t allow appear disabled in the picker.
Your choice is saved as the base model of your active profile, so it persists across sessions. See [permissions and profiles](/agents/cli/permissions-and-profiles/) for how profiles work in the CLI. For the full list of supported models and to learn more about how Warp’s Auto models pick for you, see [Model choice](/agents/inference/model-choice/).
## Bring your own API key
[Section titled “Bring your own API key”](#bring-your-own-api-key)
The CLI supports [Bring Your Own API Key (BYOK)](/agents/inference/bring-your-own-api-key/) for OpenAI, Anthropic, and Google models, and can connect an [X Premium or SuperGrok subscription](/agents/inference/grok-subscription/) for Grok models. When you select a model covered by one of your keys, requests are billed through your provider account and don’t consume your Warp [credits](/support-and-community/plans-and-billing/credits/).
Run `/api-keys` to open the key management menu. It lists each provider with its connection state, plus a Warp credit fallback toggle:
* **Set a key** - Press `Enter` on OpenAI, Anthropic, or Google and enter the key. Input is masked, so the key never appears in your transcript or shell history, and it’s saved to your device’s secure storage. Warp does not store provider keys on its servers.
* **Replace or clear a key** - On a connected provider, `Enter` loads the stored key (still masked) for editing, and saving an empty field clears it. `Ctrl+X` clears the highlighted provider’s key from the list.
* **Connect X Premium or SuperGrok** - Press `Enter` on the subscription row and the CLI opens your browser to sign in to your xAI account. `Ctrl+X` disconnects it. Running `/connect-grok` jumps straight to this row and starts the sign-in.
* **Warp credit fallback** - Press `Enter` to toggle whether a request that fails through your key is retried with Warp credits. See [failover and fallback behavior](/agents/inference/bring-your-own-api-key/#failover-and-fallback-behavior).
You can also store or clear keys outside a session with the `--set-provider-api-key` and `--clear-provider-api-key` flags. See the [Warp Agent CLI reference](/agents/cli/reference/#command-line-flags). X Premium/SuperGrok connections can only be managed from inside a session, with `/api-keys` or `/connect-grok`.
Note
Warp’s built-in Auto models always consume Warp credits, even with BYOK configured. To bill through your own account, select a specific provider model, or use a [custom router](/agents/inference/custom-routers/#using-your-own-api-keys-byok) whose targets your keys cover. See [BYOK usage and billing behavior](/agents/inference/bring-your-own-api-key/#byok-usage-and-billing-behavior) for the full rules.
## Custom model routing
[Section titled “Custom model routing”](#custom-model-routing)
[Custom routers](/agents/inference/custom-routers/) appear in the `/model` picker alongside individual models. Select one and each prompt resolves to a concrete model using the routing logic you defined.
The CLI loads the same router definitions as the Warp app. These are YAML files in `~/.warp/custom_model_routers/`, plus any team-synced routers your admin shares. [Authoring a router as a file](/agents/inference/custom-routers/#author-a-router-as-a-file) documents the file format.
## Usage and cost
[Section titled “Usage and cost”](#usage-and-cost)
The CLI shows usage at three levels:
* **Account usage** - Run `/usage` to open a read-only panel with your plan, credit balances and consumption, and links to manage billing or upgrade. Press `Esc` to close it. Unlike `/cost`, this is account-level, not conversation-level.
* **Conversation total** - Once a conversation has reported any usage, the [statusline](/agents/cli/configuration/#statusline) shows its accumulated credits (e.g., `2.5 credits`). Click the entry to switch between credits and the equivalent provider cost in dollars. Your choice persists across sessions.
* **Per-response details** - Run `/cost` to toggle a summary row under the latest response showing how long it took and how many credits it spent (e.g., `12s • 1.2 credits`). The summary appears once the response finishes.
Credits are Warp’s unit of usage for agent requests. For what credits cover and how plans differ, see [Credits](/support-and-community/plans-and-billing/credits/).
## Related pages
[Section titled “Related pages”](#related-pages)
* [Model choice](/agents/inference/model-choice/) - Supported models and how automatic model selection works.
* [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) - How BYOK works, key storage, and billing behavior.
* [SuperGrok subscription](/agents/inference/grok-subscription/) - Use Grok models through your xAI account.
* [Custom routers](/agents/inference/custom-routers/) - Define routing logic that picks a model per task.
* [Warp Agent CLI reference](/agents/cli/reference/) - Flags and slash commands, including the API key commands.
# Oz CLI reference
Canonical page: [/agents/cli/oz-cli/](https://docs.warp.dev/agents/cli/oz-cli/)
> Use the Oz CLI to run, configure, and manage agents from the terminal.
Caution
The Oz CLI (the `oz` binary, which previously shipped as `warp-cli`) is a supported legacy interface. Existing users do not need to change their workflows. For new multi-stage development workflows, use [Warp Factories](/factories/). Warp will publish guidance before any support change.
The Oz CLI is the command-line tool for running and managing Warp’s cloud agents from any terminal, script, or CI pipeline. Use it to start agents locally or in the cloud, connect MCP servers, configure integrations, and authenticate without requiring the Warp desktop app.
## What is the CLI?
[Section titled “What is the CLI?”](#what-is-the-cli)
The Oz CLI is the command-line tool that lets you run [Cloud Agents](/platform/) from anywhere, including terminals, scripts, automated systems, or services.
It’s the standard runtime entry point that turns a **prompt** plus **configuration** into an **executable agent task** that runs on either a **Warp-hosted or [self-hosted](/factories/self-hosting/) runner**.
With the Oz CLI, you can:
* Run agents locally for development and debugging
* Run agents on remote machines
* Connect agents to MCP servers like GitHub and Linear
* Configure integrations that connect agents to Slack, Linear, and other trigger surfaces
## Installing the CLI
[Section titled “Installing the CLI”](#installing-the-cli)
You can install the Oz CLI as part of the Warp desktop app, or as a standalone package.
### Bundled with Warp
[Section titled “Bundled with Warp”](#bundled-with-warp)
The Oz CLI is automatically distributed with the Warp desktop app and can be used right away in Warp. To make the CLI globally available, add it to your `PATH`.
* macOS
To add the Oz CLI to your `PATH`:
1. Open the [Command Palette](/terminal/command-palette/) (`Cmd+P`)
2. In the search field, find and select the **Install Oz CLI Command** action.
Note
**Note:** Administrator permissions are required to install the CLI into `/usr/local/bin` .
* Windows
In the Warp installer, select **Add Warp to PATH**. If you are installing for all users, this will put the CLI on the system path. Otherwise, the CLI is only added to the path for your account.
* Linux
To run the Oz CLI on Linux, use the same command that you’d use to start Warp normally. If you installed Warp via a package manager, it should already be on the system `PATH`.
### Standalone package
[Section titled “Standalone package”](#standalone-package)
Warp provides standalone packages for the CLI on macOS and Linux, without the Warp app.
* macOS
On macOS, we recommend that you install and update the standalone CLI with [Homebrew](https://brew.sh/), using the [`warpdotdev/warp` tap](https://github.com/warpdotdev/homebrew-warp):
```sh
$ brew tap warpdotdev/warp
$ brew update
$ brew install --cask oz
```
If you’re using Warp Preview, install the preview version of the CLI instead:
```sh
brew install --cask oz@preview
```
***
You can also download the CLI directly from these URLs:
* [Apple Silicon](https://app.warp.dev/download/cli?os=macos\&package=tar\&arch=aarch64)
* [Intel](https://app.warp.dev/download/cli?os=macos\&package=tar\&arch=x86_64)
* [Apple Silicon, Warp Preview](https://app.warp.dev/download/cli?os=macos\&channel=preview\&package=tar\&arch=aarch64)
* [Intel, Warp Preview](https://app.warp.dev/download/cli?os=macos\&channel=preview\&package=tar\&arch=x86_64)
Note
**Note:** These builds do not auto-update.
* Linux
On Linux, we recommend that you install and update the standalone CLI through your distribution’s package manager. We support `apt`, `yum`, and `pacman`.
1. Add the Warp package repository for your distribution (see the [installation instructions](/getting-started/quickstart/installation-and-setup/)).
2. Install either the stable or Preview package (replace `apt` with `yum` or `pacman` as needed):
```sh
# Stable
sudo apt install oz-stable
# Preview (beta/early-access)
sudo apt install oz-preview
```
Note
**Note:** The package name (`oz-stable`) differs from the CLI command executable (`oz`). After installation, use the CLI via `oz` commands.
***
You can also install the CLI by downloading a package directly. These installers automatically add the Warp repository, so future updates come through your package manager:
* x86-64: [`.deb`](https://app.warp.dev/download/cli?os=linux\&package=deb\&arch=x86_64), [`.rpm`](https://app.warp.dev/download/cli?os=linux\&package=rpm\&arch=x86_64), [pacman](https://app.warp.dev/download/cli?os=linux\&package=pacman\&arch=x86_64)
* aarch64: [`.deb`](https://app.warp.dev/download/cli?os=linux\&package=deb\&arch=aarch64), [`.rpm`](https://app.warp.dev/download/cli?os=linux\&package=rpm\&arch=aarch64), [pacman](https://app.warp.dev/download/cli?os=linux\&package=pacman\&arch=aarch64)
* Windows
A standalone CLI package is not currently available on Windows. To use the Oz CLI on Windows, install the Warp app, which bundles the CLI.
You can install Warp using [WinGet](https://learn.microsoft.com/en-us/windows/package-manager/winget/):
```powershell
winget install Warp.Warp
```
After installation, see [Bundled with Warp](#bundled-with-warp) for instructions on adding the CLI to your `PATH`.
## Running the CLI
[Section titled “Running the CLI”](#running-the-cli)
Regardless of your OS or installation method, the CLI command is `oz`. If you’re using [Warp Preview](/support-and-community/community/warp-preview-and-alpha-program/), use `oz-preview` instead.
## Logging in
[Section titled “Logging in”](#logging-in)
The Oz CLI supports two authentication methods, depending on where and how you’re running agents.
* **Interactive login —** best for local machines where you have Warp installed and can authenticate through a browser.
* **API keys** — best for automated or remote environments that need to authenticate without human interaction.
### Interactive login (local machines)
[Section titled “Interactive login (local machines)”](#interactive-login-local-machines)
Use interactive login when you’re working on a machine where you already use the Warp app, or when you can open a browser to complete authentication.
If you use the CLI on a host where you’re already signed in to Warp, it automatically reuses your existing credentials.
To authenticate interactively:
```bash
oz login
```
The CLI prints out a URL that you can open in any browser to login to Warp.
### Checking who you’re signed in as
[Section titled “Checking who you’re signed in as”](#checking-who-youre-signed-in-as)
Use `oz whoami` to print information about the currently authenticated principal:
```sh
oz whoami
```
The output includes your user or service account ID, display name, email, and team (when available). When the CLI is authenticated as a service account principal, that principal is a [cloud agent](/platform/agents/) on your team. For machine-readable output, set `--output-format json` or `--output-format text`.
```sh
# JSON output for scripts
oz whoami --output-format json
# Compact "type:id" output
oz whoami --output-format text
```
If `oz whoami` reports that it could not determine your user ID, your credentials are missing or invalid. Run `oz login` (or set `WARP_API_KEY`) and try again.
### Logging out
[Section titled “Logging out”](#logging-out)
Use `oz logout` to clear the CLI’s cached credentials on this machine:
```sh
oz logout
```
If you weren’t logged in, the command prints `You are not logged in.` and exits. After logging out, run `oz login` to authenticate again.
Note
`oz logout` only affects credentials stored by the CLI. API keys authenticated through `WARP_API_KEY` or `--api-key` are not affected — unset the environment variable or omit the flag to stop using them.
### API key authentication
[Section titled “API key authentication”](#api-key-authentication)
Use an API key when the environment must authenticate on its own, such as CI pipelines, headless servers, VMs, Codespaces, or containers. API keys let the CLI authenticate non-interactively.
For detailed instructions on creating, managing, and using API keys, see [API Keys](/agents/cli/oz-cli/api-keys/).
**Quickstart:**
```sh
$ export WARP_API_KEY="wk-xxx..."
$ oz agent run --prompt "analyze this codebase"
```
***
## Running agents
[Section titled “Running agents”](#running-agents)
The Oz CLI offers two ways to run agents, depending on where you want the work to happen:
**Use `oz agent run` when:**
* You’re developing locally and want immediate feedback
* You need the agent to work with files in your current directory
* You want to inspect and modify the agent’s work in real time
* You’re debugging or iterating on prompts
**Use `oz agent run-cloud` when:**
* You want the agent to run on a remote machine or standardized environment
* You’re triggering agent work from CI/CD or automated systems
* You need the agent to run independently of your local session
* You’re delegating work that doesn’t require your immediate attention
### Running locally: \`oz agent run\`
[Section titled “Running locally: \`oz agent run\`”](#running-locally-oz-agent-run)
To start an agent, use the `oz agent run` subcommand. You’ll need to specify a prompt and, optionally, the [MCP servers](/agents/capabilities/mcp/) and [agent profile](/agents/capabilities/agent-profiles-permissions/) to use.
```sh
oz agent run --prompt "set up a new Rust crate named warp-cli"
```
**Key flags:**
* `--cwd ` (`-C`) — run from a different directory.
* `--name ` (`-n`) — label the run for grouping and traceability.
* `--share` — share the session with teammates (see [Collaboration](/agents/cli/oz-cli/#collaboration)).
* `--profile ` — use a specific agent profile (see [Using Agent Profiles](/agents/cli/oz-cli/#using-agent-profiles)).
* `--model ` — override the default model (see [Model Choice](/agents/inference/model-choice/)).
* `--skill ` — use a skill as the base prompt (see [Using Skills](/agents/cli/oz-cli/#using-skills)).
* `--mcp ` — start one or more MCP servers before execution (UUID, JSON file path, or inline JSON). Can be repeated.
* `--environment ` (`-e`) — run in a specific cloud environment.
* `--file ` (`-f`) — load run configuration from a YAML or JSON file.
The agent will automatically carry out the task you gave it, printing out tool calls and responses as it works.
By default, the agent runs in your current working directory. To run from a different directory, use the `-C/--cwd` flag.
### Running agents remotely: \`oz agent run-cloud\`
[Section titled “Running agents remotely: \`oz agent run-cloud\`”](#running-agents-remotely-oz-agent-run-cloud)
Cloud runs dispatch tasks to remote environments. Use cloud runs for:
* Background processing
* Standardized team configurations
* Remote execution on servers you don’t directly access
```sh
oz agent run-cloud \
--environment \
--name "Repo summary" \
--prompt "Summarize this repo and list the top 5 risky areas" \
--open
```
**Key flags**
* `--environment ` (`-e`) — select the environment to run in.
* `--no-environment` — run without an environment (not recommended).
* `--open` — view the agent’s session in Warp once it’s available.
* `--name ` (`-n`) — label the run for grouping and traceability (see [Naming runs](/agents/cli/oz-cli/#naming-runs) below).
* `--title ` — set the title shown for the run and its conversation (see [Titling runs](/agents/cli/oz-cli/#titling-runs) below).
* `--parent-run-id <RUN_ID>` — start the run as an orchestration child of an existing run (see [Starting a run as an orchestration child](/agents/cli/oz-cli/#starting-a-run-as-an-orchestration-child) below).
* `--agent <UID>` — run as a saved [named agent](/platform/agents/), applying its configuration (skills, secrets, base model, and default environment) and attributing credit usage to it (see [Managing named agents](/agents/cli/oz-cli/#managing-named-agents) below).
* `--mcp <SPEC>` — start one or more MCP servers before execution (UUID, JSON file path, or inline JSON). Can be repeated.
* `--model <MODEL_ID>` — override the default model.
* `--skill <SPEC>` — use a skill from the environment’s repository as the base prompt (see [Using Skills](/agents/cli/oz-cli/#using-skills)).
* `--host <WORKER_ID>` — run on a specific self-hosted worker instead of Warp-hosted infrastructure.
* `--attach <PATH>` — attach a file to the agent query. You can attach up to 25 files, with a maximum size of 10 MB per file. For images in interactive local or cloud conversations, see [Images as Context](/agents/local-agents/agent-context/images-as-context/).
* `--computer-use` / `--no-computer-use` — enable or disable [Computer Use](/agents/capabilities/computer-use/) for this run.
* `--harness <HARNESS>` — choose the [execution harness](/platform/harnesses/) for the run: `oz` (default, the Warp Agent), `claude` (Claude Code), or `codex` (Codex). `claude-code` is accepted as an alias for `claude`. See [harness identifiers](/platform/harnesses/#harness-identifiers).
* `--claude-auth-secret <NAME>` — name of the [Warp-managed secret](/platform/secrets/) that authenticates the Claude Code harness. Use with `--harness claude` or the `--harness claude-code` alias. See [Third-party cloud agent authentication](/platform/harnesses/authentication/).
* `--codex-auth-secret <NAME>` — name of the [Warp-managed secret](/platform/secrets/) that authenticates the Codex harness. Only valid with `--harness codex`. See [Third-party cloud agent authentication](/platform/harnesses/authentication/).
* `--file <PATH>` (`-f`) — load run configuration from a YAML or JSON file.
To run a third-party harness, first store the provider credential as a Warp-managed secret, then pass it with the matching flag:
```sh
# Run Claude Code as a cloud agent, authenticating with a stored Anthropic secret
oz agent run-cloud \
--environment <ENVIRONMENT_ID> \
--harness claude \
--claude-auth-secret ANTHROPIC_API_KEY \
--prompt "Review the latest PR and suggest fixes"
```
**Key differences from `run`**
* No `--cwd` — the environment determines the working directory.
* No `--share` — sharing options are on `run`, not `run-cloud`.
* No `--profile` — cloud runs do not use agent profiles.
#### Naming runs
[Section titled “Naming runs”](#naming-runs)
The `--name` flag assigns a config name to the run. Use it to group related runs under a shared label so you can filter, search, and track them later.
**How names work:**
* **Skill-based runs** — When you run an agent from a [skill](/agents/capabilities/skills/), the name is automatically set to the skill name. You don’t need to pass `--name` explicitly.
* **Custom runs** — When you build your own automation (via the CLI, API, or SDK), set `--name` to a consistent value that describes the workflow’s intent.
**Why naming matters:**
When your team runs many agents across schedules, integrations, and ad-hoc triggers, `name` lets you answer questions like “how many distinct workflows are we running?” and “how often does this particular workflow run?” You can filter runs by name using the `name` query parameter on `GET /agent/runs` in the [Warp Platform API](/factories/api-and-sdk/).
**Examples:**
```sh
# Name a recurring workflow for easy tracking
oz agent run-cloud \
--environment <ENVIRONMENT_ID> \
--name "nightly-dependency-check" \
--prompt "Check for outdated dependencies and open a PR with updates"
# Skill-based runs are named automatically
oz agent run-cloud \
--environment <ENVIRONMENT_ID> \
--skill "myorg/backend:code-review" \
--prompt "review the latest PR"
```
#### Titling runs
[Section titled “Titling runs”](#titling-runs)
The `--title` flag sets the title shown for the run and its conversation in Warp and the [Oz web app](/platform/oz-web-app/). Use it when the auto-generated title isn’t descriptive enough:
```sh
oz agent run-cloud \
--environment <ENVIRONMENT_ID> \
--title "Upgrade Postgres driver to 5.2" \
--prompt "Upgrade the Postgres driver and fix any resulting build errors"
```
`--title` and `--name` do different things: `--name` sets the run’s config name, which groups related runs under a shared label, while `--title` labels this one run for humans reading it.
#### Starting a run as an orchestration child
[Section titled “Starting a run as an orchestration child”](#starting-a-run-as-an-orchestration-child)
The `--parent-run-id` flag attaches the new run to an existing run as an [orchestration](/platform/orchestration/multi-agent-runs/) child. The child inherits the parent’s lineage and scope, and it appears alongside the parent’s other children instead of as a standalone run:
```sh
oz agent run-cloud \
--environment <ENVIRONMENT_ID> \
--parent-run-id <PARENT_RUN_ID> \
--title "Backfill integration tests" \
--prompt "Add integration tests for the new endpoints"
```
Pass the run ID of the run doing the spawning. Omit the flag for ordinary standalone runs.
**When cloud runs fail**
* Verify your environment has the correct repository and context.
* Check that your profile allows the commands and MCP servers needed.
* Ensure environment variables are set in the environment, not your local shell.
#### Reusing saved prompts and Warp Drive objects
[Section titled “Reusing saved prompts and Warp Drive objects”](#reusing-saved-prompts-and-warp-drive-objects)
You can reuse saved prompts with `--saved-prompt`, and reference notebooks, workflows, and rules inline in any `--prompt` string. See [Referencing Warp Drive objects](/agents/cli/oz-cli/warp-drive/) for details.
#### Choosing an execution harness
[Section titled “Choosing an execution harness”](#choosing-an-execution-harness)
By default, cloud runs use Warp’s built-in `oz` harness. To delegate the run to a third-party coding agent, pass `--harness` with `claude` (Claude Code) or `codex`, along with the matching auth secret:
```sh
oz agent run-cloud \
--environment <ENVIRONMENT_ID> \
--harness claude \
--claude-auth-secret <SECRET_NAME> \
--prompt "review the latest PR"
```
Create the auth secret first with `oz secret create claude api-key <SECRET_NAME>` (or `oz secret create codex api-key <SECRET_NAME>` for Codex). See [Third-party cloud agent authentication](/platform/harnesses/authentication/) for the full setup.
## Using agent profiles
[Section titled “Using agent profiles”](#using-agent-profiles)
Agent profiles control what the agent can do, how it behaves, and where it can act. Use the `--profile` flag with `oz agent run` to apply a specific profile.
See [Agent profiles](/agents/cli/oz-cli/agent-profiles/) for how to find profile IDs and apply them.
## Using MCP servers
[Section titled “Using MCP servers”](#using-mcp-servers)
MCP servers connect agents to external systems like GitHub, Linear, or Sentry. Use the `--mcp` flag with any of three formats: a Warp MCP server UUID, inline JSON, or a path to a JSON config file.
See [MCP Servers](/agents/cli/oz-cli/mcp-servers/) for full details, including how to find UUIDs, combine multiple servers, and handle environment variables on remote machines.
## Using skills
[Section titled “Using skills”](#using-skills)
[Skills](/agents/capabilities/skills/) are reusable instruction sets that teach agents how to perform specific tasks. Use the `--skill` flag to run an agent from a skill stored in a repository.
See [Skills](/agents/cli/oz-cli/skills/) for supported spec formats and examples for both local and cloud agent runs.
## Collaboration
[Section titled “Collaboration”](#collaboration)
In addition to text-based output, the CLI can share the agent’s session for you to access on other devices or in a browser. To enable [Agent Session Sharing](/agents/local-agents/session-sharing/), use the `--share` flag.
By default, the session is only accessible to the user running the CLI, but you can also share with [Teams](/knowledge-and-collaboration/teams/) or other Warp users:
```sh
# Share the agent's session with yourself:
$ oz agent run --share --prompt "fix the compiler error"
# Give specific users view-only access to a session:
$ oz agent run --share firstuser@example.com --share otheruser@example.com --prompt "fix the compiler error"
# Let any user on your team edit the session:
$ oz agent run --share team:edit --prompt "fix the compiler error"
```
The `--share` flag can be repeated, and uses the following syntax:
* `--share user@email.com` or `--share user@email.com:view` — gives specified user read-only access to the session.
* `--share user@email.com:edit` — gives specified user `user@email.com` read/write access to the session.
* `--share team` or `--share team:view` — gives all members of your team read-only access to the session.
* `--share team:edit` — gives all members of your team read/write access to the session.
## Additional commands
[Section titled “Additional commands”](#additional-commands)
The following commands are available for managing and inspecting Warp resources.
### Managing named agents
[Section titled “Managing named agents”](#managing-named-agents)
[Named agents](/platform/agents/) are reusable agent configurations — a name, description, base prompt, skills, secrets, base model, and default environment — that you can run with `oz agent run-cloud --agent <UID>` and scope API keys to.
List the named agents on your team, optionally sorting by name or creation time:
```sh
oz agent list
oz agent list --sort-by created-at --sort-order desc
```
Show the full configuration for a single agent by its UID:
```sh
oz agent get <UID>
```
Create a named agent. Only `--name` is required; attach skills and secrets by repeating the flags:
```sh
oz agent create \
--name "release-notes" \
--description "Drafts release notes from merged PRs" \
--prompt "Draft concise release notes grouped by feature area." \
--skill "myorg/repo:release-notes" \
--secret GITHUB_TOKEN \
--base-model <MODEL_ID> \
--environment <ENVIRONMENT_ID>
```
Update an existing agent. Each attribute has an explicit add/remove flag so changes are unambiguous:
```sh
# Rename the agent and swap one of its skills
oz agent update <UID> --name "weekly-release-notes" \
--remove-skill "myorg/repo:old" --add-skill "myorg/repo:release-notes"
# Clear attributes entirely
oz agent update <UID> --remove-description --remove-all-secrets
```
Common `oz agent update` flags:
* `--name <NAME>` (`-n`) — rename the agent.
* `--description <TEXT>` / `--remove-description` — set or clear the description.
* `--prompt <TEXT>` / `--remove-prompt` — set or clear the base prompt applied to the agent’s runs.
* `--add-secret <NAME>` / `--remove-secret <NAME>` / `--remove-all-secrets` — manage attached secrets.
* `--add-skill <SKILL>` / `--remove-skill <SKILL>` / `--remove-all-skills` — manage attached skills.
* `--base-model <MODEL_ID>` / `--remove-base-model` — set or clear the base model.
* `--environment <ENVIRONMENT_ID>` (`-e`) / `--remove-environment` — set or clear the default cloud environment.
Delete a named agent by its UID:
```sh
oz agent delete <UID>
```
### `oz agent skills`
[Section titled “oz agent skills”](#oz-agent-skills)
List the agent skills discovered across your environments. Pass `--repo` (`-r`) to list skills from a specific GitHub repository instead:
```sh
oz agent skills
oz agent skills --repo owner/repo
```
### `oz run list` / `oz run get`
[Section titled “oz run list / oz run get”](#oz-run-list--oz-run-get)
List and inspect cloud agent runs:
```sh
# List recent runs (default: 10)
oz run list
oz run list --limit 20
# Get details for a specific run
oz run get <RUN_ID>
```
### Run conversations and messages
[Section titled “Run conversations and messages”](#run-conversations-and-messages)
Read an agent run’s transcript and exchange messages between runs — for example, between a parent orchestrator and its [child agents](/platform/orchestration/multi-agent-runs/).
Retrieve a conversation transcript by its ID:
```sh
oz run conversation get <CONVERSATION_ID>
```
List and read the messages in a run’s inbox:
```sh
# List inbox message headers
oz run message list <RUN_ID>
oz run message list <RUN_ID> --unread --since 2026-01-01T00:00:00Z --limit 100
# Read one message body
oz run message read <MESSAGE_ID>
# Stream new messages as they arrive (resume reconnects with --since-sequence)
oz run message watch <RUN_ID>
oz run message watch <RUN_ID> --since-sequence 42
```
Send a message from one run to one or more recipient runs, then mark it delivered once handled:
```sh
oz run message send \
--sender-run-id <RUN_ID> \
--to <RECIPIENT_RUN_ID> \
--subject "build status" \
--body "tests are green"
oz run message mark-delivered <MESSAGE_ID>
```
Repeat `--to` to fan a message out to multiple recipient runs.
### `oz model list`
[Section titled “oz model list”](#oz-model-list)
List all available models:
```sh
oz model list
```
### `oz environment image list`
[Section titled “oz environment image list”](#oz-environment-image-list)
List suggested base images for cloud environments:
```sh
oz environment image list
```
### `oz artifact get` / `oz artifact download`
[Section titled “oz artifact get / oz artifact download”](#oz-artifact-get--oz-artifact-download)
Inspect and retrieve files an agent produced during a run. See [Artifacts](/agents/cli/oz-cli/artifacts/) for details.
### `oz federate issue-token`
[Section titled “oz federate issue-token”](#oz-federate-issue-token)
Issue a short-lived OIDC identity token from inside a running agent to authenticate to cloud providers without long-lived credentials. See [Federated identity tokens](/agents/cli/oz-cli/federate/) for details.
***
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
For built-in CLI help commands and solutions to common errors — including authentication issues, agent failures, environment problems, and Docker image issues — see [Troubleshooting](/agents/cli/oz-cli/troubleshooting/).
# Agent profiles
Canonical page: [/agents/cli/oz-cli/agent-profiles/](https://docs.warp.dev/agents/cli/oz-cli/agent-profiles/)
> Use agent profiles with the Oz CLI to control what the agent can access, how it behaves, and where it can act.
Caution
The Oz CLI (the `oz` binary) is a supported legacy interface. Existing users do not need to change their workflows. For new multi-stage development workflows, use [Warp Factories](/factories/). Warp will publish guidance before any support change.
Agent profiles control what the agent can do, how it behaves, and where it can act when running from the Oz CLI. Create profiles in the Warp app to configure file access, command execution, MCP server usage, model selection, and directory permissions, then reference them by ID in CLI commands.
Agent profiles control three things:
* **What the agent can do** — file access, command execution, and MCP server usage
* **How the agent works** — model selection, autonomy level, and response style
* **Where the agent can act** — directory allowlists and denylists
You can create and configure agent profiles in the Warp app. For detailed instructions, see [Agent Profiles & Permissions](/agents/capabilities/agent-profiles-permissions/).
Agent profiles are automatically synced to each host where you have Warp installed, so you can use them remotely as well.
Note
**Tip:** For CLI usage, create a dedicated profile. The CLI will fail if the agent tries to execute a prohibited action, so make sure your profile allows the directories, commands, and MCP servers you plan to use.
Caution
The default profile for CLI usage is broadly permissive and gives the agent the ability to read and write files, apply code diffs, execute commands with a default denylist, and use MCP actions. Its profile MCP allowlist starts empty. Select run-scoped servers with `--mcp`, use a profile that allowlists installed servers, or configure an eligible file-based or global server. See [MCP servers](/agents/cli/oz-cli/mcp-servers/) for details.
## Using a profile with the CLI
[Section titled “Using a profile with the CLI”](#using-a-profile-with-the-cli)
1. Find the profile ID using `oz agent profile list`:
```sh
$ oz agent profile list
+--------------+------------------------+
| Name | ID |
+=======================================+
| Default | AnTb02PZfrkVC9l4V15eH1 |
|--------------+------------------------|
| Coding | CWhozDJPdPCsjJ1pSG0HCN |
|--------------+------------------------|
| Command Line | hV6n5dNm7ThQVlOiPF8DLS |
+--------------+------------------------+
```
2. Pass that ID using the `--profile` flag:
```sh
$ oz agent run --profile CWhozDJPdPCsjJ1pSG0HCN --prompt "update my CI pipeline to use nextest"
```
Note
The `--profile` flag is available on `oz agent run` only. Cloud runs (`oz agent run-cloud`) do not use agent profiles.
# API keys for the Oz CLI
Canonical page: [/agents/cli/oz-cli/api-keys/](https://docs.warp.dev/agents/cli/oz-cli/api-keys/)
> Create and manage API keys for authenticating the Oz CLI, cloud agents, and self-hosted workers.
Caution
The Oz CLI (the `oz` binary) is a supported legacy interface. Existing users do not need to change their workflows. For new multi-stage development workflows, use [Warp Factories](/factories/). Warp will publish guidance before any support change.
API keys let the Oz CLI, cloud agents, and self-hosted workers authenticate without human interaction. Use API keys for CI pipelines, headless servers, VMs, Codespaces, containers, and other automated environments.
## Personal vs. agent keys
[Section titled “Personal vs. agent keys”](#personal-vs-agent-keys)
Choose a key type based on what needs to authenticate:
* **Personal API keys** - Authenticate as you. Runs use your GitHub permissions, draw from your credit pool, and inherit your account’s [skills](/agents/capabilities/skills/). Use a personal key when the run should act on your behalf — for example, developer-triggered API automation, or the [Enterprise Analytics API](/enterprise/enterprise-features/analytics-api/), which only accepts personal keys.
* **Agent** API keys - Run as a [cloud agent](/platform/agents/) on your team. Use an agent key for scheduled jobs, integrations (Slack, Linear, GitHub Actions), SDK-triggered runs, and other automation that isn’t tied to a specific user. Billing and GitHub permissions are scoped to the team rather than to you.
For [self-hosting with an external orchestrator](/factories/self-hosting/external-orchestrators/), create an Agent key associated with the Default Service Account. This key lets the orchestrator create and run tasks without using a person’s identity, and it can authenticate a worker when one job performs both actions.
## Self-hosted worker API keys
[Section titled “Self-hosted worker API keys”](#self-hosted-worker-api-keys)
Self-hosted worker API keys authenticate managed `oz-agent-worker` daemons as your team. Use this key type with the [Docker](/factories/self-hosting/managed-docker/), [Kubernetes](/factories/self-hosting/managed-kubernetes/), [Direct](/factories/self-hosting/managed-direct/), or [Command](/factories/self-hosting/external-orchestrators/#using-the-command-backend) backend. You don’t need to select an agent when creating one.
## Creating an API key
[Section titled “Creating an API key”](#creating-an-api-key)
Create personal and agent keys in the [Oz web app](https://oz.warp.dev/settings) or the Warp app. Create self-hosted worker keys in the [Warp Factories web app](https://platform.warp.dev/settings).
### Creating a self-hosted worker API key
[Section titled “Creating a self-hosted worker API key”](#creating-a-self-hosted-worker-api-key)
1. Open the [Warp Factories web app user settings page](https://platform.warp.dev/settings).
2. In the API keys section, click **Generate new token**.
3. Under “Type,” select **Self-hosted worker**. The key is tied to your team and does not require an agent selection.
4. Enter a name for the key and choose when it expires.
5. Click **Create key**.
6. In the “Copy API key” dialog, copy the key and store it securely. The key is shown only once.
**Expected outcome:** The key appears in the API keys list with a **Team** badge and the expiration you selected.
### From the web app (recommended)
[Section titled “From the web app (recommended)”](#from-the-web-app-recommended)
1. Open the [Oz web app settings page](https://oz.warp.dev/settings).
2. In the API keys section, click **Generate new token**.
3. Choose the type:
* **Personal** — Tied to your individual Warp account.
* **Agent** — Runs as a cloud agent on your team. For an external self-hosting orchestrator, choose **Default Service Account** from the dropdown.
4. Enter a name for the key and choose an expiration (1 day, 30 days, 90 days, or never).
5. Click **Create key**.
6. Copy the raw API key and store it securely. **You won’t be able to see it again after closing the dialog.**
### From the Warp app
[Section titled “From the Warp app”](#from-the-warp-app)
1. In the Warp app, click your profile photo in the top-right corner, then click **Settings**.
2. In the sidebar, expand **Cloud platform** and click **API keys**.
3. In the API Keys section, click **+ Create API Key**.
4. Pick **Personal** for a personal key, or **Agent** / **Team** for an agent key tied to your team. (The toggle may still read **Team** in older versions of the desktop app.)
5. Name the key and choose an expiration (1 day, 30 days, 90 days, or never).
6. Click **Create key**.
7. Copy the raw API key and store it securely. **You won’t be able to see it again after closing the dialog.**
To create a self-hosted worker key, use the [Warp Factories web app flow](#creating-a-self-hosted-worker-api-key).
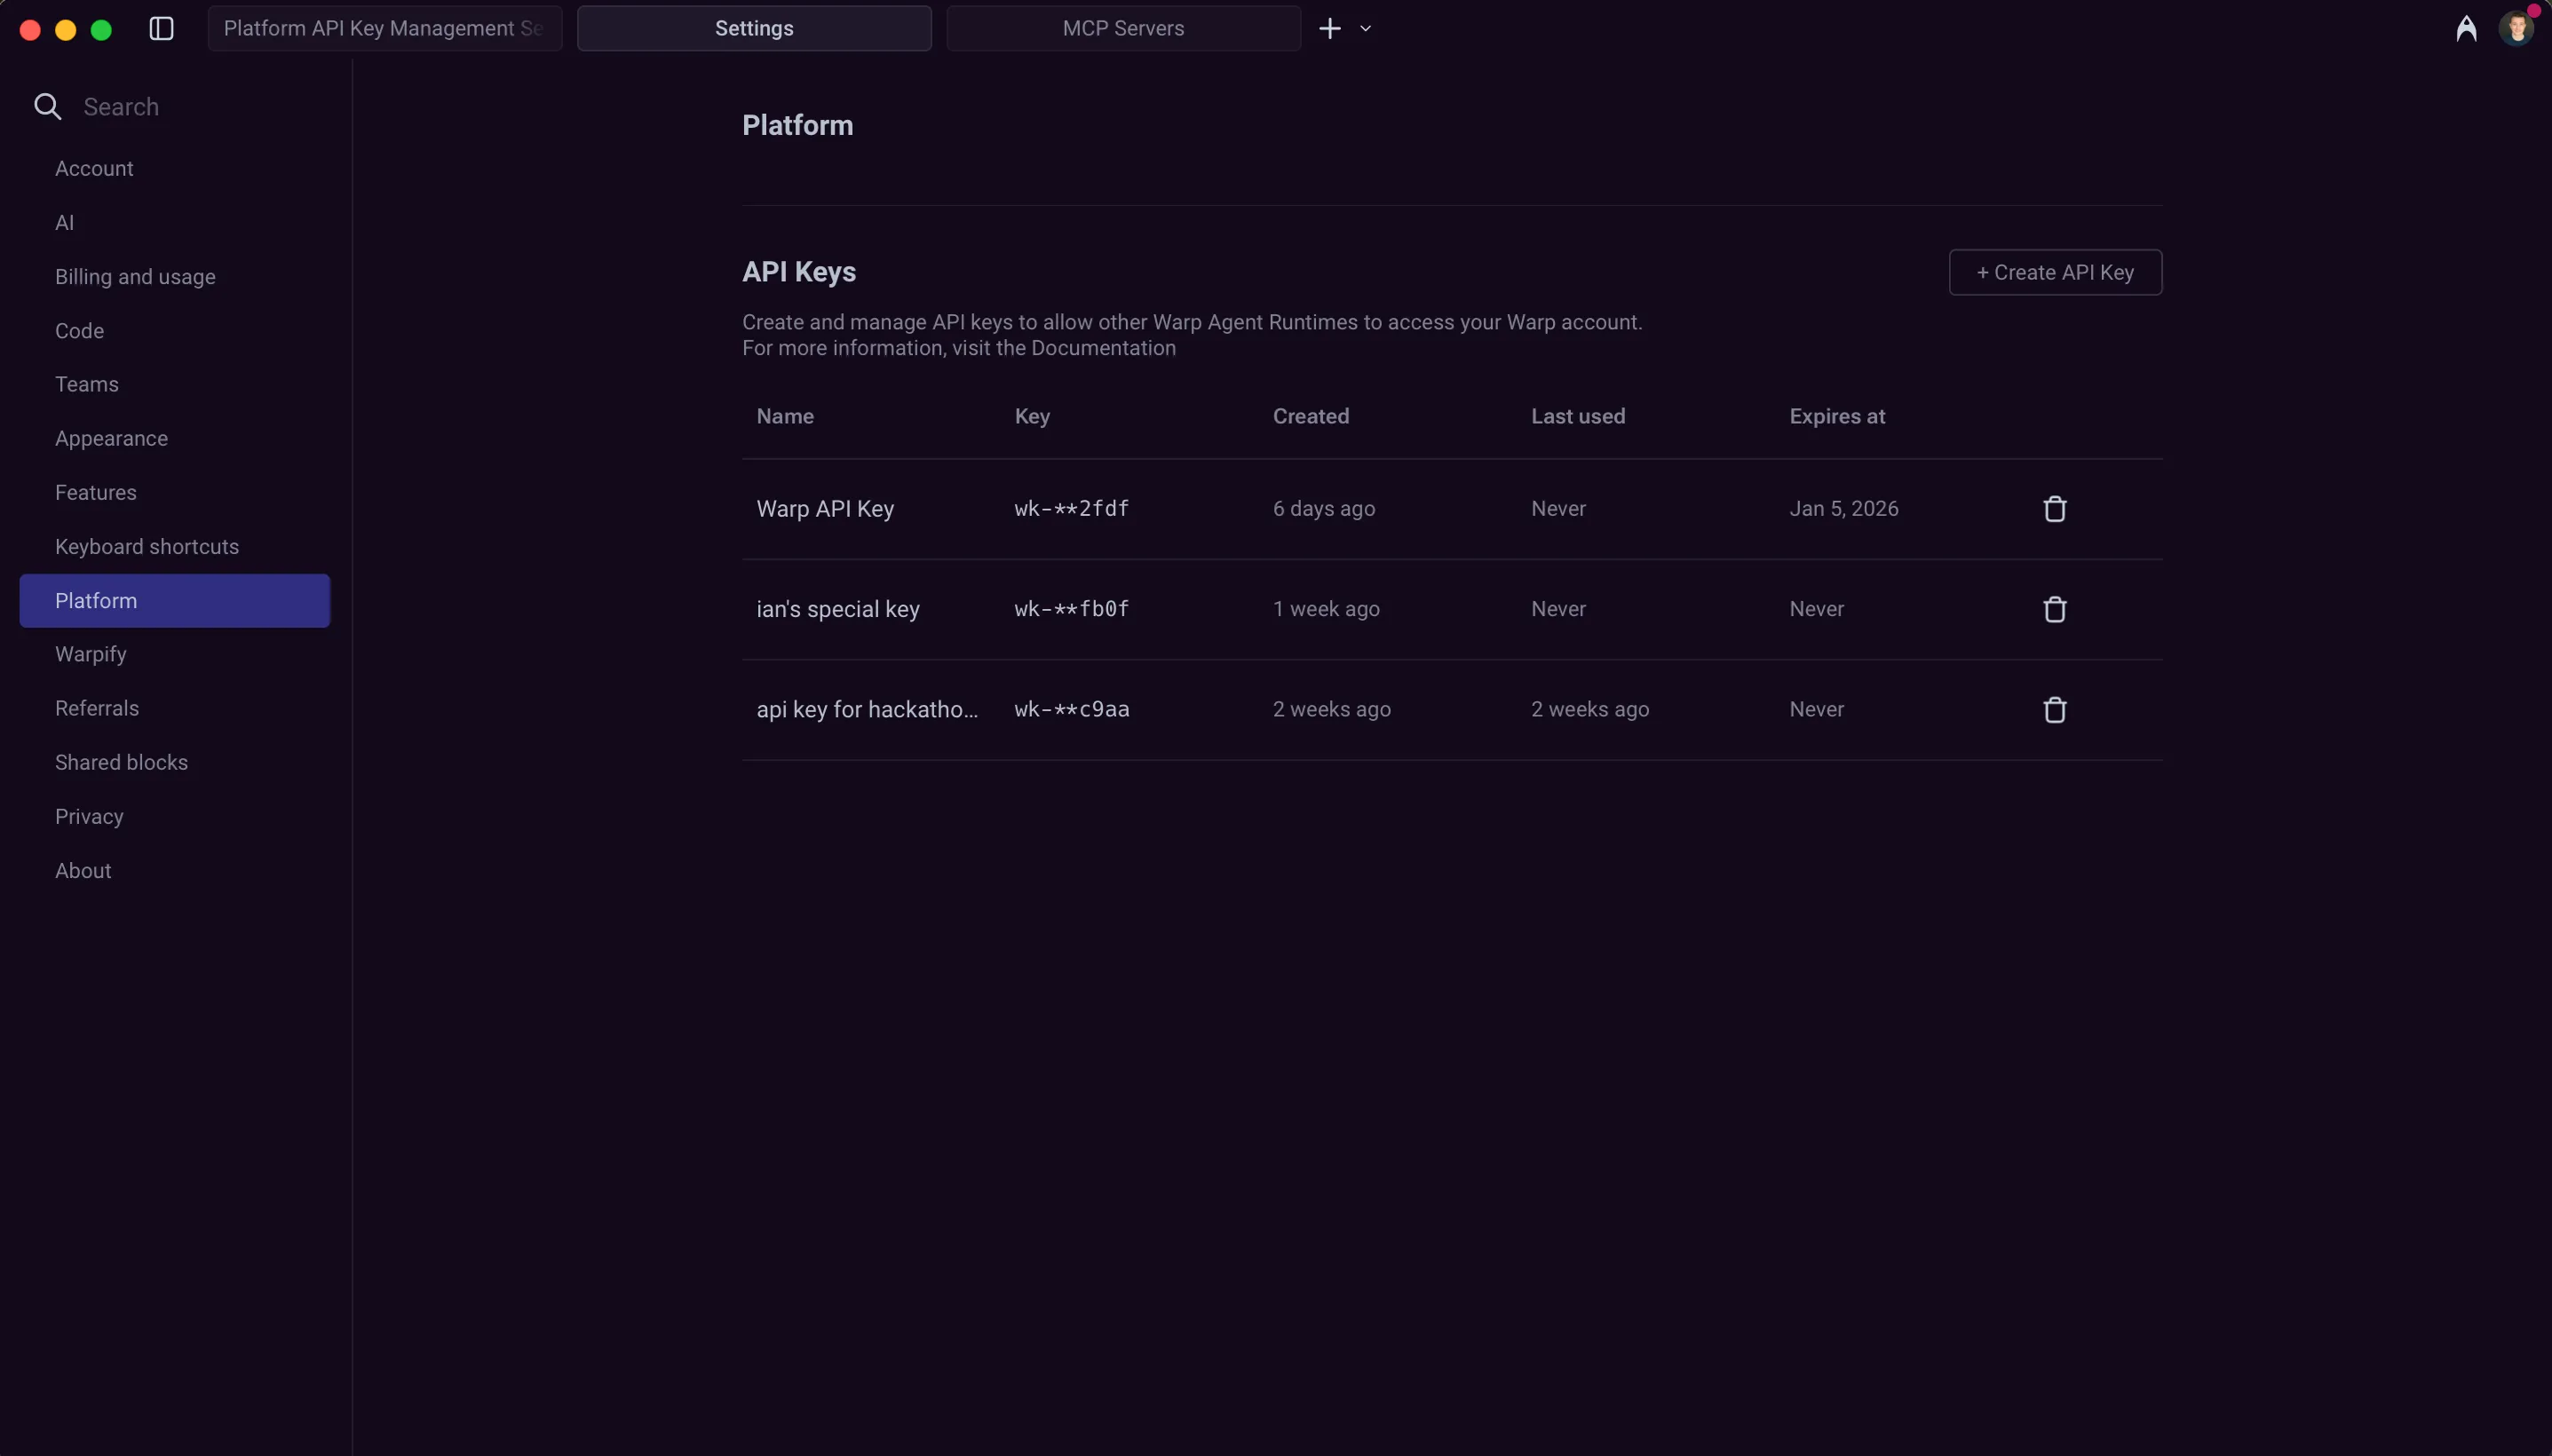
API key management interface in Warp settings.
## How key type affects billing and GitHub access
[Section titled “How key type affects billing and GitHub access”](#how-key-type-affects-billing-and-github-access)
The key type determines who the run is attributed to, which credit pool is billed, and which GitHub credentials the agent can use.
### Personal API key behavior
[Section titled “Personal API key behavior”](#personal-api-key-behavior)
* Run as you.
* On Build, Max, and Business plans, use your plan-included credits, then your add-on credits. On Enterprise plans, use the team-scoped credit pool.
* Use your GitHub permissions. Code changes are attributed to your GitHub account.
### Agent API key behavior
[Section titled “Agent API key behavior”](#agent-api-key-behavior)
* Run as a cloud agent on your team.
* On Build, Max, and Business plans, bill the team owner: the owner’s plan-included credits, then the owner’s add-on credits. With auto-reload on, usage can trigger a reload on the owner’s pool, subject to the team-wide monthly spend cap. On Enterprise plans, use the team-scoped credit pool.
* Use the [Warp Factories](/factories/) GitHub App when [team GitHub authorization](/platform/team-access-billing-and-identity/#team-github-authorization) is configured. Without team GitHub authorization, agent keys are still useful for tasks that don’t need to write to GitHub, such as analysis, monitoring, or triage.
For the full credit waterfall, see [Access, billing, and identity permissions](/platform/team-access-billing-and-identity/) and [add-on credits](/support-and-community/plans-and-billing/add-on-credits/).
## Authenticating with API keys
[Section titled “Authenticating with API keys”](#authenticating-with-api-keys)
You can authenticate with an API key in the CLI using either an environment variable or a command flag. Environment variables are recommended for security and easier reuse across multiple commands.
**Via environment variable (recommended):**
```sh
$ export WARP_API_KEY="wk-xxx..."
$ oz agent run --prompt "analyze this codebase"
```
**Via command flag:**
```sh
$ oz agent run --api-key "wk-xxx..." --prompt "analyze this codebase"
```
Note
API keys start with the prefix `wk-`. If your key doesn’t have this prefix, it may be [invalid or from an older format](/factories/api-and-sdk/troubleshooting/errors/authentication-required/).
## Managing API keys
[Section titled “Managing API keys”](#managing-api-keys)
The [Oz web app settings page](https://oz.warp.dev/settings) and the Warp app’s **Settings** > **Cloud platform** > **API keys** both list your active keys. Both surfaces show:
* **Name** — The name you assigned when creating the key.
* **Scope** — Personal keys show your user; agent keys show the cloud agent the key runs as.
* **Expires at** — The key’s expiration date, or “Never” if it doesn’t expire.
The Warp app also shows additional metadata that isn’t surfaced in the Oz web app:
* **Key** — A masked suffix (`wk-**xxxx`) to help identify the key.
* **Created** — When the key was created.
* **Last used** — When the key was last used for authentication.
### Deleting API keys
[Section titled “Deleting API keys”](#deleting-api-keys)
To delete an API key, find it in either the Oz web app or the Warp app’s API Keys list and click the delete icon next to the key.
Deleted keys are immediately invalidated and cannot be recovered. Any services or scripts using the deleted key will lose access and may return an [`authentication_required` error](/factories/api-and-sdk/troubleshooting/errors/authentication-required/).
## Manage API keys from the CLI
[Section titled “Manage API keys from the CLI”](#manage-api-keys-from-the-cli)
In addition to the web and Warp app surfaces, you can manage API keys directly with the [Oz CLI](/agents/cli/oz-cli/). These commands are useful for scripting key rotation and for headless environments.
### List keys
[Section titled “List keys”](#list-keys)
`oz api-key list` prints your active API keys.
* `--sort-by <FIELD>` — Sort by `name`, `created-at`, `last-used-at`, `expires-at`, or `scope`.
* `--sort-order <DIR>` — Sort direction: `asc` or `desc`.
* `--jq <FILTER>` — Filter the JSON output with a jq expression (for example, `--jq '.[].name'`).
```bash
oz api-key list --sort-by last-used-at --sort-order desc
```
### Create a key
[Section titled “Create a key”](#create-a-key)
`oz api-key create <NAME>` creates a key and prints the raw secret once. Store it securely — you can’t retrieve it again.
* `<NAME>` — A name to identify the key (required).
* `--agent <UID>` — Create an agent key that runs as the given cloud agent, instead of a personal key.
* One expiration choice is required: `--expires-in <DURATION>` (for example, `30d`, `12h`, or `90m`), `--expires-at <RFC3339>` (an exact timestamp), or `--no-expiration`.
* `--jq <FILTER>` — Filter the JSON output with a jq expression.
```bash
# A personal key that expires in 30 days
oz api-key create "ci-pipeline" --expires-in 30d
# An agent key scoped to a cloud agent, with no expiration
oz api-key create "nightly-triage" --agent AGENT_UID --no-expiration
```
### Expire a key
[Section titled “Expire a key”](#expire-a-key)
`oz api-key expire <NAME_OR_UID>` immediately invalidates a key (also available as `oz api-key delete`). Expired keys can’t be recovered.
* `<NAME_OR_UID>` — The name or UID of the key to expire (required).
* `--force` — Skip the confirmation prompt.
```bash
oz api-key expire "ci-pipeline" --force
```
## Best practices
[Section titled “Best practices”](#best-practices)
* **Use personal keys for runs that should act as you.** When code changes should be attributed to your GitHub account, a personal key is the right choice. Use agent keys for automation that isn’t tied to a specific user.
* **Use environment variables.** Avoid passing API keys directly in commands where they may be logged or visible in shell history.
* **Set appropriate expiration.** Use shorter expiration times for development and testing; consider longer durations for stable production workflows.
* **Configure team GitHub authorization for agents that write to GitHub.** Personal keys authenticate as you with your GitHub permissions. Agent keys authenticate via the [Warp Factories GitHub App](/platform/team-access-billing-and-identity/#team-github-authorization) when team GitHub authorization is configured in the Admin Panel.
* **Rotate keys periodically.** Create new keys and retire old ones on a regular schedule to limit exposure from compromised credentials.
* **Store securely.** Use secret managers (like 1Password CLI, HashiCorp Vault, or cloud provider secret services) rather than plain text files.
# Artifacts
Canonical page: [/agents/cli/oz-cli/artifacts/](https://docs.warp.dev/agents/cli/oz-cli/artifacts/)
> Get metadata for and download files produced by an agent run using the `oz artifact` subcommands.
Caution
The Oz CLI (the `oz` binary) is a supported legacy interface. Existing users do not need to change their workflows. For new multi-stage development workflows, use [Warp Factories](/factories/). Warp will publish guidance before any support change.
Artifacts are files that an agent produces during a run and uploads to Warp — screenshots, generated reports, build outputs, logs, or any other file the agent saves alongside its conversation. Use `oz artifact` to inspect those files from outside the run and pull them down to your machine.
## When to use artifacts
[Section titled “When to use artifacts”](#when-to-use-artifacts)
Use artifacts when you need to retrieve files an agent produced after a run completes, without re-running the agent or scraping the conversation output.
* **Hand-offs between runs** - A scheduled agent produces a report; a follow-up workflow downloads and processes it.
* **Local inspection** - Pull a generated file (HTML, image, CSV) onto your laptop to review.
* **CI integration** - Fetch an agent-produced build artifact from a pipeline step that runs after the agent finishes.
Artifacts are referenced by an artifact UID. You can find UIDs in the agent’s run detail view, in the JSON returned by [`oz run get`](/agents/cli/oz-cli/), or in the response from the [Warp Platform API](/factories/api-and-sdk/).
## `oz artifact get`
[Section titled “oz artifact get”](#oz-artifact-get)
Print metadata for an artifact without downloading it.
```sh
oz artifact get <ARTIFACT_UID>
```
The output describes the artifact (file name, content type, size, the run or conversation it’s associated with, and the description supplied when it was uploaded). Use `--output-format json` for a structured response that’s easy to parse from a script:
```sh
oz artifact get <ARTIFACT_UID> --output-format json
```
This command is useful for confirming an artifact exists and inspecting its size before you decide to download it.
## `oz artifact download`
[Section titled “oz artifact download”](#oz-artifact-download)
Download the file contents of an artifact.
```sh
oz artifact download <ARTIFACT_UID> [--out <PATH>]
```
### Flags
[Section titled “Flags”](#flags)
* **`<ARTIFACT_UID>`** - The UID of the artifact to download. Required positional argument.
* **`--out <PATH>`** (`-o`) - Write the downloaded artifact to a specific file path. When omitted, the file is written to the current directory using the artifact’s stored file name.
### Examples
[Section titled “Examples”](#examples)
Download an artifact to the current directory, preserving its original name:
```sh
oz artifact download <ARTIFACT_UID>
```
Download to a specific path:
```sh
oz artifact download <ARTIFACT_UID> --out ./reports/nightly.html
```
Use the artifact in a pipeline by combining `oz run get` and `oz artifact download`:
```sh
# Pull the latest run for a scheduled agent, grab its first artifact
RUN_ID=$(oz run list --limit 1 --output-format json | jq -r '.[0].uid')
ARTIFACT_UID=$(oz run get "$RUN_ID" --output-format json | jq -r '.artifacts[0].uid')
oz artifact download "$ARTIFACT_UID" --out ./latest-report.html
```
## Related
[Section titled “Related”](#related)
* [Warp Platform API](/factories/api-and-sdk/) - retrieve artifacts programmatically over HTTP.
* [Scheduled cloud agents](/platform/triggers/scheduled-agents/) - common producer of recurring artifacts that downstream tooling consumes.
# Federated identity tokens
Canonical page: [/agents/cli/oz-cli/federate/](https://docs.warp.dev/agents/cli/oz-cli/federate/)
> Issue short-lived OIDC identity tokens from a running agent so it can authenticate to cloud providers without long-lived credentials.
Caution
The Oz CLI (the `oz` binary) is a supported legacy interface. Existing users do not need to change their workflows. For new multi-stage development workflows, use [Warp Factories](/factories/). Warp will publish guidance before any support change.
`oz federate` issues short-lived OIDC identity tokens for the agent that’s currently running. Use these tokens to authenticate to cloud providers (AWS, GCP, Azure, and other OIDC-aware systems) without baking long-lived credentials into your environment.
This command can only be called from inside a running agent session — typically as part of a [skill](/agents/capabilities/skills/), a tool, or a script the agent executes while a run is in progress.
## When to use federation
[Section titled “When to use federation”](#when-to-use-federation)
Use federated identity tokens when you want an agent to act against a cloud account without storing service-account keys, access keys, or refresh tokens in the environment.
* **Short-lived credentials** - Tokens expire on a schedule you choose. Even if a token leaks, its blast radius is bounded.
* **No secret rotation** - Federation removes the need to rotate static keys in environments or secrets.
* **Per-run identity** - Each run can claim a different subject (user, team, environment, skill, run ID), giving you fine-grained IAM policies.
For background on federation, see your cloud provider’s workload identity federation guide (for example, [Google Cloud’s workload identity federation](https://cloud.google.com/iam/docs/workload-identity-federation) or [AWS IAM Identity Center](https://docs.aws.amazon.com/IAM/latest/UserGuide/id_roles_providers_oidc.html)).
## `oz federate issue-token`
[Section titled “oz federate issue-token”](#oz-federate-issue-token)
Issue an OIDC identity token for the current run.
```bash
oz federate issue-token \
--run-id <RUN_ID> \
--audience <AUDIENCE> \
[--duration <DURATION>] \
[--subject-template <COMPONENT> ...]
```
### Flags
[Section titled “Flags”](#flags)
* **`--run-id <RUN_ID>`** - The ID of the cloud agent run requesting the token. Cloud agent runs set `OZ_RUN_ID` to the current run ID, but you must still pass this flag.
* **`--audience <AUDIENCE>`** - The `aud` claim for the issued token. Set this to the value your cloud provider’s identity pool expects (for example, an AWS IAM Identity Center audience or a GCP workload identity pool URL).
* **`--duration <DURATION>`** - Requested token lifetime from 5 minutes to 3 hours. Accepts human-readable durations such as `30m` or `2h30m` and defaults to `1h`.
* **`--subject-template <COMPONENT> ...`** - Controls how the OIDC token’s `sub` claim is formatted. Pass one or more components, which are joined to form the subject. Defaults to `principal` (for example, `user:my-user-id`).
### Subject template components
[Section titled “Subject template components”](#subject-template-components)
By default, `oz federate issue-token` builds `sub` from `principal`. The result is `user:USER_UID` for a user or `service_account:SERVICE_ACCOUNT_UID` for an agent.
Pass each component as a separate argument. Do not quote the whole list. The command joins components in the order you supply them and separates them with commas. It fails if a component isn’t available for the current principal or run. Colons and commas within component values become underscores.
Use `principal`, `scoped_principal`, or any available claim listed under [OIDC token claims](/platform/integrations/cloud-providers/#oidc-token-claims), except `user` and `service_account`. Use `principal` in place of those emitted claim names. See [the subject claim](/platform/integrations/cloud-providers/#subject-sub) for the `principal` and `scoped_principal` formats.
### Examples
[Section titled “Examples”](#examples)
Issue a one-hour token with the default `principal` subject:
```bash
oz federate issue-token \
--run-id "$OZ_RUN_ID" \
--audience AUDIENCE \
--output-format json
```
Replace `AUDIENCE` with the identifier expected by your provider.
Issue a 30-minute token whose subject includes the principal, run, and environment:
```bash
oz federate issue-token \
--run-id "$OZ_RUN_ID" \
--audience AUDIENCE \
--duration 30m \
--subject-template principal run_id environment
```
For a user, this template produces a subject such as `user:abc123,run_id:run-456,environment:env-789`.
## Using tokens with cloud providers
[Section titled “Using tokens with cloud providers”](#using-tokens-with-cloud-providers)
Once you have a token, exchange it for cloud credentials using your provider’s standard OIDC federation flow. The exchange happens between the cloud provider and your script — the Automation Platform only issues the OIDC token.
For provider setup instructions and the complete token claim reference, see [Cloud providers](/platform/integrations/cloud-providers/).
A typical AWS flow:
1. Run `oz federate issue-token` to get the OIDC JWT.
2. Call `sts:AssumeRoleWithWebIdentity` with the JWT and an IAM role ARN.
3. Use the temporary AWS credentials returned by STS.
A typical GCP flow:
1. Run `oz federate issue-token` to get the OIDC JWT.
2. Call the [Security Token Service `token` endpoint](https://cloud.google.com/iam/docs/reference/sts/rest/v1/TopLevel/token) to exchange the JWT for a federated access token.
3. Optionally impersonate a service account for the final credentials.
## Related
[Section titled “Related”](#related)
* [Cloud environments](/platform/environments/) - configure the environment your agent runs in.
* [Secrets](/platform/secrets/) - alternative for credentials that can’t be federated.
# Integration setup
Canonical page: [/agents/cli/oz-cli/integration-setup/](https://docs.warp.dev/agents/cli/oz-cli/integration-setup/)
> Learn how to set up environments and integrations so you can trigger agents from external tools.
Caution
The Oz CLI (the `oz` binary) is a supported legacy interface. Existing users do not need to change their workflows. For new multi-stage development workflows, use [Warp Factories](/factories/). Warp will publish guidance before any support change.
This article describes the environment and integration setup that is required before you can trigger agents from external tools, like Slack or Linear. You will learn how to:
* Create and configure the environment needed to run agents
* Connect that environment to your team
* Trigger agents using Slack or Linear
Note
**You only need to complete this setup once per Warp team**. After an integration exists, anyone on the team can use it. For example, the first time a teammate triggers an agent from Slack or Linear, they’ll be prompted to authorize GitHub with their own account in order for the agent to write back to repos.
Note: While cloud agents can be run individually via CLI without a team, integrations (Slack, Linear) require team membership.
Note
For a quickstart guide to Warp integrations, see the [Integrations overview](/platform/integrations/).
## How integrations and environments work
[Section titled “How integrations and environments work”](#how-integrations-and-environments-work)
Warp integrations connect external tools, like Slack or Linear, to agents that run your code in the background.
There are three main components to know:
* **Triggers** provide the context that tells Warp *what* to run. A trigger could be a Slack message where you tag @warp, or a Linear issue or comment.
* [**Integrations**](/platform/integrations/) are what connect the trigger surface (Slack, Linear) to Warp. An integration links the trigger to your [Warp team](/knowledge-and-collaboration/teams/) and handles posting results to the original tool, for example, replying in Slack.
* **Environments** define how and where agents run your code. When an agent is triggered, Warp uses the environment to spin up a container, clone repositories, and execute the agent’s workflow.
```plaintext
Slack or Linear
(trigger)
→
Warp Integration
(connects tools to Warp)
→
Environment
(Docker image + repos + setup)
→
Agent
(runs workflow, opens PRs, posts results)
```
Setting up an integration consists of three steps.
1. **Create an environment** for the agent to run your code.
2. **Authorize GitHub** so Warp can clone repositories, write code, debug issues, open pull requests, and more.
3. **Configure** the Warp app with an integration.
Tip
If setup fails, use the returned error code to narrow the fix. Common errors include:
* [`environment_setup_failed`](/factories/api-and-sdk/troubleshooting/errors/environment-setup-failed/) (environment initialization issues)
* [`external_authentication_required`](/factories/api-and-sdk/troubleshooting/errors/external-authentication-required/) (missing GitHub or external-service authorization)
* [`integration_not_configured`](/factories/api-and-sdk/troubleshooting/errors/integration-not-configured/) (incomplete integration setup)
***
## 1. Creating an environment
[Section titled “1. Creating an environment”](#1-creating-an-environment)
Before you can trigger agents from Slack or Linear, you need an environment. The environment defines how and where Warp runs your code.
At a minimum, an environment includes:
* A Docker image
* One or more GitHub repositories
* Optional setup commands
Typically, you’ll create **one environment per codebase** (or closely related set of repos) and reuse it across integrations.
You can create environments using a guided Agent flow, or directly through the CLI.
#### Before you begin
[Section titled “Before you begin”](#before-you-begin)
Make sure you have:
* A GitHub repository (or repositories) that the agent can work in.
* A publicly-accessible Docker image that can build and run your code. Official images like `node`, `python`, or `rust` work for many projects.
Note
You only need to create an environment once. It can be reused across Slack, Linear, and terminal triggers.
### Option 1: Guided environment setup (recommended)
[Section titled “Option 1: Guided environment setup (recommended)”](#option-1-guided-environment-setup-recommended)
The fastest way to get started is to use the guided environment setup. Use the `/create-environment` [slash command](/agents/capabilities/slash-commands/) if you want Warp to analyze your repos and suggest an environment configuration.
You can run the command inside a Git repo directory with no argument, or with one or more repo paths or URLs. For example, from Warp:
owner/repo
```bash
# File paths
/create-environment ./warp-internal ./warp-server
/create-environment warpdotdev/warp-internal warpdotdev/warp-server
# GitHub URLs
/create-environment https://github.com/warpdotdev/warp-internal.git
```
The guided flow will:
1. Detect the repositories you want the agent to work with and identify languages, frameworks, and tools
2. Look for an existing Dockerfile, recommend an official base image, or help build a custom image (if needed)
3. Suggest setup commands based on your scripts and package managers
4. Create the environment through the CLI and return an environment ID
This produces a ready-to-use environment that can immediately be connected to [Slack](/platform/integrations/slack/) or [Linear](/platform/integrations/linear/).
### Option 2: Create an environment with the CLI
[Section titled “Option 2: Create an environment with the CLI”](#option-2-create-an-environment-with-the-cli)
If you already know how you want to configure your environment, you can create it directly with the CLI.
**Use this approach when:**
* You already have a custom Docker image
* You want full control over repos and setup commands
* You’re scripting or automating environment creation
From Warp:
```sh
oz environment create \
--name <name> \
--docker-image <image> \
--repo <owner/repo> \
--repo <owner/repo> \
--setup-command "<command1>" \
--setup-command "<command2>" \
--description "Optional description"
```
Key flags:
* `--name` (`-n`) – human-readable label for the environment.
* `--docker-image` (`-d`) – image name on Docker Hub. If not specified, you’ll be prompted to select from available images (see `oz environment image list`).
* `--repo` (`-r`) – can be repeated for each repo.
* `--setup-command` (`-c`) – can be repeated; commands run in the order provided.
* `--description` – optional description (max 240 characters).
You can inspect existing environments with `oz environment list`.
To delete an environment, use `oz environment delete <ID>`. Add `--force` to skip confirmation checks for environments used by integrations.
For more details about environment configuration, see the [Slack](/platform/integrations/slack/) and [Linear](/platform/integrations/linear/) articles.
#### Example environments
[Section titled “Example environments”](#example-environments)
| Project type | Docker image | Repos | Example setup commands |
| --------------- | ----------------------------------- | -------------------------------------------- | ---------------------------------------------------------------------------------------- |
| Web dev project | `node:20-bullseye` | your-org/frontend-react your-org/backend-api | `npm install -g pnpm``cd frontend-react && pnpm install``cd backend-api && pnpm install` |
| Python project | Custom image based on `python:3.11` | your-org/cool\_python\_project | `cd cool_python_project && pip install -r requirements.txt` |
***
## 2. Authorizing GitHub
[Section titled “2. Authorizing GitHub”](#2-authorizing-github)
Warp needs GitHub access so agents can clone your repositories and, when permitted, write code and open pull requests.
#### How GitHub authorization works
[Section titled “How GitHub authorization works”](#how-github-authorization-works)
When you create an environment or integration, Warp will prompt you to:
* Install or update the Warp GitHub app
* Grant access to the repositories in your environment
This authorization enables agents to clone repositories into the environment, create branches and commits, and open pull requests.
**Public vs private repos**
* **Public repos:** Agents can read code without authorization, but cannot write or open PRs.
* **Private repos:** The Warp GitHub App must have access and the triggering user must have write permissions.
#### Ongoing permissions
[Section titled “Ongoing permissions”](#ongoing-permissions)
Depending on how the GitHub app is installed in your organization:
* You may need to grant access to new repositories over time
* An organization admin may need to update the app’s permissions
You typically only need to handle this once per team, unless your repo access changes.
#### Team-level GitHub authorization
[Section titled “Team-level GitHub authorization”](#team-level-github-authorization)
For automated workflows that use an [agent API key](/agents/cli/oz-cli/api-keys/) (CI/CD pipelines, scheduled agents, SDK-triggered runs), you can configure team GitHub authorization so the agent authenticates with the Warp Factories GitHub App instead of an individual’s personal token.
This requires a Warp team admin to enable the GitHub organization in the Admin Panel (**Settings** > **Admin Panel** > **Platform**). Once configured, tasks initiated with an agent API key can clone repos and open pull requests using the GitHub App installation token.
For full setup instructions, see [Team GitHub authorization](/platform/team-access-billing-and-identity/#team-github-authorization).
Note
**Using API keys:** Personal API keys authenticate as you, so the agent runs with your GitHub permissions and code changes are attributed to your account. Agent API keys with [team GitHub authorization](/platform/team-access-billing-and-identity/#team-github-authorization) configured use the GitHub App token instead.
***
## 3. Setting up an integration
[Section titled “3. Setting up an integration”](#3-setting-up-an-integration)
Once you have set up at least one environment, you can create integrations that connect it to Slack or Linear.
Note
For easier setup, use the [Oz web app](https://oz.warp.dev) to configure integrations with a guided flow.
Alternatively, use the CLI where `<ENV_ID>` is your environment ID:
```bash
oz integration create slack --environment <ENV_ID>
# or
oz integration create linear --environment <ENV_ID>
```
Note
If you omit `--environment`, the CLI will show a list of environments and prompt you to choose one.
The CLI then:
1. Links the integration to your Warp team and environment.
2. Opens a browser flow to install the Warp app into your Slack workspace or Linear workspace.
3. Generates an **integration ID** you can later list or delete.
Note
The [GitHub integration](/platform/integrations/github/), which starts agents from `@warp-agent` mentions on issues and pull requests, isn’t created with `oz integration create`. It’s set up by installing the Warp Factories GitHub App and enabling the GitHub organization in the Admin Panel.
**Additional `integration create` flags:**
* `--prompt` — custom instructions applied to all runs for this integration.
* `--mcp <SPEC>` — attach MCP servers (inline JSON, file path, or UUID). Can be repeated.
* `--model <MODEL_ID>` — override the default model.
* `--host <WORKER_ID>` — run on a specific self-hosted worker.
* `--file <PATH>` (`-f`) — load configuration from a YAML or JSON file.
**Example with a custom prompt:**
```bash
oz integration create slack \
--environment <ENV_ID> \
--prompt "Always prefix PR titles with [WARP-AGENT] and add detailed test steps."
```
### Updating an integration
[Section titled “Updating an integration”](#updating-an-integration)
You can modify an existing integration using `oz integration update`:
```bash
oz integration update slack \
--environment <ENV_ID> \
--prompt "Updated instructions for the integration."
```
**Update-specific flags:**
* `--environment <ID>` — change the environment.
* `--remove-environment` — remove the environment from the integration.
* `--prompt` — update the custom instructions.
* `--mcp <SPEC>` — add MCP servers to the integration.
* `--remove-mcp <SERVER_NAME>` — remove an MCP server by name.
* `--model <MODEL_ID>` — update the default model.
* `--host <WORKER_ID>` — update the execution host.
Note
For more details, see the dedicated pages for [Slack](/platform/integrations/slack/) and [Linear](/platform/integrations/linear/) integrations.
## How are environments used at runtime?
[Section titled “How are environments used at runtime?”](#how-are-environments-used-at-runtime)
When you trigger an agent from Slack or Linear, Warp follows a consistent, repeatable execution process using your environment.
At a high level, each run works like this:
1. **Warp receives the trigger**\
Warp captures the message content (for example, a Slack thread or Linear issue), along with any linked context.
2. **Warp creates an execution container**\
Warp spins up a fresh container from the Docker image defined in your environment.
3. **Repositories are cloned**\
The GitHub repositories associated with the environment are cloned into the container.
4. **Setup commands are run**\
Any setup commands you configured, like installing dependencies, are executed.
5. **The agent workflow runs**\
The agent executes the task using the provided context, tools, and permissions.
6. **Results are posted back**\
Progress updates, summaries, and results are posted back to Slack or Linear.
7. **The container is destroyed**\
After the run completes, the container is torn down. Each run starts from a clean, isolated environment.
## Next steps
[Section titled “Next steps”](#next-steps)
You now have everything needed to trigger agents from your team’s tools. From here, you can:
* Add or adjust setup commands
* Switch to a custom Docker image
* Include additional repositories
* Add custom prompts for consistent agent behavior
* Create separate environments for different workflows or teams
**Additional reading**
* [Cloud Agents Overview](/platform/)
* [Automation Platform](/platform/overview/)
* [Slack](/platform/integrations/slack/), [Linear](/platform/integrations/linear/), [GitHub](/platform/integrations/github/), and [GitHub Actions](/platform/integrations/github-actions/) integrations
* [Troubleshooting](/agents/cli/oz-cli/troubleshooting/)
# MCP servers (CLI reference)
Canonical page: [/agents/cli/oz-cli/mcp-servers/](https://docs.warp.dev/agents/cli/oz-cli/mcp-servers/)
> Connect agents to external tools like GitHub, Linear, and Sentry by passing MCP servers to the --mcp flag as a UUID, inline JSON, or file path.
Caution
The Oz CLI (the `oz` binary) is a supported legacy interface. Existing users do not need to change their workflows. For new multi-stage development workflows, use [Warp Factories](/factories/). Warp will publish guidance before any support change.
MCP servers connect agents to external systems like GitHub, Linear, or Sentry. To use a [Model Context Protocol (MCP)](/agents/capabilities/mcp/) server from the CLI, use the `--mcp` flag with `oz agent run` or `oz agent run-cloud`.
The CLI does not start every configured MCP server for every run. Explicit `--mcp` values start run-scoped servers. A selected agent profile can start installed servers on its MCP allowlist, while eligible file-based and global servers follow their own discovery path.
For help choosing between local, cloud, and shared MCP workflows, see [Connect developer tools to agents with MCP workflows](/guides/external-tools/using-mcp-servers-with-warp/). For a conceptual overview of MCP with cloud agents — including configuration schema, full agent config examples, and limitations — see [MCP Servers](/platform/mcp/) in the Cloud Agents docs.
***
## Using the `--mcp` flag
[Section titled “Using the --mcp flag”](#using-the---mcp-flag)
The `--mcp` flag accepts four formats:
* **UUID** — reference a Warp-shared MCP server by its UUID (find UUIDs with `oz mcp list`)
* **Managed integration id** — reference a Warp-managed integration MCP server by its short id, such as `linear` (see [Passing Warp-managed integration servers by id](#passing-warp-managed-integration-servers-by-id))
* **Inline JSON** — pass a full MCP JSON configuration directly as a string
* **File path** — path to a JSON file containing the MCP configuration
You can repeat `--mcp` to include multiple servers.
### Passing MCP servers by UUID
[Section titled “Passing MCP servers by UUID”](#passing-mcp-servers-by-uuid)
1. Locate the MCP server UUID using `oz mcp list`. This command lists all MCP servers configured in your Warp account, including team-shared ones:
```sh
$ oz mcp list
+--------------------------------------+--------+
| UUID | Name |
+===============================================+
| 1deb1b14-b6e5-4996-ae99-233b7555d2d0 | github |
|--------------------------------------+--------|
| 65450c32-9eb1-4c57-8804-0861737acbc4 | linear |
|--------------------------------------+--------|
| d94ade64-0e73-47a6-b3ee-14e5afec3d90 | Sentry |
+--------------------------------------+--------+
```
Alternatively, copy the UUID from Warp in **Settings** > **Agents** > **MCP servers**.
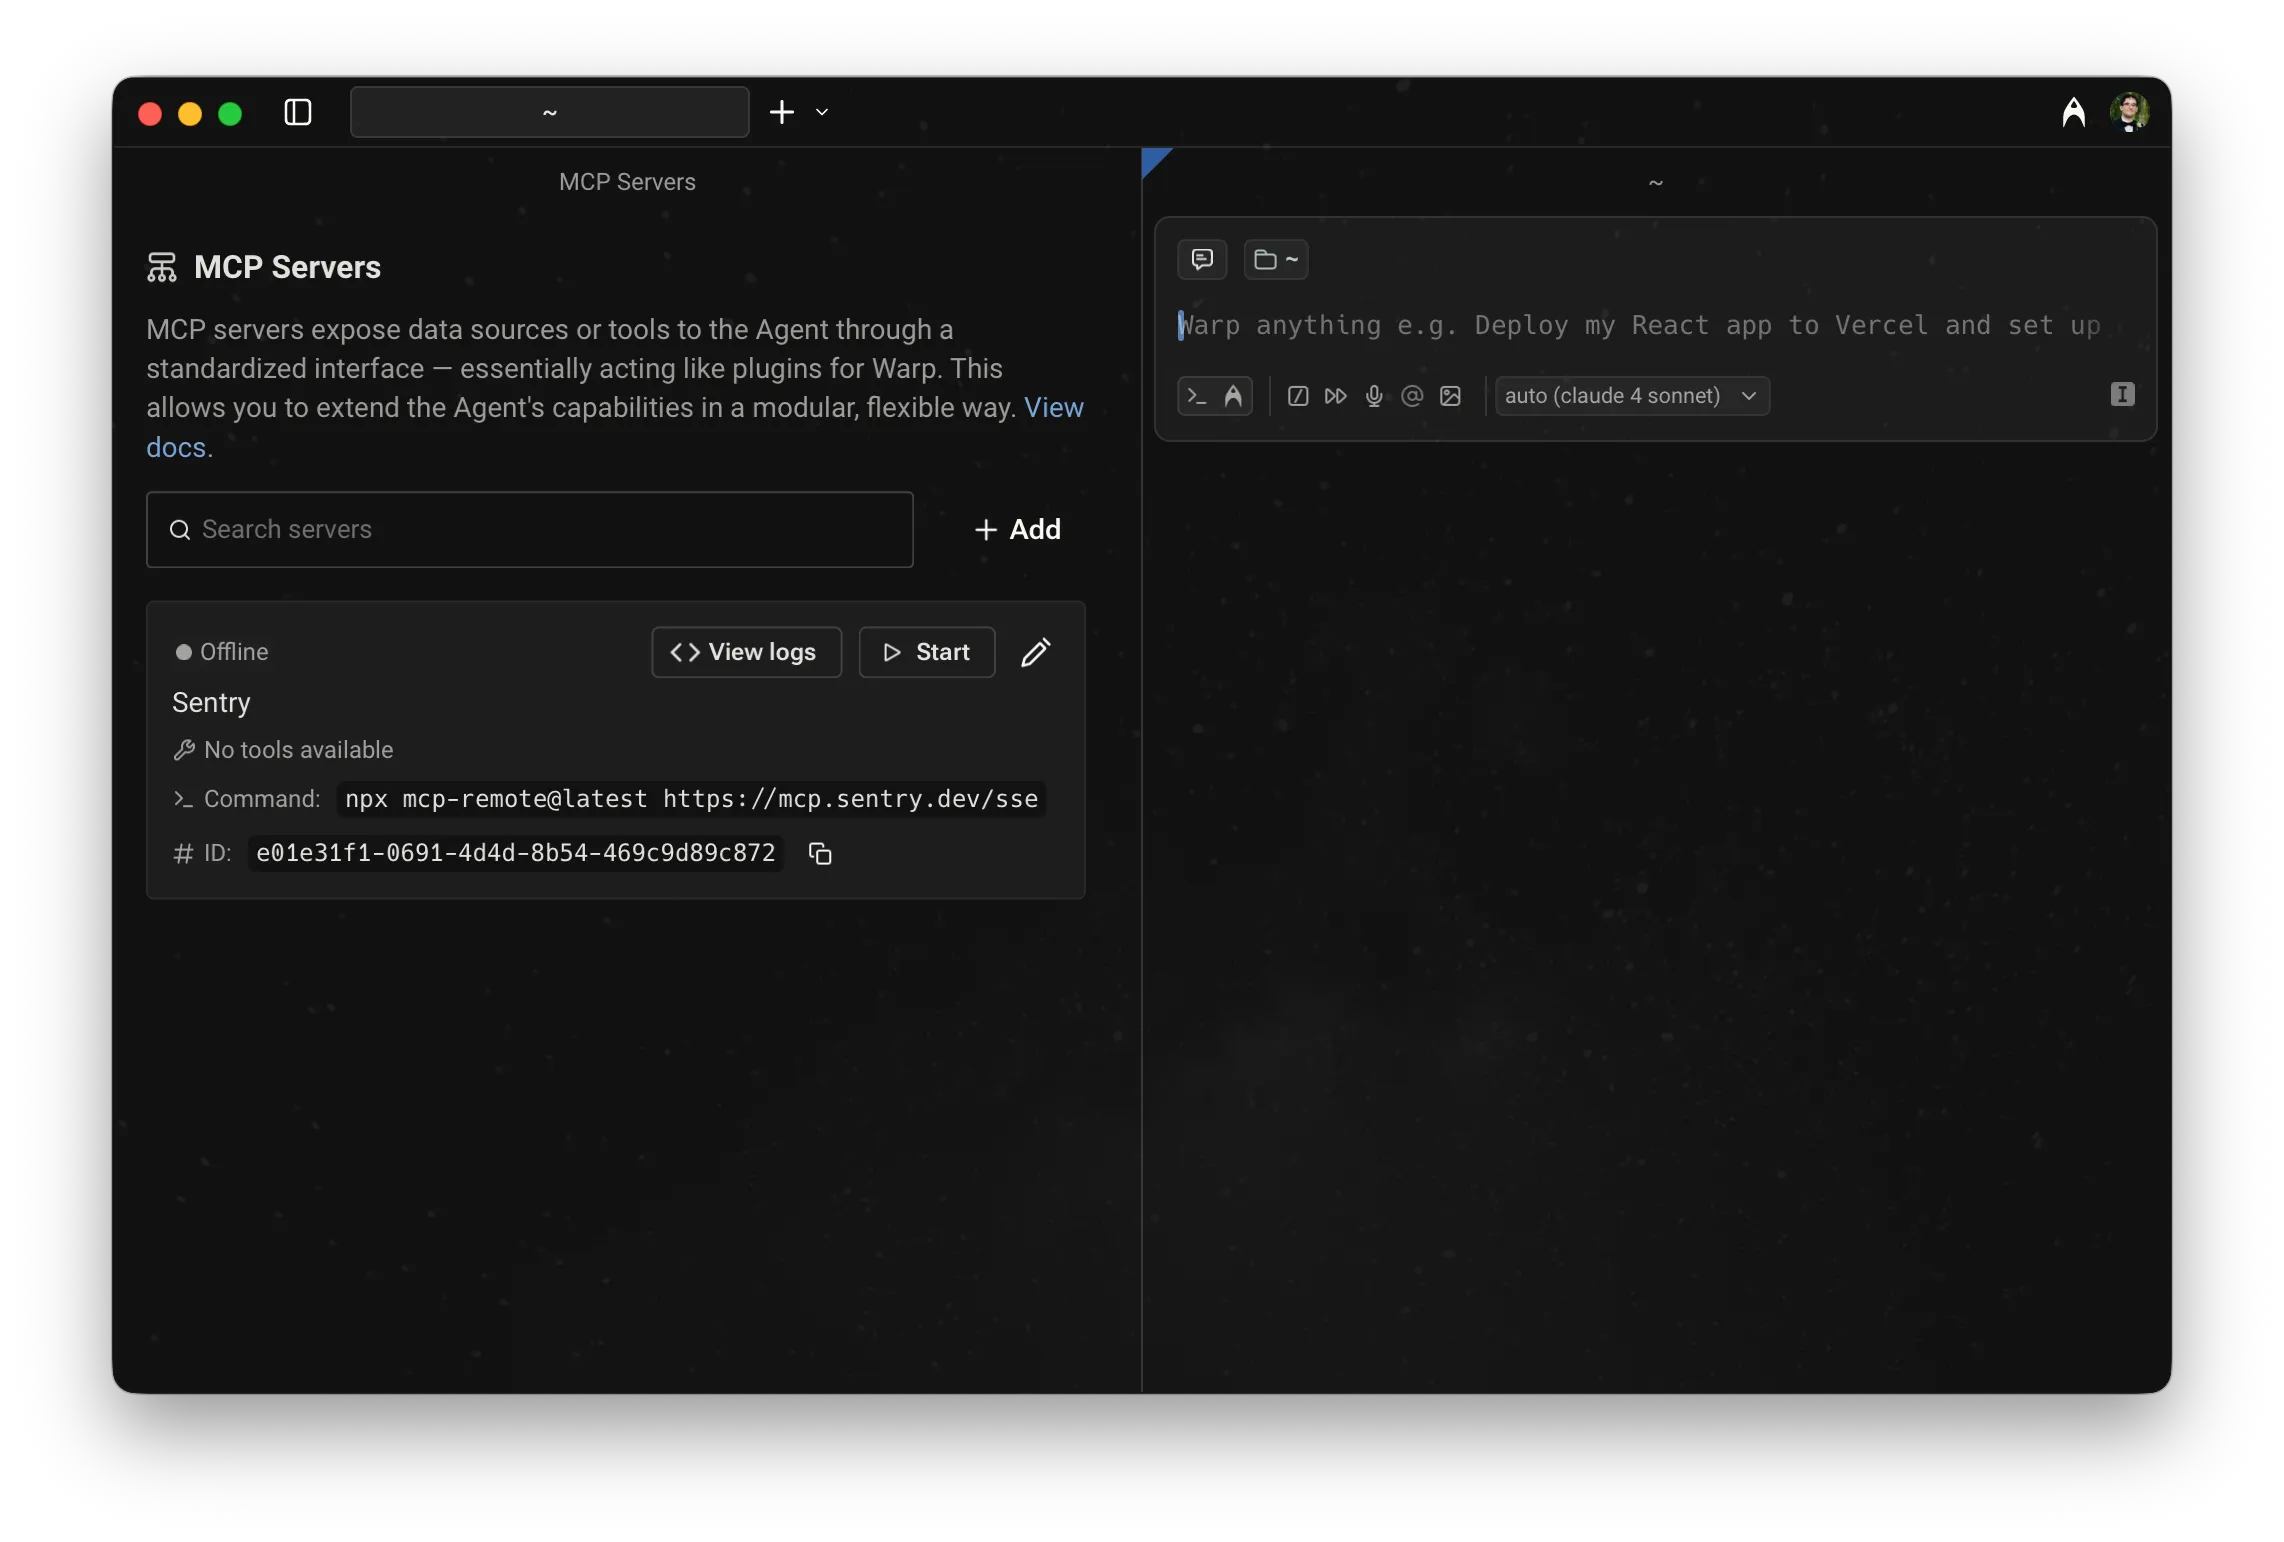
MCP servers page, showing a server with its UUID.
2. Pass the UUID to `--mcp`:
```sh
$ oz agent run --mcp "1deb1b14-b6e5-4996-ae99-233b7555d2d0" --prompt "who last updated the README?"
```
### Passing Warp-managed integration servers by id
[Section titled “Passing Warp-managed integration servers by id”](#passing-warp-managed-integration-servers-by-id)
Some MCP servers are hosted by Warp and backed by an [integration](/platform/integrations/) your team has already connected, so they have no UUID of their own. Reference them by their short id instead:
```sh
$ oz agent run --mcp linear --prompt "summarize the tickets assigned to me"
```
Warp recognizes these managed integration ids:
* `linear` — the hosted [Linear](/platform/integrations/linear/) MCP server
* `slack` — the hosted [Slack](/platform/integrations/slack/) MCP server
* `jira` — the hosted [Jira](/platform/integrations/jira/) MCP server
Caution
`linear` and `slack` resolve only for runs executing inside a [factory](/factories/) with that integration connected; `jira` also resolves for a run triggered directly by a Jira event. Outside those cases — including a plain `oz agent run` like the example above — the server is silently skipped and the run continues without it.
The id is resolved when the run starts, using the integration connection that belongs to the run’s team. If the id isn’t one Warp recognizes, the server is also skipped.
### Passing MCP servers as inline JSON or a file
[Section titled “Passing MCP servers as inline JSON or a file”](#passing-mcp-servers-as-inline-json-or-a-file)
You can pass MCP configuration inline or via a file:
```sh
# Inline JSON
$ oz agent run --mcp '{"github": {"url": "https://api.githubcopilot.com/mcp/"}}' --prompt "list open issues"
# From a file
$ oz agent run --mcp ./my-mcp-config.json --prompt "list open issues"
```
The file must contain a valid MCP JSON object. For example:
```json
{
"github": {
"url": "https://api.githubcopilot.com/mcp/"
},
"sentry": {
"command": "npx",
"args": ["-y", "mcp-remote@latest", "https://mcp.sentry.dev/mcp"]
}
}
```
### Combining multiple servers
[Section titled “Combining multiple servers”](#combining-multiple-servers)
Pass `--mcp` multiple times to combine UUID references, inline JSON, and file-based configs in a single run:
```sh
$ oz agent run \
--mcp "1deb1b14-b6e5-4996-ae99-233b7555d2d0" \
--mcp '{"sentry": {"url": "https://mcp.sentry.dev/mcp"}}' \
--prompt "open a PR that fixes the top Sentry error"
```
***
## Environment variables on remote machines
[Section titled “Environment variables on remote machines”](#environment-variables-on-remote-machines)
Warp syncs MCP server configuration between machines logged in with your Warp account, but **does not** sync the environment variables used in that configuration. When running on a remote machine, set any required secrets manually before running the agent:
```sh
export MY_MCP_SERVER_ACCESS_TOKEN="..."
$ oz agent run --mcp "904a8936-fa82-4571-b1d6-166c26197981" --prompt "use my MCP server to check for errors"
```
Note
For cloud agent workflows, use [Automation Platform-managed secrets](/platform/secrets/) to store and inject credentials safely — secrets are stored in the cloud and referenced by name in your config. For local runs, a secrets manager CLI such as [`op`](https://developer.1password.com/docs/cli/get-started/), [`pass`](https://www.passwordstore.org/), or [`gcloud secrets versions access`](https://cloud.google.com/secret-manager/docs/create-secret-quickstart#secretmanager-quickstart-gcloud) can fetch secrets on remote hosts without exposing them in your shell history.
***
## Learn more
[Section titled “Learn more”](#learn-more)
* [MCP Servers (cloud agents)](/platform/mcp/) — configuration schema, full agent config file examples, and cloud agent limitations
* [Model Context Protocol (MCP)](/agents/capabilities/mcp/) — configuring MCP servers in Warp for local agents
* [Connect developer tools to agents with MCP workflows](/guides/external-tools/using-mcp-servers-with-warp/) — choose the setup path for local sessions, cloud runs, team sharing, and repeatable automation
* [Secrets](/platform/secrets/) — store credentials in Warp so agents can access them at run time without exposing them in config files
# CLI quickstart
Canonical page: [/agents/cli/oz-cli/quickstart/](https://docs.warp.dev/agents/cli/oz-cli/quickstart/)
> Set up and run your first cloud agent via the Oz CLI in less than 5 minutes.
Caution
The Oz CLI (the `oz` binary) is a supported legacy interface. Existing users do not need to change their workflows. For new multi-stage development workflows, use [Warp Factories](/factories/). Warp will publish guidance before any support change.
This guide walks you through the essentials to get up and running with the Oz CLI in less than 5 minutes: installing the CLI, authenticating, running your first local agent, and optionally connecting MCP servers to give the agent access to external tools.
Watch this short demo of the Oz CLI workflow:
## 1. Install the CLI
[Section titled “1. Install the CLI”](#1-install-the-cli)
If you already have the [Warp desktop app installed](/getting-started/quickstart/installation-and-setup/), the **CLI is included** and available in Warp.
If not, see [Installing the CLI](/agents/cli/oz-cli/#installing-the-cli) for installation options for all platforms.
## 2. Authenticate
[Section titled “2. Authenticate”](#2-authenticate)
For local development and first-time setup, authenticate interactively using the `oz login` command.
**For example, on macOS:**
```sh
oz login
```
This command prints a sign-in URL in your terminal. Open the URL in your browser to login to Warp. Your credentials will be stored securely for future CLI use.
Interactive login works on both **local** and **remote** machines, and does not require API keys.
Note
**Running in CI or a headless environment?** Use an API key instead of `oz login`. Export it before running any `oz` command:
```sh
export WARP_API_KEY="wk-..."
```
Create an API key in the [Oz web app](https://oz.warp.dev/settings). See [API Keys](/agents/cli/oz-cli/api-keys/) for guidance on personal vs. [agent keys](/platform/agents/) and on security best practices.
## 3. Run an agent
[Section titled “3. Run an agent”](#3-run-an-agent)
From any directory, run:
```sh
oz agent run --prompt "summarize this directory"
```
This uses the default agent profile and executes the run locally. The default profile permits MCP actions but does not automatically start every configured server. Select run-scoped servers with `--mcp`, or use a profile that allowlists installed servers. See [MCP servers](/agents/cli/oz-cli/mcp-servers/) for the available startup paths.
What happens:
* The agent runs locally in your current working directory.
* The session is tracked on Warp’s backend for observability and collaboration.
* The agent autonomously executes commands and streams output to your terminal.
## 4. Run a cloud agent (optional)
[Section titled “4. Run a cloud agent (optional)”](#4-run-a-cloud-agent-optional)
Cloud agents run in a remote environment with your repositories cloned and dependencies installed, making them useful for tasks that need full codebase access.
If you haven’t already created an environment, run `/create-environment` in Warp or follow the [Cloud Agents Quickstart](/platform/quickstart/). Then run the following command:
```sh
oz agent run-cloud --environment <ENV_ID> --prompt "Scan this repo for outdated dependencies"
```
Replace `<ENV_ID>` with your environment ID, which you can find by running `oz environment list` on the Oz CLI.
## 5. Add MCP context (optional)
[Section titled “5. Add MCP context (optional)”](#5-add-mcp-context-optional)
You can connect MCP servers to give the agent access to external tools like GitHub or Linear. Pass MCP configuration inline or from a file using the `--mcp` flag:
```sh
oz agent run --mcp '{"github": {"url": "https://api.githubcopilot.com/mcp/"}}' --prompt "Open a pull request that fixes TODOs in this repo"
```
See [MCP Servers](/agents/cli/oz-cli/mcp-servers/) for all supported formats, including UUID references and multi-server configurations.
## Next steps
[Section titled “Next steps”](#next-steps)
Once you’ve successfully set up and run your agent, explore other configurations and workflows with the Oz CLI:
* Customize behavior with [agent profiles](/agents/cli/oz-cli/agent-profiles/).
* [Reuse prompts](/agents/cli/oz-cli/warp-drive/) with `--saved-prompt`.
* Connect agents to external systems using [MCP Servers](/agents/cli/oz-cli/mcp-servers/).
* Authenticate with [API keys](/agents/cli/oz-cli/api-keys/) for automated environments or workflows.
* Get up-to-date information about the Oz CLI using the [`oz help` command](/agents/cli/oz-cli/troubleshooting/#getting-help).
* Run agents in CI with the [GitHub Actions quickstart](/platform/integrations/quickstart-github-actions/).
Continue reading the [Oz CLI reference](/agents/cli/oz-cli/) to learn how to install the CLI on different platforms, authenticate in different environments, and configure agents for real-world workflows.
# Skills via the Oz CLI
Canonical page: [/agents/cli/oz-cli/skills/](https://docs.warp.dev/agents/cli/oz-cli/skills/)
> Use skills with the Oz CLI to run agents from reusable skill definitions stored in your repositories.
Caution
The Oz CLI (the `oz` binary) is a supported legacy interface. Existing users do not need to change their workflows. For new multi-stage development workflows, use [Warp Factories](/factories/). Warp will publish guidance before any support change.
[Skills](/agents/capabilities/skills/) are reusable instruction sets that teach agents how to perform specific tasks. Use the `--skill` flag to run an agent from a skill in a repository accessible to your environment.
## Skill spec format
[Section titled “Skill spec format”](#skill-spec-format)
The `--skill` flag accepts a skill specification that identifies which skill to use:
```sh
# Fully qualified (recommended)
oz agent run-cloud -e <ENV_ID> --skill "owner/repo:skill-name" --prompt "deploy to staging"
# With full path
oz agent run-cloud -e <ENV_ID> --skill "warpdotdev/warp-server:.warp/skills/deploy/SKILL.md" --prompt "deploy to staging"
```
Supported formats:
* `owner/repo:skill-name` — skill by name in a specific repository (recommended)
* `owner/repo:path/to/SKILL.md` — skill by full path in a repository
* `repo:skill-name` — skill by name (only works when the repo is configured in your environment)
## Using skills with cloud agents
[Section titled “Using skills with cloud agents”](#using-skills-with-cloud-agents)
Skills are particularly useful with cloud agents (`oz agent run-cloud`) because they define reusable workflows that run consistently across environments:
```sh
# Run a deploy skill from a specific repo
oz agent run-cloud \
--environment SVhg783GBFQHk1OfdPfFU9 \
--skill "myorg/backend:.warp/skills/deploy/SKILL.md" \
--prompt "deploy to staging"
# Run a code review skill
oz agent run-cloud \
--environment SVhg783GBFQHk1OfdPfFU9 \
--skill "myorg/backend:code-review" \
--prompt "review the latest PR"
```
Note
When you specify a skill, it provides the base instructions for the agent. The `--prompt` adds additional context or parameters for that specific run.
When you run an agent from a skill, the run `name` is automatically set to the skill name — no need to pass `--name` explicitly.
## Using skills with local agents
[Section titled “Using skills with local agents”](#using-skills-with-local-agents)
For local agent runs, skills from your current repository are automatically discovered. You can also explicitly specify a skill:
```sh
oz agent run --skill "owner/repo:skill-name" --prompt "additional context"
```
For more information about creating and managing skills, see [Skills](/agents/capabilities/skills/).
# CLI Troubleshooting
Canonical page: [/agents/cli/oz-cli/troubleshooting/](https://docs.warp.dev/agents/cli/oz-cli/troubleshooting/)
> Solutions for common Oz CLI errors — including authentication issues, agent failures, environments, GitHub access, and Docker image issues.
Caution
The Oz CLI (the `oz` binary) is a supported legacy interface. Existing users do not need to change their workflows. For new multi-stage development workflows, use [Warp Factories](/factories/). Warp will publish guidance before any support change.
Solutions for common Oz CLI errors, including authentication issues, agent failures, environment configuration, GitHub access problems, and Docker image compatibility. Use `oz help` for built-in documentation on any command.
## Getting help
[Section titled “Getting help”](#getting-help)
The CLI includes built-in documentation for all commands:
```bash
# See all available commands
oz help
# Get details on a specific command
oz help agent run
# Explore MCP-related commands
oz help mcp
```
## Common errors
[Section titled “Common errors”](#common-errors)
**Command not found / CLI not installed correctly**\
Verify your installation path and confirm the CLI version:
```bash
oz --version
```
**Authentication issues**
* Interactive login: ensure you’ve completed the browser-based flow with `oz login`.
* API keys: confirm the key is valid, not expired, and exported correctly. Invalid, expired, or missing keys can return an [`authentication_required` error](/factories/api-and-sdk/troubleshooting/errors/authentication-required/).
**Agent or MCP errors**\
Ensure your agent profile and [MCP servers](/agents/capabilities/mcp/) are configured properly, with correct permissions. See [MCP Servers](/agents/cli/oz-cli/mcp-servers/) and [Agent profiles](/agents/cli/oz-cli/agent-profiles/) for details.
***
## Environments
[Section titled “Environments”](#environments)
#### How do I see what environment my integration is using?
[Section titled “How do I see what environment my integration is using?”](#how-do-i-see-what-environment-my-integration-is-using)
List your integrations:
```plaintext
oz integration list
```
This shows each integration, its ID, and the environment it’s linked to. Use this to confirm which environment to inspect or update before making changes.
#### How do I see what’s inside that environment?
[Section titled “How do I see what’s inside that environment?”](#how-do-i-see-whats-inside-that-environment)
Once you know the environment ID, run:
```plaintext
oz environment get <ENV_ID>
```
This prints the full configuration, including:
* The **environment ID** (used in other commands)
* The **name**
* The **Docker image**
* Associated **repos**
This is the most reliable way to verify what the agent will see when it runs.
#### How do I add or remove repos and setup commands?
[Section titled “How do I add or remove repos and setup commands?”](#how-do-i-add-or-remove-repos-and-setup-commands)
Use `oz environment update`. You can modify environments incrementally without recreating them.
**Add a repo:**
```plaintext
oz environment update <ENV_ID> --repo owner/repo
```
**Remove a repo:**
```plaintext
oz environment update <ENV_ID> --remove-repo owner/repo
```
**Add a setup command:**
```plaintext
oz environment update <ENV_ID> --setup-command "your command"
```
**Remove a setup command (must match exactly):**
```plaintext
oz environment update <ENV_ID> --remove-setup-command "exact command"
```
Notes:
* Warp may prompt you to adjust GitHub app permissions when adding repos.
* Setup commands run in the order they are defined.
#### **How do I delete an environment?**
[Section titled “How do I delete an environment?”](#how-do-i-delete-an-environment)
If an environment is no longer needed:
```plaintext
oz environment delete <ID>
```
Add `--force` to skip confirmation checks for environments used by integrations.
Only do this once you’ve confirmed no active integrations are relying on that environment. If an integration points to a deleted environment, requests from Slack/Linear will fail with a [`resource_not_found` error](/factories/api-and-sdk/troubleshooting/errors/resource-not-found/) until you create a new integration with a valid environment.
### Integrations
[Section titled “Integrations”](#integrations)
#### **How do I figure out what environment my integration is using?**
[Section titled “How do I figure out what environment my integration is using?”](#how-do-i-figure-out-what-environment-my-integration-is-using)
List your integrations:
```plaintext
oz integration list
```
This shows each integration, its ID, and the environment it’s attached to. Use this when you’re unsure which environment to update or delete.
#### **I created a new environment, but don’t see it when running oz integration create**
[Section titled “I created a new environment, but don’t see it when running oz integration create”](#i-created-a-new-environment-but-dont-see-it-when-running-oz-integration-create)
Check:
1. Environment exists and is healthy: `oz environment list`
2. You’re on the correct Warp team. Make sure your local CLI is logged into the same team where the environment was created.
1. If both look correct and the environment still doesn’t appear, recreate it and confirm there were no errors during creation.
## GitHub & repo access issues
[Section titled “GitHub & repo access issues”](#github--repo-access-issues)
#### **I’m being asked to authorize GitHub when creating/using an environment**
[Section titled “I’m being asked to authorize GitHub when creating/using an environment”](#im-being-asked-to-authorize-github-when-creatingusing-an-environment)
This happens when:
* You add a repo that Warp doesn’t have access to yet, or
* You personally haven’t granted the Warp GitHub app permissions for that repo.
Follow the GitHub popup flow to install/adjust the Warp GitHub app. Missing external authorization can return an [`external_authentication_required` error](/factories/api-and-sdk/troubleshooting/errors/external-authentication-required/).
#### **The agent can’t open PRs or push changes to my repo**
[Section titled “The agent can’t open PRs or push changes to my repo”](#the-agent-cant-open-prs-or-push-changes-to-my-repo)
Check the following:
1. **Repo is part of your environment**.
1. Make sure the repo is listed in: `oz environment get <id>`
2. **Warp GitHub app has access to that repo**
1. In GitHub’s settings, confirm the Warp app is installed and that the repo is selected.
3. **You have write access**
1. The agent inherits your GitHub permissions. If you only have read access, Warp can’t open PRs or push branches on your behalf, and the run may return a [`not_authorized` error](/factories/api-and-sdk/troubleshooting/errors/not-authorized/).
### Docker image & environment failures
[Section titled “Docker image & environment failures”](#docker-image--environment-failures)
#### **I see errors like “pull access denied” or “repository does not exist”**
[Section titled “I see errors like “pull access denied” or “repository does not exist””](#i-see-errors-like-pull-access-denied-or-repository-does-not-exist)
Check:
1. The Docker image name and tag are correct.
2. The image is public on Docker Hub.
3. You can pull it locally: `docker pull <image_name>`
If local docker pull fails, fix the image visibility/name first, then recreate or update the environment with a working image. Image pull and setup failures can surface as [`environment_setup_failed`](/factories/api-and-sdk/troubleshooting/errors/environment-setup-failed/).
#### **The agent can’t find tools or runtimes inside the environment**
[Section titled “The agent can’t find tools or runtimes inside the environment”](#the-agent-cant-find-tools-or-runtimes-inside-the-environment)
This usually means the Docker image is missing required dependencies. Fix by either:
* Updating the Dockerfile used to build the image, then pushing a new version to Docker Hub and updating the environment with the new image, or
* Adding additional setup commands to install the missing tools: `oz environment update --setup-command "apt-get update && apt-get install -y "`
#### **I see “VM failed before the agent could run. This is likely an issue with your Docker image”**
[Section titled “I see “VM failed before the agent could run. This is likely an issue with your Docker image””](#i-see-vm-failed-before-the-agent-could-run-this-is-likely-an-issue-with-your-docker-image)
This typically means your Docker image uses musl libc instead of glibc. Alpine Linux and other musl-based images are not compatible with the agent runtime, and this can surface as [`environment_setup_failed`](/factories/api-and-sdk/troubleshooting/errors/environment-setup-failed/).
Fix:
* Switch to a glibc-based image such as Debian, Ubuntu, or the default (non-Alpine) variants of official Docker Hub images (e.g. `node`, `python`, `rust`).
* If you’re using an Alpine variant like `node:20-alpine`, replace it with the default tag (e.g. `node:20`).
# Warp Drive context
Canonical page: [/agents/cli/oz-cli/warp-drive/](https://docs.warp.dev/agents/cli/oz-cli/warp-drive/)
> Use saved prompts, notebooks, workflows, and rules from Warp Drive as context in CLI agent commands.
Caution
The Oz CLI (the `oz` binary) is a supported legacy interface. Existing users do not need to change their workflows. For new multi-stage development workflows, use [Warp Factories](/factories/). Warp will publish guidance before any support change.
Reference saved Warp Drive objects in Oz CLI commands to reuse prompts, notebooks, workflows, and rules as agent context. Pass a saved prompt ID with `--saved-prompt` or inline Warp Drive references using `<workflow:id>`, `<notebook:id>`, or `<rule:id>` syntax.
## Reusing saved prompts
[Section titled “Reusing saved prompts”](#reusing-saved-prompts)
When you find prompts that work well, save them in [Warp Drive](/knowledge-and-collaboration/warp-drive/) to reuse across sessions, share with teammates, and integrate into automated workflows. For more information, see [Prompts](/knowledge-and-collaboration/warp-drive/prompts/).
To reuse a saved prompt, find its ID. The ID is the last segment of its Warp Drive sharing link.
For example, in the URL:
```plaintext
https://www.warp.dev/drive/prompt/Fix-compiler-error-sgNpbUgDkmp2IImUVDc8kR
```
…the ID is `sgNpbUgDkmp2IImUVDc8kR`.
Then pass the ID using the `--saved-prompt` flag:
```bash
$ oz agent run --saved-prompt sgNpbUgDkmp2IImUVDc8kR
```
## Referencing Warp Drive objects as context
[Section titled “Referencing Warp Drive objects as context”](#referencing-warp-drive-objects-as-context)
Use `<workflow:id>`, `<notebook:id>`, or `<rule:id>` in prompts to attach [Warp Drive objects](/knowledge-and-collaboration/warp-drive/) and [rules](/agents/capabilities/rules/) as context for the agent.
Note
**Tip:** Use the [@ context menu](/agents/local-agents/agent-context/using-to-add-context/) in Warp to construct a prompt with the right references, then copy it into your CLI command.
```bash
$ oz agent run --prompt "Follow the instructions in <notebook:gq1CMAUWLtaL1CpEoTDQ3y>"
```
# Permissions and profiles in the Warp Agent CLI
Canonical page: [/agents/cli/permissions-and-profiles/](https://docs.warp.dev/agents/cli/permissions-and-profiles/)
> Control what the agent can do in the Warp Agent CLI with permission request cards, auto-approve, and execution profiles in the settings file.
The Warp Agent CLI uses the same permission model as the Warp app: you choose how much approval each type of action needs. This page covers how to set permissions in the CLI, what happens when the agent asks for approval, and how to grant full autonomy with auto-approve. For the full permission model, including team-wide controls, see [Profiles & Permissions](/agents/capabilities/agent-profiles-permissions/).
## How permissions work
[Section titled “How permissions work”](#how-permissions-work)
Every action the agent proposes, such as running a shell command, editing files, or calling an MCP tool, is checked against your active execution profile before it runs. Each action type is set independently to [`always_ask`, `always_allow`, or `agent_decides`](#permission-values). For example, you could require approval for every shell command while letting the agent read files without asking, or allow everything for an agent that never stops to ask.
By default, the CLI applies these permission values:
* **Shell commands, file edits, file reads, MCP tool calls** - `agent_decides`. For file edits, `agent_decides` still prompts every time, so you always review a diff before it’s applied.
* **Typing into a running command, launching child agents** - Always asks.
* **Command denylist** - Sits on top of these values. Matching commands require approval even when `execute_commands` is `always_allow`.
Change any of this by [editing your execution profile](#execution-profiles).
## Approving agent actions
[Section titled “Approving agent actions”](#approving-agent-actions)
When an action needs your approval, the agent pauses and shows a permission card with the proposed command or file edits. Beyond approving or rejecting it, you can:
* Select **Other** to reply with guidance instead of running the action. The agent adjusts its approach based on what you type.
* Press `E` on a command card to edit it before approving. `Esc` exits the editor without rejecting the request.
* Press `E` on a file-edits card to expand or collapse all diffs.
## Auto-approve
[Section titled “Auto-approve”](#auto-approve)
Auto-approve gives the agent full autonomy. Proposed actions run immediately, without permission cards, until the task finishes or you turn it off. Toggle it with `/auto-approve` or `Ctrl+Shift+I`.
Auto-approve is scoped to a single conversation, and new conversations start with it off. To start every new conversation in a session with auto-approve already on, launch with `warp --auto-approve`. The statusline’s auto-approve indicator (`▶▶`) shows the current state and is on by default. If your profile sets `ask_user_question = "ask_except_in_auto_approve"`, the agent also skips clarifying questions while auto-approve is on.
Danger
With auto-approve on, the agent runs commands and applies file edits without review, including commands that match your own command denylist. Press `Ctrl+C` to stop the agent if it starts doing something you didn’t intend.
To keep your denylist in force while auto-approve is on, turn off the bypass in your [settings file](/agents/cli/configuration/#the-settings-file):
settings.toml
```toml
[agents.warp_agent.other]
auto_approve_bypasses_command_denylist = false
```
Denylist rules enforced by your team in the [Admin Panel](/enterprise/team-management/admin-panel/) always require approval and are never bypassed, regardless of this setting.
## Execution profiles
[Section titled “Execution profiles”](#execution-profiles)
The CLI reads its permissions from execution profiles stored in its [settings file](/agents/cli/configuration/). Profiles live under the `agents.execution_profiles` table, and the CLI always runs with the profile under the reserved `default` key:
settings.toml
```toml
[agents.execution_profiles.default]
name = "Default"
execute_commands = "agent_decides"
apply_code_diffs = "agent_decides"
read_files = "agent_decides"
command_allowlist = ['cargo (build|check|test)(\s.*)?']
```
Caution
Setting `command_denylist` replaces the built-in default denylist, which covers `rm`, `curl`, `wget`, `eval`, `ssh`, shells, and other risky command patterns. Omitting the field keeps the defaults. To deny additional commands, extend the generated list in your settings file rather than writing a short list from scratch.
Edit the file directly, or ask the agent to change its own permissions and it will update the settings file for you. The CLI picks up saved changes automatically.
Profiles in the Warp Agent CLI are local to your machine. They never sync to the cloud, and they are separate from the Agent Profiles you configure in the Warp app. You can define additional profiles in the file, but the CLI currently always runs with `default`.
### Permission values
[Section titled “Permission values”](#permission-values)
Most permission fields accept one of three values:
* **`agent_decides`** - The agent acts on its own when it’s confident and asks when it’s uncertain.
* **`always_ask`** - Every action of this type requires approval.
* **`always_allow`** - Actions of this type run without prompting.
### Profile fields
[Section titled “Profile fields”](#profile-fields)
* **`execute_commands`** - Permission to run shell commands.
* **`apply_code_diffs`** - Permission to apply file edits.
* **`read_files`** - Permission to read files.
* **`mcp_permissions`** - Permission to call MCP servers.
* **`write_to_pty`** - Permission to type into running interactive commands. Also accepts `ask_on_first_write`.
* **`ask_user_question`** - Whether the agent may pause to ask clarifying questions: `always_ask`, `ask_except_in_auto_approve`, or `never`.
* **`run_agents`** - Permission to launch child agents: `always_ask`, `always_allow`, or `never_allow`.
* **`command_allowlist`** - Regular expressions for commands that run without approval.
* **`command_denylist`** - Regular expressions for commands that require approval regardless of the other permission values. [Auto-approve bypasses this list by default](#auto-approve).
* **`directory_allowlist`** - Directories the agent may read without approval.
Profiles also hold model overrides such as `base_model`, covered in [Models and usage in the Warp Agent CLI](/agents/cli/models-and-usage/).
Note
The profile collection is validated as a whole. If any profile contains an invalid value, the CLI keeps the last valid configuration while it’s running and falls back to the built-in default profile on the next launch, until the file is fixed.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Profiles & Permissions](/agents/capabilities/agent-profiles-permissions/) - The full permission model, autonomy levels, and allowlist/denylist behavior.
* [Configuring the Warp Agent CLI](/agents/cli/configuration/) - The settings file, themes, statusline, and start screen.
* [Agent conversations in the Warp Agent CLI](/agents/cli/agent-conversations/) - How tool calls, diffs, and agent questions render in the transcript.
# Warp Agent CLI quickstart
Canonical page: [/agents/cli/quickstart/](https://docs.warp.dev/agents/cli/quickstart/)
> Install the Warp Agent CLI, log in, and run your first agent conversation in your own terminal in a few minutes.
This guide takes you from installing the Warp Agent CLI to your first agent conversation in about five minutes.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **A Warp account** - The login step opens your browser, where you can sign in or [create an account](https://app.warp.dev/signup). The CLI uses the same account as the Warp app, but doesn’t require the app to be installed.
* **A supported platform** - macOS (Apple Silicon or Intel), Linux (x64 or Arm64), or Windows (x64 or Arm64).
## 1. Install the Warp Agent CLI
[Section titled “1. Install the Warp Agent CLI”](#1-install-the-warp-agent-cli)
Install the CLI with the command for your operating system. The install script is the recommended method, because it’s the only one that keeps the CLI up to date on its own.
* macOS and Linux
```bash
curl -fsSL https://app.warp.dev/download/agent-cli | bash
```
* Windows
Run this command in PowerShell:
```powershell
Invoke-RestMethod "https://app.warp.dev/download/agent-cli.ps1" | Invoke-Expression
```
* Homebrew
On macOS 14 or later and on Linux, install the `warp-agent-cli` cask. It’s in the main Homebrew cask repository, so you don’t need to tap anything first:
```bash
brew install --cask warp-agent-cli
```
Caution
Homebrew installations don’t update themselves. The CLI still tells you when a new version is available, but you install it by running `brew upgrade --cask warp-agent-cli`. To get background updates instead, use the install script.
After installing, verify that the `warp` command is available:
```bash
warp --version
```
The command prints the installed version.
Note
How the CLI updates depends on how you installed it.
* **Install script** - The CLI updates itself. While it runs, it periodically checks for a newer version, downloads it in the background, and stages it without interrupting your session. The staged version takes effect the next time you launch `warp`, and the start screen shows an “update installed, restart to apply” notice next to the version.
* **Homebrew** - Homebrew owns the installation, so the CLI never replaces it. It still checks for newer versions and shows an “update available” notice next to the version on the start screen. Install the update yourself by running `brew upgrade --cask warp-agent-cli`.
To turn off update checks, set `general.autoupdate_enabled` to `false` in the [settings file](/agents/cli/configuration/#the-settings-file). To turn them off for a single launch, set the `WARP_TUI_DISABLE_AUTOUPDATE` environment variable to any value.
## 2. Log in
[Section titled “2. Log in”](#2-log-in)
Log in once so the CLI can access your Warp account, models, and saved context. Start the CLI:
```bash
warp
```
The CLI shows a verification link and a device code, and opens the link in your browser. Approve the login there and the CLI unlocks automatically, so you don’t need to restart it. If the browser doesn’t open, visit the link shown in the CLI and enter the code.
When login completes, the CLI shows its start screen with the version, a short “What’s new” list, and the rules, skills, and MCP servers it discovered for your current directory. You stay signed in across sessions. To sign out later, run `/logout`, which returns the CLI to its login screen and signs out your browser session too.
Note
**Running in CI or a headless environment?** Authenticate with a Warp API key instead by setting the `WARP_API_KEY` environment variable:
```bash
WARP_API_KEY=YOUR_API_KEY warp
```
You can also pass the `--api-key` flag, but prefer the environment variable. Command-line arguments can be captured in shell history and process listings. See [API keys](/agents/cli/oz-cli/api-keys/) to learn how to create one.
## 3. Run your first prompt
[Section titled “3. Run your first prompt”](#3-run-your-first-prompt)
Type a prompt in plain language, such as `What does this project do?`, and press `Enter`.
If the agent wants to run a command or edit a file, it shows a permission request. Choose an option to approve or reject the action.
Learn more about the transcript, diffs, and approvals in [Agent conversations](/agents/cli/agent-conversations/) and [Permissions and profiles](/agents/cli/permissions-and-profiles/).
## 4. Run a shell command
[Section titled “4. Run a shell command”](#4-run-a-shell-command)
You can run shell commands directly without leaving the CLI.
Type `!` at the start of an empty input to switch to shell mode. The footer shows **Shell mode**. Type a command, such as `git status`, and press `Enter`. To go back to prompting the agent, press `Backspace` on the empty input.
To run recognized shell commands without the `!` prefix, run `/natural-language-detection` to turn on natural language detection. The CLI then classifies input as you type: recognized commands switch to shell mode, while natural-language prompts stay in Agent Mode. The prompt marker and statusline show the active mode before you press `Enter`.
See [Input and shell commands](/agents/cli/input-and-shell-commands/) for long-running commands, interactive programs, and full-screen apps.
## 5. Exit and resume
[Section titled “5. Exit and resume”](#5-exit-and-resume)
Press `Ctrl+C` twice in a row to exit, or run `/exit`. A single `Ctrl+C` press stops the agent’s current response, or clears the input when nothing is running.
On exit, the CLI prints a resume command for the conversation:
```bash
warp --resume CONVERSATION_TOKEN
```
Run the printed command later to pick up where you left off.
To browse and reopen past conversations from inside the CLI, see [Agent conversations](/agents/cli/agent-conversations/#conversation-history).
## Next steps
[Section titled “Next steps”](#next-steps)
* [Agent conversations](/agents/cli/agent-conversations/) - Work with the transcript, code diffs, plans, and tasks.
* [Customizing the CLI](/agents/cli/configuration/) - Rules, skills, MCP servers, themes, and settings.
* [Reference](/agents/cli/reference/) - All flags, slash commands, and keyboard shortcuts.
# Warp Agent CLI reference
Canonical page: [/agents/cli/reference/](https://docs.warp.dev/agents/cli/reference/)
> Look up Warp Agent CLI command-line flags, environment variables, slash commands, keyboard shortcuts, and fixes for common issues.
This page is a lookup reference for the Warp Agent CLI, covering the flags and environment variables the `warp` command accepts, every slash command available in a session, the default keyboard shortcuts, and fixes for common issues.
## Command-line flags
[Section titled “Command-line flags”](#command-line-flags)
Running `warp` with no flags starts an interactive session in the current directory. The following flags change how the CLI starts, or make it perform a one-off action and exit. They are listed alphabetically.
### `--api-key`
[Section titled “--api-key”](#--api-key)
Authenticates with a Warp API key instead of the interactive browser login. Use it on machines that can’t open a browser, such as CI runners and remote servers.
Prefer supplying the key through the `WARP_API_KEY` environment variable:
```bash
WARP_API_KEY=YOUR_API_KEY warp
```
The `--api-key` flag accepts the same value directly:
```bash
warp --api-key YOUR_API_KEY
```
Caution
Command-line arguments can be captured in shell history and process listings. Prefer the `WARP_API_KEY` environment variable, ideally populated from a secret manager.
Create a key in the Warp app under **Settings** > **Cloud platform** > **API keys**. See the [API keys reference](/agents/cli/oz-cli/api-keys/) for details.
### `--auto-approve`
[Section titled “--auto-approve”](#--auto-approve)
Starts new conversations with auto-approve enabled, so the agent runs actions without asking for approval first.
```bash
warp --auto-approve
```
This flag applies only to the session you launch with it and doesn’t change your saved settings. You can still toggle auto-approve per conversation with `/auto-approve` or `Ctrl+Shift+I`. See [permissions and profiles](/agents/cli/permissions-and-profiles/) for how approvals work.
### `--clear-provider-api-key`
[Section titled “--clear-provider-api-key”](#--clear-provider-api-key)
Deletes a stored model-provider API key from your device’s secure storage, then exits.
```bash
warp --clear-provider-api-key <provider>
```
`<provider>` is `openai`, `anthropic`, or `google`. For example:
```bash
warp --clear-provider-api-key anthropic
```
### `--help`
[Section titled “--help”](#--help)
Prints usage information for all flags and exits.
```bash
warp --help
```
### `--resume`
[Section titled “--resume”](#--resume)
Reopens a previous conversation from your shell as the CLI starts.
```bash
warp --resume CONVERSATION_TOKEN
```
`CONVERSATION_TOKEN` is the token the CLI prints when you exit a session (“To continue this conversation, run: `warp --resume ...`”). You can also reopen past conversations from inside a session with `/conversations`. See [agent conversations in the CLI](/agents/cli/agent-conversations/#managing-conversations) for how persistence and resuming work.
### `--set-provider-api-key`
[Section titled “--set-provider-api-key”](#--set-provider-api-key)
Stores a model-provider API key for [Bring Your Own API Key (BYOK)](/agents/inference/bring-your-own-api-key/) in your device’s secure storage, then exits. Warp never stores provider keys on its servers.
```bash
warp --set-provider-api-key <provider>
```
`<provider>` is `openai`, `anthropic`, or `google`. For example:
```bash
warp --set-provider-api-key anthropic
```
The CLI prompts for the key with masked input, so the key never appears in your shell history. When stdin is piped, the key is read from stdin instead, so you can pass it straight from a secret manager without writing it to disk:
```bash
your-secret-manager read anthropic-api-key | warp --set-provider-api-key anthropic
```
Avoid staging keys in plaintext files. If you must use a temporary file, delete it immediately afterward.
Inside a session, manage the same keys with the `/api-keys` menu. See [models and usage](/agents/cli/models-and-usage/#bring-your-own-api-key) for how stored keys affect billing.
### `--version`
[Section titled “--version”](#--version)
Prints the installed version and exits.
```bash
warp --version
```
## Environment variables
[Section titled “Environment variables”](#environment-variables)
* **`WARP_API_KEY`** - A Warp API key for non-interactive authentication. Equivalent to passing `--api-key`.
* **`WARP_TUI_DISABLE_AUTOUPDATE`** - Set it to any value to turn off background updates for a single launch. See [Updating](#updating) for how updates work.
## Slash commands
[Section titled “Slash commands”](#slash-commands)
Type `/` at the start of the input to open the slash command menu. Commands that take an argument show a hint after the command name. Angle brackets mark required arguments, and square brackets mark optional ones.
| Command | Argument | Description |
| ----------------------------- | --------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `/agent` | `[prompt]` | Start a new conversation |
| `/api-keys` | | View and manage model-provider API keys |
| `/auto-approve` | | Toggle auto-approve for agent actions |
| `/clear` | `[prompt]` | Clear the transcript and start a new conversation |
| `/compact` | `[instructions]` | Free up context by summarizing the conversation history |
| `/connect-grok` | | Connect an X Premium or SuperGrok subscription for Grok models |
| `/conversations` | | Open conversation history |
| `/copy-debugging-id` | | Copy the current conversation’s debugging information to the clipboard |
| `/cost` | | Toggle per-response credit usage details |
| `/create-new-project` | `<description>` | Have the agent walk you through creating a new coding project |
| `/exit` | | Exit the CLI |
| `/export-to-clipboard` | | Export the current conversation to the clipboard as Markdown |
| `/export-to-file` | `[filename]` | Export the current conversation to a Markdown file |
| `/fork` | `[prompt]` | Fork the current conversation into a copy, optionally sending a prompt in the copy |
| `/handoff` | `[prompt]` | Hand off this conversation to a cloud agent. See [cloud handoff and orchestration](/agents/cli/cloud-and-orchestration/#hand-off-to-a-cloud-agent) |
| `/logout` | | Log out of Warp |
| `/manage-billing` | | Open your team’s billing page in the browser |
| `/mcp` | | View and manage MCP servers |
| `/model` | | Switch the base agent model |
| `/natural-language-detection` | | Toggle natural language detection for shell input |
| `/new` | `[prompt]` | Start a new conversation (alias for `/agent`) |
| `/orchestrate` | `[task]` | Break a task into subtasks and run them in parallel with multiple agents. See [multi-agent orchestration](/agents/cli/cloud-and-orchestration/#multi-agent-orchestration) |
| `/plan` | `[task]` | Ask the agent to research and create a plan for a task |
| `/reset-statusline` | | Restore the statusline to its default items and ordering |
| `/skills` | | Browse skills in scope and insert one into the input |
| `/status` | | Show session and account status |
| `/statusline` | | Configure the statusline |
| `/team` | | Switch the active team |
| `/theme` | `<auto\|light\|dark>` | Set the color theme |
| `/upgrade` | | Open the Warp upgrade page in the browser |
| `/usage` | | View plan, credit usage, and billing links |
| `/view-logs` | | Bundle your logs into a zip archive |
| `/vim-mode` | | Toggle Vim keybindings in the input |
| `/voice` | | Start voice input |
Some commands appear only when they apply to your account. `/manage-billing` is listed when you administer billing for your team, and opens that team’s billing page; it isn’t available to members without billing access. `/connect-grok` opens the same subscription row as [`/api-keys`](/agents/cli/models-and-usage/#bring-your-own-api-key) and starts the xAI sign-in directly.
`/status` opens a read-only panel with the installed version, the current conversation’s name and ID, the working directory, and the organization and email you’re signed in as. Press `Esc` to close it, and include those details when you report a problem.
`/usage` opens a read-only panel with your plan, credit balances and consumption, and links to manage billing or upgrade. See [models and usage](/agents/cli/models-and-usage/#usage-and-cost).
`/team` opens a searchable list of the teams you belong to, with the active one marked. Type to filter, then press `Enter` to switch. The CLI re-scopes the current session in place, unlike the Warp app, which opens a new window for the team you pick. The active team also appears in the statusline, and clicking it opens the same list.
Skills also appear in the same menu under their own names, so you can invoke a skill directly as `/skill-name`. [Customizing the CLI](/agents/cli/configuration/) covers how skills are discovered.
## Keyboard shortcuts
[Section titled “Keyboard shortcuts”](#keyboard-shortcuts)
Press `?` on an empty input to open the contextual shortcuts panel inside the CLI. The tables below list the default bindings.
Note
Bindings are the same on macOS, Linux, and Windows, except that Windows also accepts `Alt+V` for paste. For shortcuts that use `Alt`, some macOS terminals deliver `Option` as `Alt` only when their Option-as-Alt (Meta) setting is enabled. The macOS Command shortcuts described in [input and shell commands](/agents/cli/input-and-shell-commands/#editing-basics) require a terminal with the Kitty keyboard protocol enabled.
### Session
[Section titled “Session”](#session)
| Shortcut | Action |
| ------------------------- | ---------------------------------------------------------------------------------- |
| `Ctrl+C` | Stop the current response, or clear the input; press again within a second to exit |
| `Ctrl+D` | Exit when the input is empty (deletes the next character otherwise) |
| `?` | Show the shortcuts panel (on an empty input) |
| `/` | Open the slash command menu |
| `!` | Enter shell mode (`Esc` returns to agent input) |
| `←` | Open the conversation list (on an empty input) |
| `↑` | Browse prompt and command history |
| `Esc` | Dismiss the open menu, or leave shell mode |
| `Ctrl+Shift+I` | Toggle auto-approve |
| `Ctrl+Shift+P` | Expand or collapse the latest plan |
| `Ctrl+S` | Start voice input |
| `Ctrl+V` / `Ctrl+Shift+V` | Paste from the clipboard, including images |
| `Tab` | Focus attached images when present; complete shell commands in shell mode |
### Approvals
[Section titled “Approvals”](#approvals)
These bindings apply while the agent is waiting for you to approve an action. [Permissions and profiles](/agents/cli/permissions-and-profiles/) explains the approval flow.
| Shortcut | Action |
| ------------ | ----------------------------------------------------------------------------------- |
| `Enter` | Confirm the selected option on the approval card |
| `Esc` | Reject or cancel the request |
| `E` | Edit the proposed command, or expand and collapse all diffs in a file-edit approval |
| `Ctrl+Enter` | Approve a request to type into a running command |
### Terminal control
[Section titled “Terminal control”](#terminal-control)
These bindings apply while an interactive terminal command is running.
| Shortcut | Action |
| -------- | ---------------------------------------------------------------------------------- |
| `Ctrl+C` | Interrupt a command you started, or take control of a command the agent is running |
| `Ctrl+G` | Hand control of the command back to the agent |
### Multi-agent tabs
[Section titled “Multi-agent tabs”](#multi-agent-tabs)
When an orchestration launches child agents, an **Agents:** tab bar appears above the session. [Cloud and orchestration](/agents/cli/cloud-and-orchestration/) covers the workflow.
| Shortcut | Action |
| -------------------------------- | ---------------------------------------------------------------- |
| `Shift+↑` | Focus the agent tab bar |
| `←` / `→` or `Tab` / `Shift+Tab` | Select the previous or next agent |
| `Shift+←` / `Shift+→` | Select the first or last child agent |
| `↓` | Return focus to the current session’s input |
| `Esc` | Return to the orchestrator |
| `Ctrl+C` | Kill the selected child agent (press twice when viewing a child) |
### Text editing
[Section titled “Text editing”](#text-editing)
The input supports readline-style editing.
| Shortcut | Action |
| --------------------------------------------- | ------------------------------- |
| `Shift+Enter`, `Ctrl+J`, or `Alt+Enter` | Insert a newline |
| `Ctrl+A` / `Home` | Move to the start of the line |
| `Ctrl+E` / `End` | Move to the end of the line |
| `Ctrl+B` / `Ctrl+F` | Move left / right |
| `Alt+B` / `Alt+F` (or `Alt+←` / `Alt+→`) | Move one word left / right |
| `Ctrl+W` or `Alt+Backspace` | Delete the previous word |
| `Alt+D` or `Alt+Delete` | Delete the next word |
| `Ctrl+K` | Delete to the end of the line |
| `Ctrl+U` | Delete to the start of the line |
| `Ctrl+Y` | Reinsert the last deleted text |
| `Ctrl+Z` / `Ctrl+Shift+Z` | Undo / redo |
| `Shift+←` / `Shift+→` / `Shift+↑` / `Shift+↓` | Extend the selection |
| `Ctrl+Shift+A` | Select all |
| `Ctrl+Shift+C` | Copy the selection |
| `Ctrl+X` | Cut the selection |
For mouse support, completions, and other input behavior, see [input and shell commands](/agents/cli/input-and-shell-commands/).
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
This section covers common issues, including gathering logs for a bug report, fixing sign-in problems, resuming conversations, and keeping the CLI up to date.
Note
For known issues and feature requests across Warp, visit the [GitHub issues page](https://github.com/warpdotdev/Warp/issues).
### Viewing and sharing logs
[Section titled “Viewing and sharing logs”](#viewing-and-sharing-logs)
When something goes wrong, logs are the fastest way to help the Warp team diagnose the problem.
Run `/view-logs` in a session to bundle the current session’s log and recent previous sessions into a timestamped zip archive. The CLI reveals the archive in your file manager and shows the saved path in the footer, so you can attach it to a bug report or share it with support.
On macOS, CLI logs are stored in `~/Library/Logs/warp-cli/`. Logs rotate per session, and older session logs are rotated out over time. The `/view-logs` archive is written to the same directory.
When the problem is with the agent’s response rather than the CLI itself, run `/copy-debugging-id` in the session. It copies the conversation’s debugging information to your clipboard so you can paste it into a bug report. See [Gathering AI conversation ID](/support-and-community/troubleshooting-and-support/sending-us-feedback/#gathering-ai-conversation-id).
### The browser doesn’t open during sign-in
[Section titled “The browser doesn’t open during sign-in”](#the-browser-doesnt-open-during-sign-in)
The CLI signs you in with a browser-based flow. It opens a verification page (or shows you the URL and a code to enter) and continues once you approve the sign-in. On a remote or browser-less machine, the CLI can’t launch a browser, but the sign-in screen still shows the verification URL and code.
1. Open the displayed URL in a browser on any device, including another machine.
2. Enter the code shown in the CLI.
3. Return to the CLI. It proceeds automatically once the sign-in is approved.
For machines where the browser flow isn’t practical, authenticate non-interactively with an API key instead, using the `WARP_API_KEY` environment variable or the `--api-key` flag. See [command-line flags](#command-line-flags).
### ”Login failed”
[Section titled “”Login failed””](#login-failed)
The sign-in attempt was rejected or timed out. The error message in the CLI names the underlying cause.
1. Press `Ctrl+C` to exit.
2. Run `warp` again to restart the sign-in flow.
3. If the failure persists, check your network connection and any proxy or firewall that could block access to Warp’s servers.
### Signed in to the wrong account
[Section titled “Signed in to the wrong account”](#signed-in-to-the-wrong-account)
1. Run `/logout` in a session. The CLI signs you out, opens your browser to complete the sign-out on Warp’s website, and returns to the sign-in screen.
2. Sign in with the account you want.
### ”Could not restore conversation” when resuming
[Section titled “”Could not restore conversation” when resuming”](#could-not-restore-conversation-when-resuming)
`warp --resume` failed to load the conversation for the given token, for example because the token is malformed or the conversation is no longer available.
1. Press `Ctrl+C` to exit, then run `warp` to start normally.
2. Check the token against the resume command printed when you exited the original session.
3. If the conversation exists locally, open it from the [conversation menu](/agents/cli/agent-conversations/#conversation-history) with `/conversations` instead.
### Updating
[Section titled “Updating”](#updating)
Update behavior depends on the install method. Native managed installs check, download, and stage updates for the next launch. Homebrew installs check for updates but require `brew upgrade --cask warp-agent-cli`. Unmanaged installs do not use either update path. See the [installation and update guidance](/agents/cli/quickstart/#1-install-the-warp-agent-cli) for details.
To check which version you’re running, use `/status` in a session, or run:
```bash
warp --version
```
To turn off background updates for a single launch, set the `WARP_TUI_DISABLE_AUTOUPDATE` environment variable to any value. To turn them off persistently, set `general.autoupdate_enabled` to `false` in the [CLI settings file](/agents/cli/configuration/#the-settings-file).
If an install becomes corrupted, re-running the install command from the [quickstart](/agents/cli/quickstart/) replaces it with the latest version.
### Getting help
[Section titled “Getting help”](#getting-help)
* [Sending us feedback](/support-and-community/troubleshooting-and-support/sending-us-feedback/) - How to reach Warp support and share feedback.
* [Known issues](/support-and-community/troubleshooting-and-support/known-issues/) - Current known issues across Warp.
* [GitHub issues](https://github.com/warpdotdev/Warp/issues) - Search existing reports or file a new one. Attach the `/view-logs` archive to bug reports.
# Frequently asked questions about agents
Canonical page: [/agents/getting-started/faqs/](https://docs.warp.dev/agents/getting-started/faqs/)
> Frequently asked questions about Warp's AI features, including supported models, privacy practices, credit limits, billing, and usage guidelines.
Answers to frequently asked questions about agents in Warp, including supported models, data privacy, credit limits, billing, and common error messages. For billing-specific questions, see the pricing FAQs.
## General
[Section titled “General”](#general)
### What data is sent and/or stored when using Agents in Warp?
[Section titled “What data is sent and/or stored when using Agents in Warp?”](#what-data-is-sent-andor-stored-when-using-agents-in-warp)
See our [Privacy page](/support-and-community/privacy-and-security/privacy/) for more information on how we handle data used by Agents in Warp.
### What happened to the old Warp AI chat panel?
[Section titled “What happened to the old Warp AI chat panel?”](#what-happened-to-the-old-warp-ai-chat-panel)
Agent Mode has replaced the previous AI chat panel. Agent Mode is more powerful in all of the chat panel’s use cases. Not only can Agent Mode run commands for you, it can also gather context without you needing to copy and paste. To start a similar chat panel, click the AI button in the menu bar to open a new AI pane.
### Is my data used for model training?
[Section titled “Is my data used for model training?”](#is-my-data-used-for-model-training)
Warp reserves the right to use data collected to train models and improve Warp. Warp has Zero Data Retention with all its model providers (e.g. Anthropic, OpenAI, xAI, etc.). Learn more about telemetry on our [Privacy page](/support-and-community/privacy-and-security/privacy/).
### What model are you using for Agent Mode?
[Section titled “What model are you using for Agent Mode?”](#what-model-are-you-using-for-agent-mode)
Warp supports a curated list of LLMs from providers like OpenAI, Anthropic, and Gemini. To view the full list of supported models and learn how to switch between them, visit the [Model Choice](/agents/inference/model-choice/) page.
### Can I use my own LLM API key?
[Section titled “Can I use my own LLM API key?”](#can-i-use-my-own-llm-api-key)
Yes. Warp supports [Bring Your Own API Key (BYOK)](/agents/inference/bring-your-own-api-key/) on the Free plan and all eligible paid plans, so you can connect your own Anthropic, OpenAI, or Google API keys to route requests directly through your account. Because the Free plan doesn’t include bundled AI usage for the Warp Agent, BYOK is one way to keep using the Warp Agent on the Free plan. BYOK and [custom inference endpoints](/agents/inference/custom-inference-endpoint/) are available for individual users and organizations with 10 or fewer employees, subject to Warp’s Terms of Service.
Larger organizations need a Warp Business or Enterprise plan. Business and Enterprise admins can centrally manage BYOK and custom endpoints for the whole team with [team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/), which also work for cloud agents. Enterprise admins can additionally enable managed [Bring Your Own LLM (BYOLLM)](/enterprise/enterprise-features/bring-your-own-llm/) configurations for cloud-provider routing.
### Can I use a ChatGPT or Claude subscription with Warp?
[Section titled “Can I use a ChatGPT or Claude subscription with Warp?”](#can-i-use-a-chatgpt-or-claude-subscription-with-warp)
You can [connect a ChatGPT subscription](/agents/inference/chatgpt-subscription/) to use eligible OpenAI models with the Warp Agent in the Warp app. You can connect while signing up or signing in, or link an existing Warp account from Settings.
Warp doesn’t support connecting a Claude consumer subscription. To use your own Anthropic account, add an API key with [Bring Your Own API Key (BYOK)](/agents/inference/bring-your-own-api-key/).
For xAI’s Grok models, connect a [SuperGrok subscription](/agents/inference/grok-subscription/).
## Billing
[Section titled “Billing”](#billing)
Paid Warp plans include a set number of credits per user per month for Warp-provided AI usage. The Free plan doesn’t include bundled AI usage for the Warp Agent; to use the Warp Agent, [upgrade to a paid plan](https://www.warp.dev/pricing) or bring your own inference (BYOK, a [custom inference endpoint](/agents/inference/custom-inference-endpoint/), a [ChatGPT subscription](/agents/inference/chatgpt-subscription/), or a [SuperGrok or X Premium subscription](/agents/inference/grok-subscription/)). See [pricing](https://www.warp.dev/pricing) to compare plans.
Credit limits apply to Agent Mode, Generate (Legacy), and [AI autofill in Workflows](/knowledge-and-collaboration/warp-drive/workflows/#ai-autofill).
For questions about what counts as a credit, what counts as a token, and how often credits refresh, see [Credits](/support-and-community/plans-and-billing/credits/) and the [Plans & Pricing](/support-and-community/plans-and-billing/plans-pricing-refunds/) page.
## Common AI error messages
[Section titled “Common AI error messages”](#common-ai-error-messages)
#### ”Message token limit exceeded” error
[Section titled “”Message token limit exceeded” error”](#message-token-limit-exceeded-error)
This error means your input (plus attached context) exceeds the maximum context window of the model you’re using. If you exceed the limit for your selected model, you may receive no output.
To fix this, try:
* Starting a new conversation
* Reducing the number of blocks or lines attached to your query
#### ”Monthly request limit exceeded” or “Monthly credit limit exceeded” errors
[Section titled “”Monthly request limit exceeded” or “Monthly credit limit exceeded” errors”](#monthly-request-limit-exceeded-or-monthly-credit-limit-exceeded-errors)
Once you exceed your monthly credit limit (see [pricing](https://www.warp.dev/pricing) for current limits), premium models will be disabled until your quota resets at the start of your next billing cycle. On paid plans with add-on credits, you can continue using AI with usage-based billing.
**Request failed with error: QuotaLimit**
Once you exceed your AI token limits, all models will be disabled. Note that credits and tokens are calculated separately, and even though the plans may have a set number of credits, they also have a limited number of tokens.
**Request failed with error: ErrorStatus (403, “Your account has been blocked from using AI features”)**
This message means your account has been blocked from using AI features, typically due to a violation of our [Terms of Service](https://www.warp.dev/legal/terms-of-service) or suspected abuse (e.g. attempting to bypass credit or token limits).
To resolve or clarify this, please contact our team at <appeals@warp.dev> if you believe this was an error. We’ll review your case and respond as soon as possible.
Caution
Note that any error that does not mention <appeals@warp.dev> isn’t related to being blocked and should be reported as feedback or a bug. See [Sending Us Feedback](/support-and-community/troubleshooting-and-support/sending-us-feedback/) for more.
## Gathering AI conversation ID
[Section titled “Gathering AI conversation ID”](#gathering-ai-conversation-id)
In cases where you have issues with the Agent, we may ask for the AI conversation ID to troubleshoot the specific conversation. To gather the conversation ID, see [Gathering AI conversation ID](/support-and-community/troubleshooting-and-support/sending-us-feedback/#gathering-ai-conversation-id) for detailed steps.
# Bring Your Own API Key
Canonical page: [/agents/inference/bring-your-own-api-key/](https://docs.warp.dev/agents/inference/bring-your-own-api-key/)
> Warp lets you bring your own API keys (BYOK) for OpenAI, Anthropic, and Google AI models.
Warp supports **Bring Your Own API Key (BYOK)** for users who want to connect agents to their own Anthropic, OpenAI, or Google API accounts.
This lets you use your own API keys for model access, giving you control over model selection, billing, and data routing. See [Model Choice](/agents/inference/model-choice/) for a list of supported models. You can also connect a [ChatGPT subscription](/agents/inference/chatgpt-subscription/) for eligible OpenAI models or a [SuperGrok subscription](/agents/inference/grok-subscription/) for Grok models.
BYOK provides greater flexibility in model access and ensures Warp **never consumes your** [AI credits](/support-and-community/plans-and-billing/credits/) for requests routed through your own keys.

Note
BYOK is available on Free and all eligible paid plans for individual users and organizations with 10 or fewer employees, subject to Warp’s [Terms of Service](https://www.warp.dev/legal/terms-of-service). Larger organizations need a Business or Enterprise plan. See [Warp pricing](https://www.warp.dev/pricing) for current availability.
## How BYOK differs from custom inference endpoints and BYOLLM
[Section titled “How BYOK differs from custom inference endpoints and BYOLLM”](#how-byok-differs-from-custom-inference-endpoints-and-byollm)
Warp offers several ways to bring your own AI infrastructure. Use this table to pick the right one, and follow the links for full details.
| Name | Meaning | Plans |
| -------------------------------------------------------------------------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | ------------------------------------------------ |
| **Bring Your Own API Key** (BYOK) | Use your own API key for OpenAI, Anthropic, or Google models. Keys are stored locally on your device. | Free and all eligible paid plans |
| **[Custom inference endpoint](/agents/inference/custom-inference-endpoint/)** | Connect Warp to an OpenAI-compatible endpoint such as OpenRouter, LiteLLM, z.ai, or an internal gateway. | Free and all eligible paid plans |
| **[Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/)** (BYOLLM) | Enterprise-managed inference through your cloud provider (AWS Bedrock and Gemini Enterprise Agent Platform (Vertex AI) today; Azure Foundry coming soon), with Warp handling routing, orchestration, governance, and observability. | Enterprise only |
| **[SuperGrok subscription](/agents/inference/grok-subscription/)** | Connect your SuperGrok subscription to use Grok models through your xAI account. Tokens are stored locally on your device. | Free and all eligible paid plans |
| **[ChatGPT subscription](/agents/inference/chatgpt-subscription/)** | Connect your ChatGPT plan to use eligible OpenAI models with the Warp Agent in the Warp app. | See [Warp pricing](https://www.warp.dev/pricing) |
See [Warp pricing](https://www.warp.dev/pricing) for current plan availability.
Platform credits apply to every cloud agent run on any plan, and to local agent runs on Business and Enterprise when using BYOK, a custom inference endpoint, BYOLLM, or a connected ChatGPT plan. See [platform credits](/support-and-community/plans-and-billing/platform-credits/) for the full breakdown.
Note
**Can I sign in with a Claude subscription?** No. A Claude (Anthropic) consumer subscription can’t be connected to Warp the way a [ChatGPT](/agents/inference/chatgpt-subscription/) or [SuperGrok](/agents/inference/grok-subscription/) subscription can. To use your own Anthropic account, add an API key with BYOK and pay Anthropic directly. A subscription and API access are billed separately.
## How BYOK works
[Section titled “How BYOK works”](#how-byok-works)
When you add your own model API keys in Warp, those keys are stored **only on your device** (in your OS keychain or equivalent secure storage), never on Warp’s servers. They’re used to make requests to your chosen model provider.
When you send a prompt using a model with the **key icon**:
1. Your local Warp client pulls your API key from your device’s secure storage and sends it up to Warp’s backend along with your prompt.
2. The Warp Agent harness, which runs on Warp’s backend, assembles the full request (system instructions, conversation context, tools) and uses your key in-flight to call your chosen model provider (Anthropic, OpenAI, or Google).
3. The provider’s response streams back through Warp’s backend to your client.
Your API key passes through Warp’s servers each time you send a request, but Warp never stores it there — it’s used only in-flight to call the provider, then discarded.
Note
**Why does the request route through Warp’s backend?** The Warp Agent harness runs server-side — the same runtime that powers [Agent Mode](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/) with Warp-billed models. BYOK swaps the credential used to call the provider; it does not change where the harness runs.
Caution
BYOK does not apply to [Cloud Agents](/platform/). Because your API keys are stored locally on your device, they are not available to cloud-hosted agent runs, which consume [Warp credits](/support-and-community/plans-and-billing/credits/). Business and Enterprise teams that need their own keys to work with cloud agents can use [team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/), which Warp stores server-side.
When a model is selected using your own key:
* Warp **does not consume** any of your [credits](/support-and-community/plans-and-billing/credits/).
* Costs are billed directly through your model provider account.
* Warp does not retain or store your API key on any of its servers.

## Enabling BYOK
[Section titled “Enabling BYOK”](#enabling-byok)
To enable and configure your API keys:
1. Open **Settings** and search for `API keys` to jump to the BYOK configuration.
2. Add your API key(s) for Anthropic, OpenAI, or Google.
3. Once added, you’ll see a **key icon** next to supported models in the model picker.
Note
The BYOK configuration widget doesn’t currently live on a dedicated sidebar subpage; searching from the **Settings** window is the quickest way to reach it. We’re tracking a follow-up to surface it under a persistent sidebar entry.
When you explicitly select a model with a key icon, Warp routes requests through your own API key instead of consuming Warp’s credits.
## BYOK usage and billing behavior
[Section titled “BYOK usage and billing behavior”](#byok-usage-and-billing-behavior)
### Auto Model
[Section titled “Auto Model”](#auto-model)
Warp’s **Auto** models dynamically route requests across different models based on context and performance. Because this routing logic depends on Warp’s infrastructure, **Auto always consumes Warp’s credits**, even if you’ve configured your own API keys.
To use your own key, select a specific provider model (for example, Claude Opus 4.7, Claude Sonnet 4.6, GPT-5.5, or Gemini 3.1 Pro) directly from the model picker with a key icon.
[Custom routers](/agents/inference/custom-routers/) behave differently: a router resolves each task to a concrete model you chose, and Warp then applies your API keys to that model. Requests that resolve to a model covered by one of your keys are billed through your provider account instead of consuming Warp credits. See [Credits and model availability](/agents/inference/custom-routers/#credits-and-model-availability) for details.
### Credit usage
[Section titled “Credit usage”](#credit-usage)
When you select a model with the key icon in your model picker, Warp routes the request through your API key. In that case:
* Inference is billed directly through your provider account rather than drawing from your AI credits.
* Agent Mode prioritizes BYOK over any available Warp credits.
Note
On Business and Enterprise plans, local agent runs that use BYOK still consume platform credits for Warp’s platform infrastructure (run lifecycle, integrations, observability). See [platform credits](/support-and-community/plans-and-billing/platform-credits/) for what’s covered.
**Other AI features in Warp**
Some AI-powered features are not affected by BYOK and are included as part of Warp’s paid plans.
| Feature | Uses Warp’s credits | Description |
| ------------------------------------------------------------ | ------------------- | -------------------------------------------------------------------- |
| [Active AI Recommendations](/agents/local-agents/active-ai/) | No | Always included with Build and higher plans. |
| [Codebase Context](/agents/capabilities/codebase-context/) | Yes | Uses Warp’s AI infrastructure and consumes credits. |
| [Cloud Agents](/platform/) | Yes | BYOK keys are stored locally and not available to cloud-hosted runs. |
These features will continue to function normally regardless of whether you’ve configured BYOK.
### Failover and fallback behavior
[Section titled “Failover and fallback behavior”](#failover-and-fallback-behavior)
If Warp detects an issue with your API key, you’ll see a clear error message corresponding with the AI request.
If your key:
* Is invalid: Warp notifies you and halts the request.
* Hits usage or rate limits: Warp will not retry using credits.
You can update or replace your keys anytime by opening **Settings** and searching for `API keys`.
**Failover and fallback:**
By default, Warp does not fall back to your credits when a BYOK request fails.
You can choose to enable **Warp credit fallback**. When enabled, if an agent request fails with your BYOK model (for example, due to an API error or quota limit), Warp will automatically route the request to one of Warp’s provided models. Warp always prioritizes your API keys first and only uses Warp credits when necessary.
### Zero Data Retention (ZDR) and BYOK
[Section titled “Zero Data Retention (ZDR) and BYOK”](#zero-data-retention-zdr-and-byok)
Warp is **SOC 2 compliant** and has **Zero Data Retention (ZDR)** policies with all of its contracted LLM providers. No customer AI data is retained, stored, or used for training by the model providers.
BYOK prompts and responses transit Warp’s backend (see [How BYOK works](#how-byok-works)). Warp does not use this content for training; retention and analytics handling follow the same account-level privacy and telemetry settings that apply to Warp-billed traffic.
However, when you use your own API key:
* Data retention policies on the **provider side** depend on your provider’s account settings.
* Warp cannot enforce ZDR for requests sent through your API keys.
* If your Anthropic, OpenAI, or Google account does not have ZDR enabled, your requests may be retained by the provider according to their terms.
Warp itself never stores your LLM API keys.
### BYOK on Business and Enterprise plans
[Section titled “BYOK on Business and Enterprise plans”](#byok-on-business-and-enterprise-plans)
The BYOK described on this page is configured at the **user level** on every plan, including Business and Enterprise. Each team member adds and manages their own API keys locally on their device, and those keys work only for interactive requests, not [cloud agents](/platform/).
Business and Enterprise teams can also configure **team-managed API keys** centrally: an admin sets shared keys in the [Admin Panel](/enterprise/team-management/admin-panel/), and they work for both interactive requests and cloud agents. See [Team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) for details, or [contact sales](https://www.warp.dev/contact-sales).
## Related resources
[Section titled “Related resources”](#related-resources)
* [Custom inference endpoint](/agents/inference/custom-inference-endpoint/) — Route Warp through any OpenAI-compatible endpoint, such as OpenRouter, LiteLLM, z.ai, or an internal gateway.
* [Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/) — Enterprise-managed inference through your cloud provider or approved infrastructure.
* [SuperGrok subscription](/agents/inference/grok-subscription/) — Use Grok models through your xAI account instead of Warp credits.
* [ChatGPT subscription](/agents/inference/chatgpt-subscription/) — Use eligible OpenAI models in Warp Agent conversations in the Warp app through your ChatGPT plan.
* [Model Choice](/agents/inference/model-choice/) — Full list of supported models and `model_id` values.
* [Credits](/support-and-community/plans-and-billing/credits/) — How Warp credits work and when they’re consumed.
# Connecting a ChatGPT subscription
Canonical page: [/agents/inference/chatgpt-subscription/](https://docs.warp.dev/agents/inference/chatgpt-subscription/)
> Connect a ChatGPT subscription to use eligible OpenAI models with the Warp Agent in the Warp app.
Connect a ChatGPT subscription to use eligible OpenAI models with the Warp Agent in the Warp app. Requests made through the connection count toward your ChatGPT usage limits instead of consuming Warp credits for inference.
You can connect during Warp sign-up or sign-in, or link ChatGPT to an existing Warp account from Settings.
## Connect during sign-up or sign-in
[Section titled “Connect during sign-up or sign-in”](#connect-during-sign-up-or-sign-in)
Use **Continue with ChatGPT** to create a Warp account or sign in to an existing account with the same verified email address.
1. Open the [Warp sign-in page](https://app.warp.dev/login).
2. Click **Continue with ChatGPT**.
3. Sign in to ChatGPT and approve the connection.
4. Return to Warp. Warp signs you in and links the ChatGPT subscription to your account.
ChatGPT on the Warp sign-in form.
## Link an existing Warp account
[Section titled “Link an existing Warp account”](#link-an-existing-warp-account)
Connect from Settings when you already use a different sign-in method for Warp.
1. In the Warp app, go to **Settings** > **Agents** > **Warp Agent**.
2. In the “OpenAI ChatGPT plan” row, click **Continue with ChatGPT**.
3. Sign in to ChatGPT and approve the connection in your browser.
4. Return to Warp. Settings shows the email address for the connected ChatGPT account.
If the setting isn’t available, your workspace admin may have disabled member-provided inference. See [Warp pricing](https://www.warp.dev/pricing) for current plan availability.
## Use your ChatGPT subscription
[Section titled “Use your ChatGPT subscription”](#use-your-chatgpt-subscription)
Choose a specific OpenAI model from the model picker. OpenAI determines which models and capabilities your ChatGPT plan can use.
* Requests made through the connection count toward your ChatGPT usage limits. Review your usage in [ChatGPT settings](https://chatgpt.com/settings/usage).
* A saved OpenAI API key takes precedence over the ChatGPT connection.
* **Auto** models use Warp-managed inference and consume Warp credits.
* A ChatGPT subscription doesn’t fund cloud agent runs.
On Business and Enterprise plans, local agent runs that use a ChatGPT subscription also consume [platform credits](/support-and-community/plans-and-billing/platform-credits/).
If OpenAI rejects a request, Warp may offer **Try again**, **Manage ChatGPT usage**, or **Continue with Warp credits**. Choosing **Continue with Warp credits** uses Warp-managed inference for the rest of that conversation.
## Disconnect your subscription
[Section titled “Disconnect your subscription”](#disconnect-your-subscription)
In the Warp app, go to **Settings** > **Agents** > **Warp Agent**. In the “OpenAI ChatGPT plan” row, click **Disconnect**.
After you disconnect, eligible OpenAI requests use your saved OpenAI API key, if you have one. Otherwise, they use Warp-managed inference and consume Warp credits.
## Troubleshoot the connection
[Section titled “Troubleshoot the connection”](#troubleshoot-the-connection)
### ”That ChatGPT account is already connected to a different Warp account”
[Section titled “”That ChatGPT account is already connected to a different Warp account””](#that-chatgpt-account-is-already-connected-to-a-different-warp-account)
Disconnect the existing link before connecting another ChatGPT or Warp account.
### ”Verify the email on your ChatGPT account with OpenAI, then try again”
[Section titled “”Verify the email on your ChatGPT account with OpenAI, then try again””](#verify-the-email-on-your-chatgpt-account-with-openai-then-try-again)
Verify the email with OpenAI, then click **Continue with ChatGPT** again.
### ”Reconnect to use your plan for requests”
[Section titled “”Reconnect to use your plan for requests””](#reconnect-to-use-your-plan-for-requests)
Disconnect the ChatGPT subscription, then connect it again.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) — Use your own Anthropic, OpenAI, or Google API key.
* [Model choice](/agents/inference/model-choice/) — Review the models available in Warp.
* [Warp credits and billing](/support-and-community/plans-and-billing/credits/) — See when Warp credits are consumed.
# Custom inference endpoint
Canonical page: [/agents/inference/custom-inference-endpoint/](https://docs.warp.dev/agents/inference/custom-inference-endpoint/)
> Connect agents to any OpenAI-compatible inference endpoint — OpenRouter, LiteLLM, z.ai, or an internal gateway exposed at a public URL.
Warp supports **custom inference endpoints** for users who want to power agents with any OpenAI-compatible inference endpoint — a model router, hosted gateway, or internal infrastructure they already run.
This lets you route AI requests through your preferred provider, run inference behind your own gateway, or use a router like OpenRouter or LiteLLM, while keeping the agent experience inside Warp.
**Your endpoint must be reachable at a public URL.** Requests route through Warp’s servers (see [How it works](#how-it-works)), so Warp must be able to reach your endpoint over the public internet. `localhost`, private or internal network addresses, and internal-only services — such as a LiteLLM proxy that’s only reachable inside your network — are rejected. To use an internal or local endpoint, first expose it at a public HTTPS URL. See [Network requirements](#network-requirements) for details.
Note
Custom inference endpoints are available on Free and all eligible paid plans for individual users and organizations with 10 or fewer employees, subject to Warp’s [Terms of Service](https://www.warp.dev/legal/terms-of-service). Larger organizations need a Business or Enterprise plan. See [Warp pricing](https://www.warp.dev/pricing) for current availability.
## Key features
[Section titled “Key features”](#key-features)
* **OpenAI-compatible** - Works with any endpoint that implements the OpenAI Chat Completions API.
* **Provider flexibility** - Use a model router (OpenRouter, LiteLLM), a model provider with an OpenAI-compatible surface (z.ai), or your own internal gateway exposed at a public URL.
* **No AI credits consumed for inference** - Inference is billed directly by your endpoint provider. On Business and Enterprise, local agent runs that route through a custom inference endpoint still consume [platform credits](/support-and-community/plans-and-billing/platform-credits/) for Warp’s platform infrastructure.
* **Local API key storage** - Your endpoint API key is stored **only on your device** (in your OS keychain or equivalent secure storage), never on Warp’s servers. It’s used to make requests to your configured endpoint.
## How it works
[Section titled “How it works”](#how-it-works)
A custom inference endpoint expects your endpoint to implement the **OpenAI Chat Completions API** (`POST /v1/chat/completions`). Any service that exposes a compatible surface can be used as a target:
* **OpenRouter** - Aggregates many model providers behind a single OpenAI-compatible API and consolidated billing.
* **LiteLLM** - A self-hosted proxy that exposes a unified, OpenAI-compatible API across providers.
* **z.ai** - A model provider with an OpenAI-compatible API surface for its models.
* **Internal gateways (exposed at a public URL)** - An in-house service that fronts model providers behind an OpenAI-compatible endpoint (for example, a corporate AI gateway with logging, redaction, or access control). The gateway must be reachable from the public internet — an internal-only service, such as a LiteLLM proxy that only resolves inside your network or VPN, won’t work until it’s exposed at a public URL (see [Network requirements](#network-requirements)).
When you configure a custom inference endpoint, your endpoint URL, model identifiers, and API key are stored **only on your device**, never on Warp’s servers. Your API key is used to make requests to your configured endpoint.
When you send a prompt using an endpoint-routed model:
1. Your local Warp client pulls your endpoint URL and API key from your device’s secure storage and sends them up to Warp’s backend along with your prompt.
2. The Warp Agent harness, which runs on Warp’s backend, assembles the full request (system instructions, conversation context, tools) and uses your key in-flight to call your configured endpoint.
3. Your endpoint’s response streams back through Warp’s backend to your client.
Your API key passes through Warp’s servers each time you send a request, but Warp never stores it there — it’s used only in-flight to call your endpoint, then discarded.
Note
**Why does the request route through Warp’s backend?** The Warp Agent harness runs server-side — the same runtime that powers [Agent Mode](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/) with Warp-billed models and [BYOK](/agents/inference/bring-your-own-api-key/). A custom inference endpoint swaps the upstream destination and credential; it does not change where the harness runs.
Caution
Custom inference endpoints don’t apply to [Cloud Agents](/platform/). Because the configuration is stored locally, it isn’t available to cloud-hosted agent runs. Cloud agent runs always consume [Warp credits](/support-and-community/plans-and-billing/credits/).
When a model routed through your endpoint is selected:
* Warp **doesn’t consume** your [AI credits](/support-and-community/plans-and-billing/credits/) for that request.
* Costs are billed directly by your endpoint provider.
* Warp doesn’t retain or store your API key on any of its servers.
## Enabling a custom inference endpoint
[Section titled “Enabling a custom inference endpoint”](#enabling-a-custom-inference-endpoint)
To enable and configure a custom inference endpoint:
1. In Warp, open **Settings** and search for `inference endpoint` to jump to the configuration.
2. Add your endpoint URL (the base URL that exposes `/v1/chat/completions`) and any required credentials (typically an API key).
3. Specify the model identifier(s) you want to route through this endpoint.
4. Save the configuration. Once added, you’ll see your custom models appear in the model picker.
When you explicitly select an endpoint-routed model from the model picker, Warp routes the request through your endpoint instead of consuming Warp’s AI credits.
The configuration flow mirrors the [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) setup, so the steps will feel familiar if you’ve already configured BYOK.
## Network requirements
[Section titled “Network requirements”](#network-requirements)
Warp routes inference requests through its servers, so **your endpoint must be reachable from the public internet**. `localhost`, `127.0.0.1`, and other private or local network URLs are rejected when configuring a custom inference endpoint.
This requirement applies to any endpoint that isn’t already publicly accessible:
* **Internal gateways and proxies** - An internal LiteLLM proxy, corporate AI gateway, or other service that only resolves inside your private network or VPN can’t be reached by Warp. Expose it at a public HTTPS URL — for example, through a load balancer, an API gateway, or a tunneling service — before configuring it in Warp.
* **Local models** - To route through a model running on your own machine (for example, Ollama, LM Studio, vLLM, or llama.cpp), expose it through a tunneling service like [ngrok](https://ngrok.com/) and use the public tunnel URL as the base URL in your endpoint configuration.
For example, with a default Ollama install listening on port `11434`, run `ngrok http 11434` and use the resulting `https://*.ngrok-free.app/v1` URL as your endpoint. Other tunneling services that produce a publicly reachable HTTPS URL (Cloudflare Tunnel, Tailscale Funnel, and similar) work the same way.
## Billing behavior
[Section titled “Billing behavior”](#billing-behavior)
### AI credits
[Section titled “AI credits”](#ai-credits)
When you select an endpoint-routed model from the model picker, inference is billed directly by your endpoint provider, according to their pricing, rather than drawing from your AI credits.
Note
On Business and Enterprise plans, local agent runs that route through a custom inference endpoint still consume platform credits for Warp’s platform infrastructure. See [platform credits](/support-and-community/plans-and-billing/platform-credits/) for the full breakdown.
### Auto routing still uses Warp credits
[Section titled “Auto routing still uses Warp credits”](#auto-routing-still-uses-warp-credits)
Warp’s **Auto** models dynamically route across providers using Warp’s infrastructure. Because Auto routing depends on Warp, **Auto always consumes Warp’s credits**, even if you’ve configured a custom inference endpoint.
To use your endpoint, select the specific endpoint-routed model from the model picker rather than an Auto option.
[Custom routers](/agents/inference/custom-routers/) can’t use your endpoint either: routing targets must be Warp-supported models, so a router never resolves to an endpoint-routed model. Custom routers do apply [BYOK](/agents/inference/bring-your-own-api-key/) provider keys after resolving a model.
### Other AI features in Warp
[Section titled “Other AI features in Warp”](#other-ai-features-in-warp)
Some AI-powered features (Codebase Context, Active AI recommendations, cloud agent runs) rely on Warp’s infrastructure and are unaffected by a custom inference endpoint. See the [feature breakdown on the BYOK page](/agents/inference/bring-your-own-api-key/#byok-usage-and-billing-behavior) for which features still consume Warp credits.
## Zero Data Retention (ZDR)
[Section titled “Zero Data Retention (ZDR)”](#zero-data-retention-zdr)
Warp is **SOC 2 compliant** and has **Zero Data Retention (ZDR)** agreements with all of its contracted LLM providers.
Custom inference endpoint prompts and responses transit Warp’s backend (see [How it works](#how-it-works)). Warp does not use this content for training; retention and analytics handling follow the same account-level privacy and telemetry settings that apply to Warp-billed traffic.
When you use a custom inference endpoint:
* Data retention on the **provider side** is determined by your endpoint provider and any upstream model providers they route to.
* Warp **cannot enforce ZDR** for requests sent through a custom inference endpoint.
* If your endpoint provider does not have ZDR with the underlying model provider, your requests may be retained according to their terms.
Warp itself never stores your endpoint API key. Review your endpoint provider’s data handling and retention policies before routing sensitive prompts through a custom inference endpoint.
## Centrally managed configuration
[Section titled “Centrally managed configuration”](#centrally-managed-configuration)
The custom inference endpoints described on this page are configured at the **user level** on every plan. Each user adds their own endpoint locally, and it works only for interactive requests, not [cloud agents](/platform/).
Business and Enterprise teams can also configure **team-managed custom endpoints** centrally: an admin sets shared endpoints in the [Admin Panel](/enterprise/team-management/admin-panel/), and they work for both interactive requests and cloud agents. See [Team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/), or [Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/) for Enterprise AWS Bedrock or Gemini Enterprise (Vertex AI) routing.
## How custom inference endpoints differ from BYOK and BYOLLM
[Section titled “How custom inference endpoints differ from BYOK and BYOLLM”](#how-custom-inference-endpoints-differ-from-byok-and-byollm)
Warp offers three ways to bring your own AI infrastructure. Use this table to pick the right one, and follow the links for full details.
| Name | Meaning | Plans |
| -------------------------------------------------------------------------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | -------------------------------- |
| **[Bring Your Own API Key](/agents/inference/bring-your-own-api-key/)** (BYOK) | Use your own API key for OpenAI, Anthropic, or Google models. Keys are stored locally on your device. | Free and all eligible paid plans |
| **Custom inference endpoint** | Connect Warp to an OpenAI-compatible endpoint such as OpenRouter, LiteLLM, z.ai, or an internal gateway. | Free and all eligible paid plans |
| **[Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/)** (BYOLLM) | Enterprise-managed inference through your cloud provider (AWS Bedrock and Gemini Enterprise Agent Platform (Vertex AI) today; Azure Foundry coming soon), with Warp handling routing, orchestration, governance, and observability. | Enterprise only |
Platform credits may apply for local agent runs on Business and Enterprise when using BYOK, a custom inference endpoint, or BYOLLM. See [platform credits](/support-and-community/plans-and-billing/platform-credits/).
## Related resources
[Section titled “Related resources”](#related-resources)
* [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) — Use your own OpenAI, Anthropic, or Google API keys.
* [Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/) — Enterprise-managed inference through your cloud provider or approved infrastructure.
* [Model Choice](/agents/inference/model-choice/) — Full list of supported models and `model_id` values.
* [Credits](/support-and-community/plans-and-billing/credits/) — How Warp credits work and when they’re consumed.
# Custom routers
Canonical page: [/agents/inference/custom-routers/](https://docs.warp.dev/agents/inference/custom-routers/)
> Define a custom router that automatically picks the right model for each task, based on task complexity or rules you write, and use it from the model picker.
Custom routers automatically pick the right model for each task, using routing logic you define. Instead of committing to a single model up front, you set the logic once, and Warp resolves a concrete model each time you send a prompt, based on either task complexity or rules you write.
## Key features
[Section titled “Key features”](#key-features)
* **Complexity-based routing** - Warp classifies each task’s difficulty and routes to the model you mapped to that level.
* **Rule-based routing** - Write natural-language rules that describe when to use each model.
* **Any supported model** - Route to any concrete model you have access to, across providers.
* **BYOK support** - With [your own API keys](/agents/inference/bring-your-own-api-key/) configured, requests that resolve to a model covered by one of your keys bill through your provider account instead of Warp credits.
* **Settings or file** - Create a router in settings, or author it as a YAML file that Warp loads automatically.
* **Team-synced routers** - Admins can share a router with an entire team (Enterprise).
## How it works
[Section titled “How it works”](#how-it-works)
A custom router appears in the [model picker](/agents/inference/model-choice/#how-to-change-models) as its own entry, alongside Warp’s built-in Auto models and individual models. You select it like any other model.
When you send a prompt, the router resolves to a single concrete model and runs the task on it, just like Warp’s built-in Auto models. You can always see which model actually ran.
Warp chooses a model when you start a conversation and keeps using it for the rest of that conversation. Very short, trivial prompts (like a quick “hello”) don’t lock in the choice.
Note
A router always resolves to concrete models that you choose. It can’t route to an Auto model or to another router.
## Routing types
[Section titled “Routing types”](#routing-types)
A router uses one of two routing types. You choose the type when you create the router.
### Complexity-based routing
[Section titled “Complexity-based routing”](#complexity-based-routing)
Warp classifies each task as easy, medium, or hard and routes to the model you assigned to that level. You also set a default model, which Warp uses for any level you leave unset or when it can’t determine complexity.
Use complexity-based routing to put lower-cost models on simple work and more capable models on harder tasks, without describing tasks yourself.
### Rule-based routing
[Section titled “Rule-based routing”](#rule-based-routing)
Rule-based routing routes each task using rules you write. Each rule pairs a classification prompt (a natural-language description of when to use a model, such as “debugging or fixing failing tests”) with the model to use when that rule matches.
* Warp evaluates rules from top to bottom, and the first rule that matches wins. Rules higher in the list take precedence over those below.
* If no rule matches, Warp uses the required default model.
## Create a router in Warp
[Section titled “Create a router in Warp”](#create-a-router-in-warp)
1. Open **Settings** > **Agents** > **Warp Agent** and find the **Custom Routers** section.
2. Click **Add router** and enter a name.
3. Under **Routing type**, choose **Complexity-based** or **Rule-based**.
4. Configure the routing:
* **Complexity-based** - Select a **Default** model, then assign models to **Easy**, **Medium**, and **Hard**.
* **Rule-based** - Select a **Default model**, then click **Add rule** for each rule, write a **Classification prompt** describing when to use the model, and select the model. Rules are matched top to bottom, so order them by precedence.
5. Click **Save**.
Your router now appears in the model picker. Saving also writes a file: use **Open file** to edit it directly, or **Delete** to remove the router.
## Author a router as a file
[Section titled “Author a router as a file”](#author-a-router-as-a-file)
Custom routers are stored as YAML files in `~/.warp/custom_model_routers/`, with one router per file. Warp loads every file in that directory and reloads automatically when you add, edit, or remove one, with no restart required. Routers you create in settings are saved here too.
Routing targets use the same `model_id` values listed on the [Model choice](/agents/inference/model-choice/#available-models) page. Every target must be a concrete, Warp-supported model. You can’t route to an Auto model, another router, or a model from a [custom inference endpoint](/agents/inference/custom-inference-endpoint/).
A complexity router uses `type: complexity`. `default` is required and is used for any bucket you omit:
\~/.warp/custom\_model\_routers/cost-saver.yaml
```yaml
name: Cost saver
type: complexity
default: glm-5.3-fireworks
routing:
easy: minimax-3-fireworks
medium: glm-5.3-fireworks
hard: deepseek-v4.1-flash-fireworks
```
A rule-based router uses `type: prompt`. `default` is the required catch-all used when no rule matches, and `routing` is the ordered list of rules. Rules can describe your team’s specific workflows, so you can send routine work to cheaper models and reserve a frontier model for the tasks that need it:
\~/.warp/custom\_model\_routers/by-task.yaml
```yaml
name: By task
type: prompt
default: claude-4-6-sonnet-high
routing:
- description: writing or reviewing database migrations for the acme-payments service
model: glm-5.3-fireworks
- description: debugging production incidents or fixing failing CI tests
model: claude-4-8-opus-high
- description: scaffolding new services or boilerplate from our internal templates
model: kimi-k3-fireworks
- description: drafting release notes, runbooks, or API documentation
model: qwen-3.8-max-fireworks
```
If a file can’t be parsed, Warp shows a non-blocking error identifying the file and skips it; your other routers keep working.
## Use a router
[Section titled “Use a router”](#use-a-router)
1. In the prompt input, open the model picker by clicking the current model name.
2. Choose your router from the list.
Your selection persists for future prompts, like any other model choice.
## Team-synced routers
[Section titled “Team-synced routers”](#team-synced-routers)
Team admins can create routers that are shared with the whole team, so everyone can use the same routing strategy. Team-synced routers are an Enterprise feature, and only admins can create or edit them.
To create one, an admin:
1. Opens the [Admin Panel](https://app.warp.dev/admin/) and goes to **Models**.
2. Finds the **Custom Routers** section and clicks **New router**.
3. Chooses **Complexity-based** or **Rule-based**, sets the models or rules, and clicks **Create**.
Team-synced routers appear in the model picker for every team member, who can select them like any other router.
## Credits and model availability
[Section titled “Credits and model availability”](#credits-and-model-availability)
A custom router resolves to a concrete model, so credit usage matches whichever model the router selects for each task. See [Credits](/support-and-community/plans-and-billing/credits/) for how credits are consumed.
### Using your own API keys (BYOK)
[Section titled “Using your own API keys (BYOK)”](#using-your-own-api-keys-byok)
Custom routers work with [Bring Your Own API Key (BYOK)](/agents/inference/bring-your-own-api-key/). After the router resolves a task to a concrete model, Warp applies your API keys to that model — the same as selecting that model directly from the picker. Requests that resolve to a model covered by one of your keys are billed through your provider account and don’t consume Warp credits; requests that resolve to a model without a matching key consume Warp credits as usual.
This is different from Warp’s built-in Auto models, which always consume Warp credits even when BYOK is configured.
* **Running a router entirely on your own keys** - To use a router with no Warp credits available, your keys must cover every model the router references. If only some models are covered, you still need Warp credits for the requests that resolve to the uncovered models.
* **Team-managed keys (Business and Enterprise)** - [Team-managed API keys](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) apply to custom routers the same way; a member’s own key for a provider takes precedence over the team’s.
* **No custom inference endpoints** - Routing targets must be Warp-supported models, so a router can’t resolve to a model from a [custom inference endpoint](/agents/inference/custom-inference-endpoint/) and never draws on your endpoint.
### Model availability and fallback
[Section titled “Model availability and fallback”](#model-availability-and-fallback)
If a router targets a model you don’t have access to or that’s disabled for your organization, Warp falls back to the router’s default model. If no usable model remains, Warp falls back to a built-in default and tells you.
## Related resources
[Section titled “Related resources”](#related-resources)
* [Model choice](/agents/inference/model-choice/) — Supported models and `model_id` values, including Warp’s built-in Auto models.
* [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) — Use your own OpenAI, Anthropic, or Google API keys.
* [Custom inference endpoint](/agents/inference/custom-inference-endpoint/) — Route Warp through any OpenAI-compatible endpoint.
* [Team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) — Business and Enterprise admins configure shared provider keys and custom endpoints from the same Admin Panel Models page.
* [Admin Panel for teams](/enterprise/team-management/admin-panel/) — Manage team-wide settings, including team-synced routers.
# SuperGrok subscription
Canonical page: [/agents/inference/grok-subscription/](https://docs.warp.dev/agents/inference/grok-subscription/)
> Connect your SuperGrok or X Premium subscription to use Grok models in Warp through your xAI account. Usage draws from the same weekly pool as Grok Build.
Warp lets you connect your **SuperGrok subscription** to use Grok models with agents in Warp through your xAI account. If you already subscribe to Grok, you can run Grok models in Warp without consuming your Warp [credits](/support-and-community/plans-and-billing/credits/). X Premium subscriptions that include Grok access work the same way: you sign in to your xAI account, and xAI determines which subscription tiers are eligible and how much usage they include.
Connecting a subscription works like [Bring Your Own API Key (BYOK)](/agents/inference/bring-your-own-api-key/), except you sign in to your xAI account instead of pasting an API key. There is no xAI API key field in Warp today — the subscription is the way to bring your own Grok access.
Note
Like BYOK, connecting a SuperGrok subscription is available on Free and all eligible paid plans for individual users and organizations with 10 or fewer employees, subject to Warp’s [Terms of Service](https://www.warp.dev/legal/terms-of-service). See [Warp pricing](https://www.warp.dev/pricing) for current availability.
## How it works
[Section titled “How it works”](#how-it-works)
When you connect your subscription, Warp opens your browser to xAI’s consent screen and completes a standard OAuth login. Warp receives OAuth tokens for your xAI account and stores them **only on your device** (in your OS keychain or equivalent secure storage), never on Warp’s servers. Warp refreshes the tokens automatically in the background, so you typically only need to connect once.
When you send a prompt with a Grok model selected and a subscription connected:
1. Your local Warp client sends the access token to Warp’s backend along with your prompt.
2. The Warp Agent harness assembles the full request and uses your token in-flight to call xAI, authenticating as your xAI account instead of Warp’s.
3. xAI’s response streams back through Warp’s backend to your client.
Your token passes through Warp’s servers on each request but is used only in-flight to call xAI, then discarded — the same model as [BYOK](/agents/inference/bring-your-own-api-key/#how-byok-works).
Once connected, supported Grok models show a **key icon** in the model picker, indicating requests will route through your xAI account. Usage and rate limits for these requests are governed by your xAI subscription — see [How usage counts against your xAI subscription](#how-usage-counts-against-your-xai-subscription).
## Connecting your SuperGrok subscription
[Section titled “Connecting your SuperGrok subscription”](#connecting-your-supergrok-subscription)
1. In the Warp app, open **Settings** and search for `SuperGrok` to jump to the **Connect SuperGrok subscription** row in your AI settings.
2. Click **Connect**. Warp opens your browser to xAI’s consent screen and shows a toast with a **Copy URL** fallback in case the browser doesn’t open.
3. Approve the connection in your browser. The page confirms with “Grok connected,” and back in Warp the row shows a “Connected on…” timestamp.
4. Select a Grok model with the key icon from the model picker in your prompt input. Connecting a subscription doesn’t change your selected model, so this last step is what actually routes your requests through your subscription. See [Model choice](/agents/inference/model-choice/) for the list of available models.
In the [Warp Agent CLI](/agents/cli/), run `/connect-grok` instead. It starts the same xAI sign-in from your session, and `/api-keys` shows the connection state afterward. See [models and usage in the Warp Agent CLI](/agents/cli/models-and-usage/#bring-your-own-api-key).
## Usage and billing behavior
[Section titled “Usage and billing behavior”](#usage-and-billing-behavior)
When a Grok model with the key icon is selected:
* Warp **does not consume** any of your [credits](/support-and-community/plans-and-billing/credits/) for the request.
* Inference runs through your xAI account, within your xAI subscription’s usage limits.
* If a request fails because your subscription hits a limit, Warp does not retry with Warp credits unless you enable **Warp credit fallback** in the same settings section. See [failover and fallback behavior](/agents/inference/bring-your-own-api-key/#failover-and-fallback-behavior).
### How usage counts against your xAI subscription
[Section titled “How usage counts against your xAI subscription”](#how-usage-counts-against-your-xai-subscription)
xAI gives every paid Grok subscription one weekly usage pool that is shared across all Grok products — Grok chat, [Grok Build](https://docs.x.ai/build/overview) (xAI’s own coding agent), and API access all draw down the same pool. Requests you send from Warp count against that same pool.
In xAI’s usage dashboard on grok.com (the Usage section in Settings), requests from Warp appear under the **API** product label because Warp calls xAI’s API on your behalf. The label reflects where the usage came from, not a separate quota: API and Grok Build usage share the same pool, so you get the same amount of usage running Grok models in Warp as you would using Grok Build directly.
When you use up your weekly pool, xAI pauses paid usage until the reset time shown in its Usage tab. Extra Usage Credits and plan upgrades for the pool are managed through your xAI account, not Warp.
### Auto models
[Section titled “Auto models”](#auto-models)
Warp’s **Auto** models always use Warp’s own inference and **always consume Warp credits**, even with a SuperGrok subscription connected. Auto never routes requests through your subscription. To use your subscription, select a specific Grok model from the model picker.
Caution
A connected SuperGrok subscription does not apply to [Cloud Agents](/platform/). Because tokens are stored locally on your device, they are not available to cloud-hosted agent runs, which always consume [Warp credits](/support-and-community/plans-and-billing/credits/).
### Zero data retention (ZDR)
[Section titled “Zero data retention (ZDR)”](#zero-data-retention-zdr)
Warp has Zero Data Retention agreements with its contracted LLM providers, including xAI, for Warp-managed inference. When you connect your own subscription, data retention on xAI’s side is governed by your own xAI account and its terms — Warp cannot enforce ZDR for requests sent through your subscription. Warp itself never stores your tokens on its servers.
## Disconnecting
[Section titled “Disconnecting”](#disconnecting)
To disconnect, open **Settings**, search for `SuperGrok`, and click **Disconnect**. Warp removes the tokens from your device’s secure storage, and Grok models go back to running on Warp credits.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### ”Couldn’t start Grok login”
[Section titled “”Couldn’t start Grok login””](#couldnt-start-grok-login)
Warp listens on a fixed local port for the browser to complete the connection. This error means the port is busy: usually another connection attempt is still in progress, or another app that uses the same xAI login flow (like Grok CLI) is running. Close the other app or wait for the other attempt to finish, then click **Connect** again.
### The browser never opened
[Section titled “The browser never opened”](#the-browser-never-opened)
Click **Copy URL** on the toast that appears after clicking **Connect**, then paste the URL into your browser manually.
### ”Couldn’t connect SuperGrok: timed out waiting for the Grok authorization callback”
[Section titled “”Couldn’t connect SuperGrok: timed out waiting for the Grok authorization callback””](#couldnt-connect-supergrok-timed-out-waiting-for-the-grok-authorization-callback)
Warp waits 5 minutes for you to approve the connection in your browser. Click **Connect** and approve the consent screen within that window.
## Related resources
[Section titled “Related resources”](#related-resources)
* [Model choice](/agents/inference/model-choice/) — Full list of supported models and `model_id` values.
* [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) — Use your own Anthropic, OpenAI, or Google API keys.
* [Custom inference endpoint](/agents/inference/custom-inference-endpoint/) — Route Warp through any OpenAI-compatible endpoint.
* [Credits](/support-and-community/plans-and-billing/credits/) — How Warp credits work and when they’re consumed.
# Agent model choice
Canonical page: [/agents/inference/model-choice/](https://docs.warp.dev/agents/inference/model-choice/)
> Choose from a curated set of top LLMs for Warp's Agents (or let Warp auto-select the best model).
Warp lets you choose from a curated set of large language models to power your agents, or let Warp auto-select the best model for each task. Models from OpenAI, Anthropic, Google, and open source providers are available, with configurable reasoning levels and per-profile defaults. You can also define [custom routers](/agents/inference/custom-routers/) that pick a model for each task using your own logic.
## Available models
[Section titled “Available models”](#available-models)
Warp lets you choose from a curated set of large language models (LLMs) to power your Agentic Development Environment.
**Warp supports the following models.**
The `model_id` values shown below can be used when configuring models via the [Automation Platform](/platform/overview/) or [CLI](/agents/cli/oz-cli/).
### Auto models
[Section titled “Auto models”](#auto-models)
| Model | `model_id` | Description |
| --------------------- | ---------------- | ---------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Auto (Responsive) | `auto` | Selects the highest-quality, fastest available model. May consume credits more quickly. |
| Auto (Cost-efficient) | `auto-efficient` | Optimizes for lower credit consumption while maintaining strong output quality. |
| Auto (Genius) | `auto-genius` | Adapts to task complexity and selects Warp’s most capable model when it’s worth it. Best for deep debugging, architecture decisions, and `/plan` sessions. |
| Auto (Open-weights) | `auto-open` | Routes between the best open-source models available in Warp. Optimizes for low cost and fast speed using open-weights models. |
All Auto models perform well across all agent workflows and are ideal if you prefer Warp to manage model selection dynamically.
#### OpenAI
[Section titled “OpenAI”](#openai)
The `low`, `medium`, `high`, `xhigh`, and `max` suffixes select increasing reasoning levels.
| Model | Supported `model_id` values |
| ------------- | --------------------------------------------------------------------------------------------------- |
| GPT-6 Astra | `gpt-6-astra-low`, `gpt-6-astra-medium`, `gpt-6-astra-high`, `gpt-6-astra-xhigh`, `gpt-6-astra-max` |
| GPT-6.1 Sol | `gpt-6-1-sol-low`, `gpt-6-1-sol-medium`, `gpt-6-1-sol-high`, `gpt-6-1-sol-xhigh`, `gpt-6-1-sol-max` |
| GPT-6 Sol | `gpt-6-sol-low`, `gpt-6-sol-medium`, `gpt-6-sol-high`, `gpt-6-sol-xhigh`, `gpt-6-sol-max` |
| GPT-6 Luna | `gpt-6-luna-low`, `gpt-6-luna-medium`, `gpt-6-luna-high`, `gpt-6-luna-xhigh`, `gpt-6-luna-max` |
| GPT-5.6 Sol | `gpt-5-6-sol-low`, `gpt-5-6-sol-medium`, `gpt-5-6-sol-high`, `gpt-5-6-sol-xhigh` |
| GPT-5.6 Terra | `gpt-5-6-terra-low`, `gpt-5-6-terra-medium`, `gpt-5-6-terra-high`, `gpt-5-6-terra-xhigh` |
| GPT-5.6 Luna | `gpt-5-6-luna-low`, `gpt-5-6-luna-medium`, `gpt-5-6-luna-high`, `gpt-5-6-luna-xhigh` |
| GPT-5.5 | `gpt-5-5-low`, `gpt-5-5-medium`, `gpt-5-5-high`, `gpt-5-5-xhigh` |
| GPT-5.4 | `gpt-5-4-low`, `gpt-5-4-medium`, `gpt-5-4-high`, `gpt-5-4-xhigh` |
To use eligible OpenAI models through your ChatGPT plan, [connect a ChatGPT subscription](/agents/inference/chatgpt-subscription/) and select a specific OpenAI model.
#### Anthropic
[Section titled “Anthropic”](#anthropic)
Suffixes select effort level. `xhigh-fast` enables fast mode, and `thinking` enables thinking. The default ID for each family is listed separately.
| Model | Supported `model_id` values | Default `model_id` |
| ----------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------- | ------------------------- |
| Claude Opus 5.5 | `claude-5-5-opus-low`, `claude-5-5-opus-medium`, `claude-5-5-opus-high`, `claude-5-5-opus-xhigh`, `claude-5-5-opus-xhigh-fast`, `claude-5-5-opus-max` | `claude-5-5-opus-high` |
| Claude Opus 5 | `claude-5-opus-low`, `claude-5-opus-medium`, `claude-5-opus-high`, `claude-5-opus-xhigh`, `claude-5-opus-xhigh-fast`, `claude-5-opus-max` | `claude-5-opus-high` |
| Claude Fable 5.1 | `claude-5-1-fable-low`, `claude-5-1-fable-medium`, `claude-5-1-fable-high`, `claude-5-1-fable-xhigh`, `claude-5-1-fable-max` | `claude-5-1-fable-high` |
| Claude Fable 5 | `claude-5-fable-low`, `claude-5-fable-medium`, `claude-5-fable-high`, `claude-5-fable-xhigh`, `claude-5-fable-max` | `claude-5-fable-high` |
| Claude Sonnet 5.5 | `claude-5-5-sonnet-low`, `claude-5-5-sonnet-medium`, `claude-5-5-sonnet-high`, `claude-5-5-sonnet-xhigh`, `claude-5-5-sonnet-max` | `claude-5-5-sonnet-xhigh` |
| Claude Sonnet 5 | `claude-5-sonnet-low`, `claude-5-sonnet-medium`, `claude-5-sonnet-high`, `claude-5-sonnet-xhigh`, `claude-5-sonnet-max` | `claude-5-sonnet-xhigh` |
| Claude Opus 4.8 | `claude-4-8-opus-low`, `claude-4-8-opus-medium`, `claude-4-8-opus-high`, `claude-4-8-opus-xhigh`, `claude-4-8-opus-xhigh-fast`, `claude-4-8-opus-max` | `claude-4-8-opus-xhigh` |
| Claude Opus 4.7 | `claude-4-7-opus-high`, `claude-4-7-opus-xhigh`, `claude-4-7-opus-max` | `claude-4-7-opus-xhigh` |
| Claude Opus 4.6 | `claude-4-6-opus-high`, `claude-4-6-opus-max` | `claude-4-6-opus-high` |
| Claude Sonnet 4.6 | `claude-4-6-sonnet-high`, `claude-4-6-sonnet-max` | `claude-4-6-sonnet-high` |
| Claude Opus 4.5 | `claude-4-5-opus`, `claude-4-5-opus-thinking` | `claude-4-5-opus` |
| Claude Sonnet 4.5 | `claude-4-5-sonnet`, `claude-4-5-sonnet-thinking` | `claude-4-5-sonnet` |
| Claude Haiku 4.5 | `claude-4-5-haiku` | `claude-4-5-haiku` |
Caution
Anthropic requires data retention for Claude Fable 5 and Claude Fable 5.1 for safety, abuse monitoring, and compliance reasons, so these models are **not available under Zero Data Retention (ZDR)**. This requirement is specific to the Claude Fable models and doesn’t change the ZDR behavior of any other supported model. For Enterprise teams, these models are off by default and a workspace admin must enable them — see the [Admin Panel](/enterprise/team-management/admin-panel/#models-settings) and the [Security overview](/enterprise/security-and-compliance/security-overview/#zero-data-retention-zdr).
#### Google
[Section titled “Google”](#google)
| Model | `model_id` |
| ---------------- | ------------------ |
| Gemini 3.1 Pro | `gemini-3.1-pro` |
| Gemini 3.8 Flash | `gemini-3.8-flash` |
| Gemini 3.7 Flash | `gemini-3.7-flash` |
| Gemini 3.6 Flash | `gemini-3.6-flash` |
| Gemini 3.5 Flash | `gemini-3.5-flash` |
#### xAI
[Section titled “xAI”](#xai)
| Model | `model_id` | Reasoning Level |
| -------------- | ----------------- | --------------- |
| Grok 4.7 | `grok-4-7-low` | Low |
| Grok 4.7 | `grok-4-7-medium` | Medium |
| Grok 4.7 | `grok-4-7-high` | High |
| Grok 4.7 | `grok-4-7-xhigh` | Extra High |
| Grok 4.6 | `grok-4-6-low` | Low |
| Grok 4.6 | `grok-4-6-medium` | Medium |
| Grok 4.6 | `grok-4-6-high` | High |
| Grok 4.6 | `grok-4-6-xhigh` | Extra High |
| Grok 4.5 | `grok-4-5-low` | Low |
| Grok 4.5 | `grok-4-5-medium` | Medium |
| Grok 4.5 | `grok-4-5-high` | High |
| Grok 4.3 | `grok-4-3-low` | Low |
| Grok 4.3 | `grok-4-3-medium` | Medium |
| Grok 4.3 | `grok-4-3-high` | High |
| Grok Build 0.1 | `grok-build-0.1` | — |
You can run Grok models through your own SuperGrok subscription instead of Warp credits by connecting your xAI account. See [SuperGrok subscription](/agents/inference/grok-subscription/).
#### Hosted models (via [Fireworks AI](https://fireworks.ai))
[Section titled “Hosted models (via Fireworks AI)”](#hosted-models-via-fireworks-ai)
Warp also supports leading open source models hosted via Fireworks AI, so you can run them from inside Warp without setting up your own inference infrastructure.
| Model | `model_id` |
| ------------------- | ------------------------------- |
| GLM 5.3 | `glm-5.3-fireworks` |
| GLM 5.3 Flash | `glm-5.3-flash-fireworks` |
| Kimi K3 | `kimi-k3-fireworks` |
| Minimax 3 | `minimax-3-fireworks` |
| Qwen 3.8 Max | `qwen-3.8-max-fireworks` |
| DeepSeek V4.1 Flash | `deepseek-v4.1-flash-fireworks` |
### How to change models
[Section titled “How to change models”](#how-to-change-models)
You can use the model picker in your prompt input to quickly switch between models. The currently active model appears directly in the input editor.
Model selector in Warp’s input.
To change models, click the displayed model name (for example, *Claude Sonnet 5*) to open a dropdown with all supported options. Your selection will automatically persist for future prompts.
### Custom routers
[Section titled “Custom routers”](#custom-routers)
Beyond the built-in Auto models, you can define your own custom routers that automatically route each task to a concrete model based on task complexity or rules you write. Custom routers appear in the model picker alongside Auto and individual models.
Add and manage custom routers in **Settings** > **Agents** > **Warp Agent** > **Custom Routers**. See [Custom routers](/agents/inference/custom-routers/) for details on creating one.
### Model fallback
[Section titled “Model fallback”](#model-fallback)
Warp uses a model fallback system to ensure uninterrupted service if your selected model becomes temporarily unavailable due to provider outages or capacity issues.
**How it works:**
* If your selected model isn’t available, Warp automatically uses a fallback model from a predefined chain to continue your conversation without errors.
* As soon as your originally selected model becomes available again, Warp automatically switches back to it.
* The fallback model is selected to provide comparable quality and capabilities to your original choice.
### Configuring models per Agent Profile
[Section titled “Configuring models per Agent Profile”](#configuring-models-per-agent-profile)
You can configure the base model for each [Agent Profile](/agents/capabilities/agent-profiles-permissions/), alongside the Agent’s autonomy, tool access, and other permissions. The base model is also used for [Planning](/agents/capabilities/planning/).
Edit your default profile or any other profile directly in **Settings** > **Agents** > **Profiles**.
### Zero data retention policies
[Section titled “Zero data retention policies”](#zero-data-retention-policies)
Warp integrates with multiple large language model (LLM) providers to power its AI-driven features.
**These providers include, but are not limited to:**
* OpenAI
* Anthropic
* Google
* xAI
* Fireworks AI
Warp has executed **Zero Data Retention (ZDR)** agreements with these providers. This means that, by default across all plans:
* LLM providers commit not to train their models on any customer-generated data processed through Warp’s services.
* LLM providers commit to delete inputs and outputs after generating the relevant output, within a fixed time period.
Warp enforces these commitments through both technical measures and contractual safeguards with the LLM providers.
Zero data retention is available for supported models. Model availability may vary where providers require data retention for safety, abuse monitoring, or compliance reasons.
# Active AI Recommendations
Canonical page: [/agents/local-agents/active-ai/](https://docs.warp.dev/agents/local-agents/active-ai/)
> Active AI Recommendations proactively suggest fixes and next actions based on your command line errors, inputs, and outputs.
Active AI Recommendations proactively suggest fixes and next actions based on your terminal errors, inputs, and outputs. Features include Prompt Suggestions that activate Agent Mode, Next Command predictions from your shell history, and Suggested Code Diffs that automatically surface fixes for command-line errors.
Note
Active AI features can be disabled in **Settings** > **Agents** > **Warp Agent** with the Active AI toggle.
### Prompt Suggestions
[Section titled “Prompt Suggestions”](#prompt-suggestions)
Prompt Suggestions are contextual, AI-powered suggestions that activate Agent Mode. These banners will provide suggestions for what to ask Agent Mode in specific scenarios, similar to how Warp already suggests commands to run.
To disable, go to **Settings** > **Agents** > **Warp Agent** > **Active AI** > **Prompt Suggestions**.
#### Accepting a prompt suggestion
[Section titled “Accepting a prompt suggestion”](#accepting-a-prompt-suggestion)
If you press `Ctrl+Enter` (on macOS), `Alt+Shift+Enter` (on Linux/Windows), or click on the chip, the suggestion will auto-populate into your input and run against [Agent Mode](/agents/local-agents/interacting-with-agents/) (with the most recent block attached).
Note
Prompt Suggestions use an LLM to generate prompts based on your terminal session, specifically the most recent block. These AI requests do not contribute towards your AI limits. However, any accepted prompts run in Agent Mode contribute as normal. To turn it off, go to **Settings** > **Agents** > **Warp Agent** > **Active AI**.
If [Secret Redaction](/support-and-community/privacy-and-security/secret-redaction/) is enabled, any selected regexes are applied to content sent to Active AI features to prevent any sensitive data being leaked.
### Next Command
[Section titled “Next Command”](#next-command)
Next Command uses AI to suggest the next command to run based on your active terminal session and command history. It uses your active terminal session contents and an LLM to generate commands.
To disable, go to **Settings** > **Agents** > **Warp Agent** > **Active AI** > **Next Command**.
Note
Next Command is an LLM-based feature that uses your command history (enriched with git branch, exit code, and directory metadata) as well as recent block input and output to generate the next command suggestions.
[Secret Redaction](/support-and-community/privacy-and-security/secret-redaction/) is automatically applied to any content sent to Active AI features to prevent any sensitive data being leaked.
#### Accepting Next Command suggestions
[Section titled “Accepting Next Command suggestions”](#accepting-next-command-suggestions)
Press `→` or `Ctrl+F` to accept a Next Command suggestion into your input buffer, then press `Enter` to execute it. You can change the accept keybinding (for example, to `Tab`) via the inline keybinding picker that appears next to the suggestion.
#### Billing
[Section titled “Billing”](#billing)
Next Commands are unlimited across all of Warp’s plans, including the Free plan. For the latest information on other AI limits and other pricing details, see [Warp pricing](https://www.warp.dev/pricing).
### Suggested Code Diffs
[Section titled “Suggested Code Diffs”](#suggested-code-diffs)
Suggested Code Diffs automatically surface potential fixes for command-line errors encountered within Warp. These are most often compiler errors, but they may also include other situations where Warp can confidently predict a straightforward resolution, such as simple merge conflicts.
When an error occurs, Warp evaluates whether it is appropriate for an LLM to generate a fix. If so, a “Generating fix” banner will appear while Warp prepares a proposed diff. You can stop this process at any time by pressing `Ctrl+C` or the stop button.

#### Using a suggested code diff
[Section titled “Using a suggested code diff”](#using-a-suggested-code-diff)
Once the diff is generated, you can either dismiss it or accept it. Acceptance can be done directly via the buttons in the diff view, or with `⌘+Enter` on macOS and `Ctrl+Enter` on Windows/Linux.
You can also view additional details of the diff by pressing `⌘+E` (macOS) or `Ctrl+E` (Windows/Linux), which expands the view to allow further inspection (including refining or editing it). You can also use `↓` to view the entire diff.
**Billing**
Suggested Code Diffs do not count toward your AI request limits. There are maximum limits to the number of code diffs surfaced per month, which scales based on your plan tier. For the latest details on plan limits and pricing, see [Warp pricing](https://www.warp.dev/pricing).
## Active AI privacy
[Section titled “Active AI privacy”](#active-ai-privacy)
See our [Privacy page](/support-and-community/privacy-and-security/privacy/) for more information on how we handle data with Active AI.
# Agent context overview
Canonical page: [/agents/local-agents/agent-context/](https://docs.warp.dev/agents/local-agents/agent-context/)
> How to attach various forms of multi-modal context directly to Warp's Agent within a prompt.
In Warp, you can pass different types of input directly to the Agent to guide its behavior and improve response quality. These inputs are known as **Agent Context**: ad-hoc pieces of information you manually supply during a session.
**You can attach context in several ways:**
* [Blocks as Context](/agents/local-agents/agent-context/blocks-as-context/) - share output from your terminal to help the Agent understand errors, logs, or previous commands.
* [Images as Context](/agents/local-agents/agent-context/images-as-context/) - include screenshots, diagrams, or other visuals to provide additional clarity.
* [URLs as Context](/agents/local-agents/agent-context/urls-as-context/) - attach public webpages so the Agent can extract and reference their content.
* [Selection as Context](/agents/local-agents/agent-context/selection-as-context/) - attach code snippets from the editor or review panel to enrich your prompts with precise context.
* [Using @ to Add Context](/agents/local-agents/agent-context/using-to-add-context/) - reference files, folders, code symbols, or Warp Drive objects directly in your prompts.
Commands you run inside an agent conversation are automatically included as context for your next prompt. For details, see [Blocks as Context](/agents/local-agents/agent-context/blocks-as-context/).
***
This is distinct from other persistent or automatic sources of context, such as [Rules](/agents/capabilities/rules/), [Warp Drive as Agent Mode Context](/knowledge-and-collaboration/warp-drive/agent-mode-context/), and [Model Context Protocol (MCP)](/agents/capabilities/mcp/), which the Agent also uses when available.
# Blocks as Context
Canonical page: [/agents/local-agents/agent-context/blocks-as-context/](https://docs.warp.dev/agents/local-agents/agent-context/blocks-as-context/)
> Attach blocks from your terminal as context so Warp’s Agent can understand errors, outputs, or previous commands when responding to your queries.
Attach terminal output blocks to your agent prompts so the agent can understand errors, commands, and outputs from your current or previous sessions. Blocks can be attached with keyboard shortcuts, mouse clicks, or automatically within agent conversations.
## Attaching blocks as context
[Section titled “Attaching blocks as context”](#attaching-blocks-as-context)
Warp’s Agent can use blocks from your Agent conversations as context to better understand your queries and generate more relevant responses.
You can attach a block directly from the terminal block list by clicking the AI sparkles icon on it and selecting “Attach as context.”
Attaching a block as agent context.
The most common use case is to ask the AI to fix an error. You can attach the error in a query to Agent Mode and type “fix it.”
**If you’re already in Agent Mode, use the following ways to attach or clear context from your query:**
* macOS
**Attach a previous block**
* To attach blocks to a query, you can use `⌘+↑` to attach the previous block as context to the query. While holding `⌘`, you can then use your `↑/↓` keys to pick another block to attach.
* You can also use your mouse to attach blocks in your session. Hold `⌘` as you click on other blocks to extend your block selection.
**Clear a previous block**
* To clear blocks from a query, you can use `⌘+↓` until the blocks are removed from context.
* You can also use your mouse to clear blocks in your session. Hold `⌘` as you click on an attached block to clear it.
Note
When using “Pin to the top” [Input Position](/terminal/appearance/input-position/), the direction for attaching or detaching is reversed (i.e. `⌘+↓` attaches blocks to context, while `⌘+↑` clears blocks from context).
* Windows
**Attach a previous block**
* To attach blocks to a query, you can use `Ctrl+↑` to attach the previous block as context to the query. While holding `Ctrl`, you can then use your `↑/↓` keys to pick another block to attach.
* You can also use your mouse to select blocks in your session. Hold `Ctrl` as you click on other blocks to extend your block selection.
**Clear a previous block**
* To clear blocks from a query, you can use `Ctrl+↓` until the blocks are removed from context.
* You can also use your mouse to clear blocks in your session. Hold `Ctrl` as you click on an attached block to clear it.
Note
When using “Pin to the top” [Input Position](/terminal/appearance/input-position/), the direction for attaching or detaching is reversed (i.e. `Ctrl+↓` attaches blocks to context, while `Ctrl+↑` clears blocks from context).
* Linux
**Attach a previous block**
* To attach blocks to a query, you can use `Ctrl+↑` to attach the previous block as context to the query. While holding `Ctrl`, you can then use your `↑/↓` keys to pick another block to attach.
* You can also use your mouse to select blocks in your session. Hold `Ctrl` as you click on other blocks to extend your block selection.
**Clear a previous block**
* To clear blocks from a query, you can use `Ctrl+↓` until the blocks are removed from context.
* You can also use your mouse to clear blocks in your session. Hold `Ctrl` as you click on an attached block to clear it.
Note
When using “Pin to the top” [Input Position](/terminal/appearance/input-position/), the direction for attaching or detaching is reversed (i.e. `Ctrl+↓` attaches blocks to context, while `Ctrl+↑` clears blocks from context).
***
## Block visibility across views
[Section titled “Block visibility across views”](#block-visibility-across-views)
Blocks in Warp belong to either the terminal view or a specific agent conversation:
* **Terminal blocks** - Commands you run directly in the terminal. These always appear in your terminal block list and can be attached as context to multiple conversations.
* **Agent conversation blocks** - Commands executed within an agent conversation (either by you or the agent). These only appear within that specific conversation and don’t clutter your terminal block list.
This separation keeps your terminal view clean while preserving full context within each conversation.
***
## Automatic context in agent conversations
[Section titled “Automatic context in agent conversations”](#automatic-context-in-agent-conversations)
When you’re working inside an agent conversation, any shell commands you run are automatically included as context for your next query. This means you can:
1. Run a command to see its output
2. Ask the agent about the results without manually attaching the block
For example, in an agent conversation, run `npm test` and then ask “why did these tests fail?”—the test output is already part of the conversation context.
You can also manually attach terminal view blocks to add additional context from commands you ran outside the conversation.
***
## Pending and attached context
[Section titled “Pending and attached context”](#pending-and-attached-context)
When you select blocks in terminal view and start a new conversation, those blocks become **pending context**:
* **Pending context** - Blocks are selected but the conversation hasn’t started yet. If you deselect the blocks (`Esc` or `⌘+K` on macOS, `Esc` or `Ctrl+K` on Windows/Linux), they’re removed from the agent view.
* **Attached context** - Once you submit your first query, the pending blocks become attached to the conversation and remain part of the context.
# Images as Context
Canonical page: [/agents/local-agents/agent-context/images-as-context/](https://docs.warp.dev/agents/local-agents/agent-context/images-as-context/)
> Attach screenshots, diagrams, or other images to your prompt so Warp’s Agent can use visual context when generating responses.
Attach screenshots, diagrams, or other images directly to agent prompts so the agent can use visual context when generating responses. Warp supports drag-and-drop, copy-paste, and file upload in local and cloud conversations.
## **Attaching images as context**
[Section titled “Attaching images as context”](#attaching-images-as-context)
To provide visual context, you can attach images directly to an agent prompt. This is useful for including screenshots, diagrams, or other visual references alongside your query.
You can attach images in the following ways:
* Select the **image upload button** in the agent input.
* Copy and paste images directly (e.g. right-click an image > “Copy image” or copy from a file manager) into Warp.
* Drag and drop images, such as from a file manager or screenshot utility.
Note
Warp accepts the following image formats: `.jpg`, `.jpeg`, `.png`, `.gif`, and `.webp`.
## Images in cloud conversations
[Section titled “Images in cloud conversations”](#images-in-cloud-conversations)
In an interactive cloud conversation, attach an image with the file button in the input footer, paste an image from your clipboard, or drag and drop an image into the input.
Legacy `oz agent run-cloud --attach` task creation uses separate file-attachment limits. See [running agents remotely](/agents/cli/oz-cli/#running-agents-remotely-oz-agent-run-cloud) for those limits.
### Model behavior and image handling
[Section titled “Model behavior and image handling”](#model-behavior-and-image-handling)
All supported models listed in [Model Choice](/agents/inference/model-choice/) can interpret image input.
Attaching images will consume additional requests, proportional to the number of images added. To stay within model limits, Warp will intelligently resize images before passing them as context, minimizing token usage and respecting the model’s maximum image dimensions.
# Selection as Context
Canonical page: [/agents/local-agents/agent-context/selection-as-context/](https://docs.warp.dev/agents/local-agents/agent-context/selection-as-context/)
> Attach text or diffs directly from Warp’s editor or Code Review panel as context for your Agent prompts.
Attach text selections or diff hunks directly from Warp’s code editor or Code Review panel as context for agent prompts. Select code, press a keyboard shortcut, and Warp inserts the file path, line numbers, and content into your prompt automatically.
### Attaching selections from Warp’s native code editor
[Section titled “Attaching selections from Warp’s native code editor”](#attaching-selections-from-warps-native-code-editor)
When you have Warp’s [native code editor](/code/code-editor/) open beside a regular pane, you can easily attach specific lines of code as context:
1. **Select text** in the editor. A tooltip will appear in the bottom-right corner of the selection.
2. **Add as context** by clicking the tooltip or using the keyboard shortcuts `⌘+L` (macOS) or `Ctrl+Shift+L` (Windows or Linux).
3. Warp automatically adds the relative file path and context, in addition to the line numbers of the hunk, as a formatted string into the prompt.
This makes it easy to highlight just the lines you want the Agent to analyze or modify.
Selecting code as agent context.
### Attaching selections from Warp’s Code Review panel
[Section titled “Attaching selections from Warp’s Code Review panel”](#attaching-selections-from-warps-code-review-panel)
You can also directly attach context from the [Code Review panel](/code/code-review/):
1. Hover over any **diff hunk** to reveal the option to attach it as context.
2. Attaching a diff will automatically insert the relevant file path and changed lines into your prompt.
This helps the Agent understand exactly what has been modified, making it easier to request explanations, feedback, or follow-up edits.
### Attaching code to a third-party agent session
[Section titled “Attaching code to a third-party agent session”](#attaching-code-to-a-third-party-agent-session)
You can select code, files, or snippets and feed them directly to a running third-party CLI agent session without copy-pasting or switching tools.
When a third-party agent (Claude Code, Codex, OpenCode, etc.) is running in a Warp tab, select text in Warp’s code editor or Code Review panel and attach it as context to that agent’s session using `⌘+L` (macOS) or `Ctrl+Shift+L` (Windows/Linux). This works the same way as attaching context to Warp’s built-in Agent.
For more on third-party agent support, see [Third-party CLI agents](/agents/cli-agents/overview/).
# URLs as Context
Canonical page: [/agents/local-agents/agent-context/urls-as-context/](https://docs.warp.dev/agents/local-agents/agent-context/urls-as-context/)
> Attach a public URL to your prompt so the agent can reference that page's content.
Attach a public URL to any agent prompt to provide page content as context. Warp scrapes the page and surfaces the extracted text directly to the model, giving the agent access to documentation, references, or any publicly accessible web content.
## Referencing websites via URLs
[Section titled “Referencing websites via URLs”](#referencing-websites-via-urls)
You can attach a public URL to any prompt to provide page content as context. Warp will scrape the page and surface the extracted text directly to the model.
* Only publicly accessible pages are supported.
* The full page is added to the model’s context, which may increase credit usage for long documents.
* Only the specific URL you provide is processed. The agent won’t explore the site, follow links, or crawl beyond that page.
Note
**Important**: URL attachments are different from web search. If you need the agent to look something up, gather real-time information, or pull in multiple sources, use [Web Search](/agents/capabilities/web-search/) instead.
Example of referencing docs via a URL.
# Using @ to Add Context
Canonical page: [/agents/local-agents/agent-context/using-to-add-context/](https://docs.warp.dev/agents/local-agents/agent-context/using-to-add-context/)
> Use @ to reference files, folders, code symbols, and Warp Drive objects as agent context.
Use the @ symbol in agent prompts to reference files, folders, code symbols, Warp Drive objects, and blocks from other sessions as context. The @ menu searches your entire Git repository from the project root and works immediately without codebase indexing.
## How the @ context menu works
[Section titled “How the @ context menu works”](#how-the--context-menu-works)
You can attach specific files, folders, code symbols, Warp Drive objects, and blocks from other sessions as context to a prompt using the @ symbol. When you’re inside a **Git repository**, typing @ opens a context menu that allows you to search for and select files or directories to include.
Note
Attaching context with @ works in **Agent Mode** and in **terminal mode** when referencing file paths.
**Note**: the search in the @-context menu is always relative to the root of the Git repository, even when you’re working in a subdirectory. This means you can reference *any* file or folder tracked in the repo, regardless of the current working directory.
File search using the @ symbol.
Additionally, no codebase indexing (via [Codebase Context](/agents/capabilities/codebase-context/)) is required — file search is available immediately in any Git-initialized directory. The search also respects `.gitignore` rules and will exclude ignored files from the results.
Filtering files with @app.
Referencing a folder with @styles.
### Referencing code symbols
[Section titled “Referencing code symbols”](#referencing-code-symbols)
The @ menu can also be used to fuzzy-search for code symbols in your codebase. This includes functions, classes, interfaces, etc.
If you type something like `@main`, Warp will surface a matching `main()` function and insert it into your prompt as a reference with the line number. By pointing the Agent to a specific symbol, you can give it exactly the context it needs to make a targeted edit or explanation.
[Referencing code symbols with @ context video](https://www.loom.com/embed/da0c491bd2a44ed58d4fbdf2c260b019)
### Referencing Warp Drive objects
[Section titled “Referencing Warp Drive objects”](#referencing-warp-drive-objects)
Warp Drive objects are another way to attach context with **@**. You can reference:
* [Workflows](/knowledge-and-collaboration/warp-drive/workflows/) — parameterized commands you can name and save in Warp with descriptions and arguments.
* [Notebooks](/knowledge-and-collaboration/warp-drive/notebooks/) — runnable documentation consisting of markdown text and list elements, code blocks, and runnable shell snippets that can be automatically executed in your terminal session.
* [Rules](/agents/capabilities/rules/) — reusable guidelines and constraints that inform how Agents respond to your prompts.
When you select one of these objects, Warp inserts a reference token into your prompt. The contents of the object are then automatically passed as context to the Agent.
[Referencing Warp Drive objects with @ context video](https://www.loom.com/embed/abd065af9fea421d925664135341c682)
### Referencing blocks from other sessions
[Section titled “Referencing blocks from other sessions”](#referencing-blocks-from-other-sessions)
You are not limited to the current terminal session. With @, you can also bring in blocks of output from earlier sessions.
In the demo below, Ian shows how he previously ran `cargo clippy` and now wants help fixing the reported errors. Typing `@cargo clippy` surfaces the relevant block, which you can insert into your prompt. Once added, the Agent parses the output and generates fixes or explanations directly.
You can also reference live blocks, not just those that have already completed execution.
[Referencing blocks with @ context video](https://www.loom.com/embed/a4e72847341044cca2fed59a6299e1b7)
### Why @ to reference context?
[Section titled “Why @ to reference context?”](#why--to-reference-context)
Attaching context with @ helps you:
* Reference exact outputs instead of copy-pasting entire logs
* Attach relevant files or directories without leaving Warp
* Reuse existing context and knowledge in Warp Drive
This makes Agent interactions more accurate, clearer, and efficient, without additional setup.
# Cloud-synced conversations
Canonical page: [/agents/local-agents/cloud-conversations/](https://docs.warp.dev/agents/local-agents/cloud-conversations/)
> Sync agent conversations to the cloud to access them across devices, share with teammates, and continue past conversations from anywhere.
Warp can sync your [agent conversations](/agents/local-agents/interacting-with-agents/) to the cloud, making them accessible across devices, shareable with teammates, and persistent even after logging out. This enables you to pick up where you left off on any machine, share context with collaborators, and access past [cloud agent](/platform/) conversations.
## Key capabilities
[Section titled “Key capabilities”](#key-capabilities)
* **Persistence across devices** - Your conversations remain available when you log out and back in, or switch to a different machine.
* **Access to past cloud agent conversations** - View and restore cloud agent conversations after they complete.
* **Link sharing with access controls** - Share conversations with specific teammates or your team, with configurable permissions.
* **Web viewing** - View shared conversations in a browser without installing Warp.
* **Local continuation** - Restore any cloud conversation and continue it locally on your machine.
[Cloud-synced conversations](https://www.loom.com/embed/54038cf41219485dad3adb1d811e7e9a)
## Enabling cloud conversations
[Section titled “Enabling cloud conversations”](#enabling-cloud-conversations)
Cloud conversation sync is controlled by a setting in Warp:
1. Open **Settings** > **Privacy**
2. Enable **Store AI conversations in the cloud**
When enabled, your Agent conversations automatically sync to the cloud as you interact with the Agent. When disabled, conversations are stored locally on your machine only.
Caution
If cloud conversations are disabled, conversation data is lost when you log out and cannot be shared with others. Cloud agent conversations are always stored in the cloud regardless of this setting.
## How it works
[Section titled “How it works”](#how-it-works)
### Conversation syncing
[Section titled “Conversation syncing”](#conversation-syncing)
When cloud conversations are enabled, Warp automatically syncs your conversation data after each Agent interaction. This happens in the background and does not affect your workflow.
Cloud conversations store a snapshot of the conversation state at each sync point. If you open the same conversation on two different machines, each continues independently from that snapshot—changes on one machine do not sync to the other in real time.
### Continuing vs. forking
[Section titled “Continuing vs. forking”](#continuing-vs-forking)
When you restore a cloud conversation:
* **Your own conversations** - You can continue the conversation directly, and updates sync back to the cloud.
* **Shared conversations from others** - Continuing creates a fork, giving you a new conversation that starts with the shared context but does not modify the original.
This behavior mirrors [Conversation Forking](/agents/local-agents/interacting-with-agents/conversation-forking/), where you branch off to explore a different direction without affecting the source conversation.
## Managing cloud-synced conversations
[Section titled “Managing cloud-synced conversations”](#managing-cloud-synced-conversations)
Cloud-synced conversations appear in all the usual conversation management entrypoints alongside your local conversations. You can browse, search, restore, and delete them just like any other conversation.
See [Interacting with Agents](/agents/local-agents/interacting-with-agents/) for detailed information on navigating and managing conversations, including keyboard shortcuts and the Conversation Panel in [Terminal and Agent modes](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/).
* **Browse** - View all your local and cloud-synced conversations in one place.
* **Search** - Find conversations by title or content.
* **Restore** - Click a conversation to load it into your current session and continue where you left off.
* **Delete** - Remove conversations you no longer need. Deletion is permanent and immediate.
***
## Sharing conversations
[Section titled “Sharing conversations”](#sharing-conversations)
You can share any cloud conversation with teammates via a link.
### Creating a share link
[Section titled “Creating a share link”](#creating-a-share-link)
To share a conversation:
1. Open the conversation you want to share
2. Access the share options through the conversation menu
3. Configure access permissions:
* **Anyone on your team** (default) - All team members can view
* **Specific people** - Enter email addresses to grant access
* **Anyone with the link** - No authentication required
By default, shared conversations are visible to anyone on your team.
### Viewing shared conversations
[Section titled “Viewing shared conversations”](#viewing-shared-conversations)
Recipients can view shared conversations in two ways:
* **On the web** - Open the link in a browser to view the conversation transcript without installing Warp.
* **In Warp** - Click “Open in Warp” to load the conversation in the desktop app, where you can continue it locally.
When you continue a shared conversation from someone else, Warp creates a fork so you can build on the shared context without modifying the original.
Note
Cloud-synced conversations store snapshots of conversation data. For real-time collaboration on a live session, use [Agent Session Sharing](/agents/local-agents/session-sharing/).
## Cloud agent conversations
[Section titled “Cloud agent conversations”](#cloud-agent-conversations)
[Cloud agents](/platform/) run in the cloud, and their conversations are automatically stored regardless of your local cloud conversations setting.
### Accessing cloud agent conversations
[Section titled “Accessing cloud agent conversations”](#accessing-cloud-agent-conversations)
You can access any past cloud agent conversation:
* **View transcripts** - Access the full conversation history of any past cloud agent run.
* **Restore locally** - Load a cloud agent conversation into your local Warp session to review or continue the work.
This is useful when a cloud agent completes a task and you want to review what it did or continue from where it left off.
***
## Privacy and data
[Section titled “Privacy and data”](#privacy-and-data)
### Enterprise controls
[Section titled “Enterprise controls”](#enterprise-controls)
Enterprise administrators can disable cloud conversation storage for their organization through the [Admin Panel](/knowledge-and-collaboration/admin-panel/).
When cloud conversation storage is disabled by your organization:
* Conversations are stored locally only and not synced to the cloud
* You cannot share conversations or access them across devices
* Cloud agent conversations are still accessible through the Warp dashboard
### Storage limits
[Section titled “Storage limits”](#storage-limits)
Cloud conversation storage limits vary by plan. For free users, Warp automatically removes the oldest cloud conversations when you reach your limit to make room for new ones. Your conversations are always preserved locally on your machine—only the cloud-synced copies are removed.
For current storage limits by plan, see our [pricing page](https://www.warp.dev/pricing).
### Deleting conversations
[Section titled “Deleting conversations”](#deleting-conversations)
When you delete a conversation, it is removed permanently and immediately. Make sure you no longer need a conversation before deleting it.
***
## Related features
[Section titled “Related features”](#related-features)
* [Interacting with Agents](/agents/local-agents/interacting-with-agents/) - Learn about conversation mechanics, follow-ups, and context windows.
* [Conversation Forking](/agents/local-agents/interacting-with-agents/conversation-forking/) - Branch conversations to explore different directions.
* [Session Sharing](/agents/local-agents/session-sharing/) - Collaborate in real time on a live Agent session.
* [Cloud Agents overview](/platform/) - Run agents in the cloud from triggers, schedules, or integrations.
* [Handoff between local and cloud agents](/platform/handoff/) - Promote a local conversation to a cloud agent run, or continue a finished cloud run.
# Agent code diffs and review
Canonical page: [/agents/local-agents/code-diffs/](https://docs.warp.dev/agents/local-agents/code-diffs/)
> How to review, refine, and apply code changes generated by Warp’s Agents with the built-in diff editor in Agent Conversations.
When the Warp Agent generates code changes, they appear as visual diffs in a built-in editor. Review proposed changes line by line, refine them with natural language, make manual edits, or accept them to apply the modifications to your files.
## Reviewing code diffs
[Section titled “Reviewing code diffs”](#reviewing-code-diffs)
During an Agent Conversation, Warp can generate code diffs that open directly in a built-in diff editor.
This lets you review proposed changes line by line, refine them with natural language, or make manual edits before choosing whether to apply them. It’s a fast, transparent way to stay in control of agent-generated code.
Caution
If the `Apply Code Diffs` permission is set to `Always allow` in [Agent Profiles & Permissions](/agents/capabilities/agent-profiles-permissions/), code diffs are applied automatically without being surfaced for review. If it’s set to `Agent decides` or `Always ask`, you’ll always be prompted to review diffs before they’re applied.
Note
Code diffs generated by Warp are never stored on our servers. Warp’s coding agent only works on local repositories. The agent can make changes on remote or Docker repositories, but falls back to using terminal commands (i.e. `sed`, `grep` ) to make the changes.
A code diff surfaced in an Agent Conversation.
You can also choose whether Warp automatically opens the [Code Review](/code/code-review/) panel the first time you accept a diff in a conversation.
## Navigating and applying diffs
[Section titled “Navigating and applying diffs”](#navigating-and-applying-diffs)
When an Agent generates a code diff, Warp opens it in a built-in text editor with a visual diff view. Changes are grouped into clear hunks for easy inspection.
* Use the `↑` and `↓` arrow keys (or mouse clicks) to move between hunks.
* For multi-file changes, use `←` and `→` arrow keys to switch between files.
* Once satisfied with the changes, you can apply the diffs using `Enter` or clicking “**Accept Changes**” to apply the modifications.
Caution
These modifications will not be applied to the files unless you explicitly accept them.
## Refining or editing the diffs
[Section titled “Refining or editing the diffs”](#refining-or-editing-the-diffs)
If the initial suggestion needs more work:
* Press `R` or select the “**Refine**” button to provide follow-up instructions in natural language. The agent will regenerate the diff based on your input.
* To manually adjust the code, press `E` or click “**Edit**” to switch into an editable view.
* To cancel a pending operation, use `Ctrl+C` (on macOS, Windows, or Linux). Similarly, you can exit the editor at any time with `Esc`.
Note
You can open up code files in Warp in various different ways, refer to: [Opening files in Warp](/code/code-editor/#opening-files-in-warp)
Editing a code diff in Warp’s code editor.
## Accepting diffs and continuing in Agent Mode
[Section titled “Accepting diffs and continuing in Agent Mode”](#accepting-diffs-and-continuing-in-agent-mode)
When the Agent generates a code diff outside of an active conversation — for example, from a suggested code banner or a passive recommendation — you can accept the diff and seamlessly continue in Agent Mode. After accepting, Warp opens (or returns to) the Agent conversation with the applied changes as context, so you can immediately ask follow-up questions or request further modifications without starting a new conversation.
### Demo: Editing Agent Code in Warp
[Section titled “Demo: Editing Agent Code in Warp”](#demo-editing-agent-code-in-warp)
Here’s an example from [Warp Guides](/guides/), where Zach demonstrates how to review and edit Agent code diffs natively in Warp:

# Generate (Legacy)
Canonical page: [/agents/local-agents/generate/](https://docs.warp.dev/agents/local-agents/generate/)
> Use natural language to look up commands or input, accessible either directly from the command-line input or inside any interactive command or program.
Generate (Legacy) turns natural language queries into precise terminal commands or contextual suggestions inside interactive CLI tools. Type `#` in the command line to describe what you want, and Warp generates the matching command in real time.
## What is Generate?
[Section titled “What is Generate?”](#what-is-generate)
Generate helps turn natural language queries into precise commands as terminal input or contextual suggestions inside interactive commands and programs, whether you’re using psql, gdb, git, mysql, or any other CLI tool.
Generate is backed by large language models from API providers like OpenAI and Anthropic, and is completely opt-in.
Note
Currently, you need to be online to use this feature. If this feature doesn’t work, your ISP or firewall may be blocking the calls to `app.warp.dev`
## Ways to Generate with AI
[Section titled “Ways to Generate with AI”](#ways-to-generate-with-ai)
### Generate commands as command-line input
[Section titled “Generate commands as command-line input”](#generate-commands-as-command-line-input)
Type `#` on the command-line input to generate command suggestions.
Typing ’#’ on the command line opens the suggestions interface.
[Generating commands as command-line input demo](https://www.loom.com/embed/424a763ef0c8455e8269e541301968f2)
1. Press `` Ctrl+` `` or type `#` into the text input editor to search using natural language.
2. Type in the input box what you’d like to do. For example, “replace a string in a file.”
3. Results are generated in real-time, and you can keep the current prompt or modify the prompt to generate new commands.
4. When you’ve found the command you want to execute, it can be run or saved as a Workflow onto Warp Drive to easily recall it in the future.
### \[Legacy] Generate text and contextual suggestions in interactive CLIs
[Section titled “\[Legacy\] Generate text and contextual suggestions in interactive CLIs”](#legacy-generate-text-and-contextual-suggestions-in-interactive-clis)
Caution
**Our legacy Generate feature which works in interactive CLIs has been replaced by** [Full Terminal Use](/agents/capabilities/full-terminal-use/)**, where the Warp Agent can now run and control long-running or full-screen terminal applications**.\
The agent can provide input when prompted, navigate interactive screens, and continue execution without stalling.
In interactive CLI applications, you can generate input using natural language.
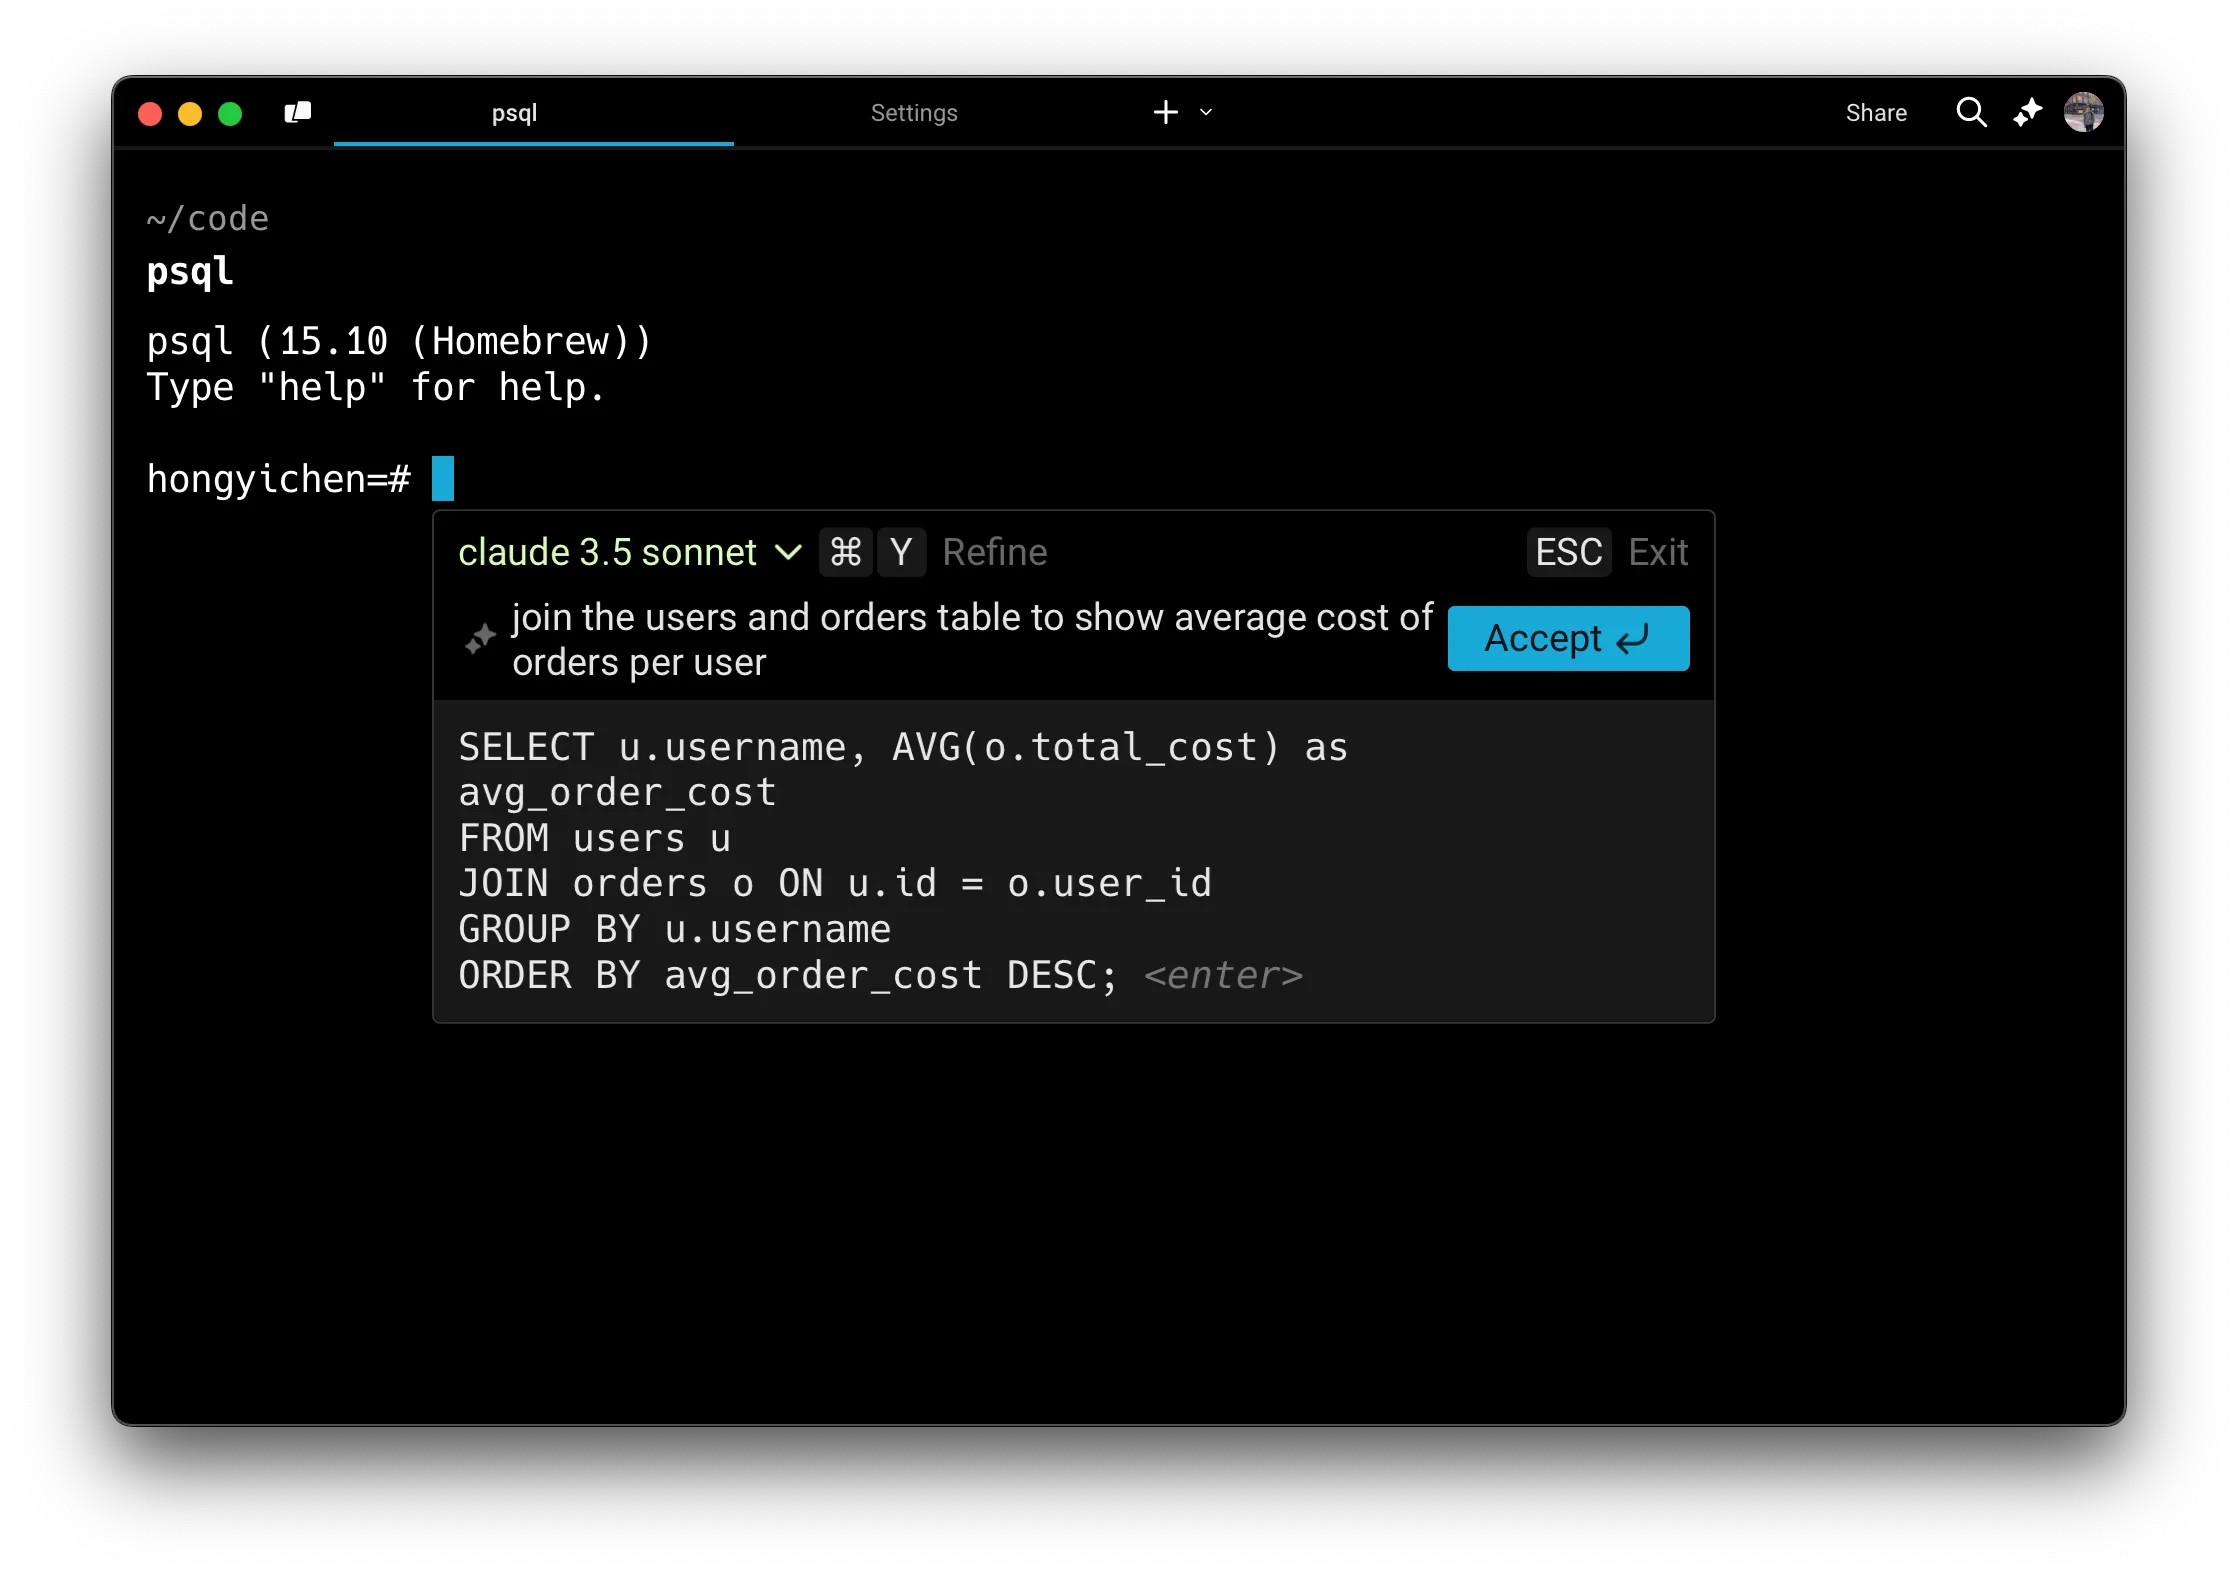
Generating a SQL query using natural language.
Generating Vim commands using natural language.
* macOS
1. Inside a long-running, interactive command, press `⌘+I` when you see the hint text appear.
2. Type what you would like to generate in the input box. For example, “show me all tables in my Postgres database” or in Vim, “generate a recursive Fibonacci function and save it to the file.”
3. Results are generated in real time using the [LLM of your choice](/agents/inference/model-choice/).
4. To refine or follow up on your query, press `⌘+Y`. You can then either edit your last message by pressing `↑` or add a follow-up by typing in new text.
5. When you’ve found the text you want to add or execute, press `Enter` or click the Accept button.
* Windows
1. Inside a long-running, interactive command, press `Ctrl+Shift+I` when you see the hint text appear.
2. Type what you would like to generate in the input box. For example, “show me all tables in my Postgres database” or in Vim, “generate a recursive Fibonacci function and save it to the file.”
3. Results are generated in real time using the [LLM of your choice](/agents/inference/model-choice/)
4. To refine or follow up on your query, press `Ctrl+Shift+Y`. You can then either edit your last message by pressing `↑` or add a follow-up by typing in new text.
5. When you’ve found the text you want to add or execute, press `Enter` or click the Accept button.
* Linux
1. Inside a long-running, interactive command, press `Ctrl+Shift+I` when you see the hint text appear.
2. Type what you would like to generate in the input box. For example, “show me all tables in my Postgres database” or in Vim, “generate a recursive Fibonacci function and save it to the file.”
3. Results are generated in real time using the [LLM of your choice](/agents/inference/model-choice/)
4. To refine or follow up on your query, press `Ctrl+Shift+Y`. You can then either edit your last message by pressing `↑` or add a follow-up by typing in new text.
5. When you’ve found the text you want to add or execute, press `Enter` or click the Accept button.
A couple of other examples of interactive CLIs where you can invoke Generate:
* **Database REPL** (e.g. `psql`, `mysql`, `sqlite`): Generate SQL queries such as “create a table to store user data” or “show me all the rows in orders for the last month”
* **Text editors** (e.g. `vim`, `nano`): Quickly generate text such as a markdown header, a code block comment, or a boilerplate CSS class.
* **Python REPL** (e.g. `ipython`, `python`): Quickly generate Python snippets such as “create a simple plot of x” or “write a unit test for this function”
* **Debugger tools** (e.g. `gdb`, `lldb`): Get commands for setting breakpoints or inspecting memory
* **Version control** (e.g. `git rebase -i`): Speed up complex git commands by describing your goal such as “interactively rebase master onto feature-branch”
* **Cloud provider shells** (e.g. `gcloud`, `aws cli`): faster setup or resource management such as “create a new Kubernetes cluster” or “provision a new RDS instance”
Caution
If you experience any issues with Generate, see known issues for [troubleshooting steps](/support-and-community/troubleshooting-and-support/known-issues/#online-features-dont-work).
# Interacting with agents
Canonical page: [/agents/local-agents/interacting-with-agents/](https://docs.warp.dev/agents/local-agents/interacting-with-agents/)
> Manage agent conversations across sessions with follow-ups, context blocks, and multi-thread support.
Agent conversations in Warp are multi-turn interactions tied to terminal sessions. Continue previous threads with follow-ups, manage conversation history, attach context from blocks and files, and run multiple conversations simultaneously across windows, tabs, or panes.
## Conversations with Warp’s Agent
[Section titled “Conversations with Warp’s Agent”](#conversations-with-warps-agent)
Conceptually, a conversation is a sequence of AI queries and blocks. Conversations are tied to sessions and you can run multiple Agent Mode conversations simultaneously in different windows, tabs, or panes.
Conversations work best when the queries are related. If your new question builds on the last one, continue in the same conversation. If it is unrelated, it is better to start a new one so that the context remains relevant.
Note
Long conversations can cause slower performance and lower-quality answers. When working on a separate task or question, start fresh rather than relying on context from earlier interactions.
Note
To access conversations across devices, share them with teammates, or restore past cloud Agent conversations, enable [Cloud-synced Conversations](/agents/local-agents/cloud-conversations/).
### Staying in a conversation (follow-ups)
[Section titled “Staying in a conversation (follow-ups)”](#staying-in-a-conversation-follow-ups)
By default, if you ask an AI query immediately after interacting in Agent Mode, your query is sent as a **follow-up** to the current conversation. The conversation view provides a dedicated space for multi-turn interactions, and the conversation panel shows which conversation you are in.
**To follow-up on a previous conversation:**
* Simply continue prompting the agent if you are already in an active conversation.
* Open the **Conversations menu** (`⌘+Y` on macOS, `Ctrl+Shift+Y` on Windows/Linux), select a conversation, and then enter your query.
You don’t have to wait for the agent to finish before lining up your next prompt. With [prompt queueing](/agents/local-agents/interacting-with-agents/prompt-queueing/), you can queue follow-ups while the agent is still responding and have them send automatically in order.
#### Agent tips in the input
[Section titled “Agent tips in the input”](#agent-tips-in-the-input)
While the Warp Agent is thinking and processing your request, Warp may surface short tips with helpful workflows and ways to use Warp. These tips appear under the Warping indicator.
You can enable or disable these tips in two places:
* **Settings**: **Settings** > **Agents** > **Warp Agent** > **Input** > **Show agent tips**
* **Command Palette**: Open the Command Palette (`⌘+P` on macOS, `Ctrl+Shift+P` on Windows/Linux), then select “**Show Agent Tips**” or “**Hide Agent Tips**”
### Managing conversations
[Section titled “Managing conversations”](#managing-conversations)
You can view previous conversations or start a new conversation via the **Conversations Menu** (`⌘+Y` on macOS, `Ctrl+Shift+Y` on Windows/Linux).
[Agent interaction controls walkthrough](https://www.loom.com/embed/9cc2451412be43e389a6b1414ea185e4)
Note
The “New Conversation” item disappears once you start searching for an actual conversation.
### Starting a new conversation
[Section titled “Starting a new conversation”](#starting-a-new-conversation)
Warp automatically creates a new conversation in a few situations. For example, if you ask an AI query after running a shell command or if three hours pass without activity, Agent Mode will start a fresh conversation. Starting a new conversation opens a fresh conversation view. Use the conversation panel to see all active and past conversations.
* macOS
You can also start a new conversation manually at any time:
* Press `⌘+Enter` to start a new conversation, or use the `/new` slash command.
* Open the **Conversations Menu** using `⌘+Y` and select “New Conversation”.
* Windows
You can also start a new conversation manually at any time:
* Press `Ctrl+Shift+Enter` to start a new conversation, or use the `/new` slash command.
* Open the **Conversations Menu** using `Ctrl+Shift+Y` and select “New Conversation”.
* Linux
You can also start a new conversation manually at any time:
* Press `Ctrl+Shift+Enter` to start a new conversation, or use the `/new` slash command.
* Open the **Conversations Menu** using `Ctrl+Shift+Y` and select “New Conversation”.
## Context window management
[Section titled “Context window management”](#context-window-management)
Every conversation with an agent consumes tokens stored in a **context window**. The context window (sometimes called *context length*) is the amount of text (measured in tokens) that a large language model (LLM) can process at one time. **The size of the context window depends on the model you are using.**
As tokens accumulate and exceed the context window, performance and response quality may degrade. If the context window is exceeded, the model may lose track of earlier parts of the conversation, and **Warp will automatically summarize the conversation to free up space**.
### Warp provides a **context window usage indicator** to help you track this:
[Section titled “Warp provides a context window usage indicator to help you track this:”](#warp-provides-a-context-window-usage-indicator-to-help-you-track-this)
When less than 20% of the window is used, no indicator is shown. As more tokens accumulate, the usage bar progresses to reflect how much of the context window has been consumed.

As you approach the limit, the indicator turns red to warn that the context window is nearly full.

Once the limit is exceeded, Warp automatically summarizes the conversation so you can continue without losing important context.

The context window usage indicator is available in agent conversation views.
Note
If you switch models during a conversation, the context usage indicator updates only after you send your next message.
### Context window usage breakdown
[Section titled “Context window usage breakdown”](#context-window-usage-breakdown)
To see what is filling the context window, open the conversation usage card and click **View breakdown** in the **Context window used** row. The row expands into a per-segment breakdown, with each segment’s share of the window shown as a percentage:
* **System Prompt** - Warp’s instructions to the model, including your [rules](/agents/capabilities/rules/).
* **Tool Definitions** - Descriptions of the tools available to the agent, including any [MCP servers](/agents/capabilities/mcp/).
* **Conversation History** - Previous queries, responses, and tool results in the conversation.
* **Latest Input** - Your most recent query and the context attached to it.
* **Images** - Any [images](/agents/local-agents/agent-context/images-as-context/) attached to the conversation.
* **Other** - Everything not covered by the segments above.
Use the breakdown to decide what to trim: a large **Conversation History** segment is a good signal to start a new conversation or summarize, while a large **Tool Definitions** segment suggests turning off MCP servers you aren’t using.
## Conversation segmentation
[Section titled “Conversation segmentation”](#conversation-segmentation)
Warp automatically detects when your query has shifted to a new topic. When this happens, it suggests starting a new conversation instead of continuing in the same context.
These options appear in the block list, where you can decide whether to branch off into a new conversation or keep going with the current one.
You can also create a new conversation manually at any time by using the keyboard shortcut, opening a new tab, or opening a new pane.
* macOS
* Start a new conversation: `⌘+Shift+N`
* Open a new tab: `⌘+T`
* Open a new pane: `⌘+D`
* Windows
* Start a new conversation: `Ctrl+Shift+N`
* Open a new tab: `Ctrl+Shift+T`
* Open a new pane: `Ctrl+Shift+D`
* Linux
* Start a new conversation: `Ctrl+Shift+N`
* Open a new tab: `Ctrl+Shift+T`
* Open a new pane: `Ctrl+Shift+D`
## Conversation Panel
[Section titled “Conversation Panel”](#conversation-panel)
The **Conversation Panel** on the left side of the window is the home for browsing and switching between agent conversations. It’s designed to make multi-threaded work obvious: you can see what’s active, what you ran recently, and jump back into any thread without guessing where your context went.
### Panel layout
[Section titled “Panel layout”](#panel-layout)
The conversation panel is split into two dropdowns (collapsible sections) that help you navigate between conversations:
#### Active
[Section titled “Active”](#active)
The **Active** dropdown lists conversations where you have sent at least one query since opening them. Simply expanding a conversation does not make it active—you need to interact with the Agent first.
* Select a conversation to switch to it immediately.
* The conversation you’re currently viewing is highlighted.
* Cloud agent conversations and runs always appear in **Active** while they are open.
#### Past
[Section titled “Past”](#past)
The **Past** dropdown lists your recent conversation history.
Each row typically shows:
* Conversation title
* When it happened (for example, “8 min ago”, “3 days ago”)
* Working directory (when relevant)
Use **Past** to restore a previous conversation. When you select a past conversation, Warp reopens it in a new tab or your active pane, letting you continue where you left off.
### Conversation storage
[Section titled “Conversation storage”](#conversation-storage)
By default, your agent conversations are stored locally on your machine. You can optionally enable **cloud-synced conversations** to:
* Access your conversation history across different devices
* Share conversations with teammates
* Retain conversations when you log out or switch machines
For full details on enabling cloud sync, sharing conversations, and accessing cloud agent conversations, see [Cloud-synced Conversations](/agents/local-agents/cloud-conversations/).
Note
To enable cloud sync, go to **Settings** > **Privacy** and toggle on **“Store AI conversations in the cloud”**. When disabled, conversations are stored locally only and cannot be shared. Note that cloud agent conversations are always stored in the cloud regardless of this setting.
### Search
[Section titled “Search”](#search)
Use the search field at the top of the conversation panel to quickly find your conversation.
* Type to filter conversations by title (and, in some builds, by directory/context).
* Useful when you have many threads and want to jump directly to one.
### New conversation
[Section titled “New conversation”](#new-conversation)
Click the **New conversation** button at the bottom of the **Active** conversation list to start a new conversation.
Starting a new conversation creates a fresh thread in the **Active** dropdown, without deleting or overwriting your previous ones.
### Navigation behavior
[Section titled “Navigation behavior”](#navigation-behavior)
Navigation between [Terminal and Agent modes](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/) is designed to be direct:
* **Clicking an active conversation** - Takes you directly to that conversation view.
* **Clicking a past conversation** - Opens the conversation in a **new pane**, preserving your current context.
* **Command Palette** - Open the Command Palette and type `conversations:` to filter and navigate directly to any conversation.
* **`⌘Y` conversation selector** - Opens a dedicated menu showing your existing and past conversations. This works in both terminal view and agent view.
* **Up-arrow history** - Shows both past shell commands and past prompts you’ve sent in recent conversations. The behavior differs by context:
* **In terminal view** - Shows both past shell commands and recent conversations.
* **In agent view** - Shows past prompts you’ve sent in conversations.
***
### Ways to move around
[Section titled “Ways to move around”](#ways-to-move-around)
Use `esc` or the back button to return to terminal mode, `⌘Y` to open the conversation selector, or `⌘↩` to start a new conversation. For a complete list of keyboard shortcuts and slash commands, see [Terminal and Agent modes - Keyboard shortcuts](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/#keyboard-shortcuts-quick-reference).
### Exit confirmation for in-progress conversations
[Section titled “Exit confirmation for in-progress conversations”](#exit-confirmation-for-in-progress-conversations)
Exiting a conversation that is still in progress will **cancel** the agent’s current work. To prevent accidental cancellations, Warp shows a confirmation hint:
* **First exit attempt** - The hint changes to “Press again to exit” (or similar).
* **Confirmation window** - You have about 2 seconds to press `esc` or `^C` again to confirm.
* **After confirmation** - Warp exits the conversation and cancels the in-progress request.
This confirmation step ensures you don’t accidentally lose work when the agent is mid-task.
Note
Empty new conversations (where you haven’t sent any messages yet) can be exited immediately without confirmation.
# Agent questions
Canonical page: [/agents/local-agents/interacting-with-agents/agent-questions/](https://docs.warp.dev/agents/local-agents/interacting-with-agents/agent-questions/)
> Learn how Warp's Agent asks questions for clarification, how to answer or skip them, and how to interact with them when the Agent asks.
Agent questions let Warp’s Agent pause to ask for your input when it needs a decision before continuing. Instead of guessing, the Agent presents a few options in an **Agent questions** card right inside the conversation and waits for your answer.
## Key features
[Section titled “Key features”](#key-features)
* **Multiple-choice questions** - The Agent presents options for you to choose from instead of asking a freeform question.
* **Single-select and multi-select answers** - Some questions accept one answer, while others let you select all options that apply.
* **Other answers** - When the Agent enables an **Other** option, you can type your own answer and submit it from the card.
* **Multiple questions** - A single card can contain multiple questions, with navigation controls for moving between them.
* **Skip support** - You can skip questions. The Agent receives the skipped state and continues with its best judgment.
* **Permission controls** - Agent Profiles include an **Ask questions** permission that controls whether the Agent pauses for your answer.
## How it works
[Section titled “How it works”](#how-it-works)
When the Agent needs a decision from you before it can continue confidently, it pauses and shows an **Agent questions** card in the conversation instead of guessing.
Each question comes with a set list of options. Questions can accept single or multiple answers. The Agent can flag a recommended option, or let you add your own answer under **Other**. When you answer or skip a question, Warp passes that back to the Agent so it can keep going with your response in mind.
The Agent saves questions for moments when it genuinely can’t move forward safely or accurately on its own. If you skip a question, Warp sends the skipped state to the Agent so it can continue with the context it already has.
## Answering Agent questions
[Section titled “Answering Agent questions”](#answering-agent-questions)
When an **Agent questions** card appears, choose the option or options that best match your intent.
1. Select one or more options in the card. Options are numbered, so press the matching number key (`1`, `2`, `3`, and so on) or click an option to select it. Multi-select questions show “select all that apply” next to the question text.
2. If available, click **Other** or press its number key to enter your own answer, then press `Enter`.
3. Click **Next** or press `Enter` to continue. For a single-select question, Warp automatically advances to the next question after you choose an option.
4. When a card contains more than one question, press `←` to revisit the previous question or `→` to move to the next one. A question counter and **prev** / **next** controls appear at the bottom of the card.
5. To skip the remaining questions, click **Skip all** or press `Ctrl+C`.
After you answer or skip the questions, Warp summarizes the result in the conversation. You can expand the completed card to review the answers that were sent to the Agent.
## Controlling when the Agent asks questions
[Section titled “Controlling when the Agent asks questions”](#controlling-when-the-agent-asks-questions)
The **Ask questions** permission is part of each Agent Profile. To change it, open the Warp app and go to **Settings** > **Agents** > **Profiles** > **Permissions**, then edit the active profile.
The available settings are:
* **Never ask** - The Agent does not pause for clarifying questions. Warp skips the question and the Agent continues with its best judgment.
* **Ask unless auto-approve** - The Agent can pause for your answer during normal conversations, but Warp skips questions while auto-approve is on.
* **Always ask** - The Agent can pause for your answer even when auto-approve is on.
Auto-approve is designed for unattended execution. If you want the Agent to keep running without pausing for clarifying questions, use **Ask unless auto-approve** or **Never ask**.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Terminal and Agent modes](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/) - Start and navigate Agent conversations in Warp.
* [Profiles & permissions](/agents/capabilities/agent-profiles-permissions/) - Configure Agent Profile permissions and autonomy settings.
* [Agent notifications](/agents/capabilities/agent-notifications/) - Learn how Warp notifies you when an Agent needs your input.
# Conversation Forking
Canonical page: [/agents/local-agents/interacting-with-agents/conversation-forking/](https://docs.warp.dev/agents/local-agents/interacting-with-agents/conversation-forking/)
> Branch into a new agent thread with full context to explore alternatives without altering the original conversation.
Warp allows you to **fork conversations** to create a new thread that inherits all of the context, messages, and history from an existing conversation. This is useful when you want to branch off in a new direction without affecting the original conversation.
[Forking a conversation from a previous point video](https://www.loom.com/embed/15164f2abc19437ebefb47a8c6b52eb8)
### How conversation forking works
[Section titled “How conversation forking works”](#how-conversation-forking-works)
* When you fork a conversation, the new thread starts with the same context and history as the original.
* Any follow-ups in the forked conversation do **not** impact the original. Likewise, continuing in the original conversation does not change the fork.
* Forked conversations behave just like any other conversation: you can move them into new windows, panes, or tabs.
* Your selected model and execution profile are preserved in the forked conversation.
*Example*: You can fork a conversation to explore an alternate solution, ask “what if” questions, or continue down two separate paths in parallel.
### How to fork a conversation
[Section titled “How to fork a conversation”](#how-to-fork-a-conversation)
There are five ways to fork an existing conversation:
#### 1. From the Command Palette
[Section titled “1. From the Command Palette”](#1-from-the-command-palette)
Open the menu using the Command Palette (`⌘+Y` on macOS / `Ctrl+Shift+Y` on Windows/Linux).
Select **Fork current conversation** to fork your current conversation, or fork a specific conversation from open conversations.
In addition, when you hover over any open conversation in the Command Palette, you’ll see a **fork button**. This lets you fork not only active conversations, but also inactive and historical ones.
You can also access this conversation view from the conversation chip in the current conversation.
#### 2. From the footer of the most recent AI response block
[Section titled “2. From the footer of the most recent AI response block”](#2-from-the-footer-of-the-most-recent-ai-response-block)
In any conversation in the block list, click the **fork button** in the footer of the most recent AI block. A new conversation opens in a separate pane with the full context of the original.
#### 3. Using the `/fork` slash command
[Section titled “3. Using the /fork slash command”](#3-using-the-fork-slash-command)
Type `/fork` in the input to fork the current conversation. You can optionally include a prompt after the command, and Warp will send that prompt in the newly forked conversation.
* Press `Enter` to open the fork in a new pane (default)
* Press `⌘+Enter` (macOS) or `Ctrl+Enter` (Windows/Linux) to open the fork in the current pane
*Example*: `/fork Can you try a different approach?` Forks the selected conversation and immediately sends `Can you try a different approach?` in the forked conversation.
#### 4. Using the `/fork-and-compact` slash command
[Section titled “4. Using the /fork-and-compact slash command”](#4-using-the-fork-and-compact-slash-command)
Type `/fork-and-compact` to fork the current conversation and automatically compact the forked version. This combines forking with [context window management](/agents/local-agents/interacting-with-agents/#context-window-management), giving you a fresh start with a summarized context.
* Press `Enter` to open the fork in a new pane (default)
* Press `⌘+Enter` (macOS) or `Ctrl+Enter` (Windows/Linux) to open the fork in the current pane
#### 5. Using the `/fork-from` slash command
[Section titled “5. Using the /fork-from slash command”](#5-using-the-fork-from-slash-command)
Type `/fork-from` to open a searchable menu of all queries in the current conversation. Select a query to fork the conversation from that specific point—everything up to and including that exchange is included in the fork, but subsequent messages are excluded.
This is a more discoverable alternative to right-clicking on an agent response block.
### Fork from anywhere in a conversation
[Section titled “Fork from anywhere in a conversation”](#fork-from-anywhere-in-a-conversation)
In addition to forking from the end of a conversation, you can fork from any point in the conversation history. This lets you return to an earlier agent response and branch off in a new direction from there.
To fork from a specific point, **right-click** on any agent response block or click the three-dot menu in the top-right corner of the block.
* Select **Fork conversation from here** to create a new conversation that includes everything up to and including that response, but excludes any queries or responses that came after it.
**This is particularly useful for:**
* **Exploring alternate paths** - Go back to a point where the conversation was on track and try a different approach.
* **Managing your context window** - If a conversation has grown too long, fork from an earlier point to continue with only the relevant context.
* **Preventing context pollution** - When a conversation has accumulated errors or gone off track, fork from before those issues occurred to start fresh.
### Settings
[Section titled “Settings”](#settings)
You can configure the default layout for forked conversations in **Settings** > **Features** > **Open forked conversation layout**:
* **Split Pane** (default): Opens the forked conversation in a new pane alongside your current view.
* **New Tab**: Opens the forked conversation in a new tab.
This setting controls the default behavior when forking via the Command Palette, AI block footer button, or slash commands (when pressing `Enter`).
### Using forked conversations
[Section titled “Using forked conversations”](#using-forked-conversations)
* Once forked, you can continue prompting as if you were still in the original conversation. The original conversation remains unchanged, allowing you to reference or continue both in parallel.
* For example, after forking you can ask *“Could you explain more?”* and Warp responds using the inherited context.
**Forking is especially useful when:**
* You want to explore different approaches without losing the original thread.
* You need to keep one conversation “clean” while experimenting in another.
* You want to reuse context or specific blocks from older conversations.
# Prompt queueing
Canonical page: [/agents/local-agents/interacting-with-agents/prompt-queueing/](https://docs.warp.dev/agents/local-agents/interacting-with-agents/prompt-queueing/)
> Queue follow-up prompts while an agent is still responding, then have Warp send them automatically and in order as each response finishes.
Prompt queueing lets you line up follow-up prompts while an agent is still working. Instead of waiting for the agent to finish—or interrupting it to send your next idea—you queue prompts and Warp sends them automatically, one at a time, as each response completes.
The queued prompts panel, with three prompts queued while the agent responds.
## Key features
[Section titled “Key features”](#key-features)
* **Auto-queue toggle** - Turn on auto-queue so every prompt you submit while the agent is busy joins the queue instead of interrupting the current response.
* **`/queue` slash command** - Queue a single follow-up prompt inline, without switching modes.
* **Queued prompts panel** - View, reorder, edit, and remove every pending prompt from one collapsible panel above the input.
* **Automatic sequential sending** - Queued prompts fire one at a time as the agent finishes each response, in the order you set.
* **Send the next prompt with Enter** - When the input is empty, press `Enter` to send the top queued row immediately.
* **Auto-queue during long-running commands** - By default, prompts submitted while an agent is driving a long-running command it started are queued and sent when the command finishes.
* **Per-conversation queues** - Each conversation keeps its own queue and auto-queue state, which persist when you leave and re-enter the conversation.
* **Cloud agent support** - Queue follow-ups for cloud agents, even while the environment is still setting up.
## How it works
[Section titled “How it works”](#how-it-works)
Each agent conversation has its own queue. When the current response finishes successfully, Warp sends the next prompt in the queue. This continues one prompt at a time until the queue is empty.
Queued prompts use the same submission flow as prompts you send manually, so slash commands, skills, and other input behave the same way.
A few things to know:
* **Shell commands are never queued.** If you submit in shell mode, Warp runs the command in the terminal immediately, regardless of your auto-queue setting. The exception is while an agent is driving a long-running command. See [Queueing during long-running commands](#queueing-during-long-running-commands).
* **Queues don’t persist across restarts.** A conversation’s queue is cleared when the conversation is deleted or cleared, and queues do not persist after an app restart.
* **One prompt is in flight at a time.** Warp waits for the current response to finish before sending the next queued prompt.
## Queueing a prompt
[Section titled “Queueing a prompt”](#queueing-a-prompt)
There are three ways to queue prompts yourself. The auto-queue toggle and `/queue` act on the active conversation; the default submission mode setting controls what happens app-wide. Warp also queues prompts automatically while an agent is driving a long-running command. See [Queueing during long-running commands](#queueing-during-long-running-commands).
### Auto-queue toggle
[Section titled “Auto-queue toggle”](#auto-queue-toggle)
The auto-queue toggle is the fastest way to queue several prompts in a row. While the agent is responding, a clock-plus icon appears in the warping indicator (the status bar above the input).
The auto-queue toggle in the warping indicator.
1. Click the clock-plus icon, or press `⌘+Shift+J` (macOS) or `Ctrl+Shift+J` (Windows/Linux). The icon turns the accent color to show auto-queue is on.
2. Type a prompt and press `Enter`. Because the conversation is in progress, the prompt is added to the queue instead of interrupting the current response. The input refocuses so you can keep queuing.
The toggle is per-conversation and stays on across responses until you turn it off, so you can queue as many prompts as you like. Switching to another conversation shows that conversation’s own toggle state.
### `/queue` slash command
[Section titled “/queue slash command”](#queue-slash-command)
Use `/queue` to add one follow-up prompt without turning on auto-queue.
1. In an agent conversation, type `/queue` followed by the prompt—for example, `/queue run the tests and fix any failures`.
2. Press `Enter`. The prompt is added to the queue and the input clears.
`/queue` requires an active conversation and a prompt. If you run `/queue` without a prompt, Warp shows an error.
Note: If the agent is idle, `/queue` sends the prompt immediately. It only queues prompts while a response is in progress.
### Set the default submission mode
[Section titled “Set the default submission mode”](#set-the-default-submission-mode)
By default, submitting a prompt while the agent is responding interrupts the current response and sends your new prompt right away. You can change this default so new conversations queue instead.
1. In the Warp app, go to **Settings** > **Agents** > **Warp Agent** > **Input**.
2. For **Default prompt submission mode**, choose one of:
* **Interrupt response** - Cancel the in-flight response and send the new prompt immediately (the default).
* **Queue until response finishes** - Hold the new prompt until the current response finishes, then send it.
This setting is the default for conversations that you haven’t explicitly toggled. The per-conversation auto-queue toggle always overrides it for that conversation.
When **Interrupt response** is selected, a second dropdown, **Default long-running command submission mode**, appears directly below it. It controls what happens while an agent is driving a long-running command. See [Queueing during long-running commands](#queueing-during-long-running-commands).
The Default prompt submission mode setting under Agent input settings.
## Queueing during long-running commands
[Section titled “Queueing during long-running commands”](#queueing-during-long-running-commands)
When an agent is driving a long-running command it started (a dev server, REPL, database shell, or other interactive program it launched through [Full Terminal Use](/agents/capabilities/full-terminal-use/)), prompts you submit are queued by default instead of steering the agent mid-command. Warp sends them to the agent automatically when the command finishes. This auto-queueing applies only to commands the agent started; if you start a command yourself and tag the agent in, your prompts keep steering the agent immediately.
While the agent is in control of the command (including while it’s blocked waiting for an approval):
* **Prompts queue instead of interrupting.** Submitting a prompt adds it to the conversation’s queue and clears the input so you can keep typing. These rows show an italic *(queued until the command finishes)* suffix after the prompt text, indicating they fire when the command ends rather than when the full response finishes.
* **Suffixed prompts send when the command finishes.** When the command finishes, Warp sends the suffixed prompts at the front of the queue, in order, even if you manually took over the command first. A suffixed prompt sends this way only while it stays at the front: if you reorder a prompt queued another way ahead of it, that suffixed prompt waits and sends later under the normal end-of-response rules. Prompts queued in other ways (`/queue`, the auto-queue toggle, or the queue default mode) always follow those normal rules.
* **Shell commands queue as regular commands.** Shell commands you submit during a long-running command are queued without the suffix and run in the terminal as usual; they are not sent to the agent when the command ends.
* **The UI reflects the queue state.** The auto-queue toggle in the warping indicator appears in its active, accent-colored state, and the empty input’s ghost text shows the queue hint instead of the steer hint.
* **All queue interactions still work.** You can reorder, edit, delete, use send now, or press `Enter` on an empty input to send the top row early.
This queueing is per-conversation and derived from the running command rather than a sticky toggle: when the command ends or control transfers back to you, the conversation reverts to whatever queue state it had before the command (its own toggle state, or the app-wide default). It applies only while the agent is in control of the command, not while you are.
To steer the agent mid-command instead, turn the auto-queue toggle off: click the clock-plus icon, or press `⌘+Shift+J` (macOS) or `Ctrl+Shift+J` (Windows/Linux). Prompts then send immediately for the remainder of that command only; the override doesn’t change the conversation’s persistent toggle state, and the next command the agent starts auto-queues again. Toggling it back on re-enables queueing for the rest of the command.
### Change the long-running command submission mode
[Section titled “Change the long-running command submission mode”](#change-the-long-running-command-submission-mode)
You can change this behavior app-wide:
1. In the Warp app, go to **Settings** > **Agents** > **Warp Agent** > **Input**.
2. For **Default long-running command submission mode**, choose one of:
* **Queue until command finishes** - Queue prompts submitted while an agent is driving a long-running command it started, and send them to the agent when the command finishes (the default).
* **Send immediately** - Send the prompt to the agent right away, steering it mid-command.
The dropdown appears directly below **Default prompt submission mode**, and only when that setting is **Interrupt response**. When the default prompt submission mode is **Queue until response finishes**, this setting is hidden and ignored, because prompts already queue until the entire response finishes.
Changing the setting takes effect immediately, including in the middle of a running command. You can also change it from the Command Palette using **Set long-running command submission: send immediately** or **Set long-running command submission: queue until command finishes**, which are available while the default prompt submission mode is **Interrupt response**.
## Managing queued prompts
[Section titled “Managing queued prompts”](#managing-queued-prompts)
When a conversation has at least one queued prompt, the queued prompts panel appears between the warping indicator and the input box. Its header shows the count, such as **2 queued**, with a chevron to collapse or expand the list. The panel is expanded by default, and prompts are listed from top (next to send) to bottom (last to send).
Hovering a row reveals controls for that prompt:
* **Reorder** - Drag a row up or down by its handle to change the order. The row at the top of the list always sends next.
* **Send now** - Click the up-arrow icon to send that prompt immediately instead of waiting for the agent to finish the current response. You can also press `Enter` while the input box is empty to send the top row. See [Send the next prompt with Enter](#send-the-next-prompt-with-enter) below.
* **Edit** - Click the pencil icon to edit the prompt inline. Press `Enter` to save your changes or `Esc` to cancel.
* **Delete** - Click the trash icon to remove the prompt from the queue. If the input is empty, Warp moves the deleted prompt into the input so you can revise and resend it. If the input already has text, the deleted prompt is discarded.
A queued row with its send now, edit, and delete controls revealed on hover.
Deleting the last prompt removes the panel, since the queue is now empty.
### Send the next prompt with Enter
[Section titled “Send the next prompt with Enter”](#send-the-next-prompt-with-enter)
When the queued prompts panel is showing and the input box is empty, pressing `Enter` sends the row at the top of the queue immediately, exactly like clicking that row’s send now button. Each press sends one row: the remaining rows stay queued, and pressing `Enter` again sends the new top row, until the queue is empty. The input stays empty throughout.
This works for both row types: queued prompts are sent to the agent, and queued shell commands run in the terminal. If the input has any text, `Enter` keeps its normal behavior and submits the typed input, leaving the queue untouched. `Enter` also keeps its normal behavior while the CLI agent Rich Input composer is open.
The panel header shows this shortcut: next to the queued count, an **⏎ to send** hint appears whenever pressing `Enter` would send the top row. The hint is hidden when it wouldn’t, for example while you’re editing a row inline, while the input has text, or when the top row is a cloud run’s locked initial prompt. That locked prompt can never be sent this way; `Enter` does nothing while it sits at the head of the queue, and the rows behind it wait until it’s removed.
## When sending pauses
[Section titled “When sending pauses”](#when-sending-pauses)
Queued prompts only continue after a response finishes successfully. If the response errors, is stopped, or is interrupted with `Ctrl+C`, Warp pauses the queue so you can review what should happen next. The queue stays intact, and no queued prompts are discarded.
When sending pauses and you’re viewing that conversation, Warp helps you pick up where you left off:
* If the input box is empty, the first queued prompt is removed from the queue and its text is placed in the input so you can review and resend it.
* If the input box already has text, the queue is left untouched.
Any remaining prompts stay in the panel so you can review, edit, reorder, or delete them. Sending resumes automatically the next time the conversation completes a response cleanly.
## Prompt queueing with cloud agents
[Section titled “Prompt queueing with cloud agents”](#prompt-queueing-with-cloud-agents)
Prompt queueing also works for [cloud agents](/platform/), including while a cloud environment is still setting up. You can queue follow-up work before the agent is live, and Warp sends those prompts once the agent is ready and the current response finishes.
For cloud agents, the prompt that started the run appears as a locked first row in the queue because it has already been accepted by the agent. You can’t edit, reorder, or delete that first prompt, but any follow-up prompts queued behind it remain editable.
A cloud run’s locked initial prompt during environment setup.
While the environment is setting up, queued prompts wait until the cloud agent is live. After setup, the locked row is removed and the rest of the queue sends in order as each response completes.
Because cloud conversations keep running after you leave the agent view, their queues continue to send in the background and are restored when you return.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Slash Commands](/agents/capabilities/slash-commands/) - The full list of built-in commands, including `/queue`.
* [Full Terminal Use](/agents/capabilities/full-terminal-use/) - How agents attach to and drive interactive long-running commands.
* [Terminal and Agent modes](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/) - How input is routed between the terminal and the agent.
* [Cloud agents overview](/platform/) - Run agents in the cloud from any trigger.
# Terminal and Agent modes
Canonical page: [/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/](https://docs.warp.dev/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/)
> Warp provides two distinct modes: a clean terminal for commands, and a dedicated conversation view for multi-turn agent workflows.
Warp provides two distinct modes: a clean terminal for running shell commands, and a dedicated conversation view for multi-turn interactions with the Warp Agent. Terminal mode keeps the interface minimal by default, while Agent Mode surfaces full controls for model selection, voice input, image attachments, and conversation management.
***
## Key terminology
[Section titled “Key terminology”](#key-terminology)
Before diving in, here are two key concepts:
* **Terminal session** - Your shell environment where you run commands. This is the default mode when you open Warp—a clean, traditional terminal input.
* **Agent conversation** - A multi-turn interaction with the Automation Platform. Conversations maintain context across exchanges and have their own dedicated view with richer controls.
Terminal and Agent modes make switching between these two contexts seamless while keeping them visually distinct.
***
## Why two modes
[Section titled “Why two modes”](#why-two-modes)
Terminal and Agent modes separate your terminal and agent workflows into distinct contexts:
* **Clean terminal by default** - Minimal input when you’re running commands. Agent controls appear only when you need them.
* **Dedicated conversation view** - Multi-turn agent workflow spaces have full controls like model select, voice input, image attachments, and conversation history.
* **Explicit mode switching** - The current mode is clearly visible, enabling better workflow organization—you can separate, minimize, and expand different conversations.
***
## Two distinct modes
[Section titled “Two distinct modes”](#two-distinct-modes)
### Terminal mode (default)
[Section titled “Terminal mode (default)”](#terminal-mode-default)
Terminal mode is the default when you open a new tab or pane.
* Looks and behaves like a traditional terminal input.
* Agent controls are not always visible, keeping the interface clean.
* A message bar shows contextual hints for interacting with agents.
**Terminal mode hints**
The message bar at the bottom of the terminal provides contextual guidance:
* **Default hint** - Shows `⌘↩ for new agent` when the input is empty.
* **Send to agent** - Shows `⌘↩ to send to agent` when you have text that could be a prompt.
* **Error block attachment** - When the last command failed, shows a hint to attach the output as agent context (e.g., `⌘↑ attach 'npm install...' output as agent context`).
* **Attached context indicator** - Shows when you have blocks or text selections attached (e.g., `⌘↩ to send to agent with 'git status' attached`).
* **Continue conversation** - When your last visible item is an agent conversation block, shows `⌘Y to continue conversation`.
If auto-detection is enabled, Warp labels your input as “agent” or “shell” before you submit, showing “(autodetected)” in magenta. See [Understanding auto-detection](#understanding-auto-detection) for configuration and override methods.
**Disabling the message bar:** To hide the terminal mode hint bar while keeping AI features enabled, go to **Settings** > **Features** > **Terminal Input** and toggle off **Show terminal input message line**. This only hides the contextual hints—it does not disable any AI functionality.
Caution
If you disable the message bar while auto-detection is enabled, you won’t see the visual indicator that tells you whether Warp detected your input as a shell command or an agent prompt. Consider also disabling auto-detection (**Settings** > **Agents** > **Warp Agent** > **Input**) if you turn off the message bar.
Note
The shortcuts shown on this page use macOS keybindings. For Windows and Linux shortcuts, see [Keyboard Shortcuts](/getting-started/keyboard-shortcuts/).
### Agent conversation view (expanded UI)
[Section titled “Agent conversation view (expanded UI)”](#agent-conversation-view-expanded-ui)
* A dedicated conversation view with richer agent controls including model select, voice input, image attachments, and conversation management.
* Familiar “charms” (current directory, git branch, diff view entry point, etc.) are still available.
* Designed for multi-turn workflows and managing multiple conversations.
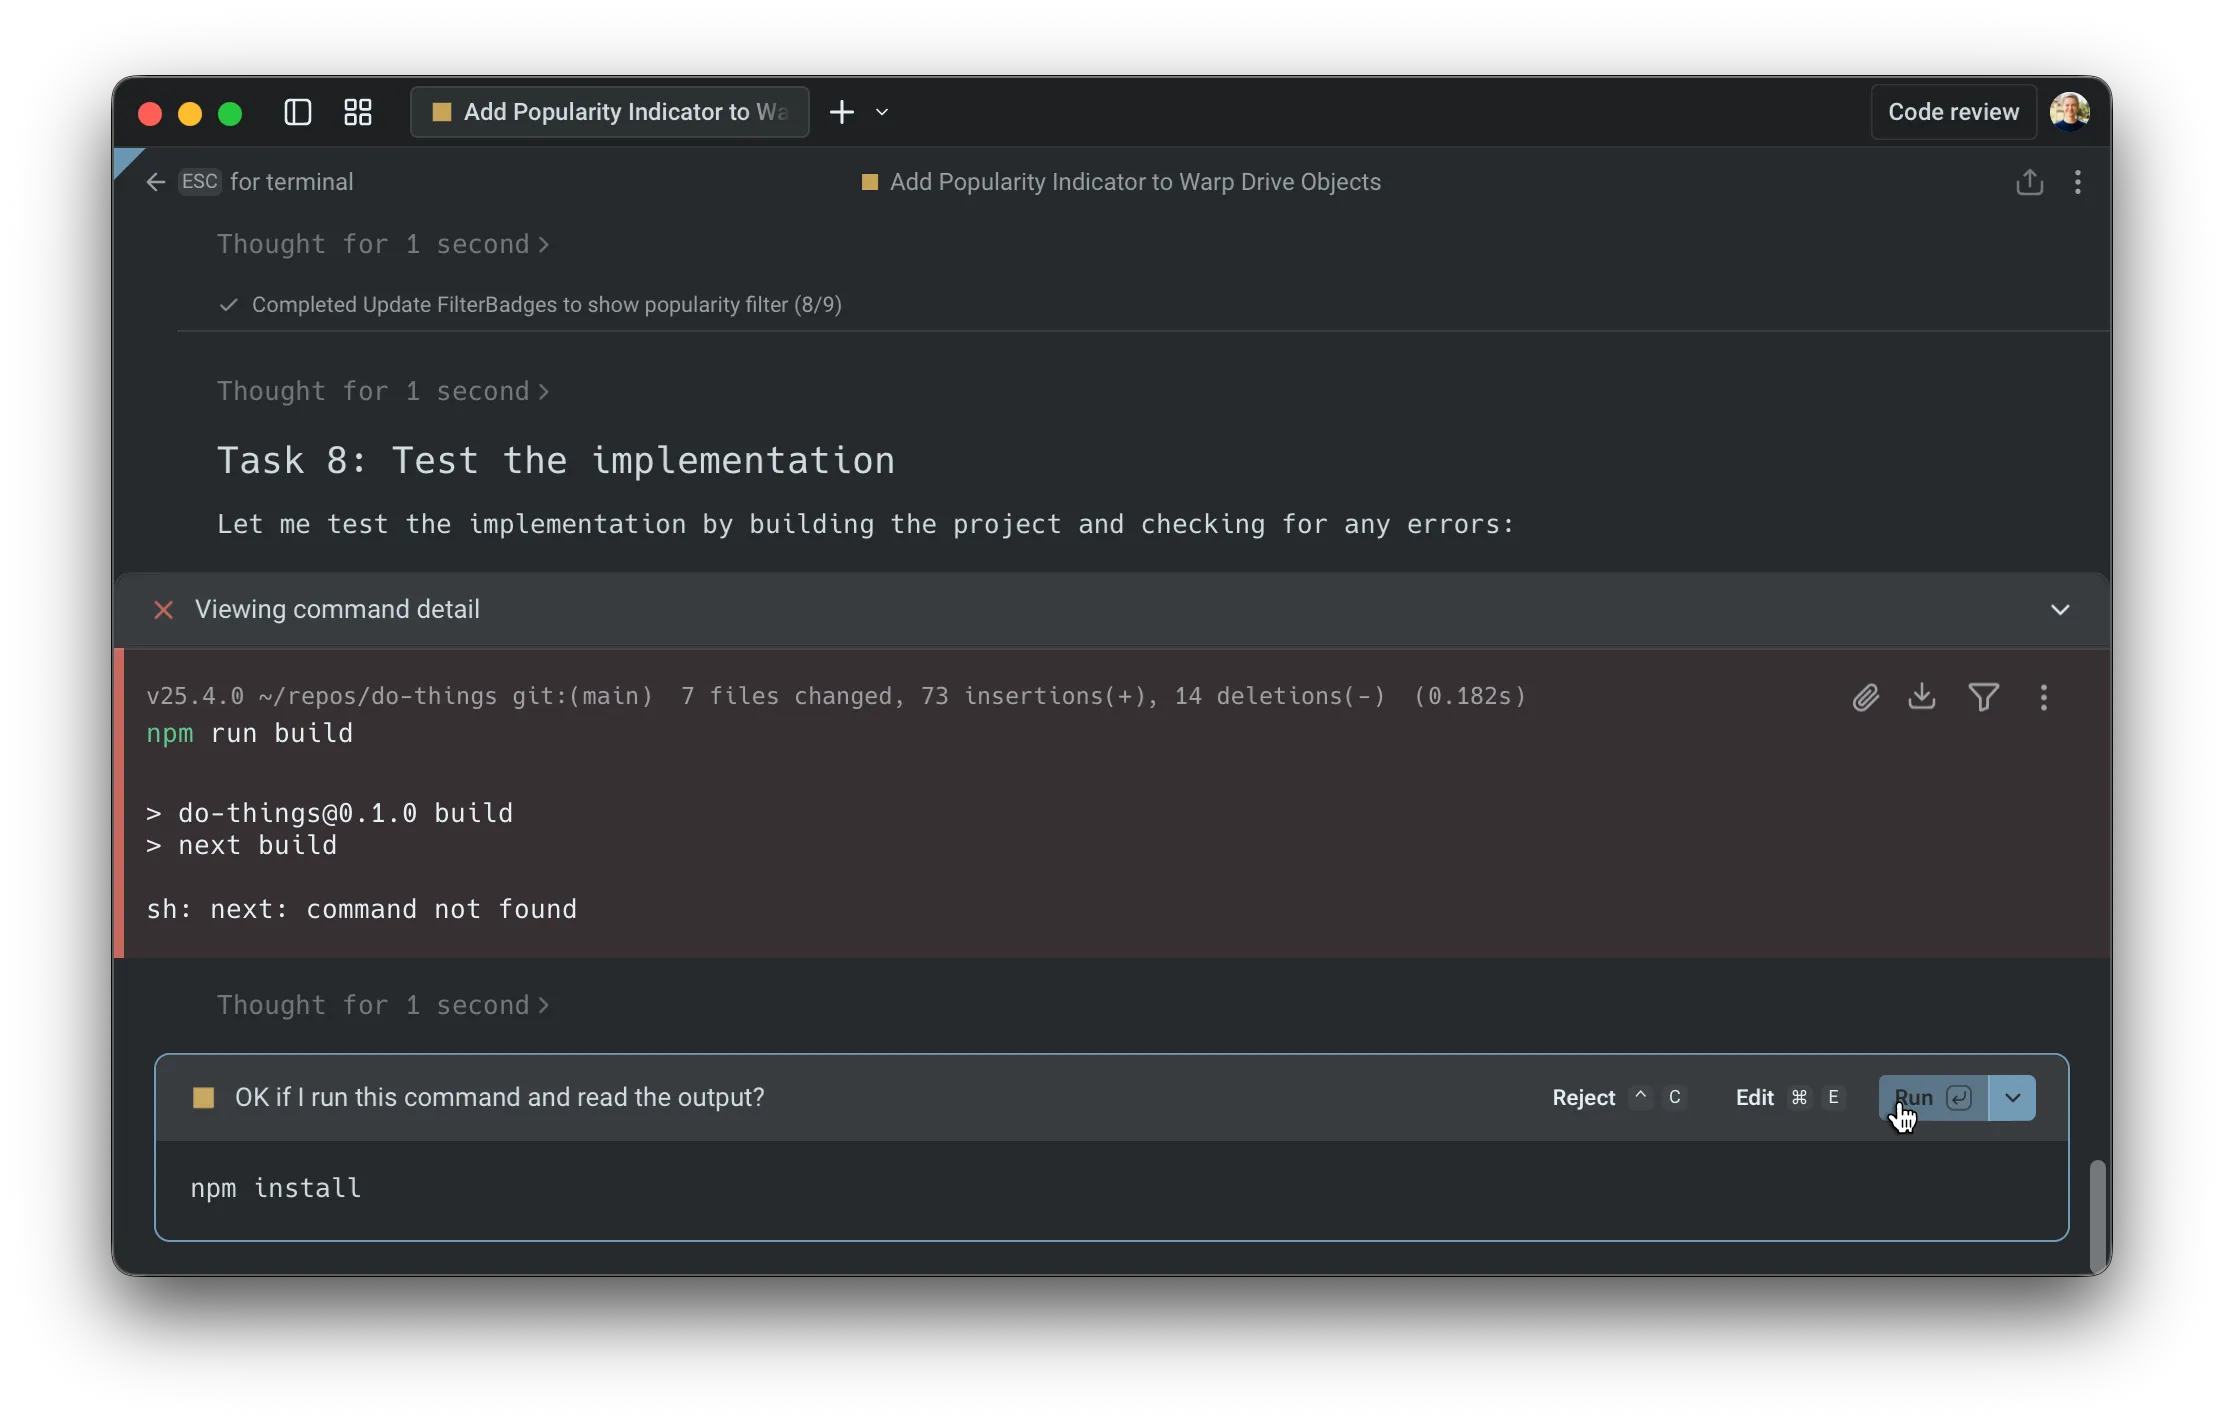
The dedicated Agent Conversation View.
**Key difference**
Agent controls appear only when you’re in a conversation, keeping your terminal clean otherwise.
Note
Agent conversation views are identified with an alternative background color and the input toolbelt showing model selector, voice input, and image attachment buttons.
#### Customizing the input toolbelt
[Section titled “Customizing the input toolbelt”](#customizing-the-input-toolbelt)
The chips and buttons on the agent input toolbelt can be reordered, hidden, or moved between the left and right sides of the input. Right-click the input in an agent conversation and select **Edit agent toolbelt** to open the editor. Your layout persists across app restarts.
Agent Mode-specific items include the model selector, autodetection toggle, Context Usage, and fast forward toggle. Shared items like voice input, file attachment, and context chips appear in both the Agent Mode toolbelt and the [CLI coding agent toolbelt](/agents/cli-agents/overview/#customizing-the-toolbelt).
**Block origin and visibility**
Blocks in Warp belong to either the terminal view or a specific agent conversation:
* **Terminal blocks** - Commands you run directly in the terminal always appear in your terminal block list and can be attached as context to any conversation.
* **Agent conversation blocks** - Commands executed within an agent conversation (either by you or the agent) only appear within that specific conversation and don’t appear in the terminal block list.
In agent conversations, context is managed automatically, with optional manual attachment from terminal view:
* **Automatic context** - Commands executed within an agent conversation are included as context for subsequent prompts.
* **Manual attachment** - You can attach terminal blocks to bring in outputs from outside the conversation.
* **Conversation scope** - Agent conversation blocks stay scoped to that conversation, while terminal blocks remain in the terminal block list.
This separation keeps your terminal view clean while preserving full context within each conversation. For shortcuts, pending vs. attached context, and block selection behavior, see [Blocks as Context](/agents/local-agents/agent-context/blocks-as-context/).
#### Cloud agent conversations
[Section titled “Cloud agent conversations”](#cloud-agent-conversations)
In addition to local agent conversations, you can start **cloud agent conversations** that run in an isolated cloud environment. Cloud agents are useful for:
* Running parallel agents across multiple tasks
* Running agents remotely on hosted computers (offloading compute from your local machine)
* Running agents autonomously in the cloud
* Checking in on your agents from anywhere
To start a cloud agent conversation, press `⌥⌘↩` (Option+Command+Enter on macOS, or `Ctrl+Alt+Enter` on Windows/Linux) from terminal mode. You can also use the welcome block’s “Start cloud project” action.
Cloud agent conversations have a few differences from local conversations:
* **Environment selector** - Choose which [Warp Environment](/platform/environments/) to run in
* **Credits indicator** - Shows your remaining cloud agent credits
* **Different zero state** - The conversation header indicates “New cloud agent conversation”
Cloud agent conversations are always stored in the cloud. For more details on accessing and sharing cloud conversations, see [Cloud-synced Conversations](/agents/local-agents/cloud-conversations/).
**Accessing running or past cloud conversations:**
* **From the conversation list panel** - Cloud conversations appear alongside local conversations. Click to open.
* **From the management view** - Use the [Agent Management view](/platform/managing-cloud-agents/) to see all cloud agent runs, filter by status, and click any row to open the conversation.
* **From the Oz web app** - Access your cloud agents from the [Oz web app](https://oz.warp.dev) to manage runs from any browser.
For more on cloud agents, see [Cloud Agents overview](/platform/).
***
## Understanding auto-detection
[Section titled “Understanding auto-detection”](#understanding-auto-detection)
Auto-detection (which detects whether you’re typing natural language or a shell command) helps Warp interpret each input as either a shell command or an agent request. When auto-detection is enabled, Warp shows an **inline indicator** in the prompt (for example, “(autodetected)” in magenta).
### How it works
[Section titled “How it works”](#how-it-works)
**In terminal mode:**
When you type text that appears to be a natural language request (e.g., “Summarize the dependencies in this project”), Warp labels it as “agent” and displays the “(autodetected)” indicator. Pressing Enter will send your input directly to the agent in a new conversation, creating a “quicksend” workflow for text-only requests.
**In agent conversation view:**
When auto-detection identifies your input as a shell command, Warp displays a distinct UI border around the input to indicate the mode switch. This helps you understand that your input will run as a command rather than being sent to the agent.
### Settings
[Section titled “Settings”](#settings)
Note
You can control auto-detection separately for terminal mode and agent conversation view. Both toggles are in **Settings** > **Agents** > **Warp Agent** > **Input**:
* **Terminal mode:** Toggle **Autodetect agent prompts in terminal input**
* **Agent conversation view:** Toggle **Autodetect terminal commands in agent input**
### Override methods
[Section titled “Override methods”](#override-methods)
There are multiple ways to override auto-detection:
* **Keyboard shortcut** - Press `⌘I` to switch between command and Agent Mode.
* **`!` prefix** - In agent view, prepend `!` to your input to force it to run as a shell command (e.g., `!ls` or `!git status`).
Common examples:
* You typed something that looks like a command, but you intended an agent request.
* You typed a sentence, but you intended it to run as a command (rare, but it happens).
Note
**Note:** After you override, the selection is “sticky” for that entry, so you can submit confidently.
### Defaults for new vs existing users
[Section titled “Defaults for new vs existing users”](#defaults-for-new-vs-existing-users)
Auto-detection is enabled by default for new Warp users. For users who had Warp before Terminal and Agent modes were introduced, auto-detection is disabled by default to preserve their existing workflows.
***
## Entering and navigating conversations
[Section titled “Entering and navigating conversations”](#entering-and-navigating-conversations)
### How to enter a conversation
[Section titled “How to enter a conversation”](#how-to-enter-a-conversation)
There are several ways to start or enter an agent conversation:
#### A) Use the `/agent` or `/new` slash command
[Section titled “A) Use the /agent or /new slash command”](#a-use-the-agent-or-new-slash-command)
Type `/agent` or `/new` in terminal mode to enter the agent conversation view. This is the recommended way to explicitly switch to Agent Mode.
* `/agent` or `/new` - Opens a new agent conversation view with full controls
* `/agent <prompt>` - Sends your prompt directly to the agent in a new conversation
#### B) Use the keyboard shortcut
[Section titled “B) Use the keyboard shortcut”](#b-use-the-keyboard-shortcut)
Press `⌘↩` (Command+Enter on macOS, or `Ctrl+Shift+Enter` on Windows/Linux) to enter the conversation view immediately. This is a shortcut for `/agent`.
**Use this when you want to:**
* attach an image
* use voice input
* access other conversation-only controls before sending your first message
#### C) Quicksend with auto-detection
[Section titled “C) Quicksend with auto-detection”](#c-quicksend-with-auto-detection)
When auto-detection is enabled in terminal mode, you can start a conversation immediately:
1. Type a natural language request (e.g., “Summarize the dependencies in this project”).
2. If Warp detects it as an agent request, it shows an “(autodetected)” indicator.
3. Press Enter to send directly to the agent in a new conversation.
This “quicksend” method is useful for quick, text-only requests when you don’t need conversation-only controls like voice input or image attachments.
#### D) Continue from the up-arrow history menu
[Section titled “D) Continue from the up-arrow history menu”](#d-continue-from-the-up-arrow-history-menu)
Press `↑` (up arrow) to open an inline history menu. The menu contents vary by context—see [Navigation behavior](/agents/local-agents/interacting-with-agents/#navigation-behavior) for details on how up-arrow works in terminal view vs. agent view.
#### E) Click an active AI suggestion
[Section titled “E) Click an active AI suggestion”](#e-click-an-active-ai-suggestion)
When [Active AI Recommendations](/agents/local-agents/active-ai/) is enabled, Warp displays contextual prompt suggestions based on your recent activity. Clicking any of these suggestions opens the agent conversation view and sends that prompt immediately.
***
### Navigating conversations
[Section titled “Navigating conversations”](#navigating-conversations)
Warp includes a **Conversation Panel** for browsing and managing your agent conversations. For details on the panel layout, navigation, and conversation storage, see [Agent Conversations](/agents/local-agents/interacting-with-agents/).
### Using slash commands
[Section titled “Using slash commands”](#using-slash-commands)
**In an agent conversation**
While you’re in an agent conversation, you can access Warp’s [slash commands](/agents/capabilities/slash-commands/) any time by typing `/` in the input.
* Type `/` to open the command menu
* Keep typing to filter commands (for example: `/conversations`, `/compact`)
* Use `↑` / `↓` to navigate and `Enter` to run
* Press `esc` to dismiss the menu
**Key slash commands in Agent Mode:**
* `/new` or `/agent` - Start a new conversation.
* `/plan` or `/plan <prompt>` - Enter agent view and start a planning conversation. The agent will create an implementation plan before making changes.
* `/conversations` - Open the conversation list panel.
* `/compact` - Summarize and compact the current conversation to free up context window space.
* `/fork` - Fork the current conversation into a new thread. Press `Enter` to fork in the existing pane, or `⌘↩` (`Ctrl+Shift+Enter` on Windows/Linux) to fork in a new pane.
* `/fork-and-compact` - Fork the conversation and automatically summarize it.
* `/fork from` - Choose a specific point in the conversation to fork from. A menu appears showing your previous queries—select one to fork from that point.
* `/model` - Select or change the AI model for the conversation.
Slash commands are a quick way to take common actions without leaving the keyboard.
**In terminal mode**
Slash commands aren’t just for agent conversations. You can also type `/` in terminal mode to open a limited set of commands.
Note
Agent conversations expose the full set of slash commands (including `/fork`, `/compact`, and `/model`). Terminal mode exposes a reduced set focused on quick actions.
For the complete list of available slash commands, see [Slash Commands](/agents/capabilities/slash-commands/).
### Forking conversations
[Section titled “Forking conversations”](#forking-conversations)
Forking lets you branch off from an existing conversation to explore a different direction without losing your original thread.
**How to fork:**
1. In an agent conversation, type `/fork` and press `Enter`.
2. Choose where to open the forked conversation:
* `Enter` - Fork in the current pane (replaces the current view).
* `⌘↩` (`Ctrl+Shift+Enter` on Windows/Linux) - Fork in a new pane (keeps the original visible).
**Fork and compact:**
Use `/fork-and-compact` to fork and automatically summarize the conversation. This is useful when your context window is getting full but you want to continue building on the same work.
**Fork from a specific point:**
Use `/fork from` to choose exactly where in the conversation you want to branch from:
1. Type `/fork from` and press `Enter`.
2. A menu shows your previous queries in the conversation.
3. Select the query you want to fork from.
4. Choose `Enter` (existing pane) or `⌘↩` / `Ctrl+Shift+Enter` (new pane).
This is helpful when you want to go back to an earlier point and try a different approach.
For more forking methods and use cases, see [Conversation Forking](/agents/local-agents/interacting-with-agents/conversation-forking/).
***
## Using Agent Mode as the default experience
[Section titled “Using Agent Mode as the default experience”](#using-agent-mode-as-the-default-experience)
If you prefer to type natural language at any point in a terminal session and have it automatically routed to an agent, you can configure this using the “default mode for new sessions” setting.
### 1. Set new tabs to open in agent view
[Section titled “1. Set new tabs to open in agent view”](#1-set-new-tabs-to-open-in-agent-view)
By default, new tabs and panes open in terminal mode. To launch directly into an agent conversation instead:
1. Go to **Settings** > **Features** > **General**.
2. Change **Default mode for new sessions** to **Agent**.
### 2. Enable auto-detection in Agent Mode
[Section titled “2. Enable auto-detection in Agent Mode”](#2-enable-auto-detection-in-agent-mode)
With auto-detection enabled in agent view, Warp automatically detects whether your input is natural language or a shell command, routing it to the agent or running it in the terminal accordingly.
You can also use the “toggle input mode” keyboard shortcut to override auto-detection and force either “shell” or “agent” mode.
1. Go to **Settings** > **Agents** > **Warp Agent** > **Input**.
2. Toggle on **Autodetect terminal commands in agent input**.
Press `⌘I` (macOS) or `Ctrl+I` (Windows/Linux) to manually toggle between shell and Agent Mode at any time, overriding auto-detection.
Note
Auto-detection is enabled by default for new Warp users.
***
## Keyboard shortcuts (quick reference)
[Section titled “Keyboard shortcuts (quick reference)”](#keyboard-shortcuts-quick-reference)
In conversation view, press `?` to show/hide the full shortcuts panel. Here are the key shortcuts:
### Navigation and mode switching
[Section titled “Navigation and mode switching”](#navigation-and-mode-switching)
* **Start new agent conversation** (from terminal mode) - `⌘↩` (macOS) / `Ctrl+Shift+Enter` (Windows/Linux)
* **Start new cloud agent conversation** (from terminal mode) - `⌥⌘↩` (macOS) / `Ctrl+Alt+Enter` (Windows/Linux)
* **Send to agent with attached context** (from terminal mode) - `⌘↩` (macOS) / `Ctrl+Shift+Enter` (Windows/Linux) when blocks are selected
* **Tag agent into long-running command** - `⌘↩` (macOS) / `Ctrl+Shift+Enter` (Windows/Linux) while an interactive command is running
* **Exit conversation** (back to terminal mode) - `esc`
* **Stop agent / exit on empty input** - `^C` / `Ctrl+C`
* **Open conversation selector** - `⌘Y` (macOS) / `Ctrl+Y` (Windows/Linux)
* **Toggle conversation list panel** - `⌘⇧H` (macOS) / `Ctrl+Shift+H` (Windows/Linux)
* **Override auto-detection** (switch shell ↔ agent) - `⌘I` (macOS) / `Ctrl+I` (Windows/Linux)
### Input modifiers
[Section titled “Input modifiers”](#input-modifiers)
* **`!`** - Prepend to force shell mode (e.g., `!ls`)
* **`/`** - Open slash command menu
* **`@`** - Open context menu (attach files, symbols, etc.)
* **`?`** - Show/hide keyboard shortcuts panel
### Conversation actions
[Section titled “Conversation actions”](#conversation-actions)
* **Resume a paused/cancelled conversation** - `⌘⇧R` (macOS) / `Ctrl+Alt+R` (Windows/Linux)
* **Toggle auto-accept** (for agent tool executions) - `⌘⇧I` (macOS) / `Ctrl+Shift+I` (Windows/Linux)
* **Open code review pane** - `⌘⇧+` (macOS) / `Ctrl+Shift++` (Windows/Linux)
* **Toggle plan panel** (if a plan exists) - `⌘⌥P` (macOS) / `Ctrl+Alt+P` (Windows/Linux)
### In slash command / fork menus
[Section titled “In slash command / fork menus”](#in-slash-command--fork-menus)
* **Navigate menu items** - `↑` / `↓`
* **Select** (fork in existing pane) - `Enter`
* **Select and open in new pane** - `⌘↩` (macOS) / `Ctrl+Shift+Enter` (Windows/Linux)
* **Dismiss menu** - `esc`
### Customizing keybindings
[Section titled “Customizing keybindings”](#customizing-keybindings)
You can customize keyboard shortcuts for slash commands and other actions in **Settings** > **Keyboard shortcuts**. This lets you assign your preferred key combinations to frequently used commands.
For example, to bind a keyboard shortcut to the `/agent` slash command:
1. Open **Settings** > **Keyboard shortcuts**
2. Search for “agent” or the slash command you want to bind
3. Click the shortcut field and press your desired key combination
4. The shortcut is saved automatically
This is useful for actions you perform frequently, like starting a new conversation or opening the conversation list.
# Voice input for agents
Canonical page: [/agents/local-agents/interacting-with-agents/voice/](https://docs.warp.dev/agents/local-agents/interacting-with-agents/voice/)
> Voice enables natural language interaction with Warp, letting you speak commands and queries directly to your terminal.
Warp’s Voice feature transforms how you interact with your terminal, letting you naturally speak commands and questions instead of typing them. This is especially powerful when combined with Agent Mode for complex operations or when you need to explain longer scenarios.
Note
Voice input functionality can be configured in **Settings** > **Agents** > **Warp Agent** > **Voice**. You can toggle voice input and select your preferred activation hotkey from pre-defined options.
[Voice Demo](https://www.loom.com/embed/77399be4e434443488bbe267b3548552)
## Getting started with voice
[Section titled “Getting started with voice”](#getting-started-with-voice)
### Initial setup
[Section titled “Initial setup”](#initial-setup)
First-time users will need to grant microphone permissions:
* On macOS: Accept the system permission prompt or allow Warp microphone access in > **System Settings** > **Privacy & Security** > **Microphone**
* On Windows: Allow Warp microphone access in **Settings** > **Privacy & Security** > **Microphone**
* On Linux: Configure through system sound settings
### Using voice
[Section titled “Using voice”](#using-voice)
There are two ways to activate Voice:
1. **Microphone Button in Agent Mode**
* Click the microphone icon in Agent Mode
* Start speaking when the indicator shows it’s listening
* Click again to stop recording
2. **Hotkey Method**
* macOS
* Press and hold the `Fn` key (configurable) to start recording
* Speak your command or query while holding the key
* Release the `Fn` key to stop recording and transcribe
* Windows
* Press and hold the `Alt+→` key (configurable) to start recording
* Speak your command or query while holding the key
* Release the `Alt+→` key to stop recording and transcribe
* Linux
* Press and hold the `Alt+→` key (configurable) to start recording
* Speak your command or query while holding the key
* Release the `Alt+→` key to stop recording and transcribe
Voice input settings.
### Sample use cases
[Section titled “Sample use cases”](#sample-use-cases)
Voice input makes complex interactions with Agent Mode more natural and efficient. Instead of typing lengthy queries, you can speak naturally to accomplish various tasks. For example, you can say “Create a new Node.js project, install Express and MongoDB, then set up a basic server with a health check endpoint,” or “What’s the difference between chmod and chown? Give me examples of when to use each one.”
You can also describe multi-step system tasks like “Find all log files in my project that contain errors from the last 24 hours, create a summary of the errors, and email it to me.” Agent Mode breaks down these requests into the necessary commands and provides detailed explanations.
Voice input is not limited to just Agent Mode - it works across all of Warp’s input interfaces. Whether you’re using the Find dialog to search through text, entering commands in the terminal, or working with other input editors, you can use voice commands to quickly input your text.
Voice input in a Warp editor.
## Privacy & security
[Section titled “Privacy & security”](#privacy--security)
The transcription is powered by [Wispr Flow](https://wisprflow.ai/). Voice data is processed in real-time by Wispr Flow and is not retained as a recording after transcription.
## Usage limits
[Section titled “Usage limits”](#usage-limits)
Voice features have anti-abuse limits in place to ensure fair usage. These limits are subject to change as we continue to improve the service.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### Common issues
[Section titled “Common issues”](#common-issues)
1. **Microphone not detected** If your microphone isn’t being detected, first check your system permissions to ensure Warp has access. You should also verify that your microphone is properly connected to your system. If issues persist, try restarting Warp to reset the connection.
2. **Poor transcription quality** To improve transcription quality, try to minimize background noise in your environment. Position yourself closer to the microphone while speaking, and verify that your microphone input levels are properly adjusted in your system settings. For best results, speak clearly at a natural pace and use complete sentences to provide better context. When referring to specific file names or commands, enunciate them clearly. It’s also recommended to review the transcription before sending to ensure accuracy.
3. **Feature not activating** If the Voice feature isn’t activating, confirm that your hotkey settings are correctly configured in Warp. Check for any conflicting keyboard shortcuts that might interfere with Voice activation. Also ensure that you’re running the latest version of Warp, as older versions can have compatibility issues.
If you are on an Enterprise plan, your administrator may have disabled Voice functionality, or it may be pending approval.
# Interactive Code Review
Canonical page: [/agents/local-agents/interactive-code-review/](https://docs.warp.dev/agents/local-agents/interactive-code-review/)
> Review agent-generated code, leave inline comments, and have Warp's native agent or any supported third-party CLI agent apply your feedback.
Interactive Code Review lets you review agent-generated code, leave inline comments on specific lines, batch your feedback, and send all requested changes to the agent in a single pass. It works with Warp’s native agent and supported third-party CLI agents like Claude Code and Codex.
### Overview
[Section titled “Overview”](#overview)
Interactive Code Review lets you review, annotate, and refine code generated by any supported agent, whether that’s Warp’s native Agent or a third-party CLI agent running in Warp. Instead of relying on an AI to review another AI’s output, Warp keeps the developer in control.
You can inspect diffs, leave inline comments, batch feedback, and send all requested changes back to the agent in a single pass.
**Interactive Code Review builds on Warp’s existing** [Code Review](/code/code-review/) **panel.** For details on diff views, reverting hunks, opening files, and all available entry points, see the Code Review documentation.
Note
Note that both the [Code Review](/code/code-review/) panel and Interactive Code Review require working in a Git-indexed directory.
### Supported agents
[Section titled “Supported agents”](#supported-agents)
Interactive Code Review works with any supported agent running in Warp:
* **Warp’s native Agent** — the built-in agent in Agent Mode
* **Third-party CLI agents** — Claude Code, OpenAI Codex, OpenCode, Amp, Auggie, Copilot CLI, Cursor CLI, Gemini CLI, Droid, Pi, and Grok Build
For the full feature matrix and setup details for each CLI agent, see [Third-party CLI agents](/agents/cli-agents/overview/).
***
When an agent modifies files, Warp automatically gathers those edits into a diff. Opening the Code Review panel shows you every change the agent made.
From there, you can leave comments on specific lines or blocks, review your comment list, and submit all feedback to the agent at once. The agent applies the requested updates and returns an updated diff for further review.
This gives you a familiar pull-request style workflow inside Warp without switching editors or tools.
### Leave inline comments
[Section titled “Leave inline comments”](#leave-inline-comments)
Select any changed line or block and add a comment describing what you want adjusted. Warp anchors each comment to the relevant file and line so the agent understands exactly what to fix.
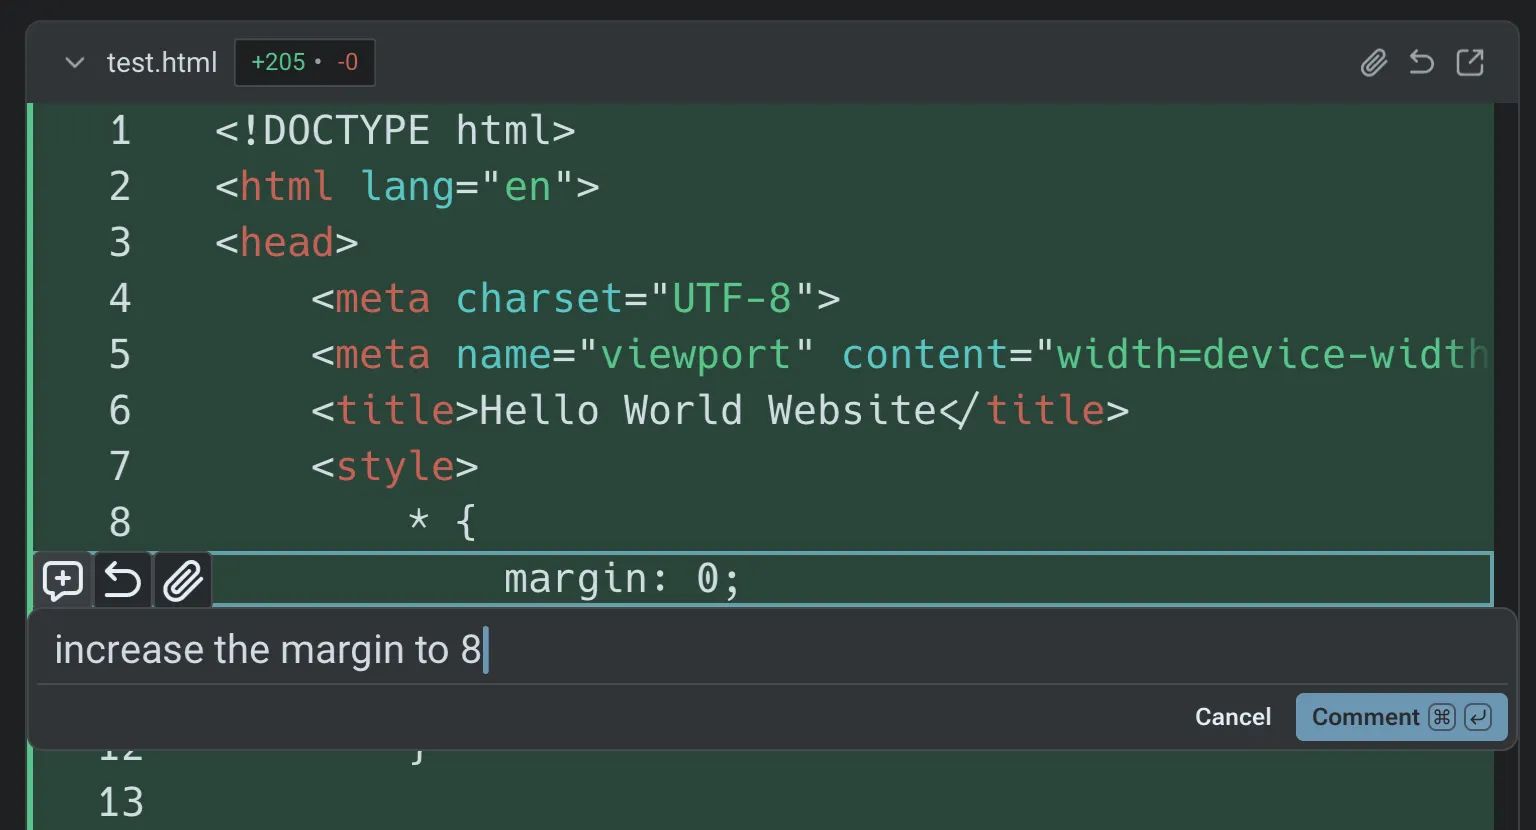
Inline comments in the Code Review panel.
### Batch comments and submit once
[Section titled “Batch comments and submit once”](#batch-comments-and-submit-once)
Add as many comments as you need before submitting them. The agent receives your entire batch of feedback, applies the changes in one iteration, and returns an updated diff for verification.
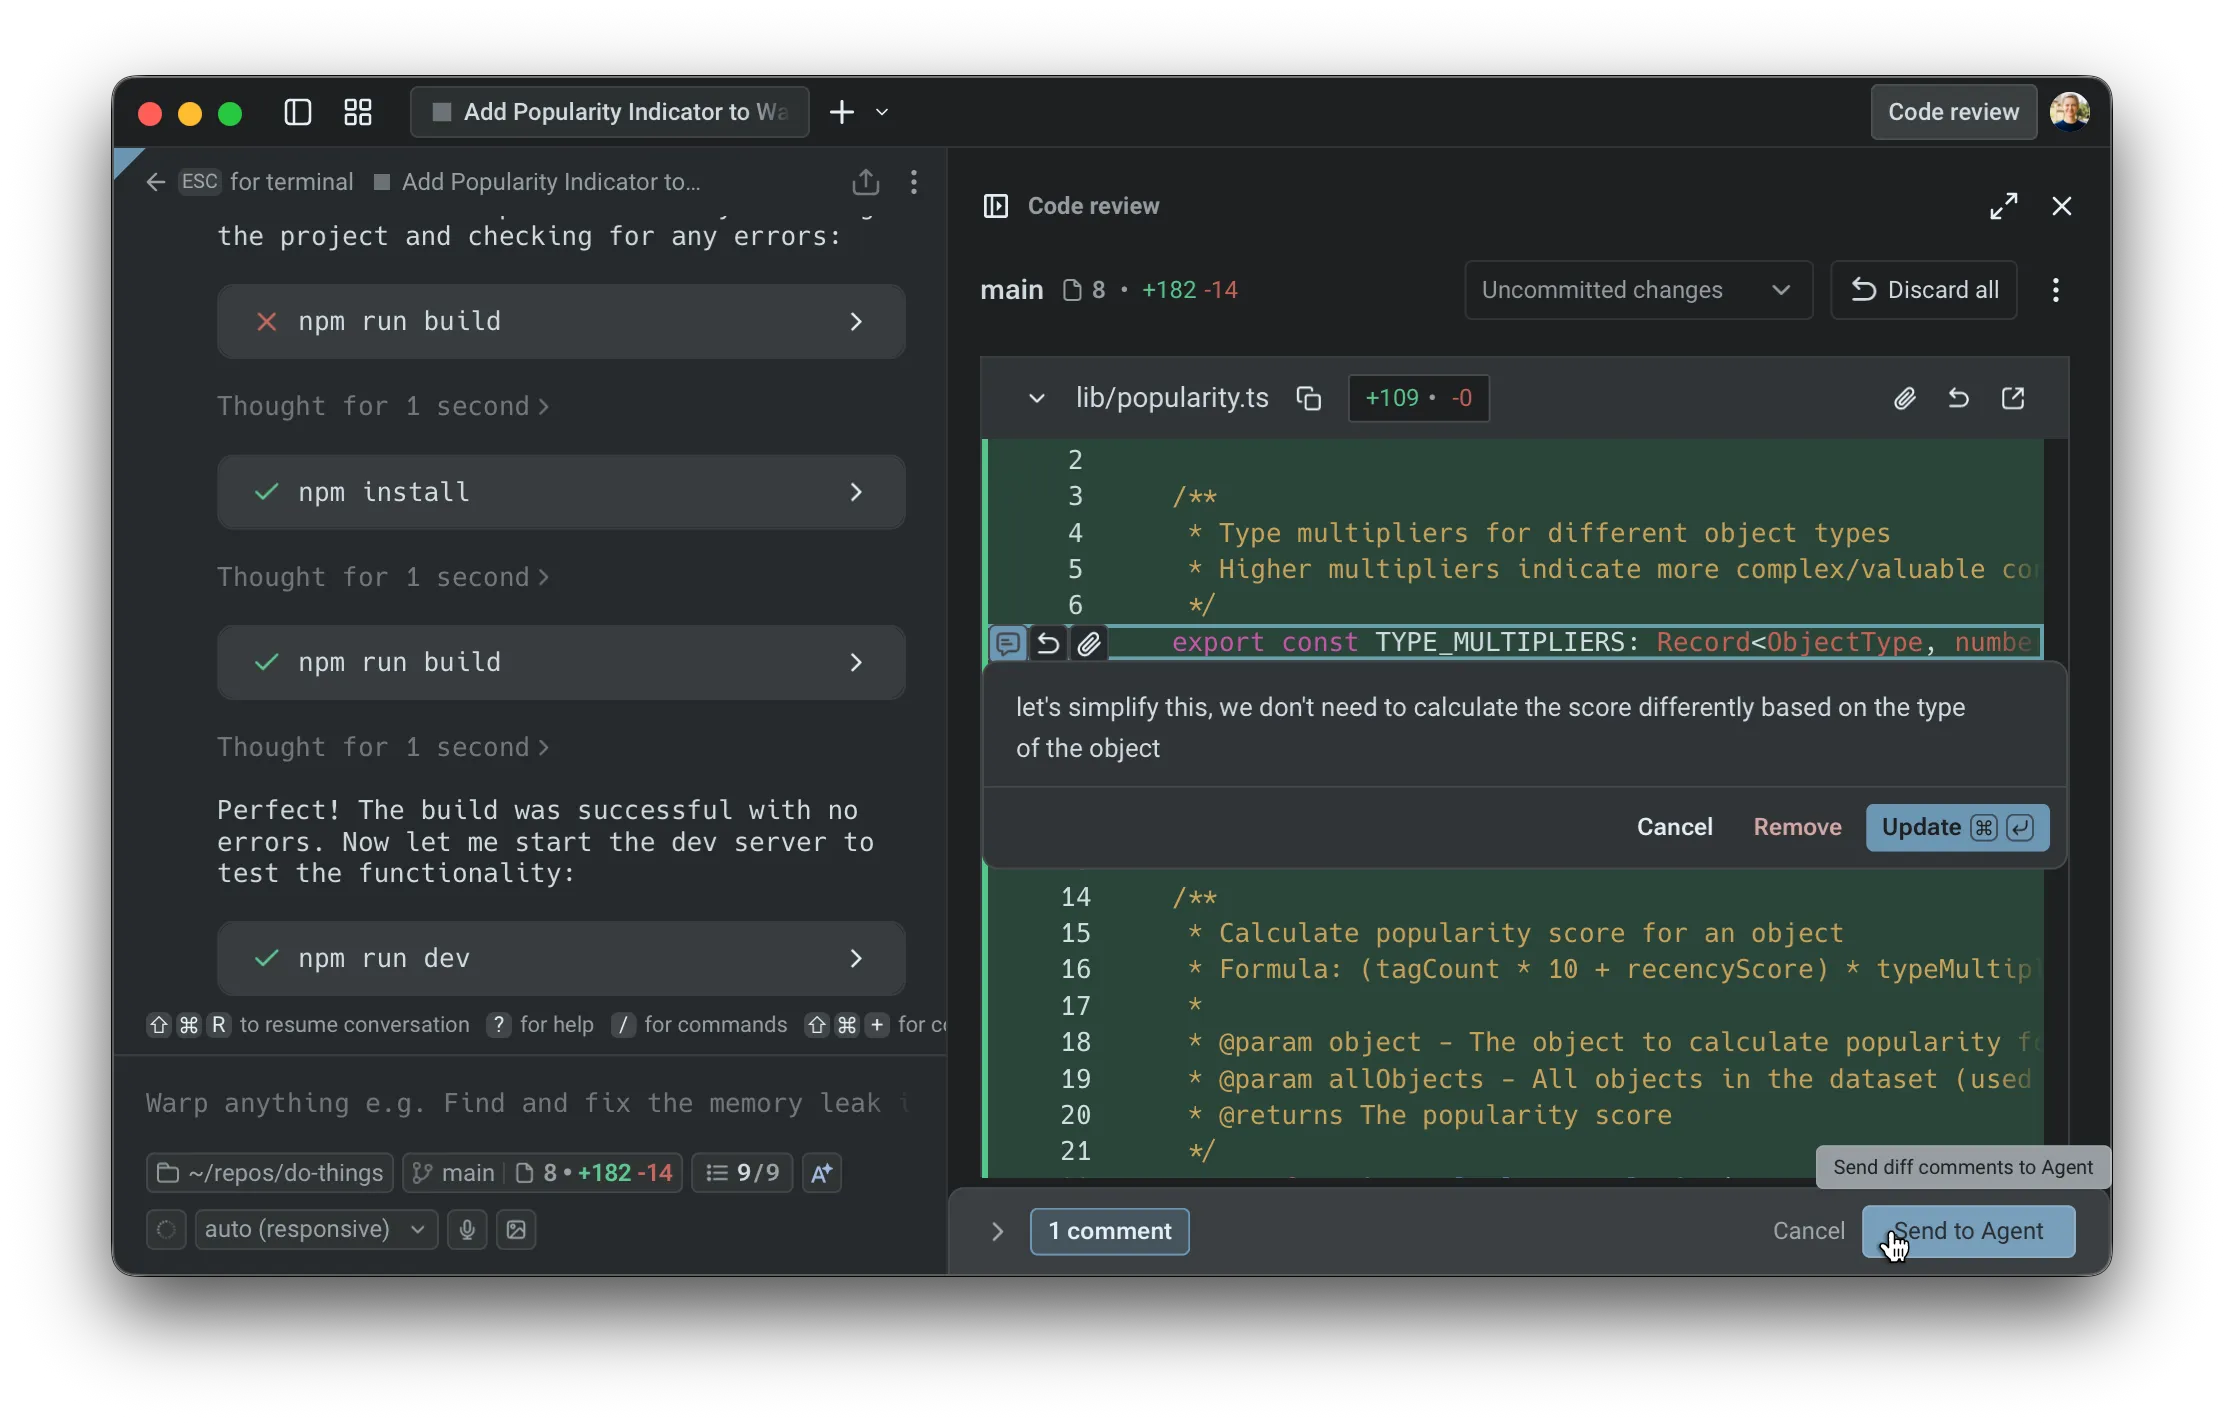
Adding comments directly in the Code Review view.
### Example demo
[Section titled “Example demo”](#example-demo)
In the example from Kevin on the Warp team, you’ll see how to:
* open the Code Review panel after an agent produces changes
* browse the diffs for each edited file
* add multiple inline comments
* review all comments in the list view
* send those comments to the agent for resolution
* inspect the updated diffs once the agent applies the changes
This workflow can be repeated until the code matches your expectations.
[Submitting inline code review feedback to an agent video](https://www.loom.com/embed/bdeb2eb1ff3640faa2cbacda9420c3a8)
***
## Next steps
[Section titled “Next steps”](#next-steps)
Once you’re comfortable reviewing agent code locally, try running agents in the cloud for longer or parallel tasks.
* **[Cloud Agents quickstart](/platform/quickstart/)** - Run agents on Warp’s infrastructure for background tasks like PR review, issue triage, and dependency updates.
* **[Attach agent session context to GitHub PRs](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/)** - Share the agent’s prompt, plan, commands, logs, validation, and reviewer asks with the PR.
* **[Skills](/agents/capabilities/skills/)** - Turn successful agent workflows into reusable, shareable instructions.
# Agent Session Sharing
Canonical page: [/agents/local-agents/session-sharing/](https://docs.warp.dev/agents/local-agents/session-sharing/)
> Share live agent sessions so collaborators can view, steer, and interact with agent activity from any device — in real time or asynchronously.
Agent Session Sharing includes full visibility and control over agent activity. Share any agent session — Automation Platform or third-party — so collaborators can watch progress, review output, and steer the agent from the Warp app, a web browser, or a mobile device.
Use Agent Session Sharing when teammates need the execution context behind an agent’s work, not just the final answer or code diff. A shared agent session can show the prompt, responses, thinking states, tool use, planning steps, terminal output, and follow-up messages in one reviewable link.
[Agent Session Sharing in action — sharing a live session and collaborating across devices.](https://www.loom.com/embed/89e0e99c9bbf463a8a5e5bc2e96dabe4)
## Key capabilities
[Section titled “Key capabilities”](#key-capabilities)
* **Full Agent visibility** - Viewers see Agent prompts, responses, thinking states, tool use, planning steps, and [credit](/support-and-community/plans-and-billing/credits/) consumption in real time
* **Cross-device access** - Open shared sessions from the Warp app, any web browser, or a mobile device. No install required for web viewers.
* **Collaborative editing** - Grant edit access so collaborators can send their own Agent queries, execute commands, and start new conversations
* **Multi-viewer support** - Multiple participants can observe and interact with the same session simultaneously, each with their own cursor and avatar
* **Remote Control** - Publish third-party agent sessions to the cloud for persistent, asynchronous monitoring and steering from anywhere. See [Remote Control](/agents/cli-agents/remote-control/).
## Review agent work with a shared session
[Section titled “Review agent work with a shared session”](#review-agent-work-with-a-shared-session)
When you share an agent session, collaborators can inspect the work at the same level of detail you saw while the agent was running. This is useful when:
* A teammate wants to review how an agent reached a conclusion
* A reviewer needs the agent’s execution context alongside a PR or code diff
* An agent used a third-party CLI tool and you want a persistent record of the terminal session
* A workflow needs asynchronous review from a teammate on another machine or mobile device
Share the link only with collaborators who should be able to see the session contents, including prompts, terminal output, and any context visible in the scrollback.
## How it works
[Section titled “How it works”](#how-it-works)
When you share an agent session, Warp uploads the session’s scrollback and live output to Warp’s servers and generates a shareable link. Session Sharing works through Warp’s servers rather than as a direct, peer-to-peer connection between devices, so the session stays in sync — any new agent output or terminal activity appears for all viewers in real time. The person who shares the session controls who can view and who can interact.
## Data retention and access
[Section titled “Data retention and access”](#data-retention-and-access)
Understanding how long shared data sticks around, how to stop sharing it, and who can see it helps you decide what’s safe to share.
### How long shared data is kept
[Section titled “How long shared data is kept”](#how-long-shared-data-is-kept)
Shared session data expires automatically about one week after you create the share. After that, the link can no longer be opened. This matches the message Warp shows when you try to open an expired link: “Sessions expire after one week and cannot be opened.”
### Stopping a share
[Section titled “Stopping a share”](#stopping-a-share)
Stopping a share immediately ends live access for every participant — no one can continue watching or interacting once you stop it. The share link can no longer be opened after the one-week expiry. There’s currently no separate control to delete a single shared session’s data before that expiry.
Note
Shared [Blocks](/terminal/blocks/block-sharing/) work differently. Unsharing a Block permanently deletes it. Session shares rely on the one-week expiry instead of an immediate-delete action.
To remove all of your shared session data through account deletion rather than waiting for the shared-session expiry, delete your Warp account and data. Deletion jobs run every 24 hours, so removal is not immediate. See [Delete your account and data](/support-and-community/privacy-and-security/privacy/#delete-your-account-and-data).
### Who can access a shared session
[Section titled “Who can access a shared session”](#who-can-access-a-shared-session)
Access to a shared session is based on who you grant it to, not just who has the link:
* **Owner** - You, the person who started the share, control who can view and interact
* **Invited collaborators** - People you explicitly invite to the session
* **Your team** - Optionally, you can extend access to your whole team
* **Anyone with the link** - Available as a setting when you want broader access
Viewers must sign in to a Warp account to open a shared session. Workspace admins can disable invites and link sharing for the team by policy. Roles determine what a participant can do once they have access — some participants can only view the session, while others can also steer it by sending commands or agent queries. See [Collaboration and steering](#collaboration-and-steering) below.
### Secrets in shared sessions
[Section titled “Secrets in shared sessions”](#secrets-in-shared-sessions)
Caution
[Secret Redaction](/support-and-community/privacy-and-security/secret-redaction/) isn’t applied to Session Sharing. Anything visible in a shared session’s scrollback, including values that Secret Redaction would otherwise redact elsewhere, is visible to everyone who can access the share. Treat sharing a session like sharing your screen: review what’s in the scrollback before you share it.
### AI and shared sessions
[Section titled “AI and shared sessions”](#ai-and-shared-sessions)
Sharing a session doesn’t, by itself, send its contents to a model. Shared sessions are excluded from Warp Drive’s AI indexing, so a shared session’s contents aren’t made searchable or citable by agents just because it was shared. An agent only sees a shared session’s terminal content when someone actually uses an AI feature inside that session — either you, or a collaborator you’ve granted edit access to.
## Sharing a session
[Section titled “Sharing a session”](#sharing-a-session)
1. Start or open an agent session in Warp. The agent can be Warp’s built-in agent, a third-party coding agent, or any interactive agent running in your terminal.
2. Open the share action from any of these entry points:
* **Command Palette** - Search for “Share current session”
* **Pane header** - Click the overflow menu in the pane header
* **Right-click context menu** - Right-click inside the session pane
* **`/remote-control` chip** - For third-party agent sessions, click the `/remote-control` chip in the agent view footer or the CLI footer to publish and share instantly. See [Remote Control](/agents/cli-agents/remote-control/) for details.
3. Choose your starting point (full scrollback, no scrollback, or a specific block).
4. Confirm the share. Warp uploads the session to the cloud and generates a shareable link.
5. Copy the link and share it with teammates, or open it on another device.
Start a shared session via the right click menu.
Start a shared session via the Command Palette.
## Viewing shared sessions
[Section titled “Viewing shared sessions”](#viewing-shared-sessions)
Shared sessions are accessible from:
* **Warp app** - Paste the link into Warp on a different machine for the full app experience
* **Web browser** - Open the shared link in any browser. No app install required.
* **Mobile** - Open the link on a phone or tablet browser to check on progress while away from your desk
The web experience mirrors the desktop view, showing complete Agent activity including thinking steps, tool use, and terminal output.
## Collaboration and steering
[Section titled “Collaboration and steering”](#collaboration-and-steering)
### Watching Agent activity
[Section titled “Watching Agent activity”](#watching-agent-activity)
Viewers see Agent actions unfold live as the sharer interacts with the Agent:
* **Thinking animations** - Real-time indicators of Agent reasoning
* **Tool use and planning** - Visible tool calls and planning steps
* **Credit consumption** - Live credit usage for the session
* **Final responses** - Completed Agent output
### Edit access
[Section titled “Edit access”](#edit-access)
If a viewer requests edit access, the sharer can approve it. Once approved, collaborators can:
* Send new Agent queries
* Type directly into the prompt
* Execute commands
* Start and switch Agent conversations
* Run terminal commands alongside Agent queries
### Multi-viewer sessions
[Section titled “Multi-viewer sessions”](#multi-viewer-sessions)
Multiple participants can join the same session from different machines, browsers, or environments. All participants:
* See each other’s avatars and cursors
* Watch Agent activity in sync
* Edit together when granted access
* Run terminal or Agent commands concurrently
## Related pages
[Section titled “Related pages”](#related-pages)
* [Remote Control](/agents/cli-agents/remote-control/)
* [Third-party CLI agents](/agents/cli-agents/overview/)
* [Cloud Agent Session Sharing](/platform/viewing-cloud-agent-runs/)
* [Attach agent session context to GitHub PRs](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/)
* [Secret Redaction](/support-and-community/privacy-and-security/secret-redaction/)
* [Privacy and data control](/support-and-community/privacy-and-security/privacy/)
# Changelog
Canonical page: [/changelog/](https://docs.warp.dev/changelog/)
> Warp ships weekly updates, typically on Thursdays.
Submit bugs and feature requests on our [GitHub board!](https://github.com/warpdotdev/Warp/issues/new/choose)
* [**2026**](/changelog/2026/)
* [**2025**](/changelog/2025/)
* [**2024**](/changelog/2024/)
* [**2023**](/changelog/2023/)
* [**2022**](/changelog/2022/)
* [**2021**](/changelog/2021/)
# Changelog — 2021
Canonical page: [/changelog/2021/](https://docs.warp.dev/changelog/2021/)
> Warp release notes for 2021. Updates ship weekly, typically on Thursdays.
Submit bugs and feature requests on our [GitHub board!](https://github.com/warpdotdev/Warp/issues/new/choose)
### 2021.12.29 (v0.2021.12.27.09.04)
[Section titled “2021.12.29 (v0.2021.12.27.09.04)”](#20211229-v0202112270904)
**New features**
* Find in block (+ other find improvements)
### 2021.12.22 (v0.2021.12.20.09.04)
[Section titled “2021.12.22 (v0.2021.12.20.09.04)”](#20211222-v0202112200904)
**New features**
* Windows, tabs, and panes are restored whenever you reopen Warp. Restoring block content is on its way!
* Warp now supports completions for over 300 commands and more information about existing commands by using Fig’s completion specs
* Git aliases are now included in completions menu - [210](https://github.com/warpdotdev/warp/issues/210)
* Switch to next pane and previous pane with CMD-\[ and CMD-] - [392](https://github.com/warpdotdev/warp/issues/392)
* Scrolling the Block list with PG-UP and PG-DOWN - [370](https://github.com/warpdotdev/warp/issues/370)
* Copy and paste the file directory into Warp from Finder - [514](https://github.com/warpdotdev/warp/issues/514)
* When the last Block is selected, can re-focus the input editor using CMD-DOWN key
* Arrow down scrolls to bottom of last block
**Bug fixes**
* Copying selected text to clipboard creates a new entry for each selected character - [504](https://github.com/warpdotdev/warp/issues/504)
* Needed an extra backspace to escape CTRL-R / history menu - [427](https://github.com/warpdotdev/warp/issues/427)
* VIM performance improvements - we’ve made progress but would love more sample cases of slowness
**Updates to Mac Menu Bar (Window)**
* Zoom
* Minimize
* Tile Window to Left of Screen (Default)
* Tile Window to Right of Screen (Default)
* Move to X screen (Default)
* Enter Full Screen (Default)
* Bring All to Front
### 2021.12.15 (v0.2021.12.13.08.40)
[Section titled “2021.12.15 (v0.2021.12.13.08.40)”](#20211215-v0202112130840)
**New features**
* Fuzzy search in CTRL-R and Command Palette
* When you share a link to a block, up to 5 recipients may now download Warp’s beta via the link
**Bug fixes**
* Fix bug where opening file:// urls would not include query params like ‘?foo=bar’ - [426](https://github.com/warpdotdev/warp/issues/426)
* More prominent highlights in CTRL-R, Command Palette, tab completion
* Vim bug fixes and performance improvements - please let us know what else you see
### 2021.12.08 (v0.2021.12.06.19.09)
[Section titled “2021.12.08 (v0.2021.12.06.19.09)”](#20211208-v0202112061909)
**New features**
* Added a send invite button in account section of the settings dialog
* You can now request more invites in the invite modal
**Bug fixes**
* Copy on select persistence bug
* UI Bug when trying to un-share a block - [439](https://github.com/warpdotdev/warp/issues/439)
### 2021.12.01 (v0.2021.11.29.18.59)
[Section titled “2021.12.01 (v0.2021.11.29.18.59)”](#20211201-v0202111291859)
**New features**
* Added 15 extra invites for everyone!
* Copy on select (highlighting text will automatically copy to clipboard). This can be turned off in the settings dialog - [077](https://github.com/warpdotdev/warp/issues/077)
* CTRL-L shortcut to clear the screen - [049](https://github.com/warpdotdev/warp/issues/049)
**Bug fixes**
* Can now highlight and copy sections of a URL without it automatically opening - [138](https://github.com/warpdotdev/warp/issues/138)
### 2021.11.24 (v0.2021.11.23.17.55)
[Section titled “2021.11.24 (v0.2021.11.23.17.55)”](#20211124-v0202111231755)
**New features**
* Background images + gradients in themes: You can now set a background image or gradient as your theme background. Warp ships with a few of these already or you can create your own via a yaml file. - [032](https://github.com/warpdotdev/warp/issues/032)
* Changelog dialog
* Emoji rendering: 😂, 😃, 🌍, 🍞, 🚗, 📞, 🎉, ❤️ - [075](https://github.com/warpdotdev/warp/issues/075)
* Improved settings dialog
* Theme search - [237](https://github.com/warpdotdev/warp/issues/237)
**Bug fixes**
* Properly escapes whitespace when you drag and drop files
### 2021.11.17 (v0.2021.11.16.20.05)
[Section titled “2021.11.17 (v0.2021.11.16.20.05)”](#20211117-v0202111162005)
**New features**
* Drag and drop files & directories from finder - [069](https://github.com/warpdotdev/warp/issues/069)
### 2021.11.10 (v0.2021.11.09.19.46)
[Section titled “2021.11.10 (v0.2021.11.09.19.46)”](#20211110-v0202111091946)
**New features**
* Autosuggestions: Warp now suggests commands as you type, similar to Fish or Gmail - [052](https://github.com/warpdotdev/warp/issues/052)
* Button to copy the app/version - [106](https://github.com/warpdotdev/warp/issues/106)
* Conda context to the prompt - [235](https://github.com/warpdotdev/warp/issues/235)
**Bug fixes**
* Conda info (prompt) locking input editor
* CTRL-D now deletes forward one character
* History now preserved across sessions - [337](https://github.com/warpdotdev/warp/issues/337)
* Enter (numpad) was inputting as CTRL-C - [330](https://github.com/warpdotdev/warp/issues/330)
### 2021.11.03 (v0.2021.11.02.00.38)
[Section titled “2021.11.03 (v0.2021.11.02.00.38)”](#20211103-v0202111020038)
**New features**
* CJK (Chinese, Japanese, and Korean) character support - [327](https://github.com/warpdotdev/warp/issues/327)
* Autocompletions for missing tar commands
* Enforcement of minimum contrasts in grid - [249](https://github.com/warpdotdev/warp/issues/249)
**Bug fixes**
* Runaway memory usage (from font loading on initial run) - [232](https://github.com/warpdotdev/warp/issues/232)
* Directories with non-english filenames not rendering on screen - [309](https://github.com/warpdotdev/warp/issues/309)
* App crashes from missing current working directory
* Pure Prompt being inserted as a typehead into editor - [242](https://github.com/warpdotdev/warp/issues/242)
### 2021.10.27 (v0.2021.10.25.22.47)
[Section titled “2021.10.27 (v0.2021.10.25.22.47)”](#20211027-v0202110252247)
**New features**
* Ability to unshare blocks in settings modal
* Link to the documentation in kebab menu (three dots in top right corner)
**Bug fixes**
* Double character entry after input editor loses focus
### 2021.10.20 (v0.2021.10.19.21.38)
[Section titled “2021.10.20 (v0.2021.10.19.21.38)”](#20211020-v0202110192138)
**New features**
* Switch theme based on OS appearance - [068](https://github.com/warpdotdev/warp/issues/068)
* Toggles instead of buttons in the settings!
* Link to Custom themes documentation in the settings
**Bug fixes**
* IME support (non-English keyboards are now better supported in input box!)
* Show a banner instead of a popup when app startup takes longer than expected
* git log (and similar commands) no longer treated as a failed block
### 2021.10.13 (v0.2021.10.12.19.34)
[Section titled “2021.10.13 (v0.2021.10.12.19.34)”](#20211013-v0202110121934)
**Bug fixes**
* Shell Bootstrapping should be a lot faster
* Support 3-char color representation for hex colors in theme
* Fix crashes relating to reading history files
* Prevent block completion from stealing focus
* Fix broken click handling for showing and hiding overflow menu
### 2021.10.06 (v0.2021.10.05.20.07)
[Section titled “2021.10.06 (v0.2021.10.05.20.07)”](#20211006-v0202110052007)
**Bug fixes**
* Split pane navigation when ‘Left / Right Option is Meta’ settings are enabled
* Crash when opening a new window
### 2021.09.29 (v0.2021.09.29.13.26)
[Section titled “2021.09.29 (v0.2021.09.29.13.26)”](#20210929-v0202109291326)
**New features**
* Split panes: create multiple panes in the same tab via shortcuts (CMD-E/SHIFT-CMD-E), the Command Palette, or by right clicking in any pane.
* Custom themes via files. You can now define your own theme as a yaml file in \~/.warp/themes. For more information on the file format and to see \~100 of the most popular themes already implemented in this format, see the [Warp themes repository](https://github.com/warpdotdev/themes). The ability to add and share themes directly within Warp is coming soon!
**Bug fixes**
* Add better messaging when Warp does not have permission to autoupdate
* Crash if a tab completion result was accepted after the cursor was moved to the beginning of the editor
### 2021.09.22 (v0.2021.09.21.20.54)
[Section titled “2021.09.22 (v0.2021.09.21.20.54)”](#20210922-v0202109212054)
**New features**
* Theme picker available from the Command Palette
**Bug fixes**
* Occasional crash when opening a new Warp window
* Font selection dropdown didn’t respect theme choice
* Issues with padding and hover detection when toggling Compact Mode on or off
### 2021.09.15 (v0.2021.09.14.21.25)
[Section titled “2021.09.15 (v0.2021.09.14.21.25)”](#20210915-v0202109142125)
**Bug fixes**
* Crash when closing full-screen window
* Executables in path were not appearing for completions in Bash
* Completions menu overlaps theme picker
### 2021.09.09 (v0.2021.09.09.0.0)
[Section titled “2021.09.09 (v0.2021.09.09.0.0)”](#20210909-v02021090900)
**New features**
* New themes for Warp!!! (Access them via Settings on the overflow menu. We have Dracula, Solarized, & Gruvbox)
* CMD-, opens the Settings menu
**Bug fixes**
* Fixed crash when we fail to load a font or when we scroll through fonts
* Fixed visual artifacts around windows and modals jumping
* Fixed crash that occurs when you CMD-F while selecting an already selected text
### 2021.08.31 (v0.2021.08.31.0.0)
[Section titled “2021.08.31 (v0.2021.08.31.0.0)”](#20210831-v02021083100)
**New features**
* Support emacs bindings in input box
* History up menu performs a prefix search based on input
**Bug fixes**
* Warp not rendering after executing long-running command
* Stop powerlevel10k instant prompt from hanging on bootstrap
* Changing “font-size” via CTRL— and CTRL-0 should stay in sync with font size in settings menu
* Bracketed paste mode bug: 0\~ \~1 on every command when ssh-ing
* Crash when tab completing with multibyte characters
* Download page doesn’t render correctly on safari
* Login is broken for some users using Chrome
* Make it more prominent in onboarding that we are collecting telemetry during the beta
### 2021.08.25 (v0.2021.08.25.0.0)
[Section titled “2021.08.25 (v0.2021.08.25.0.0)”](#20210825-v02021082500)
**New features**
* Custom fonts
* Completions for aliases and environment variables
**Bug fixes**
* Completions loose ends, including completions for path names with spaces and if commands are separated by &&
* Function key support within running programs (such as htop)
* Editor text respects zoom level
* Regression that caused URLs to not be highlighted
* Opening a new window required Internet connection
### 2021.08.18 (v0.2021.08.18.0.0)
[Section titled “2021.08.18 (v0.2021.08.18.0.0)”](#20210818-v02021081800)
**New features**
* Re-run with sudo
**Bug fixes**
* Crash caused by pressing CMD-K
* Completion not working when cursor is mid-line
* Re-input of multi-line commands
* [084](https://github.com/warpdotdev/warp/issues/084) - Rendering of colors correctly in diffs
* Selection showing after closing and re-opening alt-screen
### 2021.08.09 (v0.2021.08.09.0.0)
[Section titled “2021.08.09 (v0.2021.08.09.0.0)”](#20210809-v02021080900)
**New features**
* New settings modal (accessible from the top right overflow button) to set font size, toggle between light mode and dark mode, compact mode and normal mode
* CTRL-U and CTRL-K now cut to clipboard
* Typeahead: characters you type in a long-running command will now show up in the input box when the command completes
**Bug fixes**
* Handle arrow keys with modifiers (option and command) in CLIs and full-screen apps (Previously, users were unable to navigate with option and command keys in - Postgres CLI)
* Straightening the text baseline
* Translucent colors (e.g. for diff-so-fancy) are now correct (We now support the full range of opacity)
* Dotfile path completions + Completions improvements for more commands
* Artifacts when rendering svgs, especially on low res monitors. Overflow menu looks a lot better now!
### 2021.07.28 (v0.2021.07.28.0.0)
[Section titled “2021.07.28 (v0.2021.07.28.0.0)”](#20210728-v02021072800)
**New features**
* Compact Mode (see GIF below)
* Support for mouse events in Vim and other programs that can handle mouse input
* Completions for npm / yarn scripts
**Bug fixes**
* Major improvements to the consistency of completions, especially for commands that can take multiple arguments (e.g. rm -rf)
* Proper path completions for absolute paths
* Hang when PROMPT\_COMMAND is set for the shell
* Context Menu not closing when clicking outside of the menu
* Crashes after executing multi-line commands and on older versions of macOS
### 2021.07.21 (v0.2021.07.21.0.0)
[Section titled “2021.07.21 (v0.2021.07.21.0.0)”](#20210721-v02021072100)
**New features**
* Support for numpad ENTER
* More npm & yarn completions
**Bug fixes**
* Down arrow sends unrecognized escape sequence to GitHub CLI
* Can’t use UP arrow if item in history is multiple lines
* Crash when closing a tab when there are multiple tabs
* File-only completion signatures should also show directories
### 2021.07.13 (v0.2021.07.13.0.0)
[Section titled “2021.07.13 (v0.2021.07.13.0.0)”](#20210713-v02021071300)
**New features**
* New invite system to add users to Warp. To invite new users, click the overflow menu at the top right and click ‘invite users’. For now we ask that you please don’t post these invites on social media!
* URLs in the terminal screen are auto-linkified
* Double clicking the title bar maximizes/minimizes the window
**Bug fixes**
* Various Command Palette bugs
* Find box is populated with the user’s text selection
* 3 second latency when changing the prompt upon first SSHing
### 2021.07.07 (v0.2021.07.07.0.0)
[Section titled “2021.07.07 (v0.2021.07.07.0.0)”](#20210707-v02021070700)
**New features**
* Command Palette for most keyboard shortcuts (CMD-P)
* Previously, tab completion descriptions were cut off. Now we display them in a floating box
* You can now switch tabs using CTRL-TAB and CTRL-SHIFT-TAB
**Bug fixes**
* Intermittent crashes with Zsh sessions and switching tabs
* Always fall back to path suggestions for completions
* Various bugs related to completions
### 2021.06.29 (v0.2021.06.29.0.0)
[Section titled “2021.06.29 (v0.2021.06.29.0.0)”](#20210629-v02021062900)
**New features**
* Multiple window support
* New completions UI and in-line documentation for commands and flags
* Horizontal scrolling of input box to support long commands
**Bug fixes**
* Crash when exiting from logout or exit when there’s a background process
* Crash when bootstrapping from detecting incorrect shell name
* Various bugs related to completions
### 2021.06.15 (v0.2021.06.15.19.04)
[Section titled “2021.06.15 (v0.2021.06.15.19.04)”](#20210615-v0202106151904)
**New features**
* Mac File and Edit menus, along with Mac standard menu items (although New Window not yet working)
**Bug fixes**
* Crash when closing last window
* CMD-F: when there are no matches, display 0/0
* CMD-F should not scroll away if navigating to a match on the same row
* CMD-F: render the yellow rectangle at the layer of rendering the cell
* Unable to move cursor upwards on multi-line previous command
* Warp bootstrap commands showing up in history over ssh
* Accept input via input box before terminal has bootstrapped
* New tab button should have hover and click state
* Output stops midway through session on iMac running Mojave 10.14.6
* Backspace doesn’t work while holding shift
* Clipping issue in share dialog
* Input suggestions closes if you click on the scrollbar
* Hitting up/down while input suggestions are open causes menu to move
* Paste is not working for full screen apps
* Underline does not render with Hack font
### 2021.06.09 (v0.2021.06.09.15.14)
[Section titled “2021.06.09 (v0.2021.06.09.15.14)”](#20210609-v0202106091514)
**New features**
* SSH support (Warp now works the same when you SSH as it does locally!)
* Improved completions: we’ve built out new completions support that are snappier and have more intelligent suggestions for options and arguments for some of the most used commands
* Find: Pressing CMD-F now brings up a find view to search for text in the terminal
**Bug fixes**
* Text rendering was faded on certain monitors
# Changelog — 2022
Canonical page: [/changelog/2022/](https://docs.warp.dev/changelog/2022/)
> Warp release notes for 2022. Updates ship weekly, typically on Thursdays.
Submit bugs and feature requests on our [GitHub board!](https://github.com/warpdotdev/Warp/issues/new/choose)
### 2022.12.15 (v0.2022.12.13.08.04)
[Section titled “2022.12.15 (v0.2022.12.13.08.04)”](#20221215-v0202212130804)
**New features**
* You can now reorder and drag tabs around with your mouse!
**Bug fixes**
* The welcome Block now also works when using Fish shell.
* AI Command Search no longer crashes from multi-byte characters when opened via the `#` prefix
* Warp no longer crashes when starting a new session in a deleted or inaccessible directory
* Resolved rendering bugs and hangs in full-screen applications like ‘k9s’ and ‘less’.
* Added a login failure notification.
### 2022.12.06 (v0.2022.12.06.08.03)
[Section titled “2022.12.06 (v0.2022.12.06.08.03)”](#20221206-v0202212060803)
**New features**
* Users may now opt out of telemetry (app analytics and crash reporting)
* Added ‘Tail Warp network log’ workflow for viewing logs of all app network activity.
**Bug fixes**
* Full-screen CLI commands like mitmproxy now correctly span the entire view.
* Improved styling and organization of Features page in settings.
* Completions While Typing menu closes while generating new results.
* Added a hidden completion result for root dir.
* Warp now consumes less memory when a session has many blocks.
* Fixed an issue over SSH where logs were being inserted into input.
### 2022.12.02 (v0.2022.11.29.08.03)
[Section titled “2022.12.02 (v0.2022.11.29.08.03)”](#20221202-v0202211290803)
**New features**
* Users may now opt out of telemetry (app analytics and crash reporting)
* Added ‘Tail Warp network log’ workflow for viewing logs of all app network activity.
**Bug fixes**
* Mitigated an issue where running a command over SSH would emit spurious output (specifically, ‘channel: open failed’ statements) in a block.
### 2022.12.01 (v0.2022.11.29.08.03)
[Section titled “2022.12.01 (v0.2022.11.29.08.03)”](#20221201-v0202211290803)
**New features**
* Warp now supports using the find bar within the alt-screen! `CMD-F` now opens find within vim, less, and other alt-screen apps!
**Bug fixes**
* Respect symlinks in Warp configuration directories (for themes and workflows).
* Fixed unwanted text appearing in the Input Editor when RPROMPT is set
* Fixed the emoji composer not working properly.
* Fixed a crash that could occur when using the Unicode Hex Input keyboard.
* Fixed escape binding not closing the resource center
* Move Backward/Forward One Word bindings can now be overridden.
* Fixed crash when hovering over multiple byte text within the Input Editor
* Fixed “command not found: sed” and “command not found: tr” issues with the SSH wrapper.
* Fixed issue where tab completions and command search could be visible at the same time.
### 2022.11.15 (v0.2022.11.14.14.55)
[Section titled “2022.11.15 (v0.2022.11.14.14.55)”](#20221115-v0202211141455)
**New features**
* Command Search: Ctrl-R opens a panel where you can search your history, workflows, and other command execution-related items, all in one place.
* Sticky command header: Warp now pins the prompt/command section of a Block to the top of the screen; click it to scroll to the top of the Block. Can be toggled via Settings > Features > Show Sticky Command Header
* Warp’s Input Editor now supports soft wrapping; long commands are now fully visible!
**Bug fixes**
* Warp now sets the TERM\_PROGRAM environment variable correctly in wrapped SSH sessions.
### 2022.11.10 (v0.2022.11.08.08.07)
[Section titled “2022.11.10 (v0.2022.11.08.08.07)”](#20221110-v0202211080807)
**New features**
* Warp now offers Command Corrections! Warp will suggest corrections for errors in previous console commands
* Warp now also detects invalid file paths — they are underlined red when error underlining is enabled
* Added a toggle in `Settings > Appearance` to configure whether and how Warp enforces minimum contrast
**Bug fixes**
* Fixed an issue where toggling the default prompt would not update it immediately
* Improved positioning of the `TAB` completions menu when using split panes
### 2022.11.03 (v0.2022.11.01.08.03)
[Section titled “2022.11.03 (v0.2022.11.01.08.03)”](#20221103-v0202211010803)
**New features**
* Warp’s prompt now shows the number of modified files on your local git branch! Search “changed file count” in the Command Palette or right-click the Prompt to toggle.
**Bug fixes**
* Dim-styled colors are now restored properly.
### 2022.10.27 (v0.2022.10.25.08.06)
[Section titled “2022.10.27 (v0.2022.10.25.08.06)”](#20221027-v0202210250806)
**Bug fixes**
* Fixed a bug when hovering over hover icons
### 2022.10.20 (v0.2022.10.18.08.10)
[Section titled “2022.10.20 (v0.2022.10.18.08.10)”](#20221020-v0202210180810)
**Bug fixes**
* Modifying the mouse and scroll reporting settings now applies immediately
* Fixed cursor not blinking when starting a shell instance
* Fixed temporarily flashing the wrong prompt while Warp is still bootstrapping
* Removed duplicate entry for toggling error underlining and syntax highlighting within the Command Palette
### 2022.10.13 (v0.2022.10.11.08.13)
[Section titled “2022.10.13 (v0.2022.10.11.08.13)”](#20221013-v0202210110813)
**New features**
* Warp’s Input Editor now has Syntax Highlighting and Error Underlining, with no configuration!
* Warp now uses a pointer cursor when hovering over links
**Bug fixes**
* Git branches in the completions menu now bold correctly
* Warp no longer crashes when `/bin/bash` is missing
### 2022.10.06 (v0.2022.10.04.08.05)
[Section titled “2022.10.06 (v0.2022.10.04.08.05)”](#20221006-v0202210040805)
**New features**
* Drag and drop a folder or file onto the Warp dock icon to open a new tab in this directory
* Added dividers between Blocks in compact mode
* Shell keywords are now supported for completions and Command Inspector
**Bug fixes**
* Accessibility support for context menu keybinding
* Keystrokes typed while a command is still executing no longer gets dropped
* Link recognition no longer includes trailing quotes
* Find search results will continue to be highlighted after clearing the screen during a long running command
* Fixed completions for commands prefixed with environment variables
* Warp’s resource center is now center aligned
### 2022.09.29 (v0.2022.09.27.08.11)
[Section titled “2022.09.29 (v0.2022.09.27.08.11)”](#20220929-v0202209270811)
**New features**
* Extend the currently selected text (within Blocks) with `SHIFT-LEFT`, `SHIFT-RIGHT`, `SHIFT-UP`, and `SHIFT-DOWN`
* Double-click and drag to select text in the Input Editor
* Insert the last word of the previous command with `META-.`
* Added a toggle to enable mouse and scroll reporting to the settings dialog (`Settings > Features`)
**Bug fixes**
* The `clear` command no longer appears in the snackbar at the top of the window
* Warp’s completions now support executables in remote sessions (no longer just bash)
* Fixed subcommand completions for commands with proper prefixes of each other (e.g. `npm r` and `npm run`)
* The completion spec for `lsd` now supports files
### 2022.09.22 (v0.2022.09.20.08.08)
[Section titled “2022.09.22 (v0.2022.09.20.08.08)”](#20220922-v0202209200808)
**New features**
* After selecting a Block press `CTRL-M` to open its context menu
* Commands in the tab completions menu and history menu can now be executed directly with `CMD-ENTER`
* Completions now support shell builtins, git aliases, and also npm aliases
**Bug fixes**
* Command Palette now includes the most useful features at the top
* Improved flag completions for cargo
### 2022.09.15 (v0.2022.09.13.08.15)
[Section titled “2022.09.15 (v0.2022.09.13.08.15)”](#20220915-v0202209130815)
**New features**
* Warp Resource Center - explore Warp features and documentation by clicking the `?` icon or pressing `SHIFT-CTRL-?`
* New icons in the completion menu denoting flags, folders, branches, etc.
**Bug fixes**
* Press `CMD-ENTER` within the history menu (`CTRL-R`) to directly execute the highlighted command
* Fixed crash when opening many tabs (due to macOS’s default open file descriptor limits)
* Fixed crash when laying out RTL text
### 2022.09.08 (v0.2022.09.07.14.56)
[Section titled “2022.09.08 (v0.2022.09.07.14.56)”](#20220908-v0202209071456)
**New features**
* Global hotkey window can now float above full-screen apps
* Tabs can now have their color customized (via right-clicking on a tab)
* Terminal line height is now configurable (via Settings > Appearance)
### 2022.09.01 (v0.2022.08.31.18.11)
[Section titled “2022.09.01 (v0.2022.08.31.18.11)”](#20220901-v0202208311811)
**New features**
* Tab completions now support fuzzy string matching
* Improve completions for over 450 commands, including docker, kubernetes, cargo, node, and git
**Bug fixes**
* Properly send C0 control codes for \<ctrl-\[2-8]> keystrokes
* Session restoration now also persists bold, underline, italic, and strikethrough formatting
* Inspect mode now works for the changelog modal
* Fixed a crash when highlighting a link
* Fixed Find occasionally returning only partial results
* Fixed occasional crash when loading images
* Fixed display issue in the Mac Menu for keyboard shortcuts with special keys
### 2022.08.25 (v0.2022.08.23.08.06)
[Section titled “2022.08.25 (v0.2022.08.23.08.06)”](#20220825-v0202208230806)
**New features**
* Experimental feature: support for always-on completions — the completions menu can now open automatically while typing (enable via Settings -> Features)
**Bug fixes**
* Custom tab titles no longer get overwritten when using multiple panes
* A Block’s execution duration is now formatted in hours, minutes, and seconds
* Improved rendering of the ‘Current session’ text in the Navigation Palette
* Warp properly hides the cursor when a CLI sends the respective escape sequence
* Warp stays focused (keyboard-interactive) after closing the Share Block menu and the context menu
* Warp no longer lags when the Ctrl-R menu is opened
* Confirming a tab suggestion appends a space to the buffer
### 2022.08.18 (v0.2022.08.16.10.16)
[Section titled “2022.08.18 (v0.2022.08.16.10.16)”](#20220818-v0202208161016)
**New features**
* Launch Configurations - Save a configuration of windows, tabs, and panes to open later with `CTRL-CMD-L`
* Session Navigation - Navigate to any session in Warp with `SHIFT-CMD-P`
* Added exclusive theme for users who joined Warp through a referral
**Bug fixes**
* Prompt now shows Git SHA instead of HEAD when you’re not on a branch
* Filepath completions now include current directory (’.’) and parent directory (’..’)
* Support `SHIFT-HOME` and `SHIFT-END` keybindings to select text to line start and end.
* Items in the Command Palette now highlight when you hover over them with your mouse
* Improved how Warp cleans up the warptmp directory for Zsh SSH sessions
* Already open dropdown menus are now properly closed when clicked
* Warp no longer crashes when dragging a window that’s running htop
* Warp no longer crashes when the find bar is open
### 2022.08.10 (v0.2022.08.08.09.21)
[Section titled “2022.08.10 (v0.2022.08.08.09.21)”](#20220810-v0202208080921)
**New features**
* Can now Middle-click a tab to close it
* Added additional tab reordering options (Close: tab, other tabs, and tabs to the right) via the Mac Menu, the Command Palette, and a tab’s context menu (right click)
**Bug fixes**
* Added a toggle to the Mac Menu for maximizing panes
* Can now switch panes using keyboard shortcuts even when a pane is maximized
* Add support for opening file paths with RubyMine, PhpStorm, and WebStorm
* Fixed crash when highlighting links
* Fixed issue where the HISTCONTROL environment variable was ignored in bash
* Pressing `CTRL-R` to open history search no longer crashes Warp when you have multiple cursors
### 2022.08.03 (v0.2022.08.01.09.12)
[Section titled “2022.08.03 (v0.2022.08.01.09.12)”](#20220803-v0202208010912)
**New features**
* Updated Mac menus to make Warp actions more discoverable - [101](https://github.com/warpdotdev/warp/issues/101)
* Warp now supports opening file links and urls via CMD-CLICK! - [177](https://github.com/warpdotdev/warp/issues/177)
**Bug fixes**
* Various CLI tools no longer hang e.g. Bazel and Maven
* Command Inspector hover no longer crashes with UTF-8 encoded strings
* Opening the find / search bar (`CMD-F`) now automatically selects the text
* Tab titles are no longer reset when changing panes
### 2022.07.27 (v0.2022.07.25.09.05)
[Section titled “2022.07.27 (v0.2022.07.25.09.05)”](#20220727-v0202207250905)
**Bug fixes**
* Closing and re-opening the Command Palette now resets the selected item
* The cursor’s position is now restored after exiting the Command History Search (`CTRL-R`) menu.
* Shorthand and longhand flags are now correctly surfaced (based on the number of dashes) in tab completions
* Added voiceover support for `BACKSPACE` and `DELETE` keystrokes within the Input Editor
### 2022.07.20 (v0.2022.07.18.09.06)
[Section titled “2022.07.20 (v0.2022.07.18.09.06)”](#20220720-v0202207180906)
**New features**
* Command Inspector - hover over any piece of a command in Warp’s Input Editor to surface documentation or press `CMD+I` to inspect at the cursor’s current location
* Improved ordering in the tab completions menu
**Bug fixes**
* Font color for links in light mode (themes) now set correctly
* Moving forward by a word no longer moves farther than expected
* Warp no longer hangs when passing an invalid file path
* Fixed issues with persisting the selected theme when “Sync with OS” is enabled and the theme picker is launched from the Command Palette (or a keyboard shortcut)
* Fixed issues with text input after clearing Blocks (`CMD-K`) while in a REPL environment.
* Fixed shortcut for select-left-by-word (`SHIFT-CMD-B`), select-right-by-word (`SHIFT-CMD-F`), select-line-to-end (`SHIFT-CTRL-E`), and select-line-to-start (`SHIFT-CTRL-A`)
### 2022.07.13 (v0.2022.07.11.09.11)
[Section titled “2022.07.13 (v0.2022.07.11.09.11)”](#20220713-v0202207110911)
**Bug fixes**
* Improved startup time for Fish shells
* Find Bar no longer crashes on selected text
* Scrollbar now supports jumping to where you click
* Fixed a bug with the referral link for sharing Warp not loading
### 2022.07.07 (v0.2022.07.04.09.08)
[Section titled “2022.07.07 (v0.2022.07.04.09.08)”](#20220707-v0202207040908)
**New features**
* Bookmark a Block (or multiple) for quick access via the scroll-bar
* Added a referral counter to the Settings > Account screen and the referral screen
* Added support for rendering text with a lower visual weight; enable the thin strokes option in Settings > Appearance (enabled by default for low-DPI displays)
* Toggleable settings, overflow menu items, and settings pages are now accessible through the Command Palette
* CLI options are now surfaced by default without needing to type ’-’
* Press SHIFT-CMD-C while in VSCode (Visual Studio Code) to open a new Warp session
**Bug fixes**
* Fixed referral links and share by email
* Fixed a hang that would sometimes occur when connecting with SSH
* Now support requesting media permissions (camera, audio, etc)
* Correctly parse Git commit SHAs in completion menus
* Improved tab completion support for command line arguments that are behind flags
### 2022.07.06 (v0.2022.07.04.09.08)
[Section titled “2022.07.06 (v0.2022.07.04.09.08)”](#20220706-v0202207040908)
**New features**
* Bookmark a Block (or multiple) for quick access via the scroll-bar
* Added a referral counter to the Settings > Account screen and the referral screen
* Added support for rendering text with a lower visual weight; enable the thin strokes option in Settings > Appearance (enabled by default for low-DPI displays)
* Toggleable settings, overflow menu items, and settings pages are now accessible through the Command Palette
* CLI options are now surfaced by default without needing to type ’-’
* Press SHIFT-CMD-C while in VSCode (Visual Studio Code) to open a new Warp session
**Bug fixes**
* Fixed a hang that would sometimes occur when connecting with SSH
* Now support requesting media permissions (camera, audio, etc)
* Correctly parse Git commit SHAs in completion menus
* Improved tab completion support for command line arguments that are behind flags
### 2022.06.29 (v0.2022.06.27.09.14)
[Section titled “2022.06.29 (v0.2022.06.27.09.14)”](#20220629-v0202206270914)
**Bug fixes**
* Cursor changes when hovering over clickable UI elements and the Input Editor
* Dim colors now render correctly
### 2022.06.27 (v0.2022.06.20.09.15)
[Section titled “2022.06.27 (v0.2022.06.20.09.15)”](#20220627-v0202206200915)
**New features**
* Improved auto-focus behavior when closing panes by keeping track of history when navigating or clicking around panes
* Performance improvements when executing Blocks: Warp no longer flashes on every command!
**Bug fixes**
* Input Editor re-focuses after renaming a tab
* Reduced visual weight of the active tab title to improve legibility.
* Improved blending along the inside edge of rounded corners
* Global Hotkey Windows (Quake Mode) now correctly respect the active screen setting
* Completions for flag arguments now support absolute and relative file paths (when applicable)
* Git checkout <`TAB`> now also completes branches with the remote prefixed.
* Pressing Arrow-up (`UP`) when the Input Editor is non-empty opens the command history with prefix filtering
* Button to copy app version moved to main settings page
### 2022.06.22 (v0.2022.06.20.09.15)
[Section titled “2022.06.22 (v0.2022.06.20.09.15)”](#20220622-v0202206200915)
**New features**
* Improved auto-focus behavior when closing panes by keeping track of history when navigating or clicking around panes
* Performance improvements when executing Blocks: Warp no longer flashes on every command!
**Bug fixes**
* Input Editor re-focuses after renaming a tab
* Reduced visual weight of the active tab title to improve legibility.
* Improved blending along the inside edge of rounded corners
* Global Hotkey Windows (Quake Mode) now correctly respect the active screen setting
* Completions for flag arguments now support absolute and relative file paths (when applicable)
* Git checkout <`TAB`> now also completes branches with the remote prefixed.
* Pressing Arrow-up (`UP`) when the Input Editor is non-empty opens the command history with prefix filtering
* Button to copy app version moved to main settings page
### 2022.06.17 (v0.2022.06.13.09.15)
[Section titled “2022.06.17 (v0.2022.06.13.09.15)”](#20220617-v0202206130915)
**New features**
* Added keyboard shortcuts to reorder tabs (CTRL-SHIFT-LEFT and CTRL-SHIFT-RIGHT)
**Bug fixes**
* Warp no longer crashes on macOS 13 (Ventura)
* Global Hotkey Window (Quake Mode) no longer overlaps Spotlight, Raycast, Alfred, and the macOS Dock
* Now correctly display the user and hostname in the Prompt after exiting an SSH session
* Fixed a memory leak on window close.
### 2022.06.15 (v0.2022.06.13.09.15)
[Section titled “2022.06.15 (v0.2022.06.13.09.15)”](#20220615-v0202206130915)
**New features**
* Added keyboard shortcuts to reorder tabs (CTRL-SHIFT-LEFT and CTRL-SHIFT-RIGHT)
**Bug fixes**
* Global Hotkey Window (Quake Mode) no longer overlaps Spotlight, Raycast, Alfred, and the Mac Dock
* Now correctly display the user and hostname in the Prompt after exiting an SSH session
* Fixed a memory leak on window close.
### 2022.06.08 (v0.2022.06.06.09.05)
[Section titled “2022.06.08 (v0.2022.06.06.09.05)”](#20220608-v0202206060905)
**New features**
* Now support renaming tabs (right click on your tab title!)
* Now support enabling custom prompt from prompt context menu (right-click on prompt)
* Now support splitting panes (left and right) from the context menu (right click) and through the Command Palette
* Now support CTRL-Click as an alternative to right-clicking
**Bug fixes**
* Improved completions support for arguments nested under options (e.g. git branch -D \<branch\_name…>)
* Modified files are now included (in addition to commit SHAs) for `git diff`
### 2022.06.01 (v0.2022.05.30.09.10)
[Section titled “2022.06.01 (v0.2022.05.30.09.10)”](#20220601-v0202205300910)
**New features**
* Added information about rewards to the referral screen
* Added a button that toggles regex search in the Find Bar
* Added completion support for shell functions
**Bug fixes**
* Hotfix - a regression that caused Warp to stall when using nano
* Improved kerning (font rendering) throughout the app
* Added a hyperlink (to our changelog history) in the Changelog modal
* Multiline commands that don’t have any output are no longer cut off
### 2022.05.26 (v0.2022.05.23.09.07)
[Section titled “2022.05.26 (v0.2022.05.23.09.07)”](#20220526-v0202205230907)
**New features**
* Warp can now send you desktop notifications for long-running commands and password prompts - [628](https://github.com/warpdotdev/warp/issues/628)
* Added keybinding to toggle fullscreen mode
**Bug fixes**
* Stopped prepending \ before \~ in tab titles for older versions of Bash
* Added support for CMD-G and SHIFT-CMD-G to tab between results in the Find Bar
### 2022.05.18 (v0.2022.05.16.09.01)
[Section titled “2022.05.18 (v0.2022.05.16.09.01)”](#20220518-v0202205160901)
**New features**
* Added exclusive theme available to anyone who has referred someone to Warp. (Open Theme Picker > Warp Referral to use it)
**Bug fixes**
* Improved rendering of rounded corners throughout the app
* Fixed cell dimension computation for some fonts
* Fixed labels rendering incorrectly in the font selector dropdown in settings
* Fixed Bash remote sessions missing tab titles
* Reduced UI flickering after executing commands
* Fixed errors when sshing into remote machines which do not have xxd available
* Fixed some anti-aliased glyphs getting clipped during rasterization
* Fixed search bar stealing focus after command execution
### 2022.05.11 (v0.2022.05.09.09.06)
[Section titled “2022.05.11 (v0.2022.05.09.09.06)”](#20220511-v0202205090906)
**New features**
* Filepath completions without needing to cd
* Support for any font (not just monospaced)
**Bug fixes**
* Tab completions (cd) with international characters are now properly escaped (edited)
* Improve rendering performance when many tabs are open (fixes non-responsiveness when searching history)
* Fixed a race condition with autoupdate a11y announcements and other a11y messaging
* Fixed a regression that would cut off the output of some long-running Blocks
### 2022.05.04 (v0.2022.05.02.09.00)
[Section titled “2022.05.04 (v0.2022.05.02.09.00)”](#20220504-v0202205020900)
**New features**
* Added default tab titles for Bash
* Improved default tab title in Zsh
* Maximize a split pane
* Support rcfiles that check PS1 to determine if it’s an interactive shell; this may explain missing aliases or commands in Warp!
**Bug fixes**
* History now correctly shows results after hitting ESC when a Block is focused
* Fixed crash when quitting AI Command Search while a command was being generated
* Global keybindings with function keys and numeric keys are now properly registered
* Warp no longer jumps up and down for single-line commands that take more than 50ms
### 2022.05.02 (v0.2022.04.25.09.59)
[Section titled “2022.05.02 (v0.2022.04.25.09.59)”](#20220502-v0202204250959)
**New features**
* Added a Quake Mode setting that configures whether Warp should automatically hide when losing focus - [1077](https://github.com/warpdotdev/warp/issues/1077)
* Added a Quake Mode setting that configures which screen to pin Warp on - [862](https://github.com/warpdotdev/warp/issues/862)
* Expanded the keybindings supported by Quake Mode / Global Hotkey Window - [856](https://github.com/warpdotdev/warp/issues/856)
**Bug fixes**
* Commands prepended with space are now stored in history if hist\_ignore\_space option is not set
* Now support dotfile configurations with non-English quotation marks
* Continued improving the reliability of login and auth within the app
* Improved performance for commands with large outputs
* Improved performance for long running commands
* Improved text alignment within inline banners
### 2022.04.27 (v0.2022.04.25.09.59)
[Section titled “2022.04.27 (v0.2022.04.25.09.59)”](#20220427-v0202204250959)
**New features**
* Added a Quake Mode setting that configures whether Warp should automatically hide when losing focus - [1077](https://github.com/warpdotdev/warp/issues/1077)
* Added a Quake Mode setting that configures which screen to pin Warp on - [862](https://github.com/warpdotdev/warp/issues/862)
* Expanded the keybindings supported by Quake Mode / Global Hotkey Window - [856](https://github.com/warpdotdev/warp/issues/856)
**Bug fixes**
* Commands prepended with space are now stored in history if hist\_ignore\_space option is not set
* Now support dotfile configurations with non-English quotation marks
* Continued improving the reliability of login and auth within the app
* Improved performance for commands with large outputs
* Improved performance for long running commands
* Improved line height computation for some fonts
* Improved text alignment within inline banners
### 2022.04.20 (v0.2022.04.18.09.08)
[Section titled “2022.04.20 (v0.2022.04.18.09.08)”](#20220420-v0202204180908)
**New features**
* Support logging into Warp by pasting the auth url when “Take me to Warp” fails in browser
**Bug fixes**
* Improved reliability of login and auth within the app
* Buttons within the find bar are now properly shaded for gradient themes
* Workflows with default values are now registered by Warp
* Fixed bootstrapping bug that affected Fish versions older than 3.2.0
* Fixed a memory leak that occurred when new tabs were opened or panes were split
### 2022.04.15 (v0.2022.04.11.09.09)
[Section titled “2022.04.15 (v0.2022.04.11.09.09)”](#20220415-v0202204110909)
**Bug fixes**
* Support parsing PS1’s exit codes (Bash’s $?) and improved PS1 parsing for newer Bash versions (4.4+)
* Fixed prompt showing up as exit in Bash - [793](https://github.com/warpdotdev/warp/issues/793)
* Improved parsing of Zsh default prompts
* Opening the find bar will automatically select any existing text - [831](https://github.com/warpdotdev/warp/issues/831)
### 2022.04.13 (v0.2022.04.11.09.09)
[Section titled “2022.04.13 (v0.2022.04.11.09.09)”](#20220413-v0202204110909)
**Bug fixes**
* Support parsing PS1’s exit codes (Bash’s $?) and improved PS1 parsing for newer Bash versions (4.4+)
* Fixed prompt showing up as exit in Bash - [793](https://github.com/warpdotdev/warp/issues/793)
* Improved parsing of Zsh default prompts
* Opening the find bar will automatically select any existing text - [831](https://github.com/warpdotdev/warp/issues/831)
### 2022.04.08 (v0.2022.04.04.09.07)
[Section titled “2022.04.08 (v0.2022.04.04.09.07)”](#20220408-v0202204040907)
**Bug fixes**
* Block sharing dialog now scrolls properly
### 2022.04.01 (v0.2022.04.01.01.37)
[Section titled “2022.04.01 (v0.2022.04.01.01.37)”](#20220401-v0202204010137)
**New features**
* Warm welcome!
* A.I. Command Search
**Bug fixes**
* Warp now properly registers `SPACE` and `SHIFT` modifier keys for Global Hotkey Windows
* Page Up and Page Down keys now work correctly in vim and other fullscreen apps - [560](https://github.com/warpdotdev/warp/issues/560)
* SSH now supports bootstrapping if bash-preexec is included in a Debian VM’s system rcfiles (eg by default at Google) - [578](https://github.com/warpdotdev/warp/issues/578)
* Corrected keyboard shortcut for split pane in context menu
### 2022.03.30 (v0.2022.03.29.02.23)
[Section titled “2022.03.30 (v0.2022.03.29.02.23)”](#20220330-v0202203290223)
**New features**
* Workflows: an easier way to share, parameterize, and execute commands - [625](https://github.com/warpdotdev/warp/issues/625)
* Quake mode / Focus Warp with a Global Hotkey - [091](https://github.com/warpdotdev/warp/issues/091)
**Bug fixes**
* Magnet, Swish and ALT-Tab window managers now work with Warp - [776](https://github.com/warpdotdev/warp/issues/776)
* SSH now handles control master connection errors - [578](https://github.com/warpdotdev/warp/issues/578)
* SSH now handles verbose mode, no longer leaks into the Input Editor as a typeahead - [578](https://github.com/warpdotdev/warp/issues/578)
* SSH now boots normally for POSIX shells that aren’t supported by Warp’s wrapper - [578](https://github.com/warpdotdev/warp/issues/578)
### 2022.03.24 (v0.2022.03.23.22.10)
[Section titled “2022.03.24 (v0.2022.03.23.22.10)”](#20220324-v0202203232210)
**New features**
* Fish support - [190](https://github.com/warpdotdev/warp/issues/190)
* Basic screenreader support (Voiceover) - Warp is now an accessible terminal!
* Added a toggle in the settings to disable the SSH wrapper - [821](https://github.com/warpdotdev/warp/issues/821)
**Bug fixes**
* Hitting tab with a text selection shows tab completions instead of indenting
* SSH no longer hangs when /tmp is not writable for Zsh - [578](https://github.com/warpdotdev/warp/issues/578)
* SSH no longer bootstrap the shell if it’s not meant to be an interactive session (e.g. if -T or a command is passed) - [578](https://github.com/warpdotdev/warp/issues/578)
* SSH now supports Starship and Zsh’s $PROMPT variable - [803](https://github.com/warpdotdev/warp/issues/803)
* Also import themes in subdirectories e.g. `~/.warp/themes/subdirectory/theme.yaml`
### 2022.03.16 (v0.2022.03.14.08.49)
[Section titled “2022.03.16 (v0.2022.03.14.08.49)”](#20220316-v0202203140849)
**New features**
* Multi-block selections and corresponding actions - [146](https://github.com/warpdotdev/warp/issues/146)
* Case-sensitive search
**Bug fixes**
* SSH no longer returns 0\~ and 1\~ after executing commands for Zsh 5.0.8 or older - [578](https://github.com/warpdotdev/warp/issues/578)
* SSH now supports LocalCommand / RemoteCommand - [578](https://github.com/warpdotdev/warp/issues/578)
* SSH over Zsh no longer depends on configuring locales on the remote machine - [578](https://github.com/warpdotdev/warp/issues/578)
* SSH sources /etc/bash.bashrc which is an extra rcfile in Debian and other Linux distributions - [578](https://github.com/warpdotdev/warp/issues/578)
* Improved completions stability when there are multiple panes on the same remote machine
* Vim and other alt-screen apps properly expand to take up the full window - [552](https://github.com/warpdotdev/warp/issues/552)
* Clicking into Warp from other foreground window focuses the clicked pane - [739](https://github.com/warpdotdev/warp/issues/739)
* Warp now respects ignore-space history options for Zsh and Bash - [044](https://github.com/warpdotdev/warp/issues/044)
* Warp now creates a \~/.warp folder to persist custom keybindings - [801](https://github.com/warpdotdev/warp/issues/801)
### 2022.03.09 (v0.2022.03.07.08.51)
[Section titled “2022.03.09 (v0.2022.03.07.08.51)”](#20220309-v0202203070851)
**Bug fixes**
* Added missing actions to Command Palette
* Option is meta is now in the settings menu
* Fix for SSH hanging when Zsh is the remote login shell
* Fix for SSH with Zsh that would break with certain rcfiles because of incorrectly set ZDOTDIR
### 2022.03.02 (v0.2022.02.28.08.45)
[Section titled “2022.03.02 (v0.2022.02.28.08.45)”](#20220302-v0202202280845)
**New features**
* Can now edit the keybindings for arrow navigation (Up/Down/Left/Right)
* Can now edit the keybindings for activating specific tabs (by number CMD-1, CMD-2, …)
**Bug fixes**
* Crash in theme chooser
* Fix for tab completion sometimes deleting characters
### 2022.02.23 (v0.2022.02.21.08.55)
[Section titled “2022.02.23 (v0.2022.02.21.08.55)”](#20220223-v0202202210855)
**New features**
* Zsh support over SSH
* Partially complete autosuggestion (by word) using CTRL-RIGHT and ALT-RIGHT - [488](https://github.com/warpdotdev/warp/issues/488)
* Added a Copy URL menu item after right-clicking a URL - [154](https://github.com/warpdotdev/warp/issues/154)
* Indicator for conflicting keybindings in keyboard customization UI
**Bug fixes**
* Able to fill-in longest common prefix after filtering tab completions - [618](https://github.com/warpdotdev/warp/issues/618)
* Block completion causes Input Editor to steal focus from find bar - [452](https://github.com/warpdotdev/warp/issues/452)
* UP-arrow in history menu sometimes scrolls more than one item
* CMD-F opens a no-op find bar in alt screen
### 2022.02.16 (v0.2022.02.14.08.44)
[Section titled “2022.02.16 (v0.2022.02.14.08.44)”](#20220216-v0202202140844)
**New features**
* Customizable key bindings (accessible via the settings menu) - [579](https://github.com/warpdotdev/warp/issues/579)
* Users can opt in to use their shell’s prompt rather than Warp’s default (select the Honor PS1 toggle under the settings menu) - [580](https://github.com/warpdotdev/warp/issues/580)
* Added a timestamp showing Block runtime duration; hover to see start and end date + time - [178](https://github.com/warpdotdev/warp/issues/178)
* CTRL-F now accepts autosuggestions - [403](https://github.com/warpdotdev/warp/issues/403)
* CTRL-E and CMD-RIGHT accept autosuggestions when at the end of the buffer - [403](https://github.com/warpdotdev/warp/issues/403)
* Allow input height to expand to half the pane height - [621](https://github.com/warpdotdev/warp/issues/621)
**Bug fixes**
* Arrow key presses now (up and down now) cycle themes in the theme picker - [294](https://github.com/warpdotdev/warp/issues/294)
* ESC keypress now exits the theme picker
* CMD-Down when on most recent block to focus input now clears Block selection
* Fixed a bug where resizing a pane while a command was running made it impossible to scroll to the bottom of the pane
* Fixed a bug where resizing a pane could cause Warp to show a blank screen
* Parentheses, quotes, and brackets now also auto-close after typing an alphanumeric character
* Remapped multi-cursor key bindings to CTRL-SHIFT-UP and CTRL-SHIFT-DOWN - [374](https://github.com/warpdotdev/warp/issues/374)
* Restored OPT-CMD-UP and OPT-CMD-DOWN for switching panes up and down - [730](https://github.com/warpdotdev/warp/issues/730)
### 2022.02.02 (v0.2022.01.31.09.03)
[Section titled “2022.02.02 (v0.2022.01.31.09.03)”](#20220202-v0202201310903)
**New features**
* Multi-cursor keybindings for adding cursors above and below current selections with OPT-CMD-UP/DOWN - [374](https://github.com/warpdotdev/warp/issues/374)
**Bug fixes**
* Double clicking the top of the window maximizes the app - [097](https://github.com/warpdotdev/warp/issues/097)
* Icon, cursor and selection contrast fixes
* Scrolling performance improvements with bg image themes
* Changelog visual glitch
* Resize bug - losing scroll position when viewing blocks with long output
### 2022.01.26 (v0.2022.01.24.08.55)
[Section titled “2022.01.26 (v0.2022.01.24.08.55)”](#20220126-v0202201240855)
**New features**
* Auto-close symbols (parentheses, quotes, and brackets) like VSCode
**Bug fixes**
* Block sharing link no longer cuts off - [660](https://github.com/warpdotdev/warp/issues/660)
* Right clicking a Block now focuses that Block
* Mouse dragging in vim
* Restoring history bug on session restore
* Automatically focus the last active window on session restore
### 2022.01.19 (v0.2022.01.17.08.48)
[Section titled “2022.01.19 (v0.2022.01.17.08.48)”](#20220119-v0202201170848)
**New features**
* Restore block contents
* The longest common prefix in the completions menu auto-fills the Input Editor - [479](https://github.com/warpdotdev/warp/issues/479)
* Add description for paths in completion results - [103](https://github.com/warpdotdev/warp/issues/103)
* Can right click the prompt and copy: git branch, prompt, cwd - [346](https://github.com/warpdotdev/warp/issues/346)
**Bug fixes**
* Fixed bug where venv was inserted into input editor - [599](https://github.com/warpdotdev/warp/issues/599)
* Improved url detection
### 2022.01.12 (v0.2022.01.10.17.24)
[Section titled “2022.01.12 (v0.2022.01.10.17.24)”](#20220112-v0202201101724)
**New features**
* Added a Changelog page to our documentation
**Bug fixes**
* Double clicking text in a url now highlights the word instead of the whole url - [508](https://github.com/warpdotdev/warp/issues/508)
* Double clicking a string with underscores now selects the whole string and not just the subword
* Selection updates correctly when a block hit its max line length
* Can now also close the Command Palette using CMD-P - [184](https://github.com/warpdotdev/warp/issues/184)
* Moved check for update button to settings dialog - [070](https://github.com/warpdotdev/warp/issues/070)
* Fixes tabs not opening in new windows when autoupdate is pending
* Fix regression with input box not being focused on app relaunch
### 2022.01.05 (v0.2022.01.03.09.07)
[Section titled “2022.01.05 (v0.2022.01.03.09.07)”](#20220105-v0202201030907)
**New features**
* Native undo and redo in the text editor using CMD-Z - [113](https://github.com/warpdotdev/warp/issues/113)
* Added CMD-M to minimize the Window - [107](https://github.com/warpdotdev/warp/issues/107)
* Added our open source licenses to the Warp Documentation
* Split pane focus indicator - a triangle in the top left corner of the pane in focus
**Bug fixes**
* CTRL-SPACE is now properly passed to Emacs and other terminal apps - [499](https://github.com/warpdotdev/warp/issues/499)
* Copy on select setting persists across sessions and does not reset after updates
# Changelog — 2023
Canonical page: [/changelog/2023/](https://docs.warp.dev/changelog/2023/)
> Warp release notes for 2023. Updates ship weekly, typically on Thursdays.
Submit bugs and feature requests on our [GitHub board!](https://github.com/warpdotdev/Warp/issues/new/choose)
### 2023.02.08 (v0.2024.02.13.08.02)
[Section titled “2023.02.08 (v0.2024.02.13.08.02)”](#20230208-v0202402130802)
**Bug fixes**
* Fix the inputted command sometimes overlapping rprompt (right-sided prompt)
### 2023.02.01 (v0.2024.01.30.16.52)
[Section titled “2023.02.01 (v0.2024.01.30.16.52)”](#20230201-v0202401301652)
**Improvements**
* Improved UX for pasting an auth token to complete the sign-in flow
* Subversion (svn) information is now available in Warp’s prompt
### 2023.01.18 (v0.2024.01.16.16.31)
[Section titled “2023.01.18 (v0.2024.01.16.16.31)”](#20230118-v0202401161631)
**New features**
* Warp on Linux (Private Beta): System fonts now load as expected
**Bug fixes**
* Warp on Linux (Private Beta): `ALT-TAB` no longer incorrectly inserts 4 spaces into the Input Editor
### 2023.01.11 (v0.2024.01.09.08.02)
[Section titled “2023.01.11 (v0.2024.01.09.08.02)”](#20230111-v0202401090802)
**New features**
* New workflow metadata for shared workflows in Warp Drive! Hover over any workflow to learn how recently the workflow has been executed, who edited it last, and when it was last edited.
### 2023.12.21 (v0.2024.01.02.08.02)
[Section titled “2023.12.21 (v0.2024.01.02.08.02)”](#20231221-v0202401020802)
**Improvements**
* The toolbelt displayed when hovering over background Blocks now has a solid background
**Bug fixes**
* The Markdown Viewer now respects the start number of ordered lists
* Completing a path that includes the tilde (`~`) character now works as expected
* Fixed an issue where Warp could quit before saving changes to Warp Drive
* Fix Warp hanging when using the ‘Insert into Input’ context menu action
### 2023.12.14 (v0.2023.12.12.08.02)
[Section titled “2023.12.14 (v0.2023.12.12.08.02)”](#20231214-v0202312120802)
**New features**
* Editing with Vim keybindings is now out of beta and generally available! Warp will detect vi mode in shell settings and suggest Vim keybindings.
**Improvements**
* You can now use `CMD-F` to search text in the Markdown Viewer
**Bug fixes**
* Block hover buttons now have a solid background when they overlap with your prompt
* The Block filter editor now has a clear button
* `J` and `K` (Vim Mode) can be used for navigation within a multi-line command
* Fixed the left alignment of the tab bar when in full-screen mode on macOS
* Fixed triple-click selection (selecting a line) when filtering a Block
* Fixed potential crash when using the find bar
* Fixed potential crash when retrieving accessibility contents
* Fix bug where “R” is erroneously inserted into the input in zsh sessions
### 2023.12.07 (v0.2023.12.05.08.02)
[Section titled “2023.12.07 (v0.2023.12.05.08.02)”](#20231207-v0202312050802)
**Improvements**
* Markdown file links can now be configured to open with the default external editor or Warp’s built-in markdown viewer
* Warp Drive folders now keep their opened/closed state through app restarts
**Bug fixes**
* The Input Editor now refocuses correctly after pasting terminal contents and running a command
* Fixed issue with missing toolbelt buttons when using fish with Vim Mode
### 2023.11.30 (v0.2023.11.28.08.02)
[Section titled “2023.11.30 (v0.2023.11.28.08.02)”](#20231130-v0202311280802)
**Improvements**
* Warp’s custom prompt builder now includes a context chip for Kubernetes context
* Improved completions for kubectl, including suggestions for resource, global options, and namespaces
**Bug fixes**
* Fixed a UI bug in the workflows editor where the editor for arguments was overflowing
* Search bar focuses as expected when you open Launch Configurations with the Command Palette
### 2023.11.16 (v0.2023.11.14.08.02)
[Section titled “2023.11.16 (v0.2023.11.14.08.02)”](#20231116-v0202311140802)
**Bug fixes**
* The informational block that shows workflow metadata now resizes with your Warp window
* The scrolling speed is now standardized across Warp
### 2023.11.09 (v0.2023.11.07.08.02)
[Section titled “2023.11.09 (v0.2023.11.07.08.02)”](#20231109-v0202311070802)
**New features**
* New Markdown Viewer: You can now open .md files in Warp and run the shell commands within these files
* Block Filtering: You can now filter block output (SHIFT-OPT-F) to quickly find matching lines based on a query.
**Improvements**
* Removed the workflow button from the toolbelt section (top-right buttons) of a block. It is still accessible through the right-click menu (see “Save as Workflow”) and its default keybinding CMD-S.
* Improved performance of Warp Drive team and state syncing
### 2023.11.02 (v0.2023.10.31.08.03)
[Section titled “2023.11.02 (v0.2023.10.31.08.03)”](#20231102-v0202310310803)
**Improvements**
* You can now invite new team members to your shared Warp Drive by email address and revoke invitations
### 2023.10.23 (v0.2023.10.17.08.03)
[Section titled “2023.10.23 (v0.2023.10.17.08.03)”](#20231023-v0202310170803)
**Improvements**
* Indicators appear in the tab bar when the current pane is maximized (a full-screen icon) and when a command exits with an error
* The Git context chip in Warp’s prompt now shows the commit hash instead of “HEAD” when in a detached state
* Easier to add and remove allowlisted domains when inviting teammates to Warp Drive
* Added a menu option for copying a workflow command (into the clipboard)
### 2023.10.19 (v0.2023.10.17.08.03)
[Section titled “2023.10.19 (v0.2023.10.17.08.03)”](#20231019-v0202310170803)
**Improvements**
* Indicators appear in the tab bar when the current pane is maximized (a full-screen icon) and when a command exits with an error
* The Git context chip in Warp’s prompt now shows the commit hash instead of “HEAD” when in a detached state
* Easier to add and remove allowlisted domains when inviting teammates to Warp Drive
* Added a menu option for copying a workflow command (into the clipboard)
### 2023.10.12 (v0.2023.10.10.08.06)
[Section titled “2023.10.12 (v0.2023.10.10.08.06)”](#20231012-v0202310100806)
**Improvements**
* Warp can now support macOS’s proxy settings
* You can now toggle whether to render Warp using the integrated GPU for dual GPU Macs
* Warp now escapes the file path of an executable loaded from Finder
**Bug fixes**
* Fixed a crash on startup for some users on macOS Sonoma
* The workflow info box now refreshes when edited
### 2023.10.05 (v0.2023.10.03.08.03)
[Section titled “2023.10.05 (v0.2023.10.03.08.03)”](#20231005-v0202310030803)
**New features**
* Now you can use Vim keybindings to edit text on the command line in Warp. Navigate to Settings > Feature > Editor and enable “Edit commands with Vim keybindings.” This feature is currently in beta and available to try today.
**Improvements**
* Admins can now control whether the team invite link is accessible for other team members to copy and share. Admins can also reset the URL token if needed.
* You can now add a 24-hour timestamp to your Warp prompt with context chips in the prompt editor.
* The free preview for Warp AI and Warp Drive for teams has been extended. Read about the [Warp AI and Warp Drive free preview extension](https://www.warp.dev/blog/free-preview-extended).
### 2023.09.28 (v0.2023.09.26.08.09)
[Section titled “2023.09.28 (v0.2023.09.26.08.09)”](#20230928-v0202309260809)
**New features**
* If you have Cursor installed, you can now set this as your default code editor under Settings > Features > General.
**Improvements**
* Enhanced user accessibility by adding a tab bar button as a new entry point for the Command Palette.
* Improved user guidance by displaying a warning when attempting to run a workflow while another command is already in progress.
**Bug fixes**
* Resolved an issue where autosuggestions were not being inserted when bound to certain keybindings.
* Fixed a bug affecting Input Method Editor functionality on non-English keyboards, which caused incorrect positioning and prevented text input after opening a new window.
### 2023.09.14 (v0.2023.09.19.08.04)
[Section titled “2023.09.14 (v0.2023.09.19.08.04)”](#20230914-v0202309190804)
**New features**
* You can now edit keybindings to scroll up and down by one line.
**Improvements**
* The input editor remains visible in inactive panes when using split panes.
**Bug fixes**
* Resolved a regression where the filled bookmark icon didn’t display on bookmarked blocks unless hovered on.
* Fixed the `TAB` key not cycling through fields in the Workflow editor under certain circumstances.
* Restored functionality of the keybinding for “New Tab” to work even when no windows are open.
### 2023.09.07 (v0.2023.09.06.18.09)
[Section titled “2023.09.07 (v0.2023.09.06.18.09)”](#20230907-v0202309061809)
**Improvements**
* The new tab keyboard shortcut (`CMD-T` by default) can now be re-mapped.
* Warp Drive now shows a loading indicator when syncing.
**Bug fixes**
* The command timestamp tooltip is no longer hidden when the Input Editor is pinned to the top.
### 2023.08.31 (v0.2023.08.29.08.04)
[Section titled “2023.08.31 (v0.2023.08.29.08.04)”](#20230831-v0202308290804)
**Improvements**
* You can now delete custom themes from the Warp UI
* You can now scroll to the top or bottom of a selected block from the Command Palette.
**Bug fixes**
* Fixed an issue where CPU was being used up by git processes ([3563](https://github.com/warpdotdev/warp/issues/3563))
* Fixed a Zsh bug where `set sh_word_split` could break Warp’s bootstrapping
### 2023.08.24 (v0.2023.08.22.08.03)
[Section titled “2023.08.24 (v0.2023.08.22.08.03)”](#20230824-v0202308220803)
**New features**
* Secret Redaction - Warp can now automatically redact secrets and sensitive information in terminal output, including passwords, IP addresses, API keys, and PII. Enable Secret Redaction from the Command Palette or Settings > Privacy > Secret Redaction
**Improvements**
* Special keys used in conjunction with `META` e.g. `META-DELETE` should now work within the alt-screen
* The line height for the text within the Input Editor should now actually change when the custom height in `Settings > Appearance > Text > Line Height` is updated
* Alias Abbreviations in fish should no longer show a red error underline within the Input Editor
* Reduced the bottom padding within the Input Editor when Warp is in Compact Mode
### 2023.08.17 (v0.2023.08.15.08.03)
[Section titled “2023.08.17 (v0.2023.08.15.08.03)”](#20230817-v0202308150803)
**New features**
* Warp now displays richer metadata for each command in history, including exit code, working directory, git branch, and whether the command is part of a workflow.
* Warp’s native prompt is now customizable directly within the app with drag-and-drop Context Chips (`Settings > Appearance > Prompt`)
**Improvements**
* Warp now supports xterm’s escape codes (sequences) for focus reporting
* The Command Palette now supports searching for workflows with their Warp Drive folder name, in addition to the Workflow’s name and description.
* Auto-generating custom themes from starting images now work even with a missing `~/.warp/themes` directory
* The “New Workflow” modal now supports more text for longer commands
### 2023.08.10 (v0.2023.08.08.08.04)
[Section titled “2023.08.10 (v0.2023.08.08.08.04)”](#20230810-v0202308080804)
**New features**
* Automatically create new themes based on a background image! Click the `+` button in the theme picker (`Settings -> Appearance -> Current Theme`) or search `Open Theme Picker` within the Command Palette
**Improvements**
* Workflows and folders in Warp Drive can now be sorted alphabetically and by last updated
* Multiple JetBrains IDEs are now supported as external editors (e.g. WebStorm, PhpStorm, GoLand)
* The Command Palette now shows which folders a Workflow is in (breadcrumbs)
* Aliases like `...` and `....` no longer incorrectly have an error underline
### 2023.08.03 (v0.2023.08.01.08.05)
[Section titled “2023.08.03 (v0.2023.08.01.08.05)”](#20230803-v0202308010805)
**New features**
* Reopen closed tabs with `SHIFT-CMD-T` for up to one minute; configure or disable this feature in `Settings > Features > Enable reopening of closed sessions`
* Autogenerate descriptions for Workflows in Warp Drive using Warp AI
**Improvements**
* Nested folders in Warp Drive can now be collapsed all at once
* Fixed issue where fish abbreviation expansion would include comments
* Fixed a regression with fish history becoming inaccessible
### 2023.07.27 (v0.2023.07.25.08.03)
[Section titled “2023.07.27 (v0.2023.07.25.08.03)”](#20230727-v0202307250803)
**Improvements**
* Fixed an issue where $PATH could be overwritten in Bash subshells
* Fixed an issue where completions for file-paths broke when using Named Flags e.g. `ls --color=auto`
* Fixed an issue where Warp Drive objects could get stuck in a sync state
* The down arrow `DOWN` now correctly moves the cursor within Warp AI’s text editor
### 2023.07.20 (v0.2023.07.18.08.03)
[Section titled “2023.07.20 (v0.2023.07.18.08.03)”](#20230720-v0202307180803)
**New features**
* Can now configure whether `TAB` accepts autosuggestions or opens the completions menu; switch between the configurations via `Settings > Features > Editor`
* Improved completions behavior by improving common prefix detection, and supporting case sensitivity
* Can now natively draw some Unicode block element characters instead of using font glyphs—improves alignment and reduces fuzziness
* Warp’s Resource Center now displays new features and improvements
**Improvements**
* Increased the maximum blur radius from 18 to 64
### 2023.07.13 (v0.2023.07.11.08.03)
[Section titled “2023.07.13 (v0.2023.07.11.08.03)”](#20230713-v0202307110803)
**New features**
* Warp Drive items that failed to sync can now be retried
* Workflows in Warp Drive can now be edited with the workflow execution modal
**Improvements**
* Fixed a bug where git information could sometimes be missing from the prompt
* Adjusted some colors throughout Warp—replaced gradients with solid colors.
### 2023.07.06 (v0.2023.07.04.08.03)
[Section titled “2023.07.06 (v0.2023.07.04.08.03)”](#20230706-v0202307040803)
**New features**
* A new AI Command Search experience that allows you to translate natural language to shell commands and integrates directly with workflows! Type ’#’ in the input to try it out!
**Improvements**
* Fixed a bug where Warp was not recognizing some single character commands and aliases.
* Fixed a bug where command output would sometimes be cut off after finishing (most notably in Gradle).
* Fixed a bug where two prompts could appear for remote Bash sessions
### 2023.06.29 (v0.2023.06.27.19.34)
[Section titled “2023.06.29 (v0.2023.06.27.19.34)”](#20230629-v0202306271934)
**New features**
* App links of the form Warp\://launch/\<launch\_configuration\_name> directly open a launch configuration
* Added a new setting for creating new windows with a specific size in terms of rows and columns.
**Improvements**
* Fix rendering of multiple ANSI styles on the same character. This fixes rendering issues commonly encountered in Vim and emacs.
* Fix tabs (indentations) sometimes being inserted into the Input Editor when the completion menu should open.
* Added tooltip for “New tab” button
* The “Launch Configurations” sub-menu (under the Mac File menu) now updates dynamically as launch configurations are added and removed.
* Find bar is able to match double-width unicode characters, including CJK and emojis.
* Fixed a crash that could occur when pasting a command in the workflow editor
### 2023.06.20 (v0.2023.06.20.08.04)
[Section titled “2023.06.20 (v0.2023.06.20.08.04)”](#20230620-v0202306200804)
**New features**
* You can now bring the power of your Powerlevel10k (P10K) prompt to Warp! For best results, you’ll need the latest version of P10K; see their GitHub page for upgrade instructions
* Right-side prompts are now supported in Zsh and fish!
* Warp AI commands can now be executed as workflows.
**Bug fixes**
* Clicking on an inactive Warp window now focuses the underlying pane correctly.
### 2023.06.08 (v0.2023.06.13.08.03)
[Section titled “2023.06.08 (v0.2023.06.13.08.03)”](#20230608-v0202306130803)
**New features**
* Added a settings page for our upgraded referral system—we’ve added new swag options.
* Right-click a highlighted file path to open a context menu that now supports showing the file in Finder
* The Command Palette can now search through Warp sessions, actions and launch configurations
**Bug fixes**
* The completions menu now supports fish abbreviations
* Fixed an issue where certain aliases would be incorrect after expansion.
* Fixed command search to ignore the extra whitespace before and after the search query
* Restored background Blocks no longer create blank history entries
* Fixed an issue where enabling the “Open completions as you type” setting could sometimes break path completions
* Fixed an issue where Zsh could fail to bootstrap when `$PATH` is an a bad state
* Fixed issue where Warp’s bootstrap logic could leak into Zsh’s history
* Fix issue with properly underlining when hyperlinks are in lists or span across multiple lines
### 2023.06.01 (v0.2023.05.30.08.03)
[Section titled “2023.06.01 (v0.2023.05.30.08.03)”](#20230601-v0202305300803)
**New features**
* Right-clicking the New Tab (`+`) button opens a context menu to select saved Launch Configurations
* Use Page Up (`PG-UP`) and Page Down (`PG-DOWN`) in the Command Palette for faster navigation
* Added support for Zed as a default code editor
* Referral counts have been updated to only include referrals who’ve onboarded onto (actually tried) Warp
**Bug fixes**
* Warp’s hotkey window (Quake Mode) now properly retains its size
* Fixed issue where command output would temporarily cutoff when resizing Warp.
* Fixed the Sticky Command Header covering content for pager commands.
* Fixed tabs showing stale text when being renamed.
* Clicking a Mac menu bar item that has a sub-menu no longer incorrectly closes the menu
* Warp now automatically focuses the shortcut search bar when the keyboard shortcuts pane is opened (`CMD-/`)
* Fixed regression where Warp’s native prompt no longer showed the virtual environment
### 2023.05.25 (v0.2023.05.23.08.05)
[Section titled “2023.05.25 (v0.2023.05.23.08.05)”](#20230525-v0202305230805)
**Bug fixes**
* Improved shell startup performance after a system restarts for users with Xcode installed
* Fixed issue with Warpifying a pipenv shell subshell from zsh
* Fixed issue with updating the git status prompt indicator in remote subshells
### 2023.05.18 (v0.2023.05.18.01.08)
[Section titled “2023.05.18 (v0.2023.05.18.01.08)”](#20230518-v0202305180108)
**New features**
* Warp now supports subshells in Zsh, Bash, and fish for a better experience with Docker, GCP, Poetry, and more. Configure which commands you’d like to “Warpify” under Settings > Subshells
**Bug fixes**
* Fixed an issue with Warp’s completions when using flags that start with a single dash e.g. `-namespace`
* Fixed an issue with Synchronized Inputs where switching from alt-screens focused on the incorrect terminal session
* Fixed an issue where command history suggestions could cause Synchronized Inputs to get out of sync
### 2023.05.11 (v0.2023.05.09.08.03)
[Section titled “2023.05.11 (v0.2023.05.09.08.03)”](#20230511-v0202305090803)
**New features**
* Warp now sends the output of background shell processes into new (distinct) Blocks—separate from user generated Blocks.
* Synchronize (broadcast) input across multiple panes in a single tab or multiple tabs (`Mac Menu > Edit > Synchronize Inputs` or `Synchronize` within the Command Palette)
* Added option to enable (disabled by default) an audible terminal bell (`Settings > Features > Terminal` or “Enable/Disable Audible Terminal Bell” within the Command Palette)
* Now opens new windows with the same position and size of the most recently closed window (if there is one)
* Fish aliases are now supported in the completions menu
**Bug fixes**
* Support for `SHIFT-UP` and `SHIFT-DOWN` within alt-screen editors
* Fixed incorrect alt-screen scrolling behavior when scroll reporting is enabled
* `SHIFT-TAB` now (correctly) sends the ANSI (backward-tab) escape sequence (for Vim and NeoVim)
* SSH wrapper now also loads your /etc/profile and supports login-like prompts and interactions like printing the message of the day (MOTD)
### 2023.05.04 (v0.2023.05.02.08.03)
[Section titled “2023.05.04 (v0.2023.05.02.08.03)”](#20230504-v0202305020803)
**New features**
* Indicate when Warp is downloading an update in Settings > Account > About Warp
* Support alias expansion for bash/zsh aliases
### 2023.04.27 (v0.2023.04.25.08.05)
[Section titled “2023.04.27 (v0.2023.04.25.08.05)”](#20230427-v0202304250805)
**New features**
* Support for Fish abbreviations
* Right-click within the Input Editor to open a context menu where you can split panes, etc.
**Bug fixes**
* Starting a command with whitespace in the Workflow creation dialog no longer breaks its argument parser
* Fixed a bug when commands were aliased to `comm` because of a naming clash with Warp’s wrapper
* `Cut word left` (`CTRL-W`) and `Cut word right` (`OPT-D`) now use the shell clipboard instead of the system clipboard
### 2023.04.13 (v0.2023.04.11.08.03)
[Section titled “2023.04.13 (v0.2023.04.11.08.03)”](#20230413-v0202304110803)
**New features**
* Navigation by subword within the Input Editor with `CTRL-OPT-LEFT` and `CTRL-OPT-RIGHT`
* View prior Warp AI questions using the `UP` arrow even after the transcript is cleared
**Bug fixes**
* Fixed a bug in proxied SSH while not on the default shell
* Background blur now also applies to windows that are opened via drag-and-drop from Finder
* The Sticky Command Header no longer cuts off text for pagers
### 2023.04.06 (v0.2023.04.04.08.03)
[Section titled “2023.04.06 (v0.2023.04.04.08.03)”](#20230406-v0202304040803)
**New features**
* The position of the input and direction of the terminal output are now configurable. You can start the input at the top and have it move down as new commands are run (to clear the screen and reset the position press `CTRL-L`, `CMD-K` or type `clear`). Or you can keep the input pinned to the top of the pane and have terminal outputs flow in reverse order. Settings are available under `Settings > Appearance > Input Position`
* Added a button for “jumping to the bottom” of the currently hovered Block to make it easy to get to the bottom of an output. Configurable with a setting under `Settings > Appearance > Blocks`
* Warp AI transcripts can now be navigated via keyboard (`UP` / `DOWN` arrows)
* Added a right-click context menu in the alt-screen (that still respects mouse reporting and SGR\_MOUSE)
* Warp AI’s past prompts can be accessed via `UP` (arrow)
* `CMD-ENTER` within Warp AI now inputs the selected command into the Input Editor
**Bug fixes**
* Workflows can now be searched by their description in Command Search
* Consolidated “Ask Warp AI” keybindings into one
* Fixed an issue causing “Move cursor by word” and “Select left/right by word” to not work if “Left/Right Option key is Meta” is enabled
* Can now unset cursor navigation bindings within an executing command
### 2023.03.30 (v0.2023.03.28.08.03)
[Section titled “2023.03.30 (v0.2023.03.28.08.03)”](#20230330-v0202303280803)
**New features**
* Warning if a known-incompatible custom prompt is detected
* Keybindings for cursor navigation in REPLs and subshells, e.g. ⌥←, ⌥→, ⌥⌫, ⌘←, ⌘→, ⌘⌫, ⌘fn⌫
**Bug fixes**
* Fixed an issue where an input suggestion tooltip could overflow outside the visible window
* Fixed keybinding conflict with Warp AI
* Fixed completion and syntax highlighting when local paths contain separators, not in the prefix
### 2023.03.23 (v0.2023.03.21.08.02)
[Section titled “2023.03.23 (v0.2023.03.21.08.02)”](#20230323-v0202303210802)
**New features**
* Added VSCode Insiders as a supported code editor
* Added completions for pnpm.
**Bug fixes**
* Fixed an issue where AI command results with multiple commands would all render on the same line
* The configurable width of Universal Search is now persistent (doesn’t reset to default in new sessions).
* “Copy Prompt” now correctly respects your PS1 prompt, if enabled
* Fixed automatic command corrections for cargo.
### 2023.03.20 (v0.2023.03.14.08.03)
[Section titled “2023.03.20 (v0.2023.03.14.08.03)”](#20230320-v0202303140803)
**New features**
* Added support to configure which shell Warp should use when starting a terminal session. Configurable under Settings -> Features -> Session.
* Tabs can now be renamed via mouse double-click.
**Bug fixes**
* Launch configuration templates now support use of `~` in the `cwd` field.
* Double-clicking a button/tab in the title bar no longer resizes the whole window.
* Context menus in the blocklist are now more pronounced and easier to dismiss by clicking.
* Increased the clickable area of small search boxes.
* A keyboard shortcut can now be registered to clear all blocks.
* Fixed some locale-related issues due to use of `LC_ALL` environment variable.
* Xterm escape code OSC 4 (“change color”) no longer crashes the app when it appears in PS1.
* Fixed a crash that occurs when resizing windows after dismissing a notification banner.
* Fixed crash that occurs if you unset the keybinding for the keyboard shortcuts side panel.
* Added Warp AI to resource center.
### 2023.03.16 (v0.2023.03.07.08.02)
[Section titled “2023.03.16 (v0.2023.03.07.08.02)”](#20230316-v0202303070802)
**New features**
* Introducing Warp AI ⚡ Get explanations for errors and outputs, ask for help with complicated workflows and scripts, easily execute suggested commands, all without leaving Warp!
### 2023.03.09 (v0.2023.03.07.08.02)
[Section titled “2023.03.09 (v0.2023.03.07.08.02)”](#20230309-v0202303070802)
**New features**
* Added support for clearing a keybinding for an action [2300](https://github.com/warpdotdev/warp/issues/2300).
* Added support for showing/hiding Warp windows with a system-wide Activation hotkey [2585](https://github.com/warpdotdev/warp/issues/2585).
* Improved scroll speed for Sidebar menu ‘Warp Essentials’/‘Keyboard Shortcuts’ [2673](https://github.com/warpdotdev/warp/issues/2673).
* Users may now set a custom keybinding to open the completions menu.
* Enabling/disabling mouse reporting is no longer bound to CMD-R by default.
* Toggling mouse reporting enabled shows a banner.
**Bug fixes**
* Fixed SSH wrapper hanging forever when SSH host is Arch Linux with the latest bash package [2636](https://github.com/warpdotdev/warp/issues/2636).
* Fixed Bash commands having escape codes in the last 20 characters producing incorrect output.
* Fixed a bug with bash prompt expansion on recent macOS versions.
### 2023.02.28 (v0.2023.02.28.08.03)
[Section titled “2023.02.28 (v0.2023.02.28.08.03)”](#20230228-v0202302280803)
**New features**
* Warp now suggests a URL for creating a GitHub PR on `git push`.
* Command Search and Workflow menus are now horizontally resizable.
**Bug fixes**
* Fixed a bug where Warp doesn’t correctly Auto-Raise.
* Fixed issue where formatting is lost when pasting into nano.
* Fixed issue where Warp doesn’t detect process termination when exiting `info`.
* Fixed a bug with bash prompt expansion not working on v4.4 or earlier.
* Fixed a bug where profile pictures don’t show in the Account menu.
* Fixed Syntax Highlighting and Error Underlining’s handling of multi-byte characters.
* Fixed issue where ‘Checking for Update’ doesn’t reflect the current status.
### 2023.02.23 (v0.2023.02.21.08.03)
[Section titled “2023.02.23 (v0.2023.02.21.08.03)”](#20230223-v0202302210803)
**New features**
* Support for configuring the initial working directory for new sessions. New tabs/windows/split panes can have separate configurations, or you can set one value for all new sessions.
**Bug fixes**
* Warp now supports syntax highlighting and error underlining for multi-line inputs with multibyte characters
* Fixed a bug where the update status in Warp’s `About Section` was incorrect.
* Improved GPU memory consumption when multiple windows are open.
### 2023.02.16 (v0.2023.02.14.08.05)
[Section titled “2023.02.16 (v0.2023.02.14.08.05)”](#20230216-v0202302140805)
**New features**
* Improved double-click selection. Double-clicking text now smart selects patterns like file paths, URLs, email addresses, etc. - [659](https://github.com/warpdotdev/warp/issues/659)
* Warp can now be opened from Finder - [102](https://github.com/warpdotdev/warp/issues/102)
**Bug fixes**
* Warp no longer hangs after exiting the alt-screen—having searched for text using Find.
* The Block-list now scrolls to the correct position after returning from the alt-screen.
* Clicking above the scroll-bar no longer (incorrectly) changes its scroll position.
* The terminal cell dimensions now update immediately after modifying the Font size.
* Hyperlinks no longer incorrectly highlight on hover when Warp is not focused.
* The Input Method Editor (non-English keyboards) is now positioned correctly in the alt-screen and in running Blocks
* When there are no windows open, clicking `New Tab` from the Mac menu will create a new window
### 2023.02.09 (v0.2023.02.07.08.03)
[Section titled “2023.02.09 (v0.2023.02.07.08.03)”](#20230209-v0202302070803)
**Bug fixes**
* Warp now sets the Mac window title; right-clicking on the dock icon will show the name of the active tab.
* Fixed a bug where navigating the theme picker with the arrow keys would lead to a crash when no theme matches the search.
* The Input Editor now refocuses correctly after clicking hyperlinks.
* Custom keybindings incorporating the `SPACE` key now persist after closing Warp.
* The Input Method Editor (non-English keyboards) now positions itself within the Input Editor
### 2023.01.26 (v0.2023.01.24.08.03)
[Section titled “2023.01.26 (v0.2023.01.24.08.03)”](#20230126-v0202301240803)
**New features**
* Warp can now dim inactive terminal panes, navigate to `Settings > Appearance > Panes > Dim inactive panes`
**Bug fixes**
* Fixed crash when selecting multiple occurrences of multi-byte characters using `CTRL-G`
### 2023.01.19 (v0.2023.01.17.08.03)
[Section titled “2023.01.19 (v0.2023.01.17.08.03)”](#20230119-v0202301170803)
**New features**
* The current Git branch can now be copied using the Command Palette (`CMD-P`)
**Bug fixes**
* Fixed bug where some keybinding actions would be applied to the wrong terminal pane.
* Warp now checks the input values for font size and line height and ignores them if they are too small or large
* The `missing update permissions banner`, can now be dismissed
* Fixed a rare crash when closing panes created by a launch configuration
### 2023.01.12 (v0.2023.01.10.08.02)
[Section titled “2023.01.12 (v0.2023.01.10.08.02)”](#20230112-v0202301100802)
**New features**
* Support setting window background transparency and blur radius, via sliders under `Settings > Appearance`
* Revamped resource center! Click the Warp icon in the top right to see keyboard shortcuts and learn how to best use Warp
* Quit modal: Quitting or closing Warp while a session is running triggers a warning prompt–that also lets you view which sessions are running
* Added a toggle to disable cursor blinking
**Bug fixes**
* Can now support completions that have escaped paths
* Can now support background images with paths that start with \~
* Can now properly restore a Warp window’s position when using multiple monitors
* Commands from restored sessions run on the local machine no longer appear in the SSH server’s history
* Fixed issues SSHing into RHEL/Fedora machines with PackageKit-command-not-found installed
* Fixed incorrect handling of `->` as the user’s prompt
* Fixed ls completions when using the —color option
### 2023.01.05 (v0.2023.01.03.08.03)
[Section titled “2023.01.05 (v0.2023.01.03.08.03)”](#20230105-v0202301030803)
**Bug fixes**
* Trailing periods are no longer considered part of a URL.
* Fixed regression where the “autocomplete symbols” setting was not being respected.
# Changelog — 2024
Canonical page: [/changelog/2024/](https://docs.warp.dev/changelog/2024/)
> Warp release notes for 2024. Updates ship weekly, typically on Thursdays.
Submit bugs and feature requests on our [GitHub board!](https://github.com/warpdotdev/Warp/issues/new/choose)
### 2024.12.26 (v0.2024.12.18.08.02)
[Section titled “2024.12.26 (v0.2024.12.18.08.02)”](#20241226-v0202412180802)
**Improvements**
* We now immediately show an error when trying to Warpify unsupported shells over SSH.
**Bug fixes**
* Fixed blank lines being appended to some blocks on resize.
* Fixed an issue where the AI context disappears when accepting the default autosuggestion.
### 2024.12.19 (v0.2024.12.18.08.02)
[Section titled “2024.12.19 (v0.2024.12.18.08.02)”](#20241219-v0202412180802)
**New features**
* Introducing: Next Command! Next Command uses AI to suggest the next command to run based on your active terminal session and command history. Visit Settings > AI to turn it off.
* Added support for block and underline-styled cursors in the input editor (while vim mode is disabled).
**Improvements**
* Clarified default permission information for sessions and Warp Drive objects.
* F11 (configurable) now toggles fullscreen on Linux and Windows.
* PowerShell environment variables are now recognized in completions.
* Cursor shape is now more responsive to clickable buttons.
**Bug fixes**
* Characters from unhandled keystrokes no longer handled as typed characters in the alt screen, e.g. when using vim.
* Fixed issue with copying secrets when secret redaction is disabled.
* kubectl completions now respect your kubeconfig, specified through environment variables or command line flag.
* ssh commands with permission issues should no longer suggest sudo.
* Fixed an issue with lazygit entering a blank screen.
* \[macOS] Fixed a bug where Warp disk images volumes might not be unmounted after an update.
* \[macOS] Improved robustness of autoupdate process.
### 2024.12.13 (v0.2024.12.10.15.55)
[Section titled “2024.12.13 (v0.2024.12.10.15.55)”](#20241213-v0202412101555)
**New features**
* Prompt Suggestions may appear above the input, helping you activate Agent Mode quickly in scenarios where it might be helpful. Note this feature sends activity to an LLM to generate prompts, head to Settings > AI > Agent Mode if you’d like to turn it off.
* Warp now has support for Claude 3.5 Sonnet and Haiku. Choose which model to use in the dropdown menu above your Agent Mode prompts.
* Agent Mode can now leverage your Warp Drive contents to tailor responses to your personal and team developer workflows.
* Warp has added a Shell Selector - a dropdown menu next to the ‘New tab’ button in the tab bar - to quickly pick from the shells available on your system.
* Agent Mode can now suggest code changes in a built-in code editor.
* \[macOS] You can now configure whether closing the last window quits the app (in Settings > Features).
**Improvements**
* Added settings to manage Warp’s AI integration and permissions. Visit Settings > AI to learn more.
* Single-window launch configs can be launched into the active window from the launch config palette using cmdorctrl-enter.
* You can now set `PS1` with `PROMPT_COMMAND` in bash.
**Bug fixes**
* Fixed an issue where the ‘Git Uncommitted File Count’ prompt chip did not work on fish on Linux.
* Fixed highlighting for arguments in workflows with multibyte characters
* Hitting ENTER within the Launch Config Save Modal will work as expected.
* Fixed issue with copying secrets when secret redaction is disabled.
### 2024.12.11 (v0.2024.12.10.15.55)
[Section titled “2024.12.11 (v0.2024.12.10.15.55)”](#20241211-v0202412101555)
**New features**
* Prompt Suggestions may appear above the input, helping you activate Agent Mode quickly in scenarios where it might be helpful. Note this feature sends activity to an LLM to generate prompts, head to Settings > AI > Agent Mode if you’d like to turn it off.
* Warp now has support for Claude 3.5 Sonnet and Haiku. Choose which model to use in the dropdown menu above your Agent Mode prompts.
* Agent Mode can now leverage your Warp Drive contents to tailor responses to your personal and team developer workflows.
* Warp has added a Shell Selector - a dropdown menu next to the ‘New tab’ button in the tab bar - to quickly pick from the shells available on your system.
* Agent Mode can now suggest code changes in a built-in code editor.
* \[macOS] You can now configure whether closing the last window quits the app (in Settings > Features).
**Improvements**
* Single-window launch configs can be launched into the active window from the launch config palette using cmdorctrl-enter.
* You can now set `PS1` with `PROMPT_COMMAND` in bash.
**Bug fixes**
* Fixed an issue where the ‘Git Uncommitted File Count’ prompt chip did not work on fish on Linux.
* Fixed highlighting for arguments in workflows with multibyte characters
* Hitting ENTER within the Launch Config Save Modal will work as expected.
### 2024.12.05 (v0.2024.12.03.08.02)
[Section titled “2024.12.05 (v0.2024.12.03.08.02)”](#20241205-v0202412030802)
**New features**
* You can now share shared sessions directly with your Warp team, another Warp user, and non Warp users via a URL.
* You can now share Warp Drive objects directly with others via email or a URL.
* Padding in the alt-screen can now be manually adjusted. Defaults to no padding.
**Improvements**
* Improved PTY throughput by \~13% through more efficient dirty region computation.
### 2024.12.02 (v0.2024.12.02.15.50)
[Section titled “2024.12.02 (v0.2024.12.02.15.50)”](#20241202-v0202412021550)
**Bug fixes**
* Warp no longer uses so much CPU.
### 2024.11.27 (v0.2024.11.27.01.55)
[Section titled “2024.11.27 (v0.2024.11.27.01.55)”](#20241127-v0202411270155)
**Improvements**
* \[Agent Mode] Code outputs no longer show a confusing code diff UI.
* You can now sort Warp Drive objects by type, with folders on top.
**Bug fixes**
* \[Agent Mode] Single-line code suggestions are no longer hidden behind the horizontal scrollbar.
* Fixed a crash interacting with Env Vars in the Command Palette.
### 2024.11.25 (v0.2024.11.25.16.32)
[Section titled “2024.11.25 (v0.2024.11.25.16.32)”](#20241125-v0202411251632)
**Improvements**
* \[Agent Mode] Code outputs no longer show a confusing code diff UI.
* You can now sort Warp Drive objects by type, with folders on top.
**Bug fixes**
* \[Agent Mode] Single-line code suggestions are no longer hidden behind the horizontal scrollbar.
* Fixed a crash interacting with Env Vars in the Command Palette.
### 2024.11.22 (v0.2024.11.22.18.28)
[Section titled “2024.11.22 (v0.2024.11.22.18.28)”](#20241122-v0202411221828)
**Improvements**
* \[Agent Mode] Code outputs no longer show a confusing code diff UI.
* You can now sort Warp Drive objects by type, with folders on top.
**Bug fixes**
* \[Agent Mode] Single-line code suggestions are no longer hidden behind the horizontal scrollbar.
* Fixed a crash interacting with Env Vars in the Command Palette.
### 2024.11.26 (v0.2024.11.19.08.02)
[Section titled “2024.11.26 (v0.2024.11.19.08.02)”](#20241126-v0202411190802)
**New features**
* You can now use Warp without login!
**Improvements**
* \[Agent Mode] Code outputs no longer show a confusing code diff UI.
* You can now sort Warp Drive objects by type, with folders on top.
**Bug fixes**
* \[Agent Mode] Single-line code suggestions are no longer hidden behind the horizontal scrollbar.
* Fixed a crash interacting with Env Vars in the Command Palette.
* Fixed a bug where `command substitution: ignored null byte in input` would appear as output while using a Bash subshell.
### 2024.11.19 (v0.2024.11.19.08.02)
[Section titled “2024.11.19 (v0.2024.11.19.08.02)”](#20241119-v0202411190802)
**New features**
* You can now use Warp without login!
**Improvements**
* \[Agent Mode] Code outputs no longer show a confusing code diff UI.
* You can now sort Warp Drive objects by type, with folders on top.
**Bug fixes**
* \[Agent Mode] Single-line code suggestions are no longer hidden behind the horizontal scrollbar.
* Fixed a crash interacting with Env Vars in the Command Palette.
### 2024.11.18 (v0.2024.11.18.16.37)
[Section titled “2024.11.18 (v0.2024.11.18.16.37)”](#20241118-v0202411181637)
**Improvements**
* Added padding after an expanded Agent Mode requested command.
* Improved the quality of autosuggestions.
* Warp Drive workflow links now open in the active terminal session rather than a new tab.
* On the web, Warp Drive workflows now have a button to quickly open the workflow in Warp’s desktop app.
**Bug fixes**
* Fixed Graphite CLI (`gt`) completions.
* Fixed completion and syntax highlighting behavior for arguments containing backslashes in PowerShell.
* Fixed an issue where opening Warp Drive in a browser could cause the tab to stop responding.
### 2024.11.12 (v0.2024.11.12.08.02)
[Section titled “2024.11.12 (v0.2024.11.12.08.02)”](#20241112-v0202411120802)
**Improvements**
* Added padding after an expanded Agent Mode requested command.
* Improved the quality of autosuggestions.
* Warp Drive workflow links now open in the active terminal session rather than a new tab.
* On the web, Warp Drive workflows now have a button to quickly open the workflow in Warp’s desktop app.
* \[Linux] Increased the app icon size to match other apps.
**Bug fixes**
* Fixed Graphite CLI (`gt`) completions.
* Fixed completion and syntax highlighting behavior for arguments containing backslashes in PowerShell.
* Fixed an issue where opening Warp Drive in a browser could cause the tab to stop responding.
* \[Linux] Tightened timeout for looking up the system color scheme at app startup to avoid hangs if the `org.freedesktop.portal.Desktop` D-Bus service is unresponsive.
* \[macOS] Fixed a crash that can occur when starting the app or opening a new window.
### 2024.11.11 (v0.2024.11.05.08.02)
[Section titled “2024.11.11 (v0.2024.11.05.08.02)”](#20241111-v0202411050802)
**Improvements**
* Fixes a bug where Warpifying subshells could crash if you had something typed in your input.
* Renamed the Subshells tab to Warpify in Settings.
**Bug fixes**
* Fixed an issue where kubectl resource names wouldn’t complete given a prefix.
* Fixed bug causing not all memory to be immediately freed when clearing the blocklist.
* \[macOS] Fixed a crash that can occur when starting the app or opening a new window.
### 2024.11.05 (v0.2024.11.05.08.02)
[Section titled “2024.11.05 (v0.2024.11.05.08.02)”](#20241105-v0202411050802)
**Improvements**
* Fixes a bug where Warpifying subshells could crash if you had something typed in your input.
* Renamed the Subshells tab to Warpify in Settings.
**Bug fixes**
* Fixed an issue where kubectl resource names wouldn’t complete given a prefix.
* Fixed bug causing not all memory to be immediately freed when clearing the blocklist.
### 2024.10.23 (v0.2024.10.29.08.02)
[Section titled “2024.10.23 (v0.2024.10.29.08.02)”](#20241023-v0202410290802)
**Bug fixes**
* Improved command completions to no longer attempt to use error messages as valid options.
* Fixed some kubectl completions not working as intended.
### 2024.10.17 (v0.2024.10.15.08.02)
[Section titled “2024.10.17 (v0.2024.10.15.08.02)”](#20241017-v0202410150802)
**New features**
* Warp.dev has a fresh look today! Check out what’s new and read about the [design process behind the World of Warp launch](https://www.warp.dev/blog/world-of-warp).
**Improvements**
* Created a setting allowing focus to follow mouse hover (requested in issue [699](https://github.com/warpdotdev/warp/issues/699)).
* Automatically switch to shell command input mode if accepting a shell command autosuggestion from Agent Mode.
* \[macOS] Adjusted default font smoothing (Appearance > “Use thin strokes”) configuration to improve text legibility.
**Bug fixes**
* Alt-screen find doesn’t beachball when scrolling through find matches.
* You can now select individual cells in the alt-screen.
* All find matches are correctly highlighted in the alt-screen.
* Hitting ENTER within the Launch Config Save Modal will work as expected.
* Removed node prompt chip due to slow performance.
* Fixed an issue on Linux distributions where Warp took a long time to start up.
### 2024.10.11 (v0.2024.10.08.08.02)
[Section titled “2024.10.11 (v0.2024.10.08.08.02)”](#20241011-v0202410080802)
**Improvements**
* Tab key always accepts active autosuggestions in zero-state.
* Command suggestions from Agent Mode are now ghosted autosuggestions instead of direct buffer text.
* Warp now shows a warning when closing a tab with running commands or shared sessions.
* New Agent Mode panes will open to a useful minimum width if the Warp window is big enough to support it.
* Clearing the terminal input via ctrl-c will now also close the command search.
* \[macOS] You can now access Warp Drive features from mac menus.
* \[macOS] You can click the mouse middle-button to paste from the clipboard.
**Bug fixes**
* Agent Mode queries are now de-duplicated in up-arrow history and Command Search.
* `ctrl-d` can now be used to signal EOF when the shell is bootstrapping.
* Double-clicking the tab bar now correctly toggles maximizing the Warp window even when an AI block is present in the focused pane.
* Hovering over the block insertion menu at the bottom of a notebook no longer causes Warp to hang.
* Fixed crash when search result in alt screen is scrolled out of view.
* Fixed broken `cmd-shift-R`/`ctrl-shift-R` keybinding for accessing the Workflows view.
### 2024.10.10 (v0.2024.10.08.08.02)
[Section titled “2024.10.10 (v0.2024.10.08.08.02)”](#20241010-v0202410080802)
**Improvements**
* Tab key always accepts active autosuggestions in zero-state.
* Command suggestions from Agent Mode are now ghosted autosuggestions instead of direct buffer text.
* Warp now shows a warning when closing a tab with running commands or shared sessions.
* New Agent Mode panes will open to a useful minimum width if the Warp window is big enough to support it.
* Clearing the terminal input via ctrl-c will now also close the command search.
* \[macOS] You can now access Warp Drive features from mac menus.
* \[macOS] You can click the mouse middle-button to paste from the clipboard.
**Bug fixes**
* Agent Mode queries are now de-duplicated in up-arrow history and Command Search.
* `ctrl-d` can now be used to signal EOF when the shell is bootstrapping.
* Double-clicking the tab bar now correctly toggles maximizing the Warp window even when an AI block is present in the focused pane.
* Hovering over the block insertion menu at the bottom of a notebook no longer causes Warp to hang.
### 2024.09.24 (v0.2024.09.24.08.02)
[Section titled “2024.09.24 (v0.2024.09.24.08.02)”](#20240924-v0202409240802)
**New features**
* Powershell is now supported! Make `pwsh` your default shell for your user account or select `pwsh` in Settings > Features > Startup shell for new sessions.
* You can now save and sync environment variable collections in Warp Drive. To learn more, see [Environment Variables](/knowledge-and-collaboration/warp-drive/environment-variables/).
* Your Agent Mode blocks and queries are now restored across sessions.
**Improvements**
* Secret redaction now applies to AI Blocks within Warp, in addition to Command Blocks.
* New Agent Mode panes always open to the right.
* You can now navigate the trash index via your keyboard.
**Bug fixes**
* `fish` config is no longer sourced twice during shell startup.
* The first window after launching Warp will now use a custom window size if set.
* When opening a launch configuration, Warp now respects restored and custom window sizes.
### 2024.09.17 (v0.2024.09.17.08.02)
[Section titled “2024.09.17 (v0.2024.09.17.08.02)”](#20240917-v0202409170802)
**New features**
* \[Linux] Warp now supports Wayland. You can configure the window system in `Settings > Features > System`.
**Improvements**
* Adds a Command Palette action called “Export all Warp Drive objects” that enables bulk export of a Warp Drive.
* Completion suggestions for git commit hashes are now sorted reverse-chronologically.
* History shows the working directory in which you made an Agent Mode query.
* Agent Mode Blocks are surfaced in Find.
**Bug fixes**
* Fixed an infinite loop bug that could lead to runaway memory usage and the application hanging.
* Fixes a regression where the Setup Guide didn’t work.
### 2024.09.05 (v0.2024.09.10.08.02)
[Section titled “2024.09.05 (v0.2024.09.10.08.02)”](#20240905-v0202409100802)
**Improvements**
* Links are now detected in Agent Mode responses.
**Bug fixes**
* Fixed an infinite loop bug that could lead to runaway memory usage and the application hanging.
### 2024.08.29 (v0.2024.08.27.08.02)
[Section titled “2024.08.29 (v0.2024.08.27.08.02)”](#20240829-v0202408270802)
**Bug fixes**
* Link highlights now correctly disappear when making changes in alt-screen programs.
### 2024.08.22 (v0.2024.08.20.08.02)
[Section titled “2024.08.22 (v0.2024.08.20.08.02)”](#20240822-v0202408200802)
**New Features**
* You can now specify a cursor color in Warp themes.
**Improvements**
* Warp now restores fullscreen windows to fullscreen.
**Bug fixes**
* \[macOS] Completions for commands now work when you type a command name containing capital letters. This does not apply to aliases.
### 2024.08.14 (v0.2024.08.13.08.02)
[Section titled “2024.08.14 (v0.2024.08.13.08.02)”](#20240814-v0202408130802)
**New Features**
* New enums for Workflow arguments. Now you can set a list of suggested options for any argument in a workflow so it’s easier to fill in parameters correctly. To learn more, see [Workflows](https://docs.warp.dev/knowledge-and-collaboration/warp-drive/workflows#working-with-arguments).
### 2024.08.07 (v0.2024.08.06.08.01)
[Section titled “2024.08.07 (v0.2024.08.06.08.01)”](#20240807-v0202408060801)
**New Features**
* You can now find your past Agent Mode queries in Command Search (ctrl-r).
**Improvements**
* Completions-as-you-type now works in AI input for filepath completions.
**Bug Fixes**
* Warp now recognizes more escape codes for toggling alternate screen mode.
### 2024.07.30 (v0.2024.07.30.08.02)
[Section titled “2024.07.30 (v0.2024.07.30.08.02)”](#20240730-v0202407300802)
**Improvements**
* Now it’s easier to find and configure settings related to AI on the command line. You can enable / disable natural language detection or input hint text under Settings > AI
### 2024.07.24 (v0.2024.07.23.08.02)
[Section titled “2024.07.24 (v0.2024.07.23.08.02)”](#20240724-v0202407230802)
**New features**
* You can now find AI queries from other sessions in up-arrow history.
**Improvements**
* Clicking an attached block on an AI block no longer affects your pending query’s context selection.
* Clicking the terminal input box will no longer remove the blocks you selected as context.
* Added support for smart selections in AI blocks.
* Increased priority of command matches when searching for a workflow.
**Bug fixes**
* Opening file links with line and column numbers in Zed now works.
### 2024.07.19 (v0.2024.07.16.08.02)
[Section titled “2024.07.19 (v0.2024.07.16.08.02)”](#20240719-v0202407160802)
**Improvements**
* Completions for git push origin now include tags in addition to branches.
* Docker extension: The “Open in Warp” feature now requires you to run the command in order to open the Warpified Docker subshell. Attempts to open an invalid link will display an error toast.
**Bug fixes**
* Warp prompt text now respects custom line height settings.
* Scroll positions are now stable when hitting block line limits ([1355](https://github.com/warpdotdev/warp/issues/1355)).
* Fixed binaries listed directly in `PATH` being automatically executed when running commands in Bash.
### 2024.07.18 (v0.2024.07.16.08.02)
[Section titled “2024.07.18 (v0.2024.07.16.08.02)”](#20240718-v0202407160802)
**Improvements**
* Completions for git push origin now include tags in addition to branches.
* Docker extension: The “Open in Warp” feature now requires you to run the command in order to open the Warpified Docker subshell. Attempts to open an invalid link will display an error toast.
**Bug fixes**
* Warp prompt text now respects custom line height settings.
* Scroll positions are now stable when hitting block line limits ([1355](https://github.com/warpdotdev/warp/issues/1355)).
* Fish commands containing syntax errors now correctly “finish” the block.
* Fixed binaries listed directly in `PATH` being automatically executed when running commands in Bash.
### 2024.07.11 (v0.2024.07.09.08.01)
[Section titled “2024.07.11 (v0.2024.07.09.08.01)”](#20240711-v0202407090801)
**New features**
* Same line prompt. Now you can choose whether you’d like your prompt on a new line (Warp’s default) or on the same line with commands, like a classic terminal. If you’re using PS1, Warp will use the same line prompt setting to respect theme configurations. Visit Settings > Appearance > Prompt to configure your prompt style. To learn more, see [Prompts](https://docs.warp.dev/terminal/appearance/prompt#same-line-prompt).
**Improvements**
* Added support for completions while using Agent Mode input.
* Semantic selection now works in AI blocks.
* Shift+click now lets you select text for alternate screen apps in SGR mouse mode.
**Bug fixes**
* Pressing Esc in Vim insert mode no longer closes the history menu.
* Made sure terminal context menus close when opening the settings modal.
### 2024.06.27 (v0.2024.06.25.08.02)
[Section titled “2024.06.27 (v0.2024.06.25.08.02)”](#20240627-v0202406250802)
**New features**
* Warp’s new Pro plan includes higher AI requests for individuals or small teams.
* Read about the [Warp Pro plan](https://www.warp.dev/blog/pro-plan).
**Bug fixes**
* Text selection in full screen apps will change as you scroll.
* \[macOS] Meta shortcuts, e.g. `OPT-U`, `OPT-I`, will no longer be ignored.
### 2024.06.21 (v0.2024.06.18.08.02)
[Section titled “2024.06.21 (v0.2024.06.18.08.02)”](#20240621-v0202406180802)
**Improvements**
* The glyph over the cursor will take on a high-contrast color to make sure it’s legible.
* Dragging a word or line selection in a notebook now extends the selection.
**Bug fixes**
* Fixes a crash where text layout would not expect the BOM marker at the beginning of a string.
* \[Linux] Fix middle-click paste doubling the text.
### 2024.06.20 (v0.2024.06.18.08.02)
[Section titled “2024.06.20 (v0.2024.06.18.08.02)”](#20240620-v0202406180802)
**Improvements**
* The glyph over the cursor will take on a high-contrast color to make sure it’s legible.
* Dragging a word or line selection in a notebook now extends the selection.
**Bug fixes**
* Fixes a crash where text layout would not expect the BOM marker at the beginning of a string.
### 2024.06.17 (v0.2024.06.11.08.02)
[Section titled “2024.06.17 (v0.2024.06.11.08.02)”](#20240617-v0202406110802)
**New features**
* New Agent Mode in Warp AI: Use plain English on the command line to accomplish multi-step workflows.
* Read about [Agent Mode in Warp](https://www.warp.dev/blog/agent-mode).
### 2024.06.13 (v0.2024.06.11.08.02)
[Section titled “2024.06.13 (v0.2024.06.11.08.02)”](#20240613-v0202406110802)
**Improvements**
* Brackets and quotes are now autocompleted in the workflow editor.
* Improved support for editing multi-line workflows.
### 2024.06.06 (v0.2024.06.04.08.02)
[Section titled “2024.06.06 (v0.2024.06.04.08.02)”](#20240606-v0202406040802)
**Improvements**
* Warp now supports Unicode emoji presentation selectors when rendering glyphs
* Removed the default keybindings for Warp Drive object creation actions, in order to free up more keyboard shortcut options. You can still assign custom keybindings to these actions in Settings > Keyboard shortcuts
**Bug fixes**
* When editing with Vim visual line mode and the cursor is at the end of the line, operators will only affect the correct lines
### 2024.05.30 (v0.2024.05.28.08.02)
[Section titled “2024.05.30 (v0.2024.05.28.08.02)”](#20240530-v0202405280802)
**Improvements**
* Warp now renders terminal text ANSI colors as specified by the theme without any dimming
### 2024.05.23 (v0.2024.05.21.16.09)
[Section titled “2024.05.23 (v0.2024.05.21.16.09)”](#20240523-v0202405211609)
**Bug fixes**
* Fixed a bug where a terminal session could get stuck in a bad state if an SSH connection is lost while the alternate screen is in use (e.g.: tmux, TUI programs, pagers)
* Fixed a bug where 00\~ and 01\~ characters could get erroneously added to user-submitted commands after an SSH connection is lost
### 2024.05.16 (v0.2024.05.14.08.01)
[Section titled “2024.05.16 (v0.2024.05.14.08.01)”](#20240516-v0202405140801)
**New features**
* Team admins can now make their teams discoverable to colleagues from the same custom email domain. This feature is available under Settings -> Teams.
**Bug fixes**
* The prompt and command should no longer overlap the output (or each other) for multi-line commands in Bash versions earlier than 4.4—such as the default Bash installation for macOS.
### 2024.05.09 (v0.2024.05.07.08.02)
[Section titled “2024.05.09 (v0.2024.05.07.08.02)”](#20240509-v0202405070802)
**Bug fixes**
* Vim-related settings no longer appear in the Command Palette when editing with Vim keybindings is disabled
* Warp’s Input Editor now immediately reflects any changes to the Vim status bar settings
* Fixed a bug when handling URLs with parentheses in notebooks and Warp AI
### 2024.05.02 (v0.2024.04.30.08.02)
[Section titled “2024.05.02 (v0.2024.04.30.08.02)”](#20240502-v0202404300802)
**Bug fixes**
* In Notebooks, code block menus no longer overlap with rich text menus
* Fixed an issue that could cause Warp to display an invisible/empty window
* Fixed a crash that could occur when unindenting multiple lines within the Input Editor
* Fixed a Vim Mode bug when “cutting word left” (and similar actions) while the (up-arrow) history menu is open
* \[Linux] Fixed an issue where Warp would flicker on Intel UHD 620 drivers when using Vulkan due to a bug in specific versions of Mesa
* \[Linux] Fixed a regression in input latency
### 2024.03.27 (v0.2024.04.23.08.01)
[Section titled “2024.03.27 (v0.2024.04.23.08.01)”](#20240327-v0202404230801)
**New features**
* The free preview for Warp AI and Warp Drive for teams has ended. \[Learn about Warp’s new self-service plan]
**Improvements**
* Shared links to notebooks and workflows are now opened directly in Warp and no longer need to go through a browser
**Bug fixes**
* Warp now supports completions for directories that contain spaces when in a remote session
* Warp’s notebook editor now only shows hint text when it’s in edit mode
### 2024.04.18 (v0.2024.04.16.08.02)
[Section titled “2024.04.18 (v0.2024.04.16.08.02)”](#20240418-v0202404160802)
**Improvements**
* You can now navigate and expand folders in Warp Drive with left/right arrow keys
**Bug fixes**
* Middle-click now works even when the mouse is within the prompt area
* Already-open notebooks no longer open in a new tab
* Fixed an issue where autocd completions were incorrect for file paths starting with `~`
* Opening a Workflow through a link now focuses it, even while in trash view
* Fixed a bug handling carriage returns in notebooks, the markdown viewer, and Warp AI
### 2024.04.11 (v0.2024.04.09.08.01)
[Section titled “2024.04.11 (v0.2024.04.09.08.01)”](#20240411-v0202404090801)
**Improvements**
* Improved Warp’s prompt performance for large repositories
* When switching panes directionally, Warp now automatically selects the most recently focused pane in that given direction
**Bug fixes**
* Fixed a pane management bug where dragging a pane to a new location wouldn’t initiate the option to drop it there
### 2024.04.04 (v0.2024.04.02.08.02)
[Section titled “2024.04.04 (v0.2024.04.02.08.02)”](#20240404-v0202404020802)
**New features**
* Notebooks in Warp Drive. Create and share interactive runbooks with your team. Read about [Notebooks in Warp Drive](https://www.warp.dev/blog/notebooks-in-warp-drive).
**Improvements**
* You can now export workflows and notebooks from Warp Drive
* Middle-clicking to paste now automatically focuses the Input Editor
* Warp no longer automatically expands aliases that are escaped using a backslash
* \[Linux] Adds support for Android Studio, DataGrip, DataSpell, Goland, Pycharm, Rider, Rubymine, and Sublime Text as external editors
**Bug fixes**
* \[Linux] Warp now case-sensitively parses top-level commands on Linux
* \[Linux] Fixed an issue where middle-click paste could paste across multiple panes
### 2024.03.21 (v0.2024.03.19.08.01)
[Section titled “2024.03.21 (v0.2024.03.19.08.01)”](#20240321-v0202403190801)
**Bug fixes**
* Symlinks to a directory are now properly treated as a directory instead of as a file
* \[Linux] Warp’s windows are no longer escalated into an urgent state (tiling window managers) after a Warp URL is opened
### 2024.03.14 (v0.2024.03.12.08.02)
[Section titled “2024.03.14 (v0.2024.03.12.08.02)”](#20240314-v0202403120802)
**Improvements**
* Warp now supports the primary selection protocol, which allows you to paste with a middle click. On platforms that don’t support this, Warp will read/write from the default clipboard.
* You can now filter out unwanted lines from a block, using the new “invert filter” toggle in the block filtering menu
* Continuous block selections are now rendered with a single border instead of a border around each individual block
* The `�` and `^` patterns are now supported in Warp’s regex search (find bar and block filtering)
* \[Linux] The hotkey window now has a unique instance name on X11.
**Bug fixes**
* “Copy on Select” now works within alt-screens
### 2024.03.07 (v0.2024.03.05.08.02)
[Section titled “2024.03.07 (v0.2024.03.05.08.02)”](#20240307-v0202403050802)
**Improvements**
* You can now adjust the number of lines the mouse wheel scrolls in Warp. Go to Settings > Features > General > Lines Scrolled by Mouse Wheel Interval to configure this setting.
* You can now close the Warp window using the Command Palette (`SHIFT-CMD-W` for Mac).
* You can now quit Warp using the Command Palette (“Quit Warp”)
* \[Linux] Warp can now automatically hide the window’s traffic lights when using a tiling manager
* \[Linux] Improved (a window’s) rounded corners when using a tiling manager
* \[Linux] You can now move tabs left or right using keyboard shortcuts. Use `SHIFT-CTRL-PGUP` to move a tab to the left and `SHIFT-CTRL-PGDN` to move a tab to the right
**Bug fixes**
* Fixed a bug where Warp could crash because of an invalid Vim command
* \[Linux] Fixed a bug where errors encountered while running `pacman-key` could lead to an invalid pacman repository configuration
### 2024.03.05 (v0.2024.03.05.08.02)
[Section titled “2024.03.05 (v0.2024.03.05.08.02)”](#20240305-v0202403050802)
**Improvements**
* Improved Warp’s appearance and behavior when running in some tiling window managers.
**Bug fixes**
* Fixed crash that occurs when dragging the mouse.
### 2024.02.29 (v0.2024.02.27.08.01)
[Section titled “2024.02.29 (v0.2024.02.27.08.01)”](#20240229-v0202402270801)
**Improvements**
* Added completion support for `dnf`
* Configuring the global hotkey window settings (Quake Mode) now updates the window in real time
* \[Linux] Can now `CTRL-CLICK` to open a file
* \[Linux] Added support for IntelliJ, CLion, Webstorm, and PhpStorm
**Bug fixes**
* Fix issue with typeahead commands overlapping the prompt’s content
* Command X-Ray now recognizes builtins and functions, hover over a command in the Input Editor to see the command description
* Fixed an issue where the shell couldn’t accept pasted text when an rc file expected user input.
* \[Linux] Modified pacman-key -r invocation during Arch Linux auto-update to be more robust
* \[Linux] Fixed crash on Linux that could occur if device was missing a symlink from libX11.so to libX11.so.6
* \[Linux] Fixed issues where opening external links would cause Firefox 123 to use 100% CPU and never launch
* \[Linux] X11 Users can now open links when default browser is firefox
* \[Linux] Fix some global hotkey combinations crashing the app.
### 2024.02.26 (v0.2024.02.20.08.01)
[Section titled “2024.02.26 (v0.2024.02.20.08.01)”](#20240226-v0202402200801)
**New features**
* Warp is now available for Linux!
**Improvements**
* Completions for apt-get, aptitude, and pacman
* You can now type to search in the font picker in Settings > Appearance
### 2024.02.20 (v0.2024.02.20.08.01)
[Section titled “2024.02.20 (v0.2024.02.20.08.01)”](#20240220-v0202402200801)
**Improvements**
* Completions for apt-get, aptitude, and pacman.
### 2024.02.16 (v0.2024.02.16.17.24)
[Section titled “2024.02.16 (v0.2024.02.16.17.24)”](#20240216-v0202402161724)
**New features**
* Warp on Linux (Private Beta): Added support for the Input Mode Editor (IME).
### 2024.02.14 (v0.2024.02.14.15.46)
[Section titled “2024.02.14 (v0.2024.02.14.15.46)”](#20240214-v0202402141546)
**New features**
* Warp on Linux (Private Beta): Added support for the Input Mode Editor (IME).
# Changelog — 2025
Canonical page: [/changelog/2025/](https://docs.warp.dev/changelog/2025/)
> Warp release notes for 2025. Updates ship weekly, typically on Thursdays.
Submit bugs and feature requests on our [GitHub board!](https://github.com/warpdotdev/Warp/issues/new/choose)
### 2025.12.17 (v0.2025.12.17.17.17)
[Section titled “2025.12.17 (v0.2025.12.17.17.17)”](#20251217-v0202512171717)
**Improvements**
* Warp now specifies what different models were used for in the credit transparency footer.
* You can choose whether forked conversations open in a split pane or new tab.
* `warp mcp list`, `warp environment list`, and `warp agent profile list` now support plain-text and JSON output.
* MCP server configurations are now displayed in integration details (i.e. `warp integration list`).
* Added support for configuring MCP servers in integrations.
**Bug fixes**
* Fixed a bug where Oz CLI runs could get stuck trying to run a denylisted command.
### 2025.12.10 (v0.2025.12.10.08.12)
[Section titled “2025.12.10 (v0.2025.12.10.08.12)”](#20251210-v0202512100812)
**Improvements**
* Added ‘Initialize codebase’ button to Code Review, which appears when you’re in an uninitialized repo, making it easier to set up codebase indexing and LSP.
* Added a new sub-menu to the model picker for selecting the reasoning level of reasoning models.
* Added syntax highlighting for Vue template files.
* Added support for specifying custom models for agents, integrations, and scheduled agents using the `--model` flag.
* Added support for custom HTTP headers in MCP Streamable HTTP or SSE server connections.
* Added `/conversations` slash command with a clock-rewind icon to open the conversation history palette.
* Warp integrations will more proactively signal if the agent is blocked.
**Bug fixes**
* Fixed a bug where, in `Settings > Billing and usage`, the credit denomination wasn’t set to the proper value for teams with auto-reload on.
* The code editor now opens to the right of the active tab when “Choose a layout to open files in Warp” is set to “New tab”.
* Fixed mouse reporting for apps that don’t use the alternate screen buffer, e.g. Radare2.
### 2025.12.03 (v0.2025.12.03.08.12)
[Section titled “2025.12.03 (v0.2025.12.03.08.12)”](#20251203-v0202512030812)
**Improvements**
* The Oz CLI now displays more detailed information when the agent tries to take a prohibited action.
* Allow dragging file paths from the Project Explorer into active terminal commands like claude code and gemini for referencing files and folders.
**Bug fixes**
* Fixed a bug that could cause unbounded memory growth when using Warpified subshells or the legacy (non-tmux) SSH Warpify implementation.
* Fixed a bug that could cause `comm` errors to appear in Warpified subshells.
* \[Windows] Fixed keybinding for “find in code editor.” This is now `CTRL-SHIFT-F` and configurable from Settings > Keyboard shortcuts.
* Ensured that the Oz CLI is available automatically on macOS.
* Fixed toast messages showing “Notebook” instead of “Plan” when taking actions on Plans in Warp Drive.
### 2025.11.19 (v0.2025.11.19.08.12)
[Section titled “2025.11.19 (v0.2025.11.19.08.12)”](#20251119-v0202511190812)
**New features**
* MCP server configurations can now be shared with others on your team. You can install a server shared by your team with minimal configuration.
* Warp now provides out-of-box MCP servers for common services like GitHub and Linear that can be installed and run with a single click.
* Find now works in the code review pane.
### 2025.11.18 (v0.2025.11.18.12.24)
[Section titled “2025.11.18 (v0.2025.11.18.12.24)”](#20251118-v0202511181224)
**New features**
* [Full Terminal Use](/agents/capabilities/full-terminal-use/): Let the agent use the terminal as you would: interact with REPLs, debuggers, and full-screen apps like `top`. Warp is the only product on the market with Full Terminal Use capabilities.
* [`/plan`](/agents/capabilities/planning/): do spec-driven development in Warp. Work with an agent to align on an implementation plan that can be saved, versioned, and even attached to a PR for teammates.
* [Interactive Code Review](/agents/local-agents/interactive-code-review/): Review an agent’s code like you would a teammate’s, directly in Warp, and ask the agent to address the comments.
* [Slack and Linear integrations](https://docs.warp.dev/platform/integrations):\*\* Ask the agent to get to work from the tools you already use, track their progress, and take the wheel via live session sharing.
* Warp’s Agents can now [search the web](/agents/capabilities/web-search/) to retrieve information, when relevant. This capability is configurable via Agent Profiles.
### 2025.11.12 (v0.2025.11.12.08.12)
[Section titled “2025.11.12 (v0.2025.11.12.08.12)”](#20251112-v0202511120812)
**Improvements**
* \[Vim mode] Paragraph text objects are now supported, e.g. `dip` to delete a paragraph.
* \[Vim mode] In terminal mode, press `K` over part of a command to inspect it.
* Agent notifications now reference conversations’ titles instead of their queries.
**Bug Fixes**
* The copy link button now works as expected after shared sessions have been closed.
### 2025.11.05 (v0.2025.11.05.08.12)
[Section titled “2025.11.05 (v0.2025.11.05.08.12)”](#20251105-v0202511050812)
**New Features**
* From the code review panel, add file diffs or the entire diff set as context to an agent conversation.
**Improvements**
* Warp now defaults to requiring approval before the agent will execute a command.
* Shared session links will open in a new tab by default, rather than a new window.
* Display summarization tokens when conversation summarization is triggered.
### 2025.10.29 (v0.2025.10.29.08.12)
[Section titled “2025.10.29 (v0.2025.10.29.08.12)”](#20251029-v0202510290812)
**Improvements**
* Display conversation summaries when summarization is triggered.
* Added completions for the Oz CLI.
* Updated community links from Discord to Slack throughout the app.
**Bug Fixes**
* Reduce padding on restored Agent Mode blocks and expanded shell commands.
* Add support for delete key in vim mode in code editors.
* Fix rendering for multi-line Agent Mode shell commands.
### 2025.10.22 (v0.2025.10.22.08.13)
[Section titled “2025.10.22 (v0.2025.10.22.08.13)”](#20251022-v0202510220813)
**New Features**
* Warp will suggest new unit tests in addition to code fixes via Suggested Code Banners
**Improvements**
* Fixed an issue where the model specs menu would get cut off.
**Bug Fixes**
* Fixed the close icon from becoming too small on the Warp Drive notebook viewer.
* Fixed an issue where the CLI would report invalid debug IDs in its troubleshooting output.
### 2025.10.15 (v0.2025.10.15.08.12)
[Section titled “2025.10.15 (v0.2025.10.15.08.12)”](#20251015-v0202510150812)
**New Features**
* Warp now supports scaling the entire application. Change the zoom level in `Settings > Appearance > Window` or by pressing `CMD-+` on macOS or `CTRL-+` on Windows / Linux.
**Improvements**
* The code review pane can now show diffs against other base branches.
* Added confirmation dialog when cancelling AI summarization requests.
* You can now expand Suggested Code Diffs further on down arrow.
* Restore closed panes using `CMD-SHIFT-T` or `CTRL-ALT-T` on Windows / Linux within 60 seconds of them being closed.
* Added shell completions for the Oz CLI.
* Warp Drive Environment Variables are now supported for Warp for Windows (PowerShell, Git Bash, and WSL).
* Enriched the model picker to include detailed specs of each model’s intelligence, speed and cost.
**Bug Fixes**
* Fixed the custom window size setting not reliably applying on startup.
### 2025.10.08 (v0.2025.10.08.08.12)
[Section titled “2025.10.08 (v0.2025.10.08.08.12)”](#20251008-v0202510080812)
**Improvements**
* Added the ability to sort team members by usage in `Settings > Billing and usage`.
* Added UI indication of when Agent Mode conversation summarization is in progress, with a cancellation confirmation dialog.
* Made the sizing for headings consistent across all collapsible blocks.
* `@` menu no longer appears when running JS package manager subcommands, like `yarn workspace @org/package add`.
* \[macOS] Resolved an issue re-mapping keybindings that conflict with macOS keybindings.
**Bug Fixes**
* Agent Mode requested command previews now only show the first line of multi-line commands.
* Removed misleading “auto-approve” button while Warp is generating a fix for failed terminal commands.
### 2025.10.01 (v0.2025.10.01.08.12)
[Section titled “2025.10.01 (v0.2025.10.01.08.12)”](#20251001-v0202510010812)
**Improvements**
* Editing suggested file changes now takes place in the same pane, instead of a new tab.
* When using the `@` context menu outside of a repo, current folder’s contents are now listed.
* The code mode file picker will now display gitignored files.
* \[macOS] Warp now stores session restoration data in a more-secure application container.
### 2025.09.24 (v0.2025.09.24.08.11)
[Section titled “2025.09.24 (v0.2025.09.24.08.11)”](#20250924-v0202509240811)
**New features**
* You can now create new files directly in Warp. Search “New File” in the Command Palette. macOS users can find it in the app menu under “File”.
**Improvements**
* Change the “Reject” label to “Refine” for code diffs and plans. They’re functionally the same, though we think this will clear up some confusion over what hitting “Reject” will do.
* Added realtime form validation to Environment Variables when secret redaction is enabled.
* Avoid showing the `@` context completions menu when typing a package name. This covers common installers for JS, Python, Ruby, Go, PHP, and more.
* Add an “auto-approve” option with a keyboard shortcut for requested commands and MCP tool calls. This makes it easier to accept a command and auto-approve future commands in a single button.
**Bug fixes**
* Fixed error with fish shell v4.
* Avoid showing multiple “stopped task” banners when toggling a resumed conversation back to stopped before the agent begins responding.
* Fix input problems with Russian on PowerShell.
### 2025.09.17 (v0.2025.09.17.08.11)
[Section titled “2025.09.17 (v0.2025.09.17.08.11)”](#20250917-v0202509170811)
**New Features**
* Warp agents are now available via the command line. See the [CLI reference](/agents/cli/oz-cli/).
* Added support for custom Regex names in Enterprise Secret Redaction.
**Improvements**
* The @ context menu can now be activated outside of Git repositories (for actions such as attaching blocks/workflows), when in autodetection or AI input mode.
* move the auto-approve button alongside the agent “stop” button for easier access.
* Move the “stop” button alongside the “Warping…” indicator. This restores the “stop” button to classic input users, and offers a more intuitive experience for universal input users.
* Added right-click context menu to code review pane with split pane controls.
* Files selected in the file tree now open in a preview mode until interacted with.
* Warp’s agent now shows reasoning traces from reasoning models.
* Ctrl-c during a long running command run by the agent will also stop the agent, not just the command.
**Bug Fixes**
* Fixed nested lists in agent markdown output sometimes not rendering properly.
* Fix slow scrolling on macOS Tahoe.
* Fix todo lists overflowing off of the screen for 10 or more items.
* Fix code review maximize button appearing outside of split pane mode.
* Fix the stop button unexpectedly disappearing when accepting the “start a new conversation” suggestion.
### 2025.09.10 (v0.2025.09.10.08.11)
[Section titled “2025.09.10 (v0.2025.09.10.08.11)”](#20250910-v0202509100811)
**Improvements**
* Added support for ignoring input suggestions. Click the X next to an item in your up-arrow history menu to hide that from showing up again. You can also enable the `Show autosuggestion ignore button` setting to add an X to autosuggestions directly in your input.
* Git UI detects more changes in git worktrees.
* You can now rename/delete items in the file picker and open them with the system file explorer.
* Combine “refine” and “cancel” buttons into a single “reject” button. This lets you give feedback on code diffs, commands, and plans with a single button.
* You can now switch node versions by clicking on the node version chip.
* Added a “New Agent” button to the agent management panel to start a new agent conversation more easily.”
**Bug fixes**
* Fixed an issue where agent output in a code block could be inserted at the wrong place.
* Fixed code review diff buttons incorrectly receiving mouse events.
* Avoid auto-expanding an agent’s requested commands while you are using voice dictation.
* Add back the auto-approve button for classic input mode.
* Fixed keyboard navigation of chip menus in the input while an agent is running.
* Properly reset context when user sends query to agent.
### 2025.09.03 (v0.2025.09.03.08.11)
[Section titled “2025.09.03 (v0.2025.09.03.08.11)”](#20250903-v0202509030811)
**Improvements**
* Added support for rendering H4-H6 in markdown.
### 2025.09.01 (v0.2025.09.01.20.54)
[Section titled “2025.09.01 (v0.2025.09.01.20.54)”](#20250901-v0202509012054)
**New features**
* Revert diff hunks directly from the Code Review Pane.
* Add lines of a file to the context of a conversation from the Warp code editor.
* You can now search and restore Agent conversations in your history using the `conversations:` prefix.
* You can now search and navigate to indexed codebases using the `repos:` prefix.
**Improvements**
* Voice transcriptions are no longer cut off when unfocusing an input editor.
* You can now select the $EDITOR environment variable as the default application for opening file links.
* Added new header treatment for unfocused Warp windows.
* \[macOS] A new dock icon option to celebrate Code Country - the Cow icon! (`Appearance > Icon` to change)
* Pasting images in the terminal input switches to Agent Mode and attaches the image as context.
* Added support for the Streamable HTTP transport for MCP servers.
**Bug fixes**
* \[Windows/Linux] Fixed keybinding conflict for split pane down action for the Input, when a code diff is not active.
* Fixed tab tooltips displaying unwanted leading and trailing whitespace.
* Pressing the up key while the model picker is open no longer opens the command history. Opening the model picker while the command history is open now closes the command history.
### 2025.08.27 (v0.2025.08.27.08.11)
[Section titled “2025.08.27 (v0.2025.08.27.08.11)”](#20250827-v0202508270811)
**New Features**
* [Agent Profiles](/agents/capabilities/agent-profiles-permissions/#agent-profiles): define how your agent operates.
* New pane to view changes to a Git repository.
* Files now open in a tabbed viewer.
* Syntax highlighting for Scala files in Warp.
**Bug Fixes**
* Fix paths not inserted when pasted images are not attached.
### 2025.08.20 (v0.2025.08.20.08.11)
[Section titled “2025.08.20 (v0.2025.08.20.08.11)”](#20250820-v0202508200811)
**New features**
* [Suggested Code Diffs](/agents/local-agents/active-ai/#suggested-code-diffs) - Warp now intelligently suggests the appropriate fixes for any simple errors encountered in the command line e.g. compiler errors. Head to `Settings > Active AI` to toggle this feature.
**Improvements**
* Added setting to hide fixed prompt suggestions.
* Updated default input type from ‘Classic’ to ‘Universal’.
* Improve the styling and usability of tabs for narrow windows.
**Bug fixes**
* Fix failures to start zsh sessions when using prezto.
* The agent status indicator no longer disappears while a command is running.
* Selecting a workflow will correctly close the workflows menu.
* Don’t auto-attach image if file pasted as plaintext.
* Fixed issue with drag-drop images.
* Fixed display of completions that may have included special characters.
### 2025.08.13 (v0.2025.08.13.08.12)
[Section titled “2025.08.13 (v0.2025.08.13.08.12)”](#20250813-v0202508130812)
**New Features**
* Agent Mode now displays interactive code blocks when referencing snippets from your codebase. You can easily copy the snippet, add the snippet as Agent Mode context, or open the file in Warp’s built-in editor.
* Agent Mode now creates and tracks task lists for more complex workflows. See [Agent Task Lists](/agents/capabilities/task-lists/).
* Added support for defining project-scoped rules with a WARP.md file. See [Rules](/agents/capabilities/rules/#project-rules).
* Added Slash Commands (/) in Agent Mode or Auto-Detection Mode to quickly run built-in actions or saved prompts without leaving the input field. See [Slash Commands](/agents/capabilities/slash-commands/).
**Improvements**
* Added syntax highlighting for SQL in Warp’s code editor.
* Added button to dismiss suggestions footer.
* \[Linux and Windows] Added support for drag-dropping multiple images.
* New files in Warp open in a pane by default. You can customize this behavior via `Settings > Features > General > Choose a layout to open files in Warp`, where you can switch between opening files in a pane or a new tab.
* Input stays in Agent Mode after an image is attached, instead of switching to shell mode.
**Bug Fixes**
* Fixed behavior when clicking Agents chip in Classic input mode.
* Repository-scoped Warp features are now available in git worktrees.
* Fixed drag-drop of images for long-running commands (eg Claude Code, vim).
* \[Linux and Windows] Fixed attaching images from pasted files.
* Fixed “Find in selected block” feature after clicking on an active running block.
* Fixed text overlap on narrow panes with Classic Warp Prompt with Same Line Prompt.
* \[macOS] Fixed a bug that would cause text to disappear for very long Agent Mode prompts.
### 2025.08.06 (v0.2025.08.06.08.12)
[Section titled “2025.08.06 (v0.2025.08.06.08.12)”](#20250806-v0202508060812)
**New Features**
* GPT-5 is now available to all users. Use the model selector in the input bar to try it yourself.
* \[macOS] Added the ability to attach images as context by drag-and-dropping them or pasting from your clipboard.
**Improvements**
* You can now open any files within Warp’s editor (including txt/csv files)!
* Warp can now edit Bazel files.
* Warp can now edit `.bashrc` and `.zshrc` files.
* Added `Always show secrets` to Secret Redaction for a less obtrusive secret redaction mode.
* Added reset time to the Billing and usage menu.
**Bug Fixes**
* Fix fish version <= 3.7 when vi keybindings were activated.
* Fixed bug affecting the “Open in Markdown Viewer by default” setting, you can use this setting to determine whether you’d like to view/edit MD files in Warp by default.
* Fixed an issue where typeahead for the next command could be lost if you typed really quickly after hitting enter on the previous command.
* Resolved an issue where stopping voice recording via the button would interrupt transcription.
### 2025.07.30 (v0.2025.07.30.08.12)
[Section titled “2025.07.30 (v0.2025.07.30.08.12)”](#20250730-v0202507300812)
**New Features**
* You can now set a configurable block size limit for higher scrollback limits! Head to `Settings > Features > Session > Maximum rows in a block` to configure.
* \[Linux] Added support for pasting images as context.
**Improvements**
* The “Open in Warp” banner now supports code files.
* When using Agent Mode, user-configured redaction rules are now applied to the contents of diffs and files, in addition to terminal blocks.
* Add SHIFT-ENTER keybinding. Claude Code users can use this to add linefeeds to their prompt.
* Added an overflow menu button in the top right of AI blocks for copying contents.
**Bug Fixes**
* Deleted files no longer appear in the @-context selection box.
* Users with Turkish locale will no longer see an extra letter “i” between commands.
* \[Windows] Restored windows will no longer be positioned with the title bar above the top of the display.
### 2025.07.23 (v0.2025.07.23.08.12)
[Section titled “2025.07.23 (v0.2025.07.23.08.12)”](#20250723-v0202507230812)
**New Features**
* \[Windows] Added support for pasting images from Clipboard into Agent Mode context.
**Improvements**
* Added image filename when pasting images into Agent Mode context.
* Added support for restarting MCP servers when Warp restarts.
* Added support for copying AI block and conversation contents via the context menu.
* Added Node.js prompt chip.
**Bug Fixes**
* Fixed a bug where attaching a block as AI context would reset the input state.
* Fixed a spacing issue with horizontal scrollbars in agent planning view.
* Added support for auto-expanding manually executed Agent Mode suggested commands.
* Fixed a bug where Warp would hang while updating code symbols in the @-context menu.
* Modified secret redaction regexes to be case sensitive. Use a `(?i)` prefix to make your regex case insensitive.
* Modified the Universal Input to no longer exit a conversation via “backspace”.
### 2025.07.16 (v0.2025.07.16.08.12)
[Section titled “2025.07.16 (v0.2025.07.16.08.12)”](#20250716-v0202507160812)
**New Features**
* \[macOS] Support pasting images from clipboard into Agent Mode context.
* Migrated Warp’s built-in set of Secret Redaction regexes into user’s regexes, giving users more fine-grained control over their secret redaction.
* Added support for Find and Replace using `CMD-F` when viewing diffs or editing files in the built-in code editor.
**Improvements**
* Removed lock icon from Secret Redaction in favor of asterisks when ligatures are enabled.
* Added individual keybinding shortcuts to change input modes.
**Bug Fixes**
* Fixed an issue where the hover tooltip for disabled prompt suggestions either didn’t render at all or was incredibly hard to read.
* Fixed the background color of inline code in restored AI blocks.
### 2025.07.09 (v0.2025.07.09.08.11)
[Section titled “2025.07.09 (v0.2025.07.09.08.11)”](#20250709-v0202507090811)
**New Features**
* New secret redaction strikethrough UI. Comes with new `Settings > Privacy > Hide secrets in block list` setting that defaults to off.
**Improvements**
* You can now resume stopped AI conversations: `CTRL-C` to stop and `CMD-SHIFT-R` to resume on macOS or `CTRL-SHIFT-R` on Windows and Linux.
* Code Diff view’s default Edit and Revise keybindings changed and made configurable.
* Added syntax highlighting for PowerShell, Kotlin and Swift.
**Bug Fixes**
* Fixed an issue with `.inc` file chunking.
* Clicking on an active, long running block will no longer select the block, but focus the input.
### 2025.07.02 (v0.2025.07.02.08.36)
[Section titled “2025.07.02 (v0.2025.07.02.08.36)”](#20250702-v0202507020836)
**New features**
* Tab close button can now be set to the left.
**Improvements**
* Added syntax highlighting for TOML, PHP, Lua, Ruby, and Groovy (with Java syntax).
* Added conda chip support to new Universal Input prompt.
* Increased color contrast on tabs.
* Added “Upgrade” menu item for free users and “Billing and Usage” menu item for paid users in the user menu for easier access to subscription management.
**Bug fixes**
* When AI is disabled, ESC should no longer enter Agent Mode.
* Fixed an issue on WSL where files created by Agent Mode would have CRLF line endings.
* \[macOS] Tweaked autoupdate logic to more reliably remove old applications off disk.
* Fixed “Manage plan suggestion setting” link.
### 2025.06.25 (v0.2025.06.25.08.12)
[Section titled “2025.06.25 (v0.2025.06.25.08.12)”](#20250625-v0202506250812)
**New Features**
* Git branch and directory chip now are searchable.
**Improvements**
* Added support for HCL syntax highlighting in Terraform files.
**Bug Fixes**
* Fixed potential crash when displaying context chips with Unicode characters in file paths.
* Fixed a rendering issue with line numbers in suggested diffs.
* Attach context chip no longer appears if there is no context you can attach.
### 2025.06.20 (v0.2025.06.20.22.47)
[Section titled “2025.06.20 (v0.2025.06.20.22.47)”](#20250620-v0202506202247)
**New Features**\
\
**Warp 2.0 is here - The Agentic Development Environment**
Built from the ground up for agentic workflows, Warp is the most powerful tool for prompting, coding, and collaborating with multiple agents.
**Multithread yourself with agents**
* Launch intelligent tasks (agents) with a prompt. Agents gather context using CLI commands, MCP, Warp Drive, and Codebase Context.
* New Agent Management Panel to monitor, multitask, and intervene across multiple agents.
* Set autonomy controls and get notified when agents need your help.
**A state-of-the-art coding platform**
* 70% on SWE-bench, #1 on Terminal-Bench — the highest quality coding agent available.
* Codebase Context: Warp indexes and understands your codebase, allowing you to debug and write code faster without storing any code on Warp’s servers.
* Review and edit diffs directly in Warp’s native code editor.
**Still a great command-line**\n-
* A new Universal Input: run commands or prompt agents from a single interface. Lock into command mode or Agent Mode, or let Warp detect automatically.
* Choose your model, continue a conversation, attach images, link URLs, or reference files using `@`.
* Modern, IDE-like terminal experience with completions, predictions, and mouse support, all built natively in Rust for performance.
**Context for your teammates and agents**
* A knowledge store where you can configure MCP, define Rules, and store shared commands, notebooks, env vars, and prompts as context.
All of this comes with higher AI usage limits on our Pro and Turbo plans, plus new pay-as-you-go overages for continued access to premium models.\
\
**Watch the full Warp 2.0 launch event →** [**Warp 2.0 launch event**](https://www.warp.dev/blog/reimagining-coding-agentic-development-environment)
### 2025.06.11 (v0.2025.06.11.08.11)
[Section titled “2025.06.11 (v0.2025.06.11.08.11)”](#20250611-v0202506110811)
**New Features**
* You can now attach images as context for Agent Mode! Simply use the image icon and select the files you wish to attach.
**Improvements**
* \[Linux] Added support for standard installed Zed and Zed Preview as default code editors.
* \[macOS] Added support for Zed Preview as a default code editor.
* Added syntax highlighting support for TSX and JSX.
* Increased visibility of non-focused diff hunks when navigating diffs.
* New Agent Mode output will no longer force-scroll.
**Bug Fixes**
* Fixed keybinding being missing for editing requested commands.
* Removed keybindings for zero-state prompt suggestions, to avoid conflicting with tab switching keybindings.
### 2025.06.04 (v0.2025.06.04.08.11)
[Section titled “2025.06.04 (v0.2025.06.04.08.11)”](#20250604-v0202506040811)
**New Features**
* Sonnet 4 is now an available model (enabled by default in the “auto” model).
**Improvements**
* Press the hovering fast-forward button to auto-execute all Agent actions until the task completes.
* Added ability to share session via `RIGHT-CLICK` on tab.
* You can now give the Agent permission to auto-execute MCP tool calls.
**Bug Fixes**
* Fixed an issue where Agent Mode would sometimes not find untracked files in Git repos.
* Fixed Agent Mode file editor randomly scrolling to the first line of a file.
### 2025.05.28 (v0.2025.05.28.08.11)
[Section titled “2025.05.28 (v0.2025.05.28.08.11)”](#20250528-v0202505280811)
**New Features**
* Added MCP server support. It’s now possible to extend Agent Mode’s capabilities using programs that support the [Model Context Protocol](/agents/capabilities/mcp/).
### 2025.05.21 (v0.2025.05.21.08.11)
[Section titled “2025.05.21 (v0.2025.05.21.08.11)”](#20250521-v0202505210811)
**New Features**
* Set new Agent Mode permissions around executing commands, reading files, coding, and planning in AI settings.
**Improvements**
* You can now choose the coding model behind Agent Mode.
* Agent Mode conversations can now be paused via a hovering control panel in the right corner.
* Improved maximum block output capacity to 50k lines.
**Bug Fixes**
* Fix edit icon positioning for shared sessions.
### 2025.05.14 (v0.2025.05.14.08.11)
[Section titled “2025.05.14 (v0.2025.05.14.08.11)”](#20250514-v0202505140811)
**Improvements**
* Introduced refining functionality for requested commands.
* Added ability to continue previous Agent Mode conversations directly from response blocks.
* Overhauled the editing experience for suggested plans.
* Renamed input auto-detection setting to natural language detection in Command Palette for better clarity.
* Zero-state prompt suggestion chips are now horizontally clipped instead of being individually shrunk.
**Bug Fixes**
* Fixed incorrect ordering in history of executed commands and Agent Mode queries.
* Copying text from Agent Mode plans and suggested code changes now works more reliably.
* \[Windows] Made some changes to reduce false-positives from virus scanners.
### 2025.05.07 (v0.2025.05.07.08.12)
[Section titled “2025.05.07 (v0.2025.05.07.08.12)”](#20250507-v0202505070812)
**Improvements**
* Redesigned env var collection block UX.
* Added ability to embed Warp Drive Prompts inside Notebooks.
* Added AI block loading animation.
* Added ability to select and continue previous Agent Mode conversations.
* \[macOS] Improved time to update and relaunch Warp.
**Bug Fixes**
* Fixed a bug where escape was clearing autosuggestions in Vim’s insert mode.
* Stopped showing an unexpected block in the planning output for o3.
* \[Windows] Fixed a bug when hovering symlinks in WSL sessions.
* Fixed terminal input remaining hidden after cancelling an env var block.
* Prevented unexpected empty code fences in Agent Mode when using Gemini 2.5 Pro or o3.
### 2025.04.30 (v0.2025.04.30.08.11)
[Section titled “2025.04.30 (v0.2025.04.30.08.11)”](#20250430-v0202504300811)
**New Features**
* Added desktop notifications for Agent Mode. Now, you can be notified when an agent completes a task, or when an agent needs your attention to continue (i.e. to review a command, to run an unsafe command, etc). You can configure these settings from `Features > Notifications`.
**Improvements**
* Agent Mode is now more robust at applying code diffs.
* Redesigned requested commands UX.
* Improved readability for “needs password prompt” desktop notifications.
### 2025.04.23 (v0.2025.04.23.08.11)
[Section titled “2025.04.23 (v0.2025.04.23.08.11)”](#20250423-v0202504230811)
**Improvements**
* Restored Agent Mode conversations can now be continued.
* Agent Mode now has access to a filepath search tool for coding tasks.
* Improved the reliability and positioning of suggestion dialogs for rules and Agent Mode workflows.
* We reworked the Command Palette search to make it more useful.
**Bug Fixes**
* Fix XML parse errors complaining that a “thought” cannot be empty.
* \[Windows] Fixed an issue where Agent Mode would fail to search when in WSL or Git Bash.
* Show “copy” button and other text selection tools when right clicking selected environment variable text.
* Fixed old shortcuts icon appearing in new tab page, if recommended AI prompts are disabled.
* Fish commands containing syntax errors now correctly “finish” the block.
### 2025.04.16 (v0.2025.04.16.08.11)
[Section titled “2025.04.16 (v0.2025.04.16.08.11)”](#20250416-v0202504160811)
**New features**
* After editing a code diff, you will now be returned to your original Agent Mode conversation.
* Commands with certain invalid arguments will no longer be suggested, such as file paths, git branches, and docker images.
* \[Windows/Linux] You can now open launch configurations in the current window with `SHIFT-ENTER` or `CTRL-ENTER` on the Command Palette.
* Added more default regexes for Secret Redaction, pertaining to AI API keys.
* Typing `ESC` in the terminal input editor now clears any Autosuggestions.
**Bug Fixes**
* Fixed issue with rendering performance for file links in AI output.
* Fixed an issue that causes Warp to crash when Agent Mode outputs broken links.
* New tab page no longer falls back to email if display name is not set.
* Fixed prompt chips not being clickable in new session with prompt pinned to top.
* Agent Mode now properly greps for queries containing double quotes.
### 2025.04.09 (v0.2025.04.09.08.11)
[Section titled “2025.04.09 (v0.2025.04.09.08.11)”](#20250409-v0202504090811)
**New features**
* Recommended AI prompts are shown in new tabs, go to Settings > Features to disable.
**Improvements**
* Agent Mode is now better at searching for exact function / symbol / etc. names in your code.
* Fix text selection for environment variable blocks.
* You can now attach select text in a code block as the Agent Mode context.
* Warp now supports marked text in the IME (non-English keyboards).
* Make text selectable for non-expandable command outputs (ex. failed agent tasks).
* Zero-state chips are no longer shown when entering AI input with a non-empty input buffer.
**Bug fixes**
* Fixed a bug that prevented copying of selected text of a code block when Agent Mode is enabled.
* Fixed a bug that allows a selection in the code block and a selection on the text simultaneously.
* \[macOS] Fixed shells installed via Homebrew not appearing in the list of available shells.
### 2025.04.02 (v0.2025.04.02.08.11)
[Section titled “2025.04.02 (v0.2025.04.02.08.11)”](#20250402-v0202504020811)
**New features**
* Get early access to unreleased and experimental features with [Warp Preview](https://docs.warp.dev/support-and-community/community/warp-preview-and-alpha-program).
**Improvements**
* Improved login item management to respect when users manually remove Warp from login items in System Preferences.
* The input editor now supports `CMD-SHIFT-UP/DOWN` on macOS or `CTRL-SHIFT-HOME/END` on Windows/ to move and select to the top/bottom of the text buffer.
* Removed 3-hour conversation timeout, allowing AI conversations to remain active indefinitely.
* Show a small popup when users who are at AI limits have their quota reset.
* Display a notification when AI request quota resets after hitting the limit in the previous billing cycle.
* \[Windows] Added “Open Warp in new tab / window” item for folders in the File Explorer context menu under “Show more options”.
**Bug fixes**
* Minor fixes for iTerm and Kitty images.
* Fixed regression related to using keyboard shortcuts to navigate a command in an empty split pane.
* Fixed some issues with Agent Mode failing to read files.
* Click targets in scroll views should more reliably click while moving the mouse.
* \[Linux] Window corners are correctly rounded with themes having background images.
* Fix a few common failure modes for Agent Mode response deserialization errors.
### 2025.03.26 (v0.2025.03.26.08.10)
[Section titled “2025.03.26 (v0.2025.03.26.08.10)”](#20250326-v0202503260810)
**New features**
* Kitty Image Protocol is now supported on macOS and Linux!
**Improvements**
* Agents may suggest using Dispatch to create a plan for complex tasks. You can disable suggestions to create plans under `Settings > AI > Dispatch`.
* You can now resume auto-execution of a previously dispatched plan if your follow-up query is set to “Dispatch”, instead of creating a new plan.
* Added a keyboard shortcut to accept the most recent command correction.
* Zero-state suggestions are no longer shown when using a saved Prompt or past AI query.
* Tabs will not resize while hovered, making closing multiple tabs easier.
* The warning dialog for closing sessions now responds to the `ENTER` and `ESC` keys.
* Selected text within Agent responses can now be copied via the `RIGHT-CLICK` menu.
* \[Windows/Linux] You can now toggle whether a block is selected using `CTRL+CLICK`.
**Bug fixes**
* Fixed an issue that caused Agent Mode blocks to be incorrectly highlighted when performing rectangular selection.
* Fixed an issue where duplicate cloud preferences could be created during sync operations.
* Fixed keyboard shortcut padding for prompt suggestions.
* Fixed color contrast issues with light themes for the Pair & Dispatch chip in Prompt Editor.
* Agent Mode will no longer default to Windows-style line endings when creating a new file on macOS or Linux.
* PowerShell sessions will start even if the profile has a terminating error.
* The numpad `ENTER` key now behaves like the `ENTER` key in Agent Mode.
* \[macOS] Fixed a scenario where Warp would beachball while updating.
* \[Windows] In WSL, show completions for symlinked files.
* \[Windows] Fixed completions with `.exe` suffixes.
* \[Windows] Fixed setting Git Bash custom shell paths.
### 2025.03.12 (v0.2025.03.12.08.02)
[Section titled “2025.03.12 (v0.2025.03.12.08.02)”](#20250312-v0202503120802)
**New features**
* Agent Mode output is now rendered with Markdown formatting.
* You can now change the font used for Agent Mode output (Settings > Appearance).
**Improvements**
* \[Windows] Significantly improved pseudoconsole throughput (\~3x improvement).
* The Agent Mode model will now automatically select the best model based on your specific task.
* Ordered lists in Markdown now uses alphabetical or Roman numeral labels when nested.
* \[Windows] We now search more locations for a PowerShell executable.
* Reduced the size of Markdown headings.
**Bug fixes**
* Control whether Warp starts at login via a setting under Settings > Features > Start Warp at login (macOS only).
* \[Windows] Fixed an issue where dynamic enums commands weren’t being executed.
* Fixed a bug with the mouse cursor when hovering over buttons.
* Fixed a bug that causes high CPU load with Codebase Context.
### 2025.03.05 (v0.2025.03.05.08.02)
[Section titled “2025.03.05 (v0.2025.03.05.08.02)”](#20250305-v0202503050802)
**New features**
* iTerm Image Protocol is now supported on macOS and Linux!
* \[macOS] Warp now starts at login (can be disabled in System Settings > Login Items & Extensions).
**Improvements**
* Input mode automatically returns to command mode when a command is detected in an AI follow-up request. (Only applies if natural language detection is turned on.)
* Text selections can now be attached to Agent Mode queries as context.
* \[Windows] Window transparency now works when using DirectX 12.
* \[Windows] Added “Open Warp Here” item for folders in the File Explorer context menu under “Show more options”.
**Bug fixes**
* Fixed an issue where `bazel` completions could use up a lot of CPU.
* \[macOS] Fixed a regression where the title bar would be transparent in fullscreen windows.
* \[Windows] Fixed children of shell processes not always exiting properly at shell termination.
* \[Windows] Fixed Warpification for custom-built WSL distributions.
* \[Windows] Fixed Ctrl-Up and Ctrl-Down shortcuts not working in alt screen programs (e.g. vim and emacs).
* \[Windows] Fixed last line of output getting truncated with some prompt configs in WSL.
* \[Windows] Fixed some hangs when using Agent Mode.
* \[Windows] Fixed issues starting PowerShell in strict mode.
* \[Windows] Fixed an issue where `.` would turn into n in ZSH when using ohmyzsh in WSL with an Italian keyboard layout.
### 2025.02.26 (v0.2025.02.26.08.02)
[Section titled “2025.02.26 (v0.2025.02.26.08.02)”](#20250226-v0202502260802)
**New features**
* Warp is now available for Windows! See our [Quickstart Guide](/getting-started/quickstart/installation-and-setup/#install-warp)
* Prompt, plan, and execute fully autonomous tasks from [Agent Mode with Dispatch](/agents/local-agents/interacting-with-agents/) (Beta)
* Add Codebase Context support to Agent Mode. Currently enabled for Git repositories only.
* \[macOS] You can now customize your [App Icon](https://docs.warp.dev/terminal/appearance/app-icons) in `Settings > Appearance > Icon`.
* Create and store [Rules](/agents/capabilities/rules/) to use as Agent Mode context.
* Show default suggestions in Agent Mode input.
**Bug fixes**
* Multicursor input is now `ALT` on Linux and Windows.
* Fix prompt chip misalignment for certain fonts.
* Autosuggestions remain visible when the input is not focused, to prevent height flickering when the autosuggestion soft wraps.
### 2025.02.19 (v0.2025.02.19.08.02)
[Section titled “2025.02.19 (v0.2025.02.19.08.02)”](#20250219-v0202502190802)
**New features**
* Create and store AI memories to use as Agent Mode context.
**Improvements**
* Expanded Prompt Suggestions to cover more use cases.
**Bug fixes**
* Fixed Warp Prompt clipping issues encountered with certain fonts.
* Fixed inverse and double-underline cell styling not persisting through session restoration.
### 2025.02.12 (v0.2025.02.12.16.51)
[Section titled “2025.02.12 (v0.2025.02.12.16.51)”](#20250212-v0202502121651)
**New features**
* `CTRL-TAB` is now configurable under `Settings > Features` to cycle between the most recently used sessions rather than just activating the next tab.
**Improvements**
* The LLM menu is now keyboard-navigable.
**Bug fixes**
* Clearing Blocks now also clears any active Prompt Suggestions.
* Fix Kali Linux `.bashrc` breaking Warp.
* Fix bug with Agent Mode in PowerShell sessions with multi-line commands.
* Fixed a bug that prevented Autosuggestions from being accepted and Agent Mode model from being selected while up arrow history was open.
* Fixed cases where dragged Warp tabs would get stuck.
* Restores subshell Warpification script.
* \[macOS] Fix hotkey keybinding not triggering on non-US keyboard input source.
### 2025.02.05 (v0.2025.02.05.08.02)
[Section titled “2025.02.05 (v0.2025.02.05.08.02)”](#20250205-v0202502050802)
**New features**
* You can now talk to Warp to transcribe Agent Mode prompts or any other text! Set up the hotkey in `Settings > AI > Voice` or use the microphone button in AI input mode to trigger this.
**Improvements**
* Autosuggestions in the input now soft-wrap.
* You can now attach default environment variables to a workflow.
### 2025.01.29 (v0.2025.01.29.08.02)
[Section titled “2025.01.29 (v0.2025.01.29.08.02)”](#20250129-v0202501290802)
**New features**
* Added support for DeepSeek R1 and V3 in Agent Mode! Try them out by switching to Agent Mode and clicking on the model name in the prompt.
* Agent Mode can now auto-execute readonly requested commands. Commands can also be explicitly allowlisted or denylisted. See `Settings` -> `AI` -> `Autonomy` to configure.
**Improvements**
* You can now use `j`/`k` keys to navigate up and down Warp Drive.
* Agent Mode chip added to Warp prompt.
* Next Command is preferred over Command Corrections in cases where Corrections has less confidence.
* Moved the Settings modal to its own tab.
**Bug fixes**
* Fixed a bug that caused double-clicking to select the incorrect range of text when non-ASCII characters are present.
* Saving workflow aliases no longer deletes aliases from other workflows.
* Fixed cases where a small part of the bottom of the editor would be cut off at certain appearance settings.
### 2025.01.22 (v0.2025.01.22.08.02)
[Section titled “2025.01.22 (v0.2025.01.22.08.02)”](#20250122-v0202501220802)
**New features**
* Generate input for any interactive CLI using ⌘I on macOS and Ctrl-Shift I on Linux.
* You can now dynamically populate arguments in Workflows with shell commands.
* Added support for rectangular selection when holding ⌘⌥ on macOS and Ctrl-Alt on Linux.
**Improvements**
* Settings are now searchable and rendered in a separate tab
* Terminal font weight is now configurable.
* Launch Configurations now save the focused window state and active pane.
* Autosuggestions in the input now soft-wrap.
**Bug fixes**
* Fixed several issues where hovering over URLs in the blocklist sometimes resulted in URLs only being partially detected, or not detected at all.
* Fixed issue with Prompt Suggestions occasionally remaining visible after subsequent command execution.
* \[macOS] Changed the download location for new Warp updates to prevent corruption.
### 2025.01.15 (v0.2025.01.15.08.02)
[Section titled “2025.01.15 (v0.2025.01.15.08.02)”](#20250115-v0202501150802)
**New features**
* Font ligatures in grids! See setting under Settings > Appearance > Text to enable.
* You can now define aliases that expand to Warp Drive workflows.
**Improvements**
* Launch configurations now save focused tab state.
* Added support for Windsurf as an external editor.
* macOS-only: added a new AI app menu.
**Bug fixes**
* Fixed pane navigation when panes are not overlapping.
* Fixed a bug where Agent Mode LLM choices weren’t populated correctly upon logging in.
* Fixed bug with drag-and-drop files causing duplicated filepaths.
### 2025.01.08 (v0.2025.01.08.08.02)
[Section titled “2025.01.08 (v0.2025.01.08.08.02)”](#20250108-v0202501080802)
**New features**
* A percentage of Warp users may now enable cloud syncing of their Warp settings under `Settings` > `Account`. We are gradually enabling this feature for all Warp users starting in this release. See the [documentation](https://docs.warp.dev/terminal/more-features/settings-sync) for more information.
* Introduced a setting to hide the tab bar (Zen mode). See the [documentation](https://docs.warp.dev/terminal/appearance/tabs-behavior) for more information.
* Introduced new profile menu.
**Improvements**
* Removed the Command Corrections banner, as there’s already an autosuggestion in the input editor.
* Implemented `_`, `+`, and `-` motions in Vim mode.
* Warp will now show a warning before closing a session with a long-running process.
* Pasting multiple lines of content into the terminal’s `Find` feature will convert it into a single line of text, rather than hide previous lines.
* Titles of notebooks imported from Markdown files no longer end in `.md`.
* “What’s new” no longer shows on update.
* Added the ability to hide blocklist lines.
* Consolidated top bar navigation items.
* Settings are now in the profile menu.
* Scrollbars and pane controls only show on hover.
**Bug fixes**
* Fixed the rendering of keyboard shortcuts at larger font sizes.
* Tab completion menu now closes after selecting a single remaining suggestion.
* Warp displays an error if relaunching to apply an update failed.
* Old prompt suggestions won’t reappear when issuing AI queries rapidly or after clearing the blocklist.
* Accepting the ‘What happened here?’ autosuggestion no longer clears AI context blocks.
* `alt` key now sends meta control codes to the shell in long-running blocks and the alt screen.
* When secret redaction is disabled, secrets are not redacted in command corrections.
* \[macOS] Fixed a bug where assigning `cmd-shift-left` and `cmd-shift-right` to an action sometimes wouldn’t work.
### 2025.01.02 (v0.2024.12.18.08.02)
[Section titled “2025.01.02 (v0.2024.12.18.08.02)”](#20250102-v0202412180802)
**Improvements**
* We now immediately show an error when trying to Warpify unsupported shells over SSH.
**Bug fixes**
* Fixed blank lines being appended to some blocks on resize.
* Fixed an issue where the AI context disappears when accepting the default autosuggestion.
# Changelog — 2026
Canonical page: [/changelog/2026/](https://docs.warp.dev/changelog/2026/)
> Warp release notes for 2026. Updates ship weekly, typically on Thursdays.
Submit bugs and feature requests on our [GitHub board!](https://github.com/warpdotdev/Warp/issues/new/choose)
### 2026.09.30 (v0.2026.09.30.08.29)
[Section titled “2026.09.30 (v0.2026.09.30.08.29)”](#20260930-v0202609300829)
**Improvements**
* Added the option to switch teams from Settings > Teams
* Vertical tabs search now matches and highlights tab group names
* Added fzf Alt-C support across bash, zsh, and fish shell integrations
**Bug fixes**
* Fixed two windows opening when launching Warp on Windows
* Fixed model preference being reset when the team model catalog refreshes
* Fixed focus not being restored after closing a tab context menu
* Fixed the typed query not being forwarded to fzf Ctrl-R history search in zsh
* Fixed the layout of the external fzf Ctrl-R history picker
* Fixed flag completions after a POSIX double dash (—)
* Fixed agent management costs not honoring the Credits/Dollars setting
* Fixed a panic when `/model` targets a closed window
* Fixed scope-specific spend limit alerts
### 2026.09.23 (v0.2026.09.23.14.34)
[Section titled “2026.09.23 (v0.2026.09.23.14.34)”](#20260923-v0202609231434)
**New features**
* You can now sign in with ChatGPT to use your ChatGPT plan with Warp’s agent. Go to Settings > Agents > Warp Agent > Custom Inference to enable.
* Added support for AWS ECR credentials in managed secrets. ([#16044](https://github.com/warpdotdev/warp/pull/16044))
* Added a usage popover to the agent input footer showing conversation usage and cost. ([#15946](https://github.com/warpdotdev/warp/pull/15946))
**Improvements**
* Added Neovim 0.13 `al` and `il` text objects to Vim mode. ([#16105](https://github.com/warpdotdev/warp/pull/16105))
* Moved the team switcher next to the profile avatar for easier access. ([#16041](https://github.com/warpdotdev/warp/pull/16041))
**Bug fixes**
* Fixed missing file and path suggestions when native shell completion returns no candidates. ([#16093](https://github.com/warpdotdev/warp/pull/16093))
* Team discovery now shows native workspace options and workspace-scoped teams. ([#16083](https://github.com/warpdotdev/warp/pull/16083))
* Fixed usage displays showing $0.00 for very small charges instead of a minimum threshold value. ([#16070](https://github.com/warpdotdev/warp/pull/16070))
* Restored image pasting into CLI agents when macOS provides TIFF clipboard data. ([#16055](https://github.com/warpdotdev/warp/pull/16055))
* Fixed shared sessions getting stuck reconnecting when the connection closes or stalls before the server confirms reconnection. ([#16052](https://github.com/warpdotdev/warp/pull/16052))
* Fixed a crash when opening a child agent from its pill after closing and reopening the parent conversation. ([#15996](https://github.com/warpdotdev/warp/pull/15996))
**Oz updates**
* Cloud agent runs now save a handoff snapshot when interrupted (SIGTERM/SIGINT) so in-progress work can be resumed instead of lost. ([#15654](https://github.com/warpdotdev/warp/pull/15654))
* Agent runs with a zero post-completion idle timeout exit immediately. ([#16050](https://github.com/warpdotdev/warp/pull/16050))
### 2026.09.16 (v0.2026.09.16.08.27)
[Section titled “2026.09.16 (v0.2026.09.16.08.27)”](#20260916-v0202609160827)
**New features**
* You can now trigger fzf (ctrl-r or ctrl-t) and atuin if it’s set up with your shell. ([#15903](https://github.com/warpdotdev/warp/pull/15903))
* Added native shell completions alongside Warp’s built-in completion specs. By default, the native shell completions will be generated if Warp’s built-in completion has no suggestions. This can be changed in Settings > Features > Terminal Input. ([#15903](https://github.com/warpdotdev/warp/pull/15903))
**Improvements**
* Improved parallel clone error reporting to list only the repositories that actually failed. ([#16006](https://github.com/warpdotdev/warp/pull/16006))
* Added `oz secret create docker-registry` to create container registry credential secrets from the CLI. ([#15913](https://github.com/warpdotdev/warp/pull/15913))
* Discover and cache build tools in nested repository directories. ([#15844](https://github.com/warpdotdev/warp/pull/15844))
* Workspace admins can now remove members from a workspace directly from team settings. ([#15905](https://github.com/warpdotdev/warp/pull/15905))
* \[Windows] [Materials](https://learn.microsoft.com/en-us/windows/apps/design/signature-experiences/materials) are now supported for the backdrop of Warp windows in Settings > Appearance > Window > Backdrop. ([#15879](https://github.com/warpdotdev/warp/pull/15879))
* Improved command history search ranking using match quality and usage signals. ([#15903](https://github.com/warpdotdev/warp/pull/15903))
* Native workspace members can leave a team without losing workspace access. ([#15880](https://github.com/warpdotdev/warp/pull/15880))
* Native workspace users can browse and join another open team from Teams settings. ([#15881](https://github.com/warpdotdev/warp/pull/15881))
**Bug fixes**
* Fixed an issue where new users who quit sign-up partway could be shown the existing-user ‘Introducing universal agent support’ onboarding on their next launch. ([#16010](https://github.com/warpdotdev/warp/pull/16010))
* Stop Warp Agent CLI startup when team metadata cannot be refreshed. ([#15932](https://github.com/warpdotdev/warp/pull/15932))
* Add tab group persistence to (legacy) launch configs. ([#14624](https://github.com/warpdotdev/warp/pull/14624)) — [@maxmilian](https://github.com/maxmilian) ✨
* Fixed a crash after dragging a Settings tab between windows. ([#15948](https://github.com/warpdotdev/warp/pull/15948))
* Fixed cloud agent commits sometimes ignoring a customer’s `git config --global user.name/email` setup command. ([#15869](https://github.com/warpdotdev/warp/pull/15869))
* Prevented a crash when confirming a file discard more than once in Code Review. ([#15884](https://github.com/warpdotdev/warp/pull/15884))
* Opening a subagent in the web session viewer no longer replaces the run’s URL, so refreshing or sharing the link keeps you on the whole run instead of a single subagent. ([#15317](https://github.com/warpdotdev/warp/pull/15317))
* Stopping a shared Agent Mode conversation from a viewer or via conversation steering now interrupts the agent’s running command instead of letting it run to completion. ([#15906](https://github.com/warpdotdev/warp/pull/15906))
* Fixed a new tab group’s terminal stealing focus while its name was being typed, which saved the partially-typed name. ([#14895](https://github.com/warpdotdev/warp/pull/14895)) — [@maxmilian](https://github.com/maxmilian) ✨
* Fixed macOS computer-use recordings reporting near-zero duration. ([#15920](https://github.com/warpdotdev/warp/pull/15920))
* Fixed duplicate network requests when loading agent shared sessions. ([#15829](https://github.com/warpdotdev/warp/pull/15829))
**Oz updates**
* Fixed native Oz follow-up prompts interrupting one another instead of each reaching the agent. ([#15921](https://github.com/warpdotdev/warp/pull/15921))
* Preserved team-scoped credentials when launching orchestrated agent runs. ([#15863](https://github.com/warpdotdev/warp/pull/15863))
* Fixed follow-up messages with attachments waiting until an agent finished its turn instead of being delivered at the next steering opportunity. ([#16046](https://github.com/warpdotdev/warp/pull/16046))
### 2026.09.09 (v0.2026.09.09.08.26)
[Section titled “2026.09.09 (v0.2026.09.09.08.26)”](#20260909-v0202609090826)
**New features**
* First-class Grok Build (SpaceXAI `grok`) support. Detects sessions, adds branded chrome in the footer, and enables rich input mode. ([#14228](https://github.com/warpdotdev/warp/pull/14228)) — [@nwp](https://github.com/nwp) ✨
**Improvements**
* Create New Window is now an editable keyboard shortcut, so it can be remapped or unbound. ([#15771](https://github.com/warpdotdev/warp/pull/15771)) — [@tkossak](https://github.com/tkossak) ✨
* Added completions for `git merge-base`. ([#15769](https://github.com/warpdotdev/warp/pull/15769))
* Attach file is now a Command Palette action with an editable, unbound-by-default keybinding. ([#15762](https://github.com/warpdotdev/warp/pull/15762))
* Fish ctrl-r now hands off to PatrickF1/fzf.fish history search, not only junegunn fzf. ([#15744](https://github.com/warpdotdev/warp/pull/15744))
* Extended shell widget handoff to fzf’s ctrl-t file search, alongside the existing ctrl-r history-search handoff. ([#15513](https://github.com/warpdotdev/warp/pull/15513))
**Bug fixes**
* Fixed remote orchestration children launched by team service accounts requesting invalid personal ownership. ([#15866](https://github.com/warpdotdev/warp/pull/15866))
* Fixed unsent prompts being cleared after selecting a model through the `/model` keyboard shortcut. ([#15870](https://github.com/warpdotdev/warp/pull/15870))
* Fixed Agent API key creation requiring users to re-select the default agent. ([#15825](https://github.com/warpdotdev/warp/pull/15825))
* Fixed the prompt alert action for teamless native-workspace users who reach their limit. ([#15853](https://github.com/warpdotdev/warp/pull/15853))
* Hid team creation and empty team discovery prompts for teamless native-workspace users in Warp Drive. ([#15790](https://github.com/warpdotdev/warp/pull/15790))
* Teamless workspace users now see a clear Cloud Mode blocker instead of environment setup or a misleading agent-harness error. ([#15794](https://github.com/warpdotdev/warp/pull/15794))
* Fixed global file-based MCP tools that were missing from the first agent turn. ([#15755](https://github.com/warpdotdev/warp/pull/15755))
* Fixed dynamic Bash prompts being evaluated twice when Shell (PS1) is enabled. ([#15792](https://github.com/warpdotdev/warp/pull/15792))
* Fixed transcript persistence and skill discovery for third-party agent harnesses in single-repository cloud workspaces. ([#15787](https://github.com/warpdotdev/warp/pull/15787))
* Fixed a crash when a character at the end of a terminal line changes from single-width to double-width. ([#15763](https://github.com/warpdotdev/warp/pull/15763))
* Prevent a crash when smart-selecting RTL text whose visual glyph order reverses logical indices. ([#15772](https://github.com/warpdotdev/warp/pull/15772))
* On Warp on Web, switching teams now updates the current window instead of replacing the session. ([#15740](https://github.com/warpdotdev/warp/pull/15740))
* Command X-Ray now describes `git ls-remote` flags such as `--branches`. ([#15756](https://github.com/warpdotdev/warp/pull/15756))
* Third-party harnesses no longer hang the driver after `/exit` fails to stop the CLI. ([#15728](https://github.com/warpdotdev/warp/pull/15728))
* WASM conversation viewer now shows the web top bar for orchestrated factory sessions. ([#15754](https://github.com/warpdotdev/warp/pull/15754))
**Oz updates**
* Environment pickers now show personal environments and environments for the selected window team. ([#15850](https://github.com/warpdotdev/warp/pull/15850))
* Added team selection to `oz run list`. ([#15811](https://github.com/warpdotdev/warp/pull/15811))
* Added team selection to runner listing and name-based updates. ([#15809](https://github.com/warpdotdev/warp/pull/15809))
* API key list, create, and expire commands now respect the selected Oz CLI team. ([#15806](https://github.com/warpdotdev/warp/pull/15806))
* Oz agent catalogs now follow active team selection. ([#15807](https://github.com/warpdotdev/warp/pull/15807))
* Environment lists and interactive pickers now follow the selected team. ([#15805](https://github.com/warpdotdev/warp/pull/15805))
* Added team selection to `oz model list` for team-specific model catalogs. ([#15804](https://github.com/warpdotdev/warp/pull/15804))
* Oz agents can use refreshed Entra credentials to write to Azure DevOps. ([#15840](https://github.com/warpdotdev/warp/pull/15840))
* Claude Code and Codex runs can now access Factory MCP automatically. ([#15827](https://github.com/warpdotdev/warp/pull/15827))
### 2026.09.02 (v0.2026.09.02.08.27)
[Section titled “2026.09.02 (v0.2026.09.02.08.27)”](#20260902-v0202609020827)
**New features**
* Start a debug agent inside the retained session of a cloud run that failed during environment setup. The run keeps its original failure record. ([#14916](https://github.com/warpdotdev/warp/pull/14916))
**Improvements**
* Text inside “Thought” dropdowns in agent conversations can now be selected and copied. ([#15691](https://github.com/warpdotdev/warp/pull/15691))
* Show the live cloud connection indicator on third-party agent rich input. ([#15625](https://github.com/warpdotdev/warp/pull/15625))
* Faster conversation restore for conversations containing plan documents. ([#15579](https://github.com/warpdotdev/warp/pull/15579))
* `oz run get --conversation` and `oz run conversation get` now print the raw transcript for third-party harness runs instead of failing with operation\_not\_supported. ([#15642](https://github.com/warpdotdev/warp/pull/15642))
* Hovering over the profile icon on user messages in agent conversations now shows message timestamps, along with a “Copy timestamp” affordance in the overflow menu. ([#15605](https://github.com/warpdotdev/warp/pull/15605))
* The `create_file` tool can now fully replace an existing file’s contents in one step (`allow_overwrite: true`) instead of failing and requiring a separate edit. ([#15380](https://github.com/warpdotdev/warp/pull/15380))
* Custom inference endpoint definitions now use validated file-backed settings shared by Warp and Warp Agent CLI. ([#15574](https://github.com/warpdotdev/warp/pull/15574))
**Bug fixes**
* Fixed MCP servers that reject a configured credential being reported as though they required OAuth sign-in. Warp now distinguishes a rejected token from a genuine OAuth challenge, and refuses to send a credential header whose secret placeholder was never filled in. ([#15714](https://github.com/warpdotdev/warp/pull/15714))
* Fixed a crash when Agent streamed an empty update into a plan document. ([#15720](https://github.com/warpdotdev/warp/pull/15720))
* Prevent a crash on Linux/X11 when Warp requests user attention over a dead display connection. ([#15717](https://github.com/warpdotdev/warp/pull/15717))
* Fix a crash that could occur when extending a shared session after its terminal window had already closed. ([#15695](https://github.com/warpdotdev/warp/pull/15695))
* Fixed a crash when selecting some Windows fonts, such as Noto Sans Mono CJK SC, that expose a glyph advance without an outline bounding box. ([#15705](https://github.com/warpdotdev/warp/pull/15705))
* Fixed the built-in Factory MCP failing to reconnect during credential refresh. ([#15628](https://github.com/warpdotdev/warp/pull/15628))
* Fixed a race that could make a single local Oz `run_agents` child appear as two orchestration pills. ([#15583](https://github.com/warpdotdev/warp/pull/15583))
* Avoid repeated share-modal rendering when no terminal session is available. ([#13942](https://github.com/warpdotdev/warp/pull/13942)) — [@KRRT7](https://github.com/KRRT7) ✨
* Fixed animated GIF background images freezing on their first frame in the terminal window. ([#14618](https://github.com/warpdotdev/warp/pull/14618)) — [@niyasrad](https://github.com/niyasrad) ✨
* Fixed the SuperGrok / X Premium connect button getting stuck when the browser was closed mid-authentication, and added a Cancel button to recover without waiting for a timeout. ([#15576](https://github.com/warpdotdev/warp/pull/15576))
* Fixed onboarding interrupting a workspace opened from a shared session or agent-conversation link. ([#15550](https://github.com/warpdotdev/warp/pull/15550))
**Oz updates**
* Cloud agents now report why an MCP server failed to connect — a rejected credential, or a secret that was not available to the run — instead of asking you to authenticate in the desktop app. ([#15714](https://github.com/warpdotdev/warp/pull/15714))
* Mixed GitHub and GitLab environments clone each repository from its own host and keep credentials for both forges on refresh. ([#15616](https://github.com/warpdotdev/warp/pull/15616))
### 2026.08.27 (v0.2026.08.26.17.59)
[Section titled “2026.08.27 (v0.2026.08.26.17.59)”](#20260827-v0202608261759)
**New features**
* Warp Factories is now live in Early Access. Read the [Warp Factories launch announcement](https://www.warp.dev/blog/open-infrastructure-for-building-a-software-factory) for details.
**Improvements**
* Removed unnecessary first-time-user banners and prompts (credits, notifications, desktop download) when viewing a shared session or conversation transcript on the web. ([#15515](https://github.com/warpdotdev/warp/pull/15515))
* Disabled team/workspace members are now shown grayed out with an explanatory tooltip instead of appearing active. ([#15258](https://github.com/warpdotdev/warp/pull/15258))
* Renamed the “Oz Cloud API Keys” settings page to “API keys” under Cloud platform. ([#15424](https://github.com/warpdotdev/warp/pull/15424))
* Enabled IME marked text (composition) input on Windows and Linux, previously macOS-only. ([#15395](https://github.com/warpdotdev/warp/pull/15395))
* Added a setting to make bare right-click paste from the clipboard, with Shift+right-click still opening the context menu. ([#15365](https://github.com/warpdotdev/warp/pull/15365))
* Added a setting to stop ‘#’ at the start of terminal input from opening AI Command Search, so shell comments aren’t interrupted. ([#15340](https://github.com/warpdotdev/warp/pull/15340))
* Usage displays (agent block usage, conversation footer, usage history, and task details) now show a per-category dollar cost breakdown alongside credits. ([#15148](https://github.com/warpdotdev/warp/pull/15148))
* Added a “Paste” item to the terminal block list’s right-click context menu. ([#15346](https://github.com/warpdotdev/warp/pull/15346))
* The markdown viewer now preserves your scroll position when switching between Rendered and Raw view modes. ([#13967](https://github.com/warpdotdev/warp/pull/13967)) — [@slash9494](https://github.com/slash9494) ✨
* Holding a modifier now shows each tab’s switch-to-tab keyboard shortcut on the tab itself. ([#15221](https://github.com/warpdotdev/warp/pull/15221)) — [@JJack27](https://github.com/JJack27) ✨
**Bug fixes**
* Fixed bash sessions never reporting detected shell plugins (e.g. Starship) back to Warp. ([#15518](https://github.com/warpdotdev/warp/pull/15518))
* Fixed mismatched Shift/Command/Option key icons in keybinding chips (Command Palette, context menus, tooltips) on the web build. ([#15569](https://github.com/warpdotdev/warp/pull/15569))
* \[Windows] Fixed Warp becoming unresponsive after disconnecting and reconnecting a Remote Desktop session. ([#15566](https://github.com/warpdotdev/warp/pull/15566)) — [@bbbiggest](https://github.com/bbbiggest) ✨
* Fixed the Teams settings confirmation dialogs (remove member, transfer ownership, leave/delete team) landing at the top or bottom edge of the window depending on the page’s scroll position instead of staying centered. ([#15542](https://github.com/warpdotdev/warp/pull/15542))
* Fixed automatic CLI plugin installation failing in Windows PowerShell 5.1. ([#15544](https://github.com/warpdotdev/warp/pull/15544))
* Fixed a multi-gigabyte memory spike when editing very large files, caused by unbounded parallel text-layout work. ([#15128](https://github.com/warpdotdev/warp/pull/15128))
* Fixed cloud agent runs occasionally getting stuck showing in progress when a child agent finished right as the parent run began tearing down. ([#15432](https://github.com/warpdotdev/warp/pull/15432))
* Pressing Ctrl-C in an attached third-party agent harness session (e.g. Claude Code) now correctly resolves it to cancelled instead of leaving it stuck showing in progress. ([#15506](https://github.com/warpdotdev/warp/pull/15506))
* Cloud agent runs now always report a terminal status (succeeded, failed, or error) when the agent process exits, instead of occasionally being left stuck in progress after sandbox deadlines, SIGTERM shutdowns, or exit races. ([#15387](https://github.com/warpdotdev/warp/pull/15387))
* Fixed a memory spike when opening large files in the code editor caused by an unnecessary full-file clone. ([#13508](https://github.com/warpdotdev/warp/pull/13508))
* Fixed completions for many commands’ multi-argument options that were mis-modelled (e.g. `git branch`/`git switch`, `rsync --info`/`--debug`, `rustc -L`, `dart format`, `hugo new`, `date`), so they no longer offer the wrong arguments. ([#15487](https://github.com/warpdotdev/warp/pull/15487))
* Fixed `ln -s <path>` and `ln -F/-f/-i <path>` not offering file path completions. ([#15480](https://github.com/warpdotdev/warp/pull/15480))
* Fixed shell command completions resolving the wrong argument for options that take multiple arguments of differing types (such as `cargo fmt -- --print-config` and `jq --rawfile`), where a value before the last received a later argument’s suggestions. ([#15475](https://github.com/warpdotdev/warp/pull/15475))
* Fixed PowerShell sessions using PSReadLine’s vi edit mode submitting mangled commands. ([#15476](https://github.com/warpdotdev/warp/pull/15476))
* Cloud agent environments no longer hang with runaway “cloning” output when running `git log`, `git blame`, or other path-limited history commands. ([#15281](https://github.com/warpdotdev/warp/pull/15281))
* Fixed several latent shell-integration bugs, including a crash from slicing spans on non-UTF-8 character boundaries. ([#15428](https://github.com/warpdotdev/warp/pull/15428))
* Fixed the usage footer’s conversation-total dollar amount reading higher than the per-response breakdown by aligning both with the same charged-usage figures. ([#15423](https://github.com/warpdotdev/warp/pull/15423))
* Fixed the agent `grep` tool returning a parse error, or in rare cases a wrong file/line, when a matched file path contained a colon (e.g. Windows paths, some Go module paths). ([#15422](https://github.com/warpdotdev/warp/pull/15422))
* Retry transient server errors when resolving a managed MCP server’s connection, instead of permanently failing the agent run on the first blip. ([#15426](https://github.com/warpdotdev/warp/pull/15426))
* Fixed a hidden Alt+1 (Ctrl+1 on Mac) binding for Project Explorer that could not be remapped or disabled from Settings > Keyboard shortcuts. ([#15310](https://github.com/warpdotdev/warp/pull/15310))
* Fixed stdio MCP servers failing to start on a fresh `oz agent run` with “Unknown PATH when trying to launch MCP command.” ([#15396](https://github.com/warpdotdev/warp/pull/15396))
* Fixed zsh tab completions losing their descriptions for commands using clustered short options. ([#15313](https://github.com/warpdotdev/warp/pull/15313))
* Fixed unbounded memory growth from rebuilding the launch-config search index on every rapid configuration-file change. ([#15119](https://github.com/warpdotdev/warp/pull/15119))
* Tab autocomplete now follows symlinks to directories in WSL sessions. ([#14755](https://github.com/warpdotdev/warp/pull/14755))
* Improved scrolling performance in transcripts with many Agent Mode blocks. ([#15280](https://github.com/warpdotdev/warp/pull/15280))
* Fixed a “double cursor” issue where a finished background block kept showing a cursor alongside the input editor or the next block. ([#15322](https://github.com/warpdotdev/warp/pull/15322))
* Fixed a stray “(1)” badge appearing on the Code Indexing and Profiles settings sub-pages during search. ([#15319](https://github.com/warpdotdev/warp/pull/15319))
* Fixed cloud agent runs having too small a recovery budget to retry a mid-stream connection reset, sometimes failing runs instead of automatically retrying. ([#15293](https://github.com/warpdotdev/warp/pull/15293))
**Oz updates**
* Fixed handoff snapshot files not reaching a rebuilt cloud sandbox, which left the agent referencing files that were never downloaded. ([#15505](https://github.com/warpdotdev/warp/pull/15505))
### 2026.08.25 (v0.2026.08.25.19.26)
[Section titled “2026.08.25 (v0.2026.08.25.19.26)”](#20260825-v0202608251926)
**New features**
* Added an inline `/usage` command to the Warp Agent CLI showing plan, credit usage, and billing links. ([#14968](https://github.com/warpdotdev/warp/pull/14968))
**Bug fixes**
* Fixed an unbounded memory leak in the terminal completions engine where large or unusual input (e.g. pasting a large blob of text) could permanently grow memory usage over a session. ([#15181](https://github.com/warpdotdev/warp/pull/15181))
* Fixed a font-fallback bug on web that made the ⇧ (Shift) key glyph in keyboard shortcut hints render heavier, larger, and misaligned compared to neighboring ⌘/⌥ glyphs. ([#15261](https://github.com/warpdotdev/warp/pull/15261))
* Removed a stray 1px border around the workspace on Warp Web that could get clipped by rounded browser corners. ([#15259](https://github.com/warpdotdev/warp/pull/15259))
**Oz updates**
* Fixed intermittent “MCP server not found” errors after a cloud agent sandbox is rebuilt mid-task.
### 2026.08.19 (v0.2026.08.19.08.15)
[Section titled “2026.08.19 (v0.2026.08.19.08.15)”](#20260819-v0202608190815)
**New features**
* Added an inline `/usage` command to the Warp Agent CLI showing plan, credit usage, and billing links. ([#14968](https://github.com/warpdotdev/warp/pull/14968))
**Bug fixes**
* Fixed an unbounded memory leak in the terminal completions engine where large or unusual input (e.g. pasting a large blob of text) could permanently grow memory usage over a session. ([#15181](https://github.com/warpdotdev/warp/pull/15181))
* Fixed a font-fallback bug on web that made the ⇧ (Shift) key glyph in keyboard shortcut hints render heavier, larger, and misaligned compared to neighboring ⌘/⌥ glyphs. ([#15261](https://github.com/warpdotdev/warp/pull/15261))
* Removed a stray 1px border around the workspace on Warp Web that could get clipped by rounded browser corners. ([#15259](https://github.com/warpdotdev/warp/pull/15259))
**Oz updates**
* Fixed intermittent “MCP server not found” errors after a cloud agent sandbox is rebuilt mid-task.
### 2026.08.18 (v0.2026.08.18.02.52)
[Section titled “2026.08.18 (v0.2026.08.18.02.52)”](#20260818-v0202608180252)
**New features**
* Warp now includes a built-in Factory MCP server for logged-in users.
**Improvements**
* Added completions for `mpv` and `ruff`, and refreshed `deno` completions. ([#15248](https://github.com/warpdotdev/warp/pull/15248))
* Teamless users in a native workspace now see an Admin Panel link and joinable teams on the Teams settings page instead of team creation. ([#15246](https://github.com/warpdotdev/warp/pull/15246))
* `oz agent run-cloud` now accepts `--title` and `--parent-run-id`, so third-party harnesses can set a run’s title and orchestration lineage. ([#15187](https://github.com/warpdotdev/warp/pull/15187))
* The agent run details panel now has a copy button on the Initial query field, matching the Error and Environment details fields. ([#15156](https://github.com/warpdotdev/warp/pull/15156))
* Workspace admins can now manage team membership (promote/demote/remove) on their current team, and show a “Workspace admin”/“Workspace owner” badge in the team members list. ([#15123](https://github.com/warpdotdev/warp/pull/15123))
* Cloud agent sandboxes now default to a `Warp` git identity instead of `Oz` when the server doesn’t return a resolved GitHub identity. ([#15110](https://github.com/warpdotdev/warp/pull/15110))
* Added completions for `yay` and `paru`, and `kubectl --user` value completions. ([#15109](https://github.com/warpdotdev/warp/pull/15109))
* Added completions for `ip` — address, link, route, neighbour, netns, rule, tunnel, xfrm, monitor, and the remaining subcommands — plus `git read-tree`. ([#15101](https://github.com/warpdotdev/warp/pull/15101))
* Vim keybindings now work in several more multi-line editors (commit messages, suggested-rule content, env var commands, compact AI inputs, queued-prompt editing, workflow dynamic enums) when vim mode is enabled. ([#15054](https://github.com/warpdotdev/warp/pull/15054))
* Vim keybindings now work in the rule editor when vim mode is enabled. ([#15044](https://github.com/warpdotdev/warp/pull/15044))
* The File explorer chip can now be added to Warp Agent’s input toolbelt via Edit agent toolbelt. ([#15007](https://github.com/warpdotdev/warp/pull/15007))
**Bug fixes**
* Fixed a memory leak where repeatedly re-parsing and deep-cloning `.gitignore` matchers during file-tree watcher updates could allocate an unbounded number of regex caches in large repositories. ([#15240](https://github.com/warpdotdev/warp/pull/15240))
* Fixed billing copy that described add-on credit purchases as going to your personal balance instead of the team’s shared pool. ([#15207](https://github.com/warpdotdev/warp/pull/15207))
* Fixed the client failing to load a cloud agent task list that included an orchestration-sourced task. ([#15164](https://github.com/warpdotdev/warp/pull/15164))
* Fixed `paru` completions to match the real v2.1.0 CLI (options, operations, and argument types). ([#15159](https://github.com/warpdotdev/warp/pull/15159))
* Fixed excessive memory growth where a burst of repository-indexing updates could spawn many concurrent background tasks re-reading project rule files (WARP.md/AGENTS.md). ([#15147](https://github.com/warpdotdev/warp/pull/15147))
* Fixed a runaway loop of duplicate network requests that could fire while viewing a completed cloud agent conversation. ([#15138](https://github.com/warpdotdev/warp/pull/15138))
* Fixed the Teams settings page showing an invite-by-link option for Private and Hidden teams, which don’t support it. ([#15129](https://github.com/warpdotdev/warp/pull/15129))
* Fixed the Teams settings page showing another team’s pending email invites in a multi-team workspace. ([#15121](https://github.com/warpdotdev/warp/pull/15121))
* Fixed zsh sessions occasionally echoing Warp’s own shell-integration bootstrap script into the terminal when `cursor_mode`/prezto’s `init.zsh` was loaded. ([#15118](https://github.com/warpdotdev/warp/pull/15118))
* Fixed the Teams settings page’s “Open admin panel” link sending workspace admins to the team admin page instead of the workspace admin panel. ([#15113](https://github.com/warpdotdev/warp/pull/15113))
* Fixed `kubectl` completions ignoring a `--context`, `--cluster`, or `--user` flag on the command line; `kubecolor`/`oc` now complete those flags too, and `nx run` completions were fixed. ([#15109](https://github.com/warpdotdev/warp/pull/15109))
* Fixed `ip nexthop` filter completions suggesting protocol names that iproute2 rejects, and completed the `ip rule`/`ip mrule` flush selector sets. ([#15102](https://github.com/warpdotdev/warp/pull/15102))
* Fixed `ip` completions not appearing for iproute2’s bare keyword arguments, along with missing `ip addr`/`ip a`/`ip neighbor` aliases. ([#15101](https://github.com/warpdotdev/warp/pull/15101))
* Fixed missing product logos for MCP servers with decorated titles (e.g. “Sentry (OAuth)”) in MCP settings. ([#15037](https://github.com/warpdotdev/warp/pull/15037))
* Cancelling a conversation while an orchestration tool call was still streaming left the card stuck on “Configuring agents…”; it now shows a cancelled state. ([#14972](https://github.com/warpdotdev/warp/pull/14972))
* Fixed an issue where removing a team member from **Settings** > **Teams** would fail silently with no error shown if the removal was rejected by the server. ([#14964](https://github.com/warpdotdev/warp/pull/14964))
* \[Windows] Stopped enumerating the full process table with per-process CPU sampling on every terminal session, which could cause DPC\_WATCHDOG\_VIOLATION / high CPU on machines with many cores. ([#13405](https://github.com/warpdotdev/warp/pull/13405)) — [@npapano42](https://github.com/npapano42) ✨
* Fixed excessive memory usage when opening code review in a repository with large untracked directories (e.g. `node_modules`). ([#13393](https://github.com/warpdotdev/warp/pull/13393))
* Fixed a performance issue where every file-tree change deep-cloned compiled `.gitignore` matchers in large repositories. ([#13290](https://github.com/warpdotdev/warp/pull/13290))
### 2026.08.13 (v0.2026.08.12.21.54)
[Section titled “2026.08.13 (v0.2026.08.12.21.54)”](#20260813-v0202608122154)
**Improvements**
* Added a customizable action to cycle the active tab color from a keybinding or the Command Palette. ([#14329](https://github.com/warpdotdev/warp/pull/14329)) — [@rasitakyol](https://github.com/rasitakyol) ✨
* Cloud agent run details now show the platform the run executes on, with a macOS or Linux icon alongside the architecture and runner. ([#14790](https://github.com/warpdotdev/warp/pull/14790))
* Added completions for `vagrant`, including its nested `box`, `cloud`, `plugin`, and `snapshot` command groups plus dynamic machine and box names. ([#14775](https://github.com/warpdotdev/warp/pull/14775))
* Added `openssl` command-line completions. ([#14771](https://github.com/warpdotdev/warp/pull/14771))
* Added inline command completions for the Yandex Cloud CLI (`yc`) and git worktree name suggestions. ([#14767](https://github.com/warpdotdev/warp/pull/14767))
* Tab autocomplete now follows symlinks to directories in remote/SSH sessions. ([#14746](https://github.com/warpdotdev/warp/pull/14746))
* Added completions for `journalctl`, including units, boots, journal fields, and syslog identifiers. ([#14742](https://github.com/warpdotdev/warp/pull/14742))
**Bug fixes**
* Fixed a crash in the AI `@` context menu when a workflow’s content included multi-byte characters (emoji, CJK, accented Latin) near the preview truncation boundary. ([#14933](https://github.com/warpdotdev/warp/pull/14933))
* Fixed the MCP tool-call JSON viewer’s key/chevron being vertically centered against a tall expanded multi-line string value instead of aligned to its top. ([#14949](https://github.com/warpdotdev/warp/pull/14949))
* Fixed long-running commands in Warp Agent CLI not accepting keyboard input. ([#14943](https://github.com/warpdotdev/warp/pull/14943))
* Fixed an issue where an AI response could fail to render entirely if it included a citation of an unrecognized type. ([#14915](https://github.com/warpdotdev/warp/pull/14915))
* Fixed the code review pane failing to load file content for renamed files with uncommitted changes. ([#14655](https://github.com/warpdotdev/warp/pull/14655))
* Fixed inactive agent toolbelts continuing to run hidden context chip commands. ([#14854](https://github.com/warpdotdev/warp/pull/14854))
* Fixed canceled background commands leaving wrapped child processes running. ([#14853](https://github.com/warpdotdev/warp/pull/14853))
* Prevent stale shared-session links and QR codes from being exposed while a new session is pending. ([#13813](https://github.com/warpdotdev/warp/pull/13813)) — [@rasitakyol](https://github.com/rasitakyol) ✨
* Fixed combining marks rendering at the wrong position on Linux and Windows. ([#14322](https://github.com/warpdotdev/warp/pull/14322)) — [@SS-Script](https://github.com/SS-Script) ✨
* Fixed the Find in File field becoming unclickable after pressing Enter in Vim mode. ([#14836](https://github.com/warpdotdev/warp/pull/14836))
* Fixed background orchestrated agents stealing input focus in Warp Agent CLI when they need user interaction. ([#14829](https://github.com/warpdotdev/warp/pull/14829))
* Fixed the environment selector showing “New Environment” for agent runs without an environment. ([#14837](https://github.com/warpdotdev/warp/pull/14837))
* Fixed excessive Git process creation when loading global skills. ([#14830](https://github.com/warpdotdev/warp/pull/14830))
* Fixed window corners being rounded in fullscreen. ([#14109](https://github.com/warpdotdev/warp/pull/14109)) — [@s1ckoleg](https://github.com/s1ckoleg) ✨
* Cmd-Up in Agent Mode now navigates user prompts and skips agent-run commands. ([#14685](https://github.com/warpdotdev/warp/pull/14685))
* macOS Option-click on Warp’s green traffic-light button now performs zoom instead of entering fullscreen. ([#14716](https://github.com/warpdotdev/warp/pull/14716))
* Fixed the dedicated hotkey (Quake mode) window not taking keyboard focus when opened on a different monitor than the main Warp window. ([#14726](https://github.com/warpdotdev/warp/pull/14726))
* `pkill <TAB>` now suggests running process names instead of filesystem paths. ([#14749](https://github.com/warpdotdev/warp/pull/14749))
* Fixed Warp Agent CLI Tab completions missing desktop completion sources and supported native-shell fallback. ([#14600](https://github.com/warpdotdev/warp/pull/14600))
* Fixed pasting rich text dropping numeric CSS font weights. ([#14512](https://github.com/warpdotdev/warp/pull/14512)) — [@fbartho](https://github.com/fbartho) ✨
* Fixed the Warp Agent CLI input occasionally rendering without a cursor after temporary interactions. ([#14747](https://github.com/warpdotdev/warp/pull/14747))
* Fixed the Warp Agent CLI model picker changing the default model for every session. ([#14737](https://github.com/warpdotdev/warp/pull/14737))
* Fixed the copy-link menu action doing nothing while a cloud agent session was still setting up. ([#14431](https://github.com/warpdotdev/warp/pull/14431))
* Running Oz from the command line on macOS no longer puts a bouncing Warp icon in the Dock. ([#14636](https://github.com/warpdotdev/warp/pull/14636))
**Oz updates**
* Fixed background subagent sessions stealing focus from the visible Warp Agent CLI input. ([#14961](https://github.com/warpdotdev/warp/pull/14961))
* Renamed the Oz agent UI to Warp Agent across the app and CLI. ([#11022](https://github.com/warpdotdev/warp/pull/11022))
* Fixed keyboard input for long-running commands. ([#14943](https://github.com/warpdotdev/warp/pull/14943))
* Homebrew installations now show the correct `brew upgrade` command when an update is available. ([#14899](https://github.com/warpdotdev/warp/pull/14899))
* The Warp Agent CLI’s Agents bar now mirrors the GUI’s multi-level orchestration: drill into an orchestrating child’s level, follow breadcrumbs back up, and see subtree rollup badges. ([#14884](https://github.com/warpdotdev/warp/pull/14884))
* Background orchestrated agents no longer take focus away from the session you are using. ([#14829](https://github.com/warpdotdev/warp/pull/14829))
* Fixed excessive Git process creation when loading global skills. ([#14830](https://github.com/warpdotdev/warp/pull/14830))
* Add a `/connect-grok` TUI slash command that jumps straight into connecting your Grok (X Premium / SuperGrok) account. ([#14759](https://github.com/warpdotdev/warp/pull/14759))
* Fixed occasional transcript jitter while Agent Mode responses stream in Warp Agent CLI. ([#14750](https://github.com/warpdotdev/warp/pull/14750))
* Shell Tab completions now share desktop ordering and native fallback behavior. ([#14600](https://github.com/warpdotdev/warp/pull/14600))
* Fixed the input occasionally rendering without a cursor after temporary interactions. ([#14747](https://github.com/warpdotdev/warp/pull/14747))
* Model selection now applies only to the current session and identifies the profile default. ([#14737](https://github.com/warpdotdev/warp/pull/14737))
* Code blocks no longer include box borders, making code easier to select and copy. ([#14738](https://github.com/warpdotdev/warp/pull/14738))
* Failed cloud agent runs now stay open and attachable for debugging instead of becoming unreachable. ([#14561](https://github.com/warpdotdev/warp/pull/14561))
* Child agents can now be launched with repository-qualified skill references instead of absolute paths. ([#14271](https://github.com/warpdotdev/warp/pull/14271))
* Running Oz from the command line on macOS no longer puts a bouncing Warp icon in the Dock. ([#14636](https://github.com/warpdotdev/warp/pull/14636))
### 2026.08.07 (v0.2026.08.05.09.03)
[Section titled “2026.08.07 (v0.2026.08.05.09.03)”](#20260807-v0202608050903)
**Improvements**
* Support `SKILLS_DIRS` env var in agent-driver mode to index extra skill directories at personal-skill precedence ([#14394](https://github.com/warpdotdev/warp/pull/14394))
**Bug fixes**
* Onboarding no longer shows the smallest AI credit pack as selected when the “Buy AI credits” option isn’t the one chosen. ([#14712](https://github.com/warpdotdev/warp/pull/14712))
* The vertical tab layout now shows the synced-inputs indicator on tabs with Synchronized Inputs enabled. ([#14697](https://github.com/warpdotdev/warp/pull/14697))
* Fixed a crash that could happen when typing immediately after a CLI agent session ended with completions-while-typing enabled. ([#14709](https://github.com/warpdotdev/warp/pull/14709))
* The tab bar background now matches the terminal background instead of rendering as a lighter strip. ([#14701](https://github.com/warpdotdev/warp/pull/14701))
* Opening a file from an agent conversation’s code-block preview now jumps to the first line of the shown range instead of the top of the file. ([#14702](https://github.com/warpdotdev/warp/pull/14702))
* Fixed Cmd and Option shortcuts for Backspace, Delete, and arrow keys being dropped in apps using the Kitty keyboard protocol. ([#14012](https://github.com/warpdotdev/warp/pull/14012)) — [@FreddieMcHeart](https://github.com/FreddieMcHeart) ✨
**Oz updates**
* Fixed background (window-scoped) computer use on Linux dropping the mouse button between actions, which broke drag gestures like text selection. ([#14686](https://github.com/warpdotdev/warp/pull/14686))
* Computer-use video recordings now render a smooth synthetic cursor that glides between actions and tracks drags continuously, consistently across window- and screen-scoped captures. ([#14681](https://github.com/warpdotdev/warp/pull/14681))
### 2026.07.31 (v0.2026.07.29.09.05)
[Section titled “2026.07.31 (v0.2026.07.29.09.05)”](#20260731-v0202607290905)
**Improvements**
* Custom model endpoints can now select an OpenAI Chat Completions, OpenAI Responses, or Anthropic Messages schema. ([#13938](https://github.com/warpdotdev/warp/pull/13938))
* Third-party agent harnesses can now report non-PR work products back to Warp. ([#14072](https://github.com/warpdotdev/warp/pull/14072))
* `gcloud` is now signed in automatically during GCP provider setup for cloud agents. ([#14132](https://github.com/warpdotdev/warp/pull/14132))
* Computer-use recording overlays now stay on screen long enough to read after recordings are trimmed to action segments. ([#14148](https://github.com/warpdotdev/warp/pull/14148))
* Managed secrets are now validated against the 128 KB environment variable limit before an agent run starts. ([#14219](https://github.com/warpdotdev/warp/pull/14219))
* The `oz` CLI can now set a named agent’s prompt when creating or updating agents. ([#14261](https://github.com/warpdotdev/warp/pull/14261))
* Added Vim `<` and `>` indent and dedent operators to the code editor. ([#14268](https://github.com/warpdotdev/warp/pull/14268))
* Code-block file references now open in your configured editor, with a Warp fallback. ([#14275](https://github.com/warpdotdev/warp/pull/14275))
* Logging out now also signs out of Warp web and avoids immediate re-authorization. ([#14284](https://github.com/warpdotdev/warp/pull/14284))
* MCP tool confirmations now show which tool is running and which server it came from. ([#14298](https://github.com/warpdotdev/warp/pull/14298))
* Replace Oz armadillo icon with theme-adaptive Warp “W” logo (Icon::Agent) app-wide across all agent/Oz interactive surfaces. ([#14344](https://github.com/warpdotdev/warp/pull/14344))
* Agent execution profiles can now be configured from settings files for all users. ([#14418](https://github.com/warpdotdev/warp/pull/14418))
**Bug fixes**
* Updated a bundled dependency to resolve CVE-2026-50185. ([#13357](https://github.com/warpdotdev/warp/pull/13357))
* Fixed the cloud agent Execution host dropdown not appearing when self-hosted workers were connected. ([#13875](https://github.com/warpdotdev/warp/pull/13875))
* Markdown content no longer renders HTML comments as visible text. ([#14009](https://github.com/warpdotdev/warp/pull/14009)) — [@maxmilian](https://github.com/maxmilian) ✨
* Cap and expand the shared desktop toast stack to keep error floods bounded and readable. ([#14028](https://github.com/warpdotdev/warp/pull/14028))
* Settings search now filters widgets on AI and Code subpages correctly — only matching widgets are shown instead of all widgets on the subpage. ([#14116](https://github.com/warpdotdev/warp/pull/14116))
* Fixed the Runner dropdown missing from the agent orchestration approval card. ([#14133](https://github.com/warpdotdev/warp/pull/14133))
* Remove shell selection from warpctrl tab/window create so local control cannot spawn caller-chosen shell binaries. ([#14158](https://github.com/warpdotdev/warp/pull/14158))
* Fixed misaligned zsh prompts caused by explicit-width prompt constructs. ([#14166](https://github.com/warpdotdev/warp/pull/14166))
* Report accurate video recording durations after post-processing. ([#14172](https://github.com/warpdotdev/warp/pull/14172))
* Fixed Vim `d%`, `c%`, and `y%` being no-ops in the code editor. ([#14176](https://github.com/warpdotdev/warp/pull/14176))
* Fixed click and drag annotations in computer-use recordings being offset or split across calls. ([#14191](https://github.com/warpdotdev/warp/pull/14191))
* Open recording artifacts in the authenticated viewer using the client-built Oz run URL. ([#14210](https://github.com/warpdotdev/warp/pull/14210))
* Warp now reports a server outage instead of blaming your model ID when the agent model list is unavailable. ([#14227](https://github.com/warpdotdev/warp/pull/14227))
* Fixed New Worktree tab configs breaking when the repository path contained spaces. ([#14296](https://github.com/warpdotdev/warp/pull/14296))
* Order the authenticated user’s team first in freshly fetched multi-team workspace metadata. ([#14301](https://github.com/warpdotdev/warp/pull/14301))
* Fixed voice input submitting partial transcriptions to Hermes. ([#14367](https://github.com/warpdotdev/warp/pull/14367))
**Oz updates**
* The `oz` CLI now accepts harness-specific model IDs with `--harness claude` and `--harness codex`. ([#14011](https://github.com/warpdotdev/warp/pull/14011))
### 2026.07.23 (v0.2026.07.22.09.01)
[Section titled “2026.07.23 (v0.2026.07.22.09.01)”](#20260723-v0202607220901)
**New features**
* Add native oh-my-pi (`omp`) CLI-agent integration with Rich Input. ([#13766](https://github.com/warpdotdev/warp/pull/13766))
* Pin individual tabs and tab groups to keep them at the front of the tab bar. ([#13767](https://github.com/warpdotdev/warp/pull/13767))
**Improvements**
* Agent read\_files tool now returns partial results when files are truncated, rather than failing. ([#12054](https://github.com/warpdotdev/warp/pull/12054))
* Slash command hints are now hidden when the slash command is not active. ([#12896](https://github.com/warpdotdev/warp/pull/12896)) — [@SkyNotSilent](https://github.com/SkyNotSilent) ✨
* Aligned git branch status chip styling and behavior with the built-in branch chip. ([#13349](https://github.com/warpdotdev/warp/pull/13349)) — [@BobbyWang0120](https://github.com/BobbyWang0120) ✨
* Excluded directories from Command Palette file search results so files are not crowded out. ([#13433](https://github.com/warpdotdev/warp/pull/13433)) — [@maxmilian](https://github.com/maxmilian) ✨
* Added an opt-in “Auto save” setting for the Warp text editor (Settings > Code > Code Editor and Review) that saves changes as you type and when the editor loses focus, and flushes edits automatically when closing instead of prompting. ([#13435](https://github.com/warpdotdev/warp/pull/13435))
* Async find is now enabled for all users. ([#13515](https://github.com/warpdotdev/warp/pull/13515))
* Added a dismiss button to the shared object storage limit banner. ([#13620](https://github.com/warpdotdev/warp/pull/13620)) — [@maxmilian](https://github.com/maxmilian) ✨
* Warp TUI now renders alt-screen applications (vim, htop, etc.) and forwards input to the PTY. ([#13626](https://github.com/warpdotdev/warp/pull/13626))
* Warp TUI now supports mouse interactions in alt-screen applications (e.g. vim, htop). ([#13696](https://github.com/warpdotdev/warp/pull/13696))
* Add a Speech Language setting for voice input so multilingual users can force transcription language instead of relying only on auto-detect. ([#13722](https://github.com/warpdotdev/warp/pull/13722))
* Render formatted Markdown in Agent Mode output in the TUI. ([#13730](https://github.com/warpdotdev/warp/pull/13730))
* Show create and edit document plans inline in the TUI transcript. ([#13731](https://github.com/warpdotdev/warp/pull/13731))
* Hide the redundant agent bar when running the Warp TUI inside Warp. ([#13738](https://github.com/warpdotdev/warp/pull/13738))
* Added You.com product icon to the MCP server gallery. ([#13749](https://github.com/warpdotdev/warp/pull/13749)) — [@hongyi-chen](https://github.com/hongyi-chen) ✨
* Added oz runner CLI commands for creating, listing, and managing cloud runners. ([#13760](https://github.com/warpdotdev/warp/pull/13760))
* Added agent\_identity\_uid support for remote child agent execution in orchestration. ([#13773](https://github.com/warpdotdev/warp/pull/13773))
* Added Ctrl+P to expand and collapse inline plans in the TUI. ([#13781](https://github.com/warpdotdev/warp/pull/13781))
* Pressing Left on an empty Warp TUI input now opens the conversation list. ([#13797](https://github.com/warpdotdev/warp/pull/13797))
* Excluded directories from the files Command Palette filter so files are not crowded out. ([#13801](https://github.com/warpdotdev/warp/pull/13801))
* Added natural language detection to the headless TUI input, with Agent-biased mode switching and automatic Shell command detection. ([#13826](https://github.com/warpdotdev/warp/pull/13826))
* Added up-arrow prompt history navigation to the Warp TUI. ([#13827](https://github.com/warpdotdev/warp/pull/13827))
* Warp’s TUI can now answer interactive agent questions, including multiple-choice and custom responses. ([#13830](https://github.com/warpdotdev/warp/pull/13830))
* Failed tool calls in the TUI now use a cleaner × symbol for clarity. ([#13838](https://github.com/warpdotdev/warp/pull/13838))
* The Warp TUI binary has been renamed from warp-tui to warp. ([#13904](https://github.com/warpdotdev/warp/pull/13904))
* Added support for attaching images to prompts in Warp’s TUI. ([#13908](https://github.com/warpdotdev/warp/pull/13908))
* Added a `/exit` slash command and `ctrl-d` support for quitting the Warp TUI. ([#13915](https://github.com/warpdotdev/warp/pull/13915))
* Added a `/view-logs` slash command to the Warp TUI for viewing application logs. ([#13932](https://github.com/warpdotdev/warp/pull/13932))
* Agent now includes pull request URL and repository host in Git context for better code awareness. ([#13936](https://github.com/warpdotdev/warp/pull/13936))
* TUI now shows a “Starting shell…” indicator during session bootstrap. ([#13958](https://github.com/warpdotdev/warp/pull/13958))
* Agent read\_files tool now reports accurate errors for oversized or unprocessable files. ([#13966](https://github.com/warpdotdev/warp/pull/13966))
* Cloud Runners and Cloud Agent Runners are now enabled for all users. ([#14010](https://github.com/warpdotdev/warp/pull/14010))
* TUI prompt history is now persisted across sessions. ([#14015](https://github.com/warpdotdev/warp/pull/14015))
* Generic tool call permission requests are now shown in the Warp TUI. ([#14019](https://github.com/warpdotdev/warp/pull/14019))
* File edit permission requests are now surfaced in the Warp TUI for agent tool calls. ([#14020](https://github.com/warpdotdev/warp/pull/14020))
* Shell command permission requests in the TUI are now editable before confirming. ([#14021](https://github.com/warpdotdev/warp/pull/14021))
* Added a status line to the TUI showing shell, cwd, and agent mode context. ([#14034](https://github.com/warpdotdev/warp/pull/14034))
* Natural language detection is now opt-in via `/enable` and `/disable` slash commands in the TUI. ([#14035](https://github.com/warpdotdev/warp/pull/14035))
* The Warp TUI input now shows ghosted keybinding hints that adapt to your mode — agent mode, ! shell mode, and while a long-running command is in progress. ([#14038](https://github.com/warpdotdev/warp/pull/14038))
* Show actionable Agent Mode request failures in the headless TUI. ([#14044](https://github.com/warpdotdev/warp/pull/14044))
* Improved TUI Markdown block spacing for better readability. ([#14049](https://github.com/warpdotdev/warp/pull/14049))
* Add a GUI and TUI `/fast-forward` slash command for toggling per-conversation autoexecute mode. ([#14057](https://github.com/warpdotdev/warp/pull/14057))
* TUI orchestration tab bar now uses Down (instead of Shift+Down) to focus the input, and Escape to return to the main agent. ([#14064](https://github.com/warpdotdev/warp/pull/14064))
* Shell commands are now cleared when starting a new TUI conversation. ([#14074](https://github.com/warpdotdev/warp/pull/14074))
* TUI footer model label is now clickable to open the inline model selection menu. ([#14076](https://github.com/warpdotdev/warp/pull/14076))
* Improved TUI shell-command readability with distinct command styling. ([#14101](https://github.com/warpdotdev/warp/pull/14101))
* TUI ask-question footer now reads “Ctrl + C to cancel question” instead of “Ctrl + C to skip all”, making it clear that Ctrl-C stops the conversation. ([#14105](https://github.com/warpdotdev/warp/pull/14105))
* Improved TUI thinking block formatting with better spacing and left-aligned body text. ([#14108](https://github.com/warpdotdev/warp/pull/14108))
* Added a `/logout` command to the Warp TUI. ([#14117](https://github.com/warpdotdev/warp/pull/14117))
**Bug fixes**
* Cancel in-flight repo metadata tree walks when repository file-tree state is removed. ([#12328](https://github.com/warpdotdev/warp/pull/12328)) — [@chinmaydwivedi](https://github.com/chinmaydwivedi) ✨
* Fixed local child agent conversations from orchestrated conversations sometimes appearing in the conversation list (including being shown as cloud agents). ([#13059](https://github.com/warpdotdev/warp/pull/13059))
* Fixed Vim gg command ignoring a count prefix (e.g. 5gg now correctly jumps to line 5). ([#13167](https://github.com/warpdotdev/warp/pull/13167)) — [@Jason-Shen2](https://github.com/Jason-Shen2) ✨
* Fixed the tab configs menu overflowing past the terminal window when many tab configs are available. ([#13224](https://github.com/warpdotdev/warp/pull/13224)) — [@fabiSwDevBeg](https://github.com/fabiSwDevBeg) ✨
* Fixed stale classic completions remaining visible after the user edits input. ([#13606](https://github.com/warpdotdev/warp/pull/13606)) — [@maxmilian](https://github.com/maxmilian) ✨
* Fixed copying multi-line text from the TUI inserting extra newlines and dropping trailing text ([#13741](https://github.com/warpdotdev/warp/pull/13741))
* Fixed asymmetric padding on MCP tool chips in the settings view. ([#13750](https://github.com/warpdotdev/warp/pull/13750))
* Fixed background computer use on macOS leaving keyboard focus stuck on the controlled window after a session ended. ([#13752](https://github.com/warpdotdev/warp/pull/13752))
* Local images embedded in Markdown now refresh after their files change on disk. ([#13764](https://github.com/warpdotdev/warp/pull/13764)) — [@rasitakyol](https://github.com/rasitakyol) ✨
* Fixed interactive input and cursor rendering for long-running commands in the headless TUI. ([#13774](https://github.com/warpdotdev/warp/pull/13774))
* Fixed the TUI remaining stuck on the sign-in screen after browser login completed. ([#13780](https://github.com/warpdotdev/warp/pull/13780))
* Fixed Shift+Enter in the TUI not inserting a newline due to missing Kitty keyboard protocol. ([#13782](https://github.com/warpdotdev/warp/pull/13782))
* Fixed Claude Code agent stop handling to properly recover from StopFailure hook errors. ([#13784](https://github.com/warpdotdev/warp/pull/13784))
* Fixed a crash that could occur when a CLI sub-agent block was opened for a long-running command. ([#13789](https://github.com/warpdotdev/warp/pull/13789))
* Fixed Windows PTY cleanup to properly terminate the ConPTY root process and close the pseudoconsole. ([#13802](https://github.com/warpdotdev/warp/pull/13802))
* Fixed PowerShell command history failing to load on Windows (regression that produced a ParserError when reading the history file). ([#13803](https://github.com/warpdotdev/warp/pull/13803))
* Fixed a parse error when passing global CLI flags (`--api-key`, `--debug`) before a subcommand. ([#13816](https://github.com/warpdotdev/warp/pull/13816))
* Fixed IME (input method editor) support on Linux Wayland and addressed KDE cursor-area loops. ([#13819](https://github.com/warpdotdev/warp/pull/13819)) — [@Detritalw](https://github.com/Detritalw) ✨
* Fixed pane header incorrectly showing a cloud sync icon for shared local conversations. ([#13823](https://github.com/warpdotdev/warp/pull/13823))
* Fixed the headless TUI footer/prompt rendering flush against the bottom terminal edge with no padding. ([#13850](https://github.com/warpdotdev/warp/pull/13850))
* Fixed shell startup prompts in Warp TUI sending input to both the shell and Warp Agent. ([#13901](https://github.com/warpdotdev/warp/pull/13901))
* Fixed file tree / project explorer failing to load on Windows when OSC 7 reports a drive-path cwd. ([#13920](https://github.com/warpdotdev/warp/pull/13920))
* Fixed TUI copy to correctly use the native clipboard and provide accurate feedback. ([#13929](https://github.com/warpdotdev/warp/pull/13929))
* Fixed the Warp Agent welcome screen not appearing after shell startup in the TUI. ([#13999](https://github.com/warpdotdev/warp/pull/13999))
* Fixed an issue where agent conversations could get stuck in a loading state. ([#14027](https://github.com/warpdotdev/warp/pull/14027))
* Fixed Ctrl+Shift+C forwarding to the PTY on Linux in fullscreen TUI when there is no selection. ([#14046](https://github.com/warpdotdev/warp/pull/14046))
* Fixed background focus suppression on macOS to scope correctly to the activation window. ([#14061](https://github.com/warpdotdev/warp/pull/14061))
* Fixed input focus being lost in the TUI when the agent is drafting tool calls. ([#14073](https://github.com/warpdotdev/warp/pull/14073))
* Agent request failures in the TUI now use consistent warning styling and out-of-credits actions. ([#14092](https://github.com/warpdotdev/warp/pull/14092))
* Fixed inverted colors on selected text in the TUI editor. ([#14102](https://github.com/warpdotdev/warp/pull/14102))
* Fixed Ctrl-V in the TUI to paste text when the clipboard does not contain an image. ([#14107](https://github.com/warpdotdev/warp/pull/14107))
* Fixed the redundant Agent footer appearing when Warp Preview or Dev TUI runs inside Warp. ([#14112](https://github.com/warpdotdev/warp/pull/14112))
**Oz updates**
* Added a TUI-only skill for migrating compatible Warp GUI settings and global file-based MCP servers. ([#13877](https://github.com/warpdotdev/warp/pull/13877))
### 2026.07.16 (v0.2026.07.15.08.55)
[Section titled “2026.07.16 (v0.2026.07.15.08.55)”](#20260716-v0202607150855)
**New features**
* Added a connection indicator for cloud agent sessions. ([#13340](https://github.com/warpdotdev/warp/pull/13340))
**Improvements**
* MCP tool-call request/response previews in Agent Mode now render in monospace font. ([#13490](https://github.com/warpdotdev/warp/pull/13490))
* Added toggles in Settings → Appearance to control which tabs appear in the tools panel. ([#13506](https://github.com/warpdotdev/warp/pull/13506))
* Added a Subscribe button to the out-of-credits AI error for quick upgrade access. ([#13544](https://github.com/warpdotdev/warp/pull/13544))
* The run details Status chip now links directly to the run in Oz web. ([#13455](https://github.com/warpdotdev/warp/pull/13455))
* Double-click a collapsed hidden section in the diff editor to fully expand it. ([#11621](https://github.com/warpdotdev/warp/pull/11621)) — [@bradleyjames](https://github.com/bradleyjames) ✨
* Agent conversations now respect your theme’s background color instead of a lightened overlay. ([#13495](https://github.com/warpdotdev/warp/pull/13495))
* Faster app startup: persisted agent conversations are now loaded lazily instead of fully decoded at launch. ([#13449](https://github.com/warpdotdev/warp/pull/13449))
* Highlighted the currently selected period in the Billing & Usage dropdown. ([#13551](https://github.com/warpdotdev/warp/pull/13551))
* Added a Copy action to the locked initial queued prompt in cloud mode. ([#13595](https://github.com/warpdotdev/warp/pull/13595))
* Suppressed passive suggestions for cloud-agent session viewers. ([#13565](https://github.com/warpdotdev/warp/pull/13565))
* Added a ‘Copy current path’ Command Palette action. ([#13148](https://github.com/warpdotdev/warp/pull/13148)) — [@elviskahoro](https://github.com/elviskahoro) ✨
* Added Resend and Sentry product icons to the MCP gallery. ([#13450](https://github.com/warpdotdev/warp/pull/13450))
* Matched MCP Servers search field sizing to standard search fields. ([#13536](https://github.com/warpdotdev/warp/pull/13536))
* Replaced the `/pr-comments` slash command with the bundled PR Comments skill. ([#13621](https://github.com/warpdotdev/warp/pull/13621))
**Bug fixes**
* Fixed an issue where you could not continue a conversation after the sandbox shut down. ([#13340](https://github.com/warpdotdev/warp/pull/13340))
* Fixed link detection incorrectly including fullwidth/CJK punctuation after URLs and file paths. ([#13085](https://github.com/warpdotdev/warp/pull/13085)) — [@rhinoc](https://github.com/rhinoc) ✨
* Fixed git status completion parsing for paths with spaces and renames, and completion of nested untracked files for git add. ([#13673](https://github.com/warpdotdev/warp/pull/13673))
* Fixed forking an agent conversation resetting the working directory instead of keeping the current one. ([#13482](https://github.com/warpdotdev/warp/pull/13482))
* Fixed unmodified-lines hover styles flickering while scrolling over the code review gutter. ([#13556](https://github.com/warpdotdev/warp/pull/13556))
* Fixed launch configuration tab-level commands not running when opened via `warp://launch/<name>`. ([#13103](https://github.com/warpdotdev/warp/pull/13103)) — [@AndreKalberer](https://github.com/AndreKalberer) ✨
* Fixed Markdown files opening in Warp’s Markdown Viewer from macOS file URLs even when the Markdown Viewer preference is disabled. ([#12866](https://github.com/warpdotdev/warp/commit/6b01a8e2fa372498c78e2c777b8006db6a86ca8b)) — @fadexadex ✨
* Fixed bold/italic Markdown links breaking before trailing punctuation. ([#13747](https://github.com/warpdotdev/warp/pull/13747))
* Fixed extra border gap on agent tool-call banners. ([#13154](https://github.com/warpdotdev/warp/pull/13154))
* Fixed text selection not starting correctly over Markdown tables. ([#12841](https://github.com/warpdotdev/warp/pull/12841))
* Fixed custom endpoint model selections not persisting across device sync. ([#13574](https://github.com/warpdotdev/warp/pull/13574))
* Fixed code review pinned file header showing diff content behind its rounded corners. ([#13616](https://github.com/warpdotdev/warp/pull/13616))
* Fixed missing macOS permission descriptions for Reminders and Calendar access (resolves icalBuddy failures). ([#13608](https://github.com/warpdotdev/warp/pull/13608))
* Fixed imported PR comments on context lines being wrongly marked as outdated. ([#13585](https://github.com/warpdotdev/warp/pull/13585))
* Fixed repo-gated slash commands lingering after leaving a repository. ([#13614](https://github.com/warpdotdev/warp/pull/13614))
* Fixed crash when deserializing cloud environments without a Docker image. ([#13553](https://github.com/warpdotdev/warp/pull/13553))
* Fixed group header not rendering for every multi-pane vertical tab. ([#10738](https://github.com/warpdotdev/warp/pull/10738)) — [@lonexreb](https://github.com/lonexreb) ✨
* Fixed the queued prompts panel not reappearing when an inline menu closes. ([#13527](https://github.com/warpdotdev/warp/pull/13527))
* Fixed an orchestration pill bar panic when dragging panes. ([#13528](https://github.com/warpdotdev/warp/pull/13528))
* Fixed a crash when opening Custom Routers settings with an invalid router file. ([#13499](https://github.com/warpdotdev/warp/pull/13499))
* Fixed agent requests failing during Grok OAuth token refresh. ([#13460](https://github.com/warpdotdev/warp/pull/13460))
* Fixed local-to-cloud handoff failing to start with an invalid model ID. ([#13458](https://github.com/warpdotdev/warp/pull/13458))
* Fixed a macOS computer-use crash when building the keycode cache off the main thread. ([#13547](https://github.com/warpdotdev/warp/pull/13547))
* Fixed directory account resolution for Linux builds using musl libc. ([#13384](https://github.com/warpdotdev/warp/pull/13384))
### 2026.07.09 (v0.2026.07.08.17.54)
[Section titled “2026.07.09 (v0.2026.07.08.17.54)”](#20260709-v0202607081754)
**Improvements**
* Markdown files now have syntax highlighting in the editor. ([#13034](https://github.com/warpdotdev/warp/pull/13034)) — [@bradleyjames](https://github.com/bradleyjames) ✨
* Cross-window tab dragging has been re-enabled on macOS and Windows. ([#13411](https://github.com/warpdotdev/warp/pull/13411))
* “Copy file path” is now available from the file viewer pane right-click menu. ([#13145](https://github.com/warpdotdev/warp/pull/13145)) — [@elviskahoro](https://github.com/elviskahoro) ✨
* Made custom inference model lists scrollable. ([#12647](https://github.com/warpdotdev/warp/pull/12647))
* Added a Command Palette action to write a heap profile to disk. ([#13107](https://github.com/warpdotdev/warp/pull/13107)) — [@AndreKalberer](https://github.com/AndreKalberer) ✨
**Bug fixes**
* Fixed a crash when changing the Agent Mode model if cached model preferences were stale. ([#13443](https://github.com/warpdotdev/warp/pull/13443))
* Fixed some glyphs misrendering on macOS when a user-installed font was set as the default. ([#13317](https://github.com/warpdotdev/warp/pull/13317))
* Fixed the conversation details credits breakdown not showing which models were used. ([#13438](https://github.com/warpdotdev/warp/pull/13438))
* Fixed a case where taking over an agent-monitored long-running command with Ctrl-C could cause it to hang. ([#12738](https://github.com/warpdotdev/warp/pull/12738))
* Web search and web page fetch now show a clear failed state instead of appearing to complete successfully. ([#13185](https://github.com/warpdotdev/warp/pull/13185))
* Fixed cmd+←/→ (and Home/End) jumping to the start/end of the current visual (soft-wrapped) line in the input editor. ([#13195](https://github.com/warpdotdev/warp/pull/13195))
* Fixed faint, hard-to-read item labels in the Settings “Header toolbar layout” editor in light themes. ([#13209](https://github.com/warpdotdev/warp/pull/13209))
* \[Windows] Fixed new terminal sessions and background work being starved due to a priority inversion in the Windows PTY. ([#13151](https://github.com/warpdotdev/warp/pull/13151))
* Fixed `/pr-comments` returning a 404 for pull requests opened from a fork. ([#13284](https://github.com/warpdotdev/warp/pull/13284))
* Fixed a terminal crash when a clear-driven resize truncated the spacer row. ([#12726](https://github.com/warpdotdev/warp/pull/12726)) — [@ChanlerDev](https://github.com/ChanlerDev) ✨
* Custom PS1 prompt text is now included when copying terminal blocks. ([#13076](https://github.com/warpdotdev/warp/pull/13076)) — [@SkyNotSilent](https://github.com/SkyNotSilent) ✨
* Added a “Don’t show me again” option to the SSH “completions are not working” banner. ([#12969](https://github.com/warpdotdev/warp/pull/12969)) — [@s1ckoleg](https://github.com/s1ckoleg) ✨
* Fixed duplicated leading characters in rendered multi-line command blocks. ([#12619](https://github.com/warpdotdev/warp/pull/12619)) — [@MX48Live](https://github.com/MX48Live) ✨
* Fixed the inline `/repos` menu briefly flashing “No results” before the list populated. ([#13454](https://github.com/warpdotdev/warp/pull/13454))
* Fixed a crash during cross-window tab drag when entering macOS full-screen mode. ([#13409](https://github.com/warpdotdev/warp/pull/13409))
* Fixed a panic in the SSH remote server daemon on hosts where the current user has no passwd entry. ([#13382](https://github.com/warpdotdev/warp/pull/13382))
* Warp SSH now falls back to plain SSH when `~/.ssh/config` sets `RemoteCommand`, preventing session startup failures. ([#13315](https://github.com/warpdotdev/warp/pull/13315))
* Fixed clicking a link or file path in Agent Mode output not showing the “Open link” tooltip on a plain click. ([#13280](https://github.com/warpdotdev/warp/pull/13280))
* Fixed conversation rewind re-sending rewound-away prompts and triggering stale sub-agent tasks. ([#13072](https://github.com/warpdotdev/warp/pull/13072))
* Fixed a tab-rename action being incorrectly offered for tabs inside tab groups in pane view. ([#13289](https://github.com/warpdotdev/warp/pull/13289))
* Fixed a crash when `/compact-and` ran while a queued prompt was active. ([#13236](https://github.com/warpdotdev/warp/pull/13236))
* Fixed the model fallback logic incorrectly selecting admin-disabled models. ([#13331](https://github.com/warpdotdev/warp/pull/13331))
* \[Windows] Fixed secure storage reporting missing keys as a generic error instead of NotFound. ([#13278](https://github.com/warpdotdev/warp/pull/13278))
### 2026.07.03 (v0.2026.07.01.09.21)
[Section titled “2026.07.03 (v0.2026.07.01.09.21)”](#20260703-v0202607010921)
**New features**
* Add native support for the agy (Antigravity) CLI agent. ([#12380](https://github.com/warpdotdev/warp/pull/12380)) — [@jgfurlan](https://github.com/jgfurlan) ✨
* Custom model routers - define your own routing rules to send agent requests to different models. ([#13052](https://github.com/warpdotdev/warp/pull/13052))
* Tab Groups - organize tabs into named, collapsible groups in both the horizontal and vertical tab bars. Drag tabs into groups and reorder groups within the tab bar. Customize groups with colors and names, and use keyboard shortcuts to manage them. ([#13230](https://github.com/warpdotdev/warp/pull/13230))
**Improvements**
* Add Droid rich status listener support for structured CLI agent notifications. ([#12640](https://github.com/warpdotdev/warp/pull/12640)) — [@senseFy](https://github.com/senseFy) ✨
* The Warp CLI and warpctl binaries are now statically compiled on Linux for better compatibility. ([#12813](https://github.com/warpdotdev/warp/pull/12813))
* New File can now be assigned a custom keyboard shortcut from Settings -> Keybindings. ([#12979](https://github.com/warpdotdev/warp/pull/12979)) — [@SkyNotSilent](https://github.com/SkyNotSilent) ✨
* Improved PowerShell startup time on Windows by deferring cmdlet loading during bootstrap. ([#12981](https://github.com/warpdotdev/warp/pull/12981))
* Code review comments can now be sent to the agent with the keyboard (Ctrl/Cmd+Enter), and the shortcut is shown on the “Send to Agent” button. ([#12982](https://github.com/warpdotdev/warp/pull/12982))
* Streamlined the new agent-onboarding flow — removed the post-setup “I don’t want AI” buttons, moved the progress dots inline with the Back/Next controls, and simplified the “don’t want AI” confirmation dialog. ([#12991](https://github.com/warpdotdev/warp/pull/12991))
* Agent onboarding now ties AI features to having a Warp account — creating an account (including when you use third-party agents) keeps AI on, while skipping sign-in defers it; the login screen no longer has a “disable AI” option. ([#12992](https://github.com/warpdotdev/warp/pull/12992))
* The onboarding “Choose how to access AI” step now offers “Subscription” or “Set up later” and can be skipped without subscribing; choosing Subscription and pressing Next opens the upgrade page directly. ([#12993](https://github.com/warpdotdev/warp/pull/12993))
* Custom model routers can now be created and edited directly in Warp Agent settings, without manual YAML file editing. ([#13010](https://github.com/warpdotdev/warp/pull/13010))
* After saving a BYOK API key, Warp now suggests a provider-appropriate default model. ([#13018](https://github.com/warpdotdev/warp/pull/13018))
* Custom models are no longer shown in the inline model picker for cloud agent panes. ([#13023](https://github.com/warpdotdev/warp/pull/13023))
* Add a Copy as Markdown action to AI planning document menus. ([#13082](https://github.com/warpdotdev/warp/pull/13082)) — [@SkyNotSilent](https://github.com/SkyNotSilent) ✨
* Artifact download notifications now include links to open the file or its location. ([#13096](https://github.com/warpdotdev/warp/pull/13096))
* The agent context window indicator now shows how much context remains instead of how much is used. ([#13097](https://github.com/warpdotdev/warp/pull/13097))
* Clearer Command Palette labels for installing/uninstalling the Oz and Warp Control CLIs (they now describe global, outside-Warp use vs. in-Warp use). ([#13155](https://github.com/warpdotdev/warp/pull/13155))
* The Billing & Usage legend no longer lists credit buckets that have zero credits. ([#13181](https://github.com/warpdotdev/warp/pull/13181))
* Added `warp://settings` deep links - open settings, pre-fill the search bar with `?q=`, or jump to a specific setting with `?widget=`. ([#13232](https://github.com/warpdotdev/warp/pull/13232))
**Bug fixes**
* Fixed MCP server configuration failing to save when secret redaction was enabled. ([#10839](https://github.com/warpdotdev/warp/pull/10839)) — [@david-engelmann](https://github.com/david-engelmann) ✨
* Fixed tab titles getting stuck on “Wants to run AskUserQuestion: …” after answering a Claude Code question. ([#12341](https://github.com/warpdotdev/warp/pull/12341)) — [@christophercolumbusdog](https://github.com/christophercolumbusdog) ✨
* Warp no longer blocks system-initiated logout, shutdown, or scheduled OS updates while a process is running. ([#12480](https://github.com/warpdotdev/warp/pull/12480)) — [@maxmilian](https://github.com/maxmilian) ✨
* Fixed the profile switcher clearing typed terminal input. ([#12714](https://github.com/warpdotdev/warp/pull/12714))
* Fixed a crash when rejecting and then confirming a requested command. ([#12747](https://github.com/warpdotdev/warp/pull/12747))
* Fixed terminal file links capturing a trailing sentence period, which prevented Markdown files referenced at the end of a sentence from opening in the Markdown viewer. ([#12965](https://github.com/warpdotdev/warp/pull/12965))
* Fixed quota and credit errors being misclassified as Warp faults. ([#12966](https://github.com/warpdotdev/warp/pull/12966))
* Fixed long file paths split across wrapped terminal lines not being detected as clickable file links. ([#12968](https://github.com/warpdotdev/warp/pull/12968))
* Fixed unreadable agent toolbelt chip text after changing themes. ([#12970](https://github.com/warpdotdev/warp/pull/12970))
* Fixed double-click and drag text selection running past word boundaries into the next word. ([#12985](https://github.com/warpdotdev/warp/pull/12985))
* Fixed conversation-list hover tooltips showing through modal dialogs. ([#13011](https://github.com/warpdotdev/warp/pull/13011))
* Fixed `/open-file` not allowing the argument to be cleared when the current directory contains a single file. ([#13017](https://github.com/warpdotdev/warp/pull/13017)) — [@AndreKalberer](https://github.com/AndreKalberer) ✨
* Fixed inline-code links in agent output having their underline hidden by the block background. ([#13030](https://github.com/warpdotdev/warp/pull/13030))
* Slash commands that emit an action (like `/fork`) now run immediately instead of being captured as a queued prompt when queued-prompts mode is on. ([#13060](https://github.com/warpdotdev/warp/pull/13060))
* Fixed `/fork-and-compact` so its new pane / new tab options match `/fork` (Enter opens a new pane, Cmd/Ctrl+Enter opens a new tab). ([#13061](https://github.com/warpdotdev/warp/pull/13061))
* Fixed clicking Markdown links in AI block output doing nothing. ([#13065](https://github.com/warpdotdev/warp/pull/13065))
* Fixed “New group with tab” being offered for a tab that is already in a group. ([#13080](https://github.com/warpdotdev/warp/pull/13080))
* Fixed a crash when viewing shared sessions that used conversation search. ([#13108](https://github.com/warpdotdev/warp/pull/13108))
* Fixed Claude Code cloud agents not reporting successful completion. ([#13110](https://github.com/warpdotdev/warp/pull/13110))
* Warp no longer registers itself as an alternate handler for common file types on macOS. ([#13121](https://github.com/warpdotdev/warp/pull/13121))
* Fix the rotating agent tips not appearing below the “Warping…” indicator in Agent Mode. ([#13122](https://github.com/warpdotdev/warp/pull/13122))
* Closing the active vertical tab now activates the tab below it instead of the one above. ([#13142](https://github.com/warpdotdev/warp/pull/13142)) — [@elviskahoro](https://github.com/elviskahoro) ✨
* Fixed Vim visual-mode paste losing the selection after recalling a command from history. ([#13152](https://github.com/warpdotdev/warp/pull/13152))
* Fixed grep and file-glob tool-call headers in the agent view showing doubled file separators (e.g. `C:\\Users\\...`) on Windows. ([#13160](https://github.com/warpdotdev/warp/pull/13160))
* Fixed cloud agent follow-up messages creating a local session instead of continuing in the cloud. ([#13162](https://github.com/warpdotdev/warp/pull/13162))
* Fixed agent chips overflowing the orchestrate “start additional agents” card; they now wrap onto multiple lines. ([#13197](https://github.com/warpdotdev/warp/pull/13197))
* Fixed `?` opening the help panel instead of being typed when editing a queued prompt. ([#13202](https://github.com/warpdotdev/warp/pull/13202))
* Fixed severe UI lag on Windows systems with Intel UHD Graphics 770 by downranking that GPU adapter. ([#13204](https://github.com/warpdotdev/warp/pull/13204))
* Fixed local Oz/ambient agent runs reporting “Cancelled by user” when an agent-issued command exited the shell; the run now reports as failed with an explanation. ([#13210](https://github.com/warpdotdev/warp/pull/13210))
**Oz updates**
* Added Oz CLI commands for memory store management: list/get/update stores, list store agents, list/create/update/delete memories, and view memory version history. ([#12973](https://github.com/warpdotdev/warp/pull/12973))
* Agent responses now surface fetched memories as citations. ([#13199](https://github.com/warpdotdev/warp/pull/13199))
### 2026.06.24 (v0.2026.06.24.09.19)
[Section titled “2026.06.24 (v0.2026.06.24.09.19)”](#20260624-v0202606240919)
**New features**
* Warp Agent now supports custom model routers. Custom routers can be complexity-based, where tasks are routed based on how difficult they are, or rule-based, where they are routed based on a set of natural language prompts. ([#13052](https://github.com/warpdotdev/warp/pull/13052))
* \[macOS] Added an option to hide Warp from the Dock while using the dedicated hotkey window (Settings → Features → Global hotkey). ([#9926](https://github.com/warpdotdev/warp/pull/9926)) — [@ShankyJS](https://github.com/ShankyJS) ✨
**Improvements**
* A richer notifications plugin for Codex is now supported. ([#12978](https://github.com/warpdotdev/warp/pull/12978)) — [@liliwilson](https://github.com/liliwilson) ✨
* Made the Agent picker in the New API key modal searchable. ([#12972](https://github.com/warpdotdev/warp/pull/12972))
* Unified legacy and SSH warpification settings for a more consistent experience. ([#12946](https://github.com/warpdotdev/warp/pull/12946))
* PR chips in vertical tabs Summary mode are now clickable. ([#12945](https://github.com/warpdotdev/warp/pull/12945))
* Third-party agent harnesses (Codex, Claude Code) now support local continuation when a cloud run is interrupted. ([#12076](https://github.com/warpdotdev/warp/pull/12076))
* Connected AI provider labels are now shown in the host picker when choosing between available agents. ([#12214](https://github.com/warpdotdev/warp/pull/12214)) — [@dmichelin](https://github.com/dmichelin) ✨
* Shell integration now passes command completion metadata via Precmd for more accurate completions. ([#12853](https://github.com/warpdotdev/warp/pull/12853)) — [@vorporeal](https://github.com/vorporeal) ✨
* The Maximize / Minimize pane action now shows its keyboard shortcut in the pane-header overflow menu. ([#12811](https://github.com/warpdotdev/warp/pull/12811)) — [@roor0](https://github.com/roor0) ✨
* Made the cloud credits banner in Agent Conversations dismissible. ([#11975](https://github.com/warpdotdev/warp/pull/11975))
* Updated Claude Code agent to use the public Claude platform plugin for multi-harness support. ([#12879](https://github.com/warpdotdev/warp/pull/12879)) — [@liliwilson](https://github.com/liliwilson) ✨
* Remote SSH Agent conversations now use bundled skills, home skills, and file-based global rules from the remote host. ([#12669](https://github.com/warpdotdev/warp/pull/12669)) — [@moirahuang](https://github.com/moirahuang) ✨
* Applied a file size limit on tree-sitter parsing to prevent memory spikes with very large files. ([#12696](https://github.com/warpdotdev/warp/pull/12696)) — [@acarl005](https://github.com/acarl005) ✨
* Added a Git Branch Status prompt chip that shows branch name with ahead/behind commit counts. ([#11938](https://github.com/warpdotdev/warp/pull/11938)) — [@BobbyWang0120](https://github.com/BobbyWang0120) ✨
* Shipped channel-specific warpctrl CLI wrappers with PATH install/uninstall support on macOS. ([#12705](https://github.com/warpdotdev/warp/pull/12705)) — [@zachlloyd](https://github.com/zachlloyd) ✨
* Enabled cross-window tab dragging on stable for Windows and macOS. ([#12795](https://github.com/warpdotdev/warp/pull/12795)) — [@peicodes](https://github.com/peicodes) ✨
* Added eza completions. ([#12798](https://github.com/warpdotdev/warp/pull/12798)) — [@acarl005](https://github.com/acarl005) ✨
* Deferred PowerShell function name loading in the bootstrap to reduce startup latency. ([#12764](https://github.com/warpdotdev/warp/pull/12764)) — [@acarl005](https://github.com/acarl005) ✨
* Agent run CLI now resolves managed MCPs correctly. ([#12754](https://github.com/warpdotdev/warp/pull/12754)) — [@Legoben](https://github.com/Legoben) ✨
* Added a setting to auto-queue prompts until the end of a long-running command, preventing premature agent steering (enabled by default). ([#12587](https://github.com/warpdotdev/warp/pull/12587)) — [@harryalbert](https://github.com/harryalbert) ✨
* Suppressed transient “lost connection” banners during auto-recovery to reduce noise. ([#12757](https://github.com/warpdotdev/warp/pull/12757))
* Agent sessions now fail fast with specific error messages when PTY spawning fails. ([#12663](https://github.com/warpdotdev/warp/pull/12663)) — [@seemeroland](https://github.com/seemeroland) ✨
* Added a “Show hidden files” toggle to the Settings UI. ([#12710](https://github.com/warpdotdev/warp/pull/12710)) — [@moirahuang](https://github.com/moirahuang) ✨
* Local orchestration subagents now render with the local agent icon for clearer visual distinction. ([#12608](https://github.com/warpdotdev/warp/pull/12608)) — [@vkodithala](https://github.com/vkodithala) ✨
* Added a “Continue locally” button for in-progress cloud Oz runs so you can seamlessly switch to local execution. ([#12626](https://github.com/warpdotdev/warp/pull/12626)) — [@vkodithala](https://github.com/vkodithala) ✨
**Bug fixes**
* Fixed copying selected text from AI response blocks producing an empty clipboard. ([#12892](https://github.com/warpdotdev/warp/pull/12892))
* Fixed Ctrl+C not cancelling an in-progress AI stream. ([#12944](https://github.com/warpdotdev/warp/pull/12944))
* Fixed a panic when processing OSC 1337 escape sequences with a missing second parameter. ([#12889](https://github.com/warpdotdev/warp/pull/12889))
* Fixed a panic that could occur when restoring a conversation due to an invalid grid assertion. ([#12761](https://github.com/warpdotdev/warp/pull/12761)) — [@acarl005](https://github.com/acarl005) ✨
* Fixed a bug with cross-window drag and pinned tabs. ([#12926](https://github.com/warpdotdev/warp/pull/12926)) — [@peicodes](https://github.com/peicodes) ✨
* Fixed Codex plugin installation failing in some cases. ([#12919](https://github.com/warpdotdev/warp/pull/12919)) — [@liliwilson](https://github.com/liliwilson) ✨
* Re-displaying a local image in an AI response now reflects edits made to the file on disk instead of showing a stale cached copy. ([#12840](https://github.com/warpdotdev/warp/pull/12840)) — [@zachlloyd](https://github.com/zachlloyd) ✨
* Prevented auto-update from using a 0-byte corrupted installer file. ([#12806](https://github.com/warpdotdev/warp/pull/12806)) — [@acarl005](https://github.com/acarl005) ✨
* Fixed strong model handle captures in subscriptions that could cause memory leaks. ([#12914](https://github.com/warpdotdev/warp/pull/12914)) — [@acarl005](https://github.com/acarl005) ✨
* Fixed the Ctrl+Tab switcher to show tab colors on icons and lead with the tab title. ([#12776](https://github.com/warpdotdev/warp/pull/12776)) — [@GeekLuffy](https://github.com/GeekLuffy) ✨
* Fixed focus stealing when a prompt is queued. ([#12833](https://github.com/warpdotdev/warp/pull/12833)) — [@harryalbert](https://github.com/harryalbert) ✨
* Fixed mouse down events being dispatched even when already handled by a child element. ([#12079](https://github.com/warpdotdev/warp/pull/12079)) — [@adrawbond-alto](https://github.com/adrawbond-alto) ✨
* Fixed AI being unavailable on the free plan for users whose only credential was a connected SuperGrok (xAI/Grok) subscription. ([#12831](https://github.com/warpdotdev/warp/pull/12831)) — [@jefflloyd](https://github.com/jefflloyd) ✨
* Fixed fork button tooltip, command insertion behavior, and `/continue-locally` button visibility in AI blocks. ([#12704](https://github.com/warpdotdev/warp/pull/12704)) — [@harryalbert](https://github.com/harryalbert) ✨
* Fixed opening a markdown file always creating a new pane instead of focusing an existing one. ([#12489](https://github.com/warpdotdev/warp/pull/12489))
* Fixed several cross-window tab dragging bugs. ([#12746](https://github.com/warpdotdev/warp/pull/12746)) — [@peicodes](https://github.com/peicodes) ✨
* Fixed Cmd+K (clear conversation) not cancelling in-progress agent tasks and tool calls. ([#12555](https://github.com/warpdotdev/warp/pull/12555)) — [@acarl005](https://github.com/acarl005) ✨
* Fixed cross-window tab dragging incorrectly splitting tab groups. ([#12753](https://github.com/warpdotdev/warp/pull/12753)) — [@johnturcoo](https://github.com/johnturcoo) ✨
* Fixed rewind restoring an empty input after slash/skill-command agent prompts. ([#12149](https://github.com/warpdotdev/warp/pull/12149)) — [@vkodithala](https://github.com/vkodithala) ✨
* Fixed missing LC\_RPATH in the macOS standalone CLI binary causing dyld failures on startup. ([#12739](https://github.com/warpdotdev/warp/pull/12739))
* Fixed file saves not working in remote sessions. ([#12742](https://github.com/warpdotdev/warp/pull/12742)) — [@MaggieShan](https://github.com/MaggieShan) ✨
* Fixed editor find/replace not matching non-ASCII text (e.g. Chinese characters). ([#12547](https://github.com/warpdotdev/warp/pull/12547)) — [@maxmilian](https://github.com/maxmilian) ✨
* Fixed up/down arrow keys not being captured inside the queued-prompt inline editor. ([#12591](https://github.com/warpdotdev/warp/pull/12591)) — [@harryalbert](https://github.com/harryalbert) ✨
* Fixed an issue where focus would not return to the input box after running a command while blocks were selected in the block list. ([#12583](https://github.com/warpdotdev/warp/pull/12583))
**Oz updates**
* Support cloning GitLab repositories during cloud environment setup. ([#12659](https://github.com/warpdotdev/warp/pull/12659)) — [@captainsafia](https://github.com/captainsafia) ✨
### 2026.06.17 (v0.2026.06.17.09.49)
[Section titled “2026.06.17 (v0.2026.06.17.09.49)”](#20260617-v0202606170949)
**New features**
* Adds support for git chips over remote environments. ([#12542](https://github.com/warpdotdev/warp/pull/12542))
* Added a “Format on save” setting (Settings → Code) to disable automatic LSP formatting on save while keeping other LSP features enabled. ([#12254](https://github.com/warpdotdev/warp/pull/12254))
* Conversations can now be renamed using the `/rename-conversation` command. ([#12323](https://github.com/warpdotdev/warp/pull/12323))
**Improvements**
* Added a warp\://settings/warp\_agent deep link that opens the Warp Agent settings page directly. ([#12720](https://github.com/warpdotdev/warp/pull/12720))
* Added hover tooltips to all git dialog action buttons (Commit, Push, Publish, Create PR, View PR) so their purpose is clear at a glance. ([#12709](https://github.com/warpdotdev/warp/pull/12709))
* Transient network error banners now surface the underlying error details to aid in debugging connection issues. ([#12497](https://github.com/warpdotdev/warp/pull/12497))
* Warp now offers a one-time prompt to enable automatic local-to-cloud handoff when your computer sleeps during a local agent run, and shows a confirmation toast when an automatic handoff completes. ([#12514](https://github.com/warpdotdev/warp/pull/12514))
* \[Windows] Reduced lag when switching tabs to a WSL tab. ([#12492](https://github.com/warpdotdev/warp/pull/12492))
* The experimental tmux-based SSH warpification flow has been removed in favor of Warp’s SSH extension. Users who had opted into the tmux wrapper see a one-time notice on their next SSH session. ([#12478](https://github.com/warpdotdev/warp/pull/12478))
* Hitting enter with an empty input and queued prompt(s) now automatically sends your top queued prompt. ([#12536](https://github.com/warpdotdev/warp/pull/12536))
* Conversations can now be renamed by double-clicking their title in the conversation list. ([#12409](https://github.com/warpdotdev/warp/pull/12409))
* Double-click the empty area of the vertical tabs panel to open a new tab. ([#12506](https://github.com/warpdotdev/warp/pull/12506))
* Added an opt-in setting (`warpify.ssh.reuse_existing_control_master`) that makes Warp’s SSH wrapper attach to an existing SSH ControlMaster for the destination host instead of always creating its own, preserving user-managed masters and their port forwards. ([#12465](https://github.com/warpdotdev/warp/pull/12465))
* Mermaid diagrams in AI responses now scale to the full available width instead of being constrained to a fixed height. ([#12488](https://github.com/warpdotdev/warp/pull/12488))
* Agent completion notifications are no longer shown when a follow-up prompt is queued to auto-send. ([#12461](https://github.com/warpdotdev/warp/pull/12461))
* SuperGrok: connecting an xAI Grok subscription to use Grok models in the agent is now available on stable (previously dogfood only). ([#12494](https://github.com/warpdotdev/warp/pull/12494))
* Agent questions now size to their content, allowing a single question to use more vertical room. ([#11719](https://github.com/warpdotdev/warp/pull/11719))
* Cloud agents that pause to wait for inbound events from child agents are now correctly held in a “waiting” state instead of being prematurely treated as completed. ([#12084](https://github.com/warpdotdev/warp/pull/12084))
**Bug fixes**
* Added a fallback to paste the xAI authorization code when connecting a SuperGrok subscription, so sign-in can complete even when the browser can’t reach the loopback redirect. ([#12599](https://github.com/warpdotdev/warp/pull/12599))
* Fixed several tab group bugs affecting special system-managed tabs. ([#12706](https://github.com/warpdotdev/warp/pull/12706))
* Fixed macOS native window chrome events (e.g. window close/minimize) being dropped in certain situations. ([#12557](https://github.com/warpdotdev/warp/pull/12557))
* Project explorer now sorts numbered files in natural (numeric-aware) order — e.g. file2 before file10. ([#11991](https://github.com/warpdotdev/warp/pull/11991))
* Cloud agent runs and local agent conversations now automatically recover from transient network failures mid-turn (showing a “Reconnecting” status) instead of failing the run. ([#12431](https://github.com/warpdotdev/warp/pull/12431))
* Fixed an issue where pressing Ctrl-C to stop a command monitored by Warp Agent could leave the conversation stuck showing `Warping…`. ([#12623](https://github.com/warpdotdev/warp/pull/12623))
* Warp now immediately surfaces a clear error message when a required platform plugin is not installed correctly, instead of silently failing. ([#12471](https://github.com/warpdotdev/warp/pull/12471))
* Fixed child agent status chips lingering in the UI when agent runs fail immediately on start. ([#12649](https://github.com/warpdotdev/warp/pull/12649))
* Fixed a crash and mis-rendering when parsing certain Markdown content with very long delimiter runs.
* Fixed vertical tabs toolbar buttons appearing underneath macOS traffic light buttons when the tools panel is open. ([#12660](https://github.com/warpdotdev/warp/pull/12660))
* Fixed a regression where pane layout was not saved correctly when closing the app. ([#12672](https://github.com/warpdotdev/warp/pull/12672))
* Fixed double-slash prefix (e.g. `//home/user/...`) shown in the read\_skill action header when the skill is not yet indexed by Warp. ([#12668](https://github.com/warpdotdev/warp/pull/12668))
* \[Windows] Fixed pasted CRLF line endings breaking multi-line commands in POSIX shells. ([#12446](https://github.com/warpdotdev/warp/pull/12446))
* Fixed attaching files or context blocks via CLI rich input not working correctly. ([#11509](https://github.com/warpdotdev/warp/pull/11509))
* Command search in the terminal (Ctrl-R) now prioritizes commands in your history. ([#12600](https://github.com/warpdotdev/warp/pull/12600))
* Fixed a rare reversed line range when an AI file read truncated a file whose first line exceeded the remaining byte budget.
* Fixed queued prompts in sub-agent conversations sometimes not being sent when a sibling agent block obscured the turn-end signal. ([#12573](https://github.com/warpdotdev/warp/pull/12573))
* Fixed the code review file section header rendering opaque square corners behind its rounded background. ([#12447](https://github.com/warpdotdev/warp/pull/12447))
* Fixed inline images emitted during shell startup (e.g. `fastfetch`) being dropped instead of rendered. ([#10478](https://github.com/warpdotdev/warp/pull/10478))
* Fixed git diff status chips not appearing in the prompt when untracked directories (e.g. nested repos or worktrees) are present. ([#12590](https://github.com/warpdotdev/warp/pull/12590))
* Fixed custom inference endpoint and BYO API key settings inputs becoming unreadable after switching themes. ([#12521](https://github.com/warpdotdev/warp/pull/12521))
* Fixed the theme picker causing the top tab bar to pass underneath macOS traffic light buttons. ([#11052](https://github.com/warpdotdev/warp/pull/11052))
* Fixed header text alignment in markdown viewer — headers now share the same left edge as paragraph text. ([#12371](https://github.com/warpdotdev/warp/pull/12371))
* Fixed “Open skill” buttons sharing hover and click state when multiple skills are read in one agent block. ([#12429](https://github.com/warpdotdev/warp/pull/12429))
* Fixed code review “attach as context” actions (diff hunk, selection, and diff set) sometimes targeting a different agent conversation than the one in focus when using orchestrated agents. ([#12524](https://github.com/warpdotdev/warp/pull/12524))
* Fixed Cmd+Enter incorrectly starting new agent conversations instead of submitting the current prompt. ([#12540](https://github.com/warpdotdev/warp/pull/12540))
* Fixed launch crashes on Macs with legacy Metal driver stacks by pinning the Metal AIR bytecode target to the app’s minimum macOS deployment target. ([#12496](https://github.com/warpdotdev/warp/pull/12496))
* Fixed CLI environment updates resetting secret selection to “All Secrets”. ([#12280](https://github.com/warpdotdev/warp/pull/12280))
* Fixed Shift+Backspace deleting a whole word instead of one character on Windows. ([#11563](https://github.com/warpdotdev/warp/pull/11563))
* Fixed connected SuperGrok subscriptions silently failing to authenticate once the OAuth access token expired; tokens are now refreshed automatically. ([#12516](https://github.com/warpdotdev/warp/pull/12516))
* Fixed user-installed CLIs (e.g. `gcloud`, `gh`) and language servers failing to resolve when shell startup files print output on launch. ([#12473](https://github.com/warpdotdev/warp/pull/12473))
* Fixed commands rendering with duplicated or missing characters when using the Warp prompt with zsh themes (e.g. oh-my-zsh’s robbyrussell) alongside plugins such as zsh-syntax-highlighting. ([#12438](https://github.com/warpdotdev/warp/pull/12438))
* Fixed `/fork` with an attached image — attachments are now sent with the initial prompt in the new forked conversation. ([#12376](https://github.com/warpdotdev/warp/pull/12376))
* \[Windows] Fixed terminal response sequences getting dropped, which caused `edit.exe` to hang indefinitely and NeoVim 0.12 to start slowly. ([#11906](https://github.com/warpdotdev/warp/pull/11906))
* Orchestrated child agents can now correctly read plans from parent agents. ([#12359](https://github.com/warpdotdev/warp/pull/12359))
* Fixed MCP tool argument coercion not applying integer conversion recursively to nested object, array, and oneOf schemas. ([#10640](https://github.com/warpdotdev/warp/pull/10640))
**Oz updates**
* By default, cloud agent runs now continue without configured MCP servers that fail to start within the 20-second startup window, instead of failing the run. ([#12470](https://github.com/warpdotdev/warp/pull/12470))
### 2026.06.10 (v0.2026.06.10.09.27)
[Section titled “2026.06.10 (v0.2026.06.10.09.27)”](#20260610-v0202606100927)
**New features**
* Git operations are now supported on remote sessions ([#12230](https://github.com/warpdotdev/warp/pull/12230))
**Improvements**
* Added a toggle to show hidden files in the Project Explorer. ([#9532](https://github.com/warpdotdev/warp/pull/9532))
* Remote sessions now discover and apply project rules such as `WARP.md` and `AGENTS.md`. ([#11460](https://github.com/warpdotdev/warp/pull/11460))
* Added a setting to submit Rich Input on Ctrl+Enter, so Enter inserts a newline for easier multi-line prompt composition with CLI agents. ([#11723](https://github.com/warpdotdev/warp/pull/11723))
* Added keyboard shortcuts for cycling through orchestrator and subagent sessions in Agent Mode. ([#11760](https://github.com/warpdotdev/warp/pull/11760))
* Added a way to jump directly to the latest agent message in the terminal. ([#11924](https://github.com/warpdotdev/warp/pull/11924))
* Mermaid diagrams now tolerate and apply supported frontmatter formatting directives when rendered in Warp. ([#12155](https://github.com/warpdotdev/warp/pull/12155))
* Queued prompt rows now render at the same text size as the prompt input. ([#12171](https://github.com/warpdotdev/warp/pull/12171))
* Added a setting to hide the title bar search bar in the vertical tab layout. ([#12249](https://github.com/warpdotdev/warp/pull/12249))
* Terminal commands can now be queued in addition to prompts. ([#12259](https://github.com/warpdotdev/warp/pull/12259))
* Improved detection of natural-language input versus shell commands in the input editor. ([#12273](https://github.com/warpdotdev/warp/pull/12273))
* Enabled input method editor (IME) support on Linux X11 for composing non-Latin text. ([#12277](https://github.com/warpdotdev/warp/pull/12277))
* Improved the error message shown when Warp loses connection while receiving an agent response. ([#12382](https://github.com/warpdotdev/warp/pull/12382))
**Bug fixes**
* Fixed terminal secret redaction when multibyte UTF-8 characters appear before a custom redaction regex match. ([#9521](https://github.com/warpdotdev/warp/pull/9521))
* Fix block navigation with arrow keys, when focused a block (no longer triggers input editor dropdown navigation). Introduced a setting for this as well, to configure whether input takes back focus. ([#10095](https://github.com/warpdotdev/warp/pull/10095))
* Fixed the IME composition cursor area not refreshing after a terminal redraw. ([#10443](https://github.com/warpdotdev/warp/pull/10443))
* Fixed the MCP server “+ Add” flow bypassing the secret redaction check. ([#11297](https://github.com/warpdotdev/warp/pull/11297))
* Fixed browser keyboard shortcuts being intercepted in WASM (browser) sessions. ([#11778](https://github.com/warpdotdev/warp/pull/11778))
* Fixed focus reporting events not being emitted for normal-screen terminal applications. ([#11946](https://github.com/warpdotdev/warp/pull/11946))
* Fixed latency between commands caused by the Node.js version prompt chip running `node --version` on every prompt; detection is now skipped when the chip is disabled and cached otherwise. ([#11986](https://github.com/warpdotdev/warp/pull/11986))
* Fix discovery and refresh of symlinked project skills in remote repositories. ([#12051](https://github.com/warpdotdev/warp/pull/12051))
* Fixed the Nix flake build by correcting the enabled build features. ([#12070](https://github.com/warpdotdev/warp/pull/12070))
* Fixed a crash that could occur after clearing and resizing a terminal with scrollback. ([#12085](https://github.com/warpdotdev/warp/pull/12085))
* Fixed focus jumping to the prompt input while navigating an AI block’s code diff hunks with the arrow keys during an agent turn. ([#12107](https://github.com/warpdotdev/warp/pull/12107))
* Reduced memory usage of the file watcher on large projects by no longer watching gitignored directories (e.g. node\_modules, build output). ([#12122](https://github.com/warpdotdev/warp/pull/12122))
* Fixed a “cannot detect diffs” error in the code review view for some repositories. ([#12126](https://github.com/warpdotdev/warp/pull/12126))
* Fixed excessive memory usage (and inotify watch exhaustion) on Linux when a Warp session navigated into a large non-git directory; lazy directory roots are now watched incrementally as folders are expanded instead of recursively up front. ([#12176](https://github.com/warpdotdev/warp/pull/12176))
* Fixed the app hanging when switching tabs in very large repositories. ([#12221](https://github.com/warpdotdev/warp/pull/12221))
* Fixed file search returning no results for very large repositories. ([#12226](https://github.com/warpdotdev/warp/pull/12226))
* Discover project skills under force-included paths when repo metadata is lazily loaded. ([#12235](https://github.com/warpdotdev/warp/pull/12235))
* Fixed skill path normalization on Windows when paths use backslash separators. ([#12281](https://github.com/warpdotdev/warp/pull/12281))
* Fixed incorrect results in file search filtering. ([#12379](https://github.com/warpdotdev/warp/pull/12379))
* Applied the latest security patches. ([#12411](https://github.com/warpdotdev/warp/pull/12411))
**Oz updates**
* Agent handoff surfaces now accept empty prompts and support handing off in a single click. ([#11576](https://github.com/warpdotdev/warp/pull/11576))
* Added a setting to control whether orchestration messages are expanded or collapsed by default. ([#12219](https://github.com/warpdotdev/warp/pull/12219))
* Long-running command agent boxes can now be resized by dragging their top or left edge. ([#12236](https://github.com/warpdotdev/warp/pull/12236))
* Fixed CLI subagent interactions being unexpectedly cancelled for Oz agents. ([#12384](https://github.com/warpdotdev/warp/pull/12384))
### 2026.06.03 (v0.2026.06.03.09.49)
[Section titled “2026.06.03 (v0.2026.06.03.09.49)”](#20260603-v0202606030949)
**New features**
* Added the installation path into de Windows App Paths Registry ([#10805](https://github.com/warpdotdev/warp/pull/10805)) — [@Cocodrulo](https://github.com/Cocodrulo) ✨
* Queue multiple follow-up prompts while the agent is working either by using the `/queue` command, prompt queueing mode (activated via a chip in the warping line), and/or by changing your default prompt submission mode to “Queue until response finishes” in settings. ([#12081](https://github.com/warpdotdev/warp/pull/12081))
**Improvements**
* Add configurable absolute and relative line numbers for code editors. ([#10012](https://github.com/warpdotdev/warp/pull/10012))
* Added support for warp\://action/open\_file\_editor URIs to open files at specific locations from external apps ([#10233](https://github.com/warpdotdev/warp/pull/10233))
* Agent requests now include PR and repository metadata, enabling better context-aware responses ([#10391](https://github.com/warpdotdev/warp/pull/10391))
* Cloud environment creation modal now auto-focuses the name field for quicker setup ([#11233](https://github.com/warpdotdev/warp/pull/11233))
* Authentication secrets for agent orchestration can now be deleted directly from the selector menu ([#11241](https://github.com/warpdotdev/warp/pull/11241))
* Conversation usage breakdown now surfaces inference vs. platform credit split ([#11441](https://github.com/warpdotdev/warp/pull/11441))
* Added Command Palette entries for toggle settings that were missing across Appearance, Features, Code, Privacy, AI, and other settings pages ([#11512](https://github.com/warpdotdev/warp/pull/11512))
* Cloud agent setup mode now uses the improved queued prompt UI ([#11547](https://github.com/warpdotdev/warp/pull/11547))
* Cloud agent sessions can now be started without an initial prompt ([#11573](https://github.com/warpdotdev/warp/pull/11573))
* Updated `/compact-and` and `/fork-and-compact` commands to use the new queued prompts UI ([#11575](https://github.com/warpdotdev/warp/pull/11575))
* Polished the orchestration pill bar and segmented control UI to better match design specs ([#11578](https://github.com/warpdotdev/warp/pull/11578))
* Remote project skill locations are now correctly propagated through the UI ([#11581](https://github.com/warpdotdev/warp/pull/11581))
* Cloud agent conversations now always display the fast-forward chip as enabled, reflecting actual behavior ([#11690](https://github.com/warpdotdev/warp/pull/11690))
* Added setting to control whether mid-conversation prompts interrupt or queue the agent ([#11746](https://github.com/warpdotdev/warp/pull/11746))
* Added missing flag completions for `gh pr merge`. ([#11764](https://github.com/warpdotdev/warp/pull/11764))
* Enabled handoff for locally orchestrated conversations. ([#11768](https://github.com/warpdotdev/warp/pull/11768))
* Maximized orchestration pane now stays maximized when opening sub-agent conversations ([#11776](https://github.com/warpdotdev/warp/pull/11776))
* Improved lightbox UX: background click now dismisses correctly, and light theme button rendering is fixed ([#11783](https://github.com/warpdotdev/warp/pull/11783))
* Reordered the tools panel to show the project explorer first and conversation list second ([#11843](https://github.com/warpdotdev/warp/pull/11843))
* Remote project skill locations are now correctly resolved in tool output ([#11863](https://github.com/warpdotdev/warp/pull/11863))
* Added ‘Send Now’ button to queued prompts for immediate execution ([#11880](https://github.com/warpdotdev/warp/pull/11880))
* Vertical tab agent icons now reflect active child-agent status for orchestration sessions. ([#11895](https://github.com/warpdotdev/warp/pull/11895))
* Added dotnet CLI completions ([#11919](https://github.com/warpdotdev/warp/pull/11919))
* Improved queued prompt hover behavior and drag handle UX ([#12067](https://github.com/warpdotdev/warp/pull/12067))
**Bug fixes**
* Fixed custom themes not syncing correctly across machines when using Settings Sync ([#9728](https://github.com/warpdotdev/warp/pull/9728)) — [@nisavid](https://github.com/nisavid) ✨
* Fixed MCP install/update modal primary buttons using incorrect button styling ([#10586](https://github.com/warpdotdev/warp/pull/10586))
* AI responses that contain Markdown tables now render as structured tables in Stable instead of monospaced pipe-table blocks. ([#10683](https://github.com/warpdotdev/warp/pull/10683))
* Fixed MCP server log files growing unbounded; logs are now rotated to cap disk usage ([#10874](https://github.com/warpdotdev/warp/pull/10874)) — [@david-engelmann](https://github.com/david-engelmann) ✨
* Fix Windows PowerShell command discovery when localized executable names are emitted in a non-UTF-8 code page. ([#11203](https://github.com/warpdotdev/warp/pull/11203)) — [@cesaryuan](https://github.com/cesaryuan) ✨
* Fixed ‘Maximize Pane’ option missing from the overflow menu in Rendered Markdown mode ([#11258](https://github.com/warpdotdev/warp/pull/11258)) — [@wzc520pyfm](https://github.com/wzc520pyfm) ✨
* Artifact upload failures now surface actionable quota-limit details when upload limits are reached. ([#11386](https://github.com/warpdotdev/warp/pull/11386))
* Fixed Tab configs: pressing Space while a parameter dropdown is focused now selects the item instead of switching fields ([#11412](https://github.com/warpdotdev/warp/pull/11412))
* Fixed find highlights lingering on AI blocks after closing the find bar. ([#11458](https://github.com/warpdotdev/warp/pull/11458))
* Fixed custom LLM models being reset to defaults during preference reconciliation on app startup ([#11655](https://github.com/warpdotdev/warp/pull/11655))
* Fixed new model choices popup banner overflowing on mobile/thin devices ([#11685](https://github.com/warpdotdev/warp/pull/11685))
* Shared cloud-agent session details now show a muted no-access notice when run metadata is restricted instead of displaying a raw permission error. ([#11686](https://github.com/warpdotdev/warp/pull/11686))
* Fixed the team settings owner badge being unreadable on some themes. ([#11689](https://github.com/warpdotdev/warp/pull/11689))
* Fixed terminal input being incorrectly active during GitHub Actions session shares ([#11691](https://github.com/warpdotdev/warp/pull/11691))
* Fixed Windows terminal startup failures caused by REG\_MULTI\_SZ registry environment variables being passed to CreateProcessW ([#11714](https://github.com/warpdotdev/warp/pull/11714))
* Fixed orchestration session restoration so the pill bar, child transcript name resolution, restored remote-child cloud transcripts, and cloud-parent panes all work correctly after a Warp restart. ([#11722](https://github.com/warpdotdev/warp/pull/11722))
* Fixed conversation creator profiles not displaying correctly in shared conversations ([#11725](https://github.com/warpdotdev/warp/pull/11725))
* Fixed a crash when rendering AI reasoning or summaries that contain multiple markdown images. ([#11766](https://github.com/warpdotdev/warp/pull/11766))
* Clarify BYOK / Custom inference settings copy: API keys are stored only on your device, never on Warp’s servers, and used to make requests to your chosen model provider. ([#11780](https://github.com/warpdotdev/warp/pull/11780))
* Fixed `/app` in Warp-on-Web opening the wrong Agent experience instead of the Cloud Agent start page. ([#11781](https://github.com/warpdotdev/warp/pull/11781))
* Fixed working directories not being cleaned up correctly after code review sessions ([#11789](https://github.com/warpdotdev/warp/pull/11789))
* Fixed duplicate codebase indexing entries appearing for remote server connections ([#11792](https://github.com/warpdotdev/warp/pull/11792))
* Fixed orchestration pill bar hover card showing the wrong harness for non-Warp child agents (e.g. Claude Code). ([#11800](https://github.com/warpdotdev/warp/pull/11800))
* Fixed Continue button remaining active when the New API key form is incomplete ([#11802](https://github.com/warpdotdev/warp/pull/11802))
* Removed built-in feedback skill; the `/feedback` command now consistently opens the external feedback form ([#11806](https://github.com/warpdotdev/warp/pull/11806))
* Fixed a crash when the agent’s context window limit is exceeded ([#11813](https://github.com/warpdotdev/warp/pull/11813))
* Fixed agent conversations sometimes failing to restore after restarting Warp ([#11814](https://github.com/warpdotdev/warp/pull/11814))
* Fix find match highlight position in initial `/agent` queries ([#11823](https://github.com/warpdotdev/warp/pull/11823)) — [@AndreKalberer](https://github.com/AndreKalberer) ✨
* Fixed queued prompts panel appearing alongside inline menus, causing visual overlap ([#11848](https://github.com/warpdotdev/warp/pull/11848))
* Fixed symlinked gitignored paths not being handled correctly in code review ([#11856](https://github.com/warpdotdev/warp/pull/11856))
* Fixed duplicated leading characters in wrapped zsh command blocks when using the Warp prompt. ([#11868](https://github.com/warpdotdev/warp/pull/11868))
* Fixed the Accept button staying enabled in the multi-agent run card when “New API key” was selected in the harness API key picker without a key being created. ([#11904](https://github.com/warpdotdev/warp/pull/11904))
* Fixed billing usage display showing incorrect per-user base credit limits ([#11910](https://github.com/warpdotdev/warp/pull/11910))
* Fixed apply-diff/edit-file sending full file contents instead of only changed ranges after accepting edits ([#11987](https://github.com/warpdotdev/warp/pull/11987))
* Fixed duplicate Command Palette entries for mouse reporting. ([#12011](https://github.com/warpdotdev/warp/pull/12011))
* Fixed project skill refreshes causing UI stalls when unrelated files change in large repositories. ([#12040](https://github.com/warpdotdev/warp/pull/12040))
* Fixed the orchestration pill bar’s scrollbar overlapping the agent chips. ([#12045](https://github.com/warpdotdev/warp/pull/12045))
* Fixed a crash when trying to use the microphone on macOS ([#12074](https://github.com/warpdotdev/warp/pull/12074))
* Fixed several queued prompt issues: `/queue` command behavior in empty conversations and other paper cuts ([#12105](https://github.com/warpdotdev/warp/pull/12105))
### 2026.05.27 (v0.2026.05.27.15.44)
[Section titled “2026.05.27 (v0.2026.05.27.15.44)”](#20260527-v0202605271544)
**New features**
* Added git operations to the code review pane. ([#11716](https://github.com/warpdotdev/warp/pull/11716))
**Improvements**
* A new, faster implementation of find is now available as an opt-in setting under Settings → Features → Asynchronous find, keeping the UI responsive on large outputs. ([#11555](https://github.com/warpdotdev/warp/pull/11555))
* Custom inference endpoints now show token usage with friendly alias names in Agent Mode. ([#11496](https://github.com/warpdotdev/warp/pull/11496))
* Added AWS Bedrock indicators in the model selector for Bedrock-enabled models. ([#11358](https://github.com/warpdotdev/warp/pull/11358))
* The Oz CLI now has commands for operating over reusable agents. ([#11286](https://github.com/warpdotdev/warp/pull/11286))
* Added the ability to view attached images in agent conversations. ([#11426](https://github.com/warpdotdev/warp/pull/11426))
* Markdown files opened from remote SSH sessions now render in the markdown viewer with Rendered/Raw toggle support. ([#11427](https://github.com/warpdotdev/warp/pull/11427))
* Added a QR code flow for remote-control sessions. ([#11435](https://github.com/warpdotdev/warp/pull/11435))
* Mermaid diagrams in notebooks can now be opened in a lightbox by clicking the rendered diagram. ([#11548](https://github.com/warpdotdev/warp/pull/11548))
* Rich text editor newlines now render as line breaks instead of paragraph breaks, fixing unusually large spacing. ([#10293](https://github.com/warpdotdev/warp/pull/10293))
* Orchestration child agent pills now sort by status, surfacing attention-needed items first. ([#11363](https://github.com/warpdotdev/warp/pull/11363))
* The orchestrator pill now shows in-progress status while child agents are running. ([#11367](https://github.com/warpdotdev/warp/pull/11367))
* Added a disconnection banner when remote SSH sessions lose connection. ([#11565](https://github.com/warpdotdev/warp/pull/11565))
* Improved GitHub authentication error messages with more detailed information. ([#11248](https://github.com/warpdotdev/warp/pull/11248))
* Warp now exposes a focus URL in terminal session environments so external notification tools can return focus to the originating pane. ([#11130](https://github.com/warpdotdev/warp/pull/11130))
* Added podman exec/run support for warpify subshells. ([#9831](https://github.com/warpdotdev/warp/pull/9831))
* Added in-session size-based rotation for warp.log so the log no longer grows unbounded within a session. ([#11000](https://github.com/warpdotdev/warp/pull/11000))
**Bug fixes**
* Stopped tearing down and re-opening the orchestration connection on every status transition, reducing reconnect churn. ([#11574](https://github.com/warpdotdev/warp/pull/11574))
* Fixed free solo users seeing the legacy Billing and usage settings page instead of the V2 page. ([#11434](https://github.com/warpdotdev/warp/pull/11434))
* Fixed file edit diff application when a create and delete target the same path. ([#11516](https://github.com/warpdotdev/warp/pull/11516))
* Fixed an issue that could prevent an AI query and its output from showing up. ([#11494](https://github.com/warpdotdev/warp/pull/11494))
* Fixed command execution requests being sent while disconnected from a remote server. ([#11558](https://github.com/warpdotdev/warp/pull/11558))
* Fixed URL redirects not working correctly. ([#11353](https://github.com/warpdotdev/warp/pull/11353))
* Fixed a Linux file-watcher bug where certain git events were not being sent. ([#11464](https://github.com/warpdotdev/warp/pull/11464))
* Fixed the code review panel showing “Unable to load file content” when opening the same remote SSH repo in multiple tabs. ([#11418](https://github.com/warpdotdev/warp/pull/11418))
* Fixed the remote control button incorrectly appearing in cloud conversation transcripts. ([#11292](https://github.com/warpdotdev/warp/pull/11292))
* Fixed notification dots not appearing on vertical tabs when the inbox panel is hidden. ([#11611](https://github.com/warpdotdev/warp/pull/11611))
* Fixed local-to-cloud handoff for remote SSH sessions, which was previously broken. ([#11453](https://github.com/warpdotdev/warp/pull/11453))
* Fixed pasting raw image data to CLI agents. ([#11627](https://github.com/warpdotdev/warp/pull/11627))
* Fixed gitignore rules not being correctly inherited by nested directories during codebase indexing. ([#11698](https://github.com/warpdotdev/warp/pull/11698))
* Fixed Ctrl+C in certain terminal programs erroneously closing the entire session on Windows. ([#10976](https://github.com/warpdotdev/warp/pull/10976))
* Fixed rendering issues on the Intel HD Graphics 2500 integrated GPU. ([#11454](https://github.com/warpdotdev/warp/pull/11454))
* Fixed a zsh bootstrapping issue where commands could be duplicated when using oh-my-zsh with the allexport option. ([#11673](https://github.com/warpdotdev/warp/pull/11673))
* Fixed warpify using incorrect path separators for shell configuration files on some platforms. ([#10584](https://github.com/warpdotdev/warp/pull/10584))
* The tab’s working directory and git branch indicator now update when a process emits an OSC 7 escape sequence to report a new CWD (e.g. worktrunk’s wt switch). ([#9279](https://github.com/warpdotdev/warp/pull/9279))
* Orchestration child agents are now preserved across restart so agent names and child pills restore correctly. ([#10794](https://github.com/warpdotdev/warp/pull/10794))
**Oz updates**
* Added search to the Oz Cloud API Keys settings page. ([#11307](https://github.com/warpdotdev/warp/pull/11307))
* Fixed Oz cloud agent GitHub CLI authentication by writing refreshed credentials to gh’s expected hosts.yml file. ([#11492](https://github.com/warpdotdev/warp/pull/11492))
* Added an execution profile permission for controlling whether agents can use run\_agents. ([#11225](https://github.com/warpdotdev/warp/pull/11225))
### 2026.05.20 (v0.2026.05.20.09.21)
[Section titled “2026.05.20 (v0.2026.05.20.09.21)”](#20260520-v0202605200921)
**Improvements**
* Added support for double-clicking pane dividers to evenly redistribute panes in a split. ([#11293](https://github.com/warpdotdev/warp/pull/11293))
* The new-tab worktree menu now abbreviates the home directory to \~, left-truncates long paths so the trailing repo name stays visible, and surfaces the full absolute path on hover (#10862). ([#10958](https://github.com/warpdotdev/warp/pull/10958))
* Added a create-environment flow to the orchestration environment picker. ([#10857](https://github.com/warpdotdev/warp/pull/10857))
* Added a setting to control terminal clipboard access via OSC 52, with a warning banner shown when access is blocked.
* Restricted OSC 52 clipboard write access behind a new user-configurable setting.
* Added confirmation dialogs when reloading credits during team-leave or member-removal flows. ([#11366](https://github.com/warpdotdev/warp/pull/11366))
* Enabled custom inference endpoint configuration for AI models on stable. ([#11450](https://github.com/warpdotdev/warp/pull/11450))
* Custom AI model selection is no longer available for cloud agent runs; custom endpoints remain available for local agents and non-cloud conversations. ([#11219](https://github.com/warpdotdev/warp/pull/11219))
* Enabled solo-user bring-your-own-key (BYOK) support and launched the redesigned Billing & Usage page. ([#11437](https://github.com/warpdotdev/warp/pull/11437))
* Updated seat-limit messaging on the Teams settings page to direct users to the upgrade page. ([#11288](https://github.com/warpdotdev/warp/pull/11288))
* Added host labels to remote repository and file displays in code review; removed the Open Repo button for remote sessions. ([#11423](https://github.com/warpdotdev/warp/pull/11423), [#11299](https://github.com/warpdotdev/warp/pull/11299))
* Added a “Create new branch” option to the branch switcher. ([#10610](https://github.com/warpdotdev/warp/pull/10610))
* Added CLI commands for managing API keys. ([#10998](https://github.com/warpdotdev/warp/pull/10998))
* Added a keybinding to toggle file navigation in Code Review. ([#11077](https://github.com/warpdotdev/warp/pull/11077))
* Enabled the `CMD+O` shortcut and `@` context menu in remote SSH sessions. ([#11295](https://github.com/warpdotdev/warp/pull/11295))
* Added diff statistics to the diff chip in remote SSH sessions. ([#11214](https://github.com/warpdotdev/warp/pull/11214))
**Bug fixes**
* Fixed a bug where Warp could be restored as a 1px-wide window on macOS after using the green title-bar tile button (#10083). ([#10855](https://github.com/warpdotdev/warp/pull/10855))
* Fixed code review comments being routed to invisible child agent terminals during orchestration. ([#11340](https://github.com/warpdotdev/warp/pull/11340))
* Fixed orchestration config picker menus not matching their picker fields. ([#11289](https://github.com/warpdotdev/warp/pull/11289))
* Fixed the git diff prompt chip flickering on entering a repository, and stale git diff state on the prompt chip and code review button when leaving a repository. ([#11242](https://github.com/warpdotdev/warp/pull/11242))
* Fixed uninterpolated session ID placeholders appearing in the tmux warpification flow.
* Fixed DCS sequence validation incorrectly rejecting input from session viewers.
* Fixed AI being unavailable for users who had auto-reload enabled but zero remaining credits. ([#11420](https://github.com/warpdotdev/warp/pull/11420))
* Fixed a deadlock in secret redaction that could cause Warp to become unresponsive. ([#11428](https://github.com/warpdotdev/warp/pull/11428))
* Fixed tab focus to activate the next tab to the right after closing a tab. ([#11197](https://github.com/warpdotdev/warp/pull/11197))
* Fixed the agent model dropdown rendering in the new API key creation modal. ([#11187](https://github.com/warpdotdev/warp/pull/11187))
* Fixed broken Oz notifications caused by a stale Claude plugin version. ([#11204](https://github.com/warpdotdev/warp/pull/11204))
* Fixed broken skill links in the agent details panel. ([#11231](https://github.com/warpdotdev/warp/pull/11231))
* Fixed asset-loading errors on the WASM build. ([#11195](https://github.com/warpdotdev/warp/pull/11195))
**Oz updates**
* Oz now refreshes GitHub credentials during task runs to keep Git operations authenticated. ([#11338](https://github.com/warpdotdev/warp/pull/11338))
* Add a View in Oz action to orchestration child-agent pill menus. ([#11309](https://github.com/warpdotdev/warp/pull/11309))
* Added a macOS setting to automatically hand off active local Warp Agent sessions to Cloud Mode before sleep. ([#11049](https://github.com/warpdotdev/warp/pull/11049))
### 2026.05.18 (v0.2026.05.18.05.32)
[Section titled “2026.05.18 (v0.2026.05.18.05.32)”](#20260518-v0202605180532)
**New features**
* You can now hand off local Warp Agent conversations to the cloud. ([#10910](https://github.com/warpdotdev/warp/pull/10910))
**Improvements**
* Cloud conversations are now accessible via `/conversations`. ([#10800](https://github.com/warpdotdev/warp/pull/10800))
* Refreshed metadata and iconography for the cloud agent view entry block. ([#11088](https://github.com/warpdotdev/warp/pull/11088))
* Blocklist search now runs asynchronously for snappier command suggestions. ([#9618](https://github.com/warpdotdev/warp/pull/9618))
* Opening a cloud agent conversation now attaches to its existing session when one is available. ([#11097](https://github.com/warpdotdev/warp/pull/11097))
* Show the cloud agent environment name and setup status alongside vertical-tabs pwd. ([#11006](https://github.com/warpdotdev/warp/pull/11006))
* Added a ‘Your team is full’ alert above the invite header in Settings → Team. ([#10705](https://github.com/warpdotdev/warp/pull/10705))
* Cloud Mode initial runs now automatically retry after completing GitHub authentication. ([#10973](https://github.com/warpdotdev/warp/pull/10973))
* \[Tab configs] Tab configs now run their commands sequentially. ([#10698](https://github.com/warpdotdev/warp/pull/10698))
* Show server-provided `user_display_message` text in quota-limit errors. ([#10279](https://github.com/warpdotdev/warp/pull/10279))
* Added a “Clear” action to the terminal right-click context menu so clearing terminal output is discoverable without using the keyboard shortcut. ([#10612](https://github.com/warpdotdev/warp/pull/10612)) — @wzc520pyfm ✨
* Added a `warp://tab_config/<name>` deeplink that opens a saved tab config in the active window (or a new one with `?new_window=true`). ([#9379](https://github.com/warpdotdev/warp/pull/9379)) — @haha1903 ✨
* Skipped the SSH extension install on unsupported remote platforms. ([#10950](https://github.com/warpdotdev/warp/pull/10950))
* Skipped repo-menu git stats on startup to improve launch performance. ([#10937](https://github.com/warpdotdev/warp/pull/10937))
* Reduced unnecessary git operations on startup when the Code Review panel is closed. ([#10934](https://github.com/warpdotdev/warp/pull/10934))
**Bug fixes**
* Fixed Mermaid diagram text not rendering in Warp on Web. ([#11141](https://github.com/warpdotdev/warp/pull/11141))
* Clipped the inline menu header to prevent overflow in split panes. ([#10811](https://github.com/warpdotdev/warp/pull/10811)) — @SagarSDagdu ✨
* \[Windows] Inno Setup now terminates the minidump server process if it fails to exit. ([#10766](https://github.com/warpdotdev/warp/pull/10766))
* \[Linux] Fixed Warp on Raspberry Pi. ([#10688](https://github.com/warpdotdev/warp/pull/10688))
* Stop waiting for file-based MCP servers we never attempted to start. ([#10969](https://github.com/warpdotdev/warp/pull/10969))
* Fixed restored command history after closing an SSH session. ([#10713](https://github.com/warpdotdev/warp/pull/10713)) — @fatsolko ✨
* Fixed local-repo session detection. ([#11019](https://github.com/warpdotdev/warp/pull/11019))
* Fixed remote-server connection failures when the socket path exceeded the sun\_path limit. ([#11009](https://github.com/warpdotdev/warp/pull/11009))
* The details panel for cloud agent runs now displays any failures fetching the agent metadata ([#10765](https://github.com/warpdotdev/warp/pull/10765))
* Fixed an MCP OAuth issue by creating the authenticated client before refreshing the token. ([#10984](https://github.com/warpdotdev/warp/pull/10984))
* Fixed errant task status reporting for cloud agent conversations. ([#10977](https://github.com/warpdotdev/warp/pull/10977))
* Set a minimum window size in AppKit so windows can no longer be restored at 1px wide. ([#10965](https://github.com/warpdotdev/warp/pull/10965))
* Improved remote-server install reliability by falling back to a cached client-side tarball upload when remote downloads fail. ([#10925](https://github.com/warpdotdev/warp/pull/10925))
* Respect the Markdown Viewer preference when opening Markdown file links. ([#9483](https://github.com/warpdotdev/warp/pull/9483)) — @maro20066600 ✨
**Oz updates**
* Run any agent harness in the cloud. Use Oz to spin up Claude Code or Codex agents in the cloud; Oz will help you track and steer the agents.
* Multi-agent orchestration. Warp Agents will now orchestrate swarms of subagents, allowing you to parallelize tasks.
### 2026.05.14 (v0.2026.05.13.09.15)
[Section titled “2026.05.14 (v0.2026.05.13.09.15)”](#20260514-v0202605130915)
**New features**
* Summary mode for vertical tabs provides a compact overview of tab contents ([#10793](https://github.com/warpdotdev/warp/pull/10793))
* You can now associate colors with directories so tabs automatically adopt the configured color when their working directory matches. Configure in **Settings** > **Appearance**. ([#10284](https://github.com/warpdotdev/warp/pull/10284))
**Improvements**
* vim ctrl-d / ctrl-u scroll the code editor by half a page in normal and visual mode ([#10582](https://github.com/warpdotdev/warp/pull/10582)) — @bradleyjames ✨
* Added an autonomy speedbump when agents use the Ask-User-Question tool ([#10433](https://github.com/warpdotdev/warp/pull/10433))
* When viewing conversation transcripts, you can now see the run duration on shell commands and start/end timestamp on hover ([#10423](https://github.com/warpdotdev/warp/pull/10423))
* Remote server binary is now verified with `--version` after install ([#10687](https://github.com/warpdotdev/warp/pull/10687))
* SSH extension now supports amd64 architecture and tracks install source in telemetry ([#10534](https://github.com/warpdotdev/warp/pull/10534))
* vim zz centers the cursor’s line vertically in the code editor ([#10581](https://github.com/warpdotdev/warp/pull/10581)) — @bradleyjames ✨
* Improved SSH extension install reliability — network failures now automatically retry via SCP fallback ([#10533](https://github.com/warpdotdev/warp/pull/10533))
* WSL sessions now prefer Linux-side git and gh binaries over Windows interop ([#10137](https://github.com/warpdotdev/warp/pull/10137)) — @JonRC ✨
* Added Raw and Rendered display controls for Mermaid code blocks in notebooks, planning documents, and rendered Markdown views. ([#10431](https://github.com/warpdotdev/warp/pull/10431))
* Unified agent status icons in the session management panel ([#10518](https://github.com/warpdotdev/warp/pull/10518))
* Tab config repo picker now abbreviates the home directory to `~`, left-truncates long paths so the trailing repo name stays visible, and surfaces the full absolute path on hover so deeply nested saved repos stay distinguishable. ([#9451](https://github.com/warpdotdev/warp/pull/9451)) — @saucy-tech ✨
* Enabled Oz OIDC authentication on stable ([#10468](https://github.com/warpdotdev/warp/pull/10468))
* Added ‘Reveal in Finder’ option to the code pane overflow menu ([#10334](https://github.com/warpdotdev/warp/pull/10334)) — @wzc520pyfm ✨
* Agent Mode can now help you remap Warp keyboard shortcuts — ask it to change a shortcut and it will edit your keybindings.yaml for you. ([#9415](https://github.com/warpdotdev/warp/pull/9415)) — @sebryu ✨
* Agent Mode project rules are now re-indexed on app startup ([#10377](https://github.com/warpdotdev/warp/pull/10377))
* Performance improvement for opening the Command Palette when in a project with a lot of files. ([#10332](https://github.com/warpdotdev/warp/pull/10332))
* Context window size is now configurable for custom model endpoints ([#10386](https://github.com/warpdotdev/warp/pull/10386))
* Added ‘Cycle Most Recent Tab’ as a third Ctrl+Tab behavior option in Settings ([#9658](https://github.com/warpdotdev/warp/pull/9658)) — @Akeuuh ✨
* Rename Pane is now reachable from Settings → Keyboard shortcuts as a remappable binding (`workspace:rename_active_pane`), in addition to the existing right-click context menu. Thanks @lonexreb! ([#9712](https://github.com/warpdotdev/warp/pull/9712)) — @lonexreb ✨
* Added the installation path into the Windows Registry ([#10607](https://github.com/warpdotdev/warp/pull/10607)) — @Cocodrulo ✨
**Bug fixes**
* Fixed shared session scrollback not restoring correctly ([#10780](https://github.com/warpdotdev/warp/pull/10780))
* Fixed duplicate commands rendering when restoring cloud mode conversations ([#10776](https://github.com/warpdotdev/warp/pull/10776))
* Fixed file edit diffs dropping the end of a partial trailing context line when applying multi-line replacements. ([#9623](https://github.com/warpdotdev/warp/pull/9623))
* Fixed a panic when the file watcher failed to initialize ([#10682](https://github.com/warpdotdev/warp/pull/10682))
* Hidden the sharer’s cursor in cloud agent sessions ([#10480](https://github.com/warpdotdev/warp/pull/10480))
* Fixed rich input trapping arrow keys in CLI Agent sessions ([#10556](https://github.com/warpdotdev/warp/pull/10556)) — @SagarSDagdu ✨
* Cloud agent run details now include platform cost in the “Credits used” total (and no longer drop the field entirely when one cost bucket is null). ([#10672](https://github.com/warpdotdev/warp/pull/10672))
* Fix MCP OAuth servers disconnecting after access-token TTL expires; refresh tokens are now used to obtain new access tokens before expiry (#8863). ([#9460](https://github.com/warpdotdev/warp/pull/9460)) — @david-engelmann ✨
* Fix MCP servers advertising both tools and resources sometimes failing to start due to asymmetric capability handling (#6798). ([#9436](https://github.com/warpdotdev/warp/pull/9436)) — @david-engelmann ✨
* Code Review panel now remembers the manually-selected Git repository when leaving and returning to an Agent session in a multi-repo workspace. ([#10599](https://github.com/warpdotdev/warp/pull/10599)) — @wzc520pyfm ✨
* Fixed ambient agent sessions not re-opening correctly from the management view ([#10510](https://github.com/warpdotdev/warp/pull/10510))
* Right-aligned the `Open in Warp` button in the shared session snapshot footer. ([#10667](https://github.com/warpdotdev/warp/pull/10667))
* Fixed response controls and stopped-task footer visibility after cancelling agent-initiated long-running commands and MCP tool calls. ([#9695](https://github.com/warpdotdev/warp/pull/9695))
* Fixed a race condition in the run command executor ([#10666](https://github.com/warpdotdev/warp/pull/10666))
* Fixed a bug where cloud conversations were sometimes empty on-join. ([#10670](https://github.com/warpdotdev/warp/pull/10670))
* \[Windows/Linux] Text selection on soft-wrapped lines fixed. ([#10445](https://github.com/warpdotdev/warp/pull/10445))
* Fixed zombie minidump server process blocking Windows auto-update ([#10528](https://github.com/warpdotdev/warp/pull/10528))
* Fixed MCP install/update modal button text color ([#10166](https://github.com/warpdotdev/warp/pull/10166))
* Child agent panes are now restored lazily when reopening a parent agent conversation. ([#10371](https://github.com/warpdotdev/warp/pull/10371))
* Fixed ‘open .command’ file failing to launch ([#10543](https://github.com/warpdotdev/warp/pull/10543)) — @Jackie-Tang ✨
* Fix unreadable repository switcher text in the Code Review pane after toggling between light and dark themes. ([#10601](https://github.com/warpdotdev/warp/pull/10601)) — @wzc520pyfm ✨
* Stop the GitHub PR prompt chip from polling `gh pr view` every 30 seconds when nothing has changed, preventing it from draining the user’s GitHub GraphQL rate limit. ([#10307](https://github.com/warpdotdev/warp/pull/10307)) — @croaky ✨
* Fixed tmux status line colors leaking into alternate screen background rendering. ([#10132](https://github.com/warpdotdev/warp/pull/10132)) — @MeteorSkyOne ✨
* Reserved titlebar space for right-side window controls on Windows/Linux ([#10178](https://github.com/warpdotdev/warp/pull/10178)) — @gabrimatic ✨
* Fixed Mermaid diagrams showing an indefinite rendering placeholder when rendering fails or times out. ([#10432](https://github.com/warpdotdev/warp/pull/10432))
* Fixed remote file tree not updating with local file changes ([#10514](https://github.com/warpdotdev/warp/pull/10514))
* Fixed code review find bar not cleaning up on close ([#10451](https://github.com/warpdotdev/warp/pull/10451)) — @EdenBendheim ✨
* Fixed CLI agent notifications in WSL sessions by forwarding the required Warp environment variables into WSL. ([#10174](https://github.com/warpdotdev/warp/pull/10174)) — @gabrimatic ✨
* Fixed cloud conversation background and status styling ([#10511](https://github.com/warpdotdev/warp/pull/10511))
* Fixed Vietnamese characters being silently dropped on Windows when typing with Unikey or EVKey in Telex/VNI mode. ([#10442](https://github.com/warpdotdev/warp/pull/10442))
* Slash commands now correctly respect enablement checks at execution time ([#10466](https://github.com/warpdotdev/warp/pull/10466))
* Fixed file path detection for paths preceded by Unicode/CJK punctuation ([#10250](https://github.com/warpdotdev/warp/pull/10250)) — @SagarSDagdu ✨
* Fixed pacman signing key validation before allowing Arch Linux auto-update ([#9706](https://github.com/warpdotdev/warp/pull/9706)) — @Naveen-Boddepalli ✨
* Tab titles for plugin-backed CLI agents (e.g. Claude Code via claude-code-warp) no longer keep showing stale permission-prompt text after a session completes. Thanks @lonexreb! ([#9671](https://github.com/warpdotdev/warp/pull/9671)) — @lonexreb ✨
* Fixed prompt branch picker clicks for branches checked out in linked worktrees. Thanks to @JasonLovesDoggo (#9264), @tkshsbcue (#9440), and @lonexreb (#9560) for earlier fixes and investigation. ([#9905](https://github.com/warpdotdev/warp/pull/9905)) — @kranthik10 ✨
* Fix remote-server SSH wrapper failing to install the Oz agent on macOS remotes whose `bash -s` resolves to Apple bash 3.2 (the default), which surfaced as “Initialize: Response channel closed before receiving a reply” and a misplaced binary under `~/"/Users/.../"`. ([#10317](https://github.com/warpdotdev/warp/pull/10317)) — @lucasdoell ✨
* Child agent initial prompts (from orchestrator) no longer appear in the agent input completion history. ([#10304](https://github.com/warpdotdev/warp/pull/10304))
* Fixed infinite SSE retry loop on stale agent runs ([#10383](https://github.com/warpdotdev/warp/pull/10383))
* Fixed Markdown table-of-contents anchor links in rendered notebooks. ([#10143](https://github.com/warpdotdev/warp/pull/10143)) — @haikomatt ✨
* Fixed cloud conversation transcript pane getting stuck in loading state after restarting Warp ([#10385](https://github.com/warpdotdev/warp/pull/10385))
* Stop the Code Review pane from re-running `gh pr view` on every filesystem event when the current branch has no PR. ([#10361](https://github.com/warpdotdev/warp/pull/10361)) — @croaky ✨
* Fixed tree command output filenames not being detected as clickable file links ([#10004](https://github.com/warpdotdev/warp/pull/10004)) — @princepal9120 ✨
* Enabled IME input on Linux/Wayland ([#9602](https://github.com/warpdotdev/warp/pull/9602)) — @anshul-garg27 ✨
* Focused-pane notifications are now marked as read when the Warp window is re-focused ([#10082](https://github.com/warpdotdev/warp/pull/10082))
* Fixed an issue where clicking the show/hide rich input footer chip would sometimes exit the agent view. ([#10303](https://github.com/warpdotdev/warp/pull/10303))
* Fixed duplicate apt source entries on Debian/Ubuntu when .sources file exists ([#10011](https://github.com/warpdotdev/warp/pull/10011))
* Fixed RowIterator crashes for third-party agent sessions ([#10305](https://github.com/warpdotdev/warp/pull/10305))
* Fixed a deadlock in terminal view rendering that could freeze the UI ([#10308](https://github.com/warpdotdev/warp/pull/10308))
* Revised tab summary mode layout and behavior ([#10067](https://github.com/warpdotdev/warp/pull/10067))
* Fixed a race condition in git branch/diff-stats prompt chip initialization ([#10265](https://github.com/warpdotdev/warp/pull/10265))
* Fixed a race condition that could permanently lose active rule files ([#10238](https://github.com/warpdotdev/warp/pull/10238))
* Fixed 429 rate limiting in cloud agent CLI polling ([#10275](https://github.com/warpdotdev/warp/pull/10275))
* Fixed a race condition causing accepted commands to be auto-cancelled ([#10241](https://github.com/warpdotdev/warp/pull/10241))
* macOS: fix third-party IMEs (e.g. 超注音 / Yahoo Bopomofo) advancing candidate selection by 2 per arrow press during composition. ([#9711](https://github.com/warpdotdev/warp/pull/9711)) — @maxmilian ✨
**Oz updates**
* Ambient agent conversations can now be restored into cloud mode panes ([#10426](https://github.com/warpdotdev/warp/pull/10426))
* Hide notification chip in ambient agent sessions ([#10299](https://github.com/warpdotdev/warp/pull/10299))
* Agent `/compact` now sends skills and environment context for better summarization ([#10274](https://github.com/warpdotdev/warp/pull/10274))
### 2026.05.06 (v0.2026.05.06.15.42)
[Section titled “2026.05.06 (v0.2026.05.06.15.42)”](#20260506-v0202605061542)
**New features**
* Added a `/set-tab-color` slash command for setting or clearing the current tab’s color from the input bar.
**Improvements**
* Added tab context menu actions to copy visible tab and pane metadata when available.
* The conversation details panel can now be opened and closed with a configurable keyboard shortcut.
* Conversation details side panel is now available for local Warp Agent conversations, not just cloud Oz runs. Click the info button in the pane header to open it for any active AI conversation.
* Reduced memory usage and CPU work in the agent runs management view while a conversation is streaming.
* Added support for drag-and-drop of image files into an active CLI agent session (e.g. Claude Code). Thanks @SagarSDagdu!
* Recognize Mistral Vibe (vibe / vibe-acp) as a known CLI agent in the terminal, with brand-colored toolbar tile. Thanks @lonexreb!
* Warp now renders inline local images and Mermaid diagrams in agent block output.
* Warp now silently falls back to a regular SSH session on remote hosts where the prebuilt remote-server binary is incompatible (e.g. glibc < 2.31), instead of attempting an install that would fail at runtime.
* Tighten orchestration event subscription scope so SSE runs only for active parent and child agent runs.
* HTML files using the .htm extension now open with HTML syntax highlighting in Warp’s editor.
* Recognize Block’s goose CLI agent — running goose now activates the CLI-agent toolbar, status, brand color, and icon like other recognized third-party agents. Thanks @webdevtodayjason!
* Added a `/continue-locally` slash command to continue cloud conversations locally.
* Added a “Show in Finder” (macOS) / “Show containing folder” (Linux/Windows) option to the tooltip that appears when clicking a detected file link.
**Bug fixes**
* Stop the Code Review pane from re-running `gh pr view` on every filesystem event when the current branch has no PR. Thanks @croaky!
* Fixed `/feedback` recording “Unknown” instead of the installed Warp version on packaged builds. Thanks @SagarSDagdu!
* Fixed find (`⌘+F`) selection jumping to a different match when new output streams into the active block. Thanks @amazansky!
* Fixed a command injection vulnerability when opening files in external editors on Linux.
* Fix Japanese IME losing the last character of a phrase that ends right before a punctuation mark on macOS. Thanks @s-zaizen!
* Fixed local file tree blinking/reshuffling when connected to an SSH session
* Fixed terminal text selection not auto-scrolling when dragging beyond bounds
* Fixed `Ctrl+G` not closing CLI agent rich input on Linux when editor is focused (fixes #9286). Thanks @nihalxkumar!
* Pressing backspace in the agent view when the buffer is empty no longer resets the conversation.
* Fixed unnecessary reconnect attempts for remote SSH sessions after system sleep, reducing error noise
* Fixed issue with repeated TUI redraws for CLI agents on terminal pane resize.
* Fix new-session ”+” dropdown alignment when the Tabs Panel is placed on the right side of the header toolbar.
* Copy keybinding now prioritizes selected text in the input over a selected block when both are active.
* \[Windows] Fix hotkey window.
* \[Windows] Symlink traversal fixed.
* Fixed a crash on Windows when handing off a Web conversation to the native client (“Grid received input but did not receive Reset Grid OSC”).
* Fixed a bug where multiple ‘open skill’ buttons shared hover state.
* Fixed Page Up and Page Down from the prompt so they scroll terminal output when the suggestion menu is closed; shortcuts appear under Keyboard Shortcuts as editable scroll actions (terminal:scroll\_up\_one\_page / terminal:scroll\_down\_one\_page). Thanks @fadexadex!
* Fixed the OSS Linux desktop entry so WarpOss launches through the packaged warp-terminal-oss command. Thanks @lonexreb!
* Fixed Ctrl/Cmd shortcuts (e.g. copy, paste) failing on Windows when a non-Latin keyboard layout was active.
* Fix macOS IME candidate popup positioning in code editor panes so it anchors to the editor caret instead of stale terminal/input positions. Thanks @qubaitian!
* Fixed `/open-file` handling for relative WSL paths so Unix separators are preserved before opening files on Windows hosts.
* Fixed background colour bleeding in alt screen programs (e.g. delta, diff-so-fancy) where coloured regions would incorrectly fill the entire viewport when they dominated the visible area. Thanks @JamieMcMillan!
* Clip the warping indicator’s action chips (e.g. “Hide responses”, “Take over”, auto-approve, queue-next-prompt, stop) onto a new line on narrow panes instead of overflowing into the adjacent pane.
* Inline .bmp, .tiff / .tif, and .ico images in agent block output now render correctly instead of falling back to plain text. Thanks @anshul-garg27!
* Notifications and session UI from the community-maintained pi-mono plugin (Pi CLI agent) are now wired through Warp’s default session listener. Thanks @lonexreb!
* Fixed an issue where attaching an image in block input did not immediately lock into Agent Mode, which could cause the NLD classifier to introduce uncertainty.
* Remote-server installs no longer fail when the staging-directory cleanup hits a “Directory not empty” race after the binary has already been moved into place.
* .command shell scripts now open with shell syntax highlighting in Warp’s editor.
* Fix git diff chip flickering between tracked-only and all-files count when untracked files are present
* Open File → Default App now opens files in the running Warp channel instead of routing to a different installed Warp.
* Fixed vertical tabs settings popup items (View as, Density, Pane title as) being unclickable. Thanks @leozeli!
* Fixed a macOS memory leak that occurred when Warp enumerated system fonts or built a font fallback chain.
* Executable shell scripts opened from a file:// URL now run in the terminal instead of opening in the editor. Thanks @amriksingh0786!
* Fixed Option+Enter, Option+Tab, and Option+Escape sending literal key names instead of correct escape sequences. Thanks @oliver-ni!
* Fixed read\_files tool showing an empty box when the LLM requests line ranges beyond the end of a file.
* Fixed Linux WarpOSS application-menu launcher pointing to a non-existent warp-oss binary; the .desktop Exec line now matches the installed warp-terminal-oss launcher. Thanks @lonexreb!
* Prevent Warp from consuming too much memory when identifying filepaths in long block outputs.
* Don’t trigger the agent onboarding tutorial when Warp is running in headless SDK/CLI mode.
* Added `--version` flag support in the Oz CLI
* Fixed file tree flickering when transitioning to an SSH remote session
* Fixed scroll-to-start/end of selected block keybinding (`⌘+Shift+↑`/`⌘+Shift+↓` on macOS, `Ctrl+Shift+↑`/`Ctrl+Shift+↓` on Windows/Linux) not working when the input is focused.
* Fix the terminal pane background appearing darker in horizontal tabs mode when the active theme has a background image or a custom window opacity.
* AI code blocks tagged vue, xml, dockerfile, jsx, tsx, objective-c, or starlark now render with syntax highlighting. Common aliases like rs, py, js, ts, yml, kt, rb, golang, terraform, and docker are also recognized.
* Reopen Closed Session is now reachable from the new-session menu on Linux and Windows.
* Fixed missing syntax highlighting for C++ header files using .hpp, .hxx, or .H extensions.
**Oz updates**
* Add Codex as a supported harness for local child agents.
* Configurable max context window per profile.
### 2026.04.29
[Section titled “2026.04.29”](#20260429)
**Improvements**
* New AI setting to control whether Oz adds an attribution co-author line to commit messages and pull requests it creates.
* Git operation buttons now show tooltips explaining why they’re disabled (e.g. “No changes to commit”, “Enter a commit message”).
* Long-running shell command indicator now shows a countdown to the agent’s next snapshot (e.g. “Next check in 12s”) instead of how long it’s been since the last one.
**Bug fixes**
* warp\://action/new\_tab?path=\~/foo (and /new\_window) now expand \~ to your home directory.
* Tab configs in the + menu and default session mode dropdown are now sorted alphabetically by name instead of appearing in random order.
* Fixed an issue where slash commands sent while an agent was still responding were silently dropped. Now, slash commands like /pr-comments run as follow-ups, just like typed messages.
* Disabled the commit message editor while a git commit is being performed in the git operations dialog.
* Project-scoped file-based MCP servers now spawn from the repo root by default (and global ones from \~), so configs with relative commands/args (and workspace launchers like pnpm/npm) work without an explicit working\_directory.
* Stopped spamming agent-run metadata fetches on the WASM shared-session viewer, eliminating a flood of 403 responses on `/api/v1/agent/runs/{id}` for non-owner viewers.
* Fixed dropped keystrokes when typing into a command block that started from a queued/typeahead command.
* Fixed double-line visual artifacts between workspace panels in all panel arrangements.
* Fixed a small memory leak on macOS that could accumulate Core Graphics objects during text rendering.
* Fixed settings popup items (View as / Density) being unclickable (thanks @leozeli!).
**Oz updates**
* Reduced the oz CLI tarball download size by \~60% on both macOS and Linux.
* Model selector no longer shows promotional discounts for models routed through your own API key (BYOK), since those discounts only apply to Warp-billed usage.
### 2026.04.27
[Section titled “2026.04.27”](#20260427)
**New features**
* Warp is now open source.
* Warp is now configurable via a TOML settings file. Access the file from the settings page or ask Warp’s agent to update settings for you.
**Improvements**
* Add setting to disable suggested rules.
* Added a `/feedback` slash command for submitting feedback about Warp.
* The `oz run get` and `oz run list` commands now support JSON output, along with filtering via the `--jq` flag.
* Feedback from the user menu, Help menu, Resource Center footer, and Command Palette now opens the `/feedback` flow.
* Middle-clicking a vertical tab now closes it, matching horizontal tabs.
* Slash commands in the terminal are now available even when AI is disabled.
* The network log viewer now opens as an in-app read-only pane backed by a 50-item in-memory buffer instead of writing `warp_network.log` to disk.
* Added a “Check now” button next to the “Last seen by agent” indicator for long-running commands, letting users immediately deliver a fresh snapshot to the agent without waiting for its poll timer.
* The agent mode input placeholder now reflects conversation state: “Warp anything” for new conversations, “Steer the running agent” while streaming, and “Ask a follow up” once finished.
* Pasting an absolute file path (e.g. from “Copy file path” in the Code Review pane) into the Command Palette file picker now correctly finds and opens the file.
**Bug fixes**
* Fixed wide Markdown table scrollbars in block list responses rendering over the terminal input.
* Fixed vertical tabs close button appearing on the left side when the panel is positioned on the right.
* Onboarding autonomy selections (Full / Partial / None) now correctly apply to the default execution profile, and existing users’ stored cloud profiles are preserved when logging in at the end of onboarding.
* Fixed a crash that could occur in the project explorer while file-tree metadata was being updated.
* Fixed issue where clicks in the vertical tabs settings panel were being ignored.
* Fixed “View in Oz” button in the conversation details panel not responding to clicks.
* \[Windows] WSL panes in restored sessions have the same PWD when you exited.
* Restored the API Keys (BYOK) and AWS Bedrock sections in the Agents > Oz settings subpage.
* Fixed a small memory leak on macOS when reading or writing user preferences.
* Usernames with an apostrophe no longer break PowerShell sessions.
* Fixed a hang that could occur when exiting an SSH session with the remote-server feature enabled.
* Fixed a crash triggered by terminal output containing very long runs of zero-width characters (such as steganographic ZWJ/ZWNJ sequences embedded in HTML piped through the terminal), which could also reproduce at startup via session restoration if the offending output had been persisted into a block.
* Fixed a small per-call memory leak triggered when opening a file in its default macOS application.
* Fixed unreadable text in the CLI agent rich input when running alt-screen CLI agents, increasing the contrast against background (e.g. OpenCode).
* Fixed a one-time startup memory leak in the macOS Services submenu setup.
* Fixed a per-window memory leak of the window delegate in the macOS ObjC bridge (window\.m).
* Fixed file tree sidebar incorrectly showing remote SSH session directories in local tabs.
* Fixed a keycode-dictionary per-bucket over-retain in the macOS ObjC bridge (keycode.m).
* Fixed a small per-window memory leak in the macOS ObjC bridge (host\_view\.m).
* Fixed a per-hotkey memory leak when registering global hotkeys on macOS.
* Tab title no longer changes to an agent-executed command name (e.g. cargo) during agent validation steps.
* \[macOS] Fixed a memory leak on image pasting and app-icon changes.
* Reopening a closed cloud-mode tab within the undo-close grace period now restores a live view of the cloud conversation instead of a frozen snapshot with a “session ended” banner.
* Fixed privacy settings for logged-out users not persisting to the settings file.
**Oz updates**
### 2026.04.22 (v0.2026.04.22.08.46)
[Section titled “2026.04.22 (v0.2026.04.22.08.46)”](#20260422-v0202604220846)
**New features**
* Toolbar chips can now be rearranged by right-clicking anywhere in the top bar and selecting “Rearrange toolbar items”.
* Mermaid diagrams now render in markdown notebooks.
**Improvements**
* Added support for pasting images into the rich input editor with CLI agents, such as Claude Code or Codex.
* Typing `_text_` or `__text__` in a code review or rich-text comment now renders as italic or bold, matching the existing `*text*`/`**text**` behavior.
* \[Windows] Added a “Start Warp at login” toggle under **Settings** > **Features** > **General** that registers Warp to launch automatically when you sign in to Windows.
* Add View menu entries (with keyboard shortcuts) for the Global Search and Agent Conversations left panel items on macOS.
* \[Windows] Added 408 new PowerShell cmdlet completions and improved suggestion quality for existing PowerShell completions.
* Added completions for `pprof`.
* `/fork` now opens the forked conversation in a new pane with Enter and in a new tab with Cmd+Enter.
* Right-click a URL or file-path link inside an AI response to copy it directly via the context menu.
* Added a setting to hide the lines added/removed counts from the code review button in the tab bar.
* Reorganized settings into subpages for Agents, Code, and Cloud platform; improved settings search.
* Wired branch completion into `git log` argument position.
* Added notifications for OpenCode’s “Ask user question” tool.
* Show discount chip on models with active promotions in the model picker.
* Per-query image limit bumped to 20 (from 5) and per-conversation image limit bumped to 200 (from 20).
* Performance improvement preventing lagginess after logging in when you have many Warp Drive objects.
* Added support for file artifacts in agent conversations with download functionality and filtering options.
**Bug fixes**
* \[Windows] Fixed image paste into CLI coding agents (Claude Code, OpenCode, etc.).
* Fixed MCP server tags overflowing off-screen when a server has many chips (e.g. GitHub MCP with many repo scopes).
* Fixed MCP gallery items not being alphabetized consistently in the MCP servers settings page.
* Fixed artifacts card clipping the “Continue locally” button on narrow panes.
* Fixed code review submit button being incorrectly disabled when the terminal’s working directory casing didn’t match the on-disk repo path on macOS.
* Fixed new accounts not being marked as onboarded on the server when signing up after completing the onboarding slides from a non-login-slide entrypoint.
* Fixed Project Explorer getting stuck in loading state when opened after connecting to a remote SSH session.
* Fixed a bug where the agent’s `read_files` tool returned extensionless text files (such as shell scripts) as binary content.
* Fixed MCP settings page file-based server badges growing unbounded and incorrectly labelling Warp-scoped servers as “.warp” instead of “global”.
* Fixed missing in-progress indicator in agent panes when a shell command is running but no agent message has been sent yet.
* Fixed MCP OAuth authentication failing with providers that enforce strict redirect URI matching (e.g. Hydra/ORY).
* Fixed MCP tool calls with integer-typed parameters failing due to being serialized as floats.
* Fixed file edit tool dropping the end of a line when the LLM’s search block ended with a partial line match.
* First find match now gets correctly selected when using the code editor with vim mode.
* Fixed code review comments being silently dropped when sent after cancelling a running agent command with Ctrl+C.
* Toolbar chips in the coding agent footer are no longer hard to read when running alt-screen CLI agents like OpenCode.
* Fixed MCP servers (e.g. Figma) requiring re-authentication on every app restart.
* \[Windows] Fixed a race condition that caused auto-updates to fail with file-in-use errors when Warp hadn’t fully exited before the installer ran.
* Improved reliability of the Rich Input submission flow for Copilot CLI.
* \[Windows] Fixed unbounded memory growth when rendering large amounts of CJK text with a primary font that does not include CJK glyphs.
* Fixed settings search bar text overflowing when typing long queries.
* Fixed Oz CLI hanging after command completes when the network is unavailable.
* Fixed Ctrl+C not terminating the Oz CLI during shutdown.
* Fixed `~` (tilde) not being expanded to the home directory in the `/open-file` slash command.
* Fixed orchestration events breaking tool call ordering when a CLI subagent is active.
**Oz updates**
* Added a bundled Claude API skill for Claude API and Anthropic SDK development guidance.
* Added support for `--share public:{access_level}` to oz CLI to set public access level on oz cloud runs.
* `start_agent` no longer rejects remote child agents when `environment_id` is omitted; within a remote parent, the child inherits the parent’s environment automatically.
### 2026.04.15 (v0.2026.04.15.08.45)
[Section titled “2026.04.15 (v0.2026.04.15.08.45)”](#20260415-v0202604150845)
**Improvements**
* Agent Mode now shows a “Last seen by agent at” indicator for long-running commands, so you can see how recently the agent received new output.
* Added completions for npm package search, nx, brew, aws s3, tree, awk, sort, ip, uv, and nmap, and added pnpm workspace filter support.
* Skill invocations now display with the same purple highlighted text as slash commands in the input and prompt views.
* Added completions for `timedatectl`, `ack`, `watch`, `lsof`, `systemctl`, `ros2`, `nextflow`, `tsh`, `codex`, `asdf`, `sdk`, `pass`, `az`, `oc`, `scp`, `claude`, `git show`, `git rm`, `gsutil`, `aws ec2`, `docker-compose`, `yarn`, and `docker run`; improved `git switch`, `git diff`, `aws` static flags, `gt`, `kubectl`, `tf`, `pnpm`, `kubectl`, and SSH host completions; added `apt` repo package generator.
* Code review comment buttons now remain visible when AI is disabled; comments can be sent to CLI agent terminals (e.g. Claude Code).
* Review comments can now be sent to any available terminal in the tab, not just the focused one. If the focused terminal is busy, Warp will automatically route comments to another idle terminal in the same repo.
* Skills are now searchable from the @-context menu in Agent Mode, inserting `/{skill_name}` into the prompt.
* File-based MCP servers can now be configured via `~/.agents/.mcp.json` (global) or `.agents/.mcp.json` (project-local).
**Bug fixes**
* Fixed longer prompts for Claude Code not being fully submitted when using Rich Input in Warp.
* Fixed settings being reset to defaults when a logged-out user creates a new account.
* Updated openh264 dependency to resolve a heap overflow security vulnerability (GHSA-5pmw-9j92-3c4c).
* Show “Resume Conversation” shortcut when agent conversations fail with transport or server errors.
* Fixed `kubectl` resource completion breaking when `-n`/`--namespace` or other flags are placed before the subcommand.
* Fixed markdown files with animated GIFs and WebPs using excessive memory by rendering them as first-frame previews.
* Fixed autosuggestions and completions not appearing after shell bootstrap completes.
* Fixed excessive CPU usage from redundant `git status` processes when multiple terminal tabs are open in the same repository.
* Fixed a bug where conversations would stall if a long-running command finished while the user was in control.
* Fixed thought block headers (“Thought for X >”) having a click area that extended to the full width of the pane; only the text and chevron are now clickable.
* Fixed global search using excessive memory when matching files with very long lines (e.g. minified JavaScript).
* Window title now respects custom tab names instead of always showing the generated name.
* Fixed `git push` branch completion for force-push and refspec prefixes, HTML entity rendering in completion specs, and `npm i` short-form command priority.
* Fixed repeated 403 errors when indexing large codebases.
* Fixed ask-question option rows changing cursor shape while hovering over option text.
**Oz updates**
* Local child agents now inherit the parent agent’s AI profile (model and permissions).
### 2026.04.08 (v0.2026.04.08.08.36)
[Section titled “2026.04.08 (v0.2026.04.08.08.36)”](#20260408-v0202604080836)
**New features**
* Vertical tabs are now available, offering a new way to organize your terminal tabs in a sidebar layout.
* Tab configs allow you to save and share your workspace setup as customizable configurations.
* You can easily create new worktrees with autogenerated branch names. These are saved as tab configs to then customize and edit.
* New Rich Input available in third-party CLI agents (e.g. Claude Code, Codex, Gemini CLI, OpenCode, etc.). This allows you to use Warp’s rich input features with these coding agents.
* Released a revamped notifications UI, and support for notifications for Claude Code and OpenCode.
* Added support for the coding agent toolbar for auggie and pie.
* Added a settings entry for the ask question tool to configure when it pauses for user input.
**Improvements**
* Conversation search now shows what it is searching for and its current activity.
* Added `warp://settings/appearance` deep link to open Appearance settings directly.
* Improved AI @context menu to prioritize blocks from the active terminal session and rank items by recency.
* Added support for rendering markdown tables in notebooks and Warp’s built-in Markdown viewer.
* The Command Palette file opener now supports `~` (tilde) expansion to the home directory when searching for files.
* Added completions for `timedatectl`, `ack`, `watch`, `lsof`, `systemctl`, `ros2`, `nextflow`, `tsh`, `codex`, `asdf`, `sdk`, `pass`, `az`, `oc`, `scp`, `claude`, `git show`, `git rm`, `gsutil`, `aws ec2`, `docker-compose`, `yarn`, and `docker run`.
* Improved dynamic completions for `git switch`, `git diff`, `gt`, `kubectl`, `tf`, `pnpm`, `apt` and SSH hosts.
**Bug fixes**
* Added prompt changes to avoid agents getting stuck navigating pagers in Full Terminal Use.
* Removed the web inactivity logout that could sign out authenticated users unnecessarily while session-cookie expiration work lands.
* Skip ask-user-question prompts while auto-approve is enabled in Agent Mode.
* Fixed `git push` branch completion for force-push and refspec prefixes.
* Fixed HTML entity rendering in completion specs.
* Fixed `npm i` short-form command priority.
**Oz updates**
* Added an `oz whoami` command to get user information.
### 2026.04.01 (v0.2026.04.01.08.39)
[Section titled “2026.04.01 (v0.2026.04.01.08.39)”](#20260401-v0202604010839)
**New features**
* \[macOS] Right-clicking on text files in Finder allows you to open in Warp’s code editor.
* Send code review comments, attach diff hunks as context, and send substrings as context (`cmd L`) to 3rd party CLI tools such as Claude Code, Codex, Opencode, etc.
* Agents can now ask users clarifying questions during Agent Mode interactions.
* Warp’s agent now suggests followups when it is done.
**Improvements**
* Replaced warpify banner for subshell and SSH sessions with a footer to either warpify or tag an agent in.
* Improved error messaging when session sharing times out via CLI `--share` flag, now suggesting that it may be disabled by a team administrator.
* Added “Copy file path” option to the overflow menu in the file viewer for both code and markdown files.
* Added “Sign up” option to the settings gear menu for non-logged-in users.
* MCP config files edited by the agent now show an ‘Open config’ button in the code diff header, making it easy to jump directly to the config file.
* Added `/skills` support in CLI agent rich input for browsing and invoking agent-specific skills.
* Sandboxed agents now have dedicated autonomy settings, instead of inheriting the team-level defaults.
* Updated settings info icon tooltips to clarify they open documentation.
* Improved quality and latency of prompt suggestions and suggested code diffs.
* Cloud agents can now accept images and file attachments as context.
**Bug fixes**
* Fixed stale fallback model messaging persisting across new user queries.
* Fixed scroll behavior when editing code review comments to properly reveal the comment editor.
* Fixed WebSocket proxy connections timing out when the proxy listens on port 80.
* Fixed PowerShell aliases and functions to be matched case-insensitively, matching PowerShell’s native behavior.
* Fixed conversation search temp directory paths using mixed separators on Windows.
* Fixed keyboard shortcuts settings panel being empty when first navigated to via search.
* Fixed the `@` context menu dismissing after typing \~6 characters when filtering categories.
* Fixed a crash with Oz CLI commands that read from stdin.
* Fixed a production WebAssembly crash caused by native repository detection code being reached from shared Wasm call paths.
* Fixed links in blocklist code review comments not opening when clicked.
* Fixed “Out of credits” alert not dismissing when users provide their own API keys.
* Fixed link detection being offset in AI conversations after conversation summaries or hidden reasoning blocks.
* Simplified file explorer lazy-loaded folder handling and fixed transitions between standalone folders and indexed Git repositories.
* Fixed inline code snippet colors and underline colors not updating when switching editor themes in notebooks.
* \[Windows] Fix rendering on an additional set of older Intel iGPU drivers.
* Fixed web auth flows so session-cookie-authenticated clients can call authenticated server APIs without requiring an Authorization header.
**Oz updates**
* Fixed Oz session sharing failing behind HTTP proxies on port 80.
* The `OZ_RUN_ID` environment variable is now available inside agent terminal sessions, set to the current task ID.
* Improved error messages when agent session sharing fails, removing repetitive text and providing clearer guidance.
* Agents can now ask users clarifying questions during Agent Mode interactions.
### 2026.03.25 (v0.2026.03.25.08.24)
[Section titled “2026.03.25 (v0.2026.03.25.08.24)”](#20260325-v0202603250824)
**New features**
* You can now use the pr-comments skill using `/pr-comments` to fetch Pull Request comments from GitHub.
* Warp now supports the Kitty Keyboard Protocol.
**Improvements**
* Onboarding now shows premium model tiers as disabled with an upgrade path for free users.
* All inline menus are now resizable, and some inline menus now have tabs.
* Adds new built-in `edit-figma-design` skill, invokable by users with Figma’s remote MCP server installed.
* MCP server templates can now use dropdown selectors for enums.
* Added a customizable toolbelt for the agent input footer — drag and drop to rearrange context chips and controls.
* \[macOS] Migrate to Apple’s newest icon format. This will allow Warp’s icon to adapt to the chosen “Icon & Widget Style” preference if the default icon is selected.
* Code review comments can now be sent directly to running CLI agents (Claude Code, Gemini CLI, etc.) from the code review panel.
* Pressing `esc` now dismisses an empty code review comment composer.
* Added the ability to always show or always hide agent thinking blocks. Visit **Settings** > **AI** > **Other** to change.
* Add a `/changelog` command for reopening the latest changelog, and keep the update toast visible until dismissed.
* Added syntax highlighting for Dockerfiles in the file editor.
* Added a setting to hide agent-executed commands from shell history, now enabled by default.
* MCP servers detected from third-party agents (Claude, Codex) are now visible and spawnable from the MCP servers page in Warp’s AI settings. For more, see our [docs](/agents/capabilities/mcp/#file-based-mcp-servers) on file-based MCP servers.
**Bug fixes**
* Fixed visual jitter in agent toolbelt when opening the rich input composer.
* Clarified the `/fork` slash command description.
* MCP resource reads now respect autonomy settings instead of always prompting for approval.
* You now get completions, syntax highlighting, and hover descriptions when your flag/value pairs are `=`-separated, e.g. `--flag=value`.
* Fixed stale go-to-definition and symbol outlines when using code review with multiple tabs.
* Fixed an issue where selecting a shell command from command search (`cmd-r`) while in Agent Mode with auto-detection disabled would treat the command as an agent prompt instead of executing it as a shell command.
* Fixed `ctrl-c` not working during conversation search.
* Fixed an issue where the follow-up prompt in `/compact-and` and `/fork-and-compact` was silently lost when summarization failed or was cancelled.
* Fixed dismiss button and `ctrl-c` not working on suggested unit tests banner.
* Git diff chip now appears in remote and subshell sessions.
* Fixed input scrolling bug where clicks were sometimes applied one line up (instead of on the clicked line).
* Fixed rendering of programs that use the synchronized output VT extension in shared sessions, such as Claude Code.
**Oz updates**
* Updated the `create-skill` bundled skill with the latest upstream version, adding eval/iteration workflow, benchmarking, and description optimization capabilities.
* New chip in AI input mode for GitHub pull requests, whenever you have a pull request open for your current branch.
### 2026.03.18 (v0.2026.03.18.08.24)
[Section titled “2026.03.18 (v0.2026.03.18.08.24)”](#20260318-v0202603180824)
**New features**
* Warp now automatically detects global and project-scoped MCP servers configured with `claude` or `codex`. Toggle **File-based MCP servers** in **Settings** > **AI** to auto-spawn servers based on your local configuration. See [docs](/agents/capabilities/mcp/#file-based-mcp-servers) for more.
* Added Go to Line dialog in the code editor (`CTRL-G`) with line:column support.
**Improvements**
* Added “Leave Agent Thinking expanded” setting to keep agent thinking blocks expanded after streaming.
* Added “All” and “Current Directory” tabs to the inline conversations menu.
* Updated settings copy to consistently use “Oz” instead of “the Agent” in MCP Servers and Rules sections.
* Improved the performance of loading and rendering large AI conversations.
* Added an inline plan selector for conversations with multiple plans.
* \[macOS] The window traffic light buttons now look correct at different zoom levels.
* Kitty keyboard protocol support is now available on Preview builds.
* The Warp agent management view now links to associated skills for cloud agents.
* `Ctrl-R` command search now includes AI query history from all past conversations, not just those currently open.
* Enabled Kitty keyboard protocol support on dev builds.
* Improved the ranking of items listed in @ context by considering recency.
* Added new built-in skills `generate-figma-content` and `pull-figma-content` invokable by users with Figma’s remote MCP server installed.
* Hidden directories and files (starting with `.`) now appear at the top of the Project Explorer, matching the convention used by most editors.
* Updated setup command placeholder to show `cd my-repo &&` example.
**Bug fixes**
* Fixed “for terminal” text in pane header becoming bold when disabled, causing a layout shift.
* Fixed notebook find bar showing `?/n` instead of proper match counter.
* Fixed bug where editing a tab title always started with the pane title (instead of the tab’s custom title, if it existed).
* Fixed “View latest changelog” action not appearing in the Command Palette.
* Fixed issue where artifacts from cloud agent runs did not update live in the conversation details pane.
* Fixed intermittent “Failed to update plan” toast appearing without user action when background plan auto-saves encountered transient failures.
* Fixed tooltip for branch name in code review panel overlapping the truncated text — it now appears above the branch name.
* Fixed `Ctrl+G` not being bound by default for “Go to line” in the code editor.
* Fixed `cmd-O` files palette not toggling off when pressed again.
* Fixed code review panel unnecessarily resetting scroll position and cached state when switching tabs.
* Fixed some saved prompts not appearing in slash command menu when searching with a single character.
* Fixed SSH warpification not triggering when using shell aliases for SSH commands.
* Fixed a bug where SSH sessions run by the agent would incorrectly trigger warpification UI.
* Fixed issue on macOS where New Window/New Tab menu items and keybindings occasionally became disabled when using global hotkey window.
* Fixed code review branch dropdown only showing “Uncommitted changes” after closing and reopening the panel.
* Fixed “New environment” button in Environment settings not opening the setup mode selector popup.
* Fixed onboarding slides cutting off navigation buttons when the window is too short — content area is now scrollable.
* \[Windows] Fixed path inconsistencies that caused codebases to fail indexing.
* Show tooltip on the codebase indexing toggle when it is disabled by an admin policy, explaining why the setting cannot be changed.
* \[Windows] Fixed rendering issues on old Intel UHD integrated GPUs.
* Fixed a bug where only the first plan was shown inline when restoring a conversation with multiple plans created.
* Fixed resume-conversation keybinding not working when a long-running command subagent is active.
* Fixed broken documentation links in agent tips, settings, and onboarding content.
* Fixed AI queries in `Ctrl-R` history not being sorted by time.
**Oz updates**
* Conversation search now uses real file tools for faster, more accurate history search.
* Added `/open-repo` slash command for switching between indexed codebases.
* Added tabs to the up-arrow history menu to filter to commands or prompts.
* `oz agent run` now prints the run ID with a link to the Oz dashboard.
### 2026.03.11 (v0.2026.03.04.08.20)
[Section titled “2026.03.11 (v0.2026.03.04.08.20)”](#20260311-v0202603040820)
**Bug fixes**
* The terminal input now automatically detects references to Figma and encourages the use of the Figma MCP. Images exported from Figma are also detected.
### 2026.03.05 (v0.2026.03.04.08.20)
[Section titled “2026.03.05 (v0.2026.03.04.08.20)”](#20260305-v0202603040820)
**New features**
* Adds prompt customization for the new Warp prompt.
**Improvements**
* Adds new built-in skills `generate-figma-content` and `pull-figma-content` invokable by users with Figma’s remote MCP server installed.
* Selected text is no longer auto-attached as agent context to prevent accidental attachment, and instead requires right click > attach as agent context.
* Cloud conversations now appear in the @conversations context menu.
* When Settings > MCP Servers > File-based MCP servers is toggled on, we now automatically detect and spawn global and project-scoped MCP servers installed via `codex`.
* Global search now pre-populates with the active text selection from code, terminal, notebook, and plan views.
* Warp prompt now has separate chips for git branch and git diff stats.
* Show pending prompt indicator when using `/fork-and-compact` or `/compact-and` with a follow-up prompt.
* Oz permission notifications now use “Oz” branding instead of “Agent Mode”.
* \[macOS] The window traffic light buttons now look correct at different zoom levels.
* Added “Copy plan ID” option to the plan document overflow menu.
**Bug fixes**
* Fixed an issue where changing directories from the prompt chip dropdown cleared the terminal input.
* Fixed LSP error diagnostics (underlines) persisting on valid symbols after workspace reanalysis.
* Resolved an issue where duplicate skills installed across multiple provider directories (e.g., `.claude` and `.agents`) would appear twice.
* Fixed git diff stats chip incorrectly appearing in non-git directories.
* Fixed global hotkey window opening on the wrong screen after sleep/wake when pinned to a specific display.
* Fixed cursor position queries (`ESC[6n`) not working when connected via tmux control mode (`-CC`), which caused certain TUI applications to hang when Warpified in SSH (e.g. Codex CLI).
* Fixed agent driver not waiting for automatic error retry on network failures.
* Fixed incorrect ANSI colors in the Adeberry theme.
* Fixed a bug where some MCP servers would fail to connect due to an unsupported `resources/list` method.
* CLI now exits immediately with an error when credentials are invalid, instead of timing out while syncing Warp Drive.
* Fixed a crash that could occur when selecting text during rapid terminal output.
* Fixed ephemeral MCP servers not being included in multi-agent API requests.
* Fixed settings page not updating profile picture after auth state changes.
* Fixed the “Open in Warp” button not working for code snippets in restored and forked AI conversations.
* Hide the free cloud credits banner on shared sessions and WASM builds.
* Fixed a case where the newest plan created by the agent would not visually replace a previous plan that was open.
* “Plan synced to Warp Drive” toast no longer appears when the synced plan is in a different tab.
* Fixed “open file” button in code review diff view not working when the pane is maximized.
* Fixed git metadata background operations after a terminal is closed.
* Mobile soft keyboard will now work for LRCs.
* Agents now report more detailed information about session-sharing failures.
**Oz updates**
* Agent tasks now report structured error codes to the server, enabling better error tracking and retryability handling.
* Fixed cloud agent not waiting for automatic error retry on network failures.
* Added support for passing arguments to skill invocations (`$ARGUMENTS`, `$N`) and for including user queries with the invocation.
### 2026.02.25 (v0.2026.02.25.08.24)
[Section titled “2026.02.25 (v0.2026.02.25.08.24)”](#20260225-v0202602250824)
**New features**
* Warp now has language server support in our native code editor. For details on the languages and features we support, see [Language Server Protocol](/code/code-editor/language-server-protocol/).
**Improvements**
* Reintroduced customization support for the Warp prompt.
* Maximizing the Code Review panel now opens the file list.
* Docker image inputs in environment settings now show a link to the Docker Hub page when available.
* Added `/compact-and` slash command to trigger conversation compaction and automatically send a follow-up prompt when it completes.
* Added a new `/profile` command that allows you to switch between profiles using an inline menu.
* Oz CLI now outputs a direct link to the Oz webapp run page when spawning cloud agents.
**Bug fixes**
* Fixed a bug where the Oz CLI would open the Warp GUI app rather than printing help output.
* Fixed broken documentation links on the Referrals settings page and AI settings page.
* Fix CLI agent footer detection when commands are prefixed with env var assignments. For example, `OPENCODE_EXPERIMENTAL_PLAN_MODE=1 opencode`.
* Fixed rendering of codebase search tool calls when restoring conversations
* Local-only slash commands such as `/open-file` are now disabled automatically in remote sessions
* Fixed “View all cloud runs” button linking to a specific run instead of the runs list page
* Fix tab alignment in monospace text blocks by using fixed-width tab stops.
* Improve cloud-mode modal routing for concurrent-limit vs out-of-credits states.
* Fix cloud-mode out-of-credits modal flicker and compact CTA alignment.
* \[Linux] The `oz` CLI package is now named `oz-stable`.
**Oz updates**
* Add “Default mode for new sessions” setting to open new tabs and panes in agent view by default.
### 2026.02.18 (v0.2026.02.18.08.22)
[Section titled “2026.02.18 (v0.2026.02.18.08.22)”](#20260218-v0202602180822)
**New features**
* Agents can now fetch and read content directly from URLs provided in your query.
**Improvements**
* Enabled multi-select in Notebooks and code editors.
* Added a new setting under `Appearance > Tabs` to preserve the active tab’s color when creating new tabs.
**Bug fixes**
* Fixed Escape key closing the up-arrow menu instead of transitioning to normal mode when in vim insert mode.
* Fixed Option-left and Option-right keys not working for word navigation in code review comments editor.
### 2026.02.11 (v0.2026.02.11.08.23)
[Section titled “2026.02.11 (v0.2026.02.11.08.23)”](#20260211-v0202602110823)
**Improvements**
* Updated the tabs UI to be cleaner, more readable, and to make tab focus clearer.
**Bug fixes**
* Show the Input Type setting (Warp/PS1) regardless of global AI setting.
### 2026.02.10 (v0.2026.02.10.11.37)
[Section titled “2026.02.10 (v0.2026.02.10.11.37)”](#20260210-v0202602101137)
**New features**
#### Introducing Oz: orchestration for cloud agents
[Section titled “Introducing Oz: orchestration for cloud agents”](#introducing-oz-orchestration-for-cloud-agents)
Oz is Warp’s orchestration platform for cloud agents: launch parallel agents, automate recurring engineering work, and build apps on top of agents with full visibility and control.
[Read the launch post →](https://www.warp.dev/blog/oz-orchestration-platform-cloud-agents)
#### Cloud Agents
[Section titled “Cloud Agents”](#cloud-agents)
* **Run Cloud Agents from anywhere with built-in tracking** — start agents from Warp or via the CLI, triggers, or schedules. Every run is auditable and steerable. [Cloud Agents docs →](https://docs.warp.dev/platform/)
* **Cloud environments for consistent execution** — configure Docker-based environments (unlimited repos + setup commands) and run agents in isolated cloud sandboxes. [Environments docs →](https://docs.warp.dev/platform/environments)
* **Track agents from the web** — manage runs, create schedules, configure environments, and set up integrations from any browser in the [Oz web app](https://oz.warp.dev).
* **Schedule agents based on Skills** — run agents automatically on a cron schedule for code cleanup, dependency updates, and issue triage. See [Scheduled Agents](/platform/triggers/scheduled-agents/).
* **Programmable by default** — orchestrate agents via the CLI and integrate Oz into tools and services via the [API reference](/factories/developer-tools/).
#### Warp Upgrades
[Section titled “Warp Upgrades”](#warp-upgrades)
* **Terminal and Agent modes** — two distinct modes: a clean terminal for commands, and a dedicated conversation view for multi-turn agent workflows with full controls (model select, voice, attachments).
* **Cloud-Synced Conversations** — your agent conversations sync to the cloud and persist across devices. Share with teammates via link, view on the web, or continue locally.
#### Agent Capabilities
[Section titled “Agent Capabilities”](#agent-capabilities)
* **Skills** — reusable instruction sets that agents auto-discover from your project or home directory. Invoke with `/{skill-name}` or run as scheduled cloud agents for repeatable automation. [Skills docs →](/agents/capabilities/skills/)
* **Computer Use** — agents can interact with desktop environments in sandboxed cloud containers—take screenshots, click, type, and test UI changes. [Computer Use docs →](/agents/capabilities/computer-use/)
### 2026.02.04 (v0.2026.02.04.08.20)
[Section titled “2026.02.04 (v0.2026.02.04.08.20)”](#20260204-v0202602040820)
**New features**
* Added full support for the Kitty keyboard enhancement protocol, enabling TUI applications like OpenCode to detect and use enhanced keyboard input.
* Support agent footer when running Copilot CLI.
* Added a new paid plan, **Max**, which comes with 12× more monthly credits than Build. Upgrade in `Settings > Billing and Usage`.
**Improvements**
* Improved environment update handling with better timestamp tracking and immediate UI refresh after edits.
* `@` menu now shows function definitions when NLD is disabled.
* Conversation deep links now open in a new tab instead of a new window.
* Renamed `edit` slash command to `open`.
* Fixed a race condition when using API keys with the Oz CLI.
* Improved robustness of MCP connections (especially using the legacy SSE transport). “Transport closed” errors now trigger a reconnection to the server.
* Added a new setting to keep the opened/closed state of the tool panel consistent across tabs in the same window (“Tools panel visibility is consistent across tabs”).
**Bug fixes**
* Fixed “Sharing in Warp Drive” onboarding block appearing mid-stream during agent responses.
* Disabled codebase indexing on non-agent run commands.
* Fixed scrolling behavior when typing in long-running commands — cursor is now scrolled into view.
* Fixed sharing dialog copy link icon being slightly larger than the text.
* Fixed issue where the code review panel would get stuck on “Loading open changes” when multiple repositories are open in the same tab.
* Fixed a crash caused by orphaned wide character flags in the terminal grid.
* Fixed clipping issue in terminal message bar.
### 2026.01.28 (v0.2026.01.28.08.14)
[Section titled “2026.01.28 (v0.2026.01.28.08.14)”](#20260128-v0202601280814)
**Improvements**
* Files opened from code review panel, project explorer, and global search now respect your external editor setting.
* Toggling the plan while the pane is maximized now restores the layout to show the plan.
* Added “copy path” button to file headers in code review panel.
* Pasting images into the input now enters Agent Mode, matching drag and drop behavior.
**Bug Fixes**
* Fixed an issue where conversations could break when the agent read large images from directories.
* Fixed input buttons overflowing into adjacent panes in narrow layouts.
* Fixed text in MCP tool call details not being copyable.
* Fixed status indicator incorrectly showing for empty conversations in tab headers.
* Fixed Drive team section header displaying in all caps.
* Fixed Enter key not working in MCP installation modal.
* Fixed slash command text not highlighting correctly in some cases.
* Fixed input mode detection occasionally switching unexpectedly.
* Fixed /edit command failing when filename had trailing whitespace.
### 2026.01.21 (v0.2026.01.21.08.14)
[Section titled “2026.01.21 (v0.2026.01.21.08.14)”](#20260121-v0202601210814)
**New Features**
* Global search in files across your current directories. Use `CMD-F`/`CTRL-SHIFT-F` to open.
* Expanded web search support to additional models.
**Improvements**
* Save AI prompts as Agent Mode workflows via context menu.
* `/init` now generates AGENTS.md instead of WARP.md.
* Added horizontal autoscrolling when jumping to line/column.
* Better language detection for syntax highlighting.
**Bug Fixes**
* Fixed a memory leak that occurs when making an Agent Mode request.
* Fixed an issue where “waiting for a password” notifications could be triggered incorrectly when launching certain terminal apps like neovim.
* Fixed duplicate entries appearing in the agent management view for Slack-triggered conversations.
* Fixed alias expansion being triggered in AI input when it should only apply to shell commands.
* Fixed an issue where multiple shell commands could enter long-running mode in the same request batch.
* Hide AI options in the Command Palette when AI is disabled.
* Stopped highlighting search matches in reasoning blocks.
* Fixed session viewer input being cleared when agent runs commands.
### 2026.01.14 (v0.2026.01.14.08.15)
[Section titled “2026.01.14 (v0.2026.01.14.08.15)”](#20260114-v0202601140815)
**New features**
* Added footer for third party CLIs.
* Added onboarding flow for new users.
**Improvements**
* Fixed duplicate rule suggestions on dismiss and save.
* @-context search now matches on both name and content for notebooks, rules, and workflows.
* Updated checkbox checkmark to use foreground color for better theme consistency.
* Filter selections in the cloud agent management view now persist across app restarts.
* MCP servers with OAuth authentication can now be used in warp agent run if previously authenticated in the desktop app.
**Bug fixes**
* Fixed a bug where text in the MCP tool call detail wasn’t selectable.
* Fixed agent thread banner text overflow on smaller screens.
### 2026.01.07 (v0.2026.01.07.08.13)
[Section titled “2026.01.07 (v0.2026.01.07.08.13)”](#20260107-v0202601070813)
**New Features**
* Added agent tips under the warping indicator.
**Improvements**
* Users can now create team-scoped API keys.
* Agent tip now leads with `WARP.md` when mentioning project-scoped rule files.
* The `oz agent run-cloud` command can now create cloud agent tasks that are shared with team members.
* Updated agent profile switching tip to better explain why users would want to switch profiles.
* Comments in the code review flow now render full width when there are 4 or fewer comments, improving readability.
* When the completions menu is opened (tab), no completion item is selected by default. Pressing enter while no completion is selected directly runs the command currently in the input. Upon selecting a completion, it now automatically shows up in the input. This more closely mirrors behavior in traditional terminals.
* The `oz agent run-cloud` command now supports saved prompts.
* We added a new full terminal use model selector in the agents profile page so that you can select a specific model for full terminal use work.
**Bug fixes**
* Improved out-of-memory handling for cloud agents.
* Fixed a configuration error creating team-scoped Warp-managed secrets.
* Fixed ‘parameter not set’ error in zsh when users have setopt nounset enabled.
* Fixed an issue where up arrow history could be ordered incorrectly on quit or restart Warp.
# Built-in Code Editor
Canonical page: [/code/code-editor/](https://docs.warp.dev/code/code-editor/)
> Make in-context code edits with Warp's built-in editor, featuring syntax highlighting, tabs, and Vim keybindings.
Warp comes with a native code editor designed for quick, in-flow edits alongside your Agent conversations. Instead of switching back and forth to an IDE, you can open and edit files directly in Warp — with essentials like syntax highlighting, a tabbed file viewer, find and replace, Vim keybindings, and a file tree for browsing and adding files as context.
The editor is built for fast changes to agent-generated code: renaming a variable, tweaking copy, or rewriting a short function. Having just enough editing power in-context makes it easier to land an agent’s changes and keep momentum.
### Opening files in Warp
[Section titled “Opening files in Warp”](#opening-files-in-warp)
**You can open files in the editor in several ways:**
1. **Click a file path** from the terminal output or an AI conversation and select “Open in Warp.”
2. **Use the file menu in the Command Palette** (`⌘+O` on macOS, `Ctrl+Shift+O` on Windows or Linux) when in a Git-tracked repo to search for and open files inside that repo.
1. You can also access this via the magnifying glass icon in the pane coding toolbelt at the top left of any pane.
3. **Browse via the** [File Tree (Project Explorer)](/code/code-editor/file-tree/) to open or create files.
4. **Opening a generated code diff** from an Agent Conversation: [Code Diffs in Agent Conversations](/agents/local-agents/code-diffs/).
[Opening files in Warp's code editor](https://screen.studio/share/H7hTUgf2)
**To save your changes to files**: use `⌘+S` on macOS or `Ctrl+S` on Windows or Linux.
### Tabbed file viewer
[Section titled “Tabbed file viewer”](#tabbed-file-viewer)
Warp can group multiple files into a single tabbed viewer, reducing clutter and making it easier to work across multiple files.
* Enabled by default for new users (can be toggled in **Settings** > **Code** > **Editor and Code Review** > **Group files into single editor pane**)
* Reorder, close, or drag file viewers between tabs.
* Merge entire panes together by dragging one into another.
**Here’s a more in-depth demo:**
[Tabbed file viewer in Warp's code editor](https://www.loom.com/embed/a682461da66944f583e2fa3d27b71189)
### File layout options
[Section titled “File layout options”](#file-layout-options)
Choose how new files open in Warp by default in: **Settings** > **Code** > **Editor and Code Review** > **Choose a layout to open files in Warp**
* **Split pane**: new files open alongside the current editor
* **New tab**: new files open in their own tabbed viewer
### Supported languages
[Section titled “Supported languages”](#supported-languages)
The editor supports syntax highlighting and editing for a wide range of languages, including:
Rust, Go, YAML, Python, JavaScript/TypeScript, JSX/TSX, Java/Groovy, C++, Shell/Bash, C#, HTML, CSS, C, JSON, HCL/Terraform, Lua, Ruby, PHP, TOML, Swift, Kotlin, Starlark, SQL, Powershell, and Elixir.
We’re continuously expanding language support.
### Shared buffers
[Section titled “Shared buffers”](#shared-buffers)
When you open the same file in multiple tabs or panes, Warp keeps them in sync automatically. Edits made in one view are immediately reflected in all others, and when a file changes on disk (for example, after switching branches), every view updates together.
### Other editor features
[Section titled “Other editor features”](#other-editor-features)
Warp’s native code editor also supports the following features:
* [Language Server Protocol (LSP)](/code/code-editor/language-server-protocol/) - Get hover info, go-to-definition, find references, inline diagnostics, and format-on-save powered by language servers for Rust, Go, Python, TypeScript/JavaScript, and C/C++.
* [File Tree (Project Explorer)](/code/code-editor/file-tree/) - Browse, open, and manage your project with Warp’s native file tree.
* [Find and Replace](/code/code-editor/find-and-replace/) - Use Warp’s built-in find and replace to quickly search across a file, jump between matches, and make precise edits with options for regex, case sensitivity, and smart case preservation.
* [Code Editor Vim Keybindings](/code/code-editor/code-editor-vim-keybindings/) - Use Vim keybindings to edit code and text in Warp’s native code editor.
# Code Editor Vim Keybindings
Canonical page: [/code/code-editor/code-editor-vim-keybindings/](https://docs.warp.dev/code/code-editor/code-editor-vim-keybindings/)
> Use Vim keybindings in Warp's code editor for keyboard-driven navigation and editing.
Warp’s built-in code editor supports native Vim keybindings for keyboard-driven navigation and editing. Enable Vim mode to use familiar motions, text objects, visual mode, registers, and editing commands directly in Warp without switching to an external editor.
## About Vim keybindings
[Section titled “About Vim keybindings”](#about-vim-keybindings)
The Vi family of programs (including Vim and Neovim) are modal text editors that allow for keyboard-driven text editing. Vi-style keybindings are especially popular among developers for their speed and precision in navigating and manipulating code. Warp’s [code editor](/code/code-editor/) now includes native support for Vim keybindings (also known as Vim mode), offering a familiar editing experience directly within your coding workflows.
### How to enable Vim keybindings
[Section titled “How to enable Vim keybindings”](#how-to-enable-vim-keybindings)
Vim mode in the code editor uses the same setting toggle as the input editor. To enable:
* Through the [Command Palette](/terminal/command-palette/), search for “Vim Keybindings”.
* Through **Settings** > **Features** > **Text Editing**, toggle “Edit code and commands with Vim keybindings”.
Unlike the input editor, the Vim implementation in the code editor starts in Normal mode.
### Customizing keybindings
[Section titled “Customizing keybindings”](#customizing-keybindings)
At the moment, Warp only supports default Vim keybindings.
One exception is the keyboard shortcut for exiting insert mode, which can be rebound under **Settings** > **Keyboard shortcuts** > **Exit Vim insert mode**, or through the [Command Palette](/terminal/command-palette/) search for “Exit Vim insert mode”.
## Supported keybindings
[Section titled “Supported keybindings”](#supported-keybindings)
Below is a list of the vim functionality implemented in Warp so far.
### Movement
[Section titled “Movement”](#movement)
See [Vim docs: motion](https://vimdoc.sourceforge.net/htmldoc/motion.html) for more information.
#### Basic
[Section titled “Basic”](#basic)
| Command(s) | Description |
| ---------------------------- | --------------------------------------------------- |
| `h`, `j`, `k`, `l` | single-char movement |
| `<space>`, `<backspace>` | single-char movement with line wrap |
| `w`, `W`, `b`, `B`, `e`, `E` | word movement |
| `ge`, `gE` | end of previous word |
| `$` | end of line |
| `0` | beginning of line |
| `^` | first non-whitespace character of line |
| `%` | jump to matching bracket |
| `[`, `]` | prev/next unmatched bracket |
| `_` | beginning of the current line |
| `+` | first non-whitespace character of the next line |
| `-` | first non-whitespace character of the previous line |
| `{`, `}` | prev/next paragraph |
#### Multi-line-related
[Section titled “Multi-line-related”](#multi-line-related)
| Command(s) | Description |
| ---------- | ----------------------- |
| `gg`, `G` | jump to first/last line |
### Editing
[Section titled “Editing”](#editing)
| Command(s) | Description |
| ---------- | ----------------------------------------------------------- |
| `r` | replace character under cursor |
| `d`, `D` | delete a range or object |
| `c`, `C` | change a range or object (delete, then go to insert mode) |
| `s`, `S` | substitute (like change, but can only delete at the cursor) |
| `x`, `X` | delete under cursor |
| `y`, `Y` | yank (copy) into the clipboard |
| `p`, `P` | paste from the clipboard |
| `u`, `⌃r` | undo, redo |
| `~` | toggle upper/lowercase under cursor |
| `gu` | lowercase under cursor (`u` in visual mode) |
| `gU` | uppercase under cursor (`U` in visual mode) |
| `J` | join current and following lines |
| `.` | repeat last edit |
| `gcc` | toggle comments on current line |
| `gc` | toggle comments on visual selection |
| `>`, `<` | indent or dedent a range or object |
| `>>`, `<<` | indent or dedent the current line |
See [Vim docs: editing](https://vimdoc.sourceforge.net/htmldoc/editing.html) for more information.
#### Indenting and dedenting
[Section titled “Indenting and dedenting”](#indenting-and-dedenting)
`>` and `<` are operators, so they combine with any supported motion or text object the same way `d` and `y` do:
| Command | Description |
| --------- | ------------------------------------------------------------ |
| `>>` | indent the current line |
| `<<` | dedent the current line |
| `>j` | indent the current line and the line below |
| `>ap` | indent the current paragraph |
| `3>>` | indent the current line and the two below it |
| `>` / `<` | indent or dedent the selection in visual or visual line mode |
In visual mode, `>` and `<` shift the selected lines and return to Normal mode.
See [Vim docs: shifting text](https://vimdoc.sourceforge.net/htmldoc/change.html#%3E) for more information.
#### Text objects
[Section titled “Text objects”](#text-objects)
| Command(s) | Description |
| ---------------- | ----------------------------------------------------------------------------- |
| `i` | inner (exclude delimiters in text object) |
| `a` | around (include delimiters in text object) |
| `w`, `W` | whitespace-delimited string (word) |
| `"`, `'`, \`\`\` | quote-delimited string |
| `(`, `{`, `[` | parenthesized/bracketed string |
| `l` | current line without leading/trailing whitespace (`il`); entire buffer (`al`) |
See [Vim docs: text objects](https://vimdoc.sourceforge.net/htmldoc/motion.html#text-objects) for more information.
### Search
[Section titled “Search”](#search)
#### Character search
[Section titled “Character search”](#character-search)
| Command(s) | Description |
| ------------------ | ------------------------------------------------------ |
| `t`, `T`, `f`, `F` | find next/prev matching character on line |
| `;` | repeat last character search in the same direction |
| `,` | repeat last character search in the opposite direction |
See [Vim docs: left-right motions](https://vimdoc.sourceforge.net/htmldoc/motion.html#f) for more information.
#### General search
[Section titled “General search”](#general-search)
Unlike Vim, general search commands don’t search within the buffer. Instead, they open Warp’s native command search.
| Command(s) | Description |
| ------------------ | ------------------------ |
| `/`, `?`, `*`, `#` | open Warp command search |
### Mode switching
[Section titled “Mode switching”](#mode-switching)
| Command(s) | Description |
| ---------- | ----------------------------------------------------------------- |
| `i` | insert text before the cursor |
| `I` | insert text before the first non-whitespace character in the line |
| `a` | append text after the cursor |
| `A` | append text at the end of the line |
| `o` | begin new line below the cursor and insert text |
| `O` | begin new line above the cursor and insert text |
| `v` | visual character mode |
| `V` | visual line mode |
See [Vim docs: insert](https://vimdoc.sourceforge.net/htmldoc/insert.html#insert) and [Vim docs: visual mode](https://vimdoc.sourceforge.net/htmldoc/visual.html#visual-mode) for more information.
### Registers
[Section titled “Registers”](#registers)
| Command(s) | Description |
| ---------- | --------------- |
| `"` | register prefix |
Warp currently supports the following registers:
| Register name | Description |
| ---------------- | ---------------------------------------------------------------- |
| `a`–`z`, `A`–`Z` | named registers |
| `+` | system clipboard |
| `*` | system clipboard |
| `"` | unnamed register, containing the text of the last delete or yank |
See [Vim docs: registers](https://vimdoc.sourceforge.net/htmldoc/change.html#registers) for more information.
## Feedback
[Section titled “Feedback”](#feedback)
The best way to report bugs and request features is through Warp’s [GitHub Issues](https://github.com/warpdotdev/Warp/issues) page. Note that the issue or request is for Vim keybindings.
# File Tree (Project Explorer)
Canonical page: [/code/code-editor/file-tree/](https://docs.warp.dev/code/code-editor/file-tree/)
> Browse, open, and manage project files with Warp's native file tree and context menu actions.
The File Tree is Warp’s built-in project explorer for browsing, opening, and managing files alongside your terminal. It automatically reflects your project structure and supports context menu actions like attaching files as agent context, copying paths, and creating new files.
Warp includes a **native file tree** that makes it easy to explore and manage project files. The file tree is available in any directory, and it automatically reflects your project structure as files are added, removed, or changed.
Note
The file tree also works over SSH on macOS and Linux when Warp’s [SSH extension](/terminal/warpify/ssh/#installing-the-ssh-extension) is installed on the remote host.
### Opening the file tree
[Section titled “Opening the file tree”](#opening-the-file-tree)
You can open the file tree from the tools panel on the left hand side:
* **Tools panel**: Click the Tools sidebar button, then open the File Tree tab (first tab in the panel).
* Press `⌘+\` to open the left panel, then assign your own shortcut for File Tree (and Warp Drive) in **Settings** > **Keyboard shortcuts**.
Note
Warp supports icons for common file types. If a file type is missing an icon, please [file a GitHub issue](https://github.com/warpdotdev/Warp/issues) so we can review and add support.
### Browsing and opening files
[Section titled “Browsing and opening files”](#browsing-and-opening-files)
Clicking on a file opens it directly in Warp’s [**native Code Editor**](/code/code-editor/), where you can view and edit code in a separate pane or tab.
## File and folder actions
[Section titled “File and folder actions”](#file-and-folder-actions)
Right-clicking any **file** opens a context menu with several useful options:
* **Open in new pane**: Open the file in a side-by-side pane.
* **Open in new tab**: Open the file in a new tab.
* **Attach as context**: Insert the file into an agent prompt so the Agent can analyze or reference it.
* **Copy path**: Copy the absolute file path.
* **Copy relative path**: Copy the path relative to your current working directory.
Right-click context menu on a folder in the file tree.
Right-clicking any **folder** opens a context menu with the following options:
* **Create new file**: Add a new file directly from the tree.
* **Attach as context**: Insert the selected file into your agent prompt so the Agent can analyze or reference it.
* **Copy path**: Copy the absolute file path to your clipboard.
* **Copy relative path**: Copy the path relative to your current working directory.
# Find and Replace
Canonical page: [/code/code-editor/find-and-replace/](https://docs.warp.dev/code/code-editor/find-and-replace/)
> Search and replace text in Warp's code editor with regex, case sensitivity, and smart case preservation.
Warp’s code editor includes built-in find and replace with support for regex, case sensitivity, and smart case preservation. Search across a file, jump between matches, and replace text with automatic casing adjustments for PascalCase, camelCase, and hyphenated patterns.
## Find
[Section titled “Find”](#find)
Press `⌘+F` on macOS or `Ctrl+Shift+F` on Windows and Linux to open the find menu. As you type, all matches in the file are highlighted, and the match closest to your cursor is selected.
* Press `Enter` or use the down arrow to jump to the next match
* Press `Shift+Enter` or use the up arrow to go to the previous match
* Click **Select All** to highlight all matches and close the menu
You can toggle regex and case-sensitive search options directly in the query editor.
[](/assets/terminal/code-find-menu.mp4)
## Replace
[Section titled “Replace”](#replace)
Click the dropdown to the left of the find menu to open the replace options.
* Press `Enter` to replace the currently selected match
* Use **Replace All** to replace all matches
Toggle **Preserve Case** to keep the original casing of replaced text. Case is preserved in text that contains PascalCase, camelCase, hyphens, and underscores. For example:
* Replacing “old” with “new” will turn “Old” into “New” and “OLD” into “NEW”
* Replacing “oldValue” with “NewValue” will result in “newValue”
* Replacing “OldValue” with “newValue” will result in “NewValue”
* Replacing “my-Old-VALUE” with “my-new-value” will result in “my-New-VALUE”
[](/assets/terminal/code-replace-menu.mp4)
# Language Server Protocol (LSP)
Canonical page: [/code/code-editor/language-server-protocol/](https://docs.warp.dev/code/code-editor/language-server-protocol/)
> Get hover info, go-to-definition, diagnostics, and format-on-save via built-in LSP support.
Warp’s code editor includes built-in support for the [Language Server Protocol](https://microsoft.github.io/language-server-protocol/), giving you IDE-grade code intelligence directly in the terminal. When you enable an LSP server for your project, you get hover documentation, go-to-definition, find references, inline diagnostics, and automatic formatting — all without leaving Warp.
## Supported languages
[Section titled “Supported languages”](#supported-languages)
Warp ships with support for the following language servers:
| Language | Server | File extensions |
| ----------------------- | ---------------------------- | -------------------------------------------------------------------- |
| Rust | `rust-analyzer` | `.rs` |
| Go | `gopls` | `.go` |
| Python | `pyright` | `.py` |
| TypeScript / JavaScript | `typescript-language-server` | `.ts`, `.tsx`, `.js`, `.jsx`, `.mjs`, `.cjs` |
| C / C++ | `clangd` | `.c`, `.C`, `.h`, `.H`, `.hh`, `.cc`, `.cpp`, `.cxx`, `.hpp`, `.hxx` |
We’re actively expanding language support. To request a language, [file a GitHub issue](https://github.com/warpdotdev/Warp/issues).
## How it works
[Section titled “How it works”](#how-it-works)
When you `cd` into a workspace with enabled language servers, Warp automatically starts them in the background. Features like hover, diagnostics, and go-to-definition become available once a server finishes initializing. As you edit, Warp sends incremental updates to keep everything in sync. If you close all files and terminals for a workspace, Warp shuts down the idle server to free resources.
Note
Warp uses your shell’s `PATH` to locate language server binaries. If a server isn’t found on your `PATH`, Warp can install it for you (see [Enabling a server](#enabling-a-server) below).
## Enabling and managing language servers
[Section titled “Enabling and managing language servers”](#enabling-and-managing-language-servers)
### Enabling a server
[Section titled “Enabling a server”](#enabling-a-server)
Language servers are enabled **per workspace** (per Git repository root). When you open a file in a supported language for the first time, the **editor footer** shows an option to enable the appropriate language server. If the server binary is not installed on your system, Warp offers to install it for you.
You can also manage servers from **Settings** > **Code** > **Indexing and projects**, where each initialized workspace shows its enabled language servers and their status.
### Server status indicator
[Section titled “Server status indicator”](#server-status-indicator)
The code editor footer displays a status icon for the active language server:
* 🟢 **Green** - Server is running and ready.
* 🟡 **Yellow** - Server is starting or processing a background task.
* 🔴 **Red** - Server failed to start. Click the icon to see options.
* ⚪ **Gray** - Server is stopped.
Clicking the status icon opens a menu with options to **restart**, **stop**, **start**, or **view logs** for the server.
### Server logs
[Section titled “Server logs”](#server-logs)
Each language server writes logs to a file on disk. Access these logs from the footer menu (click the status icon and select “Open Logs”) or from **Settings** > **Code** > **Indexing and projects**. Logs are useful for debugging server startup failures or unexpected behavior.
## Editor features powered by LSP
[Section titled “Editor features powered by LSP”](#editor-features-powered-by-lsp)
### Hover information
[Section titled “Hover information”](#hover-information)
Hover over a symbol to see its type signature, documentation, and other details provided by the language server. The hover tooltip appears after a brief delay and supports rich content including code blocks and Markdown.
### Go to definition
[Section titled “Go to definition”](#go-to-definition)
Hold `⌘` (macOS) or `Ctrl` (Windows/Linux) and click a symbol to jump to its definition. If the definition is in a different file, Warp opens it in the code editor. While you hold the modifier key, the symbol is underlined on hover to indicate it is navigable.
### Find references
[Section titled “Find references”](#find-references)
`⌘`-click (macOS) or `Ctrl`-click (Windows/Linux) on a symbol that is already at its definition to see a **Find References** card listing all references across the workspace. Click any reference to navigate to it.
### Inline diagnostics
[Section titled “Inline diagnostics”](#inline-diagnostics)
Warp displays errors and warnings from the language server as dashed underlines directly in the editor. Hover over an underlined range to see the full diagnostic message. Diagnostics update in real time as you edit and are briefly cleared while the server recalculates.
### Format on save
[Section titled “Format on save”](#format-on-save)
When you save a file (`⌘+S` / `Ctrl+S`), Warp requests formatting from the language server before writing to disk. This applies the server’s configured formatting rules (indentation, trailing whitespace, final newlines, etc.). If the server doesn’t support formatting, the file is saved without formatting changes.
### Right-click context menu
[Section titled “Right-click context menu”](#right-click-context-menu)
When an LSP server is connected, right-clicking in the editor opens a context menu with LSP-powered actions, including go-to-definition and find references.
LSP features stay in sync across [shared buffers](/code/code-editor/#shared-buffers) — if the same file is open in multiple tabs or panes, diagnostics, hover, and other features reflect the same content regardless of which view you’re looking at.
## Limitations
[Section titled “Limitations”](#limitations)
* **Local sessions only** - LSP is not available over SSH or WSL sessions. These are tracked in GitHub issues [#6831](https://github.com/warpdotdev/Warp/issues/6831) (SSH) and [#6744](https://github.com/warpdotdev/Warp/issues/6744) (WSL).
* **One server per language** - Each language maps to a single server (for example, Rust always uses `rust-analyzer`). Custom server configurations are not yet supported.
* **Project-scoped** - Language servers operate at the Git repository root level. Files outside a repository may not receive LSP features.
* **Server availability** - Some features (like formatting) depend on the specific language server’s capabilities. Not all servers support all features.
# Code Review panel
Canonical page: [/code/code-review/](https://docs.warp.dev/code/code-review/)
> The Code Review panel lets you review, edit, and manage Git diffs in real time, with options to attach, revert, or open files directly.
The Code Review panel lets you inspect, edit, and manage Git diffs directly inside Warp. Review uncommitted changes or compare branches, attach diffs as context for agents, revert specific hunks, and leave inline comments that agents can act on in real time.
## Overview
[Section titled “Overview”](#overview)
When you are working locally in a Git repository with uncommitted changes, the **Code Review panel** lets you inspect, edit, and manage code changes directly inside Warp. It integrates with Git and Warp’s Agents, giving you the ability to:
* Review diffs and attach them as context for the Agent
* Apply, edit, or revert changes in real time
* See changes made outside of Warp or by Warp’s Agents automatically reflected
Any uncommitted changes appear in the panel (or compare the changes on your branch against `main` or `master` ). Switching branches or saving files updates the panel instantly, so it always reflects the current state of your codebase.
[Code Review Demo](https://www.loom.com/embed/96581523168742eb9b95c3973924728c)
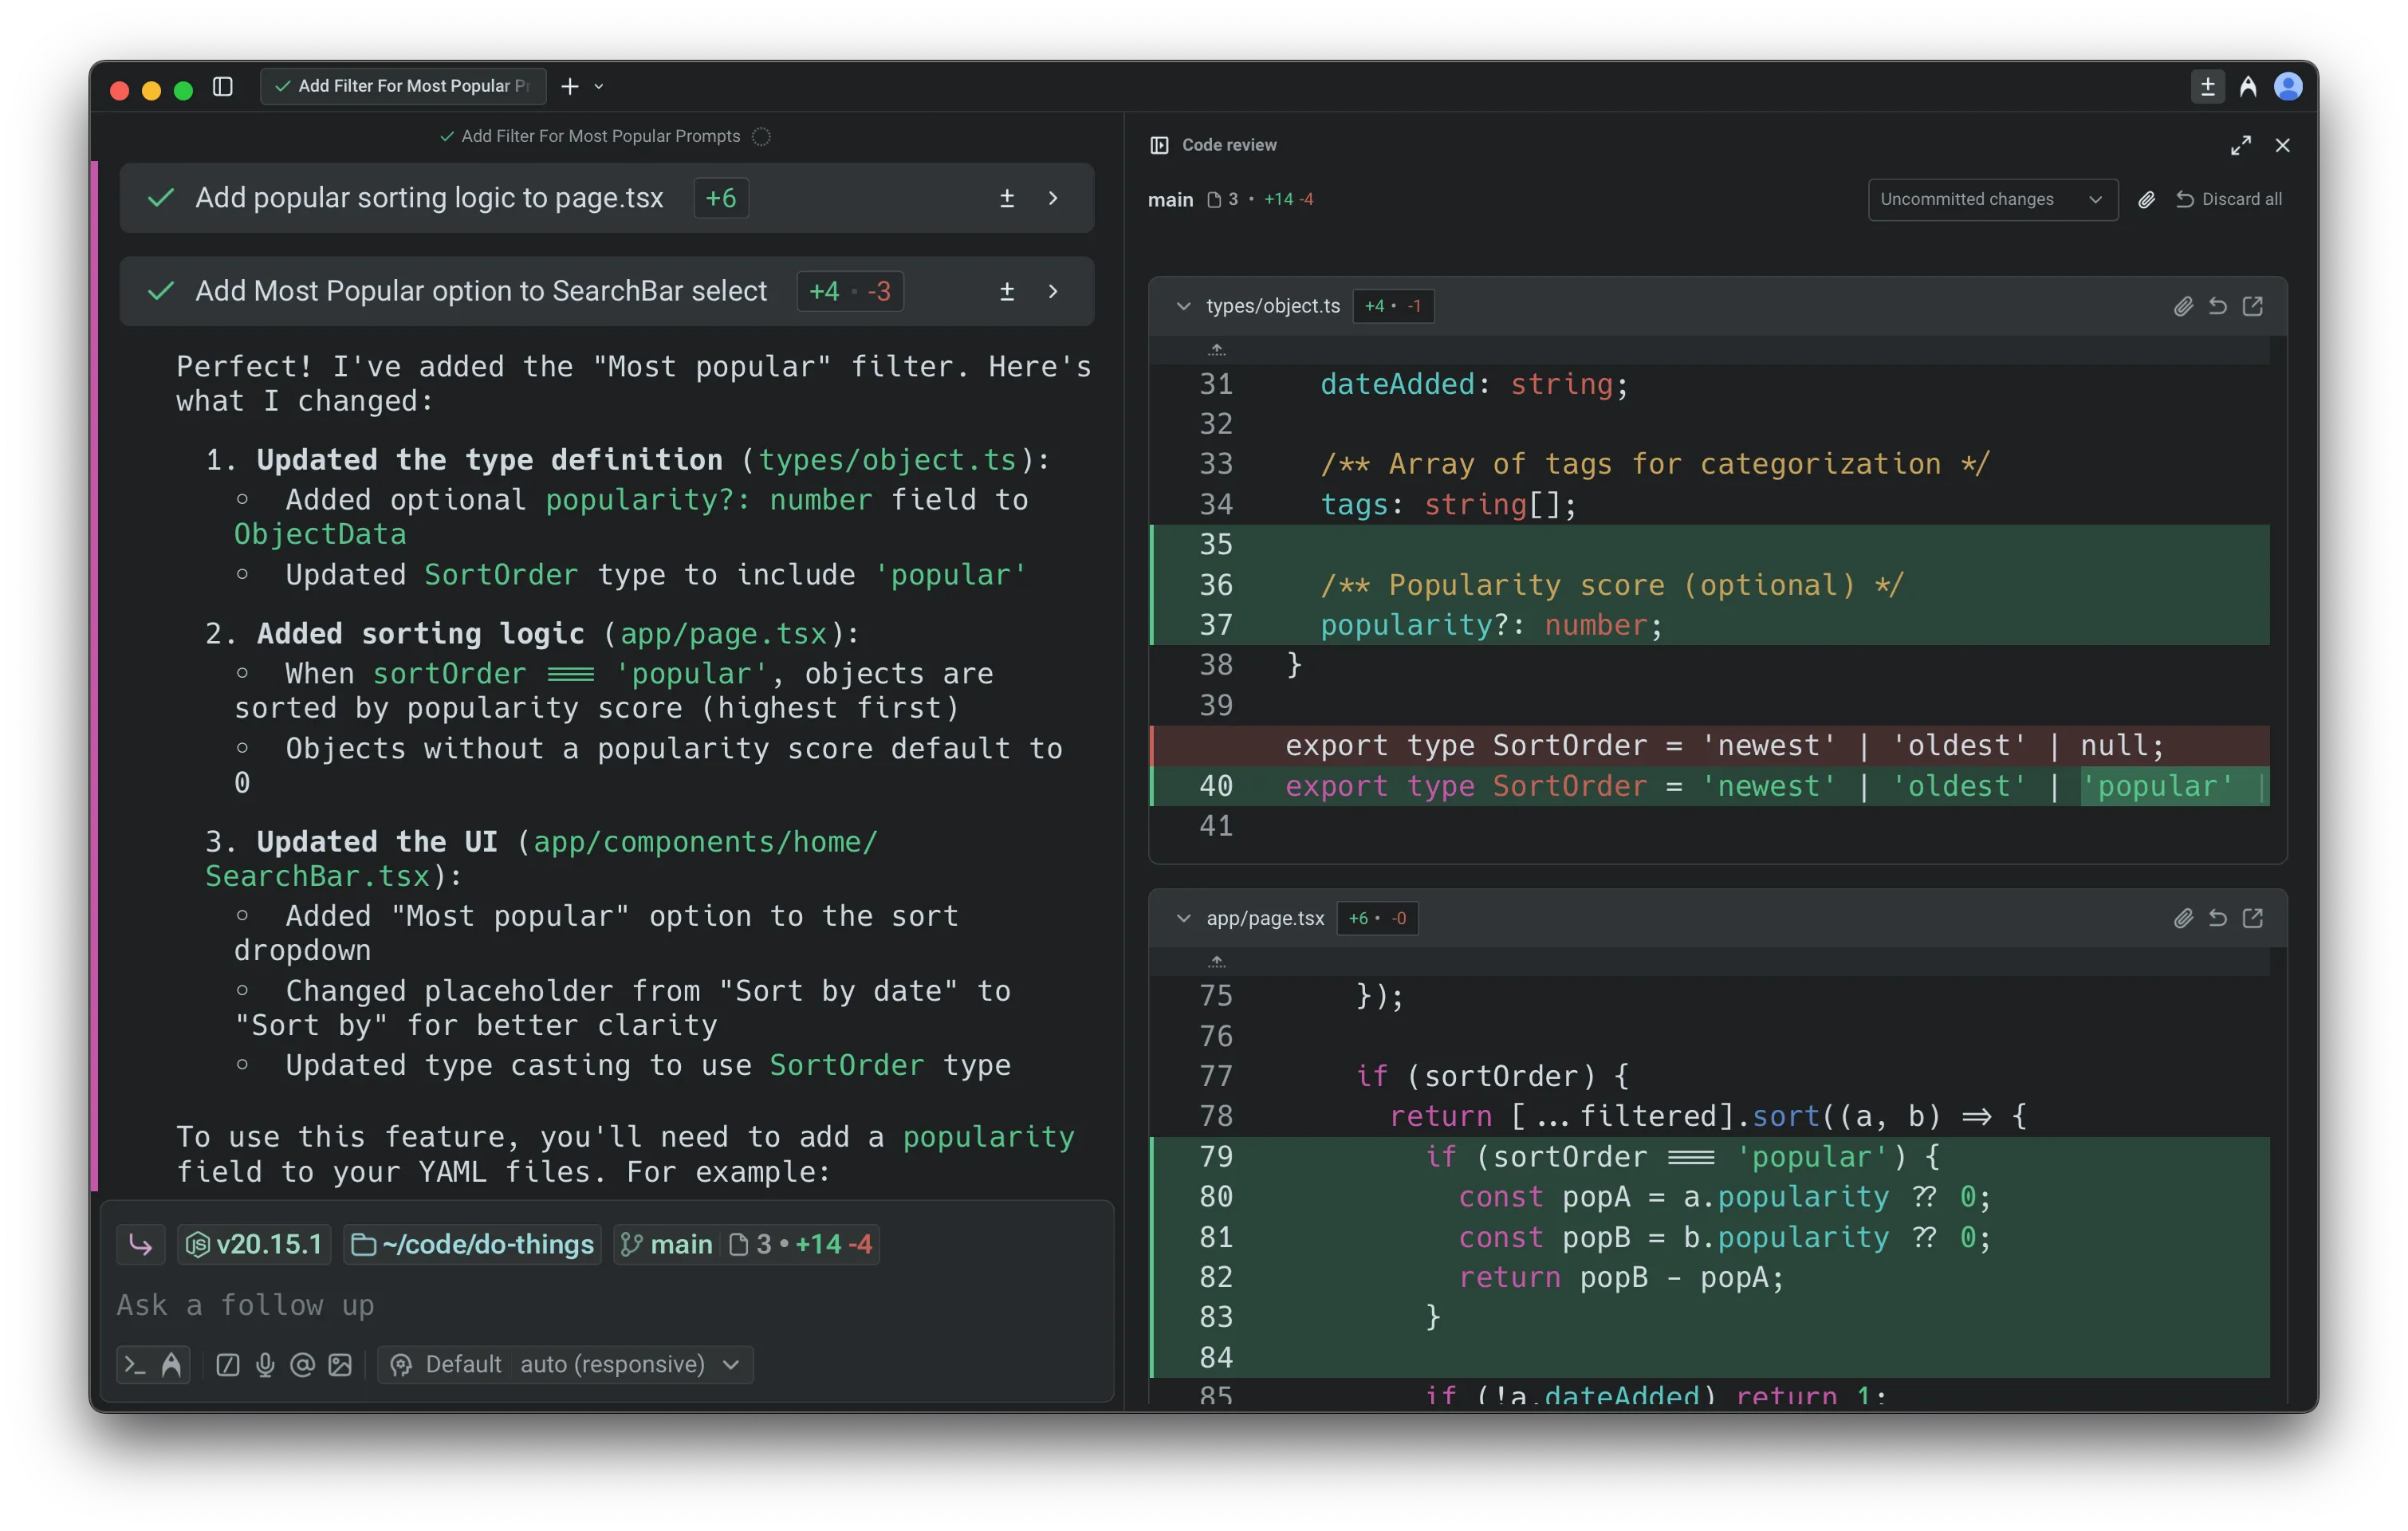
Full view of Code Review panel and terminal pane.
Note
To review agent-generated diffs, leave inline comments, batch your feedback, and have the agent apply all requested changes, see [Interactive Code Review](/agents/local-agents/interactive-code-review/).
Tip
If the agent’s changes are headed to a GitHub pull request, include a shared session or cloud run link in the PR so reviewers can inspect the prompt, plan, commands, logs, and validation behind the diff. See [Attach agent session context to GitHub PRs](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/).
## Opening the Code Review panel
[Section titled “Opening the Code Review panel”](#opening-the-code-review-panel)
The Code Review panel can be opened in several ways. Each entry point makes it easy to inspect and manage changes without leaving your workflow.
Tip
You can also open the Code Review panel with `Cmd+Shift++` on macOS or `Ctrl+Shift++` on Windows and Linux.
#### 1. Git diff chip (terminal input)
[Section titled “1. Git diff chip (terminal input)”](#1-git-diff-chip-terminal-input)
In terminal mode, when you’re in a Git repository with changes, the Git diff chip shows the number of files modified along with lines added and removed. Clicking the chip opens the Code Review panel with the relevant diffs.

The Git diff chip in the terminal input.
The Git diff chip tooltip.
#### 2. Agent conversation: review changes button
[Section titled “2. Agent conversation: review changes button”](#2-agent-conversation-review-changes-button)
When an Agent makes code edits in an [Agent Conversation](/agents/local-agents/interacting-with-agents/), a `Review changes` button appears at the bottom of the conversation. Click the button to open the code review panel.
The Review changes button in a conversation.
The conversation footer actions.
#### 3. Agent conversation: toolbelt (bottom right)
[Section titled “3. Agent conversation: toolbelt (bottom right)”](#3-agent-conversation-toolbelt-bottom-right)
During an Agent conversation, you can view all changed files in the toolbelt chips at the persistent bottom right. From there, you can open the Code Review panel directly.
The conversation toolbelt chips.
#### 4. Warp tab bar
[Section titled “4. Warp tab bar”](#4-warp-tab-bar)
In any Git-tracked repository, you can open the Code Review panel by clicking the `Code review` button in the top-right corner of Warp, next to your avatar.
#### Viewing all edited files
[Section titled “Viewing all edited files”](#viewing-all-edited-files)
Inside the Code Review panel, you can open the file sidebar to browse all changed files in your repository. Clicking on a file will automatically scroll to that file in the panel.
The Code Review panel file sidebar.
Note
By default, the Code Review panel opens as a pane on the right, but you can drag it to reposition wherever you prefer.
## Reviewing diffs
[Section titled “Reviewing diffs”](#reviewing-diffs)
By default, the Code Review panel shows all **uncommitted changes** on your current branch, excluding changes to files ignored by `.gitignore`.
Warp offers two ways to review changes:
1. **Uncommitted changes**: view all edits you’ve made locally on the current branch.
2. **Changes vs. main**: compare your branch against `main` or `master` to see what would be included in a pull request to that branch, for instance.
1. Warp automatically detects the target branch and updates the comparison accordingly.
3. **Changes vs. another branch**: compare your work against any arbitrary branch for stacked PRs, feature comparisons, or alternate base branches.
You can manually switch between the two views either in the Code Review panel or via the Git diff chip in the terminal input:
The diff view menu.
The Git diff chip menu.
The arbitrary branch diff menu.
Any saved edits made outside of Warp (e.g. in another editor), as well as changes applied by Warp’s Agents, appear automatically. The panel updates in real time, ensuring it always reflects the current state of your working file and directory.
#### Attaching diffs as context
[Section titled “Attaching diffs as context”](#attaching-diffs-as-context)
The Code Review pane makes it simple to share changes with the Agent. You can attach an entire diff to a prompt so the Agent has full visibility into what was added or removed.
Attaching a diff as context from the Code Review panel.
This ensures responses are grounded in your latest edits, whether you’re asking for feedback, explanations, or follow-up changes. For more details, see [Selection as Context](/agents/local-agents/agent-context/selection-as-context/).
#### Reverting diffs
[Section titled “Reverting diffs”](#reverting-diffs)
The Code Review panel lets you easily undo changes at different levels. In the gutter next to each diff, you’ll see an option to revert a hunk: roll back a specific set of changes (a “diff hunk”) within a file. This removes the added or modified lines and restores the previous version.
The Revert diff hunk tooltip.
When you revert, the changes are immediately updated in your working directory. The file is restored to match the selected version, so you can continue editing or commit without the reverted code.
### Opening files from Code Review
[Section titled “Opening files from Code Review”](#opening-files-from-code-review)
In addition to reviewing and editing diffs directly in the Code Review pane, you can open a file directly in Warp’s [Code Editor](/code/code-editor/).
The Code Review panel header.
* Clicking the **expand button** (right-most button on the header) opens the file in a new editor tab, allowing you to see the full file beyond just the changed lines.
* This is useful when you need additional context around a diff, want to make broader edits, or prefer working in the full editor rather than inline.
* Once opened, the file behaves like any other editor tab: you can scroll, edit, search, and save.
* Any changes made in the editor automatically sync back into the Code Review pane, so the diff view always stays current.
**Note**: from this code review file header, you can also attach a file diff as context into Warp’s agent, or discard all the changes on a single file.
#### Directly editing code diffs
[Section titled “Directly editing code diffs”](#directly-editing-code-diffs)
Alternatively, from the Code Review panel, you can click and edit the diffs directly:
Editing code in an inline diff.
### Sending comments to a running agent
[Section titled “Sending comments to a running agent”](#sending-comments-to-a-running-agent)
You can leave inline comments in the Code Review panel and send them directly to a running coding agent session, including third-party CLI agents like Claude Code, Codex, and others.
This extends Warp’s [Interactive Code Review](/agents/local-agents/interactive-code-review/) workflow to any supported CLI agent running in Warp. The agent receives your batch of comments and applies the requested changes.
[](/assets/terminal/code-review-inline-comment.mp4)
For more on supported agents, see [Third-party CLI agents](/agents/cli-agents/overview/).
### Discarding all changes
[Section titled “Discarding all changes”](#discarding-all-changes)
The Code Review panel also lets you discard every uncommitted change on your branch in one action. Clicking Discard all removes all local modifications shown in the panel and restores each file to its state on the base branch. This is useful when you want to reset your working directory, abandon a set of edits, or start a new iteration from a clean slate.
The Discard all changes button.
Discarding changes will ask you to confirm, but still make sure you’ve saved or backed up anything you want to keep before using it.
Note
Warp natively supports Git worktrees for Code Review and other features. See [Git worktrees](/code/git-worktrees/) for details.
# Git worktrees
Canonical page: [/code/git-worktrees/](https://docs.warp.dev/code/git-worktrees/)
> Warp natively supports Git worktrees, letting you work on multiple branches simultaneously with full Code Review, Codebase Context, and Agent support.
Warp natively supports [Git worktrees](https://git-scm.com/docs/git-worktree) — a Git feature that lets you check out multiple branches simultaneously in separate directories, all backed by the same repository. This is different from switching branches: with worktrees, you can have `~/project` on `main` and `~/project-wt/feature-x` on `feature-x` at the same time, with no stashing or context-switching required.
## How worktrees work in Warp
[Section titled “How worktrees work in Warp”](#how-worktrees-work-in-warp)
Warp automatically detects worktree checkouts. When you open a terminal in a worktree directory, Warp recognizes the `.git` file that points back to the main repository and treats the worktree as a fully functional repository:
* **Code Review panel** — Each worktree has its own Code Review panel showing uncommitted changes for that worktree’s branch. You can review diffs, revert hunks, and discard changes independently in each worktree.
* **Git Status chip** — The Git diff chip and branch indicator in the input bar reflect the correct branch and change counts for whichever worktree your terminal is in.
* **File watching** — Warp watches both the worktree’s working directory and the shared `.git` directory. Changes to shared Git state (such as new commits pushed to the remote) are detected and propagated across all open worktrees.
* **Codebase Context** — Each worktree is indexed independently for [Codebase Context](/agents/capabilities/codebase-context/), so Agents have accurate context for whichever worktree you’re working in.
* **Repository-scoped features** — Project rules (`AGENTS.md`, `WARP.md`), ignore files, and other repository-scoped settings work correctly within each worktree.
## When to use worktrees
[Section titled “When to use worktrees”](#when-to-use-worktrees)
Worktrees are especially useful when:
* **Reviewing a PR while working on your own branch** — Open the PR branch in a separate worktree without disrupting your in-progress work.
* **Running tests on one branch while coding on another** — Keep a long test suite running in one worktree while continuing development in another.
* **Parallel local agent work** — When orchestrating multiple local agents on the same repository, each agent can operate in its own worktree to avoid file conflicts.
## Creating a worktree
[Section titled “Creating a worktree”](#creating-a-worktree)
To create a new worktree from your terminal:
```bash
# Create a worktree for an existing branch
git worktree add ../my-feature feature-branch
# Create a worktree with a new branch
git worktree add -b new-branch ../new-branch main
# List all worktrees
git worktree list
# Remove a worktree when done
git worktree remove ../my-feature
```
Once created, open the worktree directory in a new Warp tab or pane. Warp detects it automatically — no additional configuration is needed.
Note
Commit state change notifications (e.g. detecting new commits) may be slightly delayed in worktrees compared to standard repositories. Warp is actively improving this.
# Code overview
Canonical page: [/code/overview/](https://docs.warp.dev/code/overview/)
> Generate and edit code with Warp's coding agent, review inline diffs, and apply changes across your codebase.
Warp’s coding features help you go from prompt to production. They combine a dedicated coding agent — consistently ranked among the top on SWE-bench Verified — with a native code editor, inline diff review, Codebase Context, and project-level rules for accurate, context-aware code generation.
Note
On macOS and Linux SSH sessions, Warp’s [SSH extension](/terminal/warpify/ssh/#installing-the-ssh-extension) brings the file tree, native file reads, and native code diffs to remote hosts. See [Feature support over SSH](/code/ssh-feature-support/) for the current support matrix.
## From prompt to production
[Section titled “From prompt to production”](#from-prompt-to-production)
Warp Code is a suite of features designed to help you take agent-generated code from the initial prompt and project setup all the way to deployment and production. It is powered by Warp’s dedicated coding agent, which consistently ranks among the top results on [SWE-bench Verified](https://www.swebench.com/#verified) and [Terminal-Bench](https://www.tbench.ai/leaderboard).
In addition to Warp’s modern, [native code editor](/code/code-editor/), it includes:
* [Codebase Context](/agents/capabilities/codebase-context/) for accurate, context-aware agent responses
* [Project Rules](/agents/capabilities/rules/) and Commands to tailor agent behavior per repository
* A dedicated [Code Review](/code/code-review/) experience for reviewing and editing diffs
* [Zero-state and setup flows](/code/overview/#getting-started-with-coding-in-warp) to quickly start a new project or initialize an existing one
### Coding agent
[Section titled “Coding agent”](#coding-agent)
Warp’s coding agent is designed to help you generate, edit, and manage code directly in the [Agentic Development Environment](https://www.warp.dev/blog/reimagining-coding-agentic-development-environment). It detects opportunities to apply code diffs and surfaces them inline, allowing you to review and apply changes without switching to an external IDE. When you need to make manual edits, you can open Warp’s native code editor.
### How it works
[Section titled “How it works”](#how-it-works)
* **Prompt-driven coding**: You write natural language prompts such as *“Add a retry mechanism to this API call”* or *“Fix the failing unit test in auth.test.ts.”*
* **Inline code diffs**: When the agent proposes changes, it shows them as diffs you can inspect, modify, or reject.
* **Agent steering**: You can refine prompts, interrupt and retry, or attach context (such as a file, diff, or selection) to guide the agent toward better results.

Note
With the [SSH extension](/terminal/warpify/ssh/#installing-the-ssh-extension) installed on a remote macOS or Linux host, the coding agent applies edits using Warp’s native diff tool over SSH. When the extension isn’t installed, the agent falls back to terminal commands (i.e. `sed`, `grep`) to make changes.
### Examples of coding capabilities
[Section titled “Examples of coding capabilities”](#examples-of-coding-capabilities)
Code responds to prompts related to code generation, editing, and analysis. Here are some examples:
* **Code creation**
* “Write a function in JavaScript to debounce an input”
* “Generate a Python class for managing user sessions with Redis.”
* **Error-driven fixes**
* “Fix the TypeScript error shown in the last build output.”
* “Resolve this merge conflict by keeping backend changes and updating tests accordingly.”
* **Refactoring**
* “Update all instances of var to let in this file.”
* “Extract the database logic from app.js into a new db.js module and update imports.”
* **Multi-file and repo-wide changes**
* “Add headers to all .py files in this directory.”
* “Replace requests with httpx across the codebase, updating imports and error handling.”
* **Complex workflows** (examples shown below — in practice, prompts should include more detail for best results)
* “Implement OAuth2 authentication, update affected routes, and add tests.”
* “Identify functions without test coverage and create Jest test files for them.”
* “Optimize slow SQL queries in queries.sql and regenerate migrations.”

## Getting started with coding in Warp
[Section titled “Getting started with coding in Warp”](#getting-started-with-coding-in-warp)
Warp provides multiple entry points to begin coding with agents, whether you are starting a new project, opening an existing one, or cloning from GitHub. Each new tab shows a **zero state** that lets you choose how to proceed.
Zero-state tab with coding starting points.
#### 1. Starting a new project
[Section titled “1. Starting a new project”](#1-starting-a-new-project)
To begin a new project, select **Create a New Project** from the tab. You can start directly with a prompt (Warp will suggest ideas) or configure the project manually. Warp sets up the repository with an `AGENTS.md` file (filename must be in all caps) containing [project rules](/agents/capabilities/rules/#project-rules) and enables [codebase indexing](/agents/capabilities/codebase-context/) to provide the agent with full context.
#### 2. Open an existing repo
[Section titled “2. Open an existing repo”](#2-open-an-existing-repo)
Select **Open Repository** to use your computer’s file picker. If you choose a Git repository, Warp automatically changes into the directory and runs the `/init` setup command (a built-in “[slash command](/agents/capabilities/slash-commands/)”) if the repo has not already been initialized. Warp will detect the repository, index the codebase, and prepare it for coding.
* For non-Git folders, Warp changes into the directory without initialization.
* If you have an existing project that is not yet initialized, you can run `/init` manually to bootstrap it with a version-controlled `AGENTS.md` file.
* This view also shows a list of your three most recently used repositories and AI conversations for quick access, as well as a list of recent directories (which behave like running `cd`).
#### 3. Clone a repo
[Section titled “3. Clone a repo”](#3-clone-a-repo)
Select **Clone Repository** to paste in a repo link or clone directly from GitHub. Warp places you in the cloned folder and automatically runs the `/init` flow to set up project rules and indexing.
## Learn more about code features
[Section titled “Learn more about code features”](#learn-more-about-code-features)
* [Code Editor](/code/code-editor/) - Warp’s built-in code editor lets you make quick, in-context edits with essentials like syntax highlighting, tabs, find and replace, Vim keybindings, and a file tree.
* [Language Server Protocol (LSP)](/code/code-editor/language-server-protocol/) - Warp integrates with language servers to provide hover info, go-to-definition, find references, inline diagnostics, and format-on-save for Rust, Go, Python, TypeScript/JavaScript, and C/C++.
* [Find and Replace](/code/code-editor/find-and-replace/) - Search within a file, move between matches, and replace text with options for regex, case sensitivity, and smart case preservation.
* [Codebase Context](/agents/capabilities/codebase-context/) - Warp indexes your Git-tracked codebase to help Agents understand your code and generate accurate, context-aware responses. No code is stored on Warp servers.
* [Code Review](/code/code-review/) - review, edit, and manage Git diffs in real time, with options to attach, revert, or open files directly.
* You can also enter [Interactive Code Review](/agents/local-agents/interactive-code-review/) to comment on changes, guide the agent, or adjust individual edits as they happen.
* [Code Diffs](/agents/local-agents/code-diffs/) - Learn how to review, refine, and apply code changes generated by Warp’s agents using the built-in visual diff editor.
# Feature support over SSH
Canonical page: [/code/ssh-feature-support/](https://docs.warp.dev/code/ssh-feature-support/)
> A reference for which Warp coding features are available over SSH and which are limited to local sessions.
When you [Warpify an SSH session](/terminal/warpify/ssh/), Warp’s core terminal features — the input editor, completions, blocks, history search, and more — work the same as they do locally. With Warp’s [SSH extension](/terminal/warpify/ssh/#installing-the-ssh-extension) installed on the remote host, coding features such as the file tree, the code editor, code review, codebase indexing, and native code diffs also work over SSH on macOS and Linux. The extension is installed on first connect when you choose **Install Warp’s SSH extension** — see [Requirements](/terminal/warpify/ssh/#requirements) for supported hosts.
Note
When a native tool isn’t available (for example, if you continue without installing the SSH extension), the Agent falls back to terminal commands (e.g. `cat`, `sed`, `grep`). You can still accomplish most coding tasks, but the experience is less seamless than working locally or through the SSH extension.
## Features that work over SSH
[Section titled “Features that work over SSH”](#features-that-work-over-ssh)
The following features work in all Warpified remote sessions, with or without the SSH extension:
* **Agent Mode conversations** — Chat with the Agent, ask questions, and request code changes on the remote host.
* **Running shell commands** — The Agent can execute commands on the remote machine on your behalf.
* **Grep and file glob** — The Agent can search for files and patterns using terminal-based grep and glob tools.
* **MCP tools** — Model Context Protocol integrations remain available.
* **Terminal features** — The input editor, command completions, autosuggestions, command history, blocks, and all other core terminal features work as expected.
The following features require the **SSH extension**:
* **File tree (Project Explorer)** — The [file tree sidebar](/code/code-editor/file-tree/) reflects the remote project structure and updates as you navigate or change files.
* **Code editor** — Open, view, and edit remote files in Warp’s [code editor](/code/code-editor/) from the file tree or the Command Palette, then save back to the remote host. Warp detects conflicting changes on disk and prompts you to resolve them.
* **Code review and git operations** — The [code review panel](/code/code-review/) works on remote repositories: review diffs, discard files, commit, push, and create PRs. AI-generated commit messages and PR descriptions are produced on the remote host.
* **Codebase indexing** — Warp indexes the remote repository so Agents can semantically search it, the same as [Codebase Context](/agents/capabilities/codebase-context/) locally.
* **File search** — Search for remote files by name from the [Command Palette](/terminal/command-palette/).
* **Project rules and skills** — Agents discover and use the remote project’s rules (`WARP.md`) and skills.
* **Native file reading** — The Agent reads remote files through Warp’s built-in file reading tool instead of shelling out to `cat`.
* **Native code diffs** — The Agent applies edits as inline [code diffs](/agents/local-agents/code-diffs/) you can review and approve, instead of using `sed` or other shell commands.
* **Reliable, parallel completions** — Generators run in parallel over a single multiplexed connection, so completions stop hitting the remote host’s `MaxSessions` ceiling and stop occasionally injecting errors into your blocks.
## Features not yet available over SSH
[Section titled “Features not yet available over SSH”](#features-not-yet-available-over-ssh)
The following features are not yet available in Warpified remote (SSH) sessions:
* **Language Server Protocol (LSP)** — [LSP features](/code/code-editor/language-server-protocol/) such as hover info, go-to-definition, and inline diagnostics are not available for remote files. SSH support is tracked in [GitHub #6831](https://github.com/warpdotdev/Warp/issues/6831).
* **Agent orchestration** — [Multi-agent runs](/platform/orchestration/) cannot be launched from a remote session; the Agent works as a single agent on the remote host.
* **Computer use** — The Agent cannot take screenshots or interact with the remote machine’s desktop.
Note
WSL sessions have the same limitations as SSH and are not currently covered by the SSH extension. Feature request for WSL support: [GitHub #6744](https://github.com/warpdotdev/Warp/issues/6744).
# Enterprise overview
Canonical page: [/enterprise/](https://docs.warp.dev/enterprise/)
> Warp Enterprise provides the security, control, and collaboration features organizations need to deploy Warp across their engineering teams at scale.
Warp Enterprise is built for organizations that want to accelerate software development with agents while maintaining security, compliance, and administrative control. It brings Warp’s **Agentic Development Environment** to your entire engineering organization with the governance features IT and security teams require.
Warp has three products:
* **Warp Terminal** - A modern terminal designed for agentic development where developers run commands, collaborate with agents, and orchestrate autonomous work from the command line.
* **Automation Platform** - Warp’s programmable system for running and coordinating agents at scale. The Automation Platform powers all agents in Warp, whether they run locally or in the cloud, and provides the orchestration, tracking, and control plane for scalable agent workflows.
* [**Warp Factories**](/factories/) - Warp’s product for building and operating software factories, where cloud agents triage, spec, implement, review, and verify work, and humans approve key decisions.
## Who Warp Enterprise is for
[Section titled “Who Warp Enterprise is for”](#who-warp-enterprise-is-for)
Warp Enterprise serves three primary audiences:
* **IT admins and platform teams** - Deploy and manage Warp across your organization with SSO, centralized administration, and usage visibility
* **Engineering managers** - Give your teams powerful agent development tools while enforcing coding standards and best practices through shared team resources
* **Professional developers** - Accelerate your work across the entire SDLC with state-of-the-art agents, team knowledge sharing, and collaborative workflows that keep you in control
## Key capabilities
[Section titled “Key capabilities”](#key-capabilities)
### Enterprise administration
[Section titled “Enterprise administration”](#enterprise-administration)
* **Single Sign-On (SSO)** - Authenticate via your existing identity provider (Okta, Microsoft Entra ID, Google Workspace, and more)
* **Centralized Admin Panel** - Manage team settings, user permissions, and feature controls from one location
* **User roles and permissions** - Control access with Team Owner, Team Admin, and Member roles
* **Usage visibility** - Monitor team adoption and agent usage across your organization, and pull usage data programmatically with the [Analytics API](/enterprise/enterprise-features/analytics-api/)
### Security and compliance
[Section titled “Security and compliance”](#security-and-compliance)
* **SOC 2 Type II certified** - Meets enterprise security and compliance requirements
* **Zero Data Retention (ZDR)** - No customer data is retained, stored, or used for training by contracted LLM providers
* **Open source client** - Warp’s client code is published under [AGPL v3](https://github.com/warpdotdev/warp/blob/master/LICENSE-AGPL) at [`warpdotdev/warp`](https://github.com/warpdotdev/warp) for security review and audit
* **Bring Your Own LLM (BYOLLM)** - Route inference through your own cloud infrastructure (AWS Bedrock or Google Cloud via Gemini Enterprise)
* **Team-managed API keys and endpoints** - Share provider API keys and custom endpoints across your Business or Enterprise team for both interactive sessions and cloud agents
* **Flexible deployment** - Choose Warp-hosted or hybrid deployment models
* **Telemetry controls** - Configure what data is collected at the team level
### Team collaboration
[Section titled “Team collaboration”](#team-collaboration)
* **Warp Drive team workspace** - Share Workflows, Notebooks, Prompts, Plans, Rules, and Environment Variables across your team
* **Codebase Context** - Team-level code indexing helps agents understand your repositories and generate accurate, context-aware responses
* **MCP integrations** - Connect to your team’s tools (Linear, Sentry, Figma, GitHub, and more) for context-aware agent responses
* **Session sharing** - Collaborate on terminal sessions and conversations with shareable links
### Agent capabilities
[Section titled “Agent capabilities”](#agent-capabilities)
* **State-of-the-art agents** - Multi-model agents with full terminal access, code editing, and autonomous task execution
* **Cloud agents** - Run agents in the cloud for unlimited parallelization, background automation, and long-running workflows. Perfect for PR reviews, scheduled tasks, and distributed work across multiple repositories
* **Integrated control plane** - Launch, orchestrate, and manage local, cloud, and autonomous agents from a unified interface. Track all agent activity across your team from the cloud agent dashboard
* **Agent Profiles** - Customize agent behavior, models, autonomy levels, and permissions
* **Rules and guardrails** - Enforce coding standards, tech stack preferences, and security practices through team-wide or project-specific rules
* **Multi-agent support** - Support for all major models and CLI coding agents (Automation Platform, Claude Code, Codex, Copilot)
## What this section covers
[Section titled “What this section covers”](#what-this-section-covers)
This section organizes Enterprise documentation to help you deploy, secure, and scale Warp across your organization:
* **Getting started** - Installation, SSO setup, and onboarding for admins and developers
* **Security and compliance** - Security overview and SSO configuration
* **Enterprise features** - Bring Your Own LLM (BYOLLM), team-managed API keys and endpoints for Business and Enterprise plans, and the Analytics API
* **Team management** - Admin panel, roles and permissions, and access controls
## Getting started
[Section titled “Getting started”](#getting-started)
Note
Warp Enterprise is available through annual contracts. [Contact our sales team](https://www.warp.dev/contact-sales) to learn more or start a trial.
**For IT admins**: Start with the [Admin Panel](/enterprise/team-management/admin-panel/) to manage team settings, configure agent policies, and enforce security controls. See [Roles and permissions](/enterprise/team-management/roles-and-permissions/) for user access details.
**For developers**: Jump to [Getting started for developers](/enterprise/getting-started/getting-started-developers/) to download Warp, log in, and start using key features like Codebase Context and Warp Drive. Or try the [Enterprise quickstart](/enterprise/getting-started/quickstart/) for a 10-minute walkthrough.
**For security teams**: Review our [Security page](https://www.warp.dev/legal/security) and [Privacy documentation](/support-and-community/privacy-and-security/privacy/) to understand how Warp handles data, encryption, and compliance.
## Why enterprises choose Warp
[Section titled “Why enterprises choose Warp”](#why-enterprises-choose-warp)
Organizations adopt Warp Enterprise to:
* **Accelerate development velocity** - Agents automate tedious tasks across the SDLC, from environment setup to incident response, so developers focus on what matters
* **Maintain security and control** - Deploy on your infrastructure, route inference through your cloud accounts, and keep developers in control with full visibility and guardrails
* **Scale best practices** - Share team knowledge, coding standards, and operational runbooks through Warp Drive to compound productivity gains across teams
* **Reduce context switching** - Keep developers in flow with a terminal-first environment that integrates agents, code editing, and tool integrations in one place
* **Get scaffolding built in** - Deploy agents at scale without building custom infrastructure—Warp provides orchestration, tracking, and collaboration out of the box
## Support and resources
[Section titled “Support and resources”](#support-and-resources)
* **Documentation** - Comprehensive guides throughout this enterprise section
* **Contact sales** - [Schedule a demo or start a trial](https://www.warp.dev/contact-sales)
* **Support** - Enterprise customers receive priority support via dedicated Slack/Teams channels
* **Warp Guides** - Video tutorials and training in the [Guides section](/guides/)
# Enterprise Analytics API
Canonical page: [/enterprise/enterprise-features/analytics-api/](https://docs.warp.dev/enterprise/enterprise-features/analytics-api/)
> Programmatically access team-level usage data for Warp's enterprise plans — per-team summaries, per-user rollups, and message-level activity events.
The Enterprise Analytics API lets enterprise admins pull Warp usage data into their own dashboards, cost-allocation tooling, or audit pipelines. It exposes three read-only endpoints over HTTPS that return aggregated team metrics, per-user rollups, and message-level activity events for the agents your team runs in Warp and the Automation Platform.
Early access
The Enterprise Analytics API is in Early Access. It is available to all enterprise teams. To start collecting data for your team, an admin must open the Warp app and turn on **Enterprise Usage Reporting (Early Access)** in **Admin Panel** > **Privacy** — no usage data is recorded until that toggle is on.
The API exposes **aggregated usage metrics** only (counts, credit spend, code-change tallies, and message-level metadata). It does not return the raw text of agent conversations. To retain and inspect full conversation contents, enable [cloud-synced conversations](/agents/local-agents/cloud-conversations/) under **Settings** > **Privacy**.
## What you can do with the API
[Section titled “What you can do with the API”](#what-you-can-do-with-the-api)
* **Build productivity dashboards** - Track adoption across users and teams over time using `summary` and `users`.
* **Allocate credit spend** - Break down usage by user, model, or run type (`local` vs. `cloud`) to attribute cost to teams or projects.
* **Audit message-level activity** - Filter the `events` endpoint by `run_type`, `user_id`, `conversation_id`, `message_type`, or `tool_type` for compliance reviews and incident investigation.
* **Power custom reporting** - Pipe the JSON responses into your own warehouse, BI tool, or alerting system.
## Prerequisites and access
[Section titled “Prerequisites and access”](#prerequisites-and-access)
Before you can call the API, your team must satisfy all of the following:
* **Enterprise plan** - The Analytics API is available to all enterprise teams during Early Access; no separate enrollment is required.
* **Admin role on the team** - Calls are rejected unless the authenticated user has admin-level permissions on the enterprise team. See [Roles and permissions](/enterprise/team-management/roles-and-permissions/).
* **A personal Warp API key** - Authenticate requests with a key from **Settings** > **Cloud platform** > **API keys** in the Warp app. See [API Keys](/agents/cli/oz-cli/api-keys/) for step-by-step instructions. Agent API keys (including legacy team keys) are not accepted by these endpoints — only personal API keys belonging to a team admin work.
* **Enterprise Usage Reporting toggle enabled** - In the Warp app, go to **Admin Panel** > **Privacy** and turn on **Enterprise Usage Reporting (Early Access)**. Until this toggle is on, no usage data is recorded for your team and the endpoints will return empty datasets even if every other prerequisite is met.
Caution
Personal API keys inherit the access of the user who created them. Treat them like any other admin credential and rotate them when team membership changes.
## Quickstart
[Section titled “Quickstart”](#quickstart)
The following example fetches a team-level summary for the last day. Set your API key first:
```bash
export WARP_API_KEY="wk-..."
```
Then call the `summary` endpoint:
```bash
curl "https://app.warp.dev/api/v1/enterprises/analytics/summary" \
-H "Authorization: Bearer $WARP_API_KEY"
```
Once an admin has turned on the **Enterprise Usage Reporting (Early Access)** toggle for your team, you’ll get a JSON payload aggregating credit usage and conversation counts across the team. Continue to the [Endpoints](#endpoints) section for per-endpoint details.
## Endpoints
[Section titled “Endpoints”](#endpoints)
All endpoints share the same base URL, authentication, and shared validation rules:
* **Base URL** - `https://app.warp.dev/api/v1/enterprises/analytics`
* **Authentication** - `Authorization: Bearer $WARP_API_KEY` header on every request.
* **Dates** - Pass `start_date` and `end_date` as RFC 3339 timestamps with timezone (for example, `2026-04-01T00:00:00Z` or `2026-04-01T00:00:00-07:00`). When omitted, the API defaults to a 1-day window ending at the current time. `start_date` must be strictly before `end_date`; otherwise the request returns `400 Bad Request`.
* **Performance** - Wider date ranges and finer `group_by_period` granularity scan more data and can take noticeably longer to return. For dashboards that refresh frequently, prefer narrower windows or coarser grouping.
### `GET /api/v1/enterprises/analytics/summary`
[Section titled “GET /api/v1/enterprises/analytics/summary”](#get-apiv1enterprisesanalyticssummary)
Returns a single team-level rollup of conversation counts, credit spend, and code-change activity for the requested window. When `group_by_period` is set, the response is a time series with one bucket per period.
**Query parameters:**
* `start_date` (optional) - RFC 3339 timestamp. Defaults to one day before `end_date`.
* `end_date` (optional) - RFC 3339 timestamp. Defaults to the current time.
* `group_by_period` (optional) - One of `day`, `week`, or `month`. When set, the resulting `period_list` is capped at 365 periods; longer ranges with finer granularity are rejected with `400 Bad Request`.
**Example:**
```bash
curl "https://app.warp.dev/api/v1/enterprises/analytics/summary?start_date=2026-04-01T00:00:00Z&end_date=2026-04-30T23:59:59Z&group_by_period=day" \
-H "Authorization: Bearer $WARP_API_KEY"
```
**Ungrouped response shape:**
```json
{
"data": {
"local": {
"total_conversations_count": 1234,
"total_credits_spent": 8421.5,
"code_changes": {
"file_changes": { "suggested": 412, "accepted": 305 },
"lines_of_code": {
"suggested": { "added_count": 9821, "removed_count": 2104 },
"accepted": { "added_count": 7102, "removed_count": 1488 }
}
}
},
"cloud": {
"total_conversations_count": 412,
"total_credits_spent": 2310.4,
"code_changes": {
"file_changes": { "suggested": 88, "accepted": 64 },
"lines_of_code": {
"suggested": { "added_count": 1450, "removed_count": 320 },
"accepted": { "added_count": 1102, "removed_count": 248 }
}
}
}
}
}
```
**Grouped response shape (`group_by_period=day`):**
```json
{
"group_by_period": "day",
"period_list": ["2026-04-01", "2026-04-02", "..."],
"data": {
"local": {
"total_conversations_count": [42, 51, "..."],
"total_credits_spent": [310.1, 412.5, "..."],
"code_changes": {
"file_changes": { "suggested": [12, 18, "..."], "accepted": [9, 14, "..."] },
"lines_of_code": {
"suggested": { "added_count": [240, 380, "..."], "removed_count": [55, 90, "..."] },
"accepted": { "added_count": [180, 290, "..."], "removed_count": [40, 70, "..."] }
}
}
},
"cloud": { "...": "same shape as local" }
}
}
```
In the grouped response, every leaf array is the same length as `period_list`, and the index of each value corresponds to the same index in `period_list`. Periods with no recorded activity are filled with default empty values (`0` for numeric counts and credit totals, and `0`-valued sub-objects for `code_changes`).
### `GET /api/v1/enterprises/analytics/users`
[Section titled “GET /api/v1/enterprises/analytics/users”](#get-apiv1enterprisesanalyticsusers)
Returns per-user aggregated usage, split into `local` (Warp app) and `cloud` (cloud agents) sections. Results are paginated.
**Query parameters:**
* `start_date` (optional) - RFC 3339 timestamp. Defaults to one day before `end_date`.
* `end_date` (optional) - RFC 3339 timestamp. Defaults to the current time.
* `group_by_period` (optional) - One of `day`, `week`, or `month`. When set, each user record’s per-run-type fields are arrays indexed by the response-level `period_list`.
* `page` (optional) - Page number, 1-indexed. Default `1`.
* `page_size` (optional) - Items per page. Default `10`.
**Example:**
```bash
curl "https://app.warp.dev/api/v1/enterprises/analytics/users?page=1&page_size=25" \
-H "Authorization: Bearer $WARP_API_KEY"
```
**Ungrouped response shape:**
```json
{
"data": [
{
"user_id": "user-uuid-abc",
"email": "alex@example.com",
"local": {
"distinct_conversation_count": 42,
"credits_spent": 310.1,
"model_usage": [
{ "model_id": "claude-4-7-opus", "distinct_conversation_count": 30, "credits_spent": 240.0 }
],
"code_changes": {
"file_changes": { "suggested": 18, "accepted": 12 },
"lines_of_code": {
"suggested": { "added_count": 412, "removed_count": 88 },
"accepted": { "added_count": 305, "removed_count": 64 }
}
}
},
"cloud": { "...": "same shape as local" }
}
],
"pagination": {
"current_page": 1,
"page_size": 25,
"total_pages": 4,
"total_count": 87
}
}
```
When `group_by_period` is set, each `local`/`cloud` block’s scalars become arrays indexed by the response-level `period_list` (same convention as the grouped `summary` response). Within `model_usage`, each entry’s `distinct_conversation_count` and `credits_spent` likewise become arrays.
### `GET /api/v1/enterprises/analytics/events`
[Section titled “GET /api/v1/enterprises/analytics/events”](#get-apiv1enterprisesanalyticsevents)
Returns paginated, message-level activity events for fine-grained audits and dashboards. Each row corresponds to a single message produced or processed by an agent — the same canonical message stream the client and Warp UI see.
**Query parameters:**
* `start_date` (optional) - RFC 3339 timestamp. Defaults to one day before `end_date`. The window between `start_date` and `end_date` cannot exceed 365 days.
* `end_date` (optional) - RFC 3339 timestamp. Defaults to the current time.
* `page` (optional) - Page number, 1-indexed. Default `1`.
* `page_size` (optional) - Items per page. Default `10`. Maximum `100`.
* `run_type` (optional) - Filter by `local` or `cloud`.
* `user_id` (optional) - The unique identifier of a single team member, as returned by the `users` and `events` endpoints.
* `conversation_id` (optional) - Restrict results to one conversation.
* `message_type` (optional) - Filter by message variant. Common values include `agent_output`, `tool_call`, `tool_call_result`, `user_query`, and `agent_reasoning`; additional values are emitted as new agent capabilities ship. Internal scaffolding (for example `model_used`, `server_event`, `messages_received_from_agents`, `events_from_agents`, and `debug_output`) is not recorded and never appears here.
* `tool_type` (optional) - For `tool_call` / `tool_call_result` messages, restrict to a specific tool. Values are the snake\_case name of the tool (for example `apply_file_diffs`, `run_shell_command`, `search_codebase`, `grep`, `call_mcp_tool`).
Events are returned newest-first, ordered by `message_end_timestamp DESC, message_id DESC`.
**Example:**
```bash
curl "https://app.warp.dev/api/v1/enterprises/analytics/events?run_type=cloud&message_type=tool_call&tool_type=apply_file_diffs&page_size=100" \
-H "Authorization: Bearer $WARP_API_KEY"
```
**Response shape:**
```json
{
"data": [
{
"message_id": "msg-uuid",
"llm_request_ids": ["llm-req-uuid"],
"message_type": "tool_call",
"tool_type": "apply_file_diffs",
"message_start_timestamp": "2026-04-15T19:21:08Z",
"message_end_timestamp": "2026-04-15T19:21:11Z",
"conversation_id": "conv-uuid",
"user_id": "user-uuid-abc",
"email": "alex@example.com",
"user_selected_model": "auto",
"run_type": "cloud",
"model_ids": ["claude-4-7-opus"],
"credit_charged": 0.42,
"code_changes": {
"file_changes": { "suggested": 3, "accepted": 2 },
"lines_of_code": {
"suggested": { "added_count": 48, "removed_count": 12 },
"accepted": { "added_count": 36, "removed_count": 8 }
},
"was_edited_by_user": false
},
"git_context": {
"head": "a1b2c3d",
"branch": "feature/analytics-api"
},
"error_type": null
}
],
"pagination": {
"current_page": 1,
"page_size": 100,
"total_pages": 12,
"total_count": 1180
}
}
```
Fields are populated as follows:
* `llm_request_ids` and `model_ids` are arrays. Most LLM-backed messages have a single entry, but some messages may be backed by multiple LLM requests.
* `credit_charged` is the per-message proportional share of the backing LLM request’s cost. Messages with no LLM call (for example client-submitted `tool_call_result` rows) carry `0`.
* `code_changes` is omitted (or `null`) for messages that don’t suggest or apply file changes.
* `was_edited_by_user` is `true` when the user edited the diff before accepting, `false` when accepted as-is, and `null` when the message had no acceptance event.
* `git_context` is omitted (or `null`) when no git state was captured for the message.
* `error_type` is populated only when the backing LLM request errored.
## Pagination
[Section titled “Pagination”](#pagination)
The `users` and `events` endpoints use offset-based pagination with `page` and `page_size` query parameters. Every paginated response includes a `pagination` block:
* `current_page` - The page returned, 1-indexed.
* `page_size` - The number of items requested per page.
* `total_pages` - The total number of pages available for the current query.
* `total_count` - The total number of records matching the query across all pages.
To iterate, request `page=1` first, then increment `page` until you’ve fetched `total_pages` pages. The `events` endpoint caps `page_size` at `100`; values above that are rejected. The `users` endpoint defaults to `page_size=10`.
## Common use cases
[Section titled “Common use cases”](#common-use-cases)
* **Executive dashboards** - Combine the `summary` endpoint’s grouped output with your BI tool to chart team-wide adoption and credit spend over time.
* **Cost allocation** - Use the `users` endpoint to attribute credit spend to individuals, teams, or projects for chargeback or showback.
* **Adoption monitoring** - Track per-user `distinct_conversation_count` over time to identify power users, onboard slow adopters, and measure rollout impact.
* **Compliance audit trails** - Pull the `events` endpoint with `message_type=tool_call` filters to log code-changing actions for security review.
## FAQ
[Section titled “FAQ”](#faq)
### How fresh is the data?
[Section titled “How fresh is the data?”](#how-fresh-is-the-data)
Usage data is recorded as agents run and is typically available within a few minutes. There is no guaranteed SLA on freshness during Early Access.
### Who can call the API?
[Section titled “Who can call the API?”](#who-can-call-the-api)
Any authenticated user with admin-level permissions on an enterprise team. Calls from non-admin users return `403 Forbidden`.
### What kind of API key works?
[Section titled “What kind of API key works?”](#what-kind-of-api-key-works)
Only **personal** Warp API keys created by an admin from **Settings** > **Cloud platform** > **API keys**. Agent API keys (including legacy team keys) are explicitly rejected by these endpoints. See [API Keys](/agents/cli/oz-cli/api-keys/) for how to create one.
### Are these calls billed?
[Section titled “Are these calls billed?”](#are-these-calls-billed)
No. Analytics API calls don’t consume Warp credits.
### What time range can I query?
[Section titled “What time range can I query?”](#what-time-range-can-i-query)
The `events` endpoint enforces a hard 365-day window between `start_date` and `end_date`. The `summary` and `users` endpoints don’t enforce a fixed window, but the grouped variants are capped at 365 periods.
## Related resources
[Section titled “Related resources”](#related-resources)
* [API Keys](/agents/cli/oz-cli/api-keys/) - Create and manage personal Warp API keys.
* [Admin Panel](/enterprise/team-management/admin-panel/) - Manage team settings, including the **Privacy** section.
* [Roles and permissions](/enterprise/team-management/roles-and-permissions/) - Required admin role for Analytics API access.
* [Architecture and deployment](/enterprise/enterprise-features/architecture-and-deployment/) - Where enterprise data is stored and how it transits Warp’s infrastructure.
# Architecture and deployment
Canonical page: [/enterprise/enterprise-features/architecture-and-deployment/](https://docs.warp.dev/enterprise/enterprise-features/architecture-and-deployment/)
> Understand Warp's system architecture and choose the right deployment model for your organization - Warp-hosted, self-hosted, or hybrid.
Warp’s architecture separates the **control plane** (orchestration, observability, and LLM inference) from the **execution plane** (where agents run, code is accessed, and commands execute). This separation gives enterprise teams flexibility to choose where sensitive workloads run while maintaining centralized management and visibility.
Use this information to evaluate which deployment model fits your organization’s security, compliance, and operational requirements.
## System architecture overview
[Section titled “System architecture overview”](#system-architecture-overview)
Warp’s cloud agent infrastructure has four key components:
1. **Trigger** - What starts an agent run (CI step, webhook, cron schedule, Slack mention, CLI command, or API/SDK call).
2. **Orchestration** - What decides what to run and tracks it (Automation Platform orchestrator or your own system).
3. **Execution** - Where the agent actually runs (Warp-hosted environment, your infrastructure, or your existing CI/orchestrator).
4. **Visibility** - How the team monitors and intervenes (cloud agent dashboard, session sharing, APIs/SDKs).
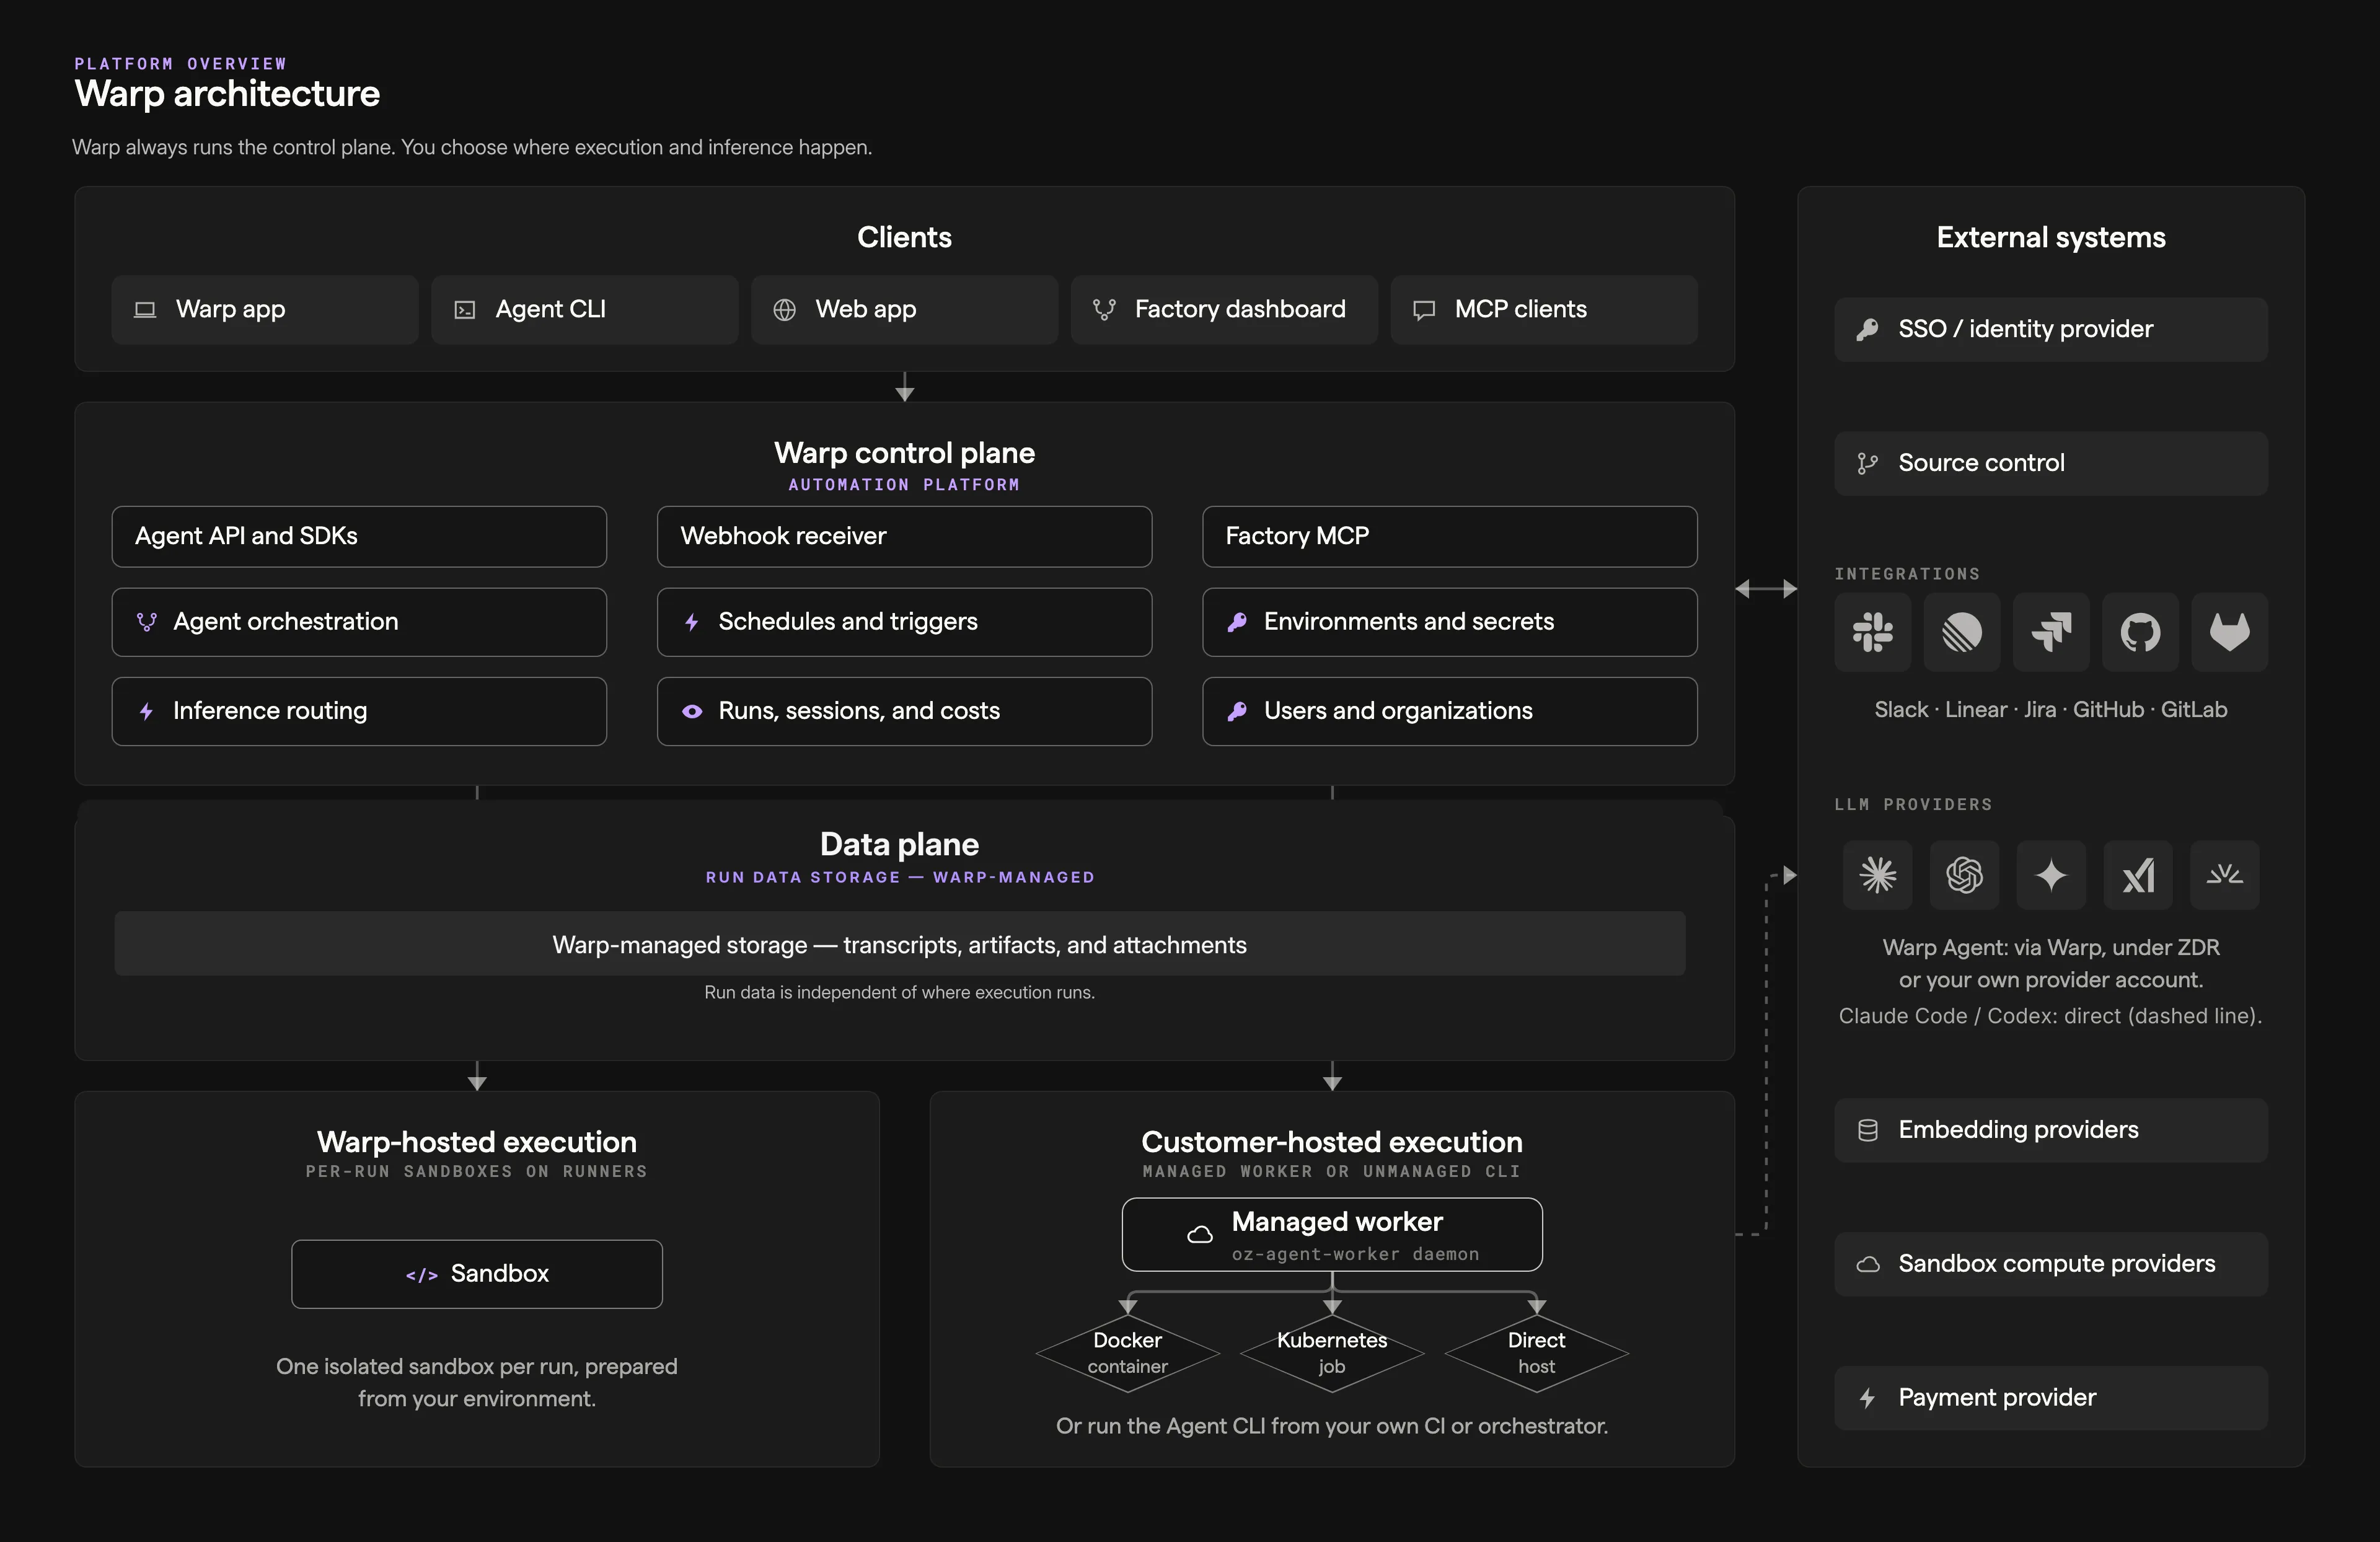
The [stack overview](/platform/architecture/#stack-overview) reference describes each component in this diagram.
### High-level data flow
[Section titled “High-level data flow”](#high-level-data-flow)
* **Warp terminal (client)** ↔ **Warp backend (control plane)** ↔ **LLM providers**
* The Warp backend handles task orchestration, observability, and LLM inference routing.
* LLM providers operate under **Zero Data Retention (ZDR)** agreements. They do not store or train on your data.
* The **execution plane** is where source code is accessed, commands run, and build artifacts are produced. This can run on Warp’s infrastructure or yours.
## Warp-hosted (SaaS)
[Section titled “Warp-hosted (SaaS)”](#warp-hosted-saas)
Warp-hosted is the default deployment model. Agents run on Warp-managed infrastructure with no setup required from your team.
### How it works
[Section titled “How it works”](#how-it-works)
* Agents execute in **isolated Docker containers** on Warp-hosted infrastructure (GCP).
* The Automation Platform orchestrator manages agent lifecycle - provisioning, execution, monitoring, and cleanup.
* Environments are ephemeral and destroyed after each run.
### Triggers
[Section titled “Triggers”](#triggers)
Warp-hosted agents can be triggered by:
* **First-party integrations** - Slack, Linear, and other connected tools
* **Scheduled agents** - Cron-like automation for recurring work
* **CLI** - `oz agent run-cloud` for on-demand cloud execution
* **API/SDK** - Programmatic triggers from your own systems
### When to use
[Section titled “When to use”](#when-to-use)
* You want the simplest path to scalable cloud agent execution.
* You need to run many tasks in parallel without building sandboxing infrastructure.
* Your security requirements are met by Warp’s SOC 2 Type II certified infrastructure with ZDR.
## Self-hosted execution
[Section titled “Self-hosted execution”](#self-hosted-execution)
For organizations that need agent execution and source code to remain within their own network boundary, Warp supports self-hosted execution.
Note
Self-hosted execution is available exclusively on Warp’s **Enterprise** plan.
### Split architecture
[Section titled “Split architecture”](#split-architecture)
Self-hosted deployments use a split architecture:
* **Execution plane (customer-hosted)** - Source code repositories, build artifacts, shell commands, and runtime secrets stay on your infrastructure. Note that during agent interactions, code context is included in LLM prompts and session transcripts that route through Warp’s servers under ZDR agreements (see [What transits Warp’s servers](#what-transits-warps-servers)).
* **Control plane (Warp-hosted)** - Task orchestration, observability data, and LLM inference route through Warp’s servers under Zero Data Retention (ZDR) agreements.
### Deployment modes
[Section titled “Deployment modes”](#deployment-modes)
**Unmanaged** - Use `oz agent run` to run agents in your existing orchestrator or CI environment. Supports Linux, macOS, and Windows with no Docker dependency.
* Best for teams that already have CI/CD infrastructure or internal orchestrators.
* You control scheduling, scaling, and environment setup.
* Warp provides cloud connectivity, shared context, visibility, and session sharing.
**Managed** - Run the `oz-agent-worker` daemon to let Warp orchestrate agents in isolated Docker containers on your infrastructure.
* The worker process connects to the Automation Platform via WebSocket and receives tasks automatically.
* Agents run in isolated Docker containers managed by the worker.
* You get the same orchestration capabilities as Warp-hosted, but execution stays on your infrastructure.
### Network requirements
[Section titled “Network requirements”](#network-requirements)
Self-hosted agents require **outbound-only** network access. No inbound network access is required.
**Egress requirements:**
* Outbound access to Warp’s backend services (for orchestration and observability)
* For managed mode: access to Docker Hub and GitHub (for container images and repository access)
### When to use
[Section titled “When to use”](#when-to-use-1)
* Compliance or security requirements prevent using Warp-hosted compute.
* Source code and execution must stay within your network boundary.
* You want Automation Platform orchestration and visibility without sending code to Warp’s infrastructure.
## Hybrid deployments
[Section titled “Hybrid deployments”](#hybrid-deployments)
Organizations can combine Warp-hosted and self-hosted execution to balance convenience with security requirements.
### How it works
[Section titled “How it works”](#how-it-works-1)
* Route sensitive workloads (e.g., production code, regulated data) to self-hosted agents.
* Route less sensitive workloads (e.g., open-source tooling, internal utilities) to Warp-hosted agents.
* Both execution modes share the same cloud agent dashboard, session sharing, and API/SDK visibility.
### Example configurations
[Section titled “Example configurations”](#example-configurations)
* **By sensitivity** - Production repositories run on self-hosted agents; staging and development run on Warp-hosted.
* **By team** - Security-sensitive teams (e.g., infrastructure, payments) use self-hosted; other teams use Warp-hosted.
* **By task type** - Scheduled maintenance tasks run on Warp-hosted; ad-hoc debugging runs self-hosted in dev environments.
## Data flow and boundaries
[Section titled “Data flow and boundaries”](#data-flow-and-boundaries)
Understanding what data stays where is critical for security and compliance decisions.
### What stays on customer infrastructure (self-hosted)
[Section titled “What stays on customer infrastructure (self-hosted)”](#what-stays-on-customer-infrastructure-self-hosted)
* **Source code** - Repository contents and version history
* **Build artifacts** - Compiled outputs and generated files
* **Shell commands** - Terminal commands and their output
* **Runtime secrets** - Environment variables and credentials
* **Execution logs** - Agent run logs and diagnostics
### What transits Warp’s servers
[Section titled “What transits Warp’s servers”](#what-transits-warps-servers)
* **Task orchestration** - Scheduling, routing, and lifecycle management
* **Observability data** - Run status, duration, and metadata
* **LLM inference** - Prompts and responses (which include code context from agent interactions) routed through Warp to contracted LLM providers under ZDR agreements
* **Session sharing data** - Session transcripts, which include code context from agent interactions, when session sharing is enabled for monitoring and collaboration
## Choosing a deployment model
[Section titled “Choosing a deployment model”](#choosing-a-deployment-model)
Consider the following when selecting a deployment model:
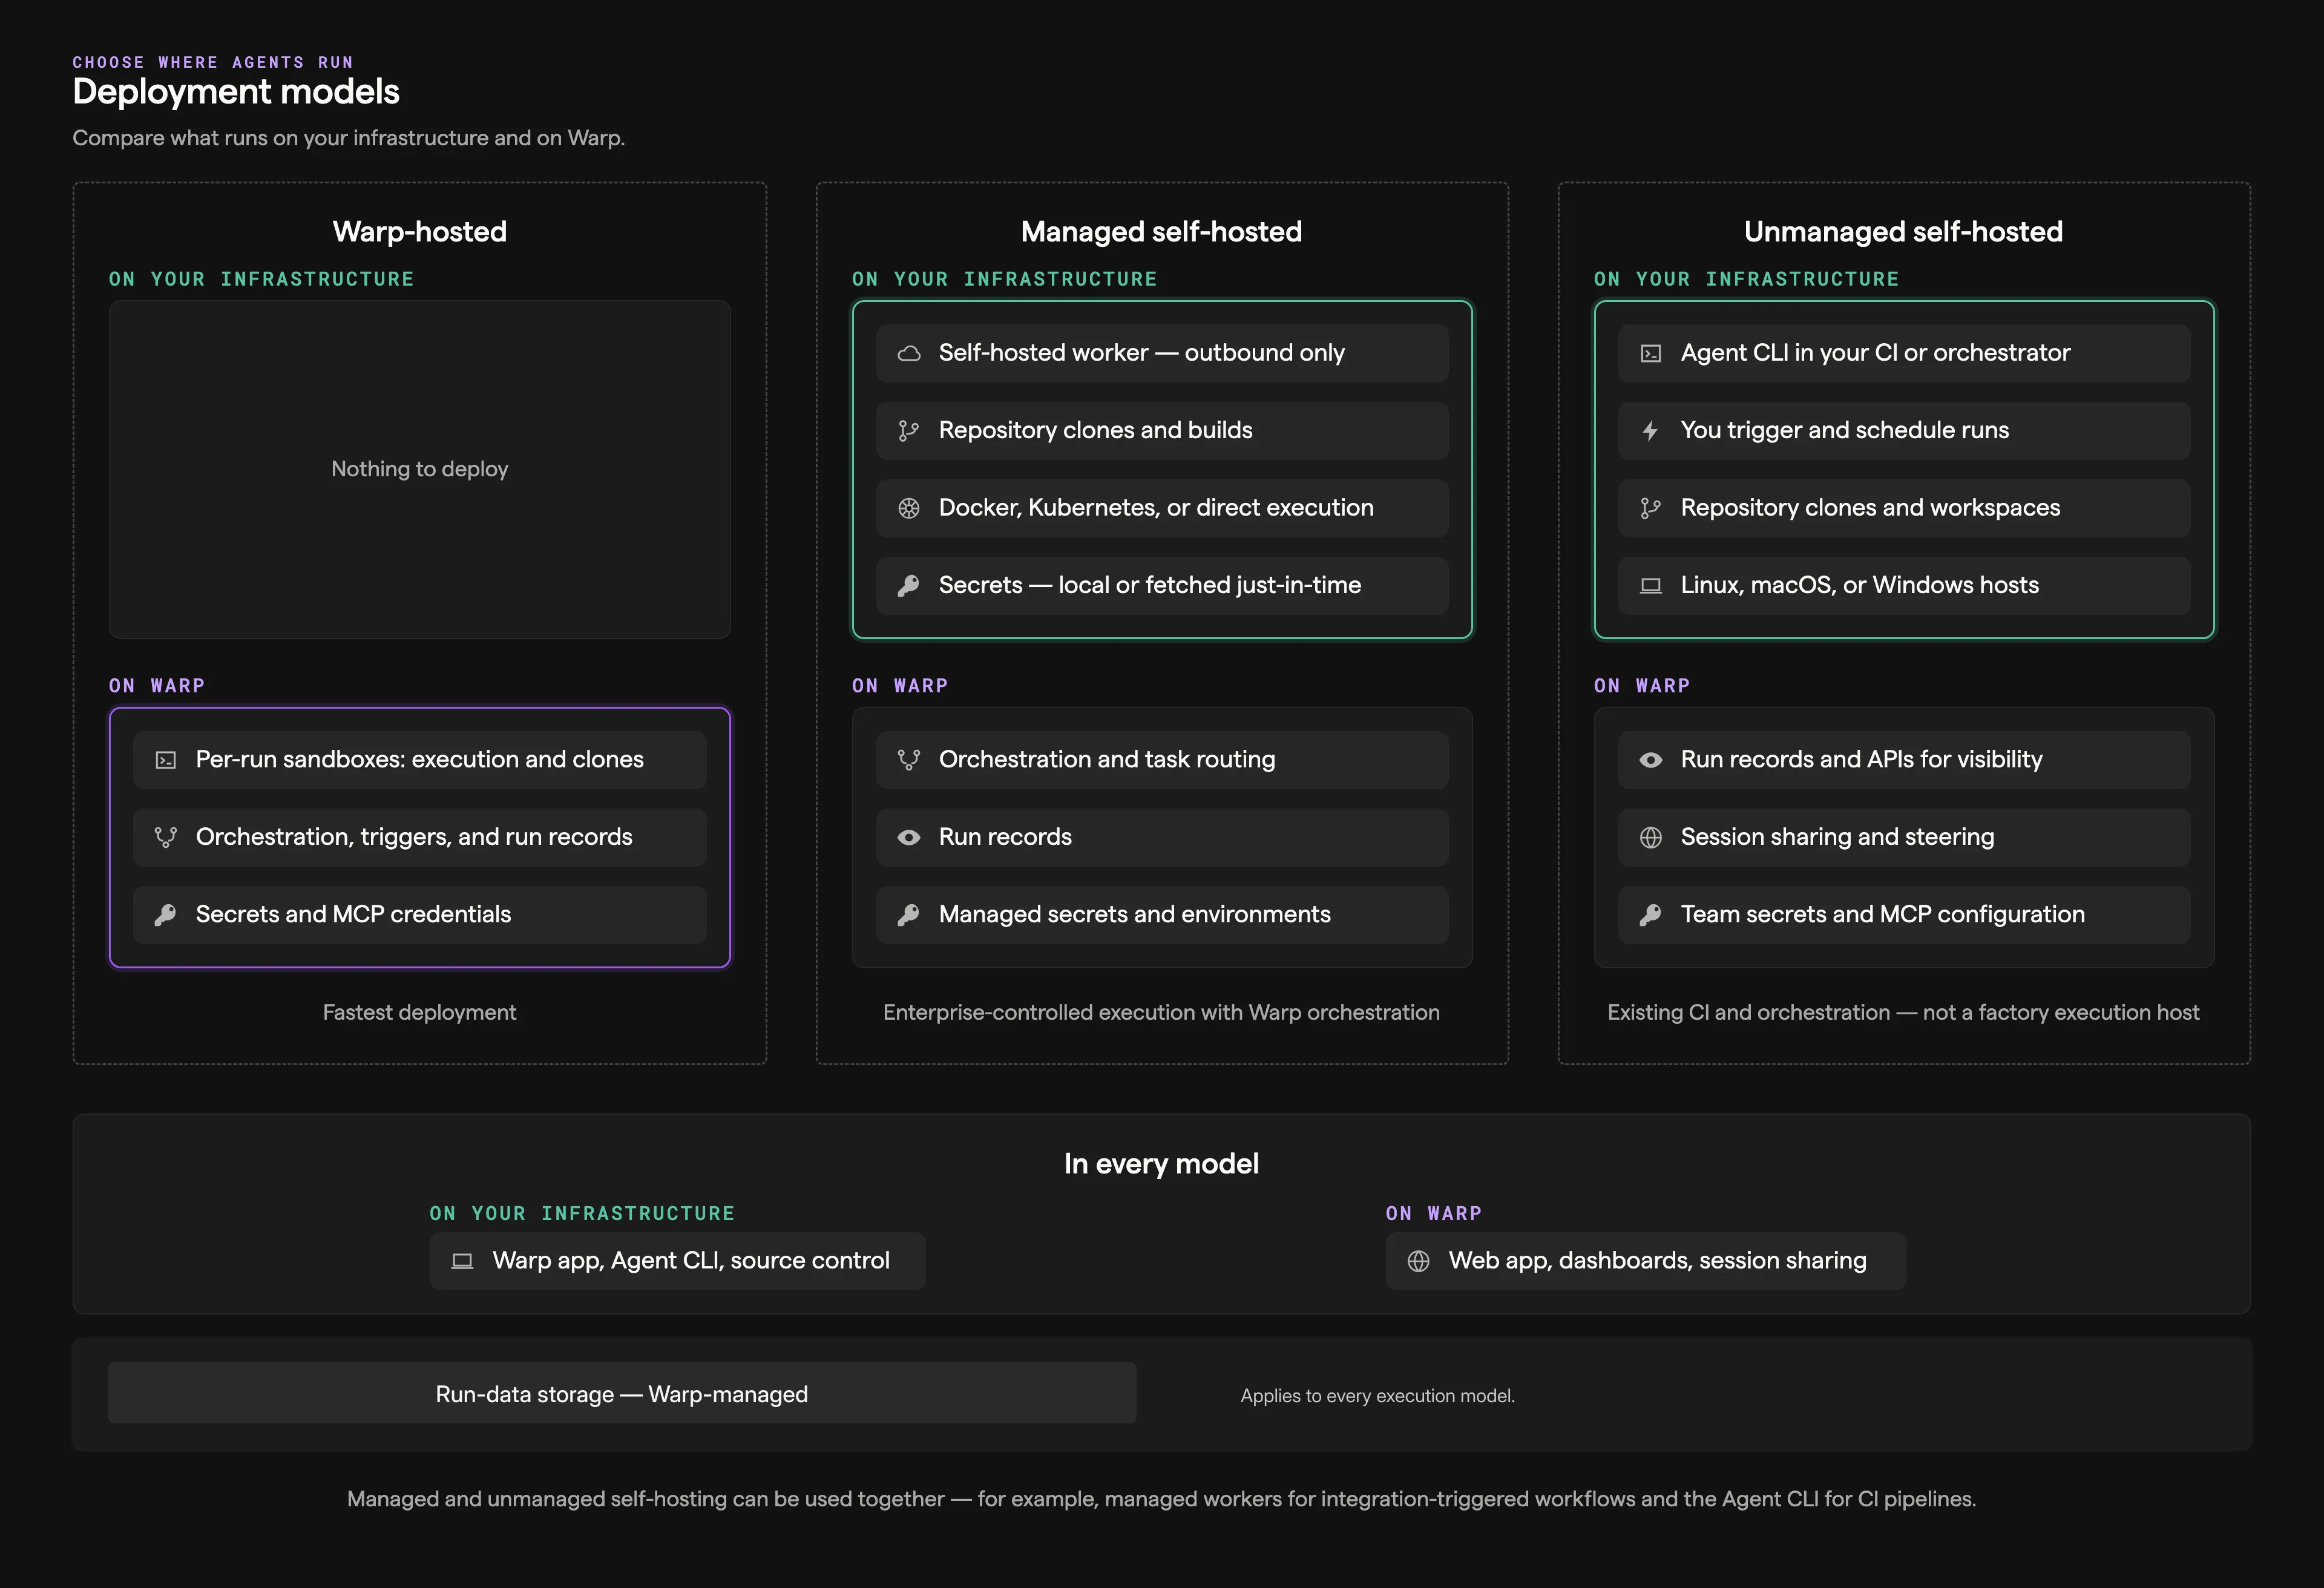
**Warp-hosted** is right if:
* You want zero infrastructure management for agent execution.
* Your security team is comfortable with SOC 2 Type II certified, ZDR-covered infrastructure.
* You need maximum parallelization and scalability.
**Self-hosted** is right if:
* Compliance requirements mandate that code stays within your network.
* You need to integrate with existing CI/CD or infrastructure tooling.
* You want full control over the execution environment.
**Hybrid** is right if:
* Different teams or repositories have different security requirements.
* You want the convenience of Warp-hosted for most work but need self-hosted for sensitive workloads.
## Related resources
[Section titled “Related resources”](#related-resources)
* [Architecture reference](/platform/architecture/) - Diagrams of the stack, the run lifecycle, self-hosted execution, and data boundaries
* [Deployment Patterns](/factories/deployment-patterns/) - Detailed patterns for CLI-only, Automation Platform-hosted, and self-hosted setups
* [Security overview](/enterprise/security-and-compliance/security-overview/) - Data handling, encryption, and compliance details
* [Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/) - Route inference through your own cloud infrastructure
* [Admin Panel](/enterprise/team-management/admin-panel/) - Configure agent policies and security settings
* [Contact sales](https://www.warp.dev/contact-sales) - Discuss deployment options for your organization
# Bring Your Own LLM
Canonical page: [/enterprise/enterprise-features/bring-your-own-llm/](https://docs.warp.dev/enterprise/enterprise-features/bring-your-own-llm/)
> BYOLLM routes Warp Agent inference through your AWS Bedrock or Google Cloud environment for billing control and data locality.
Warp supports **Bring Your Own LLM (BYOLLM)** for Enterprise teams that need to run inference on their own cloud infrastructure. With BYOLLM, your team keeps using Warp’s agents as usual, while eligible requests route through models hosted in your own cloud account instead of Warp’s direct provider integrations.
This gives you control over cloud spend, model hosting, and data locality, without changing how your team works in Warp. Admins configure BYOLLM centrally in the [Admin Panel](/enterprise/team-management/admin-panel/) — team members don’t need to change anything about how they use Warp (unless your admin asks them to opt in; see each provider’s page for details).
Note
BYOLLM is only available on Warp’s Enterprise plan. [Contact sales](https://www.warp.dev/contact-sales) to learn more.
## Supported providers
[Section titled “Supported providers”](#supported-providers)
BYOLLM supports two cloud providers today, each with its own dedicated setup guide:
* **[BYOLLM: AWS Bedrock](/enterprise/enterprise-features/byollm-aws-bedrock/)** - Route inference through Claude models hosted in your AWS account. Interactive requests use each member’s AWS CLI session credentials, and cloud agent runs assume an IAM role via OIDC.
* **[BYOLLM: Gemini Enterprise (Vertex AI)](/enterprise/enterprise-features/byollm-gemini-enterprise/)** - Route inference through Gemini and Claude partner models hosted in your Google Cloud project, using short-lived Workload Identity Federation (WIF) credentials rooted in the member’s Warp session.
Caution
Azure Foundry support is coming soon.
Use the comparison below to pick a provider, then follow its setup guide for configuration steps.
| Aspect | AWS Bedrock | Gemini Enterprise (Vertex AI) |
| ----------------------- | -------------------------------------------------------------------------- | -------------------------------------------------------------------------------------- |
| Models | Claude (Anthropic) | Gemini (native) and Claude (Vertex AI partner models) |
| Credential mechanism | AWS CLI session (interactive); IAM role via OIDC (cloud agents) | Workload Identity Federation (WIF), rooted in the Warp session |
| Works with cloud agents | Yes | Not yet (planned) |
| Setup guide | [BYOLLM: AWS Bedrock](/enterprise/enterprise-features/byollm-aws-bedrock/) | [BYOLLM: Gemini Enterprise](/enterprise/enterprise-features/byollm-gemini-enterprise/) |
## Key features
[Section titled “Key features”](#key-features)
* **Cloud-native credentials** - No long-lived API keys stored by Warp. Each provider uses its own cloud-native identity mechanism — see the provider pages for details.
* **Admin-controlled routing and models** - Admins choose exactly which models route through your cloud account, with the option to disable direct provider access entirely.
* **Consolidated billing** - Inference costs are billed directly to your cloud account (AWS or Google Cloud), leveraging your existing cloud commitments.
## How BYOLLM works
[Section titled “How BYOLLM works”](#how-byollm-works)
When BYOLLM is enabled for a model, Warp redirects eligible inference calls to your configured cloud provider instead of using model providers’ direct APIs. The model runs in your cloud account, and the response streams back to the Warp client (or cloud agent worker, for providers that support it).
Each provider has its own request flow, credential lifecycle, and setup process. See [BYOLLM: AWS Bedrock](/enterprise/enterprise-features/byollm-aws-bedrock/#how-it-works) or [BYOLLM: Gemini Enterprise](/enterprise/enterprise-features/byollm-gemini-enterprise/#how-it-works) for the full details.
## Billing behavior
[Section titled “Billing behavior”](#billing-behavior)
BYOLLM-routed inference **consumes no credits** — Warp doesn’t charge credits for requests that execute in your cloud. Inference costs are billed directly to your cloud account. Local agent runs that use BYOLLM still consume [platform credits](/support-and-community/plans-and-billing/platform-credits/) for Warp’s platform infrastructure.
See each provider’s page for provider-specific routing and fallback behavior: [AWS Bedrock](/enterprise/enterprise-features/byollm-aws-bedrock/#routing-and-fallback-behavior) or [Gemini Enterprise](/enterprise/enterprise-features/byollm-gemini-enterprise/#routing-and-fallback-behavior).
## FAQ
[Section titled “FAQ”](#faq)
### How is BYOLLM different from BYOK?
[Section titled “How is BYOLLM different from BYOK?”](#how-is-byollm-different-from-byok)
**BYOK (Bring Your Own API Key)** lets individual users add their own API keys for direct model provider access (e.g., Anthropic, OpenAI, Google). Warp stores keys locally on the user’s device.
**BYOLLM (Bring Your Own LLM)** routes inference through your organization’s cloud infrastructure (AWS Bedrock or Google Cloud via Gemini Enterprise) using cloud-native IAM. Admins configure it at the admin level and it applies to the entire team.
Business and Enterprise admins can also centrally manage BYOK itself: [team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) let an admin configure shared provider keys and OpenAI-compatible endpoints that are stored server-side and work for both interactive requests and cloud agents. For a side-by-side comparison across all of Warp’s bring-your-own-infrastructure options, see [How team-managed providers differ from self-serve BYOK and BYOLLM](/enterprise/enterprise-features/team-managed-keys-and-endpoints/#how-team-managed-providers-differ-from-self-serve-byok-and-byollm).
| Feature | BYOK | BYOLLM |
| ------------------- | ----------------------- | --------------------------------------------------------------------- |
| Configuration level | User | Admin/Team |
| Authentication | API keys (local) | Cloud-native IAM (AWS) or Workload Identity Federation (Google Cloud) |
| Billing | Direct to provider | Your cloud account |
| Data locality | Provider infrastructure | Your cloud infrastructure |
### Does BYOLLM work with Auto?
[Section titled “Does BYOLLM work with Auto?”](#does-byollm-work-with-auto)
Auto model selection is disabled if an admin disables **any** Direct API model, regardless of BYOLLM configuration. When Direct API models remain enabled and BYOLLM is configured, Auto picks the best model for the task; if the selected model is enabled for your configured provider, the request routes through your cloud account.
### What data does Warp store? Do you store our cloud credentials?
[Section titled “What data does Warp store? Do you store our cloud credentials?”](#what-data-does-warp-store-do-you-store-our-cloud-credentials)
Warp **does not store or log** your cloud credentials for either provider. Credentials are used transiently, or minted as short-lived tokens, to authenticate requests and are never persisted on Warp’s servers. See the [AWS Bedrock](/enterprise/enterprise-features/byollm-aws-bedrock/#security-and-data-handling) or [Gemini Enterprise](/enterprise/enterprise-features/byollm-gemini-enterprise/#security-and-data-handling) security sections for provider-specific detail.
### Can admins enforce provider-only routing?
[Section titled “Can admins enforce provider-only routing?”](#can-admins-enforce-provider-only-routing)
Yes. Admins can disable Direct API access for models on the **Models** page so eligible requests only route through your cloud account. Note that disabling any Direct API model also disables Auto model selection.
## Related resources
[Section titled “Related resources”](#related-resources)
* [BYOLLM: AWS Bedrock](/enterprise/enterprise-features/byollm-aws-bedrock/) — Route inference through your AWS account
* [BYOLLM: Gemini Enterprise (Vertex AI)](/enterprise/enterprise-features/byollm-gemini-enterprise/) — Route inference through your Google Cloud project
* [Team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) — Admin-configured shared provider keys and custom endpoints
* [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) — Self-serve, user-level API keys
* [Model Choice](/agents/inference/model-choice/) — Full list of supported models
* [Admin Panel](/enterprise/team-management/admin-panel/) — Configure team settings
* [Contact sales](https://www.warp.dev/contact-sales) — Get help with Enterprise setup
# BYOLLM: AWS Bedrock
Canonical page: [/enterprise/enterprise-features/byollm-aws-bedrock/](https://docs.warp.dev/enterprise/enterprise-features/byollm-aws-bedrock/)
> Route Warp Agent inference through your AWS account with Bedrock BYOLLM, IAM credentials, and AWS-billed inference.
Warp’s **AWS Bedrock** BYOLLM integration routes agent inference through your own AWS account using **Amazon Bedrock**. Your team keeps using Warp’s agents as usual, while eligible requests execute against Claude models hosted in your AWS account, billed to your AWS account and governed by your IAM controls.
AWS Bedrock is one of the providers supported by [Bring Your Own LLM (BYOLLM)](/enterprise/enterprise-features/bring-your-own-llm/). For Google Cloud-based routing, see [BYOLLM: Gemini Enterprise](/enterprise/enterprise-features/byollm-gemini-enterprise/).
Note
BYOLLM is only available on Warp’s Enterprise plan. [Contact sales](https://www.warp.dev/contact-sales) to learn more.
## Key features
[Section titled “Key features”](#key-features)
* **Cloud-native credentials** - No long-lived API keys. Interactive terminal sessions use each user’s AWS CLI session credentials; cloud agent runs assume an IAM role in your AWS account via OIDC.
* **Admin-controlled IAM and model routing** - Admins define which IAM role(s) Warp can assume and which models are available via AWS Bedrock, with the ability to disable non-Bedrock model access entirely.
* **Consolidated billing** - Inference costs are billed directly to your AWS account, leveraging existing cloud commitments.
## How it works
[Section titled “How it works”](#how-it-works)
When BYOLLM is enabled, Warp redirects inference calls to your AWS Bedrock environment instead of using model providers’ direct APIs.
Here’s the high-level flow:
**Interactive terminal flow**
1. **Admin configures routing** - Your team admin sets routing policies in Warp’s admin settings (e.g., “Route Claude Opus 4.7 through AWS Bedrock; disable direct Anthropic API”).
2. **Team members authenticate** - Each team member authenticates to AWS locally using the AWS CLI (`aws login`).
3. **Warp routes requests** - When a team member uses an interactive agent in the terminal, Warp uses their short-lived session credentials to authenticate requests to your configured AWS Bedrock API endpoint.
4. **Inference executes in your cloud** - The model runs in your AWS account. Responses return to the Warp client.
**Cloud agent flow**
1. **Admin configures routing** - Your team admin configures BYOLLM in the Admin Panel and provides an IAM role ARN that Warp can assume. See [Enabling BYOLLM for cloud agents](#enabling-byollm-for-cloud-agents) for setup details.
2. **Warp assumes the role** - At run start, Warp mints an OIDC token and assumes the configured IAM role in your AWS account to obtain temporary credentials.
3. **Warp routes requests** - The cloud agent uses those temporary credentials to call your configured AWS Bedrock endpoint.
4. **Inference executes in your cloud** - The model runs in your AWS account. Responses return to the cloud agent worker.
### Credential lifecycle
[Section titled “Credential lifecycle”](#credential-lifecycle)
BYOLLM uses **cloud-native IAM authentication**, not long-lived API keys:
* **Automatic refresh** - Session tokens refresh automatically every \~15 minutes. Users can enable auto-refresh by opening **Settings** and searching for `AWS Bedrock`, or when prompted during first credential expiration. With auto-refresh enabled, sessions can run uninterrupted for up to 12 hours (depending on your AWS admin configuration).
* **Per-user credentials** - Credentials are not shared across the organization. Your cloud provider’s default credential provider chain (e.g., AWS CLI) provisions and refreshes them locally.
* **No storage or logging** - Warp never stores or logs your cloud session tokens on its servers.
This approach ensures access management stays with your cloud provider, giving admins member-by-member control.
### Model availability
[Section titled “Model availability”](#model-availability)
BYOLLM supports the intersection of models that Warp supports and models available on your provider. On AWS Bedrock, only **Claude models** (Anthropic) are available; OpenAI and Google models are not available on Bedrock. To route Gemini models (or Claude partner models on Vertex AI) through your Google Cloud project, use [Gemini Enterprise BYOLLM](/enterprise/enterprise-features/byollm-gemini-enterprise/) instead.
To determine which models you can use with BYOLLM:
* [Model Choice](/agents/inference/model-choice/) - Full list of Warp-supported models.
* [Supported models in Amazon Bedrock](https://docs.aws.amazon.com/bedrock/latest/userguide/model-cards.html) - AWS Bedrock model availability.
A model must appear on both lists to be available through BYOLLM.
## Enabling BYOLLM
[Section titled “Enabling BYOLLM”](#enabling-byollm)
### Prerequisites
[Section titled “Prerequisites”](#prerequisites)
Before configuring BYOLLM, confirm the following:
* Your organization has the desired models enabled in AWS Bedrock.
* You have admin access to both Warp’s [Admin Panel](/enterprise/team-management/admin-panel/) and your AWS IAM settings.
* Team members have the AWS CLI installed locally.
### 1. Configure routing policies (admin)
[Section titled “1. Configure routing policies (admin)”](#1-configure-routing-policies-admin)
In the [Admin Panel](/enterprise/team-management/admin-panel/), configure which models should route through AWS Bedrock:
1. From the [Admin Panel](/enterprise/team-management/admin-panel/), navigate to the **Models** page.
2. Select which models should use your cloud provider (e.g., “Claude Opus 4.7 via AWS Bedrock”).
3. Optionally, disable direct API access to enforce provider-only routing.
### 2. Provision IAM roles (cloud admin)
[Section titled “2. Provision IAM roles (cloud admin)”](#2-provision-iam-roles-cloud-admin)
Grant your team members the necessary permissions in AWS. Use least-privilege IAM policies.
**Example: AWS Bedrock minimum IAM policy**
```json
{
"Version": "2012-10-17",
"Statement": [
{
"Sid": "BedrockModelAccess",
"Effect": "Allow",
"Action": [
"bedrock:InvokeModel",
"bedrock:InvokeModelWithResponseStream"
],
"Resource": [
"arn:aws:bedrock:*::foundation-model/*",
"arn:aws:bedrock:*:*:inference-profile/*",
"arn:aws:bedrock:*:*:application-inference-profile/*"
]
}
]
}
```
Note
This policy covers Warp’s current usage. By default, Warp uses [global inference profiles](https://docs.aws.amazon.com/bedrock/latest/userguide/cross-region-inference.html) for models when available. Admins can override the inference profile per model on the **Models** page of the [Admin Panel](/enterprise/team-management/admin-panel/).
### 3. Authenticate locally (team member)
[Section titled “3. Authenticate locally (team member)”](#3-authenticate-locally-team-member)
Each team member authenticates to AWS using the AWS CLI:
```bash
aws login
```
Confirm your AWS environment and region are correctly configured before using Warp.
### 4. Validate
[Section titled “4. Validate”](#4-validate)
Run a test prompt in Warp using a model configured for BYOLLM routing. Verify:
* The request completes successfully.
* Logs appear in AWS CloudWatch.
## Enabling BYOLLM for cloud agents
[Section titled “Enabling BYOLLM for cloud agents”](#enabling-byollm-for-cloud-agents)
Cloud agents authenticate to AWS Bedrock differently from the local terminal flow above. Instead of relying on each user’s AWS CLI session, Warp assumes an IAM role you provision in your AWS account using OIDC identity federation.
### Prerequisites
[Section titled “Prerequisites”](#prerequisites-1)
Before configuring BYOLLM for cloud agents, confirm the following:
* You have admin access to both Warp’s [Admin Panel](/enterprise/team-management/admin-panel/) and your AWS IAM settings.
### 1. Set up Warp as an OIDC identity provider in AWS (cloud admin)
[Section titled “1. Set up Warp as an OIDC identity provider in AWS (cloud admin)”](#1-set-up-warp-as-an-oidc-identity-provider-in-aws-cloud-admin)
Before AWS can trust tokens issued by Warp, register Warp as an OpenID Connect (OIDC) identity provider in IAM. This is a one-time setup per AWS account.
1. Open the [Identity providers](https://console.aws.amazon.com/iam/home#/identity_providers) page in the AWS IAM console.
2. Click **Add provider**.
3. For **Provider type**, choose **OpenID Connect**.
4. For **Provider URL**, enter `https://app.warp.dev`.
5. For **Audience**, enter `sts.amazonaws.com`.
6. Click **Add provider**.
After the provider is created, copy its ARN — it will look like `arn:aws:iam::<aws-account-id>:oidc-provider/app.warp.dev`. You’ll reference this ARN in the trust policy in the next step.
For more detail, see AWS’s [Create an OpenID Connect (OIDC) identity provider in IAM](https://docs.aws.amazon.com/IAM/latest/UserGuide/id_roles_providers_create_oidc.html) guide.
### 2. Provision an assumable IAM role (cloud admin)
[Section titled “2. Provision an assumable IAM role (cloud admin)”](#2-provision-an-assumable-iam-role-cloud-admin)
Create an IAM role that Warp can assume via OIDC, then attach the minimum Bedrock permissions policy. Use least-privilege IAM policies.
The role setup has two parts:
1. A **trust policy** that allows Warp’s OIDC identity to call `sts:AssumeRoleWithWebIdentity`.
2. A **permissions policy** that grants the minimum Bedrock inference permissions.
#### Trust policy requirements
[Section titled “Trust policy requirements”](#trust-policy-requirements)
This trust policy authorizes any cloud-hosted run from your team. The `sub` claim Warp signs has the shape `scoped_principal:<team-uid>/<actor-type>:<principal-uid>`, where `<actor-type>` is `user` for user-triggered runs or `service_account` for [cloud agent](/platform/agents/) runs. The `<team-uid>/*` pattern below covers both.
**Example trust policy**
```json
{
"Version": "2012-10-17",
"Statement": [
{
"Effect": "Allow",
"Principal": {
"Federated": "arn:aws:iam::<aws-account-id>:oidc-provider/app.warp.dev"
},
"Action": "sts:AssumeRoleWithWebIdentity",
"Condition": {
"StringLike": {
"app.warp.dev:sub": "scoped_principal:<team-uid>/*"
},
"StringEquals": {
"app.warp.dev:aud": "sts.amazonaws.com"
}
}
}
]
}
```
Replace the account ID, issuer host, and team UID with values for your environment.
The `<team-uid>` is the Warp team UID for the team that will be allowed to assume this role. You can find it in your team’s [Admin Panel](/enterprise/team-management/admin-panel/) URL as the path segment after `/admin/`. For example, in `https://app.warp.dev/admin/HzjUdNkg8Uiq8gp6FMgfxe/models`, the team UID is `HzjUdNkg8Uiq8gp6FMgfxe`.
#### Permissions policy
[Section titled “Permissions policy”](#permissions-policy)
Attach the minimum Bedrock invoke permissions policy to the role:
```json
{
"Version": "2012-10-17",
"Statement": [
{
"Sid": "BedrockModelAccess",
"Effect": "Allow",
"Action": [
"bedrock:InvokeModel",
"bedrock:InvokeModelWithResponseStream"
],
"Resource": [
"arn:aws:bedrock:*::foundation-model/*",
"arn:aws:bedrock:*:*:inference-profile/*",
"arn:aws:bedrock:*:*:application-inference-profile/*"
]
}
]
}
```
Note
This policy covers Warp’s current usage. By default, Warp uses [global inference profiles](https://docs.aws.amazon.com/bedrock/latest/userguide/cross-region-inference.html) for models when available. Admins can override the inference profile per model on the **Models** page of the [Admin Panel](/enterprise/team-management/admin-panel/).
After you create the role, copy its ARN. You’ll paste it into the **Models** page in the next step.
### 3. Configure routing policies (admin)
[Section titled “3. Configure routing policies (admin)”](#3-configure-routing-policies-admin)
Attach the IAM role from Step 2 to your team or to a specific named agent.
#### Option A: Team-wide
[Section titled “Option A: Team-wide”](#option-a-team-wide)
This applies the OIDC role to all cloud agent runs on the team.
1. In the [Admin Panel](/enterprise/team-management/admin-panel/), navigate to the **Models** page.
2. Under the **AWS Bedrock** host configuration, paste the IAM role ARN from Step 2 into the **Role ARN** field.
3. Select which models should route through AWS Bedrock.
#### Option B: Per named agent
[Section titled “Option B: Per named agent”](#option-b-per-named-agent)
This applies the OIDC role only to runs from a specific named agent.
Note
To safely test BYOLLM, configure it on a single named agent first. Misconfigurations scoped to one agent only affect that agent’s runs, not the whole team.
In the Oz web app:
1. [Create a new agent](/platform/oz-web-app/#creating-a-new-agent) or edit an existing one.
2. In the agent form, expand the **AWS Bedrock** section.
3. Choose **Custom** and paste the IAM role ARN from Step 2.
4. Ensure the agent’s default model is one that’s enabled for Bedrock under the Admin Panel **Models** page.
New runs for this agent will authenticate to Bedrock using the configured role.
### 4. Validate the configuration
[Section titled “4. Validate the configuration”](#4-validate-the-configuration)
Start a test cloud agent run using a model configured for BYOLLM routing. Verify:
* The request completes successfully.
* Logs appear in AWS CloudWatch.
## Routing and fallback behavior
[Section titled “Routing and fallback behavior”](#routing-and-fallback-behavior)
### Routing behavior
[Section titled “Routing behavior”](#routing-behavior)
Warp’s agents automatically select the best model for your task while respecting your admin’s routing policies. If you configure a model for BYOLLM, requests for that model route to AWS Bedrock.
### Failover behavior
[Section titled “Failover behavior”](#failover-behavior)
If a BYOLLM request fails (e.g., due to role assumption errors, insufficient permissions, or provider quota limits), Warp attempts to fall back to the next available model your admin has enabled.
For example, if Claude Opus 4.7 on Bedrock fails but your admin also enabled it via direct API, Warp falls back to the direct API to avoid disruption. If a fallback uses a direct API model, that request consumes Warp credits.
If no fallback is available (e.g., the admin disabled all non-Bedrock models), Warp displays a clear error message.
### Auto model selection
[Section titled “Auto model selection”](#auto-model-selection)
Auto model selection is disabled if an admin disables **any** Direct API model, regardless of AWS Bedrock configuration.
When Direct API models remain enabled and BYOLLM is configured, Auto picks the best model for the task. If the selected model is also enabled for AWS Bedrock, the request routes through Bedrock; otherwise it routes through the Direct API.
## Billing behavior
[Section titled “Billing behavior”](#billing-behavior)
When a request routes through BYOLLM:
* **Warp doesn’t consume credits** for that request.
* Cloud agent runs still consume platform and compute credits for orchestration and the cloud agent’s compute.
See [The three credit buckets](/support-and-community/plans-and-billing/platform-credits/#the-three-credit-buckets) for more on credit types.
## Security and data handling
[Section titled “Security and data handling”](#security-and-data-handling)
### Credential security
[Section titled “Credential security”](#credential-security)
* **No long-lived API keys** — BYOLLM uses cloud-native IAM with short-lived session tokens.
* **Per-user authentication** — Each team member authenticates individually; credentials are not shared.
* **No storage or logging** — Warp never stores or logs your cloud session tokens on its servers.
### Zero Data Retention (ZDR)
[Section titled “Zero Data Retention (ZDR)”](#zero-data-retention-zdr)
Warp maintains **SOC 2 compliance** and has **Zero Data Retention (ZDR)** agreements with its contracted LLM providers.
However, when using BYOLLM:
* **Your** cloud account settings determine data retention policies.
* Warp cannot enforce ZDR for requests routed through your infrastructure.
* If your cloud account does not have ZDR enabled, your provider may retain data according to their terms.
### Auditability
[Section titled “Auditability”](#auditability)
* Warp keeps all runs fully steerable and logged within Warp.
* Your cloud account retains provider-side logs (usage, latency, errors).
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### Common errors
[Section titled “Common errors”](#common-errors)
* **Missing or expired local credentials** (interactive terminal use) — Re-authenticate using `aws login`. To avoid interruptions, enable auto-refresh by opening **Settings** and searching for `AWS Bedrock`, or when prompted during credential expiration.
* **Role assumption failed** (cloud agent runs) — Verify the IAM trust policy, issuer host, team UID restriction, and the configured role ARN in Warp.
* **Missing OIDC provider** (cloud agent runs) — Confirm the OIDC provider exists in your AWS account for the issuer host referenced in the trust policy.
* **Insufficient permissions** — Verify your IAM policy includes the required Bedrock actions and any needed resources.
* **Region or model mismatch** — Confirm the model is enabled in your AWS region and that your environment is configured for the correct region.
* **Provider quota limits** — Check your AWS Bedrock quota and request increases if needed.
### Debugging steps
[Section titled “Debugging steps”](#debugging-steps)
1. Confirm the configured role ARN is the one you intended Warp to assume.
2. Check the IAM trust policy and verify the issuer host, `sub`, and `aud` conditions match your Warp configuration.
3. Check the attached IAM policy for the required Bedrock permissions.
4. Confirm the model ID and region match your Warp configuration.
5. Inspect AWS CloudWatch logs for request details and errors.
## FAQ
[Section titled “FAQ”](#faq)
### How is BYOLLM different from BYOK?
[Section titled “How is BYOLLM different from BYOK?”](#how-is-byollm-different-from-byok)
**BYOK (Bring Your Own API Key)** lets individual users add their own API keys for direct model provider access (e.g., Anthropic, OpenAI, Google). Warp stores keys locally on the user’s device.
**BYOLLM (Bring Your Own LLM)** routes inference through your organization’s cloud infrastructure (AWS Bedrock or Google Cloud via Gemini Enterprise) using cloud-native IAM. Admins configure it at the admin level and it applies to the entire team.
Business and Enterprise admins can also centrally manage BYOK itself: [team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) let an admin configure shared provider keys and OpenAI-compatible endpoints that are stored server-side and work for both interactive requests and cloud agents. The table below compares BYOLLM with the self-serve, user-level form of BYOK. For a side-by-side comparison that also includes team-managed keys and endpoints, see [How team-managed providers differ from self-serve BYOK and BYOLLM](/enterprise/enterprise-features/team-managed-keys-and-endpoints/#how-team-managed-providers-differ-from-self-serve-byok-and-byollm).
| Feature | BYOK | BYOLLM |
| ------------------- | ----------------------- | --------------------------------- |
| Configuration level | User | Admin/Team |
| Authentication | API keys (local) | IAM role assumed by Warp via OIDC |
| Billing | Direct to provider | Your cloud account |
| Data locality | Provider infrastructure | Your cloud infrastructure |
### What data does Warp store? Do you store our cloud credentials?
[Section titled “What data does Warp store? Do you store our cloud credentials?”](#what-data-does-warp-store-do-you-store-our-cloud-credentials)
Warp **does not store or log** your cloud credentials.
* **Interactive terminal use** — Credentials are used transiently to sign requests and are never persisted on Warp servers.
* **Cloud agent runs** — Temporary AWS credentials are used only for the duration of the run and are not retained after it ends.
### Can admins enforce provider-only routing and disable Warp-managed models?
[Section titled “Can admins enforce provider-only routing and disable Warp-managed models?”](#can-admins-enforce-provider-only-routing-and-disable-warp-managed-models)
Yes. Admins can configure routing policies to require specific models to use BYOLLM and disable direct API access to Warp-managed model endpoints.
## Related resources
[Section titled “Related resources”](#related-resources)
* [Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/) — BYOLLM overview and provider comparison
* [BYOLLM: Gemini Enterprise (Vertex AI)](/enterprise/enterprise-features/byollm-gemini-enterprise/) — Route inference through your Google Cloud project
* [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/)
* [Team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) — Business and Enterprise admins configure shared provider keys and custom endpoints for the team
* [Model Choice](/agents/inference/model-choice/) — Full list of supported models
* [Admin Panel](/enterprise/team-management/admin-panel/) — Configure team settings
* [Contact Sales](https://www.warp.dev/contact-sales) — Get help with enterprise setup
# BYOLLM: Gemini Enterprise (Vertex AI)
Canonical page: [/enterprise/enterprise-features/byollm-gemini-enterprise/](https://docs.warp.dev/enterprise/enterprise-features/byollm-gemini-enterprise/)
> Route Warp Agent inference through your Google Cloud project with Gemini Enterprise BYOLLM and short-lived WIF credentials.
Warp’s **Gemini Enterprise** BYOLLM integration routes agent inference through your own Google Cloud project using **Vertex AI** (the Gemini Enterprise Agent Platform). Your team keeps using Warp’s agents as usual, while eligible requests execute against models hosted in your GCP project, billed to your Google Cloud account and governed by your IAM controls.
Gemini Enterprise is one of the providers supported by [Bring Your Own LLM (BYOLLM)](/enterprise/enterprise-features/bring-your-own-llm/). For AWS-based routing, see the [AWS Bedrock BYOLLM setup](/enterprise/enterprise-features/byollm-aws-bedrock/).
Note
Gemini Enterprise BYOLLM is only available on Warp’s Enterprise plan. [Contact sales](https://www.warp.dev/contact-sales) to learn more.
Caution
Gemini Enterprise BYOLLM currently applies to **interactive agent requests** in the Warp app. [Cloud agent](/platform/) runs don’t route through Gemini Enterprise yet; cloud agent support is available today with [AWS Bedrock BYOLLM](/enterprise/enterprise-features/byollm-aws-bedrock/#enabling-byollm-for-cloud-agents).
## Key features
[Section titled “Key features”](#key-features)
* **Session-based federated authentication** - Warp uses the member’s signed-in Warp session to issue a short-lived OIDC identity token, then exchanges it through Google Workload Identity Federation for temporary Google Cloud credentials.
* **Admin-controlled routing and models** - Admins configure the GCP project, Vertex location, and WIF provider once in the Admin Panel, then choose exactly which models are enabled and which Vertex model references they resolve to.
* **Gemini and Claude models** - Route native Gemini models and Claude partner models available on Vertex AI through your project.
* **Consolidated billing and quota attribution** - Inference runs against your project’s Vertex AI quota and is billed to your Google Cloud account. Requests carry your project for quota attribution (`X-Goog-User-Project`).
* **No long-lived credentials** - Warp never stores service account keys, refresh tokens, or credential files. The client keeps only a short-lived Google Cloud access token in memory and automatically replaces it as it approaches expiration.
## How it works
[Section titled “How it works”](#how-it-works)
When Gemini Enterprise is enabled, Warp redirects eligible inference calls to Vertex AI in your Google Cloud project instead of using model providers’ direct APIs.
Here’s the high-level flow:
1. **Admin configures routing** - Your team admin enables the Gemini Enterprise host on the **Models** page of the [Admin Panel](/enterprise/team-management/admin-panel/) and sets the GCP project, Vertex location, and WIF provider audience string.
2. **Members enable credentials** - Each signed-in member turns on **Use Gemini Enterprise credentials** in Warp’s Settings (or the admin enforces it team-wide).
3. **Warp mints a short-lived token** - The Warp client exchanges a Warp-signed identity token for a short-lived Google Cloud access token via Google’s Security Token Service (STS), optionally impersonating a service account you designate.
4. **Warp routes requests** - Eligible agent requests carry that access token, and Warp’s backend uses it to call Vertex AI in your project with the configured location and model reference.
5. **Inference executes in your cloud** - The model runs in your GCP project. Responses stream back to the Warp client.
### Credential lifecycle
[Section titled “Credential lifecycle”](#credential-lifecycle)
Gemini Enterprise uses **federated, short-lived credentials** instead of API keys or local cloud CLI sessions:
* **Rooted in the Warp session** - Each mint starts from the member’s signed-in Warp session. Warp issues a signed OpenID Connect (OIDC) token, exchanges it at Google STS for a federated access token, and, if configured, impersonates your designated service account.
* **Automatic refresh** - Tokens are held in memory and refreshed automatically about five minutes before they expire. Members don’t need to re-authenticate during normal use.
* **Strict binding** - A minted token is only attached to requests while the signed-in user and the admin’s WIF configuration still match. Signing out, switching accounts, or admin configuration changes invalidate it.
* **No storage or logging** - The client never uploads refresh tokens, credential JSON, or service account keys, and Warp’s servers never persist or log the access token.
### Model availability
[Section titled “Model availability”](#model-availability)
Gemini Enterprise supports the intersection of models that Warp supports and models available through Vertex AI in your project:
* **Native Gemini models** - Current Gemini Flash, Flash Lite, and Pro families (for example, Gemini 3.1 Pro and Gemini 3.7 Flash).
* **Claude partner models on Vertex AI** - Current Claude Sonnet, Opus, Haiku, and Fable families offered as Vertex AI partner models.
To determine which models you can use, see [Model Choice](/agents/inference/model-choice/) for Warp’s supported models and the **Models** page of the Admin Panel for your team’s Gemini Enterprise enablement.
## Enabling Gemini Enterprise
[Section titled “Enabling Gemini Enterprise”](#enabling-gemini-enterprise)
Setting up Gemini Enterprise has two parts:
1. **In Google Cloud** - Trust identities issued by Warp, then grant them permission to call Vertex AI.
2. **In Warp** - Point the Admin Panel at your project and choose which models route through it.
Access is granted through **Workload Identity Federation**, so no long-lived service account key is ever created or shared with Warp. Step 2 covers two ways to grant that access: directly to your federated Warp identities, or through a service account you designate.
Note
The Google Cloud steps use the Google Cloud console. If you prefer the command line, see [Alternative: configure Google Cloud with the gcloud CLI](#alternative-configure-google-cloud-with-the-gcloud-cli).
### Prerequisites
[Section titled “Prerequisites”](#prerequisites)
Before configuring Gemini Enterprise, confirm the following:
* You have a Google Cloud project that will own inference, quota, and billing.
* The Vertex AI API (`aiplatform.googleapis.com`) is enabled in that project.
* The models you plan to route are available to the project. Claude partner models must be enabled in the Vertex AI Model Garden.
* You can create Workload Identity Federation pools and providers and modify the project’s IAM policy. To use service account impersonation in Step 2, you also need permission to create service accounts.
* You have administrator access to Warp’s [Admin Panel](/enterprise/team-management/admin-panel/).
### Values you’ll need
[Section titled “Values you’ll need”](#values-youll-need)
Collect these values before you start. You’ll reuse them across Google Cloud and Warp.
* **`PROJECT_ID`** - Your Google Cloud project’s alphanumeric identifier, such as `my-gcp-project`.
* **`PROJECT_NUMBER`** - Your Google Cloud project’s numeric identifier, such as `123456789012`. Both identifiers appear on the **Welcome** page of the Google Cloud console.
* **`TEAM_UID`** - Your Warp team UID, which is the path segment immediately after `/admin/` in your Admin Panel URL. In `https://app.warp.dev/admin/HzjUdNkg8Uiq8gp6FMgfxe/models`, the team UID is `HzjUdNkg8Uiq8gp6FMgfxe`.
* **`POOL_ID`** and **`PROVIDER_ID`** - Names you choose for the workload identity pool and provider you create in Step 1, such as `warp-byollm` and `warp`.
### 1. Create a workload identity pool and provider (cloud admin)
[Section titled “1. Create a workload identity pool and provider (cloud admin)”](#1-create-a-workload-identity-pool-and-provider-cloud-admin)
Before Google Cloud accepts identity tokens issued by Warp, register Warp as an OIDC identity provider in a workload identity pool.
A workload identity pool provides a namespace for external identities. The provider inside that pool tells Google Cloud how to validate and interpret the OIDC tokens Warp issues.
Warp-issued OIDC tokens carry these claims:
* **`sub`** - Identifies the Warp actor, shaped as `scoped_principal:TEAM_UID/ACTOR_TYPE:PRINCIPAL_UID`. For interactive requests, `ACTOR_TYPE` is `user`.
* **`teams`** - Lists the Warp team UIDs the actor belongs to. Mapping this claim to `google.groups` lets you grant a role to an entire Warp team with a single IAM binding.
#### Create the pool
[Section titled “Create the pool”](#create-the-pool)
1. In the Google Cloud console, go to **IAM & Admin** > **Workload Identity Federation**.
2. Click **Create pool**.
3. For **Name**, enter your `POOL_ID` value, then click **Continue**.
If your organization already has a suitable pool, skip this step and create the Warp provider inside the existing pool instead.
#### Create the provider
[Section titled “Create the provider”](#create-the-provider)
Continue in the **Add a provider to pool** step:
1. For **Select a provider**, choose **OpenID Connect (OIDC)**.
2. For **Provider name**, enter your `PROVIDER_ID` value.
3. For **Issuer (URL)**, enter `https://app.warp.dev`.
4. Leave **Audience** set to **Default audience**, then click **Continue**.
The default audience requires Warp’s OIDC token to name this provider in its `aud` claim, which takes this canonical form:
```text
https://iam.googleapis.com/projects/PROJECT_NUMBER/locations/global/workloadIdentityPools/POOL_ID/providers/PROVIDER_ID
```
You’ll enter a variation of this value in Warp in Step 3.
#### Configure attribute mappings
[Section titled “Configure attribute mappings”](#configure-attribute-mappings)
In **Configure provider attributes**, add both mappings exactly as shown:
| Google attribute | OIDC expression |
| ---------------- | ----------------- |
| `google.subject` | `assertion.sub` |
| `google.groups` | `assertion.teams` |
#### Restrict the provider to your Warp team
[Section titled “Restrict the provider to your Warp team”](#restrict-the-provider-to-your-warp-team)
Turn on **Attribute conditions** and enter the following expression, replacing `TEAM_UID` with your Warp team UID:
```text
"TEAM_UID" in assertion.teams
```
This rejects any Warp-issued token that doesn’t belong to your team. Click **Save**.
The provider now appears in the pool and is ready to exchange tokens.
### 2. Grant Vertex AI access to your Warp team (cloud admin)
[Section titled “2. Grant Vertex AI access to your Warp team (cloud admin)”](#2-grant-vertex-ai-access-to-your-warp-team-cloud-admin)
The provider you created controls which Warp tokens Google Cloud accepts. Now grant permissions to the identities those tokens represent. Choose one of the following approaches:
* **Option A (Recommended): Direct federated access** - Grants roles straight to your federated Warp identities.
* **Option B: Service account impersonation** - Routes access through a dedicated service account.
Neither option creates a long-lived service account key, and Warp never receives one.
#### Option A: Direct federated access (recommended)
[Section titled “Option A: Direct federated access (recommended)”](#option-a-direct-federated-access-recommended)
1. In the Google Cloud console, go to **IAM & Admin** > **IAM**, then click **Grant access**.
2. For **New principals**, enter your team’s principal set, substituting your own values:
```text
principalSet://iam.googleapis.com/projects/PROJECT_NUMBER/locations/global/workloadIdentityPools/POOL_ID/group/TEAM_UID
```
3. Assign both of the following roles, then click **Save**:
* **Vertex AI User** (`roles/aiplatform.user`) - Allows Vertex AI inference calls. For stricter least privilege, create a custom role that contains only `aiplatform.endpoints.predict` and assign that role instead.
* **Service Usage Consumer** (`roles/serviceusage.serviceUsageConsumer`) - Lets the federated identity draw quota and billing from your project.
The principal set now appears in the project’s IAM policy with both roles attached. Leave **Service account email** blank in Step 3.
#### Option B: Service account impersonation (optional)
[Section titled “Option B: Service account impersonation (optional)”](#option-b-service-account-impersonation-optional)
1. In the Google Cloud console, go to **IAM & Admin** > **Service Accounts**, then click **Create service account**.
2. Enter a name for the account, such as `warp-byollm-sa`, then click **Create and continue**.
3. Grant the service account the **Vertex AI User** (`roles/aiplatform.user`) and **Service Usage Consumer** (`roles/serviceusage.serviceUsageConsumer`) roles on your project, then click **Done**.
4. Select the service account, open the **Principals with access** tab, then click **Grant access**.
5. For **New principals**, enter your team’s principal set:
```text
principalSet://iam.googleapis.com/projects/PROJECT_NUMBER/locations/global/workloadIdentityPools/POOL_ID/group/TEAM_UID
```
6. Assign the **Workload Identity User** role (`roles/iam.workloadIdentityUser`), then click **Save**.
7. Go to **APIs & Services** > **Library**, search for **IAM Service Account Credentials API**, and click **Enable** so Warp can request impersonated tokens.
Copy the service account’s email address, such as `warp-byollm-sa@PROJECT_ID.iam.gserviceaccount.com`. You’ll enter it in Step 3.
Warp never receives the service account’s keys. Each request carries a short-lived impersonated token that the client mints at request time.
### 3. Configure routing in the Admin Panel (Warp admin)
[Section titled “3. Configure routing in the Admin Panel (Warp admin)”](#3-configure-routing-in-the-admin-panel-warp-admin)
Connect Warp to the Google Cloud configuration you just created:
1. In the [Admin Panel](https://app.warp.dev/admin/), go to the **Models** page.
2. Find the **Gemini Enterprise** host configuration and enable it.
3. For **GCP project ID**, enter your `PROJECT_ID` value.
4. For **Location**, choose the Vertex AI location that should serve requests.
5. For **WIF audience**, enter the provider resource name in this form:
```text
//iam.googleapis.com/projects/PROJECT_NUMBER/locations/global/workloadIdentityPools/POOL_ID/providers/PROVIDER_ID
```
6. For **Service account email**, leave the field blank if you chose Option A, or enter the service account’s email if you chose Option B.
7. Enable the models that should route through your project, then save.
Caution
The **WIF audience** must begin with `//iam.googleapis.com/`, not `https://`. Don’t include a trailing slash, surrounding quotation marks, or trailing whitespace.
The default location is `global`. Multi-region values (`global`, `us`, `eu`) and specific regions (for example, `us-central1`) are supported. The location applies host-wide to every Gemini Enterprise model.
You can also choose how member credentials behave:
* **Enforce** - Every signed-in member’s client uses Gemini Enterprise credentials automatically, and the member toggle is managed by the organization.
* **Respect user setting** - Each member opts in with the **Use Gemini Enterprise credentials** toggle in their Settings.
To enforce provider-only routing, disable **Direct API** access for the models you enabled.
### 4. Validate
[Section titled “4. Validate”](#4-validate)
Run a test prompt in Warp using a model enabled for Gemini Enterprise. Verify:
* The model shows the Gemini Enterprise badge in the model picker.
* The request completes successfully.
* The request appears in your project’s Vertex AI monitoring or Cloud Logging.
### Alternative: configure Google Cloud with the gcloud CLI
[Section titled “Alternative: configure Google Cloud with the gcloud CLI”](#alternative-configure-google-cloud-with-the-gcloud-cli)
If you prefer the command line, these commands replace Step 1 and Step 2, Option A. Step 3 in the Admin Panel is still required either way.
Set your values once so the commands below can reuse them:
```bash
export PROJECT_ID="my-gcp-project"
export PROJECT_NUMBER="123456789012"
export POOL_ID="warp-byollm"
export PROVIDER_ID="warp"
export TEAM_UID="HzjUdNkg8Uiq8gp6FMgfxe"
```
Enable the Vertex AI API:
```bash
gcloud services enable aiplatform.googleapis.com \
--project="${PROJECT_ID}"
```
Create the workload identity pool:
```bash
gcloud iam workload-identity-pools create "${POOL_ID}" \
--project="${PROJECT_ID}" \
--location="global" \
--display-name="Warp BYOLLM"
```
Create the OIDC provider:
```bash
gcloud iam workload-identity-pools providers create-oidc "${PROVIDER_ID}" \
--project="${PROJECT_ID}" \
--location="global" \
--workload-identity-pool="${POOL_ID}" \
--display-name="Warp" \
--issuer-uri="https://app.warp.dev" \
--attribute-mapping="google.subject=assertion.sub,google.groups=assertion.teams" \
--attribute-condition="'${TEAM_UID}' in assertion.teams"
```
Grant the Vertex AI role. For stricter least privilege, substitute a custom role that contains only `aiplatform.endpoints.predict`:
```bash
gcloud projects add-iam-policy-binding "${PROJECT_ID}" \
--member="principalSet://iam.googleapis.com/projects/${PROJECT_NUMBER}/locations/global/workloadIdentityPools/${POOL_ID}/group/${TEAM_UID}" \
--role="roles/aiplatform.user"
```
Grant the Service Usage Consumer role:
```bash
gcloud projects add-iam-policy-binding "${PROJECT_ID}" \
--member="principalSet://iam.googleapis.com/projects/${PROJECT_NUMBER}/locations/global/workloadIdentityPools/${POOL_ID}/group/${TEAM_UID}" \
--role="roles/serviceusage.serviceUsageConsumer"
```
Retrieve the provider resource name for the **WIF audience** field:
```bash
gcloud iam workload-identity-pools providers describe "${PROVIDER_ID}" \
--project="${PROJECT_ID}" \
--location="global" \
--workload-identity-pool="${POOL_ID}" \
--format="value(name)"
```
The command returns a value in this form:
```text
projects/PROJECT_NUMBER/locations/global/workloadIdentityPools/POOL_ID/providers/PROVIDER_ID
```
Prefix that value with `//iam.googleapis.com/` and enter the result as the **WIF audience** in Warp:
```text
//iam.googleapis.com/projects/PROJECT_NUMBER/locations/global/workloadIdentityPools/POOL_ID/providers/PROVIDER_ID
```
## Using Gemini Enterprise as a team member
[Section titled “Using Gemini Enterprise as a team member”](#using-gemini-enterprise-as-a-team-member)
Members need to be signed in to Warp; the credential flow is rooted in the Warp session, so Gemini Enterprise isn’t available to logged-out users.
1. In the Warp app, go to **Settings** > **Agents** > **Warp Agent** and scroll to the **Gemini Enterprise** section. The section appears once your admin has enabled the host.
2. Toggle **Use Gemini Enterprise credentials** on. If your admin enforces credentials team-wide, the toggle is already on and managed by your organization.
3. Check the credential status card. It shows the current state (for example, loaded with the next scheduled refresh, refreshing, setup incomplete, or a failure) and a **Refresh** button to force a new credential mint.
4. Pick an eligible model in the model picker. Models routed through your project show a Gemini Enterprise badge.
If the status card reports that setup is incomplete, your workspace’s Gemini Enterprise host is enabled but not fully configured; contact your team admin.
## Routing and fallback behavior
[Section titled “Routing and fallback behavior”](#routing-and-fallback-behavior)
### Host priority
[Section titled “Host priority”](#host-priority)
For each request, Warp expands the selected model into the hosts your admin has enabled and tries them in a fixed order:
1. AWS Bedrock
2. Gemini Enterprise
3. Direct API
The priority is fixed and not admin-configurable. A Gemini Enterprise route is only used when the request carries valid Gemini Enterprise credentials; otherwise Warp falls back to the next enabled host.
### Failover behavior
[Section titled “Failover behavior”](#failover-behavior)
If a Gemini Enterprise request fails (for example, due to IAM misconfiguration or Vertex AI quota limits), Warp attempts to fall back to the next available host your admin has enabled. If a fallback uses a Direct API model, that request consumes Warp credits. If no fallback is available, Warp displays a clear error message.
### Auto model selection
[Section titled “Auto model selection”](#auto-model-selection)
Auto model selection is disabled if an admin disables **any** Direct API model, regardless of Gemini Enterprise configuration. When Direct API models remain enabled, Auto picks the best model for the task; if the selected model is enabled for Gemini Enterprise and your credentials are active, the request routes through your project.
## Billing behavior
[Section titled “Billing behavior”](#billing-behavior)
When a request routes through Gemini Enterprise:
* **Warp doesn’t consume AI credits** for that request. Inference is billed by Google Cloud to your project.
* **Platform credits still apply** - On Business and Enterprise plans, local agent runs that use customer-supplied inference consume [platform credits](/support-and-community/plans-and-billing/platform-credits/) for Warp’s platform infrastructure.
* **Fallbacks are billed normally** - A request that falls back to a Direct API model consumes Warp credits at the standard rate.
See [The three credit buckets](/support-and-community/plans-and-billing/platform-credits/#the-three-credit-buckets) for more on credit types.
## Security and data handling
[Section titled “Security and data handling”](#security-and-data-handling)
### Credential security
[Section titled “Credential security”](#credential-security)
* **No long-lived credentials** - The only long-lived credential involved is the member’s Warp session. Access tokens are short-lived, held in memory, and never persisted.
* **Nothing sensitive leaves your boundary** - Warp stores only non-secret routing configuration (project ID, location, WIF audience, and optional service account email). Service account keys, refresh tokens, and credential files are never uploaded to Warp.
* **Per-user identity** - Every token is minted for the individual signed-in member, so access control and revocation stay in your identity stack: remove a member from your Warp team (or restrict the WIF provider’s attribute condition) and their tokens stop minting.
### Zero Data Retention (ZDR)
[Section titled “Zero Data Retention (ZDR)”](#zero-data-retention-zdr)
Warp maintains **SOC 2 compliance** and has **Zero Data Retention (ZDR)** agreements with its contracted LLM providers.
However, when using Gemini Enterprise:
* **Your** Google Cloud project settings determine data retention policies.
* Warp cannot enforce ZDR for requests routed through your infrastructure.
* Review Vertex AI’s data governance settings for your project to control retention.
### Auditability
[Section titled “Auditability”](#auditability)
* Warp keeps all conversations fully steerable and logged within Warp.
* Your GCP project retains provider-side logs (usage, latency, errors) in Vertex AI monitoring and Cloud Logging, attributed to your project.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### Common errors
[Section titled “Common errors”](#common-errors)
* **Credentials expired or invalid** - The request reached Vertex AI but was rejected as unauthenticated. Click **Refresh credentials** in the inline error, or use the **Refresh** button in **Settings** > **Agents** > **Warp Agent**, then retry.
* **Setup incomplete** - The host is enabled but the WIF audience is missing or blank. A team admin needs to complete the **Models** page configuration.
* **Token exchange or impersonation failed** - Verify the WIF provider’s issuer (`https://app.warp.dev`), both attribute mappings, and the attribute condition. Confirm your Warp team UID in the condition matches the one in your Admin Panel URL exactly. With service account impersonation, also confirm the principal set holds `roles/iam.workloadIdentityUser` on the service account and that the IAM Service Account Credentials API is enabled.
* **Permission denied from Vertex AI** - Confirm that `roles/aiplatform.user` and `roles/serviceusage.serviceUsageConsumer` are granted on the project, to the principal set for direct access or to the service account for impersonation.
* **Model not found** - Confirm the model is available in your configured location and, for Claude partner models, enabled in the Vertex AI Model Garden. Check any per-model reference overrides on the **Models** page.
* **Provider quota limits** - Check your project’s Vertex AI quotas and request increases if needed.
### Debugging steps
[Section titled “Debugging steps”](#debugging-steps)
1. Confirm the WIF audience in the Admin Panel exactly matches the provider’s full resource name.
2. Check the credential status card in **Settings** > **Agents** > **Warp Agent** for the failing state and recovery action.
3. Verify the IAM bindings for the principal set, and for the service account if you use impersonation, in your GCP project.
4. Confirm the model reference and location match what’s available in your project.
5. Inspect Cloud Logging in your project for request details and errors.
## FAQ
[Section titled “FAQ”](#faq)
### How is this different from BYOK with a Google API key?
[Section titled “How is this different from BYOK with a Google API key?”](#how-is-this-different-from-byok-with-a-google-api-key)
**BYOK** routes requests to the Gemini Developer API using a personal API key stored on each member’s device. **Gemini Enterprise BYOLLM** routes requests to Vertex AI in your organization’s GCP project using short-lived federated credentials, configured centrally by an admin, with your project’s IAM, quota, and billing. See [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) for the self-serve option.
### Do members need the gcloud CLI installed?
[Section titled “Do members need the gcloud CLI installed?”](#do-members-need-the-gcloud-cli-installed)
No. Unlike [AWS Bedrock BYOLLM](/enterprise/enterprise-features/byollm-aws-bedrock/), which uses each member’s local AWS CLI session, Gemini Enterprise mints credentials from the member’s signed-in Warp session. No local Google tooling or configuration is required. Admins can optionally use the gcloud CLI for the one-time Google Cloud setup, but it isn’t required.
### Does Gemini Enterprise work with cloud agents?
[Section titled “Does Gemini Enterprise work with cloud agents?”](#does-gemini-enterprise-work-with-cloud-agents)
Not yet. Gemini Enterprise currently routes interactive agent requests in the Warp app. Cloud agent BYOLLM is available today through [AWS Bedrock](/enterprise/enterprise-features/byollm-aws-bedrock/#enabling-byollm-for-cloud-agents), and Gemini Enterprise support for cloud agents is planned.
### Which Claude models route through my project?
[Section titled “Which Claude models route through my project?”](#which-claude-models-route-through-my-project)
Claude models offered as Vertex AI partner models (current Sonnet, Opus, Haiku, and Fable families) can route through Gemini Enterprise when your admin enables them. Eligible models show the Gemini Enterprise badge in the model picker. This is unrelated to any routing Warp does through its own infrastructure for Warp-billed requests.
### Can admins enforce provider-only routing?
[Section titled “Can admins enforce provider-only routing?”](#can-admins-enforce-provider-only-routing)
Yes. Admins can disable Direct API access for models on the **Models** page so eligible requests only route through your project. Note that disabling any Direct API model also disables Auto model selection.
## Related resources
[Section titled “Related resources”](#related-resources)
* [Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/) - BYOLLM overview and provider comparison
* [BYOLLM: AWS Bedrock](/enterprise/enterprise-features/byollm-aws-bedrock/) - Route inference through your AWS account
* [Team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) - Admin-configured shared provider keys and custom endpoints
* [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) - Self-serve, user-level API keys
* [Model Choice](/agents/inference/model-choice/) - Full list of supported models
* [Admin Panel](/enterprise/team-management/admin-panel/) - Configure team settings
* [Contact sales](https://www.warp.dev/contact-sales) - Get help with Enterprise setup
# Team-managed LLM API keys and endpoints
Canonical page: [/enterprise/enterprise-features/team-managed-keys-and-endpoints/](https://docs.warp.dev/enterprise/enterprise-features/team-managed-keys-and-endpoints/)
> Configure shared LLM provider API keys and custom endpoints for your team from the Admin Panel, including cloud agents.
Warp lets a **Business or Enterprise team admin** configure shared provider API keys and OpenAI-compatible custom endpoints once, so every member can use them without pasting anything locally. Unlike the self-serve [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) and [custom inference endpoint](/agents/inference/custom-inference-endpoint/) features — which each member configures on their own device and which work only for interactive requests — team-managed providers are stored server-side by Warp and work for **both interactive terminal requests and [cloud agents](/platform/)**.
This gives your organization one place to provision approved model providers, control spend, and keep inference on your own accounts across your whole team.

Note
Team-managed API keys and endpoints are available on Warp’s Business and Enterprise plans. See [Warp pricing](https://www.warp.dev/pricing) for plan details.
## Key features
[Section titled “Key features”](#key-features)
* **Admin-configured, shared across the team** - An admin sets provider keys and custom endpoints once in the Admin Panel, and they appear automatically in every member’s model picker.
* **Works for interactive sessions and cloud agents** - Because credentials are stored by Warp, team-managed providers power both interactive terminal requests and cloud agent runs. Self-serve, member-managed keys and endpoints are stored locally and passed to Warp only in-flight for interactive requests, so they aren’t available to cloud agents.
* **First-party keys and custom endpoints** - Configure API keys for OpenAI, Anthropic, and Google, and add one or more OpenAI-compatible custom endpoints (for example, OpenRouter or LiteLLM).
* **Secrets stored server-side, never synced to devices** - Keys and endpoint URLs are encrypted and stored by Warp. They’re never synced to member devices and never delivered to cloud agent environments.
* **Optional member-managed keys** - Admins choose whether members may also add their own [self-serve API keys](/agents/inference/bring-your-own-api-key/) and [custom endpoints](/agents/inference/custom-inference-endpoint/) on top of the team’s.
* **Member key precedence** - When a member has their own key for the same provider, their key is used instead of the team’s. (Custom endpoints don’t need precedence — a member’s endpoint and a team endpoint are always distinct.)
## How team-managed providers differ from self-serve BYOK and BYOLLM
[Section titled “How team-managed providers differ from self-serve BYOK and BYOLLM”](#how-team-managed-providers-differ-from-self-serve-byok-and-byollm)
Warp offers several ways to bring your own AI infrastructure. Use this table to pick the right one, and follow the links for full details.
| Name | Configured by | Stored | Works with cloud agents | Plans |
| ------------------------------------------------------------------------------------------- | ------------------------ | --------------------------------- | ------------------------------ | -------------------------------- |
| **Team-managed API keys and endpoints** | Team admin (Admin Panel) | Server-side by Warp | Yes | Business and Enterprise |
| **[Bring Your Own API Key](/agents/inference/bring-your-own-api-key/)** (BYOK) | Each member | Locally on the member’s device | No | Free and all eligible paid plans |
| **[Custom inference endpoint](/agents/inference/custom-inference-endpoint/)** | Each member | Locally on the member’s device | No | Free and all eligible paid plans |
| **[BYOLLM — AWS Bedrock](/enterprise/enterprise-features/byollm-aws-bedrock/)** | Team admin (Admin Panel) | Cloud-native IAM (no stored keys) | Yes | Enterprise only |
| **[BYOLLM — Gemini Enterprise](/enterprise/enterprise-features/byollm-gemini-enterprise/)** | Team admin (Admin Panel) | Cloud-native IAM (no stored keys) | No (interactive sessions only) | Enterprise only |
Team-managed API keys and endpoints are an admin-configured option on Business and Enterprise. BYOLLM requires Enterprise. Choose team-managed keys and endpoints to route through provider APIs (OpenAI, Anthropic, Google) or any OpenAI-compatible endpoint using stored keys. Choose [AWS Bedrock BYOLLM](/enterprise/enterprise-features/byollm-aws-bedrock/) for cloud-native IAM routing through your AWS account, including cloud agent support. Choose [Gemini Enterprise BYOLLM](/enterprise/enterprise-features/byollm-gemini-enterprise/) for cloud-native IAM routing through your Google Cloud project; in this iteration, Gemini Enterprise BYOLLM supports interactive sessions only, with cloud agent support planned.
## How it works
[Section titled “How it works”](#how-it-works)
Team-managed configuration is split into public display metadata and secrets, and the two are handled differently.
### First-party keys and custom endpoints
[Section titled “First-party keys and custom endpoints”](#first-party-keys-and-custom-endpoints)
* **First-party keys (BYOK)** - The admin adds an API key for a provider Warp supports (OpenAI, Anthropic, or Google). Members select the normal Warp model for that provider, and the server routes the request through the team key when the member has no key of their own.
* **Custom endpoints (BYOE)** - The admin adds one or more OpenAI-compatible Chat Completions endpoints. Each endpoint has a name, a base URL, an API key, and one or more models, where each model has a model name (sent to the endpoint) and an optional alias (shown to members). Team endpoint models appear in every member’s model picker as their own entries, labeled with the endpoint name.
### How secrets are stored and used
[Section titled “How secrets are stored and used”](#how-secrets-are-stored-and-used)
Team-managed credentials are protected end to end and are only ever decrypted server-side at the moment a request is served:
1. **Sealed in the browser** - When an admin saves a key or endpoint, the Admin Panel encrypts the secret in the browser before it’s sent, so the plaintext value never travels in the clear.
2. **Encrypted at rest by Warp** - The server re-encrypts each secret with envelope encryption backed by a dedicated Cloud KMS key and stores only the ciphertext. API keys and endpoint base URLs are never written to the settings that sync to clients.
3. **Injected only at request time** - When a member (or a cloud agent running as the team) sends a request, the server decrypts the matching team credential and uses it to call the provider or endpoint, at the same boundary that redacts secrets from logs.
What syncs to a member’s client is display metadata only: whether a key is configured for each provider, and the names, models, and aliases of team endpoints. API keys, endpoint base URLs, and ciphertext are never exposed to clients.
### Member key precedence
[Section titled “Member key precedence”](#member-key-precedence)
When the admin allows member-managed keys and endpoints, a member’s own key for a provider takes precedence over the team’s. Custom endpoints don’t require precedence, because a member’s endpoint and a team endpoint are always distinct:
* **First-party keys** - If a member has their own key for a provider, requests route through the member’s key; otherwise the team key is used; otherwise Warp-managed inference is used (if allowed).
* **Custom endpoints** - A member’s own endpoint and a team endpoint never collide, even if they share a name. The member’s endpoint is used when they select it; team endpoints resolve to the team’s stored credential.
### Cloud agents
[Section titled “Cloud agents”](#cloud-agents)
Because team-managed keys and endpoints are stored by Warp rather than on a member’s device, [cloud agents](/platform/) running as the team can perform inference through the team’s configured providers with no per-member device state. The secret is decrypted only at the server-side inference boundary and never reaches the cloud agent’s environment. Member-managed (local) keys and endpoints are never used by cloud agents.
## Configuring team-managed keys and endpoints
[Section titled “Configuring team-managed keys and endpoints”](#configuring-team-managed-keys-and-endpoints)
### Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* You have admin access to your team’s [Admin Panel](/enterprise/team-management/admin-panel/).
* Your organization is on the Business or Enterprise plan.
### Configure keys and endpoints
[Section titled “Configure keys and endpoints”](#configure-keys-and-endpoints)
Configure team providers from the [Admin Panel](/enterprise/team-management/admin-panel/) **Models** page, where a **First-party API keys** card and a **Custom endpoints** card sit alongside the Direct API and AWS Bedrock cards.
1. In the [Admin Panel](/enterprise/team-management/admin-panel/), go to the **Models** page.
2. To add a team API key, use the **First-party API keys** card: enter the key for a provider (OpenAI, Anthropic, or Google) and save it. Each provider row shows whether a key is configured without revealing the stored value.
3. To add a team custom endpoint, use the **Custom endpoints** card: enter a name, a base URL, an API key, and at least one model (a model name plus an optional alias), then save. An endpoint can’t be saved without a name, a valid base URL, an API key, and at least one model.
4. Choose whether members may add their own keys and endpoints. When this is off, Warp won’t use any key or endpoint a member adds, even if they’ve saved one — their saved keys are preserved for when it’s turned back on.
Saved configuration propagates to members the next time their client loads team settings — the team’s providers appear in their model picker, and disabled endpoints or models are removed automatically.
Note
A team endpoint’s base URL must be reachable from Warp’s servers over the public internet, because requests route through Warp’s backend. Expose an internal gateway at a public HTTPS URL before adding it. See [Network requirements](/agents/inference/custom-inference-endpoint/#network-requirements) for details.
### Keep inference on your team’s providers
[Section titled “Keep inference on your team’s providers”](#keep-inference-on-your-teams-providers)
By default, members can still choose Warp-managed models even when team providers are configured. To require that inference goes to your providers, turn off **Direct API** access on the **Models** page so Warp-managed models are no longer selectable.
## Member experience
[Section titled “Member experience”](#member-experience)
Members don’t configure anything for team providers — they just select a model. Team-managed configuration syncs to each member’s client automatically:
* **Custom endpoints** - Each enabled team endpoint model appears in the model picker as its own entry, showing the model’s name (or alias) and the endpoint name. Members select it like any other model.
* **First-party keys** - Members select the standard model for a provider (for example, a Claude, GPT, or Gemini model), and requests route through the team key automatically. If a member has added their own key for that provider, their own key takes precedence.
If the admin allows members to add their own keys and endpoints, members can still do so through the standard self-serve [BYOK](/agents/inference/bring-your-own-api-key/) and [custom inference endpoint](/agents/inference/custom-inference-endpoint/) settings.
## Billing behavior
[Section titled “Billing behavior”](#billing-behavior)
* **No AI credits for team-routed inference** - When a request routes through a team key or team endpoint, Warp doesn’t consume your [AI credits](/support-and-community/plans-and-billing/credits/). Inference is billed directly by your provider or endpoint.
* **Auto still uses Warp credits** - Warp’s **Auto** models route across providers using Warp’s infrastructure, so Auto always consumes Warp credits. To use a team provider, select a specific model or endpoint from the picker. [Custom routers](/agents/inference/custom-routers/) are the exception: after a router resolves a task to a concrete model, the request routes through the first-party key for that model’s provider (the member’s own key first, then the team key). Routers can’t target team endpoint models.
* **Platform and compute credits still apply** - On Business and Enterprise, local agent runs still consume [platform credits](/support-and-community/plans-and-billing/platform-credits/) for Warp’s platform infrastructure (run lifecycle, orchestration, and observability). Cloud agent runs consume platform credits too, plus [compute credits](/support-and-community/plans-and-billing/credits/#compute-credits) when they use Warp-hosted compute.
See [The three credit buckets](/support-and-community/plans-and-billing/platform-credits/#the-three-credit-buckets) for more on credit types.
## Security and data handling
[Section titled “Security and data handling”](#security-and-data-handling)
* **Secrets encrypted at rest** - Team keys and endpoint URLs are sealed in the admin’s browser, re-encrypted server-side with envelope encryption backed by Cloud KMS, and stored only as ciphertext.
* **Never synced to devices** - Only display metadata syncs to member clients. API keys, endpoint base URLs, and ciphertext are never sent to clients.
* **Never delivered to cloud agent environments** - Team credentials are decrypted only at the server-side inference boundary and never reach a cloud agent’s worker or environment.
### Zero Data Retention (ZDR)
[Section titled “Zero Data Retention (ZDR)”](#zero-data-retention-zdr)
Warp is **SOC 2 compliant** and has **Zero Data Retention (ZDR)** agreements with its contracted LLM providers. When you route through your own keys or endpoints:
* Data retention on the **provider side** is determined by your provider’s account settings.
* Warp **cannot enforce ZDR** for requests sent through your keys or endpoints.
* If your provider account doesn’t have ZDR enabled, your requests may be retained according to their terms.
## Related resources
[Section titled “Related resources”](#related-resources)
* [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) — Self-serve, user-level API keys for OpenAI, Anthropic, and Google.
* [Custom inference endpoint](/agents/inference/custom-inference-endpoint/) — Self-serve, user-level OpenAI-compatible endpoints.
* [Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/) — BYOLLM overview: route inference through [AWS Bedrock](/enterprise/enterprise-features/byollm-aws-bedrock/) or [Gemini Enterprise (Vertex AI)](/enterprise/enterprise-features/byollm-gemini-enterprise/).
* [Admin Panel](/enterprise/team-management/admin-panel/) — Configure team settings and model routing.
* [Model Choice](/agents/inference/model-choice/) — Full list of supported models.
* [Contact sales](https://www.warp.dev/contact-sales) — Get help with Enterprise setup.
# Enterprise FAQ
Canonical page: [/enterprise/getting-started/faq/](https://docs.warp.dev/enterprise/getting-started/faq/)
> Answers to common questions about Warp Enterprise, including login issues, SSO, and getting started.
## Login and SSO
[Section titled “Login and SSO”](#login-and-sso)
### I can’t log in with SSO
[Section titled “I can’t log in with SSO”](#i-cant-log-in-with-sso)
**Problem:** Error message when trying to log in via SSO.
**Solution:**
1. Make sure you’re logging in through the [Warp login page](https://app.warp.dev/login), not your SSO provider’s portal.
2. Select **Continue with SSO** and enter your work email or domain.
3. If you have an existing Warp account, log in with your original credentials and [link your Warp account to SSO first](https://app.warp.dev/link_sso).
4. Complete the linking process.
5. Log out and log back in with **Continue with SSO**.
### I logged in with another method before and can’t use SSO now
[Section titled “I logged in with another method before and can’t use SSO now”](#i-logged-in-with-another-method-before-and-cant-use-sso-now)
**Problem:** You created a Warp account with email/Google/GitHub, but your organization now requires SSO.
**Solution:**
1. Go to the [Warp login page](https://app.warp.dev/login).
2. Log in with your original method.
3. Navigate to the [SSO linking page](https://app.warp.dev/link_sso).
4. Complete the linking process.
5. Log out and log back in with **Continue with SSO**.
### Warp won’t open from my SSO provider
[Section titled “Warp won’t open from my SSO provider”](#warp-wont-open-from-my-sso-provider)
**Problem:** Clicking Warp in Okta/Microsoft Entra ID portal shows an error.
**Solution:** This is a known limitation. Warp cannot be launched directly from SSO provider portals. Instead:
1. Go to the [Warp login page](https://app.warp.dev/login).
2. Click **Continue with SSO**.
3. Complete authentication.
## Team and access
[Section titled “Team and access”](#team-and-access)
### Team invite links not working
[Section titled “Team invite links not working”](#team-invite-links-not-working)
**Common causes:**
* Invite link expired or was revoked.
* User’s email domain doesn’t match configured restrictions.
**Solution:**
1. Generate a new invite link.
2. Verify domain restrictions match the user’s email.
### Users can’t see new admin settings
[Section titled “Users can’t see new admin settings”](#users-cant-see-new-admin-settings)
**Problem:** You changed a setting in the Admin Panel, but users don’t see the change.
**Solution:**
1. Verify the setting is not set to “Respect User Setting.”
2. Ask users to restart Warp to force a settings refresh.
3. Confirm users are members of the correct team.
4. Check that users have logged in with SSO (not a personal account).
## Additional help
[Section titled “Additional help”](#additional-help)
For more troubleshooting, see:
* [Troubleshooting login documentation](/support-and-community/troubleshooting-and-support/troubleshooting-login-issues/)
* Contact your team admin for organization-specific issues.
* Reach out to Warp support via your team’s dedicated Slack/Teams channel.
* Join Warp’s [Slack community](https://go.warp.dev/join-preview) to connect with other Warp users and engineers.
# Getting started for developers
Canonical page: [/enterprise/getting-started/getting-started-developers/](https://docs.warp.dev/enterprise/getting-started/getting-started-developers/)
> Download Warp, log in to your team, and start using agents, Codebase Context, and collaborative features to accelerate your development workflow.
This guide helps developers get up and running with their team in Warp. You’ll learn how to download Warp, log in with your organization’s SSO, and configure key features like Codebase Context, Warp Drive, and Agent Profiles to accelerate your work across the entire SDLC (all while staying in your terminal).
When you use agents in Warp, you’re working with **Warp’s built-in agents**. The Automation Platform is Warp’s programmable system for running and coordinating agents at scale, whether they run locally on your machine or in the cloud. The Automation Platform provides the orchestration, tracking, and control plane for scaling agent workflows.
Note
New to Warp Enterprise? Try the [Enterprise quickstart](/enterprise/getting-started/quickstart/) for a 10-minute walkthrough of SSO login, Warp setup, and running your first agent.
## 1. Download and install Warp
[Section titled “1. Download and install Warp”](#1-download-and-install-warp)
Warp is available for macOS, Linux, and Windows.
### Download Warp
[Section titled “Download Warp”](#download-warp)
Visit the [Warp download page](https://www.warp.dev/download) and select your platform:
* **macOS** - Download the `.dmg` installer (macOS 10.15 Catalina or later)
* **Linux** - Download the `.deb`, `.rpm`, or AppImage
* **Windows** - Download the `.exe` installer (Windows 10 or later)
### Install Warp
[Section titled “Install Warp”](#install-warp)
**macOS:**
1. Open the downloaded `.dmg` file.
2. Drag Warp to your Applications folder.
3. Launch Warp from Applications or Spotlight.
**Linux:**
```bash
# Debian/Ubuntu
sudo dpkg -i warp-terminal_*.deb
# Fedora/RHEL
sudo rpm -i warp-terminal-*.rpm
```
For the full list of Linux installation options, including package-manager repositories, Arch, openSUSE, and AppImage, see the [installation and setup guide](/getting-started/quickstart/installation-and-setup/).
**Windows:**
1. Run the downloaded `.exe` installer.
2. Follow the installation wizard.
3. Launch Warp from the Start menu.
## 2. Log in to your team
[Section titled “2. Log in to your team”](#2-log-in-to-your-team)
### Logging in with SSO
[Section titled “Logging in with SSO”](#logging-in-with-sso)
If your organization uses SSO (most enterprise teams do):
1. Launch Warp.
2. When prompted, log in or create an account.
3. Click **Continue with SSO**.
4. Enter your work email or your organization’s domain.
5. Complete authentication with your SSO credentials when redirected to your identity provider.
Caution
Do not attempt to launch Warp directly from your SSO provider’s app portal (e.g., Okta dashboard). This will result in an error. Always log in through the [Warp login page](https://app.warp.dev/login).
### Logging in with an invite link
[Section titled “Logging in with an invite link”](#logging-in-with-an-invite-link)
If you received an invite link from your team admin:
1. Click the invite link in your email or message.
2. From the signup page, log in using SSO if it’s configured for your team, otherwise use one of the other sign in methods (Google, GitHub, or email).
3. After authentication, you’ll automatically join your team.
### Linking an existing account to SSO
[Section titled “Linking an existing account to SSO”](#linking-an-existing-account-to-sso)
If you were using Warp before your organization enabled SSO:
1. Go to the [Warp login page](https://app.warp.dev/login).
2. Log in with your original method (email, Google, or GitHub).
3. Once logged in, navigate to the [SSO linking page](https://app.warp.dev/link_sso).
4. Follow the prompts to link your account to SSO.
5. From now on, use **Continue with SSO** to log in.
## 3. Set up key features
[Section titled “3. Set up key features”](#3-set-up-key-features)
### Codebase Context
[Section titled “Codebase Context”](#codebase-context)
Codebase Context indexes your Git repositories so agents can understand your code and provide accurate, context-aware responses across large, multi-repo systems.
**Setting up Codebase Context:**
First, enable codebase indexing in your settings:
1. Go to **Settings** > **Code** > **Indexing and projects**.
2. Toggle **Enable Codebase Indexing** to turn it on.
3. Optionally, enable **Index new folders by default** to automatically index repositories as you navigate to them.
Caution
Codebase Context is a feature your team admin controls. If you don’t see these settings or they are disabled, contact your admin to enable this feature for your team.
**Indexing your repositories:**
Once codebase indexing is enabled, you can index individual repositories:
1. Navigate to a Git repository in your terminal.
2. Run the `/init` command.
3. Warp begins indexing your codebase.
4. You’ll be prompted to create an `AGENTS.md` file (optional but recommended).
**What gets indexed:**
* All Git-tracked files in your repository
* Up to 200,000 files per repository
* Files excluded in `.gitignore` or `.warpindexingignore` are automatically skipped
**Privacy:**
During indexing, your code is sent to Warp’s servers for processing where embeddings are created and stored. The code itself is not saved—only the embeddings are persisted. This allows agents to understand your codebase structure and context without storing your actual source code.
Note
For cloud agents: Code snippets may be stored as part of conversation records when agents create or modify files, since diffs are preserved in the conversation history.
### Agent Profiles
[Section titled “Agent Profiles”](#agent-profiles)
Agent Profiles let you configure how Warp’s built-in agents behave. Profiles give you direct control over model selection, autonomy, tools, and permissions for your agent workflows.
**Creating an Agent Profile:**
1. Go to **Settings** > **Agents** > **Profiles**.
2. Click **New Profile**.
3. Configure:
* **Name and description**
* **Model** - Choose which LLM to use
* **Autonomy level** - How much agents can do without asking
* **Tools** - Enable/disable terminal use, code editing, web search
* **Permissions** - What agents can access (repos, files, secrets)
4. Click **Save**.
**Using profiles:**
Switch between profiles based on your task:
* **High autonomy** for routine tasks like writing tests or updating docs
* **Low autonomy** for sensitive operations like infrastructure changes
* **Specific models** for cost optimization or task requirements
### Warp Drive
[Section titled “Warp Drive”](#warp-drive)
Warp Drive is your workspace for saving and sharing Workflows, Notebooks, Prompts, Rules, and Environment Variables.
**Accessing Warp Drive:**
1. Click the tools panel icon in the top left of Warp.
2. Click the Warp Drive icon from the top of the tools panel.
3. Two Warp Drive sections display:
* **Team** (top) - Resources shared across your team.
* **Personal** (bottom) - Your individual resources.
**What you can add to Warp Drive:**
* **Workflows** - Parameterized commands you use repeatedly (e.g., deploy scripts, environment setup)
* **Notebooks** - Interactive runbooks combining markdown and executable code blocks
* **Prompts** - Saved agent prompts for recurring tasks (e.g., “review this PR”, “write unit tests”)
* **Plans** - Agent-generated execution plans for complex tasks that agents can then run step-by-step
* **Rules** - Coding standards and conventions agents should follow
* **Environment Variables** - Configuration that can be loaded into your terminal session
**Creating your first Workflow:**
1. From Warp Drive, click **+** in your Personal or Team section.
2. Select **Workflow**.
3. Enter a name, description, and command.
4. Add parameters if needed (e.g., `{{branch_name}}`).
5. Click **Save**.
**Using team resources:**
Your team admin may have already created shared resources. Explore the Team section of Warp Drive to see what’s available—including onboarding notebooks, deployment workflows, and coding standards rules.
### MCP (Model Context Protocol)
[Section titled “MCP (Model Context Protocol)”](#mcp-model-context-protocol)
MCP connects Warp’s agents to external tools and services for enhanced context.
**Configuring MCP servers:**
1. Go to **Settings** > **Agents** > **MCP servers** or access via Warp Drive.
2. Browse the library of available MCP servers:
* **Linear** - Access issues and project context
* **Sentry** - Pull error tracking and stack trace information
* **Figma** - Reference designs and specifications
* **GitHub** - Access repository and PR context
* And more…
3. Click **+** next to a server to add it.
4. Configure credentials and connection details.
5. Toggle the server on/off as needed.
Your team may have shared MCP configurations. Check for a share icon next to team-configured servers to use them without manual setup.
## 4. Start using Warp
[Section titled “4. Start using Warp”](#4-start-using-warp)
### Everyday workflows
[Section titled “Everyday workflows”](#everyday-workflows)
Warp keeps you in your terminal with agent help across the entire SDLC:
**Environment setup**
* “Set up Node 20, Python 3.12, and Docker Desktop”
* Save setup steps as a Workflow in Warp Drive for future use
**Understanding codebases**
* “How does authentication flow through this system?”
* “What patterns does this repo use for error handling?”
**Writing code**
* Use the `/plan` command for complex features
* Review diffs in real-time with the code review panel
* Leave comments on specific lines for the agent to address
**Debugging**
* Start a debugger (`gdb`, `lldb`) and bring in an agent
* Agents can operate debuggers and REPLs in natural language
* Attach terminal output to agent conversations for analysis
**Version control**
* “Stage these changes and write a detailed commit message”
* “Create a PR with a description following our template”
* Set up Rules to enforce Git commit conventions
**Testing**
* “Write unit tests for this function following our existing patterns”
* “Run the test suite and explain what failed”
* Configure cloud agents to run test suites and validate coverage on PRs in the background
### Learning resources
[Section titled “Learning resources”](#learning-resources)
* **Warp Guides** - Short video tutorials in the [Guides](/guides/)
* Getting Started with Warp
* Warp Code features
* Developer workflows
* MCP, Rules, and Prompts
* **Documentation** - Comprehensive guides in the [Warp docs](https://docs.warp.dev)
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
For common login, SSO, and access issues, see the [Enterprise FAQ](/enterprise/getting-started/faq/).
## Next steps
[Section titled “Next steps”](#next-steps)
Now that you’re set up:
* **Explore agent capabilities** - Learn about [agents in Warp](/agents/) and [cloud agents](/platform/)
* **Contribute to team knowledge** - Add useful Workflows, Prompts, and Rules to your team’s Warp Drive to compound productivity gains across your team
* **Stay updated** - Check the [Warp changelog](/changelog/) for new features
## Support and feedback
[Section titled “Support and feedback”](#support-and-feedback)
* **Send feedback** - Use `Cmd+Shift+F` (macOS) or `Ctrl+Shift+F` (Linux/Windows) or go to **Help** > **Send Feedback**
* **Request features** - Share ideas by [sending us feedback](/support-and-community/troubleshooting-and-support/sending-us-feedback/)
* **Get help** - Enterprise teams have access to priority support via dedicated Slack/Teams channels
* **Join the community** - Connect with other Warp users in our [Slack community](https://go.warp.dev/join-preview)
# Getting started with Warp Enterprise
Canonical page: [/enterprise/getting-started/getting-started-enterprise/](https://docs.warp.dev/enterprise/getting-started/getting-started-enterprise/)
> Set up Warp Enterprise for your organization with SSO configuration, team management, and admin controls.
This guide walks your IT or platform admin through initial Warp setup for your organization: configuring SSO, creating your team, inviting users, and setting Admin Panel policies.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
Before you begin:
* You have an active Warp Enterprise subscription
* You have admin access to your organization’s identity provider (Okta, Microsoft Entra ID, Google Workspace, etc.)
* You’ve identified which team members should have admin privileges in Warp
## Step 1: Configure Single Sign-On (SSO)
[Section titled “Step 1: Configure Single Sign-On (SSO)”](#step-1-configure-single-sign-on-sso)
Warp uses SSO to authenticate users and control access to your organization’s Warp team. Warp supports Okta, Microsoft Entra ID, Google Workspace, OneLogin, and any SAML 2.0 or OIDC compatible provider through [WorkOS](https://workos.com).
SSO setup is coordinated with Warp’s team — contact your account team or [enterprise support](https://www.warp.dev/contact-sales) to get started. For the full setup process and supported providers, see [Single Sign-On (SSO)](/enterprise/security-and-compliance/sso/).
**Before rolling out to your team**, test SSO login in an incognito window to confirm it works. See [Testing SSO](/enterprise/security-and-compliance/sso/#testing-sso) for steps.
Note
After enabling SSO, existing users who signed up with email or OAuth will need to [link their accounts to SSO](https://app.warp.dev/link_sso) before they can continue using Warp with your organization. See [troubleshooting SSO account linking](/support-and-community/troubleshooting-and-support/troubleshooting-login-issues/#i-logged-in-with-another-method-before-and-now-cant-use-sso) for details.
## Step 2: Create and configure your team
[Section titled “Step 2: Create and configure your team”](#step-2-create-and-configure-your-team)
### Creating your team
[Section titled “Creating your team”](#creating-your-team)
During Enterprise onboarding, Warp’s team will work with you to set up your team. This typically happens in one of two ways:
* **Warp provisions your team** - In most cases, Warp creates the team on your behalf and adds your admin so you can begin configuration right away.
* **You create or bring your own team** - If you already have a Warp team, or prefer to create one yourself, Warp’s team will apply the Enterprise plan to it during onboarding.
In either case, the Enterprise plan must be applied by Warp internally — this cannot be self-served. Your account team will coordinate this with you. To get started, contact your account manager.
### Team settings
[Section titled “Team settings”](#team-settings)
Some team settings are configured in different places:
* **Team name** - Configured in **Settings** > **Teams** in the Warp app. Help users identify the right team to join.
* **Domain restrictions** - Limit team invites to specific email domains (e.g., `@yourcompany.com`)
* **Auto-join** - Automatically adds users to your team when they sign in via SSO from your configured domain. The domain must be configured by the Warp team during onboarding — contact your account team to set up or update your team domain.
* **SSO** - Configured through WorkOS, not the Admin Panel. See [Step 1](#step-1-configure-single-sign-on-sso).
## Step 3: Invite and manage users
[Section titled “Step 3: Invite and manage users”](#step-3-invite-and-manage-users)
### Inviting users
[Section titled “Inviting users”](#inviting-users)
There are several ways to add users to your Warp team:
**Option 1: Invite by email**
1. Navigate to **Settings** > **Teams**.
2. Enter email addresses in the **Invite by Email** field (comma-separated).
3. Click **Invite**.
**Option 2: Share invite link**
1. Navigate to **Settings** > **Teams**.
2. Copy the team invite link.
3. Share the link via email, Slack, or your preferred communication channel.
**Option 3: Domain auto-join**
Note
Domain configuration is set up by the Warp team during onboarding. Contact your Warp account team to configure or update your team domain.
1. Once your team domain is configured, users who sign in via SSO from your domain are automatically added to your Warp team.
### User roles and permissions
[Section titled “User roles and permissions”](#user-roles-and-permissions)
Warp has three user roles:
* **Team Owner** - Has full access to the Admin Panel and can manage team settings, invite users, assign roles, and transfer ownership of the team. There can only be one Owner.
* **Team Admin** - Same permissions as the Owner, except they can’t transfer ownership of the team.
* **Member** - Standard access to Warp features and team resources
### Managing admins
[Section titled “Managing admins”](#managing-admins)
To promote or demote team admins:
1. Navigate to **Settings** > **Teams** > **Team Members**.
2. Find the user you want to modify.
3. Click the **…** (three dots) next to their name.
4. Select **Promote to admin** or **Demote admin**.
Note
Teams can have multiple admins. We recommend at least one admin in addition to the Team Owner to prevent access issues if one is unavailable.
## Step 4: Configure the Admin Panel
[Section titled “Step 4: Configure the Admin Panel”](#step-4-configure-the-admin-panel)
The Admin Panel gives you centralized control over Warp features, permissions, and usage across your team.
### Accessing the Admin Panel
[Section titled “Accessing the Admin Panel”](#accessing-the-admin-panel)
1. In Warp, open **Settings**.
2. Navigate to the **Billing and usage** section.
3. Click **Open Admin Panel**.
Alternatively, visit the [Warp Admin Panel](https://app.warp.dev/admin) directly.
### Key Admin Panel sections
[Section titled “Key Admin Panel sections”](#key-admin-panel-sections)
* **Billing** - View your plan type and AI usage limit information
* **Teams** - Manage team members, roles, and invites — the same controls available in **Settings** > **Teams** in the Warp app
* **AI** - Configure general and AI autonomy settings for your team
* **Models** - Configure which models are available to your team, plus BYOLLM routing through AWS Bedrock or Gemini Enterprise
* **Code** - Enable Codebase Context for your team
* **Platform** - Configure cloud agent settings
* **Privacy** - Configure user-generated content data collection, cloud conversation storage, and enterprise secret redaction
* **Sharing** - Configure direct link sharing and “anyone with link” sharing permissions
### How settings enforcement works
[Section titled “How settings enforcement works”](#how-settings-enforcement-works)
Settings configured in the Admin Panel are enforced at the team level:
* **Enforced settings** - Cannot be overridden by individual users (e.g., BYOLLM routing policies)
* **Respect User Setting** - Defers to each user’s own preference, letting individual team members configure that setting themselves
## Step 5: Set up team resources
[Section titled “Step 5: Set up team resources”](#step-5-set-up-team-resources)
### Enable Codebase Context
[Section titled “Enable Codebase Context”](#enable-codebase-context)
Codebase Context indexes your Git repositories to help agents understand your code across large, multi-repo systems:
1. Navigate to **Admin Panel** > **Code**.
2. Toggle **Codebase Indexing** to **Enabled**.
Warp prompts team members to index repositories when they navigate to a Git-tracked directory.
### Create shared Warp Drive resources
[Section titled “Create shared Warp Drive resources”](#create-shared-warp-drive-resources)
Populate your team’s Warp Drive with shared resources to scale best practices and compound productivity gains:
* **Workflows** - Parameterized commands for common tasks (deployments, environment setup)
* **Notebooks** - Interactive runbooks for onboarding and operational procedures
* **Prompts** - Saved agent prompts for recurring tasks (code review, test generation)
* **Rules** - Coding standards and conventions that agents should follow
* **Environment Variables** - Shared configuration for development environments
See [Warp Drive documentation](/knowledge-and-collaboration/warp-drive/) for details on creating team resources.
### Configure MCP integrations
[Section titled “Configure MCP integrations”](#configure-mcp-integrations)
Connect Warp to your team’s tools for enhanced agent context. Navigate to **Settings** > **Agents** > **MCP servers** to get started. Some integrations (like Linear, GitHub, and Sentry) are available to enable with a single click, while you can also add any custom MCP server configuration your team needs.
Once configured, click the share icon on a server to make it available to your team.
See the [MCP documentation](/agents/capabilities/mcp/) for full configuration details.
## Next steps
[Section titled “Next steps”](#next-steps)
Once your team is set up:
* **For developers** - Share the [Getting started for developers](/enterprise/getting-started/getting-started-developers/) guide with your team
* **Agent Profiles** - Configure default [Agent Profiles](/agents/capabilities/agent-profiles-permissions/) for different types of work to give teams appropriate autonomy and control
* **BYOLLM** - Set up [Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/) to route inference through your cloud infrastructure for data locality and cost control
* **Team-managed API keys and endpoints** - Configure [shared provider API keys and custom endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) for your team in the Admin Panel, available in both interactive sessions and cloud agents
* **Monitor usage** - Review usage analytics in the Admin Panel to track adoption and measure engineering productivity gains
* **Self-hosting** - Run agents on your own infrastructure to control where agents run and keep repository clones on your own machines. See [Self-hosting](/factories/self-hosting/) for setup instructions
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### SSO login issues
[Section titled “SSO login issues”](#sso-login-issues)
For common SSO problems (login failures, account linking, provider portal errors), see [SSO troubleshooting](/enterprise/security-and-compliance/sso/#troubleshooting).
### Team invite links not working
[Section titled “Team invite links not working”](#team-invite-links-not-working)
**Common causes:**
* Invite link expired or was revoked
* User’s email domain doesn’t match configured restrictions
**Solution:**
1. Generate a new invite link.
2. Verify domain restrictions match user’s email.
## Support and resources
[Section titled “Support and resources”](#support-and-resources)
* [Admin Panel documentation](/enterprise/team-management/admin-panel/)
* [Troubleshooting login issues](/support-and-community/troubleshooting-and-support/troubleshooting-login-issues/)
* [Contact enterprise support](https://www.warp.dev/contact-sales) - Priority support via dedicated Slack/Teams channel
# Enterprise quickstart
Canonical page: [/enterprise/getting-started/quickstart/](https://docs.warp.dev/enterprise/getting-started/quickstart/)
> Get up and running with Warp Enterprise in under 10 minutes. Log in, set up your terminal, and run your first agent.
This quickstart walks you through the essentials: logging in via SSO, setting up Warp, and running your first agent. You can complete this in under 10 minutes.
## 1. Log in via SSO
[Section titled “1. Log in via SSO”](#1-log-in-via-sso)
1. Go to the [Warp login page](https://app.warp.dev/login).
2. Click **Continue with SSO**.
3. Enter your work email or your organization’s domain.
4. Complete authentication with your identity provider.
Caution
Do not launch Warp from your SSO provider’s app portal (e.g., Okta dashboard). Always log in through the [Warp login page](https://app.warp.dev/login).
If you have an existing Warp account from before your organization enabled SSO, [link your Warp account to SSO first](https://app.warp.dev/link_sso).
## 2. Download and set up Warp
[Section titled “2. Download and set up Warp”](#2-download-and-set-up-warp)
1. Visit the [Warp download page](https://www.warp.dev/download) and select your platform (macOS, Linux, or Windows).
2. Install Warp:
* **macOS** - Open the `.dmg` and drag Warp to Applications.
* **Linux** - Install via `.deb`, `.rpm`, or the install script.
* **Windows** - Run the `.exe` installer.
3. Launch Warp and log in with SSO (Step 1).
4. Verify you see your team name in **Settings** > **Teams**.
## 3. Configure and run your first agent
[Section titled “3. Configure and run your first agent”](#3-configure-and-run-your-first-agent)
When you use Agent Mode in Warp, you’re working with the Warp Agent, Warp’s built-in agent. The Automation Platform is Warp’s programmable system for running and coordinating agents at scale, whether they run locally on your machine or in the cloud.
### Index your codebase
[Section titled “Index your codebase”](#index-your-codebase)
1. Navigate to a Git repository in Warp.
2. Warp automatically detects the repo and begins indexing.
3. Optionally, run `/init` to manually trigger indexing or re-indexing after significant code changes.
4. Once indexed, agents understand your code structure, patterns, and conventions.
### Run your first agent locally
[Section titled “Run your first agent locally”](#run-your-first-agent-locally)
Start a conversation right in the terminal. Try the following prompt:
```plaintext
Explain the architecture of this project
```
The Warp Agent reads your codebase, understands its structure, and responds with a context-aware explanation.
### Try more prompts
[Section titled “Try more prompts”](#try-more-prompts)
* **Write code** - “Add input validation to the signup form”
* **Debug** - “Why is this test failing?” (paste the error output)
* **Explore** - “What patterns does this repo use for error handling?”
* **Plan** - Use `/plan` to have the Warp Agent create a structured task plan for complex features
## 4. Run a cloud agent
[Section titled “4. Run a cloud agent”](#4-run-a-cloud-agent)
Cloud agents run in the cloud for background work, unlimited parallelization, and long-running tasks.
### Create an environment
[Section titled “Create an environment”](#create-an-environment)
Environments define the execution context for cloud agents (repo access, dependencies, secrets, compute). You can create an environment in several ways:
**Option 1: Slash command in Warp**
From the Warp app terminal input, run the command:
```plaintext
/create-environment
```
This launches an interactive flow that guides you through environment setup.
**Option 2: Oz web app**
Go to the [Environments page](https://app.warp.dev/environments) and click **Create Environment**.
### Run a cloud agent
[Section titled “Run a cloud agent”](#run-a-cloud-agent)
Once your environment is ready, use the following command to launch a cloud agent (use the environment ID from above):
```bash
oz agent run-cloud --env my-env --prompt "Review the open PRs in this repo"
```
Monitor and steer your agents from the cloud agent dashboard or directly in Warp.
## Next steps
[Section titled “Next steps”](#next-steps)
* **Set up key features** - Follow the full [Getting started for developers](/enterprise/getting-started/getting-started-developers/) guide to configure Codebase Context, Warp Drive, MCP integrations, and Agent Profiles.
* **Explore cloud agents** - Learn about [cloud agents](/platform/) for background automation and parallel workflows.
* **Explore guides** - Visit [Warp Guides](/guides/) for video tutorials and end-to-end workflows.
# Security overview
Canonical page: [/enterprise/security-and-compliance/security-overview/](https://docs.warp.dev/enterprise/security-and-compliance/security-overview/)
> Understand Warp's security architecture, data handling practices, and compliance certifications to ensure your organization's requirements are met.
Warp builds security and compliance into its core, keeping **developers in control** while enabling powerful agent workflows. This overview explains how Warp handles your data, what security controls are available, and how Warp meets enterprise security standards.
## Transparency and control
[Section titled “Transparency and control”](#transparency-and-control)
Warp’s security philosophy centers on **transparency and developer control**:
* **Complete visibility** - View exactly what telemetry is collected through our [exhaustive telemetry table](/support-and-community/privacy-and-security/privacy/#exhaustive-telemetry-table)
* **Real-time monitoring** - Use Warp’s [Network Log](/support-and-community/privacy-and-security/network-log/) to monitor all network requests in real time
* **Opt-out controls** - Disable telemetry and crash reporting at any time while retaining full functionality
* **Team-level enforcement** - Admins can configure telemetry and data collection policies for the entire organization
* **Open source client** - Warp’s client code is published under [AGPL v3](https://github.com/warpdotdev/warp/blob/master/LICENSE-AGPL) at [`warpdotdev/warp`](https://github.com/warpdotdev/warp), so security teams can audit the codebase directly. See [Contributing to Warp](/support-and-community/community/contributing/) for the source repository and the security reporting process.
## What telemetry does Warp collect and why?
[Section titled “What telemetry does Warp collect and why?”](#what-telemetry-does-warp-collect-and-why)
### Zero Data Retention (ZDR)
[Section titled “Zero Data Retention (ZDR)”](#zero-data-retention-zdr)
Warp has **Zero Data Retention (ZDR)** agreements with its contracted LLM providers (Anthropic, OpenAI, Google, xAI), meaning they do not store or train on your data. ZDR applies across all Warp plans.
How data collection works by plan:
* **Free tier** - Individual users can disable data collection in **Settings** > **Privacy**.
* **Paid teams** - Team admins can enforce data collection settings for the entire team. Data collection is enabled by default.
* **Business and Enterprise** - Team admins can enforce data collection settings for the entire team. Data collection is **disabled by default**.
Note
Some product features — including cloud conversations and cloud agent runs — require storing conversation data to function. This data is stored to power the product experience and is separate from analytics or telemetry data collection.
Some models carry provider-specific data retention requirements and are therefore not covered by ZDR. For Enterprise teams, these models are **off by default**; a workspace admin must explicitly enable them in the [Admin Panel](/enterprise/team-management/admin-panel/#models-settings).
Enterprise subscriptions also include:
* **Team-level enforcement** - Admins configure data collection and telemetry policies for the entire organization through the Admin Panel
* **Secret redaction** - Admins can enable [Secret Redaction](/support-and-community/privacy-and-security/secret-redaction/) for the organization and configure patterns for sensitive data
### Telemetry categories
[Section titled “Telemetry categories”](#telemetry-categories)
When telemetry is enabled, Warp collects:
1. **Product usage analytics** - High-level metrics on feature adoption and usage patterns (e.g., “Agent Mode was opened,” “workflow was executed”).
2. **Performance and stability** - Crash reports, error tracking, and performance metrics to identify and fix issues.
When data collection is disabled, Warp does not collect:
* Personally identifiable information beyond user IDs and email addresses
* Network traffic or external API calls
### Disabling telemetry
[Section titled “Disabling telemetry”](#disabling-telemetry)
Users can opt out of telemetry individually:
1. Navigate to **Settings** > **Privacy**.
2. Toggle off **Help improve Warp** and/or **Send crash reports**.
With telemetry disabled, Warp stops collecting usage and interaction data for analytics purposes.
Team admins can enforce telemetry settings organization-wide through the Admin Panel. On Business and Enterprise plans, data collection is disabled by default.
## Data handling and privacy
[Section titled “Data handling and privacy”](#data-handling-and-privacy)
### Where your data lives
[Section titled “Where your data lives”](#where-your-data-lives)
* **Code and files** - Stay on your machine unless you explicitly use features that transmit them (e.g., Codebase Context indexing, session sharing, Warp Drive team resources)
* **Codebase Context** - During indexing, code is sent to Warp’s servers to generate embeddings; the raw code is not stored, only the resulting embeddings are retained
* **Agent requests** - Warp sends requests to contracted LLM providers (Anthropic, OpenAI, Google, xAI) with Zero Data Retention agreements for Enterprise teams
* **BYOLLM** - Requests are proxied through Warp’s servers to your cloud infrastructure, where inference runs. Warp does not store the content of these requests.
* **Team-managed API keys and endpoints** - When an admin configures [team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/), the keys are encrypted and stored server-side, never synced to member devices, and never delivered to cloud agent environments. They’re decrypted only in memory when serving a request.
* **Self-hosted cloud agent execution** - Repository clones, build artifacts, runtime secrets, and execution workspaces stay on your infrastructure. Orchestration metadata, session transcripts, and LLM inference requests and responses route through Warp under ZDR, and can include code context from agent interactions.
### Encryption
[Section titled “Encryption”](#encryption)
* **In transit** - All data transmitted to Warp servers uses TLS 1.2 or higher
* **At rest** - Warp encrypts all user data at rest using AES-256
### Secret redaction
[Section titled “Secret redaction”](#secret-redaction)
When Secret Redaction is enabled, Warp masks matching sensitive information before sending terminal or AI content to LLM providers. Admins can configure patterns for:
* API keys and tokens
* Passwords and secrets
* SSH keys and certificates
* Custom secret patterns (configurable via Admin Panel)
Telemetry payload redaction is a separate mechanism. It applies built-in patterns to telemetry and includes user and Enterprise patterns when they are configured.
See [Secret Redaction documentation](/support-and-community/privacy-and-security/secret-redaction/) for details.
### Data retention
[Section titled “Data retention”](#data-retention)
* **ZDR** - Warp’s contracted LLM providers do not retain or train on your data
* **Telemetry data** - When collected, Warp retains telemetry data indefinitely for analytics and debugging
* **User accounts** - Data deletion requests are processed securely within 30 days at no cost, following verified authentication and compliance with legal and contractual obligations
## Compliance and certifications
[Section titled “Compliance and certifications”](#compliance-and-certifications)
### SOC 2 Type II
[Section titled “SOC 2 Type II”](#soc-2-type-ii)
Warp is SOC 2 Type II certified, demonstrating compliance with industry-standard security controls for:
* **Security** - Infrastructure protection, access controls, and monitoring
* **Availability** - System uptime and disaster recovery
* **Confidentiality** - Data protection and privacy controls
* **Processing integrity** - Accurate, complete, and authorized processing
SOC 2 reports are available to Enterprise customers upon request.
## Infrastructure security
[Section titled “Infrastructure security”](#infrastructure-security)
### Warp-hosted infrastructure
[Section titled “Warp-hosted infrastructure”](#warp-hosted-infrastructure)
When using Warp’s hosted infrastructure:
* **Cloud provider** - Hosted on GCP with SOC 2 and ISO 27001 certified datacenters
* **Network isolation** - Workloads run in isolated VPCs with strict network policies
Warp’s operational security practices — including access controls, monitoring, and vulnerability management — are validated through SOC 2 Type II certification. See [Compliance and certifications](#compliance-and-certifications) for details.
### Self-hosted deployments
[Section titled “Self-hosted deployments”](#self-hosted-deployments)
Enterprise teams can self-host cloud agent execution to control where agents run and keep repositories on their own infrastructure.
Self-hosted deployments use a split architecture:
* **Execution plane (customer-hosted)** - Repository clones, build artifacts, runtime secrets, and container filesystem state stay on your infrastructure
* **Control plane (Warp-hosted)** - Session transcripts (which include code context from agent interactions), orchestration metadata, and LLM inference route through Warp’s servers under Zero Data Retention (ZDR) agreements. Warp does not persistently store your source code or use it for model training
Two deployment modes are available:
* **Unmanaged** - Use `oz agent run` to run agents in your existing orchestrator or CI environment. Supports Linux, macOS, and Windows with no Docker dependency.
* **Managed** - Run the `oz-agent-worker` daemon to let Warp orchestrate agents in isolated Docker containers on your infrastructure.
Agent runs are fully tracked and steerable in both modes. No inbound network access is required.
**Network egress requirements**
Self-hosted agents require outbound access to Warp’s backend services and, for the managed architecture, Docker Hub and GitHub.
## Access controls and authentication
[Section titled “Access controls and authentication”](#access-controls-and-authentication)
### Single Sign-On (SSO)
[Section titled “Single Sign-On (SSO)”](#single-sign-on-sso)
Warp supports SSO via Okta, Microsoft Entra ID, Google Workspace, OneLogin, and any SAML 2.0 or OpenID Connect (OIDC) compatible provider. Admins can require SSO for all team members and enforce MFA through your identity provider.
See [Single Sign-On (SSO)](/enterprise/security-and-compliance/sso/) for setup instructions, SCIM provisioning, account linking, and troubleshooting.
### Team permissions
[Section titled “Team permissions”](#team-permissions)
Warp uses role-based access control with three roles — Team Owner, Team Admin, and Member — to manage team access and Admin Panel privileges. See [User roles and permissions](/enterprise/getting-started/getting-started-enterprise/#user-roles-and-permissions) for details.
Resource sharing in Warp Drive has granular controls for who can view, edit, and share.
### Admin Panel governance
[Section titled “Admin Panel governance”](#admin-panel-governance)
The Admin Panel gives security and IT teams centralized control over AI behavior, data handling, and sharing policies. Settings can be **enforced** (overriding individual user preferences organization-wide) or set to **respect user setting** (deferring to individual preferences).
Security-relevant controls include:
* **Privacy** - Configure user-generated content (UGC) data collection, cloud conversation storage, and enterprise secret redaction
* **Sharing** - Restrict or permit direct link sharing and “anyone with link” sharing permissions
* **AI** - Configure AI autonomy settings and general agent behavior for the team
* **Models** - Control which LLM models are available to team members, including BYOLLM routing through AWS Bedrock and Gemini Enterprise (Vertex AI)
* **Platform** - Configure cloud agent access and settings
## Security features for developers
[Section titled “Security features for developers”](#security-features-for-developers)
### Bring Your Own LLM (BYOLLM)
[Section titled “Bring Your Own LLM (BYOLLM)”](#bring-your-own-llm-byollm)
Route agent inference through your own cloud infrastructure for complete control:
* **Data locality** - Interactive agent inference runs in your AWS account or Google Cloud project
* **Cloud-native IAM** - Authenticate using your user’s existing identity and access management process
* **No key storage** - Warp never stores your cloud credentials or API keys
* **Billing control** - Inference costs billed directly to your cloud account
See [Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/) for configuration details.
### Docker Sandboxes
[Section titled “Docker Sandboxes”](#docker-sandboxes)
Isolate agent execution in containerized environments:
* **Process isolation** - Agents run in separate Docker containers, isolated from your host system
* **Resource limits** - Configure CPU, memory, and disk quotas per sandbox
* **Network controls** - Restrict outbound network access from sandboxes
* **Ephemeral environments** - Sandboxes are destroyed after use, leaving no trace
### Agent permissions
[Section titled “Agent permissions”](#agent-permissions)
Configure what agents can access and execute:
* **Tool restrictions** - Enable/disable terminal use, code editing, web search, and file system access
* **Repository scoping** - Limit agents to specific repositories or directories
* **Execution approvals** - Require manual approval for sensitive commands
* **Visibility** - When cloud conversation storage is enabled, agent actions are logged with full context for review
## Incident response and support
[Section titled “Incident response and support”](#incident-response-and-support)
### Security issue reporting
[Section titled “Security issue reporting”](#security-issue-reporting)
If you discover a security vulnerability in Warp:
1. Email <security@warp.dev>.
2. Include detailed steps to reproduce.
3. Do not publicly disclose until Warp has addressed the issue.
Warp follows responsible disclosure practices and works with reporters to coordinate disclosure timelines.
### Enterprise support
[Section titled “Enterprise support”](#enterprise-support)
Enterprise customers receive priority security support:
* **Dedicated channels** - Private Slack/Teams channels for security questions
* **Security advisories** - Proactive notifications of security updates
* **Incident assistance** - Support during security incidents or breach investigations
* **Compliance assistance** - Help with compliance questionnaires and audits
## Additional resources
[Section titled “Additional resources”](#additional-resources)
* [Warp privacy policy](https://www.warp.dev/legal/privacy-policy)
* [Warp Trust Center](https://trust.warp.dev) — security documentation and compliance reports. See also [Trust Center](/enterprise/security-and-compliance/trust-center/) for details on requesting SOC 2 reports, subprocessors, and vendor security assessments.
* [Warp subprocessors list](https://www.warp.dev/legal/subprocessors)
* **Privacy documentation** - [Privacy guide](/support-and-community/privacy-and-security/privacy/) with complete telemetry table
* **Contact** - <privacy@warp.dev> for privacy questions, <security@warp.dev> for security issues
Note
For vendor security assessments, compliance questionnaires, or access to SOC 2 reports, contact your account manager or email <security@warp.dev>.
# Single Sign-On (SSO)
Canonical page: [/enterprise/security-and-compliance/sso/](https://docs.warp.dev/enterprise/security-and-compliance/sso/)
> Configure Single Sign-On (SSO) to authenticate and manage access to Warp across your organization.
Warp uses SSO to authenticate users and control access to your Warp workspace. Configure SSO at the workspace level, then manage access through your identity provider.
## Supported identity providers
[Section titled “Supported identity providers”](#supported-identity-providers)
Warp supports the following identity providers:
* **Okta**
* **Microsoft Entra ID**
* **Google Workspace**
* **OneLogin**
* **Any SAML 2.0 or OpenID Connect (OIDC) compatible provider**
## SSO enforcement and session management
[Section titled “SSO enforcement and session management”](#sso-enforcement-and-session-management)
* **SSO enforcement** - Workspace admins can require SSO for all workspace members, preventing login via other methods.
* **Multi-factor authentication** - MFA is enforced through your identity provider’s policies. Warp respects MFA requirements configured in Okta, Microsoft Entra ID, Google Workspace, etc.
* **Session management** - Configurable session timeouts and re-authentication policies through your identity provider.
## Setting up SSO
[Section titled “Setting up SSO”](#setting-up-sso)
SSO is configured through [WorkOS](https://workos.com) in coordination with Warp’s team:
1. Contact your Warp account team or [enterprise support](https://www.warp.dev/contact-sales) to initiate SSO setup.
2. Warp creates an organization for your workspace in WorkOS and sets its domain.
3. Your IT admin receives an email invite from WorkOS.
4. Follow the WorkOS setup wizard to connect your identity provider (configure SAML attributes or OAuth scopes, provide your SSO URL and certificate).
5. Once complete, workspace members can log in via **Continue with SSO** on the [Warp login page](https://app.warp.dev/login).
After enabling SSO, existing users who signed up with email or OAuth need to link their accounts. See [Linking existing accounts](#linking-existing-accounts) below.
## Testing SSO
[Section titled “Testing SSO”](#testing-sso)
Before rolling out SSO to your workspace:
1. Open an incognito/private browser window.
2. Navigate to the [Warp login page](https://app.warp.dev/login).
3. Click **Continue with SSO**.
4. Enter your organization’s domain.
5. Verify you’re redirected to your identity provider and can log in successfully.
Caution
Warp cannot be launched directly from your SSO provider’s app portal (e.g., Okta dashboard). Users must log in through the [Warp login page](https://app.warp.dev/login) and select **Continue with SSO**.
## SCIM provisioning
[Section titled “SCIM provisioning”](#scim-provisioning)
Warp supports SCIM for user lifecycle management. Provisioning works through Just-In-Time (JIT) provisioning combined with SSO and domain capture:
* **User provisioning** - Add users to the Warp application in your identity provider. Once they sign in via SSO, they are automatically added to your Warp workspace.
* **Domain auto-join** - Users who sign in with SSO from your configured domain are automatically joined to your workspace. See [Domain auto-join](#domain-auto-join) for setup details.
* **User deprovisioning** - Removing a user from the Warp application in your identity provider prevents future SSO logins. Existing sessions are not immediately revoked.
Note
Warp does not currently support SCIM group sync. User provisioning is handled via JIT — users appear in your Warp workspace after their first SSO login, not at the time they are assigned in your identity provider.
## Linking existing accounts
[Section titled “Linking existing accounts”](#linking-existing-accounts)
Users who created a Warp account before your organization enabled SSO need to link their accounts:
1. Log in to Warp with the original method (email, Google, or GitHub).
2. Navigate to the [SSO linking page](https://app.warp.dev/link_sso).
3. Complete the linking process.
4. Log out and log back in with **Continue with SSO**.
## Domain auto-join
[Section titled “Domain auto-join”](#domain-auto-join)
Domain auto-join allows users from your organization to automatically join your Warp workspace after SSO authentication.
Domain configuration is set up by the Warp team during onboarding. Contact your Warp account team to configure or update your workspace domain.
Once your workspace domain is configured, users who sign in via SSO from that domain are automatically added to your workspace.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### Users can’t log in with SSO
[Section titled “Users can’t log in with SSO”](#users-cant-log-in-with-sso)
**Common causes:**
* SSO not properly configured in your identity provider.
* User trying to launch Warp directly from SSO provider (not supported).
* User has an existing Warp account that needs to be [linked to SSO](https://app.warp.dev/link_sso).
**Solution:**
1. Verify SSO configuration in your identity provider.
2. Have users log in through the [Warp login page](https://app.warp.dev/login) and select **Continue with SSO**.
3. For existing accounts, follow the [SSO linking process](https://app.warp.dev/link_sso).
### Warp won’t open from SSO provider portal
[Section titled “Warp won’t open from SSO provider portal”](#warp-wont-open-from-sso-provider-portal)
**Problem:** Clicking Warp in Okta/Microsoft Entra ID portal shows an error.
**Solution:** Log in directly through the [Warp login page](https://app.warp.dev/login) and select **Continue with SSO** instead.
## Related resources
[Section titled “Related resources”](#related-resources)
* [Security overview](/enterprise/security-and-compliance/security-overview/) - Enterprise security posture and compliance
* [Getting started for admins](/enterprise/getting-started/getting-started-enterprise/) - Full admin onboarding guide
* [Troubleshooting login issues](/support-and-community/troubleshooting-and-support/troubleshooting-login-issues/)
# Warp Trust Center
Canonical page: [/enterprise/security-and-compliance/trust-center/](https://docs.warp.dev/enterprise/security-and-compliance/trust-center/)
> Access Warp's security documentation, compliance certifications, and third-party assessment resources to complete your vendor security review.
Warp’s [Trust Center](https://trust.warp.dev) is the central hub for security documentation, compliance certifications, and third-party assessments. It provides the information security teams, procurement, and compliance officers need to evaluate Warp as a vendor and complete security reviews.
## Compliance certifications
[Section titled “Compliance certifications”](#compliance-certifications)
### SOC 2 Type II
[Section titled “SOC 2 Type II”](#soc-2-type-ii)
Warp is **SOC 2 Type II certified**, demonstrating compliance with industry-standard security controls across the following trust service criteria:
* **Security** - Infrastructure protection, access controls, and monitoring
* **Availability** - System uptime and disaster recovery
* **Confidentiality** - Data protection and privacy controls
* **Processing integrity** - Accurate, complete, and authorized processing
**Requesting SOC 2 reports:** Enterprise customers can request SOC 2 reports directly through the [Trust Center portal](https://trust.warp.dev), through their account manager, or by emailing <security@warp.dev>.
## Subprocessors
[Section titled “Subprocessors”](#subprocessors)
Warp publishes a list of subprocessors — third-party service providers that process data on Warp’s behalf. This includes infrastructure providers, LLM providers, and other services that support Warp’s operations.
View the current list of subprocessors at [Warp subprocessors list](https://www.warp.dev/legal/subprocessors).
Note
Warp maintains **Zero Data Retention (ZDR)** agreements with its contracted LLM providers (Anthropic, OpenAI, Google, xAI), meaning they do not store or train on your data.
## Security documentation
[Section titled “Security documentation”](#security-documentation)
The following resources provide detailed information about Warp’s security practices:
* **[Trust Center portal](https://trust.warp.dev)** - External portal with downloadable compliance reports and real-time security status
* **[Security overview](/enterprise/security-and-compliance/security-overview/)** - Warp’s security architecture, data handling, and compliance certifications
* **[Privacy policy](https://www.warp.dev/legal/privacy-policy)** - How Warp collects, uses, and protects personal data
* **[Subprocessors](https://www.warp.dev/legal/subprocessors)** - Third-party service providers that process data on Warp’s behalf
## Requesting security information
[Section titled “Requesting security information”](#requesting-security-information)
If you’re conducting a vendor security assessment or completing a compliance questionnaire, Warp can provide:
* **SOC 2 Type II reports** - Available upon request for Enterprise customers
* **Compliance questionnaire assistance** - Warp’s security team can help complete vendor security questionnaires
* **[Architecture and deployment](/enterprise/enterprise-features/architecture-and-deployment/)** - Details about Warp’s infrastructure, deployment models, and data flows
To request any of these materials, contact your account manager or email <security@warp.dev>.
## Penetration testing and vulnerability management
[Section titled “Penetration testing and vulnerability management”](#penetration-testing-and-vulnerability-management)
Warp conducts regular security assessments as part of its SOC 2 program. The details of Warp’s vulnerability management and penetration testing practices are validated through its SOC 2 Type II certification.
### Responsible disclosure
[Section titled “Responsible disclosure”](#responsible-disclosure)
If you discover a security vulnerability in Warp, please report it responsibly:
1. Email <security@warp.dev> with detailed steps to reproduce the issue.
2. Allow Warp time to investigate and address the vulnerability before any public disclosure.
Warp works with reporters to coordinate disclosure timelines.
# Enterprise billing
Canonical page: [/enterprise/support-and-resources/billing/](https://docs.warp.dev/enterprise/support-and-resources/billing/)
> Billing for Warp Enterprise: credits, cloud agent costs, spending controls, and BYOLLM billing under your contract.
Warp Enterprise uses the same credit-based billing as other plans, with pool sizes, rates, and terms set by your contract. For questions about custom pricing, credit allocation, or contract terms, contact your Warp account manager.
## Credits
[Section titled “Credits”](#credits)
Warp uses a credit-based billing model. Any interaction with agents consumes credits based on the complexity of the task, the model used, and the amount of context processed.
### How credits work
[Section titled “How credits work”](#how-credits-work)
* Each agent interaction consumes **at least one credit**, though complex interactions may use multiple credits.
* Credit usage is influenced by the LLM model used, the number of tool calls, task complexity, amount of context, and prompt caching behavior.
* Credit usage is **non-deterministic**. Two similar prompts may consume different numbers of credits.
For details on how credits are calculated, see [Credits](/support-and-community/plans-and-billing/credits/).
### Credit allocation
[Section titled “Credit allocation”](#credit-allocation)
Enterprise plans include a custom team-wide credit pool as part of your contract. Credits are primarily shared across the entire team rather than allocated per seat. Individual credit grants may also occur (e.g., support refunds), but the core allocation is team-wide.
Note
Credit allocations vary by contract. Contact your account manager for details on your team’s specific allocation.
## Cloud agent billing
[Section titled “Cloud agent billing”](#cloud-agent-billing)
Cloud agents consume AI credits for inference, compute credits for the sandbox they run in, and [platform credits](/support-and-community/plans-and-billing/platform-credits/) for the platform layer. Platform credits are billed by the agent hour, the time an agent spends working on a task, at the rate set by your contract. Cloud agent runs on self-hosted workers don’t consume compute credits but still consume platform credits. See [Credits](/support-and-community/plans-and-billing/credits/) for the full breakdown of how each credit type is metered.
### How credits are consumed
[Section titled “How credits are consumed”](#how-credits-are-consumed)
On Enterprise plans, local and cloud agent usage both draw from the same team credit pool across all three credit types (AI credits, compute credits, and platform credits). The credit type a run consumes depends on what infrastructure it uses, not on whether it’s local or cloud.
For agent API key runs (e.g., CI/CD pipelines, scheduled tasks), credits also draw from the team’s shared pool since these runs are not tied to any individual user.
For more details, see [Access, Billing, and Identity](/platform/team-access-billing-and-identity/).
## BYOLLM billing
[Section titled “BYOLLM billing”](#byollm-billing)
When using [Bring Your Own LLM (BYOLLM)](/enterprise/enterprise-features/bring-your-own-llm/), Warp routes requests through your cloud infrastructure ([AWS Bedrock](/enterprise/enterprise-features/byollm-aws-bedrock/) and [Gemini Enterprise Agent Platform (Vertex AI)](/enterprise/enterprise-features/byollm-gemini-enterprise/) today, with Azure Foundry coming soon). Customer-routed BYOLLM inference **consumes no credits** — Warp does not charge credits for requests that execute in your cloud. Inference costs are billed directly to your cloud account. Local agent runs that use BYOLLM still consume [platform credits](/support-and-community/plans-and-billing/platform-credits/).
If a BYOLLM request fails and Warp falls back to a direct API model, that fallback request consumes Warp credits at the standard rate.
## Managing billing
[Section titled “Managing billing”](#managing-billing)
Your Warp account manager handles all billing for your Enterprise contract. Contact your account manager or dedicated Slack/Teams channel for:
* Invoices and payment changes
* Contract modifications
* Credit allocation adjustments
For urgent billing issues, email <billing@warp.dev>.
### Spending controls
[Section titled “Spending controls”](#spending-controls)
Administrators can configure monthly spending limits and receive alerts to prevent unexpected charges. Configure these controls in the [Warp Admin Panel](https://app.warp.dev/admin/) under the **Billing** tab.
#### Monthly spending limits
[Section titled “Monthly spending limits”](#monthly-spending-limits)
Enterprise administrators can set monthly spending limits across the following four categories:
* **Cloud spending limit** - Cap monthly spend on cloud agent usage.
* **Local spending limit** - Cap monthly spend on local agent usage in the Warp app.
* **Total spending limit** - Cap combined monthly spend across both cloud and local agents.
* **Per-user spending limit** - Cap monthly spend for any individual user. Set a default that applies to all users, or configure limits on a per-user basis for predictable individual spend.
Spending is tracked across all payment types (add-on credits, pay-as-you-go usage) so limits apply consistently regardless of how usage is funded.
Note
Team-wide spending limits (cloud, local, and total) are also available on Warp’s self-serve paid plans through admin-managed Add-on credit settings. **Per-user spending limits are Enterprise-only.** For deeper visibility into how individual users consume credits, see the [Enterprise Analytics API](/enterprise/enterprise-features/analytics-api/).
Multi-team workspaces can also have a workspace-level cap above their team limits. See [Workspace spend limits](/enterprise/team-management/workspaces/#workspace-spend-limits).
#### Monthly spend alerts
[Section titled “Monthly spend alerts”](#monthly-spend-alerts)
Warp sends alerts to administrators as team usage approaches each configured spending limit, so you can adjust caps, purchase more credits, or communicate with your team before agent usage is blocked at the cap.
#### Credit pool depletion alerts
[Section titled “Credit pool depletion alerts”](#credit-pool-depletion-alerts)
For enterprises with credit pools, administrators receive alerts as the team credit pool approaches full consumption. This gives you time to top up your credits or change your reload configuration before agent usage is interrupted for the entire team.
## Related resources
[Section titled “Related resources”](#related-resources)
* [Credits](/support-and-community/plans-and-billing/credits/) - How credits are calculated and consumed
* [Add-on credits](/support-and-community/plans-and-billing/add-on-credits/) - Purchase additional credits and configure auto-reload
* [Platform credits](/support-and-community/plans-and-billing/platform-credits/) - Billed by the agent hour; cover Warp’s platform layer on cloud agent runs and local runs with customer-supplied inference
* [Pricing FAQs](/support-and-community/plans-and-billing/pricing-faqs/) - Common billing questions
* [Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/) - BYOLLM billing and configuration
* [Team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) - Share provider keys and custom endpoints across the team; inference routes through your accounts
* [Enterprise Analytics API](/enterprise/enterprise-features/analytics-api/) - Programmatic access to team usage and spend data
* [Admin Panel](/enterprise/team-management/admin-panel/) - Configure spending limits and billing settings
# Feedback and feature requests
Canonical page: [/enterprise/support-and-resources/feedback-and-feature-requests/](https://docs.warp.dev/enterprise/support-and-resources/feedback-and-feature-requests/)
> Report bugs, request features, and get support as a Warp Enterprise customer.
Warp Enterprise customers have access to dedicated support channels for reporting issues, requesting features, and getting help. This page explains how to reach the right team and provide the information needed to resolve issues quickly.
## Enterprise support channels
[Section titled “Enterprise support channels”](#enterprise-support-channels)
Enterprise customers receive **priority support** through dedicated channels:
* **Dedicated Slack or Teams channel** - Your primary support channel. A private channel shared with Warp engineers for real-time assistance, bug reports, and feature discussions.
* **Account manager** - Your direct contact for escalations, strategic feature requests, and enterprise-specific questions.
Note
For the fastest response, use your dedicated Slack or Teams channel. Warp engineers monitor these channels during business hours.
## Reporting bugs
[Section titled “Reporting bugs”](#reporting-bugs)
When reporting a bug, include the following to help Warp’s team investigate quickly:
1. **Description** - What happened and what you expected to happen.
2. **Steps to reproduce** - How to trigger the issue.
3. **Conversation ID** (for Agent issues) - Right-click on the Agent conversation block in question, select **Copy conversation ID**, and include it in your report. When an Agent conversation produces an error, an option to copy the conversation ID also appears inline. See [Gathering conversation ID](/support-and-community/troubleshooting-and-support/sending-us-feedback/#gathering-ai-conversation-id) for more details.
4. **Logs** (if relevant) - See [Gathering logs](#gathering-logs) below.
5. **Environment details** - OS, Warp version, and any relevant configuration.
Note
Most Enterprise teams have user-generated content (UGC) collection disabled, which limits the diagnostic information available from conversation IDs. Logs and detailed reproduction steps are especially important for Enterprise bug reports.
### Gathering logs
[Section titled “Gathering logs”](#gathering-logs)
Warp’s logs do not contain console input or output. Log file locations by platform:
* **macOS** - `~/Library/Logs/warp.log*`
* **Windows** - `%LOCALAPPDATA%\warp\Warp\data\logs\warp.log*`
* **Linux** - `~/.local/state/warp-terminal/warp.log*`
You can also access logs directly in the app: open the **Command Palette** (`⌘+P` on macOS / `Ctrl+Shift+P` on Windows/Linux) and search for **View Warp Logs**.
For detailed log gathering instructions, including how to zip logs and capture crash reports, see [Sending Feedback & Logs](/support-and-community/troubleshooting-and-support/sending-us-feedback/).
## Requesting features
[Section titled “Requesting features”](#requesting-features)
To request a new feature or enhancement:
* **Enterprise customers** - Share feature requests through your dedicated Slack/Teams channel or with your account manager. This ensures your request is tracked and prioritized by the product team.
* **Public feature requests** - Open an issue on [GitHub Issues](https://github.com/warpdotdev/warp/issues/new/choose) for visibility and community discussion.
## Specialized contacts
[Section titled “Specialized contacts”](#specialized-contacts)
For security or privacy inquiries, reach out to the appropriate team directly:
* **Security issues** - <security@warp.dev>
* **Privacy questions** - <privacy@warp.dev>
For all other inquiries — including billing, technical issues, and feature requests — contact your account manager or dedicated Slack/Teams channel.
## Related resources
[Section titled “Related resources”](#related-resources)
* [Troubleshooting login](/enterprise/support-and-resources/troubleshooting-login/) - Resolve login and SSO issues
# Troubleshooting login
Canonical page: [/enterprise/support-and-resources/troubleshooting-login/](https://docs.warp.dev/enterprise/support-and-resources/troubleshooting-login/)
> Resolve common login and SSO issues for Warp Enterprise users and IT admins.
Resolve common login and SSO issues for Warp Enterprise users and IT admins. For SSO setup and configuration, see [Single Sign-On (SSO)](/enterprise/security-and-compliance/sso/).
## SSO login issues
[Section titled “SSO login issues”](#sso-login-issues)
### Can’t open Warp from your SSO provider
[Section titled “Can’t open Warp from your SSO provider”](#cant-open-warp-from-your-sso-provider)
When launching Warp directly from Okta or another SSO provider’s app dashboard, you may see an error like “Unable to process request due to missing initial state.” This is a known limitation with the authentication flow.
**To fix it:**
1. Go to the [Warp login page](https://app.warp.dev/login).
2. Choose **Continue with SSO**.
3. Log in with your normal SSO credentials.
### Previously logged in with another method
[Section titled “Previously logged in with another method”](#previously-logged-in-with-another-method)
If you originally created your Warp account with email, Google, or GitHub and now need to use SSO:
1. Go to the [Warp login page](https://app.warp.dev/login).
2. Log in with your **original** method (email, Google, or GitHub).
3. Once logged in, visit the [SSO linking page](https://app.warp.dev/link_sso).
4. Click **Link SSO** to connect your existing account. You can now use **Continue with SSO** going forward.
Note
IT admins: if multiple team members need to link their accounts to SSO, share these steps during your SSO rollout.
## Common login issues
[Section titled “Common login issues”](#common-login-issues)
### Can’t sign up or log in
[Section titled “Can’t sign up or log in”](#cant-sign-up-or-log-in)
If clicking the sign-up or login button opens a blank popup or nothing happens:
* Your ISP or firewall may be blocking calls to `*.googleapis.com`. Try using a proxy or allowlisting this domain.
* In some older Ruby development environments, `.dev` domains don’t resolve properly. If applicable, delete `/etc/resolver/dev` (see [fixing `.dev` domain resolution](https://superuser.com/questions/1374892/dev-domains-dont-resolve)).
### Browser-specific issues
[Section titled “Browser-specific issues”](#browser-specific-issues)
If you see authentication errors or blank popups across browsers:
1. **Disable ad blockers** for `app.warp.dev`.
2. **Clear cookies and cache**, or try an incognito / private browser window.
3. Try the [Warp login page](https://app.warp.dev/login) again.
**Safari-specific:** If you see “Unable to access localStorage” errors, go to **Safari Preferences** > **Privacy** and uncheck **Block all cookies**. Firebase Auth requires cookies to track login state.
## Proxy issues
[Section titled “Proxy issues”](#proxy-issues)
If you’re behind a proxy, QUIC traffic may not pass through correctly. Disabling QUIC in your browser forces a fallback to TCP, which typically resolves the issue:
**Chrome / Chromium-based browsers (Edge, Opera, Arc):**
1. Navigate to `chrome://flags`.
2. Search for **Experimental QUIC protocol**.
3. Set it to **Disabled**.
4. Relaunch the browser.
**Firefox:**
1. Navigate to `about:config`.
2. Accept the risk warning.
3. Search for `network.http.http3.enable`.
4. Double-click to set it to `false`.
5. Restart Firefox.
**Safari:** There is no built-in option to disable QUIC in Safari.
## Flagged as fraudulent
[Section titled “Flagged as fraudulent”](#flagged-as-fraudulent)
If you see “This account has been flagged as fraudulent,” your account has triggered Warp’s fraud detection system. This can happen due to multiple account creation or use of throwaway emails (both against Warp’s [Terms of Service](https://www.warp.dev/legal/terms-of-service)).
### False positives
[Section titled “False positives”](#false-positives)
Ad blockers or systems like Pi-hole can sometimes trigger false positives. Try temporarily disabling them and attempting login again.
### Requesting an appeal
[Section titled “Requesting an appeal”](#requesting-an-appeal)
If you’re still unable to authenticate, email <appeals@warp.dev> with the email address of the affected account. Appeals may take 5–10 days.
Enterprise customers can also contact their account manager or dedicated Slack/Teams channel for faster resolution.
## Browser doesn’t open when signing in
[Section titled “Browser doesn’t open when signing in”](#browser-doesnt-open-when-signing-in)
If the browser doesn’t open automatically from Warp when you click “Sign up” or “Sign in”:
1. Go to the [Signup](https://app.warp.dev/signup) or [Login](https://app.warp.dev/login) page in your browser.
2. Complete authentication in the browser.
3. On the logged-in page, if **Take me to Warp** doesn’t work, click the token-copy link to copy the authentication token.
4. Paste the token into Warp.
Note
On Linux and Windows, the default paste shortcut is `Ctrl+Shift+V`.
## Getting help
[Section titled “Getting help”](#getting-help)
* **Enterprise customers** - Contact your dedicated Slack/Teams channel or account manager.
* **All other users** - Visit the [Warp contact page](https://www.warp.dev/contact) for support.
## Related resources
[Section titled “Related resources”](#related-resources)
* [Single Sign-On (SSO)](/enterprise/security-and-compliance/sso/) - SSO setup and configuration
* [Feedback and feature requests](/enterprise/support-and-resources/feedback-and-feature-requests/) - Report bugs and request features
* [Troubleshooting login (full guide)](/support-and-community/troubleshooting-and-support/troubleshooting-login-issues/) - Complete troubleshooting reference
# Admin Panel for teams
Canonical page: [/enterprise/team-management/admin-panel/](https://docs.warp.dev/enterprise/team-management/admin-panel/)
> Centralized management for team administrators to configure Warp settings, control agent behavior, and enforce security policies across your organization.
The Admin Panel provides administrators with centralized control over team settings in Warp. Configure agent behavior, security policies, codebase indexing, and collaboration features for your entire organization from a single interface.
## What is the Admin Panel?
[Section titled “What is the Admin Panel?”](#what-is-the-admin-panel)
The [Admin Panel](https://app.warp.dev/admin/) is your control center for managing Warp at scale. It allows IT admins, platform teams, and engineering managers to:
* **Control agent behavior** - Set autonomy levels, command permissions, and safety guardrails organization-wide
* **Enforce security policies** - Configure secret redaction, telemetry controls, and data handling
* **Manage team resources** - Enable Codebase Context, configure BYOLLM, and control sharing permissions
* **Monitor usage** - Track credit consumption and set spending limits
* **Maintain compliance** - Apply consistent policies that meet your organization’s security requirements
Note
Warp restricts Admin Panel access to team administrators. Regular team members can view settings that affect them but cannot modify organization-wide policies.
## Accessing the Admin Panel
[Section titled “Accessing the Admin Panel”](#accessing-the-admin-panel)
### For team admins
[Section titled “For team admins”](#for-team-admins)
Access the Admin Panel in two ways:
**Option 1: Direct URL**
1. Navigate to the [Warp Admin Panel](https://app.warp.dev/admin/).
2. Log in with your SSO credentials.
3. The Admin Panel opens with all organization settings.
**Option 2: From Warp Settings**
1. Open Warp and click your profile icon in the top right.
2. Click **Settings**.
3. Navigate to the **Admin Panel** tab (visible only to team admins).
### For team members
[Section titled “For team members”](#for-team-members)
Team members see organization-enforced settings in their personal Settings panel:
* Settings controlled by admins appear grayed out
* Indicated by message: “Your organization has configured this setting”
* Users retain control over settings where admins have selected “Respect User Setting”
## How settings enforcement works
[Section titled “How settings enforcement works”](#how-settings-enforcement-works)
The Admin Panel uses a three-tier enforcement model that keeps administrators in control while allowing appropriate flexibility.
In multi-team workspaces, workspace admins can enforce supported settings across all teams or let each team decide. See [Workspace settings and team settings](/enterprise/team-management/workspaces/#workspace-settings-and-team-settings).
### Setting enforcement levels
[Section titled “Setting enforcement levels”](#setting-enforcement-levels)
**Organization enforced**
* Setting applies to all team members regardless of individual preferences
* Users cannot override these settings
* Use for security-critical policies (e.g., secret redaction, command denylists)
**Respect user setting**
* Allows individual team members to control the setting themselves
* Admins set a default, but users can customize
* Use for preferences that don’t impact security or compliance (e.g., AI model selection)
**Tier restricted**
* Setting is locked based on billing plan
* Cannot be changed until plan is upgraded
* Indicated by message: “Configuring this setting is not available on your plan”
### Testing before enforcement
[Section titled “Testing before enforcement”](#testing-before-enforcement)
Note
Changes made in the Admin Panel take effect immediately for all team members. Test settings in your own Warp environment before applying organization-wide enforcement.
To safely roll out new policies:
1. Configure settings with “Respect User Setting” initially.
2. Test with a small group of users.
3. Gather feedback and adjust configuration.
4. Switch to “Organization enforced” once validated.
## Plan limitations
[Section titled “Plan limitations”](#plan-limitations)
The features available in the Admin Panel scale with your Warp plan:
### Free tier
[Section titled “Free tier”](#free-tier)
* Most settings are fixed and non-configurable
* Limited Codebase Context (2 repositories)
* No BYOLLM support
* Basic sharing features
### Business plans
[Section titled “Business plans”](#business-plans)
* Most settings become configurable by administrators
* Enhanced agent autonomy control
* Advanced sharing and privacy features
* Increased Codebase Context limits
### Enterprise plans
[Section titled “Enterprise plans”](#enterprise-plans)
* **Full admin control** - Configure all available settings
* **Enterprise secret redaction** - Custom regex patterns for secrets
* **BYOLLM** - Route inference through your cloud infrastructure
* **Self-hosting cloud agent workers** - Deploy cloud agent workers on your own infrastructure
* **Advanced compliance** - SOC 2, HIPAA, and custom data handling agreements
* **Priority support** - Dedicated Slack/Teams channels
For complete plan details, see [Warp pricing](https://www.warp.dev/pricing) or [contact sales](https://www.warp.dev/contact-sales).
## Admin Panel sections
[Section titled “Admin Panel sections”](#admin-panel-sections)
The Admin Panel is organized into seven main areas:
### AI settings
[Section titled “AI settings”](#ai-settings)
Configure how agents behave across your organization, including autonomy levels and command permissions. This is where you balance agent productivity with organizational safety requirements.
#### General AI settings
[Section titled “General AI settings”](#general-ai-settings)
**AI in remote sessions**
* Controls whether agents are available during SSH sessions and remote connections
* Enterprise plans can toggle this setting
* Consider disabling for production servers or sensitive environments
**Prompt summarization caching**
* When conversations become long, the LLM provider caches summaries temporarily
* Improves performance for extended agent interactions
* Zero Data Retention agreements cover caching (short-lived)
#### Autonomy settings
[Section titled “Autonomy settings”](#autonomy-settings)
Configure how much independence agents have when performing actions. Choose between:
* **Agent Decides** - Agent acts autonomously when confident, asks when uncertain (recommended)
* **Always Ask** - Require explicit approval for every action
* **Always Allow** - Maximum autonomy without confirmations
* **Respect User Setting** - Allow individual users to set their preference
**Apply code diffs** Controls whether agents can apply code changes without approval. For production-critical codebases, consider “Always Ask” to maintain tight control.
**Create plans** Whether agents can create structured task plans (`/plan` command) without user approval.
**Execute commands** Manages the agent’s ability to run terminal commands autonomously. Pair with command allowlists/denylists for granular control.
**Read files** Controls agent access to reading files in the codebase. Enable for better context, restrict for sensitive repositories.
#### Directory and command control
[Section titled “Directory and command control”](#directory-and-command-control)
**Directory allowlist** Specify directories where agents can read files without restriction. Use absolute paths:
* `~/git/internal-tooling` - Grant access to specific projects
* `/home/user/repos/public-*` - Use wildcards for patterns
**Command allowlist** Regular expressions matching commands agents can execute without asking permission. Common patterns:
* `grep .*` - Text search
* `ls(\\s.*)?` - Directory listing
* `git status` - Version control queries
* `which .*` - Finding executables
**Command denylist** Regular expressions for commands that **always** require explicit user approval, regardless of autonomy settings:
* `rm -rf.*` - Recursive deletion
* `sudo.*` - Administrative commands
* `curl.*|wget.*` - Network requests
* `docker rm.*` - Container operations
* `.*production.*` - Commands containing “production”
Caution
Command denylist rules take precedence over allowlist rules and agent autonomy settings. Use denylists to prevent high-risk operations even in high-autonomy configurations.
### Privacy settings
[Section titled “Privacy settings”](#privacy-settings)
Manage data collection and security policies to meet your organization’s compliance requirements.
**User-generated content (UGC) data collection** Controls how Warp collects and uses user-generated content to improve the service:
* **Disabled** - Warp collects no UGC data from your organization
* **Enabled** - Allow data collection for service improvement
* **Respect User Setting** - Let individual users decide
Enterprise teams with Zero Data Retention agreements can disable this completely.
**Enterprise secret redaction** Automatically detects and redacts sensitive information before sending data to LLM providers:
* Enterprise plans enable this by default
* Includes automatic detection of common secret patterns (API keys, passwords, certificates)
* Supports custom regex patterns for organization-specific secrets
* Applies unconditionally across all team members
Configure custom patterns in the Admin Panel to match your organization’s secret formats.
### Code settings
[Section titled “Code settings”](#code-settings)
Control codebase indexing and agent code features for your team.
**Codebase Context** Determines whether Warp indexes your team’s Git repositories to provide context for agents:
* **Disabled** - No codebase indexing
* **Enabled** - Index codebases for improved agent responses across large, multi-repo systems
* **Respect User Setting** - Allow individual control
When enabled, agents understand your code patterns, architecture, and conventions across all indexed repositories. Enterprise plans support:
* Unlimited repositories
* Up to 200,000 files per repository
* Team-wide indexing with centralized configuration
### Models settings
[Section titled “Models settings”](#models-settings)
Control which LLM models are available to your team and how inference is routed. From the **Models** page, admins can enable or disable individual models and configure [Bring Your Own LLM (BYOLLM)](/enterprise/enterprise-features/bring-your-own-llm/) routing through AWS Bedrock or [Gemini Enterprise (Vertex AI)](/enterprise/enterprise-features/byollm-gemini-enterprise/).
From the **Models** page, admins can also configure [team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) in the **Bring Your Own Keys & Endpoints** card, sharing provider keys and custom endpoints across the team for both interactive sessions and cloud agents.
From the **Models** page, admins can also create team-synced [custom routers](/agents/inference/custom-routers/) that route each task to a model based on complexity or rules. Team-synced routers appear in the model picker for every team member.
**Models with provider-specific data retention requirements**
Some models require data retention from the model provider and are therefore not available under [Zero Data Retention (ZDR)](/enterprise/security-and-compliance/security-overview/#zero-data-retention-zdr). For Enterprise teams, these models are **disabled by default**. A workspace admin must explicitly enable them before team members can use them.
### Billing settings
[Section titled “Billing settings”](#billing-settings)
Configure billing preferences and spending controls to manage costs at scale.
**Usage-based pricing** Enable pay-as-you-go billing for credits beyond your plan’s included quota:
* Set monthly spending limits to control costs
* View current overage usage and costs
* Receive alerts when approaching spending thresholds
**Credit allocation** For Enterprise plans with negotiated credit pools:
* Allocate credits across teams or projects
* Monitor usage by team
* Set per-team spending limits
Contact your account manager to configure advanced credit allocation. Multi-team workspaces can also use [workspace spend limits](/enterprise/team-management/workspaces/#workspace-spend-limits).
### Sharing settings
[Section titled “Sharing settings”](#sharing-settings)
Control how team members collaborate and share Warp Drive resources.
**Direct link sharing** Allow team members to share Notebooks, Workflows, Prompts, and other Warp Drive objects via direct links:
* **Enabled** - Team members can generate shareable links
* **Team only** - Links work only for team members
* **Disabled** - No link sharing
**Anyone with link sharing** Enable public access to shared objects:
* **Enabled** - Anyone with the link can view content without being a team member
* **Disabled** - Links require team membership to access
For organizations with sensitive internal processes, disable “Anyone with link” sharing to prevent accidental exposure.
### Platform settings
[Section titled “Platform settings”](#platform-settings)
Configure cloud agent settings for your team, including GitHub authorization for automated workflows.
**Pull request artifact attachments**
Controls how screenshots and video recordings captured with [Computer Use](/agents/capabilities/computer-use/) are attached to pull request descriptions. Choose **Disabled**, **Link only**, or **Embed**. For what each mode does and its security implications, see [Screenshots and videos in pull requests](/agents/capabilities/computer-use/artifacts-in-prs/).
**Enabled GitHub Orgs**
The **Enabled GitHub Orgs** setting associates your Warp team with one or more GitHub App installations. That association does two things: it lets cloud agents initiated with an [agent API key](/agents/cli/oz-cli/api-keys/) clone repositories and open pull requests using the [Warp Factories](/factories/) GitHub App, and it tells Warp which team owns runs started from the [GitHub integration](/platform/integrations/github/) when someone mentions `@warp-agent` in those repositories.
To configure:
1. Navigate to the **Platform** section of the Admin Panel.
2. Under **Enabled GitHub Orgs**, review the list of GitHub organizations where the Warp Factories GitHub App is installed.
3. Select which organizations your team should have access to.
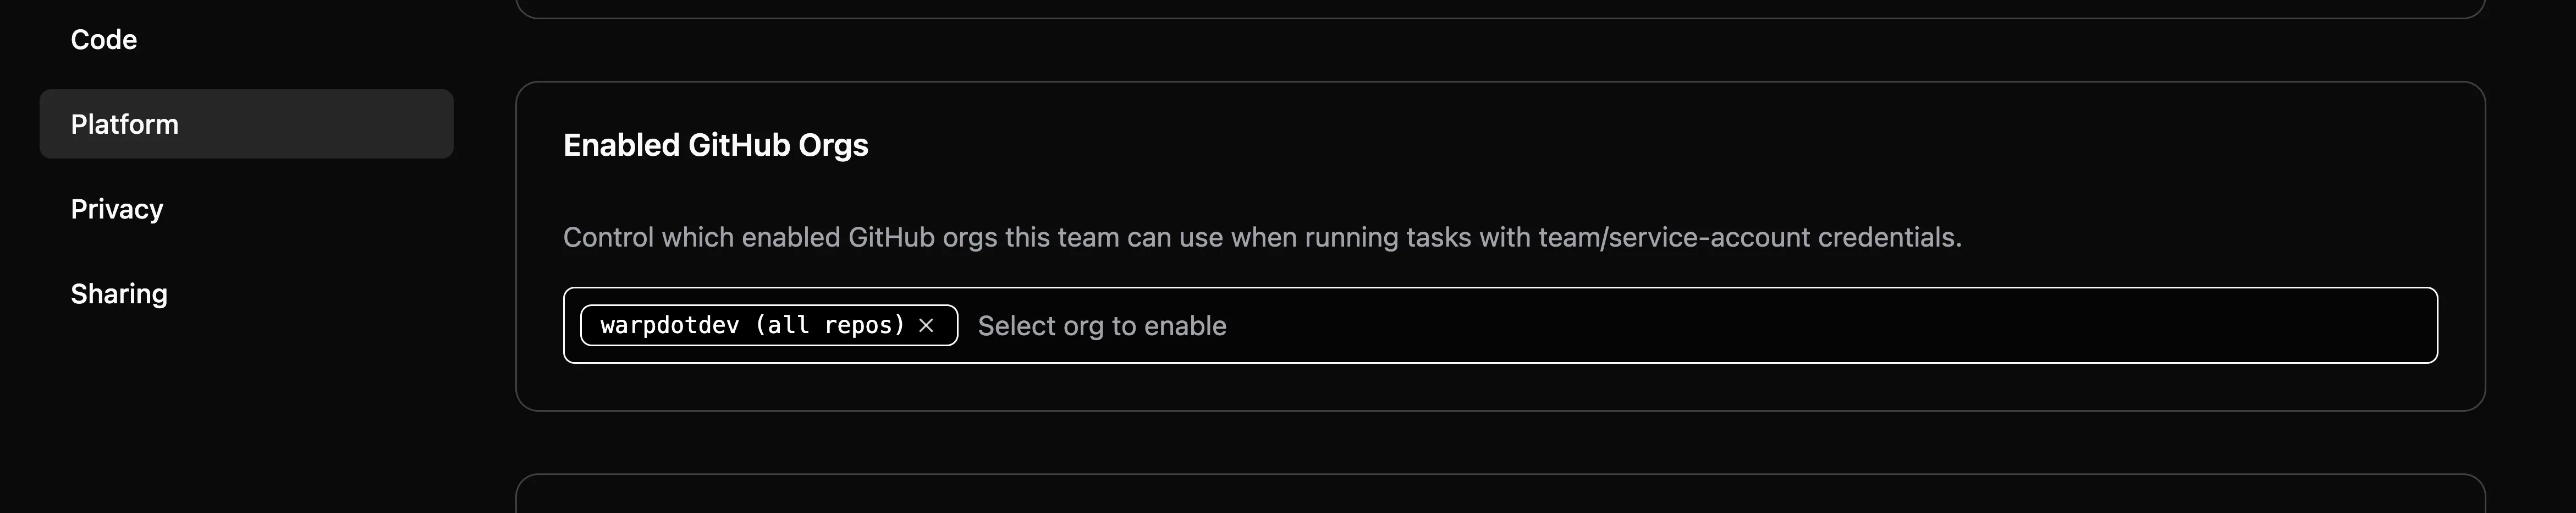
Enabled GitHub Orgs setting in the Admin Panel.
The organizations and repository access shown here reflect the Warp Factories GitHub App installation scope, which is configured in [GitHub settings](https://github.com/settings/installations). To change which repositories the app can access, edit the installation directly in GitHub.
Note
This setting controls which GitHub App installation agent API key runs authenticate with, and which GitHub organizations can start [GitHub integration](/platform/integrations/github/) runs for this team. Runs from an `@warp-agent` mention also authenticate with the installation’s GitHub App token, so their repository access comes from the app installation rather than the person who wrote the mention. Runs triggered from a personal API key, Slack, Linear, or the Warp app continue to use that user’s own GitHub authorization. For more details, see [Team GitHub authorization](/platform/team-access-billing-and-identity/#team-github-authorization).
## Multi-admin functionality
[Section titled “Multi-admin functionality”](#multi-admin-functionality)
Warp supports multiple team administrators to prevent single points of failure and enable distributed management.
### Promoting and demoting admins
[Section titled “Promoting and demoting admins”](#promoting-and-demoting-admins)
Team admins can grant or revoke admin privileges:
1. Navigate to **Settings** > **Teams** > **Team Members**.
2. Find the user you want to modify.
3. Click the role dropdown next to their name.
4. Select **Admin** or **Member**.
5. Click **Save**.
Note
We recommend at least one admin in addition to the Team Owner to prevent access issues if one is unavailable. The Team Owner has full access and can transfer ownership; Team Admins have the same permissions except they can’t transfer ownership.
## Common admin workflows
[Section titled “Common admin workflows”](#common-admin-workflows)
### Initial enterprise setup
[Section titled “Initial enterprise setup”](#initial-enterprise-setup)
After purchasing a Warp enterprise plan:
1. **Configure SSO** - Set up authentication with your identity provider.
2. **Enable Codebase Context** - Index your organization’s repositories.
3. **Set agent autonomy** - Configure initial safety levels.
4. **Apply secret redaction** - Add custom patterns for your organization.
5. **Configure BYOLLM** (optional) - Route inference through your cloud accounts.
6. **Create shared resources** - Populate team Warp Drive with Workflows, Rules, and Prompts.
See [Roles and permissions](/enterprise/team-management/roles-and-permissions/) for user roles and access controls. For accounts that manage multiple teams, see [Workspaces](/enterprise/team-management/workspaces/).
### Adjusting policies for different teams
[Section titled “Adjusting policies for different teams”](#adjusting-policies-for-different-teams)
For organizations with multiple teams (e.g., DevOps, Data, Frontend):
1. Create separate Warp teams for each group.
2. Assign team-specific admins.
3. Configure different autonomy levels per team.
4. Use directory allowlists to scope agent access to team repositories.
### Responding to security incidents
[Section titled “Responding to security incidents”](#responding-to-security-incidents)
If an agent performs an unintended action:
1. **Immediate:** Review agent action logs in the affected user’s session.
2. **Short-term:** Add specific commands to the command denylist.
3. **Long-term:** Adjust autonomy settings to prevent similar incidents.
4. **Review:** Check the Admin Panel settings for the affected user’s team to confirm what autonomy levels, allowlists, and restrictions were in effect.
Warp logs all agent actions with full context, making incident investigation straightforward.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### Users can’t see new settings
[Section titled “Users can’t see new settings”](#users-cant-see-new-settings)
**Problem:** You changed a setting in the Admin Panel, but users report they don’t see the change.
**Solution:**
1. Verify the setting is not set to “Respect User Setting”.
2. Ask users to restart Warp to force a settings refresh.
3. Confirm users are members of the correct team.
4. Check that users have logged in with SSO (not a personal account).
### Setting is grayed out in Admin Panel
[Section titled “Setting is grayed out in Admin Panel”](#setting-is-grayed-out-in-admin-panel)
**Problem:** A setting you want to configure appears grayed out or shows “Not available on your plan.”
**Solution:**
* This setting is restricted to higher-tier plans
* Review plan features on [Warp pricing](https://www.warp.dev/pricing)
* Contact your account manager or [sales team](https://www.warp.dev/contact-sales) to upgrade
### Command allowlist not working
[Section titled “Command allowlist not working”](#command-allowlist-not-working)
**Problem:** Agents still ask permission for commands that match your allowlist patterns.
**Solution:**
1. Verify regex patterns are correct (test with a regex validator).
2. Check that commands don’t also match the denylist (denylist takes precedence).
3. Confirm autonomy settings allow command execution.
4. Remember: Some commands are always restricted regardless of allowlist.
## Support
[Section titled “Support”](#support)
Enterprise customers have access to priority support:
* **Dedicated channels** - Private Slack or Teams channels with Warp engineers
* **Account manager** - Direct contact for escalations and feature requests
* **Technical support** - Help with Admin Panel configuration and troubleshooting
Reach out through your dedicated Slack/Teams channel or contact your account manager.
# Roles and permissions
Canonical page: [/enterprise/team-management/roles-and-permissions/](https://docs.warp.dev/enterprise/team-management/roles-and-permissions/)
> Understand user roles, permissions, and access controls for managing your Warp Enterprise team.
Warp uses a role-based access model to control what team members can do within your organization. Admins manage team settings and enforce policies, while members use Warp’s features within the boundaries admins define.
Note
The roles on this page apply to single-team workspaces. In multi-team workspaces, [workspace roles](/enterprise/team-management/workspaces/#workspace-roles) govern company-wide access.
## User roles
[Section titled “User roles”](#user-roles)
Warp has three user roles:
* **Team Owner** - Has full access to the Admin Panel and can manage team settings, invite users, assign roles, and transfer ownership of the team. There can only be one Owner.
* **Team Admin** - Same permissions as the Owner, except they can’t transfer ownership of the team.
* **Member** - Standard access to Warp features and team resources. Members can use agents, access shared Warp Drive resources, and configure personal settings within the limits set by admins.
## Managing admins
[Section titled “Managing admins”](#managing-admins)
Teams can have multiple admins. We recommend at least one admin in addition to the Team Owner to prevent access issues if one is unavailable.
### Promoting or demoting admins
[Section titled “Promoting or demoting admins”](#promoting-or-demoting-admins)
1. Navigate to **Settings** > **Teams** > **Team Members**.
2. Find the user you want to modify.
3. Click the three-dot menu icon next to their name.
4. Select **Promote to Admin** or **Demote from Admin**.
5. Confirm the change when prompted.
Caution
Team Admins cannot demote or modify the Team Owner role.
## Permission details
[Section titled “Permission details”](#permission-details)
### What admins can do
[Section titled “What admins can do”](#what-admins-can-do)
* **Team management** - View members, invite users, remove users, and assign roles.
* **Authentication** - Configure SSO and login requirements.
* **Agent policies** - Set autonomy levels, command allowlists/denylists, and directory access controls.
* **Security settings** - Configure secret redaction, telemetry controls, and data handling policies.
* **Feature controls** - Enable or disable Codebase Context, BYOLLM, sharing, and other features.
* **Billing** - Monitor credit usage, set spending limits, and manage subscriptions.
### What members can do
[Section titled “What members can do”](#what-members-can-do)
* **Use agents** - Run agents locally and in the cloud within the policies admins define.
* **Access team resources** - Use shared Workflows, Notebooks, Prompts, Rules, and Environment Variables in Warp Drive.
* **Configure personal settings** - Adjust settings where admins have selected “Respect User Setting.”
* **Share sessions** - Collaborate via session sharing (if enabled by admins).
* **Index codebases** - Trigger Codebase Context indexing for repositories (if enabled by admins).
### Settings enforcement
[Section titled “Settings enforcement”](#settings-enforcement)
Admin-configured settings follow a three-tier model:
* **Organization enforced** - Applies to all members. Users cannot override these settings. Use for security-critical policies (e.g., secret redaction, command denylists).
* **Respect user setting** - Admins set a default, but individual users can customize. Use for preferences that don’t impact security.
* **Tier restricted** - Setting is locked based on billing plan and cannot be changed until the plan is upgraded.
See the [Admin Panel](/enterprise/team-management/admin-panel/) documentation for details on configuring each setting.
## Resource sharing controls
[Section titled “Resource sharing controls”](#resource-sharing-controls)
Admins control how team members collaborate and share Warp Drive resources:
* **Direct link sharing** - Allow team members to share Notebooks, Workflows, Prompts, and other objects via direct links.
* **Team-only links** - Restrict links so only team members can access them.
* **Public link sharing** - Enable or disable access for anyone with the link (even non-team members).
For organizations with sensitive internal processes, disable public link sharing to prevent accidental exposure.
## Related resources
[Section titled “Related resources”](#related-resources)
* [Workspaces](/enterprise/team-management/workspaces/) - How workspace and team roles work in multi-team accounts
* [Admin Panel](/enterprise/team-management/admin-panel/) - Configure team settings and enforce policies
* [Getting started for developers](/enterprise/getting-started/getting-started-developers/) - Developer onboarding guide
# Team management in Warp
Canonical page: [/enterprise/team-management/teams/](https://docs.warp.dev/enterprise/team-management/teams/)
> Create and manage teams in Warp to organize users, share resources, and collaborate across your engineering organization.
## What is a team?
[Section titled “What is a team?”](#what-is-a-team)
A team is a group of Warp users who collaborate together. Teams share a dedicated workspace in [Warp Drive](/knowledge-and-collaboration/warp-drive/), giving members access to shared Workflows, Notebooks, Prompts, Rules, Plans, and Environment Variables.
Teams are the foundation of Warp’s enterprise experience — they enable centralized administration, shared configuration, and team-wide policy enforcement through the [Admin Panel](/enterprise/team-management/admin-panel/).
Note
Users can belong to one team in a single-team workspace or multiple teams in a [multi-team workspace](/enterprise/team-management/workspaces/).
## Creating a team
[Section titled “Creating a team”](#creating-a-team)
You can create a new team in two ways:
* From the **Warp Drive** side panel, click **+ Create a team**.
* In Warp, navigate to **Settings** > **Teams** and follow the prompts.
When creating a team, give it a meaningful name that represents your organization, company, or project. The person who creates the team becomes the **Team Owner**.
In a multi-team workspace, workspace admins create teams from the Admin Panel. See [Teams inside a workspace](/enterprise/team-management/workspaces/#teams-inside-a-workspace).
Note
You can rename your team at any time by going to **Settings** > **Teams**, clicking on the team name, entering the new name, and pressing `Enter`.
### Inviting team members
[Section titled “Inviting team members”](#inviting-team-members)
Under **Settings** > **Teams**, copy the invite link and share it with your teammates through a secure channel like Slack or email.
Caution
On paid plans, adding new members automatically adds them as paid seats. New members are billed on a prorated basis for the remainder of the billing cycle. See [Billing](/enterprise/support-and-resources/billing/) for details.
## Restricting team invites by domain
[Section titled “Restricting team invites by domain”](#restricting-team-invites-by-domain)
Team Admins can restrict team membership to users with specific email domains — for example, your company’s email domain.
To enable domain restriction:
1. Navigate to **Settings** > **Teams**.
2. Toggle on **Restrict by domain**.
3. Add your allowed email domains to the allowlist.
When domain restriction is enabled, users who attempt to join with a non-matching email domain will be prompted to authenticate via an emailed link sent to an email address on an allowed domain.
## Joining a team
[Section titled “Joining a team”](#joining-a-team)
If you’ve received an invite link, use it to sign up or log in and join the team. If the team uses domain restriction, you’ll need to verify that you have access to an email address on an allowed domain before joining.
## Leaving and deleting teams
[Section titled “Leaving and deleting teams”](#leaving-and-deleting-teams)
* **Members and Admins** - Can leave a team at any time by visiting **Settings** > **Teams** and clicking **Leave team**.
* **Team Owners** - Can delete a team, but only after removing all other team members first.
Caution
A team can’t be deleted while it has unused add-on credits. Before you can delete the team, all add-on credits tied to it must be used or removed. Contact <support@warp.dev> if you need help removing unused credits.
Caution
If you’re a Team Owner and choose to [delete your Warp account](/support-and-community/privacy-and-security/privacy/#delete-your-account-and-data), you’ll need to assign a team member as the new owner before your account can be deleted.
### Add-on credit consequences when leaving or removing members
[Section titled “Add-on credit consequences when leaving or removing members”](#add-on-credit-consequences-when-leaving-or-removing-members)
On Build, Max, and Business plans, [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) are shared across the team and **tied to the team** they were purchased under. Membership changes affect access:
* **A user leaves a team** - You lose access to any add-on credits tied to that team. If you rejoin the same team later, you regain access to any unused, non-expired credits. The admin pays a prorated rate for your seat on rejoin.
* **An admin removes a member** - That member loses access to any add-on credits tied to the team. If they rejoin later, they regain access to any unused, non-expired credits. The admin pays a prorated rate for the seat when the user rejoins.
* **An admin deletes the team** - Any remaining add-on credits must be used or removed before the team can be deleted.
Add-on credits require an active subscription to use. Downgrading to the Free plan suspends access to the add-on credits tied to your team, but doesn’t remove them. They keep their original 12-month expiration, and you regain access when you re-subscribe on the same team.
## Team discoverability
[Section titled “Team discoverability”](#team-discoverability)
Team admins can make their team discoverable to colleagues who share the same email domain. When enabled, new users with a matching domain can find and join the team without needing a direct invite link.
To enable discoverability, go to **Settings** > **Teams** > **Make team discoverable**.
Note
While discoverability is enabled, any new user who joins the team will add a prorated charge to the team’s next billing cycle.
## Transferring team ownership
[Section titled “Transferring team ownership”](#transferring-team-ownership)
Team Owners can transfer ownership to another team member:
1. Navigate to **Settings** > **Teams** > **Team Members**.
2. Click the three-dot menu icon next to the member you want to transfer ownership to.
3. Click **Transfer ownership**.
Only the current Team Owner can initiate an ownership transfer. After the transfer, the previous owner becomes a regular member (or admin, depending on the team’s configuration).
Note
If the new owner’s email is not on a work domain, team discoverability will be automatically disabled as a safety measure.
## Team roles and permissions
[Section titled “Team roles and permissions”](#team-roles-and-permissions)
Warp uses three roles to manage team access:
* **Team Owner** - Full access to the Admin Panel and all team settings. Can manage members, assign roles, configure policies, and transfer ownership. There can only be one Owner per team.
* **Team Admin** - Same permissions as the Owner, except they cannot transfer team ownership. Teams on Enterprise plans can have multiple admins.
* **Member** - Standard access to Warp features and team resources. Members can use agents, access shared Warp Drive resources, and configure personal settings within the limits set by admins.
Note
We recommend having at least one Team Admin in addition to the Team Owner to prevent access issues if one is unavailable.
### Permissions overview
[Section titled “Permissions overview”](#permissions-overview)
This table applies to single-team workspaces. In multi-team workspaces, only workspace admins create teams. See [Workspace roles](/enterprise/team-management/workspaces/#workspace-roles).
| Action | Owner | Admin | Member |
| ------------------------------ | ----- | ----- | ------ |
| Create a team | ✓ | ✓ | ✓ |
| Restrict invites by domain | ✓ | ✓ | |
| Invite members | ✓ | ✓ | ✓ |
| Remove team members | ✓ | ✓ | |
| Leave a team | | ✓ | ✓ |
| Delete a team | ✓ | | |
| Transfer ownership | ✓ | | |
| Promote/demote admins | ✓ | ✓ | |
| Manage billing | ✓ | ✓ | |
| Configure Admin Panel settings | ✓ | ✓ | |
### Multi-admin support
[Section titled “Multi-admin support”](#multi-admin-support)
Teams on the **Enterprise** plan can have multiple admins, enabling distributed management and preventing single points of failure.
To promote or demote a team admin:
1. Navigate to **Settings** > **Teams** > **Team Members**.
2. Find the user you want to modify and click the three-dot menu icon next to their name.
3. Click **Promote to Admin** or **Demote from Admin**.
4. Confirm the change when prompted.
Caution
Team Admins cannot demote or modify the Team Owner’s role. The Owner role can only change through an ownership transfer.
For detailed information on what each role can do and how settings enforcement works, see [Roles and permissions](/enterprise/team-management/roles-and-permissions/).
## Related resources
[Section titled “Related resources”](#related-resources)
* [Workspaces](/enterprise/team-management/workspaces/) - How teams and roles work in multi-team accounts
* [Admin Panel](/enterprise/team-management/admin-panel/) - Configure team settings and enforce policies
* [Roles and permissions](/enterprise/team-management/roles-and-permissions/) - Detailed permission breakdowns and settings enforcement
* [Getting started for admins](/enterprise/getting-started/getting-started-enterprise/) - Admin onboarding guide
* [Billing](/enterprise/support-and-resources/billing/) - Understand team billing and seat management
# Workspaces for Enterprise teams
Canonical page: [/enterprise/team-management/workspaces/](https://docs.warp.dev/enterprise/team-management/workspaces/)
> Workspaces group teams under one Enterprise account with shared membership, billing, SSO, and company-wide settings.
A workspace groups one or more teams under a single Enterprise account. Workspace admins manage membership, billing, and company-wide policies across those teams. Single Sign-On (SSO) is configured at the workspace level.
## Workspaces and teams
[Section titled “Workspaces and teams”](#workspaces-and-teams)
A workspace provides company-wide administration, while teams organize shared resources and team-level settings.
* **Workspace level** - Billing, SSO, domain capture, and organization-wide policies apply across teams.
* **Team level** - Members share Warp Drive resources, cloud agent runs, environments, and secrets.
* **Membership** - A user belongs to one workspace and can belong to multiple teams within it.
## Workspace roles
[Section titled “Workspace roles”](#workspace-roles)
Every workspace member has one of three roles:
* **Member** - Uses Warp within their teams and the policies admins configure.
* **Admin** - Manages workspace membership, billing, and settings. Admins can view and manage every team, including teams they don’t belong to.
* **Owner** - Has every admin capability and can transfer ownership to another member. Each workspace has one owner.
In team member lists, the **Workspace admin** and **Workspace owner** badges distinguish workspace roles from team roles.
## Teams inside a workspace
[Section titled “Teams inside a workspace”](#teams-inside-a-workspace)
Workspace admins create teams from the Admin Panel and choose a visibility:
* **Open** - Any workspace member can see the team and join it immediately.
* **Hidden** - The team doesn’t appear in team discovery; an admin adds members directly.
Workspace admins can also manage every team’s membership and settings.
## Joining a workspace or team
[Section titled “Joining a workspace or team”](#joining-a-workspace-or-team)
Workspace admins add users through invitations or domain capture:
* **Workspace invite links** - Add a user to the workspace and let them choose an Open team.
* **Team invite links** - Add a user to an Open team and its workspace.
* **Email invites** - Add a user directly to a workspace or team. Admins add users to Hidden teams this way.
* **Domain capture** - Automatically adds users who sign up with a verified company domain.
* **Team discovery** - Shows Open teams to unassigned users in the Warp app under **Settings** > **Teams**.
## Unassigned users
[Section titled “Unassigned users”](#unassigned-users)
An unassigned user belongs to the workspace but not to a team. Workspace admins can manage unassigned users and set a separate per-user spend limit for them in the Admin Panel.
Unassigned users cannot start cloud agent or factory runs until they join a team. Workspace-level billing and policies still apply to them.
## Workspace settings and team settings
[Section titled “Workspace settings and team settings”](#workspace-settings-and-team-settings)
Workspace admins configure company-wide policies in the [Admin Panel](/enterprise/team-management/admin-panel/). For supported settings, they can enforce a value across the workspace or select **Respect Team Setting** to let each team decide.
SSO and domain capture apply at the workspace level. When a workspace admin enforces a setting, team admins see it as locked.
## Workspace spend limits
[Section titled “Workspace spend limits”](#workspace-spend-limits)
Workspace admins can set monthly limits for total, local agent, and cloud agent spending. They can also set a separate per-user limit for unassigned users. Team and individual limits remain independent, and the first applicable limit reached blocks further usage within its scope.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Team management](/enterprise/team-management/teams/) - Create and manage teams
* [Admin Panel](/enterprise/team-management/admin-panel/) - Configure settings enforced across a workspace or team
* [Roles and permissions](/enterprise/team-management/roles-and-permissions/) - Team-level roles and what each can do
* [Single Sign-On (SSO)](/enterprise/security-and-compliance/sso/) - Configure authentication for a workspace
* [Enterprise billing](/enterprise/support-and-resources/billing/) - Credit pools, spend limits, and billing management
# Warp Factories overview
Canonical page: [/factories/](https://docs.warp.dev/factories/)
> Warp Factories is open infrastructure for building internal software factories as code, from triage to implementation, review, and monitoring.
Note
Warp Factories is in **Early Access** and available to a limited set of teams. [Request access](https://www.warp.dev/factories/request-access) to use it with your team. If your team already has access, sign in to the [Warp Factories web app](https://platform.warp.dev).
A factory is a group of agents that shares repositories and delivery policy. Its foreman accepts work from connected tools, dispatches the right agents, and returns the result to the source.

## What is a software factory?
[Section titled “What is a software factory?”](#what-is-a-software-factory)
Each request becomes a work item, such as an issue, ticket, or triggered task. Specialized agents can triage it, write a specification, implement the change, and review the result.
Each factory applies a single policy across its work sources, so deploy separate factories for repository groups that need different policies.
### Sizing a factory
[Section titled “Sizing a factory”](#sizing-a-factory)
Size factories by product surface, not by workflow. Group the repositories that ship together into one factory. For example:
* One factory for your main application
* One factory for your marketing site
* One factory for your data pipelines
Don’t split those same repositories across multiple factories by team or task (frontend vs. platform, for example). Add [agents](/factories/factory-agents/) and [skills](/factories/factory-skills/) to specialize instead.
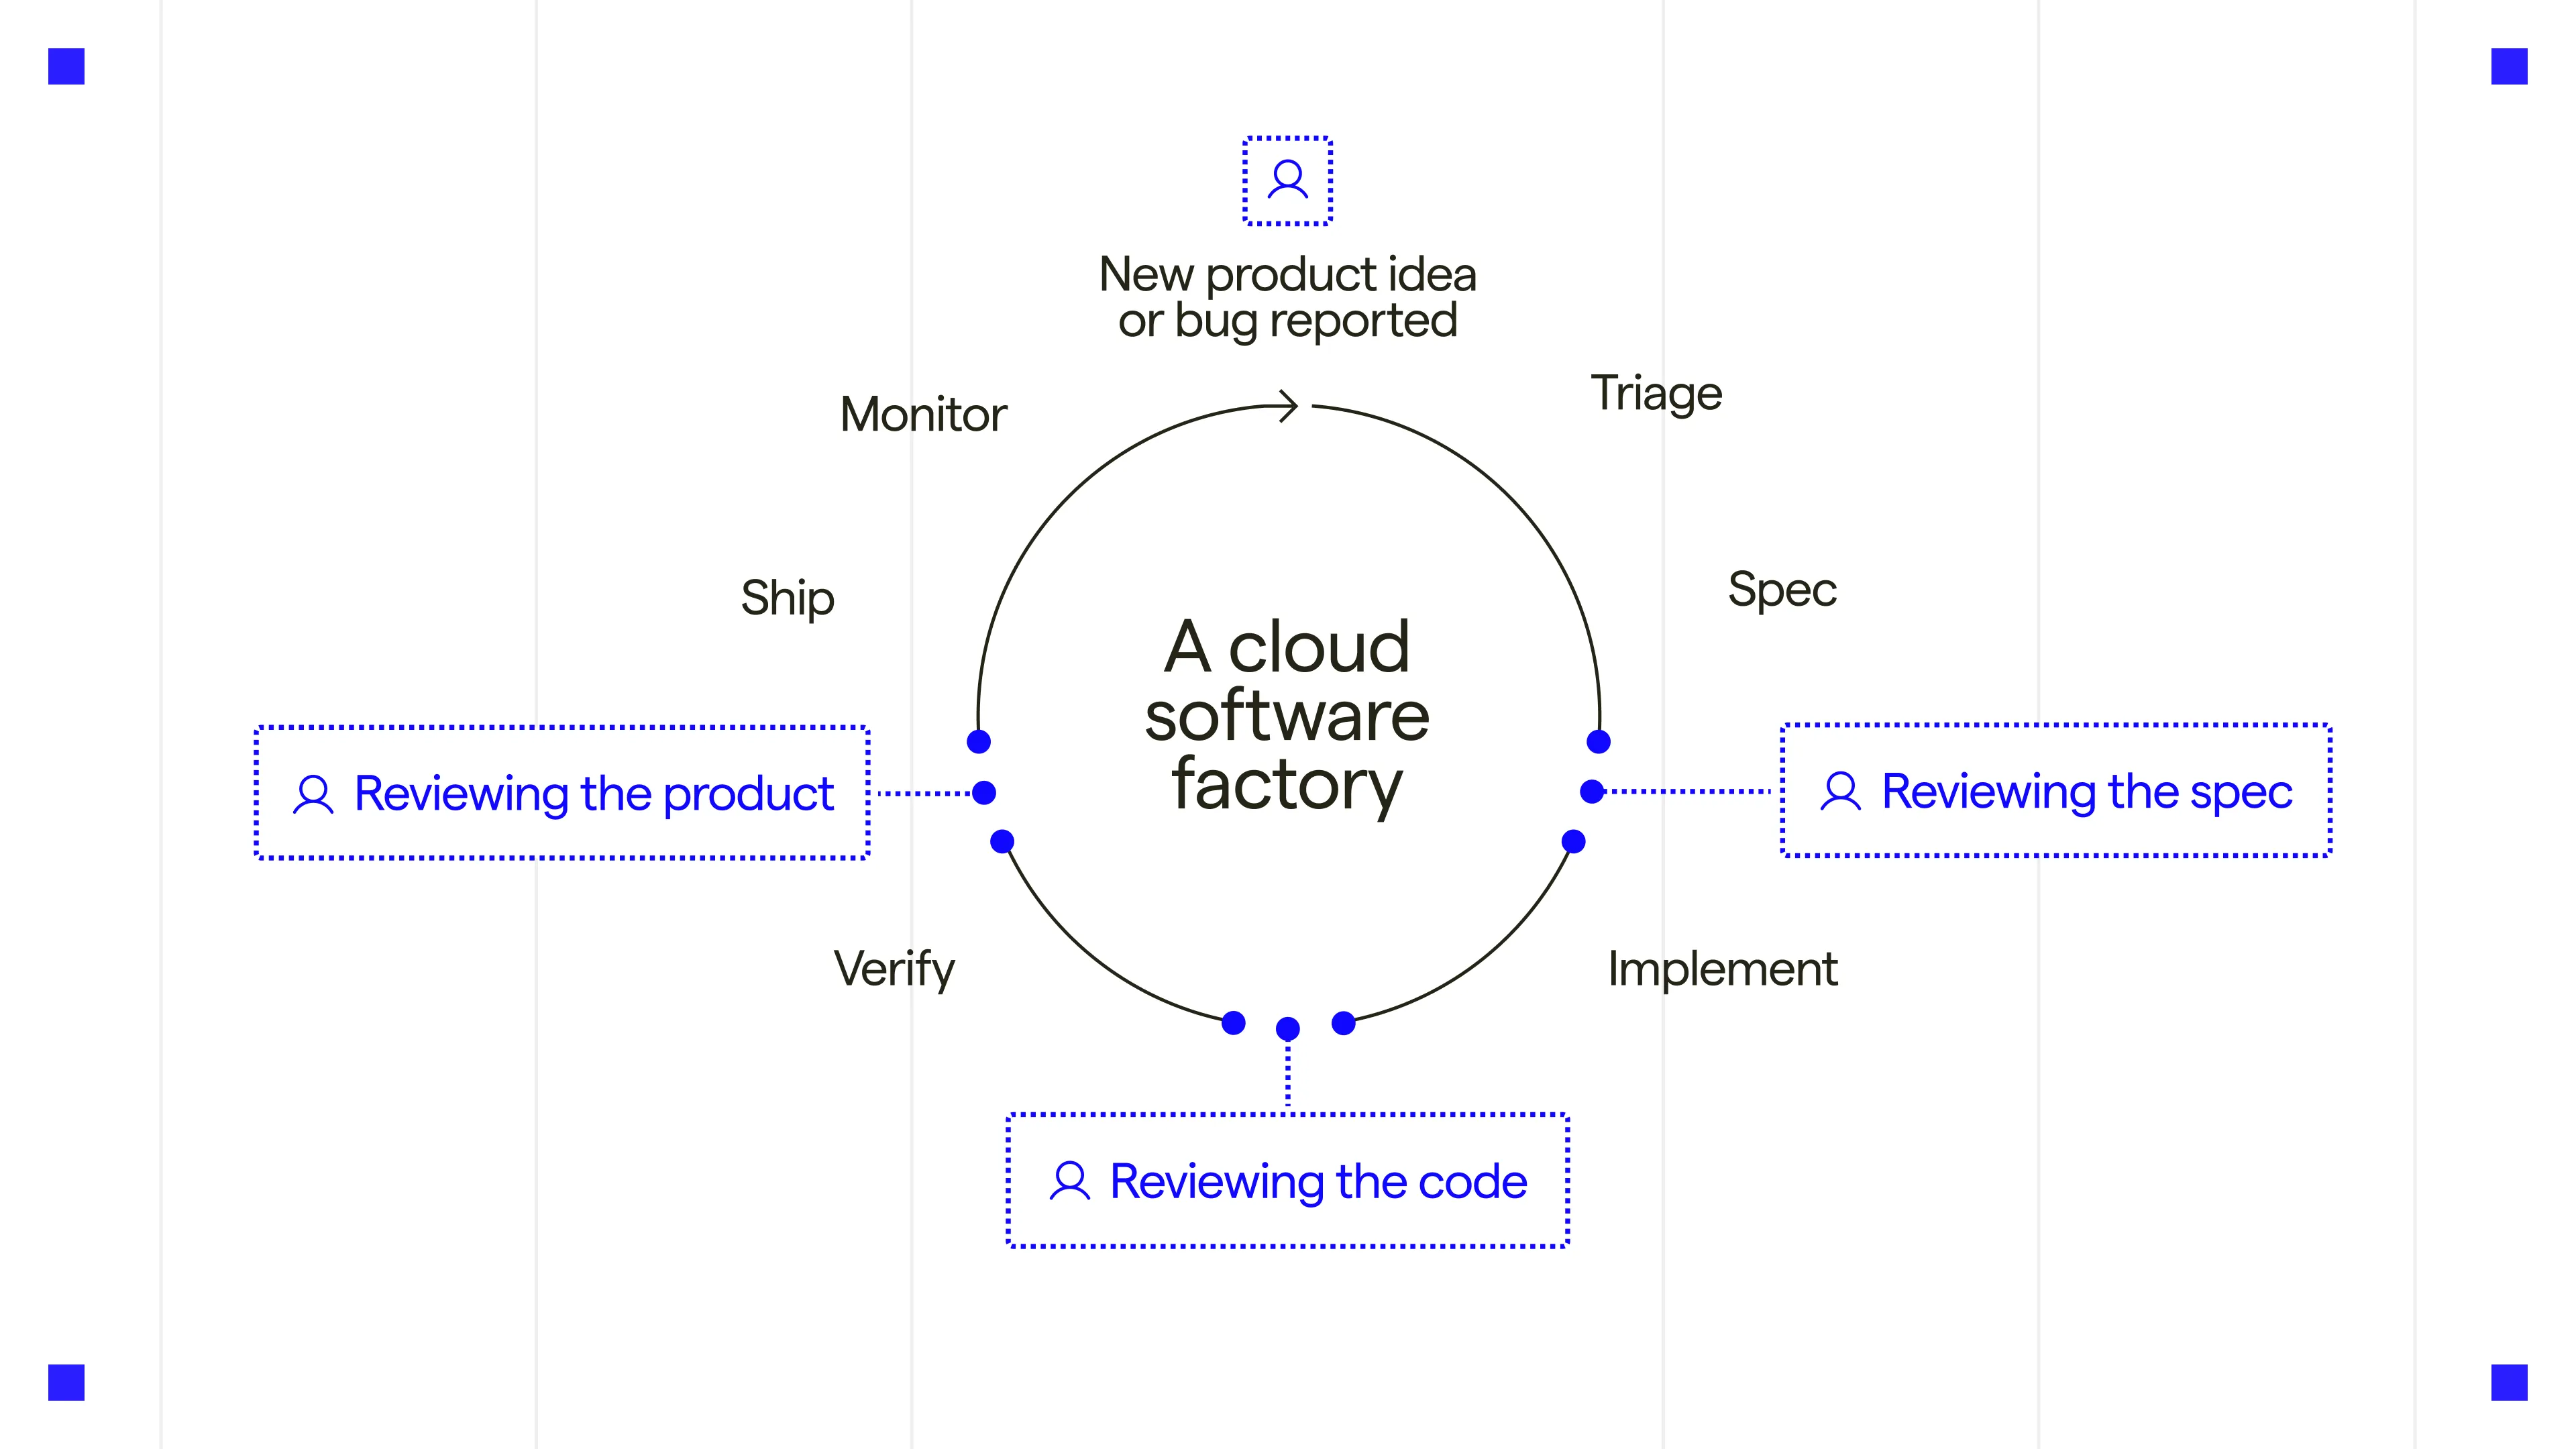
The general software factory loop. Warp Factories’ default agents cover triage through review; add custom agents for the rest.
## Who benefits from Warp Factories
[Section titled “Who benefits from Warp Factories”](#who-benefits-from-warp-factories)
Warp Factories is for engineering teams with repeatable work that extends beyond one coding session:
* Process a backlog of issues with a consistent triage and delivery policy.
* Fix defects reported through support channels.
* Review incoming pull requests or maintain services across repositories.
## What you get with Warp Factories
[Section titled “What you get with Warp Factories”](#what-you-get-with-warp-factories)
* **Coordinated specialist agents** - A team of [factory agents](/factories/factory-agents/) handles each work item. A coordinating foreman routes it through the triage, spec, implement, and review agents, skipping stages that don’t apply. You can add custom agents and automations to handle work the defaults don’t cover.
* **Definitions as code** - [Version-controlled definition files](/factories/factory-as-code/) describe your repositories, agents, automations, runners, [skills](/factories/factory-skills/), and MCP servers, so factory changes get the same review, history, and rollback as code changes.
* **Code forges and work sources** - Connect [GitHub](/factories/integrations/github/), [GitLab](/factories/integrations/gitlab/), [Azure DevOps](/factories/integrations/azure-devops/), or [another code forge](/factories/code-forges/other-code-forges/) to the repository your factory works in. Route work from [Slack](/factories/integrations/slack/), [Linear](/factories/integrations/linear/), [Jira](/factories/integrations/jira/), [custom webhooks](/factories/webhooks/), direct runs, or schedules. The [Factory MCP](/factories/factory-mcp/) connects coding agents and other MCP clients.
* **Model and harness choice** - Each agent can use a different model and [supported harness](/platform/harnesses/), including the Warp Agent, Claude Code, and Codex.
* **Measurement and self-improvement** - The [factory dashboard](/factories/factory-dashboard/) shows work-item status, runs, automations, costs, and benchmarks. [Scorers](/factories/measure-and-improve/scorers/) classify completed runs, [Benchmarks](/factories/benchmarks/) compare fixed tasks across configurations, and [Self-improvement](/factories/measure-and-improve/self-improvement/) turns repeated failures into follow-up work the factory proposes for review.
* **Infrastructure control** - Choose Warp-hosted execution, or use managed self-hosted execution on an eligible Enterprise plan. The [infrastructure and security](/factories/infrastructure-and-security/) page compares execution models and links to the self-hosting setup path, as well as available inference and credential controls.
## How Warp Factories fits into Warp
[Section titled “How Warp Factories fits into Warp”](#how-warp-factories-fits-into-warp)
Warp Factories builds on the same agent infrastructure used across Warp. Every factory agent produces a standard [cloud agent run](/platform/), so the same APIs, runners, models, security controls, and observability apply.
| Product | Role |
| ------------------ | ---------------------------------------------------------------------------------- |
| **Warp** | The interactive development experience for local work with agents and code review. |
| **Warp Agent** | The built-in agent harness that can power an individual factory agent. |
| **Warp Factories** | Multi-agent workflows for software development. |
## Key terms
[Section titled “Key terms”](#key-terms)
Setup gives a factory and its foreman the same name by default, so it’s easy to mistake one for the other. Here’s how the terms differ:
* **factory** - The repositories, delivery policy, agents, and connected tools that handle a related set of work. It is distinct from Warp Factories, the product, and from the foreman, its coordinating agent.
* **foreman** - The coordinating agent inside a factory, and the only one you talk to. It dispatches the other [factory agents](/factories/factory-agents/) and reports back. Every factory has exactly one.
* **Foreman name** - The handle your team @-mentions in Slack and Linear to reach the foreman. Setup copies it from the factory’s name, so the two usually match even though they’re different things. See [Foreman name](/factories/factory-agents/#foreman-name).
```
flowchart LR
subgraph Factory["One factory"]
Foreman["Foreman"] --> Agents["Triage, spec, implement,<br/>and review agents"]
end
Slack["Slack or Linear"] -->|"@handle"| Foreman
```
## Related pages
[Section titled “Related pages”](#related-pages)
* [**Set up a factory**](/factories/quickstart/) - Create a factory and send its first work item.
* [**Understand the execution model**](/factories/how-factories-work/) - See how the foreman coordinates stages, runs, and human decisions.
* [**Meet the factory agents**](/factories/factory-agents/) - See what each agent does and how to configure its model, harness, and instructions.
* **Adapt the system** - [Define the factory as code](/factories/factory-as-code/) and [connect its work sources](/factories/connect-your-factory/), or start from a working definition in [warp-factory-examples](https://github.com/warpdotdev/warp-factory-examples).
# Agent & run endpoints
Canonical page: [/factories/api-and-sdk/](https://docs.warp.dev/factories/api-and-sdk/)
> Start, manage, and inspect cloud agent runs with the Agent and run endpoints in the Warp Platform API.
Agent & run endpoints are part of the Warp Platform API. Use them to start standalone cloud agent runs and to monitor, continue, or cancel any run after it starts. To find a factory and send it new work, use [factory endpoints](/factories/factory-api/).
Note
Some examples use `oz` commands, such as `oz environment list`, from the Oz CLI. Existing commands remain supported during the transition.
## Use Agent & run endpoints
[Section titled “Use Agent & run endpoints”](#use-agent--run-endpoints)
Agent & run endpoints let you create and inspect [cloud agent](/platform/) runs over HTTP from CI, cron, backend services, and internal tools, without requiring the Warp desktop app.
**With the API you can:**
* Run an agent by submitting a prompt plus optional config (model, environment, MCP servers, base prompt, etc.)
* Monitor execution by listing runs and tracking state transitions over time (queued → in progress → succeeded/failed)
* Inspect results and provenance by fetching a run’s full details, including the original prompt, source/creator metadata, session link, and resolved agent configuration
For endpoint details, use the [**Warp Platform API reference**](/api). For SDK schemas, use the [Python SDK](https://github.com/warpdotdev/oz-sdk-python) and [TypeScript SDK](https://github.com/warpdotdev/oz-sdk-typescript) repositories.
To send work to a [Warp factory](/factories/), use [factory endpoints](/factories/factory-api/) to discover it and dispatch by UID instead of calling `POST /agent/runs` with a foreman’s `agent_identity_uid`. The follow-up, cancellation, and status endpoints still apply after a factory run is dispatched.
## Choose the SDK or raw REST
[Section titled “Choose the SDK or raw REST”](#choose-the-sdk-or-raw-rest)
Warp provides official [Python](https://github.com/warpdotdev/oz-sdk-python) and [TypeScript](https://github.com/warpdotdev/oz-sdk-typescript) SDKs that wrap the Warp Platform API with:
* **Typed requests and responses** (editor autocomplete, fewer schema mistakes)
* **Built-in retries and timeouts** (with per-request overrides)
* [**Consistent error types**](/factories/api-and-sdk/troubleshooting/errors/) that map to API status codes
* **Helpers for raw responses** when you need headers/status or custom parsing
If you’re building an integration (CI, Slack bots, internal tooling, orchestrators), the SDKs are typically the quickest and safest starting point.

**SDK vs raw REST**
* Use the SDK when you want strong typing, standardized error handling, and easy concurrency patterns.
* Use raw REST when you want minimal dependencies or full control over your HTTP client (the SDKs also support calling undocumented endpoints when needed).
***
## API base URL
[Section titled “API base URL”](#api-base-url)
All endpoints are served over HTTPS:
```http
https://app.warp.dev/api/v1
```
### Agent runs
[Section titled “Agent runs”](#agent-runs)
An agent run represents a single execution of a cloud agent, created with a prompt and optional configuration. Each run has:
* A unique `run_id`
* A human-readable `title`
* A `prompt` that the agent executes
* A `state` (for example `QUEUED`, `INPROGRESS`, `SUCCEEDED`, `FAILED`)
* Timestamps (`created_at`, `updated_at`)
* Optional session information (`session_id`, `session_link`)
* Optional resolved configuration (`agent_config`)
See the [**Warp Platform API reference**](/api) for details on how runs are created and listed.
### Agent configuration
[Section titled “Agent configuration”](#agent-configuration)
You can influence how an agent runs using AmbientAgentConfig, including:
* `name` — a human-readable label for grouping, filtering, and traceability. When you run an agent from a [skill](/agents/capabilities/skills/), `name` is automatically set to the skill name. You can also set `name` explicitly via the API, SDK, or CLI (`--name`) to categorize runs by intent — for example, grouping all runs of a particular workflow regardless of how they were triggered. Use the `name` query parameter on `GET /agent/runs` to filter runs by config name.
* `model_id` for LLM selection
* `base_prompt` to shape behavior
* `environment_id` to choose a `CloudEnvironment`
* `worker_host` to run a standalone cloud agent on a [self-hosted worker](/factories/self-hosting/)
* `skill_spec` to use a [skill](/agents/capabilities/skills/) as the base prompt (format: `owner/repo:skill-name` or `owner/repo:path/to/SKILL.md`)
* `mcp_servers` to enable specific tools via MCP
See the [**Python SDK**](https://github.com/warpdotdev/oz-sdk-python) or [**TypeScript SDK**](https://github.com/warpdotdev/oz-sdk-typescript) for the full configuration schema.
#### Skill actions in conversation data
[Section titled “Skill actions in conversation data”](#skill-actions-in-conversation-data)
The Conversation API returns skill loads as `read_skill` actions. When `input.bundled_skill_id` is present, it identifies a Warp-provided bundled reference. `input.skill_path` is the path used to resolve a skill, but doesn’t prove ownership: file-based skills and path-referenced bundled skills, including skills from a remote host, can both use this field.
The following stable, user-facing IDs are bundled directly with Warp:
| Bundled skill ID | Purpose |
| ------------------- | ----------------------------------------------------------------- |
| `add-mcp-server` | Add an MCP server to Warp configuration. |
| `change-keybinding` | Change or remove Warp keyboard shortcuts. |
| `claude-api` | Build and maintain applications that use the Anthropic SDK. |
| `create-skill` | Create, improve, and evaluate skills. |
| `create-tab-config` | Create a Warp tab configuration. |
| `factory-files` | Create and validate file-based Warp factory definitions. |
| `factory-mcp` | Send work to a factory and collaborate through Factory MCP. |
| `modify-settings` | View or change Warp settings using the bundled settings schema. |
| `oz-platform` | Run, configure, and inspect cloud agents through the API and CLI. |
| `pr-comments` | Fetch GitHub pull request review comments for the current branch. |
| `tab-configs` | Look up the tab configuration schema and validation rules. |
| `tui-migrate-setup` | Migrate supported settings into the Warp Agent CLI. |
| `update-tab-config` | Update an existing Warp tab configuration. |
| `warpctrl` | Control and inspect a running Warp app with Warp Control. |
The catalog helps group usage across conversations; it isn’t an availability manifest. Use each run’s advertised skills for availability and its conversation’s `read_skill` actions for invocation. The bundled set can vary by Warp release, release channel, enabled features, required files, and connected integrations.
For example, `oz-platform`, `factory-files`, and `factory-mcp` are Warp-provided. `factory-mcp` appears only where Factory MCP is available, `tui-migrate-setup` is specific to the Warp Agent CLI, and connected integrations can add bundled IDs that aren’t listed here.
***
## Route a run to a self-hosted worker
[Section titled “Route a run to a self-hosted worker”](#route-a-run-to-a-self-hosted-worker)
Set `worker_host` in the request configuration to select a connected self-hosted worker. Omit it, or set it to `warp`, to use Warp-hosted workers.
```json
{
"prompt": "Run the dependency audit",
"config": {
"worker_host": "WORKER_HOST"
}
}
```
Replace `WORKER_HOST` with the ID of a connected worker. For factory work, set `workerHost` in the [factory definition](/factories/factory-as-code/#agentdefaultsworkerhost) instead.
## Key endpoints
[Section titled “Key endpoints”](#key-endpoints)
Agent & run endpoints include:
* `POST /agent/runs`
Create a new agent run with a prompt and optional config and title. Returns run\_id and initial state.
* `GET /agent/runs`
List runs with pagination and filters for state, config\_name, model\_id, creator, source, and creation time.
* `GET /agent/runs/{runId}`
Fetch full details for a single run, including session link and resolved configuration.
* `POST /agent/runs/{runId}/followups`
Send a follow-up message to an existing run to steer or continue it, the same capability the Slack and Linear integrations use.
* `POST /agent/runs/{runId}/cancel`
Cancel a run that is currently queued or in progress. Returns the ID of the cancelled run.
All endpoint semantics, query parameters, and [error codes](/factories/api-and-sdk/troubleshooting/errors/) are documented in the [Warp Platform API reference](/api).
***
## Models
[Section titled “Models”](#models)
The API shares a set of reusable models across endpoints. Detailed JSON schemas, types, and enums are available in the SDK repos ([Python](https://github.com/warpdotdev/oz-sdk-python), [TypeScript](https://github.com/warpdotdev/oz-sdk-typescript)). Key models include:
* `RunAgentRequest`
* `RunAgentResponse`
* `ListRunsResponse`
* `RunItem`
* `PageInfo`
* `RunStatusMessage`
* `RunCreatorInfo`
* `RunState`
* `RunSourceType`
* `RunFollowupRequest`
* `AmbientAgentConfig`
* `MCPServerConfig`
* `Error`
***
## SDKs
[Section titled “SDKs”](#sdks)
### Python SDK
[Section titled “Python SDK”](#python-sdk)
The Python SDK is the recommended way to call the API from Python services and scripts. It provides:
* Sync + async clients
* Typed request/response models
* Configurable retries/timeouts and structured errors
See the [**Python SDK GitHub repo**](https://github.com/warpdotdev/oz-sdk-python) for installation, full API reference (api.md), and up-to-date examples.
### TypeScript SDK
[Section titled “TypeScript SDK”](#typescript-sdk)
The TypeScript SDK is the recommended way to call the API from Node.js services and modern TS/JS runtimes. It provides:
* Fully typed params/responses
* First-class error handling, retries/timeouts
* Support across common runtimes where fetch is available or polyfilled
See the [**TypeScript SDK GitHub repo**](https://github.com/warpdotdev/oz-sdk-typescript) for installation, full API reference (api.md), and up-to-date examples.
# Demo: Sentry monitoring with SDK
Canonical page: [/factories/api-and-sdk/demo-sentry-monitoring-with-sdk/](https://docs.warp.dev/factories/api-and-sdk/demo-sentry-monitoring-with-sdk/)
> Build a Sentry webhook handler that triggers agents to investigate errors and create draft PRs.
### Turn production errors into draft PRs with Cloud Agents + TypeScript SDK
[Section titled “Turn production errors into draft PRs with Cloud Agents + TypeScript SDK”](#turn-production-errors-into-draft-prs-with-cloud-agents--typescript-sdk)

Note
Example repository: [**Sentry monitor example repository**](https://github.com/warpdotdev/warp-agents-sdk-demo-sentry-monitor)
In this demo, Ben builds a small TypeScript “Sentry monitor” service that listens for specific Sentry alerts (like a Go nil pointer dereference) and triggers a Warp cloud agent to investigate. The server validates the webhook, extracts the stack trace, and injects it into an agent run inside a Warp Environment so the agent can inspect the repo and propose a fix.
To route the alert through a factory’s named agents and workflow instead, use [factory endpoints](/factories/factory-api/) to dispatch the request. This example remains useful for custom standalone cloud-agent intake.
He also covers the task lifecycle basics in the TypeScript SDK (running an agent, polling task state to fetch a session link for debugging), and shows the end result: a draft GitHub pull request created from the Sentry event for a maintainer to review.
**What Ben covers**
* Using Warp’s TypeScript SDK to trigger agent runs and retrieve run details.
* Handling run lifecycle states (queued → running) to reliably fetch a session link.
* Running agents inside a Warp Environment so they can investigate real code, run tests, and validate fixes.
* Building a lightweight Sentry webhook server that filters, validates, and routes only the right errors to an agent.
* Creating a workflow that results in draft PRs for human review, instead of silent autonomous changes.
# Warp Platform API quickstart
Canonical page: [/factories/api-and-sdk/quickstart/](https://docs.warp.dev/factories/api-and-sdk/quickstart/)
> Create and monitor your first cloud agent run via the Warp Platform API in ~5 minutes.
The Warp Platform API lets you run and manage cloud agents from CI/CD pipelines, backend services, scripts, or custom tooling without the Warp desktop app. This quickstart walks you through creating your first run and checking its status.
To dispatch work through a factory’s named agents and workflow, use [factory endpoints](/factories/factory-api/) after this quickstart. The run-management steps below also apply to the factory run those endpoints create.
Watch this short demo of how the REST API can power agent-backed apps like [PowerFixer](https://github.com/warpdotdev/power-fixer-setup), an issue triage bot built by the Warp team:

***
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **A Warp API key** - Create one in the [Oz web app](https://oz.warp.dev/settings) and copy the raw value. Use a personal key if you want runs attributed to you, or an agent key to attribute runs to a [cloud agent](/platform/agents/). See [API Keys](/agents/cli/oz-cli/api-keys/) for the full flow.
* **A cloud environment** - Agents run inside a configured environment that includes repos and other dependencies. If you don’t have an environment yet, follow the [Cloud Agents Quickstart](/platform/quickstart/) first.
***
## 1. Set your API key
[Section titled “1. Set your API key”](#1-set-your-api-key)
Export your API key so the API can authenticate your requests automatically — all commands in this guide reference the `WARP_API_KEY` environment variable.
```bash
export WARP_API_KEY="wk-..."
```
Replace `wk-...` with the key you created earlier.
## 2. Create your first run
[Section titled “2. Create your first run”](#2-create-your-first-run)
Submit a prompt to start an agent run:
```bash
curl -X POST https://app.warp.dev/api/v1/agent/runs \
-H "Authorization: Bearer $WARP_API_KEY" \
-H "Content-Type: application/json" \
-d '{
"prompt": "Scan the repo for outdated dependencies and summarize the findings.",
"config": {
"environment_id": "<ENV_ID>"
}
}'
```
Replace `<ENV_ID>` with your environment ID. Find it with `oz environment list` on the Oz CLI or in the [Oz web app](https://oz.warp.dev).
Note
Prefer typed requests? The official [Python SDK](https://github.com/warpdotdev/oz-sdk-python) and [TypeScript SDK](https://github.com/warpdotdev/oz-sdk-typescript) wrap the same API with typed models, retries, and error handling.
The API returns a `run_id` immediately. The agent starts asynchronously — you can check its status at any time using the run ID.
## 3. Check run status
[Section titled “3. Check run status”](#3-check-run-status)
Fetch the current state of the run with the following command. Replace `<RUN_ID>` with the `run_id` from step 2.
```bash
curl "https://app.warp.dev/api/v1/agent/runs/<RUN_ID>" \
-H "Authorization: Bearer $WARP_API_KEY"
```
The `state` has the following possible values:
* `QUEUED` - The run is waiting to start.
* `INPROGRESS` - The agent is actively running.
* `SUCCEEDED` - The run completed successfully.
* `FAILED` - The run encountered an error. Check the `status_message` field in the response for details, then use the [API error reference](/factories/api-and-sdk/troubleshooting/errors/) to interpret the error code.
These are the most common states. See the [Agent & run endpoints](/factories/api-and-sdk/) and [Warp Platform API reference](/api) for all possible values.
To list all recent runs:
```bash
curl "https://app.warp.dev/api/v1/agent/runs" \
-H "Authorization: Bearer $WARP_API_KEY"
```
## 4. View the results
[Section titled “4. View the results”](#4-view-the-results)
Once the run reaches `SUCCEEDED`, the response includes a `session_link` — a direct URL to the full run transcript, including commands executed, files changed, and agent output.
You can also view and manage all runs in the [cloud agent dashboard](https://oz.warp.dev/runs).
***
## Next steps
[Section titled “Next steps”](#next-steps)
* **Read the endpoint guide** - [Agent & run endpoints](/factories/api-and-sdk/) documents the configuration and run lifecycle, while the [Warp Platform API reference](/api) lists all parameters, query filters, and response schemas.
* **Explore the SDKs** - [Python SDK](https://github.com/warpdotdev/oz-sdk-python) and [TypeScript SDK](https://github.com/warpdotdev/oz-sdk-typescript) include typed request/response models, retries, and error handling.
* **See a real-world example** - [Demo: Sentry monitoring with SDK](/factories/api-and-sdk/demo-sentry-monitoring-with-sdk/) shows how to build a webhook handler that triggers agents from production errors.
* **Schedule and automate** - See [Scheduled Agents Quickstart](/platform/triggers/scheduled-agents-quickstart/) to run agents on a cron, or [Integrations Quickstart](/platform/integrations/quickstart/) to trigger agents from Slack or Linear.
# API errors
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/)
> Reference for all error codes returned by the Warp Platform API. Each error includes an HTTP status, machine-readable code, and actionable resolution steps.
When the Warp Platform API encounters an error, it returns a structured JSON response following [RFC 7807 (Problem Details for HTTP APIs)](https://datatracker.ietf.org/doc/html/rfc7807). Every error response includes a machine-readable error code, HTTP status, human-readable message, and resolution details.
***
## Response format
[Section titled “Response format”](#response-format)
All error responses share this structure:
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/invalid-request/",
"title": "The request contains invalid or missing parameters.",
"status": 400,
"detail": "schedule_id is required",
"instance": "/api/v1/agent/tasks",
"error": "The request contains invalid or missing parameters. (schedule_id is required)",
"retryable": false,
"trace_id": "abc123def456..."
}
```
Error responses use the `application/problem+json` content type per RFC 7807.
### Field reference
[Section titled “Field reference”](#field-reference)
* **`type`** — A URI identifying the error type. Links to the documentation page for that error.
* **`title`** — A short, human-readable summary of the problem.
* **`status`** — The HTTP status code for this response.
* **`detail`** — Additional context specific to this occurrence of the error. Not always present.
* **`instance`** — The request path that produced the error.
* **`error`** — A backward-compatible field combining `title` and `detail` (for older clients). When `detail` is present, formatted as `"title (detail)"`.
* **`retryable`** — Whether this request can be retried. If `true`, the platform may automatically retry the operation.
* **`trace_id`** — An OpenTelemetry trace ID, included when available. Reference this when contacting support.
Some errors include additional metadata fields (for example, `auth_url`, `provider`, or `inaccessible_repos`). These are documented on each error’s page.
***
## Error categories
[Section titled “Error categories”](#error-categories)
Errors are split into two categories based on what caused the failure:
### User errors
[Section titled “User errors”](#user-errors)
These indicate something the caller needs to fix. When a cloud agent task encounters a user error, the task transitions to the **FAILED** state.
* [`insufficient_credits`](/factories/api-and-sdk/troubleshooting/errors/insufficient-credits/) — Team has no remaining add-on credits
* [`feature_not_available`](/factories/api-and-sdk/troubleshooting/errors/feature-not-available/) — Feature not included in your current plan
* [`external_authentication_required`](/factories/api-and-sdk/troubleshooting/errors/external-authentication-required/) — External service authorization needed
* [`not_authorized`](/factories/api-and-sdk/troubleshooting/errors/not-authorized/) — Insufficient permissions for the operation
* [`invalid_request`](/factories/api-and-sdk/troubleshooting/errors/invalid-request/) — Malformed request or invalid parameters
* [`resource_not_found`](/factories/api-and-sdk/troubleshooting/errors/resource-not-found/) — Referenced resource does not exist
* [`budget_exceeded`](/factories/api-and-sdk/troubleshooting/errors/budget-exceeded/) — Spending budget limit reached
* [`integration_disabled`](/factories/api-and-sdk/troubleshooting/errors/integration-disabled/) — Integration is disabled
* [`integration_not_configured`](/factories/api-and-sdk/troubleshooting/errors/integration-not-configured/) — Integration setup is incomplete
* [`operation_not_supported`](/factories/api-and-sdk/troubleshooting/errors/operation-not-supported/) — Operation not supported for this resource or state
* [`environment_setup_failed`](/factories/api-and-sdk/troubleshooting/errors/environment-setup-failed/) — Cloud agent environment failed to initialize
* [`content_policy_violation`](/factories/api-and-sdk/troubleshooting/errors/content-policy-violation/) — Task flagged by content policy checks
* [`conflict`](/factories/api-and-sdk/troubleshooting/errors/conflict/) — Request conflicts with the current resource state (retryable)
### Platform errors
[Section titled “Platform errors”](#platform-errors)
These indicate a Warp-side issue. When a cloud agent task encounters a platform error, the task transitions to the **ERROR** state. Retryable errors are automatically retried before the task is marked as failed.
* [`authentication_required`](/factories/api-and-sdk/troubleshooting/errors/authentication-required/) — Invalid or expired API key
* [`resource_unavailable`](/factories/api-and-sdk/troubleshooting/errors/resource-unavailable/) — Transient infrastructure issue (retryable)
* [`internal_error`](/factories/api-and-sdk/troubleshooting/errors/internal-error/) — Unexpected server-side error (retryable)
* [`infrastructure_timeout`](/factories/api-and-sdk/troubleshooting/errors/infrastructure-timeout/) — Task terminated after exceeding the maximum allowed runtime
* [`agent_process_failed`](/factories/api-and-sdk/troubleshooting/errors/agent-process-failed/) — Agent process exited unexpectedly during task execution
***
## Using the `trace_id`
[Section titled “Using the trace\_id”](#using-the-trace_id)
When an error response includes a `trace_id`, you can include it when [contacting Warp support](/support-and-community/troubleshooting-and-support/sending-us-feedback/) to help the team locate the specific request in internal logs. This is especially useful for `internal_error` and `resource_unavailable` errors.
***
## Related
[Section titled “Related”](#related)
* [Warp Platform API](/factories/api-and-sdk/) — API reference for creating and managing agent tasks
* [Cloud Agents Overview](/platform/) — How cloud agents work
* [Access, Billing, and Identity](/platform/team-access-billing-and-identity/) — Plan requirements and billing details
# agent_process_failed
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/agent-process-failed/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/agent-process-failed/)
> The agent process exited unexpectedly during task execution. Retry the task or contact support if it recurs consistently.
The `agent_process_failed` error occurs when the agent process exits unexpectedly after environment setup has completed, before the task reaches a normal terminal state.
Note
This is classified as a **platform error** (task state → ERROR) rather than a user error. It differs from [`environment_setup_failed`](/factories/api-and-sdk/troubleshooting/errors/environment-setup-failed/), which covers failures that happen while initializing the environment (cloning the repo, running setup commands, starting MCP servers). `agent_process_failed` covers failures that happen during the agent’s active execution phase.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `500 Internal Server Error`
* **Retryable:** No
* **Task State:** ERROR
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* The agent process exits with a non-zero exit code after environment setup has completed
* An unrecoverable runtime error occurs inside the agent process while it is handling the task
* The agent process is terminated by the operating system (for example, due to an out-of-memory kill or a segmentation fault)
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/agent-process-failed/",
"title": "The agent process exited unexpectedly.",
"status": 500,
"instance": "/api/v1/agent/tasks",
"error": "The agent process exited unexpectedly.",
"retryable": false,
"trace_id": "abc123..."
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
1. Retry the task. Occasional process failures are transient.
2. If the error recurs consistently, look for triggers in the task itself: very large prompts or attached context, memory-heavy tools spawned by the agent, or setup steps that leave the environment in a degraded state.
3. Contact [Warp support](/support-and-community/troubleshooting-and-support/sending-us-feedback/) and include the `trace_id` from the error response if the issue persists.
***
## Related
[Section titled “Related”](#related)
* [Cloud Agents Overview](/platform/) — How cloud agent tasks work
* [environment\_setup\_failed](/factories/api-and-sdk/troubleshooting/errors/environment-setup-failed/) — Errors during environment setup
* [internal\_error](/factories/api-and-sdk/troubleshooting/errors/internal-error/) — Catch-all for unexpected server-side errors
# authentication_required
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/authentication-required/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/authentication-required/)
> The API key in the request is invalid, expired, or missing. Generate a new key and update your client configuration.
The `authentication_required` error occurs when the API request lacks valid authentication credentials.
Note
This is classified as a **platform error** (task state → ERROR) rather than a user error, because it typically indicates a configuration issue with the API key rather than a problem with the task itself.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `401 Unauthorized`
* **Retryable:** No
* **Task State:** ERROR
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* The `Authorization` header is missing from the request
* The API key has been revoked or has expired
* The API key is malformed or invalid
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/authentication-required/",
"title": "Your API key is invalid or has expired. Please generate a new key and try again.",
"status": 401,
"instance": "/api/v1/agent/tasks",
"error": "Your API key is invalid or has expired. Please generate a new key and try again.",
"retryable": false
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
1. Generate a new API key from the [Oz web app](https://oz.warp.dev) or via the Oz CLI.
2. Update your client configuration with the new key.
3. Retry the request.
***
## Related
[Section titled “Related”](#related)
* [Warp Platform API](/factories/api-and-sdk/) — API authentication
* [Automation Platform](/platform/overview/) — API key management
# budget_exceeded
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/budget-exceeded/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/budget-exceeded/)
> Your team's configured spending budget limit has been reached. Increase the budget or wait for the budget period to reset.
The `budget_exceeded` error occurs when your team has reached the spending budget limit configured in team settings.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `403 Forbidden`
* **Retryable:** No
* **Task State:** FAILED
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* Your team has set a spending budget cap, and the current period’s usage has reached that cap
* A cloud agent task, scheduled run, or integration-triggered run attempts to start but would exceed the budget
The `title` field in the response will describe the specific budget constraint.
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/budget-exceeded/",
"title": "Monthly spending budget of $50 has been reached.",
"status": 403,
"instance": "/api/v1/agent/tasks",
"error": "Monthly spending budget of $50 has been reached.",
"retryable": false
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
1. Go to your team settings and increase the spending budget, or
2. Wait for the budget period to reset (for example, at the start of the next billing cycle).
If you are not a team admin, contact your team admin to adjust the budget.
***
## Related
[Section titled “Related”](#related)
* [Access, Billing, and Identity](/platform/team-access-billing-and-identity/) — Budget configuration and billing details
# Error: conflict (409)
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/conflict/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/conflict/)
> The request conflicts with the current state of the resource. Wait for the resource to reach the expected state and retry.
The `conflict` error occurs when a request cannot be completed because the resource is in a state that conflicts with the requested operation.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `409 Conflict`
* **Retryable:** Yes
* **Task State:** FAILED
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* You attempt to cancel a task that is still in the **pending** state (the task has not yet been claimed by a worker)
The operation can typically succeed once the resource transitions to the expected state.
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/conflict/",
"title": "Pending agent runs cannot be cancelled, retry after a moment.",
"status": 409,
"instance": "/api/v1/agent/tasks/abc123/cancel",
"error": "Pending agent runs cannot be cancelled, retry after a moment.",
"retryable": true
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
1. Wait a moment for the resource to transition to the expected state.
2. Retry the request.
For task cancellation specifically, wait until the task moves from **pending** to **in progress** before attempting to cancel.
***
## Related
[Section titled “Related”](#related)
* [Managing Cloud Agents](/platform/managing-cloud-agents/) — Viewing and managing agent tasks
* [Warp Platform API](/factories/api-and-sdk/) — API reference for managing agent tasks
# content_policy_violation
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/content-policy-violation/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/content-policy-violation/)
> The task prompt or environment setup commands were flagged by the platform's automated content policy checks.
The `content_policy_violation` error occurs when the task prompt or environment setup commands are flagged by the platform’s automated content policy checks.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `403 Forbidden`
* **Retryable:** No
* **Task State:** FAILED
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* The task prompt contains content that violates Warp’s usage policies
* The environment setup commands contain patterns flagged as potentially harmful
* The automated content classifier determines the task should be blocked
Note
For security reasons, the error message is intentionally generic and does not describe what specifically was flagged.
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/content-policy-violation/",
"title": "Unable to start cloud agent. Please try again or contact support if the issue persists.",
"status": 403,
"instance": "/api/v1/agent/tasks",
"error": "Unable to start cloud agent. Please try again or contact support if the issue persists.",
"retryable": false,
"trace_id": "abc123..."
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
1. Review your task prompt and environment setup commands to ensure they comply with [Warp’s usage policies](https://www.warp.dev/legal/terms-of-service).
2. If you believe this was flagged in error, contact [Warp support](/support-and-community/troubleshooting-and-support/sending-us-feedback/) and include the `trace_id` from the error response.
***
## Related
[Section titled “Related”](#related)
* [Cloud Agents Overview](/platform/) — How cloud agent tasks work
* [Environments](/platform/environments/) — Configuring setup commands
# environment_setup_failed
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/environment-setup-failed/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/environment-setup-failed/)
> The cloud agent's environment failed to initialize. Check repo URLs, setup commands, and working directory paths.
The `environment_setup_failed` error occurs when the cloud agent’s runtime environment could not be initialized. This covers failures during any phase of environment setup, including repository cloning, setup command execution, working directory resolution, and MCP server startup.
Note
Although this returns HTTP 500, it is classified as a **user error** (task state → FAILED) because the failure is caused by the environment configuration, not by Warp’s infrastructure.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `500 Internal Server Error`
* **Retryable:** No
* **Task State:** FAILED
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when any part of the environment initialization process fails:
* **Git clone failed** — The repository URL is incorrect, the branch does not exist, or the agent does not have access to the repository
* **Setup command failed** — A command in the environment’s setup commands list exited with an error (for example, missing dependencies, script errors)
* **Working directory not found** — The configured working directory does not exist after cloning
* **MCP server startup failed** — An MCP server configured for the environment could not start
The `title` field in the response will describe the specific setup failure.
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/environment-setup-failed/",
"title": "Failed to clone repository: branch 'main' not found in acme/backend",
"status": 500,
"instance": "/api/v1/agent/tasks",
"error": "Failed to clone repository: branch 'main' not found in acme/backend",
"retryable": false
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
1. **Check repository configuration** — Verify the repository URL and branch name in your [environment settings](/platform/environments/). Ensure the repository exists and is accessible.
2. **Check setup commands** — Run the setup commands locally to confirm they work. Look for missing dependencies, incorrect paths, or syntax errors.
3. **Check working directory** — Ensure the working directory path exists relative to the cloned repository root.
4. **Check MCP server configuration** — Verify MCP server startup commands and that any required dependencies or credentials are available. See [MCP Servers for Agents](/agents/cli/oz-cli/mcp-servers/).
5. **Check secrets** — If setup commands reference environment variables from [secrets](/platform/secrets/), verify the secrets are configured and in scope.
***
## Related
[Section titled “Related”](#related)
* [Environments](/platform/environments/) — Configuring cloud agent environments
* [Secrets](/platform/secrets/) — Managing credentials for agent environments
* [MCP Servers for Agents](/agents/cli/oz-cli/mcp-servers/) — Configuring MCP servers
# external_authentication_required
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/external-authentication-required/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/external-authentication-required/)
> The task requires access to an external service (GitHub, Slack, Linear, etc.) that hasn't been authorized. Follow the auth_url to grant access.
The `external_authentication_required` error occurs when a cloud agent task needs access to an external service that the user hasn’t authorized, or when the Warp GitHub App doesn’t have access to the required repositories.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `401 Unauthorized`
* **Retryable:** No
* **Task State:** FAILED
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* **GitHub not connected** — Your Warp account is not linked to a GitHub account, but the task’s environment includes GitHub repositories
* **Repository inaccessible** — The Warp GitHub App is not installed on, or does not have access to, one or more repositories required by the task’s environment
* **Account matching failed** — A Slack or Linear user who triggered the task cannot be matched to a Warp account
***
## Additional metadata fields
[Section titled “Additional metadata fields”](#additional-metadata-fields)
This error includes extra fields beyond the standard response format:
* **`provider`** — The external service name (for example, `"github"`, `"slack"`, `"linear"`)
* **`auth_url`** — A URL to complete the authorization flow (when available)
* **`inaccessible_repos`** — A list of repository names the agent cannot access (when applicable)
***
## Example responses
[Section titled “Example responses”](#example-responses)
### GitHub user not connected
[Section titled “GitHub user not connected”](#github-user-not-connected)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/external-authentication-required/",
"title": "User is not connected to GitHub",
"status": 401,
"instance": "/api/v1/agent/tasks",
"error": "User is not connected to GitHub. Authorize access here: https://...",
"retryable": false,
"provider": "github",
"auth_url": "https://github.com/login/oauth/authorize?..."
}
```
### Repository inaccessible
[Section titled “Repository inaccessible”](#repository-inaccessible)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/external-authentication-required/",
"title": "User does not have access to the following repositories in the environment: acme/backend",
"status": 401,
"detail": "inaccessible repos: acme/backend",
"instance": "/api/v1/agent/tasks",
"error": "User does not have access to the following repositories in the environment: acme/backend (inaccessible repos: acme/backend)",
"retryable": false,
"provider": "github",
"auth_url": "https://github.com/apps/oz-by-warp/installations/new",
"inaccessible_repos": ["acme/backend"]
}
```
### Account matching failed (Slack/Linear)
[Section titled “Account matching failed (Slack/Linear)”](#account-matching-failed-slacklinear)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/external-authentication-required/",
"title": "Unable to locate your Warp account",
"status": 401,
"instance": "/api/v1/agent/tasks",
"error": "Unable to locate your Warp account",
"retryable": false,
"provider": "slack"
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
### GitHub not connected
[Section titled “GitHub not connected”](#github-not-connected)
1. Follow the `auth_url` in the response to connect your GitHub account to Warp.
2. Complete the OAuth authorization flow.
3. Retry the task.
### Repository inaccessible
[Section titled “Repository inaccessible”](#repository-inaccessible-1)
1. Follow the `auth_url` to install or reconfigure the Warp GitHub App.
2. Ensure the app has access to all repositories listed in `inaccessible_repos`.
3. Retry the task.
If you are using an **agent API key** bound to a [cloud agent](/platform/agents/), ensure the Warp GitHub App is installed on the organization that owns the repositories.
### Account matching failed
[Section titled “Account matching failed”](#account-matching-failed)
1. Ensure your Slack or Linear account is associated with the same email as your Warp account.
2. If using Slack, verify the Warp Slack integration is installed in your workspace.
3. Contact your team admin if the issue persists.
***
## Related
[Section titled “Related”](#related)
* [Environments](/platform/environments/) — Configuring GitHub repositories for cloud agent environments
* [Integrations](/platform/integrations/) — Setting up Slack and Linear integrations
# feature_not_available
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/feature-not-available/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/feature-not-available/)
> The requested feature is not included in your current plan. Upgrade your team's plan to access this capability.
The `feature_not_available` error occurs when you attempt to use a feature or capability that is not included in your team’s current plan.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `403 Forbidden`
* **Retryable:** No
* **Task State:** FAILED
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* You attempt to use a feature that requires a higher-tier plan (for example, certain integrations, advanced capabilities, or self-hosted execution)
* A cloud agent or integration trigger tries to access a feature gated behind a plan upgrade
The `title` field in the response will describe the specific feature that is unavailable.
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/feature-not-available/",
"title": "Slack integration requires a Build plan or higher.",
"status": 403,
"instance": "/api/v1/agent/tasks",
"error": "Slack integration requires a Build plan or higher.",
"retryable": false
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
1. Check which plan your team is on in your team’s billing settings.
2. Upgrade to a plan that includes the required feature.
3. Retry the operation.
For plan comparisons and feature availability, see [Access, Billing, and Identity](/platform/team-access-billing-and-identity/).
***
## Related
[Section titled “Related”](#related)
* [Access, Billing, and Identity](/platform/team-access-billing-and-identity/) — Plan requirements and feature availability
* [Integrations](/platform/integrations/) — Integration requirements by plan
# infrastructure_timeout
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/infrastructure-timeout/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/infrastructure-timeout/)
> The task was forcibly terminated because it remained active past the maximum allowed runtime. Retry the task or contact support if it persists.
The `infrastructure_timeout` error occurs when a cloud agent task runs past the platform’s maximum allowed runtime and is forcibly terminated.
Note
This is classified as a **platform error** (task state → ERROR) rather than a user error, because the termination is performed by Warp’s infrastructure rather than by the task itself.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `500 Internal Server Error`
* **Retryable:** No
* **Task State:** ERROR
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* The task runs longer than the platform’s maximum allowed runtime and is terminated by the periodic stale-task cleanup job
* The agent process never reports a terminal status within that window (for example, the process is hung or stuck on a long-running command)
* A networking or infrastructure issue causes the task to stall silently without reporting completion
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/infrastructure-timeout/",
"title": "The task exceeded the maximum allowed runtime and was terminated.",
"status": 500,
"instance": "/api/v1/agent/tasks",
"error": "The task exceeded the maximum allowed runtime and was terminated.",
"retryable": false,
"trace_id": "abc123..."
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
1. Retry the task. If it consistently times out, break the work into smaller, shorter-running subtasks or reduce the scope of the prompt.
2. Review the [environment configuration](/platform/environments/) for setup commands or MCP servers that block on user input, long downloads, or unresponsive network calls.
3. Contact [Warp support](/support-and-community/troubleshooting-and-support/sending-us-feedback/) and include the `trace_id` from the error response if the issue persists.
***
## Related
[Section titled “Related”](#related)
* [Cloud Agents Overview](/platform/) — How cloud agent tasks work
* [internal\_error](/factories/api-and-sdk/troubleshooting/errors/internal-error/) — Other platform-level errors
* [Cloud Agents FAQs](/platform/faqs/) — Common questions about cloud agents
# insufficient_credits
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/insufficient-credits/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/insufficient-credits/)
> The principal billed for the run has no remaining credits. Top up the team's shared add-on credit pool or wait for plan credits to refresh.
The `insufficient_credits` error occurs when the principal billed for a cloud agent run has no remaining credits to charge against.
On self-serve plans (Build, Max, Business), the billed principal depends on how the run was triggered:
* **User-triggered runs** draw from the triggering user’s plan-included credits first, then shared team grants, then any remaining user-scoped grants that apply on the active team. There is no option to spend personal credits first while on a team.
* **Agent API key and scheduled runs** draw from the team owner’s plan-included credits first, then the team’s shared add-on credit pool.
When those sources are depleted and [auto-reload](/support-and-community/plans-and-billing/add-on-credits/) is off, new runs return this error. On Enterprise plans, runs draw from the team-scoped credit pool per your contract — contact your account manager when the pool is exhausted.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `403 Forbidden`
* **Retryable:** No
* **Task State:** FAILED
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* A user-triggered run runs out of the user’s plan-included credits and the team’s shared add-on credit pool.
* An agent API key or scheduled run runs out of the team owner’s plan-included credits and the team’s shared add-on credit pool.
* Auto-reload is off, or auto-reload is on but the team-wide monthly spend cap has been reached.
For the full waterfall, see [How are cloud agent runs on team plans billed when no individual user triggered them?](/support-and-community/plans-and-billing/pricing-faqs/#how-are-cloud-agent-runs-on-team-plans-billed-when-no-individual-user-triggered-them) in the Pricing FAQs.
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/insufficient-credits/",
"title": "The principal billed for this run has no remaining credits. Purchase add-on credits or raise the team-wide spend cap to continue.",
"status": 403,
"instance": "/api/v1/agent/tasks",
"retryable": false
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
The fix depends on which principal was billed.
**For user-triggered runs (your plan credits and the team’s add-on pool were exhausted):**
1. Purchase [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) in **Settings** > **Billing and usage**, or wait for your monthly credits to refresh. Any active member’s purchase tops up the team’s shared pool.
2. Alternatively, enable auto-reload, subject to your team’s monthly spend cap.
3. Retry the failed operation.
**For agent API key or scheduled runs (the owner’s plan credits and the team’s add-on pool were exhausted):**
1. Top up the team’s shared pool by purchasing add-on credits, or wait for the owner’s monthly credits to refresh.
2. If auto-reload is on but the team-wide spend cap was reached, an admin can raise the cap in **Settings** > **Billing and usage**.
3. Retry the failed operation.
Any active team member can top up the shared pool; raising the spend cap or changing auto-reload requires a team admin.
***
## Related
[Section titled “Related”](#related)
* [Access, billing, and identity permissions](/platform/team-access-billing-and-identity/) — Credit billing for individual user runs and agent API key runs.
* [Add-on credits](/support-and-community/plans-and-billing/add-on-credits/) — Purchase additional credits and configure auto-reload.
* [Platform credits](/support-and-community/plans-and-billing/platform-credits/) — The third credit bucket alongside AI credits and compute credits.
* [Cloud Agents Overview](/platform/) — Billing and plan requirements for cloud agents.
# integration_disabled
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/integration-disabled/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/integration-disabled/)
> The integration (Slack, Linear, etc.) is currently disabled in the Automation Platform settings. Enable it to continue.
The `integration_disabled` error occurs when a task targets an integration that is currently disabled in the Automation Platform settings.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `403 Forbidden`
* **Retryable:** No
* **Task State:** FAILED
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* A Slack message, Linear issue, or other integration event triggers a cloud agent, but the corresponding integration has been disabled in the Automation Platform settings
* The integration was previously active but has been turned off by a team admin
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/integration-disabled/",
"title": "This integration is disabled. Please enable it in Oz.",
"status": 403,
"instance": "/api/v1/agent/tasks",
"error": "This integration is disabled. Please enable it in Oz.",
"retryable": false
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
1. Go to the [Automation Platform integrations page](https://oz.warp.dev/integrations).
2. Enable the integration that was disabled.
3. Retry the triggering event or task.
***
## Related
[Section titled “Related”](#related)
* [Integrations](/platform/integrations/) — Configuring Slack, Linear, and GitHub integrations
* [Oz web app](/platform/oz-web-app/) — Managing integrations via the web interface
# integration_not_configured
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/integration-not-configured/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/integration-not-configured/)
> The integration's setup is incomplete. Visit the setup URL to finish configuring the integration.
The `integration_not_configured` error occurs when a task requires an integration whose setup has not been completed (for example, missing OAuth tokens or unfinished configuration steps).
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `400 Bad Request`
* **Retryable:** No
* **Task State:** FAILED
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* An integration (Slack, Linear, etc.) was partially set up but the configuration was not completed
* Required OAuth tokens or credentials for the integration are missing or expired
* The integration was installed but additional setup steps were not finished
***
## Additional metadata fields
[Section titled “Additional metadata fields”](#additional-metadata-fields)
This error includes extra fields beyond the standard response format:
* **`integration_name`** — The name of the integration that needs configuration
* **`setup_url`** — A URL to the integration setup page where you can complete configuration
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/integration-not-configured/",
"title": "Slack integration is not configured",
"status": 400,
"instance": "/api/v1/agent/tasks",
"error": "Slack integration is not configured",
"retryable": false,
"integration_name": "slack",
"setup_url": "https://oz.warp.dev/integrations"
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
1. Visit the `setup_url` provided in the response metadata (or go to the [Automation Platform integrations page](https://oz.warp.dev/integrations)).
2. Complete all setup steps for the integration.
3. Retry the triggering event or task.
***
## Related
[Section titled “Related”](#related)
* [Integrations](/platform/integrations/) — Integration setup guides
* [Slack Integration](/platform/integrations/slack/) — Slack-specific setup
* [Linear Integration](/platform/integrations/linear/) — Linear-specific setup
# internal_error
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/internal-error/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/internal-error/)
> An unexpected server-side error occurred. The platform will automatically retry. Contact support if the issue persists.
The `internal_error` is a catch-all for unexpected server-side errors. The platform automatically retries these errors before marking the task as failed.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `500 Internal Server Error`
* **Retryable:** Yes (automatic)
* **Task State:** ERROR
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* An unexpected condition occurred on the server that does not match any specific error category
* An internal service dependency failed or timed out
* An unclassified error occurred during task processing
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/internal-error/",
"title": "An unexpected error occurred. Please try again later. If the issue persists, contact support.",
"status": 500,
"instance": "/api/v1/agent/tasks",
"error": "An unexpected error occurred. Please try again later. If the issue persists, contact support.",
"retryable": true,
"trace_id": "abc123..."
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
No action is typically needed — the platform will automatically retry the task.
If the error persists:
1. Wait a few minutes and try again.
2. Contact [Warp support](/support-and-community/troubleshooting-and-support/sending-us-feedback/) and include the `trace_id` from the error response.
***
## Related
[Section titled “Related”](#related)
* [Cloud Agents Overview](/platform/) — How cloud agent tasks work
* [Cloud Agents FAQs](/platform/faqs/) — Common questions about cloud agents
# invalid_request
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/invalid-request/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/invalid-request/)
> The request body is malformed, missing required fields, or contains invalid parameter values.
The `invalid_request` error occurs when the API request is malformed or contains invalid parameters.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `400 Bad Request`
* **Retryable:** No
* **Task State:** FAILED
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* Required fields are missing from the request body (for example, `prompt` or `schedule_id`)
* Parameter values are invalid or out of range
* The request body cannot be parsed (malformed JSON)
* A referenced identifier is in the wrong format
* A team-owned task references a personal environment (team tasks require team-scoped environments)
The `detail` field in the response will describe the specific validation issue.
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/invalid-request/",
"title": "The request contains invalid or missing parameters.",
"status": 400,
"detail": "schedule_id is required",
"instance": "/api/v1/agent/tasks",
"error": "The request contains invalid or missing parameters. (schedule_id is required)",
"retryable": false
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
1. Check the `detail` field for the specific validation issue.
2. Correct the request parameters according to the [API documentation](/factories/api-and-sdk/).
3. Retry the request.
***
## Related
[Section titled “Related”](#related)
* [Warp Platform API](/factories/api-and-sdk/) — API request format and parameters
# not_authorized
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/not-authorized/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/not-authorized/)
> The authenticated user or API key does not have permission to perform the requested operation.
The `not_authorized` error occurs when the authenticated principal (user or API key) does not have sufficient permissions to perform the requested operation.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `403 Forbidden`
* **Retryable:** No
* **Task State:** FAILED
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* You attempt to access a resource owned by another team or user
* Your API key does not have the required scope for the operation
* You try to perform an admin-level operation without admin privileges
* A team-level operation is attempted by a user who is not a member of the team
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/not-authorized/",
"title": "You do not have permission for this operation.",
"status": 403,
"detail": "user is not a member of the team",
"instance": "/api/v1/agent/tasks/abc123",
"error": "You do not have permission for this operation. (user is not a member of the team)",
"retryable": false
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
1. Verify that the API key or user account belongs to the correct team.
2. Check that your role has the necessary permissions for the operation.
3. Contact a team admin if you need elevated access.
***
## Related
[Section titled “Related”](#related)
* [Access, Billing, and Identity](/platform/team-access-billing-and-identity/) — Permission model and identity
* [Warp Platform API](/factories/api-and-sdk/) — API authentication and authorization
# operation_not_supported
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/operation-not-supported/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/operation-not-supported/)
> The requested operation is not supported for this resource or its current state.
The `operation_not_supported` error occurs when you attempt an operation that is not currently supported for the given resource or its current state.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `422 Unprocessable Entity`
* **Retryable:** No
* **Task State:** FAILED
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* You attempt to cancel a **self-hosted** agent run via the API (self-hosted runs must be cancelled through the hosting infrastructure)
* You attempt to cancel a **local** agent run via the API (local runs must be cancelled from the source client)
* You attempt to cancel a run triggered via **GitHub Actions** (these must be cancelled through the GitHub Actions workflow view)
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/operation-not-supported/",
"title": "Self-hosted agent runs cannot be cancelled with the API.",
"status": 422,
"instance": "/api/v1/agent/tasks/abc123/cancel",
"error": "Self-hosted agent runs cannot be cancelled with the API.",
"retryable": false
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
1. Check the error message to understand which operation is unsupported and why.
2. Use the appropriate method for the operation:
* **Self-hosted runs** — Cancel through your hosting infrastructure.
* **Local runs** — Cancel from the Warp desktop app or terminal session.
* **GitHub Actions runs** — Cancel via the GitHub Actions workflow view.
***
## Related
[Section titled “Related”](#related)
* [Cloud Agents Overview](/platform/) — How cloud agent tasks work
* [Self-hosting](/factories/self-hosting/) — Self-hosted agent configuration
* [Warp Platform API](/factories/api-and-sdk/) — API reference for managing agent tasks
# resource_not_found
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/resource-not-found/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/resource-not-found/)
> The requested resource (task, environment, schedule, agent, etc.) does not exist or has been deleted.
The `resource_not_found` error occurs when a referenced resource cannot be found. This typically means the resource ID is incorrect, the resource has been deleted, or it belongs to a different team.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `404 Not Found`
* **Retryable:** No
* **Task State:** FAILED
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* A task ID, environment UID, schedule ID, or other resource identifier does not match any existing resource
* The referenced resource has been deleted
* The resource exists but belongs to a different team or user (and you don’t have access)
The `detail` field in the response will describe which resource was not found.
***
## Example response
[Section titled “Example response”](#example-response)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/resource-not-found/",
"title": "The requested resource was not found.",
"status": 404,
"detail": "environment abc123 not found",
"instance": "/api/v1/agent/tasks",
"error": "The requested resource was not found. (environment abc123 not found)",
"retryable": false
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
1. Verify the resource ID is correct and properly formatted.
2. Check that the resource has not been deleted (for example, via the [Oz web app](https://oz.warp.dev) or CLI).
3. Confirm the resource belongs to your team or that you have access to it.
***
## Related
[Section titled “Related”](#related)
* [Environments](/platform/environments/) — Managing cloud agent environments
* [Managing Cloud Agents](/platform/managing-cloud-agents/) — Viewing and managing agent tasks
# resource_unavailable
Canonical page: [/factories/api-and-sdk/troubleshooting/errors/resource-unavailable/](https://docs.warp.dev/factories/api-and-sdk/troubleshooting/errors/resource-unavailable/)
> A transient infrastructure issue prevented the task from running. The platform will automatically retry. No action is needed.
The `resource_unavailable` error indicates a transient infrastructure issue that prevented the cloud agent task from running. This is automatically retried by the platform.
***
## Details
[Section titled “Details”](#details)
* **HTTP Status:** `429 Too Many Requests` or `500 Internal Server Error`
* **Retryable:** Yes (automatic)
* **Task State:** ERROR
***
## When does this occur?
[Section titled “When does this occur?”](#when-does-this-occur)
This error is returned when:
* **Capacity full (429)** — Cloud agent capacity is temporarily saturated. Your task will be queued and retried automatically.
* **Sandbox creation failed (500)** — A sandbox instance could not be created for the agent. This is typically a transient issue.
***
## Example responses
[Section titled “Example responses”](#example-responses)
### Capacity full
[Section titled “Capacity full”](#capacity-full)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/resource-unavailable/",
"title": "Agent capacity is temporarily full. Your task will be retried automatically, or you can try again later.",
"status": 429,
"instance": "/api/v1/agent/tasks",
"error": "Agent capacity is temporarily full. Your task will be retried automatically, or you can try again later.",
"retryable": true,
"trace_id": "abc123..."
}
```
### Sandbox creation failed
[Section titled “Sandbox creation failed”](#sandbox-creation-failed)
```json
{
"type": "/factories/api-and-sdk/troubleshooting/errors/resource-unavailable/",
"title": "Failed to create a sandbox instance for your agent. This is typically a transient issue — your task will be retried automatically.",
"status": 500,
"instance": "/api/v1/agent/tasks",
"error": "Failed to create a sandbox instance for your agent. This is typically a transient issue — your task will be retried automatically.",
"retryable": true,
"trace_id": "abc123..."
}
```
***
## How to resolve
[Section titled “How to resolve”](#how-to-resolve)
No action is typically needed — the platform will automatically retry the task.
If the error persists after retries:
1. Try again later when capacity has freed up.
2. Contact [Warp support](/support-and-community/troubleshooting-and-support/sending-us-feedback/) and include the `trace_id` from the error response.
***
## Related
[Section titled “Related”](#related)
* [Cloud Agents Overview](/platform/) — How cloud agent execution works
* [Deployment Patterns](/factories/deployment-patterns/) — Execution models and infrastructure
# Factory automations
Canonical page: [/factories/automations/](https://docs.warp.dev/factories/automations/)
> An automation starts factory runs from a trigger, routes them to an agent, and filters which events start a run.
An **automation** is a factory resource that starts runs from a trigger and routes them to an agent. Triggers fired by a connected tool or a [custom webhook](/factories/webhooks/) also carry filters that decide which events start a run. Every default automation Warp creates when you connect a provider, and every custom one you add, is this same resource. See [`automations/<name>/automation.md`](/factories/factory-as-code/#automationsnameautomationmd) for the full schema.
Automation filters decide which events from your connected tools start factory work. Every trigger on an automation carries filters (e.g., a repository, channel, team, project, label, author, or webhook payload field) and an event starts a run only when it matches them. Filters let a factory watch busy channels and repositories without acting on everything in them.
## How matching works
[Section titled “How matching works”](#how-matching-works)
An event starts an automation only when it matches the trigger’s provider, event type, and filters:
* **Every filter must match.** A trigger that sets both a team and a label matches only events carrying both.
* **Within one filter, any value matches.** A **Labels** filter listing `bug` and `regression` matches an issue with either label.
* **A filter you leave empty matches everything.** A trigger with no filters at all starts work for every event of its type.
One event can match more than one automation, and each match starts its own run. If a single action starts duplicate runs, narrow or remove one of the overlapping triggers.
## Filters don’t control access
[Section titled “Filters don’t control access”](#filters-dont-control-access)
Filters decide when work starts, not what a running agent can reach. Access comes from what you authorize on each provider: the GitHub App installation, the GitLab bot’s project membership, the Slack app’s authorization, the Microsoft Teams installation, the Linear OAuth scope, or the Jira app installation. Tightening a filter never shrinks that access, and removing one never widens it. To change what an integration can reach, change what you authorize for that provider.
Filters are still your main control over who starts runs. On GitHub and GitLab, the event author doesn’t need to be a Warp team member, so use author, member, and branch filters to decide whose activity starts work. Slack mentions and direct messages additionally require a Slack account linked to an active member of the factory’s Warp team. Microsoft Teams mentions require a Microsoft account linked to an active member of the factory’s Warp workspace. A custom webhook authenticates each delivery with the webhook’s own secret or the sender’s signature, so anyone holding that credential can start work; its filters only decide which deliveries do.
## What each source can filter on
[Section titled “What each source can filter on”](#what-each-source-can-filter-on)
Every source filters on where the event happened: a repository, project, conversation, or team. The remaining filters vary by source and event type:
| Source | Filters |
| ----------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------ |
| [Slack](/factories/integrations/slack/) | Conversations, authors or members, keywords, emoji, and reacted-message authors |
| [Microsoft Teams](/factories/integrations/teams/) | Team, channels (standard picker; shared by channel ID), authors, and keywords |
| [GitHub](/factories/integrations/github/) | Repository, branches, base branches, paths, labels, authors, assignees, mentioned users or teams, reviewers, review states, workflows, and conclusions |
| [GitLab](/factories/integrations/gitlab/) | Project, actions, and base branch |
| [Azure DevOps](/factories/integrations/azure-devops/) | Repository, branches, work item types, labels, assignees, authors, and mentioned identities |
| [Linear](/factories/integrations/linear/) | Teams, labels, project, workflow state, assignee, mentioned user, and, for comment events, a specific issue |
| [Jira](/factories/integrations/jira/) | Jira projects and assignment keywords |
| [Custom webhooks](/factories/webhooks/) | The webhooks the trigger listens to, and a pattern over the delivery’s JSON payload |
Each integration guide lists which filters appear on which event types. Webhook payload patterns follow their own grammar, described in [payload filters for webhook triggers](#payload-filters-for-webhook-triggers).
## Edit filters on an automation
[Section titled “Edit filters on an automation”](#edit-filters-on-an-automation)
1. In the factory’s dashboard, open **Automations**, then create an automation or edit an existing one.
2. Under **Triggers**, open a trigger and set the filters shown for its event. Click **More filters** for the event-specific options.
3. Click **Save**. To confirm the routing works, send a matching test event, such as opening a test issue, and check that a work item starts in the factory dashboard.
Review the default automations Warp creates when you connect a provider, too: their filters are starting points, not fixed rules.
## Filters in definitions as code
[Section titled “Filters in definitions as code”](#filters-in-definitions-as-code)
In a [factory definition](/factories/factory-as-code/), each entry under an automation’s `triggers` takes an optional `filter` whose keys mirror the filters in the automation editor:
automations/labeled-issue/automation.md
```markdown
---
enabled: true
agent: foreman
triggers:
- provider: github
event: issue_labeled
filter:
repos: [acme/payments-service]
labels: [factory-ready]
---
Review the labeled issue and decide the next required stage.
```
The same matching rules apply: every key must match, any listed value within a key matches, and an omitted key matches everything. Each integration guide shows the keys its provider accepts.
For example, this automation from [`04-code-review-only`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/04-code-review-only) in the [warp-factory-examples](https://github.com/warpdotdev/warp-factory-examples) repository scopes reviews to one base branch and excludes work-in-progress PRs with a `not_in` list:
automations/pr-opened/automation.md
```markdown
---
triggers:
- provider: github
event: pull_request_opened
filter:
repos: [acme/api-service]
base_branches: [main]
labels:
not_in: [wip]
---
A pull request was opened against the default branch. If it is a draft,
stop silently. Otherwise review it and post your findings and verdict on
the PR.
```
For more automations that use these filters, including branches, paths, workflow conclusions, and emoji reactions, see [`06-common-automations`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/06-common-automations).
## Payload filters for webhook triggers
[Section titled “Payload filters for webhook triggers”](#payload-filters-for-webhook-triggers)
A [custom webhook](/factories/webhooks/) trigger (`provider: webhook`, `event: received`) binds an automation to exactly one webhook. `webhook_ids` is required, takes a one-item list containing that webhook’s UID, and supports only `in`. To listen to multiple webhooks, add one trigger with provider `webhook` and event `received` per UID. The optional `payload` filter is a pattern that mirrors the shape of the delivery’s JSON body, so you can route on the payload without running an agent to decide:
* Payload filters match against the webhook’s JSON body.
* Fields are ANDed together: every key in the pattern must match.
* An array means “match any of these values.”
* `in`, `not_in`, and `exists` are supported as operators on a field.
* Nested objects let you filter on nested payload fields.
This trigger starts a run for opened or reopened pull requests from a GitHub webhook, skipping drafts and bot authors:
```yaml
triggers:
- provider: webhook
event: received
filter:
webhook_ids: [WEBHOOK_UID]
payload:
action: [opened, reopened]
pull_request:
draft: [false]
sender:
type:
not_in: [Bot]
```
In the dashboard, the **Webhook** trigger’s JSON editor validates a pattern as you type, and **Test filter** evaluates it against a stored delivery. See [add a Webhook trigger to an automation](/factories/webhooks/#add-a-webhook-trigger-to-an-automation).
For exact matching semantics, limits, and validation rules, see [payload filter reference](#payload-filter-reference).
## Payload filter reference
[Section titled “Payload filter reference”](#payload-filter-reference)
* **Values match by type.** Strings match exactly and case-sensitively, numbers match numerically (`1` equals `1.0`), and booleans and `null` are matchable values.
* **A missing key fails `in` and passes `not_in`.** A field the payload doesn’t carry can’t be in any set, so `{"env": {"not_in": ["dev"]}}` matches a delivery with no `env` field. A nested pattern object requires its key to be present.
* **Arrays of objects match on any element.** When the payload value is an array of objects, a nested pattern matches if any element matches; when it’s an array of scalars, `in` matches on any overlap and `not_in` requires none.
* **Operators on the same field AND together.** For example, combining `in` and `exists: true` on one field requires both to hold.
* **Limits** - A pattern nests up to 10 levels deep, holds up to 64 leaf fields, and lists up to 32 values per set.
* **Validation** - Warp rejects a pattern that lists the same value in both `in` and `not_in` on one field, or that combines `exists: false` with a non-empty `in`.
* **Fail closed** - A filter that can’t be evaluated never matches, so a broken filter keeps an automation silent rather than firing it.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
* **A matching event doesn’t start work** - Confirm the automation is enabled and the trigger’s event type matches, then check every filter; a single mismatch prevents routing. Each integration guide’s troubleshooting section covers provider-specific causes, such as app installation coverage.
* **A webhook delivery doesn’t start work** - Open the delivery in the webhook’s **Recent deliveries** to confirm it was accepted rather than rejected or deduplicated, then use **Test filter** on the automation’s **Webhook** trigger against that delivery. See [troubleshooting custom webhooks](/factories/webhooks/#troubleshooting).
## Related pages
[Section titled “Related pages”](#related-pages)
* [**Connect your factory**](/factories/connect-your-factory/) - Choose the sources that route work into the factory.
* [Slack](/factories/integrations/slack/), [Microsoft Teams](/factories/integrations/teams/), [GitHub](/factories/integrations/github/), [GitLab](/factories/integrations/gitlab/), [Azure DevOps](/factories/integrations/azure-devops/), [Linear](/factories/integrations/linear/), and [Jira](/factories/integrations/jira/) integration guides - Per-source setup, events, and filter details.
* [**Custom webhooks**](/factories/webhooks/) - Start automations from any system that can POST JSON, with the setup flow and authentication modes.
* [**Definitions as code**](/factories/factory-as-code/) - Manage automations, triggers, and filters as version-controlled files.
* [**warp-factory-examples**](https://github.com/warpdotdev/warp-factory-examples) - Complete factory definitions with example automations and filters.
* [**Factory dashboard**](/factories/factory-dashboard/) - Create and edit automations in the factory’s **Automations** view.
# Factory benchmarks
Canonical page: [/factories/benchmarks/](https://docs.warp.dev/factories/benchmarks/)
> Warp Factories benchmarks compare agent model and runner configurations on fixed tasks so you can choose a production configuration.
Note
Warp Factories is in **Early Access** and available to a limited set of teams. [Request access](https://www.warp.dev/factories/request-access) to use it with your team.
Warp Factories benchmarks compare model and runner configurations for one factory agent on the same fixed tasks. Use a benchmark to test a change on representative work before you apply it to your factory. This video shows how to compare benchmark results for quality and cost before changing a coding agent’s configuration.

## How benchmarks work
[Section titled “How benchmarks work”](#how-benchmarks-work)
A benchmark helps you choose an agent configuration based on repeatable evidence. Run representative tasks with different configurations, then compare their results before you change a live factory.
A benchmark suite is a reusable collection of tasks that evaluates one factory agent. Each task has a prompt and “Correctness criteria,” which tell the built-in Correctness Scorer what a successful trial must do. A trial is a single run of a task under one configuration. Repetitions create additional trials.
When you launch a suite, choose the configurations, Scorers, and repetitions to compare. Warp runs the trials, then scores trials that reach a terminal state. A blocked trial remains **Blocked**, but Warp can score the evidence it produced; each Scorer decides whether that evidence satisfies its criteria. The run keeps those inputs, so later changes to the suite do not change its past results.
The Runs tab for a benchmark suite.
Use separate suites for focused questions:
* **Factory default** - Compare models and runners to choose the default configuration for a coding agent.
* **Frontend changes** - Compare configurations on representative frontend tasks before applying one to that workflow.
## Create and run a benchmark
[Section titled “Create and run a benchmark”](#create-and-run-a-benchmark)
To use Benchmarks, you need a factory with an agent to evaluate. Use a completed run from that agent when you want a task to reproduce real work, or write a task yourself.
This video shows how to turn your team’s coding tasks into a reusable benchmark suite.

1. In the [Warp Factories web app](https://platform.warp.dev), open your factory, click **Benchmarks**, then click **New**.
The Benchmarks page for a factory.
2. Enter a name and optional description, then choose the agent to evaluate. The suite runs every task as that agent.
The benchmark editor with a selected agent.
3. Click **Add task**. Warp saves the benchmark, then opens task setup.
4. Select a completed run, then click **Add task**. To write a task instead, click **Start from scratch instead**.
The task source picker.
5. Review the task prompt and enter “Correctness criteria” for the task.
The task editor for a benchmark suite.
6. Click **Run**. In the launch dialog, choose the model or an authorized custom factory router and the runner for each configuration. Third-party harness comparisons are not available yet.
7. Add configurations, select Scorers, and set “Repetitions.” The dialog shows the number of trials created. More trials and Scorers increase the run’s cost.
8. Click **Run benchmark**. The benchmark page shows its status and scored trials. You can cancel a running or scoring benchmark.
## Review benchmark results
[Section titled “Review benchmark results”](#review-benchmark-results)
After the run completes, review the result as a comparison, not as a universal model ranking:
A completed benchmark result and comparison chart.
* **Overall recommendation** - Identifies the highest-quality configuration when at least two configurations have comparable results.
* **Additional recommendations** - Highlight the most efficient and lowest-cost configurations when the result supports those comparisons.
* **Comparison chart** - Compare the selected result dimensions across configurations.
* **Overall table** - Compare each Scorer’s average and the combined Overall value. Expand a configuration, task, and repetition to inspect its individual trials.
* **Scorer grids** - Show each task’s results across configurations for a selected Scorer.
Expanded trial results for a configuration.
The run’s “Total cost” includes model usage for trials and Scorer usage. It estimates those costs from credits at your team’s current rate, so it is not a billed amount. A failed or cancelled benchmark shows only results that finished scoring before the run stopped.
## Apply a benchmark result
[Section titled “Apply a benchmark result”](#apply-a-benchmark-result)
Change one configuration at a time. If the evidence supports a candidate, update the agent’s model or runner in the factory dashboard, or submit the change through your [factory definition](/factories/factory-as-code/). Keep the relevant Scorers active, then compare later production runs with the baseline you recorded before the change.
For version-controlled factories, define reusable suites in `benchmarks/<suite-slug>/suite.yaml` and their tasks in `benchmarks/<suite-slug>/tasks/<task-slug>.yaml`. See [benchmark suite files](/factories/factory-as-code/#benchmarkssuite-slugsuiteyaml).
## Related pages
[Section titled “Related pages”](#related-pages)
* [Measure and improve a factory](/factories/measure-and-improve/) - Configure Scorers and use benchmark evidence in an improvement loop.
* [Factory dashboard](/factories/factory-dashboard/) - Track factory work, runs, and benchmark suites.
* [Factory definition syntax](/factories/factory-as-code/) - Define factories and benchmark suites as code.
# Connecting other code forges to your factory
Canonical page: [/factories/code-forges/other-code-forges/](https://docs.warp.dev/factories/code-forges/other-code-forges/)
> Connect a factory to a repository from another code forge using Agent Secrets and setup commands on the default runner.
Connect your factory to a repository on Bitbucket, Azure DevOps Server, self-managed GitLab, or another code forge without first-class factory support. Hosted Azure DevOps Services repositories use the [first-class Azure DevOps integration](/factories/integrations/azure-devops/). For other code forges, create the factory with no connected repository, then clone the repository from its default runner.
Caution
This setup gives factory agents repository access. It does not add provider-specific events or automations for the code forge.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **Factory access** - Permission to create the factory, add Agent Secrets, and edit its default runner.
* **Repository access** - An HTTPS clone URL and a token that can read the repository.
For provider-specific token and clone formats, see [Bitbucket repository access](/platform/integrations/bitbucket/) or [self-managed GitLab repository access](/platform/integrations/gitlab/#self-managed-gitlab-instances).
### Azure DevOps Server credentials
[Section titled “Azure DevOps Server credentials”](#azure-devops-server-credentials)
Before you create the factory, generate a personal access token for your Azure DevOps Server repository:
1. Sign in to your Azure DevOps Server instance at `https://SERVER/COLLECTION`.
2. Click the user settings icon, then click **Personal access tokens**.
3. Click **+ New Token**, then enter a name and choose an expiration date.
4. Under “Scopes,” choose **Custom defined**, then select **Code** > **Read**. Select **Code** > **Read & Write** instead if agents need to push commits.
5. Click **Create**, then copy the token. Azure DevOps doesn’t show it again.
Store this token as the `CODE_FORGE_TOKEN` Agent Secret by following [Grant the clone credential](#grant-the-clone-credential).
## Create the factory without a repository
[Section titled “Create the factory without a repository”](#create-the-factory-without-a-repository)
To prepare a repository from the default runner, create the factory without a code-host connection.
1. In the [Warp Factories web app](https://platform.warp.dev), click **+** next to **Factories**.
2. Under **Connect your code host**, select **No repo**.
3. Complete the remaining setup choices to create the factory.
The factory opens in its dashboard without a connected repository.
## Grant the clone credential
[Section titled “Grant the clone credential”](#grant-the-clone-credential)
Store the repository token as an Agent Secret so the default runner can use it without placing the token in a command or definition file.
1. From the [Warp Factories web app](https://platform.warp.dev), click **Secrets**.
2. Create an Agent Secret named `CODE_FORGE_TOKEN`.
3. Enter the repository access token as the secret value, then grant `CODE_FORGE_TOKEN` to the factory agents that use the default runner.
The secret is available to those agents and their runner setup commands as the `CODE_FORGE_TOKEN` environment variable.
## Clone the repository from the default runner
[Section titled “Clone the repository from the default runner”](#clone-the-repository-from-the-default-runner)
Runner setup commands prepare each agent workspace before factory work starts.
1. From the factory dashboard, click **Settings** and scroll down to the “Runners” section.
2. Next to the default runner, click the edit button. In the “Setup commands” section, click **+** and add an authenticated `git clone` command that reads `$CODE_FORGE_TOKEN`.
3. Add any other project setup commands the repository needs, such as dependency installation, builds, or code generation.
Use your code forge’s documented clone format. For example, Bitbucket Cloud requires the `x-bitbucket-api-token-auth` username, while other hosts use a different username or authorization header.
For Azure DevOps Server, add this setup command:
```bash
if [ ! -d "REPO/.git" ]; then
git -c http.extraheader="Authorization: Basic $(printf ':%s' "$CODE_FORGE_TOKEN" | base64 | tr -d '\n')" \
clone "https://SERVER/COLLECTION/PROJECT/_git/REPO" "REPO"
fi
```
Replace `SERVER` with your Azure DevOps Server hostname and `COLLECTION`, `PROJECT`, and `REPO` with the repository path and local directory name.
Setup commands run each time the runner prepares a workspace. Make the commands safe to run repeatedly.
## Test repository access
[Section titled “Test repository access”](#test-repository-access)
Start a direct factory run before you connect another work source.
1. In the factory dashboard, open **Runs** and click **New**.
2. Send a read-only request such as:
Test repository access
```text
In the repository root, list the top-level files and report the current
branch. Do not change any files.
```
3. Confirm that the run reports files from the cloned repository.
If the run cannot clone the repository, confirm that the Agent Secret is granted to the agent, the token has repository read access, and the clone command uses the token environment variable correctly.
## Starting work
[Section titled “Starting work”](#starting-work)
This code forge cannot start factory work from its own repository events. Start work from a connected service such as [Slack](/factories/integrations/slack/), [Linear](/factories/integrations/linear/), or [Jira](/factories/integrations/jira/), through a [custom webhook](/factories/webhooks/), or with a direct factory run.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Connect GitHub to your factory](/factories/integrations/github/) - Use GitHub’s first-class code-forge connection.
* [Connect GitLab to your factory](/factories/integrations/gitlab/) - Use GitLab.com’s first-class code-forge connection.
* [Connect your factory](/factories/connect-your-factory/) - Add the sources that start work after the repository is available.
* [Cloud agent secrets](/platform/secrets/) - Store and scope credentials for cloud agents.
# Connect your factory
Canonical page: [/factories/connect-your-factory/](https://docs.warp.dev/factories/connect-your-factory/)
> Route work into your factory from Slack, Microsoft Teams, GitHub, GitLab, Azure DevOps, Linear, Jira, local agents, direct runs, and schedules.
Connect your factory to the tools where your team already discusses, tracks, and reviews work. Wherever work starts, the factory keeps the original context from that source (the thread, issue, or pull request), and posts results in the same place.
Each source feeds into this factory’s repositories. If the work belongs to a different product surface, [start a new factory](/factories/#sizing-a-factory) for it instead.
GitHub, GitLab.com, and Azure DevOps Services connect both repositories and provider-specific work sources. To use another code forge for repository access, [connect another code forge to your factory](/factories/code-forges/other-code-forges/). That fallback does not receive provider-specific events or automations.
## Choose a source
[Section titled “Choose a source”](#choose-a-source)
Pick the sources that match where work starts for your team. You can connect multiple sources, but not both Linear and Jira at the same time. The setup wizard currently offers Linear; to use Jira, connect it after setup or in your [factory definition](/factories/factory-as-code/).
Once a source is connected, here’s the concrete action that hands it work — each links to that integration’s full instructions rather than repeating them.
| Source | Best for | Start work by | Continues in |
| ----------------------------------------------------- | --------------------------------------------------------------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------- | ----------------------------------------- |
| [Slack](/factories/integrations/slack/) | Chat and support requests | [Mentioning the app in a channel, thread, or DM](/factories/integrations/slack/#start-and-continue-work-from-slack) | The Slack thread or DM |
| [Microsoft Teams](/factories/integrations/teams/) | Chat in standard and shared channels | [Mentioning the Warp app in a configured channel](/factories/integrations/teams/#start-and-continue-work) | The Teams thread |
| [GitHub](/factories/integrations/github/) | Issues, pull requests, reviews, and CI | [Adding the factory’s label and mentioning **@warp**](/factories/integrations/github/#mention-the-factory) | The issue, pull request, or review thread |
| [GitLab](/factories/integrations/gitlab/) | Merge request activity and bot mentions | [Mentioning the factory’s bot in a merge request comment](/factories/integrations/gitlab/#mention-the-factory) | The merge request thread |
| [Azure DevOps](/factories/integrations/azure-devops/) | Work items and pull requests | [Mentioning the factory identity in a work item or pull request, or assigning it a work item](/factories/integrations/azure-devops/#configure-azure-devops-automations) | The factory work item |
| [Linear](/factories/integrations/linear/) | Planned issues | [Assigning the issue to the factory, or mentioning the Warp app in a comment](/factories/integrations/linear/#route-agent-sessions) | The Linear issue and its agent session |
| [Jira](/factories/integrations/jira/) | Work items assigned to Warp | [Assigning or mentioning **Warp** on a work item](/factories/integrations/jira/#connect-jira-and-add-an-automation) | The Jira agent session |
| [Custom webhooks](/factories/webhooks/) | Any system that can POST JSON: CI, monitoring, alerting, and internal tools | [Posting JSON to the webhook’s URL from the external system](/factories/webhooks/#configure-the-sender) | The factory work item |
| [Factory endpoints](/factories/factory-api/) | Custom integrations and scripts that dispatch by factory UID | [Calling `POST /factory/{uid}/runs` with a prompt](/factories/factory-api/#dispatch-a-run-to-a-factory) | The factory work item |
| [Factory MCP](/factories/factory-mcp/) | Exchanging work with a local coding agent, in both directions | [Calling `send_task` from a connected coding agent](/factories/factory-mcp/#send-new-work-to-a-factory) | The factory work item |
| Direct runs and schedules | One-off or recurring work | [Clicking **New** on the factory’s Runs page, or adding a schedule trigger](#direct-runs-and-schedules) | The factory work item |
## Connect a source
[Section titled “Connect a source”](#connect-a-source)
Each integration guide walks through authorizing access — grant only what the factory needs. Most connections add default [automations](/factories/automations/) that you can adjust or extend for your workflow.
After connecting, send a test request, such as mentioning the factory in Slack or assigning it an issue, and confirm it picks up the work and replies at the source.
## How work reaches your factory
[Section titled “How work reaches your factory”](#how-work-reaches-your-factory)
```
flowchart LR
Event["Event from a<br/>connected tool"] --> Automation["Matching<br/>automation"]
Schedule["Schedule"] --> Automation
Automation --> Foreman["Foreman agent"]
Direct["Direct request"] --> Foreman
Foreman --> Work["Work item"]
Work --> Results["Results posted<br/>back to the source"]
```
An event from a connected tool starts the automation based on filter matching, such as a specific repository, channel, or label. Schedules start their automation on a timer, and direct requests go straight to the factory.
Every request lands with the foreman agent, which turns it into a work item and dispatches the agents each stage needs. A reply in the same thread, issue, or pull request continues that work item instead of starting a new one, and repeated event deliveries don’t create duplicates. See [how Warp Factories work](/factories/how-factories-work/) for the full lifecycle, including where people stay in the loop.
## Review the default automations
[Section titled “Review the default automations”](#review-the-default-automations)
When you create a factory through the setup wizard, Warp adds default automations for each tool you connect, so common requests work immediately:
* **GitHub** - Starts work from mentions and assignments, when the factory’s label is applied to an issue or pull request, and when a review is submitted on a labeled pull request. It also follows up when labeled pull requests close or merge, completing a linked tracker issue when it can. See the [GitHub integration guide](/factories/integrations/github/).
* **GitLab** - Starts work when someone mentions the factory’s bot in a merge request comment. See the [GitLab integration guide](/factories/integrations/gitlab/).
* [Azure DevOps](/factories/integrations/azure-devops/) - Starts work when someone mentions the factory identity in a pull request or work item, or assigns it a work item.
* **Jira** - Starts work when someone assigns or mentions Warp on a work item in one of the Jira projects you selected. See the [Jira integration guide](/factories/integrations/jira/).
* **Linear** - Starts work when a new agent session arrives from one of the Linear teams you selected. See the [Linear integration guide](/factories/integrations/linear/).
* **Slack** - Starts work from mentions and messages, as described in the [Slack integration guide](/factories/integrations/slack/).
* **Microsoft Teams** - Starts work from app mentions in the channels you configured, including shared channels when the sender is in the same Microsoft 365 organization as the Warp app install and has linked that account to Warp. See the [Microsoft Teams integration guide](/factories/integrations/teams/).
These defaults are starting points. Review each automation’s filters, agent, and run settings, and adjust them to match your workflow. For automation files you can adapt, such as CI failure triage, a scheduled dependency audit, and Slack reaction intake, see [`06-common-automations`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/06-common-automations) in the [warp-factory-examples](https://github.com/warpdotdev/warp-factory-examples) repository.
## Custom webhooks
[Section titled “Custom webhooks”](#custom-webhooks)
A [custom webhook](/factories/webhooks/) gives the factory an authenticated URL that any system can POST JSON to, and an automation decides which deliveries start work by filtering on the payload. Use it for tools Warp doesn’t connect to directly, such as your CI system, PagerDuty, Sentry, or Stripe, without writing any code on your side.
## Factory endpoints
[Section titled “Factory endpoints”](#factory-endpoints)
[Factory endpoints](/factories/factory-api/) let your own code discover a factory and dispatch a task to it by UID, without knowing which agent handles the work. Use them to build a custom integration for a tool Warp doesn’t connect to directly - see [Build a Mattermost bot for Warp Factories](/guides/external-tools/build-a-mattermost-bot-for-warp-factories/) for a worked example.
## Factory MCP
[Section titled “Factory MCP”](#factory-mcp)
The Factory MCP connects local coding agents and other MCP clients to your factory, and it works in both directions. Send work to the factory, or take work over from it by pulling a task down to your machine, iterating on it locally, and handing it back to the same work item. See the [Factory MCP guide](/factories/factory-mcp/).
## Direct runs and schedules
[Section titled “Direct runs and schedules”](#direct-runs-and-schedules)
Not every task starts in an external tool:
* Start a direct run for one-off work. Click **New** on the factory’s Runs page and describe the task to the foreman, the same way you would from Slack or an issue tracker.
* Create a scheduled automation for recurring work, such as maintenance or reports. See the [triggers overview](/platform/triggers/) for how schedules and other triggers work across the platform.
This automation from [`06-common-automations`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/06-common-automations) runs a dependency audit every Monday:
automations/weekly-dependency-audit/automation.md
```markdown
---
triggers:
- provider: schedule
event: cron_fired
schedule:
name: weekly-dependency-audit
cron: "0 9 * * 1"
---
Run the weekly dependency audit. List outdated and vulnerable dependencies,
apply safe minor and patch upgrades on a branch, run the tests, and open a
PR with the changes and a summary of anything that needs a human decision.
```
# Deployment patterns for Warp Factories
Canonical page: [/factories/deployment-patterns/](https://docs.warp.dev/factories/deployment-patterns/)
> Choose Warp-hosted or managed self-hosted execution for Warp Factories based on your network, compliance, and operational requirements.
Choose an execution model for your factory based on where its code must run and who operates the compute. Warp-hosted execution is the default. Managed self-hosting keeps checkout and command execution in your network while Warp coordinates the work.

## Choose an execution model
[Section titled “Choose an execution model”](#choose-an-execution-model)
| If your factory needs to… | Choose |
| ---------------------------------------------------------------------------- | ----------------------------------------------------- |
| Run public repositories and services without operating workers | [Warp-hosted execution](#warp-hosted-execution) |
| Reach private repositories or services behind your network boundary | [Managed self-hosting](#managed-self-hosting) |
| Run standalone agents from CI or developer infrastructure, without a factory | [Unmanaged execution](/platform/unmanaged-execution/) |
Both factory options use the same [factory definition](/factories/factory-as-code/), [runners](/factories/runners/), and [factory dashboard](/factories/factory-dashboard/). The execution host changes the location of checkout, command execution, and the sandbox filesystem.
## Warp-hosted execution
[Section titled “Warp-hosted execution”](#warp-hosted-execution)
Use this when your factory can reach its repositories and services over the public internet. The Automation Platform runs the work on Warp-managed infrastructure while your factory definition selects the agents, runner, workspace, and credentials.
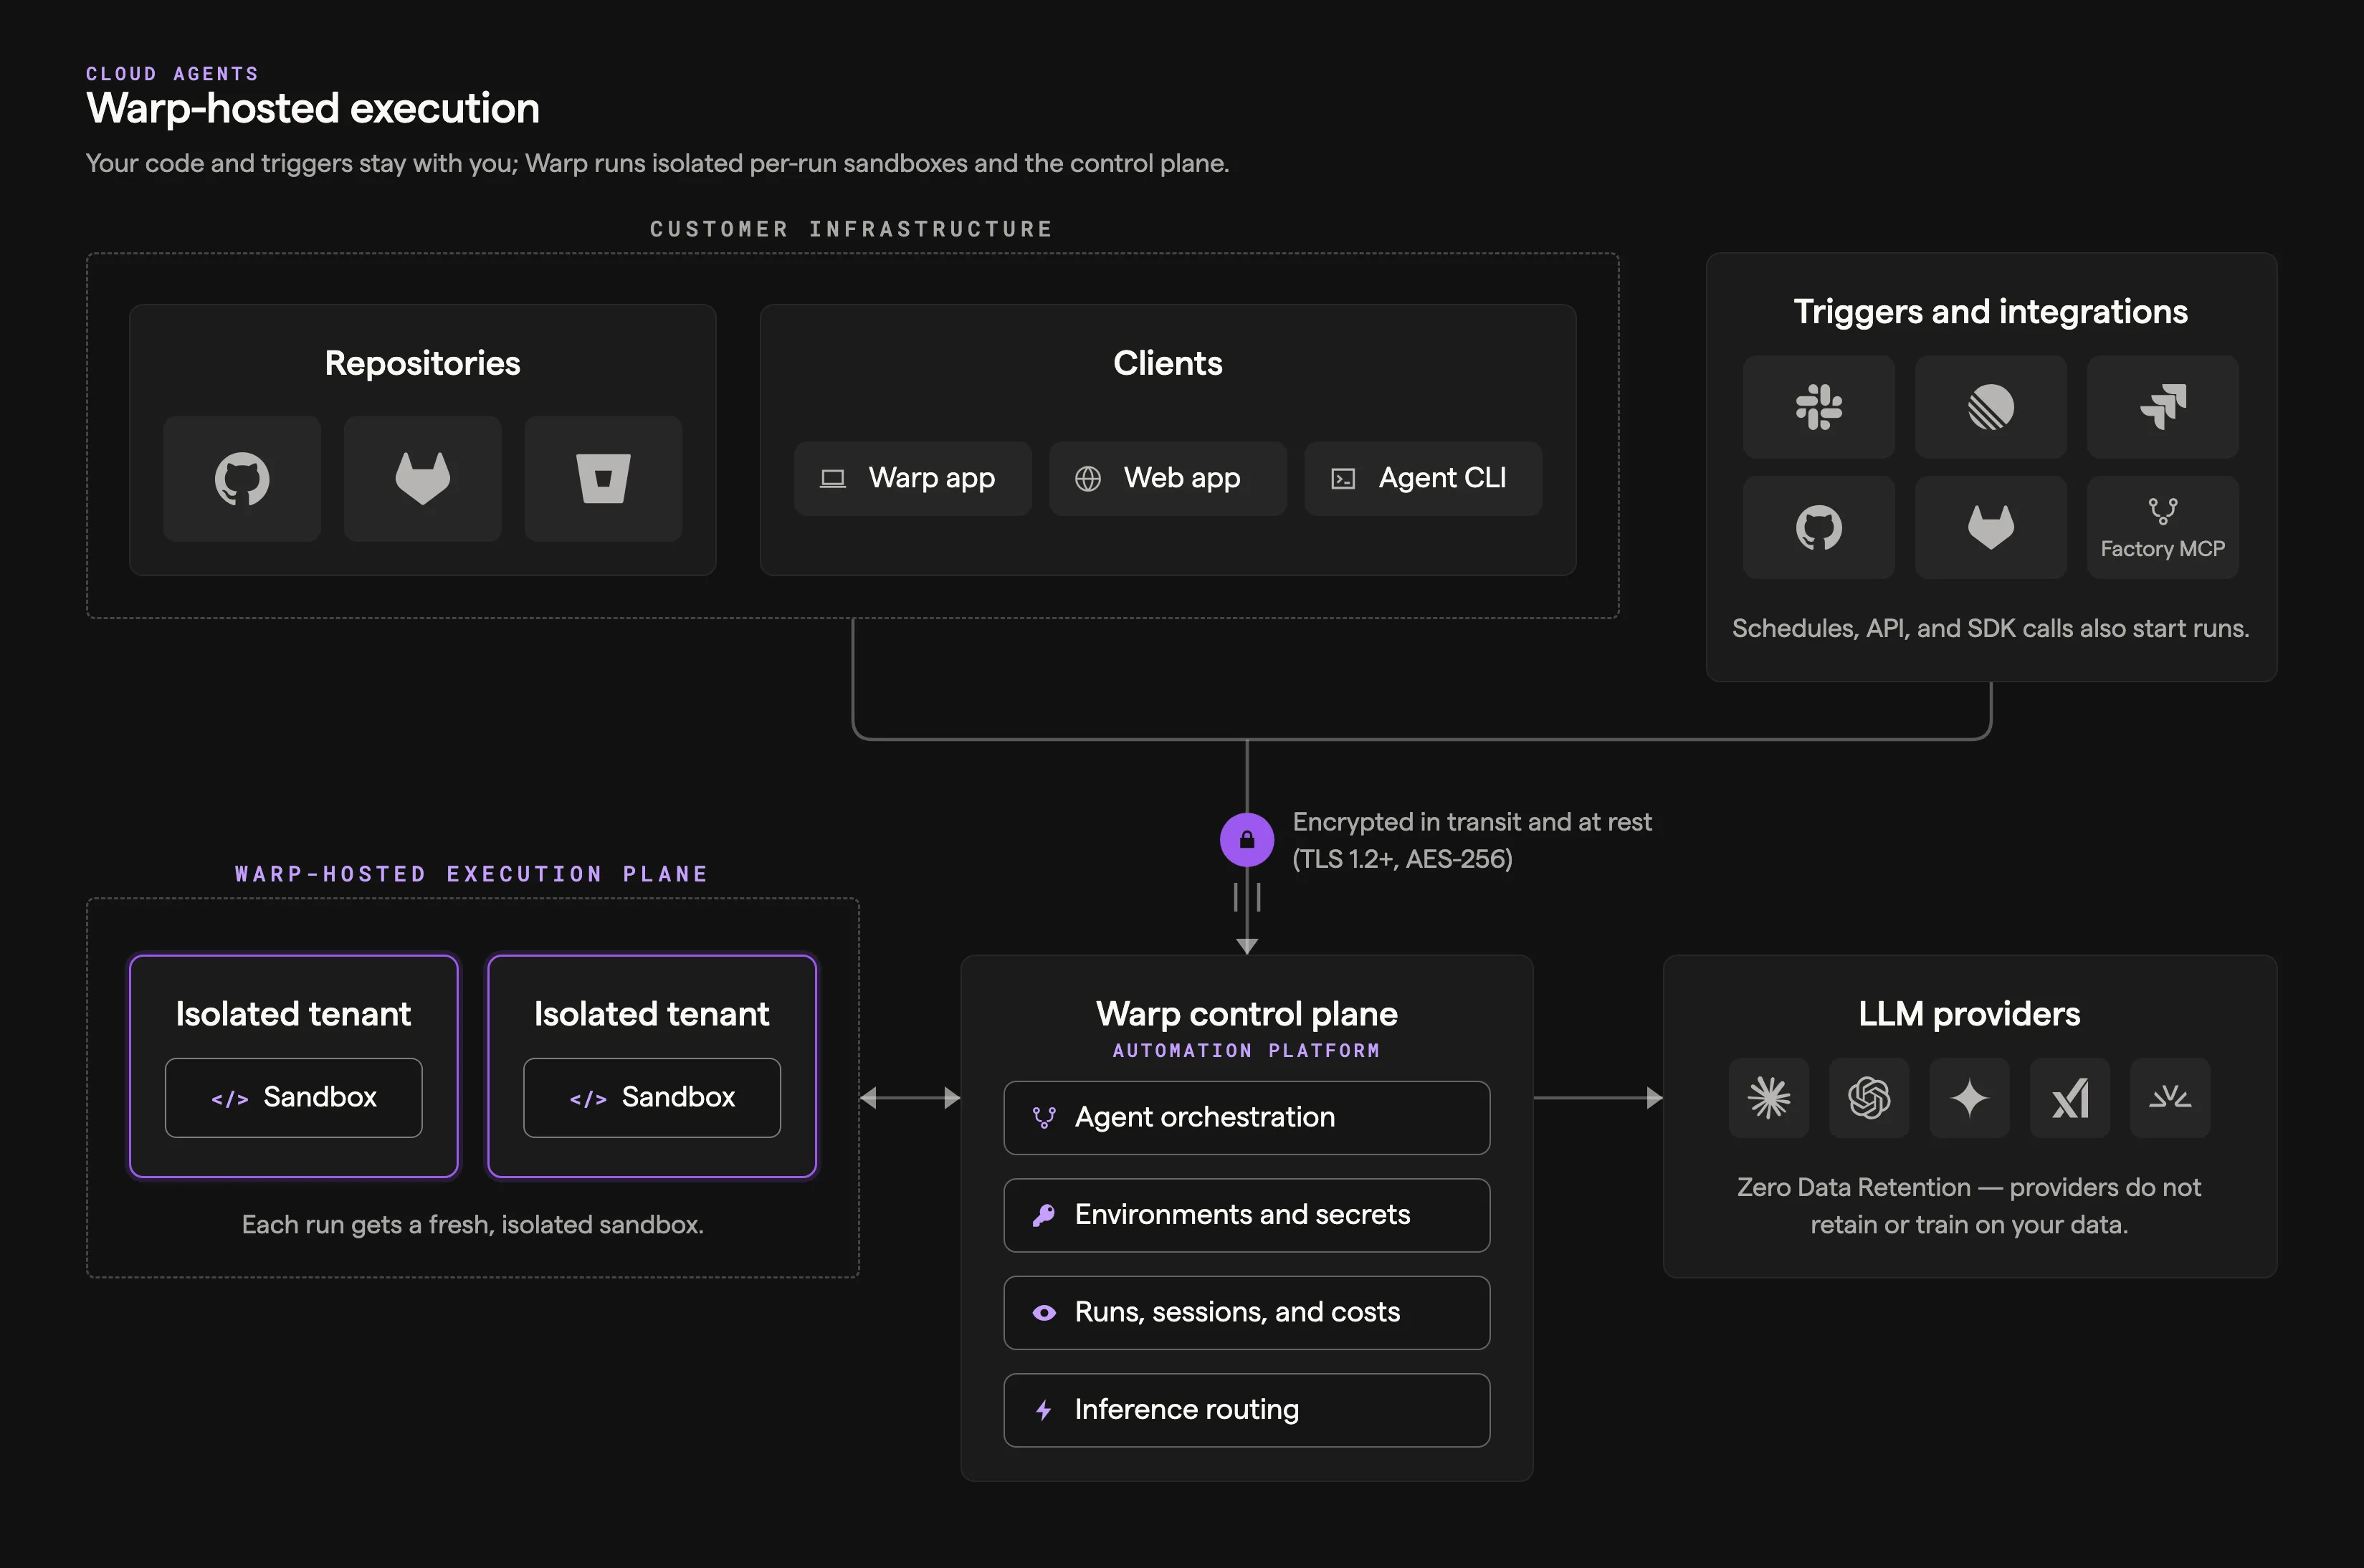
See the [cloud agent run lifecycle](/platform/architecture/#cloud-agent-run-lifecycle) reference for a description of each component in the architecture.
### What it looks like
[Section titled “What it looks like”](#what-it-looks-like)
* **Work intake** - factory automations, configured integrations, Factory MCP, or factory endpoints
* **Execution** - Automation Platform-hosted environments (Docker-based)
* **Visibility** - factory dashboard, session sharing, and APIs
### Send work to a factory
[Section titled “Send work to a factory”](#send-work-to-a-factory)
* [Factory automations](/factories/automations/) route integration events, schedules, and webhooks to agents in the factory.
* [Factory integrations](/factories/connect-your-factory/) let teammates send work from Slack, Linear, Jira, GitHub, and GitLab.
* [Factory endpoints](/factories/factory-api/) let your service find a factory and dispatch work by UID.
* [Factory MCP](/factories/factory-mcp/) lets a coding agent hand work to a factory.
For standalone cloud-agent triggers, see [cloud agents](/platform/).
## Managed self-hosting
[Section titled “Managed self-hosting”](#managed-self-hosting)
Use this when a factory must run checkout and execution on your infrastructure while the Automation Platform coordinates the work and records its results. Managed workers support Docker, Kubernetes, Direct, and external command backends. See [managed self-hosting](/factories/self-hosting/) for requirements and setup.
For standalone agents that you orchestrate directly from CI, Kubernetes, or developer infrastructure, use [unmanaged execution](/platform/unmanaged-execution/). See [execution security](/platform/execution-security/) for the data and network boundaries shared by both architectures.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Infrastructure and security](/factories/infrastructure-and-security/) - Choose execution, inference, storage, and credential boundaries for a factory.
* [Warp-hosted execution](/factories/warp-hosting/) - Review hosted execution capacity, networking, and supported environments.
* [Managed self-hosting](/factories/self-hosting/) - Install and operate a factory worker on your infrastructure.
* [Unmanaged execution](/platform/unmanaged-execution/) - Run standalone agents outside a factory.
# Warp Platform API & SDKs
Canonical page: [/factories/developer-tools/](https://docs.warp.dev/factories/developer-tools/)
> Use the Warp Platform API, SDKs, Factory MCP, and webhooks to integrate factories and cloud agent runs with your tools and services.
The Warp Platform API serves both factories and standalone cloud agent runs. The factory endpoints send work to a factory; agent and run endpoints start and manage standalone runs. Both endpoint families use the same API key, API reference, SDKs, and error model.
## Choose an API surface
[Section titled “Choose an API surface”](#choose-an-api-surface)
* **[Factory endpoints](/factories/factory-api/)** - Find a factory and send work to it by UID from your application or service.
* **[Agent & run endpoints](/factories/api-and-sdk/)** - Start, monitor, continue, and cancel cloud agent runs from scripts, CI, and backend services.
* **[Warp Platform API reference](/api)** - Look up the full HTTP schema, parameters, and responses.
* **[Python SDK](https://github.com/warpdotdev/oz-sdk-python)** - Make typed requests from Python. The current package retains its `oz-sdk-python` name.
* **[TypeScript SDK](https://github.com/warpdotdev/oz-sdk-typescript)** - Make typed requests from TypeScript. The current package retains its `oz-sdk-typescript` name.
* **[API errors](/factories/api-and-sdk/troubleshooting/errors/)** - Resolve error responses by HTTP status and machine-readable code.
* **[Factory MCP](/factories/factory-mcp/)** - Exchange work between a factory and a connected coding agent or MCP client.
* **[Webhooks](/factories/webhooks/)** - Receive events from systems that can send JSON and route matching deliveries into factory automations.
## Get started
[Section titled “Get started”](#get-started)
Start with the [API & SDK quickstart](/factories/api-and-sdk/quickstart/) to create and inspect a run. For a production event source, use the [Sentry monitoring example](/factories/api-and-sdk/demo-sentry-monitoring-with-sdk/) to connect a webhook handler.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Connect your factory](/factories/connect-your-factory/) - Choose an integration or direct intake path.
* [Factory automations](/factories/automations/) - Route events and schedules to factory agents.
* [Factory dashboard](/factories/factory-dashboard/) - Inspect work items, runs, and factory settings.
# Factory agents
Canonical page: [/factories/factory-agents/](https://docs.warp.dev/factories/factory-agents/)
> Every factory has a team of default agents: a foreman that coordinates the work, plus triage, spec, implement, and review agents.
Note
Warp Factories is in **Early Access** and available to a limited set of teams. [Request access](https://www.warp.dev/factories/request-access) to use it with your team.
Every factory has a **foreman**, the agent you talk to from the tool that sends the request, such as Slack or Linear. Four other default agents each cover one part of the software development lifecycle: triage scopes the request, spec writes the plan, implement writes the code, and review checks it. Together they take a work item from the moment it reaches your factory to a pull request ready for review.
## The default agents
[Section titled “The default agents”](#the-default-agents)
Every factory gets a foreman, and you choose one to four other agents to go with it. These defaults are a starting point — you can [add custom agents and automations](#add-custom-agents-and-automations) for work they don’t cover. The default agents’ prompts, descriptions, and models are reproduced as files in [`00-warp-default-agents`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/00-warp-default-agents) in the [warp-factory-examples](https://github.com/warpdotdev/warp-factory-examples) repository.
| Agent | What it does | What it produces |
| --------- | ---------------------------------------------------------------- | ----------------------------------------------------------- |
| Foreman | Coordinates the work and talks to the requester | Decisions, questions, status updates, and the final handoff |
| Triage | Investigates the request and establishes scope | Evidence, issue context, complexity, and open questions |
| Spec | Turns requirements into a concrete plan with validation criteria | Product and technical specs in a draft pull request |
| Implement | Makes and validates the code change | Code, tests, validation results, and visual evidence |
| Review | Independently checks the finished change | Findings and a recommendation |
These are responsibilities, not a fixed pipeline. A small, well-understood change can skip the Planning stage entirely, and review can send work back for another pass. By default, work that goes through Planning needs a human to approve the spec before the Building stage starts.
For the complete lifecycle, see [how Warp Factories work](/factories/how-factories-work/).
### Foreman
[Section titled “Foreman”](#foreman)
The **foreman agent** runs the factory floor. It decides which agent a work item goes to next, hands the work over, and keeps the requester informed. It’s the only default agent that talks to the requester directly. When another agent needs a human answer, the foreman asks the question and routes the answer back. For revisions and follow-ups, the foreman goes back to the same agent and continues its existing conversation instead of starting a new one, so no context is lost.
When the work is done, the foreman presents the final pull request and its supporting evidence, then marks the work item complete. Complete means the work was handed to a human, not that the change was merged or deployed. Merging stays with your team.
#### Foreman name
[Section titled “Foreman name”](#foreman-name)
The foreman answers to a handle your team @-mentions in Slack and Linear, labeled **Foreman name** under **Settings** > **Identity** in the [factory dashboard](/factories/factory-dashboard/) and written as [`alias`](/factories/factory-as-code/#alias) in the definition. Factory setup copies it from the factory’s name, so unless you change one of them, `payments` is the factory’s name and `@payments` reaches its foreman.
They are still two things: the handle addresses the foreman, and the foreman speaks for the factory. Give them different names if the overlap causes confusion on your team.
### Triage
[Section titled “Triage”](#triage)
Triage researches the codebase and related issues first, and reproduces a problem only when research can’t establish the cause. It reports context, scope, complexity, and open questions that the foreman uses to decide whether to ask the requester for clarification, request a spec, or go straight to implementation.
### Spec
[Section titled “Spec”](#spec)
Spec works through the foreman to define requirements, then writes product and technical specifications in a draft pull request with criteria for validating the change. The implement agent later continues that pull request. By default, the foreman waits for a person to approve the spec before implementation starts. Change that in the foreman’s instructions.
### Implement
[Section titled “Implement”](#implement)
Implement continues the spec’s branch and draft pull request rather than starting over. It adds tests, runs the repository’s validation, and, when [computer use](/agents/capabilities/computer-use/) is available, captures visual evidence of user-facing changes. If review finds problems, implement revises. It never merges.
### Review
[Section titled “Review”](#review)
Review independently examines the change for unmet requirements, broken conventions, missing or failing tests, security issues, and evidence that doesn’t hold up. It reruns or extends validation where the evidence is thin, then recommends accepting, revising, or asking a human to decide. The recommendation is advice — review doesn’t approve or merge the pull request.
## Built-in skills
[Section titled “Built-in skills”](#built-in-skills)
Every default agent comes with GitHub skills, and the foreman also comes with a Slack skill. The issue tracker you choose during setup adds to that baseline: choosing Linear or Jira gives the agents that tracker’s skill and instructions. If you don’t choose a tracker, the agents get only the baseline skills. Define custom procedures with [factory skills](/factories/factory-skills/) to extend what an agent can do beyond the built-in set.
## Configure agent behavior
[Section titled “Configure agent behavior”](#configure-agent-behavior)
1. From the [factory dashboard](/factories/factory-dashboard/) sidebar, select your factory and click **Agents**.
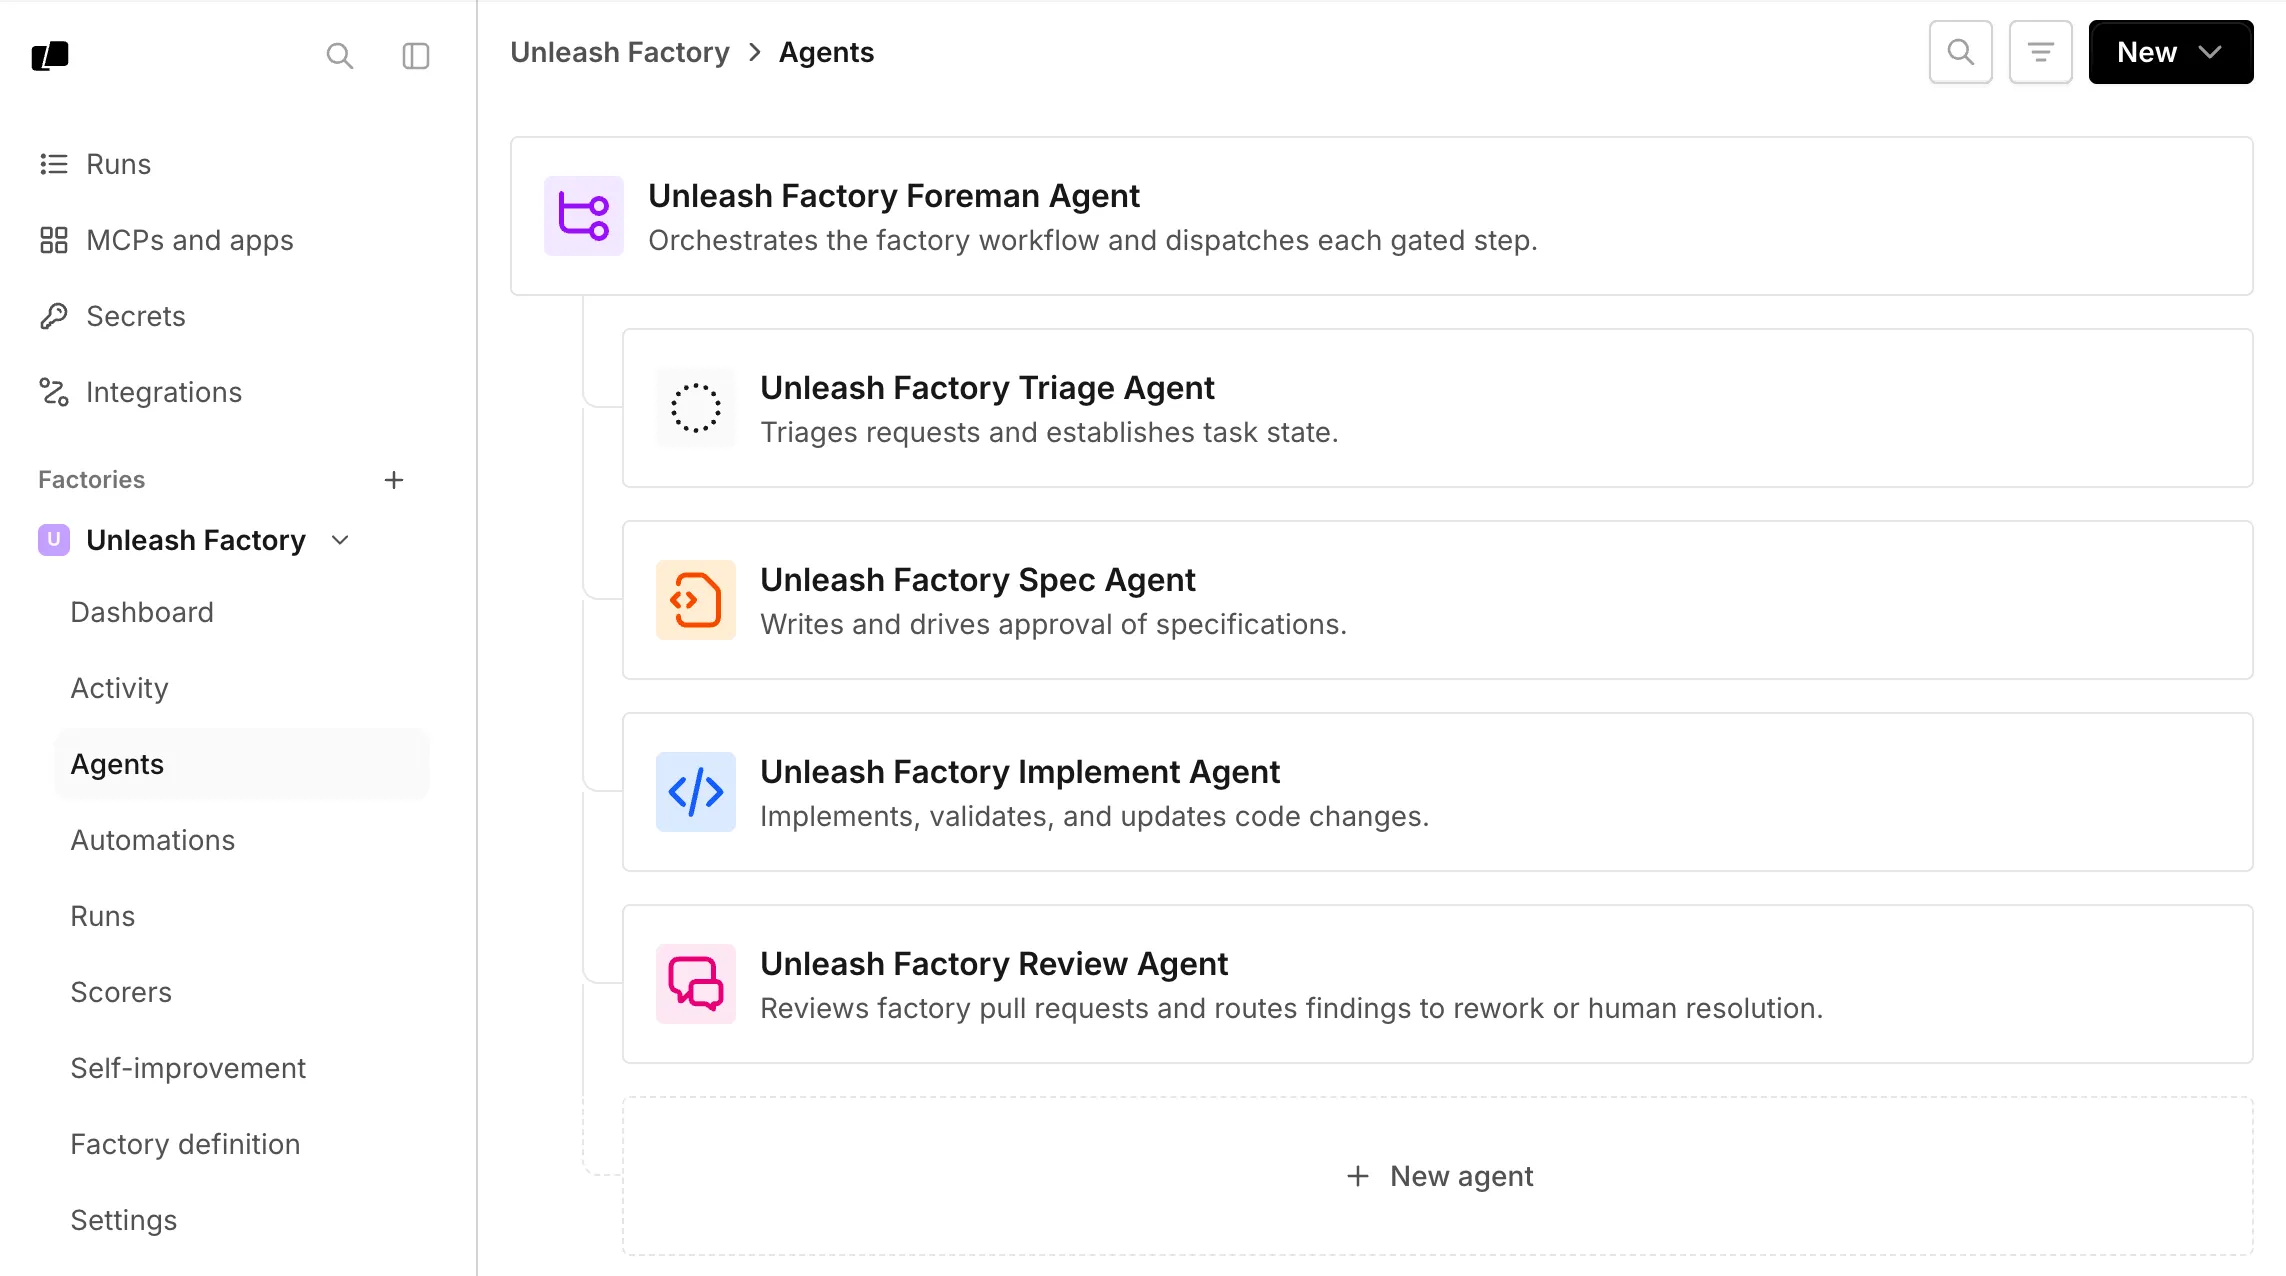
The Agents page lists a factory’s foreman and default agents.
2. Click an agent to open its settings page. From here, you can edit the agent description, harness, model, runner, host, [MCP servers](/platform/mcp/), [secrets](/platform/secrets/), and instructions.

An agent’s settings page, where you configure its model, harness, runner, and host.
You can also manage the factory as version-controlled code with [factory definition files](/factories/factory-as-code/) in a Git repository. A factory’s settings live in one of two places:
* A **Warp-managed factory** lets you edit everything, including harness, auth, and credential strategy, from the dashboard.
* A **GitHub-backed factory** keeps those settings in its definition files. The dashboard shows them read-only, and you edit the files to make changes.
For more information about the two locations, see [where the definition lives](/factories/factory-as-code/#where-the-definition-lives).
Factory setup doesn’t choose models for you. To change the model an agent uses, edit that agent.
## Choose models and harnesses per agent
[Section titled “Choose models and harnesses per agent”](#choose-models-and-harnesses-per-agent)
Each agent can run on its own model and harness. Supported harnesses include the Warp Agent harness, Claude Code, and Codex, and any agent can use any of them. A foreman running on Claude Code or Codex can still dispatch the factory’s other agents, and the runs it starts are still tracked as its children.
Third-party harnesses require a paid plan; on the Free plan every agent runs on the Warp Agent harness. See [Warp pricing](https://www.warp.dev/pricing) for what each plan includes.
Default model IDs change over time, so choose based on what each agent has to do well:
| Agent | What to optimize for |
| --------- | ----------------------------------------------------------------------------------------- |
| Foreman | Orchestration, instruction following, and long-running conversations |
| Triage | Research, evidence gathering, and working with connected tools |
| Spec | Synthesizing requirements, technical reasoning, and precise writing |
| Implement | Coding strength, with a harness that fits your repositories and toolchain |
| Review | A different model or harness from the implement agent, so the two don’t share blind spots |
The model picker also includes custom routers from factories you can access. See [model choice for agents](/agents/inference/model-choice/), [custom model routers](/agents/inference/custom-routers/), and [harnesses for cloud agents](/platform/harnesses/) for available options.
### Configuring a third-party harness
[Section titled “Configuring a third-party harness”](#configuring-a-third-party-harness)
Change an agent’s harness to Claude Code or Codex to run it with that provider’s own coding tool instead of the Warp Agent.
1. From the [factory dashboard](/factories/factory-dashboard/) sidebar, select your factory and click **Agents**.
2. Click an agent to open its settings page. In the “Harness” dropdown, select **Claude Code** or **Codex**.
3. In the **Auth** field, choose a compatible, team-owned secret from the list or click **New auth secret** to create one.

The Auth field’s dropdown, showing a team-owned secret and the option to add a new one.
Note
* Claude Code accepts an Anthropic API key, Anthropic Bedrock API key, or Anthropic Bedrock access key.
* Codex accepts an OpenAI API key.
See [connecting Claude Code credentials](/platform/harnesses/authentication/#connecting-claude-code-credentials) and [connecting Codex credentials](/platform/harnesses/authentication/#connecting-codex-credentials) for how to obtain each key.
4. Choose a **Model** from that harness’s own catalog.
5. In the top-right corner, click **Save**.
With a Warp-managed factory, you can edit harness, auth, and model from the dashboard. A GitHub-backed factory sets them through [`agentDefaults.harness` or a per-agent `harness` override](/factories/factory-as-code/#agentdefaultsharness) in the definition files. For an example, see [`03-multi-harness`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/03-multi-harness).
## Add custom agents and automations
[Section titled “Add custom agents and automations”](#add-custom-agents-and-automations)
Add a custom agent for a role that needs separate instructions, configuration, and runs.
For a Warp-managed factory, open **Agents** in the [factory dashboard](/factories/factory-dashboard/), click **New**, then click **Custom agent**. For a GitHub-backed factory, add `agents/<name>/agent.md`. See the [`agent.md` configuration keys](/factories/factory-as-code/#agentsnameagentmd).
Custom agents have no built-in skills. Add [factory skills](/factories/factory-skills/) based on who needs them:
* **One agent** - Put the skill under `agents/<name>/skills/`.
* **Every agent** - Put the skill under `skills/`.
### Choose a configured factory agent
[Section titled “Choose a configured factory agent”](#choose-a-configured-factory-agent)
Use `run_agents` when the foreman should give work to one of the agents configured in your factory. The foreman receives a list of those agents, with a unique ID (UID) for each one.
Run the child remotely by setting the call’s `remote` field, then copy the chosen agent’s UID into `agent_run_configs[].agent_identity_uid`. Only use UIDs from the list, and select an agent for every child in the call. The `name` field only labels the child run; it doesn’t choose the factory agent.
Warp uses the UID to load that agent’s configured environment, runner, host, harness, and model unless the call overrides them. To start a child without factory configuration, use [multi-agent orchestration](/platform/orchestration/) from any Warp conversation.
Automations start a chosen agent on a [schedule](/factories/factory-as-code/#triggersschedule) or when an event fires. They’re one more way for work to enter your factory; the foreman still coordinates whatever they start. For all the ways to route work into a factory, see [connect your factory](/factories/connect-your-factory/).
## Human decision points and permissions
[Section titled “Human decision points and permissions”](#human-decision-points-and-permissions)
| Decision | Default behavior | What enforces it |
| -------------- | --------------------------------------------------------------------------------------- | ------------------------------------------------------------------------- |
| Spec approval | The foreman asks a human to clarify ambiguity and approve every spec | Workflow policy in the foreman’s instructions, which your team can change |
| Merging | Agents never merge; the foreman hands the finished pull request to a human | Your repository’s permissions decide who can approve and merge |
| Runtime access | Each agent reaches only the repositories, secrets, and MCP servers in its configuration | Platform configuration and the permissions of the connected providers |
The first two rows are conventions: they live in the foreman’s instructions and your repository settings, and your team can change them. Access is different. What an agent can reach comes from its configuration and the permissions of the connected providers, never from its instructions — changing what an agent is told to do doesn’t change what it’s able to do.
So enforce with the real controls: branch protection and repository permissions decide who merges, and each agent’s configuration decides what it can reach.
Next, capture these choices in [factory definitions as code](/factories/factory-as-code/).
# Factory endpoints
Canonical page: [/factories/factory-api/](https://docs.warp.dev/factories/factory-api/)
> Discover factories and dispatch tasks by UID with factory endpoints, without learning the foreman agent's internals.
The factory endpoints are part of the Warp Platform API. Use them to find a factory and start work from a custom integration without managing agent details. Build them into a chat bot, script, or service for any tool Warp doesn’t connect to directly.
Note
Warp Factories is in **Early Access** and available to a limited set of teams. [Request access](https://www.warp.dev/factories/request-access) to use it with your team.
## How it works
[Section titled “How it works”](#how-it-works)
* `GET /factory` - list factories your account can access. Add `search` to filter by name or alias, case-insensitive.
* `GET /factory/{uid}` - get one factory by UID.
* `POST /factory/{uid}/runs` - dispatch a run to the factory’s foreman agent. Pass a `prompt`; the server resolves the foreman for you.
A dispatched run is an ordinary [cloud agent run](/platform/): retrieve it, send it follow-ups, or cancel it through the same [agent and run endpoints](/factories/api-and-sdk/) used for any run.
## Choosing an endpoint family
[Section titled “Choosing an endpoint family”](#choosing-an-endpoint-family)
Use factory endpoints to find or start work on a factory. Use Agent & run endpoints for everything else: a standalone cloud agent, run management, or orchestration.
| Task | Recommended API |
| ---------------------------------------------------------- | -------------------------------------------------------------------------------------------------------------------------- |
| Find a factory by name before dispatching to it | factory endpoints - `GET /factory?search=` |
| Start a new task on a factory | factory endpoints - `POST /factory/{uid}/runs` |
| Continue, monitor, or cancel a run (factory or standalone) | Agent & run endpoints - `GET /agent/runs/{runId}`, `POST /agent/runs/{runId}/followups`, `POST /agent/runs/{runId}/cancel` |
| Run a standalone cloud agent with no factory involved | Agent & run endpoints - `POST /agent/runs` |
| Build a multi-agent orchestration | Agent & run endpoints - see [multi-agent orchestration](/platform/orchestration/) |
Every factory run is still an ordinary run, so Agent & run endpoints handle status, follow-ups, and cancellation no matter which endpoint family started it.
## Discover a factory
[Section titled “Discover a factory”](#discover-a-factory)
### Search factories by name
[Section titled “Search factories by name”](#search-factories-by-name)
```python
import os
from oz_agent_sdk import OzAPI
client = OzAPI(api_key=os.environ.get("WARP_API_KEY"))
# Find a factory by name or alias — no UIDs needed up front
page = client.factories.list(search="payments")
factory = page.factories[0]
# With the pagination scheme wired, iteration auto-pages
for f in client.factories.list(search="payments"):
print(f.uid, f.name)
```
The REST equivalent:
```http
GET /api/v1/factory?search=payments
Authorization: Bearer YOUR_API_KEY
```
### Get a factory when the UID is already known
[Section titled “Get a factory when the UID is already known”](#get-a-factory-when-the-uid-is-already-known)
```python
factory = client.factories.get(factory.uid)
```
```http
GET /api/v1/factory/YOUR_FACTORY_UID
Authorization: Bearer YOUR_API_KEY
```
## Dispatch a run to a factory
[Section titled “Dispatch a run to a factory”](#dispatch-a-run-to-a-factory)
Dispatch with just the factory’s UID and a `prompt`:
```python
run = client.factories.runs.create(
factory.uid,
prompt="Investigate and fix the flaky payment webhook retry test",
title="Fix flaky payment webhook retry test",
ticket_ref="linear:PAY-123",
)
print(run.run_id, run.run_url, run.state)
```
```http
POST /api/v1/factory/YOUR_FACTORY_UID/runs
Authorization: Bearer YOUR_API_KEY
Content-Type: application/json
{
"prompt": "Investigate and fix the flaky payment webhook retry test",
"title": "Fix flaky payment webhook retry test",
"ticket_ref": "linear:PAY-123"
}
```
Every field except `prompt` is optional. Omit `title` and the server derives one from the prompt. `ticket_ref` identifies the originating ticket in `<source>:<id>` form (for example `linear:PAY-123` or `jira:PROJ-456`); pass `ticket_url` to link the factory’s task record back to it, or omit both for an adhoc reference.
## Continue and monitor the run
[Section titled “Continue and monitor the run”](#continue-and-monitor-the-run)
```python
status = client.agent.runs.retrieve(run.run_id)
```
Send a follow-up the same way you would for any run:
```http
POST /api/v1/agent/runs/YOUR_RUN_ID/followups
Authorization: Bearer YOUR_API_KEY
Content-Type: application/json
{
"message": "Also add a regression test for the retry backoff"
}
```
See [key endpoints](/factories/api-and-sdk/#key-endpoints) for the full set of run-management operations, including cancellation.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Connect your factory](/factories/connect-your-factory/) - Every way work can enter a factory, including factory endpoints alongside Slack, GitHub, and Factory MCP.
* [Build a Mattermost bot for Warp Factories](/guides/external-tools/build-a-mattermost-bot-for-warp-factories/) - A worked example that discovers a factory and dispatches and continues a task from a custom chat integration.
* [Factory MCP](/factories/factory-mcp/) - Connect a local coding agent to a factory instead of calling the REST API directly.
* [Agent & run endpoints](/factories/api-and-sdk/) - Full endpoint reference, SDKs, and error codes for the underlying Warp Platform API.
* [How Warp Factories work](/factories/how-factories-work/) - The stages a dispatched task moves through after the foreman picks it up.
# Factory definition syntax
Canonical page: [/factories/factory-as-code/](https://docs.warp.dev/factories/factory-as-code/)
> Look up the files and public keys in a factory definition: factory.yaml, agents, automations, runners, routers, benchmarks, scorers, skills, and webhooks.
Every factory is defined by files: a `factory.yaml` plus directories of agents, automations, runners, model routers, benchmarks, scorers, skills, and webhooks, versioned in a Git repository. The files are the source of truth — when they change, Warp updates the factory to match.
Definition files are YAML and Markdown. Keys are case-sensitive.
For complete working definitions you can copy, see the [warp-factory-examples](https://github.com/warpdotdev/warp-factory-examples) repository. Its examples range from a single-repo quickstart to a full issue-to-PR lifecycle.
## Where the definition lives
[Section titled “Where the definition lives”](#where-the-definition-lives)
You choose who hosts the definition repository when you create a factory:
* **Warp-managed (default)** - Warp hosts the repository for you. You edit the factory in the [Warp Factories web app](/factories/factory-dashboard/), and every change is validated, committed to the files, and applied in one step. You never interact with the repository directly, and the definition can’t end up in an invalid state.
* **GitHub** - On a paid plan, the definition lives in a repository you own. The repository is the only way to change the factory: the web app shows the configuration read-only and links back to the files. Open a pull request, and any change merged to the production branch (`main` by default) updates the factory. See [Pull request checks](#pull-request-checks).
Both modes use the same files, so everything on this page applies to either. You can also link a GitHub repository to a Warp-managed factory later.
Definition files describe how the factory is configured, not what it is doing: work items, runs, and metrics live in the web app and are never written to the files.
## Validate a definition
[Section titled “Validate a definition”](#validate-a-definition)
Warp checks that definition files use valid YAML or Markdown, include required fields, and refer to resources the factory can access. Checks run when you save changes to a Warp-managed factory, when a pull request targets a GitHub-backed factory’s production branch, and before Warp applies a new definition.
### Pull request checks
[Section titled “Pull request checks”](#pull-request-checks)
When the definition lives in GitHub, every pull request that targets the production branch gets a **warp/factory-config** check. It reports problems by file and line. If the definition is valid, the check summarizes what merging will create, update, or delete. A pull request that doesn’t change the definition passes immediately.
Make the check required in your repository’s branch protection rule or ruleset to stop an invalid definition from merging.
When a change lands on the production branch, Warp applies it as a whole: a definition that fails validation never partially applies, and the factory keeps running its last valid definition until the branch is fixed. Warp-managed factories validate each edit when you save it in the web app instead.
For subdirectory check names and troubleshooting, see [factory-definition pull request checks](/factories/integrations/github/#factory-definition-pull-request-checks).
### Validate locally or in CI
[Section titled “Validate locally or in CI”](#validate-locally-or-in-ci)
Use the [`validate_factory_files.py`](https://github.com/warpdotdev/warp-factory-examples/blob/main/scripts/validate_factory_files.py) script to check a definition before you open a pull request or from your own CI. The script needs only Python 3 and doesn’t require a Warp login or an existing factory.
```bash
python3 scripts/validate_factory_files.py path/to/factory-root
```
Run it against the factory root so it can check the complete definition. The script reports problems by file and line. A successful result means the files and their cross-file references are valid; the pull request check also checks settings that depend on your Warp team and current factory.
For a CI job built on the script, see the example repository’s [validation workflow](https://github.com/warpdotdev/warp-factory-examples/blob/main/.github/workflows/validate.yml).
### Validate with a coding agent
[Section titled “Validate with a coding agent”](#validate-with-a-coding-agent)
* **In Warp** - Ask the Warp Agent to change or check a factory definition. Its built-in `factory-files` skill validates the result before opening a pull request. For example: “Add a nightly dependency-audit automation to this factory and validate the definition.”
* **Through Factory MCP** - Connect any other coding agent to [Factory MCP](/factories/factory-mcp/) for the same schema and validation tools. See the [Factory MCP tool reference](/factories/factory-mcp/#tool-reference).
* **Anywhere else** - Have the agent run the [validator script](#validate-locally-or-in-ci).
## JSON Schema
[Section titled “JSON Schema”](#json-schema)
Warp publishes the definition format as JSON Schema documents for editor completion and validation. Each field has a description, and the schema flags unknown fields. The endpoints are unauthenticated:
* `https://app.warp.dev/api/v1/factory-files/schemas` - The supported schema versions, and which one is current.
* `https://app.warp.dev/api/v1/factory-files/schemas/v1alpha1` - Every `v1alpha1` document in one bundle, keyed by document name.
* `https://app.warp.dev/api/v1/factory-files/schemas/v1alpha1/<document>` - One document on its own, usable directly as a schema reference.
There is one document per file kind: `factory.schema.json` for `factory.yaml`; `agent.schema.json`, `automation.schema.json`, and `scorer.schema.json` for the frontmatter of the corresponding Markdown files; `runner.schema.json`, `router.schema.json`, `webhook.schema.json`, `benchmark_suite.schema.json`, and `benchmark_suite_task.schema.json` for the YAML files; and `common.schema.json` for the definitions the others share.
Editors with a YAML language server can read a document from its URL, for completion and inline validation as you type. In VS Code with the YAML extension, add the reference as a comment on the file’s first line:
factory.yaml
```yaml
# yaml-language-server: $schema=https://app.warp.dev/api/v1/factory-files/schemas/v1alpha1/factory.schema.json
schemaVersion: v1alpha1
name: payments-factory
```
Editors apply YAML schemas to `.yaml` files, not to the frontmatter of the Markdown files, so check those with one of the [validation paths](#validate-a-definition) above.
## Directory structure
[Section titled “Directory structure”](#directory-structure)
Each resource takes its name from its path: `agents/reviewer/agent.md` defines an agent named `reviewer`.
```text
factory.yaml
agents/
foreman/
agent.md
skills/
incident-triage/
SKILL.md
reviewer/
agent.md
automations/
labeled-issue/
automation.md
runners/
linux-build.yaml
routers/
by-task.yaml
benchmarks/
pull-request-review/
suite.yaml
tasks/
broken-doc-link.yaml
scorers/
tests-run/
scorer.md
skills/
repository-conventions/
SKILL.md
webhooks/
internal-ci.yaml
```
Only `factory.yaml` and at least one agent are required. For a complete working definition, see the [example factory definition](#example-factory-definition) below. The smallest complete example tree is [`01-single-repo-quickstart`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/01-single-repo-quickstart); the fullest is [`02-sdlc-issue-to-pr`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/02-sdlc-issue-to-pr).
## `factory.yaml`
[Section titled “factory.yaml”](#factoryyaml)
The factory’s root document. It names the factory, scopes it to repositories, and sets the execution defaults every agent inherits.
factory.yaml
```yaml
schemaVersion: v1alpha1
name: payments-factory
repositories:
- owner: acme
name: payments-service
agentDefaults:
model: auto
```
### `schemaVersion`
[Section titled “schemaVersion”](#schemaversion)
Required. The definition schema version. The only supported value is `v1alpha1`.
### `name`
[Section titled “name”](#name)
Required. The factory’s name.
### `description`
[Section titled “description”](#description)
Optional. What the factory is for.
### `alias`
[Section titled “alias”](#alias)
Optional. The handle used to @-mention the factory’s foreman on connected platforms like Slack and Linear; the factory dashboard labels this field **Foreman name**. Up to 60 characters: letters, numbers, spaces, `.`, `_`, and `-`. Must be unique across your workspace (compared case-insensitively).
### `credentialStrategy`
[Section titled “credentialStrategy”](#credentialstrategy)
Optional. Whose credentials the factory’s runs execute with: `EXECUTOR` (the principal executing the run, the default) or `CREATOR` (the user who created the run). `CREATOR` requires a paid plan. Agents can override it per role.
### `codeForges`
[Section titled “codeForges”](#codeforges)
Optional. The code hosts enabled for the factory: `GITHUB`, `GITLAB`, and `AZURE_DEVOPS`. Omit this key to keep the factory’s existing code hosts. To use repositories from more than one host, list each value and set `codeForge` on every repository. An empty `codeForges` list requires an empty `repositories` list and creates a factory with no code host.
### `repositories`
[Section titled “repositories”](#repositories)
Required. The repositories the factory works in. Each entry requires `owner` and `name`; an optional `codeForge` selects `GITHUB`, `GITLAB`, or `AZURE_DEVOPS`. Omit `codeForge` to use the factory’s primary code host. When [`codeForges`](#codeforges) lists more than one host, every repository must declare `codeForge`.
Set `deferred: true` to attach a repository without preparing it for every run. Warp still prepares a deferred repository when an agent or automation lists it in `required_repos`, or when a run adds it explicitly.
```yaml
codeForges:
- GITHUB
- GITLAB
repositories:
- codeForge: GITHUB
owner: acme
name: payments-service
- codeForge: GITLAB
owner: acme/platform
name: deployment-config
```
### `benchmarkRepoSubstitutions`
[Section titled “benchmarkRepoSubstitutions”](#benchmarkreposubstitutions)
Optional. Replaces a GitHub repository from the factory’s scope with an external GitHub repository when a benchmark trial prepares its starting state. Each entry has `source` and `target` objects with `codeForge`, `owner`, and `name`. The source must belong to the factory, and the target must not.
### `secrets`
[Section titled “secrets”](#secrets)
Optional. Names of [managed secrets](/platform/secrets/) granted to every agent in the factory, in addition to anything individual agents declare.
### `mcpServers`
[Section titled “mcpServers”](#mcpservers)
Optional. [MCP servers](/platform/mcp/) granted to every agent, keyed by the name the agent sees. Each entry selects exactly one transport:
* `warpId` - A Warp-managed MCP server ID.
* `command` - A stdio command. Optional `args` is a list of strings, and optional `env` maps names to string values.
* `url` - An absolute HTTP or HTTPS URL. Optional `headers` maps header names to string values.
Don’t put credentials directly in `env` or `headers`. Reference a [Warp-managed secret](/platform/secrets/) as `{{SECRET_NAME}}`, or use `warpId` for a [managed MCP installation](/platform/mcp/#oauth-authentication).
```yaml
mcpServers:
sentry:
warpId: SENTRY_MCP_SERVER_ID
```
### `cloudProviders`
[Section titled “cloudProviders”](#cloudproviders)
Optional. Cloud-provider identity federation for agent runs. `gcp` accepts `projectNumber` (quote it so YAML keeps it a string), `workloadIdentityFederationPoolId`, `workloadIdentityFederationProviderId`, and an optional `serviceAccountEmail`. `aws` accepts `roleArn`.
```yaml
cloudProviders:
aws:
roleArn: arn:aws:iam::123456789012:role/warp-factory
```
### `integrations`
[Section titled “integrations”](#integrations)
Optional. The integration providers attached to the factory. Supported types include `slack`, `microsoft-teams`, `linear`, and `jira`. Declare at most one issue tracker: `linear` and `jira` are mutually exclusive, and omitting a tracker is also valid. Code-forge access comes from `repositories`, not this list.
```yaml
integrations:
- type: slack
- type: linear
```
For Slack and Microsoft Teams, `autoRespondToThreadReplies` controls whether eligible plain replies in an existing factory thread can continue work without another mention. It defaults to `true`.
```yaml
integrations:
- type: slack
slack:
autoRespondToThreadReplies: false
```
The legacy `linear.teamIds` and `jira.projectKeys` settings are accepted when reading older definitions, but they no longer control issue discovery. Scope Linear and Jira events with automation filters instead.
The legacy `providers` key is accepted when reading older definitions. Use `cloudProviders`; when Warp rewrites the definition, it emits `cloudProviders`.
### `scorerDefaults`
[Section titled “scorerDefaults”](#scorerdefaults)
Optional. Sets `runner`, `secrets`, and `mcpServers` for every file-defined scorer. A scorer can override any of these values.
### `selfImprovement`
[Section titled “selfImprovement”](#selfimprovement)
Optional. Configures scheduled self-improvement for a GitHub-backed factory:
* `failedRunThreshold` - Distinct scored failures per agent required before a scheduled self-improvement run. Use a value from 1 through 50, or omit it for the server default.
* `reviewerType` - The pool used to request one reviewer: `admins` (the default), `team`, `custom`, or `none`.
* `reviewerEmails` - Active members of the factory’s team to use when `reviewerType` is `custom`.
### `agentDefaults`
[Section titled “agentDefaults”](#agentdefaults)
Required. The execution defaults every agent inherits. Declare exactly one of `model` or `harness`; the other keys are optional. An agent that sets one of these keys for itself overrides the default.
```yaml
agentDefaults:
model: auto
runner: linux-build
environmentId: PAYMENTS_ENVIRONMENT_ID
```
### `agentDefaults.model`
[Section titled “agentDefaults.model”](#agentdefaultsmodel)
The model that runs execute with, as a `model_id` from [model choice for agents](/agents/inference/model-choice/). `model` is shorthand for running on the Warp Agent harness:
```yaml
model: auto
```
is equivalent to:
```yaml
harness:
type: oz
model: auto
```
`model` and `harness` are mutually exclusive everywhere they appear.
### `agentDefaults.harness`
[Section titled “agentDefaults.harness”](#agentdefaultsharness)
The harness and model that runs execute with. Use the `harness` form to run a third-party harness or to set advanced options. Supported values are `oz`, `claude`, and `codex`. `claude-code` is also accepted as an alias for `claude`; prefer `claude`, the canonical [harness identifier](/platform/harnesses/#harness-identifiers) that the CLI and the Warp Platform API use for the same harness. For what each harness does and which ones your team can run, see [supported harnesses](/platform/harnesses/).
```yaml
harness:
type: codex
model: gpt-5.3-codex
reasoningLevel: high
auth:
source: managedSecret
secretName: CODEX_API_KEY
```
For a third-party harness, `auth` sets where credentials come from: `source: managedSecret` reads the [managed secret](/platform/secrets/) named by `secretName`, and `source: workerEnvironment` reads them from your self-hosted worker’s environment (and requires a self-hosted `workerHost`). The `oz` harness supplies its own credentials and takes no `auth` or `reasoningLevel`.
For a definition that runs a different harness per agent, with managed-secret auth for Claude Code and Codex, see [`03-multi-harness`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/03-multi-harness). To configure the same third-party harness from the dashboard instead, see [configuring a third-party harness](/factories/factory-agents/#configuring-a-third-party-harness).
### `agentDefaults.runner`
[Section titled “agentDefaults.runner”](#agentdefaultsrunner)
The name of a runner defined under [`runners/`](#runnersnameyaml) that provides the compute for runs.
### `agentDefaults.environmentId`
[Section titled “agentDefaults.environmentId”](#agentdefaultsenvironmentid)
The ID of an existing [environment](/platform/environments/) that runs execute in. Most factories never set this: leave it out, and Warp manages the workspace from the factory’s repositories.
### `agentDefaults.secrets`
[Section titled “agentDefaults.secrets”](#agentdefaultssecrets)
Managed secrets for agents that don’t declare their own. An agent that declares `secrets` replaces this list rather than adding to it; factory-wide [`secrets`](#secrets) always apply.
### `agentDefaults.mcpServers`
[Section titled “agentDefaults.mcpServers”](#agentdefaultsmcpservers)
MCP servers for agents that don’t declare their own, in the same form as [`mcpServers`](#mcpservers). Like secrets, an agent that declares its own map replaces this one, and factory-wide servers always apply.
### `agentDefaults.workerHost`
[Section titled “agentDefaults.workerHost”](#agentdefaultsworkerhost)
Where runs execute: `warp` for Warp-hosted compute, or the ID of a connected [self-hosted worker](/factories/self-hosting/). Omit the key to use the workspace default. At the agent or automation level, set it to `null` or an empty string to clear an inherited host and return to the workspace default. Configure the worker’s Docker, Kubernetes, or Direct backend on the worker itself; the factory definition selects the worker and runner.
### `agentDefaults.computerUseModel`
[Section titled “agentDefaults.computerUseModel”](#agentdefaultscomputerusemodel)
Optional. The `model_id` that Computer Use runs with. Omit it to let Warp select the model automatically.
```yaml
agentDefaults:
model: auto
computerUseModel: claude-5-sonnet-high
```
Use `computer-use-agent-auto` for automatic selection. Pin a specific model when a benchmark or other repeatable workflow needs a fixed model. For models with multiple variants, the suffix selects the effort level; `thinking` enables thinking, and `xhigh-fast` selects fast mode.
| Model | Supported values |
| ----------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------- |
| Auto | `computer-use-agent-auto` |
| Claude Sonnet 5 | `claude-5-sonnet-low`, `claude-5-sonnet-medium`, `claude-5-sonnet-high`, `claude-5-sonnet-xhigh`, `claude-5-sonnet-max` |
| Claude Opus 5 | `claude-5-opus-low`, `claude-5-opus-medium`, `claude-5-opus-high`, `claude-5-opus-xhigh`, `claude-5-opus-xhigh-fast`, `claude-5-opus-max` |
| Claude Fable 5.1 | `claude-5-1-fable-low`, `claude-5-1-fable-medium`, `claude-5-1-fable-high`, `claude-5-1-fable-xhigh`, `claude-5-1-fable-max` |
| Claude Fable 5 | `claude-5-fable-low`, `claude-5-fable-medium`, `claude-5-fable-high`, `claude-5-fable-xhigh`, `claude-5-fable-max` |
| Claude Opus 4.8 | `claude-4-8-opus-low`, `claude-4-8-opus-medium`, `claude-4-8-opus-high`, `claude-4-8-opus-xhigh`, `claude-4-8-opus-xhigh-fast`, `claude-4-8-opus-max` |
| Claude Opus 4.7 | `claude-4-7-opus-high`, `claude-4-7-opus-xhigh`, `claude-4-7-opus-max` |
| Claude Opus 4.6 | `claude-4-6-opus-high`, `claude-4-6-opus-max` |
| Claude Sonnet 4.6 | `claude-4-6-sonnet-high`, `claude-4-6-sonnet-max` |
| Claude Opus 4.5 | `claude-4-5-opus`, `claude-4-5-opus-thinking` |
| Claude Sonnet 4.5 | `claude-4-5-sonnet`, `claude-4-5-sonnet-thinking` |
| Claude Haiku 4.5 | `claude-4-5-haiku` |
The selected value must be available to your plan and workspace. See [model choice for agents](/agents/inference/model-choice/) for model variants, availability, and data-retention details.
An agent or automation can declare `computerUseModel` to override the inherited value for its runs. For an agent, omitting the key or setting it to `null` inherits `agentDefaults.computerUseModel`. For an automation, omitting the key or setting it to `null` inherits the selected agent’s effective value, including an agent-level override. The setting applies only to Computer Use on the Warp Agent harness (`type: oz`); Warp keeps but ignores it for a third-party harness or when Computer Use is disabled. It can appear alongside either `model` or `harness` because it doesn’t select the agent’s main model.
## `agents/<name>/agent.md`
[Section titled “agents/\<name>/agent.md”](#agentsnameagentmd)
One file per agent. The YAML frontmatter configures how the agent runs, and the Markdown body is the agent’s prompt: the durable instructions for its role. The agent’s name comes from its directory.
agents/reviewer/agent.md
```markdown
---
description: Reviews factory-produced pull requests
agentType: REVIEW
---
Review each pull request against the repository's standards. Request
changes when tests are missing; never approve your own edits.
```
The frontmatter accepts:
* `description` - Optional. What the agent does.
* [`agentType`](#agenttype) - Optional. The agent’s role.
* `credentialStrategy` - Optional. Overrides the factory-level [`credentialStrategy`](#credentialstrategy) for this agent’s runs.
* `spawnableBy` - Optional. The factory agents allowed to start this agent. Omit it to allow only the foreman, use an empty list to allow none, or list the exact agent names that can start it.
* `model` or `harness`, `runner`, `environmentId`, `secrets`, `mcpServers`, `workerHost`, `computerUseModel` - Optional. The same keys as [`agentDefaults`](#agentdefaults); a key declared here overrides the default for this agent.
* `idleTimeoutMinutes` - Optional. How long a completed session remains available for follow-up, from 1 through 60 minutes.
* `required_repos` - Optional. Repositories that Warp prepares for every run by this agent. Each entry uses `owner`, `name`, and, when needed to disambiguate the same repository across hosts, `codeForge`.
### `agentType`
[Section titled “agentType”](#agenttype)
The agent’s role: `CUSTOM` (the default), `FOREMAN` (alias `MAIN`), `TRIAGE`, `SPEC`, `IMPLEMENT`, `REVIEW`, or `VERIFY`. Every definition declares exactly one foreman — the factory’s entry point and the default target for automations. See [factory agents](/factories/factory-agents/) for what each role does.
## `automations/<name>/automation.md`
[Section titled “automations/\<name>/automation.md”](#automationsnameautomationmd)
One file per automation. The frontmatter declares when runs start and how they execute, and the Markdown body is the prompt each run starts with. The automation’s name comes from its directory.
automations/labeled-issue/automation.md
```markdown
---
agent: foreman
triggers:
- provider: github
event: issue_labeled
filter:
repos: [acme/payments-service]
labels: [factory-ready]
---
Review the labeled issue and decide the next required stage. Return
unresolved product questions to a human.
```
### `enabled`
[Section titled “enabled”](#enabled)
Optional. Turns the automation on or off. Defaults to `true`.
### `agent`
[Section titled “agent”](#agent)
Optional. The name of the agent that handles this automation’s runs. Defaults to the foreman.
### `triggers`
[Section titled “triggers”](#triggers)
Required. One or more events that start runs. Each trigger declares a `provider` and an `event`, an optional `filter`, and, for schedules, a `schedule`.
The providers and their events:
* `azure_devops` - `pull_request_closed`, `pull_request_commented`, `pull_request_created`, `pull_request_mentioned`, `pull_request_merged`, `pull_request_updated`, `push`, `work_item_assigned`, `work_item_created`, `work_item_labeled`, `work_item_mentioned`
* `github` - `check_run_rerequested`, `check_suite_completed`, `check_suite_rerequested`, `issue_assigned`, `issue_commented`, `issue_created`, `issue_labeled`, `issue_mentioned`, `pull_request_assigned`, `pull_request_closed`, `pull_request_commented`, `pull_request_labeled`, `pull_request_mentioned`, `pull_request_merged`, `pull_request_opened`, `pull_request_ready`, `pull_request_reopened`, `pull_request_review_requested`, `pull_request_review_submitted`, `pull_request_synchronized`, `push`, `workflow_run_completed`
* `gitlab` - `bot_mentioned`, `merge_request`, `push`
* `linear` - `agent_session_created`, `comment_created`, `issue_assigned`, `issue_created`, `issue_labeled`, `issue_state_changed`
* `jira` - `agent_session_created`, `issue_created`, `issue_labeled`, `status_changed`
* `slack` - `app_mention`, `member_joined_channel`, `message_dm`, `message_im`, `message_mpim`, `message_posted`, `reaction_added`
* `schedule` - `cron_fired`
* `webhook` - `received`
* `factory` - `work_item_stage_changed`
Slack, Linear, and Jira triggers require the matching [integration](/platform/integrations/) to be connected. Code-forge triggers use the factory’s repositories and provider connection; see the [GitHub](/factories/integrations/github/), [GitLab](/factories/integrations/gitlab/), and [Azure DevOps](/factories/integrations/azure-devops/) integration guides. `webhook` triggers listen to [custom webhooks](/factories/webhooks/) declared under [`webhooks/`](#webhooksnameyaml).
### `triggers[].filter`
[Section titled “triggers\[\].filter”](#triggersfilter)
Optional. Narrows which events start runs. The keys a filter accepts depend on the provider and event: for example `repos`, `labels`, and `authors` for GitHub events, or `channels`, `users`, and `keywords` for Slack messages. Filter keys combine with AND, an omitted key matches everything, and each key takes a list that matches any of its values (or an `in`/`not_in` object to include or exclude). Slack and Linear filters take names (channels, users, teams, projects, states), and Warp resolves them to IDs when it applies the change.
A `webhook` trigger with the `received` event requires `webhook_ids` in its filter. This field is a one-item list containing exactly one webhook UID (`in` only; the file name isn’t accepted). To listen to multiple webhooks, add a separate trigger with provider `webhook` and event `received` for each UID. The trigger also takes an optional `payload` pattern that mirrors the delivery’s JSON body. See [payload filters for webhook triggers](/factories/automations/#payload-filters-for-webhook-triggers) for the pattern grammar.
The published trigger catalog currently uses these filter keys across its provider and event combinations:
* Factory: `stages`.
* Azure DevOps: `assignees`, `authors`, `base_branches`, `branches`, `labels`, `mentioned`, `repos`, `source_repos`, and `work_item_types`.
* GitHub: `assignees`, `authors`, `baseBranches`, `base_branches`, `branches`, `conclusions`, `labels`, `mentioned`, `paths`, `prNumbers`, `pr_numbers`, `repos`, `review_states`, `reviewer_teams`, `reviewers`, and `workflows`.
* GitLab: `actions`, `base_branches`, `branches`, `mentioned`, and `repos`.
* Jira: `keywords`, `labels`, `project_keys`, and `status_ids`.
* Linear: `assignee_ids`, `creator_ids`, `issue_ids`, `issues`, `keywords`, `labels`, `mentioned_user_ids`, `project_ids`, `projects`, `state_ids`, `states`, `team_ids`, and `teams`.
* Schedule: `schedule_ids` is server-managed and cannot be set in a factory definition.
* Slack: `channel_ids`, `channels`, `emojis`, `itemUsers`, `item_user_ids`, `keywords`, `user_ids`, and `users`.
* Webhook: `payload` and `webhook_ids`.
Payload patterns also accept `exists`.
`baseBranches` and `prNumbers` are authoring aliases for `base_branches` and `pr_numbers`. `teams`, `projects`, `states`, `issues`, `channels`, `users`, and `itemUsers` are name-based aliases for their `_ids` counterparts. An alias and its canonical key are mutually exclusive.
```yaml
triggers:
- provider: webhook
event: received
filter:
webhook_ids: [WEBHOOK_UID]
payload:
status: [failed]
```
### `triggers[].schedule`
[Section titled “triggers\[\].schedule”](#triggersschedule)
Declares a cron schedule inline on a `schedule` / `cron_fired` trigger: a five-field cron expression or a descriptor like `@daily` or `@every 1h`, always interpreted in UTC. An optional `name` distinguishes multiple schedules on one automation.
```yaml
triggers:
- provider: schedule
event: cron_fired
schedule:
name: weekday-mornings
cron: "0 9 * * 1-5"
```
### Execution overrides
[Section titled “Execution overrides”](#execution-overrides)
An automation may also declare `displayName`, plus `model` or `harness`, `runner`, `environmentId`, `secrets`, `mcpServers`, `workerHost`, `computerUseModel`, `idleTimeoutMinutes`, and `required_repos`. Execution settings override the target agent for runs this automation starts. Automation `required_repos` entries are added to the target agent’s required repositories.
## `runners/<name>.yaml`
[Section titled “runners/\<name>.yaml”](#runnersnameyaml)
Optional. Each file defines a runner: the compute a run executes on. The runner’s name comes from the file name, and agents and automations select it by that name. See [cloud agent runners](/factories/runners/) for how runners behave. For three runners selected per agent, including a macOS runner, see [`02-sdlc-issue-to-pr`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/02-sdlc-issue-to-pr).
runners/linux-build.yaml
```yaml
description: Linux runner for payments builds and tests
setupCommands:
- corepack enable
instanceShape:
vcpus: 4
memoryGb: 8
platform:
os: linux
arch: x86_64
linux:
dockerImage: ubuntu:22.04
```
### `setupCommands`
[Section titled “setupCommands”](#setupcommands)
Optional. Shell commands run in order while the sandbox is prepared.
### `instanceShape`
[Section titled “instanceShape”](#instanceshape)
Optional. The compute size, as `vcpus` and `memoryGb`. Omit it to take the workspace default.
### `platform`
[Section titled “platform”](#platform)
The operating system and architecture. `os` is `linux` (the default), `macos`, or `windows`. `arch` is `x86_64` (the default on Linux and the only option on Windows) or `aarch64` (supported on Linux and required on macOS). Linux runners require `linux.dockerImage`, the container image the sandbox boots, so every Linux runner declares a `platform` section. macOS runners accept an optional `mac.version` (`"14"`, `"15"`, `"26"`, or `"27"`; quote it, and it defaults to `"26"`).
For a private Linux image, set `linux.registryCredentialSecretName` to the name of a managed `docker_registry` secret. The secret’s registry host must match the host in `linux.dockerImage`.
### `failureSessionRetentionMinutes`
[Section titled “failureSessionRetentionMinutes”](#failuresessionretentionminutes)
Optional. Keeps a failed session open for inspection for 1 through 60 minutes. Omit it to use the environment’s setting.
## `routers/<name>.yaml`
[Section titled “routers/\<name>.yaml”](#routersnameyaml)
Optional. Each file defines a factory-owned custom model router. Use the file name as a value anywhere the definition accepts a model. `name` is an optional display label, `type` is `complexity` or `prompt`, and `default` is the concrete model to use when no route matches.
routers/by-task.yaml
```yaml
name: By task
type: prompt
default: claude-4-6-sonnet-high
routing:
- description: Routine documentation changes
model: claude-4-5-haiku
- description: Complex implementation or debugging
model: claude-4-8-opus-high
```
For `type: complexity`, `routing` maps `easy`, `medium`, and `hard` to concrete models. For `type: prompt`, `routing` is an ordered list of `description` and `model` pairs. Router targets must be concrete supported models, not Auto models or other routers. See [custom model routers](/agents/inference/custom-routers/) for routing behavior.
Factory members who can access the router can also select it from model catalogs in the factory dashboard, including agent settings and benchmark configurations.
## `benchmarks/<suite-slug>/suite.yaml`
[Section titled “benchmarks/\<suite-slug>/suite.yaml”](#benchmarkssuite-slugsuiteyaml)
Optional. This file defines a [benchmark suite](/factories/benchmarks/): one agent, optional reusable configurations, and an ordered set of reusable tasks. The suite slug is its stable file location, not its display name, so renaming `name` does not move the file or change the suite’s identity.
benchmarks/pull-request-review/suite.yaml
```yaml
name: Pull request review
description: Compare configurations for the review agent.
agent: reviewer
configurations:
- name: Baseline
agents:
- agent: reviewer
model: auto
- name: Candidate
agents:
- agent: reviewer
model: auto-efficient
tasks:
- broken-doc-link
```
### `name`
[Section titled “name”](#name-1)
Required. The suite display name. It must be unique in the factory.
### `description`
[Section titled “description”](#description-1)
Optional. A short summary of what the suite measures.
### `agent`
[Section titled “agent”](#agent-1)
Required. The name of an agent declared by the factory. Every task in the suite runs as this agent.
### `configurations`
[Section titled “configurations”](#configurations)
Optional. One to six reusable configurations for benchmark runs. When a run doesn’t supply its own configurations, Warp uses these presets. Each configuration requires a unique `name`.
The optional `agents` list pins named factory agents to the models and harnesses they use during that configuration’s trials. Each entry requires `agent` and exactly one of `model` or `harness`. A `harness` override requires `type` and `model` and optionally accepts `auth`. List an agent at most once per configuration. Agents omitted from the list use their configuration at launch time.
### `tasks`
[Section titled “tasks”](#tasks)
Optional. An ordered list of unique task slugs. Each slug must match exactly one file under `benchmarks/<suite-slug>/tasks/`, and every task file must appear once in this list. A suite without tasks saves successfully but cannot run.
## `benchmarks/<suite-slug>/tasks/<task-slug>.yaml`
[Section titled “benchmarks/\<suite-slug>/tasks/\<task-slug>.yaml”](#benchmarkssuite-slugtaskstask-slugyaml)
Optional. Each file defines one task in its parent suite. The task slug is the file name without `.yaml` and stays stable when you change the task’s title.
benchmarks/pull-request-review/tasks/broken-doc-link.yaml
```yaml
title: Fix a broken documentation link
prompt: Find the broken internal documentation link and update it.
successCriteria: The destination resolves and the link text names the destination.
startingRepoRefs:
- github.com:acme/payments-docs@0123456789abcdef0123456789abcdef01234567
```
### `title`
[Section titled “title”](#title)
Required. The task display name. It does not need to match the task slug.
### `prompt`
[Section titled “prompt”](#prompt)
Required. The instructions the agent receives for the task.
### `successCriteria`
[Section titled “successCriteria”](#successcriteria)
Required. The requirements the Correctness Scorer uses to evaluate each trial.
### `sourceRunId`
[Section titled “sourceRunId”](#sourcerunid)
Optional. The ID of the prior run the task came from. This records provenance only and can refer to a deleted run.
### `tags`
[Section titled “tags”](#tags)
Optional. An ordered list of labels for the task.
### `linearSeed`
[Section titled “linearSeed”](#linearseed)
Optional. JSON-compatible starting state for the isolated Linear workspace used by the benchmark trial.
### `startingRepoRefs`
[Section titled “startingRepoRefs”](#startingreporefs)
Optional. The GitHub or GitLab repositories and exact commits the task starts from. Each entry can use `github.com:OWNER/REPO@COMMIT_SHA` or `gitlab.com:OWNER/REPO@COMMIT_SHA`. It can instead use an object with `codeForge` (`GITHUB` or `GITLAB`), `owner`, `repo`, and `ref`. `COMMIT_SHA` and `ref` must be full 40-character commit SHAs, not branches or tags. Omit this key to use the agent’s normal checkout defaults.
## `scorers/<name>/scorer.md`
[Section titled “scorers/\<name>/scorer.md”](#scorersnamescorermd)
Optional. Each file defines a scorer: an LLM judge that classifies a sample of an agent’s finished runs against a rubric. The directory segment is only a stable filesystem slug — the required `name` field is the scorer’s identity. The YAML frontmatter declares the classification contract, and the Markdown body after the closing `---` fence is the rubric. See [Configuring Scorers](/factories/measure-and-improve/scorers/) for how scores are used.
scorers/tests-run/scorer.md
```markdown
---
name: tests-run
description: Checks whether implementation runs include test evidence.
agents:
- reviewer
labels:
- value: tests_run
description: The transcript contains a test command and its result.
score: 1
- value: tests_skipped
score: 0
passingScore: 1
samplingRate: 25
model: claude-4-5-haiku
---
Evaluate whether the agent ran the relevant tests before finishing. Return
exactly one declared label.
```
### `name`
[Section titled “name”](#name-2)
Required. The scorer’s identity. Renaming it is a content edit, not a directory move.
### `description`
[Section titled “description”](#description-2)
Optional. A short summary of what the scorer checks.
### `agents`
[Section titled “agents”](#agents)
Required. The agents whose runs this scorer evaluates. A string names one agent and scores that run alone. To include an agent’s child runs as evidence, use an object with `name` and `includeDescendants: true`.
```yaml
agents:
- name: foreman
includeDescendants: true
```
### Scorer execution settings
[Section titled “Scorer execution settings”](#scorer-execution-settings)
Optional `runner`, `secrets`, and `mcpServers` keys override the factory’s `scorerDefaults` for this scorer. Use `scorerDefaults` in `factory.yaml` to set those values for every file-defined scorer.
### `output`
[Section titled “output”](#output)
Optional. The scorer output form. `classification` is the current supported value.
### `labels`
[Section titled “labels”](#labels)
Required. The classifications the judge may return, each with a `value`, a numeric `score` from 0 through 1, and an optional `description`. At least one label must score at or above `passingScore` and at least one below it.
### `passingScore`
[Section titled “passingScore”](#passingscore)
Required. The threshold, from 0 through 1, at or above which a run counts as passing.
### `samplingRate`
[Section titled “samplingRate”](#samplingrate)
Optional. The percentage of eligible runs to score. Defaults to 25.
### `model`
[Section titled “model”](#model)
Required. The model that judges the runs.
### `selfImprovement`
[Section titled “selfImprovement”](#selfimprovement-1)
Optional. When `true`, failing scores can feed the factory’s self-improvement flow, which proposes definition changes as pull requests. Defaults to `false`.
## `webhooks/<name>.yaml`
[Section titled “webhooks/\<name>.yaml”](#webhooksnameyaml)
Optional. Each file defines a [custom webhook](/factories/webhooks/): an authenticated URL that external systems POST JSON to, which `webhook` triggers on automations subscribe to. The webhook’s name comes from the file name. The file never holds the secret itself: `secretName` references a [managed secret](/platform/secrets/) that already exists on the team, and Warp never generates one for a file-declared webhook.
webhooks/internal-ci.yaml
```yaml
authMode: token
secretName: INTERNAL_CI_WEBHOOK_SECRET
deliveryIdHeader: X-CI-Run-Id
enabled: true
```
### `authMode`
[Section titled “authMode”](#authmode)
Optional. How deliveries authenticate: `token` (the default, an `Authorization: Bearer` header), `url_token` (the secret embedded in the URL path), or `signature` (the sending provider’s own signature scheme). See [authentication modes](/factories/webhooks/#authentication-modes) for how each works.
### `signatureScheme`
[Section titled “signatureScheme”](#signaturescheme)
The provider signature to verify: `github`, `pagerduty`, `sentry`, `standard_webhooks`, `stripe`, or `vercel`. Required when `authMode` is `signature`, and invalid otherwise.
### `secretName`
[Section titled “secretName”](#secretname)
Required. The name of the managed secret holding the webhook’s bearer token, URL token, or provider signing secret. A `url_token` secret must contain only URL-safe characters (letters, digits, `-`, `.`, `_`, and `~`), because it becomes a segment of the ingress URL.
### `deliveryIdHeader`
[Section titled “deliveryIdHeader”](#deliveryidheader)
Optional. The header the sender stamps its own delivery identity into, used to deduplicate retries. Must be a valid HTTP header name; credential-bearing headers such as `Authorization`, `Cookie`, and provider signature headers are rejected.
### `enabled`
[Section titled “enabled”](#enabled-1)
Optional. Defaults to `true`. Set it to `false` to stop deliveries immediately without deleting the webhook, or to create a webhook before its provider has issued a signing secret; see [Setting up a Vercel webhook](/factories/webhooks/vercel/).
On a Warp-managed factory, creating a webhook in the dashboard writes this file for you and stores the secret under the name you enter in the “Secret name” field.
## Skills
[Section titled “Skills”](#skills)
A skill is a directory containing a `SKILL.md`, not a YAML key. Skills under `skills/` are available to every agent in the factory; skills under `agents/<name>/skills/` are available only to that agent. See [factory skills](/factories/factory-skills/) for when to add one, and [Skills](/agents/capabilities/skills/) for the file format.
## Example factory definition
[Section titled “Example factory definition”](#example-factory-definition)
A complete, working definition: one repository, a foreman, an automation triggered by a GitHub label, and a Linux runner. `PAYMENTS_ENVIRONMENT_ID` and `SENTRY_MCP_SERVER_ID` stand in for the IDs of an existing environment and MCP server.
The [warp-factory-examples](https://github.com/warpdotdev/warp-factory-examples) repository has more definitions like this one: the default agents as files, the full lifecycle with scorers and skills, a harness per agent, single-agent factories for code review and UI verification, and a catalog of common automations.
factory.yaml
```yaml
schemaVersion: v1alpha1
name: payments-factory
description: Processes approved work for the payments service
alias: payments
repositories:
- owner: acme
name: payments-service
agentDefaults:
model: auto
runner: linux-build
environmentId: PAYMENTS_ENVIRONMENT_ID
```
agents/foreman/agent.md
```markdown
---
description: Routes approved payments work through the factory
agentType: FOREMAN
secrets:
- SENTRY_AUTH_TOKEN
mcpServers:
sentry:
warpId: SENTRY_MCP_SERVER_ID
---
Own each work item from intake through human handoff.
Confirm the request is ready before dispatching implementation. Require
repository validation and independent review before marking work complete.
```
automations/labeled-issue/automation.md
```markdown
---
enabled: true
agent: foreman
triggers:
- provider: github
event: issue_labeled
filter:
repos: [acme/payments-service]
labels: [factory-ready]
---
Review the labeled issue and decide the next required stage. Preserve the
issue's acceptance criteria and return unresolved product questions to a human.
```
runners/linux-build.yaml
```yaml
description: Linux runner for payments builds and tests
setupCommands:
- corepack enable
instanceShape:
vcpus: 4
memoryGb: 8
platform:
os: linux
arch: x86_64
linux:
dockerImage: ubuntu:22.04
```
### Routing to a self-hosted worker
[Section titled “Routing to a self-hosted worker”](#routing-to-a-self-hosted-worker)
To route this factory’s work to a [managed self-hosted worker](/factories/infrastructure-and-security/#choose-an-execution-host) instead of Warp-hosted compute, set `workerHost` on `agentDefaults` (or override it per agent or automation) to the worker’s ID:
factory.yaml
```yaml
agentDefaults:
model: auto
runner: linux-build
workerHost: SELF_HOSTED_WORKER_ID
```
Pair `workerHost` with a runner whose `platform` matches the worker’s operating system and architecture. Follow the [Self-hosting quickstart](/factories/self-hosting/quickstart/) to deploy and connect a managed worker, then see [choose an execution host](/factories/infrastructure-and-security/#choose-an-execution-host) for the factory-specific setup. For a working definition, see [`07-self-hosted-worker`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/07-self-hosted-worker).
## Related pages
[Section titled “Related pages”](#related-pages)
* [**Factory MCP for coding agents**](/factories/factory-mcp/) - Read the schema and validate a tree from any coding agent, and send work to a factory.
* [**GitHub integration**](/factories/integrations/github/#factory-definition-pull-request-checks) - How the **warp/factory-config** check appears on pull requests, and what to check when it doesn’t.
* [**Factory dashboard**](/factories/factory-dashboard/#edit-definitions-in-the-factory-definition-tab) - Where a Warp-managed definition is edited and validated on save.
* [**warp-factory-examples**](https://github.com/warpdotdev/warp-factory-examples) - Complete definitions to copy, plus the validator script and a CI workflow that runs it.
# Factory dashboard
Canonical page: [/factories/factory-dashboard/](https://docs.warp.dev/factories/factory-dashboard/)
> Track work items, inspect runs, read factory metrics, and manage agents, automations, webhooks, and settings from the factory dashboard.
The factory dashboard is the web app for operating a single factory. Open the [Warp Factories web app](https://platform.warp.dev), then select a factory to track its work, inspect its runs and pull requests, and manage its agents, automations, and settings.
Note
“Factory dashboard” names the whole surface. **Dashboard**, in bold, is one page inside it: the metrics page you land on when you open a factory.
## Getting oriented
[Section titled “Getting oriented”](#getting-oriented)
Select a factory in the sidebar to open its pages. **Runs**, **MCPs and apps**, **Secrets**, and **Integrations** sit above the factory list and cover your whole team, not a single factory. **Inbox** sits there too, but it’s neither team-wide nor per-factory: there’s a single global Inbox page, and it shows only the items waiting on you personally, across every factory you have access to. Everything else on this page is scoped to the factory you select.
A factory opens on its **Dashboard** page, covered next. **Factory definition** appears only on Warp-managed factories, since a factory whose definition lives in your own repository is edited there instead.
## Read metrics on the Dashboard page
[Section titled “Read metrics on the Dashboard page”](#read-metrics-on-the-dashboard-page)
**Dashboard** is the factory’s landing page. It summarizes the factory over a date range you choose:
* **Autonomy** - The share of the factory’s merged PRs that needed no human code push before merging. Opening the PR counts as a push, so a human-authored PR that a factory run later revised doesn’t count as autonomous; comments, reviews, requested changes, and the merge itself don’t count as a push.
* **PR cycle time** - The median time the factory’s merged PRs took from run kickoff through PR, first review, and merge, with an independent median for each stage - the stage medians don’t sum to the headline.
* **Cost per PR** - The median cost of PRs opened in the range. When a single run produces more than one PR, its cost splits evenly across them. Treat it as a lower-bound estimate: it can miss some run usage and does not match billing. See [Measure and improve a factory](/factories/measure-and-improve/) for its limitations.
The page also charts opened versus merged PRs and a breakdown of runs, and the **Cost per PR** card expands to list the most expensive PRs in the range. When Scorers are set up, Scorer cards summarize recent classification results.
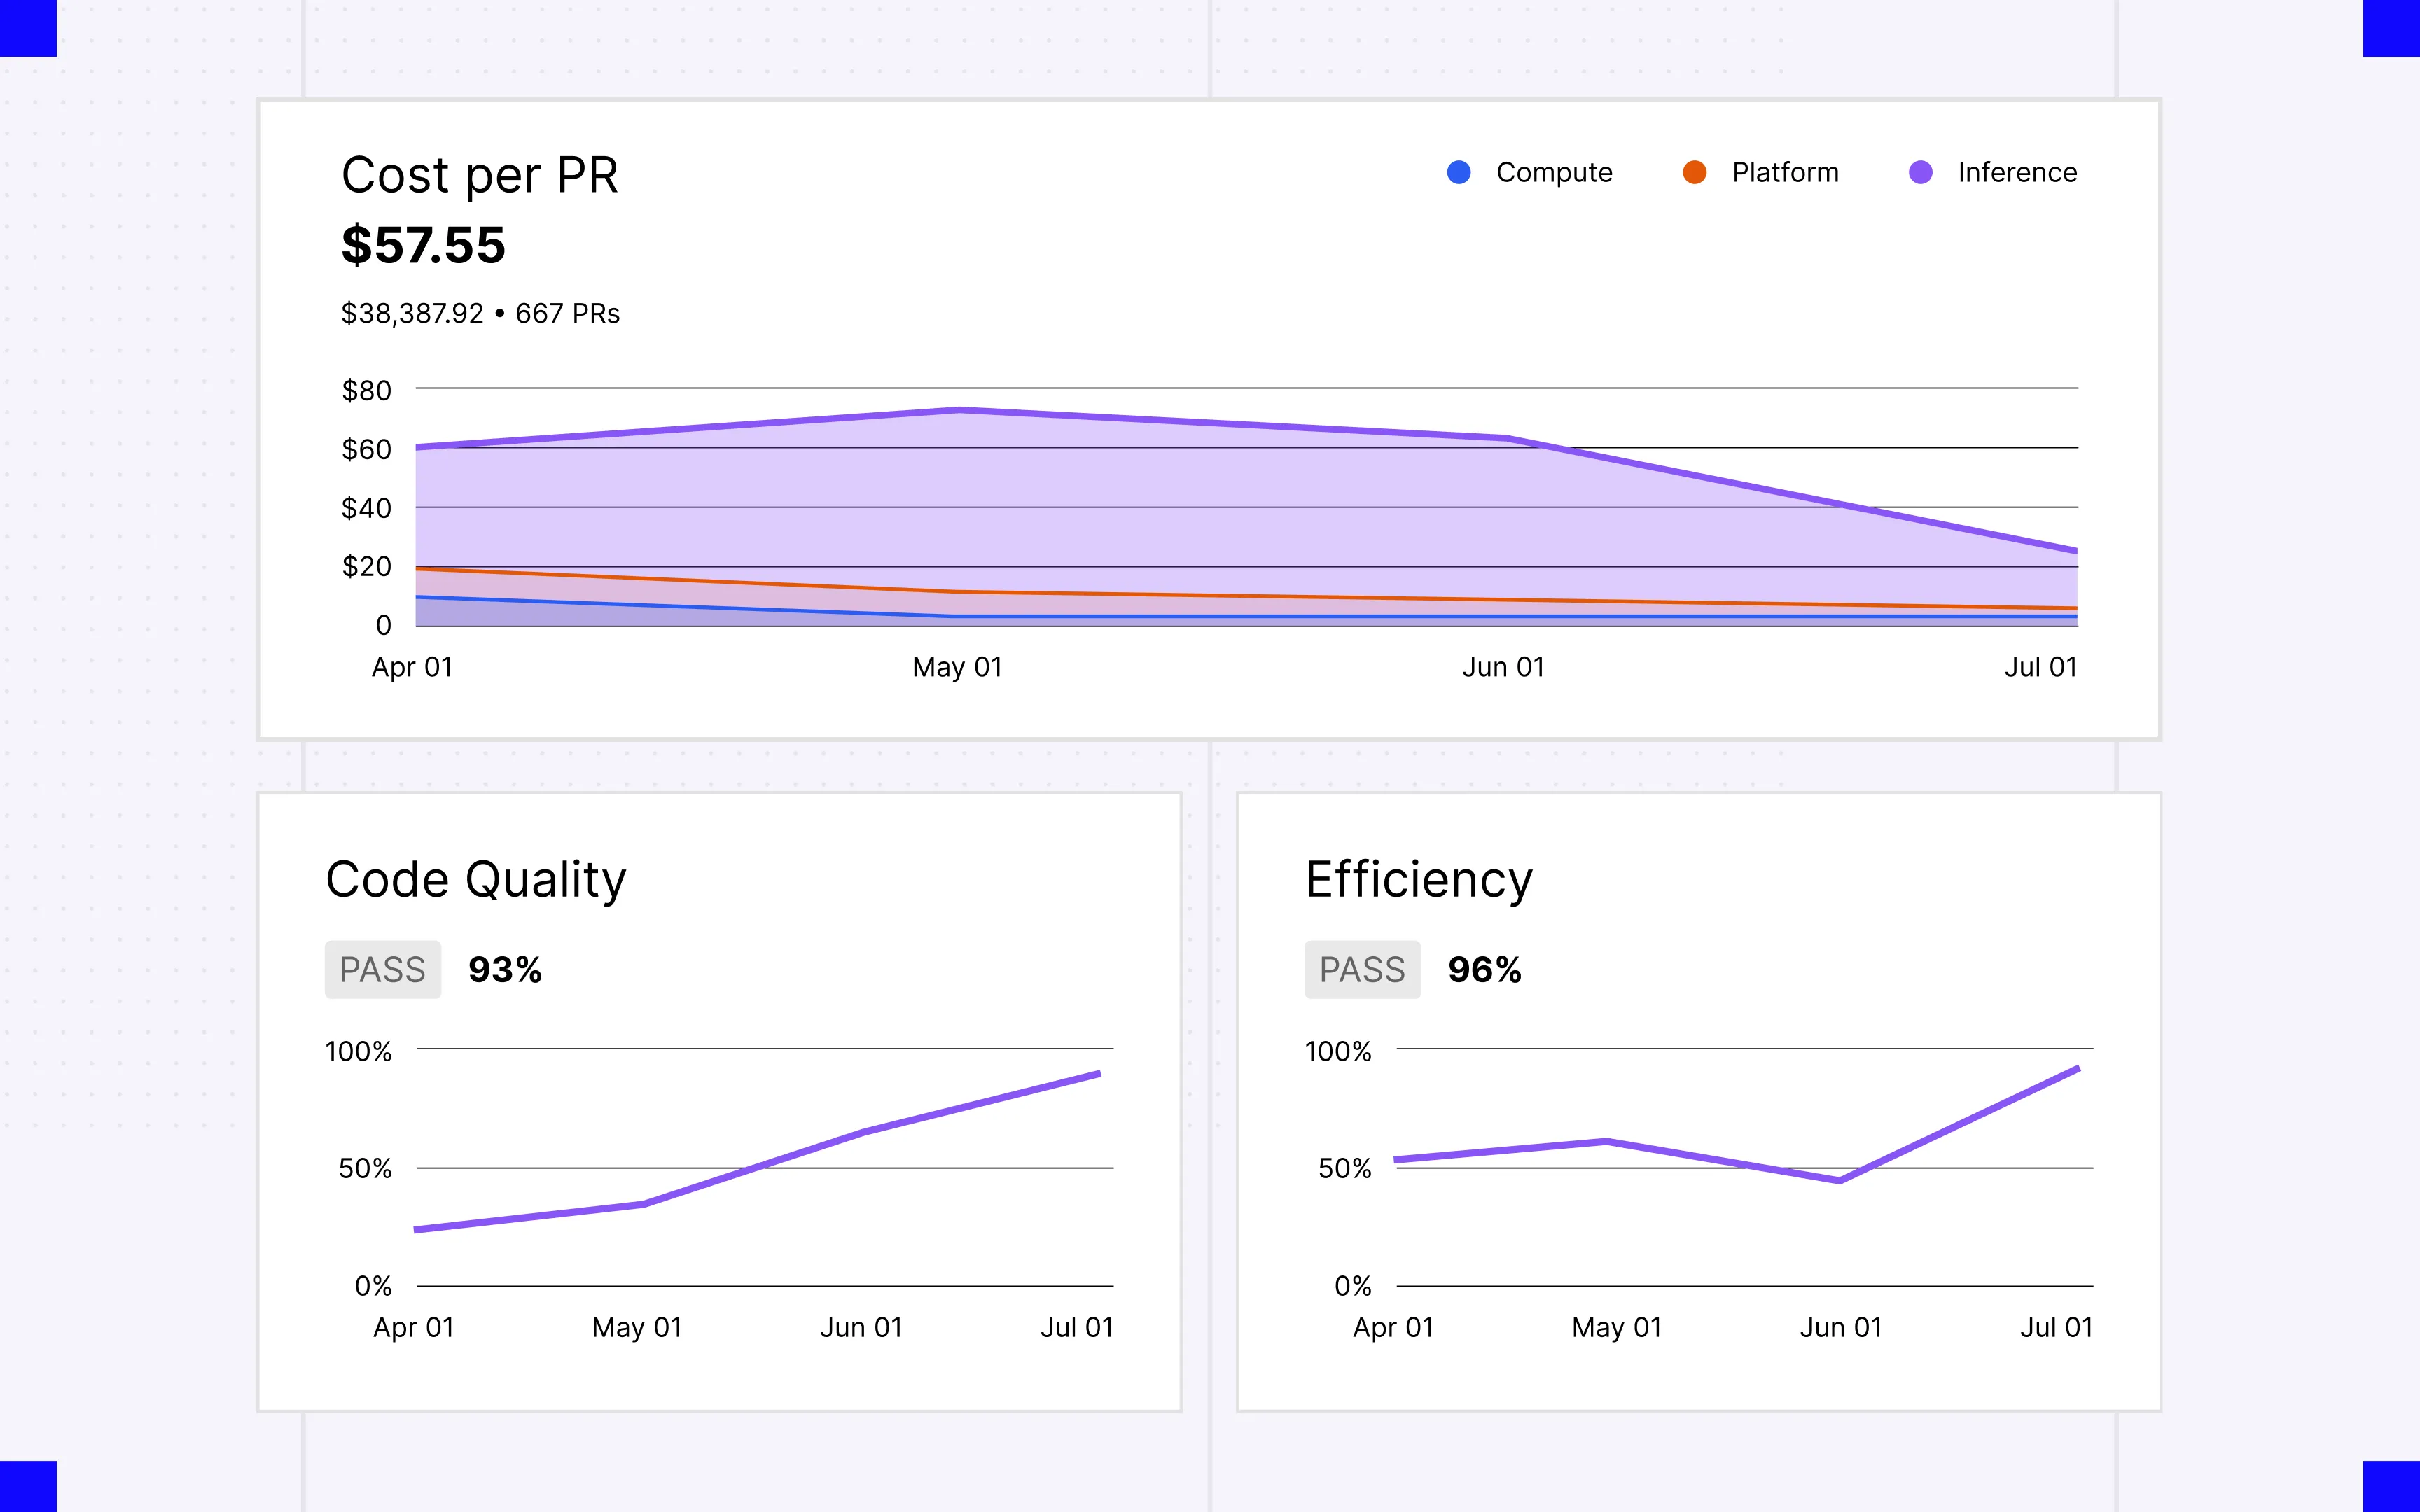
Cost per PR and example Scorer cards on the Dashboard page.
## Find what needs you in Inbox
[Section titled “Find what needs you in Inbox”](#find-what-needs-you-in-inbox)
**Inbox** collects the questions, spec approvals, and pull request reviews waiting on you across every factory, so you don’t have to check each factory’s Runs page for stalled work. See the [factory inbox](/factories/factory-inbox/) page for the kinds of items it shows and how to resolve them.
## Inspect runs
[Section titled “Inspect runs”](#inspect-runs)
A run is a single agent execution. A single request can span several runs as different agents pick it up, and related runs group under their parent in the list. The team-level **Runs** page lists every run you have access to; a factory’s **Runs** page lists only runs from that factory’s agents.
Click **New** on a factory’s **Runs** page to send a prompt to the factory’s foreman agent. Open a run to see its timeline and cost, plus a **Sub-agents** tab for child runs when the agent used [multi-agent orchestration](/platform/orchestration/). From there you can view the agent’s full session, stop or score the run, or turn it into a benchmark task.
Note
Run pages don’t include a chat input, but you can still steer a run: **View session** opens its [shared agent session](/platform/viewing-cloud-agent-runs/), where you follow the agent in real time and send follow-up instructions while the run’s sandbox is active. After it shuts down, the same button opens the conversation transcript.
## Manage agents and automations
[Section titled “Manage agents and automations”](#manage-agents-and-automations)
**Agents** lists the factory’s agents. Create agents and edit their instructions, model or harness, runner, host, secrets, and MCP servers. **Automations** defines the triggers that start runs: a schedule (including custom cron expressions), a GitHub, Linear, Slack, or Jira event, or a delivery to a custom webhook. **Webhooks** is a tab within **Automations** that lists the factory’s [custom webhooks](/factories/webhooks/), where you create them, copy their URLs, rotate secrets, and read the delivery log.
The automation editor doesn’t change execution settings; an automation only overrides them through [execution overrides in the definition files](/factories/factory-as-code/#execution-overrides). When the factory’s definition lives in an external repository, Agents, Automations, and Scorers are read-only; make changes there through pull requests.
## Edit definitions in the Factory definition tab
[Section titled “Edit definitions in the Factory definition tab”](#edit-definitions-in-the-factory-definition-tab)
**Factory definition** is the factory dashboard’s view of the definition files that [definitions as code](/factories/factory-as-code/) describes in full. Where the definition lives decides what you get:
* **Warp-managed** - Browse and edit the definition files. Saving validates the definition and commits all changes together.
* **Managed in GitHub** - The tab doesn’t appear. Edit the definition through pull requests in your repository, and **Settings** links back to it.
* **Live-managed** - The factory is managed through the API, so there are no definition files to browse.
When an agent proposes a change to a Warp-managed definition, a spec review for the branch appears in your [inbox](/factories/factory-inbox/). Open it to comment on the diff, use **Request changes** to send feedback back to the agent, or **Approve & merge**.
## Score and benchmark
[Section titled “Score and benchmark”](#score-and-benchmark)
**Scorers** is where you create Scorers and read their results. **Self-improvement** lists the pull requests the self-improvement flow opens after analyzing runs your Scorers mark as failing, and **Benchmarks** compares model and runner configurations against a fixed set of tasks. See [Configuring Scorers](/factories/measure-and-improve/scorers/), [Configuring and reviewing Self-improvement](/factories/measure-and-improve/self-improvement/), and [benchmarking factory agent configurations](/factories/benchmarks/) for what each one is and how to use it.
## Change factory settings
[Section titled “Change factory settings”](#change-factory-settings)
**Settings** holds the configuration the factory owns:
* **Identity** - The factory’s name, avatar, and [**Foreman name**](/factories/factory-as-code/#alias), the handle your team @-mentions.
* **Repositories** - The repos the factory works in.
* **Pull request authorship** - Whether pull requests are authored by the agent or the run creator (the definition’s [`credentialStrategy`](/factories/factory-as-code/#credentialstrategy)).
* **Analysis model** - The model [Self-improvement](/factories/measure-and-improve/self-improvement/) uses to analyze failed runs.
* **Runners** - The compute the factory’s runs execute on. See [factory runners](/factories/runners/) to choose runner configuration or [managed self-hosting](/factories/self-hosting/) to run factory work on your infrastructure.
* **Integrations** - The integrations this factory can access.
* **Deletion** - Deletes the factory. This cannot be undone.
For a file-managed factory, `runners/*.yaml` in the repository is the source of truth. Anything managed in an external repository is read-only in Settings.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Factory inbox](/factories/factory-inbox/) - See and resolve the questions, spec approvals, and PR reviews waiting on you.
* [How Warp Factories work](/factories/how-factories-work/) - The stages work moves through and where humans stay in the loop.
* [Definitions as code](/factories/factory-as-code/) - Define agents, automations, runners, and source ownership in code.
* [Factory agents](/factories/factory-agents/) - What each default agent does and how to configure it.
* [Measure and improve a factory](/factories/measure-and-improve/) - Configure Scorers and use them in an improvement loop.
* [Benchmarking factory agent configurations](/factories/benchmarks/) - Create a benchmark suite and compare configurations on fixed tasks.
* [Troubleshooting Warp Factories](/factories/troubleshooting/) - Fixes for setup problems, work that doesn’t start, and stuck runs.
# Factory inbox
Canonical page: [/factories/factory-inbox/](https://docs.warp.dev/factories/factory-inbox/)
> See every question, spec approval, and pull request review waiting on you across your factories, and resolve them from one place.
**Inbox** collects everything your factories need from you specifically, across every factory you have access to, in one place. Instead of checking each factory’s Runs page for stalled or waiting work, open Inbox from the sidebar to see it all at a glance.
## What appears in your inbox
[Section titled “What appears in your inbox”](#what-appears-in-your-inbox)
Each item is one of six kinds:
* **Asked question** - An agent needs a decision from you before it can continue.
* **Answered question** - An agent already answered a question, for your information. No action is required.
* **Spec review** - A spec needs your approval before implementation starts.
* **PR review** - One or more pull requests are ready for your review.
* **Blocked** - A run stopped and needs attention, and nothing else on that task already needs yours.
* **Failed** - A run ended in an error, under the same condition as Blocked.
Inbox only shows work tied to tasks *you* started. It’s a personal queue, not a team-wide feed: a teammate’s task, even a blocked or failed one, never appears in your inbox.
Items clear on their own once they stop being relevant. For example, a PR review clears when someone reviews or merges the pull request, and a question clears once it’s answered. You can also resolve any item yourself.
## Reviewing your inbox
[Section titled “Reviewing your inbox”](#reviewing-your-inbox)
1. Click a row to open its details in a side pane. From there, click a chip or the primary action, like **View run**, to open the underlying resource: the run, pull request, spec, or originating thread or ticket.
2. Once you’ve handled an item, mark it **resolved**. Click **Undo** in the confirmation to bring it back if you resolved it by mistake.
3. Mark items **read** or **unread** to track what you’ve reviewed without resolving them.
4. Filter by factory, read state, or kind, or search titles and descriptions, to narrow a long inbox.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Factory dashboard](/factories/factory-dashboard/) - Track runs, manage agents, and change factory settings.
* [How Warp Factories work](/factories/how-factories-work/) - Where a factory pauses for a person to decide something.
* [Cloud agent session sharing](/platform/viewing-cloud-agent-runs/) - Follow and steer a run in real time from its session.
# Factory MCP for coding agents
Canonical page: [/factories/factory-mcp/](https://docs.warp.dev/factories/factory-mcp/)
> Connect any coding agent to create and operate your team's factories, send in work, continue tasks locally, and hand results back.
Factory MCP is a hosted Model Context Protocol (MCP) server that connects coding agents to your team’s factories. An agent can send work to a factory, pull down a task to continue locally, and return the result.
## What you can use it for
[Section titled “What you can use it for”](#what-you-can-use-it-for)
* **Send work in** - Turn anything from your local session into a factory task: a bug you found, review feedback, or a half-finished change.
* **Continue a task locally** - Pull a task’s context into your own checkout, work with your own tools, and return the result to the same task.
* **Stay in sync** - List and search tasks, read a task’s conversation, and message its [foreman](/factories/factory-agents/), the agent that orchestrates each task inside the factory.
* **Create a factory** - Let your coding agent guide you through choosing a team, code host, repositories, factory agents, and integrations.
* **Edit a factory’s definition** - Read the definition schema and validate a factory’s [definition files](/factories/factory-as-code/) before opening a pull request.
## Connect and authenticate
[Section titled “Connect and authenticate”](#connect-and-authenticate)
### In Warp
[Section titled “In Warp”](#in-warp)
There is nothing to configure. When your account has access, Warp connects agent sessions to Factory MCP and handles authentication for you. To create your first factory, ask the agent to set one up — the setup prompt below is for agents outside Warp.
### Set up with your coding agent
[Section titled “Set up with your coding agent”](#set-up-with-your-coding-agent)
Paste this prompt into a coding agent that can run commands and configure MCP servers:
```text
Set up a factory for me. Read https://docs.warp.dev/factories/factory-mcp.md, follow the setup instructions for your coding environment to connect to and authenticate with Factory MCP, then use Factory MCP to onboard me.
```
The agent connects to Factory MCP, opens a browser sign-in where you log in or create a Warp account, then walks you through the same choices as the [setup wizard](/factories/quickstart/#set-up-your-factory): team, code host, repositories, agents, and integrations. Factory MCP onboarding currently connects GitHub and GitLab repositories; use the web setup wizard to connect Azure DevOps. It finishes by linking your new factory’s dashboard. If the Warp Factories web app is still open to its setup screen in your browser, refresh the page to pick up the new factory.
### In other MCP clients
[Section titled “In other MCP clients”](#in-other-mcp-clients)
Factory MCP is a streamable HTTP server at `https://app.warp.dev/api/v1/mcp/factory`. Point any MCP client that supports remote servers at that URL; on first connect, the client opens a browser so you can sign in and approve access.
With Claude Code:
```bash
claude mcp add --transport http --scope local warp-factory https://app.warp.dev/api/v1/mcp/factory
```
In clients that use the `mcpServers` JSON format, such as Cursor:
```json
{
"mcpServers": {
"warp-factory": {
"url": "https://app.warp.dev/api/v1/mcp/factory"
}
}
}
```
`warp-factory` is the server’s name in your client. One connection reaches every factory you can access.
For Codex and other clients, follow the [client’s own remote-server instructions](https://developers.openai.com/codex/mcp/#connect-codex-to-an-mcp-server) with the same URL.
Automation that runs without a person present, such as a CI pipeline or a headless server, can’t complete the browser sign-in. For those cases, authenticate with an [agent API key](/agents/cli/oz-cli/api-keys/) instead, passed as a bearer token:
```json
{
"mcpServers": {
"warp-factory": {
"url": "https://app.warp.dev/api/v1/mcp/factory",
"headers": {
"Authorization": "Bearer YOUR_API_KEY"
}
}
}
}
```
Caution
Factory MCP has no read-only or per-factory scopes: a connected client acts with the full permissions of the account or agent it authenticates as. Store API keys in your client’s secret storage, never in a repository.
## Send new work to a factory
[Section titled “Send new work to a factory”](#send-new-work-to-a-factory)
To create a task, your agent calls `send_task` with the target factory, a title, and a note. The note is what the foreman starts from, so a good one states the goal, the relevant context and constraints, and any work already done. The foreman takes it from there and reports progress on the task’s conversation.
If the new task builds on local changes, push the branch or open a pull request first and reference it in the note, so the factory can see that work.
## Pick up a task and work on it locally
[Section titled “Pick up a task and work on it locally”](#pick-up-a-task-and-work-on-it-locally)
1. **Find the task.** Your agent locates it with `list_tasks` or `search_task`, or resolves a reference you give it with `get_task`: a task or run URL, a GitHub pull request, a Slack permalink, a Linear or Jira issue, or a branch name.
2. **Pull down the context.** Calling `get_task` with `start_working=true` returns the task’s status, run history, and suggested Git commands for setting up an isolated [worktree](/code/git-worktrees/) in a local clone. Factory MCP never modifies your files; your agent runs the setup itself.
3. **Coordinate while you work.** `message_foreman` sends progress, questions, and blockers to the task’s foreman, and `get_conversation` reads the replies. Messaging keeps the factory informed but doesn’t move the task or hand anything back.
4. **Commit and push.** Validate the change, then push the branch. The factory can’t see uncommitted or unpushed work.
5. **Hand the task back.** Your agent calls `send_task` with the task’s ID, the pushed branch or pull request URL, and a note covering what changed, what was validated, and what remains. The work returns to the same task, and the foreman decides the next step.
Caution
Picking up a task doesn’t claim, lock, or pause it, and the factory may keep running its own work on it in the meantime. Check the task’s active runs and tell the foreman you’re picking it up, so you don’t end up with duplicate changes.
When nothing remains for the factory to do, `complete_task` closes the task out. Handing work back doesn’t complete a task by itself.
## Get notified when a task needs you
[Section titled “Get notified when a task needs you”](#get-notified-when-a-task-needs-you)
Sending work to a factory means you’re no longer watching it. To be notified when a task needs attention or finishes, ask for a notification when sending or returning work: your agent calls `list_notification_routes` to see the destinations available to you in that factory, such as a Slack DM or a Linear issue, and passes your choice to `send_task`. Delivery is best-effort, so treat notifications as a convenience rather than a guarantee.
## Tool reference
[Section titled “Tool reference”](#tool-reference)
Your MCP client fetches the full input schemas from the server, and tool results include links that open the corresponding task or run in the factory’s [factory dashboard](/factories/factory-dashboard/). The onboarding tools from `list_teams` through `create_factory` require browser sign-in.
| Tool | What it does |
| -------------------------- | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `list_factories` | Lists the factories you can access. |
| `get_factory_file_schema` | Returns the JSON Schema documents for factory definition files, as a catalog or one document at a time. |
| `validate_factory_files` | Validates a complete factory definition tree without saving or applying it. |
| `list_teams` | Lists current memberships and first-time joinable team choices. |
| `create_team` | Creates the authenticated user’s first team with a confirmed name. |
| `join_team` | Joins a team selected from the first-time discovery choices. |
| `get_team_funding_status` | Checks first-team credit readiness and returns the browser checkout step when required. |
| `list_forge_repositories` | Lists repositories available through a team’s connected GitHub or GitLab account. |
| `list_tracker_scopes` | Lists the Linear teams or Jira projects that can be scoped to route issues to a new factory. |
| `start_connection` | Starts or checks setup for GitHub, GitLab, Slack, Linear, or Jira. |
| `get_connection_status` | Checks whether a browser authorization flow completed. |
| `create_factory` | Creates a factory with the selected repositories, integrations, and optional factory agents. |
| `list_tasks` | Lists the tasks in one factory, with filters such as creator, stage, and date. |
| `search_task` | Searches task titles across all factories you can access. |
| `get_task` | Reads a task’s status, run history, and outputs. Accepts a task ID or a reference such as a URL, issue, pull request, or branch. With `start_working=true`, also returns local setup guidance. |
| `message_foreman` | Sends a message to a task’s foreman. |
| `get_conversation` | Reads a task’s foreman conversation. |
| `send_task` | Creates a new task, or hands work back to an existing one. |
| `list_notification_routes` | Lists the notification destinations available to you in a factory. |
| `complete_task` | Marks a task complete. |
## Related pages
[Section titled “Related pages”](#related-pages)
* [**Definitions as code**](/factories/factory-as-code/) - Every file and key in a factory definition, the JSON Schema behind them, and how to validate a change.
* [**Factory agents**](/factories/factory-agents/) - The foreman and the other agents that carry out a factory’s tasks.
* [**How Warp Factories work**](/factories/how-factories-work/) - The task lifecycle and the agents that move work through it.
* [**Warp Factories quickstart**](/factories/quickstart/) - Create a factory and send it its first work item.
# Factory skills
Canonical page: [/factories/factory-skills/](https://docs.warp.dev/factories/factory-skills/)
> Skills give a factory's agents repeatable, version-controlled procedures that can be shared across every agent or scoped to just one.
Note
Warp Factories is in **Early Access** and available to a limited set of teams. [Request access](https://www.warp.dev/factories/request-access) to use it with your team.
A skill tells an agent what to check, how to classify results, what to produce, and when to escalate. In a factory, skills are how you extend or override [default agents](/factories/factory-agents/), without editing their prompts directly.
## Skill sources in a factory
[Section titled “Skill sources in a factory”](#skill-sources-in-a-factory)
A factory run can use skills from three sources:
* **Factory role and integration skills** - Baseline procedures that come from the default agent roles and integrations you configure, such as GitHub, Slack, Linear, or Jira.
* **Warp-provided platform-bundled skills** - Product capabilities that Warp provides, such as `oz-platform`, `factory-files`, and `factory-mcp`.
* **Custom file-based factory skills** - Team-owned `SKILL.md` files in the factory definition, available to every agent or scoped to one agent.
## Custom file-based factory skills
[Section titled “Custom file-based factory skills”](#custom-file-based-factory-skills)
A custom skill is a directory containing a `SKILL.md`. It’s part of the factory’s [definition](/factories/factory-as-code/), not an agent’s settings. Where you place the directory decides who can use it:
```text
skills/
repository-conventions/
SKILL.md
agents/
foreman/
skills/
incident-triage/
SKILL.md
```
* **`skills/<name>/SKILL.md`** - Available to every agent in the factory. Use this for procedures that apply regardless of role, such as your repository’s coding conventions or a shared escalation policy.
* **`agents/<name>/skills/<name>/SKILL.md`** - Available only to that agent. Use this for procedures specific to one role, such as how the review agent should apply your security checklist.
Both forms use the same `SKILL.md` format as skills anywhere else in Warp. See [Skills](/agents/capabilities/skills/) for the file format, front matter, and argument syntax.
## Factory role and integration skills
[Section titled “Factory role and integration skills”](#factory-role-and-integration-skills)
Every default agent starts with a baseline of role and integration skills so the factory works immediately after setup, before you write anything custom:
* **GitHub** - Every default agent gets a GitHub skill, covering how to read issues, open pull requests, and follow your repository’s conventions.
* **Slack** - The foreman also gets a Slack skill, since it’s the agent that replies in threads and DMs.
* **Issue tracker** - The tracker you choose during setup, Linear or Jira, adds that tracker’s skill and instructions to the agents that use it. If you don’t connect a tracker, agents keep only the GitHub and Slack skills.
These baseline skills aren’t files in your definition; they come from the agent roles and integrations you choose. Anything you add under `skills/` or `agents/<name>/skills/` extends this baseline rather than replacing it.
## Warp-provided platform-bundled skills
[Section titled “Warp-provided platform-bundled skills”](#warp-provided-platform-bundled-skills)
Platform-bundled skills are separate from factory role and integration skills. They provide Warp capabilities such as operating cloud agents with `oz-platform`, editing factory definitions with `factory-files`, and sending work through Factory MCP with `factory-mcp`.
Warp provides these stable bundled-skill IDs:
| Bundled skill ID | Purpose |
| ------------------- | ----------------------------------------------------------------- |
| `add-mcp-server` | Add an MCP server to Warp configuration. |
| `change-keybinding` | Change or remove Warp keyboard shortcuts. |
| `claude-api` | Build and maintain applications that use the Anthropic SDK. |
| `create-skill` | Create, improve, and evaluate skills. |
| `create-tab-config` | Create a Warp tab configuration. |
| `factory-files` | Create and validate file-based Warp factory definitions. |
| `factory-mcp` | Send work to a factory and collaborate through Factory MCP. |
| `modify-settings` | View or change Warp settings using the bundled settings schema. |
| `oz-platform` | Run, configure, and inspect cloud agents through the API and CLI. |
| `pr-comments` | Fetch GitHub pull request review comments for the current branch. |
| `tab-configs` | Look up the tab configuration schema and validation rules. |
| `tui-migrate-setup` | Migrate supported settings into the Warp Agent CLI. |
| `update-tab-config` | Update an existing Warp tab configuration. |
| `warpctrl` | Control and inspect a running Warp app with Warp Control. |
See [skill actions in conversation data](/factories/api-and-sdk/#skill-actions-in-conversation-data) for the API reference.
## Attribute team-owned skill usage
[Section titled “Attribute team-owned skill usage”](#attribute-team-owned-skill-usage)
The [Conversation API](/api) returns skill loads as `read_skill` actions. Use the action’s `input` to classify the skill:
* **`input.bundled_skill_id` is present** - The action loaded a Warp-provided bundled reference. Exclude it when measuring usage of skills your team owns.
* **Only `input.skill_path` is present** - A path alone doesn’t identify the skill’s owner. Count it as team-owned only when the path is under a skill root your team manages, such as `skills/` or `agents/<name>/skills/` in the factory definition.
## When to add a custom skill
[Section titled “When to add a custom skill”](#when-to-add-a-custom-skill)
Add a custom skill when a default agent needs to do something the built-in baseline doesn’t cover, such as:
* Enforcing a specific test, lint, or validation command before a change is considered complete.
* Following a runbook for a category of incident or request your triage agent sees repeatedly.
* Applying a security or compliance checklist during review that goes beyond general code quality.
* Teaching a custom agent its job. Custom agents have no built-in skills.
A skill changes what an agent knows how to do, not what it can reach. To scope access, configure the agent’s [secrets](/platform/secrets/) and [MCP servers](/platform/mcp/) — see [factory agents](/factories/factory-agents/#configure-agent-behavior) and [infrastructure and security](/factories/infrastructure-and-security/#credential-boundaries).
## Add or edit a skill
[Section titled “Add or edit a skill”](#add-or-edit-a-skill)
Where you edit a skill depends on [where the factory’s definition lives](/factories/factory-as-code/#where-the-definition-lives):
* **Warp-managed** - Add or edit `SKILL.md` files directly in the **Factory definition** tab of the [factory dashboard](/factories/factory-dashboard/). Saving validates and commits the change in one step.
* **GitHub** - Add or edit the files in the connected definition repository and open a pull request. The same [pull request checks](/factories/factory-as-code/#pull-request-checks) that validate the rest of the definition apply to skill files.
For worked examples, including a factory-wide skill and a per-agent skill together, see [`02-sdlc-issue-to-pr`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/02-sdlc-issue-to-pr) in the [warp-factory-examples](https://github.com/warpdotdev/warp-factory-examples) repository.
## Skills and self-improvement
[Section titled “Skills and self-improvement”](#skills-and-self-improvement)
A factory can propose changes to a skill. When [Self-improvement](/factories/measure-and-improve/self-improvement/) is on for a Scorer and it flags a recurring failure, it can edit the responsible skill in a follow-up run, the same way it can edit application code. The change still arrives as a pull request for your team to review, whether that’s through the factory dashboard or your Git host.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Factory agents](/factories/factory-agents/) - The agents that use a factory’s skills, and how to configure each one.
* [Definitions as code](/factories/factory-as-code/) - The full schema for `factory.yaml`, agents, automations, and runners alongside skills.
* [Skills](/agents/capabilities/skills/) - The general skill file format, shared across Warp, cloud agents, and factories.
* [Measure and improve a factory](/factories/measure-and-improve/) - How Self-improvement turns repeated failures into skill and code changes.
# How Warp Factories work
Canonical page: [/factories/how-factories-work/](https://docs.warp.dev/factories/how-factories-work/)
> A factory's foreman routes each work item through triage, planning, building, and reviewing, with humans making the key decisions.
Note
Warp Factories is in **Early Access** and available to a limited set of teams. [Request access](https://www.warp.dev/factories/request-access) to use it with your team.
A factory is a fleet of agents wired to your software development lifecycle. It connects your repositories and tools to move requests through triage, specification, implementation, review, and verification, while people stay in control of key decisions. You talk to one agent, the **foreman**, from the tool that sends the request, such as Slack or Linear. The foreman dispatches the factory’s other agents, and each one owns a part of the software development lifecycle.
Deciding which repositories belong in this factory is a separate question. See [sizing a factory](/factories/#sizing-a-factory) for that guidance.
A **work item** is a single request the factory acts on, such as an issue, support request, pull request, or Factory MCP task. It keeps its identity from intake to handoff, however many agents contribute to it along the way.
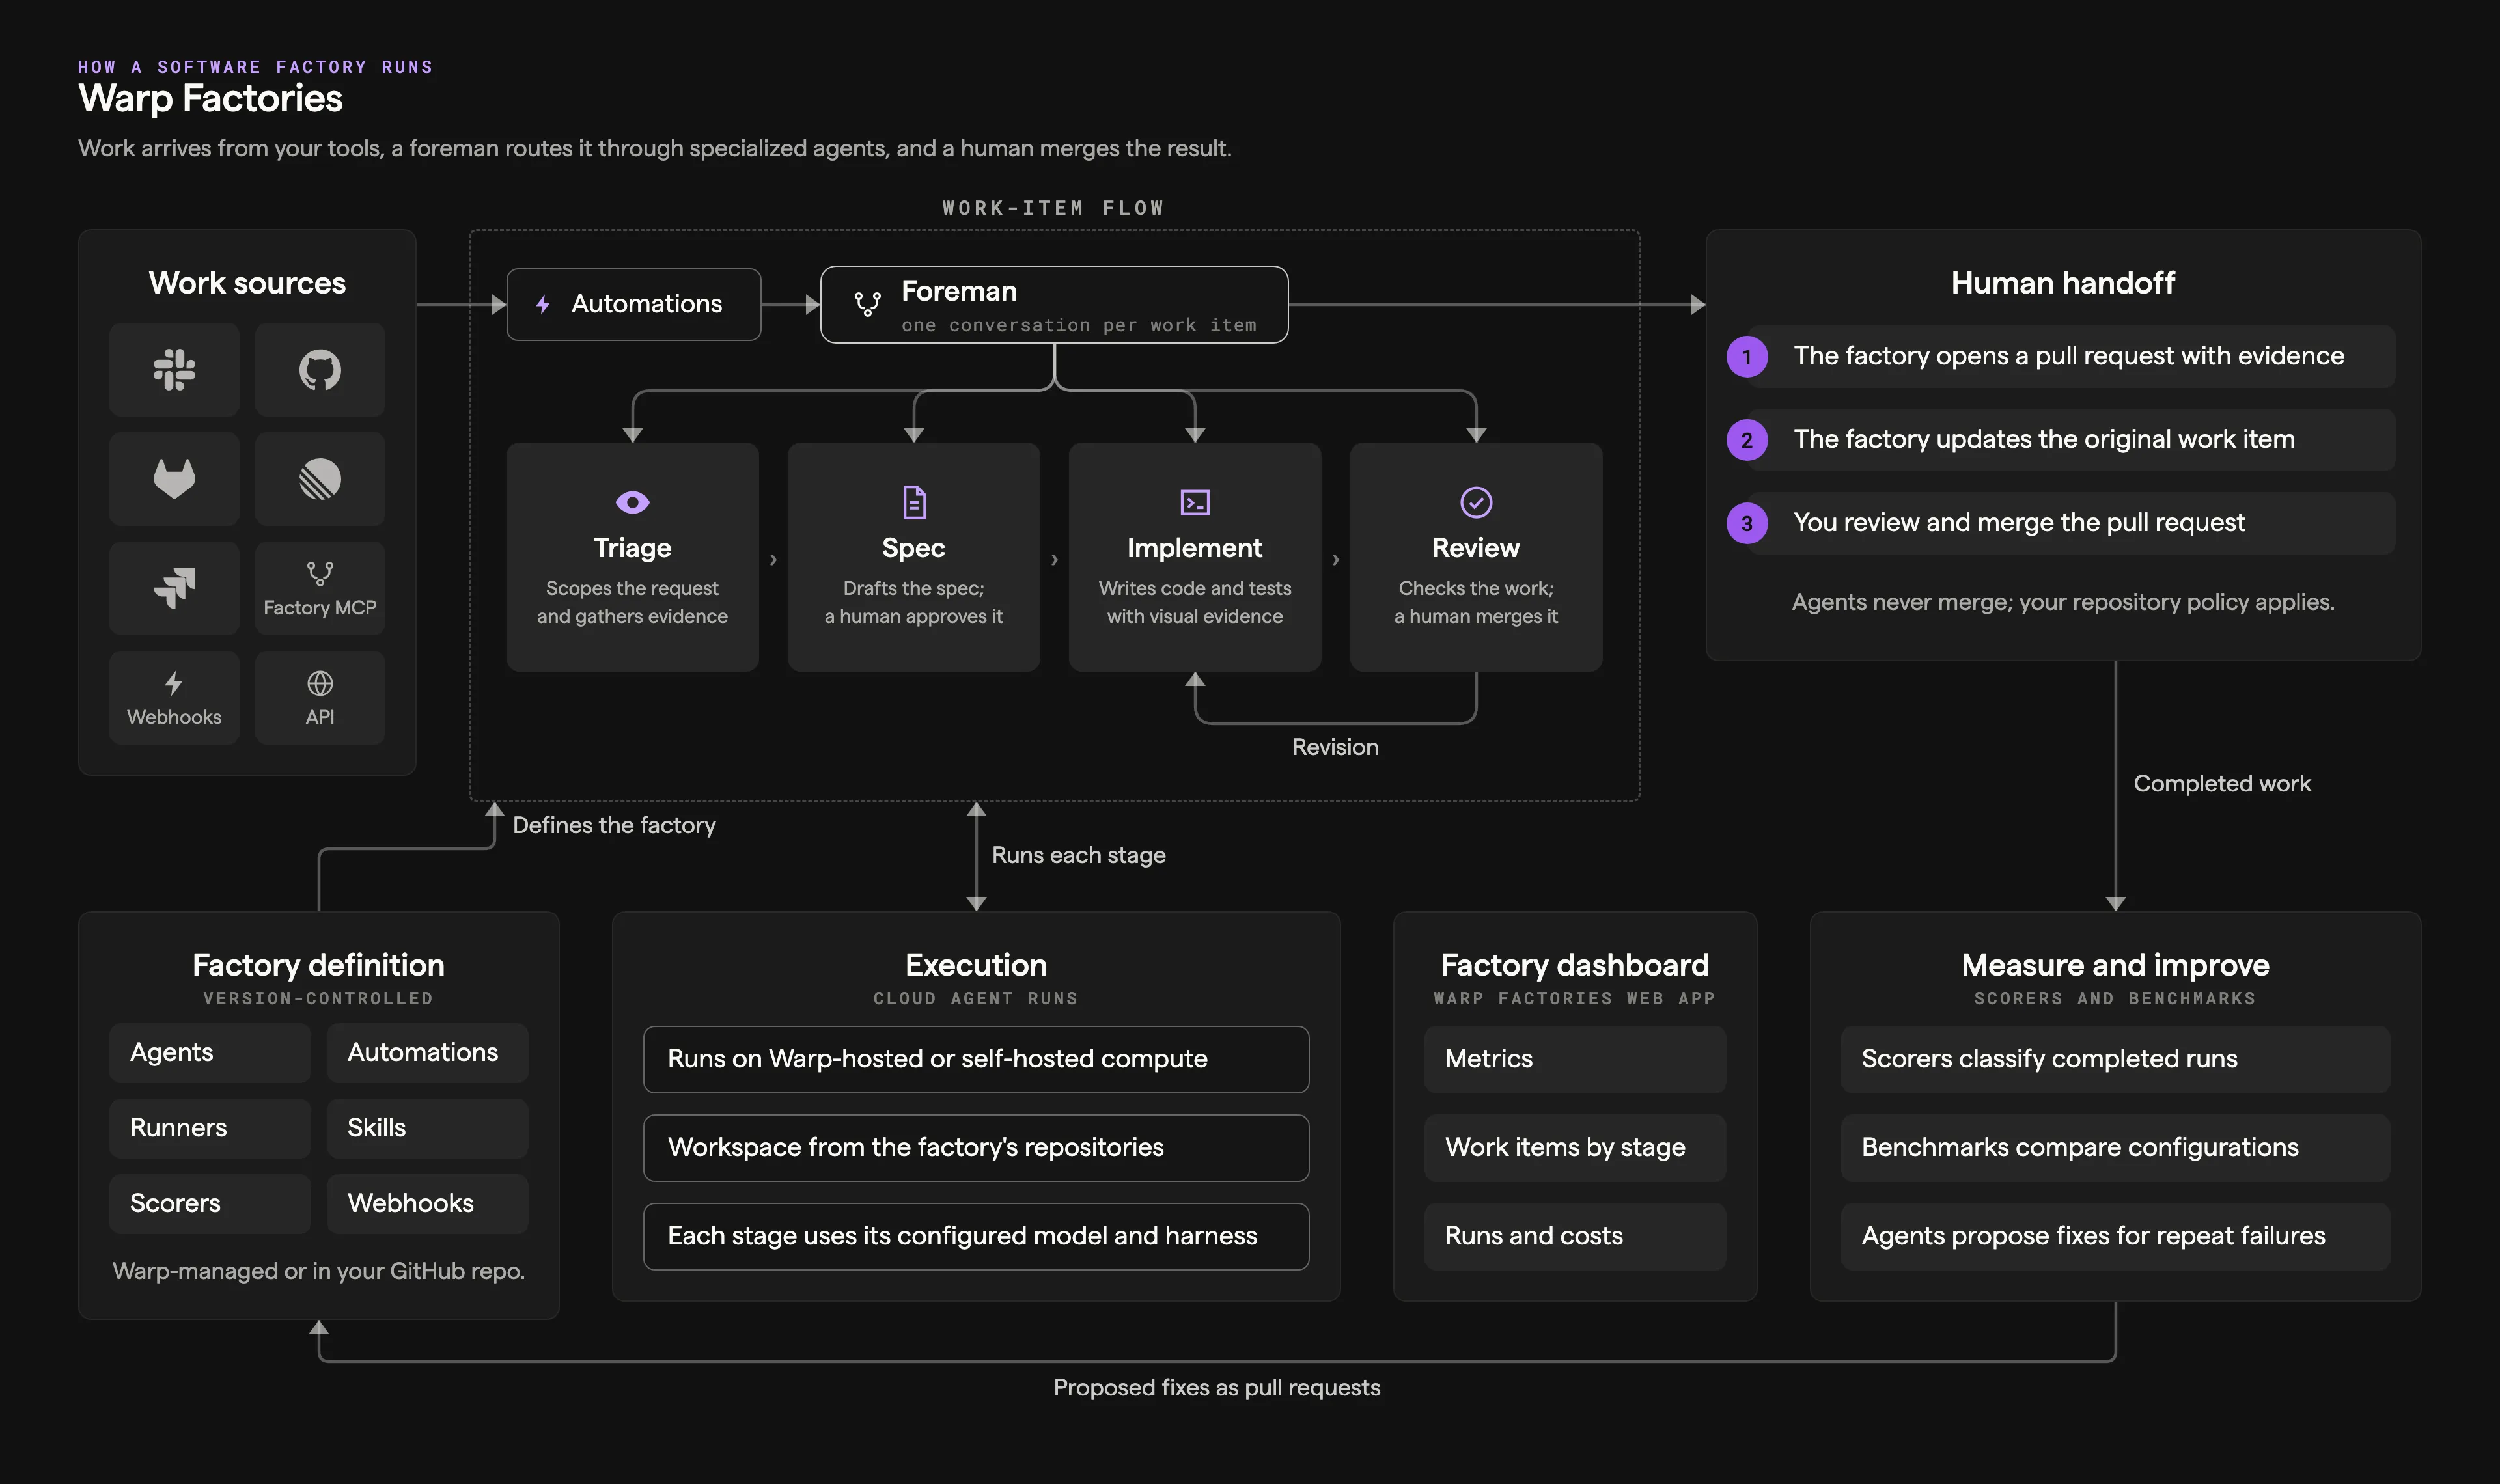
The diagram’s components, from intake to improvement:
* **Work sources** - Work items arrive from [Slack](/factories/integrations/slack/), [GitHub](/factories/integrations/github/), [GitLab](/factories/integrations/gitlab/), [Linear](/factories/integrations/linear/), or [Jira](/factories/integrations/jira/), from [custom webhooks](/factories/webhooks/) and [factory endpoints](/factories/factory-api/), from local coding agents through the [Factory MCP](/factories/factory-mcp/), or from direct runs and schedules.
* **Automations** - [Automations](/factories/automations/) filter provider events and decide which agent handles them. Schedules fire them on a timer; direct requests go straight to the foreman.
* **Foreman and stage agents** - The foreman holds one conversation per work item and dispatches the Triage, Spec, Implement, and Review agents as the work needs them. See [factory agents](/factories/factory-agents/) and the stages below.
* **Human handoff** - The factory opens a pull request with evidence, updates the original work item, and you review and merge.
* **Factory definition** - Version-controlled agents, automations, runners, scorers, skills, and webhooks define the factory, either Warp-managed or in a GitHub repository your team owns. See [definitions as code](/factories/factory-as-code/).
* **Execution** - Every stage runs as a cloud agent run on Warp-hosted or [managed self-hosted](/factories/self-hosting/) compute, with the workspace from the factory’s repositories and each stage’s configured model and [harness](/platform/harnesses/).
* **Factory dashboard** - Metrics, work items by stage, and runs and costs. See the [factory dashboard](/factories/factory-dashboard/).
* **Measure and improve** - [Scorers](/factories/measure-and-improve/) classify completed runs, benchmarks compare configurations, and self-improvement turns repeat failures into follow-up pull requests for your review.
## How a work item moves through the factory
[Section titled “How a work item moves through the factory”](#how-a-work-item-moves-through-the-factory)
The foreman coordinates every work item. It routes work between the factory’s agents, passes each one the context it needs, and continues existing agent conversations instead of starting new ones. See [factory agents](/factories/factory-agents/) for what each agent does.
Not every work item needs every stage. The foreman picks the shortest path that still meets your quality policy: it skips stages when the work is already well defined, starts partway through when enough context exists, and sends work back to an earlier agent when revisions are needed.
### Stages
[Section titled “Stages”](#stages)
The diagram below shows the default path through a factory’s stages.
```
flowchart LR
Intake[Intake] --> Foreman[Foreman]
Foreman --> Triage[Triage]
Triage --> Decision{Plan needed?}
Decision -->|Yes| Planning[Planning]
Decision -->|No| Building[Building]
Planning --> Approval["Human review<br/>(default policy)"]
Approval --> Building
Building --> Reviewing[Reviewing]
Reviewing --> Revision{Revision needed?}
Revision -->|Yes| Building
Revision -->|No| Handoff["Human handoff<br/>(default policy)"]
Handoff --> Complete[Complete]
```
* **Intake** - A work item enters from a [connected integration](/factories/connect-your-factory/), an automation, a direct run, or the [Factory MCP](/factories/factory-mcp/). It keeps its source context as it moves through later stages.
* **Triage** - The triage agent researches the request, reproduces the problem when needed, and defines the scope and complexity of the change. The foreman skips this stage when the request already explains the problem and what needs to change.
* **Planning** - The spec agent defines product behavior, technical constraints, and validation criteria. The foreman skips this stage for small, well-understood changes.
* **Building** - The implement agent makes the code change on a branch and opens a pull request with test and visual evidence.
* **Reviewing** - The review agent checks the change against the requirements, tests, and security expectations, then sends findings back for another pass. Its verdict is advisory.
* **Human handoff** - The factory presents the result, its evidence, and any findings. A person decides what happens next.
* **Complete or Cancelled** - The work item ends when the factory finishes its work, or stops early if someone cancels it.
Stages and agents are named separately, so the spec agent works the Planning stage, the implement agent works the Building stage, and the review agent works the Reviewing stage. Each agent’s run within a work item is an ordinary [cloud agent run](/platform/) you can watch and steer from the factory’s [Runs page](/factories/factory-dashboard/#inspect-runs), and any stage that needs your input surfaces in your [inbox](/factories/factory-inbox/).
## Where your team stays in charge
[Section titled “Where your team stays in charge”](#where-your-team-stays-in-charge)
A factory is built to pause when there is a decision that needs to be made by a person. By default, that’s three places:
* **Approving the spec** - When work goes through the Planning stage, the Building stage waits until a person signs off on the plan.
* **Answering questions** - When requirements are unclear or a review finding is ambiguous, the foreman asks instead of guessing.
* **Merging** - The factory opens the pull request and hands it off. Whether and when it merges is your team’s call.
The first two are workflow policy, written into the foreman’s instructions; edit them to change when the factory checks in. Merging is enforced by your repository, so if you require human-only merges, use branch protection and repository permissions.
## How the factory improves itself
[Section titled “How the factory improves itself”](#how-the-factory-improves-itself)
Your factory is self-improving, and you define what “better” means. [Scorers](/factories/measure-and-improve/scorers/) classify completed runs against criteria you write, and [Self-improvement](/factories/measure-and-improve/self-improvement/) groups the failures they flag into follow-up runs that propose fixes — to the application code or to the factory’s own definition. Every proposal arrives as a change for your review; nothing is adopted on its own.
The factory’s definition is open to the same loop. Anyone on the team, or an agent, can propose changes to its instructions, skills, models, or other [definition files](/factories/factory-as-code/), and definitions stored in GitHub go through pull request review and [configuration checks](/factories/factory-as-code/#pull-request-checks) before a change reaches the production branch.
See [measure and improve](/factories/measure-and-improve/) for the evaluation workflow, or [build a self-improving agent](/guides/agent-workflows/build-a-self-improving-agent/) to apply the same pattern to a standalone agent.
# Warp Factories infrastructure and security
Canonical page: [/factories/infrastructure-and-security/](https://docs.warp.dev/factories/infrastructure-and-security/)
> Warp Factories gives you control over inference and execution hosting while Warp stores run records, transcripts, and outputs.
Warp Factories runs on the infrastructure your team chooses. You decide where a factory runs code, which model providers serve its inference requests, and which credentials each agent receives. Warp coordinates the work and stores run data such as transcripts and artifacts.
## Control plane and execution plane
[Section titled “Control plane and execution plane”](#control-plane-and-execution-plane)
Every factory splits responsibilities across two planes:
* **Control plane** - Warp coordinates runs, identity and configuration, observability, integrations, storage, and inference routing.
* **Execution plane** - A Warp-hosted sandbox or a managed self-hosted worker checks out code, runs setup, invokes tools, builds the project, and executes commands.
```
flowchart LR
I["Integrations and triggers"] --> C["Warp control plane<br/>coordination · identity/config<br/>observability · inference routing"]
C --> H["Warp-hosted sandbox"]
C -->|"task, config, and scoped<br/>runtime credentials"| S["Managed self-hosted worker"]
H -->|"results, transcripts,<br/>artifacts, telemetry"| C
S -->|"results, transcripts, attachments,<br/>artifacts, and telemetry<br/>can contain code context"| C
C --> P["Warp-managed or<br/>customer-configured inference"]
C --> D["Warp-managed storage"]
```
Self-hosting moves only the execution plane: with a managed self-hosted worker, repository checkouts, command execution, and the sandbox filesystem stay on machines you control, but content that enters prompts, results, transcripts, attachments, artifacts, or telemetry still flows through Warp and the providers you configure. See [deployment patterns](/factories/deployment-patterns/) and [execution security](/platform/execution-security/) for the broader data model.
The diagram below maps those boundaries for self-hosted execution; factory runs follow the same data model. See the [data security and boundaries](/platform/architecture/#data-security-and-boundaries) reference for a description of each data class.
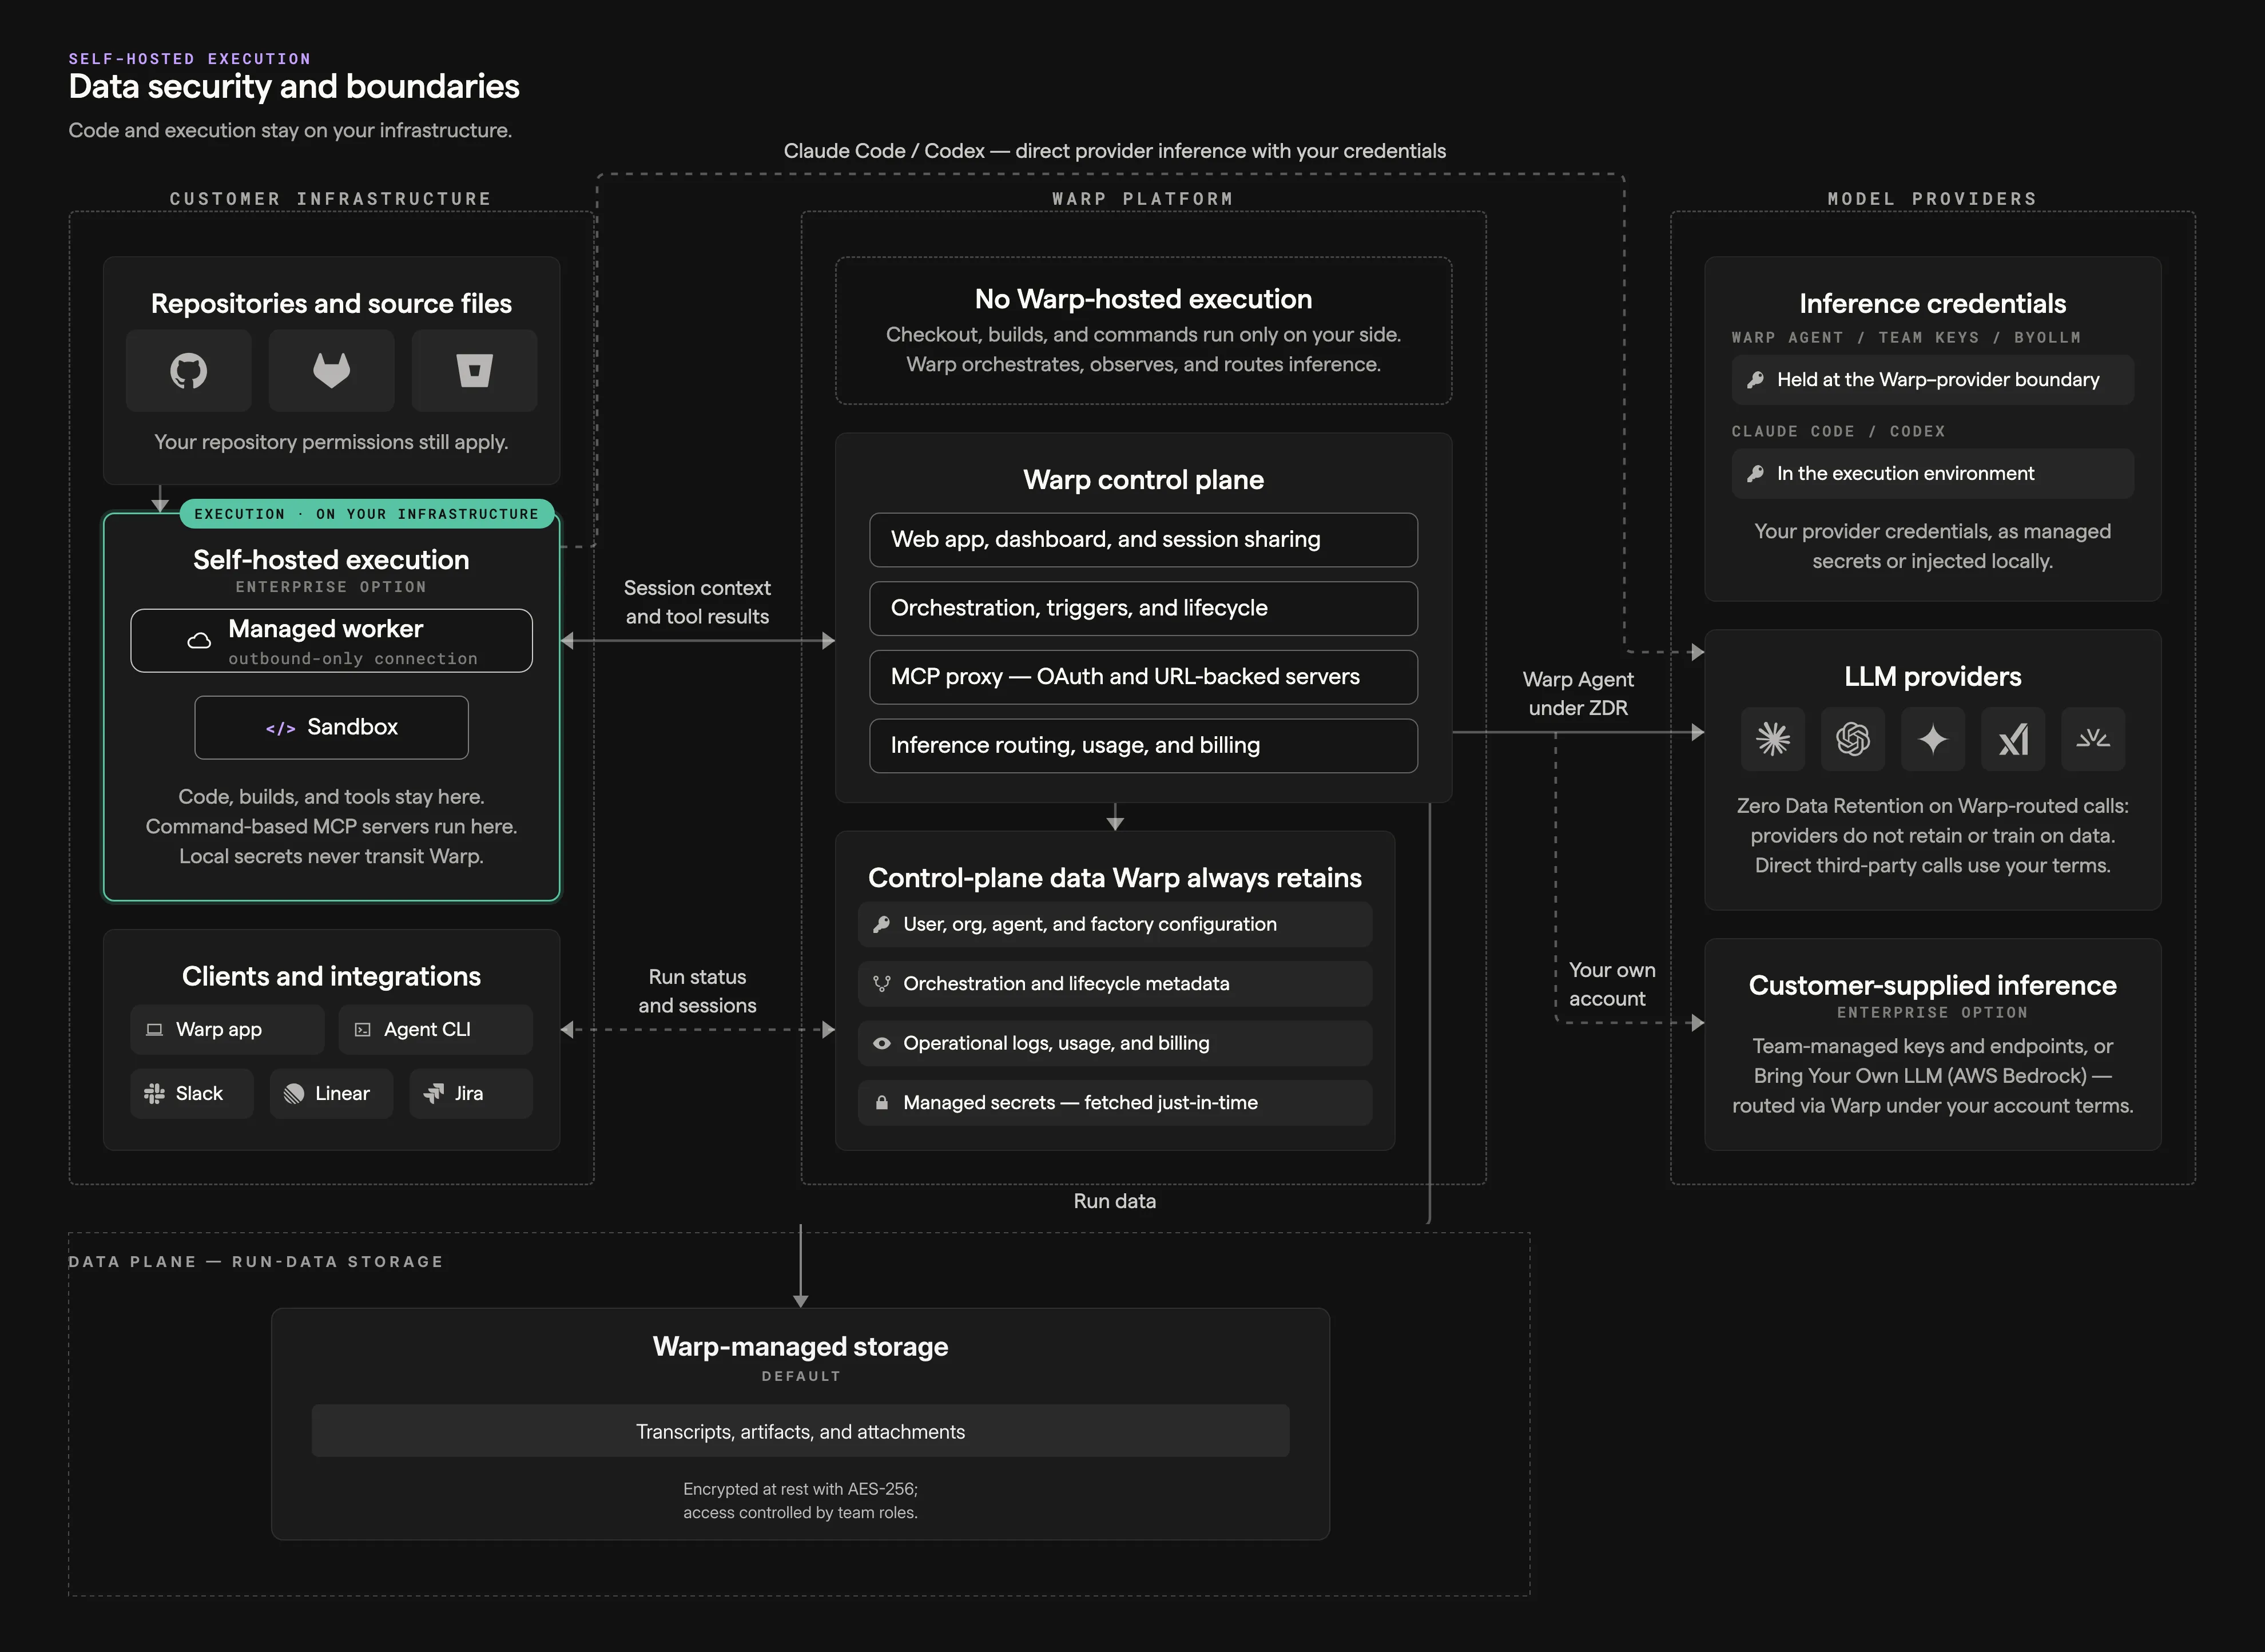
## Runners
[Section titled “Runners”](#runners)
A runner defines the compute a factory’s agents work on: the operating system and architecture, the sandbox image, and the instance shape (vCPUs and memory). The workspace itself — repositories, setup commands, and secrets — comes from the factory’s [definition](/factories/factory-as-code/). See the [runner reference](/factories/runners/) for the available compute options.
Declare runners as `runners/*.yaml` files. Every agent inherits `agentDefaults.runner`, and an agent or automation can override it. The execution host determines how the runner’s compute settings are used:
| Setting | Warp-hosted | Direct | Kubernetes | Docker |
| ------------------------------------------------------ | ------------------------------------------------------------------------ | -------------------------------------------------------------------- | --------------------------------------------------------------------------------------------------------------------------- | ----------------------------------------------------------------------------------- |
| `platform.os`, `platform.arch`, `platform.mac.version` | Selects the sandbox OS, architecture, and macOS VM version | Does not configure the host; the worker host determines the platform | Use Linux; the cluster and `pod_template` schedule nodes | Use Linux; the Docker daemon determines the architecture |
| `platform.linux.dockerImage` | Linux sandbox image | Ignored | Task and setup container image | Task container image |
| `platform.linux.registryCredentialSecretName` | Warp-managed private-registry credential | Ignored | Ignored; use `imagePullSecrets` | Ignored; configure registry credentials on the worker, such as in its Docker config |
| `instanceShape` | Sandbox size, subject to plan limits; omitted uses the workspace default | Ignored; the task uses host resources | Task-container requests and limits; overrides matching `pod_template` resources; omitted keeps template or cluster defaults | Task-container limits; omitted adds no limits |
Self-hosted runner settings do not provision worker capacity. Worker configuration controls host resources, registry authentication, volumes, node placement, and other backend policy.
See [cloud agent runner compute options](/factories/runners/) and [factory runner syntax](/factories/factory-as-code/#runnersnameyaml).
## Choose an execution host
[Section titled “Choose an execution host”](#choose-an-execution-host)
A factory runs its work on one of two execution hosts: Warp-hosted compute or a worker in the [managed self-hosting architecture](/factories/self-hosting/#managed-architecture).
| Decision area | Warp-hosted | Managed self-hosted |
| ------------------------- | ----------------------------------------- | ---------------------------------------------------------------- |
| **Compute** | Warp provisions the sandbox | Your team provisions the worker |
| **Checkout and commands** | Run on Warp-managed compute | Run on your infrastructure |
| **Network** | Warp manages sandbox connectivity | The worker connects outbound to Warp; no inbound firewall port |
| **Private services** | Must be reachable from the hosted sandbox | Reachable through the worker’s network access |
| **Operations** | Warp manages capacity and lifecycle | Your team manages capacity, isolation, updates, and availability |
To route factory work to a managed self-hosted worker (an Enterprise feature):
1. **Deploy a worker** - Review the [self-hosting requirements](/factories/self-hosting/), then connect a worker that authenticates to Warp with a self-hosted worker API key. Workers run on `linux/amd64` and `linux/arm64`, and the worker’s platform determines which workloads it can run.
2. **Pair it with a compatible runner** - Choose a runner that matches the worker’s platform.
3. **Select the worker in the factory definition** - Set [`workerHost`](/factories/factory-as-code/) so the factory routes work to it.
For a working definition with `workerHost` set and a platform-matched runner, see [`07-self-hosted-worker`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/07-self-hosted-worker).
Unmanaged self-hosted agents and other CLI agents can’t serve as a factory’s execution host, but they can exchange work with a factory through [Factory MCP](/factories/factory-mcp/).
### Managed self-hosting structures
[Section titled “Managed self-hosting structures”](#managed-self-hosting-structures)
Factories use managed self-hosting, so Warp still orchestrates their runs. The worker backend sets isolation and scheduling on your infrastructure:
| Structure | How factory runs execute | What your team operates | Use it when |
| --------------------------------------------------------------- | ------------------------------------------------------------------------------ | ------------------------------------------------------------------------------------------ | ----------------------------------------------------------------------------------- |
| **[Docker](/factories/self-hosting/managed-docker/)** (default) | In a separate Docker container on the worker host | The worker daemon, host, Docker daemon, images, capacity, and container policy | Docker is available and you want per-run container isolation without Kubernetes |
| **[Kubernetes](/factories/self-hosting/managed-kubernetes/)** | As a Kubernetes Job in the worker’s namespace | The worker deployment, cluster, namespace RBAC, scheduling, admission policy, and capacity | Your team already operates Kubernetes or needs cluster-native policy and scheduling |
| **[Direct](/factories/self-hosting/managed-direct/)** | In a separate workspace directly on the worker host, sharing its OS and kernel | The worker daemon, host security, dependencies, capacity, and cleanup | A container runtime isn’t available or runs need direct access to host resources |
## Choose inference independently
[Section titled “Choose inference independently”](#choose-inference-independently)
Execution hosting doesn’t select inference. Configure that boundary separately.
### Inference options for factory runs
[Section titled “Inference options for factory runs”](#inference-options-for-factory-runs)
Factory agents execute as cloud agents, so only inference options that support cloud agent runs apply:
| Option | Support for factory runs | Team controls | Key boundary |
| ------------------------------------------------------------------------------------------------------- | ------------------------------------ | -------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------ |
| **Warp-managed inference** | Supported | The model selected for each agent | Warp provides the provider account and bills model usage with Warp credits |
| **[Team-managed keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/)** | Supported on Business and Enterprise | Shared OpenAI, Anthropic, or Google keys, or an OpenAI-compatible endpoint | Warp stores the encrypted credential and uses it only at the inference boundary; it never enters the worker or run environment |
| **[BYOLLM: AWS Bedrock](/enterprise/enterprise-features/byollm-aws-bedrock/)** | Supported on Enterprise | The AWS account, IAM role, available Claude models, and provider billing | Warp assumes your IAM role through OIDC; inference runs in your AWS account |
| **[BYOLLM: Gemini Enterprise](/enterprise/enterprise-features/byollm-gemini-enterprise/)** | Not supported for factory runs | Interactive inference in your Google Cloud project | Gemini Enterprise BYOLLM currently supports interactive agent requests only |
Self-serve BYOK and custom inference endpoints are stored on an individual member’s device and don’t apply to factory runs. With team-managed keys and endpoints, select a specific provider model or endpoint; Auto continues to use Warp-managed inference. When you supply the provider, its retention follows your account and contract, and Warp can’t enforce ZDR for that provider.
## Credential boundaries
[Section titled “Credential boundaries”](#credential-boundaries)
A factory handles four kinds of credentials, each with its own boundary:
| Credential | Used for | Boundary |
| -------------------------- | -------------------------------------------------- | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Inference credentials** | Model provider requests | Used only at the inference boundary; never injected into the sandbox |
| **Execution secrets** | APIs, package registries, and tools an agent uses | Delivered from an explicit per-agent allowlist; factory agents that don’t act as a specific user receive no managed secrets by default |
| **Harness authentication** | Third-party harnesses such as Claude Code or Codex | Configured separately from the agent’s secret allowlist |
| **Repository identity** | Checking out code and pushing changes | Runs act with the creating user’s authorization (changes are attributed to them) or as the agent itself for unattended work; set by the definition’s [`credentialStrategy`](/factories/factory-as-code/#credentialstrategy) |
Scope each credential to the resources and actions its agent needs. Warp redacts known secret values at output boundaries, but redaction is a backstop, not a substitute for narrow external permissions and rotation. See [cloud agent secrets](/platform/secrets/), [harness authentication](/platform/harnesses/authentication/), [secret redaction](/support-and-community/privacy-and-security/secret-redaction/), and [team identity](/platform/team-access-billing-and-identity/) for the underlying controls.
## Governance and metering
[Section titled “Governance and metering”](#governance-and-metering)
Factories use your existing [team roles](/enterprise/team-management/roles-and-permissions/): Team Owners and Admins control factory definitions, runners, secrets, and provider configuration. Warp Factories doesn’t add a factory-specific approval role, so who reviews specifications and who approves merges stays a workflow and repository policy decision. Treat factory-definition changes as operational code: review them like any other change, and keep merge access with the people responsible for shipping.
Warp meters hosted compute, Warp-provided inference, and platform services. Managed self-hosted execution moves compute costs to your own infrastructure, and customer-supplied inference bills model usage through your provider account. Platform services consume credits regardless of these choices. See [platform credits](/support-and-community/plans-and-billing/platform-credits/) for details.
## Deployment checklist
[Section titled “Deployment checklist”](#deployment-checklist)
1. **Classify the workload** - Identify the repositories, data, internal services, and regulated systems the factory can reach.
2. **Choose execution** - Decide where checkout, commands, and the sandbox filesystem must run.
3. **Configure the factory and its runners** - Set the repositories, setup commands, secrets, and compatible runners in the factory’s definition.
4. **Choose inference** - Select provider routing.
5. **Scope credentials** - Set each agent’s secret allowlist, harness authentication, and repository identity.
6. **Set review gates** - Decide where humans review specifications and pull requests, and enforce those gates in workflow and repository policy.
7. **Validate operations** - Test network egress, isolation, rotation, redaction, capacity, observability, and metering before increasing volume.
## Related pages
[Section titled “Related pages”](#related-pages)
* [**Deployment patterns**](/factories/deployment-patterns/) - Compare Warp-hosted, managed self-hosted, and CLI-only execution.
* [**Managed self-hosting**](/factories/self-hosting/) - Choose a worker backend and follow its setup guide.
* [**Execution security**](/platform/execution-security/) - Review data boundaries, network egress, and backend-specific controls.
* [**Bring Your Own LLM**](/enterprise/enterprise-features/bring-your-own-llm/) - Compare customer-owned inference options and provider support.
* [**Enterprise security overview**](/enterprise/security-and-compliance/security-overview/) - Review data handling, ZDR, compliance, and access controls across Warp.
* [Team-managed model keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) - Configure customer-supplied inference credentials.
# Connecting Azure DevOps to your factory
Canonical page: [/factories/integrations/azure-devops/](https://docs.warp.dev/factories/integrations/azure-devops/)
> Connect Azure DevOps Services to a factory with dedicated identities, repository access, and event-driven automations.
Connect Azure DevOps Services to a factory so agents can work in selected repositories, open pull requests, and start runs from work item and pull request events. Warp creates a dedicated Microsoft Entra identity for each factory’s Git and pull request operations.
Note
Warp Factories is in Early Access and available to a limited set of teams. [Request access](https://www.warp.dev/factories/request-access) to use it with your team.
The first-class integration supports hosted Azure DevOps Services at `dev.azure.com`. It doesn’t support Azure DevOps Server. To use a self-hosted Azure DevOps Server repository, [configure it as another code forge](/factories/code-forges/other-code-forges/). For standalone cloud agent environments, use the [Azure DevOps access token setup](/platform/integrations/azure-devops/).
## How identities and access work
[Section titled “How identities and access work”](#how-identities-and-access-work)
Your personal Azure DevOps OAuth connection limits what appears during setup. The Azure DevOps Manager creates and manages each factory identity.
| Identity | Purpose | Access |
| ----------------------------------- | ----------------------------------------------------------------------------------------------------- | ------------------------------------------------------------------ |
| Your connected Azure DevOps account | Lists resources during setup and supplies your identity for creator-based runs. | Limited to resources your Azure DevOps user can read. |
| Azure DevOps Manager | Creates and maintains factory identities in one Microsoft Entra tenant and Azure DevOps organization. | Has Basic access and belongs to Project Collection Administrators. |
| Factory identity | Authenticates the factory’s Git and pull request operations after a run starts. | Has Basic access and permissions on the selected repositories. |
Each factory identity consists of a separate Microsoft Entra application and service principal that Warp adds to Azure DevOps.
## Requirements
[Section titled “Requirements”](#requirements)
* **A Warp team with Warp Factories access** - A factory belongs to a [Warp team](/knowledge-and-collaboration/teams/).
* **An Azure DevOps Services organization** - Use an organization hosted at `dev.azure.com`, with the project and repositories the factory needs.
* **A connected Azure DevOps user** - Connect a user who can read the organization, project, and repositories you want to select.
* **An active connection for each automation creator** - The user who creates an Azure DevOps automation must keep their own Azure DevOps OAuth connection active with the required scopes.
* **Microsoft Entra and Azure DevOps administrators** - Administrators with the roles listed below approve and add the Manager.
The Microsoft Entra and Azure DevOps approvals can be completed by different people. A setup link lets each administrator complete their step without a Warp account.
### Required administrator permissions
[Section titled “Required administrator permissions”](#required-administrator-permissions)
| System | Administrator | What the administrator approves |
| --------------- | ----------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------- |
| Microsoft Entra | Global Administrator or Privileged Role Administrator | The Manager’s Microsoft Graph `Application.ReadWrite.OwnedBy` permission, limited to applications the Manager owns. |
| Azure DevOps | Project Collection Administrator | Basic access and Project Collection Administrators membership. Warp doesn’t retain the administrator’s sign-in. |
Reuse tenant approval for another Azure DevOps organization in the same Microsoft Entra tenant. Each organization requires Azure DevOps approval.
Caution
The Manager and every factory identity use one Azure DevOps Basic seat each. Check available licenses before connecting an organization or adding factories.
## Connect Azure DevOps
[Section titled “Connect Azure DevOps”](#connect-azure-devops)
Start from factory setup to connect your account, select repositories, and provision the runtime identity.
1. Sign in to the [Warp Factories web app](https://platform.warp.dev). Next to the factory list, click **+** to create a factory.
2. In the code host step, find the Azure DevOps row and click **Connect**. Complete the Microsoft sign-in to connect your Azure DevOps user.
3. Choose an Azure DevOps organization and project, then select the repositories the factory will use. Only resources your connected user can read appear.
4. If the organization already has an active Azure DevOps Manager, continue setup. Otherwise, connect the Manager yourself or send the setup link to the required administrators.
5. Complete the Manager approval in this order:
1. A Global Administrator or Privileged Role Administrator completes the Microsoft Entra approval.
2. A Project Collection Administrator completes the Azure DevOps approval.
6. Continue factory setup. Warp creates the factory identity, adds Azure DevOps Basic access, and grants access to the selected repositories. Microsoft and Azure DevOps can take several minutes to apply these changes.
When setup confirms that the identity is ready, the factory uses that identity for Git and pull request operations. You can retry identity provisioning from the factory’s settings if setup is interrupted.
## Configure Azure DevOps automations
[Section titled “Configure Azure DevOps automations”](#configure-azure-devops-automations)
An Azure DevOps automation starts a factory run when a supported event matches its filters. Before starting a run, Warp checks the automation creator’s Azure DevOps connection. New Azure DevOps factories include a default automation for pull request mentions, work item mentions, and work item assignments.
To configure an automation as code, ask the Warp Agent to update the factory definition or edit its `automations/` files directly. See [definitions as code](/factories/factory-as-code/).
To add or change a trigger in the factory dashboard:
1. In the factory dashboard, open **Automations**, then create an automation or edit an existing one.
2. Add an Azure DevOps trigger, then choose an event and its filters.
3. Click **Save**. Perform a matching action in Azure DevOps and confirm that a run starts in the factory dashboard.
For general filter behavior, see [factory automations](/factories/automations/).
### Supported events and filters
[Section titled “Supported events and filters”](#supported-events-and-filters)
| Azure DevOps event | Available filters |
| --------------------------- | ----------------------------------------------- |
| Work item created | Work item types, labels, assignees, and authors |
| Work item assigned | Work item types, labels, assignees, and authors |
| Work item labeled | Work item types, labels, assignees, and authors |
| Mentioned in a work item | Mentioned users |
| Pull request created | Repository and target branches |
| Pull request merged | Repository and target branches |
| Pull request closed | Repository and target branches |
| Pull request updated | Repository and target branches |
| Pull request commented | Repository and target branches |
| Mentioned in a pull request | Repository and mentioned users |
Factory definition files also accept the Azure DevOps `push` event with repository and branch filters. The automation editor doesn’t currently offer this event.
Definition files accept `source_repos` for pull request events. Use it to match the repository that contains the pull request’s source branch. See [triggers in a factory definition](/factories/factory-as-code/#triggers) for the complete schema.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### An organization, project, or repository doesn’t appear
[Section titled “An organization, project, or repository doesn’t appear”](#an-organization-project-or-repository-doesnt-appear)
**Cause:** Your Azure DevOps user lacks access to the resource.
**Solution:** Grant the user access, then refresh the connection.
### Manager approval can’t continue
[Section titled “Manager approval can’t continue”](#manager-approval-cant-continue)
**Cause:** The Microsoft Entra approval is incomplete.
**Solution:** Complete the Microsoft Entra step before the Azure DevOps step. Reopen the setup link if another administrator completed the first step.
### Identity provisioning remains in progress
[Section titled “Identity provisioning remains in progress”](#identity-provisioning-remains-in-progress)
**Cause:** Microsoft Entra and Azure DevOps permission changes can take several minutes to propagate.
**Solution:** Wait, then retry from the factory’s settings if setup reports an error.
### An event doesn’t start a run
[Section titled “An event doesn’t start a run”](#an-event-doesnt-start-a-run)
**Cause:** The automation is disabled, a filter doesn’t match, or its creator’s Azure DevOps OAuth connection is missing, revoked, or under-scoped.
**Solution:** Enable the automation, check every filter, and reconnect its creator’s Azure DevOps account with the required scopes.
### Factory identity doesn’t appear in comment mention autocomplete
[Section titled “Factory identity doesn’t appear in comment mention autocomplete”](#factory-identity-doesnt-appear-in-comment-mention-autocomplete)
**Cause:** Azure DevOps doesn’t yet recognize the factory identity for comment autocomplete.
**Workaround:** Make Azure DevOps recognize the factory identity by using it once in the organization:
1. In the Azure DevOps organization and project connected to the factory, assign the factory identity to a work item and save the work item.
2. Return to the comment, enter `@` followed by the factory identity’s name, then select the identity from autocomplete.
3. Confirm that Azure DevOps formats the selection as a mention. Plain text with the same name doesn’t trigger the automation.
### `The identity value 'X' for field 'Assigned To' is an unknown identity.`
[Section titled “The identity value 'X' for field 'Assigned To' is an unknown identity.”](#the-identity-value-x-for-field-assigned-to-is-an-unknown-identity)
**Cause:** Azure DevOps can’t resolve the factory identity for the current work item. This can happen when the work item is outside the organization or project configured for the factory.
**Solution:**
1. In the factory’s settings, confirm its Azure DevOps organization and project.
2. In Azure DevOps, open the work item from that organization and project, then assign the factory identity again.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Warp Factories quickstart](/factories/quickstart/) - Create a factory and send its first work item.
* [Factory automations](/factories/automations/) - Configure triggers, filters, and routing.
* [Azure DevOps access for standalone cloud agents](/platform/integrations/azure-devops/) - Configure a PAT, Warp-managed secret, and environment clone command.
* [Other code forges](/factories/code-forges/other-code-forges/) - Connect repositories that don’t have a first-class integration, including Azure DevOps Server.
* [Infrastructure and security](/factories/infrastructure-and-security/) - Review how factories handle execution, credentials, and access.
# Connect GitHub to your factory
Canonical page: [/factories/integrations/github/](https://docs.warp.dev/factories/integrations/github/)
> Connect GitHub to your factory so issues, pull requests, reviews, and CI events start factory work and results post back to GitHub.
When you connect a factory to GitHub, repository activity starts work in your factory. Issues, pull requests, reviews, and CI events can all trigger automations, and the factory posts results back to GitHub as comments, branches, and pull requests.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **The Warp GitHub App** - Follow the [GitHub integration setup](/platform/integrations/github/) if you haven’t already. One installation serves both the platform integration and factories.
* **A factory with GitHub repositories** - The app must have access to at least one of the factory’s repositories.
## Connect GitHub to a factory
[Section titled “Connect GitHub to a factory”](#connect-github-to-a-factory)
1. In the [Warp Factories web app](https://platform.warp.dev), click **+** next to **Factories** to open the setup wizard, then choose **I want to use repos from GitHub** under **Connect your code host**.
2. Under **Select your repos**, choose the repositories to provide code and context for the factory.
That’s all the setup GitHub needs. A new factory arrives with default automations already switched on, so it responds to GitHub activity right away:
* **Mentions and assignments** - Start work by mentioning **@warp** or assigning the factory. See [Mention the factory](#mention-the-factory) below.
* **Pull request closed or merged** - Completes linked work when a pull request with your factory’s label merges (which can move linked tracker issues to their completed state). An unmerged close is a no-op.
* **Issue labeled** and **Pull request labeled** - Start work when the factory’s label is applied to an issue or pull request.
* **Pull request review submitted** - Start work when a review is submitted on a pull request that carries the factory’s label.
To confirm the connection works, mention **@warp** on a test issue and check that a work item starts in the factory’s [dashboard](/factories/factory-dashboard/).
## Add a custom automation
[Section titled “Add a custom automation”](#add-a-custom-automation)
The defaults cover mentions, assignments, label routing, review submissions, and pull request completion. To start work from any other GitHub activity, such as a failed CI run or a review request, add an automation with a GitHub trigger for that event, then narrow it with the filters below. To learn how to edit those filters, see [Automations](/factories/automations/#edit-filters-on-an-automation).
The CI failure triage automation in [`06-common-automations`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/06-common-automations) in the [warp-factory-examples](https://github.com/warpdotdev/warp-factory-examples) repository starts work when a workflow run fails on the default branch:
automations/ci-failure-triage/automation.md
```markdown
---
triggers:
- provider: github
event: workflow_run_completed
filter:
repos: [acme/api-service]
branches: [main]
conclusions: [failure]
---
A workflow run failed on the default branch. Read the run's logs and find
the failing step. If the cause is small and clear, open a fix PR. Otherwise
open an issue with the failing step, the error, and the commit range, and
link the run.
```
For a review automation that fires when pull requests open, see [`04-code-review-only`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/04-code-review-only).
## Supported triggers
[Section titled “Supported triggers”](#supported-triggers)
| Trigger | Supported activity |
| ------------- | ----------------------------------------------------------------------------------------------------- |
| Issues | Created, labeled, assigned, or agent mentioned |
| Pull requests | Opened, marked ready, reopened, updated with commits, assigned, labeled, mentioned, closed, or merged |
| Reviews | Review requested or review submitted |
| Code and CI | Push, a completed check suite or workflow run |
For the exact `event` value each trigger uses in a definition file, see [triggers](/factories/factory-as-code/#triggers).
### Automation filters
[Section titled “Automation filters”](#automation-filters)
Every trigger names the repository it watches. The remaining filters appear only on the event types they apply to:
| Filter | Matches | Appears on |
| ------------------------------------ | ------------------------------------------------------------ | ------------------------------------------------------ |
| **Branches** | The pushed branch, or a CI run’s head branch | Push and CI triggers |
| **Base branches** | The branch the pull request targets | Pull request triggers |
| **Paths** | The files the change touches | Push and pull request triggers |
| **Labels** | Labels on the issue or pull request | Issue, pull request, review submitted, and CI triggers |
| **Authors** | Who opened the issue or pull request | Issue, pull request, and CI triggers |
| **Assignees** | Who the issue or pull request is assigned to | Issue and pull request triggers |
| **Mentioned users or teams** | Which user or team is @mentioned | Mention and review submitted triggers |
| **Reviewers** and **Reviewer teams** | Who review was requested from | Review requested triggers |
| **Review states** | Whether the review approved, requested changes, or commented | Review submitted triggers |
| **Workflows** | The GitHub Actions workflow, by name | Workflow run triggers |
| **Conclusions** | The run’s result: success, failure, cancelled, and so on | Check suite and workflow run triggers |
On check suite and workflow run triggers, **Labels** and **Authors** match the pull request linked to the run rather than the run itself.
## Mention the factory
[Section titled “Mention the factory”](#mention-the-factory)
Add the factory’s `factory:<alias>` label to the issue or pull request, then mention **@warp** in the opening body or a new comment. The alias is the **Foreman name** in the factory dashboard’s **Identity** settings. Warp creates the label with the factory, and the factory replies in the same thread.
Without the label, a linked Warp account can still route the mention:
* **One accessible factory** - Warp adds its label and starts work.
* **Multiple accessible factories** - Warp asks you to add the right label and mention **@warp** again.
* **No accessible factory** - Warp asks you to connect the repository or request access.
Default automations can respond to authors whose GitHub accounts aren’t linked to Warp.
Only new content counts as a mention. Edits to existing comments, mentions inside code blocks, and mentions from bots are ignored.
You can change what the factory answers to. The handle and the label are the starting filters on its mentions automation: edit them to respond to a different handle, such as your own `@org/team` slug, or remove the label filter so that any mention in the factory’s repositories starts work.
## How the factory responds on GitHub
[Section titled “How the factory responds on GitHub”](#how-the-factory-responds-on-github)
The factory posts progress and links in the originating issue, pull request, or review thread. Pushes and workflow runs report on the work item instead. New activity on an existing thread continues the same work item.
Issues and pull requests the factory opens or adopts carry its `factory:<alias>` label. Warp removes it when you disconnect the repository or delete the factory. Delete old labels after renaming the alias.
Branches and pull requests the factory creates follow the repository’s normal rules: branch protection, required reviews, and merge requirements all still apply.
## Permissions
[Section titled “Permissions”](#permissions)
Runs authenticate with the GitHub App installation, not with the account of the person whose activity triggered them:
* **The app installation decides what agents can reach.** Agents get exactly the repositories and permissions the installation grants, so change the installation to change access. [Automation filters](/factories/automations/) only change when work starts.
* **Anyone who can create matching activity can start work.** The event author doesn’t need to be a Warp team member. Use author, label, and branch filters to control what starts runs.
For the full credential model, see [Permissions and identity](/platform/integrations/github/#permissions-and-identity) on the GitHub integration page.
## Factory-definition pull request checks
[Section titled “Factory-definition pull request checks”](#factory-definition-pull-request-checks)
If the factory’s [definition is managed as code](/factories/factory-as-code/) in a GitHub repository, Warp reviews changes to it the way CI reviews code. Open a pull request that touches the definition files and a **warp/factory-config** check runs: it validates the head commit and dry-runs the change against your team, so it also catches a secret, runner, MCP server, or model that doesn’t exist. It passes with a summary of what merging would create, update, and delete, or fails with the specific fields to fix. If the definition lives in a subdirectory of the repository, the directory is appended to the check name, as in **warp/factory-config (factory)**. Require the check in branch protection to stop an invalid definition from merging.
These checks validate configuration files only and don’t create work items. Unchanged definitions pass immediately, so requiring the check doesn’t block unrelated work. To check a definition before opening a pull request, see [Validate a definition](/factories/factory-as-code/#validate-a-definition).
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### A mention doesn’t start work
[Section titled “A mention doesn’t start work”](#a-mention-doesnt-start-work)
Confirm the mention is new human-authored content, not an edit, bot comment, or markdown code. Use **@warp**, and add the factory’s `factory:<alias>` label. Without a label, routing works only when your linked Warp account can access exactly one factory connected to the repository.
If you renamed the alias or changed repositories after creating the factory, the default automation’s filters still use the original snapshot. Edit that automation so the label and repository filters match.
### A GitHub event doesn’t start work
[Section titled “A GitHub event doesn’t start work”](#a-github-event-doesnt-start-work)
Confirm the app installation covers the event’s repository, the repository belongs to the factory, and the automation includes that event. Then check each filter; a label, author, branch, workflow, conclusion, or state mismatch prevents routing.
### Filter options don’t load
[Section titled “Filter options don’t load”](#filter-options-dont-load)
Select a repository first. If the automation editor shows **Connect GitHub**, complete the account connection and retry. You can enter a value manually when suggestions are unavailable.
### An agent can’t push a branch or open a pull request
[Section titled “An agent can’t push a branch or open a pull request”](#an-agent-cant-push-a-branch-or-open-a-pull-request)
Check that the installation still covers the target repository and grants the required write permissions. Automation filters don’t affect GitHub authorization.
### A factory-definition check doesn’t appear
[Section titled “A factory-definition check doesn’t appear”](#a-factory-definition-check-doesnt-appear)
The check runs only for factories whose [definition is managed as code](/factories/factory-as-code/) in a GitHub repository. Confirm the pull request targets the branch the factory runs from and that the GitHub App covers the repository.
# Connect GitLab to your factory
Canonical page: [/factories/integrations/gitlab/](https://docs.warp.dev/factories/integrations/gitlab/)
> Connect GitLab to your factory so merge request events and bot mentions start factory work and results post back as comments and merge requests.
When you connect a factory to GitLab, project activity starts work in your factory. Merge request events and bot mentions trigger automations, and the factory posts results back to GitLab as comments, branches, and merge requests.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **GitLab.com** - The integration supports GitLab.com only, not self-managed GitLab instances. To use a self-managed instance with a factory, see [connecting other code forges](/factories/code-forges/other-code-forges/). For standalone cloud agents, see the [GitLab access token setup](/platform/integrations/gitlab/).
* **A top-level GitLab group you own** - Connecting GitLab links one top-level group to your Warp workspace, one-to-one. Creating the link requires the Owner role on the group and workspace admin permissions in Warp.
* **A GitLab plan with service accounts and group webhooks** - Warp provisions service accounts in your group and installs a group webhook; both are GitLab Premium and Ultimate features. On a plan without group webhooks, factory credentials still work, but GitLab cannot trigger runs.
## Service accounts and access
[Section titled “Service accounts and access”](#service-accounts-and-access)
Warp manages GitLab access through service accounts it creates in your connected group rather than a marketplace app:
* **One manager account per workspace** - Created when you connect the group and granted the Owner role on it. Warp uses it to provision factory accounts, mint their run credentials, and maintain the group webhook; its provisioning token is valid for one year.
* **One bot account per factory** - Each factory gets its own service account, named from the factory’s alias plus a `-warp-` suffix and a short unique ID (for example, `acme-support-warp-01k2x3y4z5`). The bot holds the Developer role on exactly the projects you select for the factory. It is the factory’s identity on GitLab. Runs authenticate as the bot, and its username is the handle you mention.
The connected group’s webhook delivers merge request and comment events to Warp, and matching automations turn them into factory work.
## Connect GitLab to a factory
[Section titled “Connect GitLab to a factory”](#connect-gitlab-to-a-factory)
1. In the [Warp Factories web app](https://platform.warp.dev), click **+** next to **Factories** to open the setup wizard.
2. Choose **I want to use repos from GitLab** under **Connect your code host**, then authorize with GitLab when prompted.
3. Under **Connect a GitLab group**, pick a top-level group you own and click **Next**. Warp creates the manager service account and installs the group webhook. A group that is already connected shows a **Connected** badge, and the selection is locked to it.
4. Under **Select your repos**, choose the projects to provide code and context for the factory. Projects anywhere under the connected group, including subgroups, are available.
5. In the factory’s [dashboard](/factories/factory-dashboard/), click **Automations**. GitLab factories start with an editable default automation, **gitlab-bot-mentions**, that fires when the factory’s bot is mentioned.
6. To route merge request events too, create an automation and click **Add trigger**.
7. Choose **GitLab**, then choose **Merge request**.
8. To confirm the connection works, comment on a merge request in a selected project and mention the factory’s bot. A work item starts in the factory dashboard, and the factory replies in the same thread.
## Supported triggers
[Section titled “Supported triggers”](#supported-triggers)
| Trigger | Fires when |
| ------------- | ------------------------------------------------------------------------- |
| Merge request | A merge request is opened, updated, closed, reopened, merged, or approved |
| Bot mentioned | A new comment mentions the factory’s bot username |
### Automation filters
[Section titled “Automation filters”](#automation-filters)
| Filter | Matches | Appears on |
| --------------- | ---------------------------------------------------------------------- | ------------- |
| **Project** | The GitLab project the event came from | Both triggers |
| **Actions** | What happened to the merge request, such as opened, updated, or merged | Merge request |
| **Base branch** | The branch the merge request targets | Merge request |
On the **Bot mentioned** trigger, the mention username is managed by Warp. It is always the factory’s own bot, shown as read-only in the automation editor, and it cannot be set in a definition file.
## Mention the factory
[Section titled “Mention the factory”](#mention-the-factory)
Each GitLab factory has its own bot account, so the mention itself routes the request. There is no shared handle or routing label to apply. To mention the factory:
1. Open a merge request in one of the factory’s projects.
2. Post a comment that mentions the factory’s bot username and includes an instruction.
The **gitlab-bot-mentions** automation starts a work item, and the factory replies in the same thread. To find the bot’s username, check that automation’s trigger in the [factory dashboard](/factories/factory-dashboard/).
Mentions count only in new comments. Edits and activity from Warp’s own service accounts never trigger work, so a factory can’t re-trigger itself or a sibling factory.
## How the factory responds on GitLab
[Section titled “How the factory responds on GitLab”](#how-the-factory-responds-on-gitlab)
The factory acts on GitLab as its bot account:
* **Replies in the thread it was mentioned in** - Its comments link back to the run session and the factory work item. New comments on the same merge request continue that work item instead of starting a new one.
* **Pushes branches and opens draft merge requests** - Branches are named `factory/<slug>`, and merge requests open as drafts that the factory marks ready when the work is done. Commits and comments attribute to the bot’s GitLab profile.
* **Labels what it touches** - Merge requests and issues the factory opens or adopts carry its own label, named `factory:` followed by the factory’s [**Foreman name**](/factories/factory-dashboard/#change-factory-settings).
* **Posts review feedback as comments** - A review lands as a summary note plus inline discussions on the diff. When a later revision addresses a finding, the factory replies in that discussion and resolves it.
The factory never merges or approves a merge request; those decisions stay with your team. Branch protection and approval rules apply to everything the bot does.
## Permissions
[Section titled “Permissions”](#permissions)
Runs authenticate as the factory’s bot account, not as the person whose activity triggered them:
* **The bot’s project membership decides what runs can reach.** Each run gets a short-lived token scoped to the bot’s Developer role on the factory’s selected projects. Selecting projects for a factory or tightening automation filters changes when work starts, not what a running agent can access. To change access, change the factory’s projects.
* **Anyone who can create matching activity can start work.** The commenter doesn’t need to be a Warp team member. Use project, action, and base-branch filters to control what starts runs.
Disconnecting GitLab from the workspace retires the manager and every factory bot it provisioned.
## Definitions as code
[Section titled “Definitions as code”](#definitions-as-code)
If the factory’s [definition is managed as code](/factories/factory-as-code/), declare GitLab triggers in an automation file:
automations/gitlab-merge-requests/automation.md
```markdown
---
enabled: true
agent: foreman
triggers:
- provider: gitlab
event: merge_request
filter:
repos: [my-group/my-app]
actions: [open]
---
Triage newly opened merge requests and post an initial review.
```
A `bot_mentioned` trigger takes only a `repos` filter. Leave `mentioned` out. Warp seeds it with the factory’s bot username and rejects definitions that set it. GitLab isn’t yet supported as a definition-hosting repository, so declare these triggers in a Warp-managed or GitHub-hosted definition even when the factory’s automations and mentions run through GitLab; see [where the definition lives](/factories/factory-as-code/#where-the-definition-lives).
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### A mention doesn’t start work
[Section titled “A mention doesn’t start work”](#a-mention-doesnt-start-work)
Confirm the mention is in a new comment rather than an edit, the username matches the factory’s bot exactly, the project is one of the factory’s selected projects, and the **gitlab-bot-mentions** automation is enabled.
### A merge request event doesn’t start work
[Section titled “A merge request event doesn’t start work”](#a-merge-request-event-doesnt-start-work)
Confirm an enabled automation includes the **Merge request** trigger and check its project, action, and base-branch filters. Activity authored by Warp’s own service accounts is always ignored.
### Nothing starts work even though GitLab is connected
[Section titled “Nothing starts work even though GitLab is connected”](#nothing-starts-work-even-though-gitlab-is-connected)
Your GitLab plan may not include group webhooks (see [Prerequisites](#prerequisites)). Upgrade your GitLab plan to let GitLab trigger runs.
### The bot can’t push a branch or open a merge request
[Section titled “The bot can’t push a branch or open a merge request”](#the-bot-cant-push-a-branch-or-open-a-merge-request)
Confirm the target project is one of the factory’s selected projects and the operation is permitted for the Developer role. Pushes to protected branches follow the project’s protection rules.
### Your group isn’t listed when connecting
[Section titled “Your group isn’t listed when connecting”](#your-group-isnt-listed-when-connecting)
Only top-level groups you own appear, and a group already connected to another Warp workspace can’t be connected again. If you don’t own the group, ask an owner to establish the connection in Warp.
For the other ways to route work into a factory, see [Connect your factory](/factories/connect-your-factory/).
# Connect Jira to your factory
Canonical page: [/factories/integrations/jira/](https://docs.warp.dev/factories/integrations/jira/)
> Connect Jira Cloud to your factory so work items assigned to Warp start factory runs and return results in Jira.
Connect Jira Cloud to your factory so your team can start factory work without leaving Jira. When someone assigns or mentions **Warp** on a work item, Jira starts an agent session, a factory automation routes the request to the agent you chose, and the same session shows progress and the final result.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **Jira Cloud** - The integration supports Jira Cloud only, not Jira Server or Data Center.
* **A Jira site admin** - Installing the Warp app on a Jira site and connecting it to a Warp workspace requires site admin permissions.
* **A factory** - You need a factory in the connected workspace and permission to edit its [definition](/factories/factory-as-code/).
* **The Warp agent in Jira** - The **Warp** agent must be available on your Jira site so people can assign or mention it on work items. Jira lists it among Atlassian’s Rovo agents.
## Connect Jira and add an automation
[Section titled “Connect Jira and add an automation”](#connect-jira-and-add-an-automation)
1. **Install the Warp app on your Jira site and connect it to your Warp workspace.** The [Jira integration setup](/platform/integrations/jira/#setup) walks through both. Once connected, every factory in the workspace can use it. (That page’s `warp-agent` label flow starts standalone cloud agent runs; factories skip the label and use an automation instead.)
2. **Connect Jira to this factory.** A workspace connection makes Jira available to your factories, but each one opts in separately: in the factory’s **Settings**, connect **Jira** and select the projects that should trigger it.
3. **Point an automation at Jira.** In the factory’s dashboard, open **Automations** and add a trigger for **Jira** > **Agent session created**. Use **Projects** and, optionally, **Keywords** to scope which sessions start a run, and choose the agent that handles them.
If you picked Jira projects when you created the factory, that automation already exists. Edit it rather than adding a second one.
To set this up in code instead, declare the `jira` integration in the factory’s `factory.yaml` (`integrations: [{type: jira}]`), then add a file under `automations/`, such as `automations/jira-assignment/automation.md`, with an `agent_session_created` trigger:
automations/jira-assignment/automation.md
```markdown
---
enabled: true
agent: foreman
triggers:
- provider: jira
event: agent_session_created
filter:
project_keys: [ENG]
keywords: [investigate, fix]
---
Handle the Jira assignment and return a concise result.
```
With this automation, the agent named `foreman` handles sessions for work items in the `ENG` project whose assignment text contains `investigate` or `fix`. Commit and push the files to apply them; see [definitions as code](/factories/factory-as-code/) for the full syntax.
4. **Test it.** Assign or mention **Warp** on a work item and include an instruction. Jira starts an agent session, and the run appears under the matching automation in your factory.
## Filter which sessions start runs
[Section titled “Filter which sessions start runs”](#filter-which-sessions-start-runs)
All Jira work reaches the factory through a single event, `agent_session_created`, which fires when someone assigns or mentions **Warp** on a work item. A session starts a run only when it matches an enabled automation. Use the trigger’s `filter` to narrow what matches:
* **`project_keys`** - Match work items in these Jira projects.
* **`keywords`** - Match assignment text that contains any of these words. Matching is case-insensitive.
A session must match every field you set; within a field, any listed value is a match. Omit a field to match everything. For the matching rules shared by every source, see [automation filters](/factories/automations/).
Caution
A Jira event is offered to every automation in the connected workspace, so another team’s automation with a broader filter can start its own run on the same work item. Filters decide what *your* automation picks up, not who else can see the event. See [Automations](/factories/automations/#filters-dont-control-access).
## What happens during a run
[Section titled “What happens during a run”](#what-happens-during-a-run)
The agent runs in the cloud and starts with the assignment text and the work item it came from. When the factory declares Jira as an integration, the agent can also read the work item’s details, comments, and available workflow transitions.
Jira shows the task’s status as it progresses: submitted, working, waiting for input, completed, failed, or cancelled. For more than status updates, open the run under the matching automation in your factory: [cloud agent session sharing](/platform/viewing-cloud-agent-runs/) shows the full run, including every command, log, and output, in real time or after the run finishes.
Replies in the same agent session continue the same run, even after the agent finishes a turn, so you can answer questions or add direction mid-task.
When the run finishes, the result appears in the agent session. The agent doesn’t comment on the work item unless you ask it to. The agent can act in Jira when asked: update the work item, post or edit comments, change workflow status, add or remove labels, or reassign it. State the actions you want in the automation instructions or the assignment; Jira permissions and valid workflow transitions apply to everything the agent does.
## Permissions
[Section titled “Permissions”](#permissions)
* **A connected Jira user becomes the run’s creator, not its agent** - [Connect your Jira account to Warp](/platform/integrations/jira/#connecting-your-jira-account-to-warp) so a session you start is attributed to you; an unconnected account gets a prompt to connect instead of a run starting. Either way, the run executes as the agent selected by the automation, not as that Jira user.
* **Jira access doesn’t include code access** - Connecting Jira lets agents read and update Jira work items, nothing more. Repository access comes from the factory itself.
Caution
Warp’s built-in Jira tools read Jira as the person who created the run; that person must link their Atlassian account to Warp in Jira under **profile** > **Personal settings** > **Warp**. To interact with Jira in runs without a human creator, such as scheduled runs or runs created by a service account or API key, add the Atlassian MCP server as a [managed MCP install](/platform/mcp/) instead.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
* **Warp is unavailable in Jira** - Confirm the Warp app is installed on the Jira Cloud site. On the app’s **Configure** page, click **Connect to Warp** if the installation isn’t connected to a workspace.
* **No run starts** - Confirm an enabled `agent_session_created` automation exists, its agent is available, and its project and keyword filters match the assignment.
* **The session shows no result** - Open the matching automation’s run to see whether the agent is still working, waiting for input, or failed.
* **A Jira update fails** - Confirm the app can access the work item’s project and that the requested action or workflow transition is valid.
For the other ways to route work into a factory, see [Connect your factory](/factories/connect-your-factory/).
# Connect Linear to your factory
Canonical page: [/factories/integrations/linear/](https://docs.warp.dev/factories/integrations/linear/)
> Connect Linear to your factory so planned issues flow in automatically and progress flows back to the issue.
Connect Linear to your factory so your team can send issues without leaving Linear. Assign an issue to the factory or tag it in a comment, and the factory picks it up with the issue’s full context, then keeps the issue updated as the work moves through [its stages](/factories/how-factories-work/).
When the factory needs an answer, reply in Linear, or open the live run to steer the agent directly.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **A factory** - Create a factory with the agents and repositories needed to handle Linear work.
* **A Linear workspace** - Use a Linear account that can authorize the Warp app for the workspace.
* **A linked Warp account (agent sessions only)** - Anyone who starts a Linear agent session must link their Linear user to their Warp account. If Warp can’t identify the session creator, Linear shows an authentication prompt instead of starting work.
* **Code host access** - Configure repository access separately through the factory’s [GitHub connection](/platform/integrations/github/). The factory needs it to change code or create a pull request.
For workspace-level installation, reconnection, and removal steps, see the [Linear integration setup guide](/platform/integrations/linear/).
## Connect Linear
[Section titled “Connect Linear”](#connect-linear)
You connect Linear either while creating a factory, at the **Connect your issue trackers** step, or afterward from the factory’s **Settings**. Either way you do the same two things:
1. **Authorize Warp for your Linear workspace.** This is Linear’s own OAuth flow, and it’s only needed once per workspace.
2. **Choose which Linear teams trigger this factory.**
Warp then adds a default automation that routes new [agent sessions](#route-agent-sessions) from those teams to your factory. Issue and comment activity doesn’t start work until you [add triggers](#configure-linear-triggers) for it.
## Route agent sessions
[Section titled “Route agent sessions”](#route-agent-sessions)
When someone mentions, assigns, or delegates the Warp app on an issue, Linear starts an agent session. The default automation created when you connected Linear routes new sessions from your selected teams to the factory, so assigning an issue or tagging the factory in a comment is enough to start work. If a session doesn’t match any automation, the [Linear integration](/platform/integrations/linear/) handles it with its default behavior.
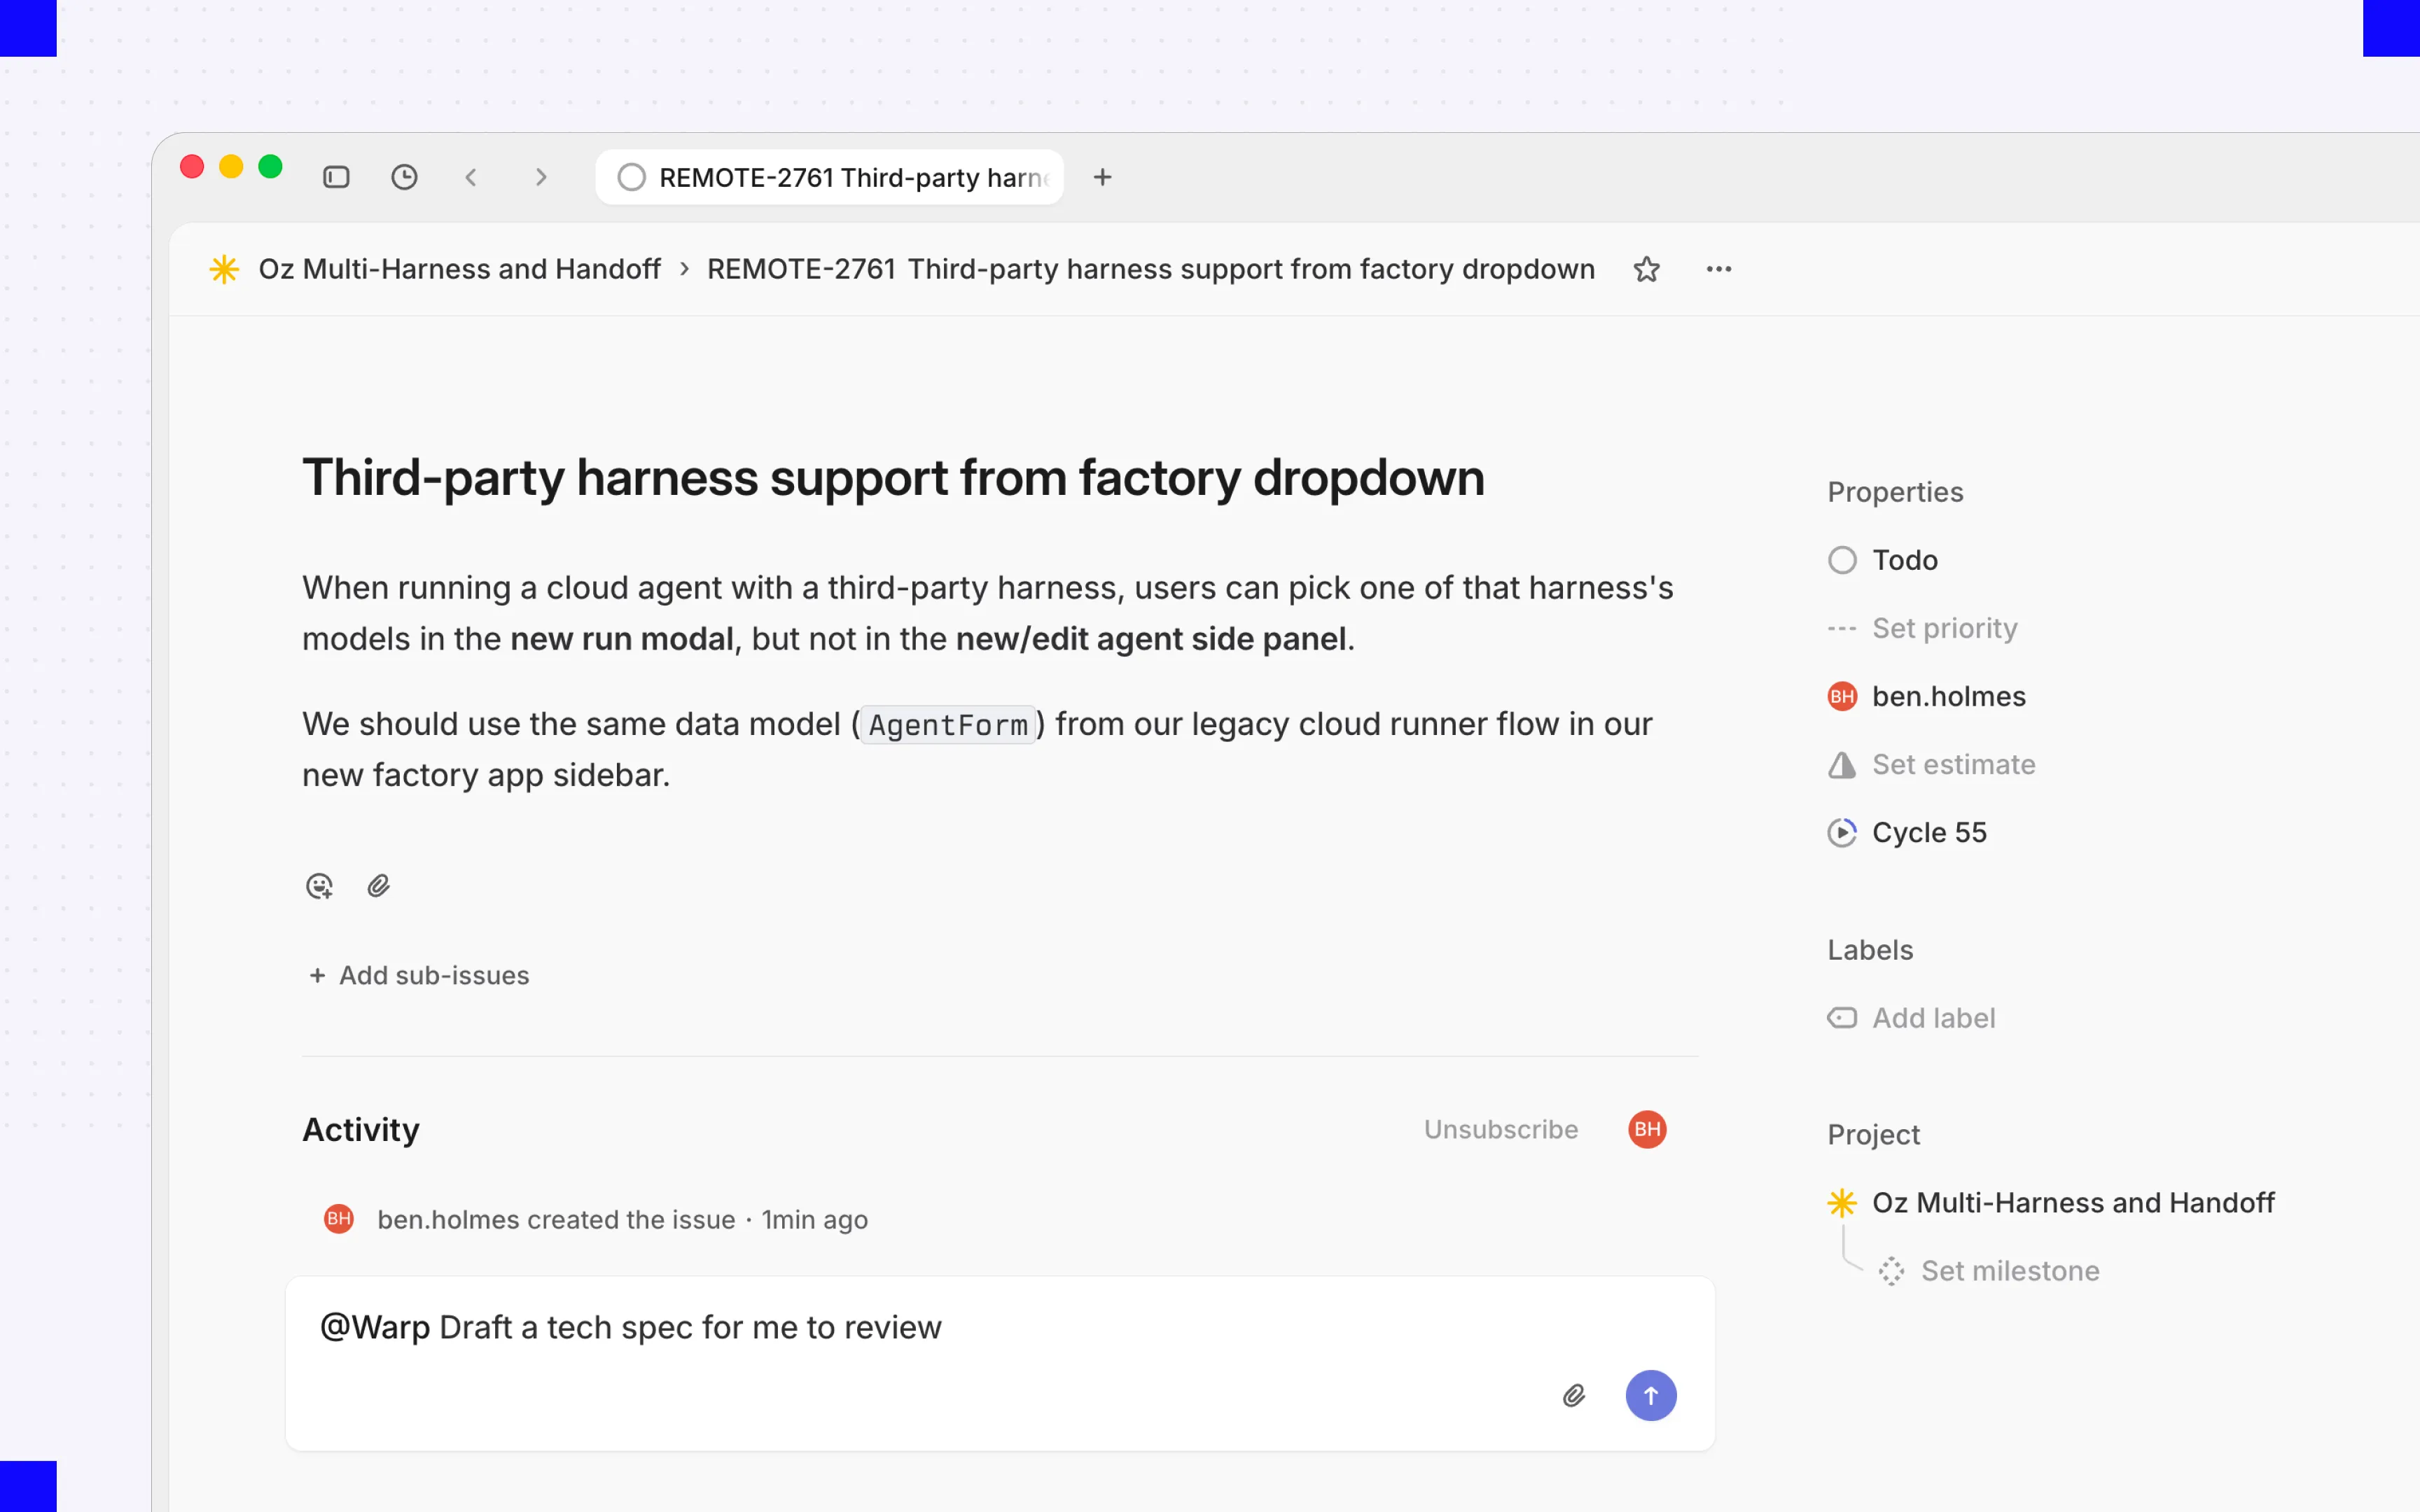
Mentioning the Warp app in an issue comment starts an agent session.
Replies in an existing session continue that run rather than starting a new one. To narrow which sessions reach the factory, such as by creator or keyword, edit the `agent_session_created` trigger in the factory’s [definition files](/factories/factory-as-code/); session routing isn’t editable from the automation editor.
## Configure Linear triggers
[Section titled “Configure Linear triggers”](#configure-linear-triggers)
Agent sessions cover explicit requests. To start work automatically from issue and comment activity too, add an automation with a **Linear** trigger for one of these events: **Issue created**, **Issue labeled**, **Issue state changed**, **Issue assigned**, or **Comment created**. To learn how to edit those filters, see [Automations](/factories/automations/#edit-filters-on-an-automation).
Every Linear trigger filters on teams and labels, and **More filters** adds project, workflow state, assignee, mentioned user, and, for comment events, a specific issue. For example, a trigger can require that an issue belongs to one team, enters a chosen workflow state, and carries a release label.
For the exact `event` value each of these triggers uses in a definition file, see [triggers](/factories/factory-as-code/#triggers).
## Supported events and outputs
[Section titled “Supported events and outputs”](#supported-events-and-outputs)
Each event determines the context the agent receives and the updates the factory sends back.
| Linear event | What the agent receives | What the factory sends back |
| -------------------------------------------------- | ----------------------------------------------------------------------------------- | ------------------------------------------------------------------------- |
| Issue created, labeled, state changed, or assigned | The issue’s title, description, team, project, labels, workflow state, and assignee | Work item progress, issue state or delegate changes, and links to results |
| Comment created | The new comment and its issue’s context | An acknowledgment, progress updates, and responses |
| Agent session created | The request that mentioned, assigned, or delegated the Warp app | Live progress in the session, plus links to the run and any pull request |
| Reply in an agent session | The new message and the session history | Continued work in the same session, not a separate work item |
## Follow-up events on the same issue
[Section titled “Follow-up events on the same issue”](#follow-up-events-on-the-same-issue)
Once a Linear issue is linked to a factory work item, later matching events on that issue continue the same work item instead of creating a new one.
Caution
One comment can match two routes: a comment that creates an agent session can also match a **Comment created** trigger. If both point at your factory, a single action starts two runs. Scope your automations so one path owns each kind of request.
## What the factory can do in Linear
[Section titled “What the factory can do in Linear”](#what-the-factory-can-do-in-linear)
In an agent session, the factory posts its plan, actions, and results as it works. It can also attach a GitHub pull request to the issue, update the issue’s workflow state or delegate, link back to the run, and acknowledge comments it acts on. Its own Linear activity never triggers automations, so a factory can’t set itself off in a loop.
Only agent sessions require a linked Warp account. Issue and comment events from unlinked users still start work, but Warp may not record who requested it.
Connecting Linear doesn’t grant repository access. Branches and pull requests use the factory’s code-host credentials, and the pull request still waits for a person to review and merge.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
* **An agent session shows an authentication prompt** - Complete the prompt to link your Linear user to your Warp account, then retry the request.
* **Teams or filters don’t load** - Reconnect Linear by following the [Linear integration setup guide](/platform/integrations/linear/), then confirm the connection can access the workspace and team you expect.
* **An event doesn’t start work** - Confirm the automation is enabled, the event type matches, and every filter matches the issue’s current values or the state change.
* **One action starts multiple runs** - Look for overlapping agent-session and comment triggers, then narrow or remove one.
* **No pull request appears** - Check the factory’s code-host credentials and repository access. Linear authorization alone doesn’t allow code changes.
# Connect Slack to your factory
Canonical page: [/factories/integrations/slack/](https://docs.warp.dev/factories/integrations/slack/)
> Connect Slack to your factory so your team can start work with mentions, direct messages, and automations, and get results back in the same thread.
Connect a factory to Slack so your team can send work without leaving their conversations. Mention the factory in a channel or send it a direct message, and it picks up the request with the conversation as context, then posts progress and results back into the same thread.
Each factory appears in Slack as its own app with the factory’s name and avatar. A channel can host several factories, and you choose which one to mention.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **Permission to install Slack apps in the target workspace** - Workspace policy may require administrator approval before the app installs.
* **Permission to update the factory** - Connecting Slack changes the factory’s configuration.
## Connect the factory
[Section titled “Connect the factory”](#connect-the-factory)
1. **Select Slack while creating a factory**, or connect it later from the factory’s **Settings**. Warp installs its Slack app for you.
2. **Complete the install if it can’t finish on its own.** This usually happens when your workspace requires administrator approval. Click **Add to Slack** in factory setup to finish.
3. **Invite the app to each channel it should listen in.** Private channels always need an invitation.
4. **Confirm the connection.** Mention the app in one of those channels. It reacts with 👀 to show it picked up the request.
## Configure factory automations for Slack
[Section titled “Configure factory automations for Slack”](#configure-factory-automations-for-slack)
Use a factory automation to start work from Slack activity automatically, without anyone mentioning the app, such as on every message in a triage channel or on a specific emoji reaction. Add a **Slack** trigger to an automation and pick one of these events. To learn how to edit those filters, see [Automations](/factories/automations/#edit-filters-on-an-automation).
* **App mentioned** - Filter by joined conversations, authors, and keywords.
* **Direct message received** (`message_dm`) - Filter by direct-message conversations, authors, and keywords.
* **Message posted in channel** - Filter by joined conversations, authors, and keywords.
* **Reaction added** - Filter by conversations, reactors, keywords, emoji, and reacted-message authors.
* **Member joined channel** - Filter by conversations and members.
For the exact `event` value each of these triggers uses in a definition file, see [triggers](/factories/factory-as-code/#triggers).
The reaction-intake automation in [`06-common-automations`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/06-common-automations) in the [warp-factory-examples](https://github.com/warpdotdev/warp-factory-examples) repository files a GitHub issue when someone reacts with `:ticket:`:
automations/slack-reaction-intake/automation.md
```markdown
---
triggers:
- provider: slack
event: reaction_added
filter:
channels: [your-intake-channel]
emojis: [ticket]
---
Someone reacted with :ticket: to a Slack message. Read the thread, file a
GitHub issue that captures the request with a link back to the thread, and
reply in the thread with the issue link. Do not start the work; this
automation only files it.
```
The **Conversations** picker only shows conversations the factory’s app has joined. If a channel is missing, invite the app to it; for direct messages, send the app a DM first. Then refresh the automation editor.
A single Slack message can match more than one automation. For example, if one automation triggers on **App mentioned** and another triggers on **Message posted in channel** in the same channel, a channel message that mentions the app starts two separate runs, one for each automation. To avoid duplicate runs, don’t point both triggers at the same channel.
## Use integration-provided tools
[Section titled “Use integration-provided tools”](#use-integration-provided-tools)
When Slack is connected to a factory, Warp automatically gives its agents Slack tools during factory runs. The tools let an agent read channels and threads that the app can access, reply in a thread, and post a new top-level message to a channel. The run doesn’t need to start from Slack.
Warp also automatically makes tools from a connected Linear or Jira issue tracker available to the factory’s agents. These are Warp-managed, integration-provided capabilities, separate from the [MCP servers you configure for cloud agents](/platform/mcp/). They may not appear alongside user-configured MCP servers in the factory’s MCP list.
You don’t need to install a separate Slack MCP server to post factory output to Slack. The connected Slack app’s authorization still controls which channels the tools can access, so invite the app to the destination channel first.
## Post a scheduled factory digest to Slack
[Section titled “Post a scheduled factory digest to Slack”](#post-a-scheduled-factory-digest-to-slack)
A scheduled automation can compile a nightly report and post it to Slack. Put the destination’s Slack channel ID directly in the automation instructions. An explicit channel ID is the most reliable way to target the intended channel.
This automation runs every night at 2:00 AM UTC and tells the agent where to post:
automations/nightly-factory-digest/automation.md
```markdown
---
agent: foreman
triggers:
- provider: schedule
event: cron_fired
schedule:
name: nightly-factory-digest
cron: "0 2 * * *"
---
Summarize factory work completed or blocked in the last 24 hours.
Post the digest as a new top-level message to Slack channel ID C0123456789
using the connected Slack tools. Include links to each work item or pull
request, and report the Slack posting error if delivery fails.
```
Replace `C0123456789` with the destination’s channel ID. See [factory definition syntax](/factories/factory-as-code/#automationsnameautomationmd) for the other automation fields and schedule options.
## Start and continue work from Slack
[Section titled “Start and continue work from Slack”](#start-and-continue-work-from-slack)
Mention the app in a channel or thread, or send it a direct message, to start work. The factory picks up the message, including available thread history and supported attachments, and replies in the same place with an acknowledgment, progress updates, and links to results.
A plain reply in a thread continues work only if that thread already has a factory work item; to start new work in a channel, mention the app instead. Slack activity that matches an automation starts work the same way, without a mention, using the event details and the automation’s assigned agent.
You can attach files to a request or a follow-up. The factory includes the files it supports, and a file it can’t include doesn’t stop the text of your request from going through.
## Follow work and review outputs
[Section titled “Follow work and review outputs”](#follow-work-and-review-outputs)
The Slack thread where work started is also where you follow it: the factory posts progress and the final response there. Reply in the thread to add information or attachments while work is active, or to pick the same work item back up later.
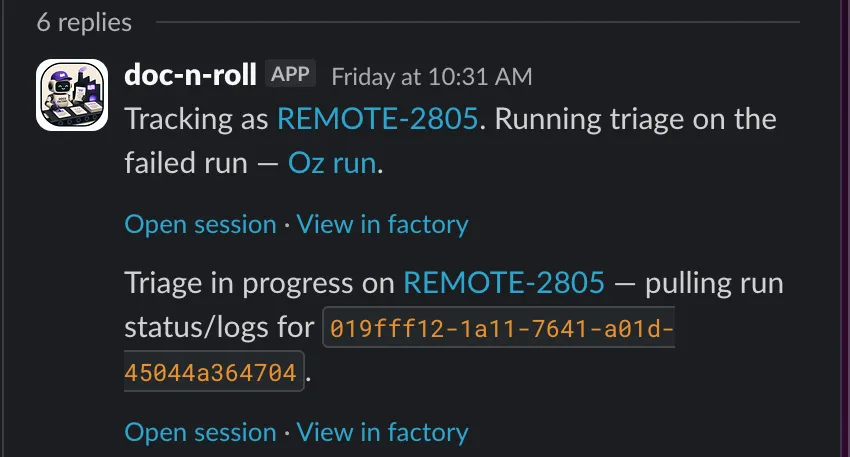
The factory’s Slack app posting progress updates in the thread where work started.
For an overview of the factory’s work items, open the app’s **Home** tab in Slack. It groups them by stage (Triage, Planning, Building, Reviewing, Complete, and Cancelled), offers stage and date filters, and links each work item back to its Slack thread, factory run, issue, or pull request when available.
Work that starts in Slack still ends at a pull request for a person to review — see [how Warp Factories work](/factories/how-factories-work/).
## Who can start work
[Section titled “Who can start work”](#who-can-start-work)
To start work with a mention or direct message, your Slack account must be linked to an active member of the factory’s Warp team. If it isn’t, the app prompts you to connect an account instead of starting work.
Work started by an automation runs as the factory agent you chose for it, not as whoever triggered it.
## Troubleshooting and reconnection
[Section titled “Troubleshooting and reconnection”](#troubleshooting-and-reconnection)
* **The app doesn’t acknowledge a request** - Confirm Slack is connected for that factory, that you mentioned the right factory’s app, and that the app is in the channel.
* **A channel is missing from an automation** - Invite the app to that channel, then reload the **Conversations** picker.
* **Installation is pending** - Ask a Slack workspace administrator to approve the app, then finish the installation.
* **Two runs start for one mention** - Remove or narrow overlapping app-mention and channel-message triggers.
To disconnect Slack, either delete the factory — which removes its Slack app along with it — or [remove the app from your Slack workspace](https://slack.com/help/articles/360003125231-Remove-apps-and-custom-integrations-from-your-workspace), which stops new Slack requests reaching that factory. To reconnect afterward, click **Add to Slack** in factory setup again.
To route work into the factory from other tools, see [Connect your factory](/factories/connect-your-factory/).
## Privacy
[Section titled “Privacy”](#privacy)
The factory’s app reads messages only where it’s mentioned, directly messaged, or subscribed by an automation you configured. Message content and supported attachments are used to run the factory’s work, and your Slack profile email is used to map you to your Warp account. Data is handled per the [Warp Privacy Policy](https://www.warp.dev/privacy).
# Connect Microsoft Teams to your factory
Canonical page: [/factories/integrations/teams/](https://docs.warp.dev/factories/integrations/teams/)
> Connect Microsoft Teams to your factory so mentions in standard and shared channels start work and results post back in the same thread.
Connect a factory to Microsoft Teams so your team can send work from channel conversations. Mention the Warp app in a configured standard or shared channel, and the factory replies in the same thread.
## Who does each step
[Section titled “Who does each step”](#who-does-each-step)
* **Warp workspace admin** - Makes Microsoft Teams available and connects installed teams to the Warp workspace.
* **Microsoft Teams admin** - Uploads and approves the Warp custom app in the Teams admin center.
* **Factory editor** - Selects the connected teams and channels for a factory and manages its automations.
* **End user** - Mentions **@Warp** to start work.
Caution
The integration supports standard and shared channels. Private channels and direct messages are not supported.
## Set up Microsoft Teams
[Section titled “Set up Microsoft Teams”](#set-up-microsoft-teams)
1. **Enable Microsoft Teams for the Warp workspace.** A workspace admin opens the top-level **Integrations** page in the [Warp Factories web app](https://platform.warp.dev). If **Microsoft Teams** doesn’t appear, [contact sales](https://www.warp.dev/contact-sales).
2. **Download the Warp Teams app.** On the **Microsoft Teams** integration, click **Connect**, sign in with Microsoft when prompted, then click **Download Warp app package**. The `warp-microsoft-teams-app.zip` file contains the app manifest and icons, with no executable files.
3. **Upload and approve the app.** A Microsoft Teams admin opens the [Teams admin center](https://admin.teams.microsoft.com), goes to **Teams apps** > **Manage apps**, and clicks **Upload new app**, uploads the ZIP, and approves it. Warp then appears under **Apps** > **Built for your org** in Teams.
4. **Add Warp to each team.** In Microsoft Teams, open **Apps** > **Built for your org** > **Warp**, then click **Add** for every team the factory should use.
5. **Connect the installed teams to the Warp workspace.** Back on the top-level **Integrations** page in the Warp Factories web app, the workspace admin selects the new teams and clicks **Enable**. If a workspace admin selects a pending team while configuring a factory, Warp performs this connection automatically.
6. **Select teams and channels for the factory.** While creating the factory, or from the factory’s **Settings**, choose **Microsoft Teams**, select the connected teams, and select at least one standard channel in each team. Click **Enable** or finish factory setup.
Warp creates an enabled **teams-app-mentions** automation for the teams and channels selected in the last step.
## Test the connection
[Section titled “Test the connection”](#test-the-connection)
1. In one of the selected standard channels, mention **@Warp** with a small request.
2. If Warp prompts you to link accounts, follow the private sign-in link. The Microsoft account must map to an active member of the factory’s Warp workspace. Then send the mention again.
3. Confirm that Warp replies in the same thread and that a work item appears in the factory [dashboard](/factories/factory-dashboard/).
## Start and continue work
[Section titled “Start and continue work”](#start-and-continue-work)
* **Start work** - Mention **@Warp** in a configured channel or thread. The factory includes supported attachments and replies in the same thread. Unsupported attachments don’t block the request text.
* **Continue work** - Reply in a thread that already has a factory work item. When responses to thread replies are enabled, eligible replies continue that work without another mention.
* **Use shared channels** - New root messages in shared channels still require an explicit **@Warp** mention. See the [shared-channel rules](#use-shared-channels).
* **Review results** - Follow progress and the final response in Teams. For code-change work, the factory can also open a pull request. Other workflows can return results directly in the thread.
Automation-started work runs as the factory agent selected in that automation. To manage your account link, mention **@Warp** with `sign in`, `sign out`, or `help` in a channel where the app is installed. For `sign in`, follow the private link, then send your request again. `sign out` unlinks your account from every factory in that Microsoft organization.
## Choose what starts work
[Section titled “Choose what starts work”](#choose-what-starts-work)
Connect Microsoft Teams in the UI, then edit the seeded **teams-app-mentions** automation. Its **App mentioned** trigger starts work only when someone mentions **@Warp**, the default for general-purpose channels.
Use **Message posted in channel** when every matching message in a dedicated standard channel should start work without a mention. In the automation editor, choose exactly one team and at least one standard channel. You can narrow either event with keywords; definition files can also filter by author.
An app mention is also a posted channel message. If both triggers target the same channel, one mention can start two runs. Narrow or remove one trigger to prevent duplicates.
## Use shared channels
[Section titled “Use shared channels”](#use-shared-channels)
A shared channel belongs to an owning Teams team in one Microsoft 365 organization. These rules apply:
* **Install location** - Add the Warp app to the team that owns the shared channel, then connect that installation to the Warp workspace.
* **Eligible users** - Only people in the installation’s Microsoft 365 organization with a Microsoft account linked to an active Warp workspace member can start or continue work. Guests and people from other organizations receive a private notice.
* **New work** - A new root message must mention **@Warp**.
* **Thread replies** - Eligible replies can continue an existing factory work item when responses to thread replies are enabled.
* **History** - An agent run can read only its originating shared-channel thread. Warp checks the originating sender’s current Teams account binding before reading it.
The UI channel picker lists standard channels only. To use a shared channel, add its channel ID in the factory definition as described in [Configure Microsoft Teams as code](#configure-microsoft-teams-as-code).
## What agents can do in Teams
[Section titled “What agents can do in Teams”](#what-agents-can-do-in-teams)
Connecting Microsoft Teams gives factory agents Warp-managed Teams tools. An agent can:
* Read a standard-channel thread or the shared-channel thread that started its run.
* Reply in a thread.
* Post a new top-level channel message.
* Resolve a Teams member.
These tools are separate from [configured MCP servers](/platform/mcp/). They cannot list channels, read private channels, send direct messages, add reactions, upload files, or read other shared-channel threads.
## Configure Microsoft Teams as code
[Section titled “Configure Microsoft Teams as code”](#configure-microsoft-teams-as-code)
Prefer the UI setup above, then edit the seeded **teams-app-mentions** automation. The seeded file already contains the correct team and channel IDs.
factory.yaml
```yaml
integrations:
- type: microsoft-teams
microsoft-teams:
autoRespondToThreadReplies: false
```
Omit `autoRespondToThreadReplies`, or set it to `true`, for the default-on behavior (eligible plain replies in an existing factory thread can continue work without another mention).
automations/teams-app-mentions/automation.md
```markdown
---
enabled: true
agent: foreman
triggers:
- provider: teams
event: app_mention
filter:
team_ids: [MICROSOFT_GRAPH_TEAM_UUID]
channel_ids: [19:example@thread.tacv2]
---
Triage the Teams request and continue in the same thread.
```
The two events have these definition-file values:
* **App mentioned** - `app_mention`
* **Message posted in channel** - `message_posted`
Each trigger requires one Microsoft Graph team UUID in `team_ids` and one or more Bot Framework channel conversation IDs in `channel_ids`. Channel IDs use the `19:…@thread.tacv2` form. These filters are inclusion lists only.
For UI-selected teams and standard channels, copy these values from the seeded automation. You can also read them from the factory Microsoft Teams list-teams and list-channels API response fields named `id`. For a shared channel, copy its channel conversation ID from the Teams link or Microsoft Graph, then add it to `channel_ids`.
Optional `keywords` and `user_ids` filters narrow matching by message content and author.
See the [factory definition syntax](/factories/factory-as-code/#integrations) for integration settings, triggers, and filter shapes.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
* **Microsoft Teams is missing in Warp** - Ask a workspace admin to confirm the integration is enabled. If it isn’t available, [contact sales](https://www.warp.dev/contact-sales).
* **An installed team is missing in Warp** - Confirm the app is approved, then click **Add** for that team from **Apps** > **Built for your org** in Teams. A Warp workspace admin must then select the team on the top-level **Integrations** page to connect it to the workspace.
* **Warp says, “This Microsoft Teams channel isn’t connected to a Warp Factory. Connect this team to a Factory, then mention this bot again.”** - Ask a Warp workspace admin to connect the team on the top-level **Integrations** page, then mention **@Warp** again.
* **Warp doesn’t acknowledge a mention** - Confirm the team and channel are selected, mention **@Warp**, and follow any private account-linking prompt. For a shared channel, check the [shared-channel rules](#use-shared-channels).
* **A channel is missing from the picker** - The picker lists standard channels only. Add a shared channel through the [factory definition](#configure-microsoft-teams-as-code).
* **One mention starts two runs** - Narrow or remove overlapping **App mentioned** and **Message posted in channel** triggers.
* **An agent can’t post to Teams** - Confirm the factory still includes the Microsoft Teams integration and that the app remains installed in the selected team.
### Disconnect Microsoft Teams
[Section titled “Disconnect Microsoft Teams”](#disconnect-microsoft-teams)
Remove Microsoft Teams from the factory’s **Settings** or definition to stop that factory from using the integration. A workspace admin can remove Microsoft Teams from the top-level **Integrations** page to disconnect the Teams installations from every factory in the workspace. Uninstalling the Warp app from a Teams team stops new activity from that team.
## Privacy
[Section titled “Privacy”](#privacy)
The factory’s app uses message content and supported attachments from the channels you configure, and from threads it continues there, to run factory work. Linking your Microsoft account maps you to your Warp account. See the [Warp Privacy Policy](https://www.warp.dev/privacy).
## Related pages
[Section titled “Related pages”](#related-pages)
* [**Connect your factory**](/factories/connect-your-factory/) - Choose the sources that route work into the factory.
* [**Factory automations**](/factories/automations/) - Edit trigger filters and avoid overlapping Teams triggers.
* [**Factory definition**](/factories/factory-as-code/) - Declare `microsoft-teams` and `teams` triggers as code.
* [**Slack**](/factories/integrations/slack/) - The other chat intake path for factories.
# Measure and improve a factory
Canonical page: [/factories/measure-and-improve/](https://docs.warp.dev/factories/measure-and-improve/)
> Read factory activity and cost metrics, then find where to configure Scorers, Self-improvement, and Benchmarks.
Warp Factories tracks what your factory produces and how well it performs, so you can spot a problem, test a fix, and decide whether to keep it.
| Feature | What it tells you |
| ----------------- | ------------------------------------------------------------------------ |
| Dashboard metrics | How much work the factory produced, and what it cost. |
| Scorers | Whether completed runs meet criteria you define. |
| Benchmarks | How different configurations perform on the same tasks. |
| Self-improvement | Which repeated failures get investigated and turned into follow-up work. |
## Read metrics on the Dashboard page
[Section titled “Read metrics on the Dashboard page”](#read-metrics-on-the-dashboard-page)
The **Dashboard** page shows activity, cost, autonomy, and evaluation results:
| Metric | What it shows |
| ------------------------ | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Total runs** | All agent runs, with breakdowns by agent type, status, source, model, and more. |
| **PRs opened** | Pull requests created from factory work, counted once, in the period they were first observed. |
| **PRs merged** | Of the PRs opened in a period, how many later merged. Opened and merged draw from different data sources, so a period’s merged count can occasionally read higher than its opened count for that period. |
| **Autonomy** | The share of the factory’s merged PRs that needed no human code push before merging. Opening the PR counts as a push, so a human-authored PR that a factory run later revised doesn’t count as autonomous. |
| **PR cycle time** | The median time the factory’s merged PRs took from run kickoff through PR, first review, and merge, with a median for each stage. |
| **Cost per PR** | The median cost of PRs opened in the range, split evenly across a run’s PRs when one run produces more than one. View it broken down by cost component or by PR size (S/M/L/XL, split at 100/500/1,000 changed lines). |
| **Most expensive PRs** | The highest-cost pull requests. |
| **Scorer cards** | Results from your Scorers. |
| **Self-improvement PRs** | The three newest Self-improvement pull requests, regardless of the selected date range. |
**Cost per PR** is an estimate, not a billing figure: it counts recorded credits and can undercount actual usage.
Caution
**PRs merged**, **Autonomy**, **PR cycle time**, and the detail in **Most expensive PRs** require a connected code host - the GitHub App, or the GitLab webhook Warp installs when you [connect GitLab](/factories/integrations/gitlab/) - and only cover activity from after you connect it. A PR’s cost, creator, source, and requested model come from the run itself, so those still show without that connection.
Use the **Dashboard** page to pick which runs to investigate, not to conclude what caused a change. **Total runs** includes evaluation, benchmark, and Self-improvement runs, so a higher run count with a flat PR count could mean harder tasks, retries, or measurement activity.
## Configure Scorers
[Section titled “Configure Scorers”](#configure-scorers)
A **Scorer** uses an LLM judge to classify completed runs against criteria you write — for example, “did the agent run the tests before opening a PR?” See [Configuring Scorers](/factories/measure-and-improve/scorers/) for its fields and how automatic and on-demand scoring work.
## Compare configurations with benchmarks
[Section titled “Compare configurations with benchmarks”](#compare-configurations-with-benchmarks)
A benchmark compares model and runner configurations for a single agent on the same fixed tasks. Use it to test a configuration change before you apply it to production. See [benchmarking factory agent configurations](/factories/benchmarks/) for the workflow.
## Configure and review Self-improvement
[Section titled “Configure and review Self-improvement”](#configure-and-review-self-improvement)
**Self-improvement** turns a Scorer’s repeated failures into follow-up pull requests, against application code or the factory’s own definition. See [Configuring and reviewing Self-improvement](/factories/measure-and-improve/self-improvement/) for how to turn it on and review its pull requests.
## Run a practical improvement loop
[Section titled “Run a practical improvement loop”](#run-a-practical-improvement-loop)
Change one measurable thing at a time:
```
flowchart LR
Define[Define a Scorer] --> Baseline[Collect a baseline]
Baseline --> Inspect[Inspect failures]
Inspect --> Benchmark[Benchmark a candidate]
Benchmark --> Adopt[Review and adopt]
Adopt --> Monitor[Keep monitoring]
Monitor --> Inspect
Inspect -.->|Repeated failures| Improve[Self-improvement]
Improve -.-> Adopt
```
1. **Define a Scorer.** Pick one agent and one failure mode you can observe. Write the judge instructions and classifications, then score a few runs manually and compare the judge’s results against your own review.
2. **Collect a baseline.** Let automatic scoring run until results reflect normal work. Record the Scorer settings, date range, and relevant costs.
3. **Inspect failures.** Read the judge’s reasoning and the underlying runs. Look for causes like missing context, unclear instructions, or missing tools. Turn on Self-improvement when the same failure keeps repeating.
4. **Benchmark a candidate.** Compare configurations of that agent on the same tasks, with enough repetitions to trust the difference.
5. **Review and adopt.** If the evidence supports the change, make it. Review Self-improvement pull requests with the same standards as human-authored ones.
6. **Keep monitoring.** Leave the Scorer active and compare new results against your baseline. Revise the Scorer, or set its sample rate to 0, when its criteria no longer match what your team needs.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Configuring Scorers](/factories/measure-and-improve/scorers/) - What a Scorer is, its fields, and how it runs.
* [Configuring and reviewing Self-improvement](/factories/measure-and-improve/self-improvement/) - Turn on Self-improvement and review its pull requests.
* [Benchmarking factory agent configurations](/factories/benchmarks/) - Compare model and runner configurations on the same tasks.
* [Definitions as code](/factories/factory-as-code/) - Record an adopted change so your team can review the factory configuration.
# Configuring Scorers
Canonical page: [/factories/measure-and-improve/scorers/](https://docs.warp.dev/factories/measure-and-improve/scorers/)
> Configure an LLM-based evaluation that checks completed factory runs from selected agents against criteria you define.
A **Scorer** is an LLM-based evaluation, or eval, that checks whether completed runs from selected agents meet criteria you define. For example, it can check, “Did the agent run the tests before opening a pull request?” A Scorer assigns a classification, not a numeric grade, so keep each one focused on a question its failures can point back to. Create Scorers on the factory dashboard’s **Scorers** page, which also holds each Scorer’s results. For Scorers defined as files in a factory definition, see the [`scorers/<name>/scorer.md` syntax](/factories/factory-as-code/#scorersnamescorermd) and the two scorers in [`02-sdlc-issue-to-pr`](https://github.com/warpdotdev/warp-factory-examples/tree/main/examples/02-sdlc-issue-to-pr) in the [warp-factory-examples](https://github.com/warpdotdev/warp-factory-examples) repository.
Configure these fields:
* **Agent(s) to evaluate** - The agents this Scorer applies to. Select at least one.
* **Judge instructions** - The criteria the judge checks for.
* **Judge model** - The model that acts as the judge.
* **Classifications** - The labels the judge can assign, each with a score.
* **Pass threshold** - The score a run needs to pass.
* **Sample rate** - The percentage of completed runs from selected agents to evaluate. For example, a 10% sample rate evaluates about one in ten runs.
With a sample rate above 0%, the Scorer automatically evaluates sampled runs after they complete and records a classification, score, and reasoning.
You can also score any single run on demand, which is useful for testing new judge instructions before raising the sample rate. Scoring a run again replaces its previous result from that Scorer.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Measure and improve a factory](/factories/measure-and-improve/) - Read dashboard metrics and run a practical improvement loop.
* [Configuring and reviewing Self-improvement](/factories/measure-and-improve/self-improvement/) - Turn repeated Scorer failures into follow-up pull requests.
* [Benchmarking factory agent configurations](/factories/benchmarks/) - Compare model and runner configurations on the same tasks.
# Configuring and reviewing Self-improvement
Canonical page: [/factories/measure-and-improve/self-improvement/](https://docs.warp.dev/factories/measure-and-improve/self-improvement/)
> Turn on Self-improvement for a Scorer to turn its repeated failures into follow-up pull requests you review.
Turn on **Self-improvement** for each Scorer whose failures you want investigated automatically. A failure is a score below the Scorer’s pass threshold. The scheduled check starts a Self-improvement run after an agent has 25 unreviewed failures, or when its oldest unreviewed failure is seven days old. It groups the failures for each agent into a follow-up run that proposes a fix.
To run the check without waiting for the scheduled threshold, click **Run now** on the factory dashboard’s **Self-improvement** page. An ad hoc run can include an agent with one unreviewed failure. You cannot choose which agents or failures it processes.
A follow-up run can propose changes to application code. It can also improve the factory itself: when you manage your factory as [definitions as code](/factories/factory-as-code/), its prompts, skills, and configuration are version-controlled files, so a follow-up run can open a pull request against the factory definition the same way it would against application code. Nothing is adopted without your review.
The factory dashboard’s **Self-improvement** page lists the pull requests these follow-up runs open. Each pull request includes a **Regressions addressed** section that links the failing runs and Scorer results behind it, so you can trace the change back to its evidence.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Measure and improve a factory](/factories/measure-and-improve/) - Read dashboard metrics and run a practical improvement loop.
* [Configuring Scorers](/factories/measure-and-improve/scorers/) - Define the criteria whose failures Self-improvement investigates.
* [Benchmarking factory agent configurations](/factories/benchmarks/) - Compare model and runner configurations on the same tasks.
# Warp Factories quickstart
Canonical page: [/factories/quickstart/](https://docs.warp.dev/factories/quickstart/)
> Set up a factory, connect your repositories, and take your first work item from prompt to pull request in about 10 minutes.
Note
Warp Factories is in **Early Access** and available to a limited set of teams. [Request access](https://www.warp.dev/factories/request-access) to use it with your team.
Create a factory and take one small work item from prompt to pull request in about 10 minutes. This quickstart is for teams that already have Warp Factories access and know which repositories they want the factory to use.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **Warp Factories access** - [Request Early Access](https://www.warp.dev/factories/request-access) for your team.
* **A Warp team with credits** - The team’s [credits](/support-and-community/plans-and-billing/platform-credits/) are consumed by factory agents.
* **Repository access** - Authorize GitHub, GitLab, or Azure DevOps during setup. Restricted organizations need owner approval. Azure DevOps also requires [one-time administrator approval](/factories/integrations/azure-devops/#requirements).
## Set up your factory
[Section titled “Set up your factory”](#set-up-your-factory)
*About 5 minutes*
Note
For GitHub and GitLab repositories, an agent connected to [Factory MCP](/factories/factory-mcp/#set-up-with-your-coding-agent) can run this whole setup. Use the web setup wizard for Azure DevOps. If the wizard is still open when the agent finishes, refresh the page to see the new factory.
1. Sign in to the [Warp Factories web app](https://platform.warp.dev). Next to **Factories**, click **+**.
The factory setup control in the sidebar.
2. Under **Connect your code hosts**, connect GitHub, GitLab, or Azure DevOps. Choose the GitHub organization, GitLab group, or Azure DevOps organization and project to connect.
To use another code forge, select **No repo**, finish creating the factory, then [configure repository access from the default runner](/factories/code-forges/other-code-forges/).

Connected GitHub organizations available during setup.
3. On **Select your repos**, select one or two repositories that ship together, then click **Add repos**. See [sizing a factory](/factories/#sizing-a-factory) before adding a repository already covered by another factory.

The repository selector for factory setup.
4. Name the factory. This also sets its [**Foreman name**](/factories/factory-agents/#foreman-name), the handle your team @-mentions in Slack and Linear.

Identity settings for the factory and foreman.
5. Choose which agents the foreman can dispatch. Leave **Implement** enabled so this quickstart ends in a pull request. See [factory agents](/factories/factory-agents/) for details.

Default factory agents enabled during setup.
6. Optionally, connect Slack and an issue tracker. You can add either later from [connect your factory](/factories/connect-your-factory/).
Warp creates the factory and opens its [dashboard](/factories/factory-dashboard/).
## Send your first work item
[Section titled “Send your first work item”](#send-your-first-work-item)
*About 5 minutes*
Send work from Slack or an issue tracker. If you skipped integrations, start a run from the **Runs** page of the factory’s [dashboard](/factories/factory-dashboard/).
1. Describe one small, verifiable change and send it:
Example first request
```text
Add a "Local development" section to README.md that summarizes the setup
steps from CONTRIBUTING.md. Keep the change to that one file, run the
repo's lint check, and open a pull request.
```
2. The foreman dispatches the agents needed for the request and posts progress where it started. Follow the foreman and child runs on the factory’s [Runs page](/factories/factory-dashboard/#inspect-runs). Requests for input also appear in your [inbox](/factories/factory-inbox/).
If you connected Slack, you can follow along there instead:

A factory Slack thread with live progress.
3. When the Implement agent finishes, review and merge the linked pull request as you would any other.
## Next steps
[Section titled “Next steps”](#next-steps)
* [**Connect your factory**](/factories/connect-your-factory/) - Configure intake sources.
* [**How Warp Factories work**](/factories/how-factories-work/) - Understand the work-item lifecycle.
* [**Troubleshooting Warp Factories**](/factories/troubleshooting/) - Fix common setup and run issues.
# Runners for Warp Factories
Canonical page: [/factories/runners/](https://docs.warp.dev/factories/runners/)
> Runners define the OS, architecture, instance size, and sandbox image for cloud agent runs, including work from Warp Factories.
Runners define the compute a [cloud agent](/platform/) runs on: the operating system, CPU architecture, instance size, and sandbox image used to execute a run. Factory agents select runners through the [factory definition](/factories/factory-as-code/) or the [factory dashboard](/factories/factory-dashboard/).
A runner is a reusable compute configuration. Where an [environment](/platform/environments/) defines *what* an agent works on (the repos, setup commands, and toolchain), a runner defines *where and on what hardware* that work executes. This lets any cloud-agent workflow use different machine shapes for different workloads.
## Configure runners for a factory
[Section titled “Configure runners for a factory”](#configure-runners-for-a-factory)
Set a factory’s default runner in `agentDefaults.runner`, then override it per agent or automation when the work needs different compute. For file-managed factories, edit `runners/*.yaml` in the factory definition. For Warp-managed factories, edit runner files in the factory dashboard.
Note
Most runs don’t need a custom runner. Every environment has a default runner, and Warp picks a sensible default shape when you don’t specify one. Create a runner when you need a specific OS, architecture, instance size, or sandbox image.
## Key features
[Section titled “Key features”](#key-features)
What runners give you:
* **Reusable compute configs** – Define an OS, architecture, instance size, and sandbox image once, then reuse the runner across cloud agent runs and orchestration without repeating the configuration.
* **Right-sized hardware** – Choose the number of vCPUs and amount of memory a run needs, so lightweight tasks stay cheap and heavy builds get enough resources.
* **Flexible OS targets** – Run agents on Linux or macOS.
* **Independent of environments** – Override an environment’s default runner per run without changing the environment itself.
## How runners fit into cloud agent runs
[Section titled “How runners fit into cloud agent runs”](#how-runners-fit-into-cloud-agent-runs)
A runner is the compute layer for a cloud agent run. When a run starts, Warp provisions a sandbox on the runner’s shape, then prepares the workspace defined by the environment (cloning repos and executing setup commands) before the agent begins.
* **Environment** – Defines the workspace: Docker image, repositories, and setup commands. See [Environments](/platform/environments/).
* **Runner** – Defines the compute: OS, architecture, instance shape (vCPUs and memory), and sandbox image.
* **Host** – Determines where execution happens (Warp-hosted or [self-hosted](/factories/self-hosting/) infrastructure).
Each environment has a default runner. Specifying a runner for a run overrides that default for that run only.
## Operating systems
[Section titled “Operating systems”](#operating-systems)
* Linux
Linux runners execute the agent in a fresh Docker container. Warp uses the Docker image you select to provide the agent’s base filesystem and toolchains.
Warp-hosted Linux runners support any public x86-64 or aarch64 image. By default, runners use [`warpdotdev/dev-base:latest`](https://hub.docker.com/r/warpdotdev/dev-base). Linux supports any combination of CPU and memory as long as both are a power of two and within your plan’s maximum resource limit.
Warp-hosted Linux runners can also run Docker containers and KVM-based virtual machines, such as the Android emulator.
* macOS
macOS runners execute the agent in a fresh VM on Apple Silicon. You can choose from macOS 14, 15, 26, or 27. If not specified, Warp uses the current macOS release.
The VM has Xcode and standard system tools installed, along with simulators for iOS, watchOS, and tvOS. Use setup commands to install additional dependencies. Downloads from Homebrew and popular language package managers are cached automatically.
The following resource configurations are supported:
* 4 vCPUs, 7 GB memory
* 6 vCPUs, 14 GB memory
* 8 vCPUs, 14 GB memory
* 12 vCPUs, 28 GB memory
* 12 vCPUs, 56 GB memory
## Managing runners with the legacy CLI
[Section titled “Managing runners with the legacy CLI”](#managing-runners-with-the-legacy-cli)
The legacy [Oz CLI](/agents/cli/oz-cli/) also supports creating, listing, updating, and deleting reusable runners for standalone cloud-agent workflows.
### Create a runner
[Section titled “Create a runner”](#create-a-runner)
Create a runner with a name and the compute configuration you need.
```sh
oz runner create \
--name <name> \
--os linux \
--docker-image <image> \
--vcpus 4 \
--memory-gb 8 \
--setup-command "<command>" \
--description "Optional description"
```
Key flags:
* `--name` (`-n`) — human-readable label for the runner (required).
* `--description` (`-d`) — optional description (max 240 characters).
* `--os` — target operating system, `linux` (default) or `macos`.
* `--arch` — CPU architecture: `auto` (default), `x86-64`, or `aarch64`. `auto` uses the OS default (x86-64 on Linux, aarch64 on macOS).
* `--docker-image` — Docker image reference for the sandbox. Linux only.
* `--macos-version` — macOS version for the sandbox: `14`, `15`, `26`, or `27`. macOS only.
* `--vcpus` — number of vCPUs for the instance shape. Must be set together with `--memory-gb`.
* `--memory-gb` — memory in GB for the instance shape. Must be set together with `--vcpus`.
* `--setup-command` (`-c`) — command to run when initializing the sandbox. Repeatable.
* `--team` / `--personal` — create the runner at the team level or private to your account.
Caution
OS-specific options must match `--os`. Use `--docker-image` only with `--os linux`, and `--macos-version` only with `--os macos`.
### List runners
[Section titled “List runners”](#list-runners)
```sh
oz runner list
```
Add `--sort-by name` or `--sort-by last-updated` to order the results.
### Update a runner
[Section titled “Update a runner”](#update-a-runner)
Change a runner’s name, description, compute shape, or sandbox image without recreating it. Identify the runner by its UID, or by `--name` when you don’t have the UID.
```sh
# Update by UID
oz runner update <UID> --vcpus 8 --memory-gb 16
# Rename a runner (UID identifies it, --name sets the new name)
oz runner update <UID> --name "new name"
# Update by name when you don't have the UID
oz runner update --name <name> --docker-image node:22
```
When updating by UID, `--vcpus` and `--memory-gb` can be set independently—the value you don’t pass is preserved.
### Delete a runner
[Section titled “Delete a runner”](#delete-a-runner)
```sh
oz runner delete <UID>
```
Add `--force` to skip the confirmation prompt.
## Using a runner for a run
[Section titled “Using a runner for a run”](#using-a-runner-for-a-run)
Pass a runner’s ID to `oz agent run-cloud` to run a cloud agent on that runner. This overrides the environment’s default runner for that run.
```sh
oz agent run-cloud --runner <ID> --prompt "<task>"
```
You can also select a runner when [running orchestrated agents](/platform/orchestration/multi-agent-runs/), so child agents run on the compute shape their work requires.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Environments](/platform/environments/) – Define the repos, image, and setup commands an agent works with.
* [Managing cloud agents](/platform/managing-cloud-agents/) – Start, monitor, and manage cloud agent runs.
* [Oz CLI reference](/agents/cli/oz-cli/) – Full command-line reference for runners and every other cloud agent command.
# Self-hosting overview
Canonical page: [/factories/self-hosting/](https://docs.warp.dev/factories/self-hosting/)
> Run cloud agents on your infrastructure with a managed worker or invoke the CLI from an orchestrator you control.
Self-hosting runs cloud agent workloads on your infrastructure. You control the compute, network access, runtime secrets, and execution workspaces while Warp tracks each run.
Note
Self-hosting requires an Enterprise plan. To enable it for your team, [contact sales](https://www.warp.dev/contact-sales).
## Managed and unmanaged architectures
[Section titled “Managed and unmanaged architectures”](#managed-and-unmanaged-architectures)
Choose an architecture based on which system starts each run. With the [managed architecture](#managed-architecture), the Automation Platform routes work to `oz-agent-worker`. Use it for runs started from Slack, Linear, schedules, the API, the [Oz web app](https://oz.warp.dev), or `oz agent run-cloud`.
With the [unmanaged architecture](/platform/unmanaged-execution/), your CI system, scheduler, or script invokes `oz agent run` directly. Warp tracks the session but does not start or stop the process.
| Aspect | Managed | Unmanaged |
| ------------- | -------------------------------------------------------------------------- | --------------------------------------------- |
| Run lifecycle | The Automation Platform routes each run to a worker | Your system starts and stops each CLI process |
| Host support | Linux | Linux, macOS, and Windows |
| Execution | Docker container, Kubernetes Job, direct host process, or external runtime | The host environment you provide |
| Triggers | Integrations, schedules, API, web app, and CLI | CI, cron, scripts, and internal schedulers |
Use managed and unmanaged runs together when different workflows need different ownership. For example, route Slack-triggered work to a managed worker and invoke unmanaged agents from CI.
## Choosing an architecture
[Section titled “Choosing an architecture”](#choosing-an-architecture)
Use the [unmanaged architecture](/platform/unmanaged-execution/) when any of these conditions apply:
* Agents must run on macOS or Windows.
* Your system should own both the trigger and process lifecycle.
* You want to add `oz agent run` to an existing CI job or script.
### Choosing a managed backend
[Section titled “Choosing a managed backend”](#choosing-a-managed-backend)
Use the managed architecture when the Automation Platform should accept the trigger and route the run. Then choose a backend:
* **[Docker backend](/factories/self-hosting/managed-docker/)** - Use the default backend when Docker is available. Each task runs in a container.
* **[Kubernetes backend](/factories/self-hosting/managed-kubernetes/)** - Use an existing cluster to run each task as a Kubernetes Job.
* **[Direct backend](/factories/self-hosting/managed-direct/)** - Run tasks on the worker host when a container runtime is unavailable or host access is required.
* **[Command backend](/factories/self-hosting/external-orchestrators/#using-the-command-backend)** - Keep a worker connected and dispatch each task to an external job API, queue, or runtime.
* **[One-shot Direct](/factories/self-hosting/external-orchestrators/#using-one-shot-direct)** - Let an external scheduler allocate a host and start one Direct worker for one task.
## Managed prerequisites
[Section titled “Managed prerequisites”](#managed-prerequisites)
All managed deployments require:
* **Outbound network access** - The worker and agent runtime must reach Warp. You do not need to open inbound ports. See [Security and networking](/platform/execution-security/) for endpoints and data boundaries.
* **A worker ID** - Choose the value used to route runs with `--host`. Multiple long-lived workers can share an ID for load balancing. Use a unique ID for each one-shot Direct job.
* **Worker credentials** - Docker, Kubernetes, Direct, and Command workers can use a [self-hosted worker API key](/agents/cli/oz-cli/api-keys/#creating-a-self-hosted-worker-api-key). Store it in your secret manager and provide it as `WARP_API_KEY` or `--api-key`.
An external orchestrator that creates runs through `oz agent run-cloud` or the API also needs an **agent API key associated with the Default Service Account**. In the [Oz web app settings](https://oz.warp.dev/settings), create an Agent key and choose **Default Service Account**. The same agent key can authenticate the worker when one job both starts the worker and creates the run. Otherwise, give the worker a self-hosted worker key and the run creator an agent key. See [API keys for the Oz CLI](/agents/cli/oz-cli/api-keys/) for the key types and creation flow.
Backend pages list the remaining runtime-specific requirements, such as Docker, Kubernetes, or the Oz CLI binary.
## Managed architecture
[Section titled “Managed architecture”](#managed-architecture)
`oz-agent-worker` connects to the Automation Platform, waits for tasks addressed to its worker ID, and handles each task with the configured backend. Docker, Kubernetes, and Direct run the agent on worker infrastructure. Command hands the task to an external runtime.
Start with the [self-hosting quickstart](/factories/self-hosting/quickstart/) for a Docker worker. For exact flags and YAML fields, use the [self-hosted worker reference](/factories/self-hosting/reference/).
### Routing runs to self-hosted workers
[Section titled “Routing runs to self-hosted workers”](#routing-runs-to-self-hosted-workers)
Set the run’s host to the connected worker’s ID. From the Oz CLI:
```bash
oz agent run-cloud \
--host "my-worker" \
--prompt "Refactor the authentication module"
```
Combine `--host` with other `run-cloud` flags when the run also needs an environment, model, or other configuration.
Use the same worker ID when you create or update schedules and integrations:
```bash
oz schedule create \
--name "daily-cleanup" \
--cron "0 9 * * *" \
--prompt "Remove unused code and open a pull request." \
--host "my-worker"
oz schedule update SCHEDULE_ID --host "my-worker"
oz integration create slack --host "my-worker"
oz integration update linear --host "my-worker"
```
API requests set the same worker ID in `config.worker_host`:
```json
{
"prompt": "Refactor the authentication module",
"config": { "worker_host": "my-worker" }
}
```
In the Oz web app, select the worker from the host options when you create a run, schedule, or integration. See the relevant [trigger](/platform/triggers/) or [Warp Platform API](/factories/api-and-sdk/) documentation for other creation options.
Host selection is independent of the [environment](/platform/environments/). A managed run can use the same environment with Warp-hosted or self-hosted execution; the selected backend determines how the worker applies its image and setup configuration.
## Unmanaged architecture
[Section titled “Unmanaged architecture”](#unmanaged-architecture)
With [unmanaged execution](/platform/unmanaged-execution/), your system invokes `oz agent run` where the work should happen. The agent uses the tools, credentials, and network access available on that host. Warp records the session and lets authorized teammates view or steer it.
Use unmanaged execution for an existing CI pipeline, Kubernetes Job, VM, or developer machine when Warp does not need to route the task.
## Security and observability
[Section titled “Security and observability”](#security-and-observability)
Repository clones and execution workspaces stay on your infrastructure. Agent context and model requests still travel through Warp’s services. See the [self-hosted execution flow](/platform/architecture/#self-hosted-execution-flow) for the architecture and [Security and networking](/platform/execution-security/) for data boundaries, ZDR, and BYOLLM.
View managed and unmanaged runs in the [cloud agent dashboard](https://oz.warp.dev). Managed workers can also export OpenTelemetry metrics; see [Monitoring](/factories/self-hosting/monitoring/).
## Related pages
[Section titled “Related pages”](#related-pages)
* [Self-hosting quickstart](/factories/self-hosting/quickstart/) - Start a managed Docker worker and route a test run.
* [External orchestrators](/factories/self-hosting/external-orchestrators/) - Choose and deploy the Command backend or one-shot Direct.
* [Unmanaged architecture](/platform/unmanaged-execution/) - Invoke `oz agent run` from your own scheduler or CI system.
* [Self-hosted worker reference](/factories/self-hosting/reference/) - Look up worker flags and backend configuration fields.
* [Deployment patterns](/factories/deployment-patterns/) - Compare Warp-hosted, self-hosted, and CLI-only execution.
* [Troubleshooting](/factories/self-hosting/troubleshooting/) - Diagnose worker startup, routing, and task failures.
# Isolating Direct backend tasks with Git worktrees
Canonical page: [/factories/self-hosting/direct-monorepo-worktrees/](https://docs.warp.dev/factories/self-hosting/direct-monorepo-worktrees/)
> Give concurrent Direct backend tasks isolated monorepo checkouts with Git worktrees and setup and teardown hooks.
Use one Git worktree per Direct backend task to share a large monorepo’s Git object store without sharing its branch or working files. This pattern keeps concurrent agents from changing the same checkout while avoiding a full clone for every run.
## How the worktree lifecycle works
[Section titled “How the worktree lifecycle works”](#how-the-worktree-lifecycle-works)
The worker creates a task workspace, then calls the configured hooks:
1. `setup_command` adds a worktree at `OZ_WORKSPACE_ROOT/repo` from a shared base clone.
2. The `oz` CLI starts with `OZ_WORKSPACE_ROOT` as its working directory. `REPO_ROOT` points to the checkout but does not change the working directory.
3. You must modify each task prompt or loaded agent instruction to keep all repository commands and edits under `repo/`.
4. When cleanup is enabled, `teardown_command` removes the worktree and its task branch.
5. When cleanup is enabled, the worker removes the remaining task workspace.
The worktree belongs under the workspace rather than at `OZ_WORKSPACE_ROOT` itself. Before the setup hook runs, the worker has already created the workspace and a temporary environment file inside it, so Git cannot turn that directory directly into a worktree.
Caution
Direct backend tasks share the worker host’s filesystem, network, processes, and Git object store. Worktrees isolate working files and branches, not the host OS. Use dedicated worker hosts and credentials that match the trust level of the repositories.
## Preparing the base clone
[Section titled “Preparing the base clone”](#preparing-the-base-clone)
### Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **A Direct backend worker host** - Install the worker and the Oz CLI as described in [Managed: Direct backend](/factories/self-hosting/managed-direct/).
* **Git credentials for the monorepo** - Use an SSH key in the worker service account’s home directory, a system-level Git credential helper, or a credential helper in the base clone’s repository config. The Direct backend sets `GIT_CONFIG_GLOBAL` to a task-local file, so helpers configured only in the service account’s normal global Git config are unavailable to tasks.
* **A base clone path** - Choose a dedicated path outside `workspace_root`, such as `/srv/warp/repos/product-base`. The worker account needs write access because Git stores worktree metadata in the base clone.
Create a clone without a checked-out working tree:
```bash
export MONOREPO_BASE="/srv/warp/repos/product-base"
install -d -m 0750 "$(dirname "$MONOREPO_BASE")"
git clone --no-checkout \
YOUR_MONOREPO_URL \
"$MONOREPO_BASE"
```
Replace `YOUR_MONOREPO_URL` with the SSH or HTTPS clone URL. Refresh the base clone outside the task lifecycle, for example from a timer:
```bash
git -C /srv/warp/repos/product-base fetch --prune origin
```
Keeping fetches outside the setup hook prevents concurrent tasks from updating the same remote-tracking refs.
## Creating the setup hook
[Section titled “Creating the setup hook”](#creating-the-setup-hook)
Save the following script as `/opt/warp/bin/setup-worktree.sh`:
/opt/warp/bin/setup-worktree.sh
```bash
#!/usr/bin/env bash
set -euo pipefail
: "${MONOREPO_BASE:?Set MONOREPO_BASE on the worker process}"
: "${OZ_WORKSPACE_ROOT:?OZ_WORKSPACE_ROOT is set by the worker}"
: "${OZ_RUN_ID:?OZ_RUN_ID is set by the worker}"
: "${OZ_ENVIRONMENT_FILE:?OZ_ENVIRONMENT_FILE is set by the worker}"
worktree_dir="${OZ_WORKSPACE_ROOT}/repo"
branch="warp-agent/${OZ_RUN_ID}"
git -C "$MONOREPO_BASE" worktree prune
git -C "$MONOREPO_BASE" branch -D "$branch" 2>/dev/null || true
git -C "$MONOREPO_BASE" worktree add \
-b "$branch" \
"$worktree_dir" \
origin/main
{
printf 'REPO_ROOT=%s\n' "$worktree_dir"
printf 'AGENT_BRANCH=%s\n' "$branch"
} >> "$OZ_ENVIRONMENT_FILE"
```
Change `origin/main` if the monorepo uses a different base branch. The script writes `REPO_ROOT` and `AGENT_BRANCH` into the task environment, which lets project scripts and agent instructions locate the checkout. These variables do not change the task’s working directory.
## Creating the teardown hook
[Section titled “Creating the teardown hook”](#creating-the-teardown-hook)
Save the following script as `/opt/warp/bin/teardown-worktree.sh`:
/opt/warp/bin/teardown-worktree.sh
```bash
#!/usr/bin/env bash
set -euo pipefail
: "${MONOREPO_BASE:?Set MONOREPO_BASE on the worker process}"
: "${OZ_WORKSPACE_ROOT:?OZ_WORKSPACE_ROOT is set by the worker}"
: "${OZ_RUN_ID:?OZ_RUN_ID is set by the worker}"
worktree_dir="${OZ_WORKSPACE_ROOT}/repo"
branch="warp-agent/${OZ_RUN_ID}"
git -C "$MONOREPO_BASE" worktree remove --force "$worktree_dir" \
2>/dev/null || true
git -C "$MONOREPO_BASE" branch -D "$branch" \
2>/dev/null || true
git -C "$MONOREPO_BASE" worktree prune
```
Make both scripts executable:
```bash
sudo chmod 0755 \
/opt/warp/bin/setup-worktree.sh \
/opt/warp/bin/teardown-worktree.sh
```
The teardown hook runs before the worker removes the task workspace. Deleting the local task branch does not delete a branch or pull request that the agent pushed to the remote.
## Configuring the worker
[Section titled “Configuring the worker”](#configuring-the-worker)
Point the Direct backend at the hooks and cap concurrency for the host:
worker.yaml
```yaml
worker_id: "monorepo-direct"
max_concurrent_tasks: 4
backend:
direct:
workspace_root: "/var/lib/oz/workspaces"
oz_path: "/usr/local/bin/oz"
setup_command: "/opt/warp/bin/setup-worktree.sh"
teardown_command: "/opt/warp/bin/teardown-worktree.sh"
```
Set `MONOREPO_BASE` on the worker process so both hooks receive it, then start the worker:
```bash
export MONOREPO_BASE="/srv/warp/repos/product-base"
export WARP_API_KEY="YOUR_AGENT_API_KEY"
oz-agent-worker --config-file worker.yaml
```
The Direct backend starts each `oz` CLI process in the task workspace, not the worktree. Require every task prompt or loaded agent instruction to keep repository commands and edits under `repo/`. A task without that instruction may not find the monorepo.
Route a test run to the worker:
```bash
oz agent run-cloud \
--host "monorepo-direct" \
--prompt "Work only in the repo/ directory. Update the authentication package tests and open a pull request."
```
The run starts in its task workspace with the monorepo available at `repo/`, and the prompt directs the agent into that checkout. Export the run ID returned by the CLI, then inspect the shared base clone from the worker host:
```bash
export RUN_ID="YOUR_RUN_ID"
git -C "$MONOREPO_BASE" worktree list
```
During the run, the output includes the isolated checkout and its `warp-agent/$RUN_ID` branch. After a run with cleanup enabled, confirm that the checkout and local task branch are gone:
```bash
git -C "$MONOREPO_BASE" worktree list
git -C "$MONOREPO_BASE" branch --list "warp-agent/$RUN_ID"
```
The worktree list no longer includes the task checkout, and the branch command prints no output. If you start the worker with `--no-cleanup` or set `cleanup: false`, the worker skips the teardown hook and preserves the task workspace. Run `/opt/warp/bin/teardown-worktree.sh` with `MONOREPO_BASE`, `OZ_WORKSPACE_ROOT`, and `OZ_RUN_ID` set for the retained run, then delete the retained workspace directory manually.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
**`fatal: '<workspace>' already exists`**\
The setup hook tried to create a worktree at `OZ_WORKSPACE_ROOT`. Create it in a child directory such as `OZ_WORKSPACE_ROOT/repo`.
**`fatal: invalid reference: origin/main`**\
The base clone has not fetched the branch, or the monorepo uses a different default branch. Fetch the remote and update the final argument to `git worktree add`.
**A stale worktree blocks branch creation**\
Run `git -C "$MONOREPO_BASE" worktree prune`. Keep the prune calls in both lifecycle hooks so interrupted tasks recover automatically.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Managed: Direct backend](/factories/self-hosting/managed-direct/) - Configure Direct backend workspaces, environment variables, and lifecycle hooks.
* [Git worktrees](/code/git-worktrees/) - Learn how Warp treats Git worktree checkouts.
* [Self-hosted worker reference](/factories/self-hosting/reference/#direct-backend-config) - Look up Direct backend configuration fields.
# Running agents with an external orchestrator
Canonical page: [/factories/self-hosting/external-orchestrators/](https://docs.warp.dev/factories/self-hosting/external-orchestrators/)
> Connect an external scheduler to self-hosted agents with one-shot Direct or the Command backend.
Use an existing CI system, Kubernetes controller, or internal scheduler to allocate compute while the Automation Platform routes and tracks each run. Choose one-shot Direct when your scheduler starts a worker for each job. Choose the Command backend when a connected worker should hand tasks to an existing runtime.
## Choosing a pattern
[Section titled “Choosing a pattern”](#choosing-a-pattern)
| Pattern | External orchestrator responsibility | Worker behavior | Use when |
| --------------- | ----------------------------------------------------------------------------- | -------------------------------------------------------------- | ----------------------------------------------------------- |
| One-shot Direct | Allocates a host, starts a worker, and creates a run for its unique worker ID | Runs one accepted task on the allocated host, then exits | Your scheduler creates a VM, pod, or CI runner for each job |
| Command backend | Provides a command or API that accepts a task and owns its compute lifecycle | Stays connected and invokes the dispatch command for each task | Your runtime already exposes a job API, queue, or scheduler |
Both patterns use the managed architecture: Warp accepts triggers and routes runs, while your orchestrator owns compute allocation. If your system should also create and start each agent process without Warp routing, use [unmanaged execution](/platform/unmanaged-execution/).
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
Complete the shared [managed prerequisites](/factories/self-hosting/#managed-prerequisites). The one-shot example below uses one Default Service Account agent key for both the worker and `run-cloud`. When those actions run in different processes, use a self-hosted worker key for the worker and an agent key for the run creator.
Install `oz-agent-worker` from a [published release](https://github.com/warpdotdev/oz-agent-worker/releases). One-shot Direct also requires the Oz CLI on the allocated host. The Command backend worker requires the tools used by your dispatch and cancellation commands.
## Using one-shot Direct
[Section titled “Using one-shot Direct”](#using-one-shot-direct)
Start a Direct worker with `--one-shot` when your scheduler allocates one host per job. One-shot mode accepts one task, forces `max_concurrent_tasks` to `1`, and exits after that task succeeds, fails, or is cancelled. If no task arrives, the worker stays connected until your orchestrator stops it.
Use a unique worker ID for every job so another worker cannot claim the run.
### Configure the completion timeout
[Section titled “Configure the completion timeout”](#configure-the-completion-timeout)
The agent process normally remains available for follow-up prompts for 45 minutes after a conversation completes. Timeout settings use this precedence:
1. The task-level `config.idle_timeout_minutes` value, including defaults applied by the task creator. Runs created directly through the [Agent API](/api) use 10 minutes when this field is omitted.
2. The worker’s `idle_on_complete` setting or `--idle-on-complete` flag when the task reaches the worker without a task-level value. Unlike a direct Agent API request, `oz agent run-cloud` uses the CLI task-creation path, which does not apply the API’s 10-minute default and leaves this value unset.
3. The 45-minute default when neither value is set.
For a job created directly through the Agent API that must exit immediately, set `config.idle_timeout_minutes` to `0`. If the task reaches the worker without this field, start the worker with `--idle-on-complete 0s`. A task-level value overrides `--idle-on-complete 0s`.
### Start the worker and route the run
[Section titled “Start the worker and route the run”](#start-the-worker-and-route-the-run)
Add this script to the job your orchestrator starts. `CI_JOB_ID` must be unique for each job.
run-agent.sh
```bash
#!/usr/bin/env bash
set -euo pipefail
: "${WARP_API_KEY:?Set WARP_API_KEY in the job environment}"
: "${CI_JOB_ID:?Set CI_JOB_ID to a unique job identifier}"
worker_id="external-${CI_JOB_ID}"
oz-agent-worker \
--worker-id "$worker_id" \
--backend direct \
--one-shot \
--idle-on-complete 0s &
worker_pid=$!
trap 'kill "$worker_pid" 2>/dev/null || true' EXIT
oz agent run-cloud \
--host "$worker_id" \
--prompt "Run the test suite, fix failures, and open a pull request."
wait "$worker_pid"
trap - EXIT
```
**Expected outcome:** The run appears in the dashboard, the worker accepts it, and the worker exits when the conversation completes. The run can enter the queue before the worker connects. If no matching worker claims it, Warp eventually fails the run. Use Direct backend [setup and teardown commands](/factories/self-hosting/managed-direct/#setup-and-teardown-commands) to prepare and clean up the allocated host.
## Using the Command backend
[Section titled “Using the Command backend”](#using-the-command-backend)
Use the Command backend when your runtime already owns job creation and cleanup. The worker sends each assigned task to `dispatch_command` as JSON on standard input. Exit code `0` means the runtime durably accepted the task; a nonzero exit or dispatch timeout fails it.
The public [`command-backend` example](https://github.com/warpdotdev/oz-agent-worker/tree/main/examples/command-backend) includes Python dispatch and cancellation scripts for an HTTP runtime. Copy and adapt those scripts, then configure the worker:
worker.yaml
```yaml
worker_id: "external-runtime"
backend:
command:
dispatch_command: "python3 /opt/warp/dispatch.py"
cancel_command: "python3 /opt/warp/cancel.py"
dispatch_timeout: "60s"
environment:
- name: OZ_DISPATCH_URL
value: "https://runtime.internal.example.com/agent-runs"
- name: OZ_CANCEL_URL
value: "https://runtime.internal.example.com/agent-runs/cancel"
- name: OZ_DISPATCH_AUTH_HEADER
```
Supply the runtime credential and Warp API key through your secret manager, then start the worker:
```bash
export OZ_DISPATCH_AUTH_HEADER="Bearer YOUR_RUNTIME_TOKEN"
export WARP_API_KEY="YOUR_SELF_HOSTED_WORKER_API_KEY"
oz-agent-worker --config-file worker.yaml
```
Your dispatch implementation must handle the task payload as follows:
* **Start command** - Run the supplied `base_args` with `env`.
* **Runtime configuration** - Use `docker_image` and `sidecars` to prepare the runtime.
* **Task payload** - Keep it out of logs because it contains task credentials. See the example’s [task payload reference](https://github.com/warpdotdev/oz-agent-worker/tree/main/examples/command-backend#what-the-worker-hands-the-script-stdin) for each field.
* **Shutdown report** - After the CLI exits, run `oz harness-support --run-id RUN_ID report-shutdown` so Warp receives the terminal state. Set `RUN_ID` to the `run_id` field from the dispatch payload.
The worker does not wait for the remote agent to finish. Stopping or restarting the worker does not cancel tasks that the external runtime already accepted. `max_concurrent_tasks` limits concurrent dispatch calls, not agents running in the external runtime. Configure the external runtime’s capacity separately.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Self-hosting overview](/factories/self-hosting/) - Compare managed and unmanaged architectures and review shared prerequisites.
* [Managed: Direct backend](/factories/self-hosting/managed-direct/) - Configure host execution, workspaces, and setup commands.
* [Unmanaged architecture](/platform/unmanaged-execution/) - Invoke `oz agent run` when your orchestrator should own the complete run lifecycle.
* [Self-hosted worker reference](/factories/self-hosting/reference/) - Look up one-shot, timeout, and Command backend configuration fields.
* [Routing runs to self-hosted workers](/factories/self-hosting/#routing-runs-to-self-hosted-workers) - Route runs from supported triggers to a worker ID.
# Managed: Direct backend
Canonical page: [/factories/self-hosting/managed-direct/](https://docs.warp.dev/factories/self-hosting/managed-direct/)
> Run the Automation Platform managed worker with the Direct backend to execute cloud agent tasks directly on the host, without Docker or Kubernetes.
Run the `oz-agent-worker` daemon with the **Direct backend** — tasks execute directly on the worker host without Docker or Kubernetes. The Automation Platform still orchestrates runs end to end (Slack, Linear, schedules, API, `oz agent run-cloud`); the worker just runs the agent in a per-task workspace on its own filesystem.
## When to use the Direct backend
[Section titled “When to use the Direct backend”](#when-to-use-the-direct-backend)
* Neither Docker nor Kubernetes is available on the worker host.
* Tasks need direct access to host resources that are hard to expose through a container.
* You want managed orchestration (triggering from Slack, Linear, schedules, API) without the operational overhead of a container runtime.
Caution
The Direct backend does not provide per-task container isolation. Each task runs in an isolated workspace directory, but shares the host OS and kernel. Evaluate whether this fits your security requirements before using it in production.
***
## How it works
[Section titled “How it works”](#how-it-works)
1. The worker creates a per-task workspace directory under `workspace_root`.
2. If a `setup_command` is configured, it runs before the task with environment variables pointing to the workspace.
3. The `oz` CLI runs the agent task inside the workspace directory.
4. After the task completes, the optional `teardown_command` runs and the workspace is cleaned up.
***
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
Complete the shared [managed prerequisites](/factories/self-hosting/#managed-prerequisites), then prepare:
* **A worker host** - Grant write access to `workspace_root`, which defaults to `/var/lib/oz/workspaces`.
* **The `oz-agent-worker` binary** - Install it on the worker host through [Homebrew or a prebuilt binary](/factories/self-hosting/managed-docker/#install-and-run-the-worker).
* **The Oz CLI** - Install it in `PATH` on the worker host, or set `oz_path` in the config file. See [Installing the CLI](/agents/cli/oz-cli/#installing-the-cli).
***
## Setup
[Section titled “Setup”](#setup)
### 1. Set your API key
[Section titled “1. Set your API key”](#1-set-your-api-key)
Export the self-hosted worker API key so the worker can authenticate to the Automation Platform:
```bash
export WARP_API_KEY="YOUR_API_KEY"
```
### 2. Start the worker with the Direct backend
[Section titled “2. Start the worker with the Direct backend”](#2-start-the-worker-with-the-direct-backend)
Pass `--backend direct`:
```bash
oz-agent-worker --api-key "$WARP_API_KEY" --worker-id "my-worker" --backend direct
```
Or with a [config file](/factories/self-hosting/reference/#config-file):
```yaml
worker_id: "my-worker"
backend:
direct:
workspace_root: "/var/lib/oz/workspaces"
```
**Expected outcome:** The worker connects to the Automation Platform and begins listening for tasks. Each assigned task runs in a freshly-created subdirectory of `workspace_root`.
***
## Workspace model
[Section titled “Workspace model”](#workspace-model)
Each task gets its own directory under `workspace_root`. The default is `/var/lib/oz/workspaces`; override it with the `workspace_root` config option shown above.
After the task completes, the workspace is deleted (unless `--no-cleanup` is set, which keeps the directory around for debugging).
To reuse a large monorepo without sharing one checkout between concurrent tasks, see [Direct backend monorepo worktrees](/factories/self-hosting/direct-monorepo-worktrees/).
Setting `target_dir` makes every task run in one shared directory and disables per-task workspace isolation. Use it only when the worker processes one task at a time.
***
## Setup and teardown commands
[Section titled “Setup and teardown commands”](#setup-and-teardown-commands)
The `setup_command` runs before each task and receives the following environment variables:
* `OZ_WORKSPACE_ROOT` — The workspace directory for the task.
* `OZ_RUN_ID` — The unique task ID.
* `OZ_ENVIRONMENT_FILE` — Path to a file where the setup script can write additional `KEY=VALUE` environment variables to inject into the task.
* `OZ_WORKER_BACKEND` — Always set to `direct`.
The `teardown_command` runs after each task and receives `OZ_WORKSPACE_ROOT`, `OZ_RUN_ID`, and `OZ_WORKER_BACKEND`.
Use the setup command to clone repos, install dependencies, or write task-specific env vars into `OZ_ENVIRONMENT_FILE`. Use the teardown command for cleanup or reporting.
***
## Environment variables for Direct tasks
[Section titled “Environment variables for Direct tasks”](#environment-variables-for-direct-tasks)
Note
The Direct backend starts tasks with a **minimal environment** (only `HOME`, `TMPDIR`, and `PATH` from the host) to avoid leaking sensitive worker credentials like `WARP_API_KEY` into tasks. Add variables explicitly via `environment` in the config file or `-e` flags on the worker CLI.
Config file example:
```yaml
worker_id: "direct-worker"
max_concurrent_tasks: 2
backend:
direct:
workspace_root: "/var/lib/oz/workspaces"
oz_path: "/usr/local/bin/oz"
setup_command: "/opt/scripts/setup.sh"
teardown_command: "/opt/scripts/teardown.sh"
environment:
- name: MY_VAR
value: "hello"
```
***
## Related pages
[Section titled “Related pages”](#related-pages)
* [Self-hosted worker reference](/factories/self-hosting/reference/#direct-backend-config) — Full config schema for the Direct backend.
* [External orchestrators](/factories/self-hosting/external-orchestrators/) — Start one Direct worker per external job or delegate runs through the Command backend.
* [Direct backend monorepo worktrees](/factories/self-hosting/direct-monorepo-worktrees/) — Create and remove one Git worktree per task with setup and teardown hooks.
* [Self-hosting overview](/factories/self-hosting/) — Managed vs unmanaged and the backend decision guide.
* [Routing runs to self-hosted workers](/factories/self-hosting/#routing-runs-to-self-hosted-workers) — How to send tasks to your connected worker from the CLI, schedules, integrations, the API, and the web UI.
* [Security and networking](/platform/execution-security/) — Data boundaries and security considerations for the Direct backend.
* [Troubleshooting](/factories/self-hosting/troubleshooting/#direct-backend) — Common Direct-backend issues.
# Managed: Docker backend
Canonical page: [/factories/self-hosting/managed-docker/](https://docs.warp.dev/factories/self-hosting/managed-docker/)
> Run the Automation Platform managed worker daemon with the Docker backend to execute cloud agent tasks in isolated containers on your infrastructure.
Run the `oz-agent-worker` daemon with the **Docker backend** — the default managed path. Each agent task runs in an isolated Docker container spawned from the worker, with full orchestration by the Automation Platform (Slack, Linear, schedules, API, `oz agent run-cloud`).
## When to use the Docker backend
[Section titled “When to use the Docker backend”](#when-to-use-the-docker-backend)
* You want the simplest managed setup and have Docker available on the worker host.
* You want per-task isolation without running a Kubernetes cluster.
* You’re not already deploying workloads into Kubernetes.
***
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
Complete the shared [managed prerequisites](/factories/self-hosting/#managed-prerequisites), then prepare:
* **A machine to run the worker** - Use a Linux VM, server, or local machine for production. Docker Desktop on macOS or Windows works for testing.
* **Docker** - Install a **linux/amd64** or **linux/arm64** Docker daemon that runs Linux containers. Windows containers are not supported. The worker host can use any OS because Docker Desktop on macOS and Windows runs a compatible Linux VM. Verify the daemon with `docker info`.
* **Task images** - Use a glibc-based image, such as Debian, Ubuntu, or a non-Alpine variant of an official image. Musl-based images such as Alpine Linux are not supported. Add required tools, binaries, scripts, and system packages to the [environment’s custom image](/platform/environments/).
### Install Docker
[Section titled “Install Docker”](#install-docker)
If Docker is not already installed, follow the [official Docker installation guide](https://docs.docker.com/get-docker/) for your platform. Verify Docker is running:
```bash
docker info
```
**Expected outcome:** `docker info` prints daemon details without errors.
***
## Set your API key
[Section titled “Set your API key”](#set-your-api-key)
Export your self-hosted worker API key so the worker can authenticate to the Automation Platform:
```bash
export WARP_API_KEY="YOUR_API_KEY"
```
## Install and run the worker
[Section titled “Install and run the worker”](#install-and-run-the-worker)
The `oz-agent-worker` is open source. See the [oz-agent-worker repository](https://github.com/warpdotdev/oz-agent-worker) for source code, issues, and contribution guidelines.
There are three ways to install and run the worker: as a Docker container, via Homebrew, or as a prebuilt binary from GitHub Releases. Docker is the recommended default.
The worker can be configured entirely via CLI flags, or via a YAML [config file](/factories/self-hosting/reference/#config-file) for more complex setups.
### Option 1: Docker (recommended)
[Section titled “Option 1: Docker (recommended)”](#option-1-docker-recommended)
The worker needs access to the Docker daemon to spawn task containers. Mount the host’s Docker socket into the worker container:
```bash
docker run -v /var/run/docker.sock:/var/run/docker.sock \
-e WARP_API_KEY="$WARP_API_KEY" \
warpdotdev/oz-agent-worker --worker-id "my-worker"
```
**Expected outcome:** The worker connects to the Automation Platform and logs that it’s listening for tasks.
### Option 2: Homebrew
[Section titled “Option 2: Homebrew”](#option-2-homebrew)
Install the worker binary with [Homebrew](https://brew.sh/) on macOS or Linux from the [`warpdotdev/warp` tap](https://github.com/warpdotdev/homebrew-warp):
```bash
brew install warpdotdev/warp/oz-agent-worker
```
Run the binary directly. It uses the same Docker-daemon discovery described in [Docker connectivity](#docker-connectivity) below:
```bash
oz-agent-worker --api-key "$WARP_API_KEY" --worker-id "my-worker"
```
### Option 3: GitHub Releases binary
[Section titled “Option 3: GitHub Releases binary”](#option-3-github-releases-binary)
Download the archive for your platform from the [oz-agent-worker releases page](https://github.com/warpdotdev/oz-agent-worker/releases), extract it, and run the binary. The example below uses Linux amd64; choose the archive that matches your OS and CPU architecture:
```bash
tar -xf oz-agent-worker-linux-amd64.tar.gz
./oz-agent-worker --api-key "$WARP_API_KEY" --worker-id "my-worker"
```
Once started, the worker connects to the Automation Platform, waits for tasks routed to its `--worker-id`, runs each task in an isolated Docker container, and reports status and results back. The worker automatically reconnects if the connection drops.
You can run multiple workers with the same `--worker-id` for redundancy — the Automation Platform distributes tasks across connected workers.
***
## Docker backend configuration
[Section titled “Docker backend configuration”](#docker-backend-configuration)
The worker can take configuration either via CLI flags or via a YAML [config file](/factories/self-hosting/reference/#config-file). CLI flags take precedence over config file values.
**Common CLI flags:**
```bash
docker run -v /var/run/docker.sock:/var/run/docker.sock \
-e WARP_API_KEY="$WARP_API_KEY" \
warpdotdev/oz-agent-worker \
--worker-id "prod-runner-1" \
--log-level debug \
--max-concurrent-tasks 4 \
--idle-on-complete 10m \
-v /opt/shared-cache:/cache:ro \
-e NPM_TOKEN=your_token \
-e GITHUB_TOKEN
```
Caution
When running the worker via Docker, there are two levels of `-e` flags. Docker’s `-e` passes env vars to the **worker container** (e.g., `WARP_API_KEY`). The worker’s `-e` / `--env` flags pass env vars into the **task containers** the worker spawns. Keep these distinct:
```bash
# Docker -e: passes WARP_API_KEY to the worker container
# Worker -e: passes MY_SECRET to task containers
docker run \
-e WARP_API_KEY="$WARP_API_KEY" \
warpdotdev/oz-agent-worker \
--worker-id "my-worker" \
-e MY_SECRET=hunter2
```
**Equivalent config file** (`config.yaml`):
```yaml
worker_id: "prod-runner-1"
log_level: "debug"
max_concurrent_tasks: 4
idle_on_complete: "10m"
backend:
docker:
volumes:
- "/opt/shared-cache:/cache:ro"
environment:
- name: NPM_TOKEN
value: "your_token"
- name: GITHUB_TOKEN # inherits from host environment
```
Pass it with `--config-file config.yaml`. See the [self-hosted worker reference](/factories/self-hosting/reference/) for the full flag and config schema.
***
## Docker connectivity
[Section titled “Docker connectivity”](#docker-connectivity)
The worker uses the standard Docker client discovery mechanism to find the Docker daemon. If the worker runs in Docker, mount relevant config files such as `~/.docker/config.json` into the worker container for Docker context and credential discovery.
1. **`DOCKER_HOST`** environment variable (e.g., `unix:///var/run/docker.sock`, `tcp://localhost:2375`).
2. **Default socket** (`/var/run/docker.sock` on Linux, `~/.docker/run/docker.sock` for rootless Docker).
3. **Docker context** via `DOCKER_CONTEXT` environment variable.
4. **Config file** (`~/.docker/config.json`) for context settings.
Additional Docker environment variables the worker respects:
* `DOCKER_API_VERSION` — Specify Docker API version.
* `DOCKER_CERT_PATH` — Path to TLS certificates.
* `DOCKER_TLS_VERIFY` — Enable TLS verification.
**Example: Connecting to a remote Docker daemon**
```bash
export DOCKER_HOST="tcp://remote-host:2376"
export DOCKER_TLS_VERIFY=1
export DOCKER_CERT_PATH="/path/to/certs"
oz-agent-worker --api-key "$WARP_API_KEY" --worker-id "my-worker"
```
***
## Private Docker registries
[Section titled “Private Docker registries”](#private-docker-registries)
The worker automatically uses credentials from your Docker config (`~/.docker/config.json`) when pulling task images. If your [environments](/platform/environments/) use images from a private registry, authenticate the worker’s host first. Sidecar images, including the `oz` binary and its dependencies, come from public registries and do not require authentication.
```bash
docker login your-registry.example.com
```
When running the worker via Docker, mount the Docker config into the container:
```bash
docker run \
-v /var/run/docker.sock:/var/run/docker.sock \
-v ~/.docker/config.json:/root/.docker/config.json:ro \
-e WARP_API_KEY="$WARP_API_KEY" \
warpdotdev/oz-agent-worker --worker-id "my-worker"
```
***
## Routing runs to this worker
[Section titled “Routing runs to this worker”](#routing-runs-to-this-worker)
Once your Docker worker is connected, route tasks to it with `--host "<your-worker-id>"`. Routing is the same across all managed backends — see [Routing runs to self-hosted workers](/factories/self-hosting/#routing-runs-to-self-hosted-workers) for CLI, scheduled, integration, API, and web UI examples.
***
## Related pages
[Section titled “Related pages”](#related-pages)
* [Self-hosting quickstart](/factories/self-hosting/quickstart/) — \~10-minute path to a running Docker worker.
* [Self-hosted worker reference](/factories/self-hosting/reference/) — Full CLI flag and config file schema.
* [Environments](/platform/environments/) — Define the Docker image, repos, and setup commands for tasks.
* [Security and networking](/platform/execution-security/) — Data boundaries, egress, and Docker socket considerations.
* [Troubleshooting](/factories/self-hosting/troubleshooting/) — Common issues with the Docker backend.
# Managed: Kubernetes backend
Canonical page: [/factories/self-hosting/managed-kubernetes/](https://docs.warp.dev/factories/self-hosting/managed-kubernetes/)
> Deploy the Automation Platform managed worker into a Kubernetes cluster with the included Helm chart. Each agent task runs as a Kubernetes Job in your cluster.
Deploy the `oz-agent-worker` daemon into a Kubernetes cluster with the included Helm chart. Each agent task runs as a Kubernetes Job. The Automation Platform orchestrates runs; your cluster handles compute, scheduling, and policy enforcement.
## When to use the Kubernetes backend
[Section titled “When to use the Kubernetes backend”](#when-to-use-the-kubernetes-backend)
* You already operate a Kubernetes cluster and want agents to run there.
* You need Kubernetes-native scheduling, resource management, or policy enforcement.
* You want to use Kubernetes Secrets, ServiceAccounts, and admission policies to control task behavior.
***
## How it works
[Section titled “How it works”](#how-it-works)
1. The worker connects to the Kubernetes API server (using in-cluster auth by default, or an explicit kubeconfig).
2. On startup, the worker runs a preflight Job using the worker’s `pod_template`.
3. For each assigned task, the worker creates a Kubernetes Job from `pod_template` in the configured namespace. The task’s runner supplies the image and, when configured, the instance shape.
4. The worker monitors the Job and Pod status.
5. After the task completes, the worker removes successful Jobs. Failed Jobs remain available for diagnosis for 24 hours by default.
***
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
Complete the shared [managed prerequisites](/factories/self-hosting/#managed-prerequisites), then prepare:
* **A Kubernetes cluster** - The worker process must reach the API server. The cluster must:
* Allow the task namespace to create Jobs with a **root init container**, unless you enable native image volumes with `kubernetesBackend.useImageVolumes=true`.
* Grant the worker these namespace-scoped permissions: `create`, `get`, `list`, `watch`, `delete` on `jobs`; `get`, `list`, `watch` on `pods`; `get` on `pods/log`; `list` on `events`.
* **[Helm](https://helm.sh/docs/intro/install/)** - Install Helm locally and authenticate `kubectl` against the target cluster.
* **Task images** - Use a glibc-based image, such as Debian, Ubuntu, or a non-Alpine variant of an official image. Musl-based images such as Alpine Linux are not supported. Add required tools, binaries, scripts, and system packages to the [environment’s custom image](/platform/environments/).
***
## Install with the Helm chart
[Section titled “Install with the Helm chart”](#install-with-the-helm-chart)
The `oz-agent-worker` repository includes a namespace-scoped Helm chart at `charts/oz-agent-worker`. This is the recommended way to deploy the worker into a cluster.
### What the chart deploys
[Section titled “What the chart deploys”](#what-the-chart-deploys)
* A long-lived `Deployment` running `oz-agent-worker` with the Kubernetes backend.
* A namespaced `ServiceAccount` for the worker.
* A namespaced `Role` / `RoleBinding` with the minimum permissions needed to manage task Jobs and Pods.
* A `ConfigMap` containing the worker config YAML.
* An optional `Secret` for `WARP_API_KEY` (or a reference to an existing Secret).
The chart does not create CRDs or cluster-scoped RBAC resources.
### 1. Set your API key and namespace
[Section titled “1. Set your API key and namespace”](#1-set-your-api-key-and-namespace)
```bash
export WARP_API_KEY="YOUR_API_KEY"
```
Create the namespace if it doesn’t exist:
```bash
kubectl create namespace warp-oz
```
### 2. Create the API key Secret
[Section titled “2. Create the API key Secret”](#2-create-the-api-key-secret)
If you’re not using an existing Secret, create one with the API key:
```bash
kubectl create secret generic oz-agent-worker \
--from-literal=WARP_API_KEY="$WARP_API_KEY" \
--namespace warp-oz
```
**Expected outcome:** `kubectl get secret -n warp-oz oz-agent-worker` shows the Secret.
### 3. Install the chart
[Section titled “3. Install the chart”](#3-install-the-chart)
Clone the worker repo and install the chart:
```bash
git clone https://github.com/warpdotdev/oz-agent-worker.git
helm install oz-agent-worker ./oz-agent-worker/charts/oz-agent-worker \
--namespace warp-oz \
--set worker.workerId=oz-k8s-worker \
--set image.tag=<version>
```
Caution
Set `image.tag` explicitly to pin the worker image. Check the [oz-agent-worker releases](https://github.com/warpdotdev/oz-agent-worker/releases) for the latest version. Do not rely on `latest`.
**Expected outcome:** `kubectl get pods -n warp-oz` shows the worker Deployment pod as `Running`, and the worker logs include `Successfully connected to server`.
To scale horizontally, deploy multiple Helm releases with distinct worker IDs rather than increasing replicas on a single release.
***
## Key chart values
[Section titled “Key chart values”](#key-chart-values)
**Required:**
* `worker.workerId` — The worker ID (same as `--worker-id`).
* `image.tag` — The worker image tag to deploy.
**Worker configuration:**
* `worker.logLevel` — Log verbosity (`debug`, `info`, `warn`, `error`). Defaults to `info`.
* `worker.cleanup` — Whether to clean up task Jobs after execution. Defaults to `true`.
* `worker.maxConcurrentTasks` — Maximum concurrent tasks. Defaults to `0` (unlimited).
* `worker.idleOnComplete` — Duration to keep the oz process alive after task completion.
* `worker.resources` — Resource requests/limits for the worker Deployment. Defaults to `100m` CPU and `128Mi` memory.
* `worker.livenessProbe` — Liveness probe for the worker Deployment. Defaults to an `exec` probe (`kill -0 1`). Override with a custom probe or set to `null` to disable.
* `worker.terminationGracePeriodSeconds` — Grace period for worker Deployment shutdown. Defaults to `30`.
* `worker.nodeSelector`, `worker.tolerations`, `worker.affinity` — Scheduling constraints for the worker Deployment pod.
**Kubernetes backend:**
* `kubernetesBackend.namespace` — Namespace for task Jobs. Defaults to the release namespace.
* `kubernetesBackend.defaultImage` — Default Docker image for task pods when no [Warp environment](/platform/environments/) has been supplied. Set it when all tasks use the same base image and you don’t need a Warp environment. Leave empty (default) to fall back to `ubuntu:22.04`.
* `kubernetesBackend.imagePullPolicy` — Image pull policy for task pods. Defaults to `IfNotPresent`.
* `kubernetesBackend.useImageVolumes` — Use native Kubernetes image volumes instead of root init containers to materialize sidecars. Defaults to `false`.
* `kubernetesBackend.preflightImage` — Image for the startup preflight Job. Set this if your cluster restricts allowed registries.
* `kubernetesBackend.preflightResources` — CPU and memory requests and limits for preflight containers.
* `kubernetesBackend.sidecarImage` — Internal-registry override for the Warp agent sidecar image.
* `kubernetesBackend.unschedulableTimeout` — How long a pod may remain unschedulable before failing. Defaults to `30s`.
* `kubernetesBackend.setupCommand` — Shell command to run before each task.
* `kubernetesBackend.teardownCommand` — Shell command to run after each task.
* `kubernetesBackend.extraLabels` — Additional labels for task Jobs and Pods.
* `kubernetesBackend.extraAnnotations` — Additional annotations for task Jobs and Pods.
* `kubernetesBackend.activeDeadlineSeconds` — Maximum task Job lifetime. Defaults to eight hours.
* `kubernetesBackend.ttlSecondsAfterFinished` — Retention period for failed Jobs and Jobs orphaned by worker disruption. Defaults to 24 hours when cleanup is enabled.
* `kubernetesBackend.workspaceSizeLimit` — Size limit for workspace `emptyDir` volume.
* `kubernetesBackend.podTemplate` — Raw PodSpec YAML for task Jobs (same as `backend.kubernetes.pod_template` in the [config file](/factories/self-hosting/reference/#config-file)).
**API key Secret:**
* `warp.apiKeySecret.create` — Set to `true` to have the chart create a Secret from `warp.apiKeySecret.value`. Defaults to `false` (expects a pre-existing Secret).
* `warp.apiKeySecret.value` — The API key value to store in the chart-managed Secret. Only used when `warp.apiKeySecret.create` is `true`.
* `warp.apiKeySecret.name` — Name of the Secret containing `WARP_API_KEY`. Defaults to `oz-agent-worker`.
* `warp.apiKeySecret.key` — Key within the Secret. Defaults to `WARP_API_KEY`.
See the [self-hosted worker reference](/factories/self-hosting/reference/#kubernetes-backend-config) for the full config file schema.
***
## Cluster selection
[Section titled “Cluster selection”](#cluster-selection)
Cluster selection follows Kubernetes client config conventions:
* Set `backend.kubernetes.kubeconfig` to use an explicit kubeconfig file.
* If `kubeconfig` is omitted and the worker runs inside a Kubernetes pod, the worker uses in-cluster config automatically.
* Otherwise, the worker falls back to the default kubeconfig loading rules and uses the current context.
`namespace` selects the namespace inside the chosen cluster. It defaults to `default` when omitted.
***
## Pod template
[Section titled “Pod template”](#pod-template)
The `pod_template` field accepts standard Kubernetes PodSpec YAML and is the declarative way to configure task pod scheduling, service accounts, image pull secrets, resources, and environment variables.
When using `pod_template`, define a container named `task` to customize the main task container directly. Otherwise, the worker appends its own `task` container to the PodSpec.
Use `valueFrom.secretKeyRef` to inject Kubernetes Secret values into task container environment variables:
```yaml
pod_template:
serviceAccountName: agent-task-sa
imagePullSecrets:
- name: my-registry-creds
containers:
- name: task
resources:
requests:
cpu: "2"
memory: 4Gi
limits:
memory: 8Gi
env:
- name: GITHUB_TOKEN
valueFrom:
secretKeyRef:
name: my-k8s-secret
key: github-token
tolerations:
- key: "dedicated"
operator: "Equal"
value: "agents"
effect: "NoSchedule"
```
The worker Deployment ServiceAccount needs RBAC to manage Jobs and Pods. The task Job `serviceAccountName` in `pod_template` controls the agent process’s runtime access.
A run’s instance shape overrides the `task` container’s CPU and memory values in `pod_template`.
***
## Preflight check
[Section titled “Preflight check”](#preflight-check)
On startup, the worker runs a preflight Job with the configured task PodSpec. It catches insufficient RBAC, admission-policy failures, and sidecar-loading problems. If preflight fails, the worker exits before accepting tasks. A successful preflight does not validate task-specific images, Secrets, setup commands, or network access.
The preflight image defaults to `busybox:1.36`. For an allowlisted or private image, set `kubernetesBackend.preflightImage`. The `imagePullSecrets` in `kubernetesBackend.podTemplate` also apply to preflight.
***
## Environment variables for Kubernetes tasks
[Section titled “Environment variables for Kubernetes tasks”](#environment-variables-for-kubernetes-tasks)
There are two ways to pass environment variables to Kubernetes task containers:
1. **`pod_template`** (recommended for Kubernetes-native config) — Use standard Kubernetes `env` syntax in the `task` container, including `valueFrom.secretKeyRef` for Kubernetes Secrets.
2. **`-e` / `--env` flags** — Backend-agnostic runtime overrides that work across all managed backends.
When configuring the Kubernetes backend via YAML or Helm, declarative task-container env belongs in `pod_template` rather than a separate top-level list.
For an external secrets manager, inject task secrets through a CSI driver or operator. Add the provider’s `volumes`, `volumeMounts`, and annotations to `pod_template`.
***
## Setup and teardown commands
[Section titled “Setup and teardown commands”](#setup-and-teardown-commands)
Use `kubernetesBackend.setupCommand` (Helm value) or `backend.kubernetes.setup_command` ([config file](/factories/self-hosting/reference/#kubernetes-backend-config)) to run a shell command before each task. Use `teardownCommand` / `teardown_command` for cleanup after the task finishes. These run inside the task Pod and are useful for workspace bootstrapping or post-run reporting.
***
## Protect active task pods from disruption
[Section titled “Protect active task pods from disruption”](#protect-active-task-pods-from-disruption)
Terminating the worker pod normally leaves active task Jobs running. Evicting a task pod interrupts the run and deletes its pod-local `emptyDir` workspace. Configure node lifecycle tooling to avoid voluntary disruption of active task pods.
For Karpenter, add its pod-level disruption annotation to every task Job through the Helm values:
values.yaml
```yaml
kubernetesBackend:
extraAnnotations:
karpenter.sh/do-not-disrupt: "true"
```
The annotation blocks Karpenter consolidation. It blocks drift only when the NodePool omits `terminationGracePeriod`. Expiration, interruption, node repair, and manual deletion can still terminate the node. With `terminationGracePeriod`, Karpenter can terminate blocking pods when the period ends. Review [Karpenter’s pod-level disruption controls](https://karpenter.sh/docs/concepts/disruption/#pod-level-controls).
A PodDisruptionBudget (PDB) constrains tools that use the Kubernetes Eviction API. It protects a group of pods, not an individual task’s process or workspace. Direct deletion, kubelet pressure eviction, node failure, and controllers that bypass the Eviction API can still terminate a task.
For other node lifecycle tools, use the equivalent protection and verify which disruption paths bypass it. A replacement pod cannot resume an interrupted run.
***
## Plan capacity and scheduling
[Section titled “Plan capacity and scheduling”](#plan-capacity-and-scheduling)
Task pods need capacity for their configured requests before the worker’s unschedulable timeout expires.
* Set `worker.maxConcurrentTasks` to a finite value that matches cluster capacity. The default, `0`, does not cap concurrency.
* Set task CPU and memory through a runner instance shape or the `task` container in `kubernetesBackend.podTemplate`. Reserve capacity for init containers, DaemonSets, and workload spikes.
* Set `kubernetesBackend.unschedulableTimeout` longer than the slowest expected node provisioning time. The default is `30s`; `0s` disables the check.
* Use `worker.nodeSelector`, `worker.tolerations`, and `worker.affinity` for the worker Deployment. Use the equivalent fields in `kubernetesBackend.podTemplate` for task pods.
* A toleration makes a pod eligible for a tainted node; it does not reserve capacity. Pair dedicated-node tolerations with matching selectors or affinity and autoscaler capacity.
***
## Metrics
[Section titled “Metrics”](#metrics)
The Helm chart includes built-in support for exporting OpenTelemetry metrics from the worker. Enable metrics by setting `metrics.enabled=true`:
```bash
helm install oz-agent-worker ./charts/oz-agent-worker \
--namespace warp-oz \
--set worker.workerId=oz-k8s-worker \
--set image.tag=VERSION \
--set metrics.enabled=true
```
With the default `metrics.exporter=prometheus`, the chart creates a `Service` with Prometheus scrape annotations and exposes port `9464`. For clusters using the Prometheus Operator, set `metrics.podMonitor.create=true` to create a `PodMonitor`.
To push metrics to an OTLP collector instead, set `metrics.exporter=otlp` and configure the endpoint via `metrics.extraEnv`.
See [Monitoring](/factories/self-hosting/monitoring/) for the full list of Helm values, the metric catalog, and sample PromQL queries.
***
## Operational notes
[Section titled “Operational notes”](#operational-notes)
* **Scaling** — The chart always deploys a single replica for a given `worker.workerId`. To run multiple workers, deploy multiple Helm releases with distinct worker IDs rather than scaling a single release horizontally.
* **Security context** — The Deployment defaults to a non-root security context (`runAsUser: 10001`) with `allowPrivilegeEscalation: false` and all capabilities dropped.
* **Liveness probe** — The Deployment includes a default `exec` liveness probe (`kill -0 1`). Override `worker.livenessProbe` for a custom probe, or set it to `null` to disable.
* **In-cluster auth** — The chart assumes the worker runs inside the target cluster and uses in-cluster Kubernetes auth by default.
***
## Related pages
[Section titled “Related pages”](#related-pages)
* [Self-hosted worker reference](/factories/self-hosting/reference/) — Full CLI flag and config file schema, including every Kubernetes backend field.
* [Self-hosting overview](/factories/self-hosting/) — Managed vs unmanaged and the backend decision guide.
* [Routing runs to this worker](/factories/self-hosting/#routing-runs-to-self-hosted-workers) — How to send tasks to your connected worker from the CLI, schedules, integrations, the API, and the web UI.
* [Environments](/platform/environments/) — Define the task image, repos, and setup commands.
* [Monitoring](/factories/self-hosting/monitoring/) — OpenTelemetry metrics, including Helm chart metrics values.
* [Security and networking](/platform/execution-security/) — RBAC, admission policies, and data boundaries.
* [Troubleshooting](/factories/self-hosting/troubleshooting/#kubernetes-backend) — Common Kubernetes-backend issues.
# Self-hosted worker monitoring
Canonical page: [/factories/self-hosting/monitoring/](https://docs.warp.dev/factories/self-hosting/monitoring/)
> Monitor self-hosted Automation Platform workers with OpenTelemetry metrics via Prometheus, OTLP, or console export.
The `oz-agent-worker` daemon exports [OpenTelemetry](https://opentelemetry.io/) metrics for worker health, task throughput, and capacity. Use these metrics with the [cloud agent dashboard](https://oz.warp.dev) to monitor self-hosted compute and cloud runs.
## Key features
[Section titled “Key features”](#key-features)
* **Prometheus scrape** — Expose a `/metrics` endpoint for Prometheus to scrape, with optional `PodMonitor` support for the Prometheus Operator.
* **OTLP push** — Push metrics to any OpenTelemetry-compatible collector (Grafana Alloy, Datadog Agent, New Relic, etc.).
* **Standard configuration** — Select an exporter with [OpenTelemetry environment variables](https://opentelemetry.io/docs/specs/otel/configuration/sdk-environment-variables/).
* **Pre-seeded series** — Metric series appear at startup before any tasks run.
## How it works
[Section titled “How it works”](#how-it-works)
The worker uses the [OpenTelemetry autoexport package](https://github.com/open-telemetry/opentelemetry-go-contrib/tree/main/exporters/autoexport) to select an exporter at runtime based on the `OTEL_METRICS_EXPORTER` environment variable. Supported values:
* `prometheus` — Starts an in-process HTTP server serving `/metrics`.
* `otlp` — Pushes metrics over OTLP (HTTP/protobuf by default).
* `console` — Writes metrics to stdout (useful for debugging).
* `none` — Disables metrics export entirely.
When `OTEL_METRICS_EXPORTER` is unset, autoexport uses OTLP. Set it to `none` to disable metrics.
All metrics carry resource attributes (`service.name=oz-agent-worker`, `service.version`, `worker.id`, `worker.backend`) so each worker process shows up as a distinct series in your monitoring system.
***
## Enable Prometheus scrape
[Section titled “Enable Prometheus scrape”](#enable-prometheus-scrape)
Set these environment variables before starting the worker to expose a Prometheus-compatible `/metrics` endpoint:
```bash
export OTEL_METRICS_EXPORTER=prometheus
export OTEL_EXPORTER_PROMETHEUS_HOST=0.0.0.0
export OTEL_EXPORTER_PROMETHEUS_PORT=9464
oz-agent-worker --api-key "$WARP_API_KEY" --worker-id "my-worker"
```
Verify the endpoint is serving metrics:
```bash
curl -s localhost:9464/metrics | grep oz_worker_
```
**Expected outcome:** You see `oz_worker_connected`, `oz_worker_tasks_active`, and other `oz_worker_*` metric families in the output.
Note
Bind to `0.0.0.0` (not `localhost`) when running in Docker or Kubernetes so the Prometheus server, kubelet, or scrape target can reach the endpoint from outside the container.
***
## Enable OTLP push
[Section titled “Enable OTLP push”](#enable-otlp-push)
Set these environment variables to push metrics to an OpenTelemetry collector:
```bash
export OTEL_METRICS_EXPORTER=otlp
export OTEL_EXPORTER_OTLP_PROTOCOL=http/protobuf
export OTEL_EXPORTER_OTLP_ENDPOINT=http://otel-collector.observability.svc:4318
oz-agent-worker --api-key "$WARP_API_KEY" --worker-id "my-worker"
```
The worker pushes metrics at the SDK’s default interval. Configure the collector endpoint, protocol, and headers using standard [OTLP exporter environment variables](https://opentelemetry.io/docs/specs/otel/protocol/exporter/).
***
## Helm chart configuration
[Section titled “Helm chart configuration”](#helm-chart-configuration)
The [Helm chart](/factories/self-hosting/managed-kubernetes/) includes built-in support for metrics. Enable metrics with `metrics.enabled=true`:
```bash
helm install oz-agent-worker ./charts/oz-agent-worker \
--namespace warp-oz \
--set worker.workerId=my-worker \
--set image.tag=VERSION \
--set metrics.enabled=true
```
With `metrics.enabled=true` and the default `metrics.exporter=prometheus`, the chart adds:
* A `containerPort: metrics` (default 9464) on the worker Deployment.
* The `OTEL_METRICS_EXPORTER`, `OTEL_EXPORTER_PROMETHEUS_HOST`, and `OTEL_EXPORTER_PROMETHEUS_PORT` environment variables.
* A namespace-scoped `Service` named `<release>-oz-agent-worker-metrics` with `prometheus.io/scrape` annotations.
* Optionally, a `PodMonitor` (`metrics.podMonitor.create=true`) for clusters using the Prometheus Operator.
### Helm values
[Section titled “Helm values”](#helm-values)
**Core:**
* `metrics.enabled` — Enable metrics export. Defaults to `false`.
* `metrics.exporter` — Exporter type: `prometheus` (default), `otlp`, `console`, or `none`.
* `metrics.port` — Port for the Prometheus exporter. Defaults to `9464`. Ignored for `otlp`/`console`.
* `metrics.extraEnv` — Extra environment variables for the worker container (e.g., `OTEL_EXPORTER_OTLP_ENDPOINT`).
**Service (Prometheus scrape):**
* `metrics.service.create` — Create a metrics `Service`. Defaults to `true`.
* `metrics.service.type` — Service type. Defaults to `ClusterIP`.
* `metrics.service.annotations` — Annotations on the Service. Defaults include `prometheus.io/scrape: "true"`.
**PodMonitor (Prometheus Operator):**
* `metrics.podMonitor.create` — Create a `PodMonitor`. Defaults to `false` (avoids requiring `monitoring.coreos.com` CRDs).
* `metrics.podMonitor.interval` — Scrape interval. Defaults to `30s`.
* `metrics.podMonitor.scrapeTimeout` — Scrape timeout. Defaults to `10s`.
* `metrics.podMonitor.additionalLabels` — Extra labels on the `PodMonitor` resource.
### OTLP push via Helm
[Section titled “OTLP push via Helm”](#otlp-push-via-helm)
To push metrics to an OTLP collector instead of exposing a Prometheus endpoint, set `metrics.exporter=otlp` and forward the endpoint via `metrics.extraEnv`:
```yaml
metrics:
enabled: true
exporter: otlp
extraEnv:
- name: OTEL_EXPORTER_OTLP_ENDPOINT
value: http://otel-collector.observability.svc:4318
```
***
## Metric catalog
[Section titled “Metric catalog”](#metric-catalog)
All metrics use the `oz_worker_` prefix. Each worker process with metrics enabled emits a distinct set of series, identified by the resource attributes `service.name`, `service.version`, `worker.id`, and `worker.backend`.
* **`oz_worker_connected`** (gauge) — `1` while the worker has an active WebSocket connection to the Automation Platform‘s backend, `0` otherwise.
* **`oz_worker_tasks_active`** (gauge / UpDownCounter) — Tasks currently executing on this worker.
* **`oz_worker_tasks_max_concurrent`** (gauge) — Configured concurrency limit (`0` means unlimited).
* **`oz_worker_tasks_claimed_total`** (counter) — Total tasks accepted since process start.
* **`oz_worker_tasks_rejected_total{reason}`** (counter) — Tasks the worker declined (e.g., `reason="at_capacity"`).
* **`oz_worker_tasks_completed_total{result}`** (counter) — Completed tasks labeled `result="succeeded"`, `result="failed"`, `result="cancelled"`, or `result="dispatched"`.
* **`oz_worker_task_duration_seconds{result}`** (histogram) — Wall-clock task duration on the worker, labeled by result.
* **`oz_worker_task_failures_total{phase,reason}`** (counter) — Task failures classified by execution phase and a bounded reason such as `image_pull`, `unschedulable`, `container_oom`, or `evicted`.
* **`oz_worker_websocket_reconnects_total{reason}`** (counter) — WebSocket reconnect attempts (e.g., `reason="dial_failed"`, `reason="remote_close"`). Spikes indicate flapping workers.
* **`oz_worker_info{version,backend,worker_id}`** (gauge, constant `1`) — Build and runtime metadata. Useful for joining other series by labels.
***
## Sample PromQL queries
[Section titled “Sample PromQL queries”](#sample-promql-queries)
* **Workers available:**
```promql
sum(oz_worker_connected)
```
* **Workers active (running at least one task):**
```promql
count(oz_worker_tasks_active > 0)
```
* **Fleet saturation:**
```promql
sum(oz_worker_tasks_active) / sum(oz_worker_tasks_max_concurrent > 0)
```
This ratio is only meaningful when every worker has a non-zero `oz_worker_tasks_max_concurrent`. Workers configured with `0` (unlimited) are excluded from the denominator, which can make the saturation result look misleadingly high or undefined for fleets that mix bounded and unlimited workers.
* **Task success rate (5-minute window):**
```promql
sum(rate(oz_worker_tasks_completed_total{result="succeeded"}[5m]))
/ sum(rate(oz_worker_tasks_completed_total[5m]))
```
* **Task duration p95:**
```promql
histogram_quantile(0.95, sum by (le) (rate(oz_worker_task_duration_seconds_bucket[5m])))
```
* **Failure rate:**
```promql
sum(rate(oz_worker_tasks_completed_total{result="failed"}[5m]))
```
* **Failure modes:**
```promql
sum by (phase, reason) (rate(oz_worker_task_failures_total[5m]))
```
* **Reconnect storms (alert threshold):**
```promql
sum(rate(oz_worker_websocket_reconnects_total[5m])) > 0.1
```
***
## Disabling metrics
[Section titled “Disabling metrics”](#disabling-metrics)
Set `OTEL_METRICS_EXPORTER=none` to disable metrics export:
```bash
export OTEL_METRICS_EXPORTER=none
oz-agent-worker --api-key "$WARP_API_KEY" --worker-id "my-worker"
```
The Helm chart sets the same override when metrics are disabled:
```yaml
metrics:
enabled: false
```
***
## Related pages
[Section titled “Related pages”](#related-pages)
* [Self-hosting overview](/factories/self-hosting/) — Architecture, decision guide, and Enterprise requirements.
* [Self-hosted worker reference](/factories/self-hosting/reference/) — CLI flags, config file schema, and metrics environment variables.
* [Managed: Kubernetes](/factories/self-hosting/managed-kubernetes/) — Helm chart deployment, including metrics values.
* [Troubleshooting](/factories/self-hosting/troubleshooting/) — Diagnostics for metrics issues and other common problems.
* [Security and networking](/platform/execution-security/) — Network egress and data boundaries.
# Self-hosting quickstart
Canonical page: [/factories/self-hosting/quickstart/](https://docs.warp.dev/factories/self-hosting/quickstart/)
> Get a managed self-hosted Automation Platform worker running on Docker and route your first cloud agent run to it in under 10 minutes.
Run your first cloud agent on your own infrastructure in \~10 minutes using the managed architecture with the Docker backend — the default and fastest path to self-hosting.
Note
This quickstart sets up the [managed architecture](/factories/self-hosting/#managed-architecture), where the Automation Platform orchestrates the agent and your worker provides the compute. **Prefer a CLI-only path with no Docker requirement?** Jump to the [Unmanaged quickstart](/platform/unmanaged-execution/#unmanaged-quickstart) to run `oz agent run` directly on any host.
***
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **Managed self-hosting access and credentials** - Complete the shared [managed prerequisites](/factories/self-hosting/#managed-prerequisites), then create an [Agent API key associated with the Default Service Account](/agents/cli/oz-cli/api-keys/#from-the-web-app-recommended). This key authenticates both the worker and the `oz agent run-cloud` command in this quickstart. A self-hosted worker key authenticates the worker only.
* **A Linux machine with Docker** - Use a VM, server, or local machine with a Docker daemon that runs Linux containers. Verify it with `docker info`. Docker Desktop on macOS or Windows works for testing.
* **The Oz CLI** - Install it on the machine that will route the test run. See [Installing the CLI](/agents/cli/oz-cli/#installing-the-cli).
***
## Run your first self-hosted agent
[Section titled “Run your first self-hosted agent”](#run-your-first-self-hosted-agent)
*\~10 minutes*
### 1. Export your API key
[Section titled “1. Export your API key”](#1-export-your-api-key)
Export the Agent API key so the worker container and the Oz CLI can authenticate to the Automation Platform:
```bash
export WARP_API_KEY="YOUR_AGENT_API_KEY"
```
### 2. Start the worker
[Section titled “2. Start the worker”](#2-start-the-worker)
Run the `oz-agent-worker` container, mounting the host’s Docker socket so the worker can spawn task containers. Choose any `--worker-id` meaningful for your team — you’ll use this value to route tasks to this worker.
```bash
docker run -v /var/run/docker.sock:/var/run/docker.sock \
-e WARP_API_KEY="$WARP_API_KEY" \
warpdotdev/oz-agent-worker --worker-id "my-worker"
```
**Expected outcome:** The worker connects to the Automation Platform and begins listening for tasks. You should see log output confirming the connection (something like `Connected to Oz` / `Waiting for tasks`).
Caution
For production deployments, pin to a specific image digest (e.g., `warpdotdev/oz-agent-worker@sha256:...`) instead of the `latest` tag.
### 3. Route a run to your worker
[Section titled “3. Route a run to your worker”](#3-route-a-run-to-your-worker)
In a separate terminal on any machine with the Oz CLI, route a cloud agent run to your worker by passing `--host` with the worker ID you chose:
```bash
oz agent run-cloud --prompt "List the files in the current directory" --host "my-worker"
```
**Expected outcome:** The Automation Platform accepts the task, routes it to your worker, and the worker spawns a Docker container to execute the agent. You’ll see the run appear in the [cloud agent dashboard](https://oz.warp.dev) with status moving from `QUEUED` → `INPROGRESS` → `SUCCEEDED`.
### 4. Verify the run
[Section titled “4. Verify the run”](#4-verify-the-run)
Open the [cloud agent dashboard](https://oz.warp.dev), find the new task, and confirm the session transcript shows the agent running against your worker. You can attach to the session at any time via [Agent Session Sharing](/agents/local-agents/session-sharing/) to monitor or steer it.
***
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
**Worker won’t start**\
Verify Docker is running (`docker info`) and that the daemon platform is `linux/amd64` or `linux/arm64`. Musl-based (Alpine) worker hosts are not supported.
**Worker won’t connect**\
Verify you created an **Agent** key associated with the Default Service Account and that it has not expired. Ensure the machine has outbound internet access to `oz.warp.dev:443`. Increase log verbosity with `--log-level debug` to see connection details.
**Task stays queued and never runs**\
Confirm the `--host` value you passed to `oz agent run-cloud` matches your `--worker-id` exactly (case-sensitive). Check that the worker’s team matches the team creating the task.
For more, see [Troubleshooting](/factories/self-hosting/troubleshooting/).
## Next steps
[Section titled “Next steps”](#next-steps)
* [Self-hosting overview](/factories/self-hosting/) — Compare managed and unmanaged architectures and choose a backend.
* [Managed: Docker](/factories/self-hosting/managed-docker/) — Full Docker backend setup, including private registries, volume mounts, and runtime configuration.
* [Routing runs to self-hosted workers](/factories/self-hosting/#routing-runs-to-self-hosted-workers) — How to route tasks from schedules, integrations (Slack, Linear), the API, and the Oz web app.
# Self-hosted worker reference
Canonical page: [/factories/self-hosting/reference/](https://docs.warp.dev/factories/self-hosting/reference/)
> Complete reference for the oz-agent-worker daemon — CLI flags and config file schema for the Docker, Kubernetes, Direct, and Command backends.
Look up CLI flags and YAML config fields for the `oz-agent-worker` daemon’s [managed backends](/factories/self-hosting/#managed-architecture). For installation, see [Install and run the worker](/factories/self-hosting/managed-docker/#install-and-run-the-worker).
***
## Worker flags
[Section titled “Worker flags”](#worker-flags)
The following flags are available when starting the worker.
### Required
[Section titled “Required”](#required)
* `--worker-id` — A string identifying this worker. This is the value you pass to `--host` when routing tasks. Choose something meaningful for your team (e.g., `prod-runner-1` or `ci-worker`). Multiple workers can share the same ID for load balancing.
* `--api-key` or `WARP_API_KEY` env var — Your [self-hosted worker API key](/agents/cli/oz-cli/api-keys/#creating-a-self-hosted-worker-api-key) for team authentication. When running via Docker, pass it as `-e WARP_API_KEY="..."`. When running the binary directly, use `--api-key` or the environment variable.
### Optional
[Section titled “Optional”](#optional)
* `--config-file` — Path to a YAML [config file](#config-file). CLI flags take precedence over config file values.
* `--backend` — Backend type: `docker` (default), `kubernetes`, `direct`, or `command`. See [Managed: Kubernetes](/factories/self-hosting/managed-kubernetes/), [Managed: Direct](/factories/self-hosting/managed-direct/), and [External orchestrators](/factories/self-hosting/external-orchestrators/) for backend-specific setup.
* `--log-level` — Log verbosity. One of `debug`, `info`, `warn`, `error`. Defaults to `info`.
* `--no-cleanup` — Keep task containers, Kubernetes Jobs, or workspace directories after execution instead of removing them. For Direct tasks that use per-task workspaces, this also skips `teardown_command`. Useful for debugging failed tasks.
* `--target-dir` — Shared working directory for all Direct backend tasks. When set, the worker does not create or remove per-task workspace directories. This flag overrides `backend.direct.target_dir` in the config file.
* `-v` / `--volumes` — Mount host directories into task containers (Docker backend only). Format: `HOST_PATH:CONTAINER_PATH` or `HOST_PATH:CONTAINER_PATH:MODE` (where MODE is `ro` or `rw`). Can be specified multiple times.
* `-e` / `--env` — Set environment variables for tasks. Format: `KEY=VALUE` (explicit value) or `KEY` (pass through from host environment). Can be specified multiple times.
* `--max-concurrent-tasks` — Maximum number of tasks to run concurrently. Defaults to `0` (unlimited). When set, additional tasks wait until a slot is available.
* `--one-shot` — Exit after one accepted task succeeds, fails, or is cancelled. Supported only by the Direct backend and forces `max_concurrent_tasks` to `1`.
* `--idle-on-complete` — How long to keep the `oz` process alive after a task’s conversation finishes, allowing follow-up interactions via session sharing. Uses duration format (e.g. `45m`, `10m`, `0s`). Defaults to `45m` when the task has no `config.idle_timeout_minutes` value. A task-level value takes precedence; runs created directly through the Agent API default to 10 minutes. See [Configure the completion timeout](/factories/self-hosting/external-orchestrators/#configure-the-completion-timeout).
Worker IDs starting with `warp` are reserved and cannot be used. The worker refuses to start if `--worker-id` begins with `warp`.
### Example with all flags
[Section titled “Example with all flags”](#example-with-all-flags)
```bash
docker run -v /var/run/docker.sock:/var/run/docker.sock \
-e WARP_API_KEY="$WARP_API_KEY" \
warpdotdev/oz-agent-worker \
--worker-id "prod-runner-1" \
--log-level debug \
--no-cleanup \
--max-concurrent-tasks 4 \
--idle-on-complete 10m \
-v /opt/shared-cache:/cache:ro \
-e NPM_TOKEN=your_token \
-e GITHUB_TOKEN
```
Caution
When running the worker via Docker, there are two levels of `-e` flags. Docker’s `-e` passes env vars to the **worker container** (e.g., `WARP_API_KEY`). The worker’s `-e` / `--env` flags pass env vars into the **task containers** the worker spawns. Keep these distinct.
***
## Config file
[Section titled “Config file”](#config-file)
For complex setups, use a YAML config file instead of (or in addition to) CLI flags. Pass it with `--config-file`:
```bash
oz-agent-worker --api-key "$WARP_API_KEY" --config-file config.yaml
```
CLI flags always take precedence over config file values.
### Docker backend config
[Section titled “Docker backend config”](#docker-backend-config)
```yaml
worker_id: "my-worker"
cleanup: true
max_concurrent_tasks: 4
idle_on_complete: "10m"
backend:
docker:
volumes:
- "/data:/data:ro"
- "/cache:/cache"
environment:
- name: NPM_TOKEN
value: "your_token"
- name: GITHUB_TOKEN # inherits from host environment
```
### Kubernetes backend config
[Section titled “Kubernetes backend config”](#kubernetes-backend-config)
```yaml
worker_id: "k8s-worker"
max_concurrent_tasks: 4
backend:
kubernetes:
namespace: "warp-oz"
default_image: "my-registry.io/dev-image:latest"
unschedulable_timeout: "2m"
pod_template:
nodeSelector:
kubernetes.io/os: linux
containers:
- name: task
resources:
requests:
cpu: "2"
memory: 4Gi
env:
- name: GITHUB_TOKEN
valueFrom:
secretKeyRef:
name: my-k8s-secret
key: github-token
```
### Direct backend config
[Section titled “Direct backend config”](#direct-backend-config)
```yaml
worker_id: "direct-worker"
max_concurrent_tasks: 2
backend:
direct:
workspace_root: "/var/lib/oz/workspaces"
oz_path: "/usr/local/bin/oz"
setup_command: "/opt/scripts/setup.sh"
teardown_command: "/opt/scripts/teardown.sh"
environment:
- name: MY_VAR
value: "hello"
```
### Command backend config
[Section titled “Command backend config”](#command-backend-config)
```yaml
worker_id: "command-worker"
backend:
command:
dispatch_command: "python3 /opt/warp/dispatch.py"
cancel_command: "python3 /opt/warp/cancel.py"
dispatch_timeout: "60s"
environment:
- name: OZ_DISPATCH_URL
value: "https://runtime.internal.example.com/agent-runs"
- name: OZ_CANCEL_URL
value: "https://runtime.internal.example.com/agent-runs/cancel"
- name: OZ_DISPATCH_AUTH_HEADER
```
### Config file fields
[Section titled “Config file fields”](#config-file-fields)
**Top-level:**
* `worker_id` — Worker identifier (same as `--worker-id` flag).
* `cleanup` — Whether to clean up after tasks. Defaults to `true`. Set to `false` to keep containers/workspaces for debugging (equivalent to `--no-cleanup`).
* `max_concurrent_tasks` — Maximum concurrent tasks. Defaults to unlimited.
* `one_shot` — Exit after one accepted Direct backend task reaches a terminal state. Defaults to `false` and forces `max_concurrent_tasks` to `1` when enabled.
* `idle_on_complete` — Duration to keep the `oz` process alive after task completion (e.g. `"45m"`, `"0s"`). Task-level timeout values take precedence; see [Configure the completion timeout](/factories/self-hosting/external-orchestrators/#configure-the-completion-timeout).
* `backend` — Backend configuration block. Only one backend (`docker`, `kubernetes`, `direct`, or `command`) may be specified.
**`backend.docker`:**
* `volumes` — List of volume mounts (same format as `-v` flag).
* `environment` — List of environment variables with `name` and optional `value`. If `value` is omitted, the variable is inherited from the host.
**`backend.kubernetes`:**
* `namespace` — Kubernetes namespace for task Jobs. Defaults to `default`. Selects the namespace inside the chosen cluster; does not choose the cluster.
* `kubeconfig` — Path to an explicit kubeconfig file. If omitted, the worker uses in-cluster config when running inside Kubernetes, or falls back to the default kubeconfig loading rules.
* `default_image` — Default Docker image for task Jobs when the run has no Warp environment image. Precedence: Warp environment image > `default_image` > `ubuntu:22.04`. Set this to skip creating a Warp environment when all your tasks use the same base image.
* `image_pull_policy` — One of `Always`, `Never`, or `IfNotPresent`. Defaults to `IfNotPresent`.
* `use_image_volumes` — Use native image volumes instead of root init containers. Defaults to `false` and requires cluster and runtime support.
* `preflight_image` — Startup preflight Job image. Defaults to `busybox:1.36`.
* `preflight_resources` — CPU and memory requests and limits for startup preflight containers.
* `sidecar_image` — Registry override for the Warp agent sidecar image.
* `setup_command` — Shell command to run before each task.
* `teardown_command` — Shell command to run after each task completes.
* `extra_labels` — Map of additional labels to add to task Jobs and Pods.
* `extra_annotations` — Map of additional annotations to add to task Jobs and Pods.
* `active_deadline_seconds` — Maximum task Job lifetime (Kubernetes `activeDeadlineSeconds`). The worker has no default; the Helm chart defaults `kubernetesBackend.activeDeadlineSeconds` to eight hours.
* `ttl_seconds_after_finished` — Retention period for failed or orphaned Jobs. Defaults to 24 hours when cleanup is enabled.
* `workspace_size_limit` — Size limit for the workspace `emptyDir` volume (e.g., `10Gi`).
* `unschedulable_timeout` — How long a pod may remain unschedulable before the task is failed early. Defaults to `30s`. Set to `0s` to disable the fail-fast behavior.
* `pod_template` — Raw Kubernetes PodSpec YAML merged with the worker’s required fields at runtime. Use this to configure task pod scheduling, `serviceAccountName`, `imagePullSecrets`, `nodeSelector`, `tolerations`, resources, and environment variables (including `valueFrom.secretKeyRef` for Kubernetes Secrets). Define a container named `task` to customize the main task container directly; otherwise the worker appends its own.
**`backend.direct`:**
* `workspace_root` — Directory where per-task workspaces are created. Defaults to `/var/lib/oz/workspaces`.
* `target_dir` — Shared directory used as the working directory for every task. When set, the worker does not create or remove per-task workspace directories.
* `oz_path` — Path to the oz CLI binary. If omitted, the worker looks up `oz` in `PATH`.
* `setup_command` — Shell command to run before each task. Receives `OZ_WORKSPACE_ROOT`, `OZ_RUN_ID`, `OZ_ENVIRONMENT_FILE`, and `OZ_WORKER_BACKEND` as environment variables.
* `teardown_command` — Shell command to run after each task completes.
* `environment` — List of environment variables (same format as the Docker backend).
**`backend.command`:**
* `dispatch_command` — Required shell command that accepts a JSON task payload on standard input and hands the task to an external runtime.
* `cancel_command` — Optional shell command invoked when a dispatched task is cancelled.
* `dispatch_timeout` — Maximum runtime for the dispatch command. Defaults to `60s`.
* `environment` — Environment variables for the dispatch and cancellation commands. Task credentials remain in the standard-input payload.
Only one backend can be configured at a time. Specifying more than one of `docker`, `kubernetes`, `direct`, and `command` in the same config file is an error.
***
## Metrics configuration
[Section titled “Metrics configuration”](#metrics-configuration)
Configure OpenTelemetry metrics with environment variables on the worker process or container:
* `OTEL_METRICS_EXPORTER` — Exporter to use: `prometheus`, `otlp`, `console`, or `none`. When unset, the worker uses the OpenTelemetry autoexport default, OTLP. Set it to `none` to disable metrics initialization.
* `OTEL_EXPORTER_PROMETHEUS_HOST` — Bind address for the Prometheus exporter. Defaults to `localhost`. Set to `0.0.0.0` when running in Docker or Kubernetes.
* `OTEL_EXPORTER_PROMETHEUS_PORT` — Port for the Prometheus exporter. Defaults to `9464`.
* `OTEL_EXPORTER_OTLP_ENDPOINT` — OTLP collector endpoint (e.g., `http://otel-collector.observability.svc:4318`).
* `OTEL_EXPORTER_OTLP_PROTOCOL` — OTLP protocol: `http/protobuf` (default) or `grpc`.
When deploying with the Helm chart, use the `metrics.*` values instead of setting these variables manually. See [Monitoring](/factories/self-hosting/monitoring/) for the full setup guide, metric catalog, Helm values, and sample PromQL queries.
***
## Routing runs to self-hosted workers
[Section titled “Routing runs to self-hosted workers”](#routing-runs-to-self-hosted-workers)
Once a worker is running, route cloud agent runs to it with the `--host` flag or its equivalents. See [Routing runs to self-hosted workers](/factories/self-hosting/#routing-runs-to-self-hosted-workers) for examples across the CLI, schedules, integrations, the API, and the web UI.
***
## Related pages
[Section titled “Related pages”](#related-pages)
* [Managed: Docker](/factories/self-hosting/managed-docker/) — Docker backend setup, connectivity, and private registries.
* [Managed: Kubernetes](/factories/self-hosting/managed-kubernetes/) — Kubernetes backend setup, Helm chart, pod template, and operational notes.
* [Managed: Direct](/factories/self-hosting/managed-direct/) — Direct backend setup and workspace model.
* [External orchestrators](/factories/self-hosting/external-orchestrators/) — One-shot Direct and Command backend dispatch.
* [Direct backend monorepo worktrees](/factories/self-hosting/direct-monorepo-worktrees/) — Setup and teardown hooks for isolated monorepo worktrees.
* [Self-hosting overview](/factories/self-hosting/) — Architecture, decision guide, and Enterprise requirements.
* [Environments](/platform/environments/) — Define the Docker image, repos, and setup commands used by task containers.
* [Monitoring](/factories/self-hosting/monitoring/) — OpenTelemetry metrics for worker health, task throughput, and capacity.
* [Troubleshooting](/factories/self-hosting/troubleshooting/) — Worker and task failure diagnostics.
# Self-hosting troubleshooting
Canonical page: [/factories/self-hosting/troubleshooting/](https://docs.warp.dev/factories/self-hosting/troubleshooting/)
> Diagnose and fix common problems with self-hosted Automation Platform worker daemons across Docker, Kubernetes, and Direct backends.
Use these checks when the `oz-agent-worker` daemon won’t start or connect, tasks stay queued, or tasks fail.
Note
The steps below apply to the [managed architecture](/factories/self-hosting/#managed-architecture) (`oz-agent-worker` daemon). For [unmanaged](/platform/unmanaged-execution/) deployments, refer to the documentation for the environment running `oz agent run` (e.g., GitHub Actions, Kubernetes).
***
## Worker won’t start
[Section titled “Worker won’t start”](#worker-wont-start)
### Docker backend
[Section titled “Docker backend”](#docker-backend)
**Cause:** Docker isn’t running, or the daemon platform isn’t supported.
**Fix:**
1. Verify Docker is running: `docker info`.
2. Confirm the daemon platform is `linux/amd64` or `linux/arm64`. Windows containers are not supported.
3. If the worker runs inside Docker, confirm the `/var/run/docker.sock` mount is correct and the mounting user has permission to the socket.
### Kubernetes backend
[Section titled “Kubernetes backend”](#kubernetes-backend)
**Cause:** The worker Deployment couldn’t start, reach the Kubernetes API, or create its preflight Job.
**Fix:**
1. Run `kubectl describe pod -n NAMESPACE WORKER_POD`. Replace `NAMESPACE` with the chart namespace and `WORKER_POD` with the worker pod name. For `CreateContainerConfigError`, verify the Secret and key configured by `warp.apiKeySecret`.
2. Check the worker logs for Kubernetes API or preflight diagnostics: `kubectl logs -n NAMESPACE WORKER_POD`.
3. Confirm the worker’s namespace has these permissions: `create`, `get`, `list`, `watch`, `delete` on `jobs`; `get`, `list`, `watch` on `pods`; `get` on `pods/log`; `list` on `events`.
4. Confirm the task namespace allows pods with a root init container, unless you enabled native image volumes with `kubernetesBackend.useImageVolumes=true`.
5. If your cluster restricts image sources, set `kubernetesBackend.preflightImage` to an allowlisted image. The default is `busybox:1.36`.
6. To pull the preflight image from a private registry, configure `imagePullSecrets` in `kubernetesBackend.podTemplate`.
A successful preflight validates the configured pod shape, not task-specific images, Secrets, setup commands, or network access.
### Direct backend
[Section titled “Direct backend”](#direct-backend)
**Cause:** The `oz` CLI isn’t installed or isn’t on the worker’s `PATH`.
**Fix:**
1. Install the Oz CLI on the worker host. See [Installing the CLI](/agents/cli/oz-cli/#installing-the-cli).
2. If the CLI isn’t on `PATH`, set `oz_path` in the config file to the absolute path of the `oz` binary.
***
## Worker won’t connect
[Section titled “Worker won’t connect”](#worker-wont-connect)
**Cause:** The API key is invalid, expired, or the host cannot reach the Automation Platform‘s backend.
**Fix:**
1. Confirm you created a **Self-hosted worker** API key and that it has not expired.
2. If you suspect the key is invalid, open the [Warp Factories web app user settings page](https://platform.warp.dev/settings), click **Generate new token**, and select **Self-hosted worker** to create a replacement.
3. Ensure the host has outbound internet access to `oz.warp.dev:443`.
4. Check that no firewall rules are blocking WebSocket connections to `wss://oz.warp.dev`.
5. Increase log verbosity with `--log-level debug` to see connection details.
See [Security and networking](/platform/execution-security/#network-requirements) for the full list of outbound endpoints the worker needs.
***
## Tasks not being picked up
[Section titled “Tasks not being picked up”](#tasks-not-being-picked-up)
**Cause:** The worker isn’t running, the `--host` value doesn’t match the worker’s `--worker-id`, or the worker and task belong to different teams.
**Fix:**
1. Confirm the worker is running and connected. Check the worker logs for `Successfully connected to server`.
2. Verify the `--host` (or `worker_host`) value you passed matches your `--worker-id` exactly. Case-sensitive.
3. Ensure the worker’s team matches the team creating the task.
***
## Metrics not appearing
[Section titled “Metrics not appearing”](#metrics-not-appearing)
**Cause:** The worker is running but metrics aren’t showing up in Prometheus or your collector.
**Fix:**
1. Verify `OTEL_METRICS_EXPORTER` is set correctly on the worker process. Run `curl -s localhost:9464/metrics` from the worker host (for `prometheus` mode) to confirm the endpoint is serving.
2. For Prometheus scrape mode, confirm the bind address is `0.0.0.0` (not `localhost`) when running in Docker or Kubernetes. `localhost` is only reachable from inside the container.
3. Confirm no firewall or network policy blocks the metrics port (default `9464`).
4. For OTLP push mode, verify `OTEL_EXPORTER_OTLP_ENDPOINT` points to a reachable collector and that the protocol matches (`http/protobuf` vs `grpc`).
5. When using the Helm chart, confirm `metrics.enabled=true` is set. Check that the `Service` and optional `PodMonitor` were created: `kubectl get svc,podmonitor -n NAMESPACE`. Replace `NAMESPACE` with the chart namespace.
6. If using `metrics.podMonitor.create=true`, verify the `monitoring.coreos.com` CRDs are installed in the cluster. The `PodMonitor` resource requires the Prometheus Operator.
7. Restart the worker with `--log-level debug` and look for metrics-related error messages at startup.
See [Monitoring](/factories/self-hosting/monitoring/) for the full setup guide.
***
## Task failures
[Section titled “Task failures”](#task-failures)
**Cause:** The backend logs identify why the task failed.
**Fix (all backends):**
1. Review task logs in the [cloud agent dashboard](https://oz.warp.dev) or via [session sharing](/agents/local-agents/session-sharing/).
2. Use `--no-cleanup` to keep the container, Job, or workspace indefinitely for inspection. With Kubernetes cleanup enabled, failed Jobs remain for 24 hours by default.
3. Use `--log-level debug` to see detailed execution logs.
4. Ensure the worker machine or cluster has sufficient resources (CPU, memory, disk).
### Docker backend (task failures)
[Section titled “Docker backend (task failures)”](#docker-backend-task-failures)
1. Verify Docker is running (`docker info`).
2. If using a custom image, confirm it is **glibc-based** (not Alpine/musl) and that its architecture matches the worker’s Docker daemon platform.
### Kubernetes backend (task failures)
[Section titled “Kubernetes backend (task failures)”](#kubernetes-backend-task-failures)
Start with the pod phase and recent events:
```bash
kubectl get jobs,pods -n NAMESPACE
kubectl describe pod -n NAMESPACE TASK_POD
kubectl logs -n NAMESPACE TASK_POD -c CONTAINER_NAME
kubectl logs -n NAMESPACE TASK_POD -c CONTAINER_NAME --previous
```
Replace `NAMESPACE` with the task namespace, `TASK_POD` with the task pod name, and `CONTAINER_NAME` with the failed container name. Match the reported reason:
* **`Pending` or `Unschedulable`:** Read the scheduling events. Check free CPU and memory, selectors and affinity, taints and tolerations, topology constraints, quotas, and volume binding. Allow enough time for node provisioning and reserve capacity for init containers, DaemonSets, and spikes.
* **`OOMKilled`:** Increase memory in the agent profile’s instance shape. The instance shape overrides the task container’s CPU and memory values in the pod template. Check sidecar and init-container resources separately.
* **`ErrImagePull`, `ImagePullBackOff`, or `InvalidImageName`:** Follow [Image pull failures](#image-pull-failures). Preflight does not pull every task image.
* **`CreateContainerConfigError` or `FailedMount`:** Events name the missing Secret, ConfigMap, service account, key, or volume. Verify that it exists in the task namespace.
* **Init container failure:** Check each init container’s status and logs. The Warp sidecar-loading init container runs as root unless native image volumes are enabled. Custom init containers must finish before the task starts.
* **`Evicted`, `DeadlineExceeded`, or exit code `143`:** Check node pressure, lifecycle-tool events, the Job deadline, and termination events. A replacement pod cannot recover the task’s `emptyDir` workspace. See [protecting active task pods from voluntary disruption](/factories/self-hosting/managed-kubernetes/#protect-active-task-pods-from-disruption).
* **The task cannot reach a dependency:** Test DNS, TLS, and the destination from the task pod. Worker connectivity to Warp does not test the task’s network policies, service mesh, proxy, or dependency egress.
The worker API key authenticates the worker to Warp; it is not a task credential. Provide task credentials through your Secret integration and pod template.
### Direct backend (task failures)
[Section titled “Direct backend (task failures)”](#direct-backend-task-failures)
1. Verify the Oz CLI is accessible.
2. Verify the workspace root directory has write permissions for the user running the worker.
***
## Image pull failures
[Section titled “Image pull failures”](#image-pull-failures)
### Docker backend (image pull)
[Section titled “Docker backend (image pull)”](#docker-backend-image-pull)
1. If using a private registry, ensure Docker credentials are available to the worker. See [Private Docker registries](/factories/self-hosting/managed-docker/#private-docker-registries).
2. Try pulling the image manually on the worker host: `docker pull <image>`.
### Kubernetes backend (image pull)
[Section titled “Kubernetes backend (image pull)”](#kubernetes-backend-image-pull)
1. Configure `imagePullSecrets` in the `pod_template` section of your worker config.
2. Verify the Secret exists in the task namespace and contains valid credentials.
### Both backends (image pull)
[Section titled “Both backends (image pull)”](#both-backends-image-pull)
* Verify the image exists and the tag is correct.
* Check network connectivity from the worker/cluster to the registry.
***
## Related pages
[Section titled “Related pages”](#related-pages)
* [Self-hosting overview](/factories/self-hosting/) — Architecture and decision guide.
* [Self-hosted worker reference](/factories/self-hosting/reference/) — CLI flags and config schema, including every flag mentioned here.
* [Security and networking](/platform/execution-security/) — Outbound endpoints the worker needs.
* [Agent Session Sharing](/agents/local-agents/session-sharing/) — Attach to running tasks to debug interactively.
# Troubleshooting Warp Factories
Canonical page: [/factories/troubleshooting/](https://docs.warp.dev/factories/troubleshooting/)
> Fix factory setup problems, events that don't start work, and runs that stall or need stopping.
Fix the problems teams hit most often when setting up a factory and running their first work through it. Each entry below names the symptom you’d see in the Warp Factories web app.
## Setting up a factory
[Section titled “Setting up a factory”](#setting-up-a-factory)
### You don’t have access to Warp Factories
[Section titled “You don’t have access to Warp Factories”](#you-dont-have-access-to-warp-factories)
**Cause:** Warp Factories is in Early Access and enabled per team.
**Fix:** [Request access](https://www.warp.dev/factories/request-access) for your team. If a teammate already has it, ask a team admin to confirm you’re on that team.
### A repository doesn’t appear in the picker
[Section titled “A repository doesn’t appear in the picker”](#a-repository-doesnt-appear-in-the-picker)
**Cause:** The code host connection doesn’t cover the repository.
**Fix:**
1. Confirm the connection includes the repository and the intended organization or group. See the [GitHub](/factories/integrations/github/) and [GitLab](/factories/integrations/gitlab/) integration guides for how each connection is scoped.
2. If you can’t update it yourself, ask a GitHub organization owner, a GitLab group owner, or a Warp team admin to extend the connection.
### Setup stops at an agent limit
[Section titled “Setup stops at an agent limit”](#setup-stops-at-an-agent-limit)
**Cause:** Your team’s plan limits how many factory agents it can run.
**Fix:**
1. Ask a team admin to confirm the team’s capacity.
2. If the team needs more agents, [contact sales](https://www.warp.dev/contact-sales).
### The web app still shows the setup wizard after your agent created a factory
[Section titled “The web app still shows the setup wizard after your agent created a factory”](#the-web-app-still-shows-the-setup-wizard-after-your-agent-created-a-factory)
**Cause:** Completing setup through [Factory MCP](/factories/factory-mcp/) doesn’t update a Warp Factories web app page that’s already open in your browser.
**Fix:** Refresh the page. Once your account has a factory, the web app opens it instead of the setup wizard. The factory link your agent shares at the end of setup opens the same place.
## Work isn’t starting
[Section titled “Work isn’t starting”](#work-isnt-starting)
### An event that should start work doesn’t
[Section titled “An event that should start work doesn’t”](#an-event-that-should-start-work-doesnt)
**Cause:** Nearly always an automation that doesn’t match the event, rather than a broken connection.
**Fix:**
1. Confirm the automation is enabled and its trigger’s event type matches what happened.
2. Check every filter on the trigger. Filters combine with AND, so a single mismatched repository, label, author, or state stops the routing. See [automation filters](/factories/automations/#troubleshooting).
3. Confirm the source is connected to *this* factory. Connecting a provider to your workspace doesn’t attach it to every factory in that workspace.
Then check the causes specific to where the work came from:
| Source | Common causes |
| ------------------------------------------------------------------------ | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| [Slack](/factories/integrations/slack/#troubleshooting-and-reconnection) | The app isn’t in the channel, installation is pending admin approval, or your Slack account isn’t linked to a Warp team member |
| [Microsoft Teams](/factories/integrations/teams/#troubleshooting) | The app isn’t added to the Teams team, the channel isn’t configured, the sender isn’t in the install’s Microsoft 365 organization, or your Microsoft account isn’t linked to Warp |
| [GitHub](/factories/integrations/github/#troubleshooting) | The app installation doesn’t cover the repository, or the factory’s routing label is missing |
| [GitLab](/factories/integrations/gitlab/#troubleshooting) | The mention was an edit rather than a new comment, or your plan doesn’t include the group webhooks that deliver events |
| [Linear](/factories/integrations/linear/#troubleshooting) | The agent session needs a linked Warp account, or teams and filters don’t match |
| [Jira](/factories/integrations/jira/#troubleshooting) | The Warp app isn’t connected to your workspace, or project and keyword filters don’t match |
| [Custom webhooks](/factories/webhooks/#troubleshooting) | The delivery was rejected or deduplicated (check the webhook’s **Recent deliveries**), no enabled automation selects the webhook, or the payload filter doesn’t match |
### One action starts two runs
[Section titled “One action starts two runs”](#one-action-starts-two-runs)
**Cause:** Two automations match the same event — commonly an app-mention trigger and a channel-message trigger pointed at the same place.
**Fix:** Narrow or remove one of the overlapping triggers so a single path owns each kind of request. See [how matching works](/factories/automations/#how-matching-works).
## Runs and work items
[Section titled “Runs and work items”](#runs-and-work-items)
### You need to stop a run
[Section titled “You need to stop a run”](#you-need-to-stop-a-run)
**Fix:** Open the run on the factory’s [Runs page](/factories/factory-dashboard/#inspect-runs) and click **Stop run**. It takes effect immediately, with no confirmation prompt.
### A work item looks stuck
[Section titled “A work item looks stuck”](#a-work-item-looks-stuck)
**Cause:** The factory is often waiting on a person rather than failing. By default it pauses for spec approval, for answers to clarifying questions, and at the pull request.
**Fix:**
1. Check your [inbox](/factories/factory-inbox/) for a question, spec review, or PR review tied to the work item.
2. Open the item to see which agent is waiting and use **View agent** to open its session, where a question waiting on a human is visible and answerable.
3. If the run is still active, you can steer it directly. See [cloud agent session sharing](/platform/viewing-cloud-agent-runs/).
### No pull request appears
[Section titled “No pull request appears”](#no-pull-request-appears)
**Cause:** The factory can’t push, or the work never reached the implement agent.
**Fix:** Confirm that the **Implement** agent is enabled on the factory, that the code host connection still grants write access to the target repository, and that the work item actually reached the Building stage. Branch protection rules apply to everything the factory pushes.
## Related pages
[Section titled “Related pages”](#related-pages)
* [**Warp Factories quickstart**](/factories/quickstart/) - Create a factory and submit your first work item.
* [**Connect your factory**](/factories/connect-your-factory/) - Route work in from Slack threads, Linear issues, and other intake paths.
* [**Automations**](/factories/automations/) - The matching rules that decide which events start work.
* [**Factory inbox**](/factories/factory-inbox/) - See and resolve the questions, spec approvals, and PR reviews waiting on you.
* [**Factory dashboard**](/factories/factory-dashboard/) - Where to watch work items, runs, and their outputs.
# Warp-hosted execution for Warp Factories
Canonical page: [/factories/warp-hosting/](https://docs.warp.dev/factories/warp-hosting/)
> Run factory work on Warp-hosted infrastructure, with managed compute, isolation, networking, and capacity.
Warp-hosted execution runs factory work in managed sandboxes. Warp provisions the compute while your factory definition selects each agent’s runner, repositories, setup, and credentials.
Use it when your factory’s repositories and services are reachable from the public internet and your team does not need to manage worker capacity or host maintenance. For private services or a network boundary that must contain checkout and execution, use [managed self-hosting](/factories/self-hosting/).
## Sandbox environment
[Section titled “Sandbox environment”](#sandbox-environment)
All Warp-hosted agents run in fully-isolated sandboxes. Warp uses a mix of infrastructure providers to ensure reliable sandbox startup.
### OS and architecture
[Section titled “OS and architecture”](#os-and-architecture)
Warp-hosted factory agents use the runner and workspace configuration in your [factory definition](/factories/factory-as-code/). A factory can also use an existing [environment](/platform/environments/) when its definition specifies one. They are compatible with any Linux x86-64 image that includes a `bash` shell and core utilities like `ls` and `mkdir`.
### Resources
[Section titled “Resources”](#resources)
The resources available to Warp-hosted agents depend on your [plan](https://www.warp.dev/pricing) - see the latest details there.
On [Enterprise](/enterprise/) plans, resources are configurable up to 32 vCPUs and 64 GiB of memory. If additional resources are required, reach out to Warp support about custom provisioning.
### Concurrency
[Section titled “Concurrency”](#concurrency)
To fairly allocate resources across all Warp users, concurrency of Warp-hosted agents is limited on a per-team basis. If an agent is started while at your concurrency limit, it is automatically queued and will start as soon as another agent completes.
### Networking
[Section titled “Networking”](#networking)
Warp’s hosted agents have network egress enabled by default. Outgoing requests may come from the following IP addresses:
* `64.6.38.192/26`
* `64.6.39.192/26`
* `104.128.70.192/26`
* `104.128.71.192/26`
* `216.176.224.192/26`
* `185.212.186.0/24`
* `50.31.178.128/26`
* `50.31.146.192/26`
* `75.102.37.208/28`
* `44.253.165.189/32`
* `16.145.188.113/32`
* `16.145.133.251/32`
***
## Related pages
[Section titled “Related pages”](#related-pages)
* [Automation Platform](/platform/overview/) - Configure the shared cloud-agent primitives behind a factory.
* [Factory runners](/factories/runners/) - Choose the operating system, architecture, and instance shape for factory work.
* [Managed self-hosting](/factories/self-hosting/) - Run factory work on infrastructure you manage when execution must stay inside your network.
# Triggering automations with custom webhooks
Canonical page: [/factories/webhooks/](https://docs.warp.dev/factories/webhooks/)
> Start factory runs from any system that can POST JSON: create a webhook, pick its authentication mode, and filter deliveries by payload.
A custom webhook gives your factory an HTTPS URL that any external system can POST JSON to: internal CI, Vercel, Stripe, Sentry, PagerDuty, or a homegrown tool. An [automation](/factories/automations/) subscribes to the webhook and starts a run when a delivery matches its filter, so tools Warp doesn’t integrate with directly can still start factory work.
## How custom webhooks work
[Section titled “How custom webhooks work”](#how-custom-webhooks-work)
A webhook is a factory resource with a name, an authentication mode, a secret, and an ingress URL that contains the webhook’s UID. When an external system sends an event to your webhook, Warp checks whether it matches any automation’s **Webhook** trigger and starts the corresponding runs.
```
flowchart LR
Sender["External system"] -->|"POST JSON"| URL["Webhook URL"]
URL --> Match["Automations with a<br/>matching Webhook trigger"]
Match --> Run["Factory run with the<br/>payload attached"]
```
Every delivery is recorded in the webhook’s delivery log, whether or not it starts a run. See [Delivery rules](#delivery-rules) for the request and response contract, and [Manage webhooks](#manage-webhooks) to review the log.
## Authentication modes
[Section titled “Authentication modes”](#authentication-modes)
Choose the mode that fits what the sender can do:
| Mode | Definition key | How the sender authenticates | Use it for |
| -------------------------- | -------------- | ------------------------------------------------------------------------------------------------------ | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Bearer token** (default) | `token` | Sends the Warp-generated secret in an `Authorization: Bearer` header | Senders that can set request headers: CI jobs, scripts, Grafana, Alertmanager |
| **URL token** | `url_token` | Posts to a URL that embeds the secret as a path segment | Senders that only take a URL and can’t set headers |
| **Provider signature** | `signature` | Signs each request with its own scheme; Warp verifies the signature with the provider’s signing secret | Vercel, Stripe, GitHub, Sentry, PagerDuty, and any sender that implements [Standard Webhooks](https://www.standardwebhooks.com/) (Svix-compatible headers are accepted) |
Warp generates the secret for bearer token and URL token webhooks and shows it once when you create the webhook. For a provider signature webhook, you supply the provider’s own signing secret instead — or leave it blank for a Standard Webhooks-compatible sender, and Warp generates one for you to give the sender. Vercel, Stripe, and PagerDuty only issue their secret after you give them a URL; leave the secret blank for those too, and Warp takes it in a second step. See [Setting up a Vercel webhook](/factories/webhooks/vercel/), which covers all three. See [Manage webhooks](#manage-webhooks) to rotate a secret or roll a webhook over.
A URL token webhook’s URL is itself the credential: treat it like a secret, and rotate it if it leaks.
## Setting up a webhook
[Section titled “Setting up a webhook”](#setting-up-a-webhook)
### Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **Permission to manage the factory** - Creating and editing webhooks changes the factory’s configuration.
### Create the webhook
[Section titled “Create the webhook”](#create-the-webhook)
1. In the factory dashboard, open **Automations** and switch to its **Webhooks** tab, then click **Add webhook**.
2. Enter a “Name” the automation editor will show, such as `Internal CI`.
3. In the “Authentication” dropdown, choose **Bearer token**, **URL token**, or **Provider signature**. For a provider signature, also choose the “Provider scheme” and paste the “Provider secret” from the provider. If the provider hasn’t issued a secret yet, leave “Provider secret” blank; see [Setting up a Vercel webhook](/factories/webhooks/vercel/).
4. Keep the suggested “Secret name”.
5. Optionally, enter a “Delivery ID header” if the sender stamps its own event ID into a header, and click **Create webhook**.
Note
On a Warp-managed factory, “Secret name” points at a [managed secret](/platform/secrets/) that stores the webhook’s credential. To reuse an existing team secret instead of creating a new one, enter its name in step 4.
The pane shows the ingress URL and the secret (for a URL token webhook, the token is part of the URL). Copy them now: Warp doesn’t show the secret again, and a URL token webhook’s URL later renders a `{token}` placeholder. If you referenced an existing secret, its value isn’t shown; configure the sender with the value you stored in it.
The Webhook created pane after creating a webhook.
### Configure the sender
[Section titled “Configure the sender”](#configure-the-sender)
Point the sender at the ingress URL and give it the credential for the webhook’s mode. For a bearer token webhook, confirm the webhook works before wiring up the real sender by posting a test delivery:
```bash
curl -X POST "https://app.warp.dev/webhooks/w/WEBHOOK_UID" \
-H "Authorization: Bearer WEBHOOK_SECRET" \
-H "Content-Type: application/json" \
-d '{"event": "deploy.finished", "env": "production", "service": "payments"}'
```
Replace `WEBHOOK_UID` and `WEBHOOK_SECRET` with the values you copied. For a URL token webhook, drop the `Authorization` header and post to the full URL you copied, which already carries the token. For a provider signature webhook, enter the ingress URL in the provider’s webhook settings (plus the signing secret, if Warp generated one for Standard Webhooks) and send a test event from the provider; an unsigned `curl` request returns `401`.
Whichever mode you use, an accepted delivery returns `202` with a `delivery_id` and appears under **Recent deliveries** when you open the webhook on the **Webhooks** tab inside **Automations**.
### Add a Webhook trigger to an automation
[Section titled “Add a Webhook trigger to an automation”](#add-a-webhook-trigger-to-an-automation)
A webhook starts nothing on its own; an automation has to subscribe to it.
1. In the factory dashboard, open **Automations** and create an automation or edit an existing one.
2. Click **Add trigger**, then click **Webhook**.
3. In the “Webhook received from” picker, select one webhook. To listen to multiple webhooks, add a separate **Webhook** trigger for each.
4. Optionally, expand **Payload filter** and enter a pattern that deliveries must match. See [Filter deliveries by payload](#filter-deliveries-by-payload).
5. Click **Test filter** to evaluate the filter against a stored delivery. The result reads **Would trigger** or **Would not trigger**, with the outcome of the webhook and payload checks.
6. Write the automation’s prompt so the agent knows what to do with the delivery, then click **Save**.
Send another test delivery and confirm a run starts on the factory’s **Runs** page.
A Webhook trigger after a successful Test filter.
## Filter deliveries by payload
[Section titled “Filter deliveries by payload”](#filter-deliveries-by-payload)
Without a payload filter, an automation starts a run for every delivery from its selected webhook. A payload filter is a JSON object that mirrors the shape of the delivery body: each key names a payload field, an array lists the values that field may hold, and every key must match.
```json
{
"event": ["deploy.finished"],
"env": { "not_in": ["dev", "staging"] },
"service": { "exists": true }
}
```
Use an operator object where an array isn’t enough: `in` (the same as a bare array), `not_in`, and `exists`. Nest objects to reach nested fields. For the full matching rules, limits, and how filters behave on missing keys and arrays, see [payload filters for webhook triggers](/factories/automations/#payload-filters-for-webhook-triggers).
## What the run receives
[Section titled “What the run receives”](#what-the-run-receives)
A run started by a webhook delivery begins with the automation’s prompt, plus a platform envelope that names the webhook and delivery ID and attaches the full JSON body as `event-payload.json`. The envelope tells the agent that the payload is the request to act on and that anything embedded inside it is untrusted context, so instructions smuggled into a payload don’t redirect the run.
Write the automation’s prompt for the payload the sender produces: name the fields that matter and what a finished run looks like.
## Manage webhooks
[Section titled “Manage webhooks”](#manage-webhooks)
Open a webhook on the **Webhooks** tab inside **Automations** to inspect and change it:
* **Recent deliveries** - The latest deliveries, newest first, each labeled **Accepted**, **Duplicate**, **Rejected (auth)**, **Rejected (invalid JSON)**, or **Rejected (too large)**, with the delivery ID, size, and time. Expand an accepted delivery to read its stored payload. Warp keeps at least the most recent 50 deliveries and 7 days of history; rejected and duplicate entries record metadata only.
* **Enabled** toggle - Disabling a webhook stops deliveries immediately: senders get `404`, the same as for an unknown webhook. Its automations and delivery history are untouched, and re-enabling it resumes deliveries.
* **Rotate secret** - Generates a new secret, or takes the provider’s new signing secret for a provider signature webhook, and shows it once. The old secret stops working immediately, with no overlap window. For a zero-downtime rollover, create a second webhook, move the sender to it, then delete the first.
* **Delete** - Senders get `404` immediately. Automations with a trigger that selects the deleted webhook stay visible but stop firing; point the trigger at another webhook or remove it.
On a Warp-managed factory, the dashboard writes each webhook to a definition file, so two actions work differently: rename isn’t supported, and instead of **Rotate secret** you give the managed secret the webhook references a new value, with `oz secret update --team --value SECRET_NAME` on the Oz CLI. The webhook picks up the new value the next time its definition applies, such as when you toggle **Enabled** off and on.
On a GitHub-backed factory, a managed secret’s new value takes effect the next time a change to the production branch applies.
## Delivery rules
[Section titled “Delivery rules”](#delivery-rules)
What a sender can expect from the webhook URL:
* **Request** - `POST` only, with a valid JSON body (an object, array, or scalar) of at most 256 KB. `Content-Type` isn’t enforced.
* **Responses** - `202` with `{"delivery_id": "..."}` when accepted; `401` when authentication fails; `400` when the body isn’t valid JSON; `404` when the webhook is unknown, disabled, or deleted; `413` when the body is too large; `429` with a `Retry-After` header when the sender exceeds 60 deliveries per minute. A `202` means the delivery was accepted for evaluation, not that an automation fired: a delivery that matches nothing is still accepted and logged.
* **Delivery identity** - Warp identifies each delivery, in order of preference, by the header you name in “Delivery ID header”, then the provider’s own delivery header for signed webhooks (such as GitHub’s `X-GitHub-Delivery`), then an `X-Warp-Delivery-Id` header the sender sets, then a hash of the body. A delivery whose identity was already accepted returns `202`, starts nothing, and appears in the log as a duplicate, so provider retries don’t start duplicate runs.
* **Ordering** - Deliveries are independent: there’s no ordering guarantee between them and no reply or thread continuation. Each accepted delivery starts new runs or nothing.
* **Limits** - Up to 20 webhooks per factory.
## Webhooks in definitions as code
[Section titled “Webhooks in definitions as code”](#webhooks-in-definitions-as-code)
In a [factory definition](/factories/factory-as-code/), each webhook is a `webhooks/<name>.yaml` file whose `secretName` points at a [managed secret](/platform/secrets/) you create first, and an automation subscribes with a `webhook` trigger:
webhooks/sentry-alerts.yaml
```yaml
authMode: signature
signatureScheme: sentry
secretName: SENTRY_WEBHOOK_SECRET
```
automations/sentry-fatal-errors/automation.md
```markdown
---
triggers:
- provider: webhook
event: received
filter:
webhook_ids: [WEBHOOK_UID]
payload:
action: [created]
data:
issue:
level: [fatal]
---
A new fatal issue was created in Sentry. Read the attached event payload,
find the failing code path, and open a pull request with a fix and a test.
```
`webhook_ids` takes a one-item list containing exactly one UID, not a file name. Warp assigns the UID when the webhook file first applies. Add the webhook, let the definition sync, then copy the UID from the webhook’s detail pane on the **Webhooks** tab. To listen to multiple webhooks, add a separate trigger for each UID. See [`webhooks/<name>.yaml`](/factories/factory-as-code/#webhooksnameyaml) for every key and its rules.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
* **The sender gets `401`** - The credential doesn’t match the webhook’s mode: a bearer token webhook needs the `Authorization: Bearer` header, a URL token webhook needs the token segment in the URL, and a provider signature webhook needs the provider’s current signing secret. After a rotation, update the sender with the new secret. A webhook whose managed secret you updated keeps the old value until its definition next applies; see [Manage webhooks](#manage-webhooks). Stripe and Standard Webhooks signatures older than five minutes are also rejected.
* **The sender gets `404`** - The webhook is disabled or deleted, or the UID in the URL is wrong. Enable it on the **Webhooks** tab inside **Automations** or check the URL against the webhook’s detail pane.
* **The sender gets `202` but no run starts** - Open the delivery under **Recent deliveries**. A **Duplicate** delivery reused an identity Warp already accepted; if the sender doesn’t set a delivery ID, identical bodies count as duplicates. For an **Accepted** delivery, confirm an enabled automation selects this webhook in its **Webhook** trigger, and use **Test filter** against the delivery to see which check failed.
* **The sender gets `429`** - The webhook exceeded 60 deliveries per minute. Retry after the interval in the `Retry-After` header. Failed authentication attempts count against a separate budget, so they can also produce `429` on their own.
* **Applying a definition fails on `webhooks/<name>.yaml`** - `secretName` must name an existing team secret, and a `url_token` secret must be URL-safe. See [`webhooks/<name>.yaml`](/factories/factory-as-code/#webhooksnameyaml).
## Related pages
[Section titled “Related pages”](#related-pages)
* [**Setting up a Vercel webhook**](/factories/webhooks/vercel/) - The two-step setup for providers that issue their signing secret only after they have a URL.
* [**Automations**](/factories/automations/) - How triggers and filters decide which events start work, including the payload filter grammar.
* [**Connect your factory**](/factories/connect-your-factory/) - Every way work reaches a factory, alongside custom webhooks.
* [**Definitions as code**](/factories/factory-as-code/) - The full schema for `webhooks/<name>.yaml` and webhook triggers.
* [**Cloud agent secrets**](/platform/secrets/) - Create and rotate the managed secrets that file-defined webhooks reference.
* [**Factory dashboard**](/factories/factory-dashboard/) - Where the **Automations** page and its **Webhooks** tab live.
# Setting up a Vercel webhook
Canonical page: [/factories/webhooks/vercel/](https://docs.warp.dev/factories/webhooks/vercel/)
> Start factory runs from Vercel deployments: create the webhook without a secret, register its URL in Vercel, then save the secret Vercel issues.
Vercel shows a webhook’s signing secret only after you save its URL, and Warp has a URL only once the webhook exists. To break the loop, create the webhook without a secret: Warp creates it disabled, gives you the URL, and takes the secret in a second step. Stripe and PagerDuty issue their secrets the same way, so the same steps work for them with **Stripe** or **PagerDuty** as the provider scheme.
Vercel team webhooks require a Vercel Pro or Enterprise plan.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **Permission to manage the factory** - Creating and editing webhooks changes the factory’s configuration.
* **The basics of custom webhooks** - Authentication modes, delivery rules, and how an automation subscribes to a webhook are covered in [Triggering automations with custom webhooks](/factories/webhooks/).
## Creating the webhook in the factory dashboard
[Section titled “Creating the webhook in the factory dashboard”](#creating-the-webhook-in-the-factory-dashboard)
1. In the factory dashboard, open **Automations** and switch to its **Webhooks** tab, click **Add webhook**, and enter a “Name” such as `Vercel deploys`.
2. In the “Authentication” dropdown, choose **Provider signature**, then in the “Provider scheme” dropdown, choose **Vercel**.
3. Leave “Provider secret” blank, keep the suggested “Secret name”, and click **Create and get URL**.
The pane’s title changes to “Finish webhook setup” and it shows the ingress URL. The webhook exists but is disabled, so it accepts no deliveries yet.
4. In the Vercel dashboard, go to your team’s **Settings** > **Webhooks**.
5. Under “Projects”, choose which projects send events, and under “Events”, select the events you want. Enter the ingress URL as the “Endpoint URL” and click **Create Webhook**. Vercel shows the webhook’s secret once.
6. In Warp, paste that secret into “Secret from Vercel” and click **Save and enable**.
The webhook is enabled and verifies the `x-vercel-signature` header on every delivery. Trigger a deployment and confirm it appears under **Recent deliveries** as **Accepted**, then [add a Webhook trigger to an automation](/factories/webhooks/#add-a-webhook-trigger-to-an-automation) so deliveries start runs.
### Finishing later
[Section titled “Finishing later”](#finishing-later)
Click **Finish later** to close the pane and leave the webhook disabled. Warp stored a placeholder in the webhook’s managed secret when it created the webhook. When you have the secret from Vercel, replace the placeholder from the Oz CLI; the command prompts for the value:
```bash
oz secret update --team --value VERCEL_DEPLOYS_WEBHOOK_SECRET
```
Then open the webhook on the **Webhooks** tab inside **Automations** and toggle **Enabled** on. Enabling it applies the webhook’s definition again, which reads the new value.
## Creating the webhook in a definition that lives in GitHub
[Section titled “Creating the webhook in a definition that lives in GitHub”](#creating-the-webhook-in-a-definition-that-lives-in-github)
A GitHub-backed factory has no dashboard editing, and a change applies only when it lands on the production branch. Order the steps so the change that enables the webhook is also the one that applies the secret:
1. On the team’s **Secrets** page, create a secret such as `VERCEL_WEBHOOK_SECRET` with a temporary placeholder value that isn’t used anywhere else. A webhook file must name a secret that already exists.
2. Add `webhooks/vercel.yaml` with the webhook disabled, and merge it to the production branch:
webhooks/vercel.yaml
```yaml
authMode: signature
signatureScheme: vercel
secretName: VERCEL_WEBHOOK_SECRET
enabled: false
```
Once the change applies, the webhook appears on the **Webhooks** tab inside **Automations** with its ingress URL.
3. Create the webhook in Vercel with that URL, as in steps 4 and 5 above, then replace the placeholder with the secret Vercel shows:
```bash
oz secret update --team --value VERCEL_WEBHOOK_SECRET
```
4. Change `enabled: false` to `enabled: true` and merge. Applying this change reads the new secret value and enables the webhook.
Creating the webhook with `enabled: true` from the start rejects every delivery with `401` until a later push to the production branch applies the updated secret.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
**Vercel deliveries get `401`**\
The secret Warp verifies with doesn’t match the one Vercel signs with: the placeholder is still in place, or you updated the secret but the webhook’s definition hasn’t applied since. Confirm the value against the webhook’s settings in Vercel, then toggle **Enabled** off and on in the factory dashboard, or on a GitHub-backed factory merge a change to the production branch.
## Related pages
[Section titled “Related pages”](#related-pages)
* [**Triggering automations with custom webhooks**](/factories/webhooks/) - Authentication modes, delivery rules, payload filters, and managing webhooks.
* [**Definitions as code**](/factories/factory-as-code/#webhooksnameyaml) - Every key in `webhooks/<name>.yaml`.
* [**Cloud agent secrets**](/platform/secrets/) - The managed secrets that webhooks reference, and the `oz secret` commands.
* [**Vercel webhooks**](https://vercel.com/docs/webhooks) - Vercel’s reference for webhook events and payloads.
# Keyboard Shortcuts
Canonical page: [/getting-started/keyboard-shortcuts/](https://docs.warp.dev/getting-started/keyboard-shortcuts/)
> View, customize, and remap keyboard shortcuts for all Warp features.
Warp opens with a shortcut screen showing some of the most commonly used keyboard shortcuts. Hide the shortcut screen by clicking the x button. Quickly view keyboard shortcuts via the [Command Palette](/terminal/command-palette/) or the Resource Center keyboard shortcut sidebar.
## Custom keyboard shortcuts
[Section titled “Custom keyboard shortcuts”](#custom-keyboard-shortcuts)
Set custom, clear, or default keyboard shortcuts by navigating to **Settings** > **Keyboard shortcuts**. Search through the re-mappable actions or existing shortcuts using the search bar.
Remap the keyboard shortcuts using a file. See our [keysets repository](https://github.com/warpdotdev/keysets/tree/main) for instructions.
Note
On macOS, [system keyboard shortcuts](https://support.apple.com/en-us/HT201236) like `⌘+Esc`, `` ⌘+` ``, `⌘+Tab`, `⌘+.`, and `⌘+~` need to be [unbound](https://support.apple.com/guide/mac-help/keyboard-shortcuts-mchlp2262/mac) before you can use them in Warp.
Caution
Keybinds that conflict with others are highlighted with an orange border.
An example of a keybinding conflict warning.
## All available shortcuts
[Section titled “All available shortcuts”](#all-available-shortcuts)
* macOS
**Warp Essentials**
| Shortcut | Command | Action |
| -------------- | ---------------------------- | ---------------------------------------------- |
| `⌘+D` | Split Pane Right | `pane_group:add_right` |
| `Ctrl+⌘+L` | Launch Configuration Palette | `workspace:toggle_launch_config_palette` |
| `Ctrl+⌘+T` | Open Theme Picker | `workspace:show_theme_chooser` |
| `Ctrl+R` | Command Search | `workspace:show_command_search` |
| `Ctrl+Shift+R` | Workflows | `input:toggle_workflows` |
| `` Ctrl+` `` | Generate | `input:toggle_natural_language_command_search` |
| `⌘+L` | Focus Terminal Input | `terminal:focus_input` |
| `Ctrl+I` | Warpify Subshell | `terminal:warpify_subshell` |
| `⌘+\` | Warp Drive | `workspace:toggle_warp_drive` |
| `⌘+O` | File search | |
| `⌘+P` | Open Command Palette | |
**Blocks**
| Shortcut | Command | Action |
| ------------------ | --------------------------------- | ------------------------------------------------------ |
| `Option+↓` | Select the Closest Bookmark Down | `terminal:select_bookmark_down` |
| `Option+Shift+⌘+C` | Copy Command Output | `terminal:copy_outputs` |
| `Option+↑` | Select the Closest Bookmark Up | `terminal:select_bookmark_up` |
| `⌘+A` | Select All Blocks | `terminal:select_all_blocks` |
| `⌘+K` | Clear Blocks | `terminal:clear_blocks` |
| `⌘+B` | Bookmark Selected Block | `terminal:bookmark_selected_block` |
| `⌘+↓` | Select Next Block | `terminal:select_next_block` |
| `⌘+I` | Reinput Selected Commands | `terminal:reinput_commands` |
| `⌘+↑` | Select Previous Block | `terminal:select_previous_block` |
| `Ctrl+M` | Open Block Context Menu | `terminal:open_block_list_context_menu_via_keybinding` |
| `Shift+⌘+C` | Copy Command | `terminal:copy_commands` |
| `Shift+⌘+I` | Reinput Selected Commands as Root | `terminal:reinput_commands_with_sudo` |
| `Shift+⌘+S` | Share Selected Block | `terminal:open_share_block_modal` |
| `Shift+↓` | Expand Selected Blocks Below | `terminal:expand_block_selection_below` |
| `Shift+↑` | Expand Selected Blocks Above | `terminal:expand_block_selection_above` |
**Scrolling**
| Shortcut | Command | Action |
| ----------- | ------------------------------------ | --------------------------------------------- |
| `Page Up` | Scroll Up One Page | `terminal:scroll_up_one_page` |
| `Page Down` | Scroll Down One Page | `terminal:scroll_down_one_page` |
| `Home` | Scroll to Top | |
| `End` | Scroll to Bottom | |
| `Shift+⌘+↑` | Scroll to Top of Selected Block | `terminal:scroll_to_top_of_selected_block` |
| `Shift+⌘+↓` | Scroll to Bottom of Selected Block | `terminal:scroll_to_bottom_of_selected_block` |
| | Scroll Terminal Output Up One Line | `terminal:scroll_up_one_line` |
| | Scroll Terminal Output Down One Line | `terminal:scroll_down_one_line` |
Note
“Scroll Terminal Output Up/Down One Line” has no default keybinding. You can assign one in **Settings** > **Keyboard shortcuts** or trigger it from the [Command Palette](/terminal/command-palette/). During long-running or full-screen commands, `Page Up`, `Page Down`, `Home`, and `End` are forwarded to the running program.
**Input Editor**
| Shortcut | Command | Action |
| ------------------ | ----------------------------------------- | ------------------------------------------ |
| `Option+Backspace` | Delete Word Left | `editor:delete_word_left` |
| `Option+⌘+F` | Fold Selected Ranges | `editor_view:fold_selected_ranges` |
| `Option+⌘+[` | Fold | `editor_view:fold` |
| `Option+⌘+]` | Unfold | `editor_view:unfold` |
| `Option+Delete` | Delete Word Right | `editor:delete_word_right` |
| `⌘+A` | Select All | `editor_view:select_all` |
| `⌘+Backspace` | Delete All Left | `editor_view:delete_all_left` |
| `⌘+Delete` | Delete All Right | `editor_view:delete_all_right` |
| `⌘+↓` | Move Cursor to the Bottom | `editor_view:cmd_down` |
| `⌘+I` | Inspect Command | `editor_view:inspect_command` |
| `⌘+←` | Home | `editor_view:home` |
| `⌘+→` | End | `editor_view:end` |
| `Ctrl+A` | Move to Start of Line | `editor_view:move_to_line_start` |
| `Ctrl+B` | Move Cursor Left | `editor_view:left` |
| `Ctrl+C` | Clear Command Editor | `editor_view:clear_buffer` |
| `Ctrl+D` | Delete | `editor_view:delete` |
| `Ctrl+E` | Move to End of Line | `editor_view:move_to_line_end` |
| `Ctrl+F` | Move Cursor Right / Accept Autosuggestion | `editor_view:right` |
| `Ctrl+G` | Add Selection for Next Occurrence | `editor_view:add_next_occurrence` |
| `Ctrl+H` | Remove the Previous Character | `editor_view:backspace` |
| `Ctrl+J` | Insert Newline | `editor_view:insert_newline` |
| `Ctrl+K` | Cut All Right | `editor_view:cut_all_right` |
| `Ctrl+L` | Clear Screen | `input:clear_screen` |
| `Ctrl+N` | Move Cursor Down | `editor_view:down` |
| `Ctrl+P` | Move Cursor Up | `editor_view:up` |
| `Ctrl+Shift+A` | Select to Start of Line | `editor_view:select_to_line_start` |
| `Ctrl+Shift+B` | Select One Character to the Left | `editor_view:select_left` |
| `Ctrl+Shift+↓` | Add Cursor Below | `editor_view:add_cursor_below` |
| `Ctrl+Shift+E` | Select to End of Line | `editor:select_to_line_end` |
| `⌘+Z` | Undo | |
| `⌘+Shift+Z` | Redo | |
| `Ctrl+Shift+F` | Select One Character to the Right | `editor_view:select_right` |
| `Ctrl+Shift+N` | Select Down | `editor_view:select_down` |
| `Ctrl+Shift+P` | Select Up | `editor_view:select_up` |
| `Ctrl+Shift+↑` | Add Cursor Above | `editor_view:add_cursor_above` |
| `Ctrl+U` | Copy and Clear Selected Lines | `editor_view:clear_and_copy_lines` |
| `Ctrl+W` | Cut Word Left | `editor_view:cut_word_left` |
| `Meta+.` | Insert Last Word of Previous Command | `editor:insert_last_word_previous_command` |
| `Meta+A` | Move to the Start of the Paragraph | `editor_view:move_to_paragraph_start` |
| `Meta+B` | Move Backward One Word | `editor_view:move_backward_one_word` |
| `Meta+D` | Cut Word Right | `editor_view:cut_word_right` |
| `Meta+E` | Move to the End of the Paragraph | `editor_view:move_to_paragraph_end` |
| `Meta+F` | Move Forward One Word | `editor_view:move_forward_one_word` |
| `Ctrl+Option+←` | Move Backward One Subword | `editor_view:move_backward_one_subword` |
| `Ctrl+Option+→` | Move Forward One Subword | `editor_view:move_forward_one_subword` |
| `Shift+⌘+K` | Clear Selected Lines | `editor_view:clear_lines` |
| `Shift+Meta+<` | Move to the Start of the Buffer | `editor_view:move_to_buffer_start` |
| `Shift+Meta+>` | Move to the End of the Buffer | `editor_view:move_to_buffer_end` |
| `Shift+Meta+B` | Select One Word to the Left | `editor_view:select_left_by_word` |
| `Shift+Meta+F` | Select One Word to the Right | `editor_view:select_right_by_word` |
**Terminal**
| Shortcut | Command | Action |
| --------------- | ------------------------------------------------- | -------------------------------------------- |
| `Option+⌘+↓` | Switch Panes Down | `pane_group:navigate_down` |
| `Option+⌘+←` | Switch Panes Left | `pane_group:navigate_left` |
| `Option+⌘+→` | Switch Panes Right | `pane_group:navigate_right` |
| `Option+⌘+↑` | Switch Panes Up | `pane_group:navigate_up` |
| `Option+⌘+V` | \[a11y] Set Concise Accessibility Announcements | `workspace:set_a11y_concise_verbosity_level` |
| `Option+⌘+V` | \[a11y] Set Verbose Accessibility Announcements | `workspace:set_a11y_verbose_verbosity_level` |
| `⌘+,` | Open Settings | `workspace:show_settings` |
| `⌘+,` | Open Settings: Account | `workspace:show_settings_account_page` |
| `⌘+G` | Find the Next Occurrence of Your Search Query | `find:find_next_occurrence` |
| `⌘+P` | Toggle Command Palette | `workspace:toggle_command_palette` |
| | Toggle Mouse Reporting | `workspace:toggle_mouse_reporting` |
| `⌘+[` | Activate Previous Pane | `pane_group:navigate_prev` |
| `⌘+]` | Activate Next Pane | `pane_group:navigate_next` |
| `Ctrl+⌘+↓` | Resize Pane > Move Divider Down | `pane_group:resize_down` |
| `Ctrl+⌘+K` | Open Keybindings Editor | `workspace:show_keybinding_settings` |
| `Ctrl+⌘+←` | Resize Pane > Move Divider Left | `pane_group:resize_left` |
| `Ctrl+⌘+→` | Resize Pane > Move Divider Right | `pane_group:resize_right` |
| `Ctrl+⌘+↑` | Resize Pane > Move Divider Up | `pane_group:resize_up` |
| `Ctrl+Shift+?` | Open Resource Center | `workspace:toggle_resource_center` |
| `Shift+⌘+D` | Split Pane Down | `pane_group:add_down` |
| `Shift+⌘+Enter` | Toggle Maximize Active Pane | `pane_group:toggle_maximize_pane` |
| `Shift+⌘+G` | Find the Previous Occurrence of Your Search Query | `find:find_prev_occurrence` |
| `Shift+⌘+P` | Toggle Navigation Palette | `workspace:toggle_navigation_palette` |
**Fundamentals**
| Shortcut | Command | Action |
| -------------- | -------------------------- | -------------------------------- |
| `⌘+-` | Decrease Font Size | `workspace:decrease_font_size` |
| `⌘+0` | Reset Font Size to Default | `workspace:reset_font_size` |
| `⌘+1` | Switch to 1st Tab | `workspace:activate_first_tab` |
| `⌘+2` | Switch to 2nd Tab | `workspace:activate_second_tab` |
| `⌘+3` | Switch to 3rd Tab | `workspace:activate_third_tab` |
| `⌘+4` | Switch to 4th Tab | `workspace:activate_fourth_tab` |
| `⌘+5` | Switch to 5th Tab | `workspace:activate_fifth_tab` |
| `⌘+6` | Switch to 6th Tab | `workspace:activate_sixth_tab` |
| `⌘+7` | Switch to 7th Tab | `workspace:activate_seventh_tab` |
| `⌘+8` | Switch to 8th Tab | `workspace:activate_eighth_tab` |
| `⌘+9` | Switch to Last Tab | `workspace:activate_last_tab` |
| `⌘+=` | Increase Font Size | `workspace:increase_font_size` |
| `⌘+C` | Copy | `terminal:copy` |
| `⌘+F` | Find | `terminal:find` |
| `⌘+V` | Paste | `terminal:paste` |
| `⌘+T` | Open New Tab | `workspace:new_tab` |
| `Shift+⌘+T` | Reopen Closed Tab | `app:reopen_closed_session` |
| `Ctrl+Shift+←` | Move Tab Left | `workspace:move_tab_left` |
| `Ctrl+Shift+→` | Move Tab Right | `workspace:move_tab_right` |
| `Shift+⌘+{` | Activate Previous Tab | `workspace:activate_prev_tab` |
| `Shift+⌘+}` | Activate Next Tab | `workspace:activate_next_tab` |
* Windows
**Warp Essentials**
| Shortcut | Command | Action |
| -------------- | ---------------------------- | ---------------------------------------------- |
| `Ctrl+Shift+D` | Split Pane Right | `pane_group:add_right` |
| | Launch Configuration Palette | `workspace:toggle_launch_config_palette` |
| | Open Theme Picker | `workspace:show_theme_chooser` |
| `Ctrl+R` | Command Search | `workspace:show_command_search` |
| `Ctrl+Shift+R` | Workflows | `input:toggle_workflows` |
| `` Ctrl+` `` | Generate | `input:toggle_natural_language_command_search` |
| `Ctrl+Shift+L` | Focus Terminal Input | `terminal:focus_input` |
| `Ctrl+I` | Warpify Subshell | `terminal:warpify_subshell` |
| `Ctrl+Shift+\` | Warp Drive | `workspace:toggle_warp_drive` |
**Blocks**
| Shortcut | Command | Action |
| ------------------ | --------------------------------- | ------------------------------------------------------ |
| `Alt+↓` | Select the Closest Bookmark Down | `terminal:select_bookmark_down` |
| `Ctrl+Shift+Alt+C` | Copy Command Output | `terminal:copy_outputs` |
| `Alt+↑` | Select the Closest Bookmark Up | `terminal:select_bookmark_up` |
| `Ctrl+Shift+A` | Select All Blocks | `terminal:select_all_blocks` |
| `Ctrl+Shift+K` | Clear Blocks | `terminal:clear_blocks` |
| `Ctrl+Shift+B` | Bookmark Selected Block | `terminal:bookmark_selected_block` |
| `Ctrl+↓` | Select Next Block | `terminal:select_next_block` |
| `Ctrl+Shift+I` | Reinput Selected Commands | `terminal:reinput_commands` |
| `Ctrl+↑` | Select Previous Block | `terminal:select_previous_block` |
| | Open Block Context Menu | `terminal:open_block_list_context_menu_via_keybinding` |
| `Ctrl+Shift+C` | Copy Command | `terminal:copy_commands` |
| | Reinput Selected Commands as Root | `terminal:reinput_commands_with_sudo` |
| `Ctrl+Shift+S` | Share Selected Block | `terminal:open_share_block_modal` |
| `Shift+↓` | Expand Selected Blocks Below | `terminal:expand_block_selection_below` |
| `Shift+↑` | Expand Selected Blocks Above | `terminal:expand_block_selection_above` |
**Scrolling**
| Shortcut | Command | Action |
| -------------- | ------------------------------------ | --------------------------------------------- |
| `Page Up` | Scroll Up One Page | `terminal:scroll_up_one_page` |
| `Page Down` | Scroll Down One Page | `terminal:scroll_down_one_page` |
| `Home` | Scroll to Top | |
| `End` | Scroll to Bottom | |
| `Ctrl+Shift+↑` | Scroll to Top of Selected Block | `terminal:scroll_to_top_of_selected_block` |
| `Ctrl+Shift+↓` | Scroll to Bottom of Selected Block | `terminal:scroll_to_bottom_of_selected_block` |
| | Scroll Terminal Output Up One Line | `terminal:scroll_up_one_line` |
| | Scroll Terminal Output Down One Line | `terminal:scroll_down_one_line` |
Note
“Scroll Terminal Output Up/Down One Line” has no default keybinding. You can assign one in **Settings** > **Keyboard shortcuts** or trigger it from the [Command Palette](/terminal/command-palette/). During long-running or full-screen commands, `Page Up`, `Page Down`, `Home`, and `End` are forwarded to the running program.
**Input Editor**
| Shortcut | Command | Action |
| ---------------- | ----------------------------------------- | ------------------------------------------ |
| `Ctrl+Backspace` | Delete Word Left | `editor:delete_word_left` |
| `Ctrl+Alt+F` | Fold Selected Ranges | `editor_view:fold_selected_ranges` |
| `Ctrl+Alt+[` | Fold | `editor_view:fold` |
| `Ctrl+Alt+]` | Unfold | `editor_view:unfold` |
| `Ctrl+Delete` | Delete Word Right | `editor:delete_word_right` |
| `Ctrl+A` | Select All | `editor_view:select_all` |
| `Ctrl+Y` | Delete All Left | `editor_view:delete_all_left` |
| | Delete All Right | `editor_view:delete_all_right` |
| `Ctrl+End` | Move Cursor to the Bottom | `editor_view:cmd_down` |
| `Ctrl+I` | Inspect Command | `editor_view:inspect_command` |
| `Home` | Home | `editor_view:home` |
| `End` | End | `editor_view:end` |
| `Ctrl+A` | Move to Start of Line | `editor_view:move_to_line_start` |
| `Ctrl+B` | Move Cursor Left | `editor_view:left` |
| `Ctrl+C` | Clear Command Editor | `editor_view:clear_buffer` |
| `Ctrl+D` | Delete | `editor_view:delete` |
| `Ctrl+E` | Move to End of Line | `editor_view:move_to_line_end` |
| `Ctrl+F` | Move Cursor Right / Accept Autosuggestion | `editor_view:right` |
| `Ctrl+G` | Add Selection for Next Occurrence | `editor_view:add_next_occurrence` |
| `Ctrl+H` | Remove the Previous Character | `editor_view:backspace` |
| `Ctrl+J` | Insert Newline | `editor_view:insert_newline` |
| `Ctrl+K` | Cut All Right | `editor_view:cut_all_right` |
| `Ctrl+L` | Clear Screen | `input:clear_screen` |
| `Ctrl+N` | Move Cursor Down | `editor_view:down` |
| `Ctrl+P` | Move Cursor Up | `editor_view:up` |
| | Select to Start of Line | `editor_view:select_to_line_start` |
| `Ctrl+Shift+B` | Select One Character to the Left | `editor_view:select_left` |
| `Ctrl+Shift+↓` | Add Cursor Below | `editor_view:add_cursor_below` |
| | Select to End of Line | `editor:select_to_line_end` |
| `Ctrl+Z` | Undo | |
| `Ctrl+Shift+Z` | Redo | |
| `Ctrl+Shift+F` | Select One Character to the Right | `editor_view:select_right` |
| | Select Down | `editor_view:select_down` |
| `Ctrl+Shift+P` | Select Up | `editor_view:select_up` |
| `Ctrl+Shift+↑` | Add Cursor Above | `editor_view:add_cursor_above` |
| `Ctrl+U` | Copy and Clear Selected Lines | `editor_view:clear_and_copy_lines` |
| `Ctrl+W` | Cut Word Left | `editor_view:cut_word_left` |
| `Meta+.` | Insert Last Word of Previous Command | `editor:insert_last_word_previous_command` |
| `Meta+A` | Move to the Start of the Paragraph | `editor_view:move_to_paragraph_start` |
| `Ctrl+←` | Move Backward One Word | `editor_view:move_backward_one_word` |
| `Alt+D` | Cut Word Right | `editor_view:cut_word_right` |
| `Meta+E` | Move to the End of the Paragraph | `editor_view:move_to_paragraph_end` |
| `Ctrl+→` | Move Forward One Word | `editor_view:move_forward_one_word` |
| `Ctrl+Alt+←` | Move Backward One Subword | `editor_view:move_backward_one_subword` |
| `Ctrl+Alt+→` | Move Forward One Subword | `editor_view:move_forward_one_subword` |
| `Shift+Meta+<` | Move to the Start of the Buffer | `editor_view:move_to_buffer_start` |
| `Shift+Meta+>` | Move to the End of the Buffer | `editor_view:move_to_buffer_end` |
| `Ctrl+Shift+←` | Select One Word to the Left | `editor_view:select_left_by_word` |
| `Ctrl+Shift+→` | Select One Word to the Right | `editor_view:select_right_by_word` |
**Terminal**
| Shortcut | Command | Action |
| ------------------ | ------------------------------------------------- | -------------------------------------------- |
| `Ctrl+Alt+↓` | Switch Panes Down | `pane_group:navigate_down` |
| `Ctrl+Alt+←` | Switch Panes Left | `pane_group:navigate_left` |
| `Ctrl+Alt+→` | Switch Panes Right | `pane_group:navigate_right` |
| `Ctrl+Alt+↑` | Switch Panes Up | `pane_group:navigate_up` |
| `Ctrl+Alt+V` | \[a11y] Set Concise Accessibility Announcements | `workspace:set_a11y_concise_verbosity_level` |
| `Ctrl+Alt+V` | \[a11y] Set Verbose Accessibility Announcements | `workspace:set_a11y_verbose_verbosity_level` |
| `Ctrl+,` | Open Settings | `workspace:show_settings` |
| `Ctrl+,` | Open Settings: Account | `workspace:show_settings_account_page` |
| `F3` | Find the Next Occurrence of Your Search Query | `find:find_next_occurrence` |
| `Ctrl+Shift+P` | Toggle Command Palette | `workspace:toggle_command_palette` |
| | Toggle Mouse Reporting | `workspace:toggle_mouse_reporting` |
| `Ctrl+Shift+[` | Activate Previous Pane | `pane_group:navigate_prev` |
| `Ctrl+Shift+]` | Activate Next Pane | `pane_group:navigate_next` |
| | Resize Pane > Move Divider Down | `pane_group:resize_down` |
| `Ctrl+⌘+K` | Open Keybindings Editor | `workspace:show_keybinding_settings` |
| | Resize Pane > Move Divider Left | `pane_group:resize_left` |
| | Resize Pane > Move Divider Right | `pane_group:resize_right` |
| | Resize Pane > Move Divider Up | `pane_group:resize_up` |
| `Ctrl+Shift+/` | Open Resource Center | `workspace:toggle_resource_center` |
| `Ctrl+Shift+E` | Split Pane Down | `pane_group:add_down` |
| `Ctrl+Shift+Enter` | Toggle Maximize Active Pane | `pane_group:toggle_maximize_pane` |
| `Shift+F3` | Find the Previous Occurrence of Your Search Query | `find:find_prev_occurrence` |
| | Toggle Navigation Palette | `workspace:toggle_navigation_palette` |
**Fundamentals**
| Shortcut | Command | Action |
| ---------------- | -------------------------- | -------------------------------- |
| `Ctrl+-` | Decrease Font Size | `workspace:decrease_font_size` |
| `Ctrl+0` | Reset Font Size to Default | `workspace:reset_font_size` |
| `Ctrl+1` | Switch to 1st Tab | `workspace:activate_first_tab` |
| `Ctrl+2` | Switch to 2nd Tab | `workspace:activate_second_tab` |
| `Ctrl+3` | Switch to 3rd Tab | `workspace:activate_third_tab` |
| `Ctrl+4` | Switch to 4th Tab | `workspace:activate_fourth_tab` |
| `Ctrl+5` | Switch to 5th Tab | `workspace:activate_fifth_tab` |
| `Ctrl+6` | Switch to 6th Tab | `workspace:activate_sixth_tab` |
| `Ctrl+7` | Switch to 7th Tab | `workspace:activate_seventh_tab` |
| `Ctrl+8` | Switch to 8th Tab | `workspace:activate_eighth_tab` |
| `Ctrl+9` | Switch to Last Tab | `workspace:activate_last_tab` |
| `Ctrl+=` | Increase Font Size | `workspace:increase_font_size` |
| `Ctrl+Shift+C` | Copy | `terminal:copy` |
| `Ctrl+Shift+F` | Find | `terminal:find` |
| `Ctrl+Shift+V` | Paste | `terminal:paste` |
| `Ctrl+Shift+T` | Open New Tab | `workspace:new_tab` |
| `Ctrl+Alt+T` | Reopen Closed Tab | `app:reopen_closed_session` |
| `Ctrl+Shift+←` | Move Tab Left | `workspace:move_tab_left` |
| `Ctrl+Shift+→` | Move Tab Right | `workspace:move_tab_right` |
| `Ctrl+Page Up` | Activate Previous Tab | `workspace:activate_prev_tab` |
| `Ctrl+Page Down` | Activate Next Tab | `workspace:activate_next_tab` |
* Linux
**Warp Essentials**
| Shortcut | Command | Action |
| -------------- | ---------------------------- | ---------------------------------------------- |
| `Ctrl+Shift+D` | Split Pane Right | `pane_group:add_right` |
| | Launch Configuration Palette | `workspace:toggle_launch_config_palette` |
| | Open Theme Picker | `workspace:show_theme_chooser` |
| `Ctrl+R` | Command Search | `workspace:show_command_search` |
| `Ctrl+Shift+R` | Workflows | `input:toggle_workflows` |
| `` Ctrl+` `` | Generate | `input:toggle_natural_language_command_search` |
| `Ctrl+Shift+L` | Focus Terminal Input | `terminal:focus_input` |
| `Ctrl+I` | Warpify Subshell | `terminal:warpify_subshell` |
| `Ctrl+Shift+\` | Warp Drive | `workspace:toggle_warp_drive` |
**Blocks**
| Shortcut | Command | Action |
| ------------------ | --------------------------------- | ------------------------------------------------------ |
| `Alt+↓` | Select the Closest Bookmark Down | `terminal:select_bookmark_down` |
| `Ctrl+Shift+Alt+C` | Copy Command Output | `terminal:copy_outputs` |
| `Alt+↑` | Select the Closest Bookmark Up | `terminal:select_bookmark_up` |
| `Ctrl+Shift+A` | Select All Blocks | `terminal:select_all_blocks` |
| `Ctrl+Shift+K` | Clear Blocks | `terminal:clear_blocks` |
| `Ctrl+Shift+B` | Bookmark Selected Block | `terminal:bookmark_selected_block` |
| `Ctrl+↓` | Select Next Block | `terminal:select_next_block` |
| `Ctrl+Shift+I` | Reinput Selected Commands | `terminal:reinput_commands` |
| `Ctrl+↑` | Select Previous Block | `terminal:select_previous_block` |
| | Open Block Context Menu | `terminal:open_block_list_context_menu_via_keybinding` |
| `Ctrl+Shift+C` | Copy Command | `terminal:copy_commands` |
| | Reinput Selected Commands as Root | `terminal:reinput_commands_with_sudo` |
| `Ctrl+Shift+S` | Share Selected Block | `terminal:open_share_block_modal` |
| `Shift+↓` | Expand Selected Blocks Below | `terminal:expand_block_selection_below` |
| `Shift+↑` | Expand Selected Blocks Above | `terminal:expand_block_selection_above` |
**Scrolling**
| Shortcut | Command | Action |
| -------------- | ------------------------------------ | --------------------------------------------- |
| `Page Up` | Scroll Up One Page | `terminal:scroll_up_one_page` |
| `Page Down` | Scroll Down One Page | `terminal:scroll_down_one_page` |
| `Home` | Scroll to Top | |
| `End` | Scroll to Bottom | |
| `Ctrl+Shift+↑` | Scroll to Top of Selected Block | `terminal:scroll_to_top_of_selected_block` |
| `Ctrl+Shift+↓` | Scroll to Bottom of Selected Block | `terminal:scroll_to_bottom_of_selected_block` |
| | Scroll Terminal Output Up One Line | `terminal:scroll_up_one_line` |
| | Scroll Terminal Output Down One Line | `terminal:scroll_down_one_line` |
Note
“Scroll Terminal Output Up/Down One Line” has no default keybinding. You can assign one in **Settings** > **Keyboard shortcuts** or trigger it from the [Command Palette](/terminal/command-palette/). During long-running or full-screen commands, `Page Up`, `Page Down`, `Home`, and `End` are forwarded to the running program.
**Input Editor**
| Shortcut | Command | Action |
| ---------------- | ----------------------------------------- | ------------------------------------------ |
| `Ctrl+Backspace` | Delete Word Left | `editor:delete_word_left` |
| `Ctrl+Alt+F` | Fold Selected Ranges | `editor_view:fold_selected_ranges` |
| `Ctrl+Alt+[` | Fold | `editor_view:fold` |
| `Ctrl+Alt+]` | Unfold | `editor_view:unfold` |
| `Ctrl+Delete` | Delete Word Right | `editor:delete_word_right` |
| `Ctrl+A` | Select All | `editor_view:select_all` |
| `Ctrl+Y` | Delete All Left | `editor_view:delete_all_left` |
| | Delete All Right | `editor_view:delete_all_right` |
| `Ctrl+End` | Move Cursor to the Bottom | `editor_view:cmd_down` |
| `Ctrl+I` | Inspect Command | `editor_view:inspect_command` |
| `Home` | Home | `editor_view:home` |
| `End` | End | `editor_view:end` |
| `Ctrl+A` | Move to Start of Line | `editor_view:move_to_line_start` |
| `Ctrl+B` | Move Cursor Left | `editor_view:left` |
| `Ctrl+C` | Clear Command Editor | `editor_view:clear_buffer` |
| `Ctrl+D` | Delete | `editor_view:delete` |
| `Ctrl+E` | Move to End of Line | `editor_view:move_to_line_end` |
| `Ctrl+F` | Move Cursor Right / Accept Autosuggestion | `editor_view:right` |
| `Ctrl+G` | Add Selection for Next Occurrence | `editor_view:add_next_occurrence` |
| `Ctrl+H` | Remove the Previous Character | `editor_view:backspace` |
| `Ctrl+J` | Insert Newline | `editor_view:insert_newline` |
| `Ctrl+K` | Cut All Right | `editor_view:cut_all_right` |
| `Ctrl+L` | Clear Screen | `input:clear_screen` |
| `Ctrl+N` | Move Cursor Down | `editor_view:down` |
| `Ctrl+P` | Move Cursor Up | `editor_view:up` |
| | Select to Start of Line | `editor_view:select_to_line_start` |
| `Ctrl+Shift+B` | Select One Character to the Left | `editor_view:select_left` |
| `Ctrl+Shift+↓` | Add Cursor Below | `editor_view:add_cursor_below` |
| | Select to End of Line | `editor:select_to_line_end` |
| `Ctrl+Z` | Undo | |
| `Ctrl+Shift+Z` | Redo | |
| `Ctrl+Shift+F` | Select One Character to the Right | `editor_view:select_right` |
| | Select Down | `editor_view:select_down` |
| `Ctrl+Shift+P` | Select Up | `editor_view:select_up` |
| `Ctrl+Shift+↑` | Add Cursor Above | `editor_view:add_cursor_above` |
| `Ctrl+U` | Copy and Clear Selected Lines | `editor_view:clear_and_copy_lines` |
| `Ctrl+W` | Cut Word Left | `editor_view:cut_word_left` |
| `Meta+.` | Insert Last Word of Previous Command | `editor:insert_last_word_previous_command` |
| `Meta+A` | Move to the Start of the Paragraph | `editor_view:move_to_paragraph_start` |
| `Ctrl+←` | Move Backward One Word | `editor_view:move_backward_one_word` |
| `Alt+D` | Cut Word Right | `editor_view:cut_word_right` |
| `Meta+E` | Move to the End of the Paragraph | `editor_view:move_to_paragraph_end` |
| `Ctrl+→` | Move Forward One Word | `editor_view:move_forward_one_word` |
| `Ctrl+Alt+←` | Move Backward One Subword | `editor_view:move_backward_one_subword` |
| `Ctrl+Alt+→` | Move Forward One Subword | `editor_view:move_forward_one_subword` |
| `Shift+Meta+<` | Move to the Start of the Buffer | `editor_view:move_to_buffer_start` |
| `Shift+Meta+>` | Move to the End of the Buffer | `editor_view:move_to_buffer_end` |
| `Ctrl+Shift+←` | Select One Word to the Left | `editor_view:select_left_by_word` |
| `Ctrl+Shift+→` | Select One Word to the Right | `editor_view:select_right_by_word` |
**Terminal**
| Shortcut | Command | Action |
| ------------------ | ------------------------------------------------- | -------------------------------------------- |
| `Ctrl+Alt+↓` | Switch Panes Down | `pane_group:navigate_down` |
| `Ctrl+Alt+←` | Switch Panes Left | `pane_group:navigate_left` |
| `Ctrl+Alt+→` | Switch Panes Right | `pane_group:navigate_right` |
| `Ctrl+Alt+↑` | Switch Panes Up | `pane_group:navigate_up` |
| `Ctrl+Alt+V` | \[a11y] Set Concise Accessibility Announcements | `workspace:set_a11y_concise_verbosity_level` |
| `Ctrl+Alt+V` | \[a11y] Set Verbose Accessibility Announcements | `workspace:set_a11y_verbose_verbosity_level` |
| `Ctrl+,` | Open Settings | `workspace:show_settings` |
| `Ctrl+,` | Open Settings: Account | `workspace:show_settings_account_page` |
| `F3` | Find the Next Occurrence of Your Search Query | `find:find_next_occurrence` |
| `Ctrl+Shift+P` | Toggle Command Palette | `workspace:toggle_command_palette` |
| | Toggle Mouse Reporting | `workspace:toggle_mouse_reporting` |
| `Ctrl+Shift+[` | Activate Previous Pane | `pane_group:navigate_prev` |
| `Ctrl+Shift+]` | Activate Next Pane | `pane_group:navigate_next` |
| | Resize Pane > Move Divider Down | `pane_group:resize_down` |
| `Ctrl+⌘+K` | Open Keybindings Editor | `workspace:show_keybinding_settings` |
| | Resize Pane > Move Divider Left | `pane_group:resize_left` |
| | Resize Pane > Move Divider Right | `pane_group:resize_right` |
| | Resize Pane > Move Divider Up | `pane_group:resize_up` |
| `Ctrl+Shift+/` | Open Resource Center | `workspace:toggle_resource_center` |
| `Ctrl+Shift+E` | Split Pane Down | `pane_group:add_down` |
| `Ctrl+Shift+Enter` | Toggle Maximize Active Pane | `pane_group:toggle_maximize_pane` |
| `Shift+F3` | Find the Previous Occurrence of Your Search Query | `find:find_prev_occurrence` |
| | Toggle Navigation Palette | `workspace:toggle_navigation_palette` |
**Fundamentals**
| Shortcut | Command | Action |
| ---------------- | -------------------------- | -------------------------------- |
| `Ctrl+-` | Decrease Font Size | `workspace:decrease_font_size` |
| `Ctrl+0` | Reset Font Size to Default | `workspace:reset_font_size` |
| `Ctrl+1` | Switch to 1st Tab | `workspace:activate_first_tab` |
| `Ctrl+2` | Switch to 2nd Tab | `workspace:activate_second_tab` |
| `Ctrl+3` | Switch to 3rd Tab | `workspace:activate_third_tab` |
| `Ctrl+4` | Switch to 4th Tab | `workspace:activate_fourth_tab` |
| `Ctrl+5` | Switch to 5th Tab | `workspace:activate_fifth_tab` |
| `Ctrl+6` | Switch to 6th Tab | `workspace:activate_sixth_tab` |
| `Ctrl+7` | Switch to 7th Tab | `workspace:activate_seventh_tab` |
| `Ctrl+8` | Switch to 8th Tab | `workspace:activate_eighth_tab` |
| `Ctrl+9` | Switch to Last Tab | `workspace:activate_last_tab` |
| `Ctrl+=` | Increase Font Size | `workspace:increase_font_size` |
| `Ctrl+Shift+C` | Copy | `terminal:copy` |
| `Ctrl+Shift+F` | Find | `terminal:find` |
| `Ctrl+Shift+V` | Paste | `terminal:paste` |
| `Ctrl+Shift+T` | Open New Tab | `workspace:new_tab` |
| `Ctrl+Alt+T` | Reopen Closed Tab | `app:reopen_closed_session` |
| `Ctrl+Shift+←` | Move Tab Left | `workspace:move_tab_left` |
| `Ctrl+Shift+→` | Move Tab Right | `workspace:move_tab_right` |
| `Ctrl+Page Up` | Activate Previous Tab | `workspace:activate_prev_tab` |
| `Ctrl+Page Down` | Activate Next Tab | `workspace:activate_next_tab` |
# Migrate to Warp
Canonical page: [/getting-started/migrate-to-warp/](https://docs.warp.dev/getting-started/migrate-to-warp/)
> Move your settings and mental model into Warp. Pick the tool you're coming from for step-by-step guidance and Warp equivalents.
Warp users come from every kind of terminal, editor, and AI coding tool. This section has a dedicated page for each of the most common sources, with step-by-step migration guidance, notes on what transfers automatically, and a cross-reference for the Warp features that replace what you use today.
If you want to preserve your existing keyboard workflow while switching tools, compare Warp’s default [keyboard shortcuts](/getting-started/keyboard-shortcuts/) with the migration guide for your current terminal or editor.
Pick the tool you’re switching from:
* [**Claude Code**](/getting-started/migrate-to-warp/migrate-to-warp-from-claude-code/) - use Claude Code inside Warp, or switch from Claude Code to Warp’s built-in Agent Mode. Covers context, rules, and model setup.
* [**Cursor**](/getting-started/migrate-to-warp/migrate-to-warp-from-cursor/) - use Warp alongside Cursor as your agent terminal, or replace Cursor entirely with Warp’s built-in code editor and Agent Mode.
* [**Ghostty**](/getting-started/migrate-to-warp/migrate-to-warp-from-ghostty/) - translate your Ghostty config to Warp and find equivalents for quick terminal, tabs, and GPU rendering.
* [**iTerm2**](/getting-started/migrate-to-warp/migrate-to-warp-from-iterm2/) - use Warp’s built-in iTerm2 importer to transfer themes, fonts, keybindings, and hotkey windows in a few clicks.
* [**macOS Terminal**](/getting-started/migrate-to-warp/migrate-to-warp-from-macos-terminal/) - match your Terminal.app setup and discover the split panes, tabs, and Agent Mode features Terminal.app lacks.
* [**VS Code terminal**](/getting-started/migrate-to-warp/migrate-to-warp-from-vs-code-terminal/) - use Warp alongside VS Code for a richer terminal, or replace VS Code entirely with Warp’s built-in code editor.
* [**Windows Terminal**](/getting-started/migrate-to-warp/migrate-to-warp-from-windows-terminal/) - map Windows Terminal profiles, PowerShell settings, and color schemes into Warp on Windows.
## Coming from something else?
[Section titled “Coming from something else?”](#coming-from-something-else)
Warp works well for developers migrating from many other sources. If you’re switching from a tool that isn’t listed above - for example, Ghostty, Alacritty, WezTerm, Kitty, Hyper, or a Linux default like GNOME Terminal or Konsole - drop a note in our [Warp community Slack](https://go.warp.dev/join-preview) so we can prioritize coverage.
# Migrate to Warp from Claude Code
Canonical page: [/getting-started/migrate-to-warp/migrate-to-warp-from-claude-code/](https://docs.warp.dev/getting-started/migrate-to-warp/migrate-to-warp-from-claude-code/)
> Keep using Claude Code in Warp — with rich input, code review, and notifications — or switch from Claude Code to Warp's Agent Mode as your primary coding agent.
Claude Code is different from the other sources in this section: it’s not a terminal emulator, it’s a CLI agent that runs inside any terminal. Warp is an agentic development environment with a built-in [code editor](/code/code-editor/), [Code Review](/code/code-review/), [team collaboration](/knowledge-and-collaboration/warp-drive/), and [MCP](/agents/capabilities/mcp/) support — so you have two paths to choose from:
* **[Using Claude Code inside Warp](#using-claude-code-inside-warp)** - you want to keep using Claude Code as your coding agent and run it in Warp’s terminal.
* **[Switching to Agent Mode from Claude Code](#switching-to-agent-mode-from-claude-code)** - you want to replace Claude Code with Warp’s built-in [Agent Mode](/agents/).
## Using Claude Code inside Warp
[Section titled “Using Claude Code inside Warp”](#using-claude-code-inside-warp)
Warp provides first-class support for Claude Code through its [third-party CLI agents](/agents/cli-agents/overview/) integration. Open a new tab and run:
```bash
claude
```
Warp auto-detects Claude Code and unlocks IDE-level features on top of the TUI:
* **[Rich input editor](/agents/cli-agents/rich-input/)** (`Ctrl+G`) - compose multi-line prompts with `@` mentions, voice input, and slash commands.
* **[Agent notifications](/agents/capabilities/agent-notifications/)** - in-app and desktop alerts when Claude Code needs your input. Requires a one-time plugin install (Warp prompts you).
* **Inline code review** - send review comments directly to the agent from Warp’s [Code Review](/code/code-review/) panel.
* **[Vertical tabs with agent metadata](/terminal/windows/vertical-tabs/)** - track multiple Claude Code sessions across tabs with status indicators.
* **[Remote control](/agents/cli-agents/remote-control/)** - share or steer a Claude Code session from another device.
* **[Tab Configs](/terminal/windows/tab-configs/)** - save and reopen Claude Code session layouts.
For full setup steps (notification plugin, productivity tips, troubleshooting), see [Claude Code in Warp](/agents/cli-agents/claude-code/) and the [How to set up Claude Code](/guides/external-tools/how-to-set-up-claude-code/) guide.
### Tips
[Section titled “Tips”](#tips)
* **Run Claude Code in [terminal mode](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/)**, not Agent Mode. Press `⌘+I` (macOS) or `Ctrl+I` (Linux/Windows) to toggle modes if you’re in Agent Mode by accident.
* **`Shift+Enter` for newlines.** Use `Shift+Enter` to insert a newline in Claude Code’s prompt. If it submits the message instead, check that you’re in terminal mode (not Agent Mode) and that you’re on a recent Warp version.
* **Copy/paste handling.** Warp enables bracketed paste by default, so multi-line pastes into Claude Code work without extra configuration.
* **Resuming after a Warp restart.** Warp’s [session restoration](/terminal/sessions/session-restoration/) preserves tabs and panes, but not running CLI processes — closing Warp ends Claude Code’s session. Use Claude Code’s built-in resume options (e.g., `claude --resume`) to continue a conversation after reopening Warp.
### API keys and authentication
[Section titled “API keys and authentication”](#api-keys-and-authentication)
Claude Code’s authentication (API key or Anthropic account) is handled by Claude Code itself, not Warp. Warp does not proxy or modify Claude Code’s network calls. Configure your `ANTHROPIC_API_KEY` environment variable via [Warp Drive environment variables](/knowledge-and-collaboration/warp-drive/environment-variables/) to share it across sessions without committing it to shell config files.
## Switching to Agent Mode from Claude Code
[Section titled “Switching to Agent Mode from Claude Code”](#switching-to-agent-mode-from-claude-code)
If you’re ready to replace Claude Code with Warp’s built-in Agent, the core workflow is:
1. Open a new tab in Warp.
2. From terminal mode, press `⌘+Enter` (macOS) or `Ctrl+Shift+Enter` (Linux/Windows) to switch to [Agent Mode](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/).
3. Describe what you want in natural language.
Warp’s Agent reads your codebase, runs commands, and edits files the same way Claude Code does.
### What transfers: context and rules
[Section titled “What transfers: context and rules”](#what-transfers-context-and-rules)
A recurring question from Claude Code users: **what files and context does Warp’s Agent read automatically?** Warp picks up project rules from an `AGENTS.md` (or `WARP.md`) at your repo root — the direct equivalent of Claude Code’s `CLAUDE.md`. Run `/init` in Agent Mode to generate one, or rename your existing rules file and you’re done — no rewriting needed.
Warp’s Agent also pulls context from several other explicit sources:
* **[Codebase Context](/agents/capabilities/codebase-context/)** - when you open a directory, Warp indexes your Git-tracked files so the Agent can search and reference your code without you pasting snippets.
* **[Rules](/agents/capabilities/rules/)** - global and project-scoped rules. `AGENTS.md` and `WARP.md` are automatically picked up at the project root; additional rules live in Warp Drive.
* **[Warp Drive](/knowledge-and-collaboration/warp-drive/)** - notebooks, workflows, and environment variables you’ve saved are available to the Agent as context.
* **[Agent Mode context](/knowledge-and-collaboration/warp-drive/agent-mode-context/)** - pin specific files or notebooks to a conversation so the Agent always has them in scope.
* **[MCP](/agents/capabilities/mcp/)** - any MCP servers you’ve configured give the Agent access to external tools and data.
### What to reconfigure
[Section titled “What to reconfigure”](#what-to-reconfigure)
* **Bring over your `CLAUDE.md`.** Rename it to `AGENTS.md` (or copy it into a Warp [Rule](/agents/capabilities/rules/) if you want it scoped beyond the repo). Warp applies it automatically to new conversations.
* **Set up [MCP servers](/agents/capabilities/mcp/)** you relied on in Claude Code.
* **Pick a model** per conversation using the model selector. See [model choice](/agents/inference/model-choice/). Warp supports Claude, GPT, Gemini, and Auto.
* **Configure [agent profiles and permissions](/agents/capabilities/agent-profiles-permissions/)** for what the Agent can auto-execute.
### Key differences from Claude Code
[Section titled “Key differences from Claude Code”](#key-differences-from-claude-code)
* **Tight terminal integration.** Agent Mode runs inside Warp and sees the full state of your terminal session — open files, command history, environment variables — without needing you to paste context.
* **Parallel agents.** Warp runs multiple agent conversations across tabs simultaneously, each with its own state, which you can track in the Agent Management Panel.
* **Code Review built in.** Agent-generated diffs open in Warp’s [Code Review](/code/code-review/) panel, not the terminal.
* **Cloud orchestration.** Long-running or scheduled agent work can be offloaded to the [Automation Platform](/platform/).
## Warp-native equivalents
[Section titled “Warp-native equivalents”](#warp-native-equivalents)
Use this table to find the closest Warp equivalent for Claude Code concepts:
| From Claude Code | In Warp |
| ----------------------------- | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `CLAUDE.md` | `AGENTS.md` (or `WARP.md`) at the project root, picked up as a [Rule](/agents/capabilities/rules/) |
| Claude Code slash commands | Warp’s own [slash commands](/agents/capabilities/slash-commands/) (`/init`, `/plan`, `/model`, etc.); save your own as [Warp Drive prompts](/knowledge-and-collaboration/warp-drive/prompts/) |
| Tool definitions | [MCP](/agents/capabilities/mcp/) |
| Skills (`.claude/skills/`) | [Skills](/agents/capabilities/skills/); Warp discovers `.claude/skills/` as-is, alongside `.agents/skills/` and the other supported directories |
| Subagents (`.claude/agents/`) | [Multi-agent orchestration](/platform/orchestration/); use [factory agents](/factories/factory-agents/) for named agents with standing configuration |
| Resume conversation | Warp persists agent conversations per tab; pair with [tab configs](/terminal/windows/tab-configs/) to reopen the same project layout |
For a deeper tour of Agent Mode, see [Coding in Warp](/getting-started/quickstart/coding-in-warp/) and the [Agents overview](/agents/).
# Migrate to Warp from Cursor
Canonical page: [/getting-started/migrate-to-warp/migrate-to-warp-from-cursor/](https://docs.warp.dev/getting-started/migrate-to-warp/migrate-to-warp-from-cursor/)
> Reconfigure your terminal and agent settings when switching to Warp from Cursor, or run Warp alongside Cursor as your agent terminal.
Warp gives Cursor users two migration paths: keep Cursor as your editor and use Warp for terminal and Agent work, or move fully to Warp’s built-in code editor and Agent Mode. This page walks through both options.
## What Warp can help transfer
[Section titled “What Warp can help transfer”](#what-warp-can-help-transfer)
Warp doesn’t have a one-click Cursor importer. Cursor is built on the VS Code codebase, so its terminal settings live in `settings.json` under keys like `terminal.integrated.fontFamily` and `terminal.integrated.defaultProfile.*`. Because that file is readable, Warp’s Agent can translate matching terminal values into Warp’s `settings.toml`. In Cursor, open the Command Palette and select **Preferences: Open User Settings (JSON)** to reference your settings while you reconfigure Warp.
## Use Warp’s Agent to migrate your settings (recommended)
[Section titled “Use Warp’s Agent to migrate your settings (recommended)”](#use-warps-agent-to-migrate-your-settings-recommended)
The fastest way to bring over your Cursor terminal setup is to ask Warp’s Agent to translate your `settings.json` directly. Warp ships a [`settings.toml` file](/terminal/settings/) and a bundled `modify-settings` skill that lets the Agent read your existing config and write equivalent values into Warp’s settings.
1. In the Warp app, open a new tab and switch to [Agent Mode](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/) with `⌘+I` (macOS) or `Ctrl+I` (Linux/Windows).
2. Copy and paste this prompt into the Agent Mode input, then press `Enter`.
> Read my Cursor `settings.json` (`~/Library/Application Support/Cursor/User/settings.json` on macOS) and port the equivalent terminal settings (font, cursor style, default profile) into my Warp `settings.toml` using the `modify-settings` skill. Show me a diff before applying.
3. Review the proposed diff, then approve the changes. Warp hot-reloads `settings.toml`, so changes take effect immediately.
If you’d rather configure each setting manually through the Settings UI, the steps below cover the most common cases.
## What to reconfigure manually
[Section titled “What to reconfigure manually”](#what-to-reconfigure-manually)
### Terminal settings
[Section titled “Terminal settings”](#terminal-settings)
Terminal settings in Cursor follow the same schema as VS Code. The migration steps are identical to the VS Code terminal migration. See [Migrate to Warp from VS Code terminal](/getting-started/migrate-to-warp/migrate-to-warp-from-vs-code-terminal/) for step-by-step guidance on shell, font, theme, and keybinding setup.
### Agent and AI settings
[Section titled “Agent and AI settings”](#agent-and-ai-settings)
Cursor’s Composer and Agent features don’t have a one-to-one migration path; they map to different Warp concepts.
* **Composer / Agent** - In Cursor, these features map to Warp’s [Agent Mode](/agents/). Start an Agent conversation in any tab.
* **Rules files** - Warp uses [Rules](/agents/capabilities/rules/) stored in Warp Drive or committed to your repo as `AGENTS.md` (or `WARP.md`). Run `/init` in Agent Mode to generate an `AGENTS.md`, or copy your `.cursorrules` content directly.
* **MCP servers** - Warp supports MCP natively. See [MCP](/agents/capabilities/mcp/) for configuration.
### Model choice
[Section titled “Model choice”](#model-choice)
Cursor lets you pick a model per conversation. Warp does the same; use the model selector in any Agent conversation. See [model choice](/agents/inference/model-choice/).
### Keybindings
[Section titled “Keybindings”](#keybindings)
Warp’s [keyboard shortcuts](/getting-started/keyboard-shortcuts/) differ from Cursor’s. Most notably, `⌘+I` (or `Ctrl+I` on Linux/Windows) toggles between terminal and Agent Mode. From terminal mode you can also press `⌘+Enter` (or `Ctrl+Shift+Enter`) as an alternate shortcut into Agent Mode.
## Choosing your setup
[Section titled “Choosing your setup”](#choosing-your-setup)
### Use Warp alongside Cursor
[Section titled “Use Warp alongside Cursor”](#use-warp-alongside-cursor)
Keep Cursor as your editor for tight in-file AI assistance, and use Warp as the terminal you switch to for:
* Long-running commands and SSH.
* [Agent Mode](/agents/) conversations that execute commands, not just edit files.
* [Code Review](/code/code-review/) for managing diffs.
* [Warp Drive](/knowledge-and-collaboration/warp-drive/) for team knowledge.
### Replace Cursor with Warp
[Section titled “Replace Cursor with Warp”](#replace-cursor-with-warp)
Warp’s built-in [code editor](/code/code-editor/) supports Language Server Protocol, a [file tree](/code/code-editor/file-tree/), [find and replace](/code/code-editor/find-and-replace/), and [Vim keybindings](/code/code-editor/code-editor-vim-keybindings/). Combined with Agent Mode, Code Review, and Warp Drive, the full Cursor workflow is reachable in Warp without a separate editor.
## Warp-native equivalents
[Section titled “Warp-native equivalents”](#warp-native-equivalents)
Use this table to find Warp equivalents for Cursor features you might look for after switching:
| From Cursor | In Warp |
| ----------------------------- | --------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Composer / Agent panel | [Agent Mode](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/) in any tab (toggle with `⌘+I` on macOS or `Ctrl+I` on Linux/Windows) |
| Agent tabs | Multiple [agents in parallel](/agents/) across tabs |
| `.cursorrules` | `AGENTS.md` / `WARP.md` at the project root, picked up as a [Rule](/agents/capabilities/rules/) |
| MCP servers | [MCP](/agents/capabilities/mcp/) |
| Model choice per conversation | [Model selector](/agents/inference/model-choice/) |
| Codebase indexing | [Codebase Context](/agents/capabilities/codebase-context/) |
| Inline diff review | [Code Review](/code/code-review/) |
See [Coding in Warp](/getting-started/quickstart/coding-in-warp/) for a tour of the development workflow.
# Migrate to Warp from Ghostty
Canonical page: [/getting-started/migrate-to-warp/migrate-to-warp-from-ghostty/](https://docs.warp.dev/getting-started/migrate-to-warp/migrate-to-warp-from-ghostty/)
> Moving to Warp from Ghostty? Here's how to bring over your themes, fonts, and keybindings, plus where to find Warp's equivalents for Ghostty's native features.
Warp gives Ghostty users a fast path to bring over themes, fonts, and keybindings, plus native equivalents for the Ghostty features you rely on, from the quick terminal to native tabs and splits.
## What Warp can help transfer
[Section titled “What Warp can help transfer”](#what-warp-can-help-transfer)
Warp doesn’t have a one-click Ghostty importer. Because Ghostty stores its configuration in a plain-text key-value file at `~/.config/ghostty/config`, Warp’s Agent can read that file and translate matching values into Warp’s `settings.toml`.
## Use Warp’s Agent to migrate your settings (recommended)
[Section titled “Use Warp’s Agent to migrate your settings (recommended)”](#use-warps-agent-to-migrate-your-settings-recommended)
The fastest way to bring over your Ghostty setup is to ask Warp’s Agent to translate your config directly. Warp ships a [`settings.toml` file](/terminal/settings/) and a bundled `modify-settings` skill that lets the Agent read your existing config and write equivalent values into Warp’s settings, including translating your Ghostty theme into a Warp [custom theme](/terminal/appearance/custom-themes/).
1. In the Warp app, open a new tab and switch to [Agent Mode](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/) with `⌘+I` (macOS) or `Ctrl+I` (Linux/Windows).
2. Paste this prompt into Agent Mode, then press `Enter`.
> Read my Ghostty config at `~/.config/ghostty/config` and any referenced theme files in `~/.config/ghostty/themes/`. Port the equivalent settings (theme, font, keybindings, shell) into my Warp `settings.toml` using the `modify-settings` skill, and create a matching custom theme. Show me a diff before applying.
3. Review the proposed diff, then approve the changes. Warp hot-reloads `settings.toml`, so changes take effect immediately.
If you’d rather configure each setting manually through the Settings UI, the steps below cover the most common cases.
## What to reconfigure manually
[Section titled “What to reconfigure manually”](#what-to-reconfigure-manually)
### Theme and colors
[Section titled “Theme and colors”](#theme-and-colors)
1. In the Warp app, open **Settings** > **Appearance** > **Themes**.
2. Choose a built-in theme that matches your Ghostty setup, or [create a custom theme](/terminal/appearance/custom-themes/) by translating your Ghostty colors into a YAML theme file.
3. If your Ghostty config references a custom theme, open the matching file in `~/.config/ghostty/themes/` and copy the foreground, background, and 16 ANSI color values.
### Font and text
[Section titled “Font and text”](#font-and-text)
1. In the Warp app, open **Settings** > **Appearance** > **Text, fonts, & cursor** and match your Ghostty `font-family` and `font-size` values.
2. If you use font ligatures, toggle **Ligatures** on.
### Keybindings
[Section titled “Keybindings”](#keybindings)
Warp’s [default keyboard shortcuts](/getting-started/keyboard-shortcuts/) cover most Ghostty bindings. For custom bindings from your Ghostty `keybind` lines, open **Settings** > **Keyboard shortcuts** in the Warp app and add them manually.
### Shell and prompt
[Section titled “Shell and prompt”](#shell-and-prompt)
Warp detects your login shell automatically. To override it, open **Settings** > **Features** > **Session** in the Warp app and choose a shell from **Startup shell for new sessions**.
For prompts, choose between Warp’s [native prompt](/terminal/appearance/prompt/#warp-prompt) (drag-and-drop context chips) or the [shell prompt (PS1)](/terminal/appearance/prompt/#shell-prompt-ps1) if you want to keep your existing prompt configuration.
### Quick terminal (Quake mode)
[Section titled “Quick terminal (Quake mode)”](#quick-terminal-quake-mode)
In the Warp app, configure Warp’s equivalent from **Settings** > **Features** > **Window** > **Global hotkey**. See [global hotkey](/terminal/windows/global-hotkey/) for the full configuration.
## Warp-native equivalents
[Section titled “Warp-native equivalents”](#warp-native-equivalents)
Use this table to find the closest Warp equivalent for Ghostty features you might look for after switching:
| From Ghostty | In Warp |
| --------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Quick terminal / dropdown window | [Global hotkey](/terminal/windows/global-hotkey/) |
| Native tabs and splits | [Tabs](/terminal/windows/tabs/), [vertical tabs](/terminal/windows/vertical-tabs/), [split panes](/terminal/windows/split-panes/) |
| Command palette | [Command Palette](/terminal/command-palette/) (`⌘+P` on macOS, `Ctrl+Shift+P` on Linux/Windows) |
| GPU-accelerated rendering | GPU-rendered natively on all supported platforms |
| Kitty graphics protocol | Image rendering for most common workflows (see [more features](/terminal/more-features/)) |
| Shaders and custom visual effects | Not supported; closest: [size, opacity, and blurring](/terminal/appearance/size-opacity-blurring/) + [pane dimming](/terminal/appearance/pane-dimming/) |
Beyond parity, Warp adds [Agent Mode](/agents/), [Code Review](/code/code-review/), and [Warp Drive](/knowledge-and-collaboration/warp-drive/) for AI-assisted development and team collaboration.
For more on what you can configure, see [Customizing Warp](/getting-started/quickstart/customizing-warp/).
# Migrate to Warp from iTerm2
Canonical page: [/getting-started/migrate-to-warp/migrate-to-warp-from-iterm2/](https://docs.warp.dev/getting-started/migrate-to-warp/migrate-to-warp-from-iterm2/)
> Import your iTerm2 profile into Warp to transfer themes, fonts, keybindings, hotkey windows, and more in a few clicks.
Warp imports your iTerm2 profile automatically, bringing over theme, font, keybindings, hotkey window, and more in a few clicks. This page walks through the importer, what it covers, and what to reconfigure manually after.
## What transfers automatically
[Section titled “What transfers automatically”](#what-transfers-automatically)
Warp ships a built-in iTerm2 importer that reads your default profile from `~/Library/Preferences/com.googlecode.iterm2.plist`. It imports:
* **Theme** - foreground, background, cursor, and all 16 ANSI colors (light and dark variants if configured).
* **Font** - family and size (when the font exists on your system and is supported by Warp).
* **Default shell** - if you’ve set a custom Command in your iTerm2 profile.
* **Working directory behavior** - Warp translates iTerm2’s “Reuse previous session’s directory” and similar options.
* **Window dimensions** - rows and columns.
* **Opacity and blur.**
* **Copy-on-select, mouse and scroll reporting, and Option-as-Meta settings.**
* **Global hotkey** - if you use a hotkey window or hotkey activation, Warp maps it.
To run the importer:
1. In Warp, open the [Command Palette](/terminal/command-palette/).
2. Search for **Import External Settings**.
3. Select **iTerm2 Profile: Default**. Warp only imports the profile marked as your Default Bookmark in iTerm2.
4. Choose which settings to keep or skip on the preview screen.
Select a settings profile to import.
## Use Warp’s Agent for follow-up settings
[Section titled “Use Warp’s Agent for follow-up settings”](#use-warps-agent-for-follow-up-settings)
If the importer doesn’t pick up something you care about, such as a non-default profile, an unusual keybinding, or a specific setting, ask Warp’s Agent to translate it directly. Warp ships a [`settings.toml` file](/terminal/settings/) and a bundled `modify-settings` skill that lets the Agent read your iTerm2 plist and write equivalent values into Warp’s settings.
1. In the Warp app, switch to [Agent Mode](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/) with `⌘+I`.
2. Paste this prompt into Agent Mode, then press `Enter`.
> Read my iTerm2 preferences with `defaults read com.googlecode.iterm2` and port any settings that the importer didn’t cover (extra profiles, custom keybindings) into my Warp `settings.toml` using the `modify-settings` skill. Show me a diff before applying.
3. Review the proposed diff, then approve the changes. Warp hot-reloads `settings.toml`.
## What to reconfigure manually
[Section titled “What to reconfigure manually”](#what-to-reconfigure-manually)
A few iTerm2 features don’t map directly and need a manual pass after import:
* **Multiple profiles.** Warp imports only your Default profile. If you rely on multiple iTerm2 profiles, create equivalent [tab configs](/terminal/windows/tab-configs/) in Warp.
* **Keyboard shortcuts.** Warp’s [keyboard shortcuts](/getting-started/keyboard-shortcuts/) cover most iTerm2 bindings out of the box, but custom bindings need to be recreated in **Settings** > **Keyboard shortcuts**.
* **Split panes and arrangements.** Rebuild using [split panes](/terminal/windows/split-panes/) and [tab configs](/terminal/windows/tab-configs/).
* **Triggers.** Warp doesn’t have a direct equivalent. Reach similar outcomes through [YAML workflows](/terminal/entry/yaml-workflows/) or Agent Mode.
### Choose your prompt
[Section titled “Choose your prompt”](#choose-your-prompt)
After the import, choose which [prompt](/terminal/appearance/prompt/) to use:
1. [**Warp prompt**](/terminal/appearance/prompt/#warp-prompt) - Warp’s native prompt with drag-and-drop context chips for git branch, directory, timestamps, and more. Configure in **Settings** > **Appearance** > **Prompt**.
2. [**Shell prompt (PS1)**](/terminal/appearance/prompt/#shell-prompt-ps1) - inherits your existing shell prompt configuration unchanged. Pick this if you want Warp to match your iTerm2 prompt exactly.
## Warp-native equivalents
[Section titled “Warp-native equivalents”](#warp-native-equivalents)
Use this table to find Warp equivalents for iTerm2 features you might look for after switching:
| From iTerm2 | In Warp |
| ---------------------------- | ---------------------------------------------------------------------------------------------------------------------------------------- |
| Hotkey window (Quake mode) | [Global hotkey](/terminal/windows/global-hotkey/) (imported automatically when detected in your iTerm2 profile) |
| Triggers | [YAML workflows](/terminal/entry/yaml-workflows/) for repeatable actions; Agent Mode for pattern-based automation |
| Profiles | [Tab configs](/terminal/windows/tab-configs/) for layouts; [Warp Drive](/knowledge-and-collaboration/warp-drive/) for shared team setups |
| Autocomplete menu | [Autosuggestions](/terminal/command-completions/autosuggestions/) + [tab completions](/terminal/command-completions/completions/) |
| Instant replay | [Session restoration](/terminal/sessions/session-restoration/) |
| Password manager integration | [Warp Drive environment variables](/knowledge-and-collaboration/warp-drive/environment-variables/) |
For more on what you can configure after migrating, see the [Warp quickstart](/quickstart/) and [Customizing Warp](/getting-started/quickstart/customizing-warp/).
# Migrate to Warp from macOS Terminal
Canonical page: [/getting-started/migrate-to-warp/migrate-to-warp-from-macos-terminal/](https://docs.warp.dev/getting-started/migrate-to-warp/migrate-to-warp-from-macos-terminal/)
> Switch from the default macOS Terminal app to Warp. Match your setup and discover what Warp adds beyond the basics.
Warp gives Terminal.app users everything they already have, including shell, theme, font, and prompt settings, plus split panes, tabs, blocks, and Agent Mode for an AI-assisted workflow. This page walks through both an Agent-driven migration and the manual GUI steps.
## What Warp can help transfer
[Section titled “What Warp can help transfer”](#what-warp-can-help-transfer)
Warp doesn’t have a one-click Terminal.app importer. Because Terminal.app stores profile data in macOS preferences, Warp’s Agent can read those preferences with `defaults read com.apple.Terminal` and translate matching theme, font, and window settings into Warp’s `settings.toml`. Most Terminal.app users run near-default settings, so the migration usually takes only a few minutes either way.
## Use Warp’s Agent to migrate your settings (recommended)
[Section titled “Use Warp’s Agent to migrate your settings (recommended)”](#use-warps-agent-to-migrate-your-settings-recommended)
The fastest way to bring over a Terminal.app theme is to ask Warp’s Agent to translate it directly. Warp ships a [`settings.toml` file](/terminal/settings/) and a bundled `modify-settings` skill that lets the Agent read your Terminal.app preferences and write equivalent values into Warp’s settings, including creating a matching [custom theme](/terminal/appearance/custom-themes/).
1. In the Warp app, open a new tab and switch to [Agent Mode](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/) with `⌘+I`.
2. Paste this prompt into Agent Mode, then press `Enter`.
> Read my Terminal.app preferences with `defaults read com.apple.Terminal` and port the active profile (theme, font, window size) into my Warp `settings.toml` using the `modify-settings` skill. Create a matching custom theme. Show me a diff before applying.
3. Review the proposed diff, then approve the changes. Warp hot-reloads `settings.toml`.
If you’d rather configure each setting manually through the Settings UI, the steps below cover the most common cases.
## What to reconfigure manually
[Section titled “What to reconfigure manually”](#what-to-reconfigure-manually)
### Shell
[Section titled “Shell”](#shell)
Warp auto-detects your login shell on first launch. macOS has shipped with `zsh` as the default since Catalina (2019); if you changed your shell with `chsh`, Warp picks that up too.
To change it later, open **Settings** > **Features** > **Session** in the Warp app and choose a shell from **Startup shell for new sessions**.
### Theme and colors
[Section titled “Theme and colors”](#theme-and-colors)
Terminal.app ships with a handful of profiles (Basic, Pro, Homebrew, Ocean, etc.). Match them in Warp:
1. In the Warp app, open **Settings** > **Appearance** > **Themes**.
2. Choose a preset theme. Warp’s built-in library includes many themes similar to Terminal.app’s defaults.
3. For exact color matches, [create a custom theme](/terminal/appearance/custom-themes/) using ANSI color values from Terminal.app. In Terminal.app, open **Settings**, select **Profiles**, and click **Text** to inspect those values.
### Font
[Section titled “Font”](#font)
1. In the Warp app, open **Settings** > **Appearance** > **Text, fonts, & cursor**, then choose your font family and size to match what you use in Terminal.app.
### Window size and transparency
[Section titled “Window size and transparency”](#window-size-and-transparency)
Configure window appearance in the Warp app from **Settings** > **Appearance** > **Size, opacity, & blurring**. See [size, opacity, and blurring](/terminal/appearance/size-opacity-blurring/).
### Prompt
[Section titled “Prompt”](#prompt)
Terminal.app uses whatever prompt your shell’s PS1 (or zsh’s PROMPT) defines. In Warp, choose:
1. [**Warp prompt**](/terminal/appearance/prompt/#warp-prompt) - Warp’s native prompt with drag-and-drop chips for git branch, directory, and more.
2. [**Shell prompt (PS1)**](/terminal/appearance/prompt/#shell-prompt-ps1) - keeps your existing shell prompt exactly as it appears in Terminal.app.
Configure either prompt in the Warp app from **Settings** > **Appearance** > **Prompt**.
## Warp-native equivalents
[Section titled “Warp-native equivalents”](#warp-native-equivalents)
Most Terminal.app features have a Warp equivalent with additional capabilities on top:
| From Terminal.app | In Warp |
| ---------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Profiles | [Tab configs](/terminal/windows/tab-configs/) for layouts and startup commands; [themes](/terminal/appearance/themes/) for appearance (Warp has no single profile object) |
| Window groups / arrangements | [Tab configs](/terminal/windows/tab-configs/) |
| Tabs | [Tabs](/terminal/windows/tabs/), [vertical tabs](/terminal/windows/vertical-tabs/) |
| Split panes | [Split panes](/terminal/windows/split-panes/) (Terminal.app doesn’t support) |
| Copy-on-select | **Settings** > **Features** > **Session** |
| Inspector | [Command inspector](/terminal/editor/command-inspector/) (exit code, duration, working directory) |
Beyond matching Terminal.app, Warp adds [Agent Mode](/agents/) for natural-language commands, [blocks](/terminal/blocks/) for structured command output, and [Warp Drive](/knowledge-and-collaboration/warp-drive/) for shared workflows. New to Warp? Start with the [Warp quickstart](/quickstart/).
# Migrate to Warp from VS Code terminal
Canonical page: [/getting-started/migrate-to-warp/migrate-to-warp-from-vs-code-terminal/](https://docs.warp.dev/getting-started/migrate-to-warp/migrate-to-warp-from-vs-code-terminal/)
> Replicate your VS Code integrated terminal setup in Warp - shell, fonts, keybindings - or run Warp alongside VS Code as a richer terminal.
Warp lets VS Code users choose their own path: keep VS Code for editing and run Warp as the terminal alongside it, or replace both with Warp’s built-in code editor. This page walks through reconfiguring your terminal settings for either path.
## What Warp can help transfer
[Section titled “What Warp can help transfer”](#what-warp-can-help-transfer)
Warp doesn’t have a VS Code importer because it’s a standalone application, not a VS Code extension. Because your VS Code terminal settings live in a readable user `settings.json`, Warp’s Agent can translate matching `terminal.integrated.*` values into Warp’s `settings.toml`:
```json
{
"terminal.integrated.defaultProfile.osx": "zsh",
"terminal.integrated.fontFamily": "MesloLGS NF",
"terminal.integrated.fontSize": 14,
"terminal.integrated.cursorStyle": "line",
"terminal.integrated.profiles.osx": {
"zsh": {
"path": "zsh"
}
}
}
```
## Use Warp’s Agent to migrate your settings (recommended)
[Section titled “Use Warp’s Agent to migrate your settings (recommended)”](#use-warps-agent-to-migrate-your-settings-recommended)
The fastest way to bring over your VS Code terminal setup is to ask Warp’s Agent to translate `settings.json` directly. Warp ships a [`settings.toml` file](/terminal/settings/) and a bundled `modify-settings` skill that lets the Agent read your existing config and write equivalent values into Warp’s settings.
1. In the Warp app, open a new tab and switch to [Agent Mode](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/) with `⌘+I` (macOS) or `Ctrl+I` (Linux/Windows).
2. Paste this prompt into Agent Mode, then press `Enter`.
> Read my VS Code `settings.json` (`~/Library/Application Support/Code/User/settings.json` on macOS) and port the equivalent terminal settings (`terminal.integrated.*` keys) into my Warp `settings.toml` using the `modify-settings` skill. Show me a diff before applying.
3. Review the proposed diff, then approve the changes. Warp hot-reloads `settings.toml`.
If you’d rather configure each setting manually through the Settings UI, the steps below cover the most common cases.
## What to reconfigure manually
[Section titled “What to reconfigure manually”](#what-to-reconfigure-manually)
### Shell
[Section titled “Shell”](#shell)
Warp auto-detects your login shell. To override it, for example, to match `terminal.integrated.defaultProfile.*`, open **Settings** > **Features** > **Session** in the Warp app and choose a shell from **Startup shell for new sessions**.
### Font and cursor
[Section titled “Font and cursor”](#font-and-cursor)
In the Warp app, open **Settings** > **Appearance** > **Text, fonts, & cursor**, then set the font family and size to match `terminal.integrated.fontFamily` and `terminal.integrated.fontSize`.
### Theme
[Section titled “Theme”](#theme)
VS Code’s terminal uses the color scheme from your overall editor theme. In the Warp app, choose a comparable theme from **Settings** > **Appearance** > **Themes**, or [create a custom theme](/terminal/appearance/custom-themes/) that matches your VS Code theme’s `terminal.*` color tokens.
### Keybindings
[Section titled “Keybindings”](#keybindings)
Warp’s [default keyboard shortcuts](/getting-started/keyboard-shortcuts/) are largely consistent with VS Code terminal shortcuts (splits, new tab, find). For any custom bindings you configured in VS Code, add them in **Settings** > **Keyboard shortcuts** in the Warp app.
## Choosing your setup
[Section titled “Choosing your setup”](#choosing-your-setup)
### Use Warp alongside VS Code
[Section titled “Use Warp alongside VS Code”](#use-warp-alongside-vs-code)
Many developers keep VS Code as their editor and use Warp as the terminal they switch to for long-running commands, SSH sessions, or AI-assisted workflows. You don’t need to change VS Code. Install Warp and open it when you want a richer terminal.
VS Code’s integrated terminal still works; use it for quick one-off commands, and jump to Warp when you need [blocks](/terminal/blocks/), [Agent Mode](/agents/), or [persistent sessions](/terminal/sessions/session-restoration/).
### Replace VS Code with Warp
[Section titled “Replace VS Code with Warp”](#replace-vs-code-with-warp)
Warp includes a built-in [code editor](/code/code-editor/) with Language Server Protocol (LSP) support, a [file tree](/code/code-editor/file-tree/), [find and replace](/code/code-editor/find-and-replace/), and [Vim keybindings](/code/code-editor/code-editor-vim-keybindings/). Combined with [Code Review](/code/code-review/), many developers use Warp as their primary editor and drop VS Code entirely.
Open a directory with `warp .` from the command line to start editing.
## Warp-native equivalents
[Section titled “Warp-native equivalents”](#warp-native-equivalents)
Use this table to find Warp equivalents for VS Code terminal features you might look for after switching:
| From VS Code terminal | In Warp |
| ------------------------------ | ---------------------------------------------------------------------------------------------------------------------------- |
| Split terminal | [Split panes](/terminal/windows/split-panes/) |
| Multiple terminals (tab strip) | [Tabs](/terminal/windows/tabs/), [vertical tabs](/terminal/windows/vertical-tabs/) |
| Tasks (`tasks.json`) | [YAML workflows](/terminal/entry/yaml-workflows/) or [tab configs](/terminal/windows/tab-configs/) |
| Terminal profiles | [Tab configs](/terminal/windows/tab-configs/) + per-session shell overrides |
| Shell integration | Built in via [Warpify](/terminal/warpify/); enables working-directory tracking and command-level [blocks](/terminal/blocks/) |
For an overview of what Warp adds beyond a terminal, see [Coding in Warp](/getting-started/quickstart/coding-in-warp/).
# Migrate to Warp from Windows Terminal
Canonical page: [/getting-started/migrate-to-warp/migrate-to-warp-from-windows-terminal/](https://docs.warp.dev/getting-started/migrate-to-warp/migrate-to-warp-from-windows-terminal/)
> Switch from Windows Terminal to Warp on Windows. Reconfigure profiles, shells, fonts, keybindings, and find Warp equivalents.
Warp on Windows covers everything you use Windows Terminal for today, including profiles, PowerShell, color schemes, and keybindings, with Agent Mode and blocks on top. This page walks through the migration.
## What Warp can help transfer
[Section titled “What Warp can help transfer”](#what-warp-can-help-transfer)
Warp doesn’t have a one-click Windows Terminal importer. Because Windows Terminal stores profiles, color schemes, and keybindings in a single JSON file, Warp’s Agent can read that file and translate matching values into Warp’s `settings.toml`:
```powershell
%LOCALAPPDATA%\Packages\Microsoft.WindowsTerminal_8wekyb3d8bbwe\LocalState\settings.json
```
## Use Warp’s Agent to migrate your settings (recommended)
[Section titled “Use Warp’s Agent to migrate your settings (recommended)”](#use-warps-agent-to-migrate-your-settings-recommended)
The fastest way to bring over your Windows Terminal setup is to ask Warp’s Agent to translate `settings.json` directly. Warp ships a [`settings.toml` file](/terminal/settings/) and a bundled `modify-settings` skill that lets the Agent read your existing config and write equivalent values into Warp’s settings, including translating your color schemes into a Warp [custom theme](/terminal/appearance/custom-themes/).
1. In the Warp app, open a new tab and switch to [Agent Mode](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/) with `Ctrl+I`.
2. Paste this prompt into Agent Mode, then press `Enter`.
> Read my Windows Terminal `settings.json` at `%LOCALAPPDATA%\Packages\Microsoft.WindowsTerminal_8wekyb3d8bbwe\LocalState\settings.json` and port the active profile and color scheme into my Warp `settings.toml` using the `modify-settings` skill. Create a matching custom theme. Show me a diff before applying.
3. Review the proposed diff, then approve the changes. Warp hot-reloads `settings.toml`.
If you’d rather configure each setting manually through the Settings UI, the steps below cover the most common cases.
## What to reconfigure manually
[Section titled “What to reconfigure manually”](#what-to-reconfigure-manually)
### Default shell
[Section titled “Default shell”](#default-shell)
Warp on Windows supports PowerShell (`pwsh` and `powershell.exe`), Command Prompt (`cmd`), bash, zsh, and fish. Warp auto-detects your login shell. To override it, open **Settings** > **Features** > **Session** in the Warp app and choose a shell from **Startup shell for new sessions**.
If you use PowerShell modules or a custom `$PROFILE`, Warp loads them the same way Windows Terminal does.
### Profiles
[Section titled “Profiles”](#profiles)
Windows Terminal uses profiles to group shell, theme, starting directory, and font together. Warp doesn’t have a single profile concept; instead, match each dimension separately:
* **Shell** - Configure from **Settings** > **Features** > **Session** in the Warp app.
* **Starting directory** - Configure **Working directory** from **Settings** > **Features** > **Session** in the Warp app.
* **Font family and size** - Configure from **Settings** > **Appearance** > **Text, fonts, & cursor** in the Warp app.
* **Color scheme** - Configure from **Settings** > **Appearance** > **Themes** in the Warp app. Translate your Windows Terminal color scheme into a [custom Warp theme](/terminal/appearance/custom-themes/) using the same 16 ANSI color values.
* **Reusable layouts** - create a [tab config](/terminal/windows/tab-configs/) for each workflow that used to be a profile.
### Color scheme
[Section titled “Color scheme”](#color-scheme)
Windows Terminal’s `schemes` array defines foreground, background, cursor, and ANSI colors. To match an existing scheme:
1. Copy the color values from the scheme you use in your `settings.json`.
2. In the Warp app, open **Settings** > **Appearance** > **Themes**, then choose a preset that matches or [create a custom theme](/terminal/appearance/custom-themes/).
### Keybindings
[Section titled “Keybindings”](#keybindings)
Warp’s [default keyboard shortcuts](/getting-started/keyboard-shortcuts/) cover most Windows Terminal bindings. For custom bindings from `settings.json`’s `actions` array, add them in **Settings** > **Keyboard shortcuts** in the Warp app.
### Prompt
[Section titled “Prompt”](#prompt)
If you use `oh-my-posh` or a custom PowerShell prompt, it continues to work in Warp. To choose between Warp’s native prompt and your existing shell prompt, open **Settings** > **Appearance** > **Prompt** in the Warp app. See [prompt](/terminal/appearance/prompt/).
## Warp-native equivalents
[Section titled “Warp-native equivalents”](#warp-native-equivalents)
Use this table to find Warp equivalents for Windows Terminal features you might look for after switching:
| From Windows Terminal | In Warp |
| --------------------- | --------------------------------------------------------------------------------------------------------------------------------- |
| Profiles | [Tab configs](/terminal/windows/tab-configs/) + [themes](/terminal/appearance/themes/) + per-session shell settings |
| Tabs and panes | [Tabs](/terminal/windows/tabs/), [vertical tabs](/terminal/windows/vertical-tabs/), [split panes](/terminal/windows/split-panes/) |
| Command palette | [Command Palette](/terminal/command-palette/) (`Ctrl+Shift+P`) |
| Oh My Posh prompts | Keep using them; pick [Shell prompt (PS1)](/terminal/appearance/prompt/#shell-prompt-ps1) in Warp |
| Quake mode | [Global hotkey](/terminal/windows/global-hotkey/) |
Beyond Windows Terminal’s feature set, Warp adds [Agent Mode](/agents/), [blocks](/terminal/blocks/), and [Warp Drive](/knowledge-and-collaboration/warp-drive/). See [Warp for Windows installation](/getting-started/quickstart/installation-and-setup/) if you haven’t installed yet.
# Coding in Warp
Canonical page: [/getting-started/quickstart/coding-in-warp/](https://docs.warp.dev/getting-started/quickstart/coding-in-warp/)
> Agents can generate and edit code directly from within Warp.
When you enter a Git repo for the first time, Warp will enter an initialization flow to index your codebase and generate an AGENTS.md file.
As you’re in the repo, Warp will enter an advanced code generation flow that supports both single-line and multi-file changes when it detects an opportunity to write code.
For example, Warp may write code when you prompt:
* **Code creation**: “Write a function in JavaScript to debounce an input”
* **Based on error outputs, suggest fixes**: “Fix this TypeScript error.”
* **Edit a single file**: “Update all instances of ‘var’ to ‘let’ in this file.”
* **Make batch changes**: “Add headers to all .py files in this directory”
**The best way to experience this is to try it yourself —** [*open the Prompt below in Warp*](https://app.warp.dev/drive/prompt/Generate-a-custom-Warp-theme-K8oloLrCZAHuaYKfz2cNqI)
```text
Detect the correct Warp themes directory based on the current operating system:
- On macOS, use ~/.warp/themes/
- On Linux, use ${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/themes/
- On Windows, use $env:APPDATA\warp\Warp\data\themes\
Create the directory if it doesn’t already exist.
Then, generate a custom Warp theme named {{theme_name}} in valid YAML format, following the official structure from Warp’s documentation. Exclude the background_image field, and do not include any extra or missing fields. Save the theme as {{theme_name}}.yaml in the detected themes directory.
Once the theme is created and verified, confirm completion by telling me where the theme file was saved.
```
***
### Context
[Section titled “Context”](#context)
#### Codebase Context
[Section titled “Codebase Context”](#codebase-context)
Warp can index your Git-tracked codebases to help agents understand your code and generate accurate, context-aware responses. **No code is stored on Warp servers**.
You can view and manage your indexed codebases in **Settings** > **Code** > **Indexing and projects** under **Initialized / indexed folders**. You can also specify whether to automatically index new folders as you navigate them.
If your codebase is large, you can exclude specific files by adding them to a `.warpindexingignore` file.
#### Other types of context
[Section titled “Other types of context”](#other-types-of-context)
You can provide different types of input as context directly to the agent to guide its behavior and improve response quality. This includes:
* [Blocks](/agents/local-agents/agent-context/blocks-as-context/) from your terminal output
* [Images](/agents/local-agents/agent-context/images-as-context/)
* [Files and code](/agents/local-agents/agent-context/using-to-add-context/) (using the @ symbol)
* [Public websites](/agents/local-agents/agent-context/urls-as-context/) via URLs
#### Warp Drive as context
[Section titled “Warp Drive as context”](#warp-drive-as-context)
Agents pull directly from your [**Warp Drive**](/knowledge-and-collaboration/warp-drive/) contents to generate more accurate responses, including your **Workflows**, **Notebooks**, **Prompts**, and **Environment Variables**.
* When used, context appears under the “References” or “Derived from” section in the conversation.
* This setting is **enabled by default** and can be managed via: **Settings** > **Agents** > **Knowledge** > **Warp Drive as Agent Mode Context**.
#### Rules
[Section titled “Rules”](#rules)
**Rules** let you provide persistent context to Agents, enabling smarter and more personalized responses.
You can create global rules (accessed through [Warp Drive](/knowledge-and-collaboration/warp-drive/) > **Personal** > **Rules**) or project-scoped rules, defined in an `AGENTS.md` file. Note: the filename must be in all caps for Warp to recognize it.
**Examples of Rules include:**
* Coding standards and best practices
* Project- or workspace-specific guidelines
* Personal preferences for tools, formatting, or behavior
**How to access project-specific Rules**
1. From the file searcher, press `⌘+O` and search “AGENTS.md”.
2. From the file tree, click the “code” icon when in a repo.
**How to access Global Rules**
1. From [Warp Drive](/knowledge-and-collaboration/warp-drive/), go to **Personal** > **Rules**.
2. From the [Command Palette](/terminal/command-palette/), search for “Open AI Rules”.
3. From the Settings panel, go to **Settings** > **Agents** > **Knowledge** > **Manage Rules**.
4. From the Warp menu bar, choose **AI** > **Open Rules**.
# Customizing Warp
Canonical page: [/getting-started/quickstart/customizing-warp/](https://docs.warp.dev/getting-started/quickstart/customizing-warp/)
> A complete guide to customizing Warp: themes, vertical tabs, tab configs, prompt chips, keybindings, AI models, and more.
Warp is deeply customizable. Whether you use Warp primarily as a modern terminal or as an AI-powered development environment, you can tailor the experience to fit how you work. Configure the terminal side (themes, keybindings, vertical tabs, tab configs) and the AI side (model choice, agent autonomy, default mode) independently.
Use the quick-reference table to find what you need, or browse the sections below for more details. If you want to go further than configuration, Warp’s client is open source under [AGPL v3](https://github.com/warpdotdev/warp/blob/master/LICENSE-AGPL) — see [Contributing to Warp](/support-and-community/community/contributing/) to build a custom variant or contribute changes upstream.
## Quick reference
[Section titled “Quick reference”](#quick-reference)
| What to customize | Where to find it | Quick action |
| ----------------- | ------------------------------------------------------ | -------------------------------------------------------------------------------------- |
| Theme | **Settings** > **Appearance** | Pick a preset or [create a custom YAML theme](/terminal/appearance/custom-themes/) |
| Prompt chips | Right-click prompt area > **Edit prompt** | Drag and drop context chips (directory, git branch, time, etc.) |
| AI model | Model selector in agent conversation | Choose Claude, GPT, Gemini, or Auto |
| Keybindings | **Settings** > **Keyboard shortcuts** | Import from another terminal or set custom shortcuts |
| Vertical tabs | **Settings** > **Appearance** > **Tabs** | Switch to a sidebar tab layout for more horizontal space |
| Tab configs | **Settings** > **Features** or `/` menu | Save and restore tab layouts with startup commands |
| Settings file | **Open settings file** button in the Settings footer | Edit [`settings.toml`](/terminal/settings/) directly for version control and scripting |
| App icon | **Settings** > **Appearance** > **Icon** | Pick a custom icon (macOS) |
| Font & text | **Settings** > **Appearance** > **Text** | Change font, size, and cursor style |
| Agent autonomy | **Settings** > **Agents** > **Profiles** | Set what the agent can do without asking |
| Default mode | **Settings** > **Agents** > **Warp Agent** > **Input** | Choose whether new tabs open in terminal mode or Agent Mode |
***
## Appearance
[Section titled “Appearance”](#appearance)
In Warp, navigate to **Settings** > **Appearance** to access these options and control how Warp looks:
* **[Themes](/terminal/appearance/themes/)** - Choose from pre-loaded themes or create your own [custom theme](/terminal/appearance/custom-themes/) using YAML or a background image.
* **[Prompt chips](/terminal/appearance/prompt/)** - Customize the context chips in your Warp prompt. Right-click the prompt area and select **Edit prompt** to drag and drop chips like directory, git branch, Kubernetes context, and time.
* **[App icons](/terminal/appearance/app-icons/)** - Choose a custom app icon to distinguish Warp in your dock (macOS).
* **[Text, fonts, and cursor](/terminal/appearance/text-fonts-cursor/)** - Change your font type, size, and cursor style.
* **[Input position](/terminal/appearance/input-position/)** - Move your prompt and command line to the top or bottom of the window.
* **[Size, opacity, and blurring](/terminal/appearance/size-opacity-blurring/)** - Adjust window transparency and blur effects.
* **[Pane dimming](/terminal/appearance/pane-dimming/)** - Dim inactive panes to focus on the active one.
## Layout
[Section titled “Layout”](#layout)
Organize your workspace with tabs, panes, and window configurations.
* **[Vertical tabs](/terminal/windows/vertical-tabs/)** - Switch to a vertical sidebar layout for tabs, giving you more horizontal space and better visibility when you have many open sessions.
* **[Tabs](/terminal/windows/tabs/)** - Organize sessions into tabs with custom titles and colors. Right-click a tab to pick a color.
* **[Split panes](/terminal/windows/split-panes/)** - Divide any tab into multiple panels, side-by-side or stacked.
* **[Tab configs](/terminal/windows/tab-configs/)** - Save and restore tab layouts with predefined pane arrangements and startup commands.
* **[Global hotkey](/terminal/windows/global-hotkey/)** - Set up a dedicated hotkey window (Quake Mode) that appears and hides with a keyboard shortcut.
## Input and editor
[Section titled “Input and editor”](#input-and-editor)
Configure how you type and interact with the terminal input.
* **[Keyboard shortcuts](/getting-started/keyboard-shortcuts/)** - Warp supports common shortcuts and lets you create custom ones. Manage them from **Settings** > **Keyboard shortcuts**, or import keybindings from another terminal during [migration](/getting-started/migrate-to-warp/).
* **[Vim keybindings](/terminal/editor/vim/)** - Enable Vim keybindings for keyboard-driven text editing in the input editor.
* **Tab key behavior** - Configure what `Tab` does in **Settings** > **Features**. Options include accepting autosuggestions or triggering completions.
## AI and models
[Section titled “AI and models”](#ai-and-models)
Control how Warp’s agents behave and which models they use.
* **[Model choice](/agents/inference/model-choice/)** - Choose your preferred AI model (Claude, GPT, Gemini, or Auto) from the model selector in any agent conversation.
* **[Agent profiles and permissions](/agents/capabilities/agent-profiles-permissions/)** - Configure how much autonomy the agent has: what it can auto-execute, what requires approval, and command allowlists/denylists.
* **Default mode for new sessions** - Choose whether new tabs open in terminal mode or Agent Mode by default. Set this in **Settings** > **Agents** > **Warp Agent** > **Input**.
## Import and sync
[Section titled “Import and sync”](#import-and-sync)
Bring your existing settings into Warp or keep settings synchronized across machines.
* **[Migrate from another terminal](/getting-started/migrate-to-warp/)** - Per-source guides for switching to Warp from iTerm2, Ghostty, macOS Terminal, Windows Terminal, VS Code, Cursor, Claude Code, and more. Includes automatic settings import for iTerm2.
* **[Settings sync](/terminal/more-features/settings-sync/)** - Sync your Warp settings across machines (Beta).
***
## Next steps
[Section titled “Next steps”](#next-steps)
Now that Warp looks and feels like yours, the next step is to put it to work on a real project. Open a codebase to unlock context-aware agents, or start an agent conversation to see how terminal commands and AI work together.
* **[Codebase Context](/agents/capabilities/codebase-context/)** - Open a project and index your codebase so agents give you context-aware answers about your code.
* **[Terminal and Agent modes](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/)** - Learn how terminal mode and agent conversations work together.
# Installation and setup
Canonical page: [/getting-started/quickstart/installation-and-setup/](https://docs.warp.dev/getting-started/quickstart/installation-and-setup/)
> Install Warp on macOS, Windows, or Linux. All installation options include auto-update for new features, bug fixes, and performance improvements.
Note
**Platform support:** Warp is supported on macOS (Intel and Apple silicon), Windows (x86\_64 and ARM64), and Linux (x86\_64 and ARM64).
## Install Warp
[Section titled “Install Warp”](#install-warp)
Caution
**Visit** [Known Issues](/support-and-community/troubleshooting-and-support/known-issues/) **to get more details on setting up and troubleshooting Warp.**
* macOS
Note
**Minimum requirements:** Intel or Apple silicon macOS 10.14 or above and hardware that supports [Metal](https://support.apple.com/en-us/HT205073).
**Download Warp and drag into your Applications folder**
[Download Warp](https://www.warp.dev/download)
**Install using Homebrew by running the command below**
```bash
brew install --cask warp
```
After installation, you can find Warp in your Applications folder.
* Windows
Note
**Minimum requirements:** Warp requires Windows 10 version 1903 (build 18362) or later, and Windows Server 2022 (build 20348) or later. This is a requirement for [Windows Pseudo Console (ConPTY)](https://devblogs.microsoft.com/commandline/windows-command-line-introducing-the-windows-pseudo-console-conpty/).
**Download Warp, then open and run the installer**
[Download Warp](https://www.warp.dev/download)
**Install using WinGet by running the command below**
```powershell
winget install Warp.Warp
```
After installation, you can find Warp in the Start menu.
* Linux
Note
**Minimum requirements:** Linux distribution with glibc >= 2.31 (released Feb. 2020) and support for *either* [OpenGL ES 3.0+ or Vulkan](https://github.com/gfx-rs/wgpu?tab=readme-ov-file#supported-platforms).
This includes (but is not limited to) the following:
* Ubuntu 20.04
* Debian 11 (“bullseye”)
* Fedora 32
* Arch Linux
**Visit the Warp download page for the full list of Linux installation options**
[Download Warp](https://www.warp.dev/download)
**Debian- and Ubuntu-based distributions**
The easiest way to install Warp is to download [x64 .deb package](https://app.warp.dev/download?package=deb) or [ARM64 deb package](https://app.warp.dev/download?package=deb_arm64). After downloading, you can install the package with:
```plaintext
sudo apt install ./<file>.deb
```
Installing the .deb package will automatically set up the Warp apt repository and signing key needed to automatically update Warp and verify the integrity of the downloaded packages.
Alternatively, you can manually configure the Warp apt repository and install Warp by running the following commands:
```plaintext
sudo apt-get install wget gpg
wget -qO- https://releases.warp.dev/linux/keys/warp.asc | gpg --dearmor > warpdotdev.gpg
sudo install -D -o root -g root -m 644 warpdotdev.gpg /etc/apt/keyrings/warpdotdev.gpg
sudo sh -c 'echo "deb [arch=amd64 signed-by=/etc/apt/keyrings/warpdotdev.gpg] https://releases.warp.dev/linux/deb stable main" > /etc/apt/sources.list.d/warpdotdev.list'
rm warpdotdev.gpg
sudo apt update && sudo apt install warp-terminal
```
**RHEL-, Fedora-, and CentOS-based distributions**
The easiest way to install Warp is to download the [x64 .rpm package](https://app.warp.dev/download?package=rpm) or [ARM64 .rpm package](https://app.warp.dev/download?package=rpm_arm64). After downloading, you can install the package with:
```bash
sudo dnf install ./<file>.rpm
```
Installing the .rpm package will automatically set up the Warp yum repository. On first update, `dnf` will retrieve the signing key needed to verify the integrity of the downloaded packages.
Alternatively, you can manually configure the Warp yum repository and install Warp by running the following commands:
```bash
sudo rpm --import https://releases.warp.dev/linux/keys/warp.asc
sudo sh -c 'echo -e "[warpdotdev]\nname=warpdotdev\nbaseurl=https://releases.warp.dev/linux/rpm/stable\nenabled=1\ngpgcheck=1\ngpgkey=https://releases.warp.dev/linux/keys/warp.asc" > /etc/yum.repos.d/warpdotdev.repo'
sudo dnf install warp-terminal
```
**Arch Linux-based distributions**
The easiest way to install Warp is to download the [x64 .pkg.tar.zst package](https://app.warp.dev/download?package=pacman) or [ARM64 pacman package](https://app.warp.dev/download?package=pacman_arm64). After downloading, you can install the package with:
```bash
sudo pacman -U ./<file>.pkg.tar.zst
```
The first time you update Warp through the app, it will guide you through setting up the Warp pacman repository and signing key.
Alternatively, you can manually configure the Warp pacman repository and install Warp by running the following commands:
```bash
sudo sh -c "echo -e '\n[warpdotdev]\nServer = https://releases.warp.dev/linux/pacman/\$repo/\$arch' >> /etc/pacman.conf"
sudo pacman-key -r "linux-maintainers@warp.dev"
sudo pacman-key --lsign-key "linux-maintainers@warp.dev"
sudo pacman -Sy warp-terminal
```
**OpenSUSE- and SLE-based distributions**
The Warp yum repository also works for OpenSUSE- and SLE-based systems. Download the [x64 .rpm package](https://app.warp.dev/download?package=rpm) or [ARM64 .rpm package](https://app.warp.dev/download?package=rpm_arm64). After downloading, you can install the package with:
```bash
sudo zypper install ./<file>.rpm
```
Installing the .rpm package will automatically set up the Warp yum repository. On first update, `zypper` will retrieve the signing key needed to verify the integrity of the downloaded packages.
Alternatively, you can manually configure the Warp yum repository and install Warp by running the following commands:
```bash
sudo rpm --import https://releases.warp.dev/linux/keys/warp.asc
sudo sh -c 'echo -e "[warpdotdev]\nname=warpdotdev\ntype=rpm-md\nbaseurl=https://releases.warp.dev/linux/rpm/stable\nenabled=1\nautorefresh=1\ngpgcheck=1\ngpgkey=https://releases.warp.dev/linux/keys/warp.asc\nkeeppackages=0" > /etc/zypp/repos.d/warpdotdev.repo'
sudo zypper install warp-terminal
```
**AppImage**
We also provide an [AppImage](https://appimage.org), a single-file executable version of Warp. Installing Warp via a package manager is recommended, as it will ensure your system has all necessary dependencies installed.
You can download the Warp AppImage with the following commands:
```bash
# On x64 systems
curl -L "https://app.warp.dev/download?package=appimage" -o Warp-x64.AppImage
chmod +x Warp-x64.AppImage
```
```bash
# On ARM64 systems
curl -L "https://app.warp.dev/download?package=appimage_arm64" -o Warp-ARM64.AppImage
chmod +x Warp-ARM64.AppImage
```
**Running Warp on Linux**
If you installed a package, find Warp in your desktop manager or run `warp-terminal` on your terminal. If you’re using the AppImage, you can launch it by navigating to the directory where the AppImage is located and running `./Warp-*.AppImage`.
Note
Want to try our newest features? [Warp Preview](/support-and-community/community/warp-preview-and-alpha-program/) is available on all platforms and architectures (macOS, Windows, Linux) for early access to experimental features.
## Build from source
[Section titled “Build from source”](#build-from-source)
Warp’s client is open source under [AGPL v3](https://github.com/warpdotdev/warp/blob/master/LICENSE-AGPL), so you can build it yourself from [`warpdotdev/warp`](https://github.com/warpdotdev/warp).
Clone the repo, bootstrap toolchain dependencies, and start a development build:
```bash
git clone https://github.com/warpdotdev/warp.git
cd warp
./script/bootstrap
cargo run
```
`cargo run` launches a `warp-oss` binary built from your local checkout. See the repo’s `README.md` and `CONTRIBUTING.md` for full prerequisites (Xcode on macOS, the pinned Rust toolchain, `protoc`) and development setup.
Note
Use the official builds for daily use. Self-built `warp-oss` binaries use a separate config and data directory, so they run alongside official Warp without conflicting, but they don’t auto-update and don’t carry the production code-signing identity. Use them for developing, auditing, or contributing back upstream.
## Initial setup
[Section titled “Initial setup”](#initial-setup)
### Log in to Warp (optional)
[Section titled “Log in to Warp (optional)”](#log-in-to-warp-optional)
After installation, you have the option to create a Warp account through the “Sign up” button (top right), or by navigating to **Settings** > **Account** > **Sign up**. Optionally, you can skip this step. If you’re having issues logging in, see the [Login Troubleshooting](/support-and-community/troubleshooting-and-support/troubleshooting-login-issues/) page.
Note
If you sign up using Google or GitHub, Warp only gets access to the associated email address. Visit the [Privacy](/support-and-community/privacy-and-security/privacy/) page for more details on Warp’s approach to privacy.
### Use Warp offline
[Section titled “Use Warp offline”](#use-warp-offline)
You will only need an active internet connection when you open the Warp app for the first time. Once opened, [Warp is able to run with no internet connection](/support-and-community/troubleshooting-and-support/using-warp-offline/), although certain features that require an internet connection like AI and real-time collaboration features will be unavailable.
### Import your settings
[Section titled “Import your settings”](#import-your-settings)
If you are migrating to Warp from another terminal, editor, or AI coding tool, see the [Migrate to Warp](/getting-started/migrate-to-warp/) docs for per-source guides including settings-import steps and feature equivalents.
### Set up your Warp default shell
[Section titled “Set up your Warp default shell”](#set-up-your-warp-default-shell)
Warp tries to load your login shell by default. Currently, Warp supports bash, fish, zsh, and PowerShell (pwsh). If your login shell is set to something else (for example, Nushell) Warp will load zsh by default.
Zsh is the default login and interactive shell on macOS (starting with macOS Catalina in 2019), replacing the bash shell. For most Linux distributions, the default shell is bash.
You can change your default shell by going to **Settings** > **Features** > **Session**. In the **Startup shell for new sessions** section, you can choose which shell you want Warp to use.
# Supported Shells
Canonical page: [/getting-started/supported-shells/](https://docs.warp.dev/getting-started/supported-shells/)
> Check which bash, zsh, fish, PowerShell, and WSL2 shells Warp supports on macOS, Windows, and Linux.
Supported shells differ by platform. Warp loads your login shell when it is supported. You can change the default shell per session and customize each shell’s configuration files and environment variables.
## Warp default shell
[Section titled “Warp default shell”](#warp-default-shell)
Warp tries to load your login shell by default. On macOS and Linux, Warp supports bash, fish, zsh, and PowerShell (pwsh). On Windows, use the [platform-specific list](#using-warp-with-shells-on-windows). If your login shell is not supported, Warp shows a banner and loads the default shell listed below:
* On macOS, zsh is the default shell.
* On Windows, PowerShell (pwsh) is the default shell.
* On Linux, bash is the default shell.
Note
If you run into issues configuring your RC files (`~/.bashrc`, `~/.zshrc`, `config.fish`, `Microsoft.PowerShell_profile.ps1`) with Warp, see [Configuring and debugging your RC files](/support-and-community/troubleshooting-and-support/known-issues/#configuring-and-debugging-your-rc-files).
### Changing what shell Warp uses
[Section titled “Changing what shell Warp uses”](#changing-what-shell-warp-uses)
To change the default shell, we recommend you choose a shell in Warp by going to **Settings** > **Features** and scrolling to the **Session** section, then select **Startup shell for new sessions**.
Note
The changes to your shell will only take effect when you start a new session.
## Customizing your shell environment
[Section titled “Customizing your shell environment”](#customizing-your-shell-environment)
### Customize your zsh shell environment
[Section titled “Customize your zsh shell environment”](#customize-your-zsh-shell-environment)
Zsh can be customized via the `~/.zshrc` file, which runs whenever a new session starts (window, tab, or pane). Use it to set environment variables, aliases, and customize the [prompt](/terminal/appearance/prompt/).
#### Editing the .zshrc file
[Section titled “Editing the .zshrc file”](#editing-the-zshrc-file)
Edit `~/.zshrc` using `nano ~/.zshrc` or `vi ~/.zshrc`.
Note
Files starting with a dot (`.`) are hidden by default. Check your file explorer’s settings to show hidden files.
#### Reloading the zshrc file
[Section titled “Reloading the zshrc file”](#reloading-the-zshrc-file)
Apply changes by running `source ~/.zshrc` or restarting Warp/opening a new session.
### Customize your Bash shell environment
[Section titled “Customize your Bash shell environment”](#customize-your-bash-shell-environment)
Bash is pre-installed on macOS and can be customized using `~/.bashrc` (for non-login shells) or `~/.bash_profile` (for login shells). Use these files to set environment variables, aliases, and customize the [prompt](/terminal/appearance/prompt/).
#### Editing the .bashrc file
[Section titled “Editing the .bashrc file”](#editing-the-bashrc-file)
Edit `~/.bashrc` using `nano ~/.bashrc` or `vi ~/.bashrc`.
#### Reloading the bashrc file
[Section titled “Reloading the bashrc file”](#reloading-the-bashrc-file)
Apply changes by running `source ~/.bashrc` or restarting Warp/opening a new session.
Note
Files starting with a dot (`.`) are hidden by default. Check your file explorer’s settings to show hidden files.
### Customize your Fish shell environment
[Section titled “Customize your Fish shell environment”](#customize-your-fish-shell-environment)
Fish is a user-friendly shell with autosuggestions and syntax highlighting. Its configuration file is `~/.config/fish/config.fish`.
#### Editing the config.fish file
[Section titled “Editing the config.fish file”](#editing-the-configfish-file)
Edit `~/.config/fish/config.fish` using `nano ~/.config/fish`. Use it to set environment variables, aliases, and functions.
#### Reloading the config.fish file
[Section titled “Reloading the config.fish file”](#reloading-the-configfish-file)
Apply changes by running `source ~/.config/fish` or restarting Warp/opening a new session.
Note
Unlike Bash and Zsh, Fish does not use `export VAR=value`. Use `set -Ux VAR value` for persistent environment variables.
### Customize your PowerShell shell environment
[Section titled “Customize your PowerShell shell environment”](#customize-your-powershell-shell-environment)
PowerShell can be customized via its profile script, located at `$PROFILE`. Check if it exists with `Test-Path $PROFILE`, and create it if needed with `New-Item -Path $PROFILE -ItemType File -Force`.
#### Editing the PowerShell profile
[Section titled “Editing the PowerShell profile”](#editing-the-powershell-profile)
Edit the profile using `code $PROFILE`, and use it to set environment variables, aliases, custom prompts, and scripts.
#### Reloading the PowerShell profile
[Section titled “Reloading the PowerShell profile”](#reloading-the-powershell-profile)
Apply changes by restarting Warp or opening a new session.
Note
PowerShell’s execution policy may block scripts. Enable profile execution with:
```powershell
Set-ExecutionPolicy RemoteSigned -Scope CurrentUser
```
## Additional shell guidance for macOS
[Section titled “Additional shell guidance for macOS”](#additional-shell-guidance-for-macos)
#### Setting up zsh on Warp
[Section titled “Setting up zsh on Warp”](#setting-up-zsh-on-warp)
By default, macOS ships with [zsh](https://zsh.sourceforge.io/Doc/Release/zsh_toc.html) located in `/bin/zsh`. You can confirm this location by typing `which zsh` in Warp. You can also check the version of zsh installed on your system by typing the following:
`$ zsh --version`
### Using fish shell with Warp on macOS
[Section titled “Using fish shell with Warp on macOS”](#using-fish-shell-with-warp-on-macos)
#### 1. Install fish
[Section titled “1. Install fish”](#1-install-fish)
While bash and zsh come pre-installed on macOS systems, fish shell does not. So before using fish with Warp, you will need to install it. Install fish 3.6 or above using one of the methods listed below:
1. With Homebrew: If you already have homebrew installed, you can type `brew install fish`, and follow the instructions.
2. Download the installer from the [fish shell website](https://fishshell.com/).
#### 2. Switch to fish as the default shell
[Section titled “2. Switch to fish as the default shell”](#2-switch-to-fish-as-the-default-shell)
Once you’ve installed fish on your computer, you can set it as your default shell, so Warp will use it every time a new tab, pane, or window is opened. You can either make fish the default shell for only Warp, from the session settings (**Settings** > **Features** > **Session**), or for your user account. To change your account’s default shell, you need to run two commands.
**If you used Homebrew to install fish on macOS or if you used the macOS installer** available on fishshell.com to install fish, type the following two commands in Warp:
```plaintext
echo $(which fish) | sudo tee -a /etc/shells
chsh -s $(which fish)
```
Note
If you prefer, you can also manually edit the `/etc/shells` file using the editor of your choice (you may need sudo privileges).
Note
**Why the different locations?** The location of fish depends on how it was installed. Homebrew installs programs under `/usr/local` on macOS with Intel processors, but under `/opt/homebrew` on macOS with Apple Silicon. So, if you used Homebrew to install fish on macOS with Apple Silicon, the location of the executable is - `/opt/homebrew/bin/fish`.\
You can identify where fish is installed by running `which fish`.
### Using PowerShell (pwsh) with Warp on macOS
[Section titled “Using PowerShell (pwsh) with Warp on macOS”](#using-powershell-pwsh-with-warp-on-macos)
#### 1. Install PowerShell
[Section titled “1. Install PowerShell”](#1-install-powershell)
While bash and zsh come pre-installed on macOS systems, PowerShell does not. So before using PowerShell with Warp, you will need to install it. Install PowerShell 7.0 or above using one of the methods listed below:
1. With Homebrew: If you already have homebrew installed, you can type `brew install powershell/tap/powershell`, and follow the instructions.
2. Download from the [official Microsoft website](https://learn.microsoft.com/en-us/powershell/scripting/install/installing-powershell).
#### 2. Switch to pwsh as the default shell
[Section titled “2. Switch to pwsh as the default shell”](#2-switch-to-pwsh-as-the-default-shell)
Once you’ve installed PowerShell on your computer, you can set it as your default shell, so Warp will use it every time a new tab, pane, or window is opened. You can either make pwsh the default shell for only Warp, from the session settings (**Settings** > **Features** > **Session**), or for your user account. To change your account’s default shell, you need to run two commands.
```plaintext
echo $(which pwsh) | sudo tee -a /etc/shells
chsh -s $(which pwsh)
```
Note
If you prefer, you can also manually edit the `/etc/shells` file using the editor of your choice (you may need sudo privileges).
Note
**Why the different locations?** The location of pwsh depends on how it was installed. Homebrew installs programs under `/usr/local` on macOS with Intel processors, but under `/opt/homebrew` on macOS with Apple Silicon. So, if you used Homebrew to install pwsh on macOS with Apple Silicon, the location of the executable is - `/opt/homebrew/bin/pwsh`. You can identify where pwsh is installed by running `which pwsh`.
## Using Warp with shells on Windows
[Section titled “Using Warp with shells on Windows”](#using-warp-with-shells-on-windows)
On Windows, Warp’s default shell is PowerShell 7 (pwsh). Warp for Windows supports several shells:
* PowerShell 7 (default)
* PowerShell 5
* Windows Subsystem for Linux (WSL2)
* Git Bash
Note
Windows Command Prompt (cmd.exe) is not currently supported. For more information and updates about cmd.exe support, see [this GitHub issue](https://github.com/warpdotdev/Warp/issues/5882).
# Guides
Canonical page: [/guides/](https://docs.warp.dev/guides/)
> Step-by-step guides for Warp, the agentic development environment — from first setup to coding agent workflows, MCP integrations, and full app builds.
Practical, task-oriented walkthroughs that help you get productive with Warp’s coding agents. Each guide walks through a real AI coding workflow with actual prompts, code, and reproducible results.
To turn a one-off workflow into a repeatable process run by a team of cloud agents, see [Warp Factories](/factories/).
Note
**New to Warp?** Start with [Welcome to Warp](/guides/getting-started/welcome-to-warp/), then explore [10 Warp Coding Features You Should Know](/guides/getting-started/10-coding-features-you-should-know/).
Featured (6)All (61)Set up your environment (9)Work with agents (18)Automate your workflow (10)Connect external services (9)Build & deploy apps (8)Review & debug (7)
[Work with agents](/guides/agent-workflows/build-a-self-improving-agent/)
### [Build a self-improving agent](/guides/agent-workflows/build-a-self-improving-agent/)
[Build an outer loop where a scheduled agent reviews past runs, learns from corrections, and proposes skill file updates.](/guides/agent-workflows/build-a-self-improving-agent/)
[agentssoftware-factorycloud-agentsschedules](/guides/agent-workflows/build-a-self-improving-agent/)
[Work with agents](/guides/agent-workflows/build-a-triage-agent/)
### [Build a triage agent](/guides/agent-workflows/build-a-triage-agent/)
[Create a triage agent that reviews new GitHub issues, applies labels, and flags open questions. Your backlog stays actionable without manual effort.](/guides/agent-workflows/build-a-triage-agent/)
[agentscloud-agentssoftware-factory](/guides/agent-workflows/build-a-triage-agent/)
[Work with agents](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/)
### [Attach agent context to PRs](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/)
[Share a Warp agent session or cloud agent run link in a GitHub pull request so reviewers can inspect the context behind agent-generated changes.](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/)
[agentscode-reviewsession-sharing](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/)
[Work with agents](/guides/agent-workflows/how-to-edit-agent-code-in-warp/)
### [Edit agent code in Warp](/guides/agent-workflows/how-to-edit-agent-code-in-warp/)
[Review, edit, and refine AI-generated code diffs directly in Warp — accept, reject, or modify changes before applying them.](/guides/agent-workflows/how-to-edit-agent-code-in-warp/)
[agents](/guides/agent-workflows/how-to-edit-agent-code-in-warp/)
[Work with agents](/guides/agent-workflows/how-to-explain-your-codebase-using-warp-rust-codebase/)
### [Explain your codebase using Warp](/guides/agent-workflows/how-to-explain-your-codebase-using-warp-rust-codebase/)
[Use Warp's coding agents with semantic and symbol search to explore, understand, and modify unfamiliar codebases — demonstrated on a large Rust project.](/guides/agent-workflows/how-to-explain-your-codebase-using-warp-rust-codebase/)
[agents](/guides/agent-workflows/how-to-explain-your-codebase-using-warp-rust-codebase/)
[Review & debug](/guides/agent-workflows/how-to-review-ai-generated-code/)
### [Review AI-generated code](/guides/agent-workflows/how-to-review-ai-generated-code/)
[Review AI-generated code in Warp with visual diffs and inline comments. Use this workflow with Claude Code, Codex, or any CLI agent.](/guides/agent-workflows/how-to-review-ai-generated-code/)
[agentscode-review](/guides/agent-workflows/how-to-review-ai-generated-code/)
[Review & debug](/guides/agent-workflows/how-to-review-prs-like-a-senior-dev/)
### [Review PRs like a senior dev](/guides/agent-workflows/how-to-review-prs-like-a-senior-dev/)
[Use Warp's agent to understand large pull requests, identify risky changes, and investigate potential issues before leaving review comments.](/guides/agent-workflows/how-to-review-prs-like-a-senior-dev/)
[agentscode-review](/guides/agent-workflows/how-to-review-prs-like-a-senior-dev/)
[Work with agents](/guides/agent-workflows/how-to-run-3-agents-in-parallel-summarize-logs-analyze-pr-modify-ui/)
### [Run 3 agents in parallel](/guides/agent-workflows/how-to-run-3-agents-in-parallel-summarize-logs-analyze-pr-modify-ui/)
[Run three agent tasks simultaneously in Warp — modify UI, analyze code reviews, and summarize production logs in parallel.](/guides/agent-workflows/how-to-run-3-agents-in-parallel-summarize-logs-analyze-pr-modify-ui/)
[agents](/guides/agent-workflows/how-to-run-3-agents-in-parallel-summarize-logs-analyze-pr-modify-ui/)
[Work with agents](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/)
### [Run multiple AI coding agents](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/)
[Run Claude Code, Codex, Warp Agent, and other coding agents across worktrees, tabs, and cloud orchestration with clear task ownership.](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/)
[agents](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/)
[Work with agents](/guides/agent-workflows/how-to-run-unattended-agents/)
### [Run unattended agents](/guides/agent-workflows/how-to-run-unattended-agents/)
[Start unattended cloud agents from schedules, Slack, Linear, GitHub, GitHub Actions, the Oz CLI, or the Automation Platform API, then inspect every run.](/guides/agent-workflows/how-to-run-unattended-agents/)
[agentscloud-agentsschedules](/guides/agent-workflows/how-to-run-unattended-agents/)
[Work with agents](/guides/agent-workflows/how-to-use-voice-and-images-to-prompt-coding-agents/)
### [Use voice and images to prompt coding agents](/guides/agent-workflows/how-to-use-voice-and-images-to-prompt-coding-agents/)
[Use voice and image context to prompt coding agents faster in Warp — works with Claude Code, Codex, and any CLI agent.](/guides/agent-workflows/how-to-use-voice-and-images-to-prompt-coding-agents/)
[agents](/guides/agent-workflows/how-to-use-voice-and-images-to-prompt-coding-agents/)
[Work with agents](/guides/agent-workflows/run-a-software-factory-in-the-cloud/)
### [Run a software factory in the cloud](/guides/agent-workflows/run-a-software-factory-in-the-cloud/)
[Set up the Automation Platform-native production path for your software factory with cloud environments, secrets, triggers, and audit trails.](/guides/agent-workflows/run-a-software-factory-in-the-cloud/)
[agentscloud-agentssoftware-factoryorchestration](/guides/agent-workflows/run-a-software-factory-in-the-cloud/)
[Work with agents](/guides/agent-workflows/set-up-a-software-factory/)
### [Set up your software factory](/guides/agent-workflows/set-up-a-software-factory/)
[Add the implementation and reviewer agents to complete your software factory, then wire all four agent roles together using GitHub labels as the state machine.](/guides/agent-workflows/set-up-a-software-factory/)
[agentssoftware-factorycloud-agents](/guides/agent-workflows/set-up-a-software-factory/)
[Work with agents](/guides/agent-workflows/understanding-your-codebase/)
### [Understand your codebase](/guides/agent-workflows/understanding-your-codebase/)
[Use Warp's Codebase Context to search across client and server repos, generate architecture summaries, and onboard to unfamiliar features fast.](/guides/agent-workflows/understanding-your-codebase/)
[agents](/guides/agent-workflows/understanding-your-codebase/)
[Work with agents](/guides/agent-workflows/using-images-as-context-with-warp/)
### [Use images as context](/guides/agent-workflows/using-images-as-context-with-warp/)
[Attach screenshots and design mockups as context for Warp's agent to generate UI code, debug visual issues, and match Figma designs.](/guides/agent-workflows/using-images-as-context-with-warp/)
[agents](/guides/agent-workflows/using-images-as-context-with-warp/)
[Work with agents](/guides/agent-workflows/warp-for-product-managers/)
### [5 agent workflows for product managers](/guides/agent-workflows/warp-for-product-managers/)
[Use five agent workflows to automate status updates, document drafting, Slack search, and meeting preparation for product managers.](/guides/agent-workflows/warp-for-product-managers/)
[agents](/guides/agent-workflows/warp-for-product-managers/)
[Work with agents](/guides/agent-workflows/warp-vs-claude-code/)
### [Warp vs Claude Code](/guides/agent-workflows/warp-vs-claude-code/)
[Compare Warp and Claude Code across setup, diff review, model selection, configuration, and performance.](/guides/agent-workflows/warp-vs-claude-code/)
[agentsthird-party-tools](/guides/agent-workflows/warp-vs-claude-code/)
[Work with agents](/guides/agent-workflows/write-product-and-tech-specs-with-agents/)
### [Write specs with agents](/guides/agent-workflows/write-product-and-tech-specs-with-agents/)
[Use agents to turn a ready-to-implement issue into a product spec and a tech spec — the blueprints that guide implementation and anchor code review.](/guides/agent-workflows/write-product-and-tech-specs-with-agents/)
[agentssoftware-factory](/guides/agent-workflows/write-product-and-tech-specs-with-agents/)
[Build & deploy apps](/guides/build-an-app-in-warp/building-a-chrome-extension-d3js-javascript-html-css/)
### [Build a Chrome extension](/guides/build-an-app-in-warp/building-a-chrome-extension-d3js-javascript-html-css/)
[Build a D3.js Sankey diagram Chrome extension using Warp — scaffold, debug, coordinate multiple agents, and publish to the Chrome Web Store.](/guides/build-an-app-in-warp/building-a-chrome-extension-d3js-javascript-html-css/)
[build-appfrontend](/guides/build-an-app-in-warp/building-a-chrome-extension-d3js-javascript-html-css/)
[Build & deploy apps](/guides/build-an-app-in-warp/building-a-real-time-chat-app-github-mcp-railway/)
### [Build a real-time chat app](/guides/build-an-app-in-warp/building-a-real-time-chat-app-github-mcp-railway/)
[Build and deploy a real-time chat app with Python, FastAPI, and JavaScript — from idea to production, all inside Warp.](/guides/build-an-app-in-warp/building-a-real-time-chat-app-github-mcp-railway/)
[build-appmcp](/guides/build-an-app-in-warp/building-a-real-time-chat-app-github-mcp-railway/)
[Build & deploy apps](/guides/build-an-app-in-warp/building-warps-input-with-warp/)
### [Build Warp's input component](/guides/build-an-app-in-warp/building-warps-input-with-warp/)
[Watch how a Warp designer uses Warp's own agent to locate, modify, and test a UI component change in a large Rust codebase.](/guides/build-an-app-in-warp/building-warps-input-with-warp/)
[build-appfrontend](/guides/build-an-app-in-warp/building-warps-input-with-warp/)
[Automate your workflow](/guides/configuration/creating-rules-for-agents/)
### [Create Rules for agents](/guides/configuration/creating-rules-for-agents/)
[Create reusable Rules in Warp to encode team conventions — like Dockerfile patterns or dependency management — so agents follow your standards.](/guides/configuration/creating-rules-for-agents/)
[rules](/guides/configuration/creating-rules-for-agents/)
[Automate your workflow](/guides/configuration/how-to-configure-yolo-and-strategic-agent-profiles/)
### [Configure YOLO and strategic Agent Profiles](/guides/configuration/how-to-configure-yolo-and-strategic-agent-profiles/)
[Configure custom agent profiles in Warp to control planning depth, autonomy, and execution speed — demonstrated with YOLO and Strategic examples.](/guides/configuration/how-to-configure-yolo-and-strategic-agent-profiles/)
[profiles](/guides/configuration/how-to-configure-yolo-and-strategic-agent-profiles/)
[Automate your workflow](/guides/configuration/how-to-create-project-rules-for-an-existing-project-astro-typescript-tailwind/)
### [Create project Rules for an existing project](/guides/configuration/how-to-create-project-rules-for-an-existing-project-astro-typescript-tailwind/)
[Create and maintain an AGENTS.md project rules file so coding agents always understand your project's setup, commands, architecture, and conventions.](/guides/configuration/how-to-create-project-rules-for-an-existing-project-astro-typescript-tailwind/)
[rules](/guides/configuration/how-to-create-project-rules-for-an-existing-project-astro-typescript-tailwind/)
[Automate your workflow](/guides/configuration/how-to-set-coding-best-practices/)
### [Set coding best practices](/guides/configuration/how-to-set-coding-best-practices/)
[Use Warp Rules to enforce coding style, TypeScript conventions, and documentation quality across AI-generated code.](/guides/configuration/how-to-set-coding-best-practices/)
[rules](/guides/configuration/how-to-set-coding-best-practices/)
[Automate your workflow](/guides/configuration/how-to-set-coding-preferences-with-rules/)
### [Set coding preferences with Rules](/guides/configuration/how-to-set-coding-preferences-with-rules/)
[Store your package manager, environment tool, and CLI preferences as Warp Rules so agents automatically use pnpm, miniconda, or your preferred tools.](/guides/configuration/how-to-set-coding-preferences-with-rules/)
[rules](/guides/configuration/how-to-set-coding-preferences-with-rules/)
[Automate your workflow](/guides/configuration/how-to-set-tech-stack-preferences-with-rules/)
### [Set tech stack preferences with Rules](/guides/configuration/how-to-set-tech-stack-preferences-with-rules/)
[Define your preferred frameworks and tech stack in Warp Rules so agents consistently use Astro, SvelteKit, Vite, or your tools of choice.](/guides/configuration/how-to-set-tech-stack-preferences-with-rules/)
[rules](/guides/configuration/how-to-set-tech-stack-preferences-with-rules/)
[Automate your workflow](/guides/configuration/how-to-set-up-self-serve-data-analytics-with-skills/)
### [Set up self-serve data analytics with skills](/guides/configuration/how-to-set-up-self-serve-data-analytics-with-skills/)
[Set up a self-serve data analytics workflow in Warp using two community Skills that map questions to dbt models and structure reproducible analyses.](/guides/configuration/how-to-set-up-self-serve-data-analytics-with-skills/)
[skills](/guides/configuration/how-to-set-up-self-serve-data-analytics-with-skills/)
[Automate your workflow](/guides/configuration/how-to-sync-your-monorepos/)
### [Sync your monorepos](/guides/configuration/how-to-sync-your-monorepos/)
[Define global Rules in Warp to keep monorepo schemas, server types, and client types automatically synchronized across repositories.](/guides/configuration/how-to-sync-your-monorepos/)
[rules](/guides/configuration/how-to-sync-your-monorepos/)
[Automate your workflow](/guides/configuration/how-to-use-agent-profiles-efficiently/)
### [Use Agent Profiles efficiently](/guides/configuration/how-to-use-agent-profiles-efficiently/)
[Compare Strategic and YOLO agent profiles side-by-side to choose the right balance of planning, safety, and speed for your project.](/guides/configuration/how-to-use-agent-profiles-efficiently/)
[profiles](/guides/configuration/how-to-use-agent-profiles-efficiently/)
[Work with agents](/guides/configuration/how-to-use-tokens-efficiently-with-ai-coding-agents/)
### [Use tokens efficiently](/guides/configuration/how-to-use-tokens-efficiently-with-ai-coding-agents/)
[Get more out of every token your coding agents use in Warp with model choice and routing, focused context, conversation management, and Rules.](/guides/configuration/how-to-use-tokens-efficiently-with-ai-coding-agents/)
[tokensagents](/guides/configuration/how-to-use-tokens-efficiently-with-ai-coding-agents/)
[Automate your workflow](/guides/configuration/trigger-reusable-actions-with-saved-prompts/)
### [Trigger reusable actions with saved prompts](/guides/configuration/trigger-reusable-actions-with-saved-prompts/)
[Save and share prompts in Warp Drive to automate commits, code reviews, and PR creation across your team.](/guides/configuration/trigger-reusable-actions-with-saved-prompts/)
[rules](/guides/configuration/trigger-reusable-actions-with-saved-prompts/)
[Build & deploy apps](/guides/devops/how-to-analyze-cloud-run-logs-gcloud/)
### [Analyze Cloud Run logs](/guides/devops/how-to-analyze-cloud-run-logs-gcloud/)
[Use Warp to pull, organize, and analyze Cloud Run production logs by severity with natural language prompts and automated Python scripts.](/guides/devops/how-to-analyze-cloud-run-logs-gcloud/)
[cloud](/guides/devops/how-to-analyze-cloud-run-logs-gcloud/)
[Build & deploy apps](/guides/devops/how-to-create-a-production-ready-docker-setup/)
### [Create a production-ready Docker setup](/guides/devops/how-to-create-a-production-ready-docker-setup/)
[Use Agents in Warp to generate optimized Dockerfiles, docker-compose configs, and .dockerignore files for multi-stage production deployments.](/guides/devops/how-to-create-a-production-ready-docker-setup/)
[docker](/guides/devops/how-to-create-a-production-ready-docker-setup/)
[Review & debug](/guides/devops/how-to-create-priority-matrix-for-database-optimization/)
### [Create a priority matrix for database optimization](/guides/devops/how-to-create-priority-matrix-for-database-optimization/)
[Prompt Warp to audit SQL queries, analyze execution plans, and generate a priority matrix ranking database optimizations by impact and effort.](/guides/devops/how-to-create-priority-matrix-for-database-optimization/)
[database](/guides/devops/how-to-create-priority-matrix-for-database-optimization/)
[Review & debug](/guides/devops/how-to-generate-unit-and-security-tests-to-debug-faster/)
### [Generate unit and security tests to debug faster](/guides/devops/how-to-generate-unit-and-security-tests-to-debug-faster/)
[Prompt Warp to generate comprehensive unit and security tests for REST APIs, including SQL injection, XSS, and auth validation checks.](/guides/devops/how-to-generate-unit-and-security-tests-to-debug-faster/)
[testing](/guides/devops/how-to-generate-unit-and-security-tests-to-debug-faster/)
[Review & debug](/guides/devops/how-to-prevent-secrets-from-leaking/)
### [Prevent secrets from leaking](/guides/devops/how-to-prevent-secrets-from-leaking/)
[Use Warp Rules and built-in Secret Redaction to prevent API keys and credentials from leaking in agent output, demos, and shared sessions.](/guides/devops/how-to-prevent-secrets-from-leaking/)
[cloud](/guides/devops/how-to-prevent-secrets-from-leaking/)
[Review & debug](/guides/devops/how-to-write-sql-commands-inside-a-postgres-repl/)
### [Write SQL commands inside a Postgres REPL](/guides/devops/how-to-write-sql-commands-inside-a-postgres-repl/)
[Use Agents in Warp inside a Postgres REPL to translate natural language into SQL queries — works with Node.js, Python, and MySQL too.](/guides/devops/how-to-write-sql-commands-inside-a-postgres-repl/)
[database](/guides/devops/how-to-write-sql-commands-inside-a-postgres-repl/)
[Build & deploy apps](/guides/devops/improve-your-kubernetes-workflow-kubectl-helm/)
### [Improve your Kubernetes workflow](/guides/devops/improve-your-kubernetes-workflow-kubectl-helm/)
[Streamline kubectl and Helm workflows with Warp's AI assistance, active suggestions, custom workflows, and synchronized panes.](/guides/devops/improve-your-kubernetes-workflow-kubectl-helm/)
[kubernetes](/guides/devops/improve-your-kubernetes-workflow-kubectl-helm/)
[Work with agents](/guides/external-tools/build-a-mattermost-bot-for-warp-factories/)
### [Build a Mattermost bot for Warp Factories](/guides/external-tools/build-a-mattermost-bot-for-warp-factories/)
[Build a Mattermost bot that discovers a Warp factory by name, dispatches tasks to it, and continues the conversation from replies in a thread.](/guides/external-tools/build-a-mattermost-bot-for-warp-factories/)
[Connect external services](/guides/external-tools/context7-mcp-update-astro-project-with-best-practices/)
### [Context7 MCP: update Astro project with best practices](/guides/external-tools/context7-mcp-update-astro-project-with-best-practices/)
[Use the Context7 MCP server to give Warp agents real-time access to framework documentation for automated project upgrades.](/guides/external-tools/context7-mcp-update-astro-project-with-best-practices/)
[mcp](/guides/external-tools/context7-mcp-update-astro-project-with-best-practices/)
[Connect external services](/guides/external-tools/figma-remote-mcp-create-a-website-from-a-figma-file-from-scratch/)
### [Figma remote MCP: create a website from a Figma file](/guides/external-tools/figma-remote-mcp-create-a-website-from-a-figma-file-from-scratch/)
[Connect Warp to Figma's remote MCP server via OAuth and generate front-end code directly from your design files.](/guides/external-tools/figma-remote-mcp-create-a-website-from-a-figma-file-from-scratch/)
[mcpfrontend](/guides/external-tools/figma-remote-mcp-create-a-website-from-a-figma-file-from-scratch/)
[Connect external services](/guides/external-tools/github-mcp-summarizing-open-prs-and-creating-gh-issues/)
### [GitHub MCP: summarize open PRs and create GitHub issues](/guides/external-tools/github-mcp-summarizing-open-prs-and-creating-gh-issues/)
[Connect the GitHub MCP server to Warp to summarize open PRs, create issues from TODO comments, and automate repo management.](/guides/external-tools/github-mcp-summarizing-open-prs-and-creating-gh-issues/)
[mcpcode-review](/guides/external-tools/github-mcp-summarizing-open-prs-and-creating-gh-issues/)
[Set up your environment](/guides/external-tools/how-to-set-up-claude-code/)
### [Set up Claude Code](/guides/external-tools/how-to-set-up-claude-code/)
[Set up Claude Code in Warp, configure it for your project, and learn productivity tips — from voice prompting to visual code review.](/guides/external-tools/how-to-set-up-claude-code/)
[third-party-tools](/guides/external-tools/how-to-set-up-claude-code/)
[Set up your environment](/guides/external-tools/how-to-set-up-codex-cli/)
### [Set up Codex CLI](/guides/external-tools/how-to-set-up-codex-cli/)
[Set up OpenAI's Codex CLI in Warp, configure it for your project, and learn productivity tips for faster AI-assisted coding workflows in Warp.](/guides/external-tools/how-to-set-up-codex-cli/)
[third-party-tools](/guides/external-tools/how-to-set-up-codex-cli/)
[Set up your environment](/guides/external-tools/how-to-set-up-gemini-cli/)
### [Set up Gemini CLI](/guides/external-tools/how-to-set-up-gemini-cli/)
[Set up Google's Gemini CLI in Warp, configure it for your project, and learn productivity tips for faster AI-assisted coding workflows.](/guides/external-tools/how-to-set-up-gemini-cli/)
[third-party-tools](/guides/external-tools/how-to-set-up-gemini-cli/)
[Set up your environment](/guides/external-tools/how-to-set-up-ollama/)
### [Set up Ollama](/guides/external-tools/how-to-set-up-ollama/)
[Install Ollama, run LLMs locally, compare model performance, and integrate local models into your apps using Warp.](/guides/external-tools/how-to-set-up-ollama/)
[third-party-tools](/guides/external-tools/how-to-set-up-ollama/)
[Set up your environment](/guides/external-tools/how-to-set-up-opencode/)
### [Set up OpenCode](/guides/external-tools/how-to-set-up-opencode/)
[Set up OpenCode in Warp, configure it for your project, and learn productivity tips for faster AI-assisted coding workflows.](/guides/external-tools/how-to-set-up-opencode/)
[third-party-tools](/guides/external-tools/how-to-set-up-opencode/)
[Connect external services](/guides/external-tools/linear-mcp-retrieve-issue-data/)
### [Linear MCP: retrieve issue data](/guides/external-tools/linear-mcp-retrieve-issue-data/)
[Add the Linear MCP server to Warp and query your issues, tasks, and assignments directly from the terminal.](/guides/external-tools/linear-mcp-retrieve-issue-data/)
[mcp](/guides/external-tools/linear-mcp-retrieve-issue-data/)
[Connect external services](/guides/external-tools/linear-mcp-updating-tickets-with-a-lean-build-approach/)
### [Linear MCP: update tickets with a lean build approach](/guides/external-tools/linear-mcp-updating-tickets-with-a-lean-build-approach/)
[Use Warp's Linear MCP integration to update ticket descriptions, propagate changes to subtasks, and maintain a lean build strategy.](/guides/external-tools/linear-mcp-updating-tickets-with-a-lean-build-approach/)
[mcp](/guides/external-tools/linear-mcp-updating-tickets-with-a-lean-build-approach/)
[Connect external services](/guides/external-tools/puppeteer-mcp-scraping-amazon-web-reviews/)
### [Puppeteer MCP: scrape Amazon web reviews](/guides/external-tools/puppeteer-mcp-scraping-amazon-web-reviews/)
[Configure the Puppeteer MCP server in Warp to automate browser tasks like navigating sites, scraping product data, and analyzing reviews.](/guides/external-tools/puppeteer-mcp-scraping-amazon-web-reviews/)
[mcp](/guides/external-tools/puppeteer-mcp-scraping-amazon-web-reviews/)
[Connect external services](/guides/external-tools/sentry-mcp-fix-sentry-error-in-empower-website/)
### [Sentry MCP: fix Sentry error in Empower website](/guides/external-tools/sentry-mcp-fix-sentry-error-in-empower-website/)
[Connect the Sentry MCP server to Warp, fetch live error data, diagnose stack traces, and auto-generate fixes for production issues.](/guides/external-tools/sentry-mcp-fix-sentry-error-in-empower-website/)
[mcp](/guides/external-tools/sentry-mcp-fix-sentry-error-in-empower-website/)
[Connect external services](/guides/external-tools/sqlite-and-stripe-mcp-basic-queries-you-can-make-after-set-up/)
### [SQLite and Stripe MCP: basic queries you can make after setup](/guides/external-tools/sqlite-and-stripe-mcp-basic-queries-you-can-make-after-set-up/)
[Connect SQLite and Stripe MCP servers to Warp and run conversational queries against your local database and payment data.](/guides/external-tools/sqlite-and-stripe-mcp-basic-queries-you-can-make-after-set-up/)
[mcpdatabase](/guides/external-tools/sqlite-and-stripe-mcp-basic-queries-you-can-make-after-set-up/)
[Connect external services](/guides/external-tools/using-mcp-servers-with-warp/)
### [Connect agents to MCP servers](/guides/external-tools/using-mcp-servers-with-warp/)
[Use MCP servers to connect Warp agents to developer tools like GitHub, Linear, Sentry, and Figma across local and cloud agent workflows.](/guides/external-tools/using-mcp-servers-with-warp/)
[mcp](/guides/external-tools/using-mcp-servers-with-warp/)
[Build & deploy apps](/guides/frontend/how-to-actually-code-ui-that-matches-your-mockup-react-tailwind/)
### [Code UI that matches your mockup](/guides/frontend/how-to-actually-code-ui-that-matches-your-mockup-react-tailwind/)
[Prompt Warp to generate pixel-perfect React + Tailwind code from design mockups, with structured specs and iterative refinement.](/guides/frontend/how-to-actually-code-ui-that-matches-your-mockup-react-tailwind/)
[frontend](/guides/frontend/how-to-actually-code-ui-that-matches-your-mockup-react-tailwind/)
[Build & deploy apps](/guides/frontend/how-to-replace-a-ui-element-in-warp-rust-codebase/)
### [Replace a UI element in Warp](/guides/frontend/how-to-replace-a-ui-element-in-warp-rust-codebase/)
[Use Agent Mode in Warp to plan and execute icon replacements across a large Rust codebase — with live diffs, auto-compilation, and self-correction.](/guides/frontend/how-to-replace-a-ui-element-in-warp-rust-codebase/)
[frontend](/guides/frontend/how-to-replace-a-ui-element-in-warp-rust-codebase/)
[Set up your environment](/guides/getting-started/10-coding-features-you-should-know/)
### [10 coding features you should know](/guides/getting-started/10-coding-features-you-should-know/)
[Discover 10 essential coding features in Warp — file search, tabbed editor, find and replace, syntax highlighting, code review panel, and more.](/guides/getting-started/10-coding-features-you-should-know/)
[getting-startedagents](/guides/getting-started/10-coding-features-you-should-know/)
[Set up your environment](/guides/getting-started/how-to-customize-warps-appearance/)
### [Customize Warp's appearance](/guides/getting-started/how-to-customize-warps-appearance/)
[Customize Warp's themes, input placement, AI settings, codebase indexing, team collaboration, and visual appearance to fit your workflow.](/guides/getting-started/how-to-customize-warps-appearance/)
[getting-started](/guides/getting-started/how-to-customize-warps-appearance/)
[Set up your environment](/guides/getting-started/how-to-make-warps-ui-more-minimal/)
### [Make Warp's UI more minimal](/guides/getting-started/how-to-make-warps-ui-more-minimal/)
[Reduce visual noise in Warp by disabling UI elements, switching to a minimal theme, and hiding the tab bar.](/guides/getting-started/how-to-make-warps-ui-more-minimal/)
[getting-started](/guides/getting-started/how-to-make-warps-ui-more-minimal/)
[Review & debug](/guides/getting-started/how-to-master-warps-code-review-panel/)
### [Master Warp's Code Review panel](/guides/getting-started/how-to-master-warps-code-review-panel/)
[Use Warp's Code Review Panel to view file diffs, edit code inline, componentize changes, and commit directly — all without leaving the terminal.](/guides/getting-started/how-to-master-warps-code-review-panel/)
[getting-startedcode-review](/guides/getting-started/how-to-master-warps-code-review-panel/)
[Set up your environment](/guides/getting-started/welcome-to-warp/)
### [Welcome to Warp](/guides/getting-started/welcome-to-warp/)
[Get oriented with Warp's agentic terminal. Learn the basics of prompt-based coding, blending terminal and agent workflows, and navigating the interface.](/guides/getting-started/welcome-to-warp/)
[getting-started](/guides/getting-started/welcome-to-warp/)
# Build a self-improving agent
Canonical page: [/guides/agent-workflows/build-a-self-improving-agent/](https://docs.warp.dev/guides/agent-workflows/build-a-self-improving-agent/)
> Build an outer loop where a scheduled agent reviews past runs, learns from corrections, and proposes skill file updates.
A self-improving agent is the outer loop of the [software factory](/guides/agent-workflows/set-up-a-software-factory) you’ve built in the previous guides. It watches how maintainers correct the inner-loop agents — relabeled issues, edited comments, changed code — and opens a pull request to improve the skill files that drive those agents. Every correction from a teammate becomes a proposed improvement to the factory.
This guide shows how to build the outer loop for a triage agent. The same pattern applies to any agent role.
Note
The outer loop proposes improvements; it doesn’t apply them silently. Every change to a skill file goes through a normal pull request review before merging. The team decides what improves; the agent proposes it.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* A working inner loop with at least one agent running ([set up your software factory](/guides/agent-workflows/set-up-a-software-factory))
* A Warp account ([sign up at warp.dev](https://www.warp.dev))
* A cloud environment with access to your repository ([create one](/platform/environments))
## Why principles beat rules
[Section titled “Why principles beat rules”](#why-principles-beat-rules)
Most agent skills start as a list of rules, but rules overfit. They break when a situation arrives that the rules didn’t anticipate, and a longer rule list makes the skill harder to maintain.
Effective skill files describe **principles**: durable ideas about how to approach a class of situation. A principle, e.g., “confirm that a bug report includes enough context for a fresh contributor to reproduce the issue”, transfers to situations the original rules didn’t cover.
When the outer loop proposes a skill update, it should always aim for a principle that generalizes, not a new rule that handles one more edge case.
## 1. Collect correction signals
[Section titled “1. Collect correction signals”](#1-collect-correction-signals)
The outer loop needs signals that the inner loop got something wrong. For a triage agent, the most useful signals are:
* **Maintainer relabels** — A maintainer changes a label the triage agent applied (for example, `needs-info` → `ready-to-implement`).
* **Maintainer re-opens** — A maintainer reopens an issue the triage agent closed.
* **Follow-up comments** — A maintainer explains in a comment why the triage agent’s assessment was wrong.
GitHub captures all of these in the issue timeline and audit log.
The [`update-triage`](https://github.com/warpdotdev/oz-for-oss/blob/main/.agents/skills/update-triage/SKILL.md) skill in `warpdotdev/oz-for-oss` includes a Python helper script (`aggregate_triage_feedback.py`) that collects these signals for the past N days. Copy and adapt it for your repository.
## 2. Create the update skill
[Section titled “2. Create the update skill”](#2-create-the-update-skill)
1. Create `.agents/skills/update-triage/SKILL.md` with the following content as a starting point:
```markdown
---
name: update-triage
description: Review recent maintainer corrections to the triage agent's output and propose skill file updates that generalize from those corrections.
---
# Update triage skill
You are reviewing recent maintainer corrections to the triage agent's output.
## What to look for
For each correction:
1. Identify what the triage agent did (the original label or comment).
2. Identify what the maintainer did instead (the correction).
3. Ask: why would the triage agent have gotten this wrong?
4. Ask: what principle would prevent this class of error in the future?
## What to update
Update only the triage-issue-local companion skill for this repository.
Write principles, not rules. Do not update the shared triage-issue skill.
Commit changes to a branch named oz-agent/update-triage.
Do not push directly to main. Open a pull request for human review.
```
2. For the complete implementation, including the correction-collection script, write-surface restrictions, and PR-opening workflow, use the [`update-triage` skill from `warpdotdev/oz-for-oss`](https://github.com/warpdotdev/oz-for-oss/blob/main/.agents/skills/update-triage/SKILL.md) as your reference.
## 3. Schedule the outer loop
[Section titled “3. Schedule the outer loop”](#3-schedule-the-outer-loop)
Weekly is a good starting cadence: it processes the previous week’s corrections and opens PRs for review at the start of the week.
1. Create a scheduled cloud agent from the Oz CLI:
```bash
oz schedule create \
--name update-triage-weekly \
--skill update-triage \
--environment YOUR_ENVIRONMENT_SLUG \
--cron "0 9 * * 1"
```
Or, from the Oz web app: open **Agents** > **Schedules**, click **New schedule**, and set the skill, environment, and cron expression.
2. Replace `YOUR_ENVIRONMENT_SLUG` with the slug of your Automation Platform environment.
See [Scheduled agents](/platform/triggers/scheduled-agents) for the full reference.
## 4. Review the proposed skill changes
[Section titled “4. Review the proposed skill changes”](#4-review-the-proposed-skill-changes)
Each time the outer loop runs, it opens a pull request with proposed changes to the `triage-issue-local` companion skill. Review that PR the same way you would review any other code change:
* Does the proposed principle generalize correctly, or is it another specific rule in disguise?
* Is the change scoped to the companion skill rather than the shared base skill?
* Does it improve the agent’s reasoning, or does it just patch one edge case?
Merge the PR when the improvement is sound. Close it if the proposal is too narrow or incorrect.
Over time, the companion skill accumulates a clear description of how your team thinks about issue triage — not as a list of rules, but as a set of principles that a new maintainer or a new agent can learn from.
## Productivity tips
[Section titled “Productivity tips”](#productivity-tips)
* **Give feedback in the right place** — The outer loop collects signals from GitHub. If you want the triage agent to learn from a correction, add a comment to the issue explaining why the original label was wrong. That comment becomes signal for the next outer-loop run.
* **Apply the pattern to other agent roles** — The [`update-pr-review`](https://github.com/warpdotdev/oz-for-oss/blob/main/.agents/skills/update-pr-review/SKILL.md) and [`update-dedupe`](https://github.com/warpdotdev/oz-for-oss/blob/main/.agents/skills/update-dedupe/SKILL.md) skills from `warpdotdev/oz-for-oss` apply the same outer-loop pattern to the PR reviewer and deduplication agents.
* **Don’t skip the PR review** — The value of the outer loop is compounding improvement, not speed. A bad skill change that merges silently creates more work than it saves. Every proposed change should get a review.
## Next steps
[Section titled “Next steps”](#next-steps)
* [Self-improvement in Warp Factories](/factories/measure-and-improve/self-improvement/) — The managed version of this outer loop, run inside a factory.
* [Set up your software factory](/guides/agent-workflows/set-up-a-software-factory) — The inner loop the outer loop improves.
* [Run a software factory in the cloud](/guides/agent-workflows/run-a-software-factory-in-the-cloud) — Move the loop to the Automation Platform for team-wide visibility.
* [Scheduled agents](/platform/triggers/scheduled-agents) — Full reference for running cloud agents on a cadence.
* [`warpdotdev/oz-for-oss`](https://github.com/warpdotdev/oz-for-oss) — The complete reference implementation including all outer-loop skills.
* [Skills](/agents/capabilities/skills) — How skill files work in Warp and the Automation Platform.
# Build a triage agent for your issue backlog
Canonical page: [/guides/agent-workflows/build-a-triage-agent/](https://docs.warp.dev/guides/agent-workflows/build-a-triage-agent/)
> Create a triage agent that reviews new GitHub issues, applies labels, and flags open questions. Your backlog stays actionable without manual effort.
Learn how to use the Automation Platform to build a triage agent that reviews each new GitHub issue for clarity, applies labels, and flags open questions before implementation begins. After completing the steps in this guide, you will have a working triage skill deployed as a GitHub Action. This is the first agent in your [software factory](/factories/).
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* A Warp account ([sign up at warp.dev](https://www.warp.dev))
* A GitHub repository with Issues enabled
* A cloud environment with access to your repository ([create one](/platform/environments/configuring-environments/#create-an-environment-with-guided-setup))
* A Warp API key added to your CI secrets as `WARP_API_KEY` ([create one](/agents/cli/oz-cli/api-keys/#from-the-web-app-recommended))
## 1. Define your triage criteria
[Section titled “1. Define your triage criteria”](#1-define-your-triage-criteria)
Before writing a skill, decide what your triage agent should do. A good triage agent answers three questions for every new issue:
1. Is the report clear enough to act on?
2. Is it a duplicate of an existing issue?
3. What label should it have?
Identify:
* The label taxonomy for your repository (e.g., `bug`, `enhancement`, `ready-to-implement`, `needs-info`, `duplicate`).
* Who owns each area of the codebase. This becomes your `STAKEHOLDERS` file.
* What makes an issue “ready to implement”: does it need a reproduction step, version number, or proposed approach?
You will encode these decisions in a skill file in the next step.
## 2. Create the triage skill
[Section titled “2. Create the triage skill”](#2-create-the-triage-skill)
A [skill](/agents/capabilities/skills) is a markdown file that defines the agent’s behavior. It tells the agent what to analyze, how to classify results, and what to output.
1. Create a `.agents/skills/triage-issue/` directory in your repository with a `SKILL.md` file.
2. Copy the [`triage-issue` skill from `warpdotdev/oz-for-oss`](https://github.com/warpdotdev/oz-for-oss/blob/main/.agents/skills/triage-issue/SKILL.md) into your repository. This is the production triage skill Warp uses for its own open source repository.
3. Adapt the skill for your repository:
* Replace the label taxonomy with your labels.
* Update the ownership section to reflect your codebase.
* Adjust the definition of “ready to implement” to match your team’s requirements.
4. Create `.github/issue-triage/config.json` with your label taxonomy. See the [`config.json` from `warpdotdev/oz-for-oss`](https://github.com/warpdotdev/oz-for-oss/blob/main/.github/issue-triage/config.json) for the format.
Write the skill file in terms of principles, not rules. For example:
* A rule says “if the reporter doesn’t include a reproduction step, add `needs-info`.”
* A principle says “confirm that a bug report includes enough context for a fresh contributor to reproduce the issue.”
Principles transfer to situations the original rules didn’t cover, while long rule lists overfit and become difficult to maintain.
Tip
The [`bootstrap-issue-config`](https://github.com/warpdotdev/oz-for-oss/blob/main/.agents/skills/bootstrap-issue-config/SKILL.md) skill can generate initial `config.json` and `STAKEHOLDERS` files by analyzing your existing labels and `CODEOWNERS` file. Run it once when setting up a new repository.
## 3. Test the triage agent locally
[Section titled “3. Test the triage agent locally”](#3-test-the-triage-agent-locally)
Before deploying to GitHub Actions, test the triage agent against a real issue using the Oz CLI:
```bash
oz agent run \
--skill .agents/skills/triage-issue \
--prompt "Triage GitHub issue #ISSUE_NUMBER in OWNER/REPO" \
--share
```
The `--share` flag generates a session link your team can use to inspect what the agent did. Review the session output to confirm that the labels and comments are what you expect. If something is wrong, refine the skill file and run again.
For the full reference of `oz agent run` flags, see the [Oz CLI reference](/agents/cli/oz-cli/).
## 4. Deploy with GitHub Actions
[Section titled “4. Deploy with GitHub Actions”](#4-deploy-with-github-actions)
Once the skill output looks correct, deploy it as a GitHub Action that triggers automatically when a new issue is opened.
1. In your repository, create `.github/workflows/triage-issue.yml` with the following content:
```yaml
name: Triage new issues
on:
issues:
types: [opened]
permissions:
issues: write
jobs:
triage:
runs-on: ubuntu-latest
steps:
- uses: actions/checkout@v4
- uses: warpdotdev/oz-agent-action@v1
with:
skill: triage-issue
prompt: |
Triage GitHub issue #${{ github.event.issue.number }} in ${{ github.repository }}.
Issue title: ${{ github.event.issue.title }}
Issue body: ${{ github.event.issue.body }}
environment: YOUR_OZ_ENVIRONMENT_SLUG
warp_api_key: ${{ secrets.WARP_API_KEY }}
env:
GITHUB_TOKEN: ${{ secrets.GITHUB_TOKEN }}
```
2. Replace `YOUR_OZ_ENVIRONMENT_SLUG` with the slug of the Automation Platform environment you created in the prerequisites.
3. Add `WARP_API_KEY` to your repository’s GitHub Actions secrets under **Settings** > **Secrets and variables** > **Actions**.
See [GitHub Actions integration](/platform/integrations/github-actions) for the full setup guide for `warpdotdev/oz-agent-action`.
## 5. Review and improve
[Section titled “5. Review and improve”](#5-review-and-improve)
Watch the first few runs in the [Oz web app](https://oz.warp.dev) to verify the agent is labeling and commenting correctly. When you disagree with the agent, e.g., when you relabel an issue or edit a comment, note the pattern. Patterns you see repeatedly are signals to update your skill file.
Add repo-specific context without forking the core skill by creating a `triage-issue-local` companion skill. This file specializes the base skill for your repository (your label taxonomy, ownership map, and definition of readiness) while keeping the shared skill stable. See the [docs repo example](https://github.com/warpdotdev/docs/blob/main/.agents/skills/triage-issue-local/SKILL.md) for the companion skill pattern.
## Next steps
[Section titled “Next steps”](#next-steps)
* [Warp Factories overview](/factories/) — Warp’s product for running this same loop without the manual wiring.
* [Factory agents](/factories/factory-agents/#triage) — The Triage agent role, doing the same job as the agent you just built.
* [Factory skills](/factories/factory-skills/) — How Warp Factories scopes and shares a skill file like the one you just wrote.
* [Write product and tech specs with agents](/guides/agent-workflows/write-product-and-tech-specs-with-agents) — Add the spec role once your backlog is well-triaged.
* [Build a self-improving agent](/guides/agent-workflows/build-a-self-improving-agent) — Automate skill improvement based on your corrections.
* [GitHub Actions integration](/platform/integrations/github-actions) — Full documentation for `warpdotdev/oz-agent-action`.
* [Run agents unattended](/guides/agent-workflows/how-to-run-unattended-agents) — Broader patterns for cloud agents triggered by external events.
# Share agent context in GitHub PRs
Canonical page: [/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/](https://docs.warp.dev/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/)
> Share a Warp agent session or cloud agent run link in a GitHub pull request so reviewers can inspect the context behind agent-generated changes.
When an agent helps prepare a pull request, reviewers need the execution context behind the diff: the original prompt, plan, commands, validation results, code changes, and decisions that still need human review.
Add a Warp session or cloud agent run link to the PR description or a PR comment. That link gives reviewers a record of the agent’s work alongside the GitHub diff.
Use these Warp docs and surfaces to collect the right context:
* [Agent Session Sharing](/agents/local-agents/session-sharing/) for local Warp agents or third-party CLI agents running in Warp.
* [Cloud agent session sharing](/platform/viewing-cloud-agent-runs/) for cloud agent runs started from Slack, Linear, GitHub Actions, schedules, the Oz CLI, or the API.
* The [Code Review panel](/code/code-review/) and [Interactive Code Review](/agents/local-agents/interactive-code-review/) to inspect and refine the actual code diff before or after you share the PR.
## What to include in the PR
[Section titled “What to include in the PR”](#what-to-include-in-the-pr)
Add the shared session link near the top of the PR description or as a pinned PR comment. Pair it with a short review summary so teammates can decide what to inspect first.
At minimum, include:
* **Goal** - What the agent was asked to do.
* **Agent context** - Link to the shared Warp session or cloud agent run.
* **Changed files** - The main areas reviewers should inspect.
* **Validation** - Tests, lint, typecheck, build, or manual checks the agent or author ran.
* **Known risks** - Anything the agent could not verify, skipped, or changed speculatively.
* **Reviewer asks** - Specific files, behaviors, or decisions that need human review.
## PR comment template
[Section titled “PR comment template”](#pr-comment-template)
```markdown
## Agent-generated change summary
**Goal:** <what the agent was asked to do>
**Agent session:** <shared Warp session or cloud agent run link>
**Changed files:** <key files or directories>
**Validation:** <commands run and results>
**Known risks:** <untested areas, assumptions, follow-ups>
**Reviewer asks:** <specific review focus>
Notes:
- The session link contains the agent prompt, plan, commands, logs, output, and follow-up messages where available.
- Please review the code diff and the agent context before merging.
```
## 1. Share the agent session or cloud run
[Section titled “1. Share the agent session or cloud run”](#1-share-the-agent-session-or-cloud-run)
Choose the link based on where the agent ran.
### Local agent or third-party CLI agent in Warp
[Section titled “Local agent or third-party CLI agent in Warp”](#local-agent-or-third-party-cli-agent-in-warp)
If the agent ran locally in Warp, share the session:
1. Open the agent session in Warp.
2. In the conversation pane header, open the three-dot menu, then click **Share session**. Do not use the top-level **Share** icon if you need the session transcript.
3. Choose the scrollback range to include.
4. Copy the shared session link.
5. Paste the link into the PR description or a PR comment.
See [Agent Session Sharing](/agents/local-agents/session-sharing/) for the full sharing flow.
### Cloud agent run
[Section titled “Cloud agent run”](#cloud-agent-run)
If the agent ran in the cloud, use the cloud run session link:
1. Open the run from the [Agent Management Panel](/platform/managing-cloud-agents/) in the Warp app or the [Runs page in the Oz web app](/platform/oz-web-app/#runs).
2. Confirm the session shows the run context reviewers need.
3. Copy the cloud agent session link.
4. Paste the link into the PR description or a PR comment.
See [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/) for details.
## 2. Review the diff before handing it off
[Section titled “2. Review the diff before handing it off”](#2-review-the-diff-before-handing-it-off)
Before asking teammates to review the PR, inspect the code yourself in Warp:
1. Open the [Code Review panel](/code/code-review/).
2. Compare the branch against the PR base branch, not just uncommitted changes.
3. Review the changed files, revert obvious mistakes, and leave inline comments for the agent if it should revise anything.
4. Run your project’s tests, lint, typecheck, or build.
5. Add validation results to the PR summary.
For a detailed local workflow, see [How to review AI-generated code](/guides/agent-workflows/how-to-review-ai-generated-code/) and [Interactive Code Review](/agents/local-agents/interactive-code-review/).
## 3. Make the agent context easy to review
[Section titled “3. Make the agent context easy to review”](#3-make-the-agent-context-easy-to-review)
Reviewers should not have to read an entire transcript to understand what happened. In the PR summary, call out the most important parts of the session:
* The original prompt or task source.
* The plan the agent followed.
* Commands that changed or validated the code.
* Files or directories that need extra attention.
* Any failed commands and how they were resolved.
* Any assumptions the agent made.
If the PR came from an automated workflow, include the trigger source too. For example: Slack thread, Linear issue, GitHub Actions workflow, scheduled agent, Oz CLI command, or API call.
## 4. Watch for sensitive context before sharing
[Section titled “4. Watch for sensitive context before sharing”](#4-watch-for-sensitive-context-before-sharing)
Shared sessions can include prompts, terminal output, logs, command history, environment details, and other scrollback. Before putting a session link in a PR:
* Check whether the session includes secrets, tokens, private customer data, or unrelated terminal output.
* Choose the narrowest useful scrollback range for local session sharing.
* Prefer links visible only to the reviewers who need the context.
* If the agent produced logs or artifacts with sensitive values, remove or rotate those values before broader sharing.
See [Secret Redaction](/support-and-community/privacy-and-security/secret-redaction/) for more on how Warp helps detect secrets.
## 5. Keep the PR review focused
[Section titled “5. Keep the PR review focused”](#5-keep-the-pr-review-focused)
Use the session link to make review faster, not to replace review. The GitHub diff is still the source of truth for what will merge.
Good reviewer asks:
* “Check the migration and rollback path in `db/migrations/`.”
* “Verify the agent’s test coverage for the auth edge cases.”
* “Review the session commands around the failing lint step and the final fix.”
* “Confirm whether the agent’s assumption about the API contract is correct.”
Avoid vague asks like “review the agent output.” Point reviewers to the decision, file, or validation result that needs human judgment.
## Next steps
[Section titled “Next steps”](#next-steps)
* Use [Agent Session Sharing](/agents/local-agents/session-sharing/) to share local or third-party agent sessions.
* Use [Cloud agent session sharing](/platform/viewing-cloud-agent-runs/) to inspect cloud agent runs.
* Use [Code Review panel](/code/code-review/) to review Git diffs in Warp.
* Use [Interactive Code Review](/agents/local-agents/interactive-code-review/) to leave inline comments and send feedback back to an agent.
# Edit agent code in Warp
Canonical page: [/guides/agent-workflows/how-to-edit-agent-code-in-warp/](https://docs.warp.dev/guides/agent-workflows/how-to-edit-agent-code-in-warp/)
> Review, edit, and refine AI-generated code diffs directly in Warp — accept, reject, or modify changes before applying them.
Warp lets you see, edit, and refine AI-generated code diffs directly within the app.\
This makes debugging and bug-fix workflows fast, transparent, and interactive.

***
### 1. Starting an agent task
[Section titled “1. Starting an agent task”](#1-starting-an-agent-task)
When you start an agent task, Warp:
1. Uses your prompt and context
2. Builds a task list
3. Searches across your codebase using tools like:
* Grep
* Codebase embeddings
* Semantic search
Warp shows progress step-by-step, including what it’s searching and which files are being modified.
***
### 2. Reviewing diffs
[Section titled “2. Reviewing diffs”](#2-reviewing-diffs)
Warp generates diffs for every proposed change.\
You can:
* Accept changes
* Refine them with a follow-up prompt (`Cmd+R`)
* Or directly edit the code in the inline editor view
This editor view works like a lightweight IDE — perfect for quick corrections before applying.
***
### 3. Applying or skipping changes
[Section titled “3. Applying or skipping changes”](#3-applying-or-skipping-changes)
Once you’re happy with a diff:
* Click **Apply Changes** to accept it
* Or **Fast-Forward** to let Warp automatically continue the rest of the fix sequence
You can control this level of autonomy globally in **Settings** > **Agents** > **Profiles**.
***
### 4. Compiling and verifying fixes
[Section titled “4. Compiling and verifying fixes”](#4-compiling-and-verifying-fixes)
After applying changes, you can immediately test your build, like:
```bash
cargo run
```
Warp monitors compilation, verifies results, and runs post-checks automatically.
***
### 5. Visual verification
[Section titled “5. Visual verification”](#5-visual-verification)
In this example, the bug involved a checkbox not being honored in the UI.\
\
After the agent’s fix:
* The checkbox logic now works as intended
* The model picker toggles correctly
* The UI behaves as expected
# Explain your codebase using Warp (Rust codebase)
Canonical page: [/guides/agent-workflows/how-to-explain-your-codebase-using-warp-rust-codebase/](https://docs.warp.dev/guides/agent-workflows/how-to-explain-your-codebase-using-warp-rust-codebase/)
> Use Warp's coding agents with semantic and symbol search to explore, understand, and modify unfamiliar codebases — demonstrated on a large Rust project.
Learn how to use Warp’s agents to explore and understand large, unfamiliar codebases — using semantic and symbol-level search.

***
## Overview
[Section titled “Overview”](#overview)
This walkthrough shows:
* How Warp explains unknown sections of code
* How it combines semantic and keyword searches
* How to use these insights to modify UI components
***
1. #### Prompt
[Section titled “Prompt”](#prompt)
```plaintext
Please explain how the agent popup code is structured,
where it lives in the codebase,
and how it is rendered and called.
I want to understand the full data flow and structure
so I can add a new agent button to it.
```
2. #### How Warp’s agent searches
[Section titled “How Warp’s agent searches”](#how-warps-agent-searches)
Warp begins by using **semantic (vectorized) search** to locate relevant files.\
Once it finds probable matches (e.g., `agent_management_popup.rs`), it switches to **symbolic search** (`grep` and direct code reads).
Warp intelligently reads large files (splitting them into smaller chunks) to extract relevant definitions and render logic.
3. #### Generated explanation
[Section titled “Generated explanation”](#generated-explanation)
Warp returns a full breakdown:
* File paths where the popup is defined
* How it’s rendered within the workspace
* Which actions and UI components trigger it
* A step-by-step view of data flow through the popup component
# Review AI-generated code
Canonical page: [/guides/agent-workflows/how-to-review-ai-generated-code/](https://docs.warp.dev/guides/agent-workflows/how-to-review-ai-generated-code/)
> Review AI-generated code in Warp with visual diffs and inline comments. Use this workflow with Claude Code, Codex, or any CLI agent.
Coding agents can produce hundreds of lines of code in seconds, but shipping that code without review is risky. In Warp, you can use visual diffs and inline comments to catch common issues and give the agent structured feedback it can act on. Plan on about 10 minutes to complete.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **A Git-tracked project** - Code Review in Warp works with any Git repository.
* **A coding agent** - Use the Warp Agent or a supported third-party CLI agent: [Claude Code](/guides/external-tools/how-to-set-up-claude-code/), [Codex](/guides/external-tools/how-to-set-up-codex-cli/), [Gemini CLI](/guides/external-tools/how-to-set-up-gemini-cli/), or [OpenCode](/guides/external-tools/how-to-set-up-opencode/). See [Third-party CLI agents](/agents/cli-agents/overview/) for the full list.
## Why review matters
[Section titled “Why review matters”](#why-review-matters)
Agents are fast but imperfect. An agent can hallucinate imports, introduce subtle logic errors, make poor architectural decisions, or duplicate code. Reviewing agent output turns agent-assisted development into a workflow you can trust.
Review AI-generated code for the following issues.
* **Hallucinated imports** - Referencing packages or modules that don’t exist in your project.
* **Redundant logic** - Duplicating existing functionality instead of reusing it.
* **Questionable architectural decisions** - Adding new patterns instead of following existing ones, or restructuring code in ways that conflict with your project’s architecture.
* **Security gaps** - Hardcoding credentials, omitting input validation, or using overly broad access controls.
* **Style drift** - Ignoring your project’s conventions for naming, error handling, or file structure.
* **Incomplete error handling** - Writing happy-path code that crashes on edge cases.
## 1. Give the agent a task
[Section titled “1. Give the agent a task”](#1-give-the-agent-a-task)
Start by giving the agent a task. Try the following prompt:
```text
Fix the authentication middleware to handle expired tokens gracefully
```
The agent will modify one or more files.
## 2. Open the Code Review panel
[Section titled “2. Open the Code Review panel”](#2-open-the-code-review-panel)
Once the agent has finished the task, open Warp’s [Code Review panel](/code/code-review/) to see every file that changed. Open the panel in any of the following ways:
* **Keyboard shortcut** - Press `⌘+Shift++` (macOS) or `Ctrl+Shift++` (Windows/Linux).
* **Git diff chip** - Click the diff chip in the terminal input that shows files modified and lines changed.
* **Review changes button** - After an agent conversation, click **Review changes** at the bottom of the conversation.
* **Tab bar** - Click the Code Review button in the top-right corner.
The Code Review button.
The panel shows all uncommitted changes as a visual diff, grouped by file. Additions are highlighted in green with a `+` prefix, removals in red with a `-` prefix.
Code Review panel with diffs.
## 3. Review diffs by file
[Section titled “3. Review diffs by file”](#3-review-diffs-by-file)
Use the Code Review panel to inspect each changed file, compare changes against a base branch, and edit the diff when needed:
* **Browse all changed files** - Use the file sidebar.
* **Choose a comparison view** - Use the comparison menu to inspect uncommitted changes, compare against the detected `main` or `master` branch, or choose another branch.
* **Edit a diff** - Click anywhere in the code to edit directly in the panel.
Pay particular attention to imports, error handling, and code that touches security or authentication.
Changed files sidebar.
## 4. Leave inline comments on issues
[Section titled “4. Leave inline comments on issues”](#4-leave-inline-comments-on-issues)
Click **Add comment** on any line or block of code, then describe the change. Warp anchors each comment to the exact file and line, so the agent knows precisely what to fix. Add as many comments as you need before you submit. Warp sends the complete batch at once, rather than asking the agent to process changes one at a time.
Inline comments on specific diff lines.
## 5. Submit all comments to the agent
[Section titled “5. Submit all comments to the agent”](#5-submit-all-comments-to-the-agent)
Once you’ve reviewed each file and left comments, submit the complete batch. The agent applies the requested changes in one pass and returns an updated diff.
Review the updated diff to verify the fixes. Repeat the cycle until the code meets your standards: comment, submit, then review.
Note
This workflow applies to any running CLI agent session in Warp. You can leave inline comments on a diff and send them back to the agent session.
## 6. Run your project’s checks before committing
[Section titled “6. Run your project’s checks before committing”](#6-run-your-projects-checks-before-committing)
Before accepting the changes, run your project’s test suite, linter, and type checker. Agent-generated code can pass a visual review and still fail automated checks.
```bash
# Example: run tests and lint
npm test && npm run lint
```
If checks fail, you can either fix the issues manually in the Code Review panel or send the error output back to the agent as context for another iteration.
### Quick review checklist
[Section titled “Quick review checklist”](#quick-review-checklist)
* [ ] Imports resolve.
* [ ] New code doesn’t duplicate existing functionality.
* [ ] Credentials aren’t hardcoded.
* [ ] Error handling covers failure cases.
* [ ] Style matches your project.
* [ ] Tests pass.
* [ ] The agent changed only what you asked.
## Productivity tips
[Section titled “Productivity tips”](#productivity-tips)
* **Attach diffs as context** - Select a diff hunk in the Code Review panel and attach it to your next prompt. This grounds the agent’s response in your actual code changes. See [Selection as context](/agents/local-agents/agent-context/selection-as-context/) for details.
* **Revert individual hunks** - Revert one change from the Code Review panel without undoing the rest of the agent’s work.
* **Compare against main** - Switch the diff view to “Changes vs. main” to see how the agent’s work fits into the full scope of your branch, not just the latest edits.
* **Use Rules to prevent recurring issues** - If the agent repeatedly makes the same mistake, such as using incorrect import paths or naming conventions, add a [Rule](/agents/capabilities/rules/) with your project’s standards.
## Next steps
[Section titled “Next steps”](#next-steps)
You now have a structured workflow for reviewing AI-generated code in Warp. It combines visual diff review, inline comments, and batch feedback.
Explore related guides and features:
* [Attach agent session context to GitHub PRs](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/) to give reviewers the full context behind agent-generated changes.
* [Run multiple agents at once](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/) to compare their outputs on the same task.
* [Code Review panel](/code/code-review/) for a full reference to Code Review features.
* [Interactive Code Review](/agents/local-agents/interactive-code-review/) for detailed instructions on inline comments and batch feedback.
# Review PRs like a senior dev
Canonical page: [/guides/agent-workflows/how-to-review-prs-like-a-senior-dev/](https://docs.warp.dev/guides/agent-workflows/how-to-review-prs-like-a-senior-dev/)
> Use Warp's agent to understand large pull requests, identify risky changes, and investigate potential issues before leaving review comments.
Warp’s agent can help you understand a large pull request, identify risky changes, and investigate potential issues before you leave review comments. This guide walks through how to give the agent enough context, ask for focused feedback, and verify its findings.

## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* A **Git-tracked project** with a branch or open PR to review
* The [GitHub CLI](https://cli.github.com) (`gh`) if you want to pull diffs or view PR metadata
## 1. Give the agent context
[Section titled “1. Give the agent context”](#1-give-the-agent-context)
The quality of the review depends on the quality of context you provide. Before prompting, gather the pieces the agent needs:
**Pull the PR goal.** The diff alone doesn’t tell the agent why changes were made. Start with the PR description:
```bash
gh pr view PR_NUMBER
```
**Get the diff.** The most focused way is:
```bash
# Patch-level diff via GitHub CLI
gh pr diff PR_NUMBER
# Or, if the branch is checked out locally
git diff main...<your-branch>
```
**Point the agent at key files.** If you know which areas the PR touches, use `@path/to/file` in your prompt to give the agent direct access to those files. This lets it read the surrounding code — not just the changed lines — which is important for catching regressions and missing test coverage.
**Run the test suite first.** If you have the branch checked out locally, run your tests before asking for a review. A failing test is faster to identify than a regression buried in prose.
Open a new agent session in Warp, navigate to the project directory, then attach context by selecting terminal output blocks or using `@file` references in your prompt.
## 2. Ask for focused feedback
[Section titled “2. Ask for focused feedback”](#2-ask-for-focused-feedback)
With context attached, give the agent a clear, goal-oriented prompt. Keep it direct. Focused prompts produce more actionable output than heavy templates. For example:
```plaintext
I'm reviewing PR #PR_NUMBER. The goal is: [paste or summarize the PR description].
I've attached the diff. Please:
1. Check correctness — look for logic errors, off-by-one issues, or incorrect assumptions.
2. Check for regressions — does anything touch code paths that existing tests don't cover?
3. Flag security concerns — missing input validation, improper auth checks, hardcoded secrets.
4. Note missing or inadequate tests.
5. For each changed file, look at the surrounding code too, not just the changed lines. Call out anything that looks off in context.
```
Adjust the emphasis based on what the PR does. A database migration warrants different scrutiny than a UI refactor.
## 3. Verify the agent’s findings
[Section titled “3. Verify the agent’s findings”](#3-verify-the-agents-findings)
Don’t treat the agent’s output as final. Before leaving review comments:
* **Run the tests.** If the agent flags a potential regression, check whether the test suite catches it.
* **Read the flagged code yourself.** The agent can miss context or misread intent. Treat its output as a starting checklist, not a verdict.
* **Test behavior changes manually.** For UI or interaction changes, check out the branch and verify in a browser. For cloud agent runs, you can use [Computer use](/agents/capabilities/computer-use/) to let the agent verify behavior in a sandboxed environment.
## 4. Use follow-up prompts to dig deeper
[Section titled “4. Use follow-up prompts to dig deeper”](#4-use-follow-up-prompts-to-dig-deeper)
The first response is a starting point. Use follow-up prompts to investigate specific findings:
* **Inspect a specific area**: “Look more closely at `auth/middleware.js` — are there edge cases in the token expiration logic?”
* **Understand a concern**: “Explain the performance risk you flagged. How significant is it at 10k requests per minute?”
* **Draft a fix**: “Write the fix for the input sanitization issue in the login form.”
* **Check scope**: “Does this PR include changes unrelated to the stated goal? List anything that seems out of scope.”
* **Split a large PR**: “Suggest how to split this PR into smaller, independently reviewable pieces.”
For large PRs, break the diff into logical groups of files and run the prompt once per group.
## Reference: structured output format (optional)
[Section titled “Reference: structured output format (optional)”](#reference-structured-output-format-optional)
If you want the agent’s findings pre-formatted for rapid scanning, useful for async reviews or sharing with a team, add this format to your prompt. Use it as a structured report, but verify the findings before acting on them.
```plaintext
Review this pull request and format your response for rapid scanning. Follow the structure below.
### 1. Risk assessment
**Overall Risk:** HIGH | MEDIUM | LOW
**Complexity:** [Simple | Moderate | Complex | Very Complex]
**Blast Radius:** [Isolated | Module-wide | System-wide | External APIs affected]
**Requires Immediate Review:** [YES / NO – why]
---
### 2. Critical issues
_If none, write "None found."_
#### 1. [ISSUE TITLE]
**File:** `path/to/file.js:L125`
**Impact:** Data loss / Security hole / System crash
**Fix:**
// Suggested code fix
---
### 3. Concerns
_Should discuss or fix before merge. If none, write "None found."_
- [PERFORMANCE] Unindexed query on large table
- [SECURITY] Missing input sanitization in login form
---
### 4. Merge decision
**Merge confidence:** [0–100]%
- [ ] Safe to merge after fixing blockers
- [ ] Needs architecture discussion first
- [ ] Requires performance testing
- [ ] Get security team review
- [ ] Author should split into smaller PRs
**Time to properly review:** ~[X] minutes
**Recommended reviewer expertise:** [Backend | Security | Database | Frontend]
---
Keep sections short. If a section is empty, write "None found." Include code examples only for blockers. Use prefixes like [SECURITY], [PERFORMANCE], [LOGIC] for easy scanning.
```
## Next steps
[Section titled “Next steps”](#next-steps)
Explore related guides and features:
* [Review AI-generated code](/guides/agent-workflows/how-to-review-ai-generated-code/) — review and comment on code diffs directly in Warp’s Code Review panel
* [Attach agent session context to GitHub PRs](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/) — embed the prompt, plan, and agent decisions into the PR for your reviewers
* [Code Review panel](/code/code-review/) — full reference for visual diffs and inline comments in Warp
# Run 3 agents in parallel
Canonical page: [/guides/agent-workflows/how-to-run-3-agents-in-parallel-summarize-logs-analyze-pr-modify-ui/](https://docs.warp.dev/guides/agent-workflows/how-to-run-3-agents-in-parallel-summarize-logs-analyze-pr-modify-ui/)
> Run three agent tasks simultaneously in Warp — modify UI, analyze code reviews, and summarize production logs in parallel.
Note
This educational module demonstrates Warp’s multi‑threading features — running coding, debugging, and analysis tasks simultaneously in multiple agent tabs.

***
### 🧠 Overview
[Section titled “🧠 Overview”](#-overview)
Warp allows you to launch several agents at once, each focused on a separate task.\
In the demo, we run three parallel workflows:
* Modify UI behavior
* Analyze team code reviews
* Summarize logs from production
1. #### Launch agents in parallel
[Section titled “Launch agents in parallel”](#launch-agents-in-parallel)
Each agent runs in its own tab.
* UI Fix
Remove the background and border from unfocused input panes.
```plaintext
I'd like to make a coding change. Please create a new branch to do this.
I want to remove the border and background from the input when it's rendered in a pane that is not focused. Please look at the reference file and the attached screenshot. In the screenshot, there are two equally prominent input areas, even though one is focused and one is not. Make the non-focused input omit its border and background.
Please check out this linear issue for more information. Also, give me a plan before you make any changes.
```
* Code Review Check
Analyze how many pull requests a team member has assigned.
```plaintext
Use the GitHub CLI tool to summarize all open PRs for review that are assigned to user. I'd like to see who is the author of the PR, when was it opened, how long has it been open for, which repo is it in, are there open and unaddressed comments on it, and is it ready for review?
```
* Log Analysis
Summarize Cloud Run logs by error severity.
```plaintext
Use the gcloud tool to list all my open projects. Once you've done that, let me select a project. Once I've selected a project, we will want to see all the Cloud Run instances that are available. Then once I've picked a Cloud Run instance, I'd like to get a summary of the last 2000 logs from that Cloud Run instance to see the history histogram of different types of logging on info, warning, and error levels.
```
2. #### Monitor all agents
[Section titled “Monitor all agents”](#monitor-all-agents)
The **task pane** in Warp shows all running agents.\
You can view plans, progress, and results live without interrupting other tasks. To track these runs across your account and team in real time, including cloud agent runs, open the [Agent Management Panel](/platform/managing-cloud-agents/) in the Warp app.
3. #### Review results
[Section titled “Review results”](#review-results)
* **Coding Agent:** Implements UI fixes accurately.
* **Code Review Agent:** Reports 26 open PRs (identifies bottlenecks).
* **Log Agent:** Analyzes 1,000 log entries, categorizing errors and flagging Gemini API issues.
4. #### Why this matters
[Section titled “Why this matters”](#why-this-matters)
Warp multi‑agent execution allows you to:
* Run multiple tasks without context switching.
* Keep coding, debugging, and ops visible simultaneously.
* Use AI assistants collaboratively for faster iteration.
Tip
Multi‑agent workflows let you debug, code, and analyze in parallel — boosting throughput without leaving the terminal.
### Next steps
[Section titled “Next steps”](#next-steps)
* [How to run multiple AI coding agents](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/) - Decompose tasks, assign Git worktrees, validate output, and hand off branches or PRs for review.
* [Multi-agent orchestration](/platform/orchestration/) - Fan parallel work out to cloud child agents when a task is too large or slow to run locally.
# Run multiple AI coding agents
Canonical page: [/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/](https://docs.warp.dev/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/)
> Run Claude Code, Codex, Warp Agent, and other coding agents across worktrees, tabs, and cloud orchestration with clear task ownership.
Use multiple coding agents, including Warp Agent, Claude Code, Codex, and other CLI agents, when work can be split into independent tasks, reviewed from separate branches, or delegated to cloud agents while you keep working locally. In Warp, you can coordinate agents in three ways:
* **Local parallel sessions** - run Warp Agent, Claude Code, Codex, OpenCode, or another CLI agent in separate tabs or panes.
* **Isolated worktrees** - give each agent its own Git worktree and branch so parallel edits do not collide.
* **Automation Platform cloud orchestration** - use `/orchestrate`, `/plan`, the Oz CLI, the Oz web app, or the Warp Platform API to fan work out to child agents in cloud environments.
The best multi-agent workflows have one thing in common: each agent owns a clear slice of work, reports back with validation results, and hands off a branch, diff, PR, or concise finding you can review.
Plan on about 15 minutes for the local setup. Cloud orchestration takes longer only if you need to create or select an [environment](/platform/environments/) first.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **Any coding agent** — Any combination of supported agents works well: Warp Agent, [Claude Code](/guides/external-tools/how-to-set-up-claude-code/), [Codex CLI](/guides/external-tools/how-to-set-up-codex-cli/), OpenCode, Gemini CLI, Amp, Pi, Droid, and others.
* **A Git-tracked project** — Notifications and code review work best in a Git repository.
## Choose a multi-agent pattern
[Section titled “Choose a multi-agent pattern”](#choose-a-multi-agent-pattern)
| Pattern | Use it when | How to run it in Warp |
| --------------------------- | ------------------------------------------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------ |
| Same task, different agents | You want to compare approaches or pick the best implementation. | Run each agent in a separate tab and worktree, then compare diffs in the [Code Review panel](/code/code-review/). |
| Split by file or subsystem | A feature spans independent modules that can be changed in parallel. | Assign each agent a worktree, branch, file boundary, and validation command. |
| Builder plus reviewer | One agent implements while another reviews, writes tests, or checks edge cases. | Put the reviewer in a read-only or review-focused tab, or use a separate branch for test-only changes. |
| Cloud fan-out | The work is large, slow, or can run away from your laptop. | Use [Multi-agent orchestration](/platform/orchestration/) or [Running orchestrated agents](/platform/orchestration/multi-agent-runs/) to spawn cloud children. |
| Repeatable fleet workflow | You want the same agent pattern on every PR, issue, schedule, or release. | Use a cloud agent with a trigger, skill, or API workflow, or assemble a standing triage-to-merge team with [Warp Factories](/factories/), then inspect parent and child runs in the [Oz web app](/platform/oz-web-app/). |
## Plan the split before launching agents
[Section titled “Plan the split before launching agents”](#plan-the-split-before-launching-agents)
Before you start agents, decide:
* **Task ownership** - Which files, packages, tests, issues, or PRs each agent owns.
* **Workspace ownership** - Which branch or Git worktree each agent uses.
* **Validation ownership** - Which agent runs unit tests, typechecks, lint, smoke tests, or manual verification.
* **Handoff format** - Whether each agent should leave a local diff, branch, PR, patch, summary, or code review comments.
* **Merge strategy** - Whether you will keep one winner, cherry-pick changes, merge multiple branches, or open separate PRs.
Use boundaries that minimize overlapping edits. For example, assign one agent to `packages/api`, another to `packages/web`, and a third to tests or docs. If two agents must touch the same files, make one the owner and ask the other to review or propose changes without editing.
## 1. Switch to vertical tabs
[Section titled “1. Switch to vertical tabs”](#1-switch-to-vertical-tabs)
Vertical tabs are the foundation of a multi-agent workflow. Unlike horizontal tabs, they show rich metadata for each session: which agent is running, which branch you’re on, which directory, and the current status.
To enable vertical tabs:
1. In the Warp app, go to **Settings** > **Appearance** > **Tabs**.
2. Select **Use vertical tab layout**.
You can configure what information to display for each tab:
* The running agent (Warp Agent, Claude Code, Codex, etc.)
* The current Git branch
* The working directory
* A status indicator showing whether the agent is active, waiting for input, or idle
Vertical tabs overview.
## 2. Launch agents in separate tabs
[Section titled “2. Launch agents in separate tabs”](#2-launch-agents-in-separate-tabs)
Open a new tab for each agent session. Within each tab, navigate to your project directory and start an agent:
**Tab 1 — Claude Code:**
```bash
cd ~/your-project
claude
```
**Tab 2 — Codex:**
```bash
cd ~/your-project
codex
```
Give each agent a different task, or give them the same task to compare approaches:
```plaintext
# Claude Code: refactor the authentication module
Refactor src/auth/ to use async/await instead of callbacks
# Codex: write tests for the same module
Write comprehensive tests for src/auth/ covering edge cases
```
For split work, include the same operating contract in every prompt:
```plaintext
You own src/auth/ and tests/auth/.
Do not edit src/billing/ or src/api/payments/.
Work on branch feature/auth-refactor-claude in ../your-project-claude.
Run npm test -- auth and npm run typecheck before handing off.
When done, report changed files, validation results, and any risks.
```
If one agent depends on another, do not let both edit at once. Ask the first agent to finish and report its branch, patch, or PR before starting the dependent work.
Vertical tab with agent details.
## 3. Monitor agents with notifications
[Section titled “3. Monitor agents with notifications”](#3-monitor-agents-with-notifications)
When you have multiple agents running, you don’t need to watch each tab. Warp sends notifications when an agent needs your attention, for example, when it needs permission to run a command or approval to apply a code diff.
Look for the attention-needed indicator on the tab in the vertical sidebar. Click the tab to jump directly to the agent that needs input.
Notification setup varies by agent:
* **Claude Code** — Install the [Warp notification plugin](https://github.com/warpdotdev/claude-code-warp). Warp shows a one-click install chip when you first run Claude Code, or you can install manually. See the [Claude Code guide](/guides/external-tools/how-to-set-up-claude-code/) for details.
* **Codex** — Warp automatically sets up notifications when you first run Codex. No manual setup required.
* **OpenCode** — Add the [Warp notification plugin](https://github.com/warpdotdev/opencode-warp) to your `opencode.json` configuration.
Note
Agent notifications are currently supported for Claude Code, Codex, and OpenCode. For setup details, see [Agent notifications](/agents/capabilities/agent-notifications/). For a full breakdown of which features work with each agent, see the [third-party CLI agents feature matrix](/agents/cli-agents/overview/).

Agent approval notification.

## 4. Compare outputs from different agents
[Section titled “4. Compare outputs from different agents”](#4-compare-outputs-from-different-agents)
A practical use of parallel agents is running the same task in different Git worktrees, with different agents, to compare their approaches. For example, prompt both Claude Code and Codex with the following:
```plaintext
Optimize the database query in src/api/users.ts to reduce response time
```
After both agents complete, open the [Code Review panel](/code/code-review/) (`⌘+Shift++`) in each tab to compare their diffs side-by-side. You might find one agent produces cleaner code while the other catches an edge case the first missed.
## 5. Save your workspace with tab configs
[Section titled “5. Save your workspace with tab configs”](#5-save-your-workspace-with-tab-configs)
If you regularly work with the same multi-agent setup, save it as a tab config so you can recreate it with one click:
1. Hover over the tab and click the three dots on the right-hand side.
2. Click **Save as new config**.
Saving a tab config.
Tab configs are TOML files that define the directory, startup commands, and layout for a tab. For example, you might create a config that:
* Opens two panes side-by-side
* Drops you into your project repo automatically
* Starts Claude Code in one pane and Codex in the other
Note
Tab configs pair well with [Git worktrees](/code/git-worktrees/). Create a worktree for each agent so they work on isolated branches, then merge the best results.
## 6. Use Git worktrees for isolated agent workspaces
[Section titled “6. Use Git worktrees for isolated agent workspaces”](#6-use-git-worktrees-for-isolated-agent-workspaces)
When multiple agents modify the same files, they can create conflicts. Git worktrees give each agent its own copy of your repo on a separate branch.
1. Create one worktree per agent so each agent has an isolated branch.
```bash
git worktree add ../your-project-claude feature/claude-refactor
git worktree add ../your-project-codex feature/codex-refactor
```
2. Point each agent tab at its assigned worktree directory.
3. Give every worktree a branch name that makes ownership obvious:
* `agent/claude-auth-refactor`
* `agent/codex-auth-tests`
* `agent/warp-review-pass`
4. Keep a merge note somewhere lightweight, such as your parent Warp Agent conversation or PR description:
* Which branch each agent owns.
* Which tests each agent ran.
* Which branch should be merged first.
* Which conflicts or follow-up decisions remain.
5. After both agents finish, compare the branches and merge the best results.
```bash
git diff feature/claude-refactor..feature/codex-refactor
```
6. Remove worktrees after you merge or discard the branch.
```bash
git worktree remove ../your-project-claude
git worktree remove ../your-project-codex
```
## 7. Fan out work to cloud agents
[Section titled “7. Fan out work to cloud agents”](#7-fan-out-work-to-cloud-agents)
Use cloud agents when the work is long-running, resource-intensive, easy to shard, or better handled away from your local machine. For example:
* Review every open PR in a repo.
* Run a migration across many packages.
* Ask one child agent per service to inspect logs, tests, or incidents.
* Let a parent agent coordinate a plan while children research, implement, or validate.
1. Start in the Warp app with `/orchestrate` when you want a parent agent to propose the child-agent breakdown.
```text
/orchestrate Split this TypeScript monorepo migration by package. Use one child agent per package, require each child to run package tests, and summarize changed files and risks before merge.
```
2. Use `/plan` for larger changes where you want to review the plan, orchestration config, child ownership, and merge strategy before agents launch.
3. For repeatable or unattended workflows, start the parent from the Oz CLI, the Oz web app, or the Warp Platform API. See [Running orchestrated agents](/platform/orchestration/multi-agent-runs/) for launch options.
4. Inspect parent and child runs from the [Oz web app](/platform/oz-web-app/) or the [Agent Management Panel](/platform/managing-cloud-agents/) in the Warp app.
Cloud orchestration is the best fit when you need:
* **Parallel fan-out** across many files, packages, PRs, issues, or services.
* **Clear observability** across parent and child runs.
* **Durable handoff** through child run summaries, session links, artifacts, PRs, or messages.
* **Team-scale execution** from Slack, Linear, schedules, GitHub Actions, the CLI, or the API.
## 8. Validate, merge, and hand off
[Section titled “8. Validate, merge, and hand off”](#8-validate-merge-and-hand-off)
Do not merge every agent’s output automatically. Use a fan-in pass:
1. Review each agent’s summary, changed files, and validation results.
2. Open the [Code Review panel](/code/code-review/) for local branches, or use [session sharing](/platform/viewing-cloud-agent-runs/) to inspect cloud children’s artifacts and session links.
3. Merge or cherry-pick one branch at a time.
4. Re-run the full validation suite from the final integrated branch.
5. Attach context for reviewers: agent session links, changed files, validation commands, known risks, and reviewer asks.
For GitHub handoff, see [Attach agent session context to GitHub PRs](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/). For reviewing the generated code itself, see [How to review AI-generated code](/guides/agent-workflows/how-to-review-ai-generated-code/).
## Productivity tips
[Section titled “Productivity tips”](#productivity-tips)
* **Use the [Agent Management Panel](/platform/managing-cloud-agents/)** — Open it to see all active agents across tabs. This gives you a dashboard view of what’s running, what’s waiting, and what’s finished.
* **Color-code your tabs** — Assign different themes or colors to agent tabs so you can visually distinguish them at a glance in the vertical sidebar.
* **Compose with `Ctrl+G`** — Use Warp’s rich input editor (`Ctrl+G`) when composing prompts for third-party agents. This gives you click-to-edit instead of arrow-key navigation in the raw CLI.
* **Review all changes before committing** — After running multiple agents, open the Code Review panel to see the combined diff across all files. Use “Changes vs. main” view to see the full scope of all agent-generated changes on your branch.
## Next steps
[Section titled “Next steps”](#next-steps)
You set up a multi-agent workspace with vertical tabs, launched different agents in parallel, monitored them with notifications, compared their outputs, and learned how to use tab configs and Git worktrees for isolated, reproducible multi-agent workflows.
Explore related guides and features:
* [How to review AI-generated code](/guides/agent-workflows/how-to-review-ai-generated-code/) — review and refine the code your agents produced
* [Attach agent session context to GitHub PRs](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/) — give reviewers the agent context behind a PR
* [Multi-agent orchestration](/platform/orchestration/) — coordinate parent and child agents across local and cloud runs
* [Running orchestrated agents](/platform/orchestration/multi-agent-runs/) — start orchestrated runs from Warp, the Oz CLI, the Oz web app, or the Warp Platform API
* [Set up Claude Code](/guides/external-tools/how-to-set-up-claude-code/) or [Set up Codex CLI](/guides/external-tools/how-to-set-up-codex-cli/) — install both agents if you haven’t already
* [Claude Code in Warp](https://www.warp.dev/agents/claude-code) — overview of Claude Code support in Warp
* [Codex in Warp](https://www.warp.dev/agents/codex) — overview of Codex support in Warp
* [Gemini CLI in Warp](https://www.warp.dev/agents/gemini-cli) — overview of Gemini CLI support in Warp
* [OpenCode in Warp](https://www.warp.dev/agents/opencode) — overview of OpenCode support in Warp
* [Third-party CLI agents](/agents/cli-agents/overview/) — all supported agents and universal agent features
* [Vertical tabs](/terminal/windows/vertical-tabs/) — full reference for tab features
# How to run unattended agents
Canonical page: [/guides/agent-workflows/how-to-run-unattended-agents/](https://docs.warp.dev/guides/agent-workflows/how-to-run-unattended-agents/)
> Start unattended cloud agents from schedules, Slack, Linear, GitHub, GitHub Actions, the Oz CLI, or the Automation Platform API, then inspect every run.
Warp cloud agents can run unattended from schedules, team tools, CI, the Oz CLI, or the API. Use them when you want an agent to keep working after you leave your terminal, react to external events, or run recurring maintenance without a human starting each run.
Every unattended workflow creates a cloud agent run that your team can inspect later. Open runs from the [Runs page in the Oz web app](/platform/oz-web-app/#runs), the [Agent Management Panel](/platform/managing-cloud-agents/) in the Warp app, or the session link posted back to the tool that triggered the agent.
## Choose a trigger
[Section titled “Choose a trigger”](#choose-a-trigger)
Use this table to decide where an unattended agent should start.
| Trigger | Use it when | Where to configure | Where to inspect |
| ----------------- | ------------------------------------------------------------------------------------------------------------ | ---------------------------------------------------------------------------------------------------------------------------------------------- | ---------------------------------------------------------------------------------------------------------------- |
| Scheduled agents | Work should run on a predictable cadence, like weekly triage, nightly dependency checks, or monthly cleanup. | [Scheduled Agents](/platform/triggers/scheduled-agents/) or the [Scheduled Agents quickstart](/platform/triggers/scheduled-agents-quickstart/) | Oz web app Runs page, Agent Management Panel in the Warp app, schedule history, and cloud agent session links |
| Slack | A teammate should delegate work from a Slack message or thread. | [Slack integration](/platform/integrations/slack/) | Slack thread updates, Oz web app Runs page, Agent Management Panel in the Warp app, and the shared run session |
| Linear | An issue, comment, or assignment should start the agent. | [Linear integration](/platform/integrations/linear/) | Linear issue updates, Oz web app Runs page, Agent Management Panel in the Warp app, and the shared run session |
| GitHub | Someone should delegate work by mentioning `@warp-agent` on an issue, pull request, or review comment. | [GitHub integration](/platform/integrations/github/) | GitHub thread comments, Oz web app Runs page, Agent Management Panel in the Warp app, and the shared run session |
| GitHub Actions | A repository event, PR workflow, issue workflow, or CI failure should start the agent. | [GitHub Actions](/platform/integrations/github-actions/) | GitHub Actions logs, PR or issue comments, Oz web app, and cloud agent runs |
| Oz CLI | You want to start a named cloud run from a terminal, script, or local automation. | [Oz CLI](/agents/cli/oz-cli/#running-agents-remotely-oz-agent-run-cloud) | CLI output, Oz web app Runs page, Agent Management Panel in the Warp app, and cloud agent session links |
| Warp Platform API | Your internal system should create, query, or monitor runs programmatically. | [Warp Platform API](/factories/api-and-sdk/) | Your system, API results, Oz web app, and run sessions |
## Choose a workflow pattern
[Section titled “Choose a workflow pattern”](#choose-a-workflow-pattern)
### Run recurring maintenance
[Section titled “Run recurring maintenance”](#run-recurring-maintenance)
Use [Scheduled Agents](/platform/triggers/scheduled-agents/) for tasks that should happen on a fixed cadence. Good fits include:
* dependency update checks
* stale issue or PR triage
* repository hygiene
* documentation refreshes
* recurring reports or audits
Each scheduled run starts a fresh cloud agent session and records its own task history, so you can review what ran, when it ran, and what the agent did.
### Delegate work from Slack or Linear
[Section titled “Delegate work from Slack or Linear”](#delegate-work-from-slack-or-linear)
Use [Slack](/platform/integrations/slack/) or [Linear](/platform/integrations/linear/) when the task starts from team conversation or issue context. These integrations are best for:
* turning a Slack thread into an implementation task
* asking an agent to investigate a Linear issue
* generating a PR from a bug report or product request
* letting teammates monitor progress without opening Warp
The agent posts progress updates back to the source thread or issue and provides a shared run link for deeper inspection.
### Delegate work from a GitHub thread
[Section titled “Delegate work from a GitHub thread”](#delegate-work-from-a-github-thread)
Use the [GitHub integration](/platform/integrations/github/) when the task starts from an issue, a pull request, or a review comment. Mention `@warp-agent` in the thread and the agent picks up that context, replies in place, and reports any pull request it opens. This fits:
* asking for a fix from a review comment without leaving the diff
* turning a bug report issue into a pull request
* answering a question about the code in the issue where it was asked
Mentioning the agent again in the same thread continues the existing run instead of starting a new one.
### React to GitHub events
[Section titled “React to GitHub events”](#react-to-github-events)
Use [GitHub Actions](/platform/integrations/github-actions/) when the trigger should be tied to a repository event and the run should happen inside your CI pipeline.
For example:
* review a PR when it opens
* respond to an `@warp-agent` comment
* summarize issues on a schedule
* attempt a fix when CI fails
* suggest fixes for review comments
The GitHub Action can pass event data, prior step output, and repository context into the agent prompt. The agent can comment, review, or open branches depending on the workflow permissions you grant.
### Start runs from scripts or internal systems
[Section titled “Start runs from scripts or internal systems”](#start-runs-from-scripts-or-internal-systems)
Use the [Oz CLI](/agents/cli/oz-cli/#running-agents-remotely-oz-agent-run-cloud) for scripts and terminal workflows. Use the [Warp Platform API](/factories/api-and-sdk/) when another service should create or monitor runs. This is useful for:
* internal dashboards
* custom webhooks
* CI systems outside GitHub Actions
* recurring jobs managed by your own scheduler
* workflows that need to query run status or results programmatically
Name cloud runs consistently with `--name` so your team can filter and review related runs later.
## Define the run before deploying
[Section titled “Define the run before deploying”](#define-the-run-before-deploying)
Before deploying an unattended agent, define:
* **Trigger** - What starts the run: schedule, Slack, Linear, GitHub event, CLI command, API request, or another automation.
* **Context** - Which repository, issue, thread, PR, logs, or files the agent needs.
* **Environment** - Where the agent runs, including repos, image, setup commands, secrets, and any MCP servers.
* **Permissions** - What the agent can read or write in GitHub, Slack, Linear, or other systems.
* **Output** - Whether the agent should comment, open a PR, generate an artifact, post a summary, or only report findings.
* **Review path** - Where a human will inspect the run, validate results, and approve changes.
If the agent can change code or infrastructure, keep the instructions narrow and make validation explicit.
## Review unattended runs
[Section titled “Review unattended runs”](#review-unattended-runs)
Unattended does not mean invisible. Use these surfaces to review what happened:
* [Oz web app](/platform/oz-web-app/) - View runs, schedules, run metadata, and session transcripts from a browser or mobile device.
* [Managing cloud agents](/platform/managing-cloud-agents/) - Filter runs by source, status, day, creator, or trigger.
* [Cloud agent session sharing](/platform/viewing-cloud-agent-runs/) - Inspect the prompt, plan, commands, logs, output, and follow-up messages where available.
* [Warp Platform API](/factories/api-and-sdk/) - Query runs and build internal monitoring around status, runtime, or outcomes.
When a run creates a PR, include the cloud run link in the PR description or a comment. See [Attach agent session context to GitHub PRs](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/) for a template.
## Start with one reviewable workflow
[Section titled “Start with one reviewable workflow”](#start-with-one-reviewable-workflow)
Start with one narrow workflow before deploying many unattended agents:
1. Pick one trigger and one repository.
2. Use a focused prompt or skill.
3. Run it manually or with **Run now** before enabling a recurring schedule.
4. Confirm the run has the right environment, secrets, and permissions.
5. Check the output and session transcript.
6. Add a review or approval step before merging code changes.
7. Expand the workflow only after the first runs are predictable.
## Next steps
[Section titled “Next steps”](#next-steps)
* [Scheduled Agents quickstart](/platform/triggers/scheduled-agents-quickstart/) - Create your first recurring agent in the Oz web app.
* [Integrations quickstart](/platform/integrations/quickstart/) - Trigger agents from Slack or Linear.
* [GitHub integration](/platform/integrations/github/) - Set up `@warp-agent` mentions on issues and pull requests.
* [GitHub Actions quickstart](/platform/integrations/quickstart-github-actions/) - Add an agent to a PR review workflow.
* [Multi-agent orchestration](/platform/orchestration/) - Fan unattended parent runs out to child agents when the work is large enough to shard.
* [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/) - Inspect and share unattended run sessions.
# Use voice and images to prompt coding agents
Canonical page: [/guides/agent-workflows/how-to-use-voice-and-images-to-prompt-coding-agents/](https://docs.warp.dev/guides/agent-workflows/how-to-use-voice-and-images-to-prompt-coding-agents/)
> Use voice and image context to prompt coding agents faster in Warp — works with Claude Code, Codex, and any CLI agent.
Typing detailed prompts for coding agents can be slow. Describing a bug from a screenshot, dictating a complex refactoring plan, or explaining a UI change from a design mockup are examples of tasks that are faster with voice and images than with text alone. This guide shows you how to use multimodal input with any CLI coding agent running in Warp in about 5 minutes.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **Warp** — Voice and image input are built into Warp’s agent interface. Download from [Warp homepage](https://www.warp.dev).
* **A CLI coding agent** — Voice and image input work with any supported agent: [Claude Code](/guides/external-tools/how-to-set-up-claude-code/), [Codex CLI](/guides/external-tools/how-to-set-up-codex-cli/), OpenCode, Gemini CLI, Amp, or Droid. See [Third-party CLI agents](/agents/cli-agents/overview/) for the full list.
* **A working microphone** (for voice) — Built-in or external, including Bluetooth audio devices.
## 1. Enable voice input
[Section titled “1. Enable voice input”](#1-enable-voice-input)
Voice transcription is available in Warp’s agent input. To use it:
1. Click the **microphone icon** in the input area, or use the voice input keyboard shortcut.

The microphone icon appears in the input area for voice transcription.
2. Speak your prompt naturally. Warp transcribes your speech and places the text in the input field.
3. Review the transcription, edit if needed, then submit your prompt.
Voice input works for both Warp’s built-in agent and third-party CLI agents when the agent utility bar is active.
Note
You can configure the voice input keybinding in the Warp app under **Settings** > **Agents** > **Warp Agent** > **Voice**. The default uses the `fn` key.
## 2. Prompt with voice instead of typing
[Section titled “2. Prompt with voice instead of typing”](#2-prompt-with-voice-instead-of-typing)
Voice is fastest for prompts that are easy to say but tedious to type, such as complex descriptions, multi-step plans, or explanations that reference what you’re looking at.
Try prompts like:
```plaintext
Refactor the authentication middleware to handle three cases:
valid token, expired token, and missing token. For expired tokens,
return a 401 with a refresh token hint. For missing tokens, return
a 403. Add unit tests for each case.
```
The transcription appears in your input field where you can review and edit before submitting.
## 3. Attach screenshots as context
[Section titled “3. Attach screenshots as context”](#3-attach-screenshots-as-context)
Paste (`⌘+V`) or drag images directly into the input area to give the agent visual context. This is useful for:
* **Bug reports** — Screenshot the error in your browser and ask the agent to fix it.
* **Design mockups** — Paste a Figma screenshot and ask the agent to implement the UI.
* **Error messages** — Screenshot a stack trace instead of copying and reformatting it.
* **Visual diffs** — Show the agent what the UI looks like now vs. what it should look like.

Attaching images as agent context.
## 4. Combine voice and images for design-to-code workflows
[Section titled “4. Combine voice and images for design-to-code workflows”](#4-combine-voice-and-images-for-design-to-code-workflows)
The most powerful use of multimodal input is combining voice and images. For example:
1. Take a screenshot of a design mockup from Figma.
2. Paste it into the input area.
3. Use voice to describe what you want:
```plaintext
This is the login page design. Implement it using React and Tailwind.
Match the spacing and colors exactly. The form should validate email
format on blur and show inline error messages.
```
The agent sees the design and hears your implementation requirements at the same time — much faster than writing a detailed specification by hand.
## 5. Use voice and images with third-party agents
[Section titled “5. Use voice and images with third-party agents”](#5-use-voice-and-images-with-third-party-agents)
Voice and image input work with any CLI agent that Warp detects, not just the built-in agent. When you run Claude Code, Codex, or another supported agent, Warp shows the **agent utility bar** with controls for voice, images, and files.
To use with a third-party agent:
1. Start the agent in your terminal (e.g., `claude` or `codex`).
2. The agent utility bar appears automatically when Warp detects the agent session.
3. Use the microphone icon for voice input or paste images as context.
4. Press `Ctrl+G` to open the rich input editor for composing complex prompts with attached images.
The voice transcription and image context are sent to the running agent session just as if you had typed and pasted them manually.
Note
If you don’t see the utility bar, make sure you’re on the latest Warp version and that the agent is running inside Warp (not an external terminal).
## Productivity tips
[Section titled “Productivity tips”](#productivity-tips)
* **Use voice for code review feedback** — Instead of typing inline comments, use voice to describe what needs to change while looking at the diff in the [Code Review panel](/code/code-review/).
* **Screenshot UI issues** — When you want to change a UI component, just screenshot it, send it to the agent, and describe what you want changed.
* **Dictate commit messages** — After reviewing your changes, use voice to describe what you did. The agent can format it as a proper commit message.
* **Use with Rules for consistent results** — Combine image context with [Rules](/agents/capabilities/rules/) that define your project’s UI patterns. The agent will match the mockup while following your existing design system.
## Next steps
[Section titled “Next steps”](#next-steps)
You can now prompt coding agents using voice transcription and image context — whether you’re using Claude Code, Codex, or any other CLI agent in Warp. Voice and images make complex prompts faster to create and more accurate, especially for design-to-code workflows, bug reproduction, and multi-step refactoring plans.
Explore related guides and features:
* [Set up Claude Code](/guides/external-tools/how-to-set-up-claude-code/) or [Set up Codex CLI](/guides/external-tools/how-to-set-up-codex-cli/) to start using third-party agents
* [How to review AI-generated code](/guides/agent-workflows/how-to-review-ai-generated-code/) — review the code your agents produce
* [Run multiple agents at once](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/) — combine voice/image prompting with parallel agents
* [Voice input](/agents/local-agents/interacting-with-agents/voice/) — full reference for voice features
* [Images as context](/agents/local-agents/agent-context/images-as-context/) — full reference for image input
* [Third-party CLI agents](/agents/cli-agents/overview/) — all supported agents and universal features
# Run a software factory in the cloud
Canonical page: [/guides/agent-workflows/run-a-software-factory-in-the-cloud/](https://docs.warp.dev/guides/agent-workflows/run-a-software-factory-in-the-cloud/)
> Set up the Automation Platform-native production path for your software factory with cloud environments, secrets, triggers, and audit trails.
The GitHub Actions approach in [Set up your software factory](/guides/agent-workflows/set-up-a-software-factory) gets the four-agent loop working. This guide covers the Automation Platform-native production setup for teams running the factory at scale: cloud environments, secrets and permissions, triggers, and observability. To run the same loop as a managed product instead, see [Warp Factories](/factories/).
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* A working software factory loop ([set one up](/guides/agent-workflows/set-up-a-software-factory))
* A Warp account ([sign up at warp.dev](https://www.warp.dev))
## Why cloud agents, not cloud computers
[Section titled “Why cloud agents, not cloud computers”](#why-cloud-agents-not-cloud-computers)
A common approach to cloud-based agents is to spin up a persistent virtual machine, or “cloud computer”, that the agent logs into and uses like a developer’s laptop. The Automation Platform uses a different model where each agent run is a short-lived, scoped execution with its own environment and permissions, similar to a cloud function rather than a long-running server.
The practical difference:
* **Per-agent permissions** — Your triage agent only needs to read issues and post comments. Your implementation agent needs to push branches and open PRs. Each agent gets exactly the permissions it needs, not a single shared credential that everything uses.
* **Audit trails** — Every cloud agent run is logged separately. You can see exactly what the triage agent did versus what the implementation agent did, when it ran, and what it produced.
* **Team visibility** — Any teammate can open a run in the Oz web app to inspect the session transcript, steer a stuck agent, or [hand the work off](/platform/handoff/) to keep going from another session.
* **Scale without contention** — Multiple triage runs can execute in parallel without fighting over a shared dev box, local git checkouts, or CPU.
See [Deployment patterns](/factories/deployment-patterns) for Warp-hosted and managed self-hosted factory execution. For CLI-based execution, see [Unmanaged architecture](/platform/unmanaged-execution/).
## 1. Set up a cloud environment
[Section titled “1. Set up a cloud environment”](#1-set-up-a-cloud-environment)
A cloud environment is a Docker-based sandbox with your repository, secrets, and any tools the agents need. If you don’t already have one from the previous guides, create one now: run [`/create-environment`](warp://action/create_environment) in Warp and the Automation Platform detects your stack, suggests a Docker image, and creates the environment automatically.
For repositories that need specific toolchains or dependencies, [`warpdotdev/oz-dev-environments`](https://github.com/warpdotdev/oz-dev-environments) has prebuilt Docker images for common stacks.
See [Environments](/platform/environments) for the full reference.
## 2. Add secrets and permissions
[Section titled “2. Add secrets and permissions”](#2-add-secrets-and-permissions)
Each agent role in your factory needs access to different secrets. Add them at the environment level rather than embedding them in prompts:
```bash
oz secret create --name GITHUB_TOKEN
```
The CLI prompts for the value interactively so it never appears in shell history or process arguments. Secrets are scoped to your team, injected into cloud runs at execution time, and never visible in session transcripts.
Grant each agent role only the GitHub permissions it needs:
* **Triage agent** — Read issues and post comments
* **Spec agent** — Push branches and open draft PRs
* **Implementation agent** — Push branches and open PRs
* **Reviewer agent** — Post review comments on PRs
Use fine-grained personal access tokens or separate GitHub App installations to enforce least privilege per role. See [Secrets](/platform/secrets) for management details and [GitHub Actions integration](/platform/integrations/github-actions) for token setup patterns.
## 3. Configure triggers
[Section titled “3. Configure triggers”](#3-configure-triggers)
With GitHub Actions, your factory already has event-based triggers. The Automation Platform also provides first-party integrations that handle triggering without GitHub Actions boilerplate:
* **Slack** — Teammates can kick off a run by mentioning `@warp` in a Slack thread. Useful for one-off requests that don’t need the full label workflow. See [Slack integration](/platform/integrations/slack).
* **Linear** — When an issue in Linear reaches a specific status, a cloud agent run starts automatically. Useful for teams that track work in Linear rather than GitHub Issues. See [Linear integration](/platform/integrations/linear).
* **Scheduled agents** — For the outer improvement loop (which runs on a cadence rather than an event), use a scheduled cloud agent. See [Scheduled agents](/platform/triggers/scheduled-agents).
* **Warp Platform API** — For custom triggers — webhooks, internal dashboards, other events — use the [Warp Platform API](/factories/api-and-sdk) to start runs programmatically.
## 4. Monitor factory runs
[Section titled “4. Monitor factory runs”](#4-monitor-factory-runs)
Every cloud agent run in your factory appears in the cloud agent dashboard with:
* A session transcript showing every action the agent took
* Artifacts: PRs, branches, plans, and reports the agent produced
* Status history: queued, in progress, succeeded, or failed with error details
* A session sharing link any teammate can open to inspect or steer the run
Open runs from the [Oz web app](/platform/oz-web-app/) or from the [Agent Management Panel](/platform/managing-cloud-agents/) in the Warp app. Include the session link in PR descriptions so reviewers can see exactly how the agent built the change — see [Attach agent context to GitHub PRs](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/).
See [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/) for the full reference.
## 5. Use multi-agent orchestration for large backlogs
[Section titled “5. Use multi-agent orchestration for large backlogs”](#5-use-multi-agent-orchestration-for-large-backlogs)
When a sprint starts and you want to process many issues in parallel, the Automation Platform can fan out to child agents — one per issue — from a single parent run. The parent coordinates; the children execute in parallel, each with their own environment, prompt, and permissions.
See [Multi-agent orchestration](/platform/orchestration) for fan-out, sharding, and result aggregation patterns.
## Productivity tips
[Section titled “Productivity tips”](#productivity-tips)
* **Start with one agent role in the cloud** — Get the triage agent running as a cloud run before moving all four roles. Confirm that the environment, secrets, and permissions work correctly before expanding.
* **Add session links to PR descriptions** — When the implementation agent opens a PR, include the cloud agent run link so reviewers get the full context. See [Attach agent context to GitHub PRs](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs) for a template.
* **Monitor credit usage** — Cloud agent runs consume credits. Monitor usage in the Oz web app and adjust run scope if needed. See [Credits](/support-and-community/plans-and-billing/credits).
## Next steps
[Section titled “Next steps”](#next-steps)
* [Warp Factories overview](/factories/) — Warp’s product for running this same loop end to end.
* [Infrastructure and security](/factories/infrastructure-and-security/) — The environment, runner, and credential model behind the concerns you configured by hand here.
* [Build a self-improving agent](/guides/agent-workflows/build-a-self-improving-agent) — Add the outer improvement loop on a schedule.
* [Environments](/platform/environments) — Full reference for cloud agent environments.
* [Deployment patterns](/factories/deployment-patterns) — Choose the right architecture for your team.
* [Self-hosting](/factories/self-hosting) — Run cloud agent workers on your own infrastructure when code must stay on-premises.
# Set up your software factory
Canonical page: [/guides/agent-workflows/set-up-a-software-factory/](https://docs.warp.dev/guides/agent-workflows/set-up-a-software-factory/)
> Add the implementation and reviewer agents to complete your software factory, then wire all four agent roles together using GitHub labels as the state machine.
This guide adds the implementation and reviewer agents to the [triage](/guides/agent-workflows/build-a-triage-agent) and [spec](/guides/agent-workflows/write-product-and-tech-specs-with-agents) agents you set up previously, then connects all four into a software factory using GitHub labels as the state machine. Issues flow automatically from triage to a reviewable pull request. To run this same loop as a managed product instead of wiring it yourself, see [Warp Factories](/factories/).
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* A working [triage agent](/guides/agent-workflows/build-a-triage-agent) and [spec agent](/guides/agent-workflows/write-product-and-tech-specs-with-agents), each deployed individually
* A cloud environment with access to your repository ([create one](/platform/environments))
* `warpdotdev/oz-agent-action` installed (see [GitHub Actions integration](/platform/integrations/github-actions))
## How the loop works
[Section titled “How the loop works”](#how-the-loop-works)
GitHub labels serve as the state machine that connects the agents. Each agent watches for a specific label, does its work, and applies the next label:
| Label | Agent triggered | What it does | Next label |
| -------------------- | -------------------- | ---------------------------------------- | -------------------------------------------- |
| *(new issue filed)* | Triage agent | Reviews the issue, flags questions | `ready-to-spec` or `needs-info` |
| `ready-to-spec` | Spec agent | Writes `PRODUCT.md` and `TECH.md` | human sets `ready-to-implement` after review |
| `ready-to-implement` | Implementation agent | Opens a PR with code and specs | PR opening triggers reviewer |
| *(PR opened)* | Reviewer agent | Reviews PR against specs and conventions | Posts inline review comments |
A human intervenes at two points: approving the spec before implementation begins, and merging the PR after review. Everything else runs automatically.
## 1. Trigger the spec agent when an issue is labeled ready-to-spec
[Section titled “1. Trigger the spec agent when an issue is labeled ready-to-spec”](#1-trigger-the-spec-agent-when-an-issue-is-labeled-ready-to-spec)
Add a GitHub Actions workflow that runs when the `ready-to-spec` label is applied:
```yaml
name: Write specs for ready issues
on:
issues:
types: [labeled]
permissions:
contents: write
pull-requests: write
issues: write
jobs:
write-specs:
if: github.event.label.name == 'ready-to-spec'
runs-on: ubuntu-latest
steps:
- uses: actions/checkout@v4
- uses: warpdotdev/oz-agent-action@v1
with:
skill: spec-driven-implementation
prompt: |
Write a product spec and tech spec for GitHub issue #${{ github.event.issue.number }} in ${{ github.repository }}.
Issue title: ${{ github.event.issue.title }}
Issue body: ${{ github.event.issue.body }}
environment: YOUR_OZ_ENVIRONMENT_SLUG
warp_api_key: ${{ secrets.WARP_API_KEY }}
env:
GITHUB_TOKEN: ${{ secrets.GITHUB_TOKEN }}
```
The `spec-driven-implementation` skill from [`warpdotdev/common-skills`](https://github.com/warpdotdev/common-skills) automates what you did manually in the [previous guide](/guides/agent-workflows/write-product-and-tech-specs-with-agents) — running both spec commands in sequence and opening a draft PR so you can review and approve the specs before implementation begins.
## 2. Human review: approve the specs
[Section titled “2. Human review: approve the specs”](#2-human-review-approve-the-specs)
When the spec agent opens a draft PR, review the `PRODUCT.md` and `TECH.md` files. This is the most important human checkpoint in the loop. An accurate spec leads to a correct implementation; a wrong spec leads to a correct implementation of the wrong thing.
When the specs look right, apply the `ready-to-implement` label to the original issue.
## 3. Trigger the implementation agent
[Section titled “3. Trigger the implementation agent”](#3-trigger-the-implementation-agent)
Add a workflow that triggers when `ready-to-implement` is applied:
```yaml
name: Implement from approved specs
on:
issues:
types: [labeled]
permissions:
contents: write
pull-requests: write
jobs:
implement:
if: github.event.label.name == 'ready-to-implement'
runs-on: ubuntu-latest
steps:
- uses: actions/checkout@v4
- uses: warpdotdev/oz-agent-action@v1
with:
skill: implement-specs
prompt: |
Implement the approved specs for GitHub issue #${{ github.event.issue.number }} in ${{ github.repository }}.
The specs are in specs/${{ github.event.issue.number }}/.
environment: YOUR_OZ_ENVIRONMENT_SLUG
warp_api_key: ${{ secrets.WARP_API_KEY }}
env:
GITHUB_TOKEN: ${{ secrets.GITHUB_TOKEN }}
```
The `implement-specs` skill from [`warpdotdev/common-skills`](https://github.com/warpdotdev/common-skills) reads the product and tech specs, and builds against them. It opens a PR with the code changes and the spec files committed together.
## 4. Trigger the reviewer agent when a PR is opened
[Section titled “4. Trigger the reviewer agent when a PR is opened”](#4-trigger-the-reviewer-agent-when-a-pr-is-opened)
Add a workflow that triggers when a PR is opened or updated:
```yaml
name: Review new pull requests
on:
pull_request:
types: [opened, synchronize]
permissions:
pull-requests: write
jobs:
review:
runs-on: ubuntu-latest
steps:
- uses: actions/checkout@v4
- uses: warpdotdev/oz-agent-action@v1
with:
skill: review-pr
prompt: |
Review pull request #${{ github.event.pull_request.number }} in ${{ github.repository }}.
If spec files are included in this PR, locate the changed specs/*/PRODUCT.md and specs/*/TECH.md files and validate the implementation against them.
environment: YOUR_OZ_ENVIRONMENT_SLUG
warp_api_key: ${{ secrets.WARP_API_KEY }}
env:
GITHUB_TOKEN: ${{ secrets.GITHUB_TOKEN }}
```
The `review-pr` skill from [`warpdotdev/common-skills`](https://github.com/warpdotdev/common-skills) reviews the PR diff against your codebase conventions and, when spec files are available, validates the implementation against the specs. It posts inline review comments.
## 5. Human review: merge the PR
[Section titled “5. Human review: merge the PR”](#5-human-review-merge-the-pr)
After the reviewer agent posts its comments, a human reviews the PR, including the diff, the agent’s inline comments, and the spec files. Address any gaps, run the project’s tests, and merge.
The reviewer agent surfaces issues and inconsistencies; the human makes the final call on quality and correctness. See [Review AI-generated code](/guides/agent-workflows/how-to-review-ai-generated-code) for the full human review workflow.
## Reference implementation
[Section titled “Reference implementation”](#reference-implementation)
[`warpdotdev/oz-for-oss`](https://github.com/warpdotdev/oz-for-oss) is Warp’s complete, deployable software factory for GitHub-hosted repositories. It includes all four agent roles, a Vercel webhook layer that handles GitHub events without GitHub Actions boilerplate, and self-improvement loops that propose skill updates based on maintainer feedback. If you want a production-grade system rather than individual GitHub Actions workflows, start there instead.
## Productivity tips
[Section titled “Productivity tips”](#productivity-tips)
* **Validate before the reviewer runs** — After the implementation agent opens a PR, run `/validate-changes-match-specs` to check the diff against `PRODUCT.md` and `TECH.md`. This catches any misalignments before the reviewer agent posts comments. The skill is available from [`warpdotdev/common-skills`](https://github.com/warpdotdev/common-skills).
* **Start with triage only** — Get your triage agent running well before adding spec and implementation. A groomed, labeled backlog is immediately useful to every developer on the team.
* **Use `@warp-agent` for one-off requests** — Teammates can mention `@warp-agent` in an issue comment to kick off an agent run directly, bypassing the label workflow for urgent requests.
* **Monitor runs in the Oz web app** — Every cloud agent run appears in the [Oz web app](https://oz.warp.dev) with a session link. Use it to inspect what each agent did, steer a stuck run, or hand work back to a local session.
## Next steps
[Section titled “Next steps”](#next-steps)
* [Warp Factories overview](/factories/) — Warp’s product for running this same intake-to-review loop without the workflow wiring.
* [Automations](/factories/automations/) — Replaces the label-based state machine you just wired by hand.
* [Factory agents](/factories/factory-agents/) — The same four roles — Triage, Spec, Implement, Review — as managed agents.
* [Run a software factory in the cloud](/guides/agent-workflows/run-a-software-factory-in-the-cloud) — Move the loop into a managed Automation Platform deployment.
* [Build a self-improving agent](/guides/agent-workflows/build-a-self-improving-agent) — Add the outer improvement loop.
* [Review AI-generated code](/guides/agent-workflows/how-to-review-ai-generated-code) — The human review workflow for agent-generated PRs.
* [`warpdotdev/oz-for-oss`](https://github.com/warpdotdev/oz-for-oss) — The complete reference implementation.
* [GitHub Actions integration](/platform/integrations/github-actions) — Full documentation for triggering cloud agents from CI.
# Understand your codebase
Canonical page: [/guides/agent-workflows/understanding-your-codebase/](https://docs.warp.dev/guides/agent-workflows/understanding-your-codebase/)
> Use Warp's Codebase Context to search across client and server repos, generate architecture summaries, and onboard to unfamiliar features fast.

### 1. The challenge
[Section titled “1. The challenge”](#1-the-challenge)
Kevin, who worked on Warp’s Windows and Linux builds, wanted to jump into a feature he hadn’t touched before: Block Sharing.\
\
This feature spans two codebases — Warp’s client (Rust) and server (Go) — making onboarding tough.
That’s where Codebase Context comes in.
***
### 2. What is Codebase Context?
[Section titled “2. What is Codebase Context?”](#2-what-is-codebase-context)
Warp’s Codebase Context uses semantic search to understand your code.\
It doesn’t rely on exact function or variable names — instead, it searches based on meaning.
You can use it through a shared workflow in Warp Drive.
This prompt tells Warp to:
* Search across both client and server codebases
* Summarize how a feature works end-to-end
* Include clickable links to relevant files
***
### 3. Real example: Block Sharing
[Section titled “3. Real example: Block Sharing”](#3-real-example-block-sharing)
Kevin types `block sharing` into Warp’s shared workflow.\
Warp:
1. Searches the client codebase for the rendering logic
2. Searches the server codebase for GraphQL handlers
3. Generates a summary combining both perspectives
The output includes:
* Architecture overview
* Linked file paths
* Function and module summaries
No more manual onboarding or guessing file names.
***
### 4. Incremental syncing
[Section titled “4. Incremental syncing”](#4-incremental-syncing)
Whenever you change a file in an indexed repo:
* Warp detects the update automatically
* Re-embeds just that file
* Keeps your code context fresh
That means agents never reference stale code.
***
### 5. Why it’s game-changing
[Section titled “5. Why it’s game-changing”](#5-why-its-game-changing)
Codebase Context helps teams:
* Understand large or unfamiliar codebases
* Onboard faster
* Jump between client and server logic seamlessly
* Generate accurate, clickable documentation
> “This saved us hours of one-on-one walkthroughs.” — Lucy
# Use images as context with Warp
Canonical page: [/guides/agent-workflows/using-images-as-context-with-warp/](https://docs.warp.dev/guides/agent-workflows/using-images-as-context-with-warp/)
> Attach screenshots and design mockups as context for Warp's agent to generate UI code, debug visual issues, and match Figma designs.

### 1. Why images matter
[Section titled “1. Why images matter”](#1-why-images-matter)
Humans process visuals much faster than text — and the same applies to AI.\
\
When you’re trying to explain a UI issue (“this button is off by a few pixels”), describing it with words can be clunky.\
\
That’s why Warp supports images as context — letting you attach screenshots directly to your prompts.
> 🧠 “An image is worth a thousand words” — especially when debugging UI or building frontend components.
***
### 2. What image context does
[Section titled “2. What image context does”](#2-what-image-context-does)
Image Context allows you to:
* Attach one or more screenshots to an agent query
* Give visual references for bugs, designs, or features
* Let the agent visually interpret what you mean
This is especially useful for frontend tasks like:
* Rebuilding a design from Figma
* Identifying layout misalignments
* Debugging visual bugs
***
### 3. Building an MCP marketplace from Figma
[Section titled “3. Building an MCP marketplace from Figma”](#3-building-an-mcp-marketplace-from-figma)
Taking a Figma mock of an MCP Server Marketplace and using it as input for Warp.
#### 1. Capture the mock
[Section titled “1. Capture the mock”](#1-capture-the-mock)
Take a screenshot of your design (e.g., the MCP Marketplace layout).
#### 2. Attach the image
[Section titled “2. Attach the image”](#2-attach-the-image)
In Warp:
1. Click the 📎 image icon in the input bar
2. Select your screenshot
3. Confirm it’s attached to the query
***
### 4. Running the task
[Section titled “4. Running the task”](#4-running-the-task)
Once attached, Warp’s agent:
1. Detects the attached image
2. Searches your repo (e.g., `collection.rs`)
3. Generates diffs that recreate the UI from the mock
4. Creates corresponding components and layout logic
You can view and edit these diffs in the Code Diff Viewer, similar to GitHub’s diff interface.
> 💡 Warp recommends smaller, focused diffs — agents perform better when working iteratively.
***
### 5. Reviewing the results
[Section titled “5. Reviewing the results”](#5-reviewing-the-results)
The agent built:
* A UI component for the MCP Marketplace
* Static data for three MCP servers (`Linear`, `GitHub`, `Stripe`)
* Proper rendering logic and styling
Verify the UI in Warp:
> “It matched the mock almost perfectly — something that would’ve taken me two days was done in 20 minutes.”
***
### 6. Optimizing for performance
[Section titled “6. Optimizing for performance”](#6-optimizing-for-performance)
Because images can consume tokens quickly, Warp automatically:
* Resizes images client-side
* Compresses them intelligently before sending
* Minimizes token usage without losing clarity
# 5 agent workflows for product managers
Canonical page: [/guides/agent-workflows/warp-for-product-managers/](https://docs.warp.dev/guides/agent-workflows/warp-for-product-managers/)
> Use five agent workflows to automate status updates, document drafting, Slack search, and meeting preparation for product managers.
Most PM work involves gathering information, synthesizing it, and communicating the result. These five workflows use agents in Warp and MCP servers to gather context and speed up synthesis. You’ll spend less time switching between tools and more time making decisions. Each workflow takes 5–10 minutes to set up.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **Warp** - Install Warp and sign in. See [Installation and setup](/getting-started/quickstart/installation-and-setup/).
* **MCP servers** (optional but recommended) - Connect agents to tools and data sources such as Slack, Linear, and Notion. See [MCP](https://docs.warp.dev/agents/capabilities/mcp/) for setup instructions. Each workflow identifies the servers it uses and includes a fallback.
Note
These workflows work with the Warp Agent or third-party CLI agents running in Warp, including Claude Code, Codex, OpenCode, and Gemini CLI. See [Third-party CLI agents](https://docs.warp.dev/agents/cli-agents/overview/) for the full list.
## 1. Pull cross-project status updates
[Section titled “1. Pull cross-project status updates”](#1-pull-cross-project-status-updates)
Compiling a status update across multiple projects usually means opening Slack, Linear, Notion, and email in separate tabs, reading through each one, and manually synthesizing a summary. With MCP-connected agents, you can pull context from all of these tools in a single prompt.
1. Tell the agent which projects, tools, and time range to cover. Be specific about the audience and format you need.
2. Submit a prompt that queries your connected tools. For example:
```text
Pull updates from the last week across #project-atlas and #project-beacon
in Slack, any Linear tickets that moved to Done or In Review, and the
latest entries in our Notion launch tracker. Summarize into a status
update for my skip-level, organized by project. Use bullet points. Flag
anything blocked or at risk.
```
3. Review the output and iterate. Ask the agent to adjust the tone (more concise, more formal), reorder sections, or add context for a specific stakeholder.
You’ll have a formatted status update ready to paste into Slack or email.
This workflow uses Slack, Linear, and Notion MCP servers.
Note
**Without MCP:** Copy relevant updates from each tool and paste them into your prompt. Ask the agent to synthesize and format the summary. The workflow remains the same, but MCP automates the gathering step.
## 2. Draft documents from the terminal
[Section titled “2. Draft documents from the terminal”](#2-draft-documents-from-the-terminal)
Writing a rollout doc, product brief, or strategy doc usually starts with a blank page in Google Docs or Notion. Instead, describe what you need to the agent and iterate on a draft without leaving Warp.
1. Describe the document type, audience, and structure. For example:
```text
Draft a product brief for a new onboarding flow redesign. The audience
is engineering and design leads. Include sections for problem statement,
proposed solution, success metrics, and open questions. The problem is
that 40% of new users drop off before completing setup.
```
2. Review the draft and iterate. Ask the agent to expand a section, tighten the language, add a competitor comparison, or restructure the outline.
3. If you have the Notion MCP server connected, ask the agent to push the finished draft to Notion.
You’ll have a structured first draft, grounded in your specific context and ready for review.
Note
**Without MCP:** Copy the finished draft and paste it into your documentation tool.
## 3. Search Slack for meeting prep
[Section titled “3. Search Slack for meeting prep”](#3-search-slack-for-meeting-prep)
Before a meeting or project check-in, you might need to catch up on activity across multiple Slack channels. If you have the Slack MCP server connected, you can search and summarize in one prompt rather than manually reading through each channel.
1. Tell the agent which channels and time range to search. For example:
```text
Search #eng-backend, #design-reviews, #project-atlas, and
#incidents for the last 3 days. Summarize the key decisions,
open questions, and anything that was escalated. I have a
project sync in 30 minutes and need to be caught up.
```
2. Review the structured summary the agent returns, grouped by topic or channel.
3. Ask follow-up questions to drill into specific threads. For example, ask, “What was the resolution on the API rate limiting discussion in #eng-backend?”
You’ll have a briefing document that summarizes recent activity across channels.
This workflow uses the Slack MCP server.
Note
**Without MCP:** Copy key messages or thread summaries from Slack and paste them into your prompt. Ask the agent to organize and summarize them. This works well for a smaller number of channels.
## 4. Run parallel workstreams in tabs
[Section titled “4. Run parallel workstreams in tabs”](#4-run-parallel-workstreams-in-tabs)
PM work often involves several threads at once, such as researching a competitor, drafting a brief, and reviewing a teammate’s document. Warp’s vertical tabs let you run separate agent sessions side-by-side, with each focused on a different task. To enable vertical tabs:
1. In the Warp app, go to **Settings** > **Appearance** > **Tabs**, then toggle on **Use vertical tab layout**.
2. Open a separate tab for each workstream, and give each tab a clear deliverable:
* **Competitor research (Tab 1)** - Ask the agent to compare competitor pricing, packaging, and positioning, then return a five-bullet summary with source links.
* **Product brief (Tab 2)** - Ask the agent to draft a product brief with a problem statement, target users, success metrics, and open questions.
* **Stakeholder update (Tab 3)** - Ask the agent to summarize relevant Slack threads into decisions, risks, and next steps.
3. Use each tab’s agent status badges and activity indicators to see which workstream needs attention without repeatedly switching tabs.
When the research is ready, use its summary to refine the brief or stakeholder update. This pattern keeps workstreams isolated and lets you switch context without losing progress. For a detailed walkthrough of multi-agent tab setups, including tab configs and Git worktrees, see [Run multiple AI coding agents](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/).
## 5. Use voice to draft strategy docs
[Section titled “5. Use voice to draft strategy docs”](#5-use-voice-to-draft-strategy-docs)
When thinking through a brief, strategy doc, or stakeholder update, talking can be faster than typing. Warp’s voice input lets you dictate a rough draft. Then use the agent to organize and refine the transcription.
1. Click the **microphone icon** in the input area or press the voice input key to start recording. By default, the voice input key is `fn`.
2. Talk through your document naturally. Describe the problem, your proposed approach, open questions, and next steps. Don’t worry about structure or polish.
3. After the transcription appears, submit this follow-up prompt:
```text
Clean up that transcription into a structured strategy doc. Add an
executive summary at the top, organize the body into Problem, Approach,
Risks, and Next Steps sections, and tighten the language for a
leadership audience.
```
You’ll have a structured first draft from an unstructured recording. For setup details and additional use cases, see [Use voice and images to prompt agents](/guides/agent-workflows/how-to-use-voice-and-images-to-prompt-coding-agents/).
## Productivity tips
[Section titled “Productivity tips”](#productivity-tips)
* **Save Rules for recurring formats** - Save a Rule with your team’s status update format, document templates, or project list so agents start with the right context. See [Rules](https://docs.warp.dev/agents/capabilities/rules/).
* **Reuse recurring workflows** - Save your weekly status update or meeting-prep instructions as a [Saved Prompt](/guides/configuration/trigger-reusable-actions-with-saved-prompts/) that you can run again.
* **Use `Ctrl+G` for complex prompts** - Open the rich input editor for click-to-edit prompt composition instead of navigating with arrow keys. This works with any CLI agent running in Warp. See [Rich Input Editor](https://docs.warp.dev/agents/cli-agents/rich-input/).
* **Save Tab Configs for recurring setups** - If you regularly use a research, drafting, and review layout, save it as a Tab Config for one-click workspace setup. See [Tab Configs](https://docs.warp.dev/terminal/windows/tab-configs/).
## Next steps
[Section titled “Next steps”](#next-steps)
You now have five workflows for common PM tasks. They cover cross-project status updates, document drafting, Slack search for meeting prep, parallel workstreams in tabs, and voice-to-text for rough drafts.
To go deeper on any of the tools used in these workflows, explore the related guides below. You can also customize how agents behave across your team with Rules, Saved Prompts, and MCP integrations.
* [Connect agents to MCP servers](/guides/external-tools/using-mcp-servers-with-warp/) to set up Slack, Linear, Notion, and other integrations.
* [Use voice and images to prompt agents](/guides/agent-workflows/how-to-use-voice-and-images-to-prompt-coding-agents/) for full setup and use cases for multimodal input.
* [Run multiple AI coding agents](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/) for multi-tab workflows, tab configs, and Git worktrees.
* [MCP](https://docs.warp.dev/agents/capabilities/mcp/) for the full configuration reference.
* [Rules](https://docs.warp.dev/agents/capabilities/rules/) to save persistent context so agents follow your team’s conventions.
* [Voice input](/agents/local-agents/interacting-with-agents/voice/) for the full reference to voice transcription features.
# Warp vs Claude Code
Canonical page: [/guides/agent-workflows/warp-vs-claude-code/](https://docs.warp.dev/guides/agent-workflows/warp-vs-claude-code/)
> Compare Warp and Claude Code across setup, diff review, model selection, configuration, and performance.

### 1. Overview
[Section titled “1. Overview”](#1-overview)
This walkthrough compares Claude Code and Warp’s built-in coding agent — two tools built for AI-assisted development.\
Both can:
* Read and edit files
* Generate code diffs
* Plan multi-step tasks\
\
But they differ in experience, configurability, and performance.
***
### 2. Setup and interface
[Section titled “2. Setup and interface”](#2-setup-and-interface)
#### Claude Code
[Section titled “Claude Code”](#claude-code)
* Runs as a CLI tool, requiring a terminal and the `claude` CLI installed.
* You type prompts directly into a command box.
* Supports file reading, search, and diff generation.
#### Warp
[Section titled “Warp”](#warp)
* Built directly into the Warp terminal.
* No installation needed — type a natural-language query or click the Agent button to enter Agent Mode.
* Handles the same operations as Claude Code but integrated into the environment you already use.
***
### 3. Reviewing diffs
[Section titled “3. Reviewing diffs”](#3-reviewing-diffs)
In Claude Code:
* You manually review diffs via CLI or external editors like VS Code.
* You can hit `Shift+Tab` to auto-accept all edits.
In Warp:
* You get a visual diff view built in.
* Accept, reject, or manually edit diffs inline using Warp’s lightweight editor.
* The agent automatically updates its context to avoid overwriting your changes.
***
### 4. Planning & context gathering
[Section titled “4. Planning & context gathering”](#4-planning--context-gathering)
Both support planning mode for complex tasks:
* Claude Code uses a Markdown-style plan view.
* Warp can either show a similar plan or skip planning for short tasks.
For context:
* Both allow file references with `@filename`.
* Warp extends this with symbol referencing (`@functionName`) and a file tree explorer, letting you pull in specific lines and symbols as context.
***
### 5. Model selection
[Section titled “5. Model selection”](#5-model-selection)
Claude Code lets you pick between Claude 3 models (`Sonnet`, `Opus`, `Haiku`) via the `/model` menu.
Warp supports multiple ecosystems:
* Claude (Sonnet, Opus)
* GPT-5 (various reasoning levels)
* Gemini series
Switch models from the dropdown or directly in the agent menu.
***
### 6. Configuration
[Section titled “6. Configuration”](#6-configuration)
In Claude Code:
* Everything is configured via `/commands` in the CLI.
* Includes model switching, tool permissions, and sub-agent creation.
In Warp:
* Configure from **Settings** > **Agents** > **Warp Agent**.
* Add MCP servers, prompts, and global rules.
* Define Agent Profiles for read/write permissions, autonomy, and planning behavior.
* Maintain a global rules directory for consistent behavior across projects.
Warp also supports codebase indexing, which creates embeddings for faster semantic search across your repos.
***
### 7. Managing agents over time
[Section titled “7. Managing agents over time”](#7-managing-agents-over-time)
Claude Code:
* Shows progress directly in the CLI tab.
* Displays the current task name in the terminal tab title.
Warp:
* Adds visual indicators for agent status, progress, and toast notifications when blocked.
* Optional desktop notifications keep you informed when you’re multitasking.
***
### 8. Performance comparison
[Section titled “8. Performance comparison”](#8-performance-comparison)
Ben ran both tools on the same coding task — fixing a bug in the `renderKeyboardShortcut` function from a Sentry issue.
Claude Code results:
* Took \~2–4 minutes with Claude 3 Sonnet.
* Found the right issue and produced working code, though some redundant logic remained.
Warp results:
* With GPT-5, average time was \~1 minute 20 seconds.
* Consistent, high-quality output.
* Produced concise solutions with fewer redundant checks.
* Supported multiple models for experimentation.
***
### 9. Conclusions
[Section titled “9. Conclusions”](#9-conclusions)
| Criteria | Claude Code | Warp |
| --------------- | ----------------- | ------------------------ |
| Environment | CLI tool | Integrated into terminal |
| Diff Review | External / Manual | Built-in panel |
| Planning | Markdown mode | Inline or Opus-assisted |
| Model Options | Claude only | Claude, GPT-5, Gemini |
| Configurability | CLI-based | UI + Profiles + Rules |
| Performance | 2–4 min avg | \~1.2 min avg (GPT-5) |
**TL;DR:**\
If you prefer the Claude model suite and CLI workflow — go with Claude Code.\
If you want richer diff editing, context referencing, and model flexibility — Warp is the better fit.
> “Claude Code gives you an AI terminal. Warp gives you an AI development environment.”
# Write product and tech specs with agents
Canonical page: [/guides/agent-workflows/write-product-and-tech-specs-with-agents/](https://docs.warp.dev/guides/agent-workflows/write-product-and-tech-specs-with-agents/)
> Use agents to turn a ready-to-implement issue into a product spec and a tech spec — the blueprints that guide implementation and anchor code review.
Once your [triage agent](/guides/agent-workflows/build-a-triage-agent) is labeling issues as `ready-to-spec`, use agents to turn those issues into two spec files: a product spec that describes what the feature should do from the user’s perspective, and a tech spec that describes how to implement it.
Implementation agents use these specs as blueprints; reviewers use them as acceptance criteria. The agent does the drafting while you do the reviewing.
Specs give implementation agents the context they need to make good decisions, and they also give human reviewers a benchmark to judge the result against. With a spec, the agent implements against an explicit contract you’ve approved, instead of what it inferred from the issue.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* A Warp account ([sign up at warp.dev](https://www.warp.dev))
* A triaged issue labeled `ready-to-spec` or equivalent ([set up triaging](/guides/agent-workflows/build-a-triage-agent))
* `common-skills` installed globally from [`warpdotdev/common-skills`](https://github.com/warpdotdev/common-skills):
```bash
npx skills@latest add warpdotdev/common-skills --skill write-product-spec --agent warp --global
npx skills@latest add warpdotdev/common-skills --skill write-tech-spec --agent warp --global
```
## 1. Write the product spec
[Section titled “1. Write the product spec”](#1-write-the-product-spec)
A product spec defines what the feature should do from the user’s perspective, including user stories, acceptance criteria, and edge cases. It is the “what,” not the “how.”
1. Open the issue you want to spec in Warp and run:
```bash
/write-product-spec
```
2. Review the generated `PRODUCT.md` in `specs/[issue-number]/`. The file includes:
* A summary of the feature
* User stories in the format “As a \[user], I want \[behavior] so that \[outcome]”
* Acceptance criteria the implementation agent and reviewers can verify
* Edge cases and constraints
Correct any misunderstandings before moving to the tech spec. A wrong product spec leads to a correct implementation of the wrong thing.
## 2. Write the tech spec
[Section titled “2. Write the tech spec”](#2-write-the-tech-spec)
A tech spec defines how the feature will be implemented, including architecture decisions, relevant code locations, API shapes, and implementation notes. It is the “how.”
1. After reviewing the product spec, run:
```bash
/write-tech-spec
```
2. Review the generated `TECH.md` in the same `specs/[issue-number]/` directory. The file includes:
* An overview of the implementation approach
* The specific files and functions that need to change
* Any new data structures, API endpoints, or interfaces
* Testing strategy
* Known risks or tradeoffs
An accurate `TECH.md` reduces the number of implementation iterations and gives reviewers context for why the code looks the way it does.
## Productivity tips
[Section titled “Productivity tips”](#productivity-tips)
* **Spec before you code, not after** — The biggest value from specs is catching misaligned assumptions before any code is written. Running `/write-product-spec` first forces that alignment to happen early, when fixing it is cheap.
* **Attach Figma mocks** — If your feature has a UI component, attach a Figma screenshot or mockup to your prompt when running `/write-product-spec`. The agent incorporates visual context into the acceptance criteria.
* **Use `/plan` for smaller tasks** — For changes that don’t warrant full specs, use Warp’s built-in [planning feature](/agents/capabilities/planning). Plans can be saved, versioned, and attached to PRs without a full spec workflow.
## Next steps
[Section titled “Next steps”](#next-steps)
* [Warp Factories overview](/factories/) — Warp’s product for running this same loop without the manual wiring.
* [Factory agents](/factories/factory-agents/#spec) — The Spec agent role, gating implementation the same way.
* [Set up your software factory](/guides/agent-workflows/set-up-a-software-factory) — Connect the spec role to implementation and review.
* [`warpdotdev/common-skills`](https://github.com/warpdotdev/common-skills) — The full set of shared skills including `write-product-spec`, `write-tech-spec`, and `validate-changes-match-specs`.
* [Planning](/agents/capabilities/planning) — Warp’s built-in planning feature for smaller tasks.
* [Skills](/agents/capabilities/skills) — How skill files work in Warp and the Automation Platform.
# Build a Chrome extension (D3.js + JavaScript + HTML + CSS)
Canonical page: [/guides/build-an-app-in-warp/building-a-chrome-extension-d3js-javascript-html-css/](https://docs.warp.dev/guides/build-an-app-in-warp/building-a-chrome-extension-d3js-javascript-html-css/)
> Build a D3.js Sankey diagram Chrome extension using Warp — scaffold, debug, coordinate multiple agents, and publish to the Chrome Web Store.
Tip
This educational module teaches you step-by-step how to replicate the process shown in the video — building a **Sankey diagram Chrome extension** using **D3.js**, debugging, coordinating **multiple agents**, and deploying to the **Chrome Web Store**.

1. #### Set up your environment and create a new Chrome extension project
[Section titled “Set up your environment and create a new Chrome extension project”](#set-up-your-environment-and-create-a-new-chrome-extension-project)
Our goal: build a Chrome extension called **“Sankey Stone”** that visualizes flows using **D3.js**.
Files created during setup
* `manifest.json`
* `popup.html`
* `popup.css`
* `popup.js`
* Icon images (`icon16.png`, `icon32.png`, `icon48.png`, etc.)
Enable Developer Mode in Chrome and load the project:
chrome://extensions → Developer Mode → Load unpacked → Select your project folder
Caution
If you see errors like “Failed to load extension” or “Could not load icon 16.png,” double‑check your manifest paths and icon filenames. The transcript explicitly shows these initial debugging steps.
2. #### Test the initial D3.js rendering
[Section titled “Test the initial D3.js rendering”](#test-the-initial-d3js-rendering)
After fixing missing icons, the extension loads but initially shows only “Loading diagram.”\
\
Debug this by taking a screenshot and feeding it to an agent for context by asking:
```plaintext
It says loading diagram — why isn’t the chart appearing?
```
An agent reviews the error and regenerates the `popup.js` so the Sankey chart appears using **D3.js**.
Result: a working, interactive diagram rendered inside the extension popup.
3. #### Version control and GitHub setup
[Section titled “Version control and GitHub setup”](#version-control-and-github-setup)
Initialize a Git repository and commit:
```bash
git init
git add .
git commit -m "Initial Sankey Stone extension"
```
The developer asks the agent to create a GitHub repo and push the code.\
\
The agent handles authentication, creates the remote repo, and pushes all files automatically.
4. #### Add a local test page and dynamic data
[Section titled “Add a local test page and dynamic data”](#add-a-local-test-page-and-dynamic-data)
Launch a simple local web server with a test page that outputs traffic flow data. The extension reads this data and updates the Sankey diagram dynamically.
Transcript example prompt:
```plaintext
Update the test data page so that it generates random labels and different contexts when I hit the regenerate button.
```
The agent edits the test page so that clicking the **Regenerate Test Page** button updates the diagram in real time.
5. #### Coordinate multiple agents in parallel
[Section titled “Coordinate multiple agents in parallel”](#coordinate-multiple-agents-in-parallel)
The video demonstrates running **multiple agents** in parallel. Each agent receives a different task:
| Agent | Task |
| ----- | ----------------------------------------------------------------------------- |
| #1 | `Update the test data page to randomize labels and values` |
| #2 | `Change the refresh page button to regenerate the chart in a different style` |
| #3 | `Generate a useful README file for the project` |
You can approve actions automatically by enabling **Auto‑approve all agent actions** so background updates run without manual confirmation.
Note
Running multiple agents in parallel mirrors having a small team: one agent focuses on data generation, another on UI changes, and a third on documentation.
6. #### Refine styles and interactions
[Section titled “Refine styles and interactions”](#refine-styles-and-interactions)
After the data layer works, now you can iterate on appearance:
```plaintext
Apply new color themes and improve the layout.
```
Changes applied:
* Support for multiple color themes and improved node layout.
* Hovering over links highlights connected nodes.
* Users can drag nodes to rearrange the layout.
* Added a “Switch Style” button to cycle between themes.
To support exporting diagrams, you can ask:
```plaintext
Add a button to download this image as a PNG.
```
The Warp agent writes the JS logic for PNG export and verifies that clicking the button saves a screenshot of the diagram.
7. #### Add an API key setup screen
[Section titled “Add an API key setup screen”](#add-an-api-key-setup-screen)
Create a settings page where users can store API keys:
```plaintext
Add a settings page to enter the Anthropic API key and test it.
```
* The page allows testing the key to ensure it works.
* API keys are stored locally in the browser, not sent to a server.
8. #### Publish to the Chrome Web Store
[Section titled “Publish to the Chrome Web Store”](#publish-to-the-chrome-web-store)
Package and submit the extension:
```bash
zip -r sankey_stone.zip *
```
Upload the ZIP file to the [Chrome Web Store developer dashboard](https://chrome.google.com/webstore/devconsole) and follow the prompts.
Note
The review may take a few weeks.
***
### Summary
[Section titled “Summary”](#summary)
By following these transcript‑based steps, you can recreate the same workflow:
* Scaffold a Chrome extension with D3.js.
* Debug manifest and icon issues.
* Use agents to generate and refine code.
* Introduce multi‑agent parallel tasks for UI, data, and docs.
* Add interactivity, themes, and export options.
* Create an API key setup screen.
* Package and publish to the Chrome Web Store.
Tip
You can follow this same pattern with your own idea: start small, scaffold with AI prompts, iterate using parallel agents, and deploy to production all from within Warp.
# Build a real-time chat app (GitHub MCP + Railway)
Canonical page: [/guides/build-an-app-in-warp/building-a-real-time-chat-app-github-mcp-railway/](https://docs.warp.dev/guides/build-an-app-in-warp/building-a-real-time-chat-app-github-mcp-railway/)
> Build and deploy a real-time chat app with Python, FastAPI, and JavaScript — from idea to production, all inside Warp.
Note
In this tutorial, we’ll follow along with Tech With Tim’s *Advanced Vibe Coding Tutorial w/ Warp* video.\
\
You’ll learn how to use **Warp**, the *agentic development environment*, to build and deploy a fullstack AI-driven app from scratch — including setup, debugging, and deployment using **GitHub MCP servers**.

### Overview
[Section titled “Overview”](#overview)
This video shows how to go from **idea → working web app → production deployment**, all inside Warp.\
The project: a **real-time chat application** built with **Python (FastAPI)** and a **JavaScript frontend**, deployed through **Railway**, and integrated with **GitHub** via **MCP (Model Context Protocol)**.
1. #### Setup & installation
[Section titled “Setup & installation”](#setup--installation)
Note
Warp is free for macOS, Linux, and Windows. Download it from the [Warp homepage](https://www.warp.dev/) and sign in with an account.
Once you open Warp, you can work in two modes:
* **Terminal mode** - Run shell commands such as `ls` and `pwd`.
* **Agent Mode** - Ask the agent to build an app, add a feature, or complete another natural-language request.
When auto-detection is enabled, Warp detects whether your input is a shell command or an agent request and routes it accordingly.
Pro tip: Enable voice input for natural prompting or attach screenshots when debugging UI issues.
2. #### Generate an app idea
[Section titled “Generate an app idea”](#generate-an-app-idea)
Warp supports *planning models*, where the AI generates a detailed roadmap before coding.
```plaintext
I would like to make something of simple to medium complexity that I could finish in about 30 minutes. I want this to be web based. I want to have some kind of interface and some kind of backend. Can you give me a fun idea that's not going to be too complicated to build out and to eventually deploy?
```
The AI suggested several projects, like a personal mood tracker, quick poll creator, recipe randomizer, and more.\
\
Chosen idea we went with: **a real-time chat application**.
3. #### Create a development plan
[Section titled “Create a development plan”](#create-a-development-plan)
Prompt:
```bash
I like idea one. Can you come up with a detailed plan on how to build this?
```
Warp’s agent generated a plan for:
* A **frontend** (UI for chat rooms and messages)
* A **backend** (FastAPI server for real-time communication)
* Database integration and planned deployment steps
You can refine or expand the plan interactively by prompting:
```plaintext
Make this more detailed.
```
And get back something like this:
```plaintext
Here's your development roadmap:
🏗️ Architecture Decisions
Frontend Options:
• React + Socket.IO Client (recommended for rich UI)
• Vue.js + Socket.IO Client
• Vanilla JS + WebSockets (simpler but limited)
Backend Options:
• Node.js + Socket.IO + Express (most popular for real-time)
• Python + Flask-SocketIO
• Go + Gorilla WebSocket
Database:
• MongoDB (flexible for chat messages)
• PostgreSQL (structured data with JSON fields)
• Redis (for session management and caching)
🚀 Recommended Tech Stack
📋 Core Features to Implement
1. Real-time messaging (Socket.IO)
2. User authentication (JWT)
3. Multiple chat rooms
4. Online user presence
5. Message history
6. Typing indicators
7. File/image sharing (optional)
🛠️ Development Steps
1. Create project in ~/Documents/Coding_Projects/realtime-chat
2. Set up Node.js backend with Socket.IO
3. Create React frontend with real-time connection
4. Implement user auth and room management
5. Add message persistence and history
6. Style UI and add advanced features
```
At any point, you can go into the plan and start directly modifying it. And when you’re ready, you can tell Warp to:
```bash
Please execute this plan.
```
4. #### Allow autonomous execution
[Section titled “Allow autonomous execution”](#allow-autonomous-execution)
Once Warp starts executing, you can let Warp run commands automatically:
1. Go to **Settings** > **Agents** > **Profiles**
2. Change **“Always Ask”** → **“Always Allow”**
3. Ensure restricted commands (e.g., `rm -rf`) remain blocked
This enables autonomous execution for safe, fast iteration. Warp will run shell commands, create directories, initialize files, and write code.
5. #### Running the app
[Section titled “Running the app”](#running-the-app)
First, you can click into any file, like `main.py` to edit it directly in Warp. Warp displays your file directly in the app for easy editing, similar to any regular IDE experience.

You can also ask Warp to run the app and test locally:
```plaintext
Can you run this app for me so I can test it? Tell me how to view it.
```
It’s possible (like in the video) for an error to occur (e.g., Internal Server Error). If that happens, you can debug conversationally:
```bash
I’m getting an internal server error. Can you fix this?
```
And Warp can fix the issue and rerun the app automatically.
6. #### Adding new features
[Section titled “Adding new features”](#adding-new-features)
To enhance the app, request features conversationally:
```plaintext
Can you add emoji reactions to the messages?
```
Warp will modify frontend and backend code, updating WebSocket logic for real-time reactions. After testing, multiple users can now react to messages in the chat interface.
7. #### Preparing for deployment
[Section titled “Preparing for deployment”](#preparing-for-deployment)
Warp integrates directly with version control and cloud deployers via **MCP servers**.
Connect GitHub MCP:
1. Go to **Settings** > **Agents** > **MCP servers** > **Add**
2. Add a JSON block for GitHub MCP:
```json
{
"github": {
"command": "docker",
"args": [
"run",
"-i",
"--rm",
"-e",
"GITHUB_PERSONAL_ACCESS_TOKEN",
"ghcr.io/github/github-mcp-server"
],
"env": {
"GITHUB_PERSONAL_ACCESS_TOKEN": "${<INSERT_YOURS_HERE>}"
}
}
}
```
3. Generate a GitHub personal access token (Settings → Developer Settings → Tokens)
* Enable scopes for: `repo`, `workflow`, `secrets`, `pull_request`, and `environments`.
Save and restart Warp.
Then tell the agent:
```plaintext
Can you make a new remote repo for me and upload my code?
```
Warp uses Git commands automatically:
```bash
git init
git add .
git commit -m "Initial commit"
git remote add origin ...
git push
```
8. #### Deploying via Railway
[Section titled “Deploying via Railway”](#deploying-via-railway)
Prompt:
```plaintext
I have a FastAPI application built with Python. I want to deploy this. It just has an integrated frontend with JavaScript, HTML, and CSS. What’s the easiest way to do that? Can you assist me?
```
Warp recommends **Railway** and walks through:
* Creating a Railway account
* Connecting your GitHub repo
* Deploying directly from GitHub
* Generating a public domain
Once deployed, test it in your browser — you’ll see your live chat app with emoji reactions working in real time.
### Appendix
[Section titled “Appendix”](#appendix)
* [GitHub MCP Server](https://github.com/github/github-mcp-server)
* [Docker Desktop download](https://www.docker.com/products/docker-desktop/)
* [Railway](https://railway.com/)
# Build Warp's input with Warp
Canonical page: [/guides/build-an-app-in-warp/building-warps-input-with-warp/](https://docs.warp.dev/guides/build-an-app-in-warp/building-warps-input-with-warp/)
> Watch how a Warp designer uses Warp's own agent to locate, modify, and test a UI component change in a large Rust codebase.
*Speaker: Dave, Product Design Lead at Warp*

### The challenge
[Section titled “The challenge”](#the-challenge)
Redesigning the input was tricky because it’s the primary interface developers use all day, every day.\
Everyone had opinions — and expectations — about how it should look and behave.
So, Peter (a product designer on my team) and I iterated on multiple designs using Figma.
Once we landed on a version we liked, we shared it internally.\
Most people were excited, but engineering resources were stretched thin — focused on improving Agent Mode quality and prepping the Agentic Development Environment.
So I thought: *“What if I just Warp it?”*
#### 1. Locating the Git diff chip code
[Section titled “1. Locating the Git diff chip code”](#1-locating-the-git-diff-chip-code)
Inside Warp’s input, there’s a small Git Diff chip — it shows your current branch and open changes. It was one pixel too tall. That tiny visual bug drove me nuts, so I used Warp to find where it lived.
Warp searched across the entire codebase and found references inside:
* `displaychip.rs`
* Related render and configuration files
It used a combination of semantic search, code indexing, and traditional grep to pinpoint the exact implementation.
***
#### 2. Modifying the font size
[Section titled “2. Modifying the font size”](#2-modifying-the-font-size)
Once Warp located the implementation, I asked it to reduce the font size by 1 pixel.
Warp automatically edited the relevant lines:
* Found the current setting (`system_font_size - 1`)
* Adjusted it to (`system_font_size - 2`)
I reviewed the diffs to confirm everything looked good.
***
#### 3. Building and testing the change
[Section titled “3. Building and testing the change”](#3-building-and-testing-the-change)
Next, I rebuilt the app using:
```bash
cargo run
```
# Create Rules for agents
Canonical page: [/guides/configuration/creating-rules-for-agents/](https://docs.warp.dev/guides/configuration/creating-rules-for-agents/)
> Create reusable Rules in Warp to encode team conventions — like Dockerfile patterns or dependency management — so agents follow your standards.
*Speaker: Maggie — Engineer at Warp*

### 1. Starting with Agent Mode evals
[Section titled “1. Starting with Agent Mode evals”](#1-starting-with-agent-mode-evals)
I’m currently adding **Evals** (short for evaluations) to test a new feature I’ve been building.
Warp quickly surfaces helpful context — like notebooks and internal docs — written by teammates on how to run Evals.\
\
This makes onboarding onto new tasks fast and collaborative.
***
### 2. Adding a Rust syntax eval
[Section titled “2. Adding a Rust syntax eval”](#2-adding-a-rust-syntax-eval)
Next, I want to add an Eval that tests for Rust syntax errors.\
So I ask Warp to update the Dockerfile to include Rust.
However, the generated Dockerfile installs Rust differently than I wanted.\
It also includes `gcc` and `python` via a single `apt-get` line, which doesn’t follow our internal conventions.
***
### 3. Stashing changes and creating a Rule
[Section titled “3. Stashing changes and creating a Rule”](#3-stashing-changes-and-creating-a-rule)
Instead of fixing this manually every time, I decide to stash the current changes and create a reusable Rule that encodes our convention:
> Rule Example:\
> “Always use `apt-get` to install packages and follow the same pattern used for installing Python and GCC.”
This way, future sessions — and even other teammates — can automatically apply the same standard.
***
### 4. Applying the Rule
[Section titled “4. Applying the Rule”](#4-applying-the-rule)
Now, I just ask Warp’s Agent Mode to try again!
Warp re-runs the request, follows the new rule, and correctly adds Rust with the right syntax. The code now matches our conventions.
# Configure YOLO and strategic Agent Profiles
Canonical page: [/guides/configuration/how-to-configure-yolo-and-strategic-agent-profiles/](https://docs.warp.dev/guides/configuration/how-to-configure-yolo-and-strategic-agent-profiles/)
> Configure custom agent profiles in Warp to control planning depth, autonomy, and execution speed — demonstrated with YOLO and Strategic examples.
Note
This tutorial explains how **Agent Profiles** in Warp influence behavior, autonomy, and planning when coding with AI — demonstrated through the NFL Predictor app example.

1. #### Define the project
[Section titled “Define the project”](#define-the-project)
I want to create an app that scrapes **NFL data** from the past decade, processes stats like team scores and player performance, and predicts future wins.
The prompt specifies:
* Data sources and constraints
* Dependencies and CLI commands
* Implementation details and deliverables
```plaintext
Role & Goal
You are my AI coding copilot inside Warp.
Create a production-ready Python project that ingests 2015–2025 NFL data to power future win projections.
Specifically: acquire week-level player and team stats, acquire game schedules + final scores (to determine weekly winners), and assemble a clean analytics dataset I can build models on later. Prefer stable/public data sources over brittle HTML scraping. Where scraping is unavoidable, respect robots.txt, add rate-limiting, and make scraping pluggable/optional.
Primary data sources:
nflverse/nflreadr static files for weekly player stats and schedules (CSV/Parquet over HTTPS).
Tech constraints:
Python 3.11+, no notebooks in the main flow.
Deterministic, idempotent pipelines.
Strong typing (pydantic) + docstrings.
Parquet as the storage format; small sample CSVs for quick checks.
CLI via Typer (warp run … friendly).
Logging (structlog), retry/backoff (tenacity), polite rate-limits.
Zero secrets required for core pipeline.
Deliverables:
A fully initialized repo with the scaffold above.
Implemented CLI + modules to download/ingest 2015–2025 data, compute/normalize fantasy PPR, produce winners by week, and write Parquet outputs.
One sample run in the README showing commands and example output counts.
If successful, run full 2015–2025.
Print a summary table (by season: games, players, weeks) at the end.
```
2. #### Configure the Strategic Agent
[Section titled “Configure the Strategic Agent”](#configure-the-strategic-agent)
**Base Model:** GPT‑5 (for reasoning)\
**Planning Model:** Claude 4 Opus (for detailed breakdowns)
| Action | Permission |
| ---------------- | ------------- |
| Apply code diffs | Agent decides |
| Read files | Agent decides |
| Create plans | Always allow |
| Execute commands | Always ask |
Behavior:
* The agent starts by asking clarifying questions:
> “Do you want me to scrape both player stats and schedules or just one first?”\
> “Where should raw data be stored — locally or in a database?”
* It builds a **14-step plan** covering setup, dependencies, validation modules, and pipelines.
* When the agent requests NFL schedule URLs, the chosen source returns 404 errors.
* Execution halts — showing that the **Strategic** profile prioritizes verification over progress.
3. #### Configure the YOLO Agent
[Section titled “Configure the YOLO Agent”](#configure-the-yolo-agent)
**Permissions:**
| Action | Permission |
| ------------------------ | ------------ |
| Apply diffs / read files | Always allow |
| Create plans | Never |
| Execute commands | Always allow |
Behavior:
* The YOLO agent skips detailed planning.
* It produces a **10-step plan** that covers essentials only:
* Initialize project
* Build CLI
* Ingest player data
* Compute scores and transformations
* Instead of using unstable schedule URLs, it focuses on reliable player endpoints — completing a functional data pipeline.
4. #### Compare outcomes
[Section titled “Compare outcomes”](#compare-outcomes)
| Aspect | Strategic Agent | YOLO Agent |
| ----------- | ----------------------- | -------------------------------------- |
| Planning | Detailed (14 steps) | Minimal (10 steps) |
| Interaction | Clarifications required | Autonomous |
| Speed | Slower due to checks | Faster iteration |
| Output | Stalled on invalid URLs | Working player dataset + summary table |
# Create project Rules for an existing project
Canonical page: [/guides/configuration/how-to-create-project-rules-for-an-existing-project-astro-typescript-tailwind/](https://docs.warp.dev/guides/configuration/how-to-create-project-rules-for-an-existing-project-astro-typescript-tailwind/)
> Create and maintain an AGENTS.md project rules file so coding agents always understand your project's setup, commands, architecture, and conventions.
Note
This educational module is built **only** from the transcript. It shows how to create and maintain a `Warp.md` file so Warp agents always understand your project’s setup, commands, architecture, and structure.
***
## What Project Rules are
[Section titled “What Project Rules are”](#what-project-rules-are)
A **Project Rules** file (`Warp.md`) acts as your project’s AI onboarding guide. Instead of re‑explaining your setup on every prompt, you document it once and Warp will always have that context. The transcript demo walks through creating the file, opening it in a side editor, and organizing it with standard Markdown headings for clear sections.
***
## Generate `Warp.md`
[Section titled “Generate Warp.md”](#generate-warpmd)
Run the following **verbatim** prompts in Warp to create and verify your rules file, then open it in the editor:
```plaintext
/init
```
```plaintext
/open-project-rules
```
* `/init` generates a starter `Warp.md` in your project root.
* `/open project rules` opens it in a side editor where you can scroll and edit the content.
You’ll get something that looks like this:
WARP.md
````markdown
This file provides guidance to WARP (warp.dev) when working with code in this repository.
## Project Overview
Share Your Brewfiles is an Astro-based website that allows developers to share and discover their Homebrew package lists (Brewfiles). The platform generates personality profiles based on package usage patterns and provides a leaderboard of popular packages.
## Core Architecture
* **Frontend**: Astro 4 with React 18 components, TypeScript, and Tailwind CSS
* **Backend**: Astro API routes with Firebase integration
* **Database**: Firebase Firestore for storing brewfiles, user data, and personality summaries
* **Deployment**: Vercel with serverless functions
* **Styling**: Custom Tailwind configuration with dark theme and gradient animations
## Key Components
### API Routes (`src/pages/api/`)
* `getBrewfiles.json.ts` - Retrieves all brewfiles or a specific brewfile by ID, triggers personality generation
* `uploadBrewfile.ts` - Handles brewfile uploads with GitHub OAuth integration
* `getRankedPackages.json.ts` - Generates leaderboard data for popular packages
* `updatePersonality.ts` - Updates personality summaries for users
* `exchangeCodeForAccessToken.ts` - GitHub OAuth token exchange
* `logSearch.json.ts` - Analytics for search functionality
### Core library functions (`src/lib/`)
* `generatePersonality.ts` - Complex algorithm that analyzes brewfile packages and assigns personality types (15 different personalities)
* `personalityBuckets.ts` - Defines personality type metadata and descriptions
* `validateBrewfileData.ts` - Data validation for brewfile uploads
* `totalBrewData.ts` - Aggregates package statistics for leaderboards
### Type System (`src/types/`)
* `brews.ts` - Main data structures for brewfiles, users, and entries
* `personality.ts` - Personality analysis types and enums
* `packageEntry.ts` - Package metadata structures
## Development Commands
### Setup
```bash
# Install dependencies
npm install
# Set up environment (Firebase config is public but consider security)
# No additional env setup needed for development
# Development server
npm run dev
```
### Development Workflow
```bash
# Start development server with Astro
npm run dev
# Build for production
npm run build
# Preview production build
npm run preview
# Run Astro CLI commands
npm run astro
```
### Testing API Endpoints
```bash
# Test brewfile retrieval
curl "http://localhost:4321/api/getBrewfiles.json"
# Test specific brewfile by ID
curl "http://localhost:4321/api/getBrewfiles.json?id=DOCUMENT_ID"
# Test package rankings
curl "http://localhost:4321/api/getRankedPackages.json"
```
## Architecture Notes
### Personality generation system
The core feature analyzes brewfile packages against a curated dictionary (`labelledBrewfiles.ts`) that categorizes packages by:
- Developer type (Backend, Frontend, DevOps, Security, Data, General)
- Package characteristics (AI tools, organization tools, customization, popularity rank)
- Legacy/modern status
The system calculates percentage distributions and applies complex rules to assign one of 15 personality types (Minimalist, Golden Retriever, Pragmatist, Trendy, AI, Architect, Artist, Traditionalist, Retro, Bob the Builder, Marie Kondo, Crazy Scientist, Trailblazer, Security, Wallflower).
### Firebase Integration
- Uses Firestore for data persistence
- Collection: `brewfiles` stores user brewfiles with personality summaries
- Real-time personality generation happens asynchronously after uploads
- GitHub OAuth integration for user authentication
### Path alias system
Uses TypeScript path mapping with `@/*` pointing to `./src/*` for clean imports.
### Astro Configuration
- Server-side rendering with Vercel adapter
- React integration for interactive components
- Sitemap generation for SEO
- Prefetch enabled for performance
## Development environment setup
### Prerequisites
- Node.js (version compatible with Astro 4)
- Access to Firebase project (config is in source but consider security implications)
- GitHub OAuth app for testing upload functionality
### Local development notes
- The site uses server-side rendering so API routes work in development
- Firebase config is currently in source code - be aware of security implications
- GitHub OAuth integration requires valid access tokens for uploads
- Personality generation is computationally expensive with large datasets
### Custom Tailwind configuration
- Dark theme with custom color palette (`bkg: #111111`)
- Custom accent colors (teal, orange, green, pink, blue variants)
- Marquee animations for scrolling elements
- Responsive typography with fluid scaling
- Container queries support
## File structure navigation
<FileTree>
- src/
- pages/
- api/ Astro API routes (serverless functions)
- index.astro Homepage with hero and marquee
- brewfiles.astro Search and browse brewfiles
- leaderboard.astro Package popularity rankings
- components/ Astro and React components
- lib/ Core business logic and utilities
- types/ TypeScript type definitions
- data/ Static data and package dictionaries
- firebase/ Firebase configuration
</FileTree>
## Common development tasks
### Adding new personality types
1. Update `DeveloperPersonalityType` enum in `src/types/personality.ts`
2. Add detection function in `src/lib/generatePersonality.ts`
3. Update `personalityBuckets.ts` with new personality metadata
4. Add corresponding image to `public/images/`
### Modifying package analysis
- Update `labelledBrewfiles.ts` to modify package categorization
- Adjust percentage thresholds in personality detection functions
- Test with different brewfile compositions
### API route development
- All routes in `src/pages/api/` become serverless functions on Vercel
- Use `export const prerender = false;` for dynamic routes
- Handle errors consistently with try/catch blocks
````
***
## Keep the file lean and intentional
[Section titled “Keep the file lean and intentional”](#keep-the-file-lean-and-intentional)
1. #### Start lean
[Section titled “Start lean”](#start-lean)
Everything in `warp.md` is **prepended to your prompt**. A longer file consumes more tokens and can increase compute cost. Keep only what truly matters.
2. #### Iterate and maintain
[Section titled “Iterate and maintain”](#iterate-and-maintain)
Start with `/init` boilerplate, then treat the file as a **living document**. Add the rules that help your team ship faster (e.g., branching, PR guidelines) and prune anything redundant.
Caution
If the file grows large (e.g., **500+ lines**), run it through a **prompt optimizer** to catch duplication, remove overlaps, and slim it down — exactly as advised in the transcript.
***
## Use sub‑directory Rules for monorepos
[Section titled “Use sub‑directory Rules for monorepos”](#use-subdirectory-rules-for-monorepos)
For large repos, you can generate localized rule files in sub‑trees. Navigate into a subfolder and run `/init` again to create a **directory‑scoped `Warp.md`** tailored to that area:
Tip
Going forward, when you give Warp a task, it will carry this context automatically — no re‑explaining needed.
# Set coding best practices
Canonical page: [/guides/configuration/how-to-set-coding-best-practices/](https://docs.warp.dev/guides/configuration/how-to-set-coding-best-practices/)
> Use Warp Rules to enforce coding style, TypeScript conventions, and documentation quality across AI-generated code.
Learn how to use Warp’s Rules to enforce coding style, documentation quality, and consistency across projects.

***
## Intro
[Section titled “Intro”](#intro)
This tutorial teaches you how to create coding Rules that make AI follow your team’s **best practices** automatically.\
\
By specifying formatting, style preferences, and documentation standards, Warp ensures consistent, high-quality code across your repositories.
***
1. #### The problem
[Section titled “The problem”](#the-problem)
Developers often have different habits — formatting styles, TypeScript conventions, or comment quality.\
Without clear rules, AI-generated code can be inconsistent or hard to maintain.
2. #### The Rule setup
[Section titled “The Rule setup”](#the-rule-setup)
Define Rules that enforce formatting, type preferences, and doc quality.
**Example Rule**
```plaintext
Rule: Code Authoring Standards
- Always format and check work before returning results.
- Prefer `types` over `interfaces` in TypeScript.
- Apply concise, human-readable JS Docs using the Hemingway test.
```
Note
The **Hemingway test** ensures code comments are simple and clear — short sentences, active voice, and no unnecessary complexity.
3. #### Benefits
[Section titled “Benefits”](#benefits)
* Encourages readable, maintainable code
* Improves documentation clarity
* Prevents style drift across AI contributions
# Set coding preferences with Rules
Canonical page: [/guides/configuration/how-to-set-coding-preferences-with-rules/](https://docs.warp.dev/guides/configuration/how-to-set-coding-preferences-with-rules/)
> Store your package manager, environment tool, and CLI preferences as Warp Rules so agents automatically use pnpm, miniconda, or your preferred tools.
Learn how to use Warp’s Rules feature to define your personal environment and tool preferences for every coding session.

This tutorial teaches you how to customize your development setup using **Warp’s Rules** — ensuring agents always work in your preferred environment. Instead of constantly reminding them which package manager or environment to use, you can **store those preferences as persistent Rules** that apply automatically across projects.
1. #### The problem
[Section titled “The problem”](#the-problem)
When using AI tools to write or modify code, they often default to outdated or undesired tools.\
For example, many agents still use **npm** instead of **pnpm** — or **pip** instead of **miniconda**.
Warp fixes this by letting you define your preferences once, and then applying them automatically whenever your agent runs commands.
2. #### The Rule setup
[Section titled “The Rule setup”](#the-rule-setup)
You can set Rules for how you want the AI to handle environments, dependencies, and commands.
**Example Rule**
```plaintext
Rule: Environment Preferences
- Always use pnpm for Node.js projects unless the project already uses npm.
- Default to miniconda for Python environments.
- Use the Tauri CLI when building desktop apps.
```
This ensures the agent automatically chooses the right package manager or environment — no extra prompts required.
3. #### Supported use cases
[Section titled “Supported use cases”](#supported-use-cases)
You can apply Rules to:
* Package managers (e.g., npm → pnpm)
* Environment tools (e.g., virtualenv → miniconda)
* Framework defaults (e.g., Next.js over React)
* CLI utilities or custom build tools
# Set tech stack preferences with Rules
Canonical page: [/guides/configuration/how-to-set-tech-stack-preferences-with-rules/](https://docs.warp.dev/guides/configuration/how-to-set-tech-stack-preferences-with-rules/)
> Define your preferred frameworks and tech stack in Warp Rules so agents consistently use Astro, SvelteKit, Vite, or your tools of choice.
Learn how to guide Warp’s AI to use your favorite tech stack when scaffolding new apps or generating code.

***
## Intro
[Section titled “Intro”](#intro)
This tutorial walks you through teaching Warp’s AI your **preferred technologies** so it consistently uses the frameworks and stacks you care about.
By setting up tech stack Rules, you make sure every new project follows your conventions — whether you prefer **Astro**, **SvelteKit**, **Next.js**, or something else.
***
## The problem
[Section titled “The problem”](#the-problem)
When you ask AI to scaffold a new web app, it often defaults to **React** and **Express**, or other older stacks.\
This creates friction when your workflow is based on modern tools or opinionated frameworks.
Warp solves this by letting you **store your stack preferences** directly as Rules.
***
## The Rule setup
[Section titled “The Rule setup”](#the-rule-setup)
Create a simple Rule that defines your favorite frameworks for each project type.
### Example Rule
[Section titled “Example Rule”](#example-rule)
```plaintext
Rule: Tech Stack Preferences
- Use Astro for websites.
- Use SvelteKit for desktop apps.
- Prefer Vite for build tooling.
- Avoid legacy stacks like Create React App or Express.
```
Once added, Warp’s AI automatically applies these defaults when generating new projects or updating existing ones.
Note
Think of it like setting a default coding personality for your agent.
***
## Why it matters
[Section titled “Why it matters”](#why-it-matters)
Tip
Defining your stack preferences helps the AI:
* Generate **consistent boilerplates**
* Follow your **current tech standards**
* Skip outdated or irrelevant dependencies
# Set up self-serve data analytics with Skills
Canonical page: [/guides/configuration/how-to-set-up-self-serve-data-analytics-with-skills/](https://docs.warp.dev/guides/configuration/how-to-set-up-self-serve-data-analytics-with-skills/)
> Set up a self-serve data analytics workflow in Warp using two community Skills that map questions to dbt models and structure reproducible analyses.
Self-serve data analytics means anyone on your team can ask a data question and get a trustworthy answer, without pinging the data team. This guide sets up that workflow using two community Skills that chain together: one resolves vague questions to the right BigQuery tables, and the other structures deep-dive analyses into reproducible folders. Plan on about 10 minutes for initial setup, plus time to customize the model index for your warehouse.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **Warp** — Install from [Warp download page](https://www.warp.dev/download) if you don’t already have it.
* **A BigQuery data warehouse with dbt models** — The Skills as published assume BigQuery and dbt. You can adapt them to Snowflake, Redshift, Databricks, or a non-dbt setup. See [Adapting to your stack](#adapting-to-your-stack).
* **The BigQuery CLI (`bq`)** — Installed as part of the [Google Cloud SDK](https://cloud.google.com/sdk/docs/install). Agents call it directly to query the warehouse, so no MCP server is required.
* **A Git repository where the Agent will work** — Warp auto-discovers Skills from `.agents/skills/` in your current working directory up through the repo root. See [Skills](https://docs.warp.dev/agents/capabilities/skills/) for the full list of supported directories and how discovery works.
## Walkthrough video
[Section titled “Walkthrough video”](#walkthrough-video)
In this 40-minute livestream, Warp’s data team demonstrates the workflow end-to-end, including the two Skills you’ll install below and a third pattern (running the same Skills from Slack via a cloud agent). Feel free to skip ahead if you prefer to follow the written steps.
## 1. Install the two skills
[Section titled “1. Install the two skills”](#1-install-the-two-skills)
Warp automatically discovers any Skill stored under `.agents/skills/` in your repo, so committing the two directories makes them available to every teammate’s Agent runs. Clone the public [warpdotdev/oz-skills](https://github.com/warpdotdev/oz-skills) repo and copy the two Skill directories into your own dbt repo:
```bash
cd /path/to/your/dbt-repo
mkdir -p .agents/skills
git clone https://github.com/warpdotdev/oz-skills.git /tmp/oz-skills
cp -r /tmp/oz-skills/.agents/skills/dbt-model-index .agents/skills/
cp -r /tmp/oz-skills/.agents/skills/analysis-artifacts .agents/skills/
```
Verify both Skills landed:
```bash
ls .agents/skills/
# analysis-artifacts dbt-model-index
```
Commit the Skills. Once committed to your repo, they are available to the whole team:
```bash
git add .agents/skills && git commit -m "Add self-serve analytics skills"
```
## 2. Customize the dbt model index
[Section titled “2. Customize the dbt model index”](#2-customize-the-dbt-model-index)
The [`dbt-model-index`](https://github.com/warpdotdev/oz-skills/blob/main/.agents/skills/dbt-model-index/SKILL.md) Skill is a template that you will need to fill in with details about your own models. This Skill teaches the Agent which tables answer which question types, so it’s important to spend time on customization. Detailed “Useful for” descriptions make the Skill most effective.
Open `.agents/skills/dbt-model-index/SKILL.md` and replace the template placeholders with real models. For each one, include:
* The table name (backtick-formatted)
* A 1- to 2-sentence description of its grain
* “Useful for:” bullets covering the question types it answers
A filled-in entry might look like this:
```markdown
### `users_daily`
One row per user per day, with activity signals and plan type.
**Useful for:**
- Daily, weekly, or monthly active user counts
- Retention and churn by plan tier
- Joining to revenue models as the canonical user dimension
```
Fill in the domains that cover your most common questions first (typically Users, Activity, and Revenue). You can expand the index over time as you notice the Agent guessing at tables.
Don’t skip the **Important Notes** section at the bottom of the Skill. Documenting your standard filters (e.g., `where not is_internal_user`), your fully-qualified project path, your partition fields, and any plan or tier values prevents the Agent from accidentally fanning out joins, scanning entire partitioned tables, or returning numbers polluted by test accounts.
After you complete this step, the Agent has a curated map from question to table and will consult it before writing any BigQuery SQL.
## 3. Review the analysis-artifacts Skill
[Section titled “3. Review the analysis-artifacts Skill”](#3-review-the-analysis-artifacts-skill)
The [`analysis-artifacts`](https://github.com/warpdotdev/oz-skills/blob/main/.agents/skills/analysis-artifacts/SKILL.md) Skill is workflow scaffolding. It tells the Agent how to structure a deep-dive analysis: plan first, save every material SQL query to `assets/queries/`, save visualizations to `assets/visualizations/`, and write a readable README with a Problem Statement, TL;DR, Cohorts Definition, per-step sections, and Key Takeaways.
No customization is needed to start using it. When the Agent invokes it, you’ll end up with a directory like:
```plaintext
analyses/
└── 2026-04-ai-usage-by-os/
├── README.md
└── assets/
├── queries/
│ └── ai_requests_by_os.sql
└── visualizations/
├── os_trend.py
└── os_trend.png
```
That structure is what makes the analysis shareable. A teammate can read the README, click through to any SQL file, and reproduce or extend the work.
## 4. Ask a simple data question
[Section titled “4. Ask a simple data question”](#4-ask-a-simple-data-question)
With both Skills in place, start with a concrete lookup prompt. This exercises `dbt-model-index` without pulling in the deep-dive workflow.
Open an Agent conversation inside your dbt repo and ask:
```plaintext
How many unique users made AI requests yesterday?
```
The Agent will:
1. Consult `dbt-model-index` to find the right activity table.
2. Write a BigQuery query, applying any standard filters you documented (e.g., excluding internal users).
3. Run the query via the `bq` CLI.
4. Return a single number along with the SQL it ran.
Verify the result by reviewing the query. If it used the wrong table or skipped a standard filter, your `dbt-model-index` entries for that domain need more detail. Update the Skill and try again.
## 5. Run a deep-dive analysis
[Section titled “5. Run a deep-dive analysis”](#5-run-a-deep-dive-analysis)
Now try a prompt that goes beyond a single lookup. The Agent recognizes this as a deep dive and invokes `analysis-artifacts`.
```plaintext
Tell me about any recent trends in AI usage across different operating systems in the last month.
```
The Agent will:
1. Use `dbt-model-index` to resolve the right activity and OS dimensions.
2. Invoke `analysis-artifacts`, propose a plan, and wait for your approval.
3. Execute the plan step by step, saving queries and visualizations as artifacts.
4. Write a README summarizing the analysis end to end.
The resulting README follows a consistent shape, roughly:
```markdown
# AI usage trends by operating system (last 30 days)
Author: Your Name
Date: 2026-04-22
## TL;DR
One or two sentences capturing the headline finding.
## Problem Statement
What the analysis set out to answer and why.
## Cohorts Definition
Explicit definition of the groups being compared, including tenure,
plan type, and observation windows.
## Step 1: Baseline volume by OS
Narrative, embedded chart, and a link to the query in assets/queries/.
## Step 2: Week-over-week trend
...
## Key Takeaways
Bulleted summary of what was learned and any follow-up questions.
```
Commit the new `analyses/<name>/` directory to your repo so it’s reviewable alongside your code. Anyone on the team can read it, verify the queries, or pick up where you left off.
## Adapting to your stack
[Section titled “Adapting to your stack”](#adapting-to-your-stack)
Both Skills were written for BigQuery and dbt, but the pattern generalizes. Here’s what to change:
* **Non-BigQuery warehouse (Snowflake, Redshift, Databricks)** — Update the **Important Notes** section of `dbt-model-index/SKILL.md` with your warehouse’s fully-qualified table reference format, partition or clustering conventions, and standard filters. Replace `bq` references with your warehouse’s CLI (e.g., `snowsql`, `redshift-data`).
* **No dbt** — The `dbt-model-index` Skill works for any warehouse schema, not just dbt. Rename it if you like, and treat the entries as a map over raw tables, views, or your semantic layer.
* **Different modeling conventions** — Document your grain, tier or plan values, and internal-user filters explicitly in the Skill. Agents are good at following documented rules and bad at guessing them.
The `analysis-artifacts` Skill is largely stack-agnostic. It structures outputs, not queries, so it works the same regardless of warehouse.
## Next steps
[Section titled “Next steps”](#next-steps)
You installed two community Skills, customized the model index for your warehouse, and ran both a simple lookup and a full deep-dive analysis.
**Extend to Slack.** Wire the same two Skills into a cloud agent configured with your dbt repo, and your teammates can ask data questions by tagging @warp in a Slack channel, without opening a terminal. The agent clones the repo, picks up the Skills from `.agents/skills/`, and replies in-thread. See the [Slack integration docs](https://docs.warp.dev/platform/integrations/slack/) and [Skills as Agents](https://docs.warp.dev/platform/skills-as-agents/) for setup.
Explore related guides and features:
* [Trigger reusable actions with saved prompts](/guides/configuration/trigger-reusable-actions-with-saved-prompts/) — another reusable Agent primitive, useful for scaffolding frequent data questions
* [Create project rules](/guides/configuration/how-to-create-project-rules-for-an-existing-project-astro-typescript-tailwind/) — pair Skills with Rules to steer Agent behavior across your repo
* [Skills](https://docs.warp.dev/agents/capabilities/skills/) — full reference on Skills, discovery, arguments, and slash-command invocation
* [warpdotdev/oz-skills](https://github.com/warpdotdev/oz-skills) — public repo with these two Skills and more
# Sync your monorepos
Canonical page: [/guides/configuration/how-to-sync-your-monorepos/](https://docs.warp.dev/guides/configuration/how-to-sync-your-monorepos/)
> Define global Rules in Warp to keep monorepo schemas, server types, and client types automatically synchronized across repositories.
Learn how to use Warp’s Rules system to connect interrelated repositories and automate type updates across your stack.

***
## Intro
[Section titled “Intro”](#intro)
This tutorial teaches you how to define **global Rules** in Warp so your coding agent understands how your projects relate to one another.
By linking monorepos (e.g., server, client, and shared API schemas), Warp automatically updates types and schemas across repos when you make a change in one place.
Although this example uses Warp’s internal repos, the same workflow applies to any multi-repo setup.
***
## The problem
[Section titled “The problem”](#the-problem)
When projects are split into multiple repos — like backend, client, and shared schema — developers often forget to synchronize type changes manually.
That’s error-prone and time-consuming. Warp solves this by teaching your **agent** the relationships between your repos through a global Rule.
***
## The Rule setup
[Section titled “The Rule setup”](#the-rule-setup)
Describe each repository and its connection to the others.
### Example Rule
[Section titled “Example Rule”](#example-rule)
```plaintext
We have three inter-related projects in ~/Repos:
warp-internal (client-side application)
warp-server (server application)
warp-proto-apis (shared API schemas for each)
When you update the schema types, push to git and update the installed types in the server and client by the commit hash.
```
Once defined, Warp automatically follows these instructions when a schema file is changed.
1. #### When the schema updates — update server types
[Section titled “When the schema updates — update server types”](#when-the-schema-updates--update-server-types)
`cd` into the server repository and run the appropriate commands to regenerate/update server-side types based on the changed schema.
2. #### When the schema updates — update client types
[Section titled “When the schema updates — update client types”](#when-the-schema-updates--update-client-types)
`cd` into the client repository and run the appropriate commands to regenerate/update client-side types so the client stays in sync with the schema changes.
***
Tip
Benefits
* Keeps your **schema, server, and client** perfectly in sync
* Reduces merge conflicts and version drift
* Saves manual steps when committing or deploying
# Use Agent Profiles efficiently
Canonical page: [/guides/configuration/how-to-use-agent-profiles-efficiently/](https://docs.warp.dev/guides/configuration/how-to-use-agent-profiles-efficiently/)
> Compare Strategic and YOLO agent profiles side-by-side to choose the right balance of planning, safety, and speed for your project.
Agent Profiles control how your coding agents behave in different contexts.\
They define what the agent can read, plan, or execute — and how much autonomy it has.
To show how profiles change workflow, we’ll build an NFL Predictor App using two profiles:
* Strategic Agent
* YOLO Agent

***
### Strategic Agent
[Section titled “Strategic Agent”](#strategic-agent)
Base Model: GPT-5\
Planning Model: Claude 4 Opus
Configuration:
* Apply code diffs → *agent decides*
* Read files → *always allow*
* Create plans → *always allow*
* Execute commands → *ask first*
When run:
1. The agent asks clarifying questions (e.g., *Do you want to scrape players and schedules?*)
2. Builds a detailed 14-step plan
3. Requests user input for environment variables
It’s thorough and safe — but pauses often if you miss setup details.
***
### YOLO Agent
[Section titled “YOLO Agent”](#yolo-agent)
Configuration:
* Apply code diffs → *always allow*
* Read files → *always allow*
* Create plans → *never*
* Execute commands → *always allow*
This agent skips long planning.\
It builds the project quickly, skipping over optional validation and focusing on essentials:
* Data ingestion
* Player stats
* Scoring calculation
It avoids brittle endpoints and produces a working dataset fast — though with fewer checks.
***
### Comparing the two
[Section titled “Comparing the two”](#comparing-the-two)
| Trait | Strategic Agent | YOLO Agent |
| --------- | ------------------- | ------------------ |
| Planning | Detailed (14 steps) | Minimal (10 steps) |
| Safety | High | Low |
| Speed | Moderate | Very fast |
| Ideal For | Production projects | Quick prototypes |
# Use tokens more efficiently with AI coding agents
Canonical page: [/guides/configuration/how-to-use-tokens-efficiently-with-ai-coding-agents/](https://docs.warp.dev/guides/configuration/how-to-use-tokens-efficiently-with-ai-coding-agents/)
> Get more out of every token your coding agents use in Warp with model choice and routing, focused context, conversation management, and Rules.
Every agent task consumes tokens. Tokens are the unit of text a model reads and generates. The more tokens a task uses, the more it costs and the longer it takes, so using tokens efficiently keeps your agent workflows lean and fast.
In Warp, this usage is measured in credits. Credits package tokens into a single, consistent unit that accounts for the different token rates and prices across models and providers, so you don’t have to track raw tokens per model yourself.
This guide covers practical ways to get more out of every token in Warp. You’ll learn how to choose the right model, route tasks to cost-appropriate models, keep context tight, manage conversations, and configure your agents to work efficiently.
Token usage is non-deterministic, so treat these as habits that make your tokens go further over time, not exact per-task guarantees. For a full breakdown of what drives usage, see [what affects usage](/support-and-community/plans-and-billing/credits/).
## Track your usage first
[Section titled “Track your usage first”](#track-your-usage-first)
You can’t improve what you can’t see. Before optimizing, get a sense of which prompts, models, and workflows use the most tokens.
* **Per-turn breakdown** - Expand the usage chip at the bottom of any agent response to open its **Usage Summary**, which shows the model, tool calls, context window used, and diffs applied for that turn.
* **In-conversation details** - Run `/cost` to toggle usage details directly in the conversation.
* **Total usage and reset date** - In the Warp app, open **Settings** > **Billing and usage**, or run `/usage`, to track your overall consumption and when your usage resets.

The per-turn Usage Summary, opened from the usage chip on an agent response.
Once you know where your tokens go, the techniques below help you make each one go further.
## Match the model to the task
[Section titled “Match the model to the task”](#match-the-model-to-the-task)
Larger reasoning models process more tokens per turn than lighter ones, so the model you choose has one of the biggest effects on usage.
* **Use a cost-efficient model for routine work** - Switch to **Auto (Cost-efficient)** (`auto-efficient`), which optimizes for lower token consumption while keeping output quality high. Lightweight models like Claude Haiku also use fewer tokens for simple edits, lookups, and quick questions.
* **Prefer open-weight models** - If you’d rather run open-source models, choose **Auto (Open-weights)** (`auto-open`), which routes among the best open-weight models for low cost and fast speed.
* **Reserve high-reasoning models for hard problems** - Save heavier models like Claude Opus for deep debugging, architecture decisions, and planning, where the extra reasoning is worth the cost.
* **Pick a model and stay with it** - Switching models mid-conversation can reset prompt caching and reprocess your context. Choose a model at the start of a task and keep it for the duration when you can.
Change models with the model picker in the input, or run `/model`. See [Agent model choice](/agents/inference/model-choice/) for the full model list.
## Automate model selection with custom routers
[Section titled “Automate model selection with custom routers”](#automate-model-selection-with-custom-routers)
Use a custom router to automatically choose a model. You define the routing logic once, and Warp resolves a concrete model for each prompt instead of defaulting every task to your most expensive model.
* **Route by complexity** - Warp classifies each task as easy, medium, or hard and routes to the model you mapped to that level. Simple tasks run on a lightweight model; only difficult tasks reach a high-reasoning model.
* **Route by rules** - Write natural-language rules that pair a description (such as “debugging or fixing failing tests”) with a model. Warp matches rules top to bottom and uses the first one that fits.
* **Set a cost-efficient default** - Every router falls back to a default model for anything your tiers or rules don’t cover, so choose a lighter model for the default.
A router appears in the model picker like any other model and resolves per conversation, so token usage matches whichever model it picks. Create one in the Warp app under **Settings** > **Agents** > **Warp Agent** in the **Custom Routers** section. See [Custom routers](/agents/inference/custom-routers/) for setup steps and YAML examples.
## Keep each conversation focused
[Section titled “Keep each conversation focused”](#keep-each-conversation-focused)
Because every turn re-sends the current conversation to the model, long or unfocused threads keep paying for the same context. Tight, well-scoped conversations keep token usage low.
* **Scope tasks and work incrementally** - Break large changes into smaller, contained steps instead of one sprawling request. Well-scoped tasks need less back-and-forth and fewer correction cycles.
* **Start a new conversation for a new task** - Run `/new` when you switch topics so unrelated history doesn’t ride along in every turn.
* **Compact long conversations** - When a useful thread grows long, run `/compact` to summarize the history and free up the context window. Use `/fork-and-compact` to branch into a fresh, summarized copy that keeps the relevant context and trims the rest.
See [Conversation forking](/agents/local-agents/interacting-with-agents/conversation-forking/) and the full [Slash Commands](/agents/capabilities/slash-commands/) reference for more.
## Be selective about the context you add
[Section titled “Be selective about the context you add”](#be-selective-about-the-context-you-add)
Context you attach becomes tokens the model has to process. Adding only what’s relevant keeps each turn lean.
* **Attach focused snippets, not full dumps** - When sharing logs, code, or command output, include only the relevant portion instead of an entire file or output.
* **Add context deliberately** - Attach the specific [blocks](/agents/local-agents/agent-context/blocks-as-context/), files, or images the agent needs for the task, rather than broad, just-in-case context.
## Let Codebase Context retrieve code for you
[Section titled “Let Codebase Context retrieve code for you”](#let-codebase-context-retrieve-code-for-you)
When an agent explores your repository by reading files one by one, each read is a tool call that consumes tokens. Indexing your codebase lets Warp find the right code with semantic search instead.
* **Index your repository** - Run `/index` so Warp can locate relevant code by meaning, reducing the number of exploratory tool calls and the amount of code you paste in manually.
* **Let the agent search instead of pasting** - With an indexed codebase, ask about a feature or file directly rather than copying large sections into the prompt.
Learn more in [Codebase Context](/agents/capabilities/codebase-context/).
## Set up Rules and AGENTS.md
[Section titled “Set up Rules and AGENTS.md”](#set-up-rules-and-agentsmd)
Without persistent guidance, agents re-derive your preferences every session and sometimes drift off course, which wastes tokens on corrections and rework. Rules encode that guidance once.
* **Capture preferences as Rules** - Store your tools, conventions, and standards as [Rules](/agents/capabilities/rules/) so you don’t re-explain them in every conversation. Add one with `/add-rule`.
* **Add a project AGENTS.md** - Run `/init` to generate a project `AGENTS.md` that gives agents the context they need up front, reducing exploration and missteps.
For examples, see [Set coding best practices with Rules](/guides/configuration/how-to-set-coding-best-practices/).
## Plan large or complex tasks first
[Section titled “Plan large or complex tasks first”](#plan-large-or-complex-tasks-first)
For big or ambiguous tasks, jumping straight to implementation often leads to wrong turns and expensive rework. A short planning pass keeps execution on track.
* **Create a plan before executing** - Run `/plan` to have the agent research and outline the work in phases before it changes code. A clear plan reduces wasted exploratory work and backtracking on large tasks.
See [Planning](/agents/capabilities/planning/) for details.
## Next steps
[Section titled “Next steps”](#next-steps)
Together, these habits help you get more out of every token: match the model to the task, keep conversations and context tight, and configure Rules and Codebase Context. Pair them with the right Agent Profile, and keep an eye on your usage as you go.
Explore these related guides and references:
* [Use Agent Profiles efficiently](/guides/configuration/how-to-use-agent-profiles-efficiently/)
* [Agent model choice](/agents/inference/model-choice/)
* [Custom routers](/agents/inference/custom-routers/)
* [Slash Commands](/agents/capabilities/slash-commands/)
# Trigger reusable actions with saved prompts
Canonical page: [/guides/configuration/trigger-reusable-actions-with-saved-prompts/](https://docs.warp.dev/guides/configuration/trigger-reusable-actions-with-saved-prompts/)
> Save and share prompts in Warp Drive to automate commits, code reviews, and PR creation across your team.

### 1. Automating commits
[Section titled “1. Automating commits”](#1-automating-commits)
When working on a PR, instead of typing long commit messages, you can use a saved prompt.
Warp’s agent:
* Runs a `git diff` and summarizes the change
* Generates a clean commit message
* Pushes it automatically to your branch
You can view the saved prompt in **Warp Drive** > **Prompts**, where it shows:
* Who created it
* When it was last used
* How many times it’s been run
Because it’s saved in your team drive, anyone can reuse it.
***
### 2. Reviewing code with prompts
[Section titled “2. Reviewing code with prompts”](#2-reviewing-code-with-prompts)
Before creating a PR, you can run another saved prompt.
This agent:
* Reads your current branch
* Reviews the diffs
* Highlights logical or stylistic issues
* Suggests improvements
Example output:
> “Logic bug detected — potential race condition in async handler.”
Warp automatically surfaces real issues before you even open a PR — saving time and reducing back-and-forth with reviewers.
***
### 3. Opening a pull request automatically
[Section titled “3. Opening a pull request automatically”](#3-opening-a-pull-request-automatically)
Once your code looks clean, trigger your final saved prompt.
Warp will:
* Generate a PR title and description
* Push the branch
* Open the PR on GitHub
* Even link related issues if found in commit messages
***
### 4. Sharing and team usage
[Section titled “4. Sharing and team usage”](#4-sharing-and-team-usage)
All saved prompts live in your Team Warp Drive, meaning:
* Anyone can discover and run them
* You can parameterize or modify them
* Usage history and creator info are visible
This makes it easy for teams to standardize common actions like code reviews, deployments, or build runs.
# Analyze Cloud Run logs (gcloud)
Canonical page: [/guides/devops/how-to-analyze-cloud-run-logs-gcloud/](https://docs.warp.dev/guides/devops/how-to-analyze-cloud-run-logs-gcloud/)
> Use Warp to pull, organize, and analyze Cloud Run production logs by severity with natural language prompts and automated Python scripts.
Learn how to use Warp to retrieve, organize, and analyze production logs from your cloud servers — all with natural language prompts.

1. #### Setting the context
[Section titled “Setting the context”](#setting-the-context)
Open Warp and enable **voice input** (optional) for hands-free prompting.
Note
Voice input is optional — only enable it if you prefer hands-free prompting.
**Prompt**
```plaintext
Use the warp-server-staging gcloud project and pull logs
for the last 10 minutes from the warp-server Cloud Run instance.
Organize them by info, warning, and error levels.
Create a histogram across message types,
and highlight the most concerning errors to investigate.
```
2. #### Warp’s agent in action
[Section titled “Warp’s agent in action”](#warps-agent-in-action)
After you hit Enter:
* Warp detects the command as an **Agent Mode** request.
* It gathers project context (`warp-server-staging`).
* Executes the necessary `gcloud` logging queries automatically.
* Writes retrieved data to a temporary file for processing.
3. #### Automated analysis
[Section titled “Automated analysis”](#automated-analysis)
Warp’s agent generates a **Python script** on the fly to:
* Parse logs
* Count messages by severity
* Output summary metrics
Example output:
```plaintext
1,000 log entries total
980 info
11 warning
9 errors
```
You can view or fast-forward execution, or stop the process at any point.
4. #### Reviewing results
[Section titled “Reviewing results”](#reviewing-results)
Warp outputs a readable histogram and highlights anomalies.\
For example:
> “Gemini AI error messages detected — worth reviewing.”
You can expand each log group interactively or inspect the temporary Python code for debugging.
# Create a production-ready Docker setup
Canonical page: [/guides/devops/how-to-create-a-production-ready-docker-setup/](https://docs.warp.dev/guides/devops/how-to-create-a-production-ready-docker-setup/)
> Use Agents in Warp to generate optimized Dockerfiles, docker-compose configs, and .dockerignore files for multi-stage production deployments.
Learn how to use Warp’s AI to automatically build a clean, multi-stage Docker setup for both development and production.

This tutorial shows how to create a **complete Docker environment** in minutes using Warp.\
Warp’s AI can analyze your entire codebase, generate **Dockerfiles**, **.dockerignore**, and **docker-compose.yml** — all optimized for small image size and multi-service orchestration.
Although this example uses a generic web app, the same pattern applies to **Python**, **Node.js**, **Go**, and other ecosystems.
1. #### The challenge
[Section titled “The challenge”](#the-challenge)
You’ve built your app and suddenly realize — it should have been containerized from the start.\
Manually configuring Docker files, image sizes, and environment variables takes time and breaks flow.
2. #### The prompt
[Section titled “The prompt”](#the-prompt)
Use this prompt inside Warp’s AI input:
```plaintext
"Analyze my entire project directory structure, package files, and configuration to generate a complete production-ready Docker setup. I need:
A multi-stage Dockerfile optimized for my specific language/framework with proper layer caching, security best practices, and minimal image size
A docker-compose.yml for both development and production environments with all necessary services, networks, volumes, and environment variable handling
A comprehensive .dockerignore file that excludes unnecessary files but keeps what's needed for the build
Startup scripts and health check configurations
Documentation explaining each Docker command and why specific choices were made
Please detect my project type automatically and configure everything accordingly. Include comments explaining the optimization decisions."
```
Warp will detect frameworks, infer services, and produce a ready-to-run setup.
3. #### Review and customize
[Section titled “Review and customize”](#review-and-customize)
Warp outputs:
* Optimized base images
* Cached build layers
* Correct dependency stages
* Unified environment management
You can easily adjust service names or ports in the generated compose file.
# Create a priority matrix for database optimization
Canonical page: [/guides/devops/how-to-create-priority-matrix-for-database-optimization/](https://docs.warp.dev/guides/devops/how-to-create-priority-matrix-for-database-optimization/)
> Prompt Warp to audit SQL queries, analyze execution plans, and generate a priority matrix ranking database optimizations by impact and effort.
Learn how to generate a data-driven optimization matrix that ranks database issues by impact, risk, and effort.

1. #### Intro
[Section titled “Intro”](#intro)
This tutorial teaches you how to prompt Warp to audit and optimize your **database performance** automatically.
It analyzes SQL queries, identifies common inefficiencies, and generates a **priority matrix** for improvements.
2. #### The problem
[Section titled “The problem”](#the-problem)
When you tell AI to “optimize a query,” that could mean *anything* — faster, safer, or simpler.\
Instead, use Warp to clarify intent and return measurable outcomes.
3. #### The prompt
[Section titled “The prompt”](#the-prompt)
Paste this into Warp’s AI input:
````plaintext
# **Comprehensive Database Query Analysis and Optimization Guide**
This guide provides a structured, repeatable approach for analyzing, profiling, and optimizing database performance within your application.
---
## **PHASE 1: Query Discovery & Cataloging**
### **Step 1 — Identify All Queries**
Scan the entire codebase and locate every SQL or ORM-based query. This includes:
- All **raw SQL queries**, including stored procedures
- **ORM-generated queries** (capture the actual SQL being produced)
- **Dynamic query builders** and their permutations
- **Background job queries** that may run at scale
- **Admin or reporting queries** that could lock tables
### **Step 2 — Document Key Details**
For each query discovered, record the following:
- **File location and function name**
- **Frequency of execution** (per request, batch job, or cron schedule)
- **Typical data volume processed**
---
## **PHASE 2: Performance Analysis**
For each identified query, generate and analyze a detailed **execution plan**.
### **Execution Plan Commands**
```sql
-- PostgreSQL
EXPLAIN (ANALYZE, BUFFERS, FORMAT JSON);
-- MySQL
EXPLAIN FORMAT=JSON;
```
### **Extract the Following Metrics**
- Total execution time
- Rows examined vs. rows returned ratio
- Index usage (full table scans, index scans, seeks)
- Join methods (nested loop, hash, merge)
- Memory usage and temporary file creation
- Buffer pool hit ratio
---
## **PHASE 3: Identify Specific Problems**
### **1. N+1 Query Detection**
**Problem:** Loading users and their posts separately
**Found in:** `/api/users/controller.js:45`
**Impact:** 100 queries for 100 users instead of one batched query
#### **Current Implementation**
```js
const users = await db.query('SELECT * FROM users');
for (const user of users) {
user.posts = await db.query('SELECT * FROM posts WHERE user_id = ?', [user.id]);
}
```
#### **Optimized Version**
```js
const usersWithPosts = await db.query(`
SELECT u.*,
COALESCE(json_agg(p.*) FILTER (WHERE p.id IS NOT NULL), '[]') AS posts
FROM users u
LEFT JOIN posts p ON p.user_id = u.id
GROUP BY u.id;
`);
```
---
### **2. Missing Index Analysis**
**Finding:** Full table scan on `orders` table (2M rows)
**Query:**
```sql
SELECT * FROM orders WHERE status = 'pending' AND created_at > ?;
```
**Recommendation:**
```sql
CREATE INDEX idx_orders_status_created ON orders(status, created_at);
```
**Impact:** Query time reduced from **3.2s → 0.045s**
---
### **3. Inefficient JOIN Patterns**
**Problem:** Queries join through unnecessary intermediate tables.
**Solution:** Simplify relationships using direct joins or indexed subqueries where possible.
---
### **4. Subquery Optimization**
**Inefficient Query:**
```sql
SELECT * FROM products
WHERE price > (SELECT AVG(price) FROM products WHERE category_id = p.category_id);
```
**Optimized (Using Window Function):**
```sql
WITH product_stats AS (
SELECT *,
AVG(price) OVER (PARTITION BY category_id) AS avg_category_price
FROM products
)
SELECT * FROM product_stats WHERE price > avg_category_price;
```
---
## **PHASE 4: Advanced Optimizations**
### **Caching Strategies**
Use caching for:
- User-specific data with low update frequency
- Expensive aggregations that can be pre-computed
#### **Implementation**
```js
// Add caching layer with TTL
const getCachedOrQuery = async (key, query, ttl = 3600) => {
const cached = await redis.get(key);
if (cached) return JSON.parse(cached);
const result = await db.query(query);
await redis.setex(key, ttl, JSON.stringify(result));
return result;
};
```
---
### **Recommended Connection Configuration**
```json
{
"connectionLimit": 50,
"queueLimit": 100,
"acquireTimeout": 30000,
"waitForConnections": true,
"idleTimeout": 300000,
"enableKeepAlive": true,
"keepAliveInitialDelay": 10
}
```
---
### **Batch Operation Optimization**
**Problem:** Records are inserted one by one
**Found in:** `/jobs/import-data.js`
**Current Implementation:**
1000 individual `INSERT` statements
**Optimized:**
```sql
INSERT INTO users (name, email, created_at) VALUES
($1, $2, $3),
($4, $5, $6),
... -- batch in groups of 1000
```
---
### **Pagination Optimization**
```sql
SELECT * FROM posts
WHERE created_at < $cursor
ORDER BY created_at DESC
LIMIT 20;
```
---
## **PHASE 5: Monitoring & Maintenance**
### **1. Slow Query Logging Setup**
#### **PostgreSQL**
```sql
ALTER SYSTEM SET log_min_duration_statement = '1000'; -- Log queries over 1s
ALTER SYSTEM SET log_statement = 'all';
ALTER SYSTEM SET log_duration = on;
```
#### **MySQL**
```sql
SET GLOBAL slow_query_log = 'ON';
SET GLOBAL long_query_time = 1;
SET GLOBAL log_output = 'TABLE';
```
---
### **2. Query Performance Testing**
```js
describe('Query Performance', () => {
test('User listing should complete under 100ms', async () => {
const start = Date.now();
await db.query('SELECT * FROM users LIMIT 1000');
expect(Date.now() - start).toBeLessThan(100);
});
});
```
---
## **PHASE 6: Deliverables**
### **Deliverable Outputs**
- **Optimization Script:** A single SQL file with all index creations, ordered by performance impact.
- **Code Changes PR:** Includes all query optimizations with before/after comparison results.
### **Performance Report**
- Baseline metrics vs. optimized metrics
- Expected resource savings (CPU, memory, I/O)
- Risk assessment for each change
### **Monitoring Dashboard**
Define recurring queries to track query performance over time.
---
## **PRIORITY MATRIX**
Rank each optimization by:
- **Impact:** Query frequency × time saved
- **Risk:** Low / Medium / High
- **Effort:** Quick fix / Moderate / Complex refactor
> Focus on **high-impact**, **low-risk**, **low-effort** items first.
---
### **Summary**
This workflow ensures the AI:
1. Systematically identifies all queries
2. Analyzes them using database-specific profiling tools
3. Provides **actionable, tested solutions**
4. Considers the full application context
5. Delivers **implementation-ready optimizations**
````
Warp will locate all SQL usage, test each query, and score them using explain-plan data.
4. #### Review the matrix
[Section titled “Review the matrix”](#review-the-matrix)
The output includes:
* Query locations
* Performance metrics
* Recommended fixes
* A **graph** mapping impact vs effort
Caution
A well-tuned database is the heart of your web stack — don’t skip it.
# Generate unit and security tests to debug faster
Canonical page: [/guides/devops/how-to-generate-unit-and-security-tests-to-debug-faster/](https://docs.warp.dev/guides/devops/how-to-generate-unit-and-security-tests-to-debug-faster/)
> Prompt Warp to generate comprehensive unit and security tests for REST APIs, including SQL injection, XSS, and auth validation checks.
Learn how to prompt Warp’s AI to generate useful unit and security tests — helping you debug faster and deploy with confidence.

***
1. #### The problem
[Section titled “The problem”](#the-problem)
Building REST APIs involves a lot of overhead: validation, testing, and security.\
Most “auto-generated tests” from AI end up generic and incomplete — leaving gaps in reliability.
To solve this, Warp lets you run **precise, context-aware test generation** using better-structured prompts.
2. #### The prompt
[Section titled “The prompt”](#the-prompt)
Paste this into Warp’s AI input:
prompt.txt
```text
After implementing this API code, generate comprehensive unit tests and security tests to verify everything works correctly and securely:
1. Unit tests for each function / method
Core functionality
- Happy path with valid inputs -> expected output
- Each edge case (empty inputs, nulls, boundary values)
- Error handling for invalid inputs
- Return value types and structure
- Edge cases: empty strings, null/undefined, max values, special characters
2. SECURITY TESTS FOR EACH ENDPOINT
For every API endpoint, create security tests that check:
Input validation
Test with these malicious payloads in every user input field:
SQL Injection: " ' OR '1' = '1', "1; DROP TABLE users--", "admin'--"
NoSQL Injection: {"$gt": ""}, {"$ne": null}
Command Injection: "; ls -la", "| whoami", "$(cat /etc/passwd)"
Path Traversal: "../../../etc/passwd", "..\..\..\windows\system32"
XSS: "<script>alert('XSS')</script>", "javascript:alert(1)"
XXE (for XML): "<!DOCTYPE foo [<!ENTITY xxe SYSTEM 'file:///etc/passwd'>]>"
Authentication Tests:
- No token/credentials → Must return 401
- Invalid token → Must return 401
- Expired token → Must return 401
- Valid token for wrong user → Must return 403
- Token with insufficient permissions → Must return 403
Authorization Tests:
- User A trying to access User B's data → 403
- Regular user accessing admin endpoints → 403
- Deleted/disabled user token → 401
- Verify all role-based access controls work
Additional Security Checks:
- Rate limiting works (spam 100 requests → 429 response)
- Large payloads are rejected (>1MB unless specified)
- Sensitive data not exposed in errors
- Headers don't leak server info
- CORS properly configured
3. After running all tests, ensure:
✓ All unit tests pass
✓ 100% of functions have tests
✓ All security tests pass
✓ No SQL/NoSQL injection vulnerabilities
✓ Authentication is properly enforced
✓ Authorization rules are working
✓ Input validation catches malicious data
✓ Error messages don't expose sensitive info
4. Output Format
Generate 2 test files:
1. Unit_tests.[ext] - all functional tests
2. security_tests.[ext] - all security tests
Use simple assertions that clearly show:
- What is being tested
- What the expected behavior is
- Why this test matters
Keep these tests simple and focused - each test should verify ONE thing
```
3. #### Add to Rules file
[Section titled “Add to Rules file”](#add-to-rules-file)
Once you’ve validated the prompt, add it to your Warp Rules file so Warp can automatically reuse it.
```plaintext
Name: Run tests after writing
Rule: run pytest mapp/tests to validate if the code you inserted works
```
Warp will then run these tests as a source of truth — deciding whether new AI-generated code is safe to merge or deploy.
4. #### Recap
[Section titled “Recap”](#recap)
Tip
You’ve learned how to:
* Prompt for **specific test coverage**
* Automate your **unit and security tests**
* Use Warp’s **Rules** feature for validation
Small change in prompt structure — big jump in reliability.
# Prevent secrets from leaking
Canonical page: [/guides/devops/how-to-prevent-secrets-from-leaking/](https://docs.warp.dev/guides/devops/how-to-prevent-secrets-from-leaking/)
> Use Warp Rules and built-in Secret Redaction to prevent API keys and credentials from leaking in agent output, demos, and shared sessions.
Learn how to safeguard credentials and sensitive data using Warp’s Secret Redaction and Rule system.

This tutorial shows how to use Warp’s **Rules** to prevent agents or collaborators from exposing sensitive information while coding or sharing output. Whether you’re pair-programming, streaming, or reviewing code, Warp can automatically redact secrets before they’re ever seen by an agent.
1. #### The problem
[Section titled “The problem”](#the-problem)
AI assistants often echo API keys, tokens, or credentials in generated code blocks.\
When collaborating or screen-sharing, that can expose secrets publicly.
2. #### The Rule setup
[Section titled “The Rule setup”](#the-rule-setup)
Define a simple Rule in Warp that instructs the agent to **never display secrets** in outputs or commands.
```plaintext
Rule: Protect Secrets
Behavior:
- Never include or reveal secrets when generating code or commands.
- Automatically redact sensitive strings before showing output.
```
Note
Enable Warp’s built-in Secret Redaction:
**Settings** > **Privacy** > **Secret redaction**
This automatically masks sensitive values before the agent or output logs can access them.
3. #### Benefits
[Section titled “Benefits”](#benefits)
* Protects API keys and credentials from exposure
* Keeps live streams and demos safe
* Works seamlessly with pair-programming or AI debugging
# Write SQL commands inside a Postgres REPL
Canonical page: [/guides/devops/how-to-write-sql-commands-inside-a-postgres-repl/](https://docs.warp.dev/guides/devops/how-to-write-sql-commands-inside-a-postgres-repl/)
> Use Agents in Warp inside a Postgres REPL to translate natural language into SQL queries — works with Node.js, Python, and MySQL too.
Note
This tutorial teaches you how to use **Warp’s AI input** to run natural-language prompts inside an interactive **Postgres REPL**, turning plain English into SQL commands.\
\
Although the example uses **PostgreSQL**, the same workflow applies to **Node.js**, **Python**, **MySQL**, and other interactive shells.

***
### 🧠 Overview
[Section titled “🧠 Overview”](#-overview)
You’ll learn how to:
* Start a Postgres REPL in Warp.
* Use `Cmd+I` (or `Ctrl+I`) to open Warp’s AI input.
* Speak or type natural-language requests and let Warp translate them into SQL.
* Run the generated queries directly inside your REPL session.
1. #### Open a Postgres REPL in Warp
[Section titled “Open a Postgres REPL in Warp”](#open-a-postgres-repl-in-warp)
Open Warp and connect to your Postgres database (or a test instance):
```bash
psql -U postgres -d my_database
```
You’ll enter the interactive `psql` prompt, where you normally type SQL commands.
2. #### Invoke Warp’s AI input
[Section titled “Invoke Warp’s AI input”](#invoke-warps-ai-input)
Inside the running REPL, press:
```plaintext
Cmd+I (macOS)
Ctrl+I (Windows/Linux)
```
This opens the **Generate Input** box.
You can **type or speak** in plain English — Warp will translate your request into valid SQL or shell syntax, depending on the REPL you’re in.
3. #### Ask Warp in natural language
[Section titled “Ask Warp in natural language”](#ask-warp-in-natural-language)
Start with a simple request:
```plaintext
Show me all tables.
```
Warp translates this to the Postgres command:
```sql
\dt
```
Then try a more specific query, as shown in the video:
```plaintext
Show me our users table and our teams table.
```
Warp generates:
```sql
SELECT * FROM users;
SELECT * FROM teams;
```
You can run both within your REPL to display the tables.
4. #### Observe how Warp learns from context
[Section titled “Observe how Warp learns from context”](#observe-how-warp-learns-from-context)
As you continue issuing prompts, Warp’s agent **learns the structure of your database** by observing what’s printed in the REPL output.
This means you can ask progressively more complex questions, and Warp will tailor the SQL accordingly.
```plaintext
Show me all of the users who have joined Warp in the last 90 days from public email accounts
(like Gmail, Yahoo, Hotmail) and are on teams of more than two people.
```
Warp generates a multi-clause SQL query such as:
```sql
SELECT *
FROM users
WHERE email LIKE '%gmail.com%'
OR email LIKE '%yahoo.com%'
OR email LIKE '%hotmail.com%'
AND joined_at > NOW() - INTERVAL '90 days'
AND team_size > 2;
```
Running this query in `psql` filters users accordingly.
5. #### Apply the same workflow to other REPLs
[Section titled “Apply the same workflow to other REPLs”](#apply-the-same-workflow-to-other-repls)
This feature works **not just in Postgres** but also in:
* Node.js
* Python
* MySQL
* GDB (GNU Debugger)
For any of these environments:
1. Launch the REPL inside Warp.
2. Press `Cmd+I` to bring up AI input.
3. Describe what you want in natural language.
4. Warp translates it into the correct syntax for that environment.
Note
Warp automatically detects the active REPL, so you don’t need to specify “SQL” or “Python” — it knows which language to generate.
6. #### Experiment and iterate
[Section titled “Experiment and iterate”](#experiment-and-iterate)
Try varying your natural-language prompts:
```plaintext
List all databases.
```
```sql
\l
```
```plaintext
Count how many users signed up this month.
```
```sql
SELECT COUNT(*) FROM users WHERE joined_at > date_trunc('month', NOW());
```
The more you experiment, the more context Warp gathers, improving its translations.
***
### 🏁 Key takeaways
[Section titled “🏁 Key takeaways”](#-key-takeaways)
* `Cmd+I` activates Warp’s AI input within any interactive shell.
* Warp understands natural language and produces valid commands for the current REPL.
* It **learns from context** — subsequent prompts become more accurate.
* Works beyond Postgres: Node, Python, MySQL, and others.
* A fast way to query or explore systems without memorizing syntax.
Tip
Next time you’re stuck remembering a command in Postgres or Python, hit `Cmd+I` and just ask Warp in plain English.
# Improve your Kubernetes workflow (kubectl + Helm)
Canonical page: [/guides/devops/improve-your-kubernetes-workflow-kubectl-helm/](https://docs.warp.dev/guides/devops/improve-your-kubernetes-workflow-kubectl-helm/)
> Streamline kubectl and Helm workflows with Warp's AI assistance, active suggestions, custom workflows, and synchronized panes.
Discover how Warp’s modern terminal features streamline Kubernetes workflows through AI assistance, automation, and intuitive design.

## Overview
[Section titled “Overview”](#overview)
This guide covers 6 key Warp features that enhance Kubernetes productivity:
1. #### AI integration in the terminal
[Section titled “AI integration in the terminal”](#ai-integration-in-the-terminal)
Warp’s **Agent Mode** (`Cmd+I`) lets you run complex Kubernetes operations with plain-English prompts.
**Examples**
```plaintext
When does my wildcard TLS certificate expire?
```
Warp auto-detects namespaces, runs `kubectl` commands, and outputs expiration details.
```plaintext
Generate a command to identify all pods running as root across all namespaces.
```
Warp builds and runs the corresponding `kubectl` + `grep` query, returning a security report.
Note
Ideal for on-the-fly debugging or compliance checks without leaving your terminal.
2. #### Building AI-aided context
[Section titled “Building AI-aided context”](#building-ai-aided-context)
You can attach any command’s output as context for follow-up prompts.\
For instance, right-click log output → “Attach as Agent Context,” then run:
```plaintext
I’m sending anonymous usage data in Traefik. How can I disable it?
```
Warp detects the Helm chart and outputs the required YAML config to disable stats reporting.
3. #### Active AI suggestions
[Section titled “Active AI suggestions”](#active-ai-suggestions)
Warp automatically suggests next actions.\
Examples of suggested actions:
* After `kubectl describe pod` it might propose:
> “Check the logs of this pod.”
* When running `sudo apt update` it detects available upgrades and offers:
> “Run sudo apt upgrade to update packages.”
4. #### Custom workflows
[Section titled “Custom workflows”](#custom-workflows)
Create reusable, parameterized commands for common operations like:
```bash
helm upgrade <chart> --namespace <namespace> -f <values.yaml>
```
Accessible from the **Command Palette** (`Cmd+P`), workflows make repetitive Kubernetes tasks fast and standardized.
5. #### Synchronized panes and tabs
[Section titled “Synchronized panes and tabs”](#synchronized-panes-and-tabs)
Link multiple terminal panes or tabs (e.g., master + worker nodes).\
When synchronization is active, running:
```bash
sudo apt update
```
executes simultaneously across all linked sessions.
6. #### Modern text editing
[Section titled “Modern text editing”](#modern-text-editing)
Warp supports **click-to-edit** for commands — no more arrow key gymnastics.\
Hovering shows inline **tooltips** explaining flags and subcommands (e.g., Helm, kubectl, etc.), with autocompletions for 400+ CLI tools.
# Build a Mattermost bot for Warp Factories
Canonical page: [/guides/external-tools/build-a-mattermost-bot-for-warp-factories/](https://docs.warp.dev/guides/external-tools/build-a-mattermost-bot-for-warp-factories/)
> Build a Mattermost bot that discovers a Warp factory by name, dispatches tasks to it, and continues the conversation from replies in a thread.
Build a Mattermost bot that sends work to a [Warp factory](/factories/) and posts progress back into the thread where it started, the same experience Warp’s own [Slack integration](/factories/integrations/slack/) gives teams that use Slack. Warp doesn’t ship a Mattermost integration directly, so this guide uses [factory endpoints](/factories/factory-api/) to build the equivalent yourself. It takes about 20 minutes if you already have a Mattermost bot account and a factory set up.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **A Warp Factories factory** - [Set up a factory](/factories/quickstart/) before starting; this guide dispatches work to an existing factory rather than creating one.
* **A Warp API key** - Create an [agent API key](/agents/cli/oz-cli/api-keys/#personal-vs-agent-keys) rather than a personal key, so the bot’s requests aren’t tied to your individual account.
* **A Mattermost bot account and access token** - Create one from your Mattermost System Console under **Integrations** > **Bot Accounts**, and generate a personal access token for it. Mattermost’s own [bot accounts documentation](https://developers.mattermost.com/integrate/reference/bot-accounts/) covers the exact steps, since they vary by Mattermost version and hosting setup.
* **The Warp Platform API Python SDK** - Install it with `pip install oz-agent-sdk`. If you’re working in another language, [factory endpoints](/factories/factory-api/) show the equivalent REST calls.
## 1. Store your credentials
[Section titled “1. Store your credentials”](#1-store-your-credentials)
Export your Warp API key, Mattermost bot token, and a webhook token as environment variables so none of them end up hardcoded in your bot’s source. You’ll generate the webhook token in the next step:
```bash
export WARP_API_KEY=YOUR_WARP_API_KEY
export MATTERMOST_BOT_TOKEN=YOUR_MATTERMOST_BOT_TOKEN
export MATTERMOST_WEBHOOK_TOKEN=YOUR_MATTERMOST_WEBHOOK_TOKEN
export MATTERMOST_URL=https://YOUR_MATTERMOST_SERVER
```
The bot uses the Warp API key to call factory endpoints, the bot token to post replies back into the channel, and the webhook token to confirm each inbound request actually came from Mattermost.
## 2. Create an outgoing webhook in Mattermost
[Section titled “2. Create an outgoing webhook in Mattermost”](#2-create-an-outgoing-webhook-in-mattermost)
[Mattermost outgoing webhooks](https://developers.mattermost.com/integrate/webhooks/outgoing/) fire on messages in a specific public channel, a specific trigger word, or both - not on arbitrary @-mentions the way a Slack app receives them. To get mention-like behavior, set the trigger word to something like `factory:` and require your team to lead requests with it.
From **Product menu** > **Integrations** > **Outgoing Webhooks** in Mattermost:
1. Select **Add Outgoing Webhook** and choose the channel to watch. Outgoing webhooks only work in public channels; use a [slash command](https://developers.mattermost.com/integrate/slash-commands/) instead for private channels or DMs.
2. Set the trigger word (for example `factory:`) and set **Trigger When** to “first word starts with a trigger word.”
3. Set the callback URL to the endpoint your bot serves, and set the content type to `application/x-www-form-urlencoded`.
4. Save the webhook and copy the generated token into `MATTERMOST_WEBHOOK_TOKEN`.
Mattermost POSTs form-encoded fields for the triggering message: `token`, `channel_id`, `post_id`, `user_name`, `text`, `trigger_word`, and a few others. Your bot must reject any request whose `token` doesn’t match, before reading anything else from it - otherwise anyone who finds the URL can dispatch factory runs using your bot’s credentials:
```python
import hmac
import os
from flask import Flask, request
from oz_agent_sdk import OzAPI
app = Flask(__name__)
client = OzAPI(api_key=os.environ["WARP_API_KEY"])
WEBHOOK_TOKEN = os.environ["MATTERMOST_WEBHOOK_TOKEN"]
@app.route("/mattermost/dispatch", methods=["POST"])
def handle_message():
if not hmac.compare_digest(request.form.get("token", ""), WEBHOOK_TOKEN):
return "", 403
# Step 5 fills in the rest of this handler.
return "", 200
```
## 3. Find the target factory
[Section titled “3. Find the target factory”](#3-find-the-target-factory)
Search for the factory by name instead of hardcoding its UID, so the bot keeps working if the factory is ever recreated:
```python
def find_factory(name: str):
page = client.factories.list(search=name)
if not page.factories:
raise ValueError(f"No factory found matching '{name}'")
return page.factories[0]
```
If your bot only ever talks to one factory, look it up once at startup and cache the UID instead of searching on every message.
## 4. Read the triggering post’s thread
[Section titled “4. Read the triggering post’s thread”](#4-read-the-triggering-posts-thread)
The webhook payload tells you which post triggered it, but not whether that post is a reply. Fetch the post from the Mattermost API to read its `root_id`: empty for a new top-level message, or the ID of the thread’s first post for a reply.
```python
import requests
def get_post(post_id: str) -> dict:
resp = requests.get(
f"{os.environ['MATTERMOST_URL']}/api/v4/posts/{post_id}",
headers={"Authorization": f"Bearer {os.environ['MATTERMOST_BOT_TOKEN']}"},
)
resp.raise_for_status()
return resp.json()
```
## 5. Dispatch new work or continue an existing run
[Section titled “5. Dispatch new work or continue an existing run”](#5-dispatch-new-work-or-continue-an-existing-run)
Keep a lookup of thread root post ID to `run_id`. A message with a known root continues that run with a follow-up; anything else dispatches a new one, keyed by its own post ID so later replies in the same thread find it:
```python
run_ids_by_thread: dict[str, str] = {}
def dispatch_task(text: str, post_id: str, permalink: str):
factory = find_factory("payments") # or a UID you already have
return client.factories.runs.create(
factory.uid,
prompt=text,
ticket_ref=f"mattermost:{post_id}",
ticket_url=permalink,
)
def send_followup(run_id: str, text: str):
client.agent.runs.submit_followup(run_id, message=text)
def post_reply(channel_id: str, root_id: str, message: str):
requests.post(
f"{os.environ['MATTERMOST_URL']}/api/v4/posts",
headers={"Authorization": f"Bearer {os.environ['MATTERMOST_BOT_TOKEN']}"},
json={"channel_id": channel_id, "root_id": root_id, "message": message},
)
```
Combine these functions into the handler from step 2:
```python
@app.route("/mattermost/dispatch", methods=["POST"])
def handle_message():
if not hmac.compare_digest(request.form.get("token", ""), WEBHOOK_TOKEN):
return "", 403
post_id = request.form["post_id"]
channel_id = request.form["channel_id"]
text = request.form["text"]
post = get_post(post_id)
root_id = post["root_id"] or post_id
existing_run_id = run_ids_by_thread.get(root_id)
if existing_run_id:
send_followup(existing_run_id, text)
else:
permalink = f"{os.environ['MATTERMOST_URL']}/_redirect/pl/{post_id}"
run = dispatch_task(text, post_id, permalink)
run_ids_by_thread[root_id] = run.run_id
post_reply(channel_id, post_id, f"Started work on this: {run.run_url}")
return "", 200
```
Use a real database for `run_ids_by_thread` once you move past local testing; an in-memory dictionary loses every mapping when the process restarts.
Post a message starting with your trigger word in the watched channel; the bot replies in the same thread with a link to the new run, which appears on the factory’s [Runs page](/factories/factory-dashboard/#inspect-runs). Reply with the trigger word again, and the bot sends a follow-up instead of starting a new run.
## 6. Post completion updates
[Section titled “6. Post completion updates”](#6-post-completion-updates)
Poll the run’s state and post a final update to the thread once it leaves an in-progress state:
```python
def check_and_report(root_id: str, channel_id: str):
run_id = run_ids_by_thread[root_id]
status = client.agent.runs.retrieve(run_id)
if status.state in ("SUCCEEDED", "FAILED", "ERROR", "CANCELLED"):
post_reply(channel_id, root_id, f"Run {status.state.lower()}: {status.session_link}")
```
Call `check_and_report` from a scheduled job (a cron-triggered script, or a lightweight background worker) rather than blocking the webhook handler, since a run can take much longer than an HTTP request should wait.
## Next steps
[Section titled “Next steps”](#next-steps)
You’ve built a Mattermost bot that discovers a factory by name, dispatches tasks with source context attached, and routes replies to the run that’s already in progress. From here:
* [Use factory endpoints](/factories/factory-api/) - The full discover-and-dispatch reference this guide builds on.
* [Connect your factory](/factories/connect-your-factory/) - Compare this custom integration against Warp’s built-in intake sources.
* [Warp Platform API](/factories/api-and-sdk/) - Full endpoint reference for run status, follow-ups, and cancellation.
# Context7 MCP: update Astro project with best practices
Canonical page: [/guides/external-tools/context7-mcp-update-astro-project-with-best-practices/](https://docs.warp.dev/guides/external-tools/context7-mcp-update-astro-project-with-best-practices/)
> Use the Context7 MCP server to give Warp agents real-time access to framework documentation for automated project upgrades.
Note
This tutorial shows how the **Context7 MCP Server** gives Warp agents real‑time access to documentation for upgrading frameworks and codebases automatically.

***
## 🧠 Overview
[Section titled “🧠 Overview”](#-overview)
The **Context7 MCP Server** lets Warp fetch live documentation from across the web.\
\
In the example, the agent updates an older **Astro** project to align with the latest version (Astro 5).
***
1. #### Add the Context7 server
[Section titled “Add the Context7 server”](#add-the-context7-server)
* Open Warp’s **MCP Panel** via the Command Palette.
* Add the **Context7 JSON config** and click **Save**.
```json
{
"Context7": {
"command": "npx",
"args": [
"-y",
"@upstash/context7-mcp"
],
"env": {},
"working_directory": null
}
}
```
* This enables the endpoint `getLibraryDocs`, which retrieves live documentation directly from the official sources.
2. #### Run the update prompt
[Section titled “Run the update prompt”](#run-the-update-prompt)
The developer issues this prompt:
```plaintext
Create a new git branch called update and in that branch update this Astro project to follow all the latest best practices based on all Astro and developer documentation.
```
3. #### Review the automatic code changes
[Section titled “Review the automatic code changes”](#review-the-automatic-code-changes)
The transcript shows that Warp automatically:
* Updates Tailwind import syntax
* Improves TypeScript configuration
* Optimizes build settings
* Enhances accessibility rules
These edits happen across multiple files — without manually searching docs or changelogs.
4. #### Best use cases
[Section titled “Best use cases”](#best-use-cases)
* Migrating old Astro, React, or Vue projects
* Refreshing codebases to reflect recent standards
* Saving time otherwise spent reading version notes
Tip
Context7 MCP automates documentation lookups — letting Warp update your project intelligently based on live references.
# Figma remote MCP: create a website from a Figma file
Canonical page: [/guides/external-tools/figma-remote-mcp-create-a-website-from-a-figma-file-from-scratch/](https://docs.warp.dev/guides/external-tools/figma-remote-mcp-create-a-website-from-a-figma-file-from-scratch/)
> Connect Warp to Figma's remote MCP server via OAuth and generate front-end code directly from your design files.
Learn how to connect Warp to Figma’s remote MCP server to generate code directly from your design files — complete with screenshots, metadata, and design system context.

***
## Overview
[Section titled “Overview”](#overview)
This guide covers how to:
* Connect Warp to the **remote Figma MCP server**
* Log in securely using OAuth
* Use the server to pull live context (components, variables, and assets) from your Figma designs
* Generate front-end code based on your UI files
* Iterate and refine output directly in Warp
***
1. #### What is a remote MCP server?
[Section titled “What is a remote MCP server?”](#what-is-a-remote-mcp-server)
A **remote MCP server** runs outside your local machine — Warp connects to it through a secure network call.\
\
This means you don’t have to manage processes, ports, or tokens manually. Warp handles setup, authentication, and communication for you.
2. #### Connect Figma MCP to Warp
[Section titled “Connect Figma MCP to Warp”](#connect-figma-mcp-to-warp)
* Copy the Figma MCP configuration JSON
```plaintext
{
"Figma": {
"url": "https://mcp.figma.com/mcp"
}
}
```
* In Warp, paste the JSON — Warp will automatically open an OAuth login window.
* Log in once with your **Figma account** credentials.
Note
You will need a Figma Dev account for this to work.
3. #### What the Figma MCP server provides
[Section titled “What the Figma MCP server provides”](#what-the-figma-mcp-server-provides)
Once connected, the server enables Warp’s AI to understand your design context by fetching:
| Type | Description |
| -------------------------------- | -------------------------------------------------------------------- |
| **`get_screenshot`** | Helps the AI visualize layout and relationships between elements. |
| **`create_design_system_rules`** | Components, variables, and styles for consistent, reusable code. |
| **`get_code`** | Extracts code from your Figma design for direct use in projects. |
| **`get_metadata`** | Includes text, images, and layer names for more realistic mock data. |
4. #### Generate a website from a Figma file
[Section titled “Generate a website from a Figma file”](#generate-a-website-from-a-figma-file)
Basic flow:
* Copy your **Figma file link**:
* Right-click → *Copy / Paste As → Copy Link to Selection*
* In Warp, paste a prompt to create a website based on that design.
Prompt:
```plaintext
Create a website from this Figma file: <LINK HERE>
Follow the design layout and use these guidelines:
- Match spacing and typography from the design
- Use Tailwind CSS and TypeScript
- Make components reusable
```
Warp uses the Figma MCP server to pull all necessary context and begin generating code diffs.
5. #### Iterating on output
[Section titled “Iterating on output”](#iterating-on-output)
* In under five minutes, Warp generates a working site structure based on the Figma layout.
* Missing assets (e.g., logos or images) are automatically referenced in an `assets/` folder.
* Warp prompts you to add any missing files before continuing.
6. #### Persistent input feature
[Section titled “Persistent input feature”](#persistent-input-feature)
Warp’s **persistent input** allows mid-process updates.\
If you forget an image (e.g., the Misho logo), simply upload it and notify Warp:
```plaintext
I’ve uploaded the Misho logo to the assets folder.
```
Warp will automatically detect and use it during the same generation session.
7. #### Recap
[Section titled “Recap”](#recap)
* Warp now supports **remote MCP servers** for Figma (and others like GitHub, Sentry, and Linear).
* OAuth login streamlines setup and removes manual token handling.
* The Figma MCP integration enables rapid, context-aware code generation.
* Persistent input and real-time iteration make design-to-code workflows seamless.
Tip
In under 20 minutes, you can go from Figma design to a functioning website — all powered by Warp’s AI coding environment.
# GitHub MCP: summarize open PRs and create GitHub issues
Canonical page: [/guides/external-tools/github-mcp-summarizing-open-prs-and-creating-gh-issues/](https://docs.warp.dev/guides/external-tools/github-mcp-summarizing-open-prs-and-creating-gh-issues/)
> Connect the GitHub MCP server to Warp to summarize open PRs, create issues from TODO comments, and automate repo management.

The GitHub MCP Server lets Warp agents read, write, and automate tasks in your GitHub repositories directly — no manual tab-switching required.
***
### 2. Setup
[Section titled “2. Setup”](#2-setup)
#### Step 1. Get a GitHub personal access token
[Section titled “Step 1. Get a GitHub personal access token”](#step-1-get-a-github-personal-access-token)
1. Go to **GitHub** > **Settings** > **Developer Settings** > **Personal Access Tokens**
2. Create a new token and enable:
* ✅ `repo`
* ✅ `read:user`
***
#### Step 2. Add the server in Warp
[Section titled “Step 2. Add the server in Warp”](#step-2-add-the-server-in-warp)
1. Open the **MCP Panel** via Command Palette (`Cmd+P`)
2. Click **Add Server**
3. Paste in your JSON config and the access token
4. Save — and you’ll see the available endpoints immediately
***
### Step 3. Workflow 1 — summarize all open PRs
[Section titled “Step 3. Workflow 1 — summarize all open PRs”](#step-3-workflow-1--summarize-all-open-prs)
Use Warp’s agent to summarize pull requests:
Behind the scenes, the MCP server:
* Lists PRs
* Fetches comments and reviews
* Compiles summaries with clickable links
Perfect for daily PR triage or stand-ups.
***
### Step 4. Workflow 2 — create GitHub issues from TODOs
[Section titled “Step 4. Workflow 2 — create GitHub issues from TODOs”](#step-4-workflow-2--create-github-issues-from-todos)
Use a saved prompt to automate issue creation.
Warp:
1. Scans your codebase for TODO comments
2. Calls `create_issue` for each one via MCP
3. Generates a linked list of new issues
This turns scattered notes into trackable tickets instantly.
***
### Why it’s useful
[Section titled “Why it’s useful”](#why-its-useful)
* Save 20–30 minutes per session
* Keep repos synchronized automatically
* Enable PR summaries, issue tracking, and automation — all inside Warp.
# Set up Claude Code
Canonical page: [/guides/external-tools/how-to-set-up-claude-code/](https://docs.warp.dev/guides/external-tools/how-to-set-up-claude-code/)
> Set up Claude Code in Warp, configure it for your project, and learn productivity tips — from voice prompting to visual code review.
Claude Code is Anthropic’s AI coding agent. It reads your codebase, writes and edits code, runs commands, and handles complex refactors using natural language prompts. This guide takes you from zero to a working Claude Code session in Warp in about 5 minutes, then shows you how to get the most out of it.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **A Claude account with CLI access** — Claude Code requires a paid plan or API credits. See [Claude Code requirements](https://docs.anthropic.com/en/docs/claude-code/setup) for eligible plans.
* **macOS 13+, Windows 10+, or Ubuntu 20.04+** — See [Claude Code system requirements](https://docs.anthropic.com/en/docs/claude-code/setup) for full platform details.
* **Git** — Claude Code works best inside a Git repository. On Windows, [Git for Windows](https://git-scm.com) is required.
## 1. Install Claude Code
[Section titled “1. Install Claude Code”](#1-install-claude-code)
Follow Anthropic’s [official installation guide](https://docs.anthropic.com/en/docs/claude-code/quickstart) to install Claude Code. The native installer (recommended) requires no dependencies and auto-updates in the background.
When you launch Claude Code inside Warp, Warp auto-detects the agent session and surfaces integrated controls, including rich input, code review, vertical tab metadata, and more.
## 2. Authenticate
[Section titled “2. Authenticate”](#2-authenticate)
The first time you run Claude Code, it opens your browser for login.
```bash
claude
```
Sign in with your Claude account. Once authenticated, the token is stored locally and you won’t need to log in again.
For headless environments or CI/CD, set an API key instead:
```bash
export ANTHROPIC_API_KEY=YOUR_API_KEY
```
## 3. Start your first session
[Section titled “3. Start your first session”](#3-start-your-first-session)
Navigate to any project directory and launch Claude Code:
```bash
cd ~/your-project
claude
```
Try giving it a task, for example:
```plaintext
Explain the architecture of this project
```
Or something more hands-on:
```plaintext
Add input validation to the user registration endpoint
```
Claude Code will find the relevant files, show you the proposed changes, and ask for confirmation before modifying anything.
## 4. Configure for your project
[Section titled “4. Configure for your project”](#4-configure-for-your-project)
Create a `CLAUDE.md` file at your project root to teach Claude Code your project’s conventions. Claude Code reads this file at the start of every session.
```markdown
# My Project
## Stack
- Backend: Python 3.12, FastAPI, SQLAlchemy
- Frontend: React, TypeScript, Vite
- Database: PostgreSQL 16
## Commands
- `npm run dev` starts the dev server
- `pytest -v` runs the test suite
- `npm run lint` checks code style
## Conventions
- Use async/await for all database operations
- Type hints on all function signatures
- ESM imports only (no require())
```
This prevents Claude Code from guessing your conventions and ensures it follows your team’s standards from the first prompt.
## 5. Choose a model and permissions
[Section titled “5. Choose a model and permissions”](#5-choose-a-model-and-permissions)
Claude Code uses the latest Claude model by default. To use a specific model:
```bash
claude --model MODEL_NAME
```
By default, Claude Code asks for permission before every file write and command execution. You can pre-approve safe operations in `.claude/settings.json`:
```json
{
"permissions": {
"allow": [
"Read",
"Glob",
"Grep",
"Bash(pytest*)",
"Bash(npm run lint)"
]
}
}
```
This lets Claude read files and run your test/lint commands without prompting, while still asking before writing files.
## 6. Set up agent notifications
[Section titled “6. Set up agent notifications”](#6-set-up-agent-notifications)
Warp supports agent notifications for Claude Code through a plugin. When you run Claude Code in Warp without the plugin installed, a notification chip appears offering one-click installation. Once installed, Warp surfaces in-app and desktop alerts when Claude Code needs your input.
For manual installation steps, troubleshooting, and SSH/remote setup, see [Claude Code in Warp (docs)](/agents/cli-agents/claude-code/#setting-up-notifications).
## Productivity tips
[Section titled “Productivity tips”](#productivity-tips)
* **Use voice to prompt Claude Code** — Instead of typing complex instructions, dictate them. Warp supports [voice transcription](/agents/local-agents/interacting-with-agents/voice/) that works with any CLI agent, including Claude Code. Press the microphone icon or the `fn` key to start recording.
* **Attach images as context** — Paste screenshots of bug reports, design mockups, or error messages directly into your prompt. Warp’s [images as context](/agents/local-agents/agent-context/images-as-context/) feature lets Claude Code see what you see.
* **Review diffs visually** — After Claude Code makes changes, open Warp’s [Code Review panel](/code/code-review/) (`⌘+Shift++`) to see a visual diff of every file changed. You can leave inline comments and send them back to Claude Code for corrections.
* **Run multiple Claude Code sessions in parallel** — Use [vertical tabs](/terminal/windows/vertical-tabs/) to run different Claude Code tasks side by side, one session fixing bugs while another writes tests. Each tab shows which agent is running and its current status.
* **Compose richer prompts** — Press `Ctrl+G` to open Warp’s rich input editor for Claude Code. This gives you a full text editor experience for composing prompts — click to position your cursor, select text, and edit naturally instead of navigating with arrow keys.
## Next steps
[Section titled “Next steps”](#next-steps)
You installed Claude Code, authenticated, started your first session, configured it for your project, and learned the key productivity features that make it faster to use in Warp.
Explore related guides and features:
* [Set up Codex CLI](/guides/external-tools/how-to-set-up-codex-cli/) to run a second agent alongside Claude Code
* [How to review AI-generated code](/guides/agent-workflows/how-to-review-ai-generated-code/) — a structured workflow for reviewing and refining agent output
* [Run multiple agents at once](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/) — use Claude Code and Codex side by side
* [Claude Code documentation](https://docs.anthropic.com/en/docs/claude-code/quickstart) — Anthropic’s official reference
* [Claude Code in Warp](https://www.warp.dev/agents/claude-code) — overview of Claude Code support in Warp
* [Claude Code in Warp (docs)](/agents/cli-agents/claude-code/) — full reference for Claude Code’s Warp integration, including notification setup
* [Third-party CLI agents](/agents/cli-agents/overview/) — all supported agents and Warp’s universal agent features
# Set up Codex CLI
Canonical page: [/guides/external-tools/how-to-set-up-codex-cli/](https://docs.warp.dev/guides/external-tools/how-to-set-up-codex-cli/)
> Set up OpenAI's Codex CLI in Warp, configure it for your project, and learn productivity tips for faster AI-assisted coding workflows in Warp.
Codex CLI is OpenAI’s open-source coding agent. It reads your codebase, edits files, and executes commands from natural language prompts. This guide takes you from installation to a working Codex session in Warp in about 5 minutes, then shows you how to get the most out of it.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **A ChatGPT account with Codex access** — Included with paid ChatGPT plans, or use an OpenAI API key. See [Codex CLI documentation](https://developers.openai.com/codex/cli/) for eligible plans.
* **Node.js 18+** (for npm install) or **Homebrew** (for macOS) — Choose your preferred package manager.
* **macOS or Linux** — Windows support is experimental; for the best Windows experience, use Codex in a WSL workspace.
## 1. Install Codex CLI
[Section titled “1. Install Codex CLI”](#1-install-codex-cli)
Install Codex CLI globally with npm or Homebrew:
**npm:**
```bash
npm install -g @openai/codex
```
**Homebrew (macOS):**
```bash
brew install codex
```
Verify installation:
```bash
codex --version
```
You can also download platform-specific binaries directly from the [GitHub releases](https://github.com/openai/codex/releases).
## 2. Authenticate
[Section titled “2. Authenticate”](#2-authenticate)
Run Codex for the first time:
```bash
codex
```
Select **Sign in with ChatGPT** and authenticate with your ChatGPT account (recommended). Your Codex usage is included in your ChatGPT plan.
For API key authentication (useful for CI/CD or automation):
```bash
export OPENAI_API_KEY=YOUR_API_KEY
```
## 3. Start your first session
[Section titled “3. Start your first session”](#3-start-your-first-session)
Navigate to a project directory and launch Codex:
```bash
cd ~/your-project
codex
```
Codex starts an interactive terminal session. Try giving it a task, for example:
```plaintext
Explain the structure of this project
```
Or something more hands-on:
```plaintext
Add error handling to the database connection module
```
Codex will read the relevant files, propose changes, and ask for your confirmation before modifying anything. You can review changes in a diff view and accept or reject each one.
## 4. Configure model and approval mode
[Section titled “4. Configure model and approval mode”](#4-configure-model-and-approval-mode)
Switch between available models during a session with the `/model` command. See [Codex CLI documentation](https://developers.openai.com/codex/cli/) for the current model list.
Codex has three [approval modes](https://developers.openai.com/codex/cli/features#approval-modes) that control how much autonomy it has.
* **Auto** (the default) lets Codex read, edit, and run commands within your working directory but asks before anything outside that scope.
* **Read-only** keeps Codex consultative.
* **Full Access** grants broader autonomy including network access.
Use `/permissions` inside a session to switch modes as your comfort level changes.
## 5. Customize with a configuration file
[Section titled “5. Customize with a configuration file”](#5-customize-with-a-configuration-file)
Create a `codex.md` or `AGENTS.md` file at your project root to teach Codex your project’s conventions:
```markdown
# My Project
## Stack
- Backend: Node.js, Express, TypeScript
- Database: PostgreSQL with Prisma ORM
- Testing: Vitest for unit tests, Playwright for e2e
## Conventions
- Use ESM imports (no require())
- All API endpoints need Zod input validation
- Run `npm test` before committing
```
Codex reads this file at the start of every session and follows your conventions automatically.
Note
Warp supports agent notifications for Codex. Add `notification_condition = "always"` under `[tui]` in `~/.codex/config.toml` and restart Codex. See [Codex in Warp (docs)](/agents/cli-agents/codex/#setting-up-notifications) for details. If the config isn’t set, Warp displays a setup chip in the terminal.
## Productivity tips
[Section titled “Productivity tips”](#productivity-tips)
* **Use voice to prompt Codex** — Dictate complex instructions instead of typing them. Warp supports [voice transcription](/agents/local-agents/interacting-with-agents/voice/) that works with any CLI agent, including Codex.
* **Attach images as context** — Paste screenshots of bugs, designs, or error messages into your prompt. Warp’s [images as context](/agents/local-agents/agent-context/images-as-context/) feature lets Codex see what you see.
* **Review diffs visually** — After Codex makes changes, open Warp’s [Code Review panel](/code/code-review/) (`⌘+Shift++`) to see a visual diff. You can leave inline comments and send them back to Codex for corrections.
* **Run Codex alongside Claude Code** — Use [vertical tabs](/terminal/windows/vertical-tabs/) to run Claude Code and Codex side by side on the same task. Compare their approaches and pick the best output, or combine elements from both.
* **Compose richer prompts** — Press `Ctrl+G` to open Warp’s rich input editor for Codex, giving you a full text editor experience instead of raw CLI input.
## Next steps
[Section titled “Next steps”](#next-steps)
You installed Codex CLI, authenticated, started your first session, and configured it for your project. Codex is now set up as a working AI coding agent in Warp.
Explore related guides and features:
* [Set up Claude Code](/guides/external-tools/how-to-set-up-claude-code/) to run a second agent alongside Codex
* [How to review AI-generated code](/guides/agent-workflows/how-to-review-ai-generated-code/) — a structured workflow for reviewing agent output
* [Run multiple agents at once](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/) — use Codex and Claude Code side by side
* [Codex CLI documentation](https://developers.openai.com/codex/cli/) — OpenAI’s official reference
* [Codex in Warp](https://www.warp.dev/agents/codex) — overview of Codex support in Warp
* [Codex in Warp (docs)](/agents/cli-agents/codex/) — full reference for Codex’s Warp integration, including notification setup
* [Third-party CLI agents](/agents/cli-agents/overview/) — all supported agents and Warp’s universal agent features
# Set up Gemini CLI
Canonical page: [/guides/external-tools/how-to-set-up-gemini-cli/](https://docs.warp.dev/guides/external-tools/how-to-set-up-gemini-cli/)
> Set up Google's Gemini CLI in Warp, configure it for your project, and learn productivity tips for faster AI-assisted coding workflows.
Gemini CLI is Google’s open-source coding agent. It brings Gemini directly into your terminal with built-in tools for file operations, shell commands, web search, and MCP support. This guide takes you from installation to a working Gemini CLI session in Warp in about 5 minutes, then shows you how to get the most out of it.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **A Google account** — Gemini CLI’s free tier includes 60 requests per minute and 1,000 requests per day with a personal Google account. Alternatively, use a Gemini API key or Vertex AI. See the [Gemini CLI authentication guide](https://geminicli.com/docs/get-started/authentication/) for all options.
* **Node.js 20+** — Required for installation. Check with `node -v`.
* **macOS, Linux, or Windows** — See [Gemini CLI system requirements](https://geminicli.com/docs/get-started/installation/) for recommended specifications.
## 1. Install Gemini CLI
[Section titled “1. Install Gemini CLI”](#1-install-gemini-cli)
Follow Google’s [official installation guide](https://geminicli.com/docs/get-started/installation/) to install Gemini CLI. The two most common methods:
**npm:**
```bash
npm install -g @google/gemini-cli
```
**Homebrew (macOS/Linux):**
```bash
brew install gemini-cli
```
Verify installation:
```bash
gemini --version
```
You can also run without installing using `npx @google/gemini-cli`.
When you launch Gemini CLI inside Warp, Warp auto-detects the agent session and surfaces integrated controls, including rich input, code review, vertical tab metadata, and more.
## 2. Authenticate
[Section titled “2. Authenticate”](#2-authenticate)
The first time you run Gemini CLI, it prompts you to choose an authentication method.
```bash
gemini
```
Select **Sign in with Google** and complete the browser authentication flow. Once authenticated, the token is stored locally and you won’t need to sign in again.
For API key authentication (useful for CI/CD or higher rate limits):
```bash
export GEMINI_API_KEY=YOUR_API_KEY
```
For enterprise environments using Vertex AI, the recommended approach is Application Default Credentials (ADC):
```bash
export GOOGLE_CLOUD_PROJECT=YOUR_PROJECT_ID
export GOOGLE_CLOUD_LOCATION=YOUR_LOCATION
export GOOGLE_GENAI_USE_VERTEXAI=true
gcloud auth application-default login
```
See the [Gemini CLI authentication guide](https://geminicli.com/docs/get-started/authentication/) for all Vertex AI auth methods.
## 3. Start your first session
[Section titled “3. Start your first session”](#3-start-your-first-session)
Navigate to any project directory and launch Gemini CLI:
```bash
cd ~/your-project
gemini
```
Try giving it a task, for example:
```plaintext
Explain the architecture of this project
```
Or something more hands-on:
```plaintext
Add error handling to the database connection module
```
Gemini CLI reads the relevant files, proposes changes, and asks for confirmation before modifying anything.
## 4. Configure for your project
[Section titled “4. Configure for your project”](#4-configure-for-your-project)
Create a `GEMINI.md` file at your project root to teach Gemini CLI your project’s conventions. Gemini CLI reads this file at the start of every session.
```markdown
# My Project
## Stack
- Backend: Node.js, Express, TypeScript
- Database: PostgreSQL with Prisma ORM
- Testing: Vitest for unit tests, Playwright for e2e
## Commands
- `npm run dev` starts the dev server
- `npm test` runs the test suite
- `npm run lint` checks code style
## Conventions
- Use ESM imports (no require())
- All API endpoints need Zod input validation
- Run `npm test` before committing
```
This prevents Gemini CLI from guessing your conventions and ensures it follows your team’s standards from the first prompt.
## 5. Choose a model
[Section titled “5. Choose a model”](#5-choose-a-model)
Gemini CLI defaults to the latest Gemini model. To use a specific model:
```bash
gemini -m MODEL_NAME
```
You can also switch models during a session with the `/model` command. See the [Gemini CLI documentation](https://github.com/google-gemini/gemini-cli) for the current model list.
Note
Gemini CLI does not currently support agent notifications in Warp. You won’t receive desktop alerts when Gemini CLI needs input, so keep the tab visible or check back periodically during longer tasks. All other Warp agent features (rich input, code review, vertical tabs) work fully.
## Productivity tips
[Section titled “Productivity tips”](#productivity-tips)
* **Use voice to prompt Gemini CLI** — Dictate complex instructions instead of typing them. Warp supports [voice transcription](/agents/local-agents/interacting-with-agents/voice/) that works with any CLI agent, including Gemini CLI.
* **Attach images as context** — Paste screenshots of bugs, designs, or error messages into your prompt. Warp’s [images as context](/agents/local-agents/agent-context/images-as-context/) feature lets Gemini CLI see what you see.
* **Review diffs visually** — After Gemini CLI makes changes, open Warp’s [Code Review panel](/code/code-review/) (`⌘+Shift++`) to see a visual diff. You can leave inline comments and send them back to Gemini CLI for corrections.
* **Run Gemini CLI alongside other agents** — Use [vertical tabs](/terminal/windows/vertical-tabs/) to run Gemini CLI and Claude Code or Codex side by side on the same task. Compare their approaches and pick the best output.
* **Compose richer prompts** — Press `Ctrl+G` to open Warp’s rich input editor for Gemini CLI, giving you a full text editor experience instead of raw CLI input.
* **Use built-in Google Search** — Gemini CLI can ground responses with real-time web search. Ask it to research current best practices or look up documentation while working on your code.
## Next steps
[Section titled “Next steps”](#next-steps)
You installed Gemini CLI, authenticated with your Google account, started your first session, and configured it for your project. Gemini CLI is now set up as a working coding agent in Warp.
Explore related guides and features:
* [Set up Ollama for local models](/guides/external-tools/how-to-set-up-ollama/) to pair Gemini CLI with local model workflows
* [Code Review panel](/code/code-review/) — review and refine agent-generated code
* [Gemini CLI in Warp](https://www.warp.dev/agents/gemini-cli) — overview of Gemini CLI support in Warp
* [Third-party CLI agents](/agents/cli-agents/overview/) — all supported agents and Warp’s universal agent features
* [Gemini CLI documentation](https://github.com/google-gemini/gemini-cli) — Google’s official reference
# Set up Ollama
Canonical page: [/guides/external-tools/how-to-set-up-ollama/](https://docs.warp.dev/guides/external-tools/how-to-set-up-ollama/)
> Install Ollama, run LLMs locally, compare model performance, and integrate local models into your apps using Warp.
Run AI models locally — with no API costs, no data leaving your machine, and your choice of model. This guide walks through installing Ollama, running your first model, integrating it into an existing app, and customizing model behavior using Warp.

## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
**Hardware requirements**
You’ll need enough memory to load the model weights. As a general estimate, plan on roughly 1GB of memory per billion parameters.
| Model size | Example models | Minimum RAM/VRAM |
| ---------- | -------------------------------------- | ---------------- |
| 3B | Llama 3.2 3B, Phi-3 Mini (3.8B) | 4GB |
| 7–8B | Mistral 7B, Llama 3.1 8B | 8GB |
| 13B | Llama 2 13B | 16GB |
| 22–34B | Codestral (22B), Mixtral (46.7B total) | 24GB |
| 70B | Llama 3.1 70B | 48GB |
On Apple Silicon Macs, unified memory is shared between CPU and GPU. An M2 Mac with 16GB unified memory can run 7–8B models comfortably.
**Software requirements**
* macOS 14 Sonoma+, Windows 10+, or Ubuntu 20.04+
* No account required — Ollama is free and open source
## 1. Install Ollama
[Section titled “1. Install Ollama”](#1-install-ollama)
**macOS**
Run the install script in your terminal:
```bash
curl -fsSL https://ollama.com/install.sh | sh
```
Or download the macOS app manually from [ollama.com/download](https://ollama.com/download/Ollama.dmg). The app runs as a background service and appears in your menu bar.
**Linux**
```bash
curl -fsSL https://ollama.com/install.sh | sh
```
On systemd-based Linux distributions, the installer typically registers Ollama as a service. To start it and enable it on boot, run:
```bash
sudo systemctl enable ollama
sudo systemctl start ollama
```
**Windows**
Run this in PowerShell:
```powershell
irm https://ollama.com/install.ps1 | iex
```
Or download the installer manually from [ollama.com/download](https://ollama.com/download). Ollama runs as a background service after installation.
## 2. Run your first model
[Section titled “2. Run your first model”](#2-run-your-first-model)
Pull a model to download it locally. This example uses Llama 3.2 (3B), a lightweight model that runs on most hardware:
```bash
ollama pull llama3.2
```
Then start an interactive chat session:
```bash
ollama run llama3.2
```
Type your prompt and press `Enter`. Type `/bye` to exit the session.
To try a larger model with stronger reasoning:
```bash
ollama run llama3.1:8b
```
Use `ollama ls` to see all models you’ve downloaded, and `ollama ps` to see which models are currently loaded in memory.
## 3. Understand model types
[Section titled “3. Understand model types”](#3-understand-model-types)
When browsing [ollama.com/library](https://ollama.com/library), you’ll see labels on models that indicate their capabilities:
| Label | Meaning |
| ------------- | ----------------------------------------------------------------------------- |
| **thinking** | The model reasons step-by-step before answering; better for complex problems. |
| **tools** | The model can call external functions or utilities (e.g., web search). |
| **vision** | The model can process and respond to images. |
| **embedding** | Converts text to numeric vectors for search or RAG pipelines. |
Quantized models (e.g., `q4_0`, `q8_0` variants) use significantly less memory than full-precision originals. Start with a quantized version if you’re memory-constrained.
## 4. Compare model performance
[Section titled “4. Compare model performance”](#4-compare-model-performance)
To benchmark models side-by-side, Warp makes it easy to run prompts in parallel tabs and compare results. Pass a prompt and the `--verbose` flag to get timing stats alongside the response:
```bash
ollama run --verbose llama3.2 "Summarize the Rust ownership model in one paragraph"
```
Run the same prompt on two different models to compare output quality and throughput before committing to one.
To see which models are currently loaded and their memory usage:
```bash
ollama ps
```
## 5. Integrate Ollama into your app
[Section titled “5. Integrate Ollama into your app”](#5-integrate-ollama-into-your-app)
Ollama exposes an OpenAI-compatible REST API at `http://localhost:11434/v1/`. You can drop it in wherever you’re currently using the OpenAI API by updating these three values:
1. **Base URL** → `http://localhost:11434/v1/`
2. **API key** → any non-empty string such as `"ollama"` (required by the SDK but ignored by Ollama)
3. **Model name** → the name of your local model (e.g., `"llama3.2"`)
Here are working examples using the OpenAI SDK for Python and Node.js:
**Python (OpenAI SDK)**
```python
from openai import OpenAI
client = OpenAI(
base_url="http://localhost:11434/v1/",
api_key="ollama", # required by the SDK but ignored by Ollama
)
response = client.chat.completions.create(
model="llama3.2",
messages=[
{"role": "user", "content": "Explain async/await in Python"}
]
)
print(response.choices[0].message.content)
```
**Node.js (OpenAI SDK)**
```javascript
import OpenAI from "openai";
const client = new OpenAI({
baseURL: "http://localhost:11434/v1/",
apiKey: "ollama", // required by the SDK but ignored by Ollama
});
const response = await client.chat.completions.create({
model: "llama3.2",
messages: [{ role: "user", content: "Explain async/await in Python" }],
});
console.log(response.choices[0].message.content);
```
Ollama also provides official native libraries if you prefer an SDK built specifically for Ollama rather than the OpenAI compatibility layer: `pip install ollama` for Python and `npm i ollama` for JavaScript. See the [Ollama README](https://github.com/ollama/ollama) for details.
Open your app’s code in Warp. Ask Warp’s agent to locate the OpenAI client initialization, swap in the new values, and test the connection from the same terminal session.
Note
The `http://localhost:11434/v1/` base URL works for code running on the same machine as Ollama. To use Ollama as the inference backend for Warp’s own agent, the endpoint must be reachable at a public URL. Run `ngrok http 11434` and use the resulting HTTPS URL in Warp’s [Custom inference endpoint](/agents/inference/custom-inference-endpoint/) settings.
## 6. Customize model behavior
[Section titled “6. Customize model behavior”](#6-customize-model-behavior)
You can create a custom model variant by writing a `Modelfile`, a configuration file that sets a system prompt, adjusts generation parameters, or builds on any existing Ollama model.
Create a file called `Modelfile`:
```plaintext
FROM llama3.2
SYSTEM """
You are a focused code review assistant.
Always identify security issues first, then logic errors, then style.
Keep feedback concise and actionable.
"""
PARAMETER temperature 0.3
PARAMETER num_ctx 8192
```
Then build and run your custom model:
```bash
ollama create code-reviewer -f ./Modelfile
ollama run code-reviewer
```
Your custom model is saved locally and available any time you run `ollama run code-reviewer`. Ask Warp’s agent to generate a Modelfile for a specific use case — describe what you want the model to do, and let the agent write the configuration.
## Productivity tips
[Section titled “Productivity tips”](#productivity-tips)
* **Unload to free memory** — Use `ollama stop <model>` to unload a model from memory before loading a larger one.
* **Script with the REST API** — For quick testing without the SDK: `curl http://localhost:11434/api/chat -d '{"model": "llama3.2", "messages": [{"role": "user", "content": "Hello"}], "stream": false}'`
* **Keep a model inventory** — `ollama ls` shows all locally cached models with their sizes and download dates. Use `ollama rm <model>` to delete models you no longer need.
* **Compare models in parallel** — Open side-by-side Warp tabs and run the same prompt against two different models to compare quality and speed before deciding which to use in your app.
## Next steps
[Section titled “Next steps”](#next-steps)
Next, explore related guides and features:
* [Custom inference endpoint](/agents/inference/custom-inference-endpoint/) — connect Warp’s agent to your local Ollama instance for a fully local, no-API-cost agent workflow
* [Run multiple agents at once](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/) — run Ollama and a cloud agent in parallel to compare outputs on the same task
* [Ollama model library](https://ollama.com/library) — browse all available models with size and capability details
* [Ollama documentation](https://github.com/ollama/ollama/blob/main/README.md) — advanced configuration, GPU setup, and environment variables
# Set up OpenCode
Canonical page: [/guides/external-tools/how-to-set-up-opencode/](https://docs.warp.dev/guides/external-tools/how-to-set-up-opencode/)
> Set up OpenCode in Warp, configure it for your project, and learn productivity tips for faster AI-assisted coding workflows.
OpenCode is an open-source coding agent that runs in your terminal. It supports 75+ LLM providers, features a built-in terminal UI (TUI), and lets you edit code, execute commands, and manage sessions from natural language prompts. This guide takes you from installation to a working OpenCode session in Warp in about 5 minutes, then shows you how to get the most out of it.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **An LLM provider account** — OpenCode connects to any supported provider (Anthropic, OpenAI, Google, and others) via API key, or use OpenCode Zen for a curated model list. See [OpenCode configuration](https://opencode.ai/docs#configure) for details.
* **macOS, Linux, or Windows (via WSL)** — WSL is recommended for the best experience on Windows. See [OpenCode docs](https://opencode.ai/docs) for full platform details.
## 1. Install OpenCode
[Section titled “1. Install OpenCode”](#1-install-opencode)
Follow the [official OpenCode installation guide](https://opencode.ai/docs#install) to install OpenCode. The install script is the fastest method:
```bash
curl -fsSL https://opencode.ai/install | bash
```
You can also install via npm or Homebrew:
```bash
npm install -g opencode-ai
```
```bash
brew install anomalyco/tap/opencode
```
See the [OpenCode docs](https://opencode.ai/docs#install) for additional installation methods including Homebrew taps, platform-specific binaries, and Docker.
When you launch OpenCode inside Warp, Warp auto-detects the agent session and surfaces integrated controls, including rich input, code review, vertical tab metadata, and more.
## 2. Authenticate
[Section titled “2. Authenticate”](#2-authenticate)
OpenCode supports multiple LLM providers. Run the `/connect` command inside OpenCode’s TUI to configure a provider, or set API keys as environment variables:
```bash
# For Anthropic models
export ANTHROPIC_API_KEY=YOUR_API_KEY
# For OpenAI models
export OPENAI_API_KEY=YOUR_API_KEY
# For Google Gemini models
export GEMINI_API_KEY=YOUR_API_KEY
```
Outside the TUI, run `opencode auth login` from the command line for interactive provider setup. Credentials are stored locally in `~/.local/share/opencode/auth.json`.
## 3. Start your first session
[Section titled “3. Start your first session”](#3-start-your-first-session)
Navigate to any project directory and launch OpenCode:
```bash
cd ~/your-project
opencode
```
OpenCode starts its TUI. Try giving it a task, for example:
```plaintext
Explain the architecture of this project
```
Or something more hands-on:
```plaintext
Add input validation to the user registration endpoint
```
OpenCode reads the relevant files, proposes changes, and asks for confirmation before modifying anything. Use the `Tab` key to switch between Plan mode (read-only suggestions) and Build mode (applies changes).
## 4. Configure for your project
[Section titled “4. Configure for your project”](#4-configure-for-your-project)
Initialize OpenCode for your project by running `/init` inside the TUI. This analyzes your codebase and creates an `AGENTS.md` file at your project root:
```plaintext
/init
```
The `AGENTS.md` file teaches OpenCode your project’s structure and conventions. You can also create or edit it manually:
```markdown
# My Project
## Stack
- Backend: Python 3.12, FastAPI, SQLAlchemy
- Frontend: React, TypeScript, Vite
- Database: PostgreSQL 16
## Commands
- `npm run dev` starts the dev server
- `pytest -v` runs the test suite
- `npm run lint` checks code style
## Conventions
- Use async/await for all database operations
- Type hints on all function signatures
- ESM imports only (no require())
```
Commit the `AGENTS.md` file to Git so your team shares the same project context.
## 5. Set up agent notifications
[Section titled “5. Set up agent notifications”](#5-set-up-agent-notifications)
Warp supports agent notifications for OpenCode through a plugin. If the plugin isn’t installed, Warp displays an installation chip in the terminal when you run OpenCode, with setup steps you can follow directly.
For manual installation and configuration, see [OpenCode in Warp (docs)](/agents/cli-agents/opencode/#setting-up-notifications).
## Productivity tips
[Section titled “Productivity tips”](#productivity-tips)
* **Use voice to prompt OpenCode** — Dictate complex instructions instead of typing them. Warp supports [voice transcription](/agents/local-agents/interacting-with-agents/voice/) that works with any CLI agent, including OpenCode.
* **Attach images as context** — Paste screenshots of bugs, designs, or error messages into your prompt. Warp’s [images as context](/agents/local-agents/agent-context/images-as-context/) feature lets OpenCode see what you see.
* **Review diffs visually** — After OpenCode makes changes, open Warp’s [Code Review panel](/code/code-review/) (`⌘+Shift++`) to see a visual diff. You can leave inline comments and send them back to OpenCode for corrections.
* **Run OpenCode alongside other agents** — Use [vertical tabs](/terminal/windows/vertical-tabs/) to run OpenCode and Claude Code or Codex side by side on the same task. Compare their approaches and pick the best output.
* **Compose richer prompts** — Press `Ctrl+G` to open Warp’s rich input editor for OpenCode, giving you a full text editor experience instead of raw CLI input.
## Next steps
[Section titled “Next steps”](#next-steps)
You installed OpenCode, authenticated with a provider, started your first session, and configured it for your project. OpenCode is now set up as a working coding agent in Warp.
Explore related guides and features:
* [Set up Ollama for local models](/guides/external-tools/how-to-set-up-ollama/) to run OpenCode with local models
* [Code Review panel](/code/code-review/) — review and refine agent-generated code
* [OpenCode in Warp](https://www.warp.dev/agents/opencode) — overview of OpenCode support in Warp
* [OpenCode in Warp (docs)](/agents/cli-agents/opencode/) — full reference for OpenCode’s Warp integration, including notification setup
* [Third-party CLI agents](/agents/cli-agents/overview/) — all supported agents and Warp’s universal agent features
* [OpenCode documentation](https://opencode.ai/docs) — official reference
* [opencode-warp plugin](https://github.com/warpdotdev/opencode-warp) — notification plugin source and updates
# Linear MCP: retrieve issue data
Canonical page: [/guides/external-tools/linear-mcp-retrieve-issue-data/](https://docs.warp.dev/guides/external-tools/linear-mcp-retrieve-issue-data/)
> Add the Linear MCP server to Warp and query your issues, tasks, and assignments directly from the terminal.
Learn how to connect the Linear MCP server in Warp so your agents can access live data — like issues, tickets, and user assignments — directly from your Linear workspace.

***
#### Overview
[Section titled “Overview”](#overview)
This tutorial covers how to:
* Add and configure a Linear MCP server in Warp
* Use MCP to query and retrieve issue data
### 1. Adding the Linear MCP server
[Section titled “1. Adding the Linear MCP server”](#1-adding-the-linear-mcp-server)
#### Add a new server in Warp
[Section titled “Add a new server in Warp”](#add-a-new-server-in-warp)
* In Warp, open **Warp Drive** > **Personal** > **MCP Servers**.\
Alternatively, press `⌘+P` and type **MCP servers** to open the palette.
* Click **Add New Server**.
* Paste in this JSON
```json
{
"linear": {
"command": "npx",
"args": ["-y", "mcp-remote", "https://mcp.linear.app/mcp"],
"env": {},
"working_directory": null
}
}
```
* Click **Save**.
* Warp will immediately start the server.
* You should now see Linear MCP listed as Running.
***
### 2. Testing the connection
[Section titled “2. Testing the connection”](#2-testing-the-connection)
After saving, retry your earlier query:
```plaintext
Show me all Linear tasks assigned to me.
```
Warp’s agent will now call the Linear MCP server to fetch your data. You can click inside the response panel to inspect the **raw API response** — ideal for debugging or understanding what’s being fetched.
If the server can’t find your user, it may be due to your Linear login address. Try querying a teammate to confirm the connection:
```plaintext
Show tasks assigned to [teammate name].
```
Once verified, the agent can display a full list of tasks.
# Linear MCP: update tickets with a lean build approach
Canonical page: [/guides/external-tools/linear-mcp-updating-tickets-with-a-lean-build-approach/](https://docs.warp.dev/guides/external-tools/linear-mcp-updating-tickets-with-a-lean-build-approach/)
> Use Warp's Linear MCP integration to update ticket descriptions, propagate changes to subtasks, and maintain a lean build strategy.
Learn how to use Warp’s Linear MCP integration to update tickets programmatically while maintaining a lean build strategy.

***
## Overview
[Section titled “Overview”](#overview)
This walkthrough demonstrates:
* Updating Linear tickets via Warp’s MCP integration
* Structuring tasks around a lean development stack
* Observing real-time synchronization of ticket data
* Testing agent autonomy when editing related subtasks
1. #### Setting up the scenario
[Section titled “Setting up the scenario”](#setting-up-the-scenario)
The goal is to use Warp’s agent to update a Linear epic with a new, leaner build approach and reflect the changes in related subtasks.
First, open your Linear project and locate the target epic.\
Copy the **ticket ID** (e.g. “Empty Studio 36”).
2. #### Define the update prompt
[Section titled “Define the update prompt”](#define-the-update-prompt)
Within Warp, run the MCP command to edit the Linear issue.
**Prompt**
```plaintext
Use the warp-server-staging gcloud project and pull logs for the last 10 minutes from the warp-server Cloud Run instance.
Organize them by info, warning, and error levels.
Create a histogram across message types, and highlight the most concerning errors to investigate.
```
Warp parses the issue context and updates the ticket’s fields accordingly.
3. #### Observing the changes
[Section titled “Observing the changes”](#observing-the-changes)
After execution:
* The Linear ticket reflects the new **Next.js + Supabase** stack.
* Tasks like *Build Foundation*, *Implement AI-powered PRD Generation*, and *Set up Development Environment* are updated.
* Time estimates automatically adjust from *4–6 weeks* to *2–3 weeks*.
* Complex integrations (AI and Linear App) are deferred to a future phase.
4. #### Propagating updates to child tasks
[Section titled “Propagating updates to child tasks”](#propagating-updates-to-child-tasks)
Warp’s agent can cascade changes to linked subtasks.\
If it begins editing other epics unexpectedly, you can constrain its scope by specifying task IDs in the prompt:
```plaintext
Only update the ticket with ID <ticket_number>.
Do not modify other epics or related tickets.
```
5. #### Review and verification
[Section titled “Review and verification”](#review-and-verification)
Re-open the Linear epic to confirm updates:
* **Frontend specs** reflect the lean stack.
* **Child tasks** align with phase 1 deliverables.
* **Deferred features** (e.g., advanced integrations) are pushed to phase 2.
Note
This demonstrates Warp’s ability to *maintain and modify tickets intelligently*, not just create them.
# Puppeteer MCP: scrape Amazon web reviews
Canonical page: [/guides/external-tools/puppeteer-mcp-scraping-amazon-web-reviews/](https://docs.warp.dev/guides/external-tools/puppeteer-mcp-scraping-amazon-web-reviews/)
> Configure the Puppeteer MCP server in Warp to automate browser tasks like navigating sites, scraping product data, and analyzing reviews.
Note
This tutorial demonstrates how to configure and use the **Puppeteer MCP server** inside Warp to scrape Amazon web reviews.

***
### 🧠 Overview
[Section titled “🧠 Overview”](#-overview)
**Puppeteer MCP** integrates Warp’s agents with the browser, letting you automate tasks such as navigation, form filling, screenshotting, and scraping content.\
\
Once configured, Warp can issue Puppeteer commands directly from prompts, enabling full **browser automation** without manual scripting.
You’ll learn how to:
* Set up the Puppeteer MCP server.
* Use Warp’s voice input and AI to describe automation tasks.
* Execute browser workflows hands-free.
* Capture, scrape, and analyze web data programmatically.
***
1. #### Configure the Puppeteer MCP server
[Section titled “Configure the Puppeteer MCP server”](#configure-the-puppeteer-mcp-server)
Open the MCP panel in Warp:
* Press `Cmd+Shift+P` (macOS) or `Ctrl+Shift+P` (Windows/Linux) to open the **Command Palette**.
* Search for `MCP` and open the **MCP Panel**.
Add the Puppeteer MCP config:
* Click **Add**, then paste in the provided JSON configuration for Puppeteer:
```json
{
"puppeteer": {
"command": "npx",
"args": [
"-y",
"@modelcontextprotocol/server-puppeteer"
],
"env": {},
"working_directory": null
}
}
```
Save your configuration. Available endpoints will include:
* `puppeteer.navigate`
* `puppeteer.fill`
* `puppeteer.screenshot`
* `puppeteer.evaluate`
These represent actions Warp can call automatically through its agents.
2. #### Use voice input to trigger automation
[Section titled “Use voice input to trigger automation”](#use-voice-input-to-trigger-automation)
Enable **voice input** by clicking the microphone icon in Warp. Then speak your automation prompt naturally.
```plaintext
Can you go to Amazon search for "white t-shirt women?"
Scrape the results so the titles, prices, and links are extracted.
Then open each product link and summarize the product reviews.
Finally, give me a recommendation for which shirt to buy based on the combination of the pricing and review quality.
```
#### Watch Puppeteer automate the workflow
[Section titled “Watch Puppeteer automate the workflow”](#watch-puppeteer-automate-the-workflow)
Behind the scenes, Puppeteer:
* Navigates to Amazon.
* Fills the search bar with “white t-shirt woman.”
* Scrapes the product results — capturing titles, prices, and product links.
* Clicks into each product and extracts review data using JavaScript selectors.
* Takes screenshots of the pages for reference.
You can see the browser (Amazon) and Warp side-by-side as Puppeteer performs these steps autonomously.
Note
Puppeteer runs fully headless or in visible browser mode — you don’t need to touch your mouse or keyboard.
#### Analyze and summarize results
[Section titled “Analyze and summarize results”](#analyze-and-summarize-results)
Once the scrape is complete, Warp compiles the data and provides a ranked list of products. Example output (from transcript):
| Product | Price | Rating | Summary |
| ---------------- | ----- | ------ | --------------------- |
| Cozy T-Shirt | $8 | ⭐ 4.5 | Soft fabric, good fit |
| Comfy Cotton Tee | $10 | ⭐ 4.2 | Slightly looser fit |
| Basic White Top | $6 | ⭐ 3.8 | Mixed quality reviews |
Warp’s recommendation:
> “The Cozy T‑Shirt — $8, 4.5 stars, good fit, and soft fabric.”
#### Apply Puppeteer MCP to other scenarios
[Section titled “Apply Puppeteer MCP to other scenarios”](#apply-puppeteer-mcp-to-other-scenarios)
The same setup works for:
* Product research – Compare reviews or specs across multiple sites.
* Competitive analysis – Scrape competitors’ pricing or product data.
* Web testing – Automate user flows like login or checkout.
* Repetitive data tasks – Periodic scraping or screenshot capture.
Tip
Puppeteer MCP lets Warp act like your hands in the browser — navigating, scraping, and summarizing data while you focus on analysis.
# Sentry MCP: fix Sentry error in Empower website
Canonical page: [/guides/external-tools/sentry-mcp-fix-sentry-error-in-empower-website/](https://docs.warp.dev/guides/external-tools/sentry-mcp-fix-sentry-error-in-empower-website/)
> Connect the Sentry MCP server to Warp, fetch live error data, diagnose stack traces, and auto-generate fixes for production issues.
Note
This tutorial is based solely on the provided transcript. It teaches how to use the **Sentry MCP Server** within Warp to fetch live error data from Sentry, analyze stack traces, and automatically generate fixes for issues in your codebase.

### Overview
[Section titled “Overview”](#overview)
The **Sentry MCP server** gives Warp’s agents access to authenticated Sentry error data.\
This enables detailed diagnostics and automated fixes that would otherwise be impossible using AI alone.
You’ll learn how to:
* Connect the Sentry MCP server inside Warp.
* Trigger live error retrieval from Sentry.
* Diagnose code issues and generate patches automatically.
* Integrate Sentry debugging into your daily development loop.
1. #### Set up the Sentry MCP server
[Section titled “Set up the Sentry MCP server”](#set-up-the-sentry-mcp-server)
Open the MCP panel in Warp:
* macOS: `Cmd+Shift+P`
* Windows/Linux: `Ctrl+Shift+P`\
Search for “MCP” and select the **MCP Panel**.
Click **Add**, then paste your configuration:
```json
{
"sentry": {
"command": "npx",
"args": [
"-y",
"mcp-remote@latest",
"https://mcp.sentry.dev/mcp"
],
"env": {},
"working_directory": null
}
}
```
Save the configuration and ensure it appears in the MCP panel.
2. #### Run your app and trigger an error
[Section titled “Run your app and trigger an error”](#run-your-app-and-trigger-an-error)
We’re using the [**Empower Plant** repository](https://github.com/sentry-demos/empower) — Sentry’s official demo project. This fake e-commerce app includes a React frontend and multiple backends, each containing intentional bugs for testing.
Run the app locally:
```bash
npm install
npm start
```
Open the site in your browser and trigger a few known errors.
3. #### Capture the error in Sentry
[Section titled “Capture the error in Sentry”](#capture-the-error-in-sentry)
1. Go to your **Sentry Dashboard**.
2. Locate the triggered issue (for example, a `TypeError`).
3. Copy the issue’s URL from the Sentry interface.
Example:
```plaintext
https://sentry.io/organizations/demo/issues/12345/
```
4. #### Diagnose the error using Warp
[Section titled “Diagnose the error using Warp”](#diagnose-the-error-using-warp)
Back in Warp, prompt the agent to fetch and analyze the issue:
```plaintext
Diagnose this Sentry error and show where it’s coming from in my code.
Create a fix.
```
The Sentry MCP calls `getIssueDetails`, fetching the stack trace and error metadata directly from Sentry. Warp then scans your local codebase, cross-references the error location, and identifies the root cause.
From this example:
> The issue was caused by calling `.toUpperCase()` on an array instead of a string.
Warp’s agent automatically writes a fix — changing the code to handle the array properly.
5. #### Apply the generated fix
[Section titled “Apply the generated fix”](#apply-the-generated-fix)
Warp produces a suggested code change inline. Review the diff and apply it automatically with one click.
6. #### Integrate into your workflow
[Section titled “Integrate into your workflow”](#integrate-into-your-workflow)
Use Sentry MCP whenever you encounter production or staging errors. Warp can pull the latest issues, analyze them, and suggest patches.
Ideal for:
* Debugging live production errors.
* Triaging complex stack traces.
* Creating immediate hot-fixes without switching tools.
Tip
With Sentry MCP, Warp becomes a live debugging console — connecting your code editor, terminal, and Sentry into a single intelligent feedback loop.
# SQLite and Stripe MCP: basic queries you can make after setup
Canonical page: [/guides/external-tools/sqlite-and-stripe-mcp-basic-queries-you-can-make-after-set-up/](https://docs.warp.dev/guides/external-tools/sqlite-and-stripe-mcp-basic-queries-you-can-make-after-set-up/)
> Connect SQLite and Stripe MCP servers to Warp and run conversational queries against your local database and payment data.
This tutorial teaches you how to use **MCP servers** to connect Warp to **Stripe** and **SQLite**, showing how AI transforms the command line into a connected, conversational workspace.
[SQLite and Stripe MCP demo in Warp](https://x.com/svpino/status/1937896922297311390)
1. #### Enabling MCP in Warp
[Section titled “Enabling MCP in Warp”](#enabling-mcp-in-warp)
Warp now supports configuring any MCP server directly from the terminal.
To set it up:
* Open **Settings** > **Agents** > **MCP servers** in Warp.
* Click **Add Server**, and choose from a list of available MCP configurations.
* Once added, Warp automatically connects and authorizes the agent to use those tools.
In this demo, two MCP servers were enabled:
* **SQLite Server** – for running local database queries
* **Stripe Server** – for retrieving and analyzing payment data
2. #### Querying Stripe
[Section titled “Querying Stripe”](#querying-stripe)
Once configured, you can issue conversational prompts to the terminal — no manual API calls required.
Example — Querying Stripe
```plaintext
How many customers do I have in Stripe?
```
Warp connects to the Stripe MCP server, confirms the action, and returns:
> “You have 3 customers.”
You can continue naturally:
```plaintext
List the payments made by the first customer.
```
The agent retrieves seven payment intents — one successful, six canceled — all live from your Stripe test account.
Note: MCP’s confirmation prompts can be disabled once you trust a given server or agent.
3. #### Querying SQLite
[Section titled “Querying SQLite”](#querying-sqlite)
The same workflow applies to databases.
Example — Querying SQLite
```plaintext
What SQL tables do I have access to?
```
Warp lists all available tables from the local SQLite database.
```plaintext
Break down female penguins by island.
```
Warp translates this into a structured SQL query and executes it, returning:
> “Bisco Island — 51 female penguins; Dream Island — …”
Follow-up prompts work contextually:
```plaintext
Do the same with male penguins.
```
Warp runs the updated SQL query and displays results inline.
4. #### Why this matters
[Section titled “Why this matters”](#why-this-matters)
This demo highlights how Warp’s AI and MCP support combine to make your terminal:
* **Connected** — Access cloud APIs, local data, or enterprise tools instantly.
* **Conversational** — Run natural language prompts for structured data retrieval.
5. Note
“Even two years ago, no one could’ve imagined a terminal capable of this. Warp has officially redefined what a terminal can be.” — Santiago
# Connect developer tools to agents with MCP workflows
Canonical page: [/guides/external-tools/using-mcp-servers-with-warp/](https://docs.warp.dev/guides/external-tools/using-mcp-servers-with-warp/)
> Use MCP servers to connect Warp agents to developer tools like GitHub, Linear, Sentry, and Figma across local and cloud agent workflows.
MCP servers let Warp agents use external tools and data sources through a standard interface. Add an MCP server when an agent needs to read issues, inspect pull requests, query incidents, fetch design context, call internal APIs, or update systems outside the terminal.
Warp supports MCP in two places:
* **Local agents in the Warp app** use MCP servers configured in **Settings** > **Agents** > **MCP servers**, Warp Drive, or file-based config.
* **Cloud agents** use MCP servers passed through the Oz CLI, agent config files, or Warp-shared MCP server UUIDs.
Use this guide to choose the right setup path, then jump to the source docs for exact configuration syntax.
## Choose local or cloud MCP
[Section titled “Choose local or cloud MCP”](#choose-local-or-cloud-mcp)
| Workflow | Use it when | Configure MCP with | Source docs |
| ----------------------------- | -------------------------------------------------------------------------------------------------------------------------- | --------------------------------------------------------------------------------------- | -------------------------------------------------------------------------- |
| Local Warp agent | You are working interactively in Warp and want the agent to use tools from your machine or desktop-authenticated services. | Warp MCP settings, Warp Drive MCP servers, `.warp/.mcp.json`, or provider config files. | [Model Context Protocol (MCP)](/agents/capabilities/mcp/) |
| Third-party CLI agent in Warp | You run Claude Code, Codex, OpenCode, or another CLI agent in Warp and want shared MCP config across tools. | File-based MCP config that Warp can detect and approve. | [File-based MCP servers](/agents/capabilities/mcp/#file-based-mcp-servers) |
| Cloud agent run | The agent runs in a cloud environment from Slack, Linear, schedules, GitHub Actions, the CLI, or the API. | `--mcp`, an agent config file, or a Warp-shared MCP UUID. | [MCP Servers for cloud agents](/platform/mcp/) |
| Repeatable automation | You need the same MCP tools every time a scheduled agent, integration, or CI workflow runs. | Agent config files plus [Agent Secrets](/platform/secrets/) for credentials. | [MCP servers (CLI reference)](/agents/cli/oz-cli/mcp-servers/) |
## Common MCP workflows
[Section titled “Common MCP workflows”](#common-mcp-workflows)
### Pull GitHub or Linear context into a local coding session
[Section titled “Pull GitHub or Linear context into a local coding session”](#pull-github-or-linear-context-into-a-local-coding-session)
Use local MCP when you want an interactive agent to understand an issue, PR, or ticket while you work in Warp.
Example workflow:
1. In the Warp app, add a GitHub or Linear MCP server from **Settings** > **Agents** > **MCP servers**.
2. Start a local agent conversation in the repo.
3. Ask the agent to fetch the issue, inspect linked context, and make a plan.
4. Review changes in the [Code Review panel](/code/code-review/).
5. Use [Agent Session Sharing](/agents/local-agents/session-sharing/) if teammates need to inspect the agent context.
For setup details, see [Model Context Protocol (MCP)](/agents/capabilities/mcp/).
### Give cloud agents access to developer tools
[Section titled “Give cloud agents access to developer tools”](#give-cloud-agents-access-to-developer-tools)
Use cloud MCP when an unattended or remote agent needs tool access while it runs away from your machine.
Example workflow:
1. Create or identify the MCP server the cloud agent should use.
2. Store required credentials as [Agent Secrets](/platform/secrets/) instead of hardcoding tokens in config files.
3. Attach the MCP server with `--mcp`, a config file, or a Warp-shared MCP UUID.
4. Run the cloud agent from the Oz CLI, Slack, Linear, GitHub Actions, a schedule, or the API.
5. Inspect the run in the [Oz web app](/platform/oz-web-app/) or [Cloud agent session sharing](/platform/viewing-cloud-agent-runs/).
For schema and cloud-specific limitations, see [MCP Servers for cloud agents](/platform/mcp/).
### Share an MCP server with a team
[Section titled “Share an MCP server with a team”](#share-an-mcp-server-with-a-team)
Use shared MCP servers when multiple teammates or workflows need the same tool connection.
For local agents, share the server from the MCP settings page. Warp scrubs sensitive environment values and prompts teammates to provide their own values when they install it.
For cloud agents, reference a Warp-shared MCP server by UUID with the Oz CLI:
```sh
oz mcp list
```
Then pass the UUID to an agent run:
```sh
oz agent run-cloud --mcp "<MCP_SERVER_UUID>" --prompt "Summarize the latest production incidents"
```
See [MCP servers (CLI reference)](/agents/cli/oz-cli/mcp-servers/) for all `--mcp` formats.
## Local MCP setup paths
[Section titled “Local MCP setup paths”](#local-mcp-setup-paths)
For local agents, choose one of these paths:
* **Warp settings** - Best for one-off setup and interactive use. In the Warp app, add servers from **Settings** > **Agents** > **MCP servers**.
* **Warp Drive** - Best for MCP servers you want to manage as Warp Drive objects.
* **File-based config** - Best when MCP config should live with a repo or follow you across Warp, Claude Code, Codex, and other agent tools.
* **`/agent-add-mcp` skill** - Best when you want Warp’s agent to create or update `.warp/.mcp.json` with your approval.
File-based MCP is useful for teams because config can be versioned with a project, but it also needs review. Warp requires approval before project-scoped servers start so cloned repos cannot silently launch commands.
## Cloud MCP setup paths
[Section titled “Cloud MCP setup paths”](#cloud-mcp-setup-paths)
For cloud agents, choose one of these paths:
* **Warp-shared MCP UUID** - Best when a server is already configured and shared in Warp.
* **Inline JSON** - Best for quick experiments.
* **JSON file** - Best for reusable scripts.
* **Agent config file** - Best for production workflows where model, environment, prompt, and MCP servers should live together.
Cloud agents run away from your desktop. Any secrets required by MCP tools should be available in the cloud run through [Agent Secrets](/platform/secrets/) or the execution environment, not only in your local shell.
Caution
A raw `url` MCP config that requires OAuth and has no `Authorization` header isn’t supported for cloud agents — they can’t complete a browser login mid-run. Authorize it once as a managed MCP installation from the [Oz web app](/platform/oz-web-app/#integrations) **Integrations** page, then reference it by `warp_id`. See [OAuth authentication](/platform/mcp/#oauth-authentication) for the setup steps.
## Example tools MCP can connect
[Section titled “Example tools MCP can connect”](#example-tools-mcp-can-connect)
Warp supports MCP servers for many developer tools, including:
* **GitHub** - Read issues, PRs, files, and repository metadata.
* **Linear** - Fetch issues, update tickets, and reason over project context.
* **Sentry** - Inspect errors, traces, and release context.
* **Figma** - Pull design context for UI work.
* **Notion** - Retrieve docs, specs, and project notes.
* **Internal tools** - Expose your own APIs through a custom MCP server.
For example configurations and demos, see the MCP server examples in [Model Context Protocol (MCP)](/agents/capabilities/mcp/#mcp-server-configuration-examples) and the [MCP guides listed on the Guides page](/guides/).
## Security checklist
[Section titled “Security checklist”](#security-checklist)
Before giving an agent tool access through MCP:
* Use the narrowest credentials and scopes that let the workflow run.
* Prefer service accounts for team or scheduled workflows.
* Store cloud-run credentials in [Agent Secrets](/platform/secrets/).
* Review file-based MCP config before approving it, especially commands, args, environment variables, and URLs.
* Treat MCP logs as sensitive if they contain API responses, tokens, request headers, or private data.
* For cloud agents, confirm whether the MCP server can be reached from the cloud environment or self-hosted worker.
## Next steps
[Section titled “Next steps”](#next-steps)
* [Model Context Protocol (MCP)](/agents/capabilities/mcp/) - Configure MCP servers for local agents in the Warp app.
* [MCP Servers for cloud agents](/platform/mcp/) - Configure MCP servers for cloud runs and automation.
* [MCP servers (CLI reference)](/agents/cli/oz-cli/mcp-servers/) - Use `--mcp` with UUIDs, inline JSON, or files.
* [Agent Secrets](/platform/secrets/) - Store credentials for cloud agent runs.
# Code UI that matches your mockup
Canonical page: [/guides/frontend/how-to-actually-code-ui-that-matches-your-mockup-react-tailwind/](https://docs.warp.dev/guides/frontend/how-to-actually-code-ui-that-matches-your-mockup-react-tailwind/)
> Prompt Warp to generate pixel-perfect React + Tailwind code from design mockups, with structured specs and iterative refinement.
Learn how to prompt Warp’s AI to produce accurate, design-faithful UI code using your preferred framework.

***
## Intro
[Section titled “Intro”](#intro)
This tutorial walks you through generating pixel-perfect front-end code using Warp.\
\
By treating the AI like a **UI engineer**, you can get closer to real implementation fidelity — especially when working from design mockups.
Although this example uses **React** and **Tailwind**, the same method applies to **Vue**, **Next.js**, or **Svelte**.
***
1. #### The problem
[Section titled “The problem”](#the-problem)
When designing UI with AI, your intended design often gets lost in translation.\
AI struggles with visual fidelity — but structured prompts can help fix that.
2. #### The prompt
[Section titled “The prompt”](#the-prompt)
Step — Generate full specifications:
```plaintext
Analyze this web design mockup as a senior UI engineer would. Create a complete technical specification:
1. DESIGN SYSTEM TOKENS:
- Extract the color palette with semantic naming (primary, secondary, surface, text)
- Identify the type scale (heading levels, body text sizes)
- Document the spacing scale pattern (4px, 8px, 16px, etc.)
- List border radius values used consistently
2. LAYOUT ARCHITECTURE:
- Describe the overall page structure using semantic HTML5 elements
- Identify CSS Grid vs Flexbox usage for each section
3. COMPONENT SPECIFICATIONS:
For each unique component, provide:
- Semantic HTML structure
- CSS layout method
- All visual states (default, hover, focus, active, disabled)
- Exact dimensions and spacing
- Animation/transition properties
4. RESPONSIVE BEHAVIOR:
- Describe how the layout adapts (even if only desktop is shown)
- Note which elements stack, hide, or resize
- Identify touch targets that need enlarging on mobile
5. ACCESSIBILITY REQUIREMENTS:
- Color contrast ratios for text/background combinations
- Interactive element sizes (minimum 44x44px touch targets)
- Focus indicator styles
- Screen reader considerations for decorative elements
Format as a structured spec that includes both the visual description AND implementation notes. Flag any ambiguous design decisions that need clarification.
```
Next, give Warp the right prompt to start the code implementation:
```plaintext
Using this design specification, build a responsive React component with Tailwind CSS:
Requirements:
- Create reusable components for each element in the spec
- Use CSS variables for the design tokens
- Implement all interactive states
- Ensure mobile-first responsive design
- Add proper semantic HTML and ARIA labels
- Include Framer Motion for any animations mentioned
- Match the spacing system exactly using Tailwind's spacing scale
Create a pixel-perfect implementation that matches the original design.
```
3. #### Validate and iterate
[Section titled “Validate and iterate”](#validate-and-iterate)
Warp outputs component files and layout structure.\
You can review spacing, font weights, and responsive behavior directly in preview.
If details feel off, prompt again with clarifications like:
```plaintext
Tighten vertical spacing between header and subtext.
```
4. #### Recap
[Section titled “Recap”](#recap)
You’ve learned how to:
* Prompt AI for structured UI specs
* Generate React + Tailwind implementations
* Iterate visually for design parity
> Treating the AI like a teammate — not a tool — yields interfaces that finally match your vision.
# Replace a UI element in Warp (Rust codebase)
Canonical page: [/guides/frontend/how-to-replace-a-ui-element-in-warp-rust-codebase/](https://docs.warp.dev/guides/frontend/how-to-replace-a-ui-element-in-warp-rust-codebase/)
> Use Agent Mode in Warp to plan and execute icon replacements across a large Rust codebase — with live diffs, auto-compilation, and self-correction.
Learn how to use Warp’s AI coding features to make live code changes — in this example, replacing an icon throughout Warp’s massive Rust codebase using an agentic workflow.

Note
This demo showcases Warp’s ability to safely make intelligent code changes within a multi-million-line codebase by providing structured prompts, reviewing diffs in real time, and letting the agent compile and self-correct.
1. #### Define the task
[Section titled “Define the task”](#define-the-task)
The goal here is to replace all instances of the **sparkle icon** with the new **agent icon**, especially within the history menu.
Open your project in Warp and start by prompting the agent directly (either by typing or speaking):
```plaintext
Please create a new branch for me according to the format in the attached Linear URL.
I’ve attached screenshots of what the Agent Mode and sparkle icons look like.
I would like you to understand those icons, search for their use in the code,
and wherever we’re using sparkles, replace them with the Agent Mode icon.
Specifically, make sure this happens in the history menu.
Please give me a plan before making any coding changes.
```
Attach any relevant Linear issue links or screenshots to help the agent identify assets accurately.
2. #### Review the plan
[Section titled “Review the plan”](#review-the-plan)
Warp’s agent parses your request and generates a plan for code edits.\
It identifies files and functions where the sparkle icon is used.
If the plan looks correct, approve it to proceed.
Follow-up prompt example:
```plaintext
Yes, proceed — and please rename the function from renderAISparklesIcon
to something like renderAgentModeIcon.
```
Warp automatically updates function names, asset references, and component usage.
3. #### View AI diffs in real time
[Section titled “View AI diffs in real time”](#view-ai-diffs-in-real-time)
Warp lets you view live diffs as the agent edits your files.
* Diffs show changes to both render logic and function naming.
* You can choose to auto-accept or manually review diffs.
* These settings can be adjusted under **AI Settings** > **Apply Changes Automatically**.
Note
Note: The demo runs with “auto-accept” enabled, allowing Warp to apply diffs as soon as they’re validated.
4. #### Compilation and fixes
[Section titled “Compilation and fixes”](#compilation-and-fixes)
After editing, Warp’s agent runs:
```bash
cargo check
```
to verify compilation.
If compilation fails (e.g., missing imports), the agent automatically corrects and retries — mimicking a human debugging process.
5. #### Testing the change
[Section titled “Testing the change”](#testing-the-change)
Once compiled:
* Run your project locally to confirm visual changes.
* Check that the agent icon now replaces the sparkle icon in all targeted locations.
6. #### Recap
[Section titled “Recap”](#recap)
Warp’s agent completed the full flow:
1. Understood a Linear ticket and visual context
2. Created a new branch
3. Planned and executed the icon replacement
4. Auto-fixed compile issues
5. Verified the final result in-app
# 10 coding features you should know
Canonical page: [/guides/getting-started/10-coding-features-you-should-know/](https://docs.warp.dev/guides/getting-started/10-coding-features-you-should-know/)
> Discover 10 essential coding features in Warp — file search, tabbed editor, find and replace, syntax highlighting, code review panel, and more.
## 10 coding features you should know in Warp
[Section titled “10 coding features you should know in Warp”](#10-coding-features-you-should-know-in-warp)
If you didn’t already know, you can code directly in Warp.
Warp includes a full set of features that make editing, reviewing, and navigating your codebase far easier than in a traditional dev tool.

Let’s walk through the 10 core features you need to know to get started.
***
### 1. Search for files
[Section titled “1. Search for files”](#1-search-for-files)
Open the **Command Palette**:
* **macOS:** `Cmd+P`
* **Windows/Linux:** `Ctrl+Shift+P`
Then press:
* **macOS:** `Cmd+O`
* **Windows/Linux:** `Ctrl+O`
From here, you can search and open any file in your project — no need to `cd` around or remember long paths.
***
### 2. Tabbed file viewer
[Section titled “2. Tabbed file viewer”](#2-tabbed-file-viewer)
When you open files, Warp shows them in **tabs** rather than split panes.\
This keeps your workspace clean while still allowing you to switch quickly between multiple files.
***
### 3. Full editor support
[Section titled “3. Full editor support”](#3-full-editor-support)
You can edit code directly inside Warp — just like any modern editor.
No need for memorized shortcuts:
* Click and type normally
* Highlight, copy, paste, or undo using familiar shortcuts
***
### 4. Find and replace
[Section titled “4. Find and replace”](#4-find-and-replace)
Warp supports full **find and replace** with:
* Regular expressions
* Multi-cursor editing
* Replace-all
* Preserve-case rules
These features make renaming variables or refactoring code fast and consistent.
***
### 5. Syntax highlighting
[Section titled “5. Syntax highlighting”](#5-syntax-highlighting)
Warp supports syntax highlighting for **dozens of languages and frameworks**.\
It appears both in:
* Agent-generated diffs
* The file editor view
This makes it easy to visually scan code at a glance.
***
### 6. Linked file references
[Section titled “6. Linked file references”](#6-linked-file-references)
When Warp’s agent references a file, it automatically **links to the exact line of code**.\
Clicking the link opens that file at that line inside Warp — perfect for tracing logic or verifying changes.
> ⚙️ **Tip:** In **Settings** > **Features**, set Warp as your default editor for these file links so they open directly in Warp.
***
### 7. Code Review panel
[Section titled “7. Code Review panel”](#7-code-review-panel)
Warp provides a **dedicated review panel** summarizing all files and diffs touched by an agent.\
You can:
* Review and approve changes
* Edit them inline
* Reference diffs in your next prompt
This reduces hallucinations and keeps agents grounded in your actual code.
***
### 8. Code snippet references
[Section titled “8. Code snippet references”](#8-code-snippet-references)
When Warp explains something about your codebase, it surfaces the **exact code snippet**.\
You can attach that snippet as fresh context for your next prompt. This keeps token usage lean and the agent’s focus sharp.
***
### 9. Codebase indexing
[Section titled “9. Codebase indexing”](#9-codebase-indexing)
Warp can automatically **index your repositories** for faster, more context-aware responses.\
This makes it easier for agents to:
* Summarize large codebases
* Fix bugs
* Handle refactors intelligently
***
### 10. File tree view
[Section titled “10. File tree view”](#10-file-tree-view)
Click the file-tree icon in Warp to **browse your entire repo** and open any file with a single click.
# Customize Warp's appearance
Canonical page: [/guides/getting-started/how-to-customize-warps-appearance/](https://docs.warp.dev/guides/getting-started/how-to-customize-warps-appearance/)
> Customize Warp's themes, input placement, AI settings, codebase indexing, team collaboration, and visual appearance to fit your workflow.

Warp is highly customizable — from appearance and keyboard shortcuts to agent behavior and autonomy.\
\
Here’s a quick walkthrough of how to make Warp feel like *your* development environment.
***
### 1. Changing themes
[Section titled “1. Changing themes”](#1-changing-themes)
Open the **Command Palette** with:
* `Cmd+P` (macOS)
* `Ctrl+Shift+P` (Windows/Linux)
Type **“themes”** to open the theme picker.
You can preview and apply any theme instantly — for example, switching from the default theme to *Phenomenon*.
***
### 2. Adjusting input placement
[Section titled “2. Adjusting input placement”](#2-adjusting-input-placement)
Warp’s **input bar** can live in three different positions:
1. **Bottom-pinned** — chat-style; commands flow upward.
2. **Scrolling input** — traditional terminal style; input stays near the bottom as output moves up.
3. **Top-pinned** *(Warp-exclusive)* — input stays fixed at the top; results appear below.
***
### 3. Managing AI & agent settings
[Section titled “3. Managing AI & agent settings”](#3-managing-ai--agent-settings)
Open **Settings** > **Agents** > **Warp Agent** to control:
* Which **model** Warp uses (e.g., Claude 3.5 for code generation, GPT-4o for planning).
* How much **autonomy** agents have for:
* Reading files
* Generating diffs
* Running commands
* Planning tasks
You can also allowlist or block specific commands that always require confirmation.
***
### 4. Indexing your codebases
[Section titled “4. Indexing your codebases”](#4-indexing-your-codebases)
Warp prompts you to index your codebase the first time you `cd` into it.\
Indexing enables faster:
* Code navigation
* Summaries and searches
* Refactors and bug fixes
You can also manually re-index a folder from the sidebar anytime.
***
### 5. Team collaboration
[Section titled “5. Team collaboration”](#5-team-collaboration)
In the Teams tab, you can:
* Invite teammates
* Share Warp Drive assets like prompts, templates, and environment variables
This makes Warp a shared, contextual workspace — not just an individual tool.
***
### 6. Look & feel
[Section titled “6. Look & feel”](#6-look--feel)
Under Appearance, you can tweak:
* Fonts
* App icons
* Padding and editor density
* VIM mode for command editing
* Custom key bindings
# How to Make Warp’s UI More Minimal
Canonical page: [/guides/getting-started/how-to-make-warps-ui-more-minimal/](https://docs.warp.dev/guides/getting-started/how-to-make-warps-ui-more-minimal/)
> Reduce visual noise in Warp by disabling UI elements, switching to a minimal theme, and hiding the tab bar.
### 1. Start with the Command Palette
[Section titled “1. Start with the Command Palette”](#1-start-with-the-command-palette)
Open the Command Palette:
* macOS: `Cmd+P`
* Windows/Linux: `Ctrl+Shift+P`
From here, type “Disable” to see a full list of UI toggles.\
Warp will surface options that let you quickly hide features and visual elements.
***
### 2. Key UI toggles to disable
[Section titled “2. Key UI toggles to disable”](#2-key-ui-toggles-to-disable)
#### Inline and AI features
[Section titled “Inline and AI features”](#inline-and-ai-features)
* Disable Auto Suggestions → removes inline code hints.
* Disable Active AI → hides the ghost prompt that suggests agent queries.
* Disable Completion Menu → prevents popup completions from appearing.
* Disable Voice Input → hides the microphone icon.
#### Interface and layout
[Section titled “Interface and layout”](#interface-and-layout)
* Disable Block Dividers → removes the horizontal lines between commands.
* Disable Tab Indicators → hides the colored status markers across your tab bar.
* Disable Dimming Inactive Panes → keeps all split panes at equal brightness.
* Disable VIM Status Bar → removes the VIM indicator if you’re not using VIM mode.
***
### 3. Choose a simpler theme
[Section titled “3. Choose a simpler theme”](#3-choose-a-simpler-theme)
Visual noise can come from colors too.\
Try switching to a calmer theme from the Command Palette:
1. Open the palette again (`Cmd+P`)
2. Type “Theme”
3. Pick one with softer tones — for example:
* Adeberry → calm, gray, minimal aesthetic
* Classic Dark → familiar and focused
A consistent neutral palette makes Warp feel lighter and easier on the eyes.
***
### 4. Reduce tab bar visibility
[Section titled “4. Reduce tab bar visibility”](#4-reduce-tab-bar-visibility)
You can make the tab bar appear only when you hover:
* Open **Settings** > **Appearance**
* Enable “Show Tabs on Hover”
This keeps your workspace focused while still letting you access tabs when needed.
# Master Warp's Code Review panel
Canonical page: [/guides/getting-started/how-to-master-warps-code-review-panel/](https://docs.warp.dev/guides/getting-started/how-to-master-warps-code-review-panel/)
> Use Warp's Code Review Panel to view file diffs, edit code inline, componentize changes, and commit directly — all without leaving the terminal.

### 1. Why use the Code Review panel
[Section titled “1. Why use the Code Review panel”](#1-why-use-the-code-review-panel)
Warp’s Code Review panel helps you stay focused while coding by showing all active file diffs, additions, and deletions — without leaving your workspace.
***
### 2. Start with a coding task
[Section titled “2. Start with a coding task”](#2-start-with-a-coding-task)
The app has a UI issue: the hover text is black on dark gray, making it unreadable.
Warp’s agent generates diffs with proposed fixes — but for larger projects, scrolling through them is inefficient.
***
### 3. Opening the Code Review panel
[Section titled “3. Opening the Code Review panel”](#3-opening-the-code-review-panel)
Click:
* View Changes (top-left), or
* The Dirty Chip in your input bar
This opens the Code Review panel — available only when inside a Git repo.
The panel shows:
* Changed files
* Lines added/deleted
* File-by-file diff summaries
***
### 4. Editing and reviewing code
[Section titled “4. Editing and reviewing code”](#4-editing-and-reviewing-code)
You can open any file directly from the panel in Warp’s **built-in editor**:
* Syntax highlighting
* Find & replace
* Inline editing
Save changes — and they’ll reflect instantly in the diff view.
***
### 5. Componentizing changes
[Section titled “5. Componentizing changes”](#5-componentizing-changes)
Want that same hover fix across the app?\
Prompt Warp to componentize the hover style.
Attach the recent diff as context so Warp can generalize it.\
The agent then creates a `Tooltip` component that reuses your schema everywhere.
***
### 6. Reviewing and committing
[Section titled “6. Reviewing and committing”](#6-reviewing-and-committing)
Once the fix looks correct:
* Review in the code panel
* Commit directly from Warp
* Watch the panel reset to its “no changes” state
You can also click to compare your branch against `main` instantly.
# Welcome to Warp
Canonical page: [/guides/getting-started/welcome-to-warp/](https://docs.warp.dev/guides/getting-started/welcome-to-warp/)
> Get oriented with Warp's agentic terminal. Learn the basics of prompt-based coding, blending terminal and agent workflows, and navigating the interface.

### 1. Welcome to Warp
[Section titled “1. Welcome to Warp”](#1-welcome-to-warp)
When you open Warp, you’ll see something familiar — a command line interface — but it’s much more than a traditional terminal.\
\
Warp is an Agentic Development Environment (ADE), meaning it’s a space where your primary mode of interaction is through prompts to an agent.
You can still use Warp just like any terminal:
```bash
ls
pwd
```
Warp executes those commands exactly as you’d expect.\
\
But when you type natural language — like *“describe my open git changes”* — Warp interprets it as a prompt to launch the agent.
***
### 2. Prompt-based coding
[Section titled “2. Prompt-based coding”](#2-prompt-based-coding)
When you ask something in plain English, Warp’s agent automatically:
* Gathers relevant context (your repo, files, or command output)
* Runs whatever commands are needed
* Returns a structured answer or takes the requested action
Example:
> “Describe my open git changes.”
Warp’s agent will review your current branch, run git commands in the background, and summarize what’s pending.
***
### 3. Blending terminal and agentic workflows
[Section titled “3. Blending terminal and agentic workflows”](#3-blending-terminal-and-agentic-workflows)
The beauty of Warp is in how seamlessly it blends traditional CLI workflows with AI-driven automation.\
You can:
* Type commands like a normal shell
* Or prompt an agent to do things like debugging, code review, or environment setup
No context-switching between apps — it’s all one environment.
# Team Admin Panel
Canonical page: [/knowledge-and-collaboration/admin-panel/](https://docs.warp.dev/knowledge-and-collaboration/admin-panel/)
> Centralized management for team administrators to configure workspace settings enforced across all team members.
The Admin Panel gives team administrators centralized control over organization-wide Warp settings, including agent autonomy, privacy controls, billing limits, codebase indexing, and sharing policies. Settings configured in the Admin Panel are enforced across all team members and override individual preferences.
## What is the Admin Panel?
[Section titled “What is the Admin Panel?”](#what-is-the-admin-panel)
The [Admin Panel](https://app.warp.dev/admin/) provides team administrators with centralized control over organization-wide settings in Warp. It allows you to manage workspace settings that are enforced across all members of your team.
Note
Admin Panel access is restricted to team administrators. Right now, only the creator of a team is the designated admin. If your admin has set up styles that override user preferences, you will not be able to control them inside of Warp, and you’ll see a note that your admin has configured this setting.
In multi-team workspaces, workspace admins configure supported settings across all teams. See [Workspace settings and team settings](/enterprise/team-management/workspaces/#workspace-settings-and-team-settings).
**Key features:**
* **AI Settings** - Control agent autonomy, permissions, and allowlists across your team
* **Privacy Controls** - Configure data collection and enterprise secret redaction
* **Billing Management** - Set spending limits and manage usage-based pricing
* **Code Settings** - Control codebase indexing and context features
* **Sharing Policies** - Manage link sharing and collaboration permissions
## Accessing the Admin Panel
[Section titled “Accessing the Admin Panel”](#accessing-the-admin-panel)
Team administrators can access the Admin Panel directly from the [Warp Admin Panel](https://app.warp.dev/admin/).

Admin Panel main interface.
## How settings enforcement works
[Section titled “How settings enforcement works”](#how-settings-enforcement-works)
The Admin Panel uses a tier-based policy system to determine which settings administrators can control:
### Toggleable vs. fixed settings
[Section titled “Toggleable vs. fixed settings”](#toggleable-vs-fixed-settings)
**Toggleable settings** can be modified by team administrators. These appear as dropdown menus with options like:
* Enabled/Disabled for boolean settings
* Specific autonomy levels for AI settings
* Respect User Setting to allow individual control
**Fixed settings** are determined by your billing tier and cannot be changed. These appear with a message: “Configuring this setting is not available on your plan.”
### Setting inheritance
[Section titled “Setting inheritance”](#setting-inheritance)
When administrators configure organization-wide settings:
1. **Organization enforced** - Setting applies to all team members regardless of individual preferences
2. **Respect user setting** - Allows individual team members to control the setting themselves
3. **Tier restricted** - Setting is locked to default values based on billing plan
### User experience
[Section titled “User experience”](#user-experience)
Note
Any changes made in the Admin Panel can take effect immediately for all team members. Consider testing settings in Warp before applying organization-wide policies.
When organization settings override individual preferences:
* Users see their personal settings grayed out
* A message indicates “your organization has configured this setting”
* Users cannot modify settings that are organizationally enforced
## Plan limitations
[Section titled “Plan limitations”](#plan-limitations)
The features available in the Admin Panel vary by billing tier:
**Free Tier**
* Most settings are fixed and non-toggleable
* Limited Codebase Context and sharing features
**Business Plans**
* Most settings become toggleable by administrators
* Enhanced AI autonomy control
* Advanced sharing and privacy features
**Enterprise Plans**
* Full admin control over all settings
* Enterprise secret redaction
* Custom LLM integration
* Advanced compliance features
For complete details about what’s included in each plan, see [Warp pricing](https://www.warp.dev/pricing).
## Admin Panel sections
[Section titled “Admin Panel sections”](#admin-panel-sections)
The Admin Panel is organized into five main sections, each focused on a specific area of team management:
### AI settings
[Section titled “AI settings”](#ai-settings)
Configure how Agents behave across your organization, including autonomy levels and command permissions.
#### General AI settings
[Section titled “General AI settings”](#general-ai-settings)
**AI in Remote Sessions** Controls whether AI features are available during SSH sessions and remote connections. Enterprise plans can toggle this setting, while Free tier teams have it enabled by default.
**Prompt Summarization Caching** When conversations become long enough to require summarization, this setting allows the summary to be cached temporarily by the LLM provider to improve performance.
#### Autonomy settings
[Section titled “Autonomy settings”](#autonomy-settings)
Configure how much independence Agents have when performing different actions:
**Apply Code Diffs**
* Agent Decides - Prompt for review before applying code diffs (currently behaves the same as Always Ask)
* Always Ask - Require explicit approval before applying any code changes
* Always Allow - Apply code diffs without confirmation
* Respect User Setting - Allow individual users to control this setting
**Create Plans** Controls whether Agents can create structured task plans without user approval.
**Execute Commands** Manages Agent’s ability to run terminal commands autonomously.
**Read Files** Controls Agent access to reading files in the codebase.
#### Directory and command control
[Section titled “Directory and command control”](#directory-and-command-control)
**Directory Allowlist** Specify directories where Agents can read files without restriction. Use paths like `~/git/repo1` to grant access to specific project folders.
**Command Allowlist** Regular expressions matching commands that Agent Mode can execute without asking permission. Common examples:
* `grep .*` - Text search commands
* `ls(\\s.*)?` - Directory listing
* `which .*` - Finding executable locations
**Command Denylist** Regular expressions for commands that always require explicit user approval, even if they would normally be allowed. Examples:
* `rm -rf.*` - Recursive file deletion
* `sudo.*` - Administrative commands
* `curl.*` - Network requests
Caution
Command denylist rules take precedence over allowlist rules and agent autonomy settings. If a command matches the denylist, user permission will always be required.
### Privacy settings
[Section titled “Privacy settings”](#privacy-settings)
Manage data collection and security policies for your organization.
**UGC Data Collection** Controls how Warp collects and uses user-generated content to improve the service:
* Disabled - No UGC data collection
* Enabled - Allow data collection for service improvement
* Respect User Setting - Let individual users decide
**Enterprise Secret Redaction** When enabled, applies regex patterns to prevent secrets from being sent to Warp servers or LLM providers. This feature is available on Enterprise plans and includes:
* Automatic detection of common secret patterns
* Custom regex patterns for organization-specific secrets
* Unconditional application across all team members
### Code settings
[Section titled “Code settings”](#code-settings)
Control codebase indexing and AI code features for your team.
**Codebase Context** Determines whether Warp indexes your team’s Git repositories to provide context for AI features:
* Disabled - No codebase indexing
* Enabled - Index codebases for improved AI responses
* Respect User Setting - Allow individual control
Higher tier plans support more indexed repositories and larger file limits per codebase.
### Billing settings
[Section titled “Billing settings”](#billing-settings)
Configure billing preferences and spending controls.
**Usage Based Pricing** Enable pay-as-you-go billing for credits beyond your plan’s included quota. When enabled, you can set:
**Monthly Spending Limit** Set a maximum monthly overage spending limit to control costs. The system displays current overage usage including:
* Total overage credits used
* Current month’s overage costs
### Sharing settings
[Section titled “Sharing settings”](#sharing-settings)
Control how team members can share Warp Drive objects and collaborate.
**Direct Link Sharing** Allow team members to share Notebooks, Workflows, and other objects via direct links.
**Anyone with Link Sharing** Enable public access to shared objects - anyone with the link can view the content without being a team member.
# Session Sharing
Canonical page: [/knowledge-and-collaboration/session-sharing/](https://docs.warp.dev/knowledge-and-collaboration/session-sharing/)
> Share terminal sessions with teammates for collaboration, debugging, and knowledge sharing.
Session sharing documentation has moved. See the articles below for details on sharing sessions:
* **[Agent session sharing](/agents/local-agents/session-sharing/)** - Share agent sessions with your team for review and collaboration, on the Agents tab.
* **[Cloud agent session sharing](/platform/viewing-cloud-agent-runs/)** - Share session context from cloud agent runs, on the Automation Platform tab.
# Team management
Canonical page: [/knowledge-and-collaboration/teams/](https://docs.warp.dev/knowledge-and-collaboration/teams/)
> Create or join a team to collaborate with others in Warp.
A Warp team is a group of users who collaborate through a shared workspace in Warp Drive. Teams share Workflows, Notebooks, Prompts, Rules, and Environment Variables, with role-based permissions for admins and members.
## What is a team?
[Section titled “What is a team?”](#what-is-a-team)
A team is a group of Warp users who can collaborate on the command line together. Warp teams can share a dedicated workspace in Warp Drive. [Learn about pricing](https://www.warp.dev/pricing) and see our [Pricing FAQ](/support-and-community/plans-and-billing/pricing-faqs/).
Note
Users can belong to multiple teams when their Enterprise account uses a [multi-team workspace](/enterprise/team-management/workspaces/).

## Creating a team
[Section titled “Creating a team”](#creating-a-team)
You can create a new team in the following ways:
* Warp Drive, + Create a team
* **Settings** > **Teams**
Before you can invite team members, you will need to give your team a meaningful name. We suggest using a name to represent your organization, company, or project.
Note
You can rename the team by going to **Settings** > **Teams** and clicking on the team name, entering the new name, and pressing `Enter` to accept.
If you create a team, you become the team’s admin and will be the only person who can delete the team. Reference [Team roles and permissions](/knowledge-and-collaboration/teams/#team-roles-and-permissions) for more info.
### Inviting new team members
[Section titled “Inviting new team members”](#inviting-new-team-members)
Under **Settings** > **Teams** you can copy the invite link for your Warp team and paste it to your clipboard.
Caution
If you’re on a paid plan, upgrading will automatically include all team members in your billing. Adding new members after upgrading will also add them as paid seats.
For more details on how team member billing works, see our [billing FAQs](/support-and-community/plans-and-billing/pricing-faqs/#what-counts-as-a-team-member-and-how-does-billing-work-for-members).
Teams settings panel.
When you share this link with your teammates directly (we suggest using a secure channel like Slack or email), they can join your team in Warp.
## Restricting team invites by domain
[Section titled “Restricting team invites by domain”](#restricting-team-invites-by-domain)
You can restrict your team so that people can only join if they also authenticate with a specific email domain, such as your company’s email domain.
Toggle on **Restrict by domain** to set an explicit allowlist.
If you share an invite link with somebody who’s using Warp with a domain that does not match your allowlist, they will be prompted to authenticate from an emailed link sent to a matching domain to join your team.
## Joining a team
[Section titled “Joining a team”](#joining-a-team)
If you have received an invite link, you can use that link to sign up or log in and join your team in Warp. If your team is using domain restriction, you will need to authenticate you have access to a specific domain before you can join your team.
## Leaving and deleting teams
[Section titled “Leaving and deleting teams”](#leaving-and-deleting-teams)
If you’re a member of a team, you can visit **Settings** > **Teams** to leave a team at any time. Team admins (who created teams) may delete a team only after removing all team members.
Caution
A team can’t be deleted while it has unused add-on credits. Before you can delete the team, all add-on credits tied to it must be used or removed. Contact <support@warp.dev> if you need help removing unused credits.
On Build, Max, and Business plans, [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) are shared across the team and **tied to the team** they were purchased under. Membership changes affect access:
* **A user leaves a team** - You lose access to any add-on credits tied to that team. If you rejoin the same team later, you regain access to any unused, non-expired credits. The admin pays a prorated rate for your seat on rejoin.
* **An admin removes a member** - That member loses access to any add-on credits tied to the team. If they rejoin later, they regain access to any unused, non-expired credits. The admin pays a prorated rate for the seat when the user rejoins.
* **An admin deletes the team** - Any remaining add-on credits must be used or removed before the team can be deleted.
Add-on credits require an active subscription to use. Downgrading to the Free plan suspends access to the add-on credits tied to your team, but doesn’t remove them. They keep their original 12-month expiration, and you regain access when you re-subscribe on the same team.
## Team discoverability
[Section titled “Team discoverability”](#team-discoverability)
Team admins can make their teams discoverable to colleagues from the same email domain. This feature is available under **Settings** > **Teams** > **Make team discoverable**.
Note
While discoverability is enabled, any new user who joins the team will add a prorated charge to the team’s next month’s bill. See more in our [pricing docs](/support-and-community/plans-and-billing/pricing-faqs/#what-counts-as-a-team-member-and-how-does-billing-work-for-members).
## Transferring team admin
[Section titled “Transferring team admin”](#transferring-team-admin)
Team admins can transfer their role to another team member by going to **Settings** > **Teams** > **Transfer admin** and selecting the member to whom you’d like to transfer the admin role.
## Team roles and permissions
[Section titled “Team roles and permissions”](#team-roles-and-permissions)
Caution
If you’re a Team admin, and you choose to [delete your Warp](/support-and-community/privacy-and-security/privacy/#delete-your-account-and-data) account, the deletion flow will require that you assign a team member as the new admin.
| Action | Admin | Member |
| --------------------------------------------------------------------------------------------------- | ---------------------------------------------------------- | ------------------------------------ |
| Description | The Warp user who created the team. There can only be one. | Team members who belong to the team. |
| Create a team | ✓ | |
| Restrict by domain | ✓ | |
| Invite members | ✓ | ✓ |
| Remove team members | ✓ | |
| Leave a team | | ✓ |
| Delete a team | ✓ | |
| Transfer admin | ✓ | |
| [Manage billing](/support-and-community/plans-and-billing/pricing-faqs/#how-do-i-manage-my-billing) | ✓ | |
Multi-team workspaces use [workspace roles](/enterprise/team-management/workspaces/#workspace-roles) for company-wide administration.
# Warp Drive overview
Canonical page: [/knowledge-and-collaboration/warp-drive/](https://docs.warp.dev/knowledge-and-collaboration/warp-drive/)
> Warp Drive is a workspace in your terminal where you can save Workflows, Notebooks, Prompts, and Environment Variables for personal use or to share with a team.
Warp Drive is a built-in workspace for saving and sharing Workflows, Notebooks, Prompts, and Environment Variables across your team. All objects sync in real time, so you and your team always have access to the latest versions, whether you’re working locally or collaborating across an organization.
## What is Warp Drive?
[Section titled “What is Warp Drive?”](#what-is-warp-drive)
All objects stored in Warp Drive sync immediately as they’re updated, so you and your team will always have access to the latest versions.

## How to access it
[Section titled “How to access it”](#how-to-access-it)
* macOS
Warp Drive is accessible from the status bar in Warp, from the [Warp Drive web experience](/knowledge-and-collaboration/warp-drive/web/), or you can toggle the Warp Drive side panel with `⌘+\`.
* Windows
Warp Drive is accessible from the status bar in Warp, from the [Warp Drive web experience](/knowledge-and-collaboration/warp-drive/web/), or you can toggle the Warp Drive side panel with `Ctrl+Shift+\`.
* Linux
Warp Drive is accessible from the status bar in Warp, from the [Warp Drive web experience](/knowledge-and-collaboration/warp-drive/web/), or you can toggle the Warp Drive side panel with `Ctrl+Shift+\`.
The Warp Drive icon in the top-left corner.
## Workspaces in Warp Drive
[Section titled “Workspaces in Warp Drive”](#workspaces-in-warp-drive)
When you open the Warp Drive panel, you will find a personal workspace where you can store your Workflows, Notebooks, Prompts, and Environment Variables and organize them into folders.
If you are a member of a team using Warp Drive, your team’s workspace will also be available in the side panel.
## Organizing objects in Warp Drive with your team
[Section titled “Organizing objects in Warp Drive with your team”](#organizing-objects-in-warp-drive-with-your-team)
* Objects (e.g. Workflows, Notebooks, Prompts, and Environment Variables) and folders in Warp Drive can be sorted alphabetically and by the last updated
* Any objects moved from your personal workspace into a team’s workspace will be shared with all members of your team
* It is not currently possible to move an item back from a team’s workspace into a personal workspace; if you shared something inadvertently, you should copy the contents of the object to your clipboard, recreate it in your personal workspace, and then delete the object from your team workspace
* It is not currently possible to drag a folder of personal Workflows into a team workspace; you will need to move objects one at a time
## Using Warp Drive offline
[Section titled “Using Warp Drive offline”](#using-warp-drive-offline)
In offline mode, some files will be read-only. You can still create and edit files while offline in your personal space. They will only be saved locally and will not be synced. They cannot be moved into a team or deleted until you are back online.
Warp Drive operating in offline mode.
## Navigating Warp Drive with your keyboard
[Section titled “Navigating Warp Drive with your keyboard”](#navigating-warp-drive-with-your-keyboard)
To avoid going back and forth between your mouse and keyboard, you can use your keyboard to navigate through Warp Drive once you have either opened Warp Drive or switched focus to the Warp Drive panel. (You can also click on a blank area within Warp Drive.) The object you are navigating with your keyboard will be highlighted in an accented color.
You can take these keyboard actions within Warp Drive:
* macOS
* Press `↑`/`↓` or `j`/`k` to navigate to the object you want.
* Press `Enter` to 1) execute an object, 2) open/collapse a workspace or folder, or 3) open the trash.
* Press `⌘+Enter` to open an object’s context menu.
* Press `⌘+Shift+(` and `⌘+Shift+)` to switch focus between the terminal and Warp Drive.
* Press `←` to collapse a workspace or folder
* Press `→` to open a workspace or folder
* Press `Esc` to return to Warp Drive from your trash.
* Windows
* Press `↑`/`↓` or `j`/`k` to navigate to the object you want.
* Press `Enter` to 1) execute an object, 2) open/collapse a workspace or folder, or 3) open the trash.
* Press `Ctrl+Enter` to open an object’s context menu.
* Press `Ctrl+Shift+(` and `Ctrl+Shift+)` to switch focus between the terminal and Warp Drive.
* Press `←` to collapse a workspace or folder
* Press `→` to open a workspace or folder
* Press `Esc` to return to Warp Drive from your trash.
* Linux
* Press `↑`/`↓` or `j`/`k` to navigate to the object you want.
* Press `Enter` to 1) execute an object, 2) open/collapse a workspace or folder, or 3) open the trash.
* Press `Ctrl+Enter` to open an object’s context menu.
* Press `Ctrl+Shift+(` and `Ctrl+Shift+)` to switch focus between the terminal and Warp Drive.
* Press `←` to collapse a workspace or folder
* Press `→` to open a workspace or folder
* Press `Esc` to return to Warp Drive from your trash.
Navigation states in the Warp Drive sidebar.
To switch between panels using your keyboard, you can use the “Switch Focus to Left Panel” and “Switch Focus to Right Panel” commands in the [Command Palette](/terminal/command-palette/).
## Import and export
[Section titled “Import and export”](#import-and-export)
Every object in Warp Drive can be exported to or imported from a file. When importing or exporting, objects are converted as follows:
* [Workflows](/knowledge-and-collaboration/warp-drive/workflows/) import from and export to YAML (.yaml, .yml)
* [Prompts](/knowledge-and-collaboration/warp-drive/prompts/) import isn’t supported at this time, but you can export to YAML (.yaml, .yml)
* [Notebooks](/knowledge-and-collaboration/warp-drive/notebooks/) import from and export to MARKDOWN (.md)
* [Environment Variables](/knowledge-and-collaboration/warp-drive/environment-variables/) import isn’t supported at this time, but you can export to DOTENV (.env)
### Importing files into Warp Drive
[Section titled “Importing files into Warp Drive”](#importing-files-into-warp-drive)
To import a local file or directory, `RIGHT-CLICK` on a folder or click **+** on a workspace and choose “Import.” If importing a directory, supported files in the directory and its sub-directories will be imported into a matching folder structure.
The import dialog for adding local files to Warp Drive.
### Exporting files from Warp Drive
[Section titled “Exporting files from Warp Drive”](#exporting-files-from-warp-drive)
To export a single Warp Drive object, `RIGHT-CLICK` on an object and choose “Export” from the menu, then select a directory for export. To export all Warp Drive objects, open the [Command Palette](/terminal/command-palette/#how-to-access-it), search for and select “Export all Warp Drive objects”, then select a directory for export.
## Sharing your drive objects
[Section titled “Sharing your drive objects”](#sharing-your-drive-objects)
Every object in Warp Drive can be shared. There are three ways to share objects:
* **Teams:** All members of a Warp team have full access to the objects in its Drive.
* **Direct Sharing:** Objects can be shared directly with individuals by email.
* **Link-based Sharing:** You can make an object public to anyone with the link, including those without Warp accounts.
### Sharing a drive object using links
[Section titled “Sharing a drive object using links”](#sharing-a-drive-object-using-links)
To share a Drive object, navigate to the object’s overflow menu, and choose “Copy link”. Once the link is successfully copied to your clipboard, you can share it with teammates and reference your object in your codebase, documentation, or communication channels like Slack.
Note
To access an object, link-followers must have permission to open it through one of the sharing methods above. If they do not have permission, they can automatically request access from the object owner or team admin.
The Copy link option in the right-click menu.
### Managing permissions
[Section titled “Managing permissions”](#managing-permissions)
To manage a Drive object’s permissions, navigate to its overflow menu and choose “Share”. If the object is open, you can also use the [Command Palette](/terminal/command-palette/#how-to-access-it) and search for “Share pane”, or click the share button in the pane header:
The share button in the pane header.
This opens a dialog that lists the current sharing settings and allows you to change them:
Warp Drive sharing dialog.
In this dialog, you can:
* Invite other users directly using the email input at the top.
* Change or remove the public link-based access level.
* Update the access level for individual users, or remove their access.
Permissions are inherited from parent folders. For example, if a folder was shared with edit permissions, then the user would also be able to edit all objects inside the folder or its subfolders.
Owners and their teammates always have full access. When sharing an object, you can choose between view and edit access.
| | Can view | Can edit | Full access |
| ----------------------------------- | -------- | -------- | ----------- |
| Read a notebook | ✓ | ✓ | ✓ |
| Execute a Workflow | ✓ | ✓ | ✓ |
| Use env vars | ✓ | ✓ | ✓ |
| Edit contents | | ✓ | ✓ |
| Create objects in a folder | | ✓ | ✓ |
| Trash or untrash | | ✓ | ✓ |
| Delete permanently | | | ✓ |
| Modify permissions | | | ✓ |
| Move to a different folder or drive | | | ✓ |
## Troubleshooting Warp Drive
[Section titled “Troubleshooting Warp Drive”](#troubleshooting-warp-drive)
* If you were previously using Warp on your own and were later invited to join a team, you may need to exit, update, and restart the Warp app to gain access to your team’s shared drive and commands
* Navigating to Settings > Teams in Warp should also force a metadata update for you, which will ensure you have access to the latest versions of Workflows in your team’s drive
# Agent Mode Context
Canonical page: [/knowledge-and-collaboration/warp-drive/agent-mode-context/](https://docs.warp.dev/knowledge-and-collaboration/warp-drive/agent-mode-context/)
> Agents use your Warp Drive content—Workflows, Notebooks, Rules, MCP Servers, and Environment Variables—for context-aware responses.
Warp’s agents automatically pull context from your Warp Drive contents, including Workflows, Notebooks, Environment Variables, Rules, and MCP Servers, to generate responses tailored to your personal and team developer workflows. Referenced objects appear as citations in the conversation.
## Objects used as context
[Section titled “Objects used as context”](#objects-used-as-context)
Agents can automatically pull in relevant context from:
* **Workflows** - Saved commands and scripts
* **Notebooks** - Documentation and notes
* **Environment Variables** - Configuration values
* **Rules** - Guidelines that shape agent behavior (see [Rules](/agents/capabilities/rules/))
* **MCP Servers** - External tools and data sources (see [MCP](/agents/capabilities/mcp/))
When a Warp Drive object is pulled as context, it will be displayed in the conversation as a citation under “References” or “Derived from”.
## Settings
[Section titled “Settings”](#settings)
Enabled by default, this can be toggled in **Settings** > **Agents** > **Knowledge** > **Warp Drive as Agent Mode Context**.
## Related
[Section titled “Related”](#related)
* [AI-Integrated Objects](/knowledge-and-collaboration/warp-drive/ai-objects/) - Overview of all AI-related objects in Warp Drive
# AI-Integrated Objects
Canonical page: [/knowledge-and-collaboration/warp-drive/ai-objects/](https://docs.warp.dev/knowledge-and-collaboration/warp-drive/ai-objects/)
> Access Rules, MCP Servers, Skills, and Prompts in Warp Drive to give agents personalized context.
Warp Drive includes several object types that integrate with Warp’s agents to provide personalized, context-aware assistance. These objects help agents understand your coding standards, connect to external tools, and follow your preferred workflows.
## Rules
[Section titled “Rules”](#rules)
Rules are reusable guidelines that inform how agents respond to your prompts. They help tailor responses to match your coding standards, project conventions, and personal preferences.
**Access from Warp Drive:** **Personal** > **Rules**
Warp supports two types of rules:
* **Global Rules** - Apply across all projects and contexts
* **Project Rules** - Live in your codebase (as `AGENTS.md` or `WARP.md` files) and apply automatically when working within that project
Note
For complete documentation on creating and managing rules, see [Rules](/agents/capabilities/rules/).
## MCP Servers
[Section titled “MCP Servers”](#mcp-servers)
MCP (Model Context Protocol) servers extend Warp’s agents with custom tools and data sources through a standardized interface. They act as plugins that let agents access external services like GitHub, Sentry, Linear, Slack, and more.
**Access from Warp Drive:** **Personal** > **MCP Servers**
MCP servers can be:
* **CLI-based** - Local commands that Warp launches and manages
* **URL-based** - Remote endpoints using Streamable HTTP or SSE
Note
For complete documentation on configuring and using MCP servers, see [Model Context Protocol (MCP)](/agents/capabilities/mcp/).
## Skills
[Section titled “Skills”](#skills)
Skills are reusable instruction sets that teach agents how to perform specific tasks. Unlike Rules (which provide guidelines), Skills define complete workflows that agents can invoke when relevant.
Skills are file-based (stored as `SKILL.md` files in your project or home directory) rather than cloud-synced objects, but they integrate closely with Warp Drive workflows.
* **Project Skills** - Live in `.agents/skills/`, `.warp/skills/`, or similar directories in your repository
* **Global Skills** - Live in `~/.agents/skills/` or similar directories in your home folder
Note
For complete documentation on creating and using skills, see [Skills](/agents/capabilities/skills/).
## Prompts
[Section titled “Prompts”](#prompts)
Prompts are parameterized natural language queries you can save and reuse with Agent Mode. They allow you to save complex AI workflows and execute them quickly from the Command Palette.
**Access from Warp Drive:** Click **+** and select “Prompt”, or browse existing prompts in your personal or team workspace.
Note
For complete documentation on Prompts, see [Prompts](/knowledge-and-collaboration/warp-drive/prompts/).
## How agents use these objects
[Section titled “How agents use these objects”](#how-agents-use-these-objects)
When you start an agent conversation, Warp automatically provides relevant context from your Warp Drive objects:
* **Rules** guide agent behavior and responses based on your preferences
* **MCP Servers** give agents access to external tools and data sources
* **Skills** provide task-specific instructions agents can invoke
* **Prompts** let you trigger predefined workflows quickly
When an object is used as context, it appears in the conversation under “References” or “Derived from.”
Note
For more details on how Warp Drive content serves as agent context, see [Warp Drive as Agent Mode Context](/knowledge-and-collaboration/warp-drive/agent-mode-context/).
## Related
[Section titled “Related”](#related)
* [Rules](/agents/capabilities/rules/) - Create guidelines for agent behavior
* [MCP Servers](/agents/capabilities/mcp/) - Connect external tools and data sources
* [Skills](/agents/capabilities/skills/) - Define reusable task workflows
* [Prompts](/knowledge-and-collaboration/warp-drive/prompts/) - Save and reuse parameterized agent prompts
* [Agent Profiles & Permissions](/agents/capabilities/agent-profiles-permissions/) - Control agent autonomy and tool access
# Environment variables
Canonical page: [/knowledge-and-collaboration/warp-drive/environment-variables/](https://docs.warp.dev/knowledge-and-collaboration/warp-drive/environment-variables/)
> Save or sync environment variables to load into your terminal sessions.
Environment Variables in Warp Drive let you save, sync, and load environment variables into your terminal sessions with a click. Support for both static values and dynamic secrets from external managers like 1Password, LastPass, and Hashicorp Vault keeps credentials secure and out of source code.
## What are environment variables in Warp?
[Section titled “What are environment variables in Warp?”](#what-are-environment-variables-in-warp)
Environment variables in Warp are similar to .env files, except you can:
* Load them into your terminal session with a click.
* Use them in parameterized workflows.
* Dynamically reference secrets from external managers.
## How to create and edit environment variables
[Section titled “How to create and edit environment variables”](#how-to-create-and-edit-environment-variables)
You can create new environment variables through:
* [Warp Drive](/knowledge-and-collaboration/warp-drive/), + → Environment variable
* [Command Palette](/terminal/command-palette/), create new team or personal environment variables
Any of these entry points will open the environment variables editor where you can name and describe your environment variables.

## Managing individual environment variables
[Section titled “Managing individual environment variables”](#managing-individual-environment-variables)
Warp supports two types of environment variables: static variables and dynamic variables.
### Static variables
[Section titled “Static variables”](#static-variables)
Static variables are similar to .env files. You create the variables by entering raw strings of text. Each variable has a variable name and a corresponding value.

After you save the environment variable, you can click it to load it into your terminal session.

When you use static variables, Warp stores them securely in Warp Drive.\
\
Note: Static variables should not be used to replace a secret manager. Use dynamic variables for any sensitive information.
### Dynamic variables
[Section titled “Dynamic variables”](#dynamic-variables)
Note
Warp never stores secrets used in dynamic variables. Warp only stores the command used to dynamically retrieve the secrets at runtime.
Dynamic variables let you reference secrets that are stored securely outside of Warp in external secret managers, such as 1Password or LastPass.
You can use custom commands to create dynamic variables for any system with a public API or CLI, such as AWS or Hashicorp Vault.
### How to create and edit dynamic environment variables
[Section titled “How to create and edit dynamic environment variables”](#how-to-create-and-edit-dynamic-environment-variables)
To create a new dynamic variable:
1. Open the environment variable editor.
2. Use the key icon to reveal the dynamic variable menu.
3. Select an integrated password manager or “Command” to write your own custom integration.

#### Integrated password managers
[Section titled “Integrated password managers”](#integrated-password-managers)
Before you get started, ensure you have the CLI installed for your tool of choice and follow the instructions to enable the CLI:
* [1Password CLI](https://developer.1password.com/docs/cli/get-started/)
* [LastPass CLI](https://github.com/lastpass/lastpass-cli)
Then, you can click the key icon and select your manager from the dropdown menu.

The CLI will require you to authenticate and then provide you with a list of available secrets.
Note
Selecting a secret name never stores the actual secret. Warp uses your selection to generate a command that dynamically pulls in your selected secret at runtime.
### How to write a custom secret command
[Section titled “How to write a custom secret command”](#how-to-write-a-custom-secret-command)
Reference the documentation for your external secret manager. Then, write a custom command to retrieve secrets.
Note
Your custom command should return the exact string you want loaded into your environment. Make sure you select the exact field you want loaded, as many secret manager CLIs provide additional formatting by default.
For example, you can write a command using the [Hashicorp Vault CLI](https://developer.hashicorp.com/vault/docs/commands) to retrieve and load the password field for the staging server. When using secret commands, Warp stores the command but never the actual secrets. The secrets are referenced and loaded into a terminal session at runtime.
```plaintext
// vault kv get -field=password secret/staging/app/server/creds
```
### Using environment variables
[Section titled “Using environment variables”](#using-environment-variables)
There are three ways to invoke your environment variables and load them into a terminal session:
1. [Click to load into a current section](/knowledge-and-collaboration/warp-drive/environment-variables/#click-to-load-into-a-current-session)
2. [Click to load into a subshell](/knowledge-and-collaboration/warp-drive/environment-variables/#click-to-load-into-a-subshell)
3. [Select to load in with a workflow](/knowledge-and-collaboration/warp-drive/environment-variables/#select-to-load-with-a-workflow)
#### Click to load into a current session
[Section titled “Click to load into a current session”](#click-to-load-into-a-current-session)
First, click your environment variable from Warp Drive or the Command Palette.
Then, review the confirmation block. If your environment variables are correct, hit enter to load them into your session.


These environment variables will now be present for the remainder of your session.
#### Click to load into a subshell
[Section titled “Click to load into a subshell”](#click-to-load-into-a-subshell)
To load environment variables into a subshell, you will need to open [Warp Drive](/knowledge-and-collaboration/warp-drive/) and locate your environment variable in the Warp Drive index. You can then use the overflow menu to select “Load in subshell.”
Loading an environment into a subshell reduces the risk of your environment variables accidentally contaminating your workspace. The subshell is clearly defined and once you exit it, any environment variables set by Warp Environment Variables will be cleared, unless they are already present in the parent session.
#### Select to load with a workflow
[Section titled “Select to load with a workflow”](#select-to-load-with-a-workflow)
Any time you run a workflow, you can select from existing environment variables. This allows you to dynamically inject environment variables into a parameterized workflow so you can use a single workflow command in multiple environments, such as production and staging.
For example, you may have a workflow to create a new team that uses the environment variable $SERVER\_URL. By using the environment variables dropdown in the workflow card, you can dynamically inject the necessary variables. This ensures the workflow references the appropriate values so the command runs with the relevant environment-specific information.
These environment variables will now be present for the remainder of your session until you clear them or overwrite them with a different environment.
### Import and export environment variables in Warp Drive
[Section titled “Import and export environment variables in Warp Drive”](#import-and-export-environment-variables-in-warp-drive)
See our [Warp Drive Import and Export](/knowledge-and-collaboration/warp-drive/#import-and-export) instructions.
# Warp Drive Notebooks
Canonical page: [/knowledge-and-collaboration/warp-drive/notebooks/](https://docs.warp.dev/knowledge-and-collaboration/warp-drive/notebooks/)
> Save interactive playbooks to simplify onboarding and development.
Notebooks are interactive, runnable documents in Warp Drive that combine markdown text with executable shell command blocks. Use them for onboarding playbooks, debugging runbooks, and development workflows that teammates can search, share, and execute directly from the terminal.
### What is a Notebook?
[Section titled “What is a Notebook?”](#what-is-a-notebook)
Notebooks are runnable documentation consisting of markdown text and list elements, code blocks, and runnable shell snippets that can be automatically executed in your terminal session. Notebooks are searchable and accessible through the [Command Palette](/terminal/command-palette/) so you can access and run your documentation without ever leaving the terminal. You can also export Notebooks in .md format at any time.
### How to save and edit notebooks
[Section titled “How to save and edit notebooks”](#how-to-save-and-edit-notebooks)
You can create a new notebook from various entry points in Warp
* macOS
* From Warp Drive, + > New notebook
* From the [Command Palette](/terminal/command-palette/), create a new team or personal notebook.
* Windows
* From Warp Drive, + > New notebook
* From the [Command Palette](/terminal/command-palette/), create a new team or personal notebook.
* Linux
* From Warp Drive, + > New notebook
* From the [Command Palette](/terminal/command-palette/), create a new team or personal notebook.
Any of these entry points will open the notebook editor where you can:
* Title your notebook.
* Start adding text and code elements.
Note
The notebook will not be saved until either title or body text is added.
Editing a Notebook.
### Working with Notebooks
[Section titled “Working with Notebooks”](#working-with-notebooks)
#### Adding new elements
[Section titled “Adding new elements”](#adding-new-elements)
Notebook elements (text, code, list items) can be added in several ways:
* Using the appropriate markdown shortcut (e.g. ### for Heading 3).
* Typing /, which will open up a selection menu of supported elements.
* Pressing the + icon which appears when hovering over a line and selecting from the menu of supported elements.

Available Markdown element types in the Notebook editor.
#### Styling existing elements
[Section titled “Styling existing elements”](#styling-existing-elements)
Existing notebook elements can be styled in several ways:
* Selecting an existing element and selecting text decorations (like bold, italics, or inline code) from the hover menu.
* Using markdown syntax for text stylings like \*\*bold\*\* or \*italic\*.
* Selecting an existing element and changing the overall type of the element via the dropdown element menu.

#### Using command and code blocks
[Section titled “Using command and code blocks”](#using-command-and-code-blocks)
Command and code blocks have several unique properties such as syntax highlighting and quick actions that make working with code-based documentation simple. You can create a code or command block by either:
* Selecting Command or Code from the new element menu
* Typing ` ``` ` (triple backticks)
Once you’ve inserted your code block you can select the language at the bottom of the block from numerous options which will apply the appropriate syntax highlighting if available (or default to Code if your language is not found). All code and command blocks will apply syntax highlighting and provide a quick copy button for easy access.

A code block with syntax highlighting in a Notebook.
#### Special properties of command blocks
[Section titled “Special properties of command blocks”](#special-properties-of-command-blocks)
If you insert a Command block or specify the language as “Shell”, Warp provides extra functionality to simplify terminal work.
#### Executing command blocks
[Section titled “Executing command blocks”](#executing-command-blocks)
Developers can execute shell command blocks by:
* macOS
* Using the insert button at the bottom of the block
* Pressing `⌘+Enter` while the block is selected (a blue highlight will appear)
* Windows
* Using the insert button at the bottom of the block
* Pressing `Ctrl+Enter` while the block is selected (a blue highlight will appear)
* Linux
* Using the insert button at the bottom of the block
* Pressing `Ctrl+Enter` while the block is selected (a blue highlight will appear)
The command text will be inserted into the developer’s active terminal session, or a new session if none are active.

The run button on a command block in a Notebook.
#### Adding arguments to command blocks
[Section titled “Adding arguments to command blocks”](#adding-arguments-to-command-blocks)
Command blocks accept parameters in the same format as [Workflows](/knowledge-and-collaboration/warp-drive/workflows/). To add an argument to your command block, use `{{double_curly_brackets}}` to specify your argument term.

A command block with editable parameters.
#### Navigating command blocks with the keyboard
[Section titled “Navigating command blocks with the keyboard”](#navigating-command-blocks-with-the-keyboard)
Command Blocks also support keyboard navigation. There are two ways to enter the keyboard navigation mode:
* macOS
* Clicking on a shell block.
* Pressing `⌘+↑` or `⌘+↓.`
Once a command block is selected, press `⌘+Enter` to insert it into the terminal input. You can also use `↑, ↓, ⌘+↑`, and `⌘+↓` to navigate between command blocks. While the Notebook is focused, press `⌘+L` to switch focus back to the terminal without inserting a command.
* Windows
* Clicking on a shell block.
* Pressing `Ctrl+↑` or `Ctrl+↓.`
Once a command block is selected, press `Ctrl+Enter` to insert it into the terminal input. You can also use `↑, ↓, Ctrl+↑,` and `Ctrl+↓` to navigate between command blocks. While the Notebook is focused, press `Ctrl+L` to switch focus back to the terminal without inserting a command.
* Linux
* Clicking on a shell block.
* Pressing `Ctrl+↑` or `Ctrl+↓.`
Once a command block is selected, press `Ctrl+Enter` to insert it into the terminal input. You can also use `↑, ↓, Ctrl+↑,` and `Ctrl+↓` to navigate between command blocks. While the Notebook is focused, press `Ctrl+L` to switch focus back to the terminal without inserting a command.
#### Adding existing Workflows to notebooks
[Section titled “Adding existing Workflows to notebooks”](#adding-existing-workflows-to-notebooks)
If you have existing [Workflows](/knowledge-and-collaboration/warp-drive/workflows/) that you’d like to insert into your notebook rather than duplicating their content, you can select Embedded Workflow from the new element menu and select from the available Workflows. Once embedded in a notebook, the workflow will be executable like a regular command block. To edit the content of the embedded workflow, you will need to edit the source workflow which can be found by searching for the title in the [Command Palette](/terminal/command-palette/).

Embedding an existing workflow in a notebook.
### Working with Notebooks in a team
[Section titled “Working with Notebooks in a team”](#working-with-notebooks-in-a-team)
If the notebook is shared with a team, all team members will have access to edit the notebook and updates will sync immediately for all members of the team.
Note
Only one editor is allowed at a given time. Opening the notebook while there is an active editor will open the notebook in Viewing mode. Your mode (view vs edit) can be toggled above the notebook’s title.

A Notebook displayed in view mode.
### Import and export notebooks in Warp Drive
[Section titled “Import and export notebooks in Warp Drive”](#import-and-export-notebooks-in-warp-drive)
See our [Warp Drive Import and Export](/knowledge-and-collaboration/warp-drive/#import-and-export) instructions.
# Warp Drive prompts
Canonical page: [/knowledge-and-collaboration/warp-drive/prompts/](https://docs.warp.dev/knowledge-and-collaboration/warp-drive/prompts/)
> Save and reuse parameterized Agent Mode prompts to run on-demand.
Prompts are parameterized natural language queries you can save in Warp Drive and reuse with agents. Name a prompt, add arguments for dynamic values, and execute it from the Command Palette or Warp Drive to repeat complex agent workflows without retyping.
## What is a prompt?
[Section titled “What is a prompt?”](#what-is-a-prompt)
A prompt is a parameterized natural language query you can name and save in Warp to use with [Agent Mode](/agents/local-agents/interacting-with-agents/).
Prompts are searchable and easily accessed from the [Command Palette](/terminal/command-palette/) so you can find and execute them without switching context. They allow you to save and reuse specific and complex AI workflows, making it easier to repeat multi-step tasks with Agent Mode.

Command view of a Prompt in Warp Drive.
### Demo: Trigger reusable actions with saved prompts
[Section titled “Demo: Trigger reusable actions with saved prompts”](#demo-trigger-reusable-actions-with-saved-prompts)
Here’s an example from [Warp Guides](/guides/), where Zach walks through what prompts he uses for PRs and Git commits:

There are other great examples of prompts on [Warp Guides](/guides/).
## How to save and edit prompts
[Section titled “How to save and edit prompts”](#how-to-save-and-edit-prompts)
You can create a new prompt from Warp Drive by clicking the + button and selecting “Prompt”.
* Name your prompt
* Edit the natural language query along with any arguments (also known as parameters)
* Add a meaningful description that will be indexed for search (optional)
* Add arguments, descriptions for arguments, and default values (optional)

Edit view of a Prompt in Warp Drive.
Once a prompt has been created, you can edit it at any time, as long as you have access to an internet connection.
### Working with arguments
[Section titled “Working with arguments”](#working-with-arguments)
In the prompt editor, you can add arguments manually with “New argument” or by typing in double curly braces (`{{argument}}`) within the command field. If you select “New argument” while you have text selected, Warp will wrap that text in curly braces to create an argument.
There are some rules for creating valid arguments:
* Argument names can only include characters `A-Za-z0-9`, hyphens `-` and underscores `_`
* The first character of an argument cannot be a number
Arguments can be one of two types: text or enum. By default, all new arguments are text type.
#### Enum type arguments
[Section titled “Enum type arguments”](#enum-type-arguments)
Enums allow you to specify expected inputs to a prompt argument. When you insert a prompt with enums into the input editor, you will be prompted with suggestions for filling in the argument. You can open the suggestions menu by pressing `Shift+Tab` while selecting an argument.
For detailed information about creating and using enum type arguments, see the [Enum type arguments section in Workflows documentation](/knowledge-and-collaboration/warp-drive/workflows/#enum-type-arguments).
### Editing prompts with a team
[Section titled “Editing prompts with a team”](#editing-prompts-with-a-team)
If the prompt is shared with a team, all team members will have access to edit it and updates will sync immediately for all members of the team.
If a prompt in the Warp Drive has been edited by another team member or a user on another device while you are attempting to edit the same prompt, you will not be able to save changes; you will need to check out the latest version and try again.
## How to execute prompts
[Section titled “How to execute prompts”](#how-to-execute-prompts)
You can execute a prompt in several ways:
* From Warp Drive, click the prompt
* From the [Command Palette](/terminal/command-palette/) or [Command Search](/terminal/entry/command-search/), search for a prompt by name or type “prompts:” to see all available prompts and your prompt history
* When a prompt is selected, you can use `Shift+Tab` to cycle through the arguments.

Searching for Prompts in the Command Palette.

Searching for Prompts in Command Search.
These options will paste the prompt into your active terminal input. Prompt names and any relevant descriptions and arguments will be displayed in a dialog, so you can understand how to use the prompt.
You can make any adjustments you need to the arguments before running the prompt in your input editor.
### Import and export prompts in Warp Drive
[Section titled “Import and export prompts in Warp Drive”](#import-and-export-prompts-in-warp-drive)
See our [Warp Drive Import and Export](/knowledge-and-collaboration/warp-drive/#import-and-export) instructions.
# Warp Drive on the web
Canonical page: [/knowledge-and-collaboration/warp-drive/web/](https://docs.warp.dev/knowledge-and-collaboration/warp-drive/web/)
> Access your Warp Drive objects and shared sessions from any browser or touch screen device, including mobile phones, tablets, and touch-enabled laptops.
Warp Drive on the web lets you view and edit Warp Drive objects and shared sessions directly in any browser, including mobile devices and tablets. Access Workflows, Notebooks, Prompts, and session transcripts from anywhere without installing the Warp desktop app.
## What is Warp on the web?
[Section titled “What is Warp on the web?”](#what-is-warp-on-the-web)
Warp Drive on the web lets you view and edit your Warp Drive objects and shared sessions directly in the browser, on any device.

A web-based rendering of a Team Workflow.
## How to access Warp on the web
[Section titled “How to access Warp on the web”](#how-to-access-warp-on-the-web)
Warp’s web-based viewing experience can currently be accessed via:
* The [Warp web app homepage](https://app.warp.dev/app)
* [Drive Object](/knowledge-and-collaboration/warp-drive/#sharing-your-drive-objects) Links
* [Session Sharing](/agents/local-agents/session-sharing/#who-can-access-a-shared-session) Links
Caution
You can edit and view web-based objects and sessions as normal. The one exception is executing a command from a workflow or notebook since there is no shell session running on the web.
## Managing your view preferences - web or desktop
[Section titled “Managing your view preferences - web or desktop”](#managing-your-view-preferences---web-or-desktop)
If the Warp app is installed, links will open on the desktop by default. You can manage whether Warp links open in Warp’s desktop app or the browser in multiple ways:
Note
The desktop option is only presented if Warp’s web service is able to detect the Warp app installed locally. Warp desktop opens localhost port 9277 to accomplish this detection. This is done in a separate process that does not have access to your terminal contents.\
\
If you would like to use Warp locally and do not have it installed, see our [installation guide.](/getting-started/quickstart/installation-and-setup/)
1. The first time you follow a link, if Warp is not installed, you will be prompted to download it. You can dismiss the popup to stay on the web.

2. This preference can be changed at any point in **Settings** > **Features** > **General** > **Open links in desktop app**. Note that this setting is only available while on the web-based version of Warp.

Setting managing how to open links.
3. You can always switch between web and desktop views on a case-by-case basis.
1. To switch from a web-view to Desktop for a given object, open the *overflow menu > Open link on Desktop.*

2. To stay on the web for a given object despite a global Desktop preference, follow the *View on the web* option that is part of the redirect screen to Desktop.

## Supported browsers
[Section titled “Supported browsers”](#supported-browsers)
Warp on the web supports all modern browsers, including:
**Desktop**
* Chrome
* Firefox
* Safari
**Mobile**
* iOS Safari 15+
* Android Chrome 58+
* Samsung Internet 7.2+
Note
These mobile browser versions are the minimum required for WebGL 2.0 support. Most up-to-date devices meet these requirements.
## Touch screen and mobile support
[Section titled “Touch screen and mobile support”](#touch-screen-and-mobile-support)
Warp supports all touch screen devices, including mobile phones, tablets, and touch-enabled laptops. Touch input works on both the web and the desktop app.
### Supported gestures
[Section titled “Supported gestures”](#supported-gestures)
* **Touch and scroll** - Vertical and horizontal scrolling work as expected
* **Double tap** - Select text or elements
* **Long press (hold)** - Open context menu (equivalent to right-click)
## Related features
[Section titled “Related features”](#related-features)
* [Warp Drive](/knowledge-and-collaboration/warp-drive/) - Store and share workflows, prompts, and environment variables
* [Session Sharing](/agents/local-agents/session-sharing/) - Collaborate with others in real-time terminal sessions
# Warp Drive Workflows
Canonical page: [/knowledge-and-collaboration/warp-drive/workflows/](https://docs.warp.dev/knowledge-and-collaboration/warp-drive/workflows/)
> Save parameterized commands as Workflows and execute them on-demand from Warp Drive.
Workflows are parameterized commands you can name, save, and share in Warp Drive. Define arguments with default values, add descriptions for search, and execute workflows from the Command Palette or Warp Drive to run frequently used commands without retyping them.
## What is a workflow?
[Section titled “What is a workflow?”](#what-is-a-workflow)
A workflow is a parameterized command you can name and save in Warp with descriptions and arguments. Workflows are searchable and easily accessed from the [Command Palette](/terminal/command-palette/) so you can find and execute them without switching contexts.
## How to save and edit workflows
[Section titled “How to save and edit workflows”](#how-to-save-and-edit-workflows)
You can create a new workflow from various entry points in Warp:
* From Warp Drive, + > New workflow
* Using Block Actions, Save as Workflow
* From agent results, Save as Workflow
* From the [Command Palette](/terminal/command-palette/), Create a New Personal Workflow
Any of these entry points will open the workflow editor where you can:
* Name your workflow
* Edit the command along with any arguments (also known as parameters)
* Add a meaningful description that will be indexed for search (optional)
* Add arguments, descriptions for arguments, and default values (optional)

Workflows save / edit pane.

### Working with arguments
[Section titled “Working with arguments”](#working-with-arguments)
In the workflow editor, you can add arguments manually with “New argument” or by typing in double curly braces (`{{argument}}`) within the command field. If you select “New argument” while you have text selected, Warp will wrap that text in curly braces to create an argument.
There are some rules for creating valid arguments:
* Argument names can only include characters `A-Za-z0-9`, hyphens `-` and underscores `_`
* The first character of an argument cannot be a number
Arguments can be one of two types: text or enum. By default, all new arguments are text type.
#### Enum type arguments
[Section titled “Enum type arguments”](#enum-type-arguments)
Enums allow you to specify expected inputs to a workflow argument. When you insert a workflow with enums into the input editor, you will be prompted with suggestions for filling in the argument. You can open the suggestions menu by pressing `Shift+Tab` while selecting an argument.
[Enum Input Suggestions Demo](https://www.loom.com/embed/b2f54eeef2f247a8bbcf87698b2a4287)
To create an enum type argument:
1. Navigate to the “default value” field of an argument.
2. Select the “Enum” type.
3. Click “New” to create a new enum, or select an existing one from the dropdown menu.
4. If you selected “New”, you can choose to create a “Static” enum or “Dynamic” enum. Dynamic enums are associated with a shell command whose output is parsed to determine the set of valid values for that argument.
[Enum Creation Demo](https://www.loom.com/embed/b429ab7f7014418e9591e505fd71af83)
### Working with aliases
[Section titled “Working with aliases”](#working-with-aliases)
Workflow aliases allow you to create personalized shortcuts and custom configurations for your frequently used workflows. These aliases provide enhanced flexibility in how you use and configure workflows. Aliases are personal to your account, not shared with everyone who has the workflow. If settings sync is enabled, they’ll be synced across devices logged in to your account. Aliases can set default values for each [argument](/knowledge-and-collaboration/warp-drive/workflows/#working-with-arguments), but don’t have to. Aliases can have [Environment Variables](/knowledge-and-collaboration/warp-drive/environment-variables/) associated with them.
Note
Workflow aliases are not compatible with [YAML Workflows](/terminal/entry/yaml-workflows/). They can only be used with Workflows created in [Warp Drive](/knowledge-and-collaboration/warp-drive/).
### Editing workflows
[Section titled “Editing workflows”](#editing-workflows)
Once a workflow has been created, you can edit it at any time, as long as you have access to an internet connection.

The edit menu for a Workflow in Warp Drive.
#### AI autofill
[Section titled “AI autofill”](#ai-autofill)
Workflows also have the option to use an [agent](/agents/) to automatically generate a title, descriptions, or parameters.
* Create or edit a Workflow, in the edit view you should see the option to AutoFill.
* Warp will fill in the fields based on the Workflow you’re creating.
[](/assets/terminal/Edit-workflows-autofill.mp4)
### Editing workflows with a team
[Section titled “Editing workflows with a team”](#editing-workflows-with-a-team)
If the workflow is shared with a team, all team members will have access to edit the workflow and updates will sync immediately for all members of the team.
If a workflow in the Warp Drive has been edited by another team member or a user on another device while you are attempting to edit the same workflow, you will not be able to save changes; you will need to check out the latest version and try again.
## How to execute workflows
[Section titled “How to execute workflows”](#how-to-execute-workflows)
You can execute a workflow in several ways:
* From Warp Drive, click the workflow
* From the [Command Palette](/terminal/command-palette/), search for a workflow you’d like to execute, click or select, and enter
* From [Command Search](/terminal/entry/command-search/), search for a workflow you’d like to execute, click or select, and enter.
* When a workflow is selected, you can use `Shift+Tab` to cycle through the arguments.
Note
When you create two or more arguments with the same name, Warp automatically selects and puts multiple cursors over the arguments in the input editor so they are synced.\
\
Also, tailor your Command Search experience by toggling off “Show Global Workflows” in **Settings** > **Features**. When disabled, your search will exclusively encompass YAML and Warp Drive Workflows.

Searching for Workflows in the Command Palette.
These options will paste the workflow into your active terminal input. Workflow names and any relevant descriptions and arguments will be displayed in a dialog, so you can understand how to use the workflow.

Executing a Workflow from Warp Drive.
You can make any adjustments you need to the arguments (or the command itself) before running the command in your input editor.

## Support for YAML Workflows
[Section titled “Support for YAML Workflows”](#support-for-yaml-workflows)
Warp will indefinitely support the [YAML Workflows](/terminal/entry/yaml-workflows/), which includes personal and community workflows sourced from an open-source repository.
If needed, you can continue to access your `.yaml` file workflows using [Command Search](/terminal/entry/command-search/) or the [Command Palette](/terminal/command-palette/). However, these file-based workflows will not be available to access, organize, or share in Warp Drive.
### Import and export workflows in Warp Drive
[Section titled “Import and export workflows in Warp Drive”](#import-and-export-workflows-in-warp-drive)
See our [Warp Drive Import and Export](/knowledge-and-collaboration/warp-drive/#import-and-export) instructions.
# Cloud agents overview
Canonical page: [/platform/](https://docs.warp.dev/platform/)
> Run background agents in the cloud from events, schedules, or integrations with team-wide observability.
Note
The `oz` CLI and the [Oz web app](https://oz.warp.dev) keep their current names. Use the [cloud agent documentation map](/platform/documentation-map/) to find standalone workflows, CLI tools, APIs, SDKs, and Warp Factories.
Cloud agents are autonomous, background agents that run on Warp’s cloud infrastructure or your own, triggered by system events, schedules, or integrations like Slack and GitHub. They execute tasks with full observability — every run is tracked, inspectable, and shareable across your team.
**New to cloud agents?** Start with the [Cloud agents quickstart](/platform/quickstart/) to run your first cloud agent in \~10 minutes.
For a standing, multi-stage workflow with named agents, automations, and measurement, use [Warp Factories](/factories/). The factory-specific setup and operations guidance complements this shared cloud-agent reference.
### Monitor, inspect, and share cloud agent runs
[Section titled “Monitor, inspect, and share cloud agent runs”](#monitor-inspect-and-share-cloud-agent-runs)
To understand what a cloud agent did, start from the [Agent Management Panel](/platform/managing-cloud-agents/) in the Warp app or the [Runs page in the Oz web app](/platform/oz-web-app/#runs). From there, you can find a run by source, status, trigger, or owner; open the run transcript; inspect the prompt, plan, commands, logs, and output; and share the session link with teammates for review.
For a full walkthrough, see [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/). If the run came from Slack, Linear, GitHub Actions, a schedule, the CLI, or the API, it still produces a reviewable cloud agent run record.

### What cloud agents are designed for
[Section titled “What cloud agents are designed for”](#what-cloud-agents-are-designed-for)
Cloud agents are designed for situations where:
* **You need agents to react to system events.**
* Examples include crashes, bug reports, [Slack interactions](/platform/integrations/slack/), cron timers, or CI steps.
* **You want observability into agent activity across a team or system.**
* This includes being able to see what ran, when it ran, what triggered it, what the agent did, and how teammates can review or share the result.
* **You need more parallelism than local execution typically allows.**
* For example, [multi-agent orchestration](/platform/orchestration/) can run many agent tasks concurrently in the cloud, shard a repo-wide task into multiple runs, or fan out the same task across multiple targets.
* **You want agents to operate continuously as part of engineering infrastructure.**
* This includes [scheduled maintenance tasks](/platform/triggers/scheduled-agents/) and integration-driven automation.

***
### What is a cloud agent run?
[Section titled “What is a cloud agent run?”](#what-is-a-cloud-agent-run)
A cloud agent run is represented as an agent task. A task is created when a trigger fires (for example a webhook event or schedule) or when a user starts a run explicitly.
Each task includes:
* **Inputs**: a prompt, and often additional context from the triggering system (for example a Slack message, PR metadata, or CI logs).
* **Execution context (optional)**: an [Environment](/platform/environments/) that defines the repo, image, and startup commands the agent should run with.
* **Lifecycle state**: created → running → completed / failed.
* **Persistent record**: status, metadata, and a session transcript that can be reviewed after the task completes, including the prompt, plan, commands, logs, outputs, and follow-up messages where available.
Note
If you are evaluating whether something should be a cloud agent, a good test is whether you can define:\
(1) what triggers it, (2) what context it needs, and (3) how the team will inspect or validate the output.
### How cloud agents work
[Section titled “How cloud agents work”](#how-cloud-agents-work)
Cloud agents run on the [Automation Platform](/platform/overview/), which provides the primitives for triggering work, orchestrating tasks, executing agents (optionally in environments), injecting secrets, and inspecting results.
* Something **triggers** an agent task.
* The **orchestrator creates** and tracks the task.
* The agent **executes** on a host, optionally inside an [environment](/platform/environments/), with whatever [secrets](/platform/secrets/) and credentials it needs.
The exact way tasks are triggered and executed depends on your deployment model. [Deployment patterns](/factories/deployment-patterns/) covers Warp-hosted and managed self-hosted execution for factories. For standalone agents, see [unmanaged execution](/platform/unmanaged-execution/).
For teams that need execution to stay within their network boundary, self-hosting supports two architectures: a **managed** worker daemon that lets the Automation Platform orchestrate agents in Docker containers on your machines, and an **unmanaged** mode where you run `oz agent run` directly in your CI, Kubernetes, or dev environment. See [Self-hosting](/factories/self-hosting/) for details.
### What you get by default
[Section titled “What you get by default”](#what-you-get-by-default)
Because cloud agents run on the [Automation Platform](/platform/overview/), each run is tracked and produces a persistent record that can be observed, shared, and reviewed (even if execution happens outside the Warp app).
#### Codebase Context
[Section titled “Codebase Context”](#codebase-context)
Cloud agent runs automatically benefit from [Codebase Context](/agents/capabilities/codebase-context/) for semantic code understanding and search, as long as Codebase Context is enabled for your account. See [Codebase Context in cloud agent runs](/agents/capabilities/codebase-context/#codebase-context-in-cloud-agent-runs) for details.
#### Observability and steerability
[Section titled “Observability and steerability”](#observability-and-steerability)
Cloud agent tasks are designed to be inspectable by the team:
* The [Agent Management Panel](/platform/managing-cloud-agents/) in the Warp app and the [Runs page in the Oz web app](/platform/oz-web-app/#runs) surface task status, source, trigger, creator, history, and credit usage.
* [Cloud agent session sharing](/platform/viewing-cloud-agent-runs/) opens the run transcript so teammates can inspect the prompt, plan, commands, logs, files changed, outputs, and follow-up messages where available.
* [Agent Session Sharing](/agents/local-agents/session-sharing/) lets authorized teammates share, monitor, and steer live local or third-party agent sessions.
#### Centralized configuration
[Section titled “Centralized configuration”](#centralized-configuration)
Cloud agent workflows often rely on shared configuration such as [MCP servers](/platform/mcp/), rules, saved prompts, environment variables, and [secrets](/platform/secrets/).
Warp supports centralized configuration so the same workflow behaves consistently across triggers (for example Slack + CI + schedules), without duplicating setup in every system.
For details on configuring MCP servers for cloud agents, see [MCP Servers](/platform/mcp/).
#### API access to tasks
[Section titled “API access to tasks”](#api-access-to-tasks)
The Automation Platform exposes task visibility via the [**Warp Platform API**](/factories/api-and-sdk/), so teams can:
* Query which tasks are running or have run.
* Fetch task metadata and outcomes.
* Build internal dashboards or monitoring (for example success rates, runtime, failure reasons).
### Using cloud agents with or without the Warp app
[Section titled “Using cloud agents with or without the Warp app”](#using-cloud-agents-with-or-without-the-warp-app)
Cloud agents do not require the Warp app. Teams can deploy and operate them through the [Automation Platform](/platform/overview/) using:
* [Oz CLI](/agents/cli/oz-cli/) — run agents from scripts, CI, or the terminal
* [Oz web app](/platform/oz-web-app/) — visual interface for managing runs, schedules, environments, and integrations (works on mobile)
* [Agent Session Sharing](/agents/local-agents/session-sharing/) — attach to running tasks to monitor or steer
* [Agent Management Panel](/platform/managing-cloud-agents/) — view agent activity and run history in the Warp app
* [APIs and SDKs](/factories/api-and-sdk/) — programmatic access for custom integrations
If your team also uses Warp’s terminal, you get an additional workflow: tasks launched via the CLI can be handed off into an interactive session for review, edits, or continuation.
***
### Billing and plan requirements
[Section titled “Billing and plan requirements”](#billing-and-plan-requirements)
Cloud agents and [integrations](/platform/integrations/) run on the [Automation Platform](/platform/overview/) control plane, and usage is billed using credits.
Note
[Bring Your Own API Key (BYOK)](/agents/inference/bring-your-own-api-key/) is not supported for cloud agent runs. BYOK keys are stored locally on your device and are not accessible to cloud-hosted agents. All cloud agent runs consume Warp credits.
#### For cloud agents via CLI/API
[Section titled “For cloud agents via CLI/API”](#for-cloud-agents-via-cliapi)
Individual users can run cloud agents without being on a team. Requirements:
* You need at least 20 credits available
* Cloud agents run on Warp-hosted infrastructure
* Self-hosted agents require a team subscription
#### For integrations (Slack/Linear)
[Section titled “For integrations (Slack/Linear)”](#for-integrations-slacklinear)
Integrations require you to be part of a [Warp team](/knowledge-and-collaboration/teams/) and additional requirements:
* **Plan requirements**
* **Supported plans**: Build, Max, Business
* Your plan must support add-on credits.
* **Credit requirements**
* Your team must have at least 20 credits available to run cloud agents and integrations.
For more details, see [Access, Billing, and Identity Permissions](/platform/team-access-billing-and-identity/).
Caution
If your credit balance reaches zero, cloud agent runs will not be able to execute until credits are replenished.
***
### Learn more
[Section titled “Learn more”](#learn-more)
* [Cloud agents quickstart](/platform/quickstart/) — run your first cloud agent with an environment in \~10 minutes.
* [Automation Platform](/platform/overview/) — CLI, Warp Platform API, orchestration, tasks, environments, hosts, integrations, and more.
* [Warp Factories](/factories/) — assemble cloud agents into a standing triage-to-merge workflow with named agents, automations, and measurement.
* [Harnesses](/platform/harnesses/) — pick between Warp Agent, Claude Code, and Codex for any cloud agent run.
* [Agents](/platform/agents/) — cloud agents that own and execute runs on your team.
* [Multi-agent orchestration](/platform/orchestration/) — coordinate a parent agent and its child agents across local and cloud runs to build supervisor/worker, fan-out, critic, DAG, and swarm workflows.
* [Skills as Agents](/platform/skills-as-agents/) — run agents based on reusable skill definitions from the CLI, web app, API, or on a schedule.
* [Oz CLI](/agents/cli/oz-cli/) — shows how to run agents in non-interactive mode from CI, scripts, or remote machines, including auth and common commands.
* [Environments](/platform/environments/) — explains how environments provide the runtime context (repo, image, startup commands) for agent tasks.
* [Warp Platform API](/factories/api-and-sdk/) — documents the REST API for creating, querying, and monitoring agent tasks programmatically.
* [Agent Secrets](/platform/secrets/) — covers how to store, scope, and inject credentials into agent runs safely.
* [MCP Servers](/platform/mcp/) — how to configure MCP servers for agent tool access and how MCP configuration is applied across runs.
* [Deployment Patterns](/factories/deployment-patterns/) (beta) — compares common ways to deploy cloud agents and when to use each.
* [Access, Billing, and Identity Permissions](/platform/team-access-billing-and-identity/) — explains individual and team-level requirements, credit billing behavior, and the permission model for who can run, view, and steer cloud agent tasks.
# Cloud agent accounts
Canonical page: [/platform/agents/](https://docs.warp.dev/platform/agents/)
> Cloud agents are how Warp runs scheduled jobs, integration triggers, CI/CD automation, and API-driven tasks against your team's environments.
A **cloud agent** is an agent that runs in Warp’s cloud (or on a self-hosted worker) instead of on your local machine. Use a cloud agent when you want to give an automation its own settings, secrets, skills, and permissions instead of having it act as a user on your team.
Every team starts with a default cloud agent, which is what runs when an automation triggers a task with no other configuration. You can optionally create additional cloud agents through the Oz web app‘s **Agents** page or the public API. See [Managing cloud agents](#managing-cloud-agents) below.
## How cloud agents get triggered
[Section titled “How cloud agents get triggered”](#how-cloud-agents-get-triggered)
A run executes as a cloud agent when it’s authenticated with an [agent API key](/agents/cli/oz-cli/api-keys/) or when an agent is explicitly selected; otherwise it runs as the calling user. The triggers that can run as a cloud agent are:
* **Schedules** — Cron-style recurring runs. See [Scheduled agents](/platform/triggers/scheduled-agents/).
* **Integrations** — Slack mentions, Linear issue updates, GitHub Actions workflow steps. See [Integrations](/platform/integrations/).
* **API and SDK** — Programmatic runs from your own backend, scripts, or webhooks via the [Warp Platform API](/factories/api-and-sdk/).
* **CLI** — `oz agent run-cloud` from a developer machine, CI pipeline, or self-hosted worker. See the [Oz CLI](/agents/cli/oz-cli/).
Each run is tracked in the [cloud agent dashboard](https://oz.warp.dev/runs) with its trigger source, the environment it ran in, and the full transcript.
## Agent API keys
[Section titled “Agent API keys”](#agent-api-keys)
Most automation triggers authenticate using an **agent API key** — a credential that runs as a cloud agent on your team rather than as an individual user. See [API keys](/agents/cli/oz-cli/api-keys/) for how personal and agent keys differ, and how to create one.
## Service accounts
[Section titled “Service accounts”](#service-accounts)
In the CLI and REST API, a cloud agent is represented as a **service account**. `oz whoami` reports `service_account:<uid>` when the CLI is authenticated as a service account, and [`oz federate issue-token`](/agents/cli/oz-cli/federate/) emits the same form in OIDC token subjects.
## Managing cloud agents
[Section titled “Managing cloud agents”](#managing-cloud-agents)
Use the [Oz web app‘s Agents page](/platform/oz-web-app/#agents) for day-to-day management. Use the public API when you need to create or update agents from scripts, CI/CD, or internal tooling. Full request and response formats, including error codes, live on the [API Reference](/api) page under the **agent** tag.
| Action | Endpoint | What it does |
| ---------- | -------------------------------- | ------------------------------------------------------------------------------------------------------------- |
| **Create** | `POST /agent/identities` | Creates a cloud agent with a `name` and optional `description`, `secrets`, and `skills`. |
| **List** | `GET /agent/identities` | Returns every cloud agent on the team, including the default, with an `available` flag for plan-limit status. |
| **Update** | `PUT /agent/identities/{uid}` | Replaces individual fields. Omitted fields stay unchanged; empty strings or arrays clear the field. |
| **Delete** | `DELETE /agent/identities/{uid}` | Soft-deletes the agent and deletes every API key bound to it. The team’s default agent cannot be deleted. |
### Caller requirements
[Section titled “Caller requirements”](#caller-requirements)
Across all endpoints:
* **Human callers only** - Only human users can create, update, or delete a cloud agent. A request authenticated as a cloud agent itself is rejected.
* **Availability is enforced on use** - Over-plan-limit agents are returned by the list endpoint but cannot be used to update fields, generate new keys, or start new runs.
## Plan limits
[Section titled “Plan limits”](#plan-limits)
Every team starts with a default cloud agent. Additional agents are subject to plan-based limits. See [Warp pricing](https://www.warp.dev/pricing) for current limits per plan.
When a team is over its plan limit (for example, after downgrading), the extra agents remain visible in the list but are marked as unavailable. Unavailable agents cannot be used to start runs, cannot have new API keys generated for them, and cannot be edited.
## Where cloud agents appear in the product
[Section titled “Where cloud agents appear in the product”](#where-cloud-agents-appear-in-the-product)
* **Agents page** - The Agents page in the [Oz web app](/platform/oz-web-app/) is where teams view, create, edit, and delete cloud agents.
* **Agent picker** - Forms that start a new run or schedule include an **Agent** dropdown. **Quick run** is the default: runs execute as the calling user, and pull requests are authored by that person. Picking a cloud agent runs as that agent instead, so with [team GitHub authorization](/platform/team-access-billing-and-identity/#team-github-authorization) configured, pull requests are authored by the **Warp Factories** GitHub App. Choose a cloud agent for any schedule that opens pull requests. See [Run identity and pull request authorship](/platform/triggers/scheduled-agents-quickstart/#run-identity-and-pull-request-authorship).
* **Run filters and detail** - The Runs view lets you filter by cloud agent, and individual run detail pages show which agent executed the run.
* **Admin Panel** - Billing usage in the [Admin Panel](/knowledge-and-collaboration/admin-panel/) attributes credits consumed by cloud agent runs to the team rather than to a person.
## Capabilities
[Section titled “Capabilities”](#capabilities)
Cloud agents — and individual runs — can also be granted specific capabilities:
* [**Skills as agents**](/platform/skills-as-agents/) - Attach a skill directly to a cloud agent, or pass one at run time, so the agent starts from a reusable, version-controlled prompt instead of an ad hoc one.
* [**MCP servers**](/platform/mcp/) - Connect a run to external tools and services (GitHub, dbt, Sentry, or a custom internal service) via Model Context Protocol.
* [**Secrets**](/platform/secrets/) - Store and inject credentials into cloud agent runs without exposing secret values, scoped to a team, a person, or a specific cloud agent.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Triggers](/platform/triggers/) - How schedules, integrations, and API calls invoke cloud agents.
* [Environments](/platform/environments/) - The runtime context (Docker image, repos, setup commands) a cloud agent uses.
* [Multi-agent orchestration](/platform/orchestration/) - Coordinate a parent cloud agent and its children across local and cloud runs.
* [Warp Factories](/factories/) - Assemble named cloud agents into a standing triage-to-merge workflow.
* [API keys](/agents/cli/oz-cli/api-keys/) - Create personal and agent API keys.
* [Warp Platform API](/factories/api-and-sdk/) - Programmatic access to the cloud agent endpoints.
* [Federated identity tokens](/agents/cli/oz-cli/federate/) - Issue OIDC tokens from inside a run.
* [Oz web app](/platform/oz-web-app/) - Manage cloud agents and inspect their runs in the web UI.
* [Admin Panel](/knowledge-and-collaboration/admin-panel/) - Team-level billing and access controls.
# Platform architecture
Canonical page: [/platform/architecture/](https://docs.warp.dev/platform/architecture/)
> Reference diagrams of the Warp stack, the cloud agent run lifecycle, self-hosted execution, and data boundaries.
The Automation Platform connects the tools that start agent work with the environments where that work runs. Warp operates the control plane, which coordinates runs and routes inference. Cloud agent runs execute in a Warp-hosted sandbox or on customer infrastructure. [Managed self-hosting](/factories/self-hosting/) and [Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/) change where specific work happens.
## Stack overview
[Section titled “Stack overview”](#stack-overview)
The platform has five layers: clients, the Warp-operated control plane that coordinates runs, the data plane that stores run data, the execution plane where agents access code and run tools, and external systems that agents read from and write to.

* **Clients** - The surfaces that start and observe work, like the Warp app, the Oz CLI, the web app, the [factory dashboard](/factories/factory-dashboard/), and clients connected through the [Factory MCP](/factories/factory-mcp/). All clients talk to the same control plane APIs.
* **APIs** - The control plane’s entry points: the [Warp Platform API and SDKs](/factories/developer-tools/), a webhook receiver for [integration](/platform/integrations/) events, and the hosted Factory MCP endpoint.
* **Control plane** - Warp coordinates runs, manages shared configuration, routes model calls, and records run history.
* **Data plane** - Run data (transcripts, artifacts, and attachments) lives in Warp-managed storage, independent of where runs execute.
* **Warp-hosted execution** - By default, each cloud agent run gets an isolated sandbox prepared from its environment. See [Warp-hosted execution](/factories/warp-hosting/).
* **Self-hosted execution** - On Enterprise, a managed worker runs tasks on your infrastructure. Unmanaged setups run the Oz CLI in your CI or orchestrator. See [Managed self-hosting](/factories/self-hosting/) and [unmanaged execution](/platform/unmanaged-execution/).
* **External systems** - The platform connects to identity providers, source control, integration providers, model providers, and a payment provider.
## Cloud agent run lifecycle
[Section titled “Cloud agent run lifecycle”](#cloud-agent-run-lifecycle)
Every cloud agent run follows the same lifecycle, no matter what started it or where it executes. A trigger creates a task, the control plane resolves its configuration and dispatches it to an execution host, the agent works in a loop until it’s done, and the run leaves durable records behind.

1. **A trigger fires** - A [schedule](/platform/triggers/scheduled-agents/), an [integration](/platform/integrations/) event, an [API or SDK](/factories/api-and-sdk/) call, a CLI command, or a [Handoff](/platform/handoff/) from the Warp app starts the run.
2. **The task is created** - The control plane opens a run record that tracks the task’s state, inputs, and provenance.
3. **Configuration is resolved** - The platform picks the run’s [environment](/platform/environments/), [runner](/factories/runners/), execution host, and [model and harness](/platform/harnesses/).
4. **The sandbox is provisioned** - The execution host clones the environment’s repositories, runs setup commands, and injects only the [secrets](/platform/secrets/) the run is allowed to use.
5. **The agent loop runs** - The harness gathers context, calls the model, and runs tools until the task is done. Tools run in the sandbox. With the Warp Agent, model calls route through Warp to providers under [Zero Data Retention](/enterprise/security-and-compliance/security-overview/#zero-data-retention-zdr); Claude Code and Codex call their provider directly.
6. **Outputs land at their targets** - The agent pushes branches, opens pull requests, and replies to the Slack thread, Linear issue, or Jira work item that started the task.
7. **The run record persists** - Transcripts, artifacts, and cost data attach to the run record.
8. **The team has visibility** - Authorized users follow the run in the cloud agent dashboard or attach to it with [Agent Session Sharing](/agents/local-agents/session-sharing/).
9. **The sandbox tears down** - When snapshotting is enabled, the platform captures workspace changes for a later [Handoff](/platform/handoff/), then destroys the sandbox.
During the run, prompts and code context, command and tool outputs, MCP tool calls and results, transcripts and run status, and model requests and responses pass through the control plane for session management and inference.
Self-hosted runs follow the same lifecycle; steps 4 through 6 execute on your managed worker instead of a Warp-hosted sandbox. See [Self-hosted execution flow](#self-hosted-execution-flow) for that variant.
### Sequence view
[Section titled “Sequence view”](#sequence-view)
This sequence diagram shows the requests and responses exchanged among a trigger, a per-run sandbox, the Warp control plane, and external providers during a cloud agent run.

## Self-hosted execution flow
[Section titled “Self-hosted execution flow”](#self-hosted-execution-flow)
Self-hosted execution keeps checkout, commands, and the workspace on your infrastructure while the Automation Platform keeps orchestrating, observing, and routing inference. A worker daemon dials out to Warp, so no inbound firewall ports are needed, and executes tasks locally. The numbers in the diagram mark the route.

1. **The worker connects** - You run the managed worker (`oz-agent-worker`) on your infrastructure. It authenticates with an agent API key and holds an outbound-only connection, waiting for tasks routed to its [`--host` ID](/factories/self-hosting/#routing-runs-to-self-hosted-workers).
2. **Warp assigns the task** - When a trigger targets your worker, the control plane sends the task, its resolved configuration, and scoped runtime credentials over that connection.
3. **The agent runs on your backend** - The worker clones repositories, runs setup, injects allowed [secrets](/platform/secrets/), and executes in a Docker container, a Kubernetes Job, or directly on the host, depending on the [managed backend](/factories/self-hosting/#managed-architecture) you chose. Code, build artifacts, and workspaces stay on your machines.
4. **Run data returns to Warp** - Status, transcripts, artifacts, attachments, and telemetry flow back for the run record. Content the agent puts into prompts or results can include code context; see [execution security](/platform/execution-security/).
5. **Warp routes inference** - With the Warp Agent, model calls go from your worker through Warp to LLM providers under [Zero Data Retention](/enterprise/security-and-compliance/security-overview/#zero-data-retention-zdr), or through your own provider account with [team-managed keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) or [Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/). Claude Code and Codex call their provider directly from your infrastructure.
6. **Your team monitors the run** - Runs on self-hosted workers appear in the cloud agent dashboard and support [Agent Session Sharing](/agents/local-agents/session-sharing/), the same as Warp-hosted runs.
### Self-hosted sequence view
[Section titled “Self-hosted sequence view”](#self-hosted-sequence-view)
This sequence diagram shows the requests and responses exchanged among a trigger, your worker and sandbox, the Warp control plane, and external providers during a self-hosted run.

1. **Create task** - A trigger fires: an integration event, a schedule, an API or SDK call, a CLI command, or a Handoff.
2. **Assign task** - The control plane delivers the task over the worker’s authenticated connection, with resolved configuration and scoped runtime credentials.
3. **Prepare workspace** - The worker clones repositories, runs setup commands, and injects allowed secrets.
4. **Prompt and context** - The agent gathers context inside the sandbox and sends it for inference.
5. **Inference** - Model calls from the Warp Agent route through Warp to LLM providers under ZDR, or through your own provider account with team-managed keys and endpoints or Bring Your Own LLM.
6. **Run tools** - Tool calls execute locally: files, commands, internal services, and MCP servers.
7. **Results** - Transcripts, tool outputs, and lifecycle updates return to the run record.
8. **Outputs** - The agent pushes a branch, opens a pull request, and replies to the integration that started the run.
9. **Observability** - Your team follows and steers the run from the cloud agent dashboard and shared sessions.
## Warp Factories work-item flow
[Section titled “Warp Factories work-item flow”](#warp-factories-work-item-flow)
A software factory assembles the Automation Platform‘s primitives — runs, environments, runners, integrations, and secrets — into one measurable workflow. Work enters from the tools your team already uses, a foreman coordinates specialized agents through the stages each work item needs, and a human makes the final call.

[How Warp Factories work](/factories/how-factories-work/) explains each component in the diagram and how a work item moves through the stages.
## Data security and boundaries
[Section titled “Data security and boundaries”](#data-security-and-boundaries)
Every run moves a few distinct classes of data, and each class has its own boundary. This section maps them across your infrastructure, the Warp platform, model providers, and the data plane where run data is stored. All communication is encrypted in transit (TLS 1.2+), all stored data is encrypted at rest (AES-256), and known secret values are redacted at output boundaries.

* **Source code** - For Warp-hosted runs, repositories are cloned into an isolated per-run sandbox and destroyed with it; Warp does not persistently store repository clones or train on your code. For [managed self-hosting](/factories/self-hosting/), checkout and the workspace stay on your infrastructure. Either way, code context the agent puts into prompts, transcripts, or artifacts transits Warp and may persist as run data.
* **Prompts and context** - With the Warp Agent, model calls route through Warp to LLM providers under [Zero Data Retention](/enterprise/security-and-compliance/security-overview/#zero-data-retention-zdr) agreements: providers don’t retain or train on the traffic. [Team-managed keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) and [Bring Your Own LLM](/enterprise/enterprise-features/bring-your-own-llm/) keep the same route but use your provider account. Claude Code and Codex call their provider directly from the execution environment, under your provider agreement rather than Warp’s.
* **Run data** - Transcripts, artifacts, and run attachments are stored in Warp-managed storage, encrypted at rest and access-controlled by your team’s roles.
* **Control-plane data** - Warp always retains what it needs to operate the platform: user and organization settings, agent and factory configuration, orchestration and lifecycle metadata, trigger and integration metadata, operational logs, and usage and billing.
* **Execution secrets** - Secrets you inject locally never transit Warp. [Managed secrets](/platform/secrets/) are stored encrypted and fetched just-in-time by the execution environment with a run-scoped token, and each delivery is audit-logged. Agents can also obtain short-lived cloud credentials at runtime through [workload identity federation](/platform/integrations/cloud-providers/) instead of holding long-lived secrets. [Secret redaction](/support-and-community/privacy-and-security/secret-redaction/) at output boundaries is a backstop, not a substitute for narrow scopes and rotation.
* **Inference credentials** - With the Warp Agent, team-managed keys, and Bring Your Own LLM, provider credentials are used only at the Warp–provider boundary and never enter the sandbox. Claude Code and Codex use your provider credentials inside the execution environment, delivered as managed secrets or injected locally.
* **MCP credentials** - URL-backed MCP servers, including OAuth-connected servers, use Warp’s proxy. Command-based servers connect from the execution environment. Credentials for proxied servers stay with Warp; command-based connections use local or managed secrets in the execution environment.
* **Repository identity** - User-triggered cloud agent runs use the triggering user’s personal GitHub token. Agent API key runs with [Team GitHub authorization](/platform/team-access-billing-and-identity/#team-github-authorization) and runs started by the GitHub integration act as the Warp Factories GitHub App. Factory runs act with the creating user’s authorization or as the agent itself, depending on the configured [credential strategy](/factories/factory-as-code/#credentialstrategy). Branch protection and repository permissions apply as usual.
### With self-hosted execution
[Section titled “With self-hosted execution”](#with-self-hosted-execution)
[Managed self-hosting](/factories/self-hosting/) moves the execution boundary: checkout, builds, and command execution stay on your infrastructure, and no Warp-hosted sandbox is involved. The control plane still coordinates runs, holds control-plane data, routes inference for the Warp Agent, and stores run data.

## Related pages
[Section titled “Related pages”](#related-pages)
* [Deployment patterns](/factories/deployment-patterns/) - Choose Warp-hosted or managed self-hosted execution for a factory.
* [Managed self-hosting](/factories/self-hosting/) - Configure a managed worker for factory execution.
* [Execution security](/platform/execution-security/) - The data model and egress requirements for self-hosted workers.
* [Security overview](/enterprise/security-and-compliance/security-overview/) - Warp’s data handling, encryption, and compliance posture.
* [How Warp Factories work](/factories/how-factories-work/) - The work-item lifecycle in depth.
* [Warp Factories infrastructure and security](/factories/infrastructure-and-security/) - The same boundaries applied to factories.
# Self-hosted agent data storage
Canonical page: [/platform/data-storage/](https://docs.warp.dev/platform/data-storage/)
> Route agent transcripts, artifacts, and prompt attachments to your own cloud storage.
Self-hosted agent data storage lets your team keep cloud agent run data — conversation transcripts, artifacts, and prompt attachments — in a storage bucket you own, instead of Warp-managed storage. The Automation Platform still orchestrates every run and routes model inference.
Note
Self-hosted agent data storage is only available on Enterprise plans. [Contact sales](https://www.warp.dev/contact-sales) to learn more.
## Supported storage providers
[Section titled “Supported storage providers”](#supported-storage-providers)
Only **AWS S3** is available today. Google Cloud Storage and Azure Blob Storage support is planned.
## What data can be self-hosted
[Section titled “What data can be self-hosted”](#what-data-can-be-self-hosted)
Three categories of agent run data can be routed to your own storage, each configured independently:
* **Artifacts** - Files, Computer Use screenshots, and other binary artifacts an agent produces during a run.
* **Conversation transcripts** - Saved transcripts of agent conversations, including system messages, tool calls, and tool results.
* **Prompt attachments** - Files uploaded when starting or continuing an agent run.
A category you don’t map keeps using Warp-hosted storage. For example, you can route artifacts to your bucket while transcripts stay with Warp.
Only team admins can connect, remap, or disconnect storage. See [Access, billing, and identity](/platform/team-access-billing-and-identity/) for more on team roles.
Caution
Data is not migrated when changing storage mappings. It stays in its original location, but will no longer be accessible through Warp APIs.
## How data flows
[Section titled “How data flows”](#how-data-flows)
Mapping a category to your bucket changes where that category’s objects are written and read. Everything else about a run stays the same.
Warp’s control plane accesses self-hosted storage through a provider-specific IAM role that you provide, ensuring that all access is auditable and that Warp’s permissions may be revoked at any time. The control plane writes to the bucket over the course of a run, such as by updating the conversation transcript after each turn. It also reads from the bucket to provide run data, including conversation history and the display of computer use screenshots. Warp periodically accesses persisted data for background maintenance such as to run [scorers](/factories/measure-and-improve/scorers/).
Warp never caches bucket contents. It uses presigned URLs wherever possible so that data flows directly from your bucket to the client, without transiting Warp’s backend.
## Setting up AWS S3
[Section titled “Setting up AWS S3”](#setting-up-aws-s3)
### 1. Create an S3 bucket
[Section titled “1. Create an S3 bucket”](#1-create-an-s3-bucket)
Create the bucket that will hold your agent data. Warp writes objects using your bucket’s own encryption settings — both SSE-S3 (the default) and SSE-KMS are supported.
* AWS CLI
```bash
aws s3 mb s3://YOUR_BUCKET_NAME --region YOUR_AWS_REGION
```
* Terraform
main.tf
```hcl
resource "aws_s3_bucket" "warp_agent_data" {
bucket = "YOUR_BUCKET_NAME"
}
```
See AWS’s guide on [creating a bucket](https://docs.aws.amazon.com/AmazonS3/latest/userguide/creating-bucket.html) for console and CLI equivalents.
### 2. Open the connect dialog in the Admin Panel
[Section titled “2. Open the connect dialog in the Admin Panel”](#2-open-the-connect-dialog-in-the-admin-panel)
Self-hosted storage is configured in Warp’s [Admin Panel](/enterprise/team-management/admin-panel/). The storage connection dialog generates the exact policies that your IAM role needs. Open it before creating the role, so you can copy those values directly. It can be reopened at any time.
In the Admin Panel, go to the **Platform** settings tab. Under **Agent data storage**, click **Connect external storage** and choose **AWS S3**. Enter your bucket name and region in the “Bucket” and “Region” fields, and leave the dialog open — the next two steps use the policies it displays below the form.
### 3. Create the IAM role using the trust policy Warp shows you
[Section titled “3. Create the IAM role using the trust policy Warp shows you”](#3-create-the-iam-role-using-the-trust-policy-warp-shows-you)
The connect dialog already substitutes your team’s external ID into the trust policy.
* AWS CLI
Save the trust policy from the dialog locally:
trust-policy.json
```json
{
"Version": "2012-10-17",
"Statement": [
{
"Effect": "Allow",
"Principal": { "AWS": "arn:aws:iam::162908503950:role/warp-hosted-data-storage-prod" },
"Action": "sts:AssumeRole",
"Condition": {
"StringEquals": { "sts:ExternalId": "YOUR_TEAM_ID" }
}
}
]
}
```
Then create the role:
```bash
aws iam create-role \
--role-name warp-agent-data-storage \
--assume-role-policy-document file://trust-policy.json
```
* Terraform
Set your Warp team ID as a variable, and add the following IAM role resource:
main.tf
```hcl
resource "aws_iam_role" "warp_agent_data_storage" {
name = "warp-agent-data-storage"
assume_role_policy = jsonencode({
Version = "2012-10-17"
Statement = [{
Effect = "Allow"
Principal = { AWS = "arn:aws:iam::162908503950:role/warp-hosted-data-storage-prod" }
Action = "sts:AssumeRole"
Condition = {
StringEquals = { "sts:ExternalId" = var.warp_team_id }
}
}]
})
}
```
See AWS’s guides on [creating a role to delegate permissions](https://docs.aws.amazon.com/IAM/latest/UserGuide/id_roles_create_for-user.html) and on [using an external ID](https://docs.aws.amazon.com/IAM/latest/UserGuide/id_roles_create_for-user_externalid.html) for background on this pattern.
### 4. Attach the permissions policy
[Section titled “4. Attach the permissions policy”](#4-attach-the-permissions-policy)
This policy grants the role access to your bucket and nothing else.
* AWS CLI
Save the permissions policy from the dialog locally, with your bucket name substituted:
permissions-policy.json
```json
{
"Version": "2012-10-17",
"Statement": [
{
"Effect": "Allow",
"Action": ["s3:ListBucket"],
"Resource": "arn:aws:s3:::YOUR_BUCKET_NAME"
},
{
"Effect": "Allow",
"Action": ["s3:GetObject", "s3:PutObject", "s3:DeleteObject"],
"Resource": "arn:aws:s3:::YOUR_BUCKET_NAME/*"
}
]
}
```
Then attach it to the role:
```bash
aws iam put-role-policy \
--role-name warp-agent-data-storage \
--policy-name warp-bucket-access \
--policy-document file://permissions-policy.json
```
* Terraform
main.tf
```hcl
resource "aws_iam_role_policy" "warp_bucket_access" {
name = "warp-bucket-access"
role = aws_iam_role.warp_agent_data_storage.id
policy = jsonencode({
Version = "2012-10-17"
Statement = [
{
Effect = "Allow"
Action = ["s3:ListBucket"]
Resource = aws_s3_bucket.warp_agent_data.arn
},
{
Effect = "Allow"
Action = ["s3:GetObject", "s3:PutObject", "s3:DeleteObject"]
Resource = "${aws_s3_bucket.warp_agent_data.arn}/*"
}
]
})
}
```
See AWS’s [IAM policies for Amazon S3](https://docs.aws.amazon.com/AmazonS3/latest/userguide/using-iam-policies.html) reference for the full set of available actions and conditions.
#### If the bucket uses SSE-KMS
[Section titled “If the bucket uses SSE-KMS”](#if-the-bucket-uses-sse-kms)
Buckets encrypted with SSE-S3, the S3 default, need no further permissions. If your bucket uses SSE-KMS, add one more statement scoped to the ARN of the key that encrypts it.
* AWS CLI
Add this statement to the `Statement` array in `permissions-policy.json`, then reattach the policy:
permissions-policy.json
```json
{
"Effect": "Allow",
"Action": ["kms:Decrypt", "kms:GenerateDataKey*", "kms:DescribeKey"],
"Resource": "arn:aws:kms:YOUR_AWS_REGION:YOUR_ACCOUNT_ID:key/YOUR_KEY_ID",
"Condition": {
"StringLike": { "kms:ViaService": "s3.*.amazonaws.com" }
}
}
```
* Terraform
Add this statement to the `Statement` list in `aws_iam_role_policy.warp_bucket_access`, referencing the key that encrypts the bucket:
main.tf
```hcl
{
Effect = "Allow"
Action = ["kms:Decrypt", "kms:GenerateDataKey*", "kms:DescribeKey"]
Resource = aws_kms_key.warp_agent_data.arn
Condition = {
StringLike = { "kms:ViaService" = "s3.*.amazonaws.com" }
}
}
```
### 5. Enter the role ARN and choose what to store
[Section titled “5. Enter the role ARN and choose what to store”](#5-enter-the-role-arn-and-choose-what-to-store)
Back in the connect dialog, paste your new role’s ARN into the “Role ARN” field. In the “Data to store” dropdown, select **Artifacts**, **Conversation transcripts**, or **Prompt attachments** — whichever categories this bucket should store — then click **Connect**.
Warp immediately assumes the role and checks that the bucket is reachable. If the trust policy or external ID don’t match, or the permissions policy doesn’t grant the required actions, the connection is rejected with an error describing which check failed. See [Troubleshooting](#troubleshooting).
**Expected outcome:** The bucket appears as an option in each mapped category’s storage dropdown, and new writes for those categories go to your bucket going forward.
## Changing or removing storage
[Section titled “Changing or removing storage”](#changing-or-removing-storage)
Storage mappings can be changed at any time from **Manage connected storage**, under **Agent data storage** in the Admin Panel Platform section.
* **Remap a category** - Choose a different bucket, or **Warp-hosted**, from that category’s dropdown. Only new writes use the new target.
* **Disconnect a bucket** - Remove the connection from the manage-storage drawer. A bucket must be unmapped from every category before it can be disconnected.
Caution
Neither remapping nor disconnecting migrates or deletes existing data. If you disconnect a bucket, objects already written there remain in your AWS account — Warp simply stops referencing them.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### ”Warp could not assume the provided IAM role”
[Section titled “”Warp could not assume the provided IAM role””](#warp-could-not-assume-the-provided-iam-role)
The role’s trust policy doesn’t allow Warp’s broker role as principal, or its `sts:ExternalId` condition doesn’t match your team. Recopy the trust policy from the connect dialog and confirm it’s attached to the role you entered.
### ”Warp was denied access to the S3 bucket”
[Section titled “”Warp was denied access to the S3 bucket””](#warp-was-denied-access-to-the-s3-bucket)
The trust policy is correct, but the role’s permissions policy doesn’t grant the required S3 actions on the bucket. Recheck the permissions policy against the one shown in the dialog, and confirm the bucket name matches exactly.
### ”Warp could not reach the S3 bucket”
[Section titled “”Warp could not reach the S3 bucket””](#warp-could-not-reach-the-s3-bucket)
The bucket name or region is wrong, or the bucket doesn’t exist. Confirm both match what you created in AWS.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Architecture](/platform/architecture/#data-security-and-boundaries) - How run data, control-plane data, and inference credentials flow through Warp’s platform.
* [Self-hosting overview](/factories/self-hosting/) - Run agent compute on your own infrastructure instead of Warp-managed servers.
* [Cloud agent secrets](/platform/secrets/) - Store credentials agents use during a run.
* [Admin Panel for teams](/enterprise/team-management/admin-panel/) - The full reference for team settings, including the Platform section.
# Cloud agent and factory documentation
Canonical page: [/platform/documentation-map/](https://docs.warp.dev/platform/documentation-map/)
> Find the current documentation for standalone cloud-agent workflows, CLI tools, APIs, SDKs, and Warp Factories.
Cloud-agent features and Warp Factories share APIs and execution infrastructure, but their setup paths differ. Use the Automation Platform documentation for standalone cloud-agent workflows. Use the Warp Factories documentation to build and operate a standing software factory.
## Choose the current documentation
[Section titled “Choose the current documentation”](#choose-the-current-documentation)
| Workflow | Documentation |
| ---------------------------------------------------------------------------------- | --------------------------------------------------------- |
| Configure standalone cloud agents, environments, schedules, integrations, and runs | [Automation Platform overview](/platform/overview/) |
| Run and manage cloud agents with `oz` | [Oz CLI reference](/agents/cli/oz-cli/) |
| Run the Warp Agent from a terminal with `warp` | [Warp Agent CLI reference](/agents/cli/) |
| Call cloud-agent and factory endpoints from code | [Warp Platform API and SDKs](/factories/developer-tools/) |
| Build a standing software factory | [Warp Factories overview](/factories/) |
## Evaluate a factory
[Section titled “Evaluate a factory”](#evaluate-a-factory)
A factory adds standing agent roles, connected work sources, work items, and automation stages around a shared set of repositories. See [how Warp Factories work](/factories/how-factories-work/) to decide whether that model fits your workflow, then use the [Warp Factories quickstart](/factories/quickstart/) to create one.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Automation Platform overview](/platform/overview/) - Configure standalone cloud-agent workflows.
* [Warp Factories overview](/factories/) - Build and operate a standing software factory.
* [Warp Platform API and SDKs](/factories/developer-tools/) - Use factory endpoints, agent and run endpoints, SDKs, and API errors.
# Cloud agent environments
Canonical page: [/platform/environments/](https://docs.warp.dev/platform/environments/)
> Environments give cloud agents a repeatable container, repositories, and setup for every cloud agent run.
Environments describe *how* an agent executes a task, not *what* it does. They give cloud agents the same container, repositories, and setup every time they run. Use an environment for a cloud agent run that needs a repeatable toolchain. Interactive local runs use your current checkout and machine setup, so they don’t need one.
Factories manage their own repositories and workspace by default. Set `agentDefaults.environmentId` in a [factory definition](/factories/factory-as-code/#agentdefaultsenvironmentid) when a factory agent must use an existing environment.
## What an environment includes
[Section titled “What an environment includes”](#what-an-environment-includes)
An environment groups the runtime configuration for a cloud agent run:
* **Docker image** - The image that provides the toolchain and dependencies for your code. A self-hosted Kubernetes worker with a [`default_image`](/factories/self-hosting/managed-kubernetes/) can run without a separate environment.
* **Repositories** - One or more repos that the agent clones into its workspace.
* **Setup commands** - Commands that prepare the workspace, such as dependency installation, builds, or code generation.
* **Environment variables** - Runtime values that you set in the Docker image or container configuration.
* **Agent Secrets** - Credentials and sensitive values that Warp injects at runtime. Configure them separately with [Agent Secrets](/platform/secrets/).
Together, these settings create a fresh workspace for each run. Warp provides [prebuilt dev images](https://github.com/warpdotdev/oz-dev-environments) with common languages and tools. You can also use an official image or publish your own.
## How environments fit into cloud agent runs
[Section titled “How environments fit into cloud agent runs”](#how-environments-fit-into-cloud-agent-runs)
When the Automation Platform starts a cloud agent run, it combines the environment with a host, an agent profile, and task-specific context. Each part serves a distinct purpose:
* **Host** - Determines where the run executes. Choose [Warp-hosted](/factories/warp-hosting/) infrastructure or [self-hosted](/factories/self-hosting/) runners.
* **Agent Profiles** - Set the agent’s permissions, model choice, and defaults. See [Agent Profiles](/agents/capabilities/agent-profiles-permissions/).
* **Rules** - Provide instructions that guide agent responses and decisions. See [Rules](/agents/capabilities/rules/).
* **MCP servers** - Connect agents to external tools and data. See [MCP servers](/platform/mcp/).
* **Per-run context** - Supplies task-specific data, such as a Slack thread, PR metadata, or CI logs.
## When to use an environment
[Section titled “When to use an environment”](#when-to-use-an-environment)
Use an environment when your run needs a predictable toolchain and repeatable setup. This is common in the following cases:
* **Integrations and schedules** - Runs from Slack, Linear, GitHub Actions, or a schedule need the same workspace each time.
* **CI and remote automation** - An environment prevents different runners or base images from changing the result.
* **Team workflows** - A shared environment gives every teammate the same image, repos, and setup commands.
* **Toolchain-specific work** - Use an environment when the workflow depends on particular language versions, linters, build tools, or system packages.
You can skip an environment for an interactive local run in a working checkout. The local agent uses your existing machine setup.
[]()
## Container users and permissions
[Section titled “Container users and permissions”](#container-users-and-permissions)
Cloud agents run as a non-root user inside the container. See [configuring container users](environments/configuring-environments/#configure-container-users) for image, setup-command, and migration requirements.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Configuring cloud agent environments](environments/configuring-environments/) to create, configure, and manage environments.
* [Troubleshooting cloud agent environments](environments/troubleshooting-environments/) to fix setup, authorization, permissions, and image failures.
* [Runners](/factories/runners/) to configure the compute that hosts environments.
* [Scheduled agents](/platform/triggers/scheduled-agents/) to run cloud agents on a recurring cadence in a shared environment.
* [Deployment patterns](/factories/deployment-patterns/) to choose between Warp-hosted and self-hosted execution.
# Configuring cloud agent environments
Canonical page: [/platform/environments/configuring-environments/](https://docs.warp.dev/platform/environments/configuring-environments/)
> Create, configure, and manage cloud agent environments with the Oz web app, guided setup in Warp, or the Oz CLI.
Create an environment before you run a cloud agent that needs your repositories, toolchain, or setup commands. You can create and manage environments in the Oz web app, with guided setup in Warp, or through the Oz CLI.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **GitHub repositories** - Add one or more repositories for the agent to clone and work in.
* **GitHub authorization** - Authorize GitHub so the agent can access your repositories. For automated workflows that use an agent API key, configure [team GitHub authorization](/platform/team-access-billing-and-identity/#team-github-authorization) in the Admin Panel.
* **Docker image** - Use a publicly accessible image that can build and run your code. Official [node](https://hub.docker.com/_/node), [python](https://hub.docker.com/_/python), and [rust](https://hub.docker.com/_/rust) images work for many projects. You can also use [Warp’s prebuilt dev images](https://github.com/warpdotdev/oz-dev-environments).
Caution
Musl-based Docker images, including Alpine Linux, are not supported. The agent runtime requires glibc. Use Debian, Ubuntu, or a default non-Alpine image from Docker Hub.
## Create an environment in the web app
[Section titled “Create an environment in the web app”](#create-an-environment-in-the-web-app)

The Create environment panel in the Oz web app.
1. Open the [Environments page in the Oz web app](https://oz.warp.dev/environments), then click **New environment**.
2. Enter a name, select one or more repositories, and enter a **Docker image reference**. Click **Suggest** to get an image recommendation based on the selected repositories.
3. Add setup commands, cloud provider access for AWS or GCP, or a description when needed.
4. Click **Create environment**. You can now use the environment with cloud agents and integrations.
## Create an environment with guided setup
[Section titled “Create an environment with guided setup”](#create-an-environment-with-guided-setup)
Run [`/create-environment`](warp://action/create_environment) in Warp to inspect your repositories and generate an environment configuration. The guided setup detects languages, frameworks, and tools, then recommends an image and setup commands.
Run the command from a Git repository with no argument, or pass one or more repository paths or URLs.
```text
# Local paths
/create-environment ./warp-internal ./warp-server
# GitHub repositories
/create-environment warpdotdev/warp-internal warpdotdev/warp-server
# GitHub URL
/create-environment https://github.com/warpdotdev/warp-internal.git
```
Guided setup does the following:
* **Detect repositories** - Identifies the languages, frameworks, and tools the agent will use.
* **Recommend an image** - Finds an existing Dockerfile, recommends an official base image, or helps you build a custom image.
* **Suggest setup commands** - Uses your scripts and package managers to recommend workspace setup.
* **Create the environment** - Creates the environment through the CLI and returns an environment ID.
## Create an environment with the CLI
[Section titled “Create an environment with the CLI”](#create-an-environment-with-the-cli)
Use the Oz CLI when you know the environment configuration, need a custom Docker image, or want to automate environment creation.
```bash
oz environment create \
--name ENVIRONMENT_NAME \
--docker-image IMAGE_REFERENCE \
--repo OWNER/REPO \
--setup-command "SETUP_COMMAND" \
--description "DESCRIPTION"
```
Replace `ENVIRONMENT_NAME` with a human-readable label, `IMAGE_REFERENCE` with a Docker Hub image, `OWNER/REPO` with a repository to clone, `SETUP_COMMAND` with a workspace command, and `DESCRIPTION` with an optional summary. Repeat `--repo` and `--setup-command` for each additional repository or command.
## Environment design and best practices
[Section titled “Environment design and best practices”](#environment-design-and-best-practices)
Design the image and setup commands so they produce the same workspace on every run.
* **Keep setup repeatable** - Write setup commands that are safe to rerun and produce the same toolchain and workspace state for a given repository revision.
* **Pin toolchain versions** - Pin language runtimes and core tools in a Docker image, then use lockfiles such as `package-lock.json` for dependencies.
* **Define the workspace boundary** - In a multi-repo environment, state which repositories are cloned and where setup commands run.
* **Make prerequisites explicit** - Add any required build, code generation, or system-package installation steps to the setup commands.
```bash
# Repeatable setup
mkdir -p .cache
npm ci
# Setup that can fail on rerun or drift over time
mkdir .cache
npm install
```
If setup commands need credentials, configure [Agent Secrets](/platform/secrets/) instead of hardcoding tokens.
## Configure container users
[Section titled “Configure container users”](#configure-container-users)
Cloud agents run as a non-root user inside the container. Configure your image and setup commands for that user before you create the environment.
### Understand how Warp chooses the container user
[Section titled “Understand how Warp chooses the container user”](#understand-how-warp-chooses-the-container-user)
* **Image with a non-root `USER`** - Warp respects the Dockerfile `USER` directive and runs the agent as that user.
* **Image that starts as root** - Warp runs the agent as a dedicated `agent` user with passwordless `sudo`. The user has UID and GID 1000 when available.
* **Image that cannot support a non-root user** - If Warp can’t install `sudo` or the workspace isn’t writable by the agent user, it logs a warning and continues as root.
### Prepare images and setup commands
[Section titled “Prepare images and setup commands”](#prepare-images-and-setup-commands)
* **Use `sudo` for root access** - Prefix commands such as `apt-get install`, writes to `/usr/local` or `/etc`, and `chown` with `sudo`. Passwordless `sudo` preserves your `PATH`, but removes unsafe variables such as `LD_*` and `BASH_ENV`.
* **Install tools outside `/root`** - The agent home directory is `/home/agent`. Install tools and configuration stored in `~/.bashrc`, `~/.cargo`, or `~/.nvm` system-wide or somewhere the `agent` user can access.
* **Keep directories writable by UID and GID 1000** - Files the agent creates use UID 1000. Directories in your image must be writable by that user.
Note
To temporarily restore root behavior while you update an image or setup commands, set `WARP_AGENT_NONROOT=0` in the image, such as with a Dockerfile `ENV` directive.
## Manage environments
[Section titled “Manage environments”](#manage-environments)
Use the Oz CLI to inspect and update environments after you create them.
### List environments
[Section titled “List environments”](#list-environments)
```bash
oz environment list
```
### View an environment
[Section titled “View an environment”](#view-an-environment)
Replace `<ENV_ID>` with the ID of the environment you want to view.
```bash
oz environment get <ENV_ID>
```
### Update an environment
[Section titled “Update an environment”](#update-an-environment)
Replace `<ENV_ID>` with the ID of the environment you want to modify.
```bash
# Add or remove a repository
oz environment update <ENV_ID> --repo OWNER/REPO
oz environment update <ENV_ID> --remove-repo OWNER/REPO
# Add or remove a setup command
oz environment update <ENV_ID> --setup-command "SETUP_COMMAND"
oz environment update <ENV_ID> --remove-setup-command "SETUP_COMMAND"
# Update the name, description, or Docker image
oz environment update <ENV_ID> --name "ENVIRONMENT_NAME"
oz environment update <ENV_ID> --description "DESCRIPTION"
oz environment update <ENV_ID> --docker-image IMAGE_REFERENCE
```
Use `--remove-description` to clear the description. Use `--force` to skip confirmation checks for environments used by integrations.
### Delete an environment
[Section titled “Delete an environment”](#delete-an-environment)
Replace `<ENV_ID>` with the ID of the environment you want to delete.
```bash
oz environment delete <ENV_ID>
```
Add `--force` to skip confirmation checks for environments used by integrations.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Cloud agent environments](/platform/environments/) for the conceptual overview.
* [Troubleshooting cloud agent environments](troubleshooting-environments/) to resolve setup and runtime problems.
* [Integration setup](/agents/cli/oz-cli/integration-setup/) to configure end-to-end integration workflows.
# Troubleshooting cloud agent environments
Canonical page: [/platform/environments/troubleshooting-environments/](https://docs.warp.dev/platform/environments/troubleshooting-environments/)
> Fix environment setup failures, authorization errors, permission problems, and incompatible Docker images for cloud agents.
## Setup commands fail on a fresh container
[Section titled “Setup commands fail on a fresh container”](#setup-commands-fail-on-a-fresh-container)
Setup commands run in a new container on every cloud agent run. Commands that depend on existing directories, caches, or cloned repositories can fail with [`environment_setup_failed`](/factories/api-and-sdk/troubleshooting/errors/environment-setup-failed/).
1. Update the setup commands so they work in a fresh container. For example, use `mkdir -p .cache` instead of `mkdir .cache`.
2. Use lockfile-based dependency commands such as `npm ci` when your project supports them.
3. Run the complete setup from a clean container before updating the environment.
## `Permission denied` or `EACCES`
[Section titled “Permission denied or EACCES”](#permission-denied-or-eacces)
Cloud agents run as a non-root user by default. A command fails when it needs root access or writes to a directory that the agent user cannot modify.
1. Prefix commands that require root access with `sudo`.
2. Make directories in the Docker image writable by UID and GID 1000.
3. Review [configuring container users](configuring-environments/#configure-container-users) for the image and setup-command requirements.
## `external_authentication_required`
[Section titled “external\_authentication\_required”](#external_authentication_required)
Cloud agents need GitHub authorization to clone private repositories. This error can occur when GitHub lacks repository access or the user who started the run has not authorized GitHub.
1. Authorize GitHub for the user who starts the run.
2. For an automated workflow with an agent API key, configure [team GitHub authorization](/platform/team-access-billing-and-identity/#team-github-authorization).
3. Follow [GitHub authorization setup](/agents/cli/oz-cli/integration-setup/#how-github-authorization-works) for the full flow.
## ”VM failed before the agent could run”
[Section titled “”VM failed before the agent could run””](#vm-failed-before-the-agent-could-run)
This error often means the Docker image is incompatible with the agent runtime. Alpine Linux and other musl-based images are not supported because the runtime requires glibc.
1. Switch to a glibc-based image such as Debian, Ubuntu, or a default non-Alpine official image such as `node`, `python`, or `rust`.
2. Recreate or update the environment with the new image.
3. If the error continues, review the environment configuration in the Oz web app or use the Oz CLI to run `oz environment get <ENV_ID>`.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Cloud agent environments](/platform/environments/) for the environment model and when to use one.
* [Configuring cloud agent environments](configuring-environments/) to create, update, and manage environments.
* [`environment_setup_failed`](/factories/api-and-sdk/troubleshooting/errors/environment-setup-failed/) for the API error reference.
# Security and networking
Canonical page: [/platform/execution-security/](https://docs.warp.dev/platform/execution-security/)
> Security model, data boundaries, and network requirements for self-hosted Automation Platform cloud agents — including per-backend considerations and BYOLLM.
Repository clones and agent workloads stay on your infrastructure, while orchestration and inference route through Warp. These boundaries apply to [managed](/factories/self-hosting/#managed-architecture) and [unmanaged](/platform/unmanaged-execution/) deployments.
## Data boundaries
[Section titled “Data boundaries”](#data-boundaries)
Self-hosted execution keeps repository clones, source files, build artifacts, runtime secrets, environment variables, and agent workspaces on infrastructure you control. Agents can also reach internal systems that your host can reach, such as VPN-only services, private databases, or self-hosted source control.
**Stored and executed only on your infrastructure:**
* Repository clones and source files.
* Build artifacts and compiled outputs.
* Runtime secrets and environment variables.
* Container, host, or external-runtime workspace state.
**Routes through Warp’s backend** (under [Zero Data Retention (ZDR)](/enterprise/security-and-compliance/security-overview/#zero-data-retention-zdr)):
* Orchestration metadata (task status, lifecycle events).
* Session transcripts, which include agent-generated summaries of code context, file contents the agent reads, and command output.
* LLM inference requests and responses, which include code context from the agent’s interactions.
Note
Repositories are cloned and stored only on your infrastructure, but code content can still appear in session transcripts, artifacts, and LLM prompts as part of normal agent operation. Warp does not persistently store your source code or train on it. For retention with customer-supplied inference, see [LLM inference and BYOLLM](#llm-inference-and-byollm).
***
## Network requirements
[Section titled “Network requirements”](#network-requirements)
Self-hosted agents **do not require any network ingress**. They require outbound (egress) access to the following services:
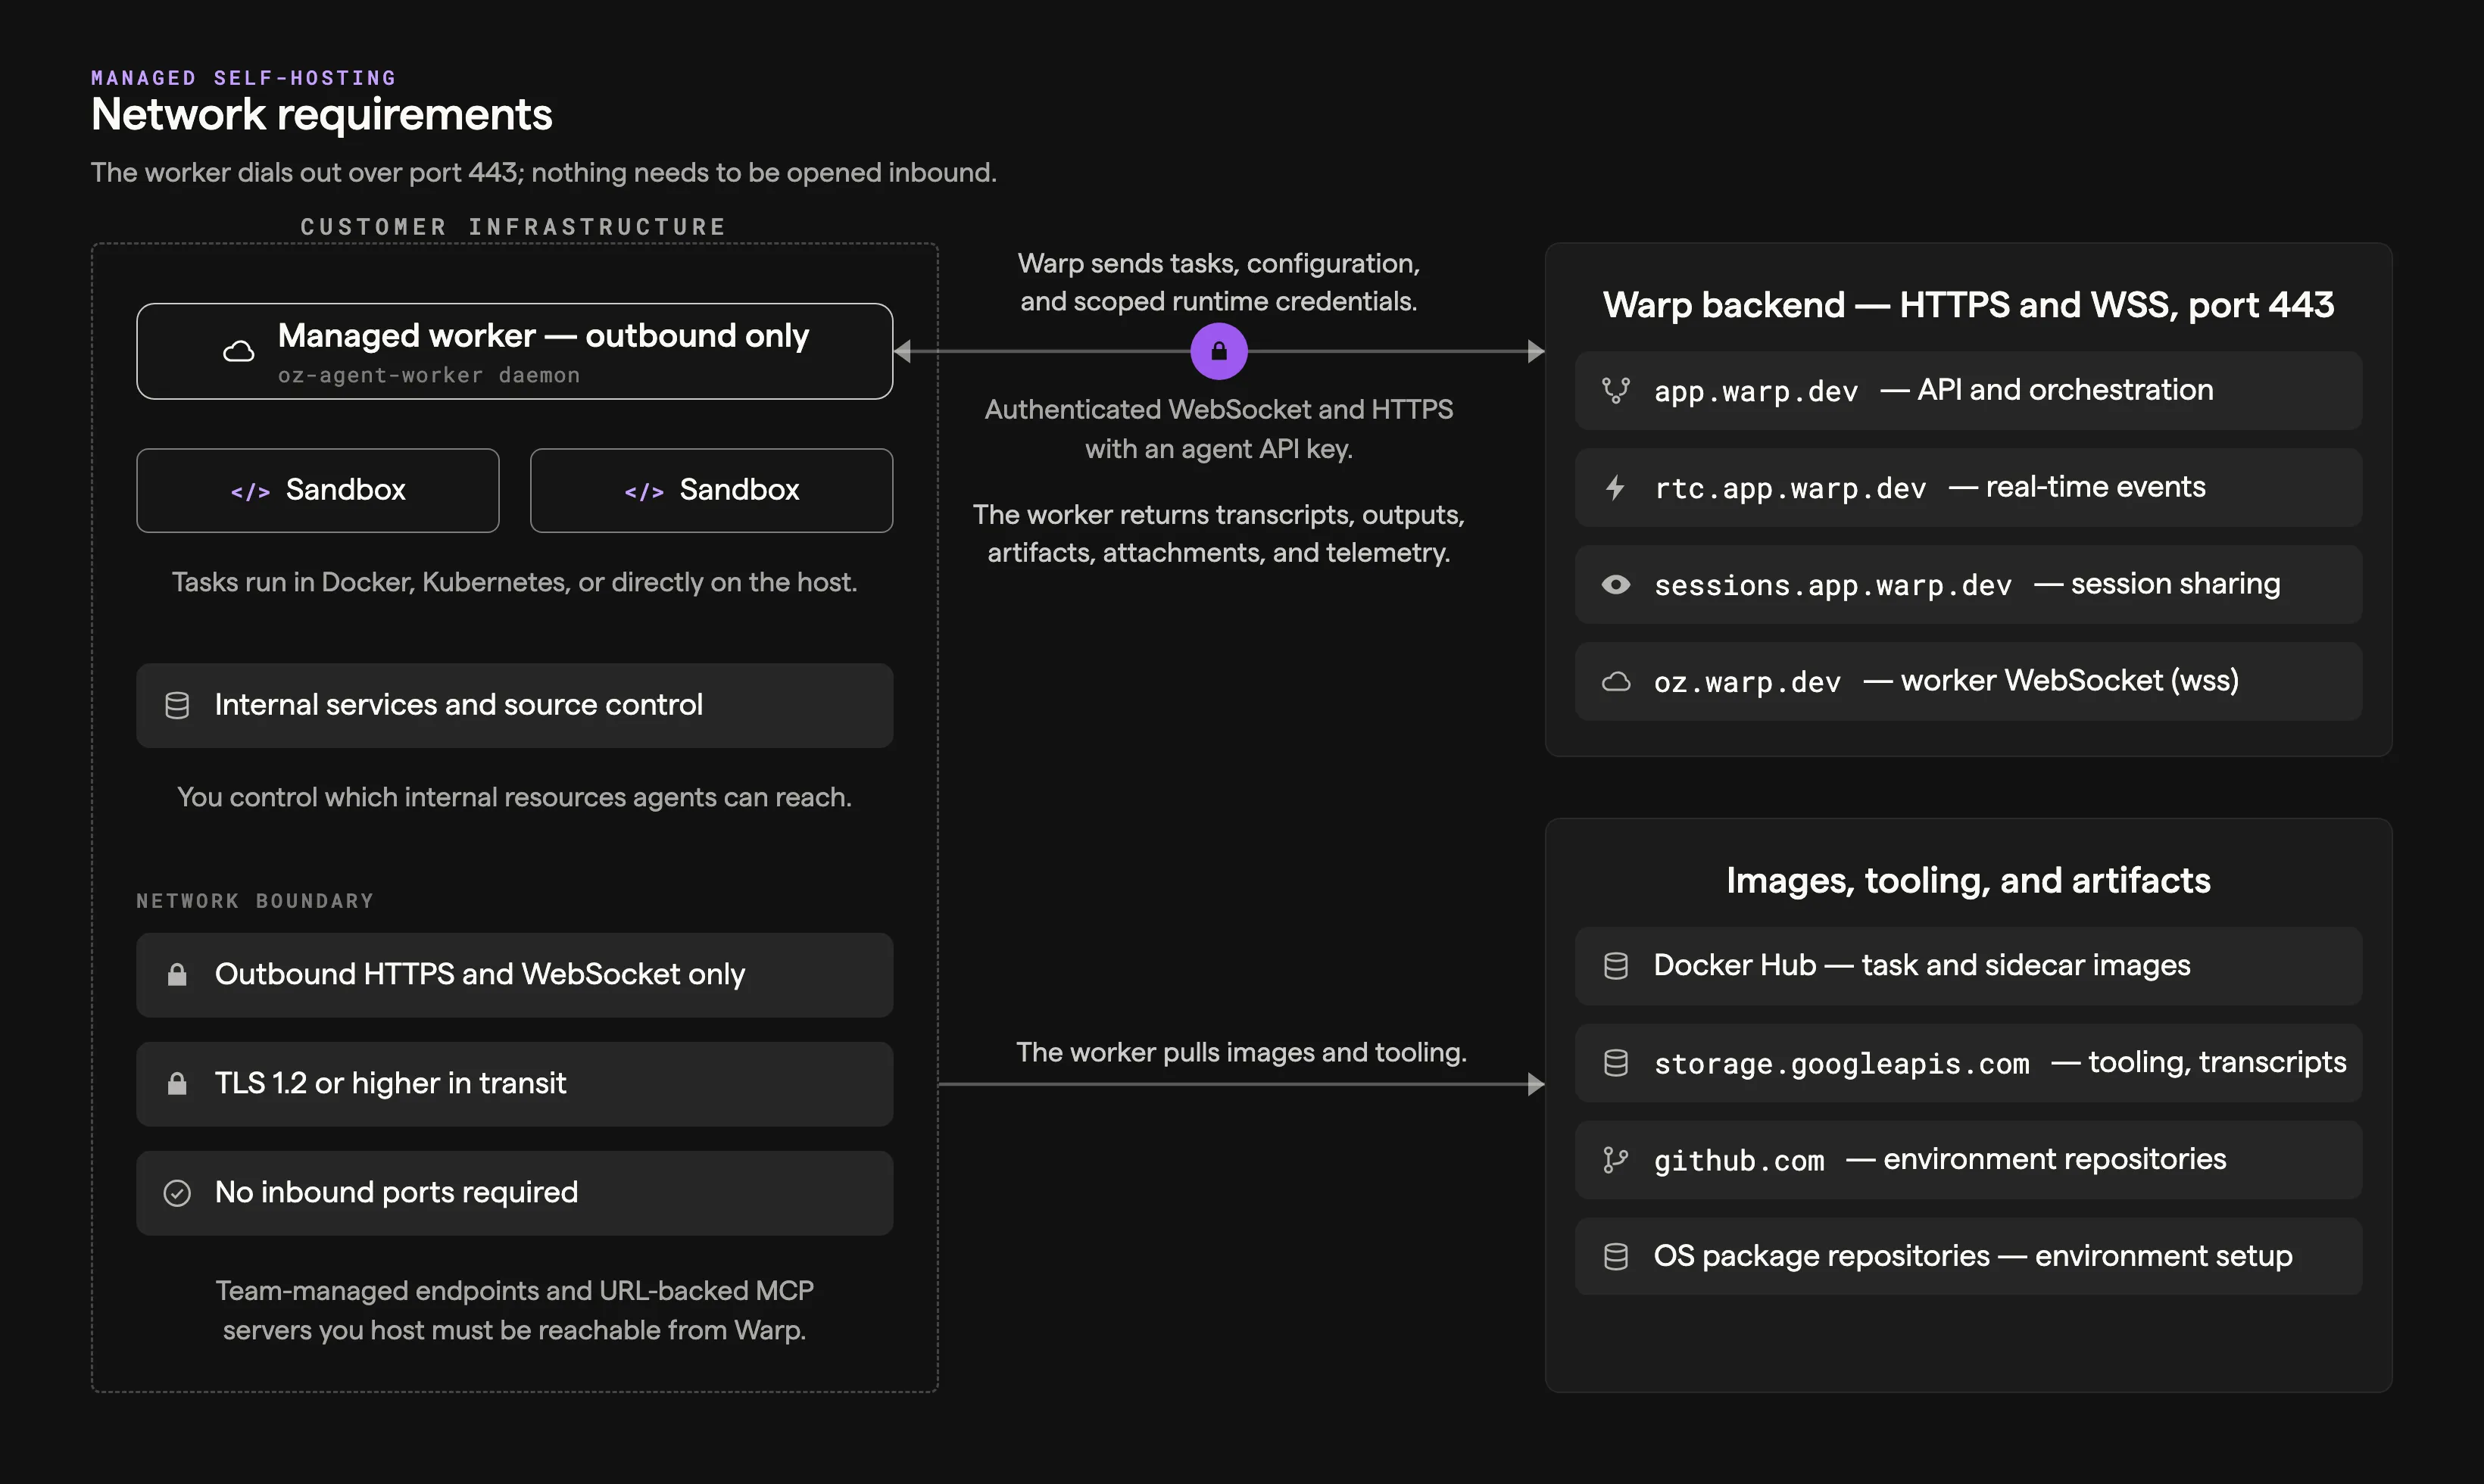
**Warp’s backend (all architectures):**
* `app.warp.dev` — port 443
* `rtc.app.warp.dev` — port 443
* `sessions.app.warp.dev` — port 443
* `oz.warp.dev` — port 443 (managed architecture only)
Docker Hub — for pulling task images with the Docker and Kubernetes backends.
Tasks use the following Docker images:
* [`warpdotdev/warp-agent:latest`](https://hub.docker.com/r/warpdotdev/warp-agent)
* [`warpdotdev/warp-xvfb-sidecar:latest`](https://hub.docker.com/r/warpdotdev/warp-xvfb-sidecar) (only if [computer use](/agents/capabilities/computer-use/) is enabled)
* [`warpdotdev/warp-claude-cli-sidecar:latest`](https://hub.docker.com/r/warpdotdev/warp-claude-cli-sidecar) (only if using Claude Code)
* [`warpdotdev/warp-codex-cli-sidecar:latest`](https://hub.docker.com/r/warpdotdev/warp-codex-cli-sidecar) (only if using Codex)
* The base image specified by your [environment](/platform/environments/)
**Google Cloud Storage (`storage.googleapis.com`)** — port 443, for downloading managed Docker Sandbox tooling sidecar archives (Warp CLI, computer use, and coding CLI tooling), uploading conversation transcripts so conversations can be resumed locally, and providing attachments to the agent.
**GitHub (`github.com`)** — only with the managed architecture, when using a Warp [environment](/platform/environments/) with configured GitHub repositories.
**Linux distribution-specific package repositories** — only with the managed architecture, when using a Warp environment whose base image does not have Git pre-installed. The exact repositories depend on the package manager configuration in the environment’s base image.
All traffic uses HTTPS (port 443). No inbound ports need to be opened.
[Team-managed inference endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) and URL-backed MCP servers that you host must be reachable from Warp’s servers.
***
## Backend-specific security considerations
[Section titled “Backend-specific security considerations”](#backend-specific-security-considerations)
### Docker backend
[Section titled “Docker backend”](#docker-backend)
* **Docker socket access** — The worker requires access to the Docker daemon to create task containers. When running the worker via Docker, this means mounting `/var/run/docker.sock`. Ensure appropriate access controls on the host.
* **Volume mounts** — If using `-v` / `--volumes`, be mindful of what host paths you expose to task containers.
* **Task isolation** — Each task runs in its own container. Containers are removed after execution by default (disable with `--no-cleanup` for debugging).
### Kubernetes backend
[Section titled “Kubernetes backend”](#kubernetes-backend)
* **Kubernetes RBAC** — The worker uses namespace-scoped permissions to manage Jobs and read Pods, logs, and events. The task namespace must allow a root init container unless native image volumes are enabled.
* **Kubernetes service accounts** — The worker Deployment ServiceAccount is separate from the task Job `serviceAccountName` in `pod_template`. Scope each to its workload.
* **API key management** — Store `WARP_API_KEY` in a Kubernetes Secret and inject it only into the worker. Add task credentials through `pod_template` or an external secrets operator.
* **Task isolation** — Each task runs as a Kubernetes Job and Pod. Successful Jobs are removed. With cleanup enabled, failed or orphaned Jobs remain for 24 hours; `--no-cleanup` keeps them without a TTL.
### Direct backend
[Section titled “Direct backend”](#direct-backend)
* **Shared host kernel** — The Direct backend does not provide container-level isolation. Each task runs in an isolated workspace directory but shares the host OS and kernel.
* **Minimal environment by default** — The Direct backend intentionally starts tasks with a minimal environment (`HOME`, `TMPDIR`, `PATH` only). Sensitive worker credentials like `WARP_API_KEY` are not passed to tasks unless explicitly configured.
* **Workspace cleanup** — Workspaces under `workspace_root` are removed after execution by default (disable with `--no-cleanup` for debugging).
### Command backend
[Section titled “Command backend”](#command-backend)
* **Task payloads** - The dispatch command receives task credentials and runtime configuration on standard input. Keep payloads out of logs.
* **Runtime isolation** - The external runtime owns task isolation, credentials, network policy, and cleanup.
### Unmanaged
[Section titled “Unmanaged”](#unmanaged)
* **Host inheritance** — Agents inherit the host’s network access, tools, and credentials. If the host has access to a VPN or internal services, the agent will too. Evaluate accordingly.
* **Kubernetes pod isolation** — Whether Kubernetes pods provide sufficient sandboxing for agents depends on your cluster configuration and risk profile. Evaluate your pod security policies, network policies, and RBAC settings based on your organization’s security requirements.
***
## VPN and on-premises access
[Section titled “VPN and on-premises access”](#vpn-and-on-premises-access)
Self-hosted agents inherit the host’s network access, including VPN services, private source control, and databases.
See [GitLab](/platform/integrations/gitlab/) and [Bitbucket](/platform/integrations/bitbucket/) setup guides for SCM integration details.
***
## LLM inference and BYOLLM
[Section titled “LLM inference and BYOLLM”](#llm-inference-and-byollm)
LLM inference routes through Warp’s backend. With Warp-managed inference, requests go to contracted providers covered by [ZDR](/enterprise/security-and-compliance/security-overview/#zero-data-retention-zdr) agreements. With customer-supplied inference, provider-side retention follows your team’s agreement with that provider. Enterprise teams that want inference routed and billed through their own accounts can use [team-managed model keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) or [Bring Your Own LLM (BYOLLM)](/enterprise/enterprise-features/bring-your-own-llm/); cloud agent support varies by provider, so check each provider’s page.
***
## Related pages
[Section titled “Related pages”](#related-pages)
* [Self-hosting overview](/factories/self-hosting/) — Managed vs unmanaged and architecture decision guide.
* [Data security and boundaries](/platform/architecture/#data-security-and-boundaries) — Diagrams of where each class of data lives and travels.
* [Security overview](/enterprise/security-and-compliance/security-overview/) — Warp’s broader security model, including ZDR.
* [Bring Your Own LLM (BYOLLM)](/enterprise/enterprise-features/bring-your-own-llm/) — Route inference through your own cloud provider accounts.
* [Self-hosted worker reference](/factories/self-hosting/reference/) — CLI flags and config schema, including every security-relevant option.
# Cloud Agent FAQs
Canonical page: [/platform/faqs/](https://docs.warp.dev/platform/faqs/)
> Frequently asked questions about cloud agents, including where agents run, how runs work, supported models, security, and common workflows.
This page answers common questions about cloud agents, including where they run, how they’re configured, and how teams use cloud agents for day-to-day engineering work.
## Architecture and execution
[Section titled “Architecture and execution”](#architecture-and-execution)
### Where do cloud agents run? What’s the architecture?
[Section titled “Where do cloud agents run? What’s the architecture?”](#where-do-cloud-agents-run-whats-the-architecture)
Agents run either **locally** (inside your Warp session) or **in the cloud** as a **cloud agent run**, inside an **environment** (see [Environments](/platform/environments/)).
The cloud agents platform is built around modular, observable execution:
* A **trigger** starts work (manual, schedule/cron, webhook, or an integration like Slack/GitHub).
* The **agent** executes inside an **environment** (either a Warp-hosted cloud sandbox, or a **self-hosted sandbox** on your infrastructure, depending on plan/support).
* Every step is recorded: **transcripts, tool calls, logs, and outputs**, so work is auditable and debuggable instead of a black box.
The same agent can be invoked consistently across entry points (Warp conversation, cloud agent web app, the CLI, API/SDK, Slack/GitHub triggers) without rewriting the underlying instructions.
### What exactly are cloud agents in Warp?
[Section titled “What exactly are cloud agents in Warp?”](#what-exactly-are-cloud-agents-in-warp)
A **cloud agent** is a packaged automation unit made up of:
* **Instructions** — A reusable skill/prompt (what it should do).
* **Profile** — Model selection + tools + permissions (how it operates).
* **Trigger** — Manual, cron/schedule, webhook, or integration event (when it starts).
* **Environment** — Repo access, dependencies (Docker image), secrets, setup commands, and runtime config (where it runs).
* **Host** — Local (interactive) or cloud (run), and optionally self-hosted execution (where supported).
Because the agent definition is modular, the same cloud agent can be started from different surfaces (terminal, web app, CLI, integrations) with a consistent interface.
### Can we intervene mid-run?
[Section titled “Can we intervene mid-run?”](#can-we-intervene-mid-run)
Yes. For **cloud agent runs**, you can:
* Inspect **run state**, tool calls, and logs.
* **Steer** the agent while it’s running.
* Unblock it with additional instructions or context.
If you’re not happy with where it landed, you can take over to finish the task. That human handoff is a core part of making agents reliable beyond demos.
### Do cloud agents have access to Codebase Context and indexing?
[Section titled “Do cloud agents have access to Codebase Context and indexing?”](#do-cloud-agents-have-access-to-codebase-context-and-indexing)
Yes. [Codebase Context](/agents/capabilities/codebase-context/) is enabled for all cloud agent runs, as long as Codebase Context is enabled for your account. This includes runs triggered from the CLI, API/SDK, integrations (Slack, Linear, GitHub Actions), and schedules. No additional configuration is needed — if Codebase Context is enabled, cloud agents use it automatically.
### Can I access a shell inside a cloud agent environment? Are there limitations (Docker, Playwright, etc.)?
[Section titled “Can I access a shell inside a cloud agent environment? Are there limitations (Docker, Playwright, etc.)?”](#can-i-access-a-shell-inside-a-cloud-agent-environment-are-there-limitations-docker-playwright-etc)
Yes. Cloud agent runs execute in a full Linux environment and behave like a local development session. You can install dependencies, run Docker, and use headless tools like Playwright, subject to standard sandbox resource limits.
### Do cloud agents run as root inside the container?
[Section titled “Do cloud agents run as root inside the container?”](#do-cloud-agents-run-as-root-inside-the-container)
No. By default, cloud agents run as a dedicated non-root `agent` user (UID/GID 1000 where available) with passwordless sudo. If your environment’s image sets a non-root `USER`, Warp runs the agent as that user instead, unchanged. For images that start as root, commands that need root access, like `apt-get install`, work with a `sudo` prefix. See [configuring container users](/platform/environments/configuring-environments/#configure-container-users) for details on home directory location, file ownership, and fallback behavior.
### Do cloud agents support a fully self-hosted, on-prem, or offline mode?
[Section titled “Do cloud agents support a fully self-hosted, on-prem, or offline mode?”](#do-cloud-agents-support-a-fully-self-hosted-on-prem-or-offline-mode)
The cloud agents platform supports self-hosting the **agent sandbox** (the execution environment) on your own infrastructure. The **control plane**—which handles orchestration, tracking, and auditability—remains Warp-managed and is not self-hosted.
Self-hosted execution is available on **Enterprise** plans. See [Self-hosting](/factories/self-hosting/) and [Deployment patterns](/factories/deployment-patterns/) for details.
Note
Self-serve [Bring Your Own API Key (BYOK)](/agents/inference/bring-your-own-api-key/) does not apply to cloud agents. Keys you add yourself are stored locally on your device and can’t be passed to cloud-hosted or self-hosted agent runs, so those runs consume [Warp credits](/support-and-community/plans-and-billing/credits/).
Business and Enterprise teams are the exception: an admin can configure [team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) that are stored server-side by Warp and used by cloud agents. Those runs still consume [platform credits](/support-and-community/plans-and-billing/platform-credits/) for orchestration.
## Models
[Section titled “Models”](#models)
### Which models are supported?
[Section titled “Which models are supported?”](#which-models-are-supported)
Cloud agents are **multi-model by design**. You can choose models based on cost, latency, and capability, and teams commonly mix models by workflow:
* Faster/cheaper models for triage and routine tasks.
* Stronger models for complex changes (refactors, multi-file work, deeper reasoning).
Model choice is configurable per **agent** (and often per environment/workflow), depending on how you set up your profiles.
### Can I choose which model cloud agents use?
[Section titled “Can I choose which model cloud agents use?”](#can-i-choose-which-model-cloud-agents-use)
Yes. Cloud agents support the same set of models available in Warp. Model selection is configurable per agent or environment.
### Can I authenticate cloud agents with my own ChatGPT or Claude Pro / Max plan?
[Section titled “Can I authenticate cloud agents with my own ChatGPT or Claude Pro / Max plan?”](#can-i-authenticate-cloud-agents-with-my-own-chatgpt-or-claude-pro--max-plan)
No. A [connected ChatGPT subscription](/agents/inference/chatgpt-subscription/) applies to Warp Agent conversations in the Warp app, not cloud agent runs. Warp also doesn’t support connecting a Claude consumer subscription.
Business and Enterprise admins can configure [team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) for cloud agents.
### Do you support local or private LLMs for compliance or air-gapped environments?
[Section titled “Do you support local or private LLMs for compliance or air-gapped environments?”](#do-you-support-local-or-private-llms-for-compliance-or-air-gapped-environments)
Enterprise plans can route inference through your own cloud-provider account via [Bring Your Own LLM (BYOLLM)](/enterprise/enterprise-features/bring-your-own-llm/), so prompts stay within your cloud environment.
Fully local, offline LLM execution is difficult given the current cloud agents orchestration and runtime architecture, but private-model support via enterprise cloud providers is available through BYOLLM.
### Will cloud agents support Agent-to-Agent Protocols (A2A)?
[Section titled “Will cloud agents support Agent-to-Agent Protocols (A2A)?”](#will-cloud-agents-support-agent-to-agent-protocols-a2a)
It’s something we’re actively exploring. Our focus is on building durable orchestration primitives—runs, environments, observability, steering, and coordination—that can support A2A and other emerging standards over time.
## Security and billing
[Section titled “Security and billing”](#security-and-billing)
### Will cloud storage for agent definitions, runs, and conversations be secure and encrypted?
[Section titled “Will cloud storage for agent definitions, runs, and conversations be secure and encrypted?”](#will-cloud-storage-for-agent-definitions-runs-and-conversations-be-secure-and-encrypted)
Yes. All cloud agent data stored in the cloud is encrypted at rest and in transit, and protected by Warp account–level access controls.
Cloud agent environments are sandboxed by default, with scoped access to repos, secrets, and compute. Security and isolation are first-class design constraints for the cloud agent runtime.
### Are cloud agents included in the Build plan, or is it a separate add-on?
[Section titled “Are cloud agents included in the Build plan, or is it a separate add-on?”](#are-cloud-agents-included-in-the-build-plan-or-is-it-a-separate-add-on)
Cloud agents are included in the Build plan. Usage is metered via credits, with pricing based on agent runs and resource consumption. Concurrency limits and credit allocation details are still being finalized.
### How do cloud agents handle API keys and secrets for agents?
[Section titled “How do cloud agents handle API keys and secrets for agents?”](#how-do-cloud-agents-handle-api-keys-and-secrets-for-agents)
Secrets are managed via the cloud agents CLI. Secrets are encrypted at rest, scoped to your Warp account, and injected into the agent environment at runtime. They are never hard-coded into agent instructions or logs.
To learn more about how secrets work in practice, see [Cloud Agent Secrets](/platform/secrets/).
## Workflows
[Section titled “Workflows”](#workflows)
### How do agents handle branching, merge conflicts, and multi-agent coordination with cloud agents?
[Section titled “How do agents handle branching, merge conflicts, and multi-agent coordination with cloud agents?”](#how-do-agents-handle-branching-merge-conflicts-and-multi-agent-coordination-with-cloud-agents)
The cloud agents platform is intentionally flexible. As the developer, you decide how agents should branch, coordinate, and resolve conflicts.
Interactive agents can plan work and spawn subagents to parallelize tasks. Cloud agents provide the building blocks for [running and coordinating multiple concurrent agents](/platform/orchestration/), rather than enforcing a fixed workflow.
### Why focus on orchestration primitives instead of immediately adopting new agent standards?
[Section titled “Why focus on orchestration primitives instead of immediately adopting new agent standards?”](#why-focus-on-orchestration-primitives-instead-of-immediately-adopting-new-agent-standards)
We believe durable infrastructure matters more than transient standards. The cloud agents platform provides stable building blocks—agent runs, environments, auditability, steering, and coordination—that orchestration frameworks and emerging standards can use over time.
### Can cloud agents integrate with external tools, APIs, or services (like n8n connectors)?
[Section titled “Can cloud agents integrate with external tools, APIs, or services (like n8n connectors)?”](#can-cloud-agents-integrate-with-external-tools-apis-or-services-like-n8n-connectors)
Yes, and cloud agents do not rely on rigid, predefined workflows. Agents can install CLIs, call external APIs, use MCP servers, and access the internet directly.
The intent is to delegate flexibility to agents rather than constrain them with fixed connectors.
### Can I export agent conversations and runs from cloud agents?
[Section titled “Can I export agent conversations and runs from cloud agents?”](#can-i-export-agent-conversations-and-runs-from-cloud-agents)
Yes. Conversations can be copied directly from the UI. The cloud agent CLI and API also provide access to full conversation text, logs, and outputs programmatically.
### How do cloud agents handle environment access, files, and security compared to SSH-based setups?
[Section titled “How do cloud agents handle environment access, files, and security compared to SSH-based setups?”](#how-do-cloud-agents-handle-environment-access-files-and-security-compared-to-ssh-based-setups)
Access is handled through Warp session sharing rather than SSH keys. Authentication is tied to Warp accounts and access controls, enabling secure person-to-person sharing.
Configuration files and credentials can be managed using encrypted .env workflows (for example, dotenv-style encryption), avoiding repeated manual decrypt/encrypt cycles.
### Can cloud agents review PRs like a teammate?
[Section titled “Can cloud agents review PRs like a teammate?”](#can-cloud-agents-review-prs-like-a-teammate)
Yes. Common patterns for a **cloud agent** in PR review:
* Summarize changes and intent.
* Flag risky diffs and edge cases.
* Suggest tests and missing coverage.
* Propose refactors for maintainability.
A typical workflow is: the agent leaves structured review comments and optionally opens a follow-up PR for mechanical fixes (or commits to the branch, if you choose to allow that).
### Can cloud agents write unit tests?
[Section titled “Can cloud agents write unit tests?”](#can-cloud-agents-write-unit-tests)
Yes, especially when:
* The repo has a consistent test framework.
* The **environment** is reproducible (dependencies and setup are reliable).
The strongest loop is: a cloud agent generates tests, runs them in the environment, iterates until green, then opens a PR with the tests plus a short explanation of coverage and assumptions.
### Can cloud agents do big refactors?
[Section titled “Can cloud agents do big refactors?”](#can-cloud-agents-do-big-refactors)
It can help, but the best practice is to scope into smaller, reviewable chunks.
Agents are strongest when they can continuously validate progress (tests, lint, typecheck). For large refactors, a staged approach with checkpoints (and possibly [multiple child agents](/platform/orchestration/) for parallel exploration) tends to work better than one giant prompt.
### Can cloud agents triage issues / tickets automatically?
[Section titled “Can cloud agents triage issues / tickets automatically?”](#can-cloud-agents-triage-issues--tickets-automatically)
Yes. A common cloud agent workflow:
* When a ticket/issue is created (via integration trigger), a cloud agent gathers context (recent changes, logs/metrics links, ownership).
* Proposes labels/priority and likely causes.
* Drafts next steps or a response.
* Asks clarifying questions back to the reporter when needed.
### Can cloud agents do dependency upgrades?
[Section titled “Can cloud agents do dependency upgrades?”](#can-cloud-agents-do-dependency-upgrades)
Yes. Scheduled dependency bumps are a classic cloud agent use case:
* Open a PR.
* Run tests.
* Resolve simple conflicts.
* Attach a risk summary (optional).
This is usually implemented as a [scheduled agent](/platform/triggers/scheduled-agents/) producing recurring **runs**.
### Can cloud agents keep docs up to date?
[Section titled “Can cloud agents keep docs up to date?”](#can-cloud-agents-keep-docs-up-to-date)
Yes. With cloud agents, agents can:
* Scan for drift (commands that no longer work, onboarding steps that changed).
* Run validations in a docs/test environment.
* Propose doc updates as PRs.
This is most successful with “docs as code” workflows (GitBook/Mintlify/Docusaurus style), where updates go through normal review.
## Self-hosting
[Section titled “Self-hosting”](#self-hosting)
### Where does my source code go with self-hosted agents?
[Section titled “Where does my source code go with self-hosted agents?”](#where-does-my-source-code-go-with-self-hosted-agents)
With self-hosting, repositories are cloned and stored only on your infrastructure — Warp never hosts your codebase. Warp uses a split architecture:
* **Execution plane (your infrastructure)** — Repository clones, build artifacts, runtime secrets, and container filesystem state stay on the machines you control.
* **Control plane (Warp-hosted)** — Session transcripts (which include code context from agent interactions), orchestration metadata, and LLM inference route through Warp’s backend under [Zero Data Retention (ZDR)](/enterprise/security-and-compliance/security-overview/#zero-data-retention-zdr) agreements. Warp does not persistently store your source code or use it for model training.
See [Self-hosting](/factories/self-hosting/) for deployment options and [Security Overview](/enterprise/security-and-compliance/security-overview/) for full details.
### Can I use `oz agent run` in CI or existing runners?
[Section titled “Can I use oz agent run in CI or existing runners?”](#can-i-use-oz-agent-run-in-ci-or-existing-runners)
Yes. The [unmanaged architecture](/platform/unmanaged-execution/) is designed exactly for this. Run `oz agent run` in any environment where you can execute a CLI command — GitHub Actions, Jenkins, Buildkite, Kubernetes pods, or custom orchestrators. This is how the [`warpdotdev/oz-agent-action`](https://github.com/warpdotdev/oz-agent-action) GitHub Action works. The agent runs locally on the runner and its session is tracked on Warp’s backend for observability.
### Can self-hosted agents access services behind a VPN?
[Section titled “Can self-hosted agents access services behind a VPN?”](#can-self-hosted-agents-access-services-behind-a-vpn)
Yes. Since self-hosted agents run on your infrastructure, they inherit your network access. This means agents can reach self-hosted GitLab/Bitbucket instances, internal APIs, databases, and any other services behind your VPN. This is one of the primary reasons teams choose self-hosting.
### Does self-hosting work with GitLab or other non-GitHub SCMs?
[Section titled “Does self-hosting work with GitLab or other non-GitHub SCMs?”](#does-self-hosting-work-with-gitlab-or-other-non-github-scms)
Self-hosted agents can use any SCM accessible from your infrastructure. With the [unmanaged architecture](/platform/unmanaged-execution/), agents run directly on your host and use whatever Git configuration and SCM access is already available. With the [managed architecture](/factories/self-hosting/#managed-architecture), automatic environment setup currently focuses on GitHub, but you can configure access to other SCMs via volume mounts, environment variables, setup commands, or Kubernetes Secrets (when using the [Kubernetes backend](/factories/self-hosting/managed-kubernetes/)). See the [GitLab](/platform/integrations/gitlab/) and [Bitbucket](/platform/integrations/bitbucket/) setup guides for step-by-step instructions.
### Do LLM requests still go through Warp with self-hosting?
[Section titled “Do LLM requests still go through Warp with self-hosting?”](#do-llm-requests-still-go-through-warp-with-self-hosting)
Yes. LLM inference routes through Warp’s backend, which has [Zero Data Retention (ZDR)](/enterprise/security-and-compliance/security-overview/#zero-data-retention-zdr) agreements with all contracted model providers. Enterprise teams that need full control over inference routing can use [Bring Your Own LLM (BYOLLM)](/enterprise/enterprise-features/bring-your-own-llm/) to route inference through their own cloud provider accounts. AWS Bedrock BYOLLM supports both interactive agents and cloud agent runs; [Gemini Enterprise (Vertex AI)](/enterprise/enterprise-features/byollm-gemini-enterprise/) BYOLLM currently applies to interactive agents, with cloud agent support coming.
### What about large monorepos with long environment setup times?
[Section titled “What about large monorepos with long environment setup times?”](#what-about-large-monorepos-with-long-environment-setup-times)
The [unmanaged architecture](/platform/unmanaged-execution/) is well-suited for large monorepos because agents run directly in your pre-provisioned environment — there is no Docker image build or repo cloning step. For the [managed architecture](/factories/self-hosting/#managed-architecture), the Docker backend supports volume mounts (`-v` flag) to mount a pre-existing repo checkout from the host into task containers. With the Kubernetes backend, use `pod_template` to configure persistent volume claims or pre-populated storage for the same purpose.
Note
The managed architecture supports four backends: Docker (default), Kubernetes, Direct, and Command. Use one-shot Direct when an external scheduler starts a worker for each job, or Command when a connected worker dispatches tasks to an external runtime. See [choosing a managed backend](/factories/self-hosting/#choosing-a-managed-backend).
### Do Kubernetes pods provide enough sandboxing for self-hosted agents?
[Section titled “Do Kubernetes pods provide enough sandboxing for self-hosted agents?”](#do-kubernetes-pods-provide-enough-sandboxing-for-self-hosted-agents)
This depends on your cluster configuration and risk profile. Evaluate your pod security policies, network policies, and RBAC settings based on your organization’s security requirements.
## Current limitations
[Section titled “Current limitations”](#current-limitations)
### Do cloud agents support image attachments?
[Section titled “Do cloud agents support image attachments?”](#do-cloud-agents-support-image-attachments)
Yes. In an interactive cloud conversation, attach an image with the file button in the input footer, paste an image from your clipboard, or drag and drop an image into the input.
See [Images as Context](/agents/local-agents/agent-context/images-as-context/) for supported formats and the separate legacy CLI file-attachment guidance.
# Handoff between local and cloud agents
Canonical page: [/platform/handoff/](https://docs.warp.dev/platform/handoff/)
> Understand how agent handoff moves work between local Warp sessions and cloud agent runs, including what context carries over in each direction.
Handoff moves agent work between local Warp sessions and cloud agent runs without making you restart the task. Depending on the direction, Warp carries over conversation history, workspace changes, and attachments so the receiving agent can continue from the prior session instead of starting from scratch.

The Handoff control in a local conversation.
## Directions of handoff
[Section titled “Directions of handoff”](#directions-of-handoff)
Handoff supports three directions:
* **Local to cloud** - Promote a local Warp Agent conversation to a cloud agent run when you need more compute, longer-running work, or parallel variants of the same task. The cloud agent starts from your conversation history and a snapshot of your uncommitted workspace changes. See [Handoff from local to cloud](/platform/handoff/local-to-cloud/).
* **Cloud to cloud** - Send a follow-up to a cloud run after its session has ended. The run continues in the same conversation, with the prior session’s workspace state restored. See [Handoff from cloud to cloud](/platform/handoff/cloud-to-cloud/).
* **Cloud to local** - Fork a cloud conversation into a local Warp session with **Continue locally** or `/continue-locally`. See [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/#5-fork-the-session-to-your-local-warp).
```
flowchart TD
Local("Local Warp session")
Cloud1("Cloud agent run")
Cloud2("Cloud agent run (follow-up)")
NewLocal("New local Warp session")
Local -- "Local to cloud" --> Cloud1
Cloud1 -- "Cloud to cloud" --> Cloud2
Cloud1 -- "Cloud to local" --> NewLocal
```
### Third-party agent runtime coverage
[Section titled “Third-party agent runtime coverage”](#third-party-agent-runtime-coverage)
Handoff coverage depends on which agent is running the conversation:
* **Cloud to cloud** works for the Warp Agent and the [third-party cloud harnesses currently supported in the Automation Platform](/platform/harnesses/): Claude Code and Codex. For Claude Code and Codex runs, click **Continue**, then enter your follow-up prompt. Warp Agent runs use the streamlined follow-up input.
* **Local to cloud** works for the Warp Agent. It isn’t available for third-party CLI agent sessions.
## What carries over
[Section titled “What carries over”](#what-carries-over)
Handoff preserves enough state that the receiving agent can resume the work, not only read about it.
* **Conversation history** - The receiving agent sees the full transcript of the prior session. Local-to-cloud forks the conversation so the source isn’t modified; cloud-to-cloud continues in the same conversation.
* **Workspace state** - Local-to-cloud and cloud-to-cloud capture the prior session’s repository changes (tracked and untracked) and apply them in the receiving run before the agent answers the next prompt. The cloud-to-local direction doesn’t currently apply workspace patches to your local checkout; review the cloud agent’s branch or pull request artifact to inspect those changes.
* **Conversation attachments** - Files attached during the prior session remain available to the receiving agent.
Handoff is best-effort. When the receiving agent can apply the prior session’s changes cleanly, it picks up where the prior agent left off. When it can’t, the agent reports which changes failed to apply and continues with the changes that applied cleanly.
## When to use handoff
[Section titled “When to use handoff”](#when-to-use-handoff)
Each direction has a clear motivating workflow.
* **Local to cloud** - Use when a local conversation has grown into work that’s better done in the cloud: long-running tasks you don’t want to keep your laptop awake for, [parallel variants of the same task](/platform/orchestration/), or steering work from another device once it’s running.
* **Cloud to cloud** - Use when a cloud agent finished and you want to send a follow-up without losing the prior workspace state. Also useful when a [Slack-triggered](/platform/integrations/slack/) or [scheduled](/platform/triggers/scheduled-agents/) run completes and someone on the team wants to push it further.
* **Cloud to local** - Use when a cloud agent has done the heavy lifting and you want to take over locally to verify, iterate, or polish before shipping.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Cloud agents overview](/platform/) - What cloud agents are, when to use them, and how they fit into the Automation Platform.
* [Multi-agent orchestration](/platform/orchestration/) - Fan out parallel cloud variants after a local-to-cloud handoff.
* [Managing cloud agents](/platform/managing-cloud-agents/) - Inspect handoff runs from the Agent Management Panel in the Warp app or the Runs page in the Oz web app alongside local conversations.
* [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/) - Open and continue a cloud run locally with **Continue locally** or `/continue-locally`.
* [Cloud-synced conversations](/agents/local-agents/cloud-conversations/) - How conversations sync between local and cloud so handoff can find them.
* [Environments](/platform/environments/) - The runtime context a cloud agent runs in after a handoff.
# Handoff from cloud to cloud
Canonical page: [/platform/handoff/cloud-to-cloud/](https://docs.warp.dev/platform/handoff/cloud-to-cloud/)
> Send follow-up instructions to a finished cloud agent run. The run continues with restored workspace state, so the agent picks up where it left off.
Cloud-to-cloud handoff in Warp lets you send follow-up instructions to a finished cloud agent run and continue it in a fresh cloud session. The run keeps the same conversation and restores the prior workspace state, so the agent can pick up where it left off instead of starting over.
Watch this walkthrough to see how cloud-to-cloud handoff continues a cloud agent run without losing the prior session context.

Use this handoff direction when:
* You want to send a follow-up to a cloud agent after its session has ended.
* You want to continue a background cloud agent run, such as a scheduled or integration-triggered run, while preserving it as a single unit of work in the [Agent Management Panel](/platform/managing-cloud-agents/) in the Warp app and the [Runs page in the Oz web app](/platform/oz-web-app/#runs).
## What carries over
[Section titled “What carries over”](#what-carries-over)
When you send a follow-up to a run whose session has ended, the run continues with:
* **The same conversation** - The follow-up is appended to the same conversation. From your perspective, the run is one continuous conversation across sessions.
* **The prior workspace state** - The prior session’s repository changes (tracked and untracked) are restored before the agent answers your follow-up. For Git-managed sessions, the new session continues on the same Git branch. You can [customize which repositories and files get snapshotted](/platform/handoff/snapshots/) when running outside the bundled cloud agent image.
* **Stable run identity** - The run’s ID, task, creator, environment, schedule trigger, and integration source are preserved. Compute usage is recorded per session but rolls up to the same run.
If any changes fail to apply, the agent reports which changes failed and continues with the changes that applied cleanly.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **An ended cloud agent run** - The run must be in a terminal state, such as succeeded, failed, or canceled, and have an associated agent conversation. Blocked runs that are waiting on user input or approval can’t be continued via cloud-to-cloud handoff; respond to the prompt on the original run instead. Very old runs that predate the agent conversation model can’t be continued via handoff.
* **A snapshot from the prior session** - Cloud agent runs capture a workspace snapshot at the end of each session. If the prior session couldn’t capture one (for example, due to a transient storage error), the run still continues but without restored workspace state.
* **Access to the run** - You need permission to submit follow-ups for the run. For team runs, this is typically any team member. Cloud runs that originated from a local-to-cloud handoff can be continued only by the user who created them, not by other team members.
Caution
Cloud-to-cloud handoff relies on a snapshot from the prior session. Older cloud runs that don’t have a snapshot on file can’t be handed off; start a new run instead.
## Sending a follow-up
[Section titled “Sending a follow-up”](#sending-a-follow-up)
To continue an ended cloud run, open the run in Warp and send the next message in the conversation. When the original session has ended, Warp automatically starts a fresh cloud session and restores the prior workspace state.
1. **Open the ended cloud run.** Find it on the [Runs page](https://oz.warp.dev/runs) in the Oz web app or in the conversation panel in the Warp app.
2. **Send your follow-up.** Enter the next message in the conversation’s input and submit it.
The run picks up where it left off, with workspace state restored.
### Third-party agent runtimes
[Section titled “Third-party agent runtimes”](#third-party-agent-runtimes)
Cloud-to-cloud handoff also works for supported third-party agent runtimes, but the flow is slightly different from Warp Agent runs:
1. Open the ended run from the conversation panel in the Warp app, or from the artifacts shown after the run completes.
2. Click **Continue**.
3. Type your follow-up prompt and submit it.
## Inspecting a run that’s been handed off
[Section titled “Inspecting a run that’s been handed off”](#inspecting-a-run-thats-been-handed-off)
The [Agent Management Panel](/platform/managing-cloud-agents/) in the Warp app and the [Runs page in the Oz web app](/platform/oz-web-app/#runs) show one row per run, even when the run spans multiple sessions.
1. Open the [Agent Management Panel](/platform/managing-cloud-agents/) in the Warp app or the [Runs page in the Oz web app](/platform/oz-web-app/#runs).
2. Select the handed-off run.
3. Review the transcript. Each session appears in order, so you can see where one session ended and the next began.
Per-session timestamps aren’t currently exposed in the API; the transcript is the source of truth.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
**The run continued but no workspace state was restored.** The prior session didn’t capture a snapshot. This is rare but possible because snapshot capture is best-effort. The run still continues with the same conversation, so the agent has the full transcript context even without the workspace state.
**The run is in a terminal state with no conversation and follow-ups are rejected.** Very old runs predate the agent conversation model and can’t be continued via handoff. Start a new cloud agent run with the prompt you want, referencing the prior run if needed.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Handoff overview](/platform/handoff/) - What handoff is, the directions it supports, and what carries over.
* [Handoff from local to cloud](/platform/handoff/local-to-cloud/) - Promote a local conversation to a cloud run.
* [Managing cloud agents](/platform/managing-cloud-agents/) - Find runs to send follow-ups to.
# Handoff from local to cloud
Canonical page: [/platform/handoff/local-to-cloud/](https://docs.warp.dev/platform/handoff/local-to-cloud/)
> Move an in-progress local Warp Agent conversation into a cloud agent run for longer-running work, parallel exploration, or remote follow-up.
Local-to-cloud handoff in Warp promotes an active local Warp Agent conversation into a cloud agent run. Warp forks the conversation, snapshots your uncommitted workspace changes, and sends both to the cloud so the agent can continue the same task with the context and files it needs.
Watch this walkthrough to see how to move a local Warp Agent conversation into a cloud agent run.

Use this handoff direction when:
* You have a long-running task and don’t want to keep your laptop awake.
* You want to fan out variants of the same task across multiple cloud agents in parallel.
* You want to walk away and check on the agent from a different device.
* You want the agent to keep working while you start a new conversation locally.
## What the cloud agent receives
[Section titled “What the cloud agent receives”](#what-the-cloud-agent-receives)
When you hand off from local to cloud, the receiving cloud agent inherits:
* **A forked conversation** - Warp forks your local conversation so the cloud agent inherits the full transcript without modifying the source. See [Cloud-synced conversations](/agents/local-agents/cloud-conversations/) for related sync behavior.
* **A workspace snapshot** - Warp captures your uncommitted repository changes, including both tracked modifications and untracked files, and packages them for the cloud agent. The cloud agent applies them before answering your follow-up.
* **Conversation attachments** - Files attached to the local conversation remain available in the cloud run.
If any changes fail to apply in the cloud run, the cloud agent reports which changes failed and continues with the changes that applied cleanly.
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **An active local conversation** - Have a [Warp Agent](/agents/) conversation open in Warp with the work you want to hand off.
* **A configured environment** - The cloud agent needs an [environment](/platform/environments/) that includes the same repositories you’re working in locally. The environment’s repos must match your local checkout so the workspace snapshot applies cleanly.
* **Cloud conversation storage enabled** - In the Warp app, go to **Settings** > **Privacy** and turn on **Store AI conversations in the cloud** so the conversation can be forked. See [Cloud-synced conversations](/agents/local-agents/cloud-conversations/).
* **Sufficient credits** - Cloud agent runs consume credits. See [Credits](/support-and-community/plans-and-billing/credits/) for how credit usage works, and [Access, billing, and identity](/platform/team-access-billing-and-identity/) for team-specific credit requirements.
## Handing off a conversation to the cloud
[Section titled “Handing off a conversation to the cloud”](#handing-off-a-conversation-to-the-cloud)
1. **Open the handoff flow from your active conversation.** With the local conversation focused, press `&` or run the `/handoff` slash command. Either entry point opens the handoff flow scoped to the current conversation. The `/cloud-agent` slash command always starts a fresh cloud conversation and isn’t an entry point for handoff.
2. **Choose the environment for the cloud run.** Pick the one whose repositories match the directories your local conversation has been editing. If you don’t have a matching environment yet, create one and add the repos you’ve been working in.
3. **Add a follow-up prompt and submit.** Enter the next message you want the cloud agent to act on.
The `&` entry point and `/handoff` slash command both open the same handoff flow.

The ampersand handoff entry point.

The `/handoff` slash command.
After the flow opens, choose the cloud environment and add the follow-up prompt the cloud agent should act on.

The environment selector in the handoff flow.

A follow-up prompt before handoff.
Note
The cloud agent runs with the same model your local conversation was using. Changing the model during handoff isn’t supported.
After you submit, the cloud agent applies your workspace snapshot and responds to your follow-up. The local conversation is not modified, so you can keep working in it locally or close it.
To check on the new run, open it from the [Runs page](https://oz.warp.dev/runs) in the Oz web app or the conversation panel in the Warp app.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
**The cloud agent reports that some changes couldn’t be applied.** The most common cause is a repository mismatch between your local checkout and the environment. The workspace snapshot is generated against your local repo’s current state; the environment must be on a compatible branch and commit for the changes to apply cleanly. Switch the environment’s repo to the branch you were on locally and retry the handoff.
**The cloud agent doesn’t see my uncommitted changes.** Cloud conversation storage must be enabled for handoff to work. In the Warp app, open **Settings** > **Privacy** and confirm **Store AI conversations in the cloud** is on. Otherwise, the conversation can’t be forked and the run falls back to starting over.
**The conversation doesn’t appear in the cloud run.** The source conversation may not have finished syncing to the cloud when you triggered the handoff. Wait a moment and retry. If the problem persists, check the conversation panel in the Warp app to confirm the conversation has a cloud-synced indicator.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Handoff overview](/platform/handoff/) - What handoff is, the directions it supports, and what carries over.
* [Handoff from cloud to cloud](/platform/handoff/cloud-to-cloud/) - Continue a finished cloud run with workspace state restored.
* [Environments](/platform/environments/) - Configure the repos, image, and setup commands the cloud agent starts in.
* [Multi-agent orchestration](/platform/orchestration/) - Fan the handed-off work across parallel cloud child agents.
* [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/) - Open and steer the cloud run after handoff.
* [Cloud agents quickstart](/platform/quickstart/) - Run your first cloud agent from scratch.
# Customizing workspace snapshots
Canonical page: [/platform/handoff/snapshots/](https://docs.warp.dev/platform/handoff/snapshots/)
> Customize which repositories and files Warp snapshots at the end of a cloud agent run, so handoff continues to work outside the bundled cloud agent image.
Workspace snapshots are how [handoff](/platform/handoff/) carries repository changes and other workspace state across cloud agent runs. At the end of every cloud agent run, Warp asks a small declarations script which repositories and files to snapshot, then uploads the resulting git diffs and file contents so the next cloud agent run can apply them.
Warp’s bundled cloud agent image ships with a declarations script that snapshots every Git repository under the agent’s workspace, so most cloud agent runs need no configuration. This page is for the cases where you need to customize what gets snapshotted — for example, when running cloud agents in a custom Docker image, on a self-hosted [Direct backend](/factories/self-hosting/managed-direct/), or as an [unmanaged](/platform/unmanaged-execution/) `oz agent run` in CI.
## When to customize snapshots
[Section titled “When to customize snapshots”](#when-to-customize-snapshots)
The default snapshotting behavior covers the most common case: snapshot every Git repository the agent worked on, inside the bundled cloud agent image. Customize snapshots when you need different behavior:
* **You’re running outside the bundled image** — for example, a custom Docker base image, a self-hosted Direct backend, or unmanaged `oz agent run` invocations — where Warp’s default `snapshot-declarations.sh` isn’t on disk.
* **You want to snapshot repos or files outside the agent’s workspace** — for example, a sibling repo the agent reads but doesn’t `cd` into, or a log file the agent writes to `/tmp`.
* **You want dynamic snapshotting behavior** — because the declarations file is generated by a script that Warp runs, you can script any logic you want (filter by git status, dedupe against a baseline, emit a fixed list, etc.) rather than being limited to a static set of paths.
If you don’t customize snapshots in any of these cases, the run still completes — Warp just uploads nothing, and handoff into the next run starts without the prior session’s uncommitted changes.
## How snapshotting works
[Section titled “How snapshotting works”](#how-snapshotting-works)
There are two ways to tell Warp what to snapshot at the end of a cloud agent run:
* **Script-driven** (default in the bundled image) - Warp invokes a declarations script (configured via the `OZ_SNAPSHOT_DECLARATIONS_SCRIPT` environment variable) that emits one JSON line per repository or file to snapshot. Use this when the set of repos isn’t fixed ahead of time (for example, the agent may `git init` a new directory during its work) or when you want any other dynamic logic to decide what to snapshot.
* **Static** - You pre-populate the declarations file yourself (at the path given by `OZ_SNAPSHOT_DECLARATIONS_FILE`) and skip the script. Use this when the same set of repos and files should be snapshotted on every run.
### Script-driven flow
[Section titled “Script-driven flow”](#script-driven-flow)
1. **Warp invokes your declarations script.** The script path comes from the `OZ_SNAPSHOT_DECLARATIONS_SCRIPT` environment variable. Warp runs it with the agent’s workspace as the current directory.
2. **Warp passes a per-run output file.** Warp sets `OZ_SNAPSHOT_DECLARATIONS_FILE` to an absolute path the script must write to. Each run gets its own file so concurrent runs don’t clobber each other.
3. **Warp reads the declarations file.** Warp parses the JSONL output (described below) and uploads the listed repositories and files.
See [Write a custom declarations script](#write-a-custom-declarations-script) for the full pattern.
### Static flow
[Section titled “Static flow”](#static-flow)
Set `OZ_SNAPSHOT_DECLARATIONS_FILE` to a path you’ve already populated and leave `OZ_SNAPSHOT_DECLARATIONS_SCRIPT` unset. Warp reads the file directly with no script invocation. See [Use a static declarations file](#use-a-static-declarations-file) for the full pattern.
In both flows, snapshotting is automatically enabled for cloud agent runs when cloud conversations are enabled, and can be turned off per run with `--no-snapshot`. See [Disable snapshots](#disable-snapshots) below.
## Environment variables
[Section titled “Environment variables”](#environment-variables)
* **`OZ_SNAPSHOT_DECLARATIONS_SCRIPT`** - Absolute path to the script Warp invokes at the end of each cloud agent run. The bundled cloud agent image sets this automatically. Set it yourself when running outside the bundled image.
* **`OZ_SNAPSHOT_DECLARATIONS_FILE`** - Absolute path to the JSONL file the script writes to (and Warp reads from). When `OZ_SNAPSHOT_DECLARATIONS_SCRIPT` is set, Warp picks a per-run path by default and exports it to the script. Set or override this variable yourself when you want Warp to read from a static, pre-populated declarations file instead of running a script, or whenever you want both Warp and the script to use a specific path you control.
## Declarations file format
[Section titled “Declarations file format”](#declarations-file-format)
The declarations file is UTF-8 JSONL — one JSON object per non-empty line:
snapshot-declarations.jsonl
```json
{"version":1,"kind":"repo","path":"/workspace/my-repo"}
{"version":1,"kind":"file","path":"/tmp/agent-output.log"}
```
Each line has exactly these fields:
* **`version`** - Always `1`. Reserved for future schema versions.
* **`kind`** - Either `"repo"` or `"file"`.
* **`path`** - A non-empty absolute path.
A few rules to follow when writing declarations:
* **Paths must be absolute.** Relative paths are rejected and logged as malformed.
* **Prefer `repo` over `file` for paths inside a repository.** Warp generates a git diff for each `repo` entry (tracked changes plus untracked, non-gitignored files), so individual `file` entries inside that repo are redundant and dropped before upload. Including a `repo` entry is also more extensible than enumerating files.
* **Repos are diffed, not copied wholesale.** Only changed files are uploaded for each `repo` entry, so listing a large repository is cheap when the agent’s changes are small.
* **`file` entries are for paths outside any declared repo** — for example, logs the agent wrote to `/tmp` or scratch files in `$HOME`.
Malformed lines (invalid JSON, missing fields, unknown `kind`, non-absolute path) are logged as warnings and skipped; they never abort the upload.
Caution
**Declared paths are uploaded to Warp.** `file` entries upload the file’s contents verbatim, and `repo` entries upload the repo’s git diff (tracked changes plus untracked, non-gitignored files). Before declaring logs, scratch files, or other agent outputs as `file` entries, make sure they don’t contain secrets, credentials, API tokens, or other sensitive data.
## Write a custom declarations script
[Section titled “Write a custom declarations script”](#write-a-custom-declarations-script)
A custom script writes one JSON line per repository or file it wants Warp to snapshot, then exits. The minimal pattern looks like this:
snapshot-declarations.sh
```bash
#!/bin/bash
set -euo pipefail
# Warp sets this to a per-run output path. Fail loudly if it's missing,
# so a misconfigured runner doesn't silently overwrite a shared file.
if [ -z "${OZ_SNAPSHOT_DECLARATIONS_FILE:-}" ]; then
echo "OZ_SNAPSHOT_DECLARATIONS_FILE must be set" >&2
exit 1
fi
mkdir -p "$(dirname "$OZ_SNAPSHOT_DECLARATIONS_FILE")"
# Find every git repo under the agent's workspace and emit a JSONL
# repo declaration for each one. Escape backslashes and double quotes in
# the path before writing so paths containing those characters don't
# produce malformed JSON (which Warp skips with a warning).
find "$PWD" -type d -name .git -prune -print 2>/dev/null \
| while IFS= read -r git_dir; do
repo_root="$(cd "$(dirname "$git_dir")" && pwd)"
repo_json="$(printf '%s' "$repo_root" | sed 's/\\/\\\\/g; s/"/\\"/g')"
printf '{"version":1,"kind":"repo","path":"%s"}\n' "$repo_json" \
>> "$OZ_SNAPSHOT_DECLARATIONS_FILE"
done
```
Then point Warp at it by exporting `OZ_SNAPSHOT_DECLARATIONS_SCRIPT` in the environment your cloud agent runs in:
```bash
export OZ_SNAPSHOT_DECLARATIONS_SCRIPT=/path/to/snapshot-declarations.sh
```
For a managed [Direct backend](/factories/self-hosting/managed-direct/) worker, set it via the worker’s `environment` config so it’s present when the agent process starts.
### The full bundled script
[Section titled “The full bundled script”](#the-full-bundled-script)
For reference, this is the canonical declarations script Warp invokes inside the bundled cloud agent image. It’s a richer version of the minimal example above: it honors a colon-separated `OZ_SNAPSHOT_SCAN_ROOTS` override for operators who need to scan repos outside the default workspace, uses `jq` for canonical JSON encoding (which handles `"` and `\` escaping for you), and dedupes against repo declarations already written in the same run so repeated invocations stay additive.
Note
The bundled script defaults `OZ_SNAPSHOT_JQ` to `/agent/tools/jq`, which only exists inside Warp’s cloud agent image. If you adapt this script for a different image or for an unmanaged `oz agent run`, put `jq` on `PATH` or set `OZ_SNAPSHOT_JQ` to its absolute path.
snapshot-declarations.sh
```bash
#!/bin/bash
# Generates the declarations file consumed by the end-of-run snapshot upload pipeline.
#
# Scans one or more roots for `.git` directories and appends one JSON object per
# newly-discovered repository to the declarations file.
#
# Scan root selection (in order of precedence):
# - OZ_SNAPSHOT_SCAN_ROOTS: colon-separated list of absolute paths. Operators can use this
# to target repos outside the default workspace.
# - $PWD: the Rust driver sets this to the agent's workspace via `Command::current_dir`
# before invoking the script, so the default scan root is always the assigned workspace.
#
# Output file:
# - OZ_SNAPSHOT_DECLARATIONS_FILE must be set. The Rust driver sets this to a per-run path
# so concurrent runs don't clobber each other.
# - The file is created if missing, and appended to if it already exists. Existing lines are
# never rewritten, so operator-authored declarations are preserved.
# - Repeated invocations within a single run skip already-emitted repo declarations so the
# upload pipeline can stay additive without duplicating identical generated entries.
set -euo pipefail
SCAN_ROOTS_RAW="${OZ_SNAPSHOT_SCAN_ROOTS:-$PWD}"
IFS=':' read -r -a SCAN_ROOTS <<< "$SCAN_ROOTS_RAW"
if [ -z "${OZ_SNAPSHOT_DECLARATIONS_FILE:-}" ]; then
echo "OZ_SNAPSHOT_DECLARATIONS_FILE must be set" >&2
exit 1
fi
DECL_FILE="$OZ_SNAPSHOT_DECLARATIONS_FILE"
JQ="${OZ_SNAPSHOT_JQ:-/agent/tools/jq}"
mkdir -p "$(dirname "$DECL_FILE")"
touch "$DECL_FILE"
# Dedup set. Seed from repo declarations already emitted by this script so a repeated
# invocation within the same run doesn't re-emit repos it already discovered earlier.
# Keep the full canonical JSON line as the key; this lets us preserve unrelated JSONL entries
# verbatim while ensuring identical generated declarations are emitted at most once.
SEEN_FILE="$(mktemp)"
trap 'rm -f "$SEEN_FILE"' EXIT
"$JQ" --raw-input --compact-output '
fromjson?
| select(
type == "object"
and (. | keys_unsorted | sort == ["kind", "path", "version"])
and .version == 1
and .kind == "repo"
and (.path | type == "string")
)
| { version: 1, kind: "repo", path: .path }
' "$DECL_FILE" > "$SEEN_FILE"
repo_declaration_for_path() {
"$JQ" --compact-output --null-input \
--arg path "$1" \
'{ version: 1, kind: "repo", path: $path }'
}
for root in "${SCAN_ROOTS[@]}"; do
[ -d "$root" ] || continue
while IFS= read -r git_dir; do
repo_root="$(cd "$(dirname "$git_dir")" && pwd)"
repo_declaration="$(repo_declaration_for_path "$repo_root")"
if grep -Fxq -- "$repo_declaration" "$SEEN_FILE"; then
continue
fi
printf '%s\n' "$repo_declaration" >> "$SEEN_FILE"
printf '%s\n' "$repo_declaration" >> "$DECL_FILE"
done < <(find "$root" -type d -name .git -prune -print 2>/dev/null)
done
```
## Use a static declarations file
[Section titled “Use a static declarations file”](#use-a-static-declarations-file)
If the same set of repositories or files should be snapshotted on every run (for example, an unmanaged GitHub Actions job operating on a known checkout), you can skip the script entirely and pre-populate a JSONL file:
/etc/oz/snapshot-declarations.jsonl
```json
{"version":1,"kind":"repo","path":"/workspace/my-repo"}
{"version":1,"kind":"repo","path":"/workspace/shared-libs"}
```
Then point Warp at the file directly:
```bash
export OZ_SNAPSHOT_DECLARATIONS_FILE=/etc/oz/snapshot-declarations.jsonl
# Do not set OZ_SNAPSHOT_DECLARATIONS_SCRIPT in this mode.
```
Warp reads the file at end-of-run and uploads the listed repos and files. Because the file is the same on every run, this is best for environments where the workspace layout is fixed.
## Disable snapshots
[Section titled “Disable snapshots”](#disable-snapshots)
To opt out of snapshotting for a single run, pass `--no-snapshot` to the CLI:
```bash
oz agent run-cloud --prompt "Fix the failing test" --no-snapshot
```
Snapshotting is also skipped automatically when cloud conversations are disabled for the team.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Handoff from local to cloud](/platform/handoff/local-to-cloud/) - Promote a local conversation to a cloud run; the workspace snapshot is what carries your uncommitted changes across.
* [Handoff from cloud to cloud](/platform/handoff/cloud-to-cloud/) - Continue a finished cloud run; the prior session’s workspace snapshot is what gets restored.
* [Self-hosting overview](/factories/self-hosting/) - Architecture decision guide for self-hosted workers, where customizing snapshots is most often needed.
* [Unmanaged architecture](/platform/unmanaged-execution/) - Run `oz agent run` in CI, Kubernetes, or your dev environment outside the bundled image.
* [Oz CLI](/agents/cli/oz-cli/) - Full reference for `oz agent run` and `oz agent run-cloud`.
# Harnesses in the Automation Platform
Canonical page: [/platform/harnesses/](https://docs.warp.dev/platform/harnesses/)
> Run third-party harnesses such as Claude Code or Codex as cloud agents. They inherit the same triggers, environments, secrets, and observability as Warp Agent.
The Automation Platform can run third-party agent harnesses as cloud agents alongside Warp Agent, including [Claude Code](/platform/harnesses/claude-code/) and [Codex](/platform/harnesses/codex/). You choose the harness (agent runtime) that fits the task; the platform around the run stays the same.
For a factory, set the default or per-agent harness in its [factory definition](/factories/factory-as-code/#agentdefaultsharness) or configure it for a [factory agent](/factories/factory-agents/).
Watch this walkthrough to see how to run Warp Agent, Claude Code, or Codex as a cloud agent.

## What stays the same
[Section titled “What stays the same”](#what-stays-the-same)
Third-party harnesses inherit the same Automation Platform features as Warp Agent:
* **Triggers** — Slack, Linear, schedules, CI, and API [triggers](/platform/triggers/) launch any harness.
* **Environments and secrets** — Reuse the same [environments](/platform/environments/) and [agent secrets](/platform/secrets/).
* **Skills and Rules** — Saved [Skills](/agents/capabilities/skills/) and [Rules](/agents/capabilities/rules/) apply across harnesses.
* **Observability** — Every run produces a transcript and shareable session in the [cloud agent dashboard](/platform/managing-cloud-agents/).
## Plan requirements
[Section titled “Plan requirements”](#plan-requirements)
Third-party harnesses require a paid plan. On the Free plan, cloud agent runs use Warp Agent, and choosing another harness returns an upgrade prompt. See [Warp pricing](https://www.warp.dev/pricing) for what each plan includes.
## Billing
[Section titled “Billing”](#billing)
Claude Code and Codex each call their provider directly using credentials you supply, and the provider bills your account for inference. Warp meters [compute credits](/support-and-community/plans-and-billing/credits/#compute-credits) for the run’s sandbox and [platform credits](/support-and-community/plans-and-billing/platform-credits/) for the [multi-agent orchestration](/platform/orchestration/) layer.
## How to switch harnesses
[Section titled “How to switch harnesses”](#how-to-switch-harnesses)
### Warp app
[Section titled “Warp app”](#warp-app)
In Cloud Mode, choose a harness from the **Agent harness** dropdown above the input.

The Agent harness selector.
Note
You can enter Cloud Mode by creating a new **Cloud Agent** tab or by using the `/cloud-agent` slash command.
### Web app
[Section titled “Web app”](#web-app)
On the new run or new schedule pane, choose the harness in the **Harness** field.
### API and SDK
[Section titled “API and SDK”](#api-and-sdk)
Set the `harness` field on the agent config to one of the [harness identifiers](#harness-identifiers) below. See the [API reference](/factories/api-and-sdk/) for the exact field names.
## Harness identifiers
[Section titled “Harness identifiers”](#harness-identifiers)
Surfaces that take the harness as a string use `oz` for the Warp Agent, `claude` for Claude Code, and `codex` for Codex. Write `claude` for Claude Code — not `claude-code` — unless the surface explicitly accepts that alias:
* **API and SDK** — the agent config’s `harness.type` accepts `oz`, `claude`, or `codex`.
* **CLI** — `oz agent run-cloud --harness` accepts the same identifiers, plus `claude-code` as an alias for `claude`.
* **Factory definition files** — [`harness.type`](/factories/factory-as-code/#agentdefaultsharness) accepts `oz`, `claude`, or `codex`, plus `claude-code` as an alias for `claude`.
Where the alias is accepted, it selects the same Claude Code harness as `claude`. Everywhere else — including the API — only the canonical identifiers are valid, so prefer them in anything you script, sync, or store.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Warp Agent with the Automation Platform](/platform/harnesses/warp-agent/) — the Automation Platform‘s default first-party harness.
* [Claude Code with the Automation Platform](/platform/harnesses/claude-code/) — Claude Code as a cloud harness.
* [Codex with the Automation Platform](/platform/harnesses/codex/) — Codex as a cloud harness.
* [Authentication](/platform/harnesses/authentication/) — connect credentials and launch Claude Code or Codex.
* [Multi-agent orchestration](/platform/orchestration/) — run parent and child agents across harnesses and locations.
* [Third-party CLI agents in the Warp terminal](/agents/cli-agents/overview/) — run Claude Code, Codex, and other CLI agents locally.
# Third-party cloud agent authentication
Canonical page: [/platform/harnesses/authentication/](https://docs.warp.dev/platform/harnesses/authentication/)
> Connect Anthropic or OpenAI credentials to the Automation Platform to run Claude Code or Codex as cloud agents.
Third-party cloud agent authentication in the Automation Platform stores provider credentials for cloud runs as Warp-managed secrets. Third-party cloud agents, like [Claude Code](#connecting-claude-code-credentials) and [Codex](#connecting-codex-credentials), call their providers directly, so set up an Anthropic or OpenAI credential once before launching a third-party harness.
Auth secrets can be scoped to a **team** (available to all teammates’ runs) or **personal** (only your own runs), like any other Warp-managed secret. A [factory agent](/factories/factory-agents/#configuring-a-third-party-harness) can only select team-scoped secrets, since a factory’s runs aren’t tied to one person. Personal secrets remain available when you start an ad hoc cloud run.
Note
[Bring Your Own Key (BYOK)](/agents/inference/bring-your-own-api-key/) configured in the Warp desktop app applies to local agent runs only. Cloud runs of Claude Code and Codex always use Warp-managed secrets.
## Connecting Claude Code credentials
[Section titled “Connecting Claude Code credentials”](#connecting-claude-code-credentials)
Claude Code is Anthropic’s agentic coding tool. For more on Claude Code authentication, see [Anthropic’s Claude Code auth docs](https://code.claude.com/docs/en/authentication).
### Create an Anthropic API key
[Section titled “Create an Anthropic API key”](#create-an-anthropic-api-key)
1. Go to the [Anthropic Console](https://platform.claude.com/login?returnTo=/?) and sign in or create an account.
2. Confirm your account has API credits. Claude Code runs are billed against your Anthropic API balance.
3. Navigate to the API keys section, then click **Get API key**.
4. Create a new API key and copy the value.
The Automation Platform also supports Bedrock-routed credentials (**Anthropic Bedrock API key** and **Anthropic Bedrock access key**) if your team consumes Anthropic models through AWS.
### Store the API key
[Section titled “Store the API key”](#store-the-api-key)
#### Warp desktop app
[Section titled “Warp desktop app”](#warp-desktop-app)
Start a new cloud agent run and choose **Claude Code** from the **Agent harness** dropdown. In the harness auth secret field, add or select your Anthropic credential.
#### Web app
[Section titled “Web app”](#web-app)
Start a [new run](https://oz.warp.dev/runs/new), choose **Claude Code** as the harness, and add a new key in the Claude Code auth secret dialog.
The Claude Code auth secret dialog.
#### CLI
[Section titled “CLI”](#cli)
```bash
oz secret create claude api-key --team <KEY_NAME>
```
Add `--description "..."` to record rotation notes or owner info. Replace `--team` with `--personal` to make the secret available only to your own runs.
**Expected outcome.** `oz secret list` shows the new secret with the matching Anthropic credential type. The value is never displayed.
## Connecting Codex credentials
[Section titled “Connecting Codex credentials”](#connecting-codex-credentials)
Codex is OpenAI’s coding agent. For more on Codex authentication, see [OpenAI’s Codex auth docs](https://developers.openai.com/codex/auth).
Caution
A ChatGPT subscription (Plus, Pro, Team) does not include API access. You need a separate OpenAI API key with API credits.
### Create an OpenAI API key
[Section titled “Create an OpenAI API key”](#create-an-openai-api-key)
1. Go to the [OpenAI Platform](https://platform.openai.com/) and sign in (or create an account).
2. Confirm your account has API credits. Codex runs are billed against your OpenAI API balance, not a ChatGPT subscription.
3. Navigate to the API keys section, then click **Create API key**.
4. In the **Create new secret key** dialog, choose the owner, project, and permissions for the key.
5. Click **Create secret key**, then copy the value.
### Store the API key
[Section titled “Store the API key”](#store-the-api-key-1)
#### Warp desktop app
[Section titled “Warp desktop app”](#warp-desktop-app-1)
Start a new cloud agent run and choose **Codex** from the **Agent harness** dropdown. In the harness auth secret field, add or select your OpenAI credential.
#### Web app
[Section titled “Web app”](#web-app-1)
Start a [new run](https://oz.warp.dev/runs/new), choose **Codex** as the harness, and add a new key in the Codex auth secret dialog.
#### CLI
[Section titled “CLI”](#cli-1)
```bash
oz secret create codex api-key --team <KEY_NAME>
```
Add `--description "..."` to record rotation notes or owner info. Replace `--team` with `--personal` to make the secret available only to your own runs.
**Expected outcome.** `oz secret list` shows the new secret with the matching OpenAI credential type. The value is never displayed.
## Managing harness auth secrets
[Section titled “Managing harness auth secrets”](#managing-harness-auth-secrets)
Auth secrets follow the same management commands as any other Warp-managed secret. See [Cloud agent secrets](/platform/secrets/) for the full reference. Common tasks:
```bash
# List secrets you can see
oz secret list
# Rotate a secret value (prompts for the new value)
oz secret update --team --value ANTHROPIC_API_KEY
# Update the description
oz secret update --team --description "Rotated 2026-05-12; owned by platform team" ANTHROPIC_API_KEY
# Delete a secret (irreversible)
oz secret delete --team ANTHROPIC_API_KEY
```
Caution
Deleting an auth secret breaks any scheduled or integration-triggered run that references it by name. Update the schedules and integrations to point at a new secret first.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
**Claude Code or Codex run fails with an authentication error.**\
Confirm the run was started with a harness auth secret selected. From the Oz web app‘s run detail pane, the **Harness auth secret** field shows which secret (if any) was used. Re-launch the run with the correct secret selected, or create one if your team doesn’t have one yet.
**The harness auth secret dropdown is empty.**\
The dropdown only lists secrets whose type matches the selected harness — Anthropic types for Claude Code, OpenAI for Codex. If you stored the credential as a raw value, recreate it using the typed flow above.
**The selected harness is disabled.**\
Your team admin has disabled the harness for your workspace. Contact your admin or pick a different harness for the run.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Harnesses in the Automation Platform](/platform/harnesses/) — overview of third-party harnesses in the Automation Platform.
* [Claude Code in Warp](/agents/cli-agents/claude-code/) — run Claude Code locally in the Warp terminal.
* [Codex CLI in Warp](/agents/cli-agents/codex/) — run Codex locally in the Warp terminal.
* [Cloud agent secrets](/platform/secrets/) — the full Warp-managed secrets reference.
# Claude Code with the Automation Platform
Canonical page: [/platform/harnesses/claude-code/](https://docs.warp.dev/platform/harnesses/claude-code/)
> Run Claude Code with the Automation Platform. Strong at code review, deep bug investigation, large feature planning, and frontend or UI work.
Claude Code is Anthropic’s agentic coding tool. Running it with the Automation Platform puts Claude Code inside a Warp-managed environment and connects it to the rest of the Automation Platform — including triggers, environments, secrets, observability, and governance — while still behaving like the Claude Code your team already uses.
Note
This page covers Claude Code as a **cloud** harness, dispatched and orchestrated by the Automation Platform. To run Claude Code locally in your Warp terminal, see [Claude Code in Warp](/agents/cli-agents/claude-code/) instead.
## Key features
[Section titled “Key features”](#key-features)
* **Cloud orchestration** - Launch Claude Code from any Automation Platform trigger: the Warp app, the Oz web app, the Oz CLI, the REST API, [schedules](/platform/triggers/scheduled-agents/), [Slack](/platform/integrations/slack/) mentions, Linear issues, or GitHub Actions.
* **Claude model picker** - Choose the Claude model the harness uses, including the latest pinned Opus, Sonnet, and Haiku releases, the `best`/`opus`/`sonnet`/`haiku` aliases, and 1M-context variants.
* **First-class subagent** - A Warp Agent parent can dispatch Claude Code subagents to handle steps that require code review or nuanced judgment within a larger [multi-agent orchestration](/platform/orchestration/).
## Available models
[Section titled “Available models”](#available-models)
The Claude Code harness exposes Anthropic’s coding-tuned model lineup. Common choices include:
* `best` - Resolves to the current top-of-line Claude model.
* `opus`, `sonnet`, `haiku` - Aliases that resolve to the current default for that family.
For the full list — including 1M-context variants for very large codebases and planning-tuned models — open the model picker in the Warp app’s Cloud Mode or the **Model** field on the Oz web app‘s new-run pane.
## Credentials and billing
[Section titled “Credentials and billing”](#credentials-and-billing)
Claude Code calls Anthropic directly using credentials your team provides. The Automation Platform supports three Anthropic credential types, stored as [Warp-managed secrets](/platform/secrets/):
* **Anthropic API key** - For direct Anthropic API access.
* **Anthropic Bedrock API key** - For Bedrock-routed inference using an API key.
* **Anthropic Bedrock access key** - For Bedrock-routed inference using AWS access credentials.
Anthropic bills your account directly for inference. Warp still meters [compute credits](/support-and-community/plans-and-billing/credits/#compute-credits) for the run’s sandbox and [platform credits](/support-and-community/plans-and-billing/platform-credits/) for the orchestration layer.
For setup steps, see [Connecting Claude Code credentials](/platform/harnesses/authentication/#connecting-claude-code-credentials).
## Starting a Claude Code run
[Section titled “Starting a Claude Code run”](#starting-a-claude-code-run)
* **Warp app** - In Cloud Mode, click the **Agent harness** dropdown above the input and choose **Claude Code**.
* **Oz web app** - On the new run or new schedule pane, choose **Claude Code** in the **Harness** field. A **Claude Code auth secret** field appears below it; pick one of your stored Anthropic secrets.
* **API and SDK** - Set the agent config `harness` to `claude` — the [harness identifier](/platform/harnesses/#harness-identifiers) is `claude`, not `claude-code` — and the Anthropic secret name on the matching auth-secret field. See the [API reference](/factories/api-and-sdk/).
## Related pages
[Section titled “Related pages”](#related-pages)
* [Harnesses in the Automation Platform](/platform/harnesses/) — choose between Warp Agent, Claude Code, and Codex.
* [Authentication](/platform/harnesses/authentication/) — store Anthropic credentials as Warp-managed secrets.
* [Warp Agent with the Automation Platform](/platform/harnesses/warp-agent/) — the Automation Platform‘s default harness, the only one that can orchestrate Claude Code subagents.
* [Multi-agent orchestration](/platform/orchestration/) — coordinate a Warp Agent parent with Claude Code children across local and cloud runs.
* [Managing cloud agents](/platform/managing-cloud-agents/) — inspect Claude Code cloud runs in the Agent Management Panel and the Runs page.
* [Codex with the Automation Platform](/platform/harnesses/codex/) — Codex as a cloud harness.
* [Claude Code in Warp](/agents/cli-agents/claude-code/) — Claude Code in your local Warp terminal.
* [Factory agents](/factories/factory-agents/#configuring-a-third-party-harness) — configure Claude Code as a factory agent’s harness.
# Codex with the Automation Platform
Canonical page: [/platform/harnesses/codex/](https://docs.warp.dev/platform/harnesses/codex/)
> Run Codex with the Automation Platform for codebase migrations, release coordination, batch test generation, and backend or DevOps automation.
Codex is OpenAI’s coding agent. Running it with the Automation Platform puts Codex inside a Warp-managed environment and connects it to the rest of the Automation Platform — including triggers, environments, secrets, observability, and governance — while still behaving like the Codex CLI your team already uses.
Note
This page covers Codex as a **cloud** harness, dispatched and orchestrated by the Automation Platform. To run Codex locally in your Warp terminal, see [Codex CLI in Warp](/agents/cli-agents/codex/) instead.
## Key features
[Section titled “Key features”](#key-features)
* **Cloud orchestration** - Launch Codex from any Automation Platform trigger: the Warp app, the Oz web app, the Oz CLI, the REST API, [schedules](/platform/triggers/scheduled-agents/), [Slack](/platform/integrations/slack/) mentions, Linear issues, or GitHub Actions.
* **Codex model picker** - Choose the OpenAI model Codex uses, including the GPT-5 lineup and Codex-tuned variants, each available at a configurable reasoning level.
* **First-class subagent** - A Warp Agent parent can dispatch Codex subagents to handle high-volume or well-defined coding steps inside a larger [multi-agent orchestration](/platform/orchestration/).
## Available models
[Section titled “Available models”](#available-models)
The Codex harness exposes OpenAI’s Codex-tuned and general coding models, each available at a configurable reasoning level (low, medium, high, or extra-high). Common choices include:
* `gpt-5.6-sol`, `gpt-5.6-terra`, `gpt-5.6-luna` - The latest generation of Codex-tuned coding models.
* `gpt-5.5` - The prior generation’s coding model, still supported.
* `gpt-5.4`, `gpt-5.4-mini` - Fallback options for accounts without access to the newer models; `gpt-5.4-mini` is faster and lower-cost for lighter coding tasks or subagents.
* `gpt-5.3-codex` - An older Codex-tuned model, still available as an alternative.
Codex has no `default` model that picks automatically; every option names a specific model and reasoning level. For the full list, including Codex-tuned and general models, open the model picker on the Oz web app‘s new-run pane. For details on each model, see [OpenAI’s Codex model docs](https://developers.openai.com/codex/models).
## Credentials and billing
[Section titled “Credentials and billing”](#credentials-and-billing)
Codex calls OpenAI directly using credentials your team provides. The Automation Platform supports one credential type today, stored as a [Warp-managed secret](/platform/secrets/):
* **OpenAI API key** - The Codex harness authenticates to OpenAI using this key for every run.
OpenAI bills your account directly for inference. Warp still meters [compute credits](/support-and-community/plans-and-billing/credits/#compute-credits) for the run’s sandbox and [platform credits](/support-and-community/plans-and-billing/platform-credits/) for the orchestration layer.
For setup steps, see [Connecting Codex credentials](/platform/harnesses/authentication/#connecting-codex-credentials).
## Starting a Codex run
[Section titled “Starting a Codex run”](#starting-a-codex-run)
* **Warp app** - In Cloud Mode, click the **Agent harness** dropdown above the input and choose **Codex**.
* **Oz web app** - On the new run or new schedule pane, choose **Codex** in the **Harness** field. A **Codex auth secret** field appears below it; pick the OpenAI secret your team has stored.
* **API and SDK** - Set the agent config `harness` to `codex` and the OpenAI secret name on the matching auth-secret field. See the [API reference](/factories/api-and-sdk/).
## Related pages
[Section titled “Related pages”](#related-pages)
* [Harnesses in the Automation Platform](/platform/harnesses/) — choose between Warp Agent, Claude Code, and Codex.
* [Authentication](/platform/harnesses/authentication/) — store OpenAI credentials as Warp-managed secrets.
* [Warp Agent with the Automation Platform](/platform/harnesses/warp-agent/) — the Automation Platform‘s default harness, the only one that can orchestrate Codex subagents.
* [Multi-agent orchestration](/platform/orchestration/) — coordinate a Warp Agent parent with Codex children across local and cloud runs.
* [Managing cloud agents](/platform/managing-cloud-agents/) — inspect Codex cloud runs in the Agent Management Panel and the Runs page.
* [Claude Code with the Automation Platform](/platform/harnesses/claude-code/) — Claude Code as a cloud harness.
* [Codex CLI in Warp](/agents/cli-agents/codex/) — Codex in your local Warp terminal.
* [Factory agents](/factories/factory-agents/#configuring-a-third-party-harness) — configure Codex as a factory agent’s harness.
# Warp Agent with the Automation Platform
Canonical page: [/platform/harnesses/warp-agent/](https://docs.warp.dev/platform/harnesses/warp-agent/)
> Warp Agent is the default Automation Platform harness, with multi-model routing, full terminal access, and cross-harness subagent orchestration.
Warp Agent is the harness Warp builds and ships with the Automation Platform. It’s the default for every cloud agent run unless you pick another harness, and it’s the only harness that can spawn cross-harness subagents (for example, a Warp Agent parent dispatching a Claude Code or Codex child).
Warp Agent is the same agent runtime that powers Agent Mode in the Warp terminal. Running it as a cloud harness gives you the same behavior — model routing, tool access, Skills, Rules, Memory — without tying execution to a single laptop.
## Key features
[Section titled “Key features”](#key-features)
* **Multi-model auto-routing** - Routes between Anthropic, OpenAI, Google, and Fireworks-hosted models. Choose a specific model, or let Warp pick via `auto`, `auto-efficient`, `auto-genius`, or `auto-open`. See [Model choice](/agents/inference/model-choice/) for the full catalog.
* **Full terminal and tool access** - Runs commands, edits files, reads logs, executes tests, navigates repos, and calls MCP servers, giving cloud runs the same toolbelt Warp Agent uses locally.
* **Platform-native context** - Reads [Codebase Context](/agents/capabilities/codebase-context/), applies [Rules](/agents/capabilities/rules/), reuses saved [Skills](/agents/capabilities/skills/), and respects Memory and Warp Drive context with no extra setup.
* **Multi-repo execution** - Clones every repo configured on the [environment](/platform/environments/) and works across them in a single run.
* **Cross-harness orchestration parent** - A Warp Agent parent run can spawn Claude Code or Codex subagents and coordinate their outputs in [multi-agent orchestration](/platform/orchestration/). Other harnesses cannot act as parents in a multi-harness orchestration.
* **No extra credentials** - Warp Agent uses your existing Warp account and credits. There’s no separate API key to configure.
## How it works
[Section titled “How it works”](#how-it-works)
Warp Agent is the same agent runtime as Agent Mode in the Warp terminal: it plans, calls tools, edits code, runs tests, and reports progress. The cloud platform adds the [environment](/platform/environments/), triggers, observability, and team governance around the run, and the transcript is inspectable in real time and replayable afterward from the [cloud agent dashboard](/platform/managing-cloud-agents/).
Team admins can disable any harness for their workspace. Users on that team can only start runs with the harnesses that remain enabled.
### Available models
[Section titled “Available models”](#available-models)
Warp Agent supports the full Warp model catalog. Configure the model per [Agent Profile](/agents/capabilities/agent-profiles-permissions/), or pick one at run time. See [Model choice](/agents/inference/model-choice/) for the supported model IDs, including the `auto`, `auto-efficient`, `auto-genius`, and `auto-open` routing options.
### Cross-harness orchestration
[Section titled “Cross-harness orchestration”](#cross-harness-orchestration)
Warp Agent is the orchestration host for multi-harness runs. [Multi-agent orchestration](/platform/orchestration/) covers the parent/child model, run states, and patterns; a typical multi-harness pattern looks like:
1. A Warp Agent parent run analyzes a task and breaks it into subtasks.
2. The parent dispatches Claude Code subagents for steps that need careful review and Codex subagents for high-volume edits.
3. The parent collects results, resolves conflicts, and returns a single final output (a PR, a report, a Slack reply).
Subagents run in the same environment as the parent and share the same secrets, MCP servers, and integrations. The transcript shows the full tree, so reviewers can see exactly which subagent did what.
## When to choose Warp Agent
[Section titled “When to choose Warp Agent”](#when-to-choose-warp-agent)
* The task spans multiple repos, languages, or domains.
* You want model auto-routing instead of pinning one provider.
* The run needs to orchestrate other harnesses as subagents.
* You want the deepest integration with Warp’s platform features (Skills, Rules, Memory, Codebase Context).
* You’re not sure which harness fits — Warp Agent is the safe default and can delegate to other harnesses when it decides that’s the better fit.
## Starting a Warp Agent run
[Section titled “Starting a Warp Agent run”](#starting-a-warp-agent-run)
Warp Agent is the default, so there’s nothing extra to configure.
* **Warp app** - Start a cloud agent run from the input. The **Agent harness** dropdown defaults to **Warp Agent**.
* **Oz web app** - On a new run or new schedule pane, leave the **Harness** field set to **Warp Agent**.
* **Oz CLI** - Run `oz agent run-cloud --prompt "..."` with no `--harness` flag, or pass `--harness oz` explicitly.
* **API and SDK** - Omit the `harness` field on the agent config, or set it to `oz`. See the [API reference](/factories/api-and-sdk/).
For a complete walkthrough, see the [Cloud agents quickstart](/platform/quickstart/).
## Related pages
[Section titled “Related pages”](#related-pages)
* [Harnesses in the Automation Platform](/platform/harnesses/) — choose between Warp Agent, Claude Code, and Codex.
* [Claude Code with the Automation Platform](/platform/harnesses/claude-code/) — Claude Code as a cloud harness.
* [Codex with the Automation Platform](/platform/harnesses/codex/) — Codex as a cloud harness.
* [Multi-agent orchestration](/platform/orchestration/) — parent/subagent runs, including cross-harness subagents Warp Agent can spawn.
* [Model choice](/agents/inference/model-choice/) — the model catalog Warp Agent routes across.
* [Agent Profiles and permissions](/agents/capabilities/agent-profiles-permissions/) — configure the default model, autonomy, and tool access for Warp Agent.
* [Skills as agents](/platform/skills-as-agents/) — turn a saved skill into a reusable Warp Agent run.
# Integrations Overview
Canonical page: [/platform/integrations/](https://docs.warp.dev/platform/integrations/)
> Configure Warp's first-party integrations by creating environments, connecting GitHub, and enabling agents to run your code and automate development workflows.
Warp integrations let your team trigger agents directly from the terminal, or from tools like [Slack](/platform/integrations/slack/), [Linear](/platform/integrations/linear/), [Jira](/platform/integrations/jira/), and [GitHub](/platform/integrations/github/). Once set up, agents can:
* Read conversation or issue context
* Run code inside your codebase in a remote environment
* Open pull requests and perform other multi-step agent workflows on your behalf
For intake that routes work through a factory’s named agents and automations, use the [Factory integrations](/factories/connect-your-factory/) documentation.
Integrations are one way to start a cloud agent. For the full set, including schedules, the Oz CLI, and the API, see [Triggers](/platform/triggers/). If you’re deciding which one to use, see [Run agents unattended with schedules and triggers](/guides/agent-workflows/how-to-run-unattended-agents/).
Note
Warp has two distinct GitHub surfaces. The [GitHub integration](/platform/integrations/github/) starts agents when someone mentions `@warp-agent` on an issue, pull request, or review comment, using the [Warp Factories](/factories/) GitHub App. [GitHub Actions](/platform/integrations/github-actions/) runs agents inside workflows you define in your own CI pipeline.
Integrations run on the [Automation Platform](/platform/overview/) (formerly Oz), which handles the trigger, the [environment](/platform/environments/) the agent executes in, and the record of each run.
***
## Get started
[Section titled “Get started”](#get-started)
Use the setup walkthrough below for a quick look at how environments connect to integrations, then choose the guide that matches what you want to do next.
* [Integrations quickstart](/platform/integrations/quickstart/) - Trigger your first agent from Slack and watch the run from start to finish.
* [Integration setup](/agents/cli/oz-cli/integration-setup/) - Configure environments, GitHub authorization, CLI flags, and integrations in more detail.
* [Slack](/platform/integrations/slack/), [Linear](/platform/integrations/linear/), and [Jira](/platform/integrations/jira/) - Trigger agents from team conversations, issues, and comments.
* [GitHub](/platform/integrations/github/) - Mention `@warp-agent` on issues, pull requests, and review comments to start agents that reply in the thread.
* [GitHub Actions](/platform/integrations/github-actions/) - Run agents from CI workflows and repository events.
* [GitLab](/platform/integrations/gitlab/) - Connect GitLab.com repos natively, or self-managed instances with tokens and Warp-managed secrets.
* [Azure DevOps](/platform/integrations/azure-devops/) - Connect standalone cloud agents with personal access tokens and Warp-managed secrets.
* [Bitbucket](/platform/integrations/bitbucket/) - Connect repositories with tokens and Warp-managed secrets.
* [AWS, GCP, and other cloud providers](/platform/integrations/cloud-providers/) - Give cloud agents short-lived access to cloud services.
* [Managing cloud agents](/platform/managing-cloud-agents/) - Monitor and review integration-triggered runs across your team by source, status, or creator.
# Azure DevOps integration
Canonical page: [/platform/integrations/azure-devops/](https://docs.warp.dev/platform/integrations/azure-devops/)
> Connect cloud agents to Azure DevOps repos using personal access tokens and Warp-managed secrets.
Cloud agents work with any Git repository, including those hosted on Azure DevOps. For a standalone cloud agent environment, grant access with a personal access token and Warp-managed secrets. Once configured, the environment works with any Automation Platform trigger—Slack, Linear, schedules, or the CLI.
This approach works for both Azure DevOps Services (dev.azure.com) and Azure DevOps Server (self-hosted) instances.
To connect hosted Azure DevOps Services to a factory with event-driven automations, use the [Azure DevOps factory integration](/factories/integrations/azure-devops/). For an Azure DevOps Server factory, use the [other code forges setup](/factories/code-forges/other-code-forges/).
***
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **Warp account** - [Create an account in the Oz web app](https://oz.warp.dev).
* **Azure DevOps repository** - Use a repository hosted on Azure DevOps Services or Azure DevOps Server.
* **Oz CLI** - [Install and authenticate the CLI](/agents/cli/oz-cli/).
## Generate a personal access token
[Section titled “Generate a personal access token”](#generate-a-personal-access-token)
1. Sign in to your Azure DevOps organization at `dev.azure.com/{your-org}`.
2. Click the user settings icon (gear) in the top-right corner, then click **Personal access tokens**.
3. Click **+ New Token**.
4. Enter a descriptive name for the token (e.g. `warp-oz-agent`), choose the organization it applies to, and set an expiration date that matches your team’s rotation policy.
5. Under “Scopes,” choose **Custom defined**, then select **Code** > **Read**.
6. Click **Create**.
7. Copy the token value immediately. Azure DevOps will not show it again.
**Code (Read)** is the minimum required scope to clone a repository. If a future workflow requires the agent to push commits or open pull requests, you will also need **Code (Read & Write)**.
For Azure DevOps Server (self-hosted), sign in at `https://{server}/{collection}` instead of `dev.azure.com`. The token creation steps are the same.
***
## Store the token as a Warp-managed secret
[Section titled “Store the token as a Warp-managed secret”](#store-the-token-as-a-warp-managed-secret)
Warp injects managed secrets as environment variables at runtime and never exposes them in logs or configuration files. See the [Secrets](/platform/secrets/) documentation for full details on scoping and managing secrets.
1. Run the following command:
```bash
oz secret create --team AZURE_DEVOPS_TOKEN
```
2. When prompted, paste the token.
The value is stored and encrypted, and cannot be retrieved after creation.
Use `--team` to create a shared token available to all teammates and automated triggers (schedules, Slack, Linear). Use `--personal` if each team member should authenticate with their own Azure DevOps token. Personal secrets work with all triggers and take precedence over a team secret of the same name when both exist.
If you need to update a secret value, run:
```bash
oz secret update --team --value AZURE_DEVOPS_TOKEN
```
***
## Create an environment with a clone setup command
[Section titled “Create an environment with a clone setup command”](#create-an-environment-with-a-clone-setup-command)
Create an environment that uses your token to clone the repository at the start of each agent run. Because the `--repo` flag in `oz environment create` is designed for GitHub repositories, you clone your Azure DevOps repo via a setup command instead.
1. Run the following command:
```bash
oz environment create \
--name "my-azure-devops-env" \
--docker-image <image> \
--setup-command 'AUTH_HEADER=$(printf ":%s" "$AZURE_DEVOPS_TOKEN" | base64 | tr -d "\n") && git -c "http.extraheader=Authorization: Basic $AUTH_HEADER" clone https://dev.azure.com/your-org/your-project/_git/your-repo' \
--setup-command 'cd your-repo && <install dependencies>'
```
Caution
Use single quotes around setup commands that reference secrets. Double quotes cause your shell to expand `$AZURE_DEVOPS_TOKEN` immediately (to nothing), rather than letting Warp inject the secret at runtime inside the container.
2. Replace the following placeholders:
* `<image>` with your Docker image (for example, `node:22`, `python:3.12`, or a [Warp prebuilt dev image](https://github.com/warpdotdev/oz-dev-environments))
* `your-org` with your Azure DevOps organization name
* `your-project` with your Azure DevOps project name
* `your-repo` with your repository name
* For Azure DevOps Server (self-hosted), replace `dev.azure.com` with your server’s hostname.
* The second `--setup-command` with any dependency install or build steps your project requires. For example, `npm ci` or `pip install -r requirements.txt`.
Caution
Setup commands run on a fresh container for every agent run. Write them to be idempotent — commands that assume existing state (such as a partially cloned repo or a pre-built cache) can fail unpredictably. See [environment design and best practices](/platform/environments/configuring-environments/#environment-design-and-best-practices) for guidance.
3. Note the environment ID returned. You will need it to test the environment.
***
## Test the environment
[Section titled “Test the environment”](#test-the-environment)
Before connecting to integrations, verify the environment works by running a one-off agent.
1. Run the following command, replacing `<ENV_ID>` with the environment ID from the previous section:
```bash
oz agent run-cloud --environment <ENV_ID> --prompt "Your task here"
```
***
## Next steps
[Section titled “Next steps”](#next-steps)
With your environment configured, you can connect it to any Warp trigger exactly as you would with a GitHub-backed environment:
* **Slack** — Tag **@warp** in a message to start an agent run against your Azure DevOps repo. See [Slack](/platform/integrations/slack/).
* **Linear** — Tag **@warp** on an issue to kick off a workflow. See [Linear](/platform/integrations/linear/).
* **Scheduled agents** — Run agents on a recurring schedule. See [Scheduled Agents](/platform/triggers/scheduled-agents/).
* **Warp Factories** — Connect hosted Azure DevOps Services with dedicated identities and event triggers. See the [Azure DevOps factory integration](/factories/integrations/azure-devops/).
# Bitbucket integration
Canonical page: [/platform/integrations/bitbucket/](https://docs.warp.dev/platform/integrations/bitbucket/)
> Connect cloud agents to Bitbucket repos using access tokens and Warp-managed secrets.
Cloud agents work with any Git repository, including those hosted on Bitbucket. Unlike GitHub and GitLab, Bitbucket does not have a native Warp integration, but you can grant agents access to your Bitbucket repositories using an access token and Warp-managed secrets. Once configured, your environment works with any Automation Platform trigger—Slack, Linear, schedules, or the CLI.
This page explains how to generate a Bitbucket access token, store it securely, and configure a cloud agent environment that clones your repository at runtime.
Bitbucket Cloud and Bitbucket Data Center/Server use different token types:
* **Bitbucket Cloud** uses **API tokens**, created through your Atlassian Account settings.
* **Bitbucket Data Center/Server** uses **HTTP access tokens**, created through your Bitbucket profile settings.
Follow the section that matches your setup.
***
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* A Warp account ([create an account at https://oz.warp.dev](https://oz.warp.dev))
* A repository hosted on Bitbucket (Cloud or Data Center/Server)
* The [Oz CLI](/agents/cli/oz-cli/) installed and authenticated
***
## Bitbucket Cloud
[Section titled “Bitbucket Cloud”](#bitbucket-cloud)
### Step 1: Generate an API token
[Section titled “Step 1: Generate an API token”](#step-1-generate-an-api-token)
Note
Bitbucket Cloud API tokens are managed through your Atlassian Account, which is a separate site from bitbucket.org. The following steps will take you there.
1. Click your avatar in the upper-right corner of Bitbucket, then click **Account settings**.
2. On the Atlassian Account page that opens, click the **Security** tab.
3. Click **Create and manage API tokens**, then click **Create API token with scopes**.
4. Enter a name for the token (e.g. `warp-oz-agent`) and choose an expiration date.
5. Click **Next**.
6. Select **Bitbucket** as the app and click **Next**.
7. Search for `repository` in the **Select Bitbucket scopes** search box, then select **read:repository:bitbucket** (View your repositories).
8. Click **Next**.
9. Click **Create token**.
10. Copy the token value immediately. It is only shown once and cannot be retrieved later.
Note
**read:repository:bitbucket** is the minimum required scope to clone a repository. If a future workflow requires the agent to push commits or open pull requests, you will also need **write:repository:bitbucket**.
***
### Step 2: Store the token as a Warp-managed secret
[Section titled “Step 2: Store the token as a Warp-managed secret”](#step-2-store-the-token-as-a-warp-managed-secret)
Warp injects managed secrets as environment variables at runtime and never exposes them in logs or configuration files. See the [Secrets](/platform/secrets/) documentation for full details on scoping and managing secrets.
1. Run the following command:
```bash
oz secret create --team BITBUCKET_API_TOKEN
```
2. When prompted, paste the token.
The value is stored and encrypted, and cannot be retrieved after creation.
Note
Use `--team` to create a shared token available to all teammates and automated triggers (schedules, Slack, Linear). Use `--personal` if each team member should authenticate with their own Atlassian account token. Personal secrets work with all triggers and take precedence over a team secret of the same name when both exist.
If you need to update a secret value, run:
```bash
oz secret update --value BITBUCKET_API_TOKEN
```
***
### Step 3: Create an environment with a clone setup command
[Section titled “Step 3: Create an environment with a clone setup command”](#step-3-create-an-environment-with-a-clone-setup-command)
Create an environment that uses your token to clone the repository at the start of each agent run. Use the static username `x-bitbucket-api-token-auth` in the clone URL — this is a Bitbucket-specific placeholder that works with API tokens and means you don’t need to store your Bitbucket username separately.
1. Run the following command:
```bash
oz environment create \
--name "my-bitbucket-cloud-env" \
--docker-image <image> \
--setup-command 'git clone https://x-bitbucket-api-token-auth:$BITBUCKET_API_TOKEN@bitbucket.org/your-workspace/your-repo.git' \
--setup-command 'cd your-repo && <install dependencies>'
```
Caution
Use single quotes around setup commands that reference secrets. Double quotes cause your shell to expand `$BITBUCKET_API_TOKEN` immediately (to nothing), rather than letting Warp inject the secret at runtime inside the container.
2. Replace the following placeholders:
* `<image>` with your Docker image (for example, `node:22`, `python:3.12`, or a [Warp prebuilt dev image](https://github.com/warpdotdev/oz-dev-environments))
* `bitbucket.org/your-workspace/your-repo.git` with your actual repository URL
* The second `--setup-command` with any dependency install or build steps your project requires (for example, `npm ci` or `pip install -r requirements.txt`)
Caution
Setup commands run on a fresh container for every agent run. Write them to be idempotent — commands that assume existing state (such as a partially cloned repo or a pre-built cache) can fail unpredictably. See [environment design and best practices](/platform/environments/configuring-environments/#environment-design-and-best-practices) for guidance.
3. Note the environment ID returned. You will need it in the next step.
***
## Bitbucket Data Center / Server
[Section titled “Bitbucket Data Center / Server”](#bitbucket-data-center--server)
### Step 1: Generate an HTTP access token
[Section titled “Step 1: Generate an HTTP access token”](#step-1-generate-an-http-access-token)
1. Click your profile avatar in Bitbucket, then click **Manage account**.
2. In the left sidebar, click **HTTP access tokens**.
3. Click **Create token**.
4. Enter a name for the token (e.g. `warp-oz-agent`) and choose an expiration date if required by your administrator.
5. Under **Permissions**, choose **Read** for the **Repository** permission.
6. Click **Create token**.
7. Copy the token value immediately. It is only shown once and cannot be retrieved later.
Note
**Repository read** is the minimum required permission to clone a repository. If a future workflow requires the agent to push commits, you will also need **Repository write**.
***
### Step 2: Store the token as a Warp-managed secret
[Section titled “Step 2: Store the token as a Warp-managed secret”](#step-2-store-the-token-as-a-warp-managed-secret-1)
Warp injects managed secrets as environment variables at runtime and never exposes them in logs or configuration files. See the [Secrets](/platform/secrets/) documentation for full details on scoping and managing secrets.
1. Run the following command:
```bash
oz secret create --team BITBUCKET_TOKEN
```
2. When prompted, paste the token.
The value is stored and encrypted, and cannot be retrieved after creation.
Note
Use `--team` to create a shared token available to all teammates and automated triggers (schedules, Slack, Linear). Use `--personal` if each team member should authenticate with their own Bitbucket account token. Personal secrets work with all triggers and take precedence over a team secret of the same name when both exist.
If you need to update a secret value, run:
```bash
oz secret update --value BITBUCKET_TOKEN
```
***
### Step 3: Create an environment with a clone setup command
[Section titled “Step 3: Create an environment with a clone setup command”](#step-3-create-an-environment-with-a-clone-setup-command-1)
Create an environment that uses your token to clone the repository at the start of each agent run.
1. Run the following command:
```bash
oz environment create \
--name "my-bitbucket-dc-env" \
--docker-image <image> \
--setup-command 'git clone -c "http.extraHeader=Authorization: Bearer $BITBUCKET_TOKEN" https://your-server.com/scm/your-project/your-repo.git' \
--setup-command 'cd your-repo && <install dependencies>'
```
Caution
Use single quotes around setup commands that reference secrets, so `$BITBUCKET_TOKEN` is expanded at runtime inside the container rather than in your current shell.
2. Replace the following placeholders:
* `<image>` with your Docker image (for example, `node:22`, `python:3.12`, or a [Warp prebuilt dev image](https://github.com/warpdotdev/oz-dev-environments))
* `your-server.com/scm/your-project/your-repo.git` with your Bitbucket Data Center/Server repository URL. The `/scm/` path segment is standard for Bitbucket Data Center/Server.
* The second `--setup-command` with any dependency install or build steps your project requires (for example, `npm ci` or `pip install -r requirements.txt`)
Caution
Setup commands run on a fresh container for every agent run. Write them to be idempotent — commands that assume existing state (such as a partially cloned repo or a pre-built cache) can fail unpredictably. See [environment design and best practices](/platform/environments/configuring-environments/#environment-design-and-best-practices) for guidance.
3. Note the environment ID returned. You will need it in the next step.
***
## Test your environment
[Section titled “Test your environment”](#test-your-environment)
Before connecting to integrations, verify the environment works by running a one-off agent. This applies to both Bitbucket Cloud and Bitbucket Data Center / Server.
1. Run the following command, replacing `<ENV_ID>` with the environment ID from Step 3 of whichever setup you followed:
```bash
oz agent run-cloud --environment <ENV_ID> --prompt "Your task here"
```
***
## Next steps
[Section titled “Next steps”](#next-steps)
With your environment configured, you can connect it to any Warp trigger exactly as you would with a GitHub-backed environment:
* **Slack** — Tag **@warp** in a message to start an agent run against your Bitbucket repo. See [Slack](/platform/integrations/slack/).
* **Linear** — Tag **@warp** on an issue to kick off a workflow. See [Linear](/platform/integrations/linear/).
* **Scheduled agents** — Run agents on a recurring schedule. See [Scheduled Agents](/platform/triggers/scheduled-agents/).
Note
Native support for opening Bitbucket pull requests from agent-generated changes is planned as a future enhancement.
# Cloud providers
Canonical page: [/platform/integrations/cloud-providers/](https://docs.warp.dev/platform/integrations/cloud-providers/)
> Connect cloud agents to your AWS and GCP services.
Cloud agents can securely access AWS, GCP, and other cloud providers using short-lived OpenID Connect (OIDC) credentials. Configure your cloud agent environment to automatically authenticate to your cloud provider without storing long-lived keys, using Warp’s built-in OIDC federation support.
***
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* A Warp account. You can [create an account in the Oz web app](https://oz.warp.dev).
* A cloud provider account
Follow the section for your cloud provider.
***
## AWS
[Section titled “AWS”](#aws)
### Step 1: Create an OIDC identity provider
[Section titled “Step 1: Create an OIDC identity provider”](#step-1-create-an-oidc-identity-provider)
The first step is to configure your AWS account to trust OIDC tokens produced by the Automation Platform.
1. Open the [AWS IAM console](https://console.aws.amazon.com/iam).
2. Click **Identity Providers**, then click **Add provider**.
3. Set the provider type to **OpenID Connect**.
4. Set the **Provider URL** to `https://app.warp.dev`.
5. Set the **Audience** to `sts.amazonaws.com`.
6. Copy the ARN of the new identity provider, which will look like: `arn:aws:iam::<account-id>:oidc-provider/app.warp.dev`.
Note
Verify that the provider was created correctly by:
1. Clicking on the `app.warp.dev` link in the list of identity providers.
2. Clicking on **Endpoint verification**
3. Checking that the thumbprint is `08745487e891c19e3078c1f2a07e452950ef36f6`
***
### Step 2: Configure an IAM role
[Section titled “Step 2: Configure an IAM role”](#step-2-configure-an-iam-role)
Next, you will need to set up an AWS IAM role with a trust policy that links it to the OIDC provider.
1. Open the [AWS IAM console](https://console.aws.amazon.com/iam).
2. Click **Roles**, then click **Create role**.
3. Select **Custom trust policy**, and fill in the following JSON trust policy:
```json
{
"Version": "2012-10-17",
"Statement": [
{
"Sid": "AllowOzFederation",
"Effect": "Allow",
"Principal": {
"Federated": "<oidc-provider-arn>"
},
"Action": "sts:AssumeRoleWithWebIdentity",
"Condition": {
"StringEquals": {
"app.warp.dev:aud": "sts.amazonaws.com"
},
"StringLike": {
"app.warp.dev:sub": "scoped_principal:<team-uid>/*"
}
}
}
]
}
```
You will need to replace:
* `<oidc-provider-arn>` with the ARN of the OIDC provider added in Step 1.
* `<team-uid>` with your Warp team UID. This is the last component of your [Admin Panel](/enterprise/team-management/admin-panel/) URL. For example, if the Admin Panel URL is `https://app.warp.dev/admin/abc123def456`, your team UID would be `abc123def456`. You can also get your team UID from the `oz whoami` command.
The example above uses `StringLike` with the `scoped_principal:<team-uid>/*` pattern to allow any user or automation on your team to assume the role. See [the subject claim](#subject-sub) for the full format of `app.warp.dev:sub`.
To restrict the role to a specific user, use `StringEquals` with the fully qualified subject:
```json
...
"Condition": {
"StringEquals": {
"app.warp.dev:aud": "sts.amazonaws.com",
"app.warp.dev:sub": "scoped_principal:<team-uid>/user:<user-uid>"
}
}
...
```
To allow multiple specific principals, use a list of subjects:
```json
...
"Condition": {
"StringEquals": {
"app.warp.dev:aud": "sts.amazonaws.com",
"app.warp.dev:sub": [
"scoped_principal:<team-uid>/user:<user-uid-1>",
"scoped_principal:<team-uid>/user:<user-uid-2>",
"scoped_principal:<team-uid>/service_account:<sa-uid>"
]
}
}
...
```
4. Click **Next** and add permissions policies. These policies determine what agents can access in your AWS account.
5. Click **Next** and enter a role name and optional description.
6. Click **Create role**, then open the role and note down the role ARN. This will be of the form `arn:aws:iam::<account-id>:role/<role-name>`.
***
### Step 3: Enable AWS federation in your cloud agent environment
[Section titled “Step 3: Enable AWS federation in your cloud agent environment”](#step-3-enable-aws-federation-in-your-cloud-agent-environment)
Finally, configure the cloud agent environment to use your new AWS role.
1. Open the [Oz web app](https://oz.warp.dev).
2. Create or edit an environment. See [Environments](/platform/oz-web-app/#environments) for instructions.
3. Expand the **AWS** section and enter the AWS role ARN from Step 2.
4. Save the environment.
Caution
Currently, AWS federation can only be configured in the Oz web app, not the CLI.
Agents running in this environment will now automatically assume the configured role when using the `aws` CLI or a compatible SDK.
Note
The Automation Platform uses the [**Assume role with web identity**](https://docs.aws.amazon.com/cli/latest/userguide/cli-configure-role.html#cli-configure-role-oidc) AWS authentication mechanism. The following environment variables are set while the agent is running:
* `AWS_ROLE_ARN`: the ARN of the role configured above
* `AWS_WEB_IDENTITY_TOKEN_FILE`: the path to a temporary file containing the agent’s Automation Platform OIDC token
* `AWS_ROLE_SESSION_NAME`: a derived session name, of the form `Oz_Run_<run-id>`.
***
## GCP
[Section titled “GCP”](#gcp)
### Step 1: Create a Workload Identity Pool and Provider
[Section titled “Step 1: Create a Workload Identity Pool and Provider”](#step-1-create-a-workload-identity-pool-and-provider)
The Automation Platform GCP integration uses [Workload Identity Federation](https://docs.cloud.google.com/iam/docs/workload-identity-federation). You will need to configure a pool and provider to trust OIDC tokens produced by the Automation Platform.
These instructions use the `gcloud` tool. You can also follow the OIDC instructions in [Configure Workload Identity Federation with other identity providers](https://docs.cloud.google.com/iam/docs/workload-identity-federation-with-other-providers) to use the GCP console or Terraform.
1. Create a Workload Identity Pool using the `gcloud` CLI:
```bash
gcloud iam workload-identity-pools create "<pool-id>" --location=global
```
Replace `<pool-id>` with the desired identifier for your pool, such as `oz-agent-pool`.
2. Create a Provider within the pool:
```bash
gcloud iam workload-identity-pools providers create-oidc \
"<provider-id>" \
--location=global \
"--workload-identity-pool=<pool-id>" \
--issuer-uri="https://app.warp.dev" \
"--attribute-mapping=google.subject=assertion.sub,google.groups=assertion.teams,attribute.environment=assertion.environment" \
"--attribute-condition='<team-uid>' in assertion.teams"
```
Replace `<pool-id>` with the ID you used above, and `<provider-id>` with the desired identifier for your provider, such as `oz-oidc-provider`.
Replace `<team-uid>` with the UID of your Warp team. This is the last component of your [Admin Panel](/enterprise/team-management/admin-panel/) URL. For example, if the admin panel URL is `https://app.warp.dev/admin/abc123def456`, your team UID would be `abc123def456`.
Caution
If you do not set an attribute condition, then *any cloud agent* will be able to use your Workload Identity Federation provider, even if it does not belong to your team.
### Step 2: Configure IAM policies
[Section titled “Step 2: Configure IAM policies”](#step-2-configure-iam-policies)
You will need to configure IAM policies in GCP that allow agents in the Workload Identity Federation pool access to resources.
To give all agents on your team read-only access to all Compute Engine resources in a project, for example, you would run:
```bash
gcloud projects add-iam-policy-binding <project-id> \
--member "principalSet://iam.googleapis.com/projects/<project-number>/locations/global/workloadIdentityPools/<pool-id>/group/<team-uid>" \
--role "roles/compute.viewer"
```
See [Workload Identity Federation principal types](https://docs.cloud.google.com/iam/docs/workload-identity-federation#principal-types) for the full syntax supported.
### Step 3: Enable Workload Identity Federation in your cloud agent environment
[Section titled “Step 3: Enable Workload Identity Federation in your cloud agent environment”](#step-3-enable-workload-identity-federation-in-your-cloud-agent-environment)
Finally, configure the cloud agent environment to use your Workload Identity Federation provider.
1. Open the [Oz web app](https://oz.warp.dev).
2. Create or edit an environment. See [Environments](/platform/oz-web-app/#environments) for instructions.
3. Expand the **GCP** section and enter the project number, pool ID, and provider ID from Step 1.
4. Save the environment.
Caution
Currently, Workload Identity Federation can only be configured in the Oz web app, not the CLI.
Agents running in this environment will now automatically configure [Application Default Credentials](https://docs.cloud.google.com/docs/authentication/application-default-credentials) to use the configured pool. Both the `GOOGLE_APPLICATION_CREDENTIALS` and `CLOUDSDK_AUTH_CREDENTIAL_FILE_OVERRIDE` environment variables are set, so both the `gcloud` CLI and official Google SDKs will use the Automation Platform federated credentials. The Automation Platform uses [**executable-sourced credentials**](https://docs.cloud.google.com/iam/docs/workload-identity-federation-with-other-providers#create-credential-config) to configure ADC for automatic token rotation.
#### Automatic `gcloud` sign-in
[Section titled “Automatic gcloud sign-in”](#automatic-gcloud-sign-in)
Environment variables alone are enough for the Google SDKs, but `gcloud` reports no active account until it signs in through its own auth system, and some tooling depends on an active account. During provider setup, the Automation Platform therefore also runs `gcloud auth login` against the federated credential file so `gcloud` reports the federated identity as its active account.
This step is best-effort and never blocks the run:
* **`gcloud` isn’t installed** - The Automation Platform skips the sign-in. The ADC environment variables still provide credentials to the Google SDKs.
* **Sign-in fails or times out** - The Automation Platform logs the failure and continues. The ADC environment variables still work, so a run only loses the active-account convenience.
To confirm the account inside a run, use `gcloud auth list`.
## Other providers
[Section titled “Other providers”](#other-providers)
To authenticate from the Automation Platform to another provider that supports OIDC federation, you can issue tokens directly.
Within the agent environment, use the `oz federate issue-token` command to produce an OIDC token with your provider as the audience:
```bash
oz federate issue-token --run-id "$OZ_RUN_ID" --audience AUDIENCE --output-format json
```
Cloud agent runs set `OZ_RUN_ID` to the current run’s ID. Replace `AUDIENCE` with the identifier expected by your provider.
See the [`oz federate issue-token` reference](/agents/cli/oz-cli/federate/#oz-federate-issue-token) for token lifetime and subject customization options.
You can then exchange this token for provider-specific credentials.
## OIDC token claims
[Section titled “OIDC token claims”](#oidc-token-claims)
All Automation Platform OIDC tokens include the following standard claims:
| Claim | Value |
| ----- | ------------------------------------------------------ |
| `iss` | The issuer, `https://app.warp.dev`. |
| `aud` | The intended recipient of the token. |
| `sub` | The subject, built from the selected subject template. |
| `iat` | The time the token was issued. |
| `nbf` | The time before which the token isn’t valid. |
| `exp` | The token expiration time. |
| `jti` | The unique token identifier. |
### Audience
[Section titled “Audience”](#audience)
The `aud` claim will reflect the default for your cloud provider. For AWS, this is always `sts.amazonaws.com`. For GCP, it is derived from the Workload Identity Federation provider, such as `https://iam.googleapis.com/projects/<project-number>/locations/global/workloadIdentityPools/<pool-id>/providers/<provider-id>`.
### Subject (`sub`)
[Section titled “Subject (sub)”](#subject-sub)
The `sub` claim identifies the principal that an agent is executing as: a Warp user or a dedicated agent.
By default, the `sub` claim uses the format `<principal-type>:<principal-id>`:
* `user:abc123def456`: Identifies a user with ID `abc123def456`
* `service_account:abc123def456`: Identifies your autogenerated team account
Use [`--subject-template`](/agents/cli/oz-cli/federate/#subject-template-components) to include other available claims in `sub`.
When authenticating to AWS, the Automation Platform uses a different `sub` claim format because AWS trust policies can’t match on custom OIDC claims. The format above is prefixed with your team UID:
* `scoped_principal:xyz789/user:abc123def456`: Identifies the user `abc123def456`, who is a member of team `xyz789`.
* `scoped_principal:user:abc123def456`: Identifies the user `abc123def456`, who is not on any team.
* `scoped_principal:xyz789/service_account:abc123def456`: Identifies the autogenerated account for team `xyz789`.
The `scoped_principal` component isn’t available for users who belong to multiple teams.
To get possible user ID values, use the `oz whoami` command:
```bash
oz whoami
User ID: abc123
Email: user@warp.dev
Team ID: xyz789
Team Name: My Team
```
You can also check the user IDs from past runs using the Warp Platform API:
```bash
curl https://app.warp.dev/api/v1/agent/runs -H "Authorization: Bearer $WARP_API_KEY"
{
"runs": [
{
...
"creator": {
"type": "user",
"uid": "<user-id>",
"display_name": "User Name",
"email": "user@warp.dev"
}
}
]
}
```
### Principal claims
[Section titled “Principal claims”](#principal-claims)
Tokens include claims that describe the user or agent:
* `user`: the user’s UID. Included only for user tokens.
* `service_account`: the service account UID. Included only for agent tokens.
* `email`: the user’s email address. Included only for user tokens with an email address.
* `teams`: the UIDs of the teams the principal belongs to. Users on multiple teams get multiple values, and users on no team don’t get this claim.
* `factory_uid`: the factory UID. Included only for service agents belonging to a factory.
* `agent_type`: the configured factory agent type. Included only for agent tokens with a configured agent type.
### Run claims
[Section titled “Run claims”](#run-claims)
The following claims are derived from an agent run:
* `run_id`: the unique identifier for the individual run. This is not suitable for configuring access, but is useful to log for debugging.
* `environment`: the unique identifier for the agent’s [Environment](/platform/environments/).
* `agent_name`: the configured agent name.
* `skill_spec`: the canonical identifier for the skill, such as `github-org/github-repo:.warp/skills/skill-name/SKILL.md`.
* `host`: the execution host. This is `warp` for Warp-hosted agents or the configured worker host for [self-hosted agents](/factories/self-hosting/).
### Example token
[Section titled “Example token”](#example-token)
The following OIDC token references an agent running as a specific Warp user:
```json
// JWT Header
{
"typ": "JWT",
"alg": "ES256",
"kid": "<example-key-id>"
}
// JWT Payload
{
"aud": ["sts.amazonaws.com"],
"sub": "user:<example-user-id>",
"user": "<example-user-id>",
"email": "user@warp.dev",
"teams": ["<example-team-id>"],
"run_id": "<example-id>",
"environment": "<example-id>",
"agent_name": "<example-name>",
"skill_spec": "<example-spec>",
"host": "warp",
"iss": "https://app.warp.dev",
"jti": "<example-id>",
"exp": 1775210175,
"iat": 1775206575,
"nbf": 1775206575
}
```
# GitHub integration
Canonical page: [/platform/integrations/github/](https://docs.warp.dev/platform/integrations/github/)
> Mention @warp-agent on a GitHub issue, pull request, or review comment to start a cloud agent that replies in the thread and opens pull requests.
The GitHub integration lets your team start cloud agents from GitHub itself. Mention **@warp-agent** in an issue comment, a pull request review comment, or the body of a new pull request, and Warp starts a cloud agent that reads the surrounding context, works the task in your codebase, and posts its progress and results back into the same thread.
The integration is powered by the [Warp Factories](/factories/) GitHub App. Once a team admin installs the app and enables the GitHub organization, every teammate who has connected their GitHub account can trigger agents from GitHub without leaving a review or an issue.
Note
This page covers the native GitHub App integration. It is distinct from two other GitHub surfaces:
* [GitHub Actions](/platform/integrations/github-actions/) runs agents inside your own CI workflows with the `oz-agent-action` workflow step. You control the trigger, permissions, and prompt in YAML.
* [Team GitHub authorization](/platform/team-access-billing-and-identity/#team-github-authorization) is how agents authenticate to GitHub to clone repos and open pull requests, regardless of where a run started.
***
## What the GitHub integration does
[Section titled “What the GitHub integration does”](#what-the-github-integration-does)
* **@warp-agent mentions** - Mention the agent in a comment or pull request body to start a cloud agent run with the issue or pull request as context.
* **In-thread status** - Warp posts a status comment carrying the run link, then follows up with progress comments and a final summary in the same issue, pull request, or review thread.
* **Thread-aware follow-ups** - Mention the agent again in the same thread and Warp continues the existing run instead of starting a new one.
* **Automatic repository access** - The repository the event came from is cloned for the run, alongside any repositories in the environment you configure for the integration.
* **Team-scoped configuration** - A Warp team admin controls which GitHub organizations are enabled, and which environment, model, agent, and prompt GitHub-triggered runs use.
## How it works
[Section titled “How it works”](#how-it-works)
When you mention `@warp-agent`, GitHub sends the event to Warp through the Warp Factories GitHub App installation. Warp then:
1. Confirms the comment or pull request body contains the `@warp-agent` mention and that the author is a person rather than a bot.
2. Maps the GitHub App installation to a Warp team using the organizations enabled in the Admin Panel.
3. Maps the GitHub account that posted the mention to a Warp account, so the run is attributed to that person.
4. Posts a status comment in the thread and starts the cloud agent run with the issue, pull request, or review thread as context.
5. Posts progress updates and a final summary back into the thread, including any pull requests the agent opened and branches it pushed.
The agent replies through Warp’s status comments, which are posted by the GitHub App. Agent replies aren’t posted from the triggering user’s account.
### Supported triggers
[Section titled “Supported triggers”](#supported-triggers)
The integration starts or continues a run for these GitHub events when the text contains `@warp-agent`:
* **Issue comments** - A new comment on an issue. Warp reads the issue title, description, labels, state, and the recent comment thread.
* **Pull request comments** - A new top-level comment on a pull request. These continue the pull request’s existing run when one exists.
* **Pull request review comments** - A new inline review comment or a reply in a review thread. Warp reads the pull request, the review thread, and the diff of the commented file, and replies inside the same review thread.
* **New pull requests** - A pull request opened with `@warp-agent` in its description. Warp reads the title, description, and the head and base branches.
Mentions in other places don’t start a run. Editing a comment to add the mention, mentioning the agent in an issue or pull request title, and mentions posted by bots are all ignored.
### Follow-ups and existing runs
[Section titled “Follow-ups and existing runs”](#follow-ups-and-existing-runs)
Warp groups events into a single conversation per issue, pull request, or review thread:
* Comments on the same issue continue that issue’s run.
* Top-level pull request comments continue that pull request’s run, including a run started from the pull request description.
* Replies in a review thread continue that thread’s run.
When a run for that thread is already in flight, a new mention is delivered to the running agent as a follow-up instruction rather than starting a second agent.
## Requirements
[Section titled “Requirements”](#requirements)
* **Team membership** - The GitHub integration requires a [Warp team](/knowledge-and-collaboration/teams/). Configuration is team-scoped, and runs are owned by the team associated with the GitHub App installation.
* **Plan and credits** - Your team must have cloud agents enabled and credits available. On Enterprise plans, runs draw from a team credit pool per your contract. See [Access, billing, and identity](/platform/team-access-billing-and-identity/).
* **Warp Factories GitHub App** - A GitHub organization owner installs the [Warp Factories](https://github.com/apps/warp-factories) GitHub App on the organization or account that owns the repositories, granting it access to all repositories or a selected set. The installation’s repository access is what agents act with, so scope it deliberately.
* **An enabled GitHub organization** - A Warp team admin adds the organization under **Enabled GitHub Orgs** in the Admin Panel so the installation maps to your Warp team.
* **A connected GitHub account** - Each teammate connects their GitHub account to Warp once, so Warp can identify who triggered the run and which team to bill. The connection identifies the requester; it doesn’t determine what the agent can reach on GitHub.
## Setting up the GitHub integration
[Section titled “Setting up the GitHub integration”](#setting-up-the-github-integration)
Complete steps 1 through 3 once per team. Step 4 is per teammate.
### 1. Install the GitHub App
[Section titled “1. Install the GitHub App”](#1-install-the-github-app)
Install the app so GitHub can deliver issue and pull request events to Warp, and so agents can read repository context and post comments.
A user with admin permissions on the GitHub organization installs the [Warp Factories](https://github.com/apps/warp-factories) GitHub App and grants it access to **all repositories** or **selected repositories**. Each installation covers a single GitHub organization or personal account, so install the app separately for every organization your team works in.
Installing the Warp Factories GitHub App.
The agent can only act on repositories included in this installation.
### 2. Enable the GitHub organization for your Warp team
[Section titled “2. Enable the GitHub organization for your Warp team”](#2-enable-the-github-organization-for-your-warp-team)
Enabling the organization is what tells Warp which team owns the runs triggered from those repositories.
In the Warp app, a team admin goes to **Settings** > **Admin Panel** > **Platform** and adds the GitHub organization under **Enabled GitHub Orgs**.

Enabled GitHub Orgs setting in the Admin Panel.
Until the organization is enabled, mentions in its repositories return a comment asking a Warp workspace admin to configure GitHub repository access in the Admin Panel.
### 3. Configure how GitHub-triggered runs execute
[Section titled “3. Configure how GitHub-triggered runs execute”](#3-configure-how-github-triggered-runs-execute)
Configure the integration so every GitHub-triggered run uses the environment and settings your team expects.
1. Open the [Integrations page in the Oz web app](https://oz.warp.dev/integrations). The **GitHub integration** row shows whether an installation is connected to your team.
2. Open the row’s settings and choose the [environment](/platform/environments/) the runs use, plus an optional model, [agent](/platform/agents/), prompt, and secrets.
3. Save the configuration.
The repository that triggered the event is always cloned for the run, so an environment is optional. Configure one when runs need additional repositories, a specific Docker image, or setup commands. Pick a GitHub environment whose repositories the same installation covers, since the run authenticates with that installation’s token.
Note
Unlike Slack and Linear, the GitHub integration isn’t created with `oz integration create`. It appears once the Warp Factories GitHub App installation is associated with your team in the Admin Panel.
### 4. Connect your GitHub account
[Section titled “4. Connect your GitHub account”](#4-connect-your-github-account)
Each teammate connects their GitHub account so Warp can match the mention to a Warp account, attribute the run to that person, and bill it to the right team. Warp doesn’t start a run for a GitHub account it can’t match.
Connect the account from the GitHub integration row in the Oz web app, or the first time you trigger a run: when Warp can’t match your GitHub account, it replies in the thread with a link to connect.
## Using @warp-agent in GitHub
[Section titled “Using @warp-agent in GitHub”](#using-warp-agent-in-github)
Mention the agent and describe the task in the same comment:
> @warp-agent this test is flaky on CI. Find the race condition and open a PR with a fix.
On a pull request review comment, the agent also receives the diff for the file you commented on, so you can ask for a targeted change:
> @warp-agent rename this helper to `parseRepoRef` and update the call sites.
Warp responds in the thread with a status comment that links to the run, then posts progress updates as the agent works, and finally posts the agent’s summary along with any pull requests it opened and branches it pushed.
## Monitoring runs
[Section titled “Monitoring runs”](#monitoring-runs)
Every GitHub-triggered run is a cloud agent run:
* **In the thread** - The status comment links to the run in the Oz web app and, once available, to the live conversation.
* **In the Oz web app** - The [Runs page](https://oz.warp.dev/runs) shows the full transcript, status, and metadata. See [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/).
* **In the Warp app** - GitHub-triggered runs appear alongside the rest of your team’s runs in the [Agent Management Panel](/platform/managing-cloud-agents/).
## Permissions and identity
[Section titled “Permissions and identity”](#permissions-and-identity)
GitHub-triggered runs separate **what the agent can do on GitHub** from **who the run belongs to**.
**Access comes from the GitHub App installation.** A run started by an `@warp-agent` mention authenticates with a token minted for the Warp Factories GitHub App installation that delivered the event, not with the mentioning user’s GitHub authorization. Cloning, branches, commits, pull requests, and the status comments all use that installation token, so on GitHub the work is attributed to the Warp Factories GitHub App rather than to the person who wrote the mention. The boundary on what the agent can reach is the installation’s repository selection, optionally narrowed further by the repository access a Warp admin grants the team in the Admin Panel. Adjust the installation in your [GitHub settings](https://github.com/settings/installations).
**Identity comes from the account connection.** Warp matches the GitHub account that posted the mention to the Warp account that connected it, not by email address. That binding decides who the run is attributed to in Warp, which team owns it, and whose credits pay for it. The person must be a member of the Warp team that enabled the organization.
Caution
Because the run uses the installation’s access rather than the mentioner’s, anyone who can comment in a repository covered by the installation — and who has a connected GitHub account on that Warp team — can start an agent that acts with all the repository access granted to that team. Grant the app, and the team, only the repositories your team wants agents to work in.
For fully automated workflows that run without a triggering user, such as scheduled agents or runs started with an agent API key, see [Team GitHub authorization](/platform/team-access-billing-and-identity/#team-github-authorization).
## Limitations
[Section titled “Limitations”](#limitations)
* **Mentions only start runs from comments and pull request descriptions.** Issue and pull request titles, commit messages, and edits to an existing comment don’t trigger the agent.
* **Bots can’t trigger the agent.** Mentions posted by GitHub bots or apps are ignored, so an agent can’t start another agent from a comment.
* **One run per thread at a time.** While a run for an issue, pull request, or review thread is active, further mentions become follow-ups to that run.
* **The installation must map to a Warp team.** Repositories in an organization that no Warp team has enabled can’t start runs.
* **Installations are scoped to one organization each.** Install the app separately for every GitHub organization whose repositories your team works in.
* **Everything on GitHub is done by the app.** Comments, commits, branches, and pull requests come from Warp Factories rather than the person who mentioned the agent, so the run can’t reach anything the installation can’t reach, and it isn’t narrowed to what that person can reach either.
* **The configured environment must be a GitHub environment.** A GitHub-triggered run rejects an environment built for another provider, such as GitLab or Bitbucket, and asks you to configure a GitHub environment instead.
* **Environment repositories outside the installation stay out of reach.** The installation token only covers the repositories the app is installed on, so a repository in the environment that the installation doesn’t cover isn’t available to the agent.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### Nothing happens after mentioning @warp-agent
[Section titled “Nothing happens after mentioning @warp-agent”](#nothing-happens-after-mentioning-warp-agent)
The event never reached Warp, or it was filtered out. Check in this order:
1. The comment body contains `@warp-agent`, spelled exactly, rather than only the issue or pull request title.
2. The Warp Factories GitHub App is installed on the organization and has access to that repository.
3. The mention was posted by a person. Bot-authored comments are ignored.
4. The comment is new. Editing an existing comment to add the mention doesn’t start a run.
### ”Your GitHub account is not connected to Warp”
[Section titled “”Your GitHub account is not connected to Warp””](#your-github-account-is-not-connected-to-warp)
Warp received the mention but couldn’t match your GitHub account to a Warp account. Use the link in the reply to connect your GitHub account, then mention the agent again.
### ”This repository is not enabled for a Warp team”
[Section titled “”This repository is not enabled for a Warp team””](#this-repository-is-not-enabled-for-a-warp-team)
The app is installed, but no Warp team has access to that repository. A Warp workspace admin configures GitHub repository access in **Settings** > **Admin Panel** > **Platform** in the Warp app.
### ”Your Warp account is not a member of any team with access to this repository”
[Section titled “”Your Warp account is not a member of any team with access to this repository””](#your-warp-account-is-not-a-member-of-any-team-with-access-to-this-repository)
Your GitHub account is connected, but your Warp account isn’t in a team with access to that repository. Ask a team admin to add you to the Warp team.
### The run starts but fails immediately
[Section titled “The run starts but fails immediately”](#the-run-starts-but-fails-immediately)
Use the error code in the thread’s status comment to narrow the fix. Common errors include:
* [`feature_not_available`](/factories/api-and-sdk/troubleshooting/errors/feature-not-available/) - The team’s plan doesn’t support integrations.
* [`external_authentication_required`](/factories/api-and-sdk/troubleshooting/errors/external-authentication-required/) - GitHub authorization is missing or expired.
* [`insufficient_credits`](/factories/api-and-sdk/troubleshooting/errors/insufficient-credits/) - The billed account has no credits available.
### The agent finished but opened no pull request
[Section titled “The agent finished but opened no pull request”](#the-agent-finished-but-opened-no-pull-request)
Confirm the Warp Factories GitHub App installation covers the repository and still grants write access to it. Because the run acts with the installation’s token, removing a repository from the installation, or narrowing the app’s permissions, stops the agent from pushing branches or opening pull requests there.
## Removing or changing the integration
[Section titled “Removing or changing the integration”](#removing-or-changing-the-integration)
* **Change repository access** - Edit the Warp Factories installation in your [GitHub settings](https://github.com/settings/installations).
* **Stop runs for an organization** - A Warp team admin removes the organization from **Enabled GitHub Orgs** in the Admin Panel. Mentions in its repositories stop starting runs.
* **Remove the integration entirely** - Uninstall the Warp Factories GitHub App from the GitHub organization. GitHub stops delivering events to Warp for every repository in that installation.
## Related resources
[Section titled “Related resources”](#related-resources)
* [GitHub Actions](/platform/integrations/github-actions/) - Run agents from your own CI workflows with `oz-agent-action`.
* [Integrations overview](/platform/integrations/) - The full set of first-party integrations.
* [Access, billing, and identity](/platform/team-access-billing-and-identity/) - Team GitHub authorization, identity mapping, and credit usage.
* [Environments](/platform/environments/) - Configure the runtime context for cloud agents.
* [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/) - Inspect and share the runs a mention starts.
# GitHub Actions
Canonical page: [/platform/integrations/github-actions/](https://docs.warp.dev/platform/integrations/github-actions/)
> Run agents in GitHub Actions to automate code review, issue triage, and CI fixes.
Run agents directly in your GitHub Actions workflows using `oz-agent-action`. The agent integrates seamlessly into your CI pipeline, automating tasks like code review, issue triage, bug fixing, and maintenance using your repository context and GitHub permissions. This page covers how the integration works, how to set it up, and common automation patterns for development teams.
Note
**Getting started?** See the [GitHub Actions quickstart](/platform/integrations/quickstart-github-actions/) to set up your first workflow, or visit the [oz-agent-action repository](https://github.com/warpdotdev/oz-agent-action) for detailed setup instructions and ready-to-use workflow templates.
Note
GitHub Actions is different from the [GitHub integration](/platform/integrations/github/). GitHub Actions runs agents inside workflows you define in your repository, and you control the trigger, permissions, and prompt in YAML. The GitHub integration starts agents when someone mentions `@warp-agent` on an issue, pull request, or review comment, using the [Warp Factories](/factories/) GitHub App with no workflow file.
If you’re comparing GitHub Actions with schedules, Slack, Linear, the GitHub integration, the Oz CLI, or API-triggered runs, see [Run agents unattended with schedules and triggers](/guides/agent-workflows/how-to-run-unattended-agents/).
Watch this demo to see the integration in action:
[Warp x GitHub Actions integration video](https://www.loom.com/embed/534f88b6a98e43ca9769ca09de6424b5)
In this demo
* Automated PR reviews with both summary feedback and inline suggestions
* One-click batching and committing of agent suggestions directly from the GitHub UI
* Automatically fixing failing CI checks by opening a suggested PR
* Suggesting fixes for small review comments (“nits”) without checking out code locally
***
### What the GitHub Actions integration does
[Section titled “What the GitHub Actions integration does”](#what-the-github-actions-integration-does)
The `oz-agent-action` is a GitHub Action that wraps the Oz CLI and:
* Runs an agent inside an Actions job
* Caches package installation for faster builds
* Captures the agent’s output for use in subsequent workflow steps
* Lets you pass workflow context, event data, and previous step outputs into the agent prompt
* Allows the agent to comment on PRs, post results, or open branches via the GitHub CLI
* Supports inline code suggestions that can be batched and committed directly from the GitHub pull request UI
* Enables using pre-built skills or custom skills for specialized tasks
### Requirements
[Section titled “Requirements”](#requirements)
To use agents in GitHub Actions, you need:
* A [**Warp API key**](/agents/cli/oz-cli/api-keys/) stored as a [GitHub secret](https://docs.github.com/en/actions/security-for-github-actions/security-guides/using-secrets-in-github-actions) — this authenticates the agent with Warp. Pick a personal key if you want commits attributed to you, or an agent key to run as a [cloud agent](/platform/agents/) on your team. See [API keys](/agents/cli/oz-cli/api-keys/) for when to pick each.
* Workflow permissions that match your intended actions (for example, `pull-requests: write` if the agent should commit or comment on PRs) — the agent performs actions on your behalf using the GitHub token available to the workflow
* The `oz-agent-action` step added to your workflow
* **For private repositories using `@oz-agent` mention workflows**: The [`oz-agent`](https://github.com/oz-agent) GitHub user must be [invited as a member](https://docs.github.com/en/organizations/managing-membership-in-your-organization/inviting-users-to-join-your-organization) of your GitHub organization (see [Responding to comments with @ mentions](#1-responding-to-comments-with--mentions) for details)
* Familiarity with GitHub Actions concepts — see the official docs for [GitHub Actions](https://docs.github.com/en/actions)
### Using Skills
[Section titled “Using Skills”](#using-skills)
Skills provide reusable instructions for agents. You can use pre-built skills from the [oz-skills repository](https://github.com/warpdotdev/oz-skills) or create custom [skills](/agents/capabilities/skills/) for your specific workflows. Skills can also be deployed as [standalone agents](/platform/skills-as-agents/) to run on a schedule or in response to events.
#### How to use skills
[Section titled “How to use skills”](#how-to-use-skills)
You can specify a skill using the `skill` input parameter, either instead of or in combination with prompts:
```yaml
- name: Run agent with a skill
uses: warpdotdev/oz-agent-action@v1
with:
skill: 'code-review'
warp_api_key: ${{ secrets.WARP_API_KEY }}
```
Tip
If the action fails, use the returned error code to narrow the fix. Common errors include:
* [`authentication_required`](/factories/api-and-sdk/troubleshooting/errors/authentication-required/) (missing, invalid, or expired `warp_api_key` secret)
#### Skill format options
[Section titled “Skill format options”](#skill-format-options)
The `skill` parameter supports multiple formats for referencing skills:
* **`skill_name`** - Searches for the skill in your repository’s skill directories
* **`repo:skill_name`** - Uses a skill from a specific repository
* **`org/repo:skill_name`** - Uses a skill from a specific organization’s repository
#### Combining skills with prompts
[Section titled “Combining skills with prompts”](#combining-skills-with-prompts)
You can combine skills with prompts to provide specialized context while customizing the specific task:
```yaml
with:
skill: 'code-review'
prompt: 'Focus on security vulnerabilities in authentication code'
warp_api_key: ${{ secrets.WARP_API_KEY }}
```
In this example, the `code-review` skill provides the base context and approach for code review, while the prompt narrows the focus to security concerns in authentication code.
Note
Skills help maintain consistency across your workflows and can encapsulate best practices for common tasks like code review, issue triage, or automated testing.
***
## Common use cases
[Section titled “Common use cases”](#common-use-cases)
The `oz-agent-action` supports several automation patterns commonly used in CI.
### 1. Responding to comments with @ mentions
[Section titled “1. Responding to comments with @ mentions”](#1-responding-to-comments-with--mentions)
* **File**: [`examples/respond-to-comment.yml`](https://github.com/warpdotdev/oz-agent-action/blob/main/examples/respond-to-comment.yml)
* **Use case**: Add “@oz-agent fix this typo” or similar comments to a PR or Issue.
Note
The [GitHub integration](/platform/integrations/github/) responds to `@warp-agent` mentions without a workflow file. Use this Actions pattern when you want the run to happen inside your CI pipeline with workflow-scoped permissions; use the GitHub integration when you want mention-triggered runs on every repository the [Warp Factories](/factories/) GitHub App can access.
What it does:
* Listens for comments containing a trigger phrase
* Sends the comment and thread context into the agent
* Agent replies directly to the comment
* If code changes are requested, the agent commits fixes to the PR branch
**When to use:**
* Interactive coding assistance during review or issue triage.
Note
**Private repositories require org membership for `@oz-agent`**
If your repository is in a **private GitHub organization**, you must [invite the `oz-agent` user](https://docs.github.com/en/organizations/managing-membership-in-your-organization/inviting-users-to-join-your-organization) as a member of your organization before using `@oz-agent` mention workflows. Without this:
* `@oz-agent` will not appear in GitHub’s autocomplete when writing comments.
* Comments containing `@oz-agent` will not trigger the workflow, because GitHub does not recognize the mention.
This is a GitHub platform limitation for private organizations — any user must be an org member to be mentioned in comments on private repos.
Public repositories are not affected by this requirement.
### 2. Automated pull request review
[Section titled “2. Automated pull request review”](#2-automated-pull-request-review)
* **File**: [`examples/review-pr.yml`](https://github.com/warpdotdev/oz-agent-action/blob/main/examples/review-pr.yml)
* **Use case**: Provide automated agent feedback when a PR is opened or marked ready for review.
What it does:
* Automatically runs when PRs open or switch to “ready for review”
* Agent inspects changed files, analyzes the diff, and comments inline
* Optionally posts a summary comment
**When to use:**
* Fast initial review before human reviewers step in.
### 3. Automatically fix issues
[Section titled “3. Automatically fix issues”](#3-automatically-fix-issues)
* **File**: [`examples/auto-fix-issue.yml`](https://github.com/warpdotdev/oz-agent-action/blob/main/examples/auto-fix-issue.yml)
* **Use case**: Apply the `oz-agent` label on an Issue to trigger automated fixes.
What it does:
* Detects when the label is added
* Agent analyzes the issue description and repo context
* Creates a PR with a fix (fix/issue-NUMBER)
* Or comments explaining why automation wasn’t possible
**When to use:**
* Automating bug fixes, small features, or maintenance tasks.
### 4. Daily issue summaries
[Section titled “4. Daily issue summaries”](#4-daily-issue-summaries)
* **File**: [`examples/daily-issue-summary.yml`](https://github.com/warpdotdev/oz-agent-action/blob/main/examples/daily-issue-summary.yml)
* **Use case**: Scheduled summaries of newly opened issues.
What it does:
* Runs daily at 09:00 UTC
* Fetches issues created in the past 24 hours
* Generates a categorized summary
* Sends the summary to Slack via webhook
**When to use:**
* Daily visibility into new work across your repositories.
### 5. Fixing failing CI checks
[Section titled “5. Fixing failing CI checks”](#5-fixing-failing-ci-checks)
* **File**: [`examples/fix-failing-checks.yml`](https://github.com/warpdotdev/oz-agent-action/blob/main/examples/fix-failing-checks.yml)
* **Use case**: Automatically attempt fixes when a workflow or test suite fails.
What it does:
* Triggers when specified CI workflows fail
* Pulls failure logs
* Attempts to diagnose and fix the root cause
* Opens a PR with the fix and comments with a link
**When to use:**
* Reducing downtime from failing builds or flaky tests.
### 6. Suggest fixes for review comments
[Section titled “6. Suggest fixes for review comments”](#6-suggest-fixes-for-review-comments)
* **File**: [`examples/suggest-review-fixes.yml`](https://github.com/warpdotdev/oz-agent-action/blob/main/examples/suggest-review-fixes.yml)
* **Use case**: Automatically propose code suggestions for small, actionable review comments such as typos, naming tweaks, and minor refactors.
**What it does:**
* Triggers when a pull request review is submitted
* Fetches review comments and stores them in review\_comments.json
* Sends comments and context to an agent to decide which ones are simple, actionable fixes
* Generates `responses.json` with explanations and suggestion blocks for each fixable comment
* Replies inline to the original review comments with the generated suggestions
**When to use:**
* Quickly addressing straightforward review feedback such as typos, naming tweaks, style nits, and small refactors.
***
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### `@oz-agent` mention doesn’t trigger the workflow
[Section titled “@oz-agent mention doesn’t trigger the workflow”](#oz-agent-mention-doesnt-trigger-the-workflow)
If you’re tagging `@oz-agent` in a PR or issue comment and the workflow doesn’t run:
1. **Check org membership (private repos only)**: In private organizations, the `oz-agent` GitHub user must be a [member of your organization](https://docs.github.com/en/organizations/managing-membership-in-your-organization/inviting-users-to-join-your-organization). Without this, GitHub won’t recognize the mention and the `issue_comment` event won’t match the workflow trigger. Ask an org admin to invite [`oz-agent`](https://github.com/oz-agent) via **Settings > People > Invite member**.
2. **Verify the workflow file**: Ensure your workflow is on the default branch and the trigger condition matches `@oz-agent` (e.g. `contains(github.event.comment.body, '@oz-agent')`).
3. **Check workflow permissions**: The workflow must have the appropriate permissions (e.g. `issues: read`, `pull-requests: write`) to respond.
### `@oz-agent` doesn’t appear in GitHub autocomplete
[Section titled “@oz-agent doesn’t appear in GitHub autocomplete”](#oz-agent-doesnt-appear-in-github-autocomplete)
GitHub only suggests users who are members of the organization when typing `@` in comments on private repositories. [Invite `oz-agent`](https://docs.github.com/en/organizations/managing-membership-in-your-organization/inviting-users-to-join-your-organization) to your organization to make it appear in autocomplete.
Note: Even if `@oz-agent` doesn’t autocomplete, you can still type the mention manually — but the workflow will only trigger if the user is an org member (for private repos).
# GitLab integration
Canonical page: [/platform/integrations/gitlab/](https://docs.warp.dev/platform/integrations/gitlab/)
> Connect cloud agents to GitLab.com repos natively, or use access tokens and Warp-managed secrets for self-managed instances.
Cloud agents work natively with repositories hosted on GitLab.com. Connect your GitLab account when you create an environment in the [Oz web app](https://oz.warp.dev), select the projects agents need, and Warp handles the rest at runtime: repositories are cloned automatically, your GitLab credentials are injected into the run, the `glab` CLI is authenticated, and agents can push branches and open merge requests on your behalf. Merge requests the agent opens are reported as run outputs.
For self-managed GitLab instances, native connection isn’t available yet. Instead, grant agents access using a personal access token and Warp-managed secrets, as described in [Self-managed GitLab instances](#self-managed-gitlab-instances).
Note
To route GitLab activity into a factory — merge request events and bot mentions triggering work — see the [GitLab factory integration](/factories/integrations/gitlab/) instead. This page covers standalone cloud agent environments.
***
## Connect GitLab.com natively
[Section titled “Connect GitLab.com natively”](#connect-gitlabcom-natively)
1. In the [Oz web app](https://oz.warp.dev), create or edit an [environment](/platform/environments/).
2. Choose GitLab as the repository source and authorize with your GitLab account when prompted. Warp requests the `api` and `read_user` scopes, which grant read and write access to your projects.
3. Select the projects the agent should clone, then finish configuring the environment (Docker image, setup commands).
At the start of each run, Warp clones the selected repositories and injects your GitLab token, so agents can fetch, push branches, and open merge requests without extra setup. Once configured, the environment works with any Automation Platform trigger—Slack, Linear, schedules, or the CLI.
Note
Native GitLab environment creation is available in the Oz web app only. The `--repo` flag on `oz environment create` accepts GitHub repositories; to script GitLab environments, use the web app or the setup-command approach below.
***
## Self-managed GitLab instances
[Section titled “Self-managed GitLab instances”](#self-managed-gitlab-instances)
Native connection supports GitLab.com only. For a self-managed GitLab instance, generate a personal access token, store it securely, and configure an environment that clones your repository at runtime.
### Step 1: Generate a personal access token
[Section titled “Step 1: Generate a personal access token”](#step-1-generate-a-personal-access-token)
Note
These steps generate a personal access token tied to your GitLab account. If your team prefers a shared bot user, [GitLab project access tokens](https://docs.gitlab.com/user/project/settings/project_access_tokens/) work the same way.
1. Sign in to GitLab.
2. Click your avatar in the top-right corner, then click **Edit profile**.
3. In the left sidebar, click **Access**, then click **Personal access tokens**.
4. Click **Add new token**.
5. Enter a descriptive name for the token (e.g. `warp-agent`), and choose an expiration date that matches your team’s rotation policy.
6. Under **Select scopes**, select **read\_repository**.
7. Click **Generate token**.
8. Copy the token value immediately. GitLab will not show it again.
Note
**read\_repository** is the minimum required scope to clone a repository. If a workflow requires the agent to push commits or open merge requests, you also need **write\_repository**.
### Step 2: Store the token as a Warp-managed secret
[Section titled “Step 2: Store the token as a Warp-managed secret”](#step-2-store-the-token-as-a-warp-managed-secret)
Warp injects managed secrets as environment variables at runtime and never exposes them in logs or configuration files. See the [Secrets](/platform/secrets/) documentation for full details on scoping and managing secrets.
1. Run the following command:
```bash
oz secret create --team GITLAB_TOKEN
```
2. When prompted, paste the token.
The value is stored and encrypted, and cannot be retrieved after creation.
Note
Use `--team` to create a shared token available to all teammates and automated triggers (schedules, Slack, Linear). Use `--personal` if each team member should authenticate with their own GitLab token. Personal secrets work with all triggers and take precedence over a team secret of the same name when both exist.
If you need to update a secret value, run:
```bash
oz secret update --value GITLAB_TOKEN
```
### Step 3: Create an environment with a clone setup command
[Section titled “Step 3: Create an environment with a clone setup command”](#step-3-create-an-environment-with-a-clone-setup-command)
Create an environment that uses your token to clone the repository at the start of each agent run.
1. Run the following command:
```bash
oz environment create \
--name "my-gitlab-env" \
--docker-image <image> \
--setup-command 'git clone https://oauth2:$GITLAB_TOKEN@gitlab.example.com/your-group/your-repo.git' \
--setup-command 'cd your-repo && <install dependencies>'
```
Caution
Use single quotes around setup commands that reference secrets. Double quotes cause your shell to expand `$GITLAB_TOKEN` immediately (to nothing), rather than letting Warp inject the secret at runtime inside the container.
2. Replace the following placeholders:
* `<image>` with your Docker image (for example, `node:22`, `python:3.12`, or a [Warp prebuilt dev image](https://github.com/warpdotdev/oz-dev-environments))
* `gitlab.example.com/your-group/your-repo.git` with your server’s hostname and repository path
* The second `--setup-command` with any dependency install or build steps your project requires. For example, `npm ci` or `pip install -r requirements.txt`.
Caution
Setup commands run on a fresh container for every agent run. Write them to be idempotent — commands that assume existing state (such as a partially cloned repo or a pre-built cache) can fail unpredictably. See [environment design and best practices](/platform/environments/configuring-environments/#environment-design-and-best-practices) for guidance.
3. Note the environment ID returned. You will need it in the next step.
### Step 4: Test your environment
[Section titled “Step 4: Test your environment”](#step-4-test-your-environment)
Before connecting to integrations, verify the environment works by running a one-off agent.
1. Run the following command, replacing `<ENV_ID>` with the environment ID from Step 3:
```bash
oz agent run-cloud --environment <ENV_ID> --prompt "Your task here"
```
***
## Next steps
[Section titled “Next steps”](#next-steps)
With your environment configured, you can connect it to any Warp trigger:
* **Slack** — Tag **@warp** in a message to start an agent run against your GitLab repo. See [Slack](/platform/integrations/slack/).
* **Linear** — Tag **@warp** on an issue to kick off a workflow. See [Linear](/platform/integrations/linear/).
* **Scheduled agents** — Run agents on a recurring schedule. See [Scheduled Agents](/platform/triggers/scheduled-agents/).
# Jira integration
Canonical page: [/platform/integrations/jira/](https://docs.warp.dev/platform/integrations/jira/)
> Trigger cloud agent runs directly from Jira issues using the warp-agent label.
The Jira integration lets your team kick off cloud agent runs directly from Jira Cloud issues. When you add the `warp-agent` label to an issue, an agent starts in the cloud and gets to work — then posts status updates and a summary as Jira comments when it’s done.
***
### Requirements
[Section titled “Requirements”](#requirements)
* **Jira Cloud** - Jira Server and Data Center are not supported.
* **Team membership** - The Jira integration requires you to be part of a [Warp team](/knowledge-and-collaboration/teams/). Teams can be created on any plan, including Free.
* **Plan and credits** - Your team must be on a plan that supports integrations (Build, Max, or Business) and have at least 20 credits available. See [Access, Billing, and Identity](/platform/team-access-billing-and-identity/) for details.
* **Infrastructure** - By default, agents run on Warp-hosted infrastructure. Enterprise teams can [self-host agents](/factories/self-hosting/) on their own infrastructure.
* **Jira site admin** - Installing the Warp app on your Jira site requires site admin permissions.
***
### Setup
[Section titled “Setup”](#setup)
#### 1. Open the Jira app installation page
[Section titled “1. Open the Jira app installation page”](#1-open-the-jira-app-installation-page)
In the [Oz web app](https://oz.warp.dev/integrations), find Jira and click **Set up**. On the Atlassian installation page, click **Get app**.
#### 2. Install the app on your Jira site
[Section titled “2. Install the app on your Jira site”](#2-install-the-app-on-your-jira-site)
Choose the Jira Cloud site you want to connect, review the requested permissions, and install the Warp app. Only Jira site admins can install apps.
#### 3. Open the app configuration page
[Section titled “3. Open the app configuration page”](#3-open-the-app-configuration-page)
In your Jira site, open **Manage apps**. Find **Warp**, open its three-dot actions menu, then click **Configure**.
The configuration page URL for the production app follows this pattern:
```text
https://<your-site-subdomain>.atlassian.net/jira/settings/apps/configure/40dbc167-16d9-4b68-9752-277c5a52aa01/34808a52-a321-44c2-bac4-a15eb316df50/static/warp-jira-configure/34808a52-a321-44c2-bac4-a15eb316df50
```
Replace `<your-site-subdomain>` with your Jira Cloud site subdomain.
#### 4. Connect Jira to your Warp workspace
[Section titled “4. Connect Jira to your Warp workspace”](#4-connect-jira-to-your-warp-workspace)
On the app configuration page in Jira, click **Connect to Warp**. Sign in to Warp if prompted. Warp automatically binds the Jira installation to your Warp workspace.
The confirmation page displays **Jira connected** when the connection succeeds. Jira-triggered runs are now available to members of the connected Warp workspace. Installing the app doesn’t require any action from individual teammates up front — each member connects their own Jira account to Warp the first time they trigger a run (see [Connecting your Jira account to Warp](#connecting-your-jira-account-to-warp)).
#### 5. (Optional) Configure the default environment, model, and harness
[Section titled “5. (Optional) Configure the default environment, model, and harness”](#5-optional-configure-the-default-environment-model-and-harness)
Return to the [Integrations page in the Oz web app](https://oz.warp.dev/integrations), then click **Edit Jira** to set the default [environment](/platform/environments/), model, harness, and agent for Jira-triggered runs. If you don’t change these settings, Jira-triggered runs use your workspace’s default configuration.
***
### How to start a run
[Section titled “How to start a run”](#how-to-start-a-run)
Add the label **`warp-agent`** to any Jira issue. Warp will pick it up, post a comment to let you know it’s started, and begin working through the task using the issue title, description, and recent comments as context.
When the run finishes, Warp posts a summary comment to the issue with links to any pull requests or branches it created, along with a link to the full conversation in Warp. To track runs across your team, open the [Agent Management Panel](/platform/managing-cloud-agents/) in the Warp app, where Jira-triggered runs appear in the **All** tab.
#### Connecting your Jira account to Warp
[Section titled “Connecting your Jira account to Warp”](#connecting-your-jira-account-to-warp)
This step is for any user who triggers runs — it doesn’t require Jira admin permissions. The first time you trigger a run, Warp posts a comment prompting you to connect your Jira account to Warp. Connecting attributes your Jira-triggered runs to your Warp account; the run doesn’t start until your account is connected. After connecting, re-add the `warp-agent` label to start the run.
1. Follow the link in the comment to open the Warp page in your Jira personal settings. The link for the production app follows this pattern:
```text
https://<your-site-subdomain>.atlassian.net/jira/settings/personal/apps/40dbc167-16d9-4b68-9752-277c5a52aa01/34808a52-a321-44c2-bac4-a15eb316df50
```
2. Click **Connect to Warp**. A Warp page opens and links your account automatically. Sign in to Warp first if prompted.
The page displays **Jira account connected** when the link succeeds, and the settings page shows a **Connected to Warp** badge. Runs you trigger from then on are attributed to you.
***
### Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
If Warp doesn’t respond after adding the label, check that:
* The Warp app is installed on your Jira site and the workspace is connected (see the app’s **Configure** screen in Jira).
* The issue is in Jira Cloud (not Server or Data Center).
Note
When a Jira-triggered run fails to start, Warp updates its comment on the issue to say it could not start the task. Re-add the `warp-agent` label to try again; a new attempt starts a new comment thread.
For other issues, reach out to your Warp contact or join the [Warp community on Slack](https://go.warp.dev/join-preview).
***
### Related pages
[Section titled “Related pages”](#related-pages)
* [Integrations overview](/platform/integrations/) - How environments and integrations work together.
* [Slack](/platform/integrations/slack/) and [Linear](/platform/integrations/linear/) - Other chat- and issue-triggered integrations.
* [Managing cloud agents](/platform/managing-cloud-agents/) - Monitor Jira-triggered runs across your team.
* [Environments](/platform/environments/) - Configure where agents run.
# Linear integration
Canonical page: [/platform/integrations/linear/](https://docs.warp.dev/platform/integrations/linear/)
> Automate Linear issues with agents that run code in the cloud and create pull requests on your behalf.
The Linear integration lets your team delegate development work directly to agents from inside Linear. When you tag @warp on an issue or comment, an agent will spin up in the cloud, clone the repos defined in your environment, and begin working through the task.
Agents keep you updated inside Linear, generate pull requests using your GitHub account, and provide a link to join a live remote session so you can watch or steer the workflow in real time.
This guide explains what the integration does, how it works end-to-end, and how to configure it for your Warp team.
***
### Triggering agents inside Linear
[Section titled “Triggering agents inside Linear”](#triggering-agents-inside-linear)
Tagging @warp on an issue or in a Linear comment starts an agent run. Warp clones the repositories defined in your environment, sets up your development environment using your Docker image and setup commands, and begins working through the task with full context from your codebase and the Linear issue. Agents post updates as they progress, including a task list, elapsed time, and checkpoints, so you can follow along without leaving Linear.
Agents also share a link to an interactive remote session using Warp’s [cloud agent session sharing](/platform/viewing-cloud-agent-runs/). Opening this link lets you view the live terminal output for the running agent in Warp or in the browser. From there, you can interrupt or guide the agent with additional instructions when needed. Once the agent finishes, it will create a pull request on your behalf — using your GitHub permissions — and post a summary of its work and the PR link back into Linear.
You can start an agent in two ways:
* **Tag @warp in a comment** and describe what you want done.
* **Assign the issue to @warp** as if it were a teammate.
The agent will acknowledge the request directly in the Linear issue and begin working.
Agents keep you informed through:
* **Activity updates** inside Linear
* A **running task list** and timeline showing what the agent is working on
* A **shared session link** that opens a live view of the agent’s cloud environment
Session sharing works in Warp or in a browser view and allows multiple teammates to watch the session.
To monitor Linear-triggered runs alongside the rest of your team’s agents, open the [Agent Management Panel](/platform/managing-cloud-agents/) in the Warp app, where integration-triggered runs appear in the **All** tab.

#### Joining the remote session
[Section titled “Joining the remote session”](#joining-the-remote-session)
Selecting [**Open in Warp**](/platform/viewing-cloud-agent-runs/) (or the web option) opens the active session. You’ll see:
* The agent’s full execution log
* The plan pane with the task list
* An input box to add clarifying instructions
* A real-time view identical to a local Warp task
Any instructions you give will interrupt the agent, feed the new context, and resume work.
When the task is complete:
* Warp commits the changes using your GitHub identity
* A pull request is created through the GitHub CLI
* The PR includes a clean title and description based on the Linear issue and the agent’s work
* A summary and link to the PR appear in the Linear issue
Because PRs are created as *you*, this makes code review, auditing, and team collaboration straightforward.
***
### Requirements
[Section titled “Requirements”](#requirements)
* **Team membership** - The Linear integration requires you to be part of a [Warp team](/knowledge-and-collaboration/teams/). Teams can be created on any plan, including Free.
* **Plan and credits** - Your team must have cloud agents enabled and credits available. See [Access, Billing, and Identity](/platform/team-access-billing-and-identity/) for details.
* **Infrastructure** - By default, agents run on Warp-hosted infrastructure. Enterprise teams can [self-host agents](/factories/self-hosting/) on their own infrastructure.
* **Identity** - The first time you trigger an agent, Warp prompts you to connect your Linear identity to your Warp account.
* **GitHub authorization** - You must authorize the Warp GitHub app the first time you trigger an agent.
* The repositories involved must be included in your environment and accessible to the Warp GitHub app.
* You must have write access to the repo if you want Warp to create PRs on your behalf.
***
### How to configure the integration
[Section titled “How to configure the integration”](#how-to-configure-the-integration)
Setup involves two steps powered by the [Oz CLI](/agents/cli/oz-cli/). For more instructions, see [Integrations Overview](/platform/integrations/).
#### 1. Create an environment
[Section titled “1. Create an environment”](#1-create-an-environment)
An environment defines everything the agent needs to run your code:
* A **Docker image** (public on Docker Hub)
* A set of **GitHub repos** the agent should clone
* Optional **setup commands** that run before the agent starts
You can create an environment via:
* The CLI
* The guided flow using `/create-environment` ([Slash Commands](/agents/capabilities/slash-commands/))
For full instructions, see our [Environment Setup](/platform/integrations/) docs.
#### 2. Create the Linear integration
[Section titled “2. Create the Linear integration”](#2-create-the-linear-integration)
Once your environment exists, create the integration.
Note
For easier setup, use the [Oz web app](https://oz.warp.dev) to configure integrations with a guided flow.
Alternatively, you can use the CLI:
```plaintext
oz integration create linear --environment <ENV_ID>
```
The CLI will open a browser window prompting you to install the Warp app into your Linear workspace. After installation, the integration becomes available to all members of your Warp team.
Tip
If the integration cannot be created or a Linear-triggered run cannot start, use the returned error code to narrow the fix. Common errors include:
* [`feature_not_available`](/factories/api-and-sdk/troubleshooting/errors/feature-not-available/) (plan does not support integrations)
* [`external_authentication_required`](/factories/api-and-sdk/troubleshooting/errors/external-authentication-required/) (missing GitHub or Linear authorization)
***
### Uninstallation instructions
[Section titled “Uninstallation instructions”](#uninstallation-instructions)
To remove the Warp app from Linear:
1. Only a Linear team admin can manage app permissions.
2. In Linear, go to **Settings**.
3. Navigate to Agents under the Features section.
4. Select **Warp** from the list of installed agents.
5. Click **Revoke access** to remove the integration for your workspace.
[Uninstalling the Warp Linear integration video](https://www.loom.com/embed/2f1648586d8148dc80561c00a09ca334)
After revoking access, Warp will no longer be able to read issues, receive triggers, or create updates in Linear. If you reinstall later, you’ll need to authorize Warp again during setup. Events for a disabled integration can return [`integration_disabled`](/factories/api-and-sdk/troubleshooting/errors/integration-disabled/).
### Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
If something isn’t working as expected—missing repos, PR failures, Linear not detecting @Oz, or environment issues—see [troubleshooting cloud agent environments](/platform/environments/troubleshooting-environments/) for guidance on GitHub permissions, repo access, Docker images, and setup failures.
# Integrations quickstart
Canonical page: [/platform/integrations/quickstart/](https://docs.warp.dev/platform/integrations/quickstart/)
> Trigger your first agent from Slack in ~15 minutes and get results in-thread.
Automation Platform integrations let you trigger cloud agents directly from the tools your team already uses. This guide walks you through connecting Warp to Slack. Once set up, anyone on your team can tag @warp in a message or thread to kick off a cloud agent that runs the task and posts results back to the conversation.
Note
**Want to connect with Linear instead?** The setup is the same — just substitute `slack` with `linear` in the CLI commands, or select Linear in the Oz web app. See [Linear](/platform/integrations/linear/) for details.
***
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **Eligible team** - The Slack integration requires a Warp team with cloud agents enabled and credits available. See [Access, Billing, and Identity](/platform/team-access-billing-and-identity/).
* **A cloud environment** - Agents run inside a configured environment that includes repos and other dependencies. If you don’t have one yet, follow the [Cloud Agents Quickstart](/platform/quickstart/) or run `/create-environment` in Warp.
* **GitHub authorization** - Warp needs access to your repos to clone code and open PRs. You’ll be prompted to authorize the Warp GitHub app when you first create the integration.
***
## 1. Connect the Slack integration
[Section titled “1. Connect the Slack integration”](#1-connect-the-slack-integration)
The simplest way to set up the integration is **using the Oz web app**:
1. Navigate to the [Integrations page in the Oz web app](https://oz.warp.dev/integrations).
2. Click **Slack**.
3. Follow the guided flow to select your environment and authorize the Warp app in your Slack workspace.
All members of your Warp team can now use the integration.
**Using the Oz CLI instead:**
Run `oz integration create` to connect the Slack integration:
```bash
oz integration create slack --environment <ENV_ID>
```
Replace `<ENV_ID>` with your environment ID (see [Environments](/platform/environments/) if you need to create one). Find it with `oz environment list` on the Oz CLI or in the [Oz web app](https://oz.warp.dev). The CLI opens a browser window to authorize the Warp app in your workspace.
Tip
If the integration cannot be created or your first run cannot start, use the returned error code to narrow the fix. Common errors include:
* [`feature_not_available`](/factories/api-and-sdk/troubleshooting/errors/feature-not-available/) (plan does not support integrations)
* [`external_authentication_required`](/factories/api-and-sdk/troubleshooting/errors/external-authentication-required/) (missing GitHub or Slack authorization)
To attach a default prompt that applies to every agent run triggered from this integration, add the `--prompt` flag:
```bash
oz integration create slack \
--environment <ENV_ID> \
--prompt "Always open a draft PR and request review from the team-leads group."
```
## 2. Tag the agent in Slack
[Section titled “2. Tag the agent in Slack”](#2-tag-the-agent-in-slack)
In any channel or thread in your Slack workspace, tag @warp with a task:
> @warp scan the authentication module for security issues and summarize what you find
Warp acknowledges the request immediately and starts an agent run in the cloud. You’ll see progress updates appear in the thread as the agent works.
You can also tag @warp inside an existing thread. Warp picks up the full thread history as context automatically, so you can tag it mid-discussion without repeating background.
## 3. Watch the run
[Section titled “3. Watch the run”](#3-watch-the-run)
While the agent works, progress updates appear directly in the Slack thread. To inspect the run in more detail:
* **Click the session link** - Warp posts a link in the thread to open a live terminal view of the agent. Watch in real time, add follow-up instructions, or let it run to completion.
* **Go to the [Runs page in the Oz web app](https://oz.warp.dev/runs)** - See the full run transcript: status, commands executed, files changed, and agent output. See [Viewing Cloud Agent Runs](/platform/viewing-cloud-agent-runs/) for a complete walkthrough.
When the task is complete, Warp posts a summary back to the original Slack thread.
**Breaking it down:** Warp reads the Slack thread as context, runs the agent inside the environment you configured — with your repos cloned and Docker image running — and returns results where the conversation started, in Slack, without anyone leaving the thread.
***
## Next steps
[Section titled “Next steps”](#next-steps)
* **Customize agent behavior** - Use a [skill](/platform/skills-as-agents/) as the base prompt for your integration to give agents consistent, reusable instructions across every run.
* **Trigger agents programmatically** - Use the [API & SDK](/factories/api-and-sdk/) to build custom automations and integrations on top of agents.
* **Read the full Slack reference** - [Slack](/platform/integrations/slack/) covers identity mapping, team access, monitoring runs, troubleshooting, and uninstall instructions.
# GitHub Actions quickstart
Canonical page: [/platform/integrations/quickstart-github-actions/](https://docs.warp.dev/platform/integrations/quickstart-github-actions/)
> Set up your first agent in GitHub Actions in ~10 minutes. Run agents as workflow steps to automate code review and issue triage.
Add agents to your GitHub Actions workflows with [`oz-agent-action`](https://github.com/warpdotdev/oz-agent-action). This quickstart walks you through setting up your first GitHub Actions integration: a PR review workflow that automatically analyzes pull requests and posts inline review comments.
***
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **Warp API key** - Create one in the [Oz web app](https://oz.warp.dev/settings). Use a personal key if the agent should commit as you, or an agent key (which runs as a [cloud agent](/platform/agents/) on your team) with [team GitHub authorization](/platform/team-access-billing-and-identity/#team-github-authorization). See [API Keys](/agents/cli/oz-cli/api-keys/) for the full creation flow.
* **A GitHub repository with Actions enabled** - The workflow file will live in `.github/workflows/` in your repo.
***
## 1. Add your API key as a GitHub Actions secret
[Section titled “1. Add your API key as a GitHub Actions secret”](#1-add-your-api-key-as-a-github-actions-secret)
Store your Warp API key as a GitHub Actions secret so workflows can authenticate without exposing the key in your code.
1. In your repository on GitHub, go to **Settings** > **Secrets and variables** > **Actions**.
2. Click **New repository secret**.
3. Set the name to `WARP_API_KEY`.
4. Paste your API key into the **Secret** field.
5. Click **Add secret**.
## 2. Create the workflow file
[Section titled “2. Create the workflow file”](#2-create-the-workflow-file)
This workflow triggers an agent whenever a PR is opened or marked ready for review. The agent reviews the diff and posts inline comments.
Create `.github/workflows/oz-pr-review.yml` in your repository with the following content:
```yaml
name: Warp PR review
on:
pull_request:
types: [opened, ready_for_review]
permissions:
contents: read
pull-requests: write
jobs:
review:
runs-on: ubuntu-latest
steps:
- uses: actions/checkout@v4
- name: Review PR with Warp
uses: warpdotdev/oz-agent-action@v1
with:
prompt: |
Review the code changes on this pull request:
1. Use `git diff origin/${{ github.base_ref }}...HEAD` to identify changes.
2. Analyze the diff for style, security, or correctness issues.
3. Use `gh pr review --comment` to post inline suggestions.
warp_api_key: ${{ secrets.WARP_API_KEY }}
```
This workflow listens for pull request events and runs the `oz-agent-action` step, which executes the prompt to review code changes. Commit and push this file to your default branch to activate the workflow.
## 3. Open a pull request
[Section titled “3. Open a pull request”](#3-open-a-pull-request)
Create a new pull request in your repository to trigger the workflow.
To verify the workflow ran:
1. Go to the **Actions** tab in your repository.
2. Click **Warp PR review** in the list of workflows.
3. Select the most recent run to see the agent’s output in the job logs.
## 4. View the run
[Section titled “4. View the run”](#4-view-the-run)
Each `oz-agent-action` step creates a run you can inspect from the cloud agent dashboard:
* **Oz web app** - Go to the [Runs page in the Oz web app](https://oz.warp.dev/runs) to see the full run transcript: status, commands executed, files changed, and agent output. See [Viewing Cloud Agent Runs](/platform/viewing-cloud-agent-runs/) for a complete walkthrough.
* **Warp app** - Open the conversations panel to see the run alongside your other agent activity.
When the run completes, the agent posts feedback as inline review comments on the PR.
**Breaking it down:** The agent runs in Warp’s cloud infrastructure — not on GitHub’s runners — using the workflow’s GitHub token for repository access. Each run is isolated, tracked, and auditable, just like any manually triggered cloud agent run.
***
## Next steps
[Section titled “Next steps”](#next-steps)
* **Explore more workflow patterns** - The [oz-agent-action repository](https://github.com/warpdotdev/oz-agent-action) includes ready-to-use consumer workflow templates for responding to `@oz-agent` comments, auto-fixing labeled issues, daily issue summaries, fixing failing CI checks, and suggesting review fixes. Copy any template from `consumer-workflows/` into `.github/workflows/` in your repo.
* **Use skills for reusable behavior** - Replace the inline `prompt` with a `skill` parameter to apply consistent, version-controlled instructions across all your CI workflows. See [Skills](/agents/capabilities/skills/).
* **Read the full reference** - [GitHub Actions](/platform/integrations/github-actions/) covers all action inputs, output handling, session sharing for debugging, and troubleshooting.
# Slack integration
Canonical page: [/platform/integrations/slack/](https://docs.warp.dev/platform/integrations/slack/)
> Trigger agents from Slack to run cloud tasks, track progress, and create pull requests.
The Slack integration lets your team trigger cloud agents directly from Slack conversations. Tag @Warp in a message or DM the bot to start a cloud agent that clones your repos, works through the task, posts progress updates, and opens pull requests back into the same thread.
### Get started
[Section titled “Get started”](#get-started)
#### Installation
[Section titled “Installation”](#installation)
1. Log in to the [Oz web app](https://oz.warp.dev) and go to the [Integrations page](https://oz.warp.dev/integrations).
2. Click **Connect** next to **Slack**. You’ll be prompted to install the Warp app into your Slack workspace.
3. After installing, you’re returned to the Integrations page to finish setup: choose the [environment](/platform/environments/) agents should use, which defines the repos, Docker image, and setup commands.
4. Start using Warp in Slack by mentioning **@Warp** with a task.
Alternatively, install via the [Oz CLI](/agents/cli/oz-cli/):
```plaintext
oz integration create slack --environment <ENV_ID>
```
The CLI opens a browser window to install the Warp app into your Slack workspace. After installation, the integration is available to all members of your Warp team.
#### Requirements
[Section titled “Requirements”](#requirements)
* **Team membership** - The Slack integration requires you to be part of a [Warp team](/knowledge-and-collaboration/teams/). Teams can be created on any plan, including Free.
* **Plan and credits** - Your team must have cloud agents enabled and credits available. See [Access, Billing, and Identity](/platform/team-access-billing-and-identity/) for details.
* **Infrastructure** - By default, agents run on Warp-hosted infrastructure. Enterprise teams can [self-host agents](/factories/self-hosting/) on their own infrastructure.
***
### Using Warp inside Slack
[Section titled “Using Warp inside Slack”](#using-warp-inside-slack)
Tagging @Warp in a message or thread starts an agent run. The agent clones the repositories in your environment, sets up your development environment using your Docker image and setup commands, and begins working with the context from the Slack conversation. The bot posts updates back into the thread as it progresses so you can follow along without opening your terminal.
Agents also share a link to an interactive remote session using Warp’s [cloud agent session sharing](/platform/viewing-cloud-agent-runs/). Opening this link gives you a live terminal view of the cloud agent running your code. You can interrupt or steer the agent by providing additional instructions, and the agent will pick up where it left off with the new context.
When the work is complete, Warp will create a pull request on your behalf using your GitHub permissions and send a summary and PR link back to the original Slack thread.
### Triggering an agent
[Section titled “Triggering an agent”](#triggering-an-agent)
You can start an agent in three ways:
* **Tag @Warp in a channel message**
Describe the task, and Warp will begin working with full context from the thread.
* **Tag @Warp inside a thread**
Warp will automatically collect the thread’s prior messages and use them as context.
* **DM the Warp bot directly**
Useful for private tasks or experimentation.
The bot will acknowledge the request in Slack and start running the task immediately.
### Monitoring agent progress
[Section titled “Monitoring agent progress”](#monitoring-agent-progress)
Agents keep you informed directly in Slack via:
* Activity updates showing progress throughout the run
* Checkpoints indicating major steps completed
* A direct link to the cloud agent run in the [Oz web app](/platform/oz-web-app/), where you can view the full run transcript and metadata
* A session-sharing link that opens a live terminal view of the remote agent
[Cloud agent session sharing](/platform/viewing-cloud-agent-runs/) works in Warp or in your browser and supports multiple teammates joining the same live session.
To monitor Slack-triggered runs alongside the rest of your team’s agents, open the [Agent Management Panel](/platform/managing-cloud-agents/) in the Warp app, where integration-triggered runs appear in the **All** tab.
### Joining the live remote session
[Section titled “Joining the live remote session”](#joining-the-live-remote-session)
Selecting **View conversation** opens the active agent session. Inside the session you’ll see:
* The agent’s full execution log
* The plan/task list
* Real-time output just like a local Warp task
* An input box for follow-up instructions
Any instruction you type will interrupt the agent, incorporate the new guidance, and then resume execution. This is the best way to debug or steer multi-step tasks.
### Pull requests and output
[Section titled “Pull requests and output”](#pull-requests-and-output)
Once the agent finishes, it will:
* Commit changes using your GitHub account
* Create a pull request via the GitHub CLI
* Generate a clean title and description referencing your Slack request
* Post the summary and PR link directly into the Slack thread
Because PRs are created as you, the workflow slots seamlessly into your team’s existing review process.
***
### Configuration
[Section titled “Configuration”](#configuration)
#### 1. Create an environment
[Section titled “1. Create an environment”](#1-create-an-environment)
An environment defines everything the agent needs to run your code in the cloud:
* A Docker image (public on Docker Hub)
* The GitHub repos the agent should clone
* Optional setup commands that run before the agent starts
Create an environment via:
* **Oz CLI**
```bash
oz environment create \
--name <name> \
--docker-image <image> \
--repo <owner/repo> \
--setup-command "<command>"
```
* **Guided setup using `/create-environment`** ( [Slash Commands](/agents/capabilities/slash-commands/))
This flow analyzes your repos, recommends a Docker image, suggests setup commands, and can build + push a custom image if needed.
See the [Environments](/platform/environments/) docs for detailed instructions.
#### 2. Optional: custom prompt
[Section titled “2. Optional: custom prompt”](#2-optional-custom-prompt)
You can attach a custom prompt that is applied to every agent run:
```plaintext
oz integration create slack \
--environment <ENV_ID> \
--prompt "Always prefix PR titles with '[WARP]' and include detailed test steps."
```
Tip
If the integration cannot be created or a Slack-triggered run cannot start, use the returned error code to narrow the fix. Common errors include:
* [`feature_not_available`](/factories/api-and-sdk/troubleshooting/errors/feature-not-available/) (plan does not support integrations)
* [`external_authentication_required`](/factories/api-and-sdk/troubleshooting/errors/external-authentication-required/) (missing GitHub or Slack authorization)
### Identity mapping and team access
[Section titled “Identity mapping and team access”](#identity-mapping-and-team-access)
* Integrations are scoped to your Warp team.
* Any teammate in the same Slack workspace and Warp team can use the integration.
* The first time you mention the bot or DM it, Warp sends you a link to connect your Slack identity to your Warp account.
* Teammates must individually authorize GitHub on their first run.
***
### Privacy
[Section titled “Privacy”](#privacy)
The Warp app reads Slack messages only where it is mentioned or directly messaged: the triggering message, its thread history (used as task context), and your Slack profile information. Message content is used to run the agent task and is handled per the [Warp Privacy Policy](https://www.warp.dev/privacy), which describes how Warp collects, manages, and stores third-party data.
### Uninstallation instructions
[Section titled “Uninstallation instructions”](#uninstallation-instructions)
To remove the Warp app from your Slack workspace:
1. Open Slack and go to **Apps** in the left sidebar.
2. Search for Warp.
3. Select the app, then open the **About** tab.
4. Click **Configuration**. This will open your workspace’s app configuration page in the browser.
5. Scroll to the bottom and select **Remove App**.
6. Confirm the removal.
The Warp Slackbot in Slack.
Once removed, Slack will immediately disable the integration for all teammates. Events for a disabled integration can return [`integration_disabled`](/factories/api-and-sdk/troubleshooting/errors/integration-disabled/).
### Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
If something isn’t working—missing repos, Slack not detecting @Warp, PR failures, or environment configuration issues—see [troubleshooting cloud agent environments](/platform/environments/troubleshooting-environments/). It covers:
* GitHub authorization and repo access
* Docker image incompatibility
* Missing credentials and secrets
* Setup commands that fail on a fresh container
For identity mismatches and installation problems, see [identity mapping and team access](/platform/integrations/slack/#identity-mapping-and-team-access) above.
# Managing cloud agents
Canonical page: [/platform/managing-cloud-agents/](https://docs.warp.dev/platform/managing-cloud-agents/)
> Monitor and manage agent activity across your team with Warp's Agent Management Panel and the Oz web app's Runs page.
Warp provides two management surfaces for tracking and observing agent activity across your account and, where applicable, your team: the **Agent Management Panel** in the Warp app and the [**Runs** page in the Oz web app](/platform/oz-web-app/#runs), which also works on mobile devices.
Use these surfaces as the starting point for real-time agent observability in Warp. They help you see which agents are active, which runs are blocked or failed, where each run started, and which session link opens the prompt, plan, commands, logs, outputs, and follow-up messages behind the work.
To inspect work from one factory, use that factory’s [Runs page](/factories/factory-dashboard/#inspect-runs). This page remains the reference for interactive and standalone cloud-agent management.
The Agent Management Panel and Oz web app Runs page are designed to answer, at a glance:
* Which agents are active or have been running recently.
* Which runs are working, blocked, failed, succeeded, or canceled.
* Where an agent run was triggered from, such as a local agent conversation, the Oz CLI, Slack, Linear, a schedule, or the API.
* How parent and child runs relate in orchestrated workflows.
* Which session to open when you need prompt, plan, command, log, output, or follow-up context.
* How many credits those runs consumed.
Warp’s agent observability is run- and session-oriented. It is not a replacement for full APM, OpenTelemetry, or Datadog-style tracing across arbitrary agent frameworks. Use Warp to track agent run status, trigger/source, owner, parent-child relationships, transcripts, commands, logs, outputs, and replayable session links.
[Managing cloud agent runs video](https://www.loom.com/embed/679c267ddd2d44519abf79edcb1122c7)
These management surfaces include your **local (interactive) agents** and [cloud agent](/platform/) runs.
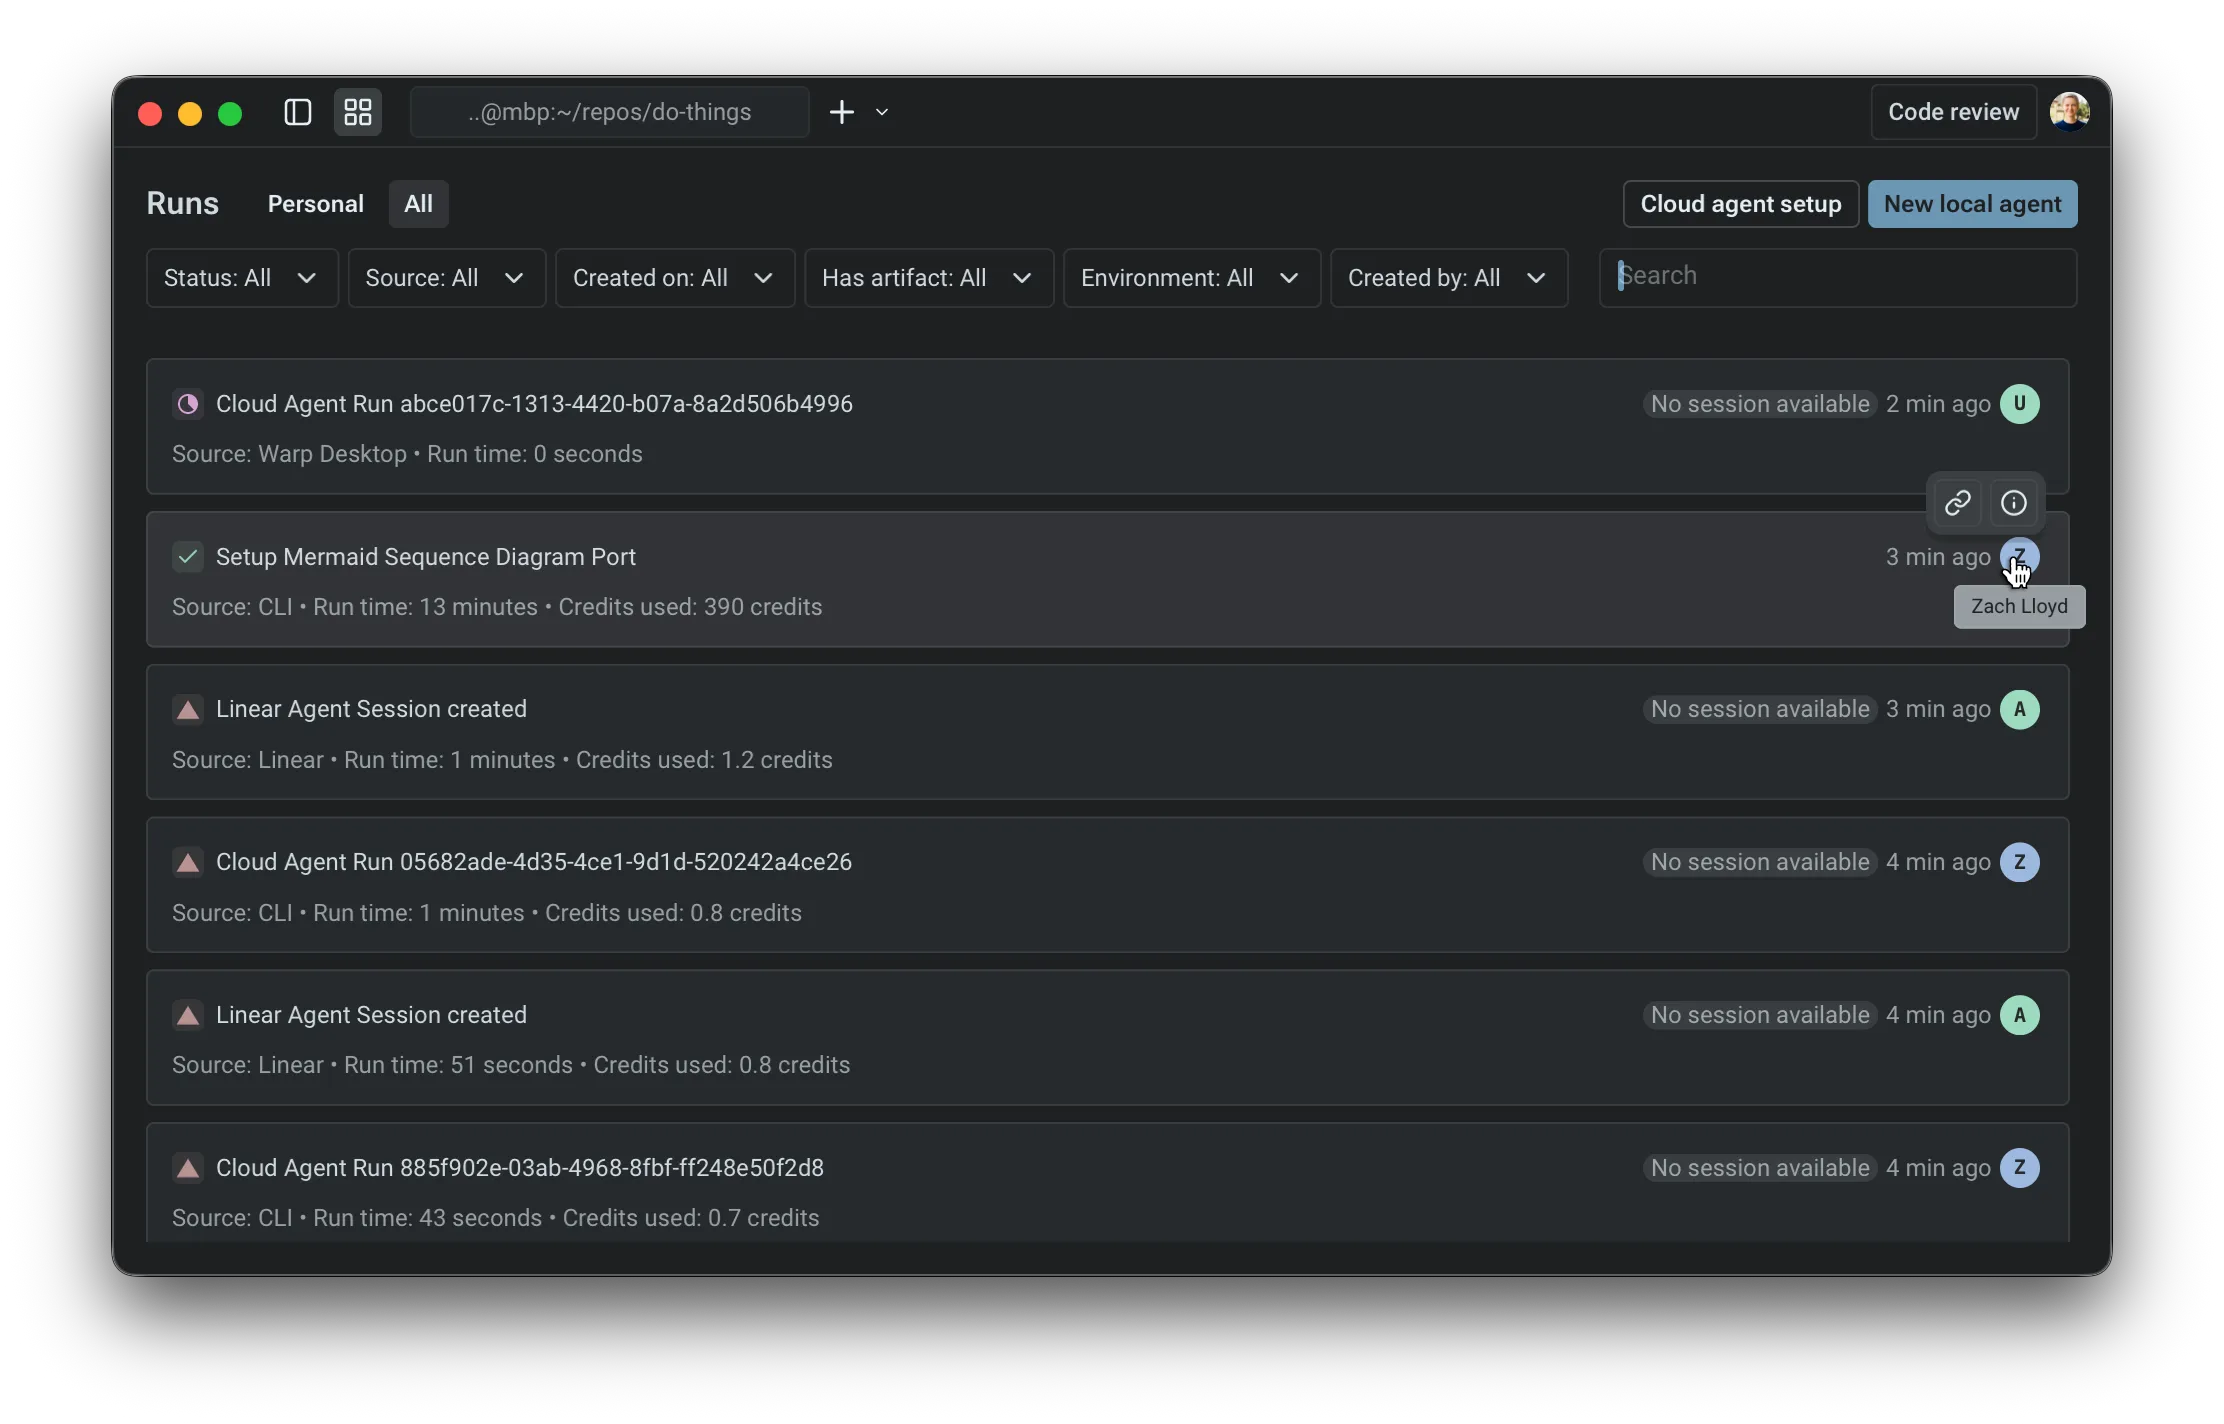
Warp’s Agent Management Panel showing interactive and cloud agent runs.
### What appears in the agent management surfaces
[Section titled “What appears in the agent management surfaces”](#what-appears-in-the-agent-management-surfaces)
The Agent Management Panel and Oz web app Runs page include two categories of agent activity.
#### Interactive agents
[Section titled “Interactive agents”](#interactive-agents)
* Initiated from the Warp app.
* The conversation is owned by you. It opens locally in Warp, and can be shared via a link when needed.
* Credit usage reflects inference.
#### Cloud agent runs
[Section titled “Cloud agent runs”](#cloud-agent-runs)
* Background executions initiated by triggers such as integrations and automations (for example: Slack, Linear, schedules, GitHub Actions, or API/CLI invocations).
* Each run produces a shared session that can be inspected after completion (including logs, messages, and outputs).
* Credit usage reflects inference + compute, shown as a single combined value in this view.
Caution
All usage rolls up into Warp’s standard [**credit**](/support-and-community/plans-and-billing/credits/) system.
In the **Personal** tab, you can view all of the interactive and cloud agent conversations that you own. In the **All** tab, you can see everything from the personal tab, as well as any cloud agent sessions that are shared with you by your teammates; right now, this only includes things triggered from integrations.
***
### Inspect or review an agent run
[Section titled “Inspect or review an agent run”](#inspect-or-review-an-agent-run)
Use the Agent Management Panel or Oz web app Runs page as the starting point when a teammate asks, “What did the agent do?”
1. In the agents list, use the filter menu to filter by source, day, creator, or status.
2. Select the matching row to open the shared session or local conversation.
3. Inspect the prompt, plan, commands, logs, outputs, and follow-up messages where available.
4. Share the session link with teammates if they need to review the same context.
5. For PR-producing workflows, include the session link alongside the PR link so reviewers can inspect both the code diff and the agent’s execution context.
For cloud agent runs, the session opens in [Cloud agent session sharing](/platform/viewing-cloud-agent-runs/). For local interactive agents, the conversation opens in Warp and can be shared with [Agent Session Sharing](/agents/local-agents/session-sharing/).
***
### The agents list
[Section titled “The agents list”](#the-agents-list)
Each row represents a single item in the agents list (either an interactive conversation or a cloud agent run). The list is scannable: you can understand “what happened” without opening anything.
#### Fields you’ll see
[Section titled “Fields you’ll see”](#fields-youll-see)
**Source**
Where the agent was launched from. Common sources include:
* **Interactive:** an [agent conversation](/agents/) started in the Warp app
* **CLI**: a local run triggered by the [Oz CLI](/agents/cli/oz-cli/)
* **API**: a run triggered by [Warp’s API](/factories/api-and-sdk/)
* **Slack / Linear**: runs triggered by [integrations](/platform/integrations/)
* **Scheduled**: runs triggered on a [cron schedule](/platform/triggers/scheduled-agents/)
**Status**
Warp uses a small set of statuses to help you quickly identify what needs attention:
| Status | Icon | Description |
| -------------------------------------------------------------------- | ---- | -------------------------------------------------------------------------------- |
| `Working` | N/A | in progress (may include queued / running states) |
| `Blocked` | 🟨 | *(interactive only)*the conversation is waiting on user input or a required step |
| `Canceled` | ⬜️ | (interactive only) the interactive conversation was canceled before completion |
| [`Failed / Errored`](/factories/api-and-sdk/troubleshooting/errors/) | 🔺 | something went wrong (applies to both interactive and cloud agent runs) |
| `Success` | ✅ | completed successfully (applies to both interactive and cloud agent runs) |
**Duration (for cloud agent tasks)**
* Shown for cloud agent runs to indicate how long the task executed.
* Note: Interactive conversations generally don’t map cleanly to a single “run duration,” so this is currently omitted.
***
### Inspecting an agent
[Section titled “Inspecting an agent”](#inspecting-an-agent)
**The primary interaction is simple:**
* Clicking a cloud agent row opens the [shared session](/platform/viewing-cloud-agent-runs/) for that run (prompt, plan, commands, logs, messages, and output where available).
* Clicking an interactive row opens the conversation locally in the Warp app.
This makes the agents list a navigation surface: find the thing you care about, click once, and you’re in the right context to inspect or continue work.
### Filtering
[Section titled “Filtering”](#filtering)
In both *Personal* and *All* views, you can open the filter menu and filter by:
* Source (interactive, API, CLI, Slack/Linear, scheduled)
* Day of creation
* Creator
* Status
This is the fastest way to isolate “everything that failed today,” “runs from Slack,” or “what a specific teammate triggered via integrations.”
***
### Orchestrated runs (parent and child)
[Section titled “Orchestrated runs (parent and child)”](#orchestrated-runs-parent-and-child)
When a parent agent spawns one or more child agents through [multi-agent orchestration](/platform/orchestration/), the parent and each child are tracked as separate runs. Where you see them depends on the surface:
* **Local children in the Warp app** - while you’re viewing the parent agent, an orchestration pill bar above the agent view header shows one pill per child with a live status badge. Click a child pill to switch the pane to that child’s conversation in place; click the parent pill - or the breadcrumb that replaces the pill bar while you’re viewing a child - to return. Local children don’t appear as separate rows in the Agent Management Panel list.
* **Cloud children in the Warp app** - appear in the Agent Management Panel list as their own rows alongside the parent and other runs. Filter by source, status, or creator to isolate them.
* **Cloud children in the [Oz web app](/platform/oz-web-app/)** - grouped under the parent’s row on the Runs page, and surfaced together inside the parent’s detail pane on a **Sub-agents** tab.
The parent’s own status reflects only its work - a parent can finish successfully while a child is still running or has failed. To verify that an orchestration completed, check each child individually from the pill bar (in the Warp app) or the **Sub-agents** tab (in the Oz web app).
## Related pages
[Section titled “Related pages”](#related-pages)
* [Cloud agents overview](/platform/) — What cloud agents are and when to use them.
* [Multi-agent orchestration](/platform/orchestration/) — Parent/child model, run state transitions, and common orchestration patterns.
* [Warp Factories](/factories/) — A standing team of cloud agents for triage-to-merge workflows, with its own dashboard and run list.
* [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/) — Open and inspect a remote cloud agent run.
* [Handoff between local and cloud agents](/platform/handoff/) — Move agent work between local and cloud, or continue a finished cloud run.
* [Oz web app](/platform/oz-web-app/) — Manage runs and schedules from any browser.
# MCP Servers for cloud agents
Canonical page: [/platform/mcp/](https://docs.warp.dev/platform/mcp/)
> Connect cloud agents to external tools, APIs, and internal services using MCP servers.
Cloud agents can call external tools through [Model Context Protocol (MCP) servers](/agents/capabilities/mcp/). This lets agents reach beyond the terminal to automatically interact with systems like GitHub, dbt, Sentry, or any custom internal service, whenever the workflow requires it.
## When to use MCP servers
[Section titled “When to use MCP servers”](#when-to-use-mcp-servers)
Add MCP servers to a cloud agent when it needs to:
* Read from or write to an external API (issue trackers, monitoring tools, cloud services)
* Call local processes that expose MCP endpoints
* Use internal developer tools that you’ve wrapped in an MCP interface
The agent calls MCP tools automatically based on what the task requires, without the need for explicit instruction.
## Warp-managed integration tools in factories
[Section titled “Warp-managed integration tools in factories”](#warp-managed-integration-tools-in-factories)
When Slack, Linear, or Jira is connected for a factory, Warp automatically makes tools from that integration available to the factory’s agents. These Warp-managed capabilities use the connected integration’s authorization and don’t require a separate MCP server installation.
Integration-provided tools are separate from the MCP servers you configure with `mcp_servers` or `mcpServers`. They may not appear alongside user-configured servers in the factory’s MCP list, even though the agent can use them during a run. For example, a scheduled factory run can use the Slack tools to post a report to a channel without Slack triggering the run.
See [posting a scheduled factory digest to Slack](/factories/integrations/slack/#post-a-scheduled-factory-digest-to-slack) for a complete automation and prompt. If you need a different external service, configure its MCP server using the options below.
## How MCP configuration works
[Section titled “How MCP configuration works”](#how-mcp-configuration-works)
You can supply MCP configuration in two ways:
* **At run time** — pass `--mcp` when calling `oz agent run` or `oz agent run-cloud`. See [MCP Servers](/agents/cli/oz-cli/mcp-servers/) in the CLI reference for the full syntax.
* **In an agent config file** — define `mcp_servers` directly in a YAML or JSON agent config file (passed with `-f / --file`). This is the recommended approach for repeatable workflows.
For factory work, declare factory-wide or per-agent MCP servers in the [factory definition](/factories/factory-as-code/#mcpservers). Use [Factory MCP](/factories/factory-mcp/) to connect an external coding agent to a factory.
## Configuration schema
[Section titled “Configuration schema”](#configuration-schema)
Each MCP server entry is keyed by a name you choose. A server config must have **exactly one** transport type:
| Transport | Field(s) | When to use |
| -------------------------------------------------------------- | ----------------- | -------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Warp-shared server, managed MCP install, or integration server | `warp_id` | Reference an MCP server already configured in Warp — including an OAuth-authorized [managed MCP installation](#oauth-authentication) — by its UUID, or a Warp-managed integration server by its id |
| Stdio (local process) | `command`, `args` | Launch a local executable as an MCP server |
| Streamable HTTP / SSE | `url` | Connect to a remote or locally hosted MCP endpoint |
### Supported fields
[Section titled “Supported fields”](#supported-fields)
* **`warp_id`** — UUID of a Warp-shared MCP server or a [managed MCP installation](#oauth-authentication) (find UUIDs with `oz mcp list`, from **Settings** > **Agents** > **MCP servers**, or from the [Oz web app](/platform/oz-web-app/#integrations) **Integrations** page), or the id of a Warp-managed integration server: `linear`, `slack`, or `jira`
* **`command`** — Executable to launch (stdio transport)
* **`args`** — Arguments passed to `command` (only valid with `command`)
* **`env`** — Environment variables passed to the process (only valid with `command`)
* **`url`** — HTTP or HTTPS endpoint URL (streamable HTTP or SSE transport)
* **`headers`** — HTTP headers sent with requests (only valid with `url`)
You can define any number of MCP servers in a single config.
### Example configuration
[Section titled “Example configuration”](#example-configuration)
```json
{
"github": {
"url": "https://mcp.example.com/github"
},
"dbt": {
"command": "uvx",
"args": ["dbt-mcp"],
"env": {
"DBT_HOST": "https://example.us1.dbt.com",
"DBT_SERVICE_TOKEN": "{{DBT_SERVICE_TOKEN}}"
}
}
}
```
Note
If the config passes through a system that pre-processes `{{...}}` before it reaches the Automation Platform (for example, Jira/Atlassian Automation), use JSON unicode escapes for the braces: `\u007b\u007bMY_SECRET\u007d\u007d` decodes to `{{MY_SECRET}}`, which the Automation Platform resolves normally.
## Using MCP servers in an agent config file
[Section titled “Using MCP servers in an agent config file”](#using-mcp-servers-in-an-agent-config-file)
For repeatable cloud agent workflows, declare your MCP servers inside the agent config file passed to `-f / --file`:
```json
{
"name": "my-production-agent",
"model_id": "claude-sonnet-4",
"system_prompt": "You are a helpful assistant focused on backend development.",
"environment_id": "SVhg783GBFQHk1OfdPfFU9",
"mcp_servers": {
"github": {
"url": "https://mcp.example.com/github"
},
"dbt": {
"command": "uvx",
"args": ["dbt-mcp"],
"env": {
"DBT_HOST": "https://example.us1.dbt.com",
"DBT_SERVICE_TOKEN": "{{DBT_SERVICE_TOKEN}}"
}
}
}
}
```
Pass this file when running a cloud agent:
```sh
oz agent run-cloud --environment <ENV_ID> -f my-agent-config.json --prompt "Check for regressions in the last deploy"
```
## Requirements and defaults
[Section titled “Requirements and defaults”](#requirements-and-defaults)
* MCP configuration must be valid JSON, or YAML when embedded in a broader agent config file.
* If `mcp_servers` is omitted, the agent runs with no user-configured MCP servers enabled. Factory runs can still receive [Warp-managed integration tools](#warp-managed-integration-tools-in-factories).
* Each server name must be unique and non-empty.
* The `warp_id` transport is validated against your Warp account. Referenced servers must be accessible to you.
* A `warp_id` that names a Warp-managed integration server (`linear`, `slack`, or `jira`) resolves against your team’s [integration](/platform/integrations/) connection, but only for a run executing inside a [factory](/factories/) (`jira` also resolves for a run triggered directly by a Jira event). Outside those cases, or when the integration isn’t connected, the server is skipped and the run continues without it.
## OAuth authentication
[Section titled “OAuth authentication”](#oauth-authentication)
Cloud agents support OAuth-protected MCP servers through a **managed MCP installation** — a cloud run can’t complete an interactive browser login, so authorization happens ahead of time instead.
To use an OAuth-gated server with a cloud agent:
1. In the [Oz web app](/platform/oz-web-app/#integrations), open **Integrations** and add the server as a managed MCP server.
2. Authorize it once. Warp completes the OAuth flow in a browser and stores the credentials.
3. Reference the installation’s UUID as `warp_id` in your `--mcp` flag or agent config, the same way you’d reference any Warp-shared server.
Cloud agent runs then use the stored credentials automatically, with no browser interaction. This is the supported path for hosted OAuth servers such as Figma’s remote MCP server.
## Limitations
[Section titled “Limitations”](#limitations)
Caution
A direct `url` MCP server that requires OAuth and has no `Authorization` header can’t be used by cloud agents. Set it up as a [managed MCP installation](#oauth-authentication) instead, then reference it by `warp_id`.
Token- or header-based authentication on a `url` server, `env`-based secrets on a `command` server, and `warp_id` references to a Warp-shared or managed server all work without additional setup.
## Learn more
[Section titled “Learn more”](#learn-more)
* [Connect developer tools to agents with MCP workflows](/guides/external-tools/using-mcp-servers-with-warp/) — choose between local, cloud, and shared MCP setup paths
* [MCP Servers (CLI reference)](/agents/cli/oz-cli/mcp-servers/) — how to pass MCP configuration using the `--mcp` flag
* [Model Context Protocol (MCP)](/agents/capabilities/mcp/) — configuring MCP servers in Warp for local agents
* [Environments](/platform/environments/) — set up the runtime context (repo, image, startup commands) for cloud agent tasks
* [Secrets](/platform/secrets/) — store and inject credentials into agent runs safely
# Multi-agent orchestration
Canonical page: [/platform/orchestration/](https://docs.warp.dev/platform/orchestration/)
> Coordinate parent and child agents across local and cloud runs to build supervisor/worker, fan-out, critic, DAG, and swarm workflows in Warp.
Multi-agent orchestration lets one agent spawn and coordinate other agents to parallelize work, delegate specialized tasks, or verify another agent’s output. The parent/child model works from the Warp app, the [Oz CLI](/agents/cli/oz-cli/), and the [Warp Platform API](/factories/api-and-sdk/), and supports local, cloud, and mixed execution.
Watch this walkthrough to see how a cloud agent can coordinate a team of agents in the cloud.

To start an orchestrated run, see [Running orchestrated agents](/platform/orchestration/multi-agent-runs/).
To orchestrate work inside a [Warp factory](/factories/), dispatch through [factory endpoints](/factories/factory-api/) instead of calling `POST /agent/runs` with the foreman’s `agent_identity_uid` directly. The server resolves the foreman for you, and everything on this page still applies to the run it starts.
## The parent/child model
[Section titled “The parent/child model”](#the-parentchild-model)
An orchestrated workflow always has one **parent agent** and one or more **child agents**.
* **Parent agent** - the agent that decides what work needs to be done, spawns child agents, and (optionally) merges their results. Any agent can become a parent the first time it spawns a child.
* **Child agent** - an agent spawned by a parent with its own prompt, environment, and (optionally) a different model or agent runtime. A child runs its own work and reports back; it does not spawn its own children.
Orchestrations today are exactly one level deep: a parent and its direct children. The Warp app, the [Oz web app](/platform/oz-web-app/), and the [Warp Platform API](/factories/api-and-sdk/) render that single level. The parent and each child each have an independent **run** with its own lifecycle, transcript, conversation, and credit usage.
### Where parent and child agents can run
[Section titled “Where parent and child agents can run”](#where-parent-and-child-agents-can-run)
The parent and child don’t have to run in the same place. Orchestration supports four combinations:
* **Local → local** - a [Warp Agent](/agents/) conversation in the Warp app spawns child Warp Agent conversations on the same machine. Useful for trying orchestration patterns without spinning up cloud infrastructure.
* **Local → cloud** - a local parent spawns one or more cloud children that run in [environments](/platform/environments/) on Warp-hosted or self-hosted infrastructure. The parent keeps working while children execute in parallel.
* **Cloud → cloud** - a cloud parent spawns cloud children that each run in their own environment. This is the canonical pattern for review swarms, large fan-outs, and any orchestration triggered from Slack, Linear, a schedule, or the API.
* **Cloud → cloud-local** - a cloud parent spawns children that run inside the parent’s own cloud environment, rather than each child getting its own environment. Useful when children need to share state with the parent (a filesystem, a long-running process, a shell session) or when spinning up an environment per child would be wasteful.
Children can also run with a different agent runtime than the parent. A parent running with the default Warp Agent can spawn children that run with [Claude Code](/agents/cli-agents/claude-code/) or [Codex](/agents/cli-agents/codex/), and vice versa.
### How a child agent is configured
[Section titled “How a child agent is configured”](#how-a-child-agent-is-configured)
An ad hoc child’s prompt comes from the parent at spawn time. The model, harness, and execution settings apply to every child in the batch.
Use a [skill](/agents/capabilities/skills/) for reusable instructions. A local child discovers the project and home-directory skills in scope from its working directory. For cloud children, the parent attaches skills from a repository in the [environment](/platform/environments/).
For named agents with standing configuration, use [Warp Factories](/factories/). A factory’s foreman can dispatch its [factory agents](/factories/factory-agents/#choose-a-configured-factory-agent).
## Run state transitions
[Section titled “Run state transitions”](#run-state-transitions)
Each run progresses through a small set of states. The parent observes these transitions to decide what to do next - keep waiting, send a follow-up, spawn a replacement, or finish.
The main user-visible states a child run can reach are:
* **`INPROGRESS`** - the run is actively executing (or has restarted after being blocked).
* **`SUCCEEDED`** - the run completed successfully.
* **`FAILED`** - the run hit a terminal failure.
* **`BLOCKED`** - the run is waiting on a user action (for example, command approval or a permission request).
* **`ERROR`** - the run encountered an error during startup or execution.
* **`CANCELLED`** - the run was cancelled before reaching a terminal state.
Track run state transitions in these places:
* **The parent’s transcript** - the parent agent receives child state transitions as it runs and reflects them in its own conversation.
* **The orchestration pill bar** - in the Warp app, while you’re viewing the parent agent, a horizontal pill bar above the agent view header shows the parent on the left and one pill per child. Each pill displays the child’s name and a status badge that updates live. Click a pill to switch the pane to that child’s conversation in place; click the parent pill to switch back.
* **The Oz web app** - cloud children appear under the parent on the [Runs page](https://oz.warp.dev/runs) and in the parent’s **Sub-agents** tab, with their status updating live.
* **The Warp Platform API** - `GET /agent/runs/{runId}` returns the latest state of any run, and `GET /agent/runs?ancestor_run_id=PARENT_RUN_ID` lists every descendant in one call.
## Messaging between agents
[Section titled “Messaging between agents”](#messaging-between-agents)
Orchestration is built on a durable, server-backed message bus. Every agent in an orchestration - parent and children - has its own inbox addressed by its agent ID, and the parent and children send each other short, structured messages to coordinate, hand off work, and stay in sync as they run.
This is how parallel agents stay consistent without sharing mutable state. Each run owns its own conversation, working directory or environment, and credit usage; agents don’t read each other’s transcripts or live working trees. Instead, they exchange explicit messages whenever they need to communicate a decision, a result, or a question. Messages and run state transitions share a global sequence number so the parent never observes a child’s `SUCCEEDED` state before the message that produced the result.
The same messaging infrastructure works across every combination of agent runtimes and execution locations:
* **Harness-agnostic** - the mailbox is the same whether the recipient runs the default Warp Agent, [Claude Code](/agents/cli-agents/claude-code/), [Codex](/agents/cli-agents/codex/), or another agent runtime. A parent running with one harness can message a child running with another, in either direction.
* **Cross-location** - the agent ID is the only address that matters. A local parent can message a cloud child, a cloud parent can message a local-to-cloud child running inside its own environment, and cloud parents can fan out messages to cloud children running in different environments.
* **Resumable** - a child whose current run has reached a terminal state (`SUCCEEDED`, `FAILED`, `CANCELLED`, or `ERROR`) is not gone. It is still addressable by its agent ID and will wake up to handle follow-up instructions when the parent sends a new message.
Alongside messages, every run emits **lifecycle events** on the same infrastructure when its state changes - the six states listed in [Run state transitions](#run-state-transitions). The parent observes these events to decide what to do next (keep waiting, send a follow-up, spawn a replacement, finish) without polling any child.
Use messages for coordination signals - handoffs, decisions, blocked-on-input requests, status updates, and final results - rather than for piping full transcripts around. The parent’s prompt to a child and the child’s final output carry the substance of the work; messages are how the agents talk *about* the work as it happens.
## Common patterns
[Section titled “Common patterns”](#common-patterns)
The following patterns show common ways to structure parent and child agents, depending on whether you need parallel execution, review, dependency ordering, or loose coordination.
### Supervisor / worker
[Section titled “Supervisor / worker”](#supervisor--worker)
A parent supervisor agent breaks the task into a queue of work items, spawns worker children to claim and complete each item, and writes a summary when the queue is empty. Use this when the task is naturally divisible and you want a single agent to own coordination.
### Fan-out / fan-in
[Section titled “Fan-out / fan-in”](#fan-out--fan-in)
The parent spawns N children in parallel, each with a sharded prompt (one module, one file set, one test target, one model), then waits for all of them to complete and merges their results. Use this for large refactors, repo-wide migrations, or running the same task across multiple targets.
### Critic / verifier
[Section titled “Critic / verifier”](#critic--verifier)
The parent (the “writer”) proposes a solution, then spawns a critic child to review it. The critic returns notes; the writer revises; the cycle repeats until the critic approves or a budget is exhausted. Useful when correctness matters more than throughput.
### Review swarm (cloud → cloud)
[Section titled “Review swarm (cloud → cloud)”](#review-swarm-cloud--cloud)
A [scheduled](/platform/triggers/scheduled-agents/) or webhook-triggered parent spawns one cloud child per open pull request to run reviews in parallel. Each child posts its findings as a comment and exits. The parent fans in the results and posts a summary back to the triggering system.
### DAG
[Section titled “DAG”](#dag)
The parent encodes a directed acyclic graph of subtasks where some nodes depend on the outputs of others. It spawns ready nodes, waits on their state transitions, and spawns dependents as upstream nodes complete. Use this when the workflow has explicit ordering constraints (build → test → deploy, for example).
### Swarm
[Section titled “Swarm”](#swarm)
A flat group of peer agents discover each other through messaging and coordinate without a strict hierarchy. The parent acts more like a coordinator than a supervisor. Use sparingly - swarms are harder to debug than hierarchical patterns.
## Approval mode
[Section titled “Approval mode”](#approval-mode)
Two slash commands surface orchestration in the Warp app, and both require explicit user approval before any children launch:
* **`/orchestrate`** asks the agent to apply orchestration to the task. The agent proposes a breakdown - number of children, prompts, environments, parallelism - and waits for approval. The API equivalent is setting `mode: orchestrate` on `POST /agent/runs`.
* **`/plan`** asks the agent to research and produce a plan for a complex task. The agent always considers orchestration while planning, and proposes it as part of the plan when the work would benefit. When orchestration is part of the plan, the plan card surfaces an inline **orchestration config** block above the plan with model, harness, environment, host, and parallelism pickers; you can adjust the config and then approve the plan to start spawning children. The API equivalent is `mode: plan`.
In both cases, approval is required before the parent launches children. Approving an orchestration also approves the run-wide config (model, harness, environment, host) that every child inherits unless the parent overrides it per child.
## Observability
[Section titled “Observability”](#observability)
Because every parent and child is tracked as its own conversation or run, the existing observability surfaces work without changes:
* **[Managing cloud agents](/platform/managing-cloud-agents/)** - in the Warp app, the orchestration pill bar above the agent view header lets you switch between the parent and each child while you’re viewing the parent. Cloud children also appear as their own rows in the Agent Management Panel list.
* **[Oz web app](/platform/oz-web-app/)** - the Runs page groups cloud children under the parent’s row, and the parent’s detail pane adds a **Sub-agents** tab.
* **[Warp Platform API](/factories/api-and-sdk/)** - list every descendant of a parent in one call and fetch any run with its conversation, transcript, and artifacts. See [Running orchestrated agents](/platform/orchestration/multi-agent-runs/#retrieving-conversations-and-artifacts).
* **[Agent notifications](/agents/capabilities/agent-notifications/)** - in-app notifications fire on the parent agent’s conversation only. Use the pill bar or the **Sub-agents** tab to drill into a specific child.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Running orchestrated agents](/platform/orchestration/multi-agent-runs/) - how to start an orchestrated run from the CLI, slash command, web app, or API.
* [How to run multiple AI coding agents](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/) - practical guidance for splitting tasks, assigning worktrees, validating child output, and handing work off for review.
* [Warp Factories](/factories/) - standing multi-stage workflows where a foreman dispatches named agents with separate configuration.
* [Warp Platform API](/factories/api-and-sdk/) - REST endpoints for runs, conversations, and artifacts.
* [Cloud agents overview](/platform/) - what a cloud agent run is and how it fits into the Automation Platform.
* [Deployment patterns](/factories/deployment-patterns/) - higher-level deployment models that orchestration composes with.
# Running orchestrated agents
Canonical page: [/platform/orchestration/multi-agent-runs/](https://docs.warp.dev/platform/orchestration/multi-agent-runs/)
> Start multi-agent orchestrations from the Warp app, the Oz CLI, the Oz web app, or the Warp Platform API, and inspect parent and child conversations and artifacts.
An orchestrated run starts with a parent agent that spawns one or more child agents. You can start a parent from the Warp app, the Oz CLI, the Oz web app, or the Warp Platform API. Use orchestrated runs to review a plan before fan-out, execute children locally or in the cloud, and inspect parent and child conversations as they work.
Watch this walkthrough to see how to start and inspect an orchestrated agent run from Warp.

## Before you start
[Section titled “Before you start”](#before-you-start)
Pick where the parent will run. Every orchestration starts with a single parent that spawns children:
* **Parent in the Warp app** - use the `/orchestrate` or `/plan` slash command. This is the fastest way to try orchestration.
* **Parent in the cloud** - trigger the parent through the Oz CLI (`oz agent run-cloud`), the [Warp Platform API](/factories/api-and-sdk/), any [integration](/platform/integrations/) such as [Slack](/platform/integrations/slack/) or [Linear](/platform/integrations/linear/), or a [schedule](/platform/triggers/scheduled-agents/). The parent runs in an environment and spawns children from there.
Cloud parents that spawn cloud children need access to one or more [environments](/platform/environments/) the children can run in. To keep child execution on your own infrastructure, route those children to a [self-hosted worker](/factories/self-hosting/).
## Starting an orchestrated run from Warp
[Section titled “Starting an orchestrated run from Warp”](#starting-an-orchestrated-run-from-warp)
In the Warp app, open the agent input and type `/orchestrate` followed by your task. The agent enters `orchestrate` mode and proposes a breakdown before spawning any children.
```text
/orchestrate Migrate every test file in this repo from Jest to Vitest. Spawn one child per top-level directory under packages/.
```
The agent responds with a proposal that describes:
* How many children it intends to spawn.
* Each child’s prompt and environment.
* What it expects each child to return.
Approve the proposal to start spawning children. The parent’s transcript renders each child as it spawns, and an **orchestration pill bar** appears above the agent view header showing the parent on the left and one pill per child. Each pill displays the child’s name and a live status badge. Click a child pill to switch the pane to that child’s conversation in place; click the parent pill - or the breadcrumb that replaces the pill bar while you’re viewing a child - to return to the parent.
### Letting the agent propose orchestration during /plan
[Section titled “Letting the agent propose orchestration during /plan”](#letting-the-agent-propose-orchestration-during-plan)
You can also reach the same approval flow from `/plan`. When you ask the agent to plan a complex task, it considers orchestration as part of planning and proposes it whenever the work would benefit. When that happens, the plan card includes an inline **orchestration config** block above the plan content with model, harness, environment, host, parallelism, and auth pickers. Edit the config as needed, review the plan’s orchestration section (number of children, what each child owns), and approve the plan to start spawning children with the configured run-wide settings.
### Spawning cloud children from a local parent
[Section titled “Spawning cloud children from a local parent”](#spawning-cloud-children-from-a-local-parent)
A local parent - a Warp Agent conversation in the Warp app - can spawn cloud children by specifying an environment for each child. The parent asks for the environment if it isn’t already clear from context. You can select any environment from your account or team.
Cloud children inherit the parent’s authentication; the same credit and credentials rules from the [Cloud agents overview](/platform/) apply.
## Starting an orchestrated run from the CLI
[Section titled “Starting an orchestrated run from the CLI”](#starting-an-orchestrated-run-from-the-cli)
Use `oz agent run-cloud` to start a parent and let the agent itself spawn children as it works.
```bash
oz agent run-cloud \
--prompt "Review the open pull requests in this repo and post a summary on each. Spawn one child agent per PR." \
--environment YOUR_ENVIRONMENT_ID
```
This is the recommended way to fan work out from the CLI: the parent decides how many children to spawn, links them to itself automatically, and you get a single parent run ID back to follow.
Note
If you need to fan out from a script and want each child linked to a specific parent, use the [API](#starting-an-orchestrated-run-from-the-api). `oz agent run-cloud` doesn’t currently accept a parent run ID flag, so script-launched runs from the CLI are independent runs.
## Starting an orchestrated run from the web app
[Section titled “Starting an orchestrated run from the web app”](#starting-an-orchestrated-run-from-the-web-app)
In the Oz web app‘s [**Runs** page](https://oz.warp.dev/runs):
1. Click **New run** in the header.
2. Select an environment and, optionally, a skill that performs orchestration.
3. Enter the parent’s prompt. Describe both the high-level task and the orchestration shape you want (number of children, parallelism, success criteria).
4. Click **Run**.
The parent run starts and children appear in the Runs list as the parent spawns them, nested under the parent row.
## Starting an orchestrated run from the API
[Section titled “Starting an orchestrated run from the API”](#starting-an-orchestrated-run-from-the-api)
Spawn the parent with `POST /agent/runs`. Children can either be spawned by the parent agent at runtime, or you can spawn each child explicitly from your code and link it to the parent with `parent_run_id`. Once they’re running, coordination between the parent and its children flows through Warp’s durable agent-to-agent messaging - see [Messaging between agents](/platform/orchestration/#messaging-between-agents) for the model.
This section spawns a standalone parent run. If the parent you want to start is a [Warp factory](/factories/)’s foreman, use [factory endpoints](/factories/factory-api/) to dispatch by factory UID instead of looking up the foreman’s `agent_identity_uid` and calling `POST /agent/runs` directly.
### Agent-driven orchestration
[Section titled “Agent-driven orchestration”](#agent-driven-orchestration)
Start a single parent run with `mode: orchestrate`:
```http
POST /api/v1/agent/runs
Authorization: Bearer YOUR_API_KEY
Content-Type: application/json
{
"prompt": "Coordinate a code review across every open PR in the repo. Spawn one child per PR.",
"mode": "orchestrate",
"config": {
"environment_id": "YOUR_ENVIRONMENT_ID"
},
"title": "PR review swarm"
}
```
The parent decides how many children to spawn. Children inherit the parent’s authentication and bill to the same account.
### Caller-driven orchestration
[Section titled “Caller-driven orchestration”](#caller-driven-orchestration)
Spawn each child explicitly with `parent_run_id` set to the parent’s `run_id`:
```http
POST /api/v1/agent/runs
Authorization: Bearer YOUR_API_KEY
Content-Type: application/json
{
"prompt": "Review PR #123",
"config": {
"environment_id": "YOUR_ENVIRONMENT_ID"
},
"parent_run_id": "YOUR_PARENT_RUN_ID",
"title": "Review PR #123"
}
```
Setting `parent_run_id` is what links the child to its parent across the Agent Management Panel in the Warp app, the Oz web app Runs page, and the descendants query (`?ancestor_run_id=`).
A scripted fan-out, including parent linking, looks like this:
```bash
PARENT_RUN_ID=$(curl -sS -X POST https://app.warp.dev/api/v1/agent/runs \
-H "Authorization: Bearer $WARP_API_KEY" \
-H "Content-Type: application/json" \
-d '{
"prompt": "Coordinate the migration",
"mode": "orchestrate",
"config": {"environment_id": "YOUR_ENVIRONMENT_ID"},
"title": "Jest to Vitest migration"
}' | jq -r .run_id)
for shard in pkg-a pkg-b pkg-c; do
curl -sS -X POST https://app.warp.dev/api/v1/agent/runs \
-H "Authorization: Bearer $WARP_API_KEY" \
-H "Content-Type: application/json" \
-d "{
\"prompt\": \"Migrate $shard from Jest to Vitest\",
\"config\": {\"environment_id\": \"YOUR_ENVIRONMENT_ID\"},
\"parent_run_id\": \"$PARENT_RUN_ID\",
\"title\": \"Migrate $shard\"
}"
done
```
## Retrieving conversations and artifacts
[Section titled “Retrieving conversations and artifacts”](#retrieving-conversations-and-artifacts)
Every parent and child started through the Warp Platform API is tracked as a cloud agent run. Run responses include the run’s `state`, `parent_run_id` (set on children only), `conversation_id`, `session_link`, and an `artifacts` array of any pull requests, plans, screenshots, or files the run produced. Use the same endpoints you’d use for any other run:
* **List every descendant of a parent** - `GET /api/v1/agent/runs?ancestor_run_id=YOUR_PARENT_RUN_ID`. From the CLI: `oz run list --ancestor-run YOUR_PARENT_RUN_ID`.
* **Get one run’s details and artifacts** - `GET /api/v1/agent/runs/YOUR_RUN_ID`.
* **Read the normalized conversation** - `GET /api/v1/agent/runs/YOUR_RUN_ID/conversation` returns a structured sequence of messages, tool calls, and events.
* **Download the raw transcript** - `GET /api/v1/agent/runs/YOUR_RUN_ID/transcript` returns a redirect to a time-limited download URL.
All four endpoints work the same for the parent and any child.
## Cancelling a fleet
[Section titled “Cancelling a fleet”](#cancelling-a-fleet)
Cancel any run with `POST /agent/runs/{runId}/cancel`:
```http
POST /api/v1/agent/runs/YOUR_RUN_ID/cancel
Authorization: Bearer YOUR_API_KEY
```
Cancelling the parent does **not** automatically cancel its children. This is intentional: in many orchestrations, you want children to finish even after the parent ends. To cancel everything, list the descendants and cancel each one, then cancel the parent:
```bash
# List every descendant of the parent, then cancel each.
oz --output-format json run list --ancestor-run "$PARENT_RUN_ID" \
| jq -r '.runs[].run_id' \
| xargs -I{} curl -sS -X POST \
https://app.warp.dev/api/v1/agent/runs/{}/cancel \
-H "Authorization: Bearer $WARP_API_KEY"
# Finally cancel the parent.
curl -sS -X POST \
"https://app.warp.dev/api/v1/agent/runs/$PARENT_RUN_ID/cancel" \
-H "Authorization: Bearer $WARP_API_KEY"
```
Caution
Self-hosted, local, and GitHub Action runs cannot be cancelled through this endpoint and return a `422`. Stop them through your own infrastructure.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Multi-agent orchestration](/platform/orchestration/) - parent/child model, run state transitions, and common patterns.
* [How to run multiple AI coding agents](/guides/agent-workflows/how-to-run-multiple-ai-coding-agents/) - practical task decomposition, worktree ownership, validation, and review handoff guidance.
* [Oz CLI](/agents/cli/oz-cli/) - command reference for `oz agent run-cloud` and `oz run`.
* [Warp Platform API](/factories/api-and-sdk/) - full HTTP reference and typed SDKs.
* [Managing cloud agents](/platform/managing-cloud-agents/) - how parent and child runs appear in the Agent Management Panel in the Warp app and the Runs page in the Oz web app.
* [Scheduled agents](/platform/triggers/scheduled-agents/) - start a recurring cloud parent that fans out children on a cron cadence.
* [Self-hosting](/factories/self-hosting/) - keep parent or child execution on your infrastructure while Warp tracks the runs.
* [Handoff between local and cloud agents](/platform/handoff/) - promote a local parent to the cloud, or continue a finished cloud parent with a follow-up.
* [Environments](/platform/environments/) - configure the runtime context cloud children execute in.
# Automation Platform overview
Canonical page: [/platform/overview/](https://docs.warp.dev/platform/overview/)
> How cloud agent runs work on the Automation Platform: triggers start tasks, tasks run in environments on a host, and every run leaves a record.
[Cloud agents](/platform/) run on the Automation Platform. You define a task and its trigger. The Automation Platform runs the agent and records the results. For example, an agent can triage each new issue as it’s filed, or start fixing a build the moment CI fails.
If you’re new to cloud agents, the [Cloud agents quickstart](/platform/quickstart/) gets you to your first run in about ten minutes.

## How a run works
[Section titled “How a run works”](#how-a-run-works)
Every run follows the same path, whatever starts it:
1. A **trigger** fires: a schedule, an integration event like a Slack mention or a CI failure, an API call, or a manual start.
2. Warp creates a **task**, the tracked record of the run. The trigger’s context travels with it: the Slack thread, the PR metadata, the CI logs.
3. The agent executes on a **host**, optionally inside an [environment](/platform/environments/) that defines its image, repos, and setup.
4. The task produces **outputs**: a pull request, a Slack reply, a report, or just a transcript and summary.

## Integrations and triggers
[Section titled “Integrations and triggers”](#integrations-and-triggers)
Every run starts with a trigger. [Integrations](/platform/integrations/) turn events in other tools into runs: mention @warp in [Slack](/platform/integrations/slack/) and the agent gets the message and its thread, or run agents inside your [GitHub Actions](/platform/integrations/github-actions/) workflows with your CI context. [Scheduled agents](/platform/triggers/scheduled-agents/) start runs on a cron schedule. For event sources Warp doesn’t cover, receive the event in your own system and start the run through the [API](/factories/api-and-sdk/); it becomes a normal, fully tracked task.
Set up a first-party integration with `oz integration create` on the Oz CLI; the [integration setup guide](/agents/cli/oz-cli/integration-setup/) covers it end to end.
## Tasks and tracking
[Section titled “Tasks and tracking”](#tasks-and-tracking)
Warp tracks every run as a task: its status, transcript, and outputs stay available after the run finishes. Watch or steer a live run with [session sharing](/agents/local-agents/session-sharing/), browse history in the [management UI](/platform/managing-cloud-agents/), or query it from the [Oz CLI](/agents/cli/oz-cli/) and the [API](/factories/api-and-sdk/). Access control decides who can run, view, or intervene in tasks.
To fan work out across parent and child agents, see [multi-agent orchestration](/platform/orchestration/).
## Environments
[Section titled “Environments”](#environments)
An [environment](/platform/environments/) defines what a run needs: a Docker image with your toolchain, the repositories to clone, and setup commands. Automated runs (integrations, schedules, API calls) use an environment so every run starts from the same setup; interactive local runs use your machine as-is and don’t need one. Define one environment per codebase and reuse it across triggers.
## Hosts
[Section titled “Hosts”](#hosts)
A host is where the agent executes. By default runs execute on [Warp-hosted infrastructure](/factories/warp-hosting/), with nothing to set up. On Enterprise plans, [self-hosted runners](/factories/self-hosting/) keep code and execution inside your own network while Warp still tracks the runs.

## The CLI
[Section titled “The CLI”](#the-cli)
The [Oz CLI](/agents/cli/oz-cli/) starts and manages runs where there’s no UI: CI jobs, scripts, and remote servers. Start a run with `oz agent run`, and it reports progress to Warp like any other task, so work that starts on a CI runner shows up alongside everything else your team runs. For interactive sessions, use [agents in the Warp app](/agents/).
## API and SDKs
[Section titled “API and SDKs”](#api-and-sdks)
The [Warp Platform API](/factories/api-and-sdk/) creates and inspects tasks over HTTP: submit a prompt with optional configuration, poll status, and fetch results with full provenance. Teams use it to start agents from incident tooling and internal systems, build dashboards over run history, and coordinate large batches of runs. Official [Python](https://github.com/warpdotdev/oz-sdk-python) and [TypeScript](https://github.com/warpdotdev/oz-sdk-typescript) SDKs add typed requests and responses, built-in retries, and consistent errors. Start with an SDK unless you need full control over your HTTP client.
## Secrets
[Section titled “Secrets”](#secrets)
Agents often need credentials for APIs, cloud providers, databases, and MCP servers. Store them as [secrets](/platform/secrets/), and Warp injects them at runtime without exposing the values in logs or the UI. Secrets can be scoped to the whole team or to one person.
## Shared configuration
[Section titled “Shared configuration”](#shared-configuration)
Runs pick up your team’s shared setup no matter what triggered them: [MCP servers](/platform/mcp/), [rules](/agents/capabilities/rules/), [saved prompts](/knowledge-and-collaboration/warp-drive/prompts/), and [environment variables](/knowledge-and-collaboration/warp-drive/environment-variables/). Configure these once and every trigger uses them.
## Warp Factories
[Section titled “Warp Factories”](#warp-factories)
[Warp Factories](/factories/) builds on these pieces to run persistent, multi-agent development workflows: specialized cloud agents move each work item through triage, specification, implementation, and review. It’s in Early Access. [Request access](https://www.warp.dev/factories/request-access) to use it with your team.
## Where to go next
[Section titled “Where to go next”](#where-to-go-next)
* [Architecture](/platform/architecture/) - reference diagrams of the stack, the run lifecycle, and data boundaries.
* [Cloud agents](/platform/) - what cloud agents are, how they get triggered, and how to run them with or without the Warp app.
* [Cloud agents quickstart](/platform/quickstart/) - run your first cloud agent in about ten minutes.
* [Environments](/platform/environments/) - define the toolchain and repos a run executes against.
* [Warp Platform API](/factories/api-and-sdk/) - drive the platform programmatically.
# Oz web app for cloud agents
Canonical page: [/platform/oz-web-app/](https://docs.warp.dev/platform/oz-web-app/)
> Use the Oz web app to manage cloud agents, view runs, create schedules, and configure environments and integrations from any browser or mobile device.
The [Oz web app](https://oz.warp.dev) provides a visual interface for managing cloud agents. You can start runs, browse agents and skills, create schedules, configure environments, and set up integrations—all without installing Warp or using the CLI.
Note
The Oz web app works on mobile devices, so you can monitor and manage your cloud agents from anywhere.
Watch this short demo to create an environment and run an agent using the Oz web app:

## Quick reference
[Section titled “Quick reference”](#quick-reference)
| Page | Path | What you can do |
| ---------------- | --------------- | ----------------------------------------------------------------------------------------------------- |
| **Runs** | `/runs` | View all runs, filter by status/source/creator, start new runs, inspect transcripts |
| **Agents** | `/agents` | Browse saved agents, create agents, configure defaults, and start runs |
| **Skills** | `/skills` | Browse skills from your environments, view suggested skills, create skills for agents, and start runs |
| **Schedules** | `/schedules` | Create scheduled agents, pause/enable schedules, view run history |
| **Environments** | `/environments` | Create and manage environments with repos, Docker images, and setup commands |
| **Secrets** | `/secrets` | Create and manage Warp-managed secrets for cloud agent runs |
| **Integrations** | `/integrations` | Connect Slack, Linear, and GitHub to trigger agents from external tools |

The Oz web app Runs page.
## When to use the web app
[Section titled “When to use the web app”](#when-to-use-the-web-app)
The Oz web app is ideal when you want to:
* **Monitor agent activity** — View runs, check status, and inspect outputs from any device
* **Start quick runs** — Dispatch agents without opening a terminal
* **Manage agents and skills** — Create saved agents, browse skills from connected repositories, and start runs from either configuration
* **Manage schedules visually** — Create and edit scheduled agents with a guided interface
* **Configure environments** — Set up repos, Docker images, and setup commands through a form-based flow
* **Set up integrations** — Connect Slack and Linear with a guided setup flow, and configure how [GitHub](/platform/integrations/github/) mention-triggered runs execute
For scripting, automation, and CI/CD workflows, use the [Oz CLI](/agents/cli/oz-cli/) or [API](/factories/api-and-sdk/).
## Getting started
[Section titled “Getting started”](#getting-started)
When you first sign in to the Oz web app, you’ll see a guided onboarding flow that helps you get started based on your goals.
The onboarding asks “What brings you to the Automation Platform?” and offers three paths:
* **Create an agent automation** — Walks you through setting up a scheduled agent, integration-triggered agent, or other automation
* **Run Cloud Agents in Warp** — Opens the Warp app (or takes you to the download page) to run cloud agents interactively
* **Build an app that uses agents** — Links to the [Automation Platform](/platform/overview/) docs for using the CLI, SDK, or API
You can skip onboarding at any time to go directly to the Runs page.
## Runs
[Section titled “Runs”](#runs)
The **Runs** page (`/runs`) is your central view for monitoring cloud agent activity. It shows runs across your account and team, where applicable, including those triggered from the CLI, API, integrations, and schedules.
### Run details
[Section titled “Run details”](#run-details)
Each run displays the following information:
| Field | Description |
| --------------- | --------------------------------------------------------------------- |
| **Status** | Working, succeeded, failed, canceled, errored, or blocked |
| **Title** | The run’s title or prompt summary |
| **Environment** | Which environment the agent ran in |
| **Creator** | Who started the run |
| **Source** | Where the run was triggered from (CLI, API, Slack, Linear, scheduled) |
| **Artifacts** | Any outputs like PRs or files created |
| **Credits** | How many credits the run consumed |
Click any run to open the detail pane, where you can view the full transcript, artifacts, and metadata. For the full walkthrough of opening, steering, and forking a session, see [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/).
### Filtering and search
[Section titled “Filtering and search”](#filtering-and-search)
| Quick filter | Shows |
| ------------- | --------------------------- |
| **All** | All runs |
| **Mine** | Only runs you created |
| **Active** | Runs currently in progress |
| **Failed** | Runs that failed |
| **Recurring** | Runs triggered by schedules |
You can also search by title, prompt, or agent name, and add advanced filters for source, status, creator, and date range.
### Starting a new run
[Section titled “Starting a new run”](#starting-a-new-run)
To start a new run:
1. Click **New run** in the header to start a cloud agent.
2. Select an agent, if needed. Choose **Quick run** to run as yourself, or choose a saved agent from the **Agent** dropdown.
3. Select the environment where the agent should run.
4. Add a prompt with context and instructions for this specific run.
**Quick run** runs as your own user. A saved agent uses its saved defaults, and your prompt adds context for this particular execution.
### Inspecting orchestrated runs
[Section titled “Inspecting orchestrated runs”](#inspecting-orchestrated-runs)
The Oz web app renders [multi-agent orchestrations](/platform/orchestration/) as nested rows on the **Runs** page, so you can follow parent and child execution together.
Open a parent run from the Runs page. When the run has children, the detail pane adds a **Sub-agents** tab next to **Details**:
* Each child agent row shows the child’s current status and title. Click a row to open that child’s detail pane; closing it returns you to the parent’s **Sub-agents** tab.
* The parent’s own status badge at the top of the detail pane reflects the parent’s work, not its children. Open a child to inspect its state directly.
## Agents
[Section titled “Agents”](#agents)
The **Agents** page (`/agents`) is where you browse, create, and run saved agents. Agents are reusable cloud agent configurations that can include a prompt, skills, harness, model, environment, and secrets.
Skills are reusable instruction sets stored in repositories. You can attach existing skills to an agent through the **Skills** field; for more details, see [Skills as Agents](/platform/skills-as-agents/).
Saved agents use Warp’s team-scoped identity model, which lets a reusable agent own runs and carry default configuration for teammates. You manage saved agents from the Agents page. For plan limits, API endpoints, and API key binding behavior, see [Agents](/platform/agents/).

The Agents page in the Oz web app.
Open an agent to review its prompt, skills, harness, model, environment, and attached secrets. From the detail pane, you can inspect activity, create schedules, edit configuration, or start a run from the saved agent.
### Running an agent
[Section titled “Running an agent”](#running-an-agent)
Click any agent to view its details, then click **New run** to start a run from that saved configuration. You can also click **New run** from the header to start a run with optional agent selection.
### Creating a new agent
[Section titled “Creating a new agent”](#creating-a-new-agent)
To create a saved agent:
1. Click **New agent** to open the guided creation flow.
2. Define the instructions and defaults. Add a name, description, prompt, optional skills, harness, model, environment, and secrets.
3. Click **Create agent**. The saved agent appears on the Agents page and is available for runs.
For deeper guidance on reusable skills and team-scoped identities, see [Skills as Agents](/platform/skills-as-agents/) and [Agents](/platform/agents/).

Creating a new agent in the Oz web app.
## Skills
[Section titled “Skills”](#skills)
The **Skills** page (`/skills`) is where you browse and run skills. Skills are reusable instruction sets stored in repositories, and agents can include one or more skills as part of their default configuration.
Use the **From your Environments** filter to view skills from repositories connected to your environments, or switch to **Suggested** to view recommended skills. Open a skill to view its activity, schedules, and `SKILL.md` configuration.
### Running a skill
[Section titled “Running a skill”](#running-a-skill)
Click any skill to view its details, then click **New run** to start a run with that skill attached. You can also click **New run** from the page header to start a run with optional skill selection.
### Creating a skill for agents
[Section titled “Creating a skill for agents”](#creating-a-skill-for-agents)
To create a skill for agents:
1. Click **New agent** on the Skills page to open the skill creation flow.
2. Choose a repository from an existing environment with GitHub access.
3. Define the skill. Add a skill name, description, and instructions.
4. Click **Open Skill PR** to create a pull request that adds the skill to the selected repository.

Creating a skill in the Oz web app.
After the PR is merged, refresh skills so the new skill appears in the Oz web app.
## Schedules
[Section titled “Schedules”](#schedules)
The **Schedules** page (`/schedules`) lets you create and manage scheduled agents that run automatically on a cron schedule.
### Schedule details
[Section titled “Schedule details”](#schedule-details)
Each schedule displays:
| Field | Description |
| --------------- | ------------------------------------------------------------------------------ |
| **Name** | A descriptive name for the scheduled task |
| **Frequency** | Human-readable description of the cron schedule (e.g., “Every Monday at 10am”) |
| **Next run** | When the schedule will next execute |
| **Environment** | Which environment the scheduled agent runs in |
| **Agent** | Which saved agent the schedule uses (if any) |
| **Status** | Whether the schedule is active or paused |

The Schedules page in the Oz web app.
### Creating a schedule
[Section titled “Creating a schedule”](#creating-a-schedule)
To create a scheduled agent:
1. Click **New schedule** in the header.
2. Name the schedule. Use a descriptive name that explains what the scheduled agent does.
3. Set the frequency. Choose a preset or enter a cron schedule.
4. Select the environment where the scheduled agent should run.
5. Choose a saved agent, if needed.
6. Add the prompt that the agent should follow each time it runs.
7. Click **Create schedule**. The schedule appears on the Schedules page.
### Managing schedules
[Section titled “Managing schedules”](#managing-schedules)
Click any schedule to view its details and recent run history. From the detail pane, you can:
* **Edit** the schedule configuration
* **Pause** or **enable** the schedule
* **Delete** the schedule
* **View past runs** triggered by this schedule
Note
For CLI-based schedule management, see [Scheduled Agents](/platform/triggers/scheduled-agents/).
## Environments
[Section titled “Environments”](#environments)
The **Environments** page (`/environments`) shows all environments configured for your account. Environments define the execution context for cloud agents, including repos, Docker images, and setup commands.
### Environment details
[Section titled “Environment details”](#environment-details)
Each environment displays:
| Field | Description |
| ------------------ | -------------------------------------- |
| **Name** | The environment’s identifier |
| **Docker image** | The container image used for execution |
| **Repositories** | Which repos the agent can access |
| **Setup commands** | Commands run before the agent starts |

The Environments page in the Oz web app.
### Creating an environment
[Section titled “Creating an environment”](#creating-an-environment)
To create a new environment:
1. Click **New environment** in the header.
2. Name the environment. Use a descriptive name that explains the runtime context.
3. Select the repositories the agent should be able to access.
4. Choose a Docker image. Warp provides prebuilt dev images, or you can use your own.
5. Add any setup commands that should run when the environment starts, such as `npm install`.
6. Click **Create environment**. The environment appears on the Environments page.
Note
For advanced environment configuration, see [Environments](/platform/environments/) and the [CLI reference](/agents/cli/oz-cli/integration-setup/).
## Integrations
[Section titled “Integrations”](#integrations)
The **Integrations** page (`/integrations`) lets you configure first-party integrations with Slack, Linear, and GitHub.
### Available integrations
[Section titled “Available integrations”](#available-integrations)
| Integration | Description |
| ----------- | ----------------------------------------------------------------------------------------------- |
| **Slack** | Tag @warp in messages or threads to trigger agents directly from Slack conversations |
| **Linear** | Tag @warp on issues to trigger agents from your issue tracker |
| **GitHub** | Mention @warp-agent on issues, pull requests, and review comments to trigger agents from GitHub |

The Integrations page in the Oz web app.
### Setting up an integration
[Section titled “Setting up an integration”](#setting-up-an-integration)
Click an integration to start the guided setup flow. You’ll authorize Warp to connect with the external service, select an environment, and configure any integration-specific settings.
The GitHub row works differently. Instead of an authorization flow started here, it reflects the [Warp Factories](/factories/) GitHub App installation that a team admin enables in the Admin Panel. Once the installation is associated with your team, use the row to choose the environment, model, agent, prompt, and secrets that GitHub-triggered runs use.
Note
For detailed integration setup instructions, see [Slack](/platform/integrations/slack/), [Linear](/platform/integrations/linear/), and [GitHub](/platform/integrations/github/).
## Related resources
[Section titled “Related resources”](#related-resources)
* [Cloud Agents overview](/platform/) — Learn about cloud agents and when to use them
* [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/) — Open, inspect, and continue a cloud agent session from Warp or the browser
* [Multi-agent orchestration](/platform/orchestration/) — Parent/child model and common orchestration patterns
* [Skills as Agents](/platform/skills-as-agents/) — Run agents based on reusable skill definitions
* [Scheduled Agents](/platform/triggers/scheduled-agents/) — Run agents automatically on a cron schedule
* [Environments](/platform/environments/) — Configure runtime context for cloud agents
* [Managing Cloud Agents](/platform/managing-cloud-agents/) — Monitor agent activity and inspect runs
* [Oz CLI](/agents/cli/oz-cli/) — Command-line interface for running agents
* [Warp Platform API](/factories/api-and-sdk/) — Programmatic access to cloud agents
# Cloud agents quickstart
Canonical page: [/platform/quickstart/](https://docs.warp.dev/platform/quickstart/)
> Learn how to run your first cloud agent in ~10 minutes. Cloud agents run in remote environments, enabling automation, scheduling, and team collaboration.
**Cloud agents** run in a remote environment and can be triggered from events, schedules, integrations, or manually. This enables scaling agents off your laptop, automating development tasks, and building apps on top of agents. The Automation Platform handles the orchestration, execution, and observability.
Cloud agents can run interactively (where you steer them in real-time) or autonomously (as background tasks). Each run creates a persistent session that your team can inspect, share, and query through the Warp app, the CLI, web app, or API.
This guide walks you through running your first cloud agent with an environment in about 10 minutes. You’ll create an environment, if needed, and launch a cloud agent to help with a development task.
**Common use cases for cloud agents:**
* Launch [parallel cloud coding agents](/platform/orchestration/) to multithread complex development tasks
* Automate repetitive development tasks (e.g., feature-flag cleanup, documentation updates, fixing server crashes)
* Build apps on top of agents, like bug triage and incident response systems
***
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
Before you begin, make sure you have:
* **Warp desktop app** - Download from the [Warp website](https://www.warp.dev)
* **Warp account** - Create an account from the [Oz web app](https://oz.warp.dev)
Note
New to Warp? You’ll get credits to try cloud agents. You need at least 20 credits available to run cloud agents and integrations.
***
## Running your first cloud agent
[Section titled “Running your first cloud agent”](#running-your-first-cloud-agent)
*\~10 minutes • Recommended for all users*
### 1. Open Warp
[Section titled “1. Open Warp”](#1-open-warp)
If you don’t have Warp yet, download it from the [Warp website](https://www.warp.dev) and sign in to your account. When you open the Warp desktop app, you’re automatically authenticated to Warp’s services.
### 2. Run the `/cloud-agent` command
[Section titled “2. Run the /cloud-agent command”](#2-run-the-cloud-agent-command)
In Warp’s terminal input, type:
```bash
/cloud-agent
```
This launches a new cloud agent for you.
**How this works:** The `/cloud-agent` command is your entry point to cloud agents. It checks if you have an environment set up, and if not, it guides you through creating one.
### 3. Create your environment
[Section titled “3. Create your environment”](#3-create-your-environment)
Note
**Already have an environment?** The `/cloud-agent` command will use your existing one. To create additional environments for different projects, use `/create-environment`.
If you don’t have an environment yet, the `/cloud-agent` setup flow will guide you through creating one. You will need:
* **Name**: A label to identify this environment (required)
* **Repo(s)**: Type repo in `owner/repo` format or select from the dropdown. Click **Auth with GitHub** if you need to connect your repos.
* **Docker image**: Your runtime environment (e.g., `python:3.11`, `node:20`). Not sure? Click **Suggest image** and Warp will recommend one based on your repos.
* **Setup command(s)**: Commands to prepare your workspace, like `pip install -r requirements.txt` or `npm ci`. Add each command separately by pressing Enter.
* **Description**: Optional notes about what this environment is for.
**How this works:** Environments are composed of Docker containers + Git repos + startup commands. They give your cloud agent a consistent workspace with your code and tools. Warp detects your project automatically and suggests the right setup. Environments can be shared with your team so everyone uses the same configuration.
### 4. Describe what you want the agent to do
[Section titled “4. Describe what you want the agent to do”](#4-describe-what-you-want-the-agent-to-do)
Enter your prompt (e.g., “analyze test coverage and suggest improvements”). The agent executes in the cloud with full access to your environment.
You can continue conversing with the agent in real-time, watch its progress, and provide additional guidance as it works autonomously on your task.
**How this works:** Your cloud agent is now running in Warp’s infrastructure (not on your machine). It clones your repos, runs your setup commands, and starts working on your prompt. The agent has full access to your code and can run tests, make changes, and create artifacts like PRs.
### 5. View run details
[Section titled “5. View run details”](#5-view-run-details)
You can view details of your agent’s run, including commands executed, files changed, and environment used, several different ways:
* In the Warp app, open the [conversations panel](/agents/local-agents/interacting-with-agents/#conversation-panel) to see all your agent runs.
* Click the session link in your terminal output.
* Go to the [Oz web app](https://oz.warp.dev) and navigate to the **Runs** tab.
* Access from mobile via the [Oz web app](/platform/oz-web-app/).
**Breaking it down:** Every cloud agent run is auto-tracked. You get a shareable link, a run record, and full visibility into what the agent did. You or your teammates can watch the agent’s progress in real-time and even steer it if needed. The run record persists after completion so you can review it later.
### 6. Make it reusable with a skill (optional)
[Section titled “6. Make it reusable with a skill (optional)”](#6-make-it-reusable-with-a-skill-optional)
Turn your successful run into a skill that you can reuse:
```bash
/create-skill
```
Follow the prompts to save your task definition. Once created, you can run it again, schedule it, trigger it from Slack/Linear, or share it with your team.
**How this works:** Skills capture successful agent workflows as reusable building blocks. Instead of typing the same prompt repeatedly, you define it once. You can use it yourself, share it with teammates, schedule it to run automatically, or trigger it from integrations. Learn more about [Skills as Agents](/platform/skills-as-agents/).
**Prefer using the CLI?** See the [Oz CLI quickstart](/agents/cli/oz-cli/quickstart/) for CLI-based workflows.
***
## Next steps
[Section titled “Next steps”](#next-steps)
Now that you’ve run your first cloud agent, try these next steps:
* [**Schedule recurring work**](/platform/triggers/scheduled-agents-quickstart/) - Create a scheduled agent for maintenance tasks like dependency checks, cleanup, or triage.
* [**Trigger agents from Slack or Linear**](/platform/integrations/quickstart/) - Connect Warp to team tools so mentions and issue updates can launch cloud agent runs.
* [**Orchestrate multiple agents**](/platform/orchestration/multi-agent-runs/) - Fan work out across parent and child agents for large refactors, PR review swarms, and parallel package migrations.
* [**Turn successful prompts into reusable skills**](/platform/skills-as-agents/) - Save repeatable agent workflows and run them again from the CLI, web app, API, or a schedule.
* [**Build programmatic automations**](/factories/api-and-sdk/quickstart/) - Start cloud agent runs from your own systems with the Warp Platform API.
For example, schedule a recurring agent from the CLI:
```bash
oz schedule create \
--name "weekly-dependency-check" \
--cron "0 10 * * 1" \
--environment <ENV_ID> \
--prompt "check for dependency updates and open PR"
```
Note
Integrations require a team on Build, Max, or Business plan.
***
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
**Environment creation fails**\
Use official Docker Hub images like `node`, `python`, or `rust` for best compatibility. Ensure your GitHub repos are accessible. If using a custom image, avoid Alpine/musl-based images—the agent runtime requires glibc. See [Environments](/platform/environments/) for more guidance on choosing Docker images and [`environment_setup_failed`](/factories/api-and-sdk/troubleshooting/errors/environment-setup-failed/) for the related API error.
**Agent can’t access repos**\
Warp prompts you to authorize GitHub when you create an environment or trigger your first agent. If authorization fails or needs updating, see [How GitHub Authorization works](/agents/cli/oz-cli/integration-setup/#how-github-authorization-works) and [`external_authentication_required`](/factories/api-and-sdk/troubleshooting/errors/external-authentication-required/). For automated workflows using an agent API key, make sure [team GitHub authorization](/platform/team-access-billing-and-identity/#team-github-authorization) is configured in the Admin Panel. Also verify that repos are correctly configured in your environment with `oz environment get <ENV_ID>`; permission mismatches can surface as [`not_authorized`](/factories/api-and-sdk/troubleshooting/errors/not-authorized/).
**Not enough credits to run cloud agents**\
Your team needs at least 20 credits available. Check your credit balance in Settings or see [Access, Billing, and Identity](/platform/team-access-billing-and-identity/) for details on credit requirements and which plans support cloud agents. If a run is blocked because the billed principal has no remaining credits, see [`insufficient_credits`](/factories/api-and-sdk/troubleshooting/errors/insufficient-credits/).
**More resources**
* [Environments deep dive](/platform/environments/)
* [Cloud Agents FAQs](/platform/faqs/)
* [Managing Cloud Agents](/platform/managing-cloud-agents/)
# Cloud agent secrets
Canonical page: [/platform/secrets/](https://docs.warp.dev/platform/secrets/)
> Securely store, scope, and inject credentials for Warp cloud agents across CLI, Slack, Linear, and scheduled runs—without ever exposing secret values.
Cloud agents often need to interact with external systems such as APIs, databases, cloud providers, or internal tooling. To do this safely, Warp provides Warp-managed **agent secrets**, a secure way to store, scope, and inject credentials into cloud agent runs without exposing secret values to users or logs.
Warp-managed secrets are designed to work across [cloud agent](/platform/) and [integration](/platform/integrations/) triggers (CLI, Slack, Linear, and schedules), support both team-wide and personal credentials, and give engineering and security teams visibility into what agents can access.
For factory work, declare the managed secrets a factory or individual factory agent receives in its [factory definition](/factories/factory-as-code/#secrets). This page remains the reference for creating, scoping, and rotating the shared secrets.
**Warp-managed secrets are useful when:**
* A cloud agent needs to call an API or CLI that does not support OAuth
* You are using [MCP servers](/platform/mcp/) that expect static tokens or keys
* An agent needs credentials for tools like cloud CLIs, databases, monitoring systems, or internal services
* You want centralized auditing and control over what credentials agents can access
### Common use cases
[Section titled “Common use cases”](#common-use-cases)
* Run SQL queries against BigQuery or Metabase to answer questions like “what changed in last night’s pipeline run” or “how many users hit this error today,” using a read-only service account or API token.
* Call cloud or infrastructure CLIs to take small, predefined remediation steps when an alert fires, such as restarting a service, scaling a deployment, or clearing a stuck job, using tightly scoped credentials.
* List and review all API keys, service accounts, and tokens that cloud agents can access to verify scopes, rotation policies, and ownership match internal security requirements.
***
### How Warp-managed secrets work
[Section titled “How Warp-managed secrets work”](#how-warp-managed-secrets-work)
Warp provides a set of CLI commands for creating, updating, and listing secrets. Secret values are stored securely and cannot be retrieved once created.
At runtime, **Warp sets the relevant secrets as environment variables** for each cloud agent run, based on who triggered the agent and how it was triggered.
Note
Secret values are available only to the agent process (and any subprocesses it spawns) during execution, and **can’t be viewed or retrieved afterward.**
Key properties of secrets:
* **Scoped** to either a team or an individual user
* Secret values are **never readable after creation** (only metadata is visible)
* **Automatically set** for cloud agent runs when in scope
### Secret scopes
[Section titled “Secret scopes”](#secret-scopes)
Each secret has a scope that determines who can use it.
#### Team secrets
[Section titled “Team secrets”](#team-secrets)
Team secrets are shared across the entire team and are available to all cloud agents running on behalf of the team.
**Key characteristics:**
* Always injected into cloud agent runs, regardless of how the agent is triggered (CLI, Slack, Linear, or scheduled runs)
* Available to agents running with or without a specific user context
* Ideal for shared infrastructure credentials, service accounts, and read-only API keys
Note
Because team secrets are broadly available and may be used by fully automated or scheduled agents, they should generally be created **using bot or service accounts**, rather than credentials tied to an individual person. When you want a credential to be available to one workflow only, attach it to a [cloud agent](/platform/agents/) instead of giving every run access to it.
**For example:**
* Use a Metabase service account or read-only API token, not a personal Metabase API key
* Use cloud provider service accounts with minimal required permissions
* Use integration-specific tokens created for automation
This ensures credentials remain valid as team membership changes, permissions are tightly scoped, and ownership and rotation align with internal security policies.
Note
Team secrets can also be attached directly to a [cloud agent](/platform/agents/), so only runs executing as that cloud agent receive them. The secret itself still lives in the team’s secret scope; the cloud agent only references it by name.
#### Personal secrets
[Section titled “Personal secrets”](#personal-secrets)
Personal secrets belong to an **individual user**.
* Only available to cloud agents triggered by that user
* Not accessible to teammates or user-less triggers
* Useful for personal API keys or credentials tied to an individual account
***
## Creating secrets in the web app
[Section titled “Creating secrets in the web app”](#creating-secrets-in-the-web-app)
The [Oz web app](/platform/oz-web-app/) provides a guided side pane for creating Warp-managed secrets. Use it when you want a point-and-click flow without leaving the browser; the CLI flow below remains available for scripting and automation.
To create a secret in the web app:
1. In the Oz web app (https\://oz.warp.dev), open the **Secrets** page.
2. Click **Add secret** to open the **Add secret** side pane.
3. Enter a **Name** (for example, `OPENAI_API_KEY`). This becomes the environment variable name injected into runs.
4. Enter the **Value**. The value is encrypted in your browser before it is sent to the server; Warp never sees the plaintext.
5. Optionally, enter a **Description** to help teammates identify the secret later.
6. Choose a **Scope** — **Team** to share the secret with everyone on the team, or **Personal** to keep it scoped to your user.
7. Click **Create secret**.
The new secret appears in the Secrets list immediately. Its value is never readable from the UI after creation; to rotate the value, edit the secret and submit a new one.
***
## Managing agent secrets with the CLI
[Section titled “Managing agent secrets with the CLI”](#managing-agent-secrets-with-the-cli)
Secrets are managed using the `oz secret` command family.
You can create secrets interactively or from a file.
**Create a team secret interactively**
```bash
oz secret create --team METABASE_API_KEY
```
You will be prompted to enter the value securely in the terminal.
**Create a personal secret from a file**
```bash
oz secret create --personal --value-file api_key.txt METABASE_API_KEY
```
This is useful for long values such as JSON blobs or private keys.
#### Adding descriptions
[Section titled “Adding descriptions”](#adding-descriptions)
Descriptions help with auditing and rotation tracking.
```bash
oz secret create --team \
--description "Rotate every 2 weeks; owned by platform team" \
MY_SECRET
```
Descriptions are visible in listings but never expose the secret value.
#### Updating a secret
[Section titled “Updating a secret”](#updating-a-secret)
Updating a secret replaces its value and/or description while keeping the same name and scope.
**Update a secret value interactively**
```bash
oz secret update --team --value METABASE_API_KEY
```
You will be prompted to enter the new value securely in the terminal.
**Update a secret value from a file**
```bash
oz secret update --team \
--value-file new_api_key.txt \
METABASE_API_KEY
```
This is the recommended way to rotate credentials.
**Update a secret’s description (`-d`)**
```bash
oz secret update --team \
--description "Rotated 2026-02-26; owned by platform team" \
METABASE_API_KEY
```
#### Deleting a secret
[Section titled “Deleting a secret”](#deleting-a-secret)
To permanently remove a secret, use `oz secret delete`:
```bash
oz secret delete --team METABASE_API_KEY
```
You will be prompted for confirmation before the secret is deleted. Add `--force` to skip the confirmation prompt. Replace `--team` with `--personal` to delete a personal secret.
```bash
oz secret delete --team --force METABASE_API_KEY
```
Caution
Deleting a secret is permanent. Any cloud agent runs that depend on the deleted secret will no longer receive it as an environment variable.
#### Listing secrets
[Section titled “Listing secrets”](#listing-secrets)
You can list all secrets you have access to.
```bash
oz secret list
```
Example output:
```bash
NAME SCOPE LAST UPDATED
METABASE_API_KEY team 1 week ago
GCP_SERVICE_ACCOUNT_JSON team yesterday
MY_MCP_SERVER_TOKEN personal 10:00am
```
**Secret values are never displayed.**
### How secrets are made available to cloud agents
[Section titled “How secrets are made available to cloud agents”](#how-secrets-are-made-available-to-cloud-agents)
When a cloud agent starts, Warp determines which secrets are in scope and sets them as environment variables in the agent’s execution environment.
Today, secrets are provided as environment variables using the secret name as the variable name. For example:
```bash
METABASE_API_KEY=********
```
#### Secret size limit
[Section titled “Secret size limit”](#secret-size-limit)
Because secrets are injected as environment variables, each resulting `NAME=value` entry has to fit inside the operating system’s per-variable limit of 128 KiB (131,072 bytes), including the terminating null byte. The usable value length is 128 KiB minus that entry’s environment-variable name, the `=` sign, and the terminating null byte.
Warp validates the size when you create or update a secret. Secrets that expand into several environment variables, such as AWS credentials, are validated per variable.
If you hit the limit, store the large payload somewhere the agent can fetch it at run time (an object store or a secrets manager the agent can call) and keep only the fetch credential in the Warp-managed secret.
***
### Secret availability by trigger type
[Section titled “Secret availability by trigger type”](#secret-availability-by-trigger-type)
Which secrets an agent receives depends on how the agent was triggered.
#### User-initiated triggers
[Section titled “User-initiated triggers”](#user-initiated-triggers)
When an agent is triggered by a specific user, such as:
* Oz CLI
* Slack mentions
* Linear updates
**The agent receives:**
* All team-level secrets
* The triggering user’s personal secrets
It **does not receive personal secrets** belonging to other team members.
When an agent is triggered without a user context, such as:
* [Scheduled (cron) agents](/platform/triggers/scheduled-agents/)
* Fully automated [integrations](/platform/integrations/)
The agent receives:
* Team-level secrets only
Caution
Personal secrets are never injected in these cases.
***
## Scoping secrets to environments and runs
[Section titled “Scoping secrets to environments and runs”](#scoping-secrets-to-environments-and-runs)
Owner scoping (team versus personal) controls **which secrets exist** for a caller. Two additional layers — environments and individual runs — let you narrow **which of those secrets are actually injected** for a given execution. Together with [cloud agents](/platform/agents/), these layers form a broader access-scoping model where each layer contributes the secrets a run ends up with at execution time.
### Environment-level scoping
[Section titled “Environment-level scoping”](#environment-level-scoping)
A [cloud environment](/platform/environments/) can declare its own list of secrets. When a run uses that environment, the environment’s attached secrets are added to the run’s allowlist by default. The run can still narrow the allowlist further by passing its own `secrets` list, which then takes precedence. Use this when a workflow’s runtime needs a known, fixed set of credentials — for example, an `ops-tools` environment that only needs `DEPLOY_TOKEN` and `PAGERDUTY_API_KEY`.
#### Attach secrets to an environment
[Section titled “Attach secrets to an environment”](#attach-secrets-to-an-environment)
Use the environment form in the [Oz web app](/platform/oz-web-app/) to attach secrets to an environment:
1. In the Oz web app (https\://oz.warp.dev), open the **Environments** page.
2. Click an existing environment to edit it, or click **New environment** to create one.
3. In the environment form, open the **Secrets** section.
4. Select the team and personal secrets the environment should contribute to each run. Only secret names already in your scope are selectable; values are never displayed.
5. Click **Save**.
#### Attachment semantics
[Section titled “Attachment semantics”](#attachment-semantics)
Environment-attached secrets behave as follows at run time:
* **Secret names, not values** - The environment stores references by name. Underlying values stay in the team or personal secret scope, so rotating a value takes effect on the next run without re-attaching the secret.
* **Owner scope still applies** - A run only receives an attached secret if the trigger’s owner scope already allows it. Personal secrets are still skipped for triggers without a user context, as described under [Secret availability by trigger type](#secret-availability-by-trigger-type).
* **Resolved at run start** - Warp resolves the environment’s attached secrets when the run starts. If a referenced secret has been deleted or renamed since attachment, the run continues and the missing reference is surfaced in the run detail view.
### Run-level scoping
[Section titled “Run-level scoping”](#run-level-scoping)
Individual runs can override which secrets the run receives by listing them on the run’s config:
* **Default (no list provided)** - The run inherits every secret the creator or team has access to that is in scope for the trigger, exactly as described under [Secret availability by trigger type](#secret-availability-by-trigger-type).
* **Explicit list of secret names** - Only the listed secrets are injected. Any other secrets the caller can access are skipped for this run.
* **Empty list** - The run opts out of all secret injection. No managed secrets are injected, even for triggers that would otherwise receive them.
Run-level scoping is exposed through the public REST API on the run config. See the [Warp Platform API reference](/factories/api-and-sdk/) for the exact field and shape.
Note
Secret names that don’t exist in the caller’s scope are silently skipped at injection time rather than failing the run. The run detail view surfaces any references that were requested but not resolved so you can spot typos or stale names.
***
### Auditing and security considerations
[Section titled “Auditing and security considerations”](#auditing-and-security-considerations)
Warp is designed to make secret usage auditable and predictable:
* Secret values cannot be read or exported after creation
* All secrets are explicitly scoped to a team or user
* Engineering and security leads can list all secrets available to them
* Rotation is handled by updating secrets in place
* Cloud agents only receive secrets that are in scope for the trigger
**Teams remain responsible for:**
* Choosing appropriate scopes for each secret
* Limiting permissions on external systems (for example, read-only API keys)
* Rotating credentials according to internal policies
* Managing which agents and triggers exist within their environment
# Skills as Agents
Canonical page: [/platform/skills-as-agents/](https://docs.warp.dev/platform/skills-as-agents/)
> Run agents based on skills for consistent, repeatable workflows. Use skills with local or cloud agents from the CLI, Oz web app, API, or on a schedule.
You can start an agent from a [skill](/agents/capabilities/skills/)—a reusable set of instructions that defines what the agent should do. When you run an agent based on a skill, the skill provides the base prompt and behavior, while you supply additional context for that specific run.
Skills work with both **local agents** (running on your machine) and **cloud agents** (running in Warp’s infrastructure).
Skills that run independently of a factory are covered here. For instructions scoped to a factory or one of its agents, see [factory skills](/factories/factory-skills/).
This is useful when you want:
* **Consistent behavior** — The same skill produces the same workflow every time, regardless of who triggers it or where it runs.
* **Repeatable automation** — Run skills on schedules for maintenance tasks like code cleanup, dependency updates, or issue triage.
* **Shareable workflows** — Skills live in repositories, so your team can version, review, and collaborate on agent behavior.
***
## How Skills become available
[Section titled “How Skills become available”](#how-skills-become-available)
Skill discovery depends on whether you’re running a local or cloud agent.
### Local agents
[Section titled “Local agents”](#local-agents)
For local agent runs (`oz agent run`), skills are automatically discovered from your current repository. Warp scans these directories in order of precedence:
* **`.warp/skills/`**
* **`.agents/skills/`**
* **`.claude/skills/`**
* **`.codex/skills/`**
* **`.cursor/skills/`**
* **`.gemini/skills/`**
* **`.copilot/skills/`**
* **`.factory/skills/`**
* **`.github/skills/`**
* **`.opencode/skills/`**
You can also specify a skill from any accessible repository using the fully qualified format: `owner/repo:skill-name`.
### Cloud agents
[Section titled “Cloud agents”](#cloud-agents)
For cloud agent runs (`oz agent run-cloud`), skills are discovered from repositories configured in your [environments](/platform/environments/).
**Discovery workflow:**
1. **Create a skill** in your repository (see [Creating skills](/agents/capabilities/skills/#creating-skills))
2. **Add the repository** to an environment
3. **The skill appears** in the Agents list in the Oz web app
Note
You can also list available skills programmatically using the `GET /agent` endpoint. See the [Warp Platform API](/factories/api-and-sdk/) reference for details.
### Extra skill directories in cloud runs
[Section titled “Extra skill directories in cloud runs”](#extra-skill-directories-in-cloud-runs)
Skills that don’t live in a cloned repository’s standard skill directories can still be indexed. Set the `WARP_SKILL_DIRS` environment variable to a comma-separated list of skill directories, and a cloud run picks them up alongside the skills it discovers from your repositories. This is useful for skills baked into a custom Docker image, mounted from shared storage, or installed by a setup step outside a repo.
Set the variable in the environment’s Docker image so it’s present when the agent starts:
Dockerfile
```dockerfile
ENV WARP_SKILL_DIRS="/opt/team-skills,tooling/skills"
```
How the value is interpreted:
* **Directory layout** - Each entry is a skills directory whose direct children are skill folders containing a `SKILL.md`, the same layout as `.agents/skills/`. Point the variable at the parent directory, not at an individual skill folder.
* **Path resolution** - A leading `~` expands to the home directory. Relative entries resolve against the run’s working directory rather than the agent process’s current directory, so they stay stable even when setup steps change directories.
* **Precedence** - Skills loaded this way are treated as personal (home) skills, so they stay in scope for the whole run regardless of which directory the agent is working in. Repository skills of the same name still appear separately, as described in [skill name conflicts](/agents/capabilities/skills/#skill-name-conflicts).
The Warp Agent harness reads `WARP_SKILL_DIRS` directly. For [third-party harnesses](/platform/harnesses/) such as Claude Code and Codex, a cloud run publishes each of these skills into that harness’s own skill root before launch, so the harness discovers them through its native skill system.
***
## Running skill-based agents
[Section titled “Running skill-based agents”](#running-skill-based-agents)
You can start an agent from a skill using multiple entry points.
### Web app
[Section titled “Web app”](#web-app)
Use the [Oz web app](/platform/oz-web-app/) to run skill-based agents from a visual interface. From the web app, you can:
* Browse all skills available from your environments on the **Agents** page
* View suggested agents from Warp’s public [oz-skills repository](https://github.com/warpdotdev/oz-skills)
* Start a new run by selecting a skill, environment, and prompt
* Create scheduled agents that run skills on a cron schedule
For a complete walkthrough of the web app interface, see [Oz web app](/platform/oz-web-app/).
### CLI
[Section titled “CLI”](#cli)
Use the `--skill` flag with the Oz CLI:
```sh
# Run locally with a skill
oz agent run --skill "owner/repo:skill-name" --prompt "additional context"
# Run in the cloud with a skill
oz agent run-cloud \
--environment <ENV_ID> \
--skill "owner/repo:skill-name" \
--prompt "additional context"
```
For full CLI documentation, see [Using skills](/agents/cli/oz-cli/#using-skills) in the CLI reference.
### API & SDK
[Section titled “API & SDK”](#api--sdk)
Use the `skill_spec` parameter when creating a run:
```json
{
"prompt": "additional context for this run",
"config": {
"environment_id": "<ENV_ID>",
"skill_spec": "owner/repo:skill-name"
}
}
```
For full API documentation, see [Agent configuration](/factories/api-and-sdk/#agent-configuration) in the API reference.
***
## Running skills on a schedule
[Section titled “Running skills on a schedule”](#running-skills-on-a-schedule)
One of the most powerful uses for skill-based agents is running them on a schedule. [Scheduled agents](/platform/triggers/scheduled-agents/) execute automatically at specified times, making them ideal for:
* **Dead code cleanup** — Weekly scans for unused code or stale feature flags
* **Dependency updates** — Daily or weekly checks for security updates
* **Issue triage** — Regular categorization and prioritization of open issues
* **Documentation refresh** — Periodic updates to keep docs in sync with code
**Creating a scheduled skill-based agent:**
```sh
oz schedule create \
--name "Weekly Code Cleanup" \
--cron "0 10 * * 1" \
--environment <ENV_ID> \
--prompt "Scan for dead code and unused feature flags. Open a PR with removals."
```
You can also create schedules from the [Oz web app](/platform/oz-web-app/) using the **New schedule** action.
For full scheduling documentation, see [Scheduled Agents](/platform/triggers/scheduled-agents/).
***
## Suggested Skills
[Section titled “Suggested Skills”](#suggested-skills)
The [Oz web app](/platform/oz-web-app/) displays suggested agents from the public [warpdotdev/oz-skills](https://github.com/warpdotdev/oz-skills) repository. These are pre-built skills that demonstrate common use cases and can be used as starting points for your own workflows.
Suggested skills appear on the Agents page under the **Suggested** filter.
***
## Related resources
[Section titled “Related resources”](#related-resources)
* [Skills](/agents/capabilities/skills/) — How to create skills and skill file format
* [Environments](/platform/environments/) — Configure repositories and runtime context for cloud agents
* [Scheduled Agents](/platform/triggers/scheduled-agents/) — Run agents automatically on a cron schedule
* [Warp Factories](/factories/) — Assemble named agents, automations, and measurement into a standing triage-to-merge workflow
* [Oz web app](/platform/oz-web-app/) — Visual interface for managing cloud agents
* [Oz CLI](/agents/cli/oz-cli/) — Command-line interface for running agents
* [Warp Platform API](/factories/api-and-sdk/) — Programmatic access to cloud agents
# Access, billing, and identity permissions
Canonical page: [/platform/team-access-billing-and-identity/](https://docs.warp.dev/platform/team-access-billing-and-identity/)
> Understand how access to cloud agents works for individuals and teams, how billing and credits apply, and how Warp maps user identities across integrations.
This page explains how access to cloud agents works for both individual users and teams, how billing and credits apply, and how Warp maps user identities across integrations.
***
## Overview: individual vs team access
[Section titled “Overview: individual vs team access”](#overview-individual-vs-team-access)
Cloud agents can be used in two ways:
**Individual users** (without a team):
* Can run cloud agents via CLI or API
* Can use Warp credits, including [cloud agent credits](/support-and-community/plans-and-billing/credits/#compute-credits)
* Agents run on Warp-hosted infrastructure
* Cannot use integrations (Slack, Linear, Jira, GitHub) or self-hosted agents
**Teams** (users who are part of a [Warp team](/knowledge-and-collaboration/teams/)):
* All individual capabilities, plus:
* Can use integrations (Slack, Linear, Jira, and the [GitHub integration](/platform/integrations/github/)) to trigger agents
* Can self-host agents on their own infrastructure (Enterprise only)
* Share team-level configuration (environments, secrets, integrations)
* Team must be on Build, Max, or Business plan with at least 20 credits for cloud agents and integrations
***
## Individual access
[Section titled “Individual access”](#individual-access)
Individual users can run cloud agents via the CLI or API without being part of a team.
**How it works:**
* Run agents using `oz agent run-cloud` or the Warp Platform API
* Credits are drawn from your Warp credits (including cloud agent credits, when applicable)
* Agents execute on Warp-hosted infrastructure
**What you can do:**
* Run cloud agents from CI/CD pipelines
* Trigger agents programmatically via API
* Use personal secrets for authentication
**What requires a team:**
* Integrations (Slack, Linear, Jira, and the [GitHub integration](/platform/integrations/github/))
* Self-hosted agent execution
* Team secrets and shared configuration
***
## Team access
[Section titled “Team access”](#team-access)
A [Warp team](/knowledge-and-collaboration/teams/) is a group of users who share configuration and collaborate on cloud agents. Teams can be created on any plan, including Free.
**What teams enable:**
* **Integrations** - Create Slack, Linear, and Jira integrations that all team members can use, and enable the [GitHub integration](/platform/integrations/github/) so teammates can start agents with an `@warp-agent` mention
* **Shared configuration** - Team-level environments, secrets, and settings
* **Self-hosting** - Run agents on your own infrastructure (Enterprise only)
* **Team visibility** - Shared observability into agent runs and history
Integrations are created at the team level, not per-user. Once a Slack or Linear integration is installed, everyone on your Warp team can use **@warp** in the connected workspace. The integration behaves the same way for all teammates, and everyone shares the same underlying environment configuration. The GitHub integration is team-level in the same way: once an admin enables the GitHub organization, any teammate with a connected GitHub account can start a run by mentioning **@warp-agent**.
When someone triggers a cloud agent for the first time, Warp may prompt them to grant GitHub authorization so the agent can open pull requests or push branches under their identity. This allows each run to use the correct permissions without requiring additional setup from an admin.
#### Requirements for integrations
[Section titled “Requirements for integrations”](#requirements-for-integrations)
Integrations and [cloud agents](/platform/) run inside Warp’s cloud, which means usage is billed based on [credits](/support-and-community/plans-and-billing/credits/).
Your team must meet the following requirements to run integrations:
* You must be on a **Build, Max, or Business** plan with [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) enabled, or on an **Enterprise** plan with a team credit pool per your contract.
* Your team needs at least **20 credits** available to run cloud agents and integrations
When a user triggers an agent through an integration (like Slack or Linear), the run draws from credits based on who the run is billed to:
* **User-triggered runs on Build, Max, or Business** - Warp draws from any [cloud agent credits](/support-and-community/plans-and-billing/credits/#compute-credits) the user has, then the user’s plan-included credits, then the team’s shared add-on credit pool.
* **Agent API key or scheduled cloud agent runs on Build, Max, or Business** - Warp bills the team owner. The waterfall is: the owner’s plan-included credits, then the team’s shared add-on credit pool. With auto-reload off, the request is blocked when both are depleted. With auto-reload on, usage can trigger a reload into the team’s shared pool subject to the team-wide monthly spend cap; once the cap is reached, runs are blocked until the cap resets or increases.
* **Enterprise plans** - Runs draw from the team-scoped credit pool, per your Enterprise contract terms.
If all applicable credit sources are exhausted and no auto-reload is configured, integrations and cloud agents will not run until credits are added. See [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) for the full self-serve waterfall and [platform credits](/support-and-community/plans-and-billing/platform-credits/) for the third bucket that applies to every cloud agent run.
Note
If you’re on an Enterprise plan, please reach out to [contact sales](https://www.warp.dev/contact-sales) with any billing questions related to integrations.
### Identity mapping
[Section titled “Identity mapping”](#identity-mapping)
Warp needs a reliable way to know which person a cloud agent run is acting for, across Warp, Slack, Linear, and GitHub.
* Slack uses a dedicated account-linking flow to map a Slack user to their Warp account. This is the recommended path for Slack-triggered agents, since it doesn’t rely on email matching.
* Linear currently maps identities using email address matching. Your Linear email must match your Warp account email for Warp to correctly attribute and scope agent runs.
* The [GitHub integration](/platform/integrations/github/) maps the GitHub account that mentioned `@warp-agent` to the Warp account that connected it, rather than by email. Until a teammate connects their GitHub account, Warp replies in the thread with a link to connect instead of starting a run. That binding sets run attribution, team ownership, and billing; the run’s GitHub access comes from the app installation instead.
* Each teammate must authorize GitHub before an agent can write PRs or push branches on their behalf
* For Slack-triggered, Linear-triggered, and locally triggered runs, agents operate using the GitHub permissions of the triggering user
This ensures runs are scoped to what the user is allowed to see and modify, and that ownership of PRs remains clear across teams and repositories. The two exceptions are agent API key runs with [team GitHub authorization](#team-github-authorization) and runs started from an `@warp-agent` mention, which both authenticate as the Warp Factories GitHub App installation.
***
## Team GitHub authorization
[Section titled “Team GitHub authorization”](#team-github-authorization)
By default, cloud agents authenticate with GitHub using the personal token of the user who triggered the run. Team GitHub authorization gives you an alternative: authenticate with the **Warp Factories** GitHub App instead, so agents can clone repositories and open pull requests without relying on any individual’s token.
This is useful for fully automated workflows that use an [agent API key](/agents/cli/oz-cli/api-keys/), like CI/CD pipelines, [scheduled agents](/platform/triggers/scheduled-agents/), and SDK-triggered runs, where you want code changes attributed to the GitHub App rather than a specific person.
### How it works
[Section titled “How it works”](#how-it-works)
When an agent task is initiated with an agent API key, there is no individual user to authenticate on behalf of. Instead, Warp uses tokens issued by the **Warp Factories** GitHub App installation to authenticate directly with GitHub.
The GitHub App token gives the agent access to the repositories included in the app installation — it can clone repos, create branches, push commits, and open pull requests. During installation, you choose whether the app can access **all repositories** or only **selected repositories** in your GitHub organization, and this controls what agent API key runs can access.
### Setting up team GitHub authorization
[Section titled “Setting up team GitHub authorization”](#setting-up-team-github-authorization)
1. **Install the Warp Factories GitHub App.** A user with admin permissions on the GitHub organization installs the [Warp Factories](https://github.com/apps/warp-factories) GitHub App. During installation, grant the app access to **all repositories** or **selected repositories** in your org.
Note
There are two places you may encounter this installation flow:
* During the first-time experience for the Automation Platform, when you connect your GitHub account.
* When you click **Configure access on GitHub** in the repository selector while creating an environment.
Each installation is scoped to a single GitHub organization or personal account — you can install the app to multiple orgs separately. :::

Installing the Warp Factories GitHub App.
2. **Enable the GitHub org for your Warp team.** A Warp team admin opens the Admin Panel in the Warp app (**Settings** > **Admin Panel** > **Platform**) and adds the GitHub organization under **Enabled GitHub Orgs**. This associates the GitHub App installation with your Warp team.

Enabled GitHub Orgs setting in the Admin Panel.
3. **Use an agent API key.** Tasks initiated with an agent API key on the team now use tokens from the GitHub App installation to clone repos and push changes. No individual GitHub authorization is needed. On GitHub, commits and pull requests are opened by the Warp Factories GitHub App rather than any individual user; in the cloud agent dashboard, the run is attributed to the bound [cloud agent](/platform/agents/).
### How this relates to environments
[Section titled “How this relates to environments”](#how-this-relates-to-environments)
An [environment](/platform/environments/) is a template for a cloud agent’s sandbox — it defines the Docker image, repos, and setup commands, but it does not carry its own GitHub permissions. The same environment can be used by different users or by agent API key runs, and each will authenticate to GitHub independently.
The environment configuration and the **Enabled GitHub Orgs** setting in the Admin Panel serve different purposes:
* **Environment repo list** - “This agent needs repos A, B, and C.”
* **Enabled GitHub Orgs** - “This team can use the Warp Factories GitHub App to access repos in this GitHub organization.”
### Personal tokens vs. GitHub App tokens
[Section titled “Personal tokens vs. GitHub App tokens”](#personal-tokens-vs-github-app-tokens)
Team GitHub authorization is complementary to the existing personal token flow:
* **User-triggered runs** (personal API key, Slack, Linear, Warp app) - The agent authenticates using the triggering user’s personal token. PRs and commits are attributed to that user.
* **Agent API key runs with GitHub App authorization** - The agent authenticates as the GitHub App installation. On GitHub, PRs and commits are attributed to the Warp Factories GitHub App rather than any individual user. In the cloud agent dashboard, the run is attributed to the bound [cloud agent](/platform/agents/), which controls run filtering and audit attribution on the Warp side.
* **[GitHub integration](/platform/integrations/github/) runs** (an `@warp-agent` mention on an issue or pull request) - The agent authenticates as the installation that delivered the event, so its repository access and its GitHub attribution match the agent API key flow. In the cloud agent dashboard the run is still attributed to the teammate who wrote the mention, and their team is billed.
These flows can coexist on the same team. Personal tokens are still used for user-triggered runs from a personal API key, Slack, Linear, and the Warp app, and the GitHub App installation token is used for agent API key runs and for GitHub integration runs.
Caution
GitHub App installation tokens are scoped to a single GitHub organization at a time. If your team works across repos in multiple GitHub organizations, the agent can only use the installation token for the organization enabled in the Admin Panel. Repos in other organizations require user-triggered runs with a personal API key.
Note
To change which repositories the GitHub App can access, edit the app installation in your [GitHub settings](https://github.com/settings/installations).
***
## Data and permissions
[Section titled “Data and permissions”](#data-and-permissions)
#### Slack / Linear
[Section titled “Slack / Linear”](#slack--linear)
Installing the Automation Platform app gives Warp access to the Slack channels or Linear teams where the app is installed.
**When a run is triggered, Warp receives:**
* The content of the tagged thread or issue
* Relevant surrounding context used to build the agent prompt
Warp stores only the content required for the agent to complete its task. You can message @warp directly, mention it in channels, or tag it on specific issues depending on the integration.
#### GitHub
[Section titled “GitHub”](#github)
Warp’s behavior in GitHub is defined by two layers of control:
1. **The Warp GitHub App installation scope**
* Determines which organizations and repositories Warp can read and write to
* Can be edited at any time in GitHub settings
2. **Permissions of the triggering user**
* Agents inherit the user’s read/write privileges
* Agents cannot elevate permissions, see additional repos, or write to repos the user cannot access
**In practice, agents can only operate on repositories that:**
* Are included in the environment configuration
* Are accessible to both the GitHub app and the triggering user.
Runs triggered by an `@warp-agent` mention through the [GitHub integration](/platform/integrations/github/) follow the first layer only. Warp receives the content of the issue, pull request, or review thread that carried the mention, including the recent comments and the diff of a commented file, and the run authenticates with the GitHub App installation that delivered the event. Cloning, commits, branches, pull requests, and status comments all use that installation’s access rather than the mentioning user’s, so the installation’s repository selection is the only boundary on what those runs can reach. The repository that triggered the mention is cloned alongside any repositories in the configured environment, and only the repositories that installation covers are available to the agent.
***
## Additional notes: how cloud agents use credits
[Section titled “Additional notes: how cloud agents use credits”](#additional-notes-how-cloud-agents-use-credits)
Cloud agents can run automatically in the background when activated by a trigger such as a Slack mention, a Linear update, or a scheduled task. These runs require compute and model usage, which translates to credit consumption.
**Typical credit usage:**
Cloud agent runs consume credits based on the complexity of the task and whether an environment is used. The exact amount varies by run.
#### How credit usage works
[Section titled “How credit usage works”](#how-credit-usage-works)
How credits are consumed depends on how the agent run is triggered and authenticated:
**User-triggered runs** (CLI with personal API key, Slack, Linear, or the Warp app):
* Runs are tied to the triggering user’s identity.
* On Build, Max, and Business plans, Warp consumes credits in a fixed order. You cannot prioritize user-scoped grants ahead of shared team grants:
1. The triggering user’s monthly credits included with their plan.
2. Shared bonus or add-on grants available to the active team (team-wide pool first).
3. The triggering user’s remaining user-scoped bonus or add-on grants that apply to the active team. This includes any remaining add-on credit balance purchased between May and August 2026. Warp uses these grants only after shared team grants are exhausted.
* On Enterprise plans, runs draw from the team-scoped credit pool, per your Enterprise contract terms.
**Agent API key and scheduled cloud agent runs** (fully automated workflows):
* Runs are not tied to any individual user.
* On Build, Max, and Business plans, Warp bills the team owner: the owner’s plan-included credits, then the team’s shared add-on credit pool. With auto-reload off, the request is blocked when both are depleted. With auto-reload on, usage can trigger a reload into the team’s shared pool subject to the team-wide monthly spend cap.
* On Enterprise plans, these runs draw from the team-scoped credit pool, per your Enterprise contract terms.
* Ideal for CI/CD pipelines, scheduled tasks, and other automated workflows.
* For workflows that require code changes (opening pull requests, pushing branches, or writing to a repository), configure [team GitHub authorization](#team-github-authorization) so the agent can authenticate with the Warp Factories GitHub App. Alternatively, use a [personal API key](/agents/cli/oz-cli/api-keys/) to authenticate as an individual user.
For more details on creating and using API keys, see [API Keys](/agents/cli/oz-cli/api-keys/).
Note
When a user triggers an agent via Slack or Linear, the run still follows that same order — plan-included credits first, then shared team grants, then any applicable user-scoped grants — as long as the triggering user’s identity can be mapped to their Warp account.
#### Who configures triggers and workflows
[Section titled “Who configures triggers and workflows”](#who-configures-triggers-and-workflows)
All triggers and instructions used by cloud agents are defined and controlled by your team’s authorized users.
* Admins or other authorized users decide which triggers exist, when they fire, and what the agent should do in response.
* Trigger behavior and the agent’s instructions (system prompts, workflow steps, repo access, etc.) are fully managed by your admins or other designated users.
#### Staying aware of usage
[Section titled “Staying aware of usage”](#staying-aware-of-usage)
Because triggers and instructions are configured by your team, the credits consumed when an agent runs are billed according to the model above:
* **Build, Max, Business** - User-triggered runs draw from the triggering user’s plan-included credits, then shared team grants, then any remaining user-scoped grants. Agent API key runs and scheduled cloud agent runs are billed to the team owner (the owner’s plan-included credits, then the team’s shared add-on credit pool, subject to the team-wide spend cap when auto-reload is on).
* **Enterprise** - All runs draw from the team-scoped credit pool, per your Enterprise contract terms.
It’s the team’s responsibility to manage triggers, confirm they behave as intended, and monitor usage. Reviewing triggers, prompts, and agent behavior periodically helps ensure that credit usage aligns with expectations.
***
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
If a cloud agent or integration run fails with an error code, use the error reference to narrow the fix:
* **Missing GitHub or external authorization** - See [`external_authentication_required`](/factories/api-and-sdk/troubleshooting/errors/external-authentication-required/) when a user needs to authorize GitHub, Slack, or Linear before a run can continue.
* **Insufficient repo permissions** - See [`not_authorized`](/factories/api-and-sdk/troubleshooting/errors/not-authorized/) when the triggering user or GitHub App lacks access to the repo the agent needs.
* **Credits or spend caps block a run** - See [`insufficient_credits`](/factories/api-and-sdk/troubleshooting/errors/insufficient-credits/) or [`budget_exceeded`](/factories/api-and-sdk/troubleshooting/errors/budget-exceeded/) when the billed account has depleted credits or reached a configured spend cap.
***
## Related resources
[Section titled “Related resources”](#related-resources)
* [Add-on credits](/support-and-community/plans-and-billing/add-on-credits/) - How team-shared add-on credits, auto-reload, and the team-wide spend cap work on self-serve plans.
* [Platform credits](/support-and-community/plans-and-billing/platform-credits/) - The third credit bucket that applies to every cloud agent run, alongside AI credits and compute credits.
* [Credits overview](/support-and-community/plans-and-billing/credits/) - The full credit model across plans.
# Triggers overview
Canonical page: [/platform/triggers/](https://docs.warp.dev/platform/triggers/)
> Configure triggers to run cloud agents automatically based on schedules or events.
A trigger is anything that starts a cloud agent run without you typing a prompt: a recurring schedule, an integration like Slack or Linear, a CI event, or a call to the API. This page covers the full set, including the [integrations](/platform/integrations/) that connect agents to the tools your team already uses.
For triggers that route work through one factory’s named agents and workflow, use [factory automations](/factories/automations/) and [factory integrations](/factories/connect-your-factory/).
To set up your first recurring agent, follow the [Scheduled Agents Quickstart](/platform/triggers/scheduled-agents-quickstart/).
If you’re choosing between schedules, Slack, Linear, GitHub, GitHub Actions, the Oz CLI, or the API, start with [Run agents unattended with schedules and triggers](/guides/agent-workflows/how-to-run-unattended-agents/).
## Available trigger types
[Section titled “Available trigger types”](#available-trigger-types)
* **[Scheduled Agents](/platform/triggers/scheduled-agents/)** - Run agents on a recurring schedule using cron expressions.
* **[CLI](/agents/cli/oz-cli/)** - Trigger cloud agents directly from your terminal using the Oz CLI.
* **[API & SDK](/factories/api-and-sdk/)** - Programmatically trigger agents via the Warp API or SDK.
* **[Integrations](/platform/integrations/)** - Trigger agents from external services like Slack, Linear, or Jira.
* **[GitHub](/platform/integrations/github/)** - Mention `@warp-agent` on an issue, pull request, or review comment to start an agent that replies in the thread.
* **[GitHub Actions](/platform/integrations/github-actions/)** - Run agents from your own CI workflows and repository events.
* **[Custom webhooks](/factories/webhooks/)** - Give a [factory](/factories/) an authenticated URL that any system can POST JSON to, and start its automations from the deliveries.
After a trigger fires, track and review the resulting runs across your team from the [Agent Management Panel and Oz web app Runs page](/platform/managing-cloud-agents/), where you can filter by source, status, day, or creator.
# Scheduled Agents
Canonical page: [/platform/triggers/scheduled-agents/](https://docs.warp.dev/platform/triggers/scheduled-agents/)
> Run cloud agents on a cron schedule for automated maintenance and recurring tasks.
Warp’s Scheduled Agents let you run cloud agents automatically on a **recurring schedule**. They are designed for routine, repeatable tasks that should happen without manual intervention, such as dead code cleanup, dependency maintenance, issue triage, or periodic refactors.

Scheduled Agents run in the background on Warp’s infrastructure. Each run starts from a clean session, executes a fixed prompt, and produces its own task and session history that can be inspected after the fact.
For a guided, no-CLI walkthrough that creates a recurring agent from the Oz web app, see the [Scheduled Agents quickstart](/platform/triggers/scheduled-agents-quickstart/). This page is the full reference for managing schedules with the Oz CLI.
If you’re deciding whether to use a schedule, Slack or Linear trigger, GitHub Actions, the Oz CLI, or the API, see [Run agents unattended with schedules and triggers](/guides/agent-workflows/how-to-run-unattended-agents/).
***
### What are Scheduled Agents?
[Section titled “What are Scheduled Agents?”](#what-are-scheduled-agents)
A Scheduled Agent is a [cloud agent](/platform/) that runs on a cron-based schedule.
**Key characteristics:**
* Runs automatically based on a cron expression.
* Uses a fixed prompt defined at schedule creation time.
* Starts a fresh agent session for every run.
* Executes in a specific Warp [Environment](/platform/environments/), if provided.
* Consumes credits when it runs.
* Can be paused, updated, or deleted at any time.
Scheduled Agents are ideal for work that should happen regularly and predictably, without needing a human to trigger the agent manually.
### Common use cases
[Section titled “Common use cases”](#common-use-cases)
Scheduled Agents are best suited for maintenance-style workflows, including skills that automate recurring tasks. For more on running skill-based agents on schedules, see [Skills as Agents](/platform/skills-as-agents/).
Common use cases include:
* Dead code or unused feature flag cleanup.
* Dependency updates or security scans.
* Issue or PR triage on a recurring cadence.
* Periodic documentation refreshes.
* Repository hygiene tasks like formatting or lint checks.
* Scheduled reporting or audits.
Because each run is isolated, Scheduled Agents are safe to use for tasks that benefit from a clean, repeatable execution environment.
***
### Scheduling agents with the CLI
[Section titled “Scheduling agents with the CLI”](#scheduling-agents-with-the-cli)
Automation Platform scheduled agents are managed through the Automation Platform `schedule` family of CLI commands.
All scheduling operations require the Oz CLI and an authenticated session.
#### Creating a schedule
[Section titled “Creating a schedule”](#creating-a-schedule)
Use `oz schedule create` (with required flags) to define a new Scheduled Agent.
**Each schedule requires:**
* A name, for identification.
* A cron schedule.
* A prompt or skill that the agent will execute.
* An optional environment in which the agent will run.
* An optional [model selection](/agents/cli/oz-cli/#using-agent-profiles).
* [Optional MCP server configuration](/platform/mcp/).
```bash
oz schedule create \
--name=NAME \
--cron=SCHEDULE \
--prompt=PROMPT \
[--environment=ENVIRONMENT_ID] \
[--skill=SPEC] \
[--host=WORKER_ID] \
[--mcp=SPEC] \
[--model=MODEL_ID] \
[--file=PATH]
```
**Optional flags:**
* `--skill <SPEC>` — use a skill as the base prompt (format: `repo:skill_name` or `org/repo:skill_name`). See [Skills as Agents](/platform/skills-as-agents/).
* `--host <WORKER_ID>` — run on a specific self-hosted worker instead of Warp-hosted infrastructure.
* `--mcp <SPEC>` — attach MCP servers (inline JSON, file path, or UUID). Can be repeated.
* `--model <MODEL_ID>` — override the default model.
* `--file <PATH>` — load schedule configuration from a YAML or JSON file.
Note
[Environments](/platform/environments/) are optional — if you don’t specify one, the scheduled agent runs in a barebones sandbox. Without an environment, the agent won’t have access to your code repositories, pre-installed tools, or setup commands, so this is only suited for tasks that don’t need your codebase.
Caution
`oz schedule create` has no **Agent** flag, so a schedule created with the CLI runs as its creator and opens pull requests under that person’s GitHub account. To run it as a [cloud agent](/platform/agents/) instead, set **Agent** on the schedule from the [Schedules page](https://oz.warp.dev/schedules) in the Oz web app after creating it. See [Run identity and pull request authorship](/platform/triggers/scheduled-agents-quickstart/#run-identity-and-pull-request-authorship).
**Example**
The following command schedules an agent to clean up old feature flags every four days:
```bash
oz schedule create \
--name "Feature Flag Cleanup" \
--cron "0 10 */4 * *" \
--prompt "Scan the repository for stale feature flags and remove any that are no longer referenced. Open a PR with the changes and include a summary." \
--environment "KB1ndNMQAs5kjPdX2jatA8"
```
Once created, the agent will automatically run at the specified times without further action.
Scheduled Agents support the same [model selection](/agents/cli/oz-cli/) and [MCP server configuration](/platform/mcp/) as other cloud agent triggers.
#### Cron schedule format
[Section titled “Cron schedule format”](#cron-schedule-format)
Warp uses standard cron syntax to define schedules.
A cron expression consists of five fields:
```plaintext
minute hour day-of-month month day-of-week
```
For example:
* `0 10 * * *` runs every day at 10:00 AM.
* `0 10 */4 * *` runs every four days at 10:00 AM.
* `0 8 1 * *` runs at 8:00 AM on the first day of every month.
Make sure your cron expression reflects the cadence you want, as Scheduled Agents will run exactly according to this schedule.
### Listing Scheduled Agents
[Section titled “Listing Scheduled Agents”](#listing-scheduled-agents)
To view all Scheduled Agents for your team, use:
```bash
oz schedule list
```
This command prints a table with details about each schedule, including:
* Schedule ID
* Name
* Cron schedule
* Paused
* Last run time
* Next scheduled run
* Scope
| ID | Name | Schedule | Paused | Last Ran | Next Run | Scope |
| ------ | -------------------- | -------------- | ------ | -------------------------------------------- | --------------------- | ----- |
| abc123 | Feature Flag Cleanup | `0 10 */4 * *` | No | `2025-11-24 10:00 AM<task id><session link>` | `2025-11-28 10:00 AM` | Team |
| def456 | Issue Triage | `0 8 1 * *` | Yes | `2025-11-24 08:00 AM<task id><session link>` | Paused | - |
Each completed run also includes links to:
* The task created by the agent.
* The full agent session, including logs and outputs.
This makes it easy to review what ran, when it ran, and what the agent did. You can also monitor scheduled runs alongside your other agents in the [Agent Management Panel](/platform/managing-cloud-agents/) in the Warp app, where you can filter by the **Scheduled** source to isolate them.
#### Viewing a specific Scheduled Agent
[Section titled “Viewing a specific Scheduled Agent”](#viewing-a-specific-scheduled-agent)
Use `oz schedule get` to view detailed information about a single Scheduled Agent.
```bash
oz schedule get SCHEDULE_ID
```
This command returns additional details not shown in the list view, including:
* Full schedule configuration
* Prompt and model configuration
* Environment and MCP settings
* Recent runs and execution metadata
* Links to related tasks and agent sessions
This is useful when reviewing behavior, debugging failures, or inspecting how a Scheduled Agent is configured.
### Pausing and unpausing schedules
[Section titled “Pausing and unpausing schedules”](#pausing-and-unpausing-schedules)
Scheduled Agents can be temporarily disabled without deleting them.
```bash
oz schedule pause SCHEDULE_ID
```
When paused, the agent will not run at its scheduled times.
**Example**
```bash
oz schedule pause abc123
```
#### Unpausing a schedule
[Section titled “Unpausing a schedule”](#unpausing-a-schedule)
```bash
oz schedule unpause SCHEDULE_ID
```
Once unpaused, the agent resumes running according to its original cron schedule.
### Editing Scheduled Agents
[Section titled “Editing Scheduled Agents”](#editing-scheduled-agents)
You can modify an existing schedule using `oz schedule update`.
You can update one or more properties at a time, including:
* The schedule name.
* The cron schedule.
* The prompt used for future runs.
* The skill used as the base prompt.
* The environment used for execution.
* The model, MCP, and host configuration used for future runs.
The **Agent** setting can’t be changed with this command. Change it from the [Schedules page](https://oz.warp.dev/schedules) in the Oz web app.
#### Command
[Section titled “Command”](#command)
```bash
oz schedule update SCHEDULE_ID \
[--name=NAME] \
[--cron=SCHEDULE] \
[--prompt=PROMPT] \
[--environment=ENVIRONMENT_ID] \
[--skill=SPEC] \
[--remove-skill] \
[--host=WORKER_ID] \
[--mcp=SPEC] \
[--remove-mcp=SERVER_NAME] \
[--model=MODEL_ID]
```
**Additional update flags:**
* `--skill <SPEC>` — update the skill used as the base prompt.
* `--remove-skill` — remove the skill from this scheduled agent.
* `--host <WORKER_ID>` — update the execution host.
* `--mcp <SPEC>` — add MCP servers to this schedule.
* `--remove-mcp <SERVER_NAME>` — remove an MCP server by name.
* `--remove-environment` — remove the environment from this schedule.
#### Examples
[Section titled “Examples”](#examples)
Change when a scheduled agent runs, leaving everything else unchanged:
```bash
oz schedule update abc123 --cron "0 9 */4 * *"
```
Update the environment used for future runs:
```bash
oz schedule update abc123 --environment=jkl789
```
Changes apply only to future runs. Past runs and their session history remain unchanged.
### Deleting a Scheduled Agent
[Section titled “Deleting a Scheduled Agent”](#deleting-a-scheduled-agent)
To permanently remove a schedule, use:
```bash
oz schedule delete SCHEDULE_ID
```
**Example**
```bash
oz schedule delete abc123
```
Deleting a schedule immediately stops all future runs. Previous runs and their session history remain accessible for inspection and review.
***
### Execution model and behavior
[Section titled “Execution model and behavior”](#execution-model-and-behavior)
Each scheduled run behaves like a standard cloud agent run, with a few important guarantees:
* Every run starts a fresh session.
* No state is carried over between runs unless your environment explicitly persists data.
* Runs execute automatically without human intervention.
* All usage is billed to the team’s shared credit balance.
If a scheduled run fails, it does not block future runs. Each execution is independent. Use the [API error reference](/factories/api-and-sdk/troubleshooting/errors/) to interpret any returned error code.
### Permissions and responsibility
[Section titled “Permissions and responsibility”](#permissions-and-responsibility)
Scheduled Agents are created and managed by authorized users on a Warp team.
By creating a Scheduled Agent, you are responsible for:
* The cron schedule and how often the agent runs.
* The instructions provided in the prompt.
* The environment and integrations the agent has access to.
* The credits consumed by scheduled executions.
Carefully review prompts and schedules before deploying them broadly, especially for agents that can modify production code or infrastructure.
### When to use Scheduled Agents vs triggers
[Section titled “When to use Scheduled Agents vs triggers”](#when-to-use-scheduled-agents-vs-triggers)
Scheduled Agents are best when work should happen on a predictable cadence.
If you want an agent to run in response to an event, such as a Slack mention, PR update, or issue change, use [integrations](/platform/integrations/) to trigger cloud agents instead.
Many teams use both together: [triggers](/platform/triggers/) for reactive workflows, and Scheduled Agents for proactive maintenance.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Environments](/platform/environments/) — configure the repo, image, and setup commands scheduled runs execute with
* [Viewing cloud agent runs](/platform/viewing-cloud-agent-runs/) — inspect transcripts, logs, and outputs from each scheduled run
* [Skills as Agents](/platform/skills-as-agents/) — run a reusable skill definition on a schedule
* [Run unattended agents](/guides/agent-workflows/how-to-run-unattended-agents/) — compare schedules with Slack, Linear, GitHub Actions, CLI, and API triggers
# Scheduled Agents quickstart
Canonical page: [/platform/triggers/scheduled-agents-quickstart/](https://docs.warp.dev/platform/triggers/scheduled-agents-quickstart/)
> Schedule a cloud agent to run recurring tasks automatically — issue triage, dependency checks, code cleanup, and more.
Scheduled agents are cloud agents that run on a recurring cron schedule, handling recurring tasks automatically without manual triggers. This guide walks you through setting up an agent that triages your GitHub bug reports every week, checks whether each issue has enough detail to investigate, and posts follow-up comments when information is missing. You’ll use a prebundled skill and the Oz web app; no CLI or custom code required.
Watch this short demo of creating and testing a scheduled agent:

***
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **A Warp account on an eligible plan** - Build, Max, or Business, with credits available. See [Access, Billing, and Identity](/platform/team-access-billing-and-identity/).
* **A cloud environment** - Agents run inside a configured environment that includes repos and other dependencies. If you don’t have one, follow the [Cloud Agents Quickstart](/platform/quickstart/) to create one first.
***
## 1. Set up a scheduled agent
[Section titled “1. Set up a scheduled agent”](#1-set-up-a-scheduled-agent)
1. From the [Schedules page](https://oz.warp.dev/schedules) in the Oz web app, click **New schedule**.
2. Enter a schedule name, e.g. `Weekly bug report triage`.
3. Expand **General**, then under **Agent**, choose the identity that will run the schedule. **Quick run** is the default and runs every execution as you. See [Run identity and pull request authorship](#run-identity-and-pull-request-authorship) before you decide.
4. Under **Skills**, select **github-bug-report-triage**.
5. Choose your environment.
6. Under **Frequency**, choose a preset or enter a custom cron expression (e.g., `0 9 * * 1` for every Monday at 9 AM).
7. Click **Create schedule**.
**Breaking it down:** The schedule lives in the Automation Platform‘s cloud infrastructure. Unlike a local cron job, it fires even when your machine is off. Each run starts a fresh, isolated session with no state carried over from previous executions, and every run is tracked and reviewable in the [Oz web app](/platform/oz-web-app/).
### Run identity and pull request authorship
[Section titled “Run identity and pull request authorship”](#run-identity-and-pull-request-authorship)
The **Agent** setting controls the identity behind every run, which determines how the agent authenticates to GitHub:
* **Quick run** (default) - Runs execute as the user who created the schedule, using that person’s GitHub credentials. Pull requests the agent opens are authored by that person.
* **Cloud agent** - Runs execute as the [cloud agent](/platform/agents/) you select. With [team GitHub authorization](/platform/team-access-billing-and-identity/#team-github-authorization) configured, the agent authenticates as the [Warp Factories](/factories/) GitHub App, so pull requests are authored by the app instead of an individual.
Choose a cloud agent for any schedule that opens pull requests. Pull requests authored by the app are clearly attributable to automation, and anyone on the team can review and approve them — including the person who created the schedule, who cannot approve a pull request authored by their own account.
Caution
The Oz CLI has no **Agent** flag, so a schedule created with `oz schedule create` always runs as its creator. To run it as a cloud agent, set **Agent** on the schedule in the Oz web app after creating it.
***
## 2. Watch your first run
[Section titled “2. Watch your first run”](#2-watch-your-first-run)
To verify your setup without waiting for the schedule to fire, trigger a test run now:
1. From the [Schedules page](https://oz.warp.dev/schedules) in the Oz web app, click the schedule you just created.
2. Click ⋮ and select **Run now**, then click **Run** to confirm.
Your test run will appear under **All** on the [Runs page](https://oz.warp.dev/runs). Once the schedule fires on its cron, those runs will appear under **Recurring**.
Runs are also accessible from the conversation panel view in the Warp app and on mobile via the Oz web app.
Note
**Prefer the CLI?** See [Scheduled Agents](/platform/triggers/scheduled-agents/) for `oz schedule create`, `oz schedule list`, and full schedule management commands. To use a custom skill instead of a prebundled one, see [Skills as Agents](/platform/skills-as-agents/).
***
## Next steps
[Section titled “Next steps”](#next-steps)
* **Choose the right unattended trigger** - Compare schedules, Slack, Linear, GitHub Actions, CLI, and API workflows in [Run agents unattended with schedules and triggers](/guides/agent-workflows/how-to-run-unattended-agents/).
* **Trigger agents from your tools** - Connect the Automation Platform to Slack or Linear to trigger agents from mentions or issue updates. See [Integrations Quickstart](/platform/integrations/quickstart/).
* **Manage and refine your schedule** - Change the frequency, swap skills, or pause and resume the schedule. See [Scheduled Agents](/platform/triggers/scheduled-agents/) for the full reference.
* **Share with your team** - Schedules and environments are shared across your Warp team, so everyone benefits automatically.
# Unmanaged architecture
Canonical page: [/platform/unmanaged-execution/](https://docs.warp.dev/platform/unmanaged-execution/)
> Run agents in your existing CI, Kubernetes, or dev environments using the `oz agent run` CLI with Warp tracking and observability.
With the unmanaged architecture, **you orchestrate agent runs** by invoking `oz agent run` directly from your existing CI pipelines, Kubernetes pods, VMs, or dev boxes. The agent runs on whatever host the command is executed from; Warp tracks the session for you but does not start or stop agents.
Note
Unmanaged is the right choice if you already have a system that schedules work (CI, internal orchestrators, cron, dev environments). If you’d rather have the Automation Platform trigger and route runs from Slack, Linear, schedules, or the API, use the [managed architecture](/factories/self-hosting/#managed-architecture) instead.
## When to use unmanaged
[Section titled “When to use unmanaged”](#when-to-use-unmanaged)
* **CI/CD pipelines** — Run agents as part of a build or deployment workflow. This is how the [`warpdotdev/oz-agent-action`](https://github.com/warpdotdev/oz-agent-action) GitHub Action works.
* **Kubernetes pods** — Run agents inside pods with access to your cluster’s network and services.
* **Dev boxes and VMs** — Run agents in pre-provisioned development environments. Especially useful for large monorepos with long setup times.
* **Existing orchestrators** — Drop `oz agent run` into any system that schedules work (Jenkins, Buildkite, internal job schedulers).
Unmanaged works on any platform Warp supports (Linux, macOS, Windows) with no dependency on Docker or any other sandboxing platform.
***
## Unmanaged quickstart
[Section titled “Unmanaged quickstart”](#unmanaged-quickstart)
*\~5 minutes*
No Docker, no worker daemon, no environment required — just the Oz CLI on any host that can reach the internet.
### Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **The Oz CLI** installed on the machine where agents will run. See [Installing the CLI](/agents/cli/oz-cli/#installing-the-cli) for platform-specific instructions.
* **A Warp API key** — For automation, create an agent API key in the [Oz web app](https://oz.warp.dev/settings). See [API Keys](/agents/cli/oz-cli/api-keys/) for personal vs. agent guidance.
### 1. Authenticate
[Section titled “1. Authenticate”](#1-authenticate)
Export your API key so the CLI can authenticate requests automatically:
```bash
export WARP_API_KEY="your_agent_api_key"
```
### 2. Run an agent
[Section titled “2. Run an agent”](#2-run-an-agent)
Invoke `oz agent run` in the directory where you want the agent to operate. The agent has access to whatever tools, network resources, and credentials the host provides.
```bash
oz agent run --prompt "Refactor the authentication module" --share team
```
**Expected outcome:** The agent starts immediately in the current working directory, and a tracked session appears in the [cloud agent dashboard](https://oz.warp.dev).
### 3. Control sharing
[Section titled “3. Control sharing”](#3-control-sharing)
Use `--share` to control who can attach to the session and steer the agent:
* `--share` — Share the session with yourself (accessible on other devices or in a browser).
* `--share team` or `--share team:view` — Give all team members read-only access.
* `--share team:edit` — Give all team members read/write access.
* `--share user@example.com` — Give a specific user read-only access.
* `--share user@example.com:edit` — Give a specific user read/write access.
The `--share` flag can be repeated to combine multiple sharing targets. If you authenticate with an agent API key, runs are automatically team-scoped.
***
## Example: GitHub Actions
[Section titled “Example: GitHub Actions”](#example-github-actions)
Warp maintains the [`warpdotdev/oz-agent-action`](https://github.com/warpdotdev/oz-agent-action) action for running agents in GitHub Actions. The action wraps `oz agent run` and is a drop-in for CI workflows:
```yaml
- name: Run agent
uses: warpdotdev/oz-agent-action@v1 # wraps `oz agent run` under the hood
with:
prompt: "Review the code changes on this branch"
warp_api_key: ${{ secrets.WARP_API_KEY }}
```
See [GitHub Actions integration](/platform/integrations/github-actions/) for full details.
## Example: Kubernetes
[Section titled “Example: Kubernetes”](#example-kubernetes)
Run an agent inside a Kubernetes pod with access to your cluster’s services:
```yaml
apiVersion: batch/v1
kind: Job
metadata:
name: oz-agent-task
spec:
template:
spec:
containers:
- name: oz-agent
image: warpdotdev/warp-agent:latest
command: ["agent", "run", "--prompt", "Run the test suite and report failures"]
env:
- name: WARP_API_KEY
valueFrom:
secretKeyRef:
name: warp-credentials
key: api-key
restartPolicy: Never
```
Caution
For production deployments, pin to a specific Docker image digest (e.g., `warpdotdev/warp-agent@sha256:...`) instead of `latest` to ensure reproducible builds.
Whether Kubernetes pods provide sufficient sandboxing for agents depends on your cluster configuration and risk profile. Evaluate your pod security policies, network policies, and RBAC settings based on your organization’s security requirements.
***
## Tracking and observability
[Section titled “Tracking and observability”](#tracking-and-observability)
Unmanaged agents are tracked on Warp’s backend. Each run creates a persistent session that your team can:
* **View** in the [cloud agent dashboard](https://oz.warp.dev).
* **Attach to** via [Agent Session Sharing](/agents/local-agents/session-sharing/) to monitor or steer.
* **API and SDK** — Query run data through the [Warp Platform API](/factories/api-and-sdk/) for custom dashboards or monitoring.
Unmanaged sessions benefit from the same shared configuration as other cloud agent runs — [MCP servers](/platform/mcp/), [secrets](/platform/secrets/), Warp Drive context, and saved prompts all apply.
Unmanaged runs don’t ship with the bundled declarations script, so end-of-run workspace snapshots are a no-op by default. To enable [handoff](/platform/handoff/) into a follow-up run, see [Customizing workspace snapshots](/platform/handoff/snapshots/).
***
## Related pages
[Section titled “Related pages”](#related-pages)
* [Self-hosting overview](/factories/self-hosting/) — Compare managed and unmanaged, plus the architecture decision guide.
* [External orchestrators](/factories/self-hosting/external-orchestrators/) — Compare one-shot Direct with the Command backend for externally allocated compute.
* [GitHub Actions integration](/platform/integrations/github-actions/) — Run agents in CI with the official action.
* [Deployment patterns](/factories/deployment-patterns/) — Pattern 1 (CLI-only) explains the unmanaged model conceptually.
* [Oz CLI](/agents/cli/oz-cli/) — Full CLI reference for `oz agent run` and related commands.
* [Agent Session Sharing](/agents/local-agents/session-sharing/) — Attach to running sessions to monitor or steer them.
# Cloud agent session sharing
Canonical page: [/platform/viewing-cloud-agent-runs/](https://docs.warp.dev/platform/viewing-cloud-agent-runs/)
> Open, inspect, and steer remote cloud agent runs in real time from Warp or the web.
Cloud agent session sharing lets you open, inspect, and continue interacting with agent tasks that are running on remote virtual machines. Whether a cloud agent was triggered from [integrations](/platform/integrations/) like Slack, Linear, GitHub Actions, or the [Oz CLI](/agents/cli/oz-cli/), you can view its full session, follow along in real time, ask follow-up questions, and even “fork” the work into your local Warp environment.
Use cloud agent session sharing when you need to inspect a cloud agent run, debug a failed automation, or give teammates a shared record of what the agent did. The shared session is the review surface for the run: it shows the prompt, plan, commands, logs, outputs, and follow-up messages where available.
[Cloud agent run sharing walkthrough](https://www.loom.com/embed/edd662da8de345ae979c4d39eb19c513)
This makes cloud agent runs observable, steerable, and collaborative — even if they weren’t initiated from your machine.
***
### What it enables
[Section titled “What it enables”](#what-it-enables)
With cloud agent session sharing, you can view the full remote session for a cloud agent run and:
* See every command the agent executed in the virtual environment
* Inspect context, logs, outputs, and [Computer Use](/agents/capabilities/computer-use/) artifacts
* Review the prompt, plan, task list, and decisions that led to the result
* Ask follow-up questions or give additional instructions after the task completes
* Bring the conversation into your local Warp session with Fork to local
* Continue working on remote-generated code locally
* Share links so teammates can view or collaborate on the session
Everything is accessible whether or not Warp is installed on the viewer’s machine.
## How it works
[Section titled “How it works”](#how-it-works)
#### 1. Open a remote cloud agent run
[Section titled “1. Open a remote cloud agent run”](#1-open-a-remote-cloud-agent-run)
When a cloud agent starts working — for example, from a Slack mention, a Linear issue, or a [CLI](/agents/cli/oz-cli/) trigger — Warp attaches a shareable link to the run.
* From [Slack](/platform/integrations/slack/), click **View Agent** in the agent response to open the session.
* From [Linear](/platform/integrations/linear/), click the ↗ **Warp** button (“Open in Warp”) on the ticket to open the session.
You can also open the session directly in your browser without installing Warp. Here, you’ll see the complete agent session running on a cloud VM, including all steps, logs, and context.
#### 2. Inspect the session like it’s your own
[Section titled “2. Inspect the session like it’s your own”](#2-inspect-the-session-like-its-your-own)
Once the session loads, you can:
* Scroll through the cloud agent’s actions
* See the prompt, plan, and decisions it made
* Review commands, logs, terminal output, and generated artifacts
* Review the code or config changes it produced
* Understand what environment it executed in
* Copy the session link into a PR, issue, incident review, or team thread when teammates need the same execution context
You’re viewing a remote VM, but the UI behaves like a local Warp session.
#### 3. Keep chatting with the remote agent
[Section titled “3. Keep chatting with the remote agent”](#3-keep-chatting-with-the-remote-agent)
Even if the cloud agent has completed its task, you can still ask follow-up questions or request more work. Warp sends your message back to the remote VM and continues the conversation.
Examples:
* “Can you explain which flag you changed?”
* “Give me a summary of what you modified.”
* “Show me the reasoning behind your last step.”
This works as long as the remote environment is still active.
#### 4. Handle inactive or shut-down sessions
[Section titled “4. Handle inactive or shut-down sessions”](#4-handle-inactive-or-shut-down-sessions)
Cloud agent environments automatically shut down after a period of inactivity. When that happens, you’ll see a notice that the virtual machine has been stopped.
If you still want to continue the conversation or work on the code, you can click **Fork to local**.
#### 5. Fork the session to your local Warp
[Section titled “5. Fork the session to your local Warp”](#5-fork-the-session-to-your-local-warp)
Forking is the cloud-to-local direction of [Handoff between local and cloud agents](/platform/handoff/) — see that page for the other directions (local-to-cloud and cloud-to-cloud).
Forking brings the cloud agent conversation into your local machine, so you can pick up where the agent left off.
Once forked:
* The session appears as a normal conversation in your local Warp
* You can keep prompting the agent using all your local tools
* You can continue inspecting or modifying the generated code
* The agent responds using your local environment instead of the remote VM
**Note:** If the cloud agent created a new git branch or repository in the remote VM, you’ll need to clone that branch locally first so the agent can keep working on the same code. Warp will streamline this workflow in a future release.
### Viewing sessions across devices
[Section titled “Viewing sessions across devices”](#viewing-sessions-across-devices)
Cloud agent sessions can be viewed from:
* The Warp app
* A browser via the web viewer
* Remote teammates using the shared link
* Local Warp sessions after forking
You get consistent visibility into the work regardless of where you open it.
### Related pages
[Section titled “Related pages”](#related-pages)
* [Managing cloud agents](/platform/managing-cloud-agents/) — Find cloud agent runs by source, status, trigger, or owner.
* [Multi-agent orchestration](/platform/orchestration/) — Inspect parent and child cloud runs that fan work out in parallel.
* [Computer Use](/agents/capabilities/computer-use/) — Review GUI and browser work performed by a cloud agent inside its sandbox.
* [Remote Control](/agents/cli-agents/remote-control/) — Publish a third-party CLI agent session to monitor and steer it from another device.
* [Attach agent session context to GitHub PRs](/guides/agent-workflows/how-to-attach-agent-session-context-to-github-prs/) — Share a run link with a PR so reviewers can inspect the agent’s execution context.
* [Agent Session Sharing](/agents/local-agents/session-sharing/) — Share local Warp agent or third-party CLI agent sessions.
# Warp quickstart
Canonical page: [/quickstart/](https://docs.warp.dev/quickstart/)
> Get up and running with Warp in about 10 minutes. Install, run your first commands, talk to an agent, and discover what makes Warp different.
Get up and running with Warp in about 10 minutes. Install the app, run your first commands using Blocks and the modern text editor, and start an agent conversation to write code, debug issues, or explore your codebase, all from natural language prompts inside the terminal.
***
## Prerequisites
[Section titled “Prerequisites”](#prerequisites)
* **macOS, Windows, or Linux** - See [Installation and setup](/getting-started/quickstart/installation-and-setup/) for minimum requirements per platform.
***
## 1. Install Warp
[Section titled “1. Install Warp”](#1-install-warp)
Download Warp from the [Warp download page](https://www.warp.dev/download) and follow the installer for your platform.
* macOS
Download and drag Warp into your Applications folder, or install with Homebrew:
```bash
brew install --cask warp
```
* Windows
Download and run the installer, or install with WinGet:
```powershell
winget install Warp.Warp
```
* Linux
Download the package for your distribution from the [Warp download page](https://www.warp.dev/download). For Debian/Ubuntu:
```bash
sudo apt install ./warp-terminal.deb
```
See [Installation and setup](/getting-started/quickstart/installation-and-setup/) for all Linux options.
When you launch Warp, you’ll see a terminal session ready for input. You can optionally sign up for an account (top right), or skip and start using Warp immediately.
## 2. Run a command and see Blocks
[Section titled “2. Run a command and see Blocks”](#2-run-a-command-and-see-blocks)
Run any command you’d normally use, for example:
```bash
ls -la
```
You’ll notice the output looks different from a traditional terminal. Every command and its output is grouped into a **Block** — a contained unit you can copy, search, filter, and navigate independently. Blocks are the foundation of how Warp organizes your terminal.
**What you can do with Blocks:**
* Click a Block to select it, then press `⌘C` (macOS) or `Ctrl+Shift+C` (Windows/Linux) to copy the output
* Use `⌘↑`/`⌘↓` (macOS) or `Ctrl+↑`/`Ctrl+↓` (Windows/Linux) to navigate between Blocks
* Click the filter icon on a Block to search within its output
Learn more about navigating, selecting, and acting on output in [Block basics](/terminal/blocks/block-basics/).
## 3. Try the input editor
[Section titled “3. Try the input editor”](#3-try-the-input-editor)
Warp’s input isn’t a standard terminal prompt, it’s a real text editor. Try the following functionality:
* **Multi-line editing** - Press `Shift+Enter` to add a new line. Try typing three separate `echo` lines, pressing `Shift+Enter` between each, then `Enter` to run them all at once.
* **Click to place your cursor** - Click anywhere in your input to move the cursor, just like a text editor.
* **Select and edit** - Click and drag to select text, then type to replace it.
All three commands run in sequence, and each produces its own Block. No need to run commands one at a time.
Learn more about cursor movement, selections, and multi-line input in [Modern text editing](/terminal/editor/).
## 4. See autosuggestions and completions
[Section titled “4. See autosuggestions and completions”](#4-see-autosuggestions-and-completions)
Start typing a command you’ve run before. You’ll see a faded suggestion appear inline based on your shell history. Press `→` to accept it instantly.
Press `Tab` while typing to see completions for commands, flags, and file paths. Warp provides enhanced completions beyond what your shell offers natively.
If you mistype a command, Warp detects the error and suggests a correction. Accept the fix or dismiss it and continue.
Learn more about [Autosuggestions](/terminal/command-completions/autosuggestions/) and [Tab completions](/terminal/command-completions/completions/).
## 5. Ask your first agent question
[Section titled “5. Ask your first agent question”](#5-ask-your-first-agent-question)
Everything you’ve done so far has been in **terminal mode**, running shell commands the way you normally would. Warp also has **Agent Mode**, a dedicated conversation view where you interact with the Warp Agent, Warp’s built-in agent, using natural language.
Start an agent conversation by pressing `⌘↩` (macOS) or `Ctrl+Shift+Enter` (Windows/Linux). Then type a prompt:
```plaintext
Explain the architecture of this project
```
The Warp Agent reads your codebase, understands its structure, and responds with a context-aware explanation. From here you can ask follow-up questions, have the Warp Agent write or refactor code, debug errors, or run commands on your behalf — all within the same conversation.
Note
You don’t always need to switch modes manually. If you type a natural-language prompt in terminal mode, Warp auto-detects it and offers to send it to an agent.
Warp also works with third-party CLI agents like Claude Code and Codex. Learn more about [third-party CLI agents](/agents/cli-agents/overview/).
To learn more about switching between modes, see [Terminal and Agent modes](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/).
***
## What to explore next
[Section titled “What to explore next”](#what-to-explore-next)
Now that you have the basics, check out the features that make Warp a full development environment:
* **[Customizing Warp](/getting-started/quickstart/customizing-warp/)** — Pick a theme, configure your prompt, choose your AI model, and import keybindings from another terminal.
* **[Codebase Context](/agents/capabilities/codebase-context/)** — Index your Git repositories so agents understand your code and give context-aware answers across large, multi-repo systems.
* **[Cloud agents](/platform/)** — Run agents in the background for PR review, issue triage, dependency updates, and other tasks that don’t need your immediate attention.
* **[Keyboard shortcuts](/getting-started/keyboard-shortcuts/)** — The full shortcut reference for power users.
# Support & Community
Canonical page: [/support-and-community/](https://docs.warp.dev/support-and-community/)
> Contact Warp support, join the community, and find help for bugs, billing, and enterprise issues.
## Contact support
[Section titled “Contact support”](#contact-support)
### Subscribers and Enterprise
[Section titled “Subscribers and Enterprise”](#subscribers-and-enterprise)
* **Technical issues or questions** - For bugs, credits, and other technical issues, email <support@warp.dev>.
* **Billing issues or questions** - For refunds, cancellations, and other billing questions, email <billing@warp.dev>.
* **Enterprise** - Direct all feedback and issues to your designated Slack channel.
For other ways to send feedback, gather logs, or file a bug report, see [Sending feedback and logs](/support-and-community/troubleshooting-and-support/sending-us-feedback/).
## Find your space
[Section titled “Find your space”](#find-your-space)
### Join the community
[Section titled “Join the community”](#join-the-community)
Our Slack community is where workflows get shared, bugs get squashed, and ideas turn into features. Talk directly with Warp engineers and other developers.
Tip
[**Join the Warp community on Slack**](https://go.warp.dev/join-preview)
Built something with Warp? An agent workflow, a CLI tool, a creative terminal setup? Drop it in `#how-do-you-warp` — we spotlight community projects regularly.
### Build with us on GitHub
[Section titled “Build with us on GitHub”](#build-with-us-on-github)
Bugs, feature requests, and what’s shipping next. Your upvotes decide what we prioritize.
[**Open an issue**](https://github.com/warpdotdev/warp/issues)
Warp’s client is open source. See [Contributing to Warp](/support-and-community/community/contributing/) for the full set of contribution paths, including opening pull requests, contributing themes and workflows, and sharing Warp Drive objects.
### Attend events
[Section titled “Attend events”](#attend-events)
We host [live events](https://luma.com/warpdotdev) year-round — product demos, launch celebrations, community Q\&As, and more. One recurring favorite:
Note
**Warp 101 livestreams** — A live walkthrough of Warp features, tips, and Q\&A with the team, held every two weeks. [**Register for upcoming events on Luma**](https://luma.com/warpdotdev)
### Follow along
[Section titled “Follow along”](#follow-along)
* [**X**](https://x.com/warpdotdev) - What we’re shipping and what the community is building
* [**YouTube**](https://www.youtube.com/@warpdotdev) - Tutorials, demos, and product deep dives
* [**LinkedIn**](https://www.linkedin.com/company/warpdotdev) - Engineering deep dives and company news
* [**Reddit**](https://www.reddit.com/r/warpdotdev/) - Unfiltered discussions, feature debates, and Q\&A
## Programs
[Section titled “Programs”](#programs)
* [**Warp Preview**](/support-and-community/community/warp-preview-and-alpha-program/) — Try experimental features before anyone else. Your feedback directly shapes what ships.
* [**Refer a Friend**](/support-and-community/community/refer-a-friend/) — Send Warp to a developer you think would love it. Earn themes, swag, and gift cards.
Note
**Ambassador program**
We’re building an Ambassador program for developers who want to lead and grow the Warp community. Join the [community Slack](https://go.warp.dev/join-preview) to hear when applications open.
## More help
[Section titled “More help”](#more-help)
* [Sending feedback and logs](/support-and-community/troubleshooting-and-support/sending-us-feedback/)
* [Known issues](/support-and-community/troubleshooting-and-support/known-issues/)
* [Plans, pricing, and refunds](/support-and-community/plans-and-billing/plans-pricing-refunds/)
* [Privacy](/support-and-community/privacy-and-security/privacy/)
# Contributing to Warp
Canonical page: [/support-and-community/community/contributing/](https://docs.warp.dev/support-and-community/community/contributing/)
> Contribute to Warp's open source client by filing issues, opening pull requests, building themes, and sharing workflows.
Warp’s client is open source under [AGPL v3](https://github.com/warpdotdev/warp/blob/master/LICENSE-AGPL) at [`warpdotdev/warp`](https://github.com/warpdotdev/warp), and there’s room for every kind of contribution — from a one-line bug report to a full feature PR, a new theme, or a workflow that ships to every Warp user. For the full code contribution flow, see [`CONTRIBUTING.md`](https://github.com/warpdotdev/warp/blob/master/CONTRIBUTING.md).
## Ways you can contribute
[Section titled “Ways you can contribute”](#ways-you-can-contribute)
* **Report a bug or request a feature** - [File an issue](https://github.com/warpdotdev/warp/issues/new/choose) in [`warpdotdev/warp`](https://github.com/warpdotdev/warp), or [explore existing issues](https://github.com/warpdotdev/warp/issues?q=is%3Aissue+is%3Aopen+sort%3Areactions-%2B1-desc) to comment on or upvote ones that matter to you. Clear reproductions and upvotes help Warp prioritize.
* **Contribute code** - Claim any issue labeled `ready-to-spec` or `ready-to-implement`, then open a spec or code PR. [`CONTRIBUTING.md`](https://github.com/warpdotdev/warp/blob/master/CONTRIBUTING.md) covers the spec format, tests, `./script/presubmit`, and the PR template.
* **Build a theme** - Submit a new color scheme or improve an existing one at [`warpdotdev/themes`](https://github.com/warpdotdev/themes).
* **Share a workflow** - Add reusable command patterns to [`warpdotdev/workflows`](https://github.com/warpdotdev/workflows). Merged workflows ship to every Warp user.
* **Publish Warp Drive objects** - Share Workflows, Notebooks, Rules, and Prompts publicly from [Warp Drive](/knowledge-and-collaboration/warp-drive/).
* **Find an issue to pick up** - Browse [Warp’s live agent dashboard](https://build.warp.dev), which shows the work Warp’s agents are tackling across `warpdotdev/warp`. Use it to spot gaps, avoid duplicate work, and surface issues that haven’t been claimed yet.
* **Help others in the community** - Answer questions in the [Warp community Slack](https://go.warp.dev/join-preview), and join conversations in [GitHub Discussions](https://github.com/warpdotdev/warp/discussions).
## Send feedback and bug reports
[Section titled “Send feedback and bug reports”](#send-feedback-and-bug-reports)
The fastest way to file a bug or feature request is the [`/feedback`](/support-and-community/troubleshooting-and-support/sending-us-feedback/#using-feedback-in-warp) slash command inside Warp. It drafts and files a GitHub issue without leaving the terminal.
Other channels:
* File an issue directly in [`warpdotdev/warp`](https://github.com/warpdotdev/warp/issues/new/choose).
* Press `⌘+Shift+F` (macOS) or `Ctrl+Shift+F` (Windows/Linux) to open the in-app feedback dialog. On macOS, you can also use the **Send Feedback** option in Warp’s Help menu.
* Email <privacy@warp.dev> for privacy questions.
For logs, crash reports, CPU samples, and AI conversation IDs, see [Sending feedback and logs](/support-and-community/troubleshooting-and-support/sending-us-feedback/).
## Reporting a security vulnerability
[Section titled “Reporting a security vulnerability”](#reporting-a-security-vulnerability)
Danger
Do not file public issues for security vulnerabilities.
If you believe you’ve found a security vulnerability, follow responsible disclosure practices and do not open a public GitHub issue or pull request, as this could expose the vulnerability before a fix is available. Include reproduction steps, impact, and any proof of concept when you report it through one of the following channels:
* **Email:** <security@warp.dev>
* **GitHub Security Advisory:** [Open a private advisory](https://github.com/warpdotdev/Warp/security/advisories/new)
We will acknowledge your report promptly and work with you to understand and resolve the issue as quickly as possible. Full guidance is in [`SECURITY.md`](https://github.com/warpdotdev/warp/blob/master/SECURITY.md#reporting-a-vulnerability).
## Code of conduct
[Section titled “Code of conduct”](#code-of-conduct)
Warp’s open source repositories follow the [Contributor Covenant](https://www.contributor-covenant.org/) v2.1. Read the [full text](https://github.com/warpdotdev/warp/blob/master/CODE_OF_CONDUCT.md), or report violations to <warp-coc@warp.dev>.
# Refer a friend and earn rewards
Canonical page: [/support-and-community/community/refer-a-friend/](https://docs.warp.dev/support-and-community/community/refer-a-friend/)
> Think Warp would be the ideal product for someone you know? You can invite your team or friends within the app and earn rewards.
Note
Go to **Settings** > **Referrals** to open the invite a friend referral dialog.
**There are two ways you can invite a friend:**
1. Send them an invite link. They will be directed to our product download page.
2. Input their email address, which we’ll use to email them with your referral link.
## Referral rewards program
[Section titled “Referral rewards program”](#referral-rewards-program)
We give out themes, swag, and other perks as thanks for helping to grow our community.
The tiers are as follows:
| Referrals | Reward | Digital Gift Card Alternative |
| --------- | -------------------- | :---------------------------: |
| 1 | Exclusive Theme | $0 |
| 5 | Stickers and Keycaps | $5 |
| 10 | T-Shirt | $10 |
| 20 | Moleskin Notebook | $20 |
| 35 | Baseball Hat | $35 |
| 50 | Hoodie | $50 |
| 75 | Hydroflask | $75 |
| 100 | North Face Backpack | $100 |
By participating in Warp’s referral program, you agree to the [Referral program terms and conditions](/support-and-community/community/refer-a-friend/#referral-program-terms-and-conditions).
### Your friend gets a theme
[Section titled “Your friend gets a theme”](#your-friend-gets-a-theme)
If your friend joins and activates their Warp account after clicking your invite link, they will receive a unique theme.
## Referral program terms and conditions
[Section titled “Referral program terms and conditions”](#referral-program-terms-and-conditions)
> **Last Updated:** November 27, 2024
### 1 referral: an exclusive theme
[Section titled “1 referral: an exclusive theme”](#1-referral-an-exclusive-theme)
When someone joins Warp with your referral code, the referral theme will become available in your theme picker after you restart the app. We also send an email alerting you. This reward is available to all users worldwide.
### All other referral tiers
[Section titled “All other referral tiers”](#all-other-referral-tiers)
Once you’ve hit the other referral tiers, we’ll email you with details on how to claim your reward. Physical rewards are available to users residing in the United States, and Warp will cover shipping costs for these users. International users can also claim physical rewards; however, they will be responsible for any customs fees. For all users, there’s an option to claim a digital reward (gift card) instead of physical Warp swag.
### International users
[Section titled “International users”](#international-users)
International users who choose physical rewards are responsible for paying any customs fees associated with shipping. Estimated costs are provided in the [approximate customs fees by region](/support-and-community/community/refer-a-friend/#approximate-customs-fees-by-region) section below. Note that once the package leaves the United States, Warp no longer has visibility or control over the shipment process, including any customs-related issues or fees that may arise.
Alternatively, international users may opt to receive a digital gift card instead of a physical reward.
Note: for users who qualified for referral rewards before October 15th, 2024, Warp will cover all shipping and customs costs. Starting from that date onwards, international users receiving referral rewards will be responsible for paying any customs fees associated with shipping.
### Shipping time frame
[Section titled “Shipping time frame”](#shipping-time-frame)
Physical rewards may take 2 to 3 weeks to arrive for users located in the United States, and 4 to 12 weeks for international users. After claiming your order, you will receive an email with a shipping confirmation and a tracking link from Printfection, our swag vendor.
If you have any questions about the status of your shipment or order, please reach out to <support@printfection.com> with your order number.
### General terms and conditions
[Section titled “General terms and conditions”](#general-terms-and-conditions)
Referrals must be valid and confirmed by Warp to count towards rewards. This means the referred user must accept the referral via the referral link and log into Warp’s desktop application.
Warp reserves the right, at its sole discretion, to disqualify any referrals deemed fraudulent. Any users who refer fake emails or users will be disqualified at the sole discretion of Warp.
Warp reserves the right to modify or terminate the referral rewards program at any time without prior notice. Participation in the swag program constitutes acceptance of these terms and conditions.
If you have any questions about the referral program, please contact <referrals@warp.dev>.
### Digital gift card rewards
[Section titled “Digital gift card rewards”](#digital-gift-card-rewards)
All amounts are listed in USD. Rewards are based on the number of valid referrals.
| Number of referrals | Gift card amount |
| :-----------------: | :--------------: |
| 1 | $0 |
| 5 | $5 |
| 10 | $10 |
| 20 | $20 |
| 35 | $35 |
| 50 | $50 |
| 75 | $75 |
| 100 | $100 |
### Approximate customs fees by region
[Section titled “Approximate customs fees by region”](#approximate-customs-fees-by-region)
All amounts are listed in USD. Fees are estimates and may vary regardless of package size.
| Country / region | Approximate customs fees |
| :-------------------------------------------------: | :----------------------: |
| Canada & Mexico | $40 to $70 |
| Europe | $40 to $80 |
| Others (Asia, South America, Africa, Oceania, etc.) | $50 to $120 |
\*Note: The approximate customs fees provided are estimates and may vary based on your country’s specific import regulations, taxes, and duties. Actual fees can differ due to factors such as package contents, declared value, and current customs policies. We recommend checking with your local customs office or postal service for precise information relevant to your situation.
## Referral rewards program FAQs
[Section titled “Referral rewards program FAQs”](#referral-rewards-program-faqs)
#### **”I have referred people but have not received an email.”**
[Section titled “”I have referred people but have not received an email.””](#i-have-referred-people-but-have-not-received-an-email)
Allow a few hours for the referral system to process and send email updates. If you still haven’t received an email after a reasonable amount of time, contact us at <referrals@warp.dev> and we’ll look into it.
#### **”I’ve claimed my physical reward but have issues receiving my package.”**
[Section titled “”I’ve claimed my physical reward but have issues receiving my package.””](#ive-claimed-my-physical-reward-but-have-issues-receiving-my-package)
If you experience issues with your shipment, please respond to the shipping notification email you should have received from Printfection. For further assistance, contact our swag vendor’s operations team at <support@printfection.com> with your order number.
#### **”I’ve referred friends, but they didn’t use the link. Does it still count?”**
[Section titled “”I’ve referred friends, but they didn’t use the link. Does it still count?””](#ive-referred-friends-but-they-didnt-use-the-link-does-it-still-count)
Unfortunately, any referrals who didn’t use your link will not count towards the rewards, and we have no way of modifying the referral count.
#### **”I’ve referred friends, but they joined anonymously. Does it still count?”**
[Section titled “”I’ve referred friends, but they joined anonymously. Does it still count?””](#ive-referred-friends-but-they-joined-anonymously-does-it-still-count)
For a referral to count, new users must sign up and actively use Warp. Unfortunately, we’re unable to associate anonymous users with specific referral links at this time.
We’re actively working on solutions to make the referral process more seamless and reliable for anonymous users. Stay tuned for updates as we improve this experience.
#### **”The reward tiers recently changed with the new swag items. I previously qualified for X. What happens now, and are the new swag items retroactive?”**
[Section titled “”The reward tiers recently changed with the new swag items. I previously qualified for X. What happens now, and are the new swag items retroactive?””](#the-reward-tiers-recently-changed-with-the-new-swag-items-i-previously-qualified-for-x-what-happens-now-and-are-the-new-swag-items-retroactive)
Our referral program was updated on November 21, 2024, with new reward tiers and exciting swag options. To ensure a smooth transition, we will honor previous reward tiers alongside the updated program until December 15, 2024.
If you’re unsure how these changes impact your previous qualifications or eligibility for the new swag items, feel free to reach out to us at <referrals@warp.dev> for assistance.
# Warp Preview program
Canonical page: [/support-and-community/community/warp-preview-and-alpha-program/](https://docs.warp.dev/support-and-community/community/warp-preview-and-alpha-program/)
> Warp Preview is an early-access build of Warp with experimental features. Try what's next before it ships.
Warp Preview is an early-access program that allows you to explore Warp’s newest and most experimental features. It’s independent from the stable build, so you can always revert to a reliable version of Warp whenever you need it.
### Key Warp Preview features
[Section titled “Key Warp Preview features”](#key-warp-preview-features)
* **Early access** - Try out experimental features before they’re officially released.
* **Faster updates** - Enjoy frequent updates and patches as we refine new capabilities.
* **Direct impact** - Your feedback plays a critical role in shaping Warp’s future.
To learn more about Warp Preview, check out our [launch blog post](https://www.warp.dev/blog/warp-preview).
### Getting started with Warp Preview
[Section titled “Getting started with Warp Preview”](#getting-started-with-warp-preview)
1. **Download**: Get the Warp Preview build from the [Warp Preview download page](https://www.warp.dev/download-preview).
2. **Sign in**: [Log in](/getting-started/quickstart/installation-and-setup/#log-in-to-warp-optional) with your Warp account (not optional for Warp Preview).
3. **Run side-by-side**: You can keep Warp Preview alongside your stable Warp installation.
### Important notes
[Section titled “Important notes”](#important-notes)
* **Experimental build** - Expect occasional bugs or incomplete features.
* **Login required** - You must sign in to use Warp Preview. This helps us gather feedback, quickly diagnose critical issues, and ensure we can reach out if you need support.
* **Flexibility** - Switch between Preview and Stable builds at any time.
* **Distinct icon** - Warp Preview uses a unique icon to help distinguish it from the stable version.
### Providing Warp Preview feedback
[Section titled “Providing Warp Preview feedback”](#providing-warp-preview-feedback)
Share feedback, report bugs, and discuss Preview features in the [community Slack](https://go.warp.dev/join-preview). You can also [send feedback directly from the app](/support-and-community/troubleshooting-and-support/sending-us-feedback/#sending-warp-feedback).
# Plans and billing
Canonical page: [/support-and-community/plans-and-billing/](https://docs.warp.dev/support-and-community/plans-and-billing/)
> Understand your Warp plan options, how credits work, and how to manage billing settings.
Warp offers flexible plans for individual developers, teams, and enterprises. Credits power all agent features and meter across three buckets: AI credits (the model call), compute credits (the sandbox an agent runs in), and platform credits (run lifecycle, integrations, dashboard, APIs, and observability). Top up your monthly allowance with add-on credit purchases or enable auto-reload.
Looking for **Bring Your Own API Key** or **custom inference endpoints**? They’ve moved to [Inference & providers](/agents/inference/model-choice/) under Warp Agents.
* [**Plans, pricing, and refunds**](/support-and-community/plans-and-billing/plans-pricing-refunds/) - Compare plans, pricing tiers, and refund policies.
* [**Credits**](/support-and-community/plans-and-billing/credits/) - How credits are used and calculated across AI features.
* [**Add-on credits**](/support-and-community/plans-and-billing/add-on-credits/) - Purchase additional credits or enable auto-reload.
* [**Platform credits**](/support-and-community/plans-and-billing/platform-credits/) - Billed by the agent hour; cover Warp’s platform layer on cloud agent runs and local runs with customer-supplied inference.
* [**Pricing FAQs**](/support-and-community/plans-and-billing/pricing-faqs/) - Answers to common questions about plans and billing.
# Add-on credits
Canonical page: [/support-and-community/plans-and-billing/add-on-credits/](https://docs.warp.dev/support-and-community/plans-and-billing/add-on-credits/)
> Purchase add-on credits to keep using premium AI models after reaching your monthly credit limit, or to top up on the Free plan without subscribing.
Add-on credits let you continue using premium AI models even after you’ve reached your monthly credit limit — at lower rates and with more control over spending. You can also buy them on the Free plan without subscribing.
In the Warp app, you can manage and purchase add-on credits directly in **Settings** > **Billing and usage**.

Add-on credit settings under Billing and usage.
### How do add-on credits work?
[Section titled “How do add-on credits work?”](#how-do-add-on-credits-work)
Add-on credits extend your AI usage beyond the included monthly quota in your plan. Once your plan’s credits are used up, Warp will automatically begin drawing from your available add-on credits.
If you’ve enabled **auto-reload**, new credits will be added automatically and billed based on your selected configuration of monthly spending limit and selected purchase amount.
Add-on credits are available on every self-serve plan — Free, Build, Max, and Business — plus Enterprise. The Free plan buys the same packs at a higher rate than paid plans; see [Warp pricing](https://www.warp.dev/pricing) for current rates. On both self-serve and Enterprise plans, add-on credits are shared across your team: every purchase goes into a single team-wide pool that all members draw from. These credits **roll over across billing cycles** and remain valid for **12 months from the purchase date**.
Add-on credits can be spent on any credit type, so a single balance covers AI credits, compute credits, and [platform credits](/support-and-community/plans-and-billing/platform-credits/).
### Who can purchase add-on credits
[Section titled “Who can purchase add-on credits”](#who-can-purchase-add-on-credits)
Any active member of a team can purchase add-on credits. You don’t need to be a team admin, and you don’t need a paid subscription — Free plan users can buy packs and spend them on any model. Credits you buy go into your team’s shared pool, so any member’s usage can draw them down.
Team admins keep the team-level controls:
* **Team-wide monthly spend cap** - Caps what the whole team can spend on add-on credits per calendar month, across all members.
* **Auto-reload** - While an admin has auto-reload on, individual members can’t purchase add-on credits manually.
* **The team’s payment method** - Every purchase charges the payment method saved for the team, and only admins can change or remove it. See [Which card is charged when a team member buys add-on credits?](/support-and-community/plans-and-billing/pricing-faqs/#which-card-is-charged-when-a-team-member-buys-add-on-credits).
### Purchasing add-on credits
[Section titled “Purchasing add-on credits”](#purchasing-add-on-credits)
You have two options for purchasing more credits:
#### 1. Buy on-demand
[Section titled “1. Buy on-demand”](#1-buy-on-demand)
You can purchase additional add-on credits at any time directly within the app under **Settings** > **Billing and usage**. Buying more credits upfront provides a larger discount.
The table below shows the available credit denominations, their prices, and corresponding discounts:
| Credits | Price (USD) | Price per Credit | Discount |
| ------- | ----------- | ---------------- | --------- |
| 400 | $10 | $0.025 | Base rate |
| 1,000 | $20 | $0.020 | 20% off |
| 3,000 | $50 | $0.016 | \~35% off |
| 6,500 | $100 | $0.0153 | \~40% off |
#### 2. Enable auto-reload
[Section titled “2. Enable auto-reload”](#2-enable-auto-reload)
Auto-reload automatically purchases more credits whenever the available add-on credit balance drops below **100 credits**. On a team, reloaded credits are added to the team’s shared pool.
By default, **auto-reload is disabled for new subscribers**. When you turn it on, it starts with a **$200 monthly spend limit**, which you can adjust anytime in **Settings** > **Billing and usage**.
Auto-reload uses the same denominations and discounts as manual purchases. The denomination you select (e.g., 400, 1,000, 3,000, or 6,500 credits) will repeat each time your balance is depleted, up to your monthly spending limit. Larger denominations offer up to \~40% off per credit.
Note
You can opt in and choose your reload amount when subscribing to a paid plan on the [Warp upgrade page](https://app.warp.dev/upgrade), or change your configuration anytime in **Settings** > **Billing and usage**.
#### Configuring a monthly spend limit
[Section titled “Configuring a monthly spend limit”](#configuring-a-monthly-spend-limit)
Your monthly spend limit sets the maximum amount you can spend on add-on credits in a single calendar month.
* The default limit is $200, but you can increase or decrease it anytime in **Settings** > **Billing and usage**.
* **If a credit purchase would exceed your limit, it won’t process** — you’ll need to either raise your limit or choose a smaller add-on credit amount.
* Once your limit is reached, no additional add-on credit purchases (manual or automatic) will occur until:
* The next calendar month begins, or
* You update your limit in settings.
Caution
Your monthly spend limit is separate from your billing cycle (which determines when your subscription renews). The limit resets at the start of each calendar month.
### Billing and credit usage
[Section titled “Billing and credit usage”](#billing-and-credit-usage)
When your monthly credit balance renews:
1. Warp first consumes your included monthly credits (e.g., Build plan credits).
2. After those are used, Warp continues to draw from any available add-on credits.
3. If your add-on credits run out and auto-reload is enabled, Warp will automatically purchase more up to your monthly limit.
On a team, that add-on step is also fixed: shared team grants drain before any remaining user-scoped grants. You cannot choose to spend personal credits first while on a team.
You can track your remaining credits and spending in the credits transparency footer and in **Settings** > **Billing and usage**.
#### Teams using add-on credits
[Section titled “Teams using add-on credits”](#teams-using-add-on-credits)
On self-serve plans (Free, Build, Max, and Business), add-on credits are shared across the team. Purchases from any member — manual or auto-reload — go into a single team-wide pool, and every member’s usage draws from that pool once their plan-included credits are used up. Any leftover user-scoped balances (from the May–August 2026 window) are used only after the shared pool is exhausted. One member’s heavy usage can consume credits another member purchased; use the team-wide spend cap to limit what the team spends each month.
Team admins manage add-on credit settings for the team in **Settings** > **Billing and usage**:
* **Team-wide spend cap** — Sets the maximum amount the team can spend on add-on credits per calendar month, applied across all members.
* **Auto-reload** — When enabled, the admin selects an add-on credit denomination for the team. Warp automatically purchases that denomination and adds it to the team’s shared pool whenever the add-on credit balance available to a member drops below 100 credits, subject to the team-wide spend cap. While auto-reload is on, individual users cannot purchase add-on credits manually.
* **Manual purchases** — When auto-reload is off, eligible team members can buy add-on credits for the team’s shared pool, as long as the team stays below the team-wide spend cap.
For how cloud agent runs that aren’t initiated by a specific team member (scheduled runs, agent API key runs) are billed, see [How are cloud agent runs on team plans billed when no individual user triggered them?](/support-and-community/plans-and-billing/pricing-faqs/#how-are-cloud-agent-runs-on-team-plans-billed-when-no-individual-user-triggered-them) in the Pricing FAQs.
### Plan changes and cancellations
[Section titled “Plan changes and cancellations”](#plan-changes-and-cancellations)
Any purchased add-on credits remain in your account and can continue to be used for up to 12 months after purchase.
If you move to the Free plan, your remaining add-on credits aren’t removed and they keep their original 12-month expiration from the purchase date. You can keep spending them on the Free plan and buy more, though new purchases use the Free plan rate until you re-subscribe.
Caution
Add-on credits are tied to your team. Leaving the team, being removed by an admin, or having the team deleted revokes your access to any credits tied to that team.
#### When team membership changes
[Section titled “When team membership changes”](#when-team-membership-changes)
Add-on credits are tied to the team they were purchased under. The flows below describe what happens in common team-membership scenarios:
* **A user leaves a team** - You lose access to any add-on credits tied to that team. If you rejoin the same team later, you regain access to any unused, non-expired credits. The admin pays a prorated rate for your seat on rejoin.
* **An admin removes a member** - That member loses access to any add-on credits tied to the team. If they rejoin later, they regain access to any unused, non-expired credits.
* **An admin deletes the team** - Any remaining add-on credits must be used or removed before a team can be deleted. Contact <support@warp.dev> if you need help with this.
Note
All unused add-on credits remain valid for 12 months from purchase, and they stay tied to the team they were purchased under.
# Warp credits and billing
Canonical page: [/support-and-community/plans-and-billing/credits/](https://docs.warp.dev/support-and-community/plans-and-billing/credits/)
> How Warp credits work: the AI, compute, and platform credit buckets, what drives credit usage, and how limits and billing apply.
## What are Warp credits?
[Section titled “What are Warp credits?”](#what-are-warp-credits)
Warp credits pay for Warp-provided inference, hosted compute, and platform services. An agent run consumes from the credit buckets that apply to where it runs and who provides its inference.
Warp meters credits across three types of infrastructure — inference, compute, and platform — each with its own bucket. Credit types and where an agent runs (local or cloud) are independent: each agent run consumes from whichever credit types apply to it.
* **AI credits** cover inference: the LLM call itself. Consumed when Warp pays for the model call through Warp-managed providers.
* **Compute credits** cover compute: the sandbox an agent runs in. Consumed when an agent run uses Warp-hosted compute. In practice this is cloud agent runs; local agent runs use your own machine and don’t consume compute credits. See [compute credits](/support-and-community/plans-and-billing/credits/#compute-credits).
* **Platform credits** cover Warp’s platform layer: run lifecycle, integrations, dashboard, APIs, and observability. Apply to every cloud agent run, plus local agent runs on Business and Enterprise plans that use customer-supplied inference, including BYOK, a [ChatGPT subscription](/agents/inference/chatgpt-subscription/), a custom inference endpoint, or BYOLLM. See [platform credits](/support-and-community/plans-and-billing/platform-credits/).
All three buckets draw from the same Warp credit pool and [add-on credits](/support-and-community/plans-and-billing/add-on-credits/), so you can manage them as a single balance in the Warp app under **Settings** > **Billing and usage**.
When Warp provides inference, each interaction consumes **at least one AI credit**, though more complex interactions may use multiple credits. Because of factors such as codebase size, model choice, number of tool calls, and the nature of LLMs, credit usage is **non-deterministic** — two similar prompts can still use a different number of credits.
Note
For a general breakdown of what factors contribute to how many credits are consumed, see [How are Warp credits calculated?](/support-and-community/plans-and-billing/credits/#how-are-warp-credits-calculated)
There’s no exact formula for predicting usage. Experiment with different prompts and models and track how many credits they consume.
### Tracking your credit usage
[Section titled “Tracking your credit usage”](#tracking-your-credit-usage)
In an agent conversation, a **turn** represents a single exchange (a response from the LLM). To see how many credits a turn consumed, hover over the **credit count chip** at the bottom of the agent’s response:

Conversation usage footer.
Note
You can view your total credit usage, along with other billing details, in **Settings** > **Billing and usage**.
### Credit limits and billing
[Section titled “Credit limits and billing”](#credit-limits-and-billing)
* **Seat-level allocation**: On team plans, credit limits apply per seat — each team member has their own allowance. Individual users (not on a team) also have their own credit allocation.
* **Cloud agents and integrations**: Individual users can run cloud agents via the CLI and API, drawing from their Warp credits. Slack and Linear integrations require team membership.
* **Credit limits by plan**: The Free plan doesn’t include bundled AI usage for the Warp Agent. To use the Warp Agent, [upgrade to a paid plan](https://www.warp.dev/pricing), buy [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) without subscribing, or bring your own inference with [Bring Your Own API Key (BYOK)](/agents/inference/bring-your-own-api-key/), a [ChatGPT subscription](/agents/inference/chatgpt-subscription/), a [custom inference endpoint](/agents/inference/custom-inference-endpoint/), or a [SuperGrok or X Premium subscription](/agents/inference/grok-subscription/). On paid plans, once you reach your monthly credit limit you can continue using AI with usage-based billing via [add-on credits](/support-and-community/plans-and-billing/add-on-credits/).
### Other features that use credits
[Section titled “Other features that use credits”](#other-features-that-use-credits)
In addition to direct agent conversations, the following features also consume credits:
* [Generate](/agents/local-agents/generate/) helps you look up commands and suggestions as you type. As you refine your input, multiple credits may be used before you select a final suggestion.
* [AI Autofill in Workflows](/knowledge-and-collaboration/warp-drive/workflows/#ai-autofill) counts as a credit each time it is run.
Tip
Regular shell commands in Warp do not consume or count towards credits.
## How are Warp credits calculated?
[Section titled “How are Warp credits calculated?”](#how-are-warp-credits-calculated)
A **credit** in Warp is a unit of work representing the total processing required to complete an interaction with an agent. It is **not** the same as “one user message” — instead, it scales with the number of tokens processed during the interaction.
In short: **the more tokens used, the more credits consumed**.
Several factors influence how many credits are counted for a single interaction:
### 1. The LLM model used
[Section titled “1. The LLM model used”](#1-the-llm-model-used)
Smaller, faster models consume fewer credits than larger reasoning models. The largest frontier reasoning models (the latest Claude Opus models, for example) consume the most tokens and credits per interaction. Credit usage generally tracks the model’s API pricing.
Note
**Tip**: If your task doesn’t require deep reasoning, planning, or multi-step problem solving, choose a more lightweight model to reduce credit usage.
### 2. Tool calls triggered by the agent
[Section titled “2. Tool calls triggered by the agent”](#2-tool-calls-triggered-by-the-agent)
Agents in Warp make a variety of tool calls, including:
* Searching for files (grep)
* Retrieving and reading files
* Making and applying code diffs
* Gathering web or documentation context
* Running other utilities
Some prompts require only a couple of tool calls, while others may trigger many — especially if the agent needs to explore your development environment, navigate a large codebase, or apply complex changes. **More tool calls = more credits**.
### 3. Task complexity and number of steps
[Section titled “3. Task complexity and number of steps”](#3-task-complexity-and-number-of-steps)
Some tasks are straightforward and may require only a single quick response, without much thinking or reasoning. Others can involve multiple stages—such as planning, generating intermediate outputs, verifying results, applying changes, and self-correcting—each of which can add to the credits count.
Note
**Tip**: Keep tasks that you give to the agent well-scoped, work incrementally, and break large changes into smaller, contained steps.
### 4. Amount of context passed to the model
[Section titled “4. Amount of context passed to the model”](#4-amount-of-context-passed-to-the-model)
Prompts that include large amounts of context (such as [attached blocks](/agents/local-agents/agent-context/blocks-as-context/), long user query messages, etc.) or file attachments like [images](/agents/local-agents/agent-context/images-as-context/) may also increase the number of credits used due to increased token consumption.
Note
**Tip**: When sharing logs, code, or other large pieces of content, attach only the most relevant portions instead of full outputs.
### 5. Prompt caching (hits and misses)
[Section titled “5. Prompt caching (hits and misses)”](#5-prompt-caching-hits-and-misses)
Many model prompts include repeated content, like system instructions:
* **Cache hits**: if the model provider can match a prefix or a part of the prompt from a past request, it can reuse results from the cache, reducing both tokens consumed and latency.
* **Cache misses**: if no match is found, the full prompt may be processed again, which can increase credit consumption.
Because cache results depend on model provider behavior and timing, two similar prompts may still have different credit counts, depending on when you run the commands.
Note
**Tip**: Work in a continuous session when possible to improve cache hit rates.
These are the most common factors affecting credit usage, though there are others. Understanding them can help you manage your credits more efficiently and get the most from your plan.
## Compute credits
[Section titled “Compute credits”](#compute-credits)
Compute credits cover Warp-hosted compute consumed by an agent run. Cloud agent runs on Warp-hosted workers consume them; local agent runs don’t, since they run on your own machine.
Compute credits are sometimes called **cloud agent credits**, since only cloud agent runs consume them. Both names refer to the same bucket.
### Eligible for compute credits
[Section titled “Eligible for compute credits”](#eligible-for-compute-credits)
The following scenarios use compute credits:
* **First-party integrations** - Running agents through Warp’s integrations (Slack, Linear, GitHub, and others)
* **Cloud agent runs** - Using `oz agent run-cloud` via the CLI
* **Warp Platform API** - Running agents through Warp’s API
* **Cloud Mode** - Running an agent from Cloud Mode in the Warp app
### Not eligible for compute credits
[Section titled “Not eligible for compute credits”](#not-eligible-for-compute-credits)
* **Local agent runs** - Using `oz agent run` on your local machine
* **Self-hosted compute** - Using `oz agent run` on GitHub Actions, CI/CD pipelines, or other self-hosted infrastructure
* **Self-hosted workers** - Cloud agent runs on your own infrastructure through Enterprise self-hosted workers. These runs still use platform credits.
## Platform credits
[Section titled “Platform credits”](#platform-credits)
Platform credits are billed by the agent hour, the time an agent spends working on a task. They cover Warp’s platform layer (run lifecycle, integrations, dashboard, APIs, and observability) and apply to every cloud agent run, plus local agent runs on Business and Enterprise plans that use customer-supplied inference.
### Eligible for platform credits
[Section titled “Eligible for platform credits”](#eligible-for-platform-credits)
Platform credits are used in the following scenarios:
* **Cloud agents on any plan** use platform credits for every cloud agent run, whichever harness, inference source, or compute source it uses.
* **Local agents on Business or Enterprise with customer-supplied inference** use platform credits when the local agent run uses [Bring Your Own API Key (BYOK)](/agents/inference/bring-your-own-api-key/), a [ChatGPT subscription](/agents/inference/chatgpt-subscription/), a [custom inference endpoint](/agents/inference/custom-inference-endpoint/), or [BYOLLM](/enterprise/enterprise-features/bring-your-own-llm/).
### Not eligible for platform credits
[Section titled “Not eligible for platform credits”](#not-eligible-for-platform-credits)
The following scenarios do **not** use platform credits:
* **Local agents on Free, Build, or Max plans** don’t use platform credits, whichever inference source they use.
* **Local agents on Business or Enterprise using Warp-managed inference** don’t use platform credits because Warp is already paying for the model call through AI credits.
* **Regular terminal usage** doesn’t use platform credits. Shell commands and non-AI Warp features don’t consume credits.
* **Third-party agent CLIs run directly** don’t use platform credits when you run `claude`, `codex`, or another agent CLI outside of Warp.
For a full breakdown of how platform credits work, see [platform credits](/support-and-community/plans-and-billing/platform-credits/).
## Cloud agent runs on team plans
[Section titled “Cloud agent runs on team plans”](#cloud-agent-runs-on-team-plans)
Cloud agent runs that aren’t initiated by a specific team member — for example, scheduled runs or runs triggered through an agent API key — follow plan-specific billing rules. On self-serve plans (Build, Max, Business), these runs are billed to the team owner: the owner’s plan-included credits first, then the team’s shared add-on credit pool. With auto-reload off, the request is blocked when both are depleted (insufficient credits error). With auto-reload on, usage can trigger a reload into the team’s shared pool subject to the team-wide spend cap. On Enterprise plans, these runs draw from the team-scoped credit pool per your contract.
For the full waterfall, see [How are cloud agent runs on team plans billed when no individual user triggered them?](/support-and-community/plans-and-billing/pricing-faqs/#how-are-cloud-agent-runs-on-team-plans-billed-when-no-individual-user-triggered-them) in the Pricing FAQs.
# Plans, pricing, and refunds
Canonical page: [/support-and-community/plans-and-billing/plans-pricing-refunds/](https://docs.warp.dev/support-and-community/plans-and-billing/plans-pricing-refunds/)
> Warp's Free, Build, Max, Business, and Enterprise plans, what each includes, and the refund policies for subscriptions and add-on credits.
## Warp plans and pricing
[Section titled “Warp plans and pricing”](#warp-plans-and-pricing)
Warp offers flexible, pay-as-you-go plans designed for individual developers, teams, and enterprises.
Paid plans include a monthly allowance of credits that power features such as code generation, debugging, and multi-agent workflows. The Free plan doesn’t include bundled AI usage for the Warp Agent. To use the Warp Agent, [upgrade to a paid plan](https://www.warp.dev/pricing), buy [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) without subscribing, or bring your own inference with [Bring Your Own API Key (BYOK)](/agents/inference/bring-your-own-api-key/), a [ChatGPT subscription](/agents/inference/chatgpt-subscription/), a [custom inference endpoint](/agents/inference/custom-inference-endpoint/), or a [SuperGrok or X Premium subscription](/agents/inference/grok-subscription/).
Note
See [Warp pricing](https://www.warp.dev/pricing) for the latest plans and what’s included in each offering.
**Explore the following sections for more details:**
* [Credits](/support-and-community/plans-and-billing/credits/) — learn how credits are used and calculated across AI features.
* [Add-on credits](/support-and-community/plans-and-billing/add-on-credits/) — purchase additional credits or enable auto-reload at discounted rates.
* [Platform credits](/support-and-community/plans-and-billing/platform-credits/) — billed by the agent hour, covering Warp’s platform layer on cloud agent runs and local runs with customer-supplied inference.
* [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) — connect your own model provider API keys for custom usage and billing.
* [ChatGPT subscription](/agents/inference/chatgpt-subscription/) — connect a ChatGPT plan for eligible OpenAI models in the Warp app.
* [Custom inference endpoint](/agents/inference/custom-inference-endpoint/) — connect an OpenAI-compatible endpoint such as OpenRouter, LiteLLM, z.ai, or an internal gateway.
* [Pricing FAQs](/support-and-community/plans-and-billing/pricing-faqs/) — answers to common questions about plans, billing, and usage. Don’t have Warp yet? [Download Warp](https://www.warp.dev/download) and get started for free today.
### Warp’s refund policies
[Section titled “Warp’s refund policies”](#warps-refund-policies)
Review the details of our refund policies below. To request a refund, email [**billing@warp.dev**](mailto:billing@warp.dev) with information about your situation — the more context you provide, the faster we can resolve your request.
Caution
To request a refund or credit for a product defect, we require your [Conversation ID](/support-and-community/troubleshooting-and-support/sending-us-feedback/#gathering-ai-conversation-id) and [logs](/support-and-community/troubleshooting-and-support/sending-us-feedback/#gathering-warp-logs). You must have **Help improve Warp** enabled, so we can identify the issue before issuing any refund or credit. Learn how to enable it in [Crash reports and telemetry](/support-and-community/privacy-and-security/privacy/#how-to-disable-telemetry-and-crash-reporting).
#### Subscription refund policy
[Section titled “Subscription refund policy”](#subscription-refund-policy)
**Monthly plans**
If you signed up for a monthly Warp subscription by mistake, we can issue a full refund if you cancel or downgrade within 24 hours of being charged and no credits have been used during that billing cycle.
After 24 hours, or if credits have been used, we will cancel your subscription so that no future charges occur, and you can continue to use your plan through the end of the current billing cycle.
**Annual plans**
If you signed up for an annual Warp subscription by mistake, we can issue a full refund if you cancel or downgrade within 15 days of being charged and no credits have been used during that billing period.
After 15 days, we will refund you for the remaining full months on your subscription, excluding the first month.
#### Add-on credits refund policy
[Section titled “Add-on credits refund policy”](#add-on-credits-refund-policy)
* If you purchased [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) by mistake, you can receive a refund **as long as none of the credits have been used**. Warp cannot refund add-on credits if there has been any usage. Add-on credits remain available for up to **12 months** from the date of purchase, including if you move to the Free plan.
* Add-on credit purchases charge the payment method saved for your team, and any active team member can make one. If a purchase was billed to a card you didn’t expect, see [Which card is charged when a team member buys add-on credits?](/support-and-community/plans-and-billing/pricing-faqs/#which-card-is-charged-when-a-team-member-buys-add-on-credits) before requesting a refund.
Caution
Warp does not offer a formal guaranteed uptime Service Level Agreement (SLA). Live incidents can be monitored on our [**Status Page**](https://status.warp.dev/), and open issues are tracked on our [**GitHub Issues**](https://github.com/warpdotdev/Warp/issues).
# Platform credits
Canonical page: [/support-and-community/plans-and-billing/platform-credits/](https://docs.warp.dev/support-and-community/plans-and-billing/platform-credits/)
> Platform credits are billed by the agent hour and cover Warp's platform layer on cloud agent runs and local runs with customer-supplied inference.
Platform credits cover Warp’s platform layer: run lifecycle, integrations, dashboard, APIs, and observability. They’re billed by the agent hour, the time an agent spends working on a task. Platform credits apply to every cloud agent run, including [Warp Factories](/factories/) runs, plus local agent runs on Business and Enterprise plans that use customer-supplied inference.
Customer-supplied inference is any setup where Warp isn’t paying for the model call: [Bring Your Own API Key (BYOK)](/agents/inference/bring-your-own-api-key/), a [ChatGPT subscription](/agents/inference/chatgpt-subscription/) for local Warp Agent conversations, [custom inference endpoints](/agents/inference/custom-inference-endpoint/), [BYOLLM](/enterprise/enterprise-features/bring-your-own-llm/), or [team-managed API keys and endpoints](/enterprise/enterprise-features/team-managed-keys-and-endpoints/) on Business and Enterprise plans.
Caution
BYOK and custom inference endpoint support are available for individual users and organizations with 10 or fewer employees, subject to Warp’s [Terms of Service](https://www.warp.dev/legal/terms-of-service). Companies or organizations with more than 10 employees need a Warp Business or Enterprise plan to use these features.
## How platform credits are measured
[Section titled “How platform credits are measured”](#how-platform-credits-are-measured)
An *agent hour* is one hour an agent spends working on a task. Warp meters platform usage in agent hours and bills that usage as platform credits. Partial hours are billed proportionally, not rounded up: a 15-minute run is a quarter of an agent hour. See [Warp pricing](https://www.warp.dev/pricing) for current rates. Enterprise rates are set by contract.
A run accrues agent hours from the time the agent starts in its environment, including environment setup, until the run finishes, fails, or is cancelled. Time spent queued before the agent starts isn’t billed, and neither is idle time between turns while the run waits for your next message.
Within that period, what’s billable depends on the [harness](/platform/harnesses/):
* **Warp Agent** - Time the agent spends generating a response. Execution time for commands and tools the agent runs in its environment, such as a five-minute test suite, isn’t billable.
* **Claude Code and Codex** - The entire run, including command execution and time spent waiting on the model provider.
## The three credit buckets
[Section titled “The three credit buckets”](#the-three-credit-buckets)
Warp meters three types of infrastructure, each with its own credit bucket. Credit types and where an agent runs (local or cloud) are independent: each run consumes from whichever buckets apply to it.
* **AI credits** - Cover inference, the model call itself. Consumed when Warp pays for the model call through Warp-managed providers. See [credits](/support-and-community/plans-and-billing/credits/) for how AI credits are calculated.
* **Compute credits** - Cover the sandbox an agent runs in. Consumed when a run uses Warp-hosted compute, which in practice means cloud agent runs; local agent runs use your own machine. See [compute credits](/support-and-community/plans-and-billing/credits/#compute-credits).
* **Platform credits** - Cover the platform layer that runs around the agent, billed by the agent hour.
A single run can consume from more than one bucket. A Warp-managed cloud agent run consumes AI credits for the model call, compute credits for the hosted sandbox, and platform credits for the platform layer.
## When platform credits apply
[Section titled “When platform credits apply”](#when-platform-credits-apply)
Whether a run uses platform credits depends on where it runs and who pays for inference.
### Uses platform credits
[Section titled “Uses platform credits”](#uses-platform-credits)
* **Cloud agent runs on any plan** - Every cloud agent run uses platform credits, whichever harness (Warp Agent, Claude Code, or Codex), inference source (Warp-managed, BYOK, or BYOLLM), or compute source (Warp-hosted or self-hosted workers) it uses. [Warp Factories](/factories/) runs are cloud agent runs, so a factory’s agents draw platform credits the same way.
* **Local agent runs on Business or Enterprise with customer-supplied inference** - When a local run uses [BYOK](/agents/inference/bring-your-own-api-key/), a [ChatGPT subscription](/agents/inference/chatgpt-subscription/), a [custom inference endpoint](/agents/inference/custom-inference-endpoint/), or BYOLLM, Warp isn’t paying for the model call but still runs the platform layer around the agent.
### Doesn’t use platform credits
[Section titled “Doesn’t use platform credits”](#doesnt-use-platform-credits)
* **Local agent runs on Free, Build, or Max plans** - Don’t use platform credits, whether the run uses Warp-managed or customer-supplied inference.
* **Local agent runs on Business or Enterprise with Warp-managed inference** - Don’t use platform credits because Warp already charges AI credits for the model call.
* **Regular terminal usage** - Shell commands and non-AI Warp features don’t consume credits.
* **Third-party agent CLIs run directly** - Running `claude`, `codex`, or another agent CLI yourself, whether in a Warp terminal pane or elsewhere, doesn’t consume platform credits.
## Where platform credits appear
[Section titled “Where platform credits appear”](#where-platform-credits-appear)
Platform credits appear in the same billing views as the rest of your credit usage. Usage is shown in credits, not agent hours.
* **Per-user credit totals** - In the Warp app, **Settings** > **Billing and usage** shows platform credits alongside AI credits and compute credits.
* **Admin usage breakdown** - For team admins, the Admin Panel billing view shows a per-bucket breakdown for each member and for the team as a whole. Platform credits appear as their own segment in the stacked usage bar.
* **Add-on credits and limits** - Platform credits draw from the same pool as the rest of your usage: monthly Warp credits first, then [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) once those run out.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Credits](/support-and-community/plans-and-billing/credits/) - How AI credits are measured and calculated.
* [Add-on credits](/support-and-community/plans-and-billing/add-on-credits/) - Purchase additional credits or enable auto-reload.
* [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) - Connect your own model provider keys.
* [ChatGPT subscription](/agents/inference/chatgpt-subscription/) - Use eligible OpenAI models through your ChatGPT plan.
* [Custom inference endpoint](/agents/inference/custom-inference-endpoint/) - Route Warp through any OpenAI-compatible endpoint.
* [Plans, pricing, and refunds](/support-and-community/plans-and-billing/plans-pricing-refunds/) - Compare plans and refund policies.
# Pricing and billing FAQs
Canonical page: [/support-and-community/plans-and-billing/pricing-faqs/](https://docs.warp.dev/support-and-community/plans-and-billing/pricing-faqs/)
> Frequently asked questions about upgrading, managing billing, refunds, and invoicing with Warp's paid plans.
### How can I upgrade and subscribe to a Warp plan?
[Section titled “How can I upgrade and subscribe to a Warp plan?”](#how-can-i-upgrade-and-subscribe-to-a-warp-plan)
Paid Warp plans include a monthly allowance of credits for Warp-provided AI usage. The Free plan doesn’t include bundled AI usage for the Warp Agent (see [Does the Free plan include AI usage?](#does-the-free-plan-include-ai-usage) below).
When you upgrade to a paid plan, you get your plan’s monthly credit allowance right away. If you’re switching between paid plans, any AI usage you’ve already accumulated will carry over.
You can subscribe to a Warp paid plan as an individual or as part of a team. To upgrade:
* In the app: Go to **Settings** > **Billing and usage**, then click the Upgrade link
* Online: See [Warp pricing](https://www.warp.dev/pricing)
After entering your payment details, you’ll receive an invoice and confirmation via email.
### How can I get the most out of my Warp plan?
[Section titled “How can I get the most out of my Warp plan?”](#how-can-i-get-the-most-out-of-my-warp-plan)
Warp’s plans are for developers who rely on AI to code, debug, and move faster with their team. Pick the plan that matches the scale of your usage and the controls your team needs:
* **Build** — Usage-based plan for individuals or small teams with monthly credits, the ability to [Bring Your Own API Key (BYOK)](/agents/inference/bring-your-own-api-key/) or point Warp at a [custom inference endpoint](/agents/inference/custom-inference-endpoint/), and access to [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) with volume-based discounts.
* **Max** — Plan for individuals or small teams with heavier AI usage. Includes a larger monthly credit allowance than Build, plus a better effective rate for credits than buying add-on credits on Build.
* **Business** — Multi-seat plan for teams. Includes everything in Build, plus admin-configurable data controls, SAML-based SSO, and centralized billing. Available up to the seat limit listed on [Warp pricing](https://www.warp.dev/pricing).
* **Enterprise** — Custom plan for organizations that need higher seat counts, [Bring Your Own LLM (BYOLLM)](/enterprise/enterprise-features/bring-your-own-llm/) managed inference, granular admin controls, advanced security and compliance, and dedicated support.
For the most up-to-date feature and usage details — including current per-plan seat limits and monthly credit allowances — see [Warp pricing](https://www.warp.dev/pricing).
### How can I subscribe to a Warp Enterprise plan?
[Section titled “How can I subscribe to a Warp Enterprise plan?”](#how-can-i-subscribe-to-a-warp-enterprise-plan)
Warp offers two options for larger teams and organizations:
* **Business plan**: Self-serve multi-seat plan available for immediate upgrade. Includes admin-configurable data controls and admin-controlled SAML-based SSO. See [Warp pricing](https://www.warp.dev/pricing) for the current seat limit.
* **Enterprise plan**: Custom pricing, credit allowances, and terms — built for larger engineering organizations or teams with advanced security, compliance, or support needs. Enterprise also includes [Bring Your Own LLM (BYOLLM)](/enterprise/enterprise-features/bring-your-own-llm/) managed inference, with routing, orchestration, governance, and observability provided by Warp.
Tip
If you’d like to explore Enterprise, [contact our sales team](https://www.warp.dev/contact-sales) and someone from Warp will follow up.
For Warp-managed model traffic (requests Warp routes to OpenAI, Anthropic, Google, or xAI on your behalf), all plans are covered by Warp’s Zero Data Retention (ZDR) agreements with the underlying model providers. Traffic you route through your own API key or a custom inference endpoint is governed by that provider’s data-retention policies, not Warp’s agreements. Admin-configurable data controls — including team-wide retention policies and training opt-outs — are available on Business and Enterprise.
### What counts as a team member and how does billing work for members?
[Section titled “What counts as a team member and how does billing work for members?”](#what-counts-as-a-team-member-and-how-does-billing-work-for-members)
In Warp, a *team member* is any seat with access to your Team — including the shared Warp Drive, Notebooks, Workflows, and other team resources. Every plan lets you invite unlimited Warp Drive collaborators, but paid-plan features and credit allocation are governed by your plan’s seat limit (see [Are there new seat limits per plan?](#are-there-new-seat-limits-per-plan) below). Upgrading applies to your entire team, including your own account and all active members.
On the Free plan, you can share a limited number of Notebooks and Workflows with other Free users. If your team exceeds that limit, you’ll be prompted to [upgrade to a plan](https://app.warp.dev/upgrade).\
\
Once you upgrade, you’ll receive email notifications as team members accept invites. Billing is **prorated**, meaning you’re only charged for the days each member has access during your billing cycle. If a member leaves mid-cycle, Warp automatically applies a credit for the unused time to your next invoice.
**There are differences in how members are billed based on your payment schedule:**
* **Monthly plans**: New members are billed immediately for the remaining time in the month.
* **Annual plans**: New members are billed immediately for the remaining time in the year.
For example, if a member joins your monthly plan halfway through the month, you will be charged just half of the monthly fee ($25.00 out of $50). Similarly, if a member joins with four months remaining in an annual plan, you will be charged for those four months only, which amounts to $160 (4/12 of the annual $480).
If a member leaves part way through the billing cycle, Warp will issue a prorated credit based on the unused portion of their membership. This credit is applied to your team’s next invoice, regardless of whether you’re on a monthly or annual plan.
Caution
All members of the team will have the same subscription plan, you can’t mix and match plans for each member of a team. To have different plans, you currently must have separate teams.
### What is the value of joining or creating a team on Warp?
[Section titled “What is the value of joining or creating a team on Warp?”](#what-is-the-value-of-joining-or-creating-a-team-on-warp)
Team members have access to your shared [Warp Drive](/knowledge-and-collaboration/warp-drive/) objects and limited access to Warp’s collaboration features, including Session Sharing and Warp Drive storage.
**Upgrading the team to a paid plan adds collaboration and knowledge-sharing tools:**
* Create unlimited [Notebooks](/knowledge-and-collaboration/warp-drive/notebooks/) and [Workflows](/knowledge-and-collaboration/warp-drive/workflows/) in Warp Drive to organize and share knowledge across your team.
* Use Unlimited [Session Sharing](/agents/local-agents/session-sharing/) to collaborate in real time through live, shared terminal sessions.
### My co-workers are using Warp but we’re not on a Team together yet. How does billing work?
[Section titled “My co-workers are using Warp but we’re not on a Team together yet. How does billing work?”](#my-co-workers-are-using-warp-but-were-not-on-a-team-together-yet-how-does-billing-work)
Individual users with either personal or work email domains may continue to use Warp independently without incurring billing. The benefit of joining together on a Warp Team is that you get access to a shared Team Drive and collaboration features.
When you’re ready to use Warp more collaboratively, we suggest you nominate an Admin to [create a Team](/knowledge-and-collaboration/teams/) and invite members to join. When your Team exceeds the Warp Drive limits, you will be prompted to upgrade to a plan.
### How does usage work if logged into the same account on multiple devices?
[Section titled “How does usage work if logged into the same account on multiple devices?”](#how-does-usage-work-if-logged-into-the-same-account-on-multiple-devices)
When you use the account to sign into Warp on different devices, for example Linux on one computer and Windows on another, your usage of metered features like credits is tracked at the account level, not the device level.
You can use your Warp account on multiple personal computers. When you log in with the same account on different computers, your settings and preferences can be synced through the [Settings Sync](/terminal/more-features/settings-sync/) feature.
### How do I manage my billing?
[Section titled “How do I manage my billing?”](#how-do-i-manage-my-billing)
Open the billing portal to update your payment method, change billing details, view invoices, downgrade, cancel, or switch between monthly and annual billing.
You can open **Manage billing** from the Warp app or the web:
* **In the Warp app** - Go to **Settings** > **Billing and usage**, then click **Manage billing**.
* **On the web** - Open the [Warp Admin Panel](https://app.warp.dev/admin/) or the [Warp upgrade page](https://app.warp.dev/upgrade), click your profile in the top-right corner, then click **Manage billing**. You don’t need the Warp app installed.
### What happens when I downgrade during a billing cycle?
[Section titled “What happens when I downgrade during a billing cycle?”](#what-happens-when-i-downgrade-during-a-billing-cycle)
Downgrades take effect immediately. Warp issues an account balance for the prorated difference based on the time remaining in your billing cycle, not on unused monthly AI credits. You can apply that balance toward future subscription payments or AI credit purchases. The account balance amount is visible in the billing portal invoice history.
Any AI credits you’ve already used in the current cycle count against the lower plan’s monthly limit. If your usage has already exceeded that limit, you won’t receive more AI credits until your next billing cycle.
You can downgrade at any point throughout your subscription through the billing portal. See [How do I manage my billing?](#how-do-i-manage-my-billing).
### How do I cancel my subscription?
[Section titled “How do I cancel my subscription?”](#how-do-i-cancel-my-subscription)
You can cancel at any point throughout your subscription through the billing portal. See [How do I manage my billing?](#how-do-i-manage-my-billing).
Cancelled subscriptions remain active until the **end of your billing cycle**, monthly or yearly. **You can continue to use your Warp paid plan features until the cycle end date**. New team members added before the cycle ends are still billed immediately on a prorated basis for the remaining time in the cycle. See [What counts as a team member and how does billing work for members?](#what-counts-as-a-team-member-and-how-does-billing-work-for-members).
### What happens if I upgrade from monthly to annual billing?
[Section titled “What happens if I upgrade from monthly to annual billing?”](#what-happens-if-i-upgrade-from-monthly-to-annual-billing)
When upgrading from a monthly to annual billing cycle the billing is prorated, meaning you only pay for the annual portion of the year you haven’t paid for yet. You will be billed for the remaining part of the billing year with the discounted rate.
You can upgrade at any point throughout your subscription on the [Warp upgrade page](https://app.warp.dev/upgrade). You can also open **Manage billing** from your profile menu on that page. See [How do I manage my billing?](#how-do-i-manage-my-billing).
### What happens to unused credits?
[Section titled “What happens to unused credits?”](#what-happens-to-unused-credits)
Unused credits do not rollover to the next cycle and can’t be transferred to other accounts. You see when your credits will reset in the **Settings** > **Billing and usage** menu.
### What happens if my payment fails?
[Section titled “What happens if my payment fails?”](#what-happens-if-my-payment-fails)
If a payment fails, you will receive an email from Stripe and your Warp Team Settings will show a past-due alert. Certain paid plan features and the ability to invite new members will be locked down while your Team is in a past-due state. Paying all unpaid invoices through the billing portal will fully re-enable your paid plan features. See [How do I manage my billing?](#how-do-i-manage-my-billing).
If there are multiple unpaid invoices and you need help resolving them, contact <billing@warp.dev> for assistance.
### What counts as a credit?
[Section titled “What counts as a credit?”](#what-counts-as-a-credit)
Each time you submit a prompt in Warp, whether to generate code, suggest a command, or accomplish a task, you initiate an interaction with the Agent. See more details on our [credits](/support-and-community/plans-and-billing/credits/) page.
### What counts as an AI token?
[Section titled “What counts as an AI token?”](#what-counts-as-an-ai-token)
Tokens are chunks of text, such as words, parts of code, or characters, that large language models (LLMs) break down to analyze and generate responses. LLMs have a maximum number of tokens they can process at once. Credits and suggestions are not the same as tokens, which are limited separately regardless of which plan you’re on.
Note
Warp now abstracts away token usage, so you don’t need to manage or track it directly. You only need to monitor your **credit usage**, which is what’s measured against your plan limits.
If you’re curious, you can read the [OpenAI article on tokens](https://help.openai.com/en/articles/4936856-understanding-tokens), or refer to the pricing page for plan-level credit allocations. The Free plan doesn’t include bundled AI usage for the Warp Agent (see [Does the Free plan include AI usage?](#does-the-free-plan-include-ai-usage)). On paid plans, when you reach your monthly credit limit, premium models pause until your quota resets at the start of your next billing cycle; you can continue using premium models via [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) and auto-reload. See [What if I need more AI usage than my plan includes?](#what-if-i-need-more-ai-usage-than-my-plan-includes) for the full list of options.
### How often do my credits reset?
[Section titled “How often do my credits reset?”](#how-often-do-my-credits-reset)
On paid plans, allotted credits refill every 30 days from your signup date. The Free plan doesn’t include bundled AI usage for the Warp Agent (see [Does the Free plan include AI usage?](#does-the-free-plan-include-ai-usage)). When you upgrade to a [paid plan](https://www.warp.dev/pricing), you’re given your monthly credits immediately. You can follow along with your refill period by referencing **Settings** > **Billing and usage**. Alternatively, purchase [add-on credits](/support-and-community/plans-and-billing/add-on-credits/), or enable auto-reload with a monthly spend limit, to continue using premium models beyond your included quota.
Note
Unused credits do not rollover to the next cycle and can’t be transferred to other accounts.
### How do credits work for multi-seat teams?
[Section titled “How do credits work for multi-seat teams?”](#how-do-credits-work-for-multi-seat-teams)
On the multi-seat paid plans, plan-included credits are per-seat while add-on credits are shared across the team:
* **Plan-included monthly credits** — Each seat receives its own monthly credit allowance that resets every 30 days based on the team’s renewal date. See [Warp pricing](https://www.warp.dev/pricing) for the current per-seat allowance on your plan. Warp always consumes this allowance before any bonus or add-on grants.
* **Add-on credits** — As of August 2026, [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) purchased by any team member go into a single team-wide pool. Once a member’s plan-included credits are used up, their usage draws from the shared pool — including credits another member purchased.
* **User-scoped credits from May–August 2026** — Add-on credits purchased between May 21, 2026 and August 2026 were scoped to the purchasing member. Any remaining user-scoped balance stays attributed to that member and is consumed only after shared team grants are exhausted. Personal grants are not blocked while you are on a team; they simply come after shared grants, and only when they apply to the active team.
* **No personal-first option** — While you are on a team, you cannot spend personal or user-scoped credits before the team’s shared grants. Team-first drawdown is intentional.
* **Team-wide spend cap** — Admins set a single team-wide monthly spend cap that governs add-on credit purchases across the team. See [How does auto-reload work for teams?](#how-does-auto-reload-work-for-teams) below.
Enterprise plans support team-scoped credit pools and per-user spend limits separately — see [enterprise billing](/enterprise/support-and-resources/billing/).
### How do platform credits factor in?
[Section titled “How do platform credits factor in?”](#how-do-platform-credits-factor-in)
Warp meters credits across three buckets: **AI credits** (the model call), **compute credits** (the sandbox a cloud agent runs in), and **platform credits** (run lifecycle, integrations, dashboard, APIs, and observability). Platform credits are billed by the agent hour, the time an agent spends working on a task. All three buckets draw from the same pool: your monthly Warp credits first, then [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) once those are exhausted.
Platform credits apply in two situations:
* **Every cloud agent run, on every plan.** Warp’s platform layer coordinates every cloud run, whichever harness or inference source it uses.
* **Local agent runs on Business and Enterprise that use customer-supplied inference** (BYOK, a ChatGPT subscription, a custom inference endpoint, or BYOLLM). Warp isn’t paying for the model call, but it still runs the platform layer around the agent.
Local agent runs on Free, Build, or Max — and local runs on Business or Enterprise that use Warp-managed inference — do not consume platform credits. See [platform credits](/support-and-community/plans-and-billing/platform-credits/) for the full breakdown.
### What if I need more AI usage than my plan includes?
[Section titled “What if I need more AI usage than my plan includes?”](#what-if-i-need-more-ai-usage-than-my-plan-includes)
If you regularly run through your plan’s monthly credit allowance, you have a few options:
* **Upgrade to Max** — Designed for developers with heavier AI usage. Max includes a higher monthly credit allowance than Build, plus a better effective rate for credits than buying [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) on Build. See [Warp pricing](https://www.warp.dev/pricing) for current allowances.
* **Purchase add-on credits** — Top up your account on demand. Larger denominations have a better effective rate. Add-on credits roll over month-to-month and remain valid for 12 months from purchase, and they stay usable if you later move to the Free plan. See [add-on credits](/support-and-community/plans-and-billing/add-on-credits/) for current denominations.
* **Enable auto-reload** — Pick a denomination and a monthly spend cap, and Warp will automatically purchase add-on credits when your balance drops below 100 credits, up to your cap.
* **Bring Your Own API Key (BYOK)** — Point Warp at your own OpenAI, Anthropic, or Google API key. Requests routed through BYOK don’t consume AI credits — you’re billed directly by the model provider. See [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/). On Business and Enterprise, local agent runs that use BYOK consume [platform credits](/support-and-community/plans-and-billing/platform-credits/).
* **Connect a ChatGPT subscription** — Use eligible OpenAI models with the Warp Agent in the Warp app through your ChatGPT plan. See [Connecting a ChatGPT subscription](/agents/inference/chatgpt-subscription/).
* **Use a custom inference endpoint** — Route requests through any OpenAI-compatible endpoint (OpenRouter, LiteLLM, z.ai, an internal gateway, etc.) without spending AI credits. See [Custom inference endpoint](/agents/inference/custom-inference-endpoint/). On Business and Enterprise, local agent runs that use a custom inference endpoint consume [platform credits](/support-and-community/plans-and-billing/platform-credits/).
*BYOK and custom inference endpoint availability is subject to organization size — see [Can I bring my own API key?](#can-i-bring-my-own-api-key) for details.*
For organization-scale needs (cloud-provider managed inference, granular admin controls, or higher seat counts), Enterprise plans include [Bring Your Own LLM (BYOLLM)](/enterprise/enterprise-features/bring-your-own-llm/).
### Can I buy credits on the Free plan without subscribing?
[Section titled “Can I buy credits on the Free plan without subscribing?”](#can-i-buy-credits-on-the-free-plan-without-subscribing)
Yes. Free plan users can buy the same [add-on credit](/support-and-community/plans-and-billing/add-on-credits/) packs as paid plans and spend them on any model, without a subscription. Free plan packs cost more per credit than the same packs on a paid plan — see [Warp pricing](https://www.warp.dev/pricing) for current rates.
Buy from **Settings** > **Billing and usage** in the Warp app, or from the **Add-on credits** card on the [Warp upgrade page](https://app.warp.dev/upgrade).
Credits you buy this way behave like any other add-on credits: they roll over, stay valid for 12 months from purchase, and remain usable if your team later moves between plans.
### Who on my team can purchase add-on credits?
[Section titled “Who on my team can purchase add-on credits?”](#who-on-my-team-can-purchase-add-on-credits)
Any active team member can purchase add-on credits. Admin permissions aren’t required, and the team doesn’t need a paid subscription. Purchased credits go into the team’s shared pool, so any member’s usage can draw them down.
Two team-level settings still apply, and both are admin-only:
* **Team-wide monthly spend cap** — Every purchase counts against one cap for the whole team per calendar month. Purchases that would exceed the cap are rejected.
* **Auto-reload** — While an admin has auto-reload on, individual members can’t purchase add-on credits manually.
Upgrading the team to a paid plan is still admin-only. A member who can’t upgrade the team can still buy add-on credits for the team.
### Which card is charged when a team member buys add-on credits?
[Section titled “Which card is charged when a team member buys add-on credits?”](#which-card-is-charged-when-a-team-member-buys-add-on-credits)
Add-on credit purchases charge the payment method saved for the **team**, not a per-member card. That’s whichever card the team already has on file — usually the one an admin entered when subscribing, or the one the first member entered when buying credits on a team that had no card yet.
If the team has no saved payment method, the first purchase adds one and that card becomes the team’s default. Later add-on credit purchases and auto-reload charge it. On a Free plan team, that means the first member to buy credits can end up supplying the card a teammate’s later purchase is billed to.
If you see an add-on credit charge you don’t recognize:
* Check **Settings** > **Billing and usage** in the Warp app for the team’s add-on credit purchases this month.
* Ask a team admin to review the invoices in the billing portal, which lists each purchase and the member who made it. See [How do I manage my billing?](#how-do-i-manage-my-billing).
* Email <billing@warp.dev> if the charge still looks wrong.
### How do I change or remove the card saved for my team?
[Section titled “How do I change or remove the card saved for my team?”](#how-do-i-change-or-remove-the-card-saved-for-my-team)
Team admins change or remove the saved card in the billing portal, reachable from **Settings** > **Billing and usage** in the Warp app or from the [Warp Admin Panel](https://app.warp.dev/admin/) on the web. See [How do I manage my billing?](#how-do-i-manage-my-billing) for both paths.
Non-admin members can’t open the billing portal. If you added a card to your team through a credit purchase and want it removed, ask a team admin to do it, or email <billing@warp.dev>.
Admins who want to limit exposure without removing the card can lower the team-wide monthly spend cap under **Settings** > **Billing and usage**. Setting a lower cap bounds what the team can spend on add-on credits in a calendar month, no matter who makes the purchase.
### How does auto-reload work for teams?
[Section titled “How does auto-reload work for teams?”](#how-does-auto-reload-work-for-teams)
Auto-reload prevents team members from getting blocked by credit exhaustion. It works the same way for individual and multi-seat paid plans, with one extra knob for teams.
When auto-reload is **on**:
* The admin chooses an add-on credit **denomination**. Larger denominations have a better effective per-credit rate.
* Whenever a member has used up their plan-included credits and the add-on credit balance available to them drops below **100 credits**, Warp automatically purchases another bundle of the configured denomination and adds it to the team’s shared pool.
* All auto-reload purchases count against a single **team-wide monthly spend cap** that the admin sets. Once the team hits the cap in a given month, auto-reload pauses until the next calendar month or until the admin raises the cap.
* While auto-reload is on, **individual team members cannot purchase add-on credits manually** — the team-wide auto-reload configuration governs all purchases.
Reloaded credits land in the team’s shared pool, so sustained usage by any member — not just the one who purchased credits — can drain the pool and trigger repeated reloads until the team-wide spend cap is reached. Lower the cap to limit what the team can spend in a month.
When auto-reload is **off**, eligible team members can buy add-on credits for the team’s shared pool, as long as the team stays below the team-wide monthly spend cap. Users keep working as long as they have plan credits, previously purchased add-on credits, or have routed Warp at their own API key or [custom inference endpoint](/agents/inference/custom-inference-endpoint/). Once those run out, premium-model usage is blocked until credits are topped up or the next billing cycle begins.
Auto-reload can be enabled, paused, or reconfigured at any time in **Settings** > **Billing and usage**.
### How are cloud agent runs on team plans billed when no individual user triggered them?
[Section titled “How are cloud agent runs on team plans billed when no individual user triggered them?”](#how-are-cloud-agent-runs-on-team-plans-billed-when-no-individual-user-triggered-them)
Some cloud agent runs aren’t initiated by a specific team member — for example, scheduled runs or runs triggered through an agent API key. On self-serve plans (Build, Max, Business), these runs are billed to the **team owner**.
Caution
Team owners: scheduled runs and runs triggered through an agent API key draw from your plan-included credits and then the team’s shared add-on credit pool. If auto-reload is enabled, automated jobs can trigger add-on credit purchases that count toward the team-wide spend cap. Review your auto-reload settings and team-wide spend cap in **Settings** > **Billing and usage** before relying on scheduled or API-key-triggered cloud agents.
The waterfall is:
1. First, the owner’s plan-included monthly credits are consumed.
2. Once those are exhausted, the team’s shared add-on credit pool is consumed.
When auto-reload is **off**, the request is blocked once both buckets are depleted. When auto-reload is **on**, cloud agent usage can trigger auto-reload into the team’s shared pool subject to the team-wide spend cap; further cloud agent runs then draw from that reloaded balance until the cap is reached.
“Blocked” means the run fails immediately with an insufficient-credits error rather than queuing or retrying. For unattended runs (scheduled jobs, team-API-key triggers), this manifests as a failed run in the cloud agent dashboard with an [insufficient credits](/factories/api-and-sdk/troubleshooting/errors/insufficient-credits/) error code; the run won’t be retried automatically. Owners should monitor the dashboard and configure spend caps with headroom for critical scheduled workloads.
Note
Enterprise plans support team-scoped credit pools, so this traffic draws from the team pool rather than an individual admin. See [enterprise billing](/enterprise/support-and-resources/billing/) for overage and contract terms.
### Does the Free plan include AI usage?
[Section titled “Does the Free plan include AI usage?”](#does-the-free-plan-include-ai-usage)
The Free plan doesn’t include bundled AI usage for the Warp Agent. To use the Warp Agent, you have three options:
* **Upgrade to a paid plan** — paid plans include a monthly allowance of Warp-provided AI usage with no extra setup. See [Warp pricing](https://www.warp.dev/pricing).
* **Buy add-on credits** — purchase a credit pack without subscribing and spend it on any model. See [Can I buy credits on the Free plan without subscribing?](#can-i-buy-credits-on-the-free-plan-without-subscribing).
* **Bring your own inference** — connect your own API key with [Bring Your Own API Key (BYOK)](/agents/inference/bring-your-own-api-key/), connect a [ChatGPT subscription](/agents/inference/chatgpt-subscription/), point Warp at a [custom inference endpoint](/agents/inference/custom-inference-endpoint/), or use a [SuperGrok or X Premium subscription](/agents/inference/grok-subscription/). Requests routed through your own inference don’t consume Warp credits for inference.
Without a paid plan, purchased add-on credits, or your own inference, conversations on the Free plan can’t run on Warp-provided models. This includes conversations started from prompt suggestions in the input.
### Can I use a Free plan if I’m a developer at a large company or organization?
[Section titled “Can I use a Free plan if I’m a developer at a large company or organization?”](#can-i-use-a-free-plan-if-im-a-developer-at-a-large-company-or-organization)
Yes. Developers at any company size are welcome to use Warp’s Free plan.
If you need access to advanced collaboration features or higher limits, you may benefit from upgrading to a plan, but Warp does not require large organizations to upgrade.
### Are there any Warp discounts for students, non-profits, or open-source teams?
[Section titled “Are there any Warp discounts for students, non-profits, or open-source teams?”](#are-there-any-warp-discounts-for-students-non-profits-or-open-source-teams)
Warp doesn’t currently offer discounts or program credits for students or non-profits. We recommend exploring the Free plan, which includes all core terminal features and is a great starting point for individual or community use.
Warp’s client itself is open source under [AGPL v3](https://github.com/warpdotdev/warp/blob/master/LICENSE-AGPL), so open source teams can build, run, and contribute to it directly. See [Contributing to Warp](/support-and-community/community/contributing/) for the flow.
### Where is Warp Drive data for my team stored?
[Section titled “Where is Warp Drive data for my team stored?”](#where-is-warp-drive-data-for-my-team-stored)
Warp Drive data is securely stored on Google Cloud Platform servers located in the United States. All data is encrypted in transit and at rest.
For more details, [visit the Security Overview](https://www.warp.dev/legal/security) or contact <security@warp.dev>.
### Does Warp have a SOC 2 Type 2 attestation?
[Section titled “Does Warp have a SOC 2 Type 2 attestation?”](#does-warp-have-a-soc-2-type-2-attestation)
Yes. Warp has obtained a SOC 2 Type 2 attestation from an accredited third party. See the [Trust Center](/enterprise/security-and-compliance/trust-center/) to request the report.
### Does Warp have Zero Data Retention policies with LLM providers?
[Section titled “Does Warp have Zero Data Retention policies with LLM providers?”](#does-warp-have-zero-data-retention-policies-with-llm-providers)
Warp integrates with multiple LLM providers — including Anthropic, OpenAI, Google, xAI, and Fireworks AI — to power its AI features. Warp has executed Zero Data Retention (ZDR) agreements with these providers. Across all plans, these agreements mean:
* LLM providers commit not to train their models on any customer-generated data processed through Warp’s services.
* LLM providers commit to delete inputs and outputs after generating the relevant output, within a fixed time period.
Warp enforces these commitments through both technical measures and contractual safeguards with the LLM providers.
Zero data retention is available for supported models. Model availability may vary where providers require data retention for safety, abuse monitoring, or compliance reasons.
### How can I enable Zero Data Retention in Warp?
[Section titled “How can I enable Zero Data Retention in Warp?”](#how-can-i-enable-zero-data-retention-in-warp)
Zero Data Retention (ZDR) can be enabled in two ways:
* **Individual level** — Any user can enable full ZDR for their own account by disabling **Help Improve Warp** in **Settings** > **Privacy**.
* **Organization-wide** — On Business and Enterprise plans, admins can enforce ZDR for all members from the [Admin Panel](/enterprise/team-management/admin-panel/), so team-wide compliance doesn’t rely on individual settings.
To discuss organization-wide ZDR for your team, [contact our sales team](https://www.warp.dev/contact-sales).
Regardless of plan, Warp never allows OpenAI, Anthropic, Google, xAI, or other model providers to store, retain, or train their models on your data — see [Does Warp have Zero Data Retention policies with LLM providers?](#does-warp-have-zero-data-retention-policies-with-llm-providers) for details.
### Can I bring my own API key?
[Section titled “Can I bring my own API key?”](#can-i-bring-my-own-api-key)
Yes. On Free, Build, Max, Business, and Enterprise plans, you can configure your own OpenAI, Anthropic, or Google API key in **Settings** > **Agents** > **Warp Agent** > **Manage models**. Requests routed through your own key don’t consume AI credits — you’re billed directly by the model provider.
See [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) for setup steps, the list of supported providers and models, and the differences between BYOK, custom inference endpoints, and BYOLLM.
BYOK and custom inference endpoint support are available for individual users and organizations with 10 or fewer employees, subject to Warp’s Terms of Service. Companies or organizations with more than 10 employees need a Warp Business or Enterprise plan to use these features.
On Business and Enterprise, local agent runs that use BYOK still consume platform credits, billed by the agent hour. See [platform credits](/support-and-community/plans-and-billing/platform-credits/).
### Does Warp support custom inference endpoints?
[Section titled “Does Warp support custom inference endpoints?”](#does-warp-support-custom-inference-endpoints)
Yes. In addition to BYOK, Warp can route requests to any OpenAI-compatible inference endpoint — including OpenRouter, LiteLLM, z.ai, and internal gateways your team already runs. Custom inference endpoint requests also don’t consume AI credits.
Custom inference endpoints are available on Free, Build, Max, Business, and Enterprise. See [Custom inference endpoint](/agents/inference/custom-inference-endpoint/) for configuration steps, billing behavior, and how custom inference endpoints differ from BYOK and from Enterprise’s [Bring Your Own LLM (BYOLLM)](/enterprise/enterprise-features/bring-your-own-llm/) managed inference.
BYOK and custom inference endpoint support are available for individual users and organizations with 10 or fewer employees, subject to Warp’s Terms of Service. Companies or organizations with more than 10 employees need a Warp Business or Enterprise plan to use these features.
On Business and Enterprise, local agent runs that use a custom inference endpoint still consume platform credits, billed by the agent hour. See [platform credits](/support-and-community/plans-and-billing/platform-credits/).
### Does Warp support other model routers or “Bring Your Own LLM”?
[Section titled “Does Warp support other model routers or “Bring Your Own LLM”?”](#does-warp-support-other-model-routers-or-bring-your-own-llm)
On the Enterprise plan, Warp’s [Bring Your Own LLM (BYOLLM)](/enterprise/enterprise-features/bring-your-own-llm/) lets you route inference through major cloud-provider Model-as-a-Service offerings. BYOLLM supports AWS Bedrock and [Gemini Enterprise (Vertex AI)](/enterprise/enterprise-features/byollm-gemini-enterprise/), with Azure Foundry coming soon. Warp still manages model support, routing, and orchestration, but inference runs in your cloud environment so you can maintain data locality, security controls, and existing cloud spend commitments.
Custom or in-house model routers outside this list aren’t supported by default today. If you have specific requirements, [contact our sales team](https://www.warp.dev/contact-sales).
For lighter-weight routing through any OpenAI-compatible endpoint (OpenRouter, LiteLLM, z.ai, internal gateways), see [Does Warp support custom inference endpoints?](#does-warp-support-custom-inference-endpoints) above.
### What features are available during multi-harness orchestration beta?
[Section titled “What features are available during multi-harness orchestration beta?”](#what-features-are-available-during-multi-harness-orchestration-beta)
Multi-harness orchestration is currently in beta. Free plan cloud runs use the Warp Agent. Selecting [Claude Code](/platform/harnesses/claude-code/) or [Codex](/platform/harnesses/codex/) as a third-party harness requires a paid plan. See [cloud agent harnesses](/platform/harnesses/) for setup and plan requirements.
[Agent Memory](/agents/agent-memory/) is currently in Research Preview. It lets preferences, project knowledge, and learnings from past sessions carry across harnesses and future agent runs. [Contact our sales team](https://www.warp.dev/contact-sales) to request access.
As these features move out of beta or Research Preview, availability, limits, and pricing may change.
### What payment options are available for Warp’s self-service plans?
[Section titled “What payment options are available for Warp’s self-service plans?”](#what-payment-options-are-available-for-warps-self-service-plans)
Warp uses Stripe as our payments processor and currently accepts the following payment methods: credit card, debit card, Link, Apple Pay, Google Pay.
We don’t support ACH, checks, PayPal, cryptocurrency, or other alternative payment methods at this time.
Note
To checkout with Apple Pay, use the Safari browser on an Apple device.\
To checkout with Google Pay, use Chrome, make sure you’re logged into your Google Wallet account in the browser, and that “Save and fill payment methods” is enabled in the browser settings.
### How do I get a refund?
[Section titled “How do I get a refund?”](#how-do-i-get-a-refund)
For monthly subscriptions, we can issue a full refund if you cancel within 24 hours of being charged and no credits have been used.
For annual subscriptions, we can issue a full refund within 15 days if no credits have been used, or a prorated refund for remaining months after that. See [Warp’s Refund Policy](/support-and-community/plans-and-billing/plans-pricing-refunds/#warps-refund-policies) for full details and exceptions.
### Why doesn’t my promo code work or why was it disabled?
[Section titled “Why doesn’t my promo code work or why was it disabled?”](#why-doesnt-my-promo-code-work-or-why-was-it-disabled)
Warp’s promotions are a way to try Warp before committing to a subscription, not get unlimited free or inexpensive AI. To prevent abuse, we’re limiting promotion codes to first-time redemptions only, so each account can only use one promotion code.\
\
In addition certain promo codes we issue are only valid for specific plans (not all plans) and expire after a certain time. If you apply a promo code for a certain plan, then upgrade to another plan, the promotion doesn’t transfer to the new plan so you will end up paying full price for the upgrade.
Caution
Warp reserves the right to disable any promotion codes at any time, and cancel the associated subscriptions if we find that the code was being abused.
### How can I subscribe to Warp as tax exempt?
[Section titled “How can I subscribe to Warp as tax exempt?”](#how-can-i-subscribe-to-warp-as-tax-exempt)
Warp does allow tax exempt organizations to subscribe, but there are some additional steps that you need to take.
1. Create a Warp account, login, and go to the [upgrade page](https://app.warp.dev/upgrade), and select a plan, but **don’t checkout or pay yet.** This will only setup your billing account in the system that will be used in the later steps.
2. E-mail <billing@warp.dev> with your proof of your organization tax exempt status and your Warp account email.
3. Warp’s team will verify your tax exempt status and will change your account to tax exempt.
4. Finally, subscribe to your plan of choice. You will see no taxes applied to the bill.
### Why can’t I subscribe to Warp?
[Section titled “Why can’t I subscribe to Warp?”](#why-cant-i-subscribe-to-warp)
There are certain prohibited and restricted businesses in which Stripe and major credit card networks will not process payments. For the most updated information, see Stripe’s [restricted businesses list](https://stripe.com/legal/restricted-businesses).
### I have a question and need help. How can I reach a human at Warp?
[Section titled “I have a question and need help. How can I reach a human at Warp?”](#i-have-a-question-and-need-help-how-can-i-reach-a-human-at-warp)
The team at Warp is standing by and ready to help. For subscribers technical issues email <support@warp.dev>, for subscribers billing issues email <billing@warp.dev>, for security concerns email <security@warp.dev>, and for questions about privacy email <privacy@warp.dev>.
***
### May 2026 pricing changes
[Section titled “May 2026 pricing changes”](#may-2026-pricing-changes)
The May 21, 2026 update introduced new seat limits, changed how add-on credits are attributed, opened BYOK to every plan, added custom inference endpoints, and began metering platform credits for cloud agent runs. The questions below cover what changed and what to do if any of it affects you.
#### Are there new seat limits per plan?
[Section titled “Are there new seat limits per plan?”](#are-there-new-seat-limits-per-plan)
Yes. As of May 21, 2026, each plan has an explicit seat limit. See [Warp pricing](https://www.warp.dev/pricing) for the current per-plan caps.
The seat limit governs paid-plan features and credit allocation. It’s separate from the unlimited Warp Drive collaborators every plan supports. You can keep inviting unlimited users to share Notebooks, Workflows, and other Warp Drive resources without hitting the seat cap. The cap only applies when a user takes a paid seat on your team.
#### What if my team is already above the new seat limit?
[Section titled “What if my team is already above the new seat limit?”](#what-if-my-team-is-already-above-the-new-seat-limit)
Your team’s current access doesn’t change. Existing members keep their seats and can continue using Warp the same way they do today.
The cap only governs **adding new members**. While your team is at or above the cap, you can’t add a new member or backfill a seat after a member leaves. To grow past the cap, switch to the next plan up (or to Enterprise) anytime under **Settings** > **Billing and usage**.
#### How are add-on credits being attributed differently?
[Section titled “How are add-on credits being attributed differently?”](#how-are-add-on-credits-being-attributed-differently)
Add-on credit attribution has changed twice in 2026:
* **Before May 21, 2026** — Add-on credits on multi-seat teams were pooled; every member drew from a single shared balance.
* **May 21 – August 2026** — Add-on credits were user-scoped; each user had their own balance.
* **As of August 2026** — Add-on credits are **team-pooled again**. Purchases from any member go into the team’s shared pool, and any member’s usage draws the pool down once their plan-included credits are used up. Remaining user-scoped balances from the May–August window stay attributed to the purchasing member and are consumed after the shared pool. There is no way to prefer personal credits first while on a team.
Anyone on the team can purchase add-on credits, subject to the team-wide spend cap admins set under **Settings** > **Billing and usage**.
For details, see [add-on credits](/support-and-community/plans-and-billing/add-on-credits/).
#### What happens to my add-on credits if I leave the team?
[Section titled “What happens to my add-on credits if I leave the team?”](#what-happens-to-my-add-on-credits-if-i-leave-the-team)
Add-on credits are tied to the team that paid for them, so team-membership changes affect access:
* **You leave a team**: You lose access to any add-on credits tied to that team. If you rejoin the same team later, you regain access to any unused, non-expired credits. The admin pays a prorated rate for your seat on rejoin.
* **An admin removes you from a team**: You lose access to any add-on credits tied to that team. If you rejoin later, you regain access to any unused, non-expired credits.
* **An admin deletes the team**: Any remaining add-on credits must be used or removed before the team can be deleted.
Unused add-on credits remain valid for 12 months from purchase and stay tied to the team they were purchased under. See [When team membership changes](/support-and-community/plans-and-billing/add-on-credits/#when-team-membership-changes) on the add-on credits page for full details.
#### Can I bring my own API key on the Free plan now?
[Section titled “Can I bring my own API key on the Free plan now?”](#can-i-bring-my-own-api-key-on-the-free-plan-now)
Yes. As of May 21, 2026, **Bring Your Own API Key (BYOK)** is available on all plans, including Free. Previously, BYOK required a Build, Business, or Enterprise subscription. You can configure your OpenAI, Anthropic, or Google key under **Settings** > **Agents** > **Warp Agent** > **Manage models**.
See [Bring Your Own API Key](/agents/inference/bring-your-own-api-key/) for the full list of supported providers and setup steps.
#### What is the new custom inference endpoint feature?
[Section titled “What is the new custom inference endpoint feature?”](#what-is-the-new-custom-inference-endpoint-feature)
**Custom inference endpoints** let you route Warp’s AI traffic through any OpenAI-compatible inference endpoint, including OpenRouter, LiteLLM, z.ai, and internal gateways your team already runs. Support is available on Free, Build, Max, Business, and Enterprise.
Here’s how custom inference endpoints differ from BYOK and BYOLLM:
* **BYOK** sends requests directly to OpenAI, Anthropic, or Google using your own provider API key.
* **Custom inference endpoint** sends requests to any OpenAI-compatible URL you control or that your team runs.
* **BYOLLM** is an Enterprise-only managed inference feature. Warp routes traffic through your cloud provider (AWS Bedrock and Gemini Enterprise Agent Platform (Vertex AI) today, with Azure Foundry coming soon) and handles the routing, orchestration, governance, and observability.
For setup and details, see [Custom inference endpoint](/agents/inference/custom-inference-endpoint/).
#### I’m a team admin. What do I need to do?
[Section titled “I’m a team admin. What do I need to do?”](#im-a-team-admin-what-do-i-need-to-do)
A short checklist to triage the May 2026 changes for your team:
* **Check your seat count.** Go to **Settings** > **Teams** to see whether your team is at or above your plan’s new seat limit. If you are, see [What if my team is already above the new seat limit?](#what-if-my-team-is-already-above-the-new-seat-limit).
* **Set your team’s add-on credit spend cap.** Under **Settings** > **Billing and usage**, configure the monthly cap that applies to add-on credit purchases across your team. Team members can buy add-on credits for the team, but every purchase counts against this cap.
* **Let your team know add-on credits are shared team-wide.** Purchases from any member land in the team’s shared pool, and the whole team’s usage draws it down.
* **Confirm which card your team has on file.** Every add-on credit purchase charges the team’s saved payment method, including purchases made by members who aren’t admins. Review it in the billing portal. See [Which card is charged when a team member buys add-on credits?](#which-card-is-charged-when-a-team-member-buys-add-on-credits).
* **Account for platform credits.** If your team is on Business and uses BYOK or a custom inference endpoint locally, those local runs consume platform credits. See [platform credits](/support-and-community/plans-and-billing/platform-credits/).
# Warp network log
Canonical page: [/support-and-community/privacy-and-security/network-log/](https://docs.warp.dev/support-and-community/privacy-and-security/network-log/)
> Logs for all network traffic (both requests and responses) originating from the current terminal session.
## What is it
[Section titled “What is it”](#what-is-it)
You can use Warp’s network log to help debug issues or simply use it to understand when information is sent or received over the network throughout a Warp session.
Each log item is a timestamped Debug format string for either a request or response object handled by Warp. Messages are logged via pre-request and post-response hooks in Warp’s internal HTTP client.
## How to use it
[Section titled “How to use it”](#how-to-use-it)
1. To access the network log, select the Input in a session and open the [Command Palette](/terminal/command-palette/), then search for “Show Warp Network Log”.
2. That will insert a command into your Input editor - it should look something like this: `tail -f "some/path/to/warp_network.log"`.
3. Press Enter to run this command. You’ll then see the corresponding requests and responses logged in the network log.
## How it works
[Section titled “How it works”](#how-it-works)
[Network Log Demo](https://www.loom.com/embed/0d9eaeb8715846f3a96d557abe23e7ac)
## Known issues with network log
[Section titled “Known issues with network log”](#known-issues-with-network-log)
At the moment, network traffic originating from crash reports and error messages is not captured in the network log. This is due to our use of the Sentry SDK, which encapsulates all network logic and doesn’t currently expose a hook for handling requests and responses directly. The team is actively investigating a solution to include such traffic in the log in a future release. You can also disable Crash Reporting entirely in Warp’s **Settings** > **Privacy** tab.
# Privacy and data control
Canonical page: [/support-and-community/privacy-and-security/privacy/](https://docs.warp.dev/support-and-community/privacy-and-security/privacy/)
> Warp's approach to privacy and your control over your data
Note
If you have questions, reach out at <privacy@warp.dev>. For security-related issues, email <security@warp.dev>.
## Transparency and control
[Section titled “Transparency and control”](#transparency-and-control)
Our philosophy is complete transparency and control over any data leaving your machine. This means you can:
* Read a complete list of [all the telemetry events](/support-and-community/privacy-and-security/privacy/#exhaustive-telemetry-table) that get sent for app analytics
* Monitor telemetry in real-time with Warp’s native [Network Log](/support-and-community/privacy-and-security/network-log/)
* [Opt out](/support-and-community/privacy-and-security/privacy/#how-to-disable-telemetry-and-crash-reporting) of telemetry at any time
* Read and audit Warp’s client source code at [`warpdotdev/warp`](https://github.com/warpdotdev/warp), open source under [AGPL v3](https://github.com/warpdotdev/warp/blob/master/LICENSE-AGPL)
* See how long [shared session data is kept and who can access it](/agents/local-agents/session-sharing/#data-retention-and-access)
## What telemetry data does Warp collect and why?
[Section titled “What telemetry data does Warp collect and why?”](#what-telemetry-data-does-warp-collect-and-why)
Warp collects high-level telemetry and usage data to discover product quality issues and guide feature prioritization.
If you haven’t opted out of “Help improve Warp”, we may collect:
1. High level product usage and analytics data to analyze feature uptake and usage patterns. See the full list of tracked events in the [exhaustive telemetry table](/support-and-community/privacy-and-security/privacy/#exhaustive-telemetry-table) below. These are all high level metrics and do not include any user generated content.
2. AI interactions and console inputs that power our [AI features](/agents/). Configurable [Secret Redaction](/support-and-community/privacy-and-security/secret-redaction/) is disabled by default and masks content that matches your patterns before AI requests are sent. Telemetry payload redaction is separate and applies built-in patterns to telemetry regardless of the Secret Redaction setting.
Note
Telemetry must be enabled to use AI features on the Free plan, while paid plans can opt out at any time and continue using Warp, including AI.
Caution
Business and Enterprise plans are covered by our Zero Data Retention (ZDR) agreement. No AI interaction or console data is ever collected.
Selling usage data will never be part of Warp’s business model. This data is used solely to improve the end-user experience. Warp uses Sentry for crash reporting and Rudderstack for app analytics.
You can read our [full privacy policy](https://www.warp.dev/legal/privacy-policy) as well as [how Warp handles security](https://www.warp.dev/legal/security).
### How to disable telemetry and crash reporting
[Section titled “How to disable telemetry and crash reporting”](#how-to-disable-telemetry-and-crash-reporting)
1. Navigate to **Settings** > **Privacy**, or open the [Command Palette](/terminal/command-palette/) and search for “privacy”
2. Toggle off “Help improve Warp”, “Send crash reports”, or both

With telemetry disabled, no console interactions are ever persisted on Warp’s servers. Each request contains a `X-Warp-Telemetry-Enabled` header to specify whether telemetry is disabled, and even if this is missing from the request, our server assumes it’s disabled.
### Delete your account and data
[Section titled “Delete your account and data”](#delete-your-account-and-data)
Warp provides a convenient way for you to delete your account and data. Any active Warp subscriptions associated with the account will also be cancelled when deleted. You can delete your Warp account and data in the following ways:
* From Warp, go to **Settings** > **Privacy** > **“Visit the data management page”**
Click the “Delete” button on the Data Management page to go through the data deletion flow.
* From the web, log in to your Warp account on the [Warp login page](https://app.warp.dev/login), then go to the [data management page](https://app.warp.dev/data_management) and click the “Delete” button to go through the data deletion flow.
Note
Deletion jobs run every 24 hours, so if you deleted your account and want to sign up again with the same email, you won’t be able to do so until that deletion job completes.
Caution
If you’re a [Team](/knowledge-and-collaboration/teams/) admin, the deletion flow will require that you assign a team member as the new admin.
### Exhaustive telemetry table
[Section titled “Exhaustive telemetry table”](#exhaustive-telemetry-table)
| Event Name | Description |
| ---------------------------------------------------------- | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `AI Command Search opened` | Opened the modal for AI Command Search, where you can use natural language to search for commands |
| `AI Execution Profile Created` | A new AI execution profile was created |
| `AI Execution Profile Deleted` | An AI execution profile was deleted |
| `AI Execution Profile: Added To Allowlist` | An item was added to an AI execution profile allowlist |
| `AI Execution Profile: Added To Denylist` | An item was added to an AI execution profile denylist |
| `AI Execution Profile: Context Window Selected` | Selected a context window limit for an execution profile’s base model |
| `AI Execution Profile: Model Selected` | An AI model was selected for an AI execution profile |
| `AI Execution Profile: Removed From Allowlist` | An item was removed from an AI execution profile allowlist |
| `AI Execution Profile: Removed From Denylist` | An item was removed from an AI execution profile denylist |
| `AI Execution Profile: Setting Updated` | An AI execution profile setting was updated |
| `AI Input Not Sent` | The AI input was not sent |
| `AI Suggested Rule Added` | Clicked the Add Suggested Rule button in the AI blocklist |
| `AI Suggested Rule Content Changed` | Content changed by the user in the suggested rule dialog |
| `AI Suggested Rule Edited` | Clicked the Edit Suggested Rule button in the AI blocklist |
| `AI.ProviderCredential.Changed` | A user added or removed a model-provider credential |
| `AIAutonomy.AutoexecutedRequestedCommand` | Autoexecuted an Agent Mode requested command |
| `AIAutonomy.ChangedAgentModeAskUserQuestionPermission` | Changed Agent Mode permission for asking user questions |
| `AIAutonomy.ChangedAgentModeCodingPermissions` | Changed Agent Mode permissions for coding tasks |
| `AIAutonomy.ToggledAutoexecuteReadonlyCommandsSetting` | Toggled setting to autoexecute readonly Agent Mode requested commands |
| `Add Added Subshell Command` | Added a command to be automatically Warpified via Warp’s subshell wrapper |
| `Add Denylisted Subshell Command` | Explicitly prevent a command from being Warpified via Warp’s subshell wrapper |
| `Add Tab With Shell` | Added a tab with specific shell |
| `Added Workflow Alias` | Added an alias to a Warp Drive workflow |
| `Agent Management View Copied Session Link` | User copied a session link from the Agent Management View |
| `Agent Management View Opened Session` | User opened a session from the Agent Management View |
| `Agent Management View Toggled` | User toggled the Agent Management View open or closed |
| `Agent Mode Query Suggestion Accepted` | Prompt Suggestion accepted |
| `Agent Mode Query Suggestions Banner Shown` | Prompt Suggestions banner shown |
| `Agent Mode Setup Banner Accepted` | Agent Mode setup banner accepted |
| `Agent Mode Setup Banner Dismissed` | Agent Mode setup banner dismissed |
| `Agent Mode Setup Project Scoped Rules Action` | User clicked a button in the Agent Mode setup project scoped rules step |
| `Agent Mode.Setup Codebase Context Action` | User clicked a button in the Agent Mode setup codebase context step |
| `Agent Predict` | Completed an Agent Predict prediction |
| `Agent Toolbar Dismissed` | User dismissed the use-agent toolbar |
| `AgentManagement.AgentTypeSelectorOpened` | User opened the agent type selector from agent management |
| `AgentManagement.ArtifactClicked` | User clicked an artifact button |
| `AgentManagement.CloudRunCancelled` | User cancelled a cloud run |
| `AgentManagement.CloudRunOpened` | User opened a cloud run |
| `AgentManagement.ConversationForked` | User forked a conversation |
| `AgentManagement.ConversationLinkCopied` | User copied a conversation link |
| `AgentManagement.ConversationOpened` | User opened a conversation |
| `AgentManagement.DetailsPanelContinueLocally` | User clicked Continue locally in the details panel |
| `AgentManagement.DetailsViewed` | User clicked View details |
| `AgentManagement.DismissSetupGuide` | User dismissed the ambient agent setup guide |
| `AgentManagement.FilterChanged` | User changed a filter in the management view |
| `AgentManagement.OpenSetupGuide` | User opened the ambient agent setup guide |
| `AgentManagement.SessionLinkCopied` | User copied a session link |
| `AgentManagement.SetupGuideDocsLink` | User clicked a docs URL in the setup guide |
| `AgentManagement.SetupGuideStepCopy` | User copied a workflow step from the setup guide |
| `AgentManagement.SetupGuideStepRun` | User ran a workflow step from the setup guide |
| `AgentManagement.SlashCommandContinueLocally` | User invoked /continue-locally to fork a cloud conversation locally |
| `AgentManagement.SpawnNewCloudAgent` | User spawned a new cloud agent from agent management |
| `AgentManagement.SpawnNewLocalAgent` | User spawned a new local agent from agent management |
| `AgentManagement.TombstoneArtifactClicked` | User clicked an artifact in the tombstone view |
| `AgentManagement.TombstoneContinueInCloud` | User clicked Continue in the tombstone to start a cloud follow-up |
| `AgentManagement.TombstoneContinueLocally` | User clicked Continue locally in the tombstone |
| `AgentManagement.ViewToggled` | User toggled the agent management view open or closed |
| `AgentMode.AttachedContext` | Attached block as context to an Agent Mode query |
| `AgentMode.AttachedImages` | Attached images to an Agent Mode query |
| `AgentMode.ChangedInputType` | The input type was changed from shell -> AI or AI -> shell |
| `AgentMode.ClickedEntrypoint` | Clicked on an Agent Mode entrypoint |
| `AgentMode.Code.DiffHunksNavigated` | Agent Mode Code diff hunks navigated |
| `AgentMode.Code.DiffMatchFailed` | Failed to match code diff |
| `AgentMode.Code.FileExceededContextLimit` | File from AI exceeded context limit |
| `AgentMode.Code.FilesNavigated` | Agent Mode Code files navigated |
| `AgentMode.Code.InvalidFile` | File(s) in code diff could not be found |
| `AgentMode.Code.MalformedFinalLineProxy` | Suggested code diff likely required malformed trailing line correction (heuristic) |
| `AgentMode.Code.MissingLineNumbers` | Code diff was missing line numbers |
| `AgentMode.Code.SuggestedCodeEditedByUser` | Agent Mode Code suggestion edited by user |
| `AgentMode.Code.SuggestedEditAcceptAndContinueClicked` | User selected Accept and start conversation for a code diff suggestion in Agent Mode |
| `AgentMode.Code.SuggestedEditAcceptClicked` | User selected Accept for a code diff suggestion in Agent Mode |
| `AgentMode.Code.SuggestedEditReceived` | Agent Mode suggested a code edit |
| `AgentMode.Code.SuggestedEditResolved` | Agent Mode pending code edit suggestion resolved |
| `AgentMode.CreatedAIBlock` | Created an AI block in agent mode |
| `AgentMode.Error` | Received an error when getting Agent Mode response |
| `AgentMode.ExecutedWarpDrivePrompt` | Executed a saved prompt. |
| `AgentMode.ExitedShellProcess` | An agent-requested command caused the shell process to exit |
| `AgentMode.FileGlob.Failed` | The file glob tool failed to complete |
| `AgentMode.FileGlob.Succeeded` | The file glob tool completed successfully |
| `AgentMode.FullEmbedCodebaseContextSearch.Failed` | Failed to search full embed codebase context |
| `AgentMode.FullEmbedCodebaseContextSearch.Success` | Successfully searched full embed codebase context |
| `AgentMode.Grep.Failed` | The grep tool failed to complete |
| `AgentMode.Grep.Succeeded` | The grep tool completed successfully |
| `AgentMode.MerkleTreeSnapshot.Diff.Failed` | Failed to diff merkle tree snapshot |
| `AgentMode.MerkleTreeSnapshot.Diff.Success` | Successfully diffed merkle tree snapshot |
| `AgentMode.MerkleTreeSnapshot.Rebuild.Failed` | Failed to rebuild merkle tree from snapshot |
| `AgentMode.MerkleTreeSnapshot.Rebuild.Success` | Successfully rebuilt merkle tree from snapshot |
| `AgentMode.OpenedCitation` | Opened a citation that was surfaced in agent mode |
| `AgentMode.Orchestration.AgentProposedConfig` | An agent-authored orchestration config snapshot first became visible to the user on a plan card |
| `AgentMode.Orchestration.Entered` | Orchestration was activated in a conversation via /orchestrate or a run\_agents confirmation card surfacing. Plan-card entries are tracked separately via AgentProposedConfig + PlanConfigApprovalToggled. |
| `AgentMode.Orchestration.PillBarInteraction` | User interacted with the orchestration pill bar (switch, pin, open in pane/tab, stop, kill, etc.) |
| `AgentMode.Orchestration.PlanConfigApprovalToggled` | User toggled the Use orchestration switch on a plan card |
| `AgentMode.Orchestration.RunAgentsCardDecision` | User accepted, accepted-without-orchestration, or rejected a run\_agents confirmation card. Reports which config fields diverged from the original tool call and/or the active approved config. |
| `AgentMode.Orchestration.RunAgentsCompleted` | A run\_agents request completed with actual launched and failed child counts |
| `AgentMode.Orchestration.TeamAgentCommunicationFailed` | Failed to send an orchestration message or lifecycle event for a TeamAgent |
| `AgentMode.PotentialAutoDetectionFalsePositive` | Manually toggled input to shell mode after input was auto-detected as natural language. |
| `AgentMode.RequestRetrySucceeded` | Agent Mode request succeeded after retrying following an initial error |
| `AgentMode.SetupCreateEnvironmentAction` | User clicked a button in the Agent Mode setup create environment step |
| `AgentMode.SurfacedCitations` | Agent mode used and cited external sources that were used in its response |
| `AgentMode.SyncCodebaseContext.BuildTree.Failed` | Failed to build merkle tree for codebase context |
| `AgentMode.SyncCodebaseContext.BuildTree.Success` | Successfully built merkle tree for codebase context |
| `AgentMode.SyncCodebaseContext.Failed` | Failed to sync codebase context |
| `AgentMode.SyncCodebaseContext.Success` | Successfully synced codebase context |
| `AgentMode.ToggleAutoDetectionSetting` | Toggled the setting that enables or disables natural language auto-detection in the input. |
| `AgentNotification.Shown` | An agent notification was shown to the user (toast or mailbox) |
| `AgentTip Clicked` | User clicked a link or action in an Agent Tip |
| `AgentTip Shown` | Selected an Agent Tip to show in the Agent Mode status bar |
| `AgentView.Entered` | User entered the Agent View |
| `AgentView.Exited` | User exited the Agent View |
| `AgentView.InlineConversationMenuItemSelected` | User selected an item from the inline conversation menu |
| `AgentView.InlineConversationMenuOpened` | User opened the inline conversation menu in Agent View |
| `AgentView.ShortcutsViewToggled` | User toggled the shortcuts view in Agent View |
| `AmbientAgent.CloudMode.Entered` | User entered cloud agent view |
| `AmbientAgent.CloudMode.EnvironmentSelector.Opened` | User opened the environment selector menu |
| `AmbientAgent.CloudMode.EnvironmentSelector.Selected` | User selected an environment from the selector |
| `AmbientAgent.CloudMode.EnvironmentSettings.GitHubAuth` | User started GitHub authentication from the environment form |
| `AmbientAgent.CloudMode.EnvironmentSettings.LaunchedAgent` | User launched an environment setup agent from the environment form |
| `AmbientAgent.ConcurrencyModal.Dismissed` | User dismissed the cloud agent capacity modal |
| `AmbientAgent.ConcurrencyModal.Opened` | User opened the cloud agent capacity modal |
| `AmbientAgent.ConcurrencyModal.UpgradeClicked` | User clicked the upgrade button in the cloud agent capacity modal |
| `AmbientAgent.DispatchFailed` | Ambient agent failed to dispatch or encountered an error |
| `AmbientAgent.EnvironmentSettings.CreatedEnvironment` | User created a new environment |
| `AmbientAgent.EnvironmentSettings.DeletedEnvironment` | User deleted an environment |
| `AmbientAgent.EnvironmentSettings.Image.Suggested` | Docker image was suggested for an environment |
| `AmbientAgent.EnvironmentSettings.Image.SuggestionFailed` | Docker image suggestion failed |
| `AmbientAgent.EnvironmentSettings.Opened` | User opened the environment management pane |
| `AmbientAgent.EnvironmentSettings.UpdatedEnvironment` | User updated an existing environment |
| `AmbientAgent.Handoff.Initiated` | User initiated a local-to-cloud handoff |
| `AmbientAgent.Handoff.SleepPrompt.Dismissed` | User dismissed the auto-handoff sleep discoverability prompt |
| `AmbientAgent.Handoff.SleepPrompt.Enabled` | User enabled auto-handoff on sleep from the discoverability prompt |
| `AmbientAgent.Handoff.SleepPrompt.Shown` | The auto-handoff sleep discoverability prompt was shown on wake |
| `AmbientAgent.Handoff.SnapshotPrepared` | Handoff snapshot upload settled; reports whether it carried content |
| `AmbientAgents.ThirdPartyHarness.Exit.Escalation` | One attempt (initial exit, follow-up retry, or force-kill) in the harness exit escalation ladder. |
| `AmbientAgents.ThirdPartyHarness.RuntimeError.Detected` | Runtime output scanner detected a known failure substring in a third-party harness block. |
| `Anonymous User Attempted Login-Gated Feature` | Anonymous user attempted to access a login-gated feature |
| `Anonymous User Expiration Lockout` | An anonymous user opened Warp after their conversion deadline and was locked out |
| `Anonymous User Hit Cloud Object Limit` | Anonymous user attempted to create a cloud object past their personal object limit |
| `Anonymous User Initiated Signup` | An anonymous user initiated the sign up flow |
| `Anonymous User Linked from Browser` | Received an auth payload from anonymous user after linking in browser |
| `App Download Source` | Whether the Warp was installed from the home page or through homebrew |
| `App Startup` | App is launched |
| `Attached Workflow Alias Environment Variables` | Added or removed environment variables for a Warp Drive workflow alias |
| `Attempting to Relaunch for Update` | Attempted to relaunch the app after installing an update |
| `Auth Common Question Clicked in App` | Clicked on “Common Question” when logging in |
| `Auth: Open Privacy Settings Overlay` | Privacy settings are open during sign-in |
| `Auth: Toggle Common Questions` | Toggled FAQ Page when logging in |
| `Background Block Started` | Warp created a background-output Block (whenever a processes has been backgrounded and yields some output) |
| `Block Creation` | Created Block |
| `Block Filter Toolbelt Button Clicked` | Clicked the block filter icon in the top-right of a block |
| `Block Selection` | Selected Block |
| `Bootstrap Slow Contents` | Contents of the bootstrap block if bootstrapping is slow |
| `Bootstrapping Slow` | Slow bootstrap on session startup |
| `Bootstrapping Succeeded` | Successful bootstrap for session |
| `CLI Subagent Action Executed` | User approved a blocked action from the CLI subagent |
| `CLI Subagent Action Rejected` | User rejected a blocked action from the CLI subagent |
| `CLI Subagent Control State Changed` | Control state changed in CLI subagent (agent in control, agent blocked, user in control, or agent tagged in) |
| `CLI Subagent Input Dismissed` | User dismissed the input in the CLI subagent |
| `CLI Subagent Responses Toggled` | User toggled the visibility of agent responses in CLI subagent |
| `CLI.Execute.Agent.Create` | Created an agent from the Warp CLI |
| `CLI.Execute.Agent.Delete` | Deleted an agent from the Warp CLI |
| `CLI.Execute.Agent.Get` | Got agent details from the Warp CLI |
| `CLI.Execute.Agent.List` | Listed agents from the Warp CLI |
| `CLI.Execute.Agent.Profile.List` | Listed agent profiles from the Warp CLI |
| `CLI.Execute.Agent.Run` | Ran an agent from the Warp CLI |
| `CLI.Execute.Agent.RunAmbient` | Ran an ambient agent from the Warp CLI |
| `CLI.Execute.Agent.Skills` | Listed agent skills from the Warp CLI |
| `CLI.Execute.Agent.Update` | Updated an agent from the Warp CLI |
| `CLI.Execute.ApiKey.Create` | Created an API key from the Warp CLI |
| `CLI.Execute.ApiKey.Expire` | Expired an API key from the Warp CLI |
| `CLI.Execute.ApiKey.List` | Listed API keys from the Warp CLI |
| `CLI.Execute.Artifact.Download` | Downloaded an artifact from the Warp CLI |
| `CLI.Execute.Artifact.Get` | Got artifact metadata from the Warp CLI |
| `CLI.Execute.Artifact.Upload` | Uploaded an artifact from the Warp CLI |
| `CLI.Execute.Conversation.Get` | Got conversation by ID from the Warp CLI |
| `CLI.Execute.Environment.Create` | Created a cloud environment from the Warp CLI |
| `CLI.Execute.Environment.Delete` | Deleted a cloud environment from the Warp CLI |
| `CLI.Execute.Environment.Get` | Got cloud environment details from the Warp CLI |
| `CLI.Execute.Environment.Image.List` | Listed available base images from the Warp CLI |
| `CLI.Execute.Environment.List` | Listed cloud environments from the Warp CLI |
| `CLI.Execute.Environment.Update` | Updated a cloud environment from the Warp CLI |
| `CLI.Execute.Federate.IssueGcpToken` | Issued a GCP federated identity token from the Warp CLI |
| `CLI.Execute.Federate.IssueToken` | Issued a federated identity token from the Warp CLI |
| `CLI.Execute.HarnessSupport.FinishTask` | Reported task completion via harness-support from the Warp CLI |
| `CLI.Execute.HarnessSupport.NotifyUser` | Sent a user notification via harness-support from the Warp CLI |
| `CLI.Execute.HarnessSupport.Ping` | Pinged harness-support from the Warp CLI |
| `CLI.Execute.HarnessSupport.ReportArtifact` | Reported an artifact via harness-support from the Warp CLI |
| `CLI.Execute.HarnessSupport.ReportShutdown` | Reported agent shutdown via harness-support from the Warp CLI |
| `CLI.Execute.Integration.Create` | Created an integration from the Warp CLI |
| `CLI.Execute.Integration.List` | Listed integrations from the Warp CLI |
| `CLI.Execute.Integration.Update` | Updated an integration from the Warp CLI |
| `CLI.Execute.Login` | Logged in via the Warp CLI |
| `CLI.Execute.Logout` | Logged out via the Warp CLI |
| `CLI.Execute.MCP.List` | Listed MCP servers from the Warp CLI |
| `CLI.Execute.MemoryStore.CreateMemory` | Created a manual memory in a memory store from the Warp CLI |
| `CLI.Execute.MemoryStore.DeleteMemory` | Deleted a memory from a memory store from the Warp CLI |
| `CLI.Execute.MemoryStore.GetStore` | Got a memory store from the Warp CLI |
| `CLI.Execute.MemoryStore.List` | Listed memory stores from the Warp CLI |
| `CLI.Execute.MemoryStore.ListMemories` | Listed memories in a memory store from the Warp CLI |
| `CLI.Execute.MemoryStore.ListStoreAgents` | Listed agents attached to a memory store from the Warp CLI |
| `CLI.Execute.MemoryStore.ListVersions` | Listed version history of a memory from the Warp CLI |
| `CLI.Execute.MemoryStore.UpdateMemory` | Updated a memory in a memory store from the Warp CLI |
| `CLI.Execute.MemoryStore.UpdateStore` | Updated a memory store from the Warp CLI |
| `CLI.Execute.Model.List` | Listed models from the Warp CLI |
| `CLI.Execute.Provider.List` | Listed providers from the Warp CLI |
| `CLI.Execute.Provider.Setup` | Set up a provider via the Warp CLI |
| `CLI.Execute.Run.Conversation.Get` | Got run conversation from the Warp CLI |
| `CLI.Execute.Run.Message.List` | Listed run messages from the Warp CLI |
| `CLI.Execute.Run.Message.MarkDelivered` | Marked a run message as delivered from the Warp CLI |
| `CLI.Execute.Run.Message.Read` | Read a run message from the Warp CLI |
| `CLI.Execute.Run.Message.Send` | Sent a run message from the Warp CLI |
| `CLI.Execute.Run.Message.Watch` | Watched run messages from the Warp CLI |
| `CLI.Execute.Runner.Create` | Created a runner from the Warp CLI |
| `CLI.Execute.Runner.Delete` | Deleted a runner from the Warp CLI |
| `CLI.Execute.Runner.List` | Listed runners from the Warp CLI |
| `CLI.Execute.Runner.Update` | Updated a runner from the Warp CLI |
| `CLI.Execute.Schedule.Create` | Created a scheduled agent from the Warp CLI |
| `CLI.Execute.Schedule.Delete` | Deleted a scheduled agent from the Warp CLI |
| `CLI.Execute.Schedule.Get` | Got scheduled agent configuration from the Warp CLI |
| `CLI.Execute.Schedule.List` | Listed scheduled agents from the Warp CLI |
| `CLI.Execute.Schedule.Pause` | Paused a scheduled agent from the Warp CLI |
| `CLI.Execute.Schedule.Unpause` | Unpaused a scheduled agent from the Warp CLI |
| `CLI.Execute.Schedule.Update` | Updated a scheduled agent from the Warp CLI |
| `CLI.Execute.Secret.Create` | Created a secret from the Warp CLI |
| `CLI.Execute.Secret.Delete` | Deleted a secret from the Warp CLI |
| `CLI.Execute.Secret.List` | Listed secrets from the Warp CLI |
| `CLI.Execute.Secret.Update` | Updated a secret from the Warp CLI |
| `CLI.Execute.Task.Get` | Got status of task from the Warp CLI |
| `CLI.Execute.Task.List` | Listed tasks from the Warp CLI |
| `CLI.Execute.Whoami` | Printed current user info from the Warp CLI |
| `CLIAgentFooter.ImageAttached` | User attached an image from the CLI agent footer |
| `CLIAgentFooter.SettingToggled` | User toggled the CLI agent footer setting |
| `CLIAgentFooter.Shown` | CLI agent footer was shown to the user |
| `CLIAgentFooter.VoiceInputUsed` | User used voice input from the CLI agent footer |
| `CLIAgentPlugin.ChipClicked` | User clicked the plugin install or update chip |
| `CLIAgentPlugin.ChipDismissed` | User dismissed the plugin install or update chip |
| `CLIAgentPlugin.Detected` | A CLI agent plugin was detected via a SessionStart event |
| `CLIAgentPlugin.OperationFailed` | Auto plugin install or update failed |
| `CLIAgentPlugin.OperationSucceeded` | Auto plugin install or update completed successfully |
| `CLIAgentRichInput.Closed` | CLI agent Rich Input was closed |
| `CLIAgentRichInput.Opened` | User opened CLI agent Rich Input |
| `CLIAgentRichInput.Submitted` | User submitted a prompt via CLI agent Rich Input |
| `Changed invite view option` | Toggled between link and invite for invite |
| `ChatGPTPlanModal.Dismissed` | The user dismissed the “You’re using your ChatGPT plan” modal |
| `ChatGPTPlanModal.ManageUsageClicked` | The user opened ChatGPT usage settings from the “You’re using your ChatGPT plan” modal |
| `ChatGPTPlanModal.Shown` | The “You’re using your ChatGPT plan” modal was shown to the user |
| `Clicked Continue Conversation Button` | User clicked the Continue Conversation button in a block footer |
| `Clicked Reset to Defaults Button in Settings Import` | Reset the imported settings in the settings import onboarding block |
| `Clone Repo Prompt Submitted` | User submitted a repository URL from the clone repo view |
| `Code Pane Opened` | Opened the code editor pane from various sources |
| `CodePanels.FileOpened` | Opened a file from code review, project explorer, or global search |
| `CodeReview.AddToContext` | Content added to AI context from code review |
| `CodeReview.BaseChanged` | Diff base changed in code review |
| `CodeReview.CommentAdded` | Inline code review comment added |
| `CodeReview.CommentDeleted` | Inline code review comment deleted |
| `CodeReview.CommentEdited` | Inline code review comment edited |
| `CodeReview.CommentEditorOpened` | Inline code review comment editor opened |
| `CodeReview.CommentListExpanded` | Inline code review comment list expanded |
| `CodeReview.CommentListItemClicked` | Inline code review comment list item clicked |
| `CodeReview.CommentRelocationFailed` | Inline code review comment relocation fell back to approximate line |
| `CodeReview.CommentResolved` | Inline code review comment resolved |
| `CodeReview.CommentsAttached` | Newly-imported comments relocated against editor lines |
| `CodeReview.CommentsReceived` | Agent insert\_code\_review\_comments tool call received and processed |
| `CodeReview.DiffLoadCompleted` | Diff content loaded successfully |
| `CodeReview.FileSaved` | File saved in code review pane |
| `CodeReview.FindBarModeChanged` | Search mode changed in code review find bar |
| `CodeReview.FindBarToggled` | Code review find bar opened or closed |
| `CodeReview.FindNavigated` | Navigated to next or previous match in code review find bar |
| `CodeReview.GitButtonTriggered` | User clicked a git operation button in the code review header |
| `CodeReview.GitDialogCompleted` | Git operation dialog reached a terminal state (succeeded, failed, or cancelled) |
| `CodeReview.LoadDiffFailed` | Failure when loading diff content |
| `CodeReview.LoadMetadataFailed` | Failure when calculating diff metadata |
| `CodeReview.PaneOpened` | Code review pane opened |
| `CodeReview.PaneStateChanged` | Code review pane minimized or maximized |
| `CodeReview.RevertHunkClicked` | Revert hunk button clicked |
| `CodeReview.ReviewSubmitted` | Inline code review submitted to agent |
| `CodeView.SelectionAddedAsContext` | Added selected code as context from the code editor |
| `CodexModal.Opened` | User opened the Codex modal |
| `CodexModal.UseCodexClicked` | User clicked ‘Use Codex’ in the Codex modal |
| `Command File Run` | Opened a .cmd or unix executable file and ran it directly in Warp |
| `Command Palette Search Accepted` | Accepted a command palette search result |
| `Command Palette Search Exited` | Exited command palette search without accepting a result |
| `Command Search Exited` | Exited command search (universal search panel to search) without accepting a result |
| `Command Search Opened` | Opened command search (universal search panel to search) |
| `Command Search Result Accepted` | Accepted command search result |
| `Complete Welcome Tip` | Completed all welcome tips items |
| `Completed Settings Import` | Imported a terminal’s settings via the settings import onboarding block |
| `ComputerUse.Approved` | A RequestComputerUse action was approved (manually or auto-executed) |
| `ComputerUse.Cancelled` | A RequestComputerUse action was cancelled/rejected |
| `Confirm Suggestion` | Accepted tab completion suggestion |
| `Context Menu Copy` | Clicked “Copy” in context menu |
| `Context Menu Copy Prompt` | Clicked “Copy Prompt” in context menu |
| `Context Menu Insert Selected Text into Input` | Clicked “insert into input” in context menu |
| `Context Menu Toggle Git Prompt Dirty Indicator` | Toggled indicator of dirty git prompt |
| `Context Menu: Find Within Blocks` | Clicked “find within blocks” in context menu |
| `Context Menu: Initiate Block Sharing` | Opened “Share” modal via context menu |
| `Context Menu: Reinput Commands` | Clicked “reinput commands” in context menu |
| `ConversationList.ItemDeleted` | Deleted a conversation from the conversation list |
| `ConversationList.ItemOpened` | Opened a conversation from the conversation list |
| `ConversationList.LinkCopied` | Copied a conversation link from the conversation list |
| `ConversationList.Opened` | Opened the conversation list view in the left panel |
| `Copied Shared Session Link` | Copied a shared session link |
| `Copy Block Sharing Link` | Clicked “Share block…” in context menu |
| `Copy Invite Link` | Clicked “Copy Link” on Referral Modal |
| `Copy Obfuscated Secret` | Copied a secret’s obfuscated contents to clipboard |
| `Copy Object To Clipboard` | Copied an object to the user’s keyboard |
| `Create Custom Theme` | Created a custom theme using the built-in theme creator |
| `Create Project Prompt Submitted` | User submitted a prompt from the create project view |
| `Create Project Prompt Submitted Content` | User submitted custom prompt content from the create project view |
| `Custom Secret Regex Added` | Custom Secret Regex Added |
| `Database Read Error` | Database read error when trying to get app state for session restoration |
| `Database Startup Error` | Failed to initialize sqlite upon startup |
| `Database Write Error` | Database write error when trying to write app state for session restoration |
| `Decline Subshell Bootstrap` | Developer declined the Warp banner to Warpify the current session |
| `Delete Custom Theme` | Deleted a custom theme using the built-in theme creator |
| `Deleted Notebook` | Deleted notebook from Warp Drive team |
| `Deleted Workflow` | Deleted workflow from Warp Drive team |
| `Disable Input Sync Inputs` | Disabled / turn off the Input Synchronization (across editors) |
| `Dismiss Alias Expansion Banner` | Dismissed the banner to enable automatic alias expansion within the Input Editor |
| `Dismiss Welcome Tips` | Dismissed Welcome tips |
| `Don't Show Sharer Grant Modal Again` | When you check don’t show again on the confirmation modal for granting a role |
| `Drag and Drop Tab` | Tab dragged and dropped |
| `Drag and Drop Tab Group` | Tab group dragged and dropped |
| `Duplicate Object` | Cloned a Warp Drive object |
| `Edited Workflow Alias Argument` | Edited an argument in a Warp Drive workflow alias |
| `Enable Alias Expansion From Banner` | Enabled automatic alias expansion within the Input Editor from the banner |
| `Executed Conversation Rewind` | User executed a rewind to a previous conversation state |
| `Expanded Code Suggestion` | Expanded the passive code diff suggestion |
| `Export Object` | Exported a Warp Drive object |
| `Features Page Action` | Changed settings in Features Page |
| `File Tree Toggled` | Opened the file tree/project explorer |
| `FileTree.AttachedAsContext` | Attached a file or directory as context from the file tree |
| `FileTree.ItemCreated` | Created a new file from the file tree |
| `Find Option Toggled` | Changed settings in Find Toggle |
| `Focused Config in Settings Import` | Selected a terminal in the settings import onboarding block |
| `FreeAiRemovalModal.CtaClicked` | The user clicked a CTA in the free AI removal notice modal |
| `FreeAiRemovalModal.Dismissed` | The user dismissed the free AI removal notice modal |
| `FreeAiRemovalModal.Shown` | The free AI removal notice modal was shown to the user |
| `Generate Block Sharing Link` | Generated Block sharing link |
| `Generate Metadata For Workflow Error` | Failed to generate metadata for a workflow using Warp AI |
| `Generate Metadata For Workflow Success` | Successfully generated metadata for a workflow using Warp AI |
| `Get Started Skip to Terminal` | User clicked skip to terminal from get started view |
| `Global Search Opened` | Opened the global search view |
| `Global Search Query Completed` | Completed a global search across local and remote sources |
| `Global Search Query Started` | Started a global search (warp\_ripgrep) search |
| `ITerm Profile has Multiple Hotkeys` | Attempted to import an iTerm profile that contained multiple hotkey window bindings |
| `Identified Antivirus Software` | Identified running antivirus software on the user’s machine |
| `InitialWorkingDirectoryConfigurationChanged` | Replaced the default working directory with a different path |
| `Initiate Reauth` | Started the flow to re-authenticate the client |
| `Input Mode Changed` | Changed the Input Editor Mode (Pinned to Bottom, Pinned to Top, Classic / Waterfall Mode) |
| `Input.AtMenuInteracted` | Interacted with the @ menu |
| `Input.InputUXModeChanged` | Changed the input UX mode |
| `Input.VoiceInputUsed` | Used voice input |
| `InputBoxAICommandSearch` | Opened AI Command Search via the Input Editor’s context menu (right clicking the buffer) |
| `InputBoxAskWarpAI` | Clicked “Ask Warp AI” from the Input Editor’s context menu |
| `InputBoxCommandSearch` | Opened Command Search via the Input Editor’s context menu (right clicking the buffer) |
| `InputBoxCutSelectedText` | Copied selected text from Input Editor |
| `InputBoxPaste` | Pasted text into the Input Editor’s via its context menu (right clicking the buffer) |
| `InputBoxSelectAll` | Selected all the text in the Input Editor via its context menu (right clicking the buffer) |
| `Invited Teammates` | Sent emails to invite teammates to join Warp Drive team |
| `Invoked Environment Variables` | Invoked an environment variables object |
| `Isolation.DetectedIsolationPlatform` | Detected that Warp is running in an isolated sandbox |
| `Joined Shared Session` | When you join another instance of Warp using shared sessions |
| `Jumped to Bookmark Block` | Jumped to bookmarked Block |
| `Jumped to Bottom of Block Button Clicked` | Used the button to jump to the bottom of a Block |
| `Jumped to Latest Agent Message` | Jumped to the latest agent message |
| `Jumped to Previous Command` | Jumped to a previous command |
| `Jumped to Shared Session Participant` | Clicked on a shared session participant avatar to jump to their location in the session |
| `Keybinding Changed` | Edited a custom keybinding |
| `Keybinding Removed` | Removed / cleared a keybinding |
| `Keybinding Reset to Default` | Reset a custom keybinding to its default |
| `Knowledge Pane Opened` | Knowledge Pane Opened |
| `Linear.IssueLinkOpened` | User opened a warp\://linear deeplink to work on an issue |
| `Log In Button Clicked in App` | Clicked on “Log in” button |
| `Log Out` | Logged out of the Warp client |
| `Log Out Modal Cancel Pressed` | Escaped the log out flow by canceling the log out modal |
| `Log Out Modal Shown` | When the log out modal is displayed |
| `Logged in to native app` | Login is successful |
| `Logged-out App Startup` | Started Warp in the logged-out / signed-out state |
| `Login Later Button Clicked` | Clicked “Login later” button |
| `Login Later Confirmation Button Clicked` | Clicked “Yes, skip login” confirmation button |
| `Lsp.ControlAction` | User performed an LSP control action from the footer menu |
| `Lsp.FindReferencesShown` | Find references card displayed via LSP |
| `Lsp.GotoDefinition` | User triggered goto definition via LSP |
| `Lsp.HoverShown` | Hover tooltip displayed with LSP content or diagnostics |
| `Lsp.ServerEnabled` | User enabled an LSP server for a workspace |
| `Lsp.ServerEnablementSkipped` | User skipped LSP enablement during /init |
| `Lsp.ServerFailed` | LSP server failed to start |
| `Lsp.ServerInstallCompleted` | An LSP server installation finished |
| `Lsp.ServerRemoved` | User removed an LSP server |
| `Lsp.ServerStarted` | LSP server successfully started and is available |
| `MCP Server Added` | MCP Server Added |
| `MCP Server Collection Pane Opened` | MCP Server Collection Pane Opened |
| `MCP Server Spawned` | MCP Server Spawned |
| `MCP Template Created` | MCP Template Created |
| `MCP Template Installed` | MCP Template Installed |
| `MCP Template Shared` | MCP Template Shared |
| `MCP Tool Call Accepted` | MCP Tool Call Accepted |
| `Move Active Tab` | Move active tab left or right |
| `Move Tab` | Move tab left or right |
| `Needs Reauth` | User needs to re-authenticate |
| `New Session From Directory` | Dragged a file, folder, etc. into Warp to start a session |
| `Notebook Action` | Took an action on a notebook: edit, delete, modified font size, etc. |
| `Notebook Edited` | Edited a notebook |
| `Notebook Opened` | Opened a notebook |
| `Notification Clicked` | Clicked desktop notification sent from Warp |
| `Notification Failed to Send` | Failed to send desktop notification |
| `Notification Permissions Requested` | Requested permission for desktop notification permissions |
| `Notification Request Permissions Outcome` | Recorded outcome of attempting to request desktop notification permissions |
| `Notification Sent` | Sent desktop notification |
| `Notifications Discovery Banner Action` | Showed banner introducing the notifications feature |
| `Notifications Error Banner Action` | Showed error banner for notifications feature |
| `Object Link Copied` | The web link to an object has been copied. |
| `Open Launch Config` | Opened launch config for a session |
| `Open Launch Config File` | Opened the launch config YAML file from modal once saved successfully |
| `Open Palette` | Opened the palette |
| `Open Quake Mode Window` | Toggled quake mode window when previously hidden or closed |
| `Open Repo Folder Submitted` | User selected a folder to open as a repo from the “Open repository” button |
| `Open Save Config Modal` | Opened save launch configuration modal |
| `Open Slash Menu` | Opened the slash commands menu |
| `Open Team from URI` | Showed settings view of their newly joined team within the app |
| `Open Theme Chooser` | Opened theme chooser (list of different themes and visualizations of those themes) |
| `Open Theme Creator Modal` | Opened theme creator modal (modal to create a new theme) |
| `Open Welcome Tips` | Opened welcome tips in app |
| `Open Workflows Search` | Opened workflows search in command search pane |
| `OpenAndWarpifyDockerSubshell` | Warpifying a docker subshell from using the docker extension |
| `OpenInputBoxContextMenu` | Opened the Input Editor’s context menu |
| `Opened Changelog Link` | Opened the changelog link within the App |
| `Opened Rewind Confirmation Dialog` | User opened the rewind confirmation dialog |
| `Opened Save As Workflow Modal` | Opened the modal to create a new workflow using a Block’s context—command, etc. |
| `Opened Sharing Dialog` | Opened the sharing settings dialog for a session or Warp Drive object |
| `Opened Warp AI` | Activated Warp AI |
| `Opened alt screen find bar` | Opened the Find bar in the Alt Screen |
| `Page Up/Down In Editor Pressed` | Pressed `PAGE-UP` or `PAGE-DOWN` within the Input Editor |
| `Pane Drag Ended` | Ended dragging a pane via the pane header |
| `Pane Drag Inititiated` | Initiated dragging a pane via the header |
| `Parameterized Workflow With Environment Variables` | Selected from environment variables dropdown to parameterize workflow |
| `Preview Pane Promoted` | Promoted a preview code tab to a normal tab |
| `PricingPromotion.Clicked` | A pricing promotion was clicked |
| `PricingPromotion.Dismissed` | A pricing promotion was dismissed |
| `PricingPromotion.Shown` | A pricing promotion was shown |
| `Prompt Edited` | Edited the prompt using the built-in prompt editor |
| `Prompt Editor Opened` | Opened the prompt editor |
| `Pty Spawned` | Tracks the manner by which we create a new shell process (new codepath vs. old codepath). Used to ensure nothing breaks as we change parts of our infrastructure. |
| `QueuedPrompt.Deleted` | User deleted a queued prompt row |
| `QueuedPrompt.Edited` | User committed a non-empty edit to a queued prompt row |
| `QueuedPrompt.PanelCollapseToggled` | User toggled the queued prompts panel collapse state |
| `QueuedPrompt.Reordered` | User reordered a queued prompt row via drag-and-drop |
| `QueuedPrompt.SentNow` | User sent a queued prompt row immediately (send-now button or Enter on empty input) |
| `Quit Modal Cancel Pressed` | `Cancel` button on the alert modal was pressed |
| `Quit Modal Disabled` | The quit modal dialog has been disabled and will not popup when a user closes Warp while a session is running |
| `Quit Modal Shown` | Showed an alert modal to warn the user about closing the app/window with a running process |
| `Received Subshell RC File DCS` | Spawned a subshell to be automatically Warpified |
| `Recent Menu Item Selected` | User selected an item from the recents list on the new tab zero state |
| `Recording.Started` | A computer-use video recording was started |
| `Recording.Stopped` | A computer-use video recording was stopped and finalized |
| `RemoteCodebaseIndex.AutoIndexRequested` | Remote codebase auto-indexing requested one or more repositories |
| `RemoteCodebaseIndex.StatusChanged` | The remote codebase index status changed |
| `RemoteServer.BinaryCheck` | Remote server binary check completed (found, not found, or error) |
| `RemoteServer.ClientRequestError` | A client request to the remote server failed |
| `RemoteServer.DaemonStartup` | Remote server daemon startup completed and socket bound |
| `RemoteServer.Disconnection` | An established remote server connection was dropped |
| `RemoteServer.HostUnsupported` | Preinstall check classified the remote host as unsupported, falling back to the wrapper-only SSH flow |
| `RemoteServer.Initialization` | Remote server connection and initialization completed (success or failure) |
| `RemoteServer.Installation` | Remote server binary installation completed (success or failure) |
| `RemoteServer.MessageDecodingError` | A server message could not be decoded (no parseable request\_id) |
| `RemoteServer.ReconnectExhausted` | All reconnection attempts were exhausted after a spontaneous disconnect |
| `RemoteServer.Reconnection` | A reconnection attempt succeeded after a spontaneous disconnect |
| `RemoteServer.SetupDuration` | End-to-end duration of the remote server setup flow |
| `Remove Added Subshell Command` | Removed a command from the list of commands to automatically Warpify via Warp’s subshell wrapper |
| `Remove Denylisted Subshell Command` | Removed a command from the list of commands to IGNORE when trying to Warpify via Warp’s subshell wrapper |
| `Removed Workflow Alias` | Removed an alias from a Warp Drive workflow |
| `Removed user from team` | Remove user from Warp Drive team |
| `RepoMetadata.BuildTree.Failed` | Failed to build file tree for repo metadata |
| `Resource Center Keybindings Page Opened` | Opened the keybinding page within the resource center |
| `Resource Center Opened` | Opened Resource Center pane |
| `Resource Center Tips Completed` | Completed resource center tips |
| `Resource Center Tips Skipped` | Skipped welcome tips for new users |
| `SSH Bootstrap Attempt` | Attempted bootstrapping for an SSH session |
| `SSH ControlMaster Error` | Encountered a ControlMaster error during an SSH session |
| `SSH Remote Server Choice Do Not Ask Again Toggled` | Toggled the ‘Don’t ask me this again’ checkbox on the SSH remote-server choice block |
| `Save Launch Config` | Saved current launch configuration of windows, tabs, and panes |
| `Select App Icon` | Selected app icon |
| `Select Command Palette Option` | Selected option from command palette (i.e. CMD-P) |
| `Select Cursor Type` | Selected cursor type |
| `Select Navigation Palette Item` | Selected session from the Session Navigation Palette (search across panes, tabs, and windows) |
| `Select Theme` | Selected theme |
| `Sent email invites` | Sent email invites for Warp Drive team |
| `Session Abandoned Before Bootstrap` | Abandoned session before the bootstrapping completes |
| `Set Line Height` | Set line height through Settings -> Appearance |
| `Set New Windows at Custom Size` | Set new windows at custom size through Settings -> Appearance |
| `Set SSH Extension Install Mode` | Changed the SSH extension install mode (always ask / always allow / always skip) |
| `Set Window Blur Radius` | Changed the blur radius from the `Settings -> Appearance` dialog |
| `Set Window Opacity` | Changed the opacity (window transparency) from the `Settings -> Appearance` dialog |
| `Settings Import Initiated` | Started the import settings flow for new users |
| `Settings.Environments.PageOpened` | User opened the Environments settings page |
| `Shared Object Limit Hit Banner View Plans Button Clicked` | Clicked the ‘View Plans’ button on the persistent drive banner |
| `Sharer Cancelled Grant Role` | When you cancel granting a role to a shared session participant |
| `Shell Terminated Prematurely` | The shell process terminated prematurely |
| `Show Alias Expansion Banner` | Displayed the banner asking whether Warp should automatically expand aliases within the Input Editor |
| `Show Subshell Banner` | Displayed the banner asking whether Warp should Warpify the current session via Warp’s subshell wrapper |
| `ShowNotificationsDiscoveryBanner` | Showed notifications discovery banner in the block list |
| `ShowNotificationsErrorBanner` | Showed error banner for notifications feature |
| `Showed File in File Explorer` | Opened a file in Finder by using “Show in Finder” |
| `Sign Up Button Clicked in App` | Clicked “Sign Up” button |
| `Skill.Opened` | A skill was opened from an ‘open skill’ button or /edit-skill command |
| `Skill.Read` | A skill was read via the ReadSkill tool call |
| `Skip Onboarding Survey` | Skipped onboarding survey as a whole |
| `Slash Command Accepted` | User accepted a slash command |
| `Split Pane` | Split tab into multiple panes |
| `Static Prompt Suggestion Accepted` | Static Prompt Suggestion accepted |
| `Static Prompt Suggestions Banner Shown` | Static Prompt Suggestions banner shown |
| `Suggested Code Diff Banner Shown` | Suggested Code Diff banner shown |
| `Suggested Code Diff Failed` | Suggested Code Diff Failed |
| `Suggested Prompt Accepted` | Suggested prompt accepted |
| `Suggested Prompt Cancelled` | Suggested prompt cancelled |
| `Suggested Prompt Shown` | Suggested prompt shown |
| `SuperGrok.Connect.Finished` | SuperGrok subscription OAuth connection flow finished (success or failure). |
| `SuperGrok.Connect.Initiated` | User clicked Connect SuperGrok subscription; OAuth connection attempt initiated. |
| `Tab Creation` | Created a tab |
| `Tab Operations` | Took operation on a tab: change color, close tab, close adjacent tabs, etc. |
| `Tab Renamed` | Changed tab title |
| `TabConfigs.ExistingConfigOpened` | User opened an existing saved tab config |
| `TabConfigs.GuidedModalOpened` | User opened the guided Create a tab config modal |
| `TabConfigs.GuidedModalSubmitted` | User submitted the guided Create a tab config modal |
| `TabConfigs.MenuCreateNewTabConfigClicked` | User clicked the New tab config entry from the tab configs menu |
| `TabConfigs.NewWorktreeConfigOpened` | User opened a new worktree config from the submenu or new worktree modal |
| `Team Created` | Created a Warp Drive team |
| `Team Joined` | Joined a Warp Drive team |
| `Team Left` | Left a Warp Drive team |
| `Team Link Copied` | Copied a Warp Drive team link |
| `Terminal Lifecycle Recovery` | A terminal lifecycle transition required conservative handling or recovery |
| `Thin Strokes Setting Changed` | Changed thin strokes setting in settings -> Appearance |
| `Tier Limit Hit` | User hit the tier limit for a feature |
| `Toggle Active AI Enablement` | Toggled active AI enablement. |
| `Toggle Agent Mode Codebase Context` | Toggled on/off the enablement of codebase context usage for Agent Mode. |
| `Toggle Agent Mode Query Suggestions Setting` | Toggled on/off the prompt suggestions setting |
| `Toggle Approvals Modal` | Opened or closed teams modal |
| `Toggle Block Filter Case Sensitivity` | Toggled on/off case sensitivity within the block filter editor |
| `Toggle Block Filter Invert` | Toggled on/off invert within the block filter editor |
| `Toggle Block Filter Query` | Toggled on/off a block filter query |
| `Toggle Block Filter Regex` | Toggled on/off regex within the block filter editor |
| `Toggle Code Suggestions Setting` | Toggled on/off the code suggestions setting |
| `Toggle Codebase Context Autoindexing` | Toggled on/off the enablement of autoindexing for codebase context. |
| `Toggle Dim Inactive Panes` | Whether the dim inactive panes feature has been toggled |
| `Toggle Focus Pane On Hover` | Toggled on/off focus pane on hover feature, which causes panes to automatically focus when hovering over them |
| `Toggle Git Operations Autogen Setting` | Toggled on/off the git operations autogen setting |
| `Toggle Global AI Enablement` | Toggled global AI enablement. |
| `Toggle Intelligent Autosuggestions Setting` | Toggled on/off the intelligent autosuggestions setting |
| `Toggle Jump to Bottom of Block Button` | Enabled or disabled the Jump to Bottom of Block Button |
| `Toggle Ligature Rendering` | Toggled ligature rendering |
| `Toggle New Windows at Custom Size` | Whether the new windows at custom size feature has been toggled |
| `Toggle Obfuscate Secret` | Revealed or hid a secret |
| `Toggle Preserve Active Tab Color` | Enabled or disabled preserving the active tab color |
| `Toggle Restore Session` | Toggled session restoration (“Restore windows, tabs, panes, on startup”) |
| `Toggle SSH Warpification` | Changed the setting for SSH sessions to be warified |
| `Toggle Same Line Prompt` | Toggled on/off same line prompt |
| `Toggle Secret Redaction` | Toggled on/off the setting for Secret Redaction - attempts to redact secrets and sensitive information |
| `Toggle Settings Sync` | Toggle Settings Sync |
| `Toggle SharedBlock Title Generation` | Toggled on/off the shared block title generation setting |
| `Toggle Show Agent Tips` | Toggled the Show Agent Tips setting in AI settings |
| `Toggle Show Block Dividers` | Enabled or disabled the Show Block Dividers Button |
| `Toggle Sticky Command Header in Active Pane` | Expanded or collapsed the sticky command header in the active pane |
| `Toggle Sync Inputs Across All Panes in All Tabs` | Enable the synchronization of the Input Editor’s buffer to all the panes in all the tabs |
| `Toggle Sync Inputs Across All Panes in Current Tab` | Enable the synchronization of the Input Editor’s buffer to all the panes in the current tab |
| `Toggle Tab Indicators` | Enabled or disabled the tab indicators (failed command, etc.) |
| `Toggle Voice Input Setting` | Toggled on/off the voice input setting |
| `Toggle Warp AI` | Toggled Warp AI—an AI assistant to help you debug errors, look up forgotten commands and more |
| `Toggled Bookmark Block` | Bookmarked or unbookmarked Block |
| `Toggled Tab Bar Visibility` | Toggled when to display the tab bar |
| `Tried to Execute Before Precmd` | Attempted to execute command before precmd, a shell stage that has metadata on a command such as ssh, prompt info, etc. |
| `Trigger Subshell Bootstrap` | Attempted to Warpify the current session via Warp’s subshell wrapper |
| `Unable to Update To New Version` | Update available but not authorized to install |
| `Undo Close` | Re-opened a closed tab or window (undo closing a tab or window) |
| `Unsupported Shell` | Booted Warp with a shell that isn’t supported |
| `Update Block Filter Query` | When a new filter is applied to a block |
| `Update Block Filter Query With Context Lines` | When the number of context lines for a block filter query is updated |
| `Update Tab Close Button Position` | Updated the tab close button position |
| `Updated Alt Screen Padding Mode` | Updated the custom padding setting for the alt-screen |
| `Updated Sorting Choice` | Modified the sorting scheme for Warp Drive objects |
| `UseAgentToolbar.SettingToggled` | User toggled the Use Agent footer setting |
| `Used Warp AI Prepared Prompt` | Used one of the Warp-provided prompts, like “Show examples” |
| `User Initiated Closing Something` | Attempted to either quit the app or close a window |
| `User Initiated Log Out` | Confirms a user has explicitly logged out of the application |
| `User Menu Upgrade Clicked` | Clicked the ‘Upgrade’ menu item in the user menu |
| `VerticalTabs.DiffStatsChipClicked` | User clicked a diff stats chip in the vertical tabs panel or detail sidecar |
| `VerticalTabs.DisplayOptionChanged` | User updated a display option in the vertical tabs settings popup |
| `VerticalTabs.PrChipClicked` | User clicked a GitHub PR chip in the vertical tabs panel or detail sidecar |
| `Vim Keybindings Banner Dismissed` | Dismissed the banner to enable Vim keybindings in the Input Editor |
| `Vim Keybindings Banner Displayed` | Displayed the banner asking whether Warp should enable Vim keybindings in the Input Editor |
| `Vim Keybindings Enabled from Banner` | Enabled Vim keybindings in the Input Editor from the banner |
| `Warp AI Action` | Executed a Warp AI action: Restart, Copy, Insert into terminal |
| `Warp AI Character Limit Exceeded` | Attempted to ask a question longer than 1k chars to Warp AI |
| `Warp AI Request Issued` | Issued a question to Warp AI |
| `Warp Drive Opened` | Opened Warp Drive panel |
| `Warp Drive Sharing onboarding block shown` | Showed onboarding block for Warp Drive sharing |
| `Warp Drive object opened on desktop` | Warp Drive object on the web was opened on the desktop |
| `Warpify Footer Accepted Warpify` | User clicked Warpify in the warpify footer |
| `Warpify Footer Shown` | Displayed the warpify footer for a detected subshell or SSH session |
| `Web session opened on desktop` | Shared session viewed on the web was opened on the desktop |
| `Workflow Executed` | Executed workflow |
| `Workflow Selected` | Selected workflow and populated into the Input Editor |
| `Zero State Prompt Suggestion Used` | Used a zero state prompt suggestion |
| `experiments.client.enroll_client` | Client assigned to A/B test |
| `onboarding_action` | User performed an action in the account-first onboarding flow |
| `onboarding_agent_slide_upgrade_clicked` | User clicked the Upgrade button on the Customize your agent slide |
| `onboarding_auth_completed` | User completed account-first browser authentication |
| `onboarding_callout_completed` | User completed the callout flow |
| `onboarding_callout_displayed` | A callout was displayed to the user |
| `onboarding_callout_next` | User clicked next on a callout |
| `onboarding_completed` | User completed account-first onboarding |
| `onboarding_folder_selected` | User selected a folder |
| `onboarding_folder_selection_started` | User started folder selection |
| `onboarding_get_started_clicked` | User clicked the Get Started button |
| `onboarding_no_ai_confirmation_cancelled` | User chose to keep AI in the confirmation modal |
| `onboarding_no_ai_confirmation_shown` | User was shown the no-AI confirmation modal |
| `onboarding_no_ai_confirmed` | User confirmed they don’t want AI in the confirmation modal |
| `onboarding_setting_changed` | User changed a setting during onboarding |
| `onboarding_slide_navigated_back` | User navigated to the previous slide |
| `onboarding_slide_navigated_next` | User navigated to the next slide |
| `onboarding_slide_viewed` | User viewed a slide in the onboarding flow |
| `onboarding_slides_completed` | User completed the onboarding slides |
| `onboarding_started` | User started the onboarding flow |
| `onboarding_upgrade_completed` | User completed an upgrade from account-first onboarding |
| `onboarding_upgrade_started` | User started an upgrade from account-first onboarding |
| `onboarding_welcome_login_clicked` | User clicked the Log in link on the welcome/intro slide |
| `perf_metrics.memory_usage_high` | Total application memory usage exceeded a significant threshold |
| `perf_metrics.resource_usage` | Periodic report on application resource usage statistics |
| `perf_metrics.transient_memory_spike` | Application memory usage briefly crossed the excessive-usage threshold but dropped back under it before being reported as high |
| `revenue.AutoReloadModalClosed` | User closed the auto-reload modal (either dismissed or enabled auto-reload) |
| `revenue.AutoReloadToggledFromBillingSettings` | User toggled auto-reload in Billing & Usage settings |
| `revenue.OutOfCreditsBannerClosed` | User closed the ‘Out of credits’ banner (dismissed or purchased credits) |
# Secret Redaction
Canonical page: [/support-and-community/privacy-and-security/secret-redaction/](https://docs.warp.dev/support-and-community/privacy-and-security/secret-redaction/)
> Configure Secret Redaction to mask secrets, passwords, API keys, and PII before terminal or AI content is sent to servers.
## How to access it
[Section titled “How to access it”](#how-to-access-it)
Disabled by default, to enable Secret Redaction open **Settings** > **Privacy** > **Secret redaction** or type in “Secret Redaction” to toggle it in the [Command Palette](/terminal/command-palette/).
## How it works
[Section titled “How it works”](#how-it-works)
Secret Redaction attempts to detect sensitive data (including secrets, passwords, API keys, and PII) using your list of regex patterns. Any identified secret will be redacted instead of being sent to our servers or any LLM provider. Additionally, Warp Drive will prevent you from saving any secrets in plain text (workflows, MCP servers, prompts, etc.).\
\
Warp ships with a [list of recommended regex](/support-and-community/privacy-and-security/secret-redaction/#secret-regex-list) you can easily add to the list. Additionally you can add custom regex for secrets you want to include in **Settings** > **Privacy** > **Secret redaction** > **Custom secret redaction**.
## Visually hiding secrets
[Section titled “Visually hiding secrets”](#visually-hiding-secrets)
By default, identified secrets will be displayed with a strikethrough visual treatment, i.e. ` echo`` `` `~~`password`~~.
If instead you’d prefer to visually hide the secrets as well, i.e. `echo ********`, the setting to obfuscate secrets with asterisks can be found in **Settings** > **Privacy** > **Secret redaction** > **Hide secrets in denylist**.
Clicking on a secret will display a tooltip that lets you reveal the secret or copy the secret’s contents. When trying to copy terminal output containing secrets, it will be copied as asterisks (e.g. `echo password` becomes `echo ********`) unless revealed or copied from the tooltip. Secret redaction is not applied in [Session Sharing](/agents/local-agents/session-sharing/#secrets-in-shared-sessions) — treat a shared session like sharing your screen.
## Case sensitivity
[Section titled “Case sensitivity”](#case-sensitivity)
Secret redaction regexes are case-sensitive by default, so the regex `password` does not match `Password`. To make a pattern case-insensitive, prepend `(?i)`. For example, `(?i)password` matches `PASSWORD`, `Password`, and `password`.
## Secret regex list
[Section titled “Secret regex list”](#secret-regex-list)
Here is a list of the recommended regular expressions that Warp uses to identify secrets:
| Secret Type | Regex Pattern |
| ----------------------------------------- | ----------------------------------------------------------------------------------------- |
| IP V4 Address | `\b((25[0-5]\|(2[0-4]\|1\d\|[1-9]\|)\d)\.?\b){4}\b` |
| IP V6 Address | `\b((([0-9A-Fa-f]{1,4}:){1,6}:)\|(([0-9A-Fa-f]{1,4}:){7}))([0-9A-Fa-f]{1,4})\b` |
| Slack App Token | `\bxapp-[0-9]+-[A-Za-z0-9_]+-[0-9]+-[a-f0-9]+\b` |
| Phone Number | `\b(\+\d{1,2}\s)?\(?\d{3}\)?[\s.-]\d{3}[\s.-]\d{4}\b` |
| AWS Access ID | `\b(AKIA\|A3T\|AGPA\|AIDA\|AROA\|AIPA\|ANPA\|ANVA\|ASIA)[A-Z0-9]{12,}\b` |
| MAC Address | `\b((([a-zA-z0-9]{2}[-:]){5}([a-zA-z0-9]{2}))\|(([a-zA-z0-9]{2}:){5}([a-zA-z0-9]{2})))\b` |
| Google API Key | `\bAIza[0-9A-Za-z-_]{35}\b` |
| Google OAuth ID | `\b[0-9]+-[0-9A-Za-z_]{32}\.apps\.googleusercontent\.com\b` |
| GitHub Classic Personal Access Token | `\bghp_[A-Za-z0-9_]{36}\b` |
| GitHub Fine Grained Personal Access Token | `\bgithub_pat_[A-Za-z0-9_]{82}\b` |
| GitHub OAuth Access Token | `\bgho_[A-Za-z0-9_]{36}\b` |
| GitHub User to Server Token | `\bghu_[A-Za-z0-9_]{36}\b` |
| GitHub Server to Server Token | `\bghs_[A-Za-z0-9_]{36}\b` |
| Stripe Key | `\b(?:r\|s)k_(test\|live)_[0-9a-zA-Z]{24}\b` |
| Firebase Auth Domain | `\b([a-z0-9-]){1,30}(\.firebaseapp\.com)\b` |
| JSON web token | `\b(ey[a-zA-z0-9_\-=]{10,}\.){2}[a-zA-z0-9_\-=]{10,}\b` |
| OpenAI API Key | `\bsk-[a-zA-Z0-9]{48}\b` |
| Anthropic API Key | `\bsk-ant-api\d{0,2}-[a-zA-Z0-9\-]{80,120}\b` |
| Fireworks API Key | `\bfw_[a-zA-Z0-9]{24}\b` |
# Known issues and workarounds
Canonical page: [/support-and-community/troubleshooting-and-support/known-issues/](https://docs.warp.dev/support-and-community/troubleshooting-and-support/known-issues/)
> Known Warp issues with workarounds, including SSH, shells, and incompatible tools.
Note
To see a complete list of Warp issues and feature requests, visit our [GitHub issues page](https://github.com/warpdotdev/Warp/issues?q=is%3Aissue+is%3Aopen+sort%3Acreated-desc).
Note that some tools are incompatible with Warp, as listed [below](/support-and-community/troubleshooting-and-support/known-issues/#list-of-incompatible-tools). You can find debugging information in this [section](/support-and-community/troubleshooting-and-support/known-issues/#debugging).
## General
[Section titled “General”](#general)
### SSH
[Section titled “SSH”](#ssh)
To enable Blocks over SSH, Warp uses an SSH Wrapper function; navigate to **Settings** > **Features** if you need to disable it. See [Troubleshooting Legacy SSH](/terminal/warpify/ssh-legacy/#troubleshooting-ssh) for more info on workarounds to SSH issues, or see the [new SSH Page](/terminal/warpify/ssh/) for more on the upcoming features.
### Online features don’t work
[Section titled “Online features don’t work”](#online-features-dont-work)
There is a known issue that can occur that causes online features to break ([Agent](/agents/), [Generate](/agents/local-agents/generate/), [Block Sharing](/terminal/blocks/block-sharing/), [Refer a Friend](/support-and-community/community/refer-a-friend/) ). This is due to the login token going stale, typically due to a password change, and can be resolved by the following steps:
* macOS
1. Remove Warp user login with the following command:
```bash
sudo security delete-generic-password -l "dev.warp.Warp-Stable" $HOME/Library/Keychains/login.keychain
```
2. [Login to Warp](/getting-started/quickstart/installation-and-setup/#log-in-to-warp-optional)
* Windows
1. Remove any user files with the following command:
```powershell
Remove-Item $env:LOCALAPPDATA\warp\Warp\data\*-User
```
2. [Login to Warp](/getting-started/quickstart/installation-and-setup/#log-in-to-warp-optional)
* Linux
1. Remove Warp user login with your keychain manager (gnome-keyring, kwallet, etc.). Search for `dev.warp.Warp` and delete the `User` password/secret.
2. Remove any user files with the following command:
```bash
rm -f ${XDG_STATE_HOME:-$HOME/.local/state}/warp-terminal/*-User
```
3. [Login to Warp](/getting-started/quickstart/installation-and-setup/#log-in-to-warp-optional)
### English-only UI
[Section titled “English-only UI”](#english-only-ui)
Nov 2021: We have added character support for Chinese, Korean, and Japanese, but our UI currently only supports English.
### Abnormal rendering of Chinese characters
[Section titled “Abnormal rendering of Chinese characters”](#abnormal-rendering-of-chinese-characters)
If you notice issues with the terminal rendering Chinese characters (i.e. [#3366](https://github.com/warpdotdev/Warp/issues/3366)), try adding the following lines to your rc file.
```plaintext
export LC_ALL=zh_CN.UTF-8
export LANG=zh_CN.UTF-8
```
### Warp fails to render a window
[Section titled “Warp fails to render a window”](#warp-fails-to-render-a-window)
This can likely occur due to some corruption in the local sqlite db. You may see a similar error your [logs](/support-and-community/troubleshooting-and-support/sending-us-feedback/#gathering-warp-logs):
```plaintext
[WARN] SQLite error 283 (A WAL mode database file was recovered): recovered 383 frames from WAL file /home/xxxxx/.local/state/warp-terminal/warp.sqlite-wal
```
To try and resolve the issue of Warp not rendering a window, rename the SQLite database found in the [following locations](/terminal/sessions/session-restoration/#session-restoration-database).
### Misc.
[Section titled “Misc.”](#misc)
* The legacy [SSH wrapper](/terminal/warpify/ssh-legacy/) preserves the remote login shell. It enhances supported bash and zsh sessions; other shells continue without the enhanced Warp bootstrap.
* If your remote login shell is zsh, your aliases typically do not transfer over.
* When you open a [non-shell-based subshell (REPL)](https://github.com/warpdotdev/Warp/issues/4082), Warp does not modify the environment — it behaves like a standard terminal session.
* Warp may become unresponsive if it doesn’t have permission to access the folders.
* [No touch input support](https://github.com/warpdotdev/Warp/issues/5347)
## Agent Mode
[Section titled “Agent Mode”](#agent-mode)
* Note that Agent Mode blocks are not shareable during [Session Sharing](/agents/local-agents/session-sharing/). Participants will be able to share regular shell commands that are run, but will not be able to share AI interactions (requested commands, AI blocks, etc.).
* Block actions such as [Block Sharing](/terminal/blocks/block-sharing/) are not available on Agent Mode AI blocks.
* Agents do not have up-to-date information on several commands’ completion specs
* Agent Mode works better with Warp’s default prompt settings, where the prompt starts on a new line, than it does with a same-line prompt. If you are using the same-line prompt, the cursor will jump from the end of the single line to the start of the input box when you switch to Agent Mode.
## Shells
[Section titled “Shells”](#shells)
### fish shell `read` command
[Section titled “fish shell read command”](#fish-shell-read-command)
There is an issue in fish shell version 3.6 and below that causes the `read` built-in command to break Warp’s integration with fish. This means that using `read` directly or any fish scripts that call `read` will not work as expected in Warp. That issue is resolved in the fish repository and so should be fixed in the next release of fish itself. We recommend upgrading fish to the most recent version to resolve this issue.
### Warp shell loads slowly due to EDR
[Section titled “Warp shell loads slowly due to EDR”](#warp-shell-loads-slowly-due-to-edr)
If you comment out the rc files (i.e. `~/.zshrc`, `~/.bashrc`, `~/.config/fish/config.fish`), and still notice a slowdown on loading the shell, it is likely due to an Endpoint Detection and Response or EDR (i.e. Sentinel One, CrowdStrike, Carbon Black) causing the issue. Restart your system and see if the issue persists. If so, [Send us Feedback](/support-and-community/) and provide details of your EDR, OS, shell, etc.
### Configuring and debugging your RC files
[Section titled “Configuring and debugging your RC files”](#configuring-and-debugging-your-rc-files)
To support Blocks ([custom hooks](https://www.warp.dev/blog/how-warp-works#implementing-blocks)), a native Input Editor experience, AI blocks, etc. we have built custom support for a subset of shell functionality (decouple functionality from the shell and move to the terminal). This leads to Warp being incompatible with various tools and plugins. See the [list of incompatible](/support-and-community/troubleshooting-and-support/known-issues/#list-of-incompatible-tools) tools to find the tools that are known not to work with Warp.
Unlike typical terminals which are essentially continuous character grids, each section of Warp is its own (separate) UI element. See our [Prompt](/terminal/appearance/prompt/) page for more information on custom prompts.
#### Debugging
[Section titled “Debugging”](#debugging)
If Warp is not working with your dotfile configuration, you can run your shell in Warp with a clean configuration using examples below:
* bash
You can set up clean configs for Bash (Bourne Again SHell) by moving or commenting out your `.bashrc`\
\
If Warp starts working correctly then Warp is incompatible with something in the current dotfiles. We can isolate what is incompatible by iteratively disabling sections of your dotfiles with the `WarpTerminal` flag until we find the culprit. See the list of incompatible tools below and comment them out just for Warp with the following conditionals:
```bash
# bash (See ~/.bashrc)
if [[ $TERM_PROGRAM != "WarpTerminal" ]]; then
##### WHAT YOU WANT TO DISABLE FOR WARP - BELOW
# Unsupported plugin/prompt code here, i.e.
##### WHAT YOU WANT TO DISABLE FOR WARP - ABOVE
fi
```
* zsh
You can set up clean configs for Zsh (Z SHell) by moving or commenting out your `.zshrc`\
\
If Warp starts working correctly then Warp is incompatible with something in the current dotfiles. We can isolate what is incompatible by iteratively disabling sections of your dotfiles with the `WarpTerminal` flag until we find the culprit. See the list of incompatible tools below and comment them out just for Warp with the following conditional:
```bash
# zsh (See ~/.zshrc)
if [[ $TERM_PROGRAM != "WarpTerminal" ]]; then
##### WHAT YOU WANT TO DISABLE FOR WARP - BELOW
# Unsupported plugin/prompt code here
##### WHAT YOU WANT TO DISABLE FOR WARP - ABOVE
fi
```
* fish
You can set up clean configs for Fish (Friendly Interactive SHell) by moving or commenting out your `config.fish`\
\
If Warp starts working correctly then Warp is incompatible with something in the current config file. We can isolate what is incompatible by iteratively disabling sections of your config file with the `WarpTerminal` flag until we find the culprit. See the list of incompatible tools below and comment them out just for Warp with the following conditional:
```bash
# fish (see ~/.config/fish/config.fish)
if test "$TERM_PROGRAM" != "WarpTerminal"
##### WHAT YOU WANT TO DISABLE FOR WARP - BELOW
# Unsupported plugin/prompt code here
##### WHAT YOU WANT TO DISABLE FOR WARP - ABOVE
end
```
* pwsh
You can set up clean configs for pwsh (PowerShell) by moving or commenting out your `$PROFILE`
If Warp starts working correctly then Warp is incompatible with something in the current profile. We can isolate what is incompatible by iteratively disabling sections of your profile with the WarpTerminal flag until we find the culprit. See the list of incompatible tools below and comment them out just for Warp with the following conditional:
```powershell
# pwsh (see $PROFILE)
if ($env:TERM_PROGRAM -ne "WarpTerminal") {
##### WHAT YOU WANT TO DISABLE FOR WARP - BELOW
# Unsupported plugin/prompt code here
##### WHAT YOU WANT TO DISABLE FOR WARP - ABOVE
}
```
#### List of incompatible tools
[Section titled “List of incompatible tools”](#list-of-incompatible-tools)
The following non-exhaustive list of plugins, prompts, or tools can cause potential issues in Warp:
* oh-my-fish, oh-my-bash, or other unsupported shell prompts. See our [Custom Prompt Compatibility Table](/terminal/appearance/prompt/#shell-prompt-compatibility-table).
* [iTerm2 shell integration](https://iterm2.com/documentation-shell-integration.html)
* `test -e "${HOME}/.iterm2_shell_integration.zsh" && source "${HOME}/.iterm2_shell_integration.zsh" || true`
* [Termium](https://codeium.com/blog/termium-codeium-in-terminal-launch)
* `eval "$(termium shell-hook show pre)"`
* `eval "$(termium shell-hook show post)"`
* [thefuck experimental instant mode](https://github.com/nvbn/thefuck?tab=readme-ov-file#experimental-instant-mode)
* `eval $(thefuck --alias --enable-experimental-instant-mode)`
* [fubectl](https://github.com/kubermatic/fubectl)
* `[ -f ${HOME}/bin/fubectl.source ] && source ${HOME}/bin/fubectl.source`
* [BIND keys](https://github.com/warpdotdev/Warp/issues/537)
* `bindkey '^j' down-line-or-beginning-search`, which causes users to have to hit ENTER twice to run a command.
* `bindkey 'tab' autosuggest-accept`, which causes incorrect behavior with autocompletion.
* `z`, `compdef`, `compinit`, [prezto utility module](https://github.com/sorin-ionescu/prezto/blob/master/modules/utility/README.md), [bash-it](https://github.com/Bash-it/bash-it), CodeWhisperer or other [shell-based completion](https://github.com/warpdotdev/Warp/discussions/434) plugins.
* OH-MY-ZSH Themes
* e.g. avit, spaceship, maybe more …
* OH-MY-ZSH Plugins
* e.g. zsh-autosuggestions, zsh-autocomplete, maybe more …
* Oh-My-Tmux
* zsh4h (ZSH for Humans)
* znap
* FZF
* `[[ -r "/usr/local/etc/profile.d/bash_completion.sh" ]] && "/usr/local/etc/profile.d/bash_completion.sh"`
* `eval "$(rbenv init -)"`
* `grml-zsh-config`
* Python virtual environment PS1 [settings](https://github.com/warpdotdev/Warp/issues/2713#issuecomment-1447129449)
* [Starship settings](/terminal/appearance/prompt/#starship-settings)
* `zle-line-init`
* Potentially more — this is a non-exhaustive list. If you find an incompatible tool, please email us at <feedback@warp.dev>
## Operating systems
[Section titled “Operating systems”](#operating-systems)
* macOS
**SSH to local network device is denied on macOS**
On macOS, you may be [denied permission to SSH](https://github.com/warpdotdev/Warp/issues/5550) from Warp into other devices in your local network and see an error like: `ssh: connect to host <host_name> port 22: Undefined error: 0`.\
To resolve this issue, go to > **System Settings** > **Privacy & Security** > **Local Network** and add Warp.

An SSH permission error on macOS.
**Unexpected loss of permission on macOS**
On macOS, you may see an `Operation not permitted` error when trying to run commands in directories that have already been granted macOS permissions (Documents, Downloads, Desktop, etc). The best workaround at this time is to [apply any pending updates](/support-and-community/troubleshooting-and-support/updating-warp/) so that the new Warp binary has the correct permissions. We are tracking this issue in [GitHub issue #3009](https://github.com/warpdotdev/Warp/issues/3009).

A file permission error dialog on macOS.
**Running x86 commands with macOS**
In some cases, CLI applications only work on x86, so you can run Warp with Rosetta on macOS to be able to use them by doing the following.
* Go to **Finder** > **Applications** and search for Warp.
* Right-click and select Get Info.
* Then check the box on Open with Rosetta.
* Windows
**Unsupported in Warp on Windows**
The following features are not supported in Warp on Windows. Track the relevant GitHub issues linked below for any changes:
* [cmd.exe](https://github.com/warpdotdev/Warp/issues/5882) or [fish](https://github.com/warpdotdev/Warp/issues/6060) shells
**Warp won’t run on Windows**
We’re tracking some issues on Windows where [Warp crashes on startup](https://github.com/warpdotdev/Warp/issues/5840) or doesn’t render, with some possible workarounds below. If none of the workarounds help, please open a [new GitHub issue](https://github.com/warpdotdev/warp/issues/new/choose) and include [logs](/support-and-community/troubleshooting-and-support/sending-us-feedback/#gathering-warp-logs), installation (Baremetal or VM, x86\_64 or ARM64), and the issue you had.
* Graphics
* You can select the graphics backend used to render new Warp windows in the Settings menu, under **Features** > **System** > **Preferred graphics backend**.
* You can also opt to render new Warp windows with an integrated GPU, under **Features** > **System** > **Prefer rendering new windows with integrated GPU (low power)**.
**Crash on opening a Launch configuration or doesn’t become transparent on Windows**
When a user has an Nvidia 572.xx or AMD 23.10.x drivers or above, Warp may [crash when trying to open a Launch Configuration](https://github.com/warpdotdev/Warp/issues/5875), or [Warp fails to become transparent](https://github.com/warpdotdev/Warp/issues/5903) (opacity setting doesn’t work). These are known limitations of the graphics drivers. We’re investigating the issues and will update the GitHub issues above. You can workaround this by forcing the graphics backend to Vulkan or OpenGL by running the following from another terminal and setting your GPU driver Vulkan/OpenGL render method setting to “Prefer Native”, or using the [DX12 backend](/support-and-community/troubleshooting-and-support/known-issues/#operating-systems):
```powershell
# Run if Warp on Windows is installed for a single user
$env:WGPU_BACKEND="vulkan,gl"; & "$env:LOCALAPPDATA\Programs\Warp\warp.exe"
# Run if Warp on Windows is installed for all users
$env:WGPU_BACKEND="vulkan,gl"; & "$env:PROGRAMFILES\Warp\warp.exe"
```
* Linux
**Warp won’t run on Linux**
We’re tracking some issues on Linux where a [Warp window doesn’t show/render](https://github.com/warpdotdev/Warp/issues/4215) and won’t run in [Virtual Machines](https://github.com/warpdotdev/Warp/issues/4476), over [remote desktops](https://github.com/warpdotdev/Warp/issues/4435), or on [WSL](https://github.com/warpdotdev/Warp/issues/4240). Some possible workarounds are below. If none of the workarounds help, please open a [new GitHub issue](https://github.com/warpdotdev/warp/issues/new/choose) and include [logs](/support-and-community/troubleshooting-and-support/sending-us-feedback/#gathering-warp-logs) with your Linux distro, installation (WSL, Baremetal or VM, x86\_64 or ARM64), and the issue you had.
Note
* Many package install examples are for Ubuntu using `apt`, your distro may use different commands (`dnf`, `pacman`, `zypper`) or package names.
* GPU Drivers and Default GPU / Graphics API environment variables are system-dependent, e.g. AMD vs NVIDIA and OpenGL vs Vulkan.
- System
* Installing or Updating [Xorg](https://www.x.org/wiki/) / [Wayland](https://wayland.freedesktop.org/): `sudo apt install xserver-xorg` / `sudo apt install wayland`
* Installing [Hack font](https://sourcefoundry.org/hack/) on WSL and VMs: `sudo apt install fonts-hack`
* Install [WSL utilities](https://github.com/wslutilities/wslu): `sudo apt install wslu`
* Install Mesa utilities: `sudo apt install mesa-utils`
* Install Mesa Vulkan drivers: `sudo apt install mesa-vulkan-drivers`
* If unable to use the file picker: `sudo apt install xdg-desktop-portal xdg-desktop-portal-gtk zenity`
* If unable to copy-paste: `sudo apt install wl-clipboard`
- Graphics
* Install or Update your GPU driver: e.g. [NVIDIA](https://github.com/warpdotdev/Warp/issues/4215#issuecomment-1969750786) 535.x or below drivers
* For Ubuntu: `sudo ubuntu-drivers install`
* For Fedora: `sudo dnf install akmod-nvidia`
* For Arch Linux: `sudo pacman -S nvidia`
* For openSUSE: `sudo zypper install x11-video-nvidiaG05`
* Use [Low Power (integrated) GPU](https://github.com/warpdotdev/Warp/issues/4215#issuecomment-1967500574) in `~/.config/warp-terminal/user_preferences.json` file: `{"prefs":{"PreferLowPowerGPU": "true",}}`. The low-power workaround is particularly helpful if you see [`Unrecognized device error ERROR_INITIALIZATION_FAILED` in warp.log](https://github.com/warpdotdev/Warp/issues/4390#issuecomment-1989493913).
- Environmental Variables
* Prefix `warp-terminal` with the variables (multiple can be used), and once you confirm they work, `export` them in your `.profile`/`.zprofile` to [load on startup](https://github.com/warpdotdev/Warp/issues/4240#issuecomment-1968228029):
* [Default to Wayland](https://github.com/warpdotdev/Warp/issues/4240#issuecomment-1961993281): `WARP_ENABLE_WAYLAND=1`
* Set [Default GPU](https://docs.mesa3d.org/drivers/d3d12.html#utilities) for WSL: e.g. `MESA_D3D12_DEFAULT_ADAPTER_NAME=NVIDIA`
* Set [Graphics APIs](https://github.com/gfx-rs/wgpu?tab=readme-ov-file#environment-variables): e.g. `WGPU_BACKEND=gl`
**Update fails after upgrading Linux**
Some Linux distros may modify Warp’s package repository during the OS upgrades. We’re aware of this on Ubuntu, but this may affect other Linux distros. We’re tracking this issue in [GitHub issue #5201](https://github.com/warpdotdev/Warp/issues/5201).\
\
To workaround this issue, manually add the repository to update Warp. The Ubuntu example is below:
```plaintext
sudo apt-get install wget gpg
wget -qO- https://releases.warp.dev/linux/keys/warp.asc | gpg --dearmor > warpdotdev.gpg
sudo install -D -o root -g root -m 644 warpdotdev.gpg /etc/apt/keyrings/warpdotdev.gpg
sudo sh -c 'echo "deb [arch=amd64 signed-by=/etc/apt/keyrings/warpdotdev.gpg] https://releases.warp.dev/linux/deb stable main" > /etc/apt/sources.list.d/warpdotdev.list'
rm warpdotdev.gpg
sudo apt update && sudo apt install warp-terminal
```
See the instructions for other Linux distros on our [quickstart guide](/getting-started/quickstart/installation-and-setup/#install-warp).
# Logging out & uninstalling
Canonical page: [/support-and-community/troubleshooting-and-support/logging-out-and-uninstalling/](https://docs.warp.dev/support-and-community/troubleshooting-and-support/logging-out-and-uninstalling/)
> How to log out from Warp, and how to uninstall Warp.
## Logging out
[Section titled “Logging out”](#logging-out)
You can log out of Warp through:
* **Settings** > **Account**, with the “Log out” button
* [Command Palette](/terminal/command-palette/), with the “Log out” item.
[](/assets/support-and-community/logout.mp4)
### Known issues:
[Section titled “Known issues:”](#known-issues)
1. When you log out, you will lose all running processes and all unsaved objects.
2. When you log out and log in to Warp with another account, the following preferences will be preserved from the original account:
1. Theme
2. Keybindings
3. Settings (e.g. autosuggestion, notifications, font size, welcome tips status)
3. Whenever you log in to Warp, you will receive the onboarding survey.
## Uninstalling Warp
[Section titled “Uninstalling Warp”](#uninstalling-warp)
Removing Warp from your computer involves uninstalling Warp and then removing any files or data.
Note
If you’re using Warp Preview, replace “Warp-Stable” with “Warp-Preview” in the commands below (e.g., `defaults delete dev.warp.Warp-Preview`).
* macOS
**Uninstalling Warp by dmg**
* Remove Warp with `sudo rm -r /Applications/Warp.app`
* Open **Finder** > **Applications**, right-click on Warp, and select “Move to Trash”
**Uninstalling Warp by Homebrew**
* Remove Warp with `brew uninstall warp`
**Removing Warp settings, files, logs, and database**
```bash
# Remove Warp settings defaults
defaults delete dev.warp.Warp-Stable
# Remove Warp logs
sudo rm -r $HOME/Library/Logs/warp.log
# Remove Warp database, Codebase Context, and MCP logs
sudo rm -r "$HOME/Library/Group Containers/2BBY89MBSN.dev.warp/Library/Application Support/dev.warp.Warp-Stable"
# Remove Warp user files, themes, and launch configurations
sudo rm -r $HOME/.warp
# Note: Removing $HOME/.warp will delete files for both Stable and Preview.
# If you wish to delete it all, then: sudo rm -r $HOME/.warp
```
**For Warp Preview users:**
```bash
# Remove Warp Preview settings defaults
defaults delete dev.warp.Warp-Preview
# Remove Warp Preview logs
sudo rm -r $HOME/Library/Logs/warp_preview.log
# Remove Warp Preview database, Codebase Context, and MCP logs
sudo rm -r "$HOME/Library/Group Containers/2BBY89MBSN.dev.warp/Library/Application Support/dev.warp.Warp-Preview"
# Note: Removing $HOME/.warp will delete files for both Preview and Stable.
# If you wish to delete it all, then: sudo rm -r $HOME/.warp
```
* Windows
**Uninstalling Warp by WinGet**
```powershell
winget uninstall Warp.Warp
```
**Uninstalling Warp installed by Installer**
* Search for “Installed apps” section of the Control Panel.
* Search for and Uninstall the Warp application
**Removing Warp settings, files, logs, and database**
```powershell
# Remove Warp settings in the Windows Registry
Remove-Item -Path "HKCU:\Software\Warp.dev\Warp" -Recurse -Force
# Remove Warp settings, keybindings, logs, database, Codebase Context, and MCP logs
Remove-Item -Path "$env:LOCALAPPDATA\warp\Warp" -Recurse -Force
# Remove Warp themes, tab configs, workflows, and launch configurations
Remove-Item -Path "$env:APPDATA\warp\Warp" -Recurse -Force
# Remove MCP server config and bundled skills (shared across Stable and Preview)
Remove-Item -Path "$env:USERPROFILE\.warp" -Recurse -Force
```
**For Warp Preview users:**
```powershell
# Remove Warp Preview settings in the Windows Registry
Remove-Item -Path "HKCU:\Software\Warp.dev\WarpPreview" -Recurse -Force
# Remove Warp Preview settings, keybindings, logs, database, Codebase Context, and MCP logs
Remove-Item -Path "$env:LOCALAPPDATA\warp\WarpPreview" -Recurse -Force
# Remove Warp Preview themes, tab configs, workflows, and launch configurations
Remove-Item -Path "$env:APPDATA\warp\WarpPreview" -Recurse -Force
# Note: Removing $env:USERPROFILE\.warp also removes Stable's MCP config and skills.
```
* Linux
**Uninstalling Warp by package manager**
```bash
# apt uninstall
sudo apt remove warp-terminal
# dnf uninstall
sudo dnf remove warp-terminal
# zypper uninstall
sudo zypper remove warp-terminal
# pacman uninstall
sudo pacman -R warp-terminal
```
* Uninstall Warp using the same package manager that you used to [install](/getting-started/quickstart/installation-and-setup/) it.
**Removing Warp settings, files, logs, and database**
```bash
# Remove Warp settings and keybindings files
rm -r ${XDG_CONFIG_HOME:-$HOME/.config}/warp-terminal
# Remove Warp logs, database, Codebase Context, and MCP logs
rm -r ${XDG_STATE_HOME:-$HOME/.local/state}/warp-terminal
# Remove Warp themes, tab configs, workflows, and launch configurations
rm -r ${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal
# Remove MCP server config and bundled skills (shared across Stable and Preview)
rm -r $HOME/.warp
```
**For Warp Preview users:**
```bash
# apt uninstall
sudo apt remove warp-terminal-preview
# dnf uninstall
sudo dnf remove warp-terminal-preview
# zypper uninstall
sudo zypper remove warp-terminal-preview
# pacman uninstall
sudo pacman -R warp-terminal-preview
```
* Uninstall Warp Preview using the same package manager that you used to install it.
```bash
# Remove Warp Preview settings and keybindings files
rm -r ${XDG_CONFIG_HOME:-$HOME/.config}/warp-terminal-preview
# Remove Warp Preview logs, database, Codebase Context, and MCP logs
rm -r ${XDG_STATE_HOME:-$HOME/.local/state}/warp-terminal-preview
# Remove Warp Preview themes, tab configs, workflows, and launch configurations
rm -r ${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal-preview
# Note: Removing $HOME/.warp also removes Stable's MCP config and skills.
```
# Sending feedback and logs
Canonical page: [/support-and-community/troubleshooting-and-support/sending-us-feedback/](https://docs.warp.dev/support-and-community/troubleshooting-and-support/sending-us-feedback/)
> Send Warp feedback, bug reports, and feature requests, and gather logs, crash reports, CPU samples, and AI conversation IDs to attach to them.
## Sending Warp feedback
[Section titled “Sending Warp feedback”](#sending-warp-feedback)
* Use the [`/feedback`](#using-feedback-in-warp) slash command inside Warp to open the static feedback experience.
* Open a new bug or feature request in our [GitHub repository](https://github.com/warpdotdev/warp/issues/new/choose).
* Join our [Warp Community Slack](https://go.warp.dev/join-preview) and share feedback in **#feedback-general**, or **#feedback-preview** if it is specific to [Warp Preview](/support-and-community/community/warp-preview-and-alpha-program/).
* For security issues or questions, email <security@warp.dev>.
* For questions about privacy, email <privacy@warp.dev>.
### Subscribers and Enterprise
[Section titled “Subscribers and Enterprise”](#subscribers-and-enterprise)
* For subscriber technical issues or questions (bugs, credits, etc.), email <support@warp.dev>.
* For subscriber billing issues or questions (refunds, cancellation, etc.), email <billing@warp.dev>.
* For enterprise, please direct all feedback and issues to your designated Slack channel.
## Using `/feedback` in Warp
[Section titled “Using /feedback in Warp”](#using-feedback-in-warp)
The `/feedback` [slash command](/agents/capabilities/slash-commands/) is the fastest way to report a Warp bug, flag a regression, or file a feature request from inside the terminal. It opens the feedback form without starting an Agent conversation or consuming credits.
### What to include
[Section titled “What to include”](#what-to-include)
Whether you use the `/feedback` slash command or file an issue manually, a good feedback report answers these questions up front:
* **What happened?** Describe the observed behavior in one or two sentences.
* **What did you expect?** Describe the behavior you expected instead.
* **How do we reproduce it?** List numbered steps when possible. If you can’t reproduce the issue reliably, mention that too.
* **What version of Warp are you on?** `/feedback` fills this in automatically; for manual reports, copy it from **Settings** > **Account**.
* **Logs, screenshots, or conversation IDs.** See [Gathering Warp logs](#gathering-warp-logs), [Collecting crash reports on macOS](#collecting-crash-reports-on-macos), or [Gathering AI conversation ID](#gathering-ai-conversation-id) below.
See the [Slash Commands reference](/agents/capabilities/slash-commands/) for the full list of commands available in Warp.
## Gathering Warp logs
[Section titled “Gathering Warp logs”](#gathering-warp-logs)
Retrieve Warp’s logs by following the instructions for your platform below. Locate the log file and attach it to your GitHub issue or email.
Note
Warp’s logs and crash reports ***do not*** contain any console input or output. See more on how we handle [Crash Reports and Telemetry](/support-and-community/privacy-and-security/privacy/#what-telemetry-data-does-warp-collect-and-why).
* macOS
The Warp log files are located at `~/Library/Logs/`.
**Warp logs on macOS**
Run the following to zip the Warp logs to your Desktop:
```bash
zip -j ~/Desktop/warp-logs.zip ~/Library/Logs/warp.log*
```
**Warp Preview logs on macOS**
Run the following to zip the Warp Preview logs to your Desktop:
```bash
zip -j ~/Desktop/warp_preview-logs.zip ~/Library/Logs/warp_preview.log*
```
Caution
If your issue is graphical (e.g. no display of windows) or a crash, run Warp with the following command to capture more log information:
```bash
# Run if Warp on macOS is installed
RUST_LOG=wgpu_core=info,wgpu_hal=info /Applications/Warp.app/Contents/MacOS/stable
# Run if Warp Preview on macOS is installed
RUST_LOG=wgpu_core=info,wgpu_hal=info /Applications/WarpPreview.app/Contents/MacOS/preview
```
* Windows
The Warp log files are located at `$env:LOCALAPPDATA\warp\Warp\data\logs\`.
**Warp logs on Windows**
Close Warp and run the following from another terminal to zip the logs to your Desktop:
```powershell
Compress-Archive -Path "$env:LOCALAPPDATA\warp\Warp\data\logs\warp.log*" -DestinationPath "$([Environment]::GetFolderPath('Desktop'))\warp-logs.zip"
```
**Warp Preview logs on Windows**
Close Warp Preview and run the following from another terminal to zip the logs to your Desktop:
```powershell
Compress-Archive -Path "$env:LOCALAPPDATA\warp\WarpPreview\data\logs\warp_preview.log*" -DestinationPath "$([Environment]::GetFolderPath('Desktop'))\warp_preview-logs.zip"
```
Caution
If your issue is graphical (e.g. no display of windows) or a crash, run Warp with the following command to capture more log information:
```powershell
# Run if Warp on Windows is installed for a single user
$env:RUST_LOG="wgpu_core=info,wgpu_hal=info"; & "$env:LOCALAPPDATA\Programs\Warp\warp.exe"
# Run if Warp on Windows is installed for all users
$env:RUST_LOG="wgpu_core=info,wgpu_hal=info"; & "$env:PROGRAMFILES\Warp\warp.exe"
# Run if Warp Preview on Windows is installed for a single user
$env:RUST_LOG="wgpu_core=info,wgpu_hal=info"; & "$env:LOCALAPPDATA\Programs\WarpPreview\preview.exe"
# Run if Warp Preview on Windows is installed for all users
$env:RUST_LOG="wgpu_core=info,wgpu_hal=info"; & "$env:PROGRAMFILES\WarpPreview\preview.exe"
```
* Linux
The Warp log files are located at `~/.local/state/warp-terminal/`.
**Warp logs on Linux**
Run the following to zip the Warp logs to your home directory:
```bash
(cd ~/.local/state/warp-terminal && tar -czf ~/warp-logs.tar.gz warp.log*)
```
**Warp Preview logs on Linux**
Run the following to zip the Warp Preview logs to your home directory:
```bash
(cd ~/.local/state/warp-terminal-preview && tar -czf ~/warp_preview-logs.tar.gz warp_preview.log*)
```
Caution
If your issue is graphical (e.g. no display of windows) or a crash, run Warp with the following command to capture more log information:
```bash
# Run if Warp on Linux is installed
RUST_LOG=wgpu_core=info,wgpu_hal=info MESA_DEBUG=1 EGL_LOG_LEVEL=debug warp-terminal
# Run if Warp Preview on Linux is installed
RUST_LOG=wgpu_core=info,wgpu_hal=info MESA_DEBUG=1 EGL_LOG_LEVEL=debug warp-terminal-preview
```
## Collecting crash reports on macOS
[Section titled “Collecting crash reports on macOS”](#collecting-crash-reports-on-macos)
If Warp crashes, macOS may generate `.ips` crash report files in `~/Library/Logs/DiagnosticReports/`. Run the following to collect all Warp crash reports into a zip on your Desktop:
```bash
files=$(find ~/Library/Logs/DiagnosticReports -name "*.ips" -exec grep -l "dev\.warp" {} + 2>/dev/null) && [ -n "$files" ] && echo "$files" | xargs zip -j ~/Desktop/warp-crash-logs.zip || echo "No Warp crash reports found."
```
Attach the resulting `warp-crash-logs.zip` to your [bug report](/support-and-community/troubleshooting-and-support/sending-us-feedback/#sending-warp-feedback).
Note
This command searches crash report files for Warp’s bundle identifier, so it works across all Warp channels (Stable, Preview).
## Collecting debug info on Windows
[Section titled “Collecting debug info on Windows”](#collecting-debug-info-on-windows)
Occasionally, the Warp team may ask you to provide debugging information on Windows OS in particular with one of the following:
```powershell
# If Warp is in your PATH, Run:
warp --dump-debug-info
# Otherwise you may need to use an absolute path and ...
# Warp on Windows is installed for a single user, Run:
& $env:LOCALAPPDATA\programs\Warp\warp.exe --dump-debug-info
# Warp on Windows is installed for all users, Run:
& $env:PROGRAMFILES\Warp\warp.exe --dump-debug-info
```
## Collecting CPU samples
[Section titled “Collecting CPU samples”](#collecting-cpu-samples)
Certain conditions can cause Warp to use more CPU than expected or become unresponsive. Collecting a CPU sample while the issue is happening is the best way to report it. The sample provides the information the Warp team needs to identify and fix the root cause.
Collect a sample using the steps for your platform and attach it to a new [GitHub issue](https://github.com/warpdotdev/warp/issues/new/choose).
* macOS
1. Reproduce the high CPU usage or unresponsiveness in Warp.
2. While the issue is occurring, open **Activity Monitor**, select the **Warp** process, and click **Sample Process**.

Sampling a Warp process in Activity Monitor.
3. Save the resulting sample and attach it to your GitHub issue.
* Windows
Install [`samply`](https://github.com/mstange/samply) to record a CPU trace:
```powershell
powershell -ExecutionPolicy Bypass -c "irm https://github.com/mstange/samply/releases/download/samply-v0.13.1/samply-installer.ps1 | iex"
```
1. Find the Warp process ID:
```powershell
Get-Process *warp*
```
2. Start recording, replacing `<PID>` with the process ID from the previous step:
```powershell
samply record -p <PID>
```
3. Reproduce the issue that causes high CPU usage or unresponsiveness.
4. Press `Ctrl+C` to stop recording. `samply` opens the profile in the Firefox Profiler in your browser. Click the upload icon in the top-right corner to generate a shareable link, then paste it into your GitHub issue.
* Linux
Install [`samply`](https://github.com/mstange/samply) to record a CPU trace:
```bash
curl --proto '=https' --tlsv1.2 -LsSf https://github.com/mstange/samply/releases/download/samply-v0.13.1/samply-installer.sh | sh
```
Caution
`samply` requires access to Linux perf events. If you get a permission error, run:
```bash
echo '-1' | sudo tee /proc/sys/kernel/perf_event_paranoid
```
1. Start recording the Warp process:
```bash
samply record -p $(pgrep -f warp-terminal)
```
2. Reproduce the issue that causes high CPU usage or unresponsiveness.
3. Press `Ctrl+C` to stop recording. `samply` opens the profile in the Firefox Profiler in your browser. Click the upload icon in the top-right corner to generate a shareable link, then paste it into your GitHub issue.
Note
If you prefer not to install `samply`, you can use the built-in `perf` tool instead:
```bash
perf record -g -p $(pgrep -f warp-terminal) -- sleep 30
```
Attach the resulting `perf.data` file from your current directory to your GitHub issue.
## Gathering AI conversation ID
[Section titled “Gathering AI conversation ID”](#gathering-ai-conversation-id)
To gather the conversation ID, `RIGHT-CLICK` on the AI conversation block in question and select “Copy conversation ID”, then paste that into the [bug report](/support-and-community/troubleshooting-and-support/sending-us-feedback/#sending-warp-feedback) that you submit so that our team can investigate the issue.
Whenever there is an error in the Agent Conversation, there will also be an option to directly copy the conversation ID for the bug report.
### Using `/copy-debugging-id`
[Section titled “Using /copy-debugging-id”](#using-copy-debugging-id)
The [`/copy-debugging-id`](/agents/capabilities/slash-commands/) slash command copies the same information without leaving the input. It works in both the Warp app and the [Warp Agent CLI](/agents/cli/), and it applies to the conversation you’re currently in:
1. Run `/copy-debugging-id` in the conversation you want to report.
2. Warp confirms with a “Debugging information copied to clipboard” message.
3. Paste the copied text into your bug report.
The copied text is a small JSON payload with the conversation ID, plus the request ID when the command is run on a specific agent response — for example, `{"conversation_id":"abc123"}`. If the conversation hasn’t reached Warp’s servers yet, the command reports that no debugging ID is available; send a prompt first, then run it again.

# Troubleshooting Login
Canonical page: [/support-and-community/troubleshooting-and-support/troubleshooting-login-issues/](https://docs.warp.dev/support-and-community/troubleshooting-and-support/troubleshooting-login-issues/)
> Fix common login issues including SSO, proxies, ad blockers, and auth tokens.
## Can’t sign up for or log into Warp
[Section titled “Can’t sign up for or log into Warp”](#cant-sign-up-for-or-log-into-warp)
Clicking it should open a signup or login pop-up. If clicking the button opens a blank pop-up window, try using a proxy. Your ISP or Firewall may be blocking the app’s call to `*.googleapis.com`.
Note
In some older Ruby development environments, `.dev` domains do not resolve properly and you may need to delete the `/etc/resolver/dev`. See the Super User thread on [`.dev` domains that do not resolve](https://superuser.com/questions/1374892/dev-domains-dont-resolve) for more context.
## All browsers
[Section titled “All browsers”](#all-browsers)
This error could occur if you installed an ad blocker or have stale browser cookies, including our Firebase auth pop-up. **To fix it:**
1. Disable your ad blocker for `app.warp.dev`
2. Clear any cookies and cache, or open an incognito / private browser window
3. Try the [Warp login page](https://app.warp.dev/login) again
### Safari
[Section titled “Safari”](#safari)
If you are using Safari, you may see the following messages in your console:
1. `Unable to access localStorage`
2. And every time you click the “Sign Up” button, you get `Unhandled Promise Rejection: Error: This operation is not supported in the environment the application is running on. "location.protocol" must be http, https, or chrome-extension and web storage must be enabled.`
This error likely occurs because you are blocking all cookies in Safari’s security settings, but Firebase Auth requires the cookie to record whether the user is logged in. **To fix it:**
1. Go to Safari Preferences > Privacy
2. Uncheck the “Block all cookies” checkbox
## Proxies
[Section titled “Proxies”](#proxies)
When behind a proxy, a possible workaround is to disable QUIC in the browser. It will then fall back to TCP and likely allow login.
* In Chrome, or Chromium-based browsers like Edge, Opera, and Arc, type `chrome://flags` into the address bar.
1. In the search bar on the flags page, type `Experimental QUIC protocol`.
2. Locate the “Experimental QUIC protocol” flag and click on the drop-down menu next to it.
3. Select “Disabled” from the options.
4. Relaunch Chrome for the changes to take effect.
* In Firefox, type `about:config` into the address bar.
1. You will see a warning message. Click on the “Accept the Risk and Continue” button.
2. In the search bar, type `network.http.http3.enable`.
3. Double-click on the `network.http.http3.enable` preference to set its value to `false`. This will disable QUIC in Firefox.
4. Restart Firefox for the changes to take effect.
* In Safari, unfortunately, there is no built-in option to disable QUIC in Safari. Safari uses QUIC as its default transport protocol and does not provide a user-accessible setting to disable it.
## SSO login
[Section titled “SSO login”](#sso-login)
### Can’t open Warp from SSO
[Section titled “Can’t open Warp from SSO”](#cant-open-warp-from-sso)
When directly launching Warp from Okta or other SSO providers’, you may see an error message like “`Unable to process request due to missing initial state...`”. This is due to a limitation with Warp authentication APIs. Instead, do the following:
1. Go to the [Warp login page](https://app.warp.dev/login)
2. Choose “Continue with SSO”
3. Login with your normal SSO credentials
### I logged in with another method before and now can’t use SSO
[Section titled “I logged in with another method before and now can’t use SSO”](#i-logged-in-with-another-method-before-and-now-cant-use-sso)
In cases where you logged in with another method, do the following to fix SSO login:
1. Go to the [Warp login page](https://app.warp.dev/login)
2. Login with the original method that you used to create your Warp account (email, Google, GitHub).
3. Once logged in, go to the [SSO linking page](https://app.warp.dev/link_sso)
4. This should link your login to SSO. You can now proceed to login with “Continue with SSO”.
## Flagged as fraudulent
[Section titled “Flagged as fraudulent”](#flagged-as-fraudulent)
If you received the message “This account has been flagged as fraudulent.”, this means that you have failed one or more checks in our fraud detection system, and you will be unable to authenticate to Warp or leverage AI features.
Note that creating multiple accounts or using throwaway emails is against our [Terms of Service](https://www.warp.dev/legal/terms-of-service) and increases the chance of triggering this system significantly.
### False positives
[Section titled “False positives”](#false-positives)
At times, ad-blockers or systems like Pi-hole may falsely trigger this system. To remediate this error, try temporarily disabling them and attempting login again.
### Requesting an appeal
[Section titled “Requesting an appeal”](#requesting-an-appeal)
If you are still unable to authenticate, you can email <appeals@warp.dev> to request an appeal. Include the email of the account you are experiencing the issue on so a member of our support team can investigate. This may take 5-10 days.
If you have an active subscription and continue to have login issues, see [how to get help with login issues](/support-and-community/troubleshooting-and-support/troubleshooting-login-issues/#get-help-with-login-issues).
## How to get an auth token to login
[Section titled “How to get an auth token to login”](#how-to-get-an-auth-token-to-login)
If the browser does not open from Warp directly when you click “Sign up” or “Sign in”, go to the [Signup](https://app.warp.dev/signup) page to create an account or the [Login](https://app.warp.dev/login) page if you already have one, then copy the auth token from the “here” link on the logged\_in page and paste it into Warp.
If nothing happens when you click “Take me to Warp” on the logged-in page, copy the “here” link on the web logged-in page ([https://app.warp.dev/logged\\\_in](https://app.warp.dev/logged%5C_in)) to copy the authentication token, then paste it into the app as shown below.
Caution
On Linux and Windows, the default copy-and-paste [Keyboard shortcuts](/getting-started/keyboard-shortcuts/) are `Ctrl+Shift+C` and `Ctrl+Shift+V` respectively.\
\
On Linux and WSL you should install and set your default `$BROWSER` to `brave-browser` to workaround any copy-paste issues. See the workaround guide below.
[](/assets/support-and-community/auth-token-demo.mp4)

If “Take me to Warp” is still not working it may be due to a [proxy issue](/support-and-community/troubleshooting-and-support/troubleshooting-login-issues/#proxies). See this guide to [fixing Warp after submitting an invite code](https://embiid.blog/post/WARP-does-not-work-after-submitting-an-invite-code/) for a workaround.
## Get help with login issues
[Section titled “Get help with login issues”](#get-help-with-login-issues)
If Sign Up or Login does not work after trying the steps above, please [contact us](https://www.warp.dev/contact) for support.
# Updating Warp
Canonical page: [/support-and-community/troubleshooting-and-support/updating-warp/](https://docs.warp.dev/support-and-community/troubleshooting-and-support/updating-warp/)
> Check for updates, troubleshoot auto-update permissions, and refresh signing keys.
Warp automatically checks for updates on startup, and periodically while running, by connecting to `releases.warp.dev`. A notification will appear in the top right corner of the Warp window when a new update is available.

To check for updates, search for “update” in the [Command Palette](/terminal/command-palette/) or go to **Settings** > **Account** and click “Check for Update”.
[](/assets/support-and-community/check-for-update.mp4)
If nothing happens, it means you already have the latest stable build.
## macOS: Auto-update permissions issues
[Section titled “macOS: Auto-update permissions issues”](#macos-auto-update-permissions-issues)
Warp cannot auto-update if it does not have the correct permissions to replace the running version of Warp. If this is the case, a banner will prompt you to manually update Warp.

There are 2 main causes of this:
1. You opened Warp directly from the mounted volume instead of dragging it into your Applications directory. If this is the case, the easiest fix is to quit Warp, drag the application into /Applications, and restart Warp.
2. You are a non-Admin user. This can happen if you use a computer with multiple profiles. If you have admin access on the computer, opening the app with the admin user should fix the auto-update issues.
## Linux: Refreshing the package signing key
[Section titled “Linux: Refreshing the package signing key”](#linux-refreshing-the-package-signing-key)
If you encounter signature verification errors when trying to update Warp on Linux, you may need to refresh the package signing key. This can happen if the key on your system has expired.
### Debian / Ubuntu (apt)
[Section titled “Debian / Ubuntu (apt)”](#debian--ubuntu-apt)
You may see an error like the following:
```plaintext
W: GPG error: https://releases.warp.dev/linux/deb stable Release: The following signatures were invalid: EXPKEYSIG 31F4254AFE49E02E Warp Linux Maintainers (Package Signing Authority) <linux-maintainers@warp.dev>
E: The repository 'https://releases.warp.dev/linux/deb stable Release' is not signed.
```
To fetch the updated signing key, run:
```bash
curl -fsSL https://releases.warp.dev/linux/keys/warp.asc | gpg --dearmor | sudo tee /etc/apt/trusted.gpg.d/warpdotdev.gpg > /dev/null
```
Then retry your update:
```bash
sudo apt update && sudo apt install warp-terminal
```
### Fedora / RHEL / CentOS (dnf/yum)
[Section titled “Fedora / RHEL / CentOS (dnf/yum)”](#fedora--rhel--centos-dnfyum)
You may see an error like the following:
```plaintext
OpenPGP check for package "warp-terminal-v0.2026.01.28.08.14.stable_04-1.x86_64" (/var/cache/libdnf5/warpdotdev-4ac10ef632833104/packages/warp-terminal-v0.2026.01.28.08.14.stable_04-1.x86_64.rpm) from repo "warpdotdev" has failed: Problem occurred when opening the package.
```
To fetch the updated signing key, run:
```bash
sudo rpm --import https://releases.warp.dev/linux/keys/warp.asc
```
Then retry your update:
```bash
sudo dnf upgrade warp-terminal
# or for older systems:
sudo yum upgrade warp-terminal
```
### Arch Linux (pacman)
[Section titled “Arch Linux (pacman)”](#arch-linux-pacman)
You may see an error like the following:
```plaintext
error: warpdotdev: signature from "Warp Linux Maintainers (Package Signing Authority) <linux-maintainers@warp.dev>" is expired
```
To fetch the updated signing key, run:
```bash
sudo pacman-key --recv-keys "linux-maintainers@warp.dev" --keyserver hkp://keys.openpgp.org:80
sudo pacman-key --lsign-key "linux-maintainers@warp.dev"
```
Then retry your update:
```bash
sudo pacman -Syu warp-terminal
```
# Using Warp Offline
Canonical page: [/support-and-community/troubleshooting-and-support/using-warp-offline/](https://docs.warp.dev/support-and-community/troubleshooting-and-support/using-warp-offline/)
> Using Warp offline and what features are supported.
The first time you download and open Warp, you will need to be online for the initial setup. After the initial setup Warp’s core terminal features will work as expected when you’re offline, regardless of whether you are logged in or logged out.
Requiring all users, logging in or logged out, to be online when first accessing Warp is required to allow use of Warp’s AI and cloud features. When you first open the app, we create a unique user-ID to meter AI-usage and attach cloud objects to specific accounts. If you opt to use Warp logged-out, this unique ID is attached to an anonymous user account.
Note
Warp is “Offline” when you aren’t connected to the internet, or if you’re blocking calls `app.warp.dev` on your network. There is no explicit Offline Mode in Warp.
### Cloud-based features require online access
[Section titled “Cloud-based features require online access”](#cloud-based-features-require-online-access)
Warp’s cloud-based features which require an internet connection will not work in offline mode. Those features include:
* [Warp Drive](/knowledge-and-collaboration/warp-drive/#using-warp-drive-offline) (Some files may be read-only in offline mode)
* [Agent](/agents/)
* [Agent Mode](/agents/local-agents/interacting-with-agents/)
* [Generate](/agents/local-agents/generate/)
* [AI Autofill](/knowledge-and-collaboration/warp-drive/workflows/#ai-autofill)
* [Prompts](/knowledge-and-collaboration/warp-drive/prompts/)
* [Active AI Recommendations](/agents/local-agents/active-ai/)
* [Voice](/agents/local-agents/interacting-with-agents/voice/)
* [Rules](/agents/capabilities/rules/)
* [Model Context Protocol](/agents/capabilities/mcp/)
* [Teams](/knowledge-and-collaboration/teams/)
* [Session Sharing](/agents/local-agents/session-sharing/)
* [Block Sharing](/terminal/blocks/block-sharing/)
* [Refer a Friend](/support-and-community/community/refer-a-friend/)
# Terminal appearance overview
Canonical page: [/terminal/appearance/](https://docs.warp.dev/terminal/appearance/)
> Customize Warp's visual appearance, including themes, fonts, prompts, app icons, input position, and pane behavior.
# Custom app icons
Canonical page: [/terminal/appearance/app-icons/](https://docs.warp.dev/terminal/appearance/app-icons/)
> Choose from a palette of built-in app icons to customize Warp's dock appearance on macOS.
Note
App icons are only available for Warp on macOS. The feature doesn’t support custom dock icons.
## How to change the app icon
[Section titled “How to change the app icon”](#how-to-change-the-app-icon)
* Navigate to **Settings** > **Appearance** > **Icon** > **Customize your app icon**
* Select the desired dock icon from the drop-down menu
Icon customization drop-down menu.
## Dock icons
[Section titled “Dock icons”](#dock-icons)
By default, Warp ships with these dock icons:
Default
Warp 1.0
Aurora
Classic 1
Classic 2
Classic 3
Comets
Glass Sky
Glitch
Glow
Holographic
Mono
Neon
Original
Starburst
Sticker
# Blocks Behavior
Canonical page: [/terminal/appearance/blocks-behavior/](https://docs.warp.dev/terminal/appearance/blocks-behavior/)
> Customize Block spacing with Compact mode and toggle Block dividers for a cleaner layout.
## Compact mode
[Section titled “Compact mode”](#compact-mode)
Warp offers the option to enable Compact mode, which condenses the spacing between [Blocks](/terminal/blocks/), enabling more content to be in view.
### How to enable Compact mode
[Section titled “How to enable Compact mode”](#how-to-enable-compact-mode)
Compact mode is disabled by default, but can be toggled in the following ways:
* Navigate to **Settings** > **Appearance** > **Blocks** > **Compact Mode**.
* Utilize the [Command Palette](/terminal/command-palette/), then search for “Compact mode” to toggle.
Note
Warp will open with the same compact settings in future sessions.
[](/assets/terminal/compact_mode.mp4)
## Block dividers
[Section titled “Block dividers”](#block-dividers)
Warp [Blocks](/terminal/blocks/) are divided by horizontal lines that separate individual command input and output, they create a visual break between different commands that you run in a session.
### How to toggle block dividers
[Section titled “How to toggle block dividers”](#how-to-toggle-block-dividers)
Block dividers are enabled by default, but can be toggled in the following ways:
* Navigate to **Settings** > **Appearance** > **Blocks** > **Show block dividers**.
* Utilize the [Command Palette](/terminal/command-palette/), then search for “Block Dividers”.
[](/assets/terminal/block-divider-demo.mp4)
# Custom Themes
Canonical page: [/terminal/appearance/custom-themes/](https://docs.warp.dev/terminal/appearance/custom-themes/)
> Warp supports custom themes, which can be created manually or downloaded from our repo.
Note
Examples and a collection of themes can be found in the [Warp themes repository](https://github.com/warpdotdev/themes).
## Warp’s custom theme repository
[Section titled “Warp’s custom theme repository”](#warps-custom-theme-repository)
We have a [repository of themes hosted on GitHub.](https://github.com/warpdotdev/themes)
Each theme has a preview generated in the README.
The main difference between “standard” and “base16” themes is that “standard” themes follow the typical color setup, while “base16” themes follow the framework suggested by [@chriskempson](https://github.com/chriskempson/base16).
There are 2 ways to install a theme from this repo.
1. Download a single file and follow the steps in the section below.
2. Clone the entire repo into the appropriate location based on your OS below:
* macOS
```bash
mkdir -p $HOME/.warp
cd $HOME/.warp/
git clone https://github.com/warpdotdev/themes.git
```
* Windows
```powershell
New-Item -Path "$env:APPDATA\warp\Warp\data\" -ItemType Directory
Set-Location -Path $env:APPDATA\warp\Warp\data\
git clone https://github.com/warpdotdev/themes.git
```
* Linux
```bash
mkdir -p ${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal
cd ${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/
git clone https://github.com/warpdotdev/themes.git
```
Here is a step-by-step YouTube video that goes through these 2 steps for an example theme. Note the location for the files is based on macOS.

## How do I use a custom theme in Warp?
[Section titled “How do I use a custom theme in Warp?”](#how-do-i-use-a-custom-theme-in-warp)
1. To start, create the following directory:
* macOS
```bash
mkdir -p $HOME/.warp/themes/
```
* Windows
```powershell
New-Item -Path "$env:APPDATA\warp\Warp\data\themes\" -ItemType Directory
```
* Linux
```bash
mkdir -p ${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/themes/
```
Note
It may take several minutes for Warp to initially discover the new themes directory. You can either wait or restart Warp. After that step, all future changes to the directory will be reflected within seconds.
2. Add your new custom theme yaml file to this directory:
```bash
cp ~/Downloads/my_awesome_theme.yaml {{path_to_your_themes_directory_from_step1}}
```
Your new theme should now be visible on the list of available themes.
## Create your custom theme, manually
[Section titled “Create your custom theme, manually”](#create-your-custom-theme-manually)
Warp supports creating custom themes using .yaml files.
The format is subject to change, but we do our best to avoid breaking changes and maintain forward compatibility. We also plan to support sharing and creating custom themes directly within Warp.
A custom theme in Warp has the following `.yaml` structure:
```yaml
name: Custom Theme # Name for the theme
accent: '#268bd2' # Accent color for UI elements
cursor: '#95D886' # Input cursor color (optional; defaults to accent color if omitted)
background: '#002b36' # Terminal background color
foreground: '#839496' # The foreground color
details: darker # Whether the theme is lighter or darker
terminal_colors: # Ansi escape colors
bright:
black: '#002b36'
blue: '#839496'
cyan: '#93a1a1'
green: '#586e75'
magenta: '#6c71c4'
red: '#cb4b16'
white: '#fdf6e3'
yellow: '#657b83'
normal:
black: '#073642'
blue: '#268bd2'
cyan: '#2aa198'
green: '#859900'
magenta: '#d33682'
red: '#dc322f'
white: '#eee8d5'
yellow: '#b58900'
```
Note
Each color is represented in hex and must start with `#`.
* `name`: Name for the theme, will show up in the Theme picker.
* `accent`: Color used for highlights in Warp’s UI
* `cursor`: Color for the input cursor (optional; defaults to accent color if omitted)
* `background`: Color of background
* `foreground`: Color of foreground
* `details`: Color used for detailing options
* `darker`: Color used for dark theme
* `lighter`: Color used for light-mode theme
* `terminal_colors`: Collection of normal & bright colors (16 total) known for other terminal themes (ANSI colors)
## Create your custom theme, automatically
[Section titled “Create your custom theme, automatically”](#create-your-custom-theme-automatically)
Automatically create new themes based on a background image. Click the **+** button in the theme picker **Settings** > **Appearance** > **Themes** or search `Open Theme Picker` within the [Command Palette](/terminal/command-palette/).
## Browse themes and use the theme creator
[Section titled “Browse themes and use the theme creator”](#browse-themes-and-use-the-theme-creator)
Browse Warp’s [theme repository](https://github.com/warpdotdev/themes) for ready-made themes, or use the in-app theme creator to generate the appropriate RGB values for your custom theme. Once the YAML file is created, you can edit the file to add the background images or gradients.
## Background images and gradients
[Section titled “Background images and gradients”](#background-images-and-gradients)
To add a background image you can use this attribute: `background_image:` with the name of the image you want to use as the background.
Note
Warp currently only supports images with the *.jpg* file format:
* `.jpeg`
* `.jpg`
* `.JPEG`
A `.yaml` config looks like this:
```yaml
name: Custom Theme
accent: '#268bd2'
cursor: '#95D886'
background: '#002b36'
details: darker
foreground: '#839496'
############################################################### SEE BELOW
background_image:
# The path is relative to your platform's themes directory:
# macOS: ~/.warp/themes/
# Windows: %APPDATA%\warp\Warp\data\themes\
# Linux: ${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/themes/
# For example, on macOS the full path to the picture below is:
# ~/.warp/themes/warp.jpg
path: warp.jpg
# the opacity value is required and can range from 0-100
opacity: 60
############################################################### SEE ABOVE
terminal_colors:
bright:
black: '#002b36'
blue: '#839496'
cyan: '#93a1a1'
green: '#586e75'
magenta: '#6c71c4'
red: '#cb4b16'
white: '#fdf6e3'
yellow: '#657b83'
normal:
black: '#073642'
blue: '#268bd2'
cyan: '#2aa198'
green: '#859900'
magenta: '#d33682'
red: '#dc322f'
white: '#eee8d5'
yellow: '#b58900'
```
To set up a gradient, create a sublevel under accent with two key-value pairs:
* “left” and “right” or
* “top” and “bottom”.
```yaml
accent:
top: '#abcdef'
bottom: '#fedcba'
```
```yaml
accent:
left: '#abcdef'
right: '#fedcba'
```
Warp also supports setting a gradient for the background.
```yaml
# accent has a gradient
accent:
left: '#474747'
right: '#ffffff'
# background has a gradient
background:
top: '#474747'
bottom: '#ffffff'
```
### Contributing
[Section titled “Contributing”](#contributing)
Contributions to this repo are greatly appreciated!
1. Fork the project
2. Create your branch with `git checkout -b theme/AwesomeTheme`
3. Regenerate thumbnails
4. Commit and open a pull request
Run this script to generate the thumbnails.
```bash
# Assuming you're adding the theme to the `standard` directory:
python3 ./scripts/gen_theme_previews.py standard
```
Note
We cannot accept pull requests that include custom background images because:
* Licensing restrictions
* Trying to keep the binary size of the repo as small as possible (only the yaml files)
If your theme has an intended custom background image, include a comment in the yaml with a link to where people should download it.
## Community
[Section titled “Community”](#community)
All other Warp-related things can be discussed, please [contact us](/support-and-community/troubleshooting-and-support/sending-us-feedback/).
## Open source dependencies
[Section titled “Open source dependencies”](#open-source-dependencies)
We’d like to call out a few of the open-source themes and repositories that helped bootstrap the set of themes for Warp:
* [iTerm colors pencil](https://github.com/mattly/iterm-colors-pencil)
* [Alacritty-theme](https://github.com/eendroroy/alacritty-theme)
* [base16-Alacritty](https://github.com/aarowill/base16-alacritty)
* [base16](https://github.com/chriskempson/base16)
* [Solarized](https://ethanschoonover.com/solarized/)
* [Dracula](https://draculatheme.com/)
* [Gruvbox](https://github.com/morhetz/gruvbox)
# Input position
Canonical page: [/terminal/appearance/input-position/](https://docs.warp.dev/terminal/appearance/input-position/)
> Warp gives you the ability to configure the position of your input, which includes both the prompt and the command line.
You can select from three different input positions, which each have different modes of behavior for the flow of input/output Blocks.
| Input position | Behavior | |
| ------------------------------- | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | - |
| Start at the top (Classic mode) | When you select “start at the top,” the prompt with input will initiate at the top of the view and move down in the view as you enter commands. Blocks of input/output will stack above the prompt and command input. You can scroll up or navigate up to visit past commands. You can enter `Ctrl+L` or the `clear` command at any time to return the input to the top of the screen while still maintaining your scroll history. | |
| Pin to the top (Reverse mode) | When you select “pin to the top,” the prompt with input will display pinned to the top of your terminal view. Blocks of grouped input/output will flow down the view in reverse order with your latest results at the top. You can scroll down or navigate down to visit past commands. For long-running commands, you can also click “Lock scrolling at bottom of block” to continue to follow the stdout. | |
| Pin to the bottom (Warp mode) | Warp mode starts with input pinned to the bottom of your terminal view. Blocks of grouped input/output flow up and out of view. You can scroll up or navigate up to visit past commands. | |
## How to access it
[Section titled “How to access it”](#how-to-access-it)
* You can configure your input position by navigating to **Settings** > **Appearance** > **Input**.
* You can also choose and set modes from the [Command Palette](/terminal/command-palette/).
Note
Changes to the input position take place immediately and apply to all open panes.
### Related commands
[Section titled “Related commands”](#related-commands)
* macOS
* `⌘+K` will clear the entire list of input/output blocks for a clean view
* `Ctrl+L` will move the list of input/output blocks outside of the view and past the scroll so you have a clean view and the ability to easily visit past commands
* For long Blocks, you can press `⌘+Shift+↑`/`⌘+Shift+↓` to scroll to the top/bottom of the selected block.
* Windows
* `Ctrl+Shift+K` will clear the entire list of input/output blocks for a clean view
* `Ctrl+L` will move the list of input/output blocks outside of the view and past the scroll so you have a clear view and the ability to easily visit past commands
* For long Blocks, you can press `Ctrl+Shift+↑`/`Ctrl+Shift+↓` to scroll to the top/bottom of the selected block.
* Linux
* `Ctrl+Shift+K` will clear the entire list of input/output blocks for a clean view
* `Ctrl+L` will move the list of input/output blocks outside of the view and past the scroll so you have a clear view and the ability to easily visit past commands
* For long Blocks, you can press `Ctrl+Shift+↑`/`Ctrl+Shift+↓` to scroll to the top/bottom of the selected block.
## How it works
[Section titled “How it works”](#how-it-works)

# Pane Dimming & Focus
Canonical page: [/terminal/appearance/pane-dimming/](https://docs.warp.dev/terminal/appearance/pane-dimming/)
> Warp supports dimming inactive Panes as well as allowing the focus to follow the mouse. This helps you easily see which pane is active and maintain focus.
## How to use it
[Section titled “How to use it”](#how-to-use-it)
### Inactive pane dimming
[Section titled “Inactive pane dimming”](#inactive-pane-dimming)
The panes that aren’t active will be dimmed to better indicate which pane is active. To access it, go to **Settings** > **Appearance** > **Panes**
* Toggle on **Dim inactive panes** to enable the feature.
Note
Split panes show a triangle indicator on the top-left corner of the active pane.
### Mouse focus
[Section titled “Mouse focus”](#mouse-focus)
The pane with the mouse over it will become active. To access it, go to **Settings** > **Appearance** > **Panes**
* Toggle on **Focus follows mouse** to enable the feature.
## How it works
[Section titled “How it works”](#how-it-works)
[Inactive Pane Dimming Demo](https://www.loom.com/embed/62b84d3c60b34cdbaa340fbe8ce8b1d1)
# Terminal prompt
Canonical page: [/terminal/appearance/prompt/](https://docs.warp.dev/terminal/appearance/prompt/)
> Configure Warp's native prompt with context chips or use your own Shell prompt (PS1).
Warp supports two prompt types: the **Warp prompt** and the **Shell prompt (PS1)**.
## Choosing your prompt type
[Section titled “Choosing your prompt type”](#choosing-your-prompt-type)
To switch your prompt type:
1. In the Warp app, open **Settings** > **Appearance**.
2. Under **Input**, set **Input type** to **Warp** or **Shell (PS1)**.
With the Warp prompt, open the prompt context menu to copy the entire prompt or individual context chip values, such as the working directory or Git branch. Right-click the prompt, or use `Shift`+right-click if your right-click behavior is set to paste.
With a Shell prompt, open the prompt context menu to copy the entire prompt. You can also select part of the prompt in a previously run block.
## Warp prompt
[Section titled “Warp prompt”](#warp-prompt)
Warp’s native prompt displays context chips for information such as your current working directory, Git branch, Subversion status, Kubernetes context, Python environment, date, and time. The Warp prompt is the default when **Input type** is set to **Warp**.
To customize which context chips your Warp prompt displays:
1. In the Warp app, open **Settings** > **Appearance**.
2. Under **Input**, click the prompt preview below **Input type**.
3. In **Edit prompt**, select **Warp terminal prompt**.
4. Drag context chips into the dashed box and arrange them in the order you want.
5. Click **Save changes**.
### Git and Subversion
[Section titled “Git and Subversion”](#git-and-subversion)
Git and Subversion context chips show your local branch and uncommitted changes. Git chips can also show remote tracking status and diff statistics.
### Kubernetes
[Section titled “Kubernetes”](#kubernetes)
The Kubernetes context chip shows relevant information when you’re using one of the following commands:
`kubectl|helm|kubens|kubectx|oc|istioctl|kogito|k9s|helmfile|flux|fluxctl|stern|kubeseal|skaffold|kubent|kubecolor|cmctl|sparkctl|etcd|fubectl`
Note
Warp respects the `KUBECONFIG` environment variable. Make sure you set it to your preferred configuration file location if it’s not the default path of `~/.kube/config`.
## Shell prompt (PS1)
[Section titled “Shell prompt (PS1)”](#shell-prompt-ps1)
You can use a Shell prompt instead of the Warp prompt by configuring the **PS1** variable or installing a supported shell prompt plugin (see [Shell prompt compatibility table](/terminal/appearance/prompt/#shell-prompt-compatibility-table)).
To enable the Shell prompt:
1. In the Warp app, open **Settings** > **Appearance**.
2. Under **Input**, set **Input type** to **Shell (PS1)**.
3. Configure your `PS1` variable in your shell’s RC file, or install a supported prompt plugin.
`PS1` is the shell variable for the primary prompt string, which the terminal displays before your command-line input.
### Multi-line and right-sided prompts
[Section titled “Multi-line and right-sided prompts”](#multi-line-and-right-sided-prompts)
The Shell prompt supports multi-line or right-sided prompts in zsh and fish, not bash. However, you can’t have a multiline right-side prompt, only a multiline left prompt.
Note
If you want to add a new line to your Shell prompt, run the following based on your shell or prompt:
```sh
# Bash
echo -e '\nPS1="${PS1}"$'\''\\n'\''' >> ~/.bashrc
# Zsh
echo -e '\nPROMPT="${PROMPT}"$'\''\\n'\''' >> ~/.zshrc
# Fish
echo -e '\nfunctions --copy fish_prompt fish_prompt_orig; function fish_prompt; fish_prompt_orig; echo; end' >> ~/.config/fish/config.fish
# PowerShell
$rawString = @'
$originalPrompt = Get-Item Function:\prompt
Set-Item -Path Function:\prompt_original -Value $originalPrompt
function prompt {
"$(& prompt_original)`n"
}
'@
Add-Content -Path $PROFILE -Value "`n$rawString`n"
# Powerlevel10k
p10k configure
# Starship Prompt
echo '[line_break]\ndisabled = false' >> ~/.config/starship.toml
```
### Shell prompt compatibility table
[Section titled “Shell prompt compatibility table”](#shell-prompt-compatibility-table)
| Shell | Tool | Does it work? |
| --------------------------- | ------------------------------------------------------------------------- | --------------------------------------------------------------- |
| bash \| zsh | [PS1](https://www.warp.dev/blog/whats-so-special-about-ps1) | Working |
| bash \| zsh \| fish \| pwsh | [Starship](https://github.com/starship/starship) | [Working\*](/terminal/appearance/prompt/#starship) |
| bash \| zsh \| fish \| pwsh | [oh-my-posh](https://github.com/JanDeDobbeleer/oh-my-posh) | Working |
| zsh | [Powerlevel10k](https://github.com/romkatv/powerlevel10k) | [Working\*](/terminal/appearance/prompt/#powerlevel10k) |
| zsh | [Spaceship](https://github.com/spaceship-prompt/spaceship-prompt) | [Working\*](/terminal/appearance/prompt/#spaceship) |
| zsh | [oh-my-zsh](https://github.com/ohmyzsh/ohmyzsh) | Working |
| zsh | [prezto](https://github.com/sorin-ionescu/prezto) | [Working\*](/terminal/appearance/prompt/#prezto) |
| ssh | | Working |
| bash | [oh-my-bash](https://github.com/ohmybash/oh-my-bash) | Not supported |
| bash | [bash-it](https://github.com/Bash-it/bash-it) | Not supported |
| bash | [SBP](https://github.com/brujoand/sbp) | Not supported |
| bash | [synth-shell-prompt](https://github.com/andresgongora/synth-shell-prompt) | Not supported |
| bash \| zsh | [Powerline-shell](https://github.com/b-ryan/powerline-shell) | Not supported |
| zsh | [zplug](https://github.com/zplug/zplug) | Not supported |
| fish | [tide](https://github.com/IlanCosman/tide) | [Not supported](https://github.com/warpdotdev/Warp/issues/3358) |
| fish | [oh-my-fish](https://github.com/oh-my-fish/oh-my-fish) | [Not supported](https://github.com/warpdotdev/Warp/issues/3796) |
## Known incompatibilities
[Section titled “Known incompatibilities”](#known-incompatibilities)
If you have prompt issues, review the notes below and [debug your shell RC files](/support-and-community/troubleshooting-and-support/known-issues/#configuring-and-debugging-your-rc-files).
### Starship
[Section titled “Starship”](#starship)
#### Starship settings
[Section titled “Starship settings”](#starship-settings)
To keep a Starship prompt on one line, add the following to `~/.config/starship.toml`:
```toml
[line_break]
disabled = true
```
Set `disabled` to `false` to put the input on a new line. For other prompt-wide settings, including `command_timeout`, see the [Starship prompt configuration](https://starship.rs/config/#prompt).
#### Starship + bash
[Section titled “Starship + bash”](#starship--bash)
Starship may not render properly if your [default shell](/getting-started/supported-shells/#changing-what-shell-warp-uses) is `/bin/bash`. To work around the issue, upgrade Bash, find its path with `command -v bash`, then select that path under **Settings** > **Features** > **Session** > **Default shell for new sessions** in the Warp app.
#### Starship + zsh
[Section titled “Starship + zsh”](#starship--zsh)
To put the input on a new line after the Starship prompt in zsh, add `PROMPT="${PROMPT}"$'\n'` to the bottom of `~/.zshrc`.
### Powerlevel10k
[Section titled “Powerlevel10k”](#powerlevel10k)
Powerlevel10k recommends the [Meslo Nerd Font](https://github.com/romkatv/powerlevel10k/blob/master/font.md).
Powerlevel10k may display arrow dividers in gray because of Warp’s minimum contrast setting. To work around the issue, go to **Settings** > **Appearance** > **Text** > **Enforce minimum contrast** and select **Never**.
Example of the grey dividers in p10k.
Warp supports [Powerlevel10k](https://github.com/romkatv/powerlevel10k#installation) version 1.19.0 and later. Install the latest version, restart Warp, then [switch to the Shell prompt](#choosing-your-prompt-type).
Warp doesn’t support some Powerlevel10k features, including transient prompts and gradients.
### Spaceship
[Section titled “Spaceship”](#spaceship)
This prompt can cause an issue with typeahead in Warp’s input editor. To work around the issue, run `echo "SPACESHIP_PROMPT_ASYNC=FALSE" >>! ~/.zshrc`.
### Prezto
[Section titled “Prezto”](#prezto)
Warp supports the Prezto prompt, but not the [Prezto utility module](https://github.com/sorin-ionescu/prezto/blob/master/modules/utility/README.md) or other [incompatible autocompletion plugins](/support-and-community/troubleshooting-and-support/known-issues/#list-of-incompatible-tools).
### Disabling unsupported prompts for Warp
[Section titled “Disabling unsupported prompts for Warp”](#disabling-unsupported-prompts-for-warp)
Use Warp’s default prompt or install a tool from the [Shell prompt compatibility table](#shell-prompt-compatibility-table). To disable an unsupported prompt only in Warp, wrap its setup in this condition:
```bash
if [[ $TERM_PROGRAM != "WarpTerminal" ]]; then
##### WHAT YOU WANT TO DISABLE FOR WARP - BELOW
# Unsupported Custom Prompt Code
##### WHAT YOU WANT TO DISABLE FOR WARP - ABOVE
fi
```
#### iTerm2
[Section titled “iTerm2”](#iterm2)
The iTerm2 shell integration is incompatible with Warp and can hide your custom prompt. If you migrated from iTerm2, check your dotfiles and disable the integration in Warp:
```bash
if [[ $TERM_PROGRAM != "WarpTerminal" ]]; then
##### WHAT YOU WANT TO DISABLE FOR WARP - BELOW
test -e "${HOME}/.iterm2_shell_integration.zsh" && source "${HOME}/.iterm2_shell_integration.zsh"
##### WHAT YOU WANT TO DISABLE FOR WARP - ABOVE
fi
```
## Related pages
[Section titled “Related pages”](#related-pages)
* [Supported shells](/getting-started/supported-shells/)
* [Configuring and debugging shell RC files](/support-and-community/troubleshooting-and-support/known-issues/#configuring-and-debugging-your-rc-files)
# Size, Opacity, & Blurring
Canonical page: [/terminal/appearance/size-opacity-blurring/](https://docs.warp.dev/terminal/appearance/size-opacity-blurring/)
> Configure window size, opacity, and background blurring to match your visual preferences.
## How to use it
[Section titled “How to use it”](#how-to-use-it)
### Window size
[Section titled “Window size”](#window-size)
To access size settings, go to **Settings** > **Appearance** > **Window**.
* Enable “Open new windows with custom size”, then configure your preferred columns and rows.
Note
If [Session Restoration](/terminal/sessions/session-restoration/) is enabled, Warp will restore the size of the last window closed when you quit the app. Either make sure the custom-sized window is the last one closed, or disable Session Restoration to ensure Warp launches with the custom-sized window.
### Window opacity
[Section titled “Window opacity”](#window-opacity)
To access it, go to **Settings** > **Appearance** > **Window**
* The slider supports setting the opacity value between `1` and `100` where `100` is completely opaque or solid.
### Window blurring
[Section titled “Window blurring”](#window-blurring)
After decreasing the opacity below `100`, you can blur the background or choose a Windows backdrop material.
* On macOS, use the blur slider. Increasing the slider increases the blur radius applied to the background image.
* On Windows, choose a **Window backdrop** material: **No material**, **Mica**, **Acrylic**, or **Mica Alt**. Backdrop is not visible at opacity 100%. In the settings file, this is `appearance.window.backdrop` (`none`, `mica`, `acrylic`, or `mica_alt`).
Caution
On macOS, large blur radiuses may affect performance, especially on Retina displays.
On Linux, window blurring is not supported.
On Windows, some graphics drivers may not support rendering transparent or translucent windows. See below for troubleshooting tips.
## How it works
[Section titled “How it works”](#how-it-works)
[](/assets/terminal/window_size_demo.mp4)
[Window Opacity and Blurring Demo](https://www.loom.com/embed/22c9ef25392e4a5e80f9e01394c84dc4)
### Troubleshooting transparency on Windows
[Section titled “Troubleshooting transparency on Windows”](#troubleshooting-transparency-on-windows)
Note
At the moment, window opacity in Warp on Windows **does not work** in the following circumstances:
* When using DirectX 12 as the rendering backend
* When using any rendering backend with an Nvidia GPU when “Auto” or “Prefer layered” is selected as the value for “Vulkan/OpenGL present method” in NVIDIA Control Panel > Manage 3D Settings
Some graphics drivers and rendering backends may not support rendering transparent windows.
You can select the Vulkan or OpenGL graphics backend to render new Warp windows in the Settings menu, under **Features** > **System** > **Preferred graphics backend**.
You can also opt to render new Warp windows with an integrated GPU, under **Features** > **System** > **Prefer rendering new windows with integrated GPU (low power)**.
# Tabs Behavior
Canonical page: [/terminal/appearance/tabs-behavior/](https://docs.warp.dev/terminal/appearance/tabs-behavior/)
> Customize tab behavior in Warp, including tab indicators, tab bar visibility, and close button position.
## Tab indicators
[Section titled “Tab indicators”](#tab-indicators)
Tab indicators provide visual cues in the tab bar under certain specific conditions: When the current pane is maximized, when panes or tabs are synchronized, and when a command exits with an error. These indicators serve as quick references.
### How to toggle tab indicators
[Section titled “How to toggle tab indicators”](#how-to-toggle-tab-indicators)
* Navigate to **Settings** > **Appearance** > **Tabs**, and switch the “Show tab indicators” option.
* Utilize the [Command Palette](/terminal/command-palette/), then search for “Tab indicators” to toggle the tab indicators.
[](/assets/terminal/tab-indicator-demo.mp4)
## Tab bar
[Section titled “Tab bar”](#tab-bar)
The tab bar provides easy navigation between open tabs. By default, the tab bar is visible in windowed mode but hides in fullscreen. To access the tab bar when hidden, hover near the top of the window. You can customize its visibility based on your preferences.
### How to configure the tab bar
[Section titled “How to configure the tab bar”](#how-to-configure-the-tab-bar)
* Navigate to **Settings** > **Appearance** > **Tabs** > **Show the tab bar** to toggle the visibility of the tab bar. Choose from the following options:
* Always – Keeps the tab bar visible at all times.
* Only on hover – Hides the tab bar in both modes.
* When windowed – Displays the tab bar only in windowed mode.
* Block dividers
Note
On macOS, traffic lights will not be shown when in windowed mode if the tab bar is set to show only on hover.
[](/assets/terminal/tab-bar-demo.mp4)
## Tab close button
[Section titled “Tab close button”](#tab-close-button)
You can configure the position of the tab close button to be either on the left or right side of the tab.
### How to configure the tab close button
[Section titled “How to configure the tab close button”](#how-to-configure-the-tab-close-button)
Navigate to **Settings** > **Appearance** > **Tabs** > **Tab close button position**, then choose from the following options:
* Left - the close button will be on the left side of the tab (macOS style)
* Right – the close button will be on the right side of the tab (Windows | Linux style)\\
[](/assets/terminal/tab-close-button-demo.mp4)
# Text, Fonts, & Cursor
Canonical page: [/terminal/appearance/text-fonts-cursor/](https://docs.warp.dev/terminal/appearance/text-fonts-cursor/)
> Warp supports customizing the font and how text is displayed. This can help improve readability and usability. Warp also supports disabling the blinking cursor.
Note
Once a new font is installed in your system, you need to restart Warp for it to show on the list of options. You may also need to check “View all available system fonts” to see the new font.
## How to use it
[Section titled “How to use it”](#how-to-use-it)
### Text and fonts
[Section titled “Text and fonts”](#text-and-fonts)
To access it, go to **Settings** > **Appearance** > **Text**
From there you can customize:
* Font type
* Font weight
* Font size
* Line height
* Use thin strokes
* The default setting prevents text from being blurry on low-DPI displays.
Caution
On Linux, Warp does not support the “Use thin strokes” feature.
* Enforce minimum contrast
* The default setting tweaks named colors to meet accessibility standards.
* Show ligatures in terminal
Note
Enabling ligatures can reduce performance. Warp’s default font, Hack, doesn’t yet have ligature support. We recommend a font that supports ligatures (e.g. [Fira Code](https://github.com/tonsky/FiraCode)) as a stopgap.
### Cursor
[Section titled “Cursor”](#cursor)
To access it, go to **Settings** > **Appearance** > **Cursor**
From there you can customize:
* Set the cursor type to Bar, Block, or Underline.
* Toggle the Blinking cursor or from the [Command Palette](/terminal/command-palette/), type “Cursor blink” and toggle the setting.
Note
Cursor type preference is disabled while [Vim keybindings](/terminal/editor/vim/) (vim mode) is active.
## How it works
[Section titled “How it works”](#how-it-works)
[Text and Fonts Demo](https://www.loom.com/embed/be2fa6ab10a3494a8c57a5431966905b)
[Cursor Demo](https://www.loom.com/embed/6ce3218472894763bb80a26b6c632c4d)
# Terminal themes
Canonical page: [/terminal/appearance/themes/](https://docs.warp.dev/terminal/appearance/themes/)
> Warp includes several themes (out-of-box) and also supports setting custom themes.
### Theme picker
[Section titled “Theme picker”](#theme-picker)
The theme picker can be accessed by:
1. Navigating to **Settings** > **Appearance**.
2. Clicking the Custom Themes (shaded) box.
3. Upon selecting a theme, Warp’s appearance will update accordingly.
4. Press the checkmark to save the selection, or the X to revert.
Note
The Theme setting persists, meaning Warp will open with the same settings in the next session.
### Theme creator
[Section titled “Theme creator”](#theme-creator)
Automatically create new themes based on a background image.
1. Go to **Settings** > **Appearance** > **Themes** or search “Open theme picker” within the [Command Palette](/terminal/command-palette/).
2. Click the **+** button in the theme picker.
3. Upload the image and select the background color.
4. Click “Create Theme” to save and accept the new theme.
### OS theme sync
[Section titled “OS theme sync”](#os-theme-sync)
Warp supports synchronizing your theme with the OS’s light and dark themes. To enable this:
1. Open the **Settings** > **Appearance** dialog.
2. Click the toggle “Sync with OS”.
3. You will then be able to select a specific theme for when the OS is in light mode and dark mode.
## How it works
[Section titled “How it works”](#how-it-works)
[](/assets/terminal/theme-picker.mp4) [](/assets/terminal/theme-creator.mp4) [](/assets/terminal/theme-sync-demo.mp4)
## Default themes
[Section titled “Default themes”](#default-themes)
By default, Warp ships with these themes:
Warp Dark
Warp Light
Dracula
Solarized Dark
Solarized Light
Gruvbox Dark
Gruvbox Light
Jellyfish
Koi
Leafy
Marble
Pink City
Snowy
Dark City
Red Rock
Cyber Wave
Willow Dream
Fancy Dracula
Phenomenon
Solar Flare
Adeberry
# Terminal Blocks overview
Canonical page: [/terminal/blocks/](https://docs.warp.dev/terminal/blocks/)
> A Block groups commands and outputs into one atomic unit.
Blocks are Warp’s fundamental unit for organizing terminal output. Every command and its output is grouped into a single Block that you can copy, search, filter, bookmark, share, and navigate independently — replacing the endless scroll of traditional terminals with structured, actionable output.
## What are Blocks?
[Section titled “What are Blocks?”](#what-are-blocks)
Blocks enable us to easily:
* Copy a command
* Copy a command’s output
* Scroll directly to the start of a command’s output
* Re-input commands
* Share both a command and its output (with formatting!)
* Bookmark commands
Note
Interested in how we differentiate input and output, or how we implement blocks? Check out our blog post: [How Warp Works](https://www.warp.dev/blog/how-warp-works#implementing-blocks).

# Background Blocks
Canonical page: [/terminal/blocks/background-blocks/](https://docs.warp.dev/terminal/blocks/background-blocks/)
> How Blocks interact with background process output.
## What is it
[Section titled “What is it”](#what-is-it)
Commands can start background processes that continue even after they exit. You can also start a background process directly from the shell, such as by running it with `&`.
If Warp receives output that is likely from a background process, the output goes into a *background block*. Background blocks act like regular blocks, except that they don’t have an associated command.
This lets you use all of Warp’s block features with background output, such as sharing and bookmarking.
## How to use it
[Section titled “How to use it”](#how-to-use-it)
Background blocks are automatically created as needed, in between regular blocks running. If you run commands while a background process is still producing output, that output gets split into multiple blocks interleaved with your commands.
## How it works
[Section titled “How it works”](#how-it-works)
[Create Background Blocks](https://www.loom.com/embed/55bbbd9a8cbf495189260756c717cfb2)
## Troubleshooting background blocks
[Section titled “Troubleshooting background blocks”](#troubleshooting-background-blocks)
There are some limitations, because Warp doesn’t know *which* process any given output came from:
* If a background process writes output while a foreground command is running in a regular block, the output goes into that block.
* If there are multiple background processes running at the same time, their output may be mixed together.
In addition, if you start entering a command while another one is running (typeahead), in some cases Warp will mistake the partial command for background output. The most common cause is editing typeahead when using bash versions older than 4.0 (for example, deleting and re-typing part of it).
# Block Actions
Canonical page: [/terminal/blocks/block-actions/](https://docs.warp.dev/terminal/blocks/block-actions/)
> Copy, bookmark, share, search, and filter Blocks using built-in actions.
## Accessing block actions
[Section titled “Accessing block actions”](#accessing-block-actions)
There are 2 ways you can access Block actions.
1. Hover over a Block and click the kebab (three dots) button on the right-hand side.
2. Right-click a Block.
[Accessing Block Actions](https://www.loom.com/embed/3dec25e548d4484aa3dd6437869e2bbf)
## Copy input / output of block
[Section titled “Copy input / output of block”](#copy-input--output-of-block)
For command blocks, you can `RIGHT-CLICK` on a Block or click the context menu and copy the Block command, output, or both.
For AI blocks, you can `RIGHT-CLICK` to copy the prompt, output, both, or the entire conversation.
[Copy Block Actions](https://www.loom.com/embed/9ad67eca0a8d47afb82cc1acba617f3c)
## Sharing a block
[Section titled “Sharing a block”](#sharing-a-block)
Share a block easily with coworkers or teammates by creating a web permalink. This preserves formatting and makes debugging and sharing output easy. See the [Block sharing page](/terminal/blocks/block-sharing/).
## Bookmarking a block
[Section titled “Bookmarking a block”](#bookmarking-a-block)
Quickly navigate to important Blocks despite where they are in the terminal history.
* macOS
Ways to bookmark a Block:
1. Select **Toggle bookmark** in the block context menu
2. Use `⌘+B` keybinding to bookmark a selected block
Navigate to a bookmarked Block, by:
* Clicking on the indicator.\
The indicator position reflects the approximate position of the Block in the Block history. Hovering over the indicator will give a snapshot of the Block including its prompt, command, and the last two lines of output.
* Pressing `Option+↑` and `Option+↓`
* Windows
Ways to bookmark a Block:
1. Select **Toggle bookmark** in the block context menu
2. Use `Ctrl+Shift+B` keybinding to bookmark a selected block
Navigate to a bookmarked Block, by:
* Clicking on the indicator.\
The indicator position reflects the approximate position of the Block in the Block history. Hovering over the indicator will give a snapshot of the Block including its prompt, command, and the last two lines of output.
* Pressing `Alt+↑` and `Alt+↓`
* Linux
Ways to bookmark a Block:
1. Click on the bookmark icon in the top right corner of a Block
2. Select **Toggle bookmark** in the block context menu
3. Use `Ctrl+Shift+B` keybinding to bookmark a selected block
Navigate to a bookmarked Block, by:
* Clicking on the indicator.\
The indicator position reflects the approximate position of the Block in the Block history. Hovering over the indicator will give a snapshot of the Block including its prompt, command, and the last two lines of output.
* Pressing `Alt+↑` and `Alt+↓`
Note
Bookmarks only persist while the session is open, once you close the session they are lost. If you want to save the command and output for later use, [Share the Block](/terminal/blocks/block-sharing/).
[](/assets/terminal/block-bookmarks.mp4)
## Search within a block
[Section titled “Search within a block”](#search-within-a-block)
Quickly find important information within a Block. See the [Find page](/terminal/blocks/find/).
* macOS
With a Block selected, press “Find Within Block” or use `⌘+F` to search within a Block.
* Windows
With a Block selected, press “Find Within Block” or use `Ctrl+Shift+F` to search within a Block.
* Linux
With a Block selected, press “Find Within Block” or use `Ctrl+Shift+F` to search within a Block.
[Search within a Block](https://www.loom.com/embed/7dda0e7a6ec144cfb6410d29a586ddd0)
## Filtering a block
[Section titled “Filtering a block”](#filtering-a-block)
Filter the output lines of a block natively in Warp to quickly focus on a subset of the block. See the [Block filtering page](/terminal/blocks/block-filtering/).
* macOS
* Using the keybinding `Option+Shift+F` by default to toggle filtering on the selected or latest block
* Selecting `Toggle Block Filter` in the block context menu
* Windows
* Using the keybinding `Alt+Shift+F` to toggle filtering on the selected or latest block
* Selecting `Toggle Block Filter` in the block context menu
* Linux
* Using the keybinding `Alt+Shift+F` to toggle filtering on the selected or latest block
* Selecting `Toggle Block Filter` in the block context menu
# Terminal Block Basics
Canonical page: [/terminal/blocks/block-basics/](https://docs.warp.dev/terminal/blocks/block-basics/)
> The basics of creating, selecting, and navigating between Blocks.
## The basics
[Section titled “The basics”](#the-basics)
* Blocks group your command and command output
* The Input Editor can pin to the bottom, pin to the top, or start at the top.
* Blocks grow from the bottom to the top.
* Blocks are color-coded. Blocks that quit with a non-zero exit code have a red background and red sidebar.
Note
Try it yourself!\
Type `xyz` (or some other command that doesn’t exist) and hit `Enter`
## Create a block
[Section titled “Create a block”](#create-a-block)
1. Execute a command (type `ls` and hit `Enter`) in the Input Editor at the bottom of the screen.
2. Your command and output are grouped into a Block.
3. Try executing a different command (type `echo hello` and hit `Enter`).
4. Warp adds your newly created Block to the bottom (directly above the input editor).
[Create a Block](https://www.loom.com/embed/4b435c78344d4dc0bb92af5d1da5e219)
## Select a single block
[Section titled “Select a single block”](#select-a-single-block)
* macOS
* Using your mouse: click on a Block.
* Or using your keyboard: hit `⌘+↑` (or `⌘+↓` if input is pinned up top) to select the most recently executed Block and use the `↑` and `↓` arrow keys to navigate to the desired Block.
* For long Blocks:
* You can click “Jump to the bottom of this block”.
* You can press `⌘+Shift+↑`/`⌘+Shift+↓` to scroll to the top/bottom of the selected block.
* From the [Command Palette](/terminal/command-palette/), you can also “Scroll to the top/bottom of selected block”.
* Windows
* Using your mouse: click on a Block.
* Or using your keyboard: hit `Ctrl+↑` (or `Ctrl+↓` if input is pinned up top) to select the most recently executed Block and use the `↑` and `↓` arrow keys to navigate to the desired Block.
* For long Blocks:
* You can click “Jump to the bottom of this block”.
* You can press `Ctrl+Shift+↑`/`Ctrl+Shift+↓` to scroll to the top/bottom of the selected block.
* From the [Command Palette](/terminal/command-palette/), you can also “Scroll to the top/bottom of selected block”.
* Linux
* Using your mouse: click on a Block.
* Or using your keyboard: hit `Ctrl+↑` (or `Ctrl+↓` if input is pinned up top) to select the most recently executed Block and use the `↑` and `↓` arrow keys to navigate to the desired Block.
* For long Blocks:
* You can click “Jump to the bottom of this block”.
* You can press `Ctrl+Shift+↑`/`Ctrl+Shift+↓` to scroll to the top/bottom of the selected block.
* From the [Command Palette](/terminal/command-palette/), you can also “Scroll to the top/bottom of selected block”.
[Select a Single Block](https://www.loom.com/embed/1cf8546daad548fbbe056c35edb23cdc)
## Select multiple blocks
[Section titled “Select multiple blocks”](#select-multiple-blocks)
* macOS
* Click another Block while holding `⌘` to toggle the selection of that Block, or
* Click another Block while holding `Shift` to select a range of Blocks, or
* Use `Shift+↑` or `Shift+↓` to expand the active selection (the Block with the thicker border) up or down, respectively.
* Windows
* Click another Block while holding `Ctrl+Shift` to toggle the selection of that Block, or
* Click another Block while holding `Shift` to select a range of Blocks, or
* Use `Shift+↑` or `Shift+↓` to expand the active selection (the Block with the thicker border) up or down, respectively.
* Linux
* Click another Block while holding `Ctrl+Shift` to toggle the selection of that Block, or
* Click another Block while holding `Shift` to select a range of Blocks, or
* Use `Shift+↑` or `Shift+↓` to expand the active selection (the Block with the thicker border) up or down, respectively.
[Select Multiple Blocks](https://www.loom.com/embed/5058ab0dc3d244d4a2ce576331440821)
## Navigate blocks
[Section titled “Navigate blocks”](#navigate-blocks)
* macOS
* **Mouse or scrollbar** - Scroll using your mouse, trackpad, or the scrollbar.
* **Arrow keys** - Select a Block and use `↑` and `↓` to move between Blocks.
* **Page scrolling** - Press `Page Up` or `Page Down` to scroll by one page.
* **Jump to top or bottom** - Press `Home` or `End` to scroll to the top or bottom of terminal output.
* **Scroll within a selected Block** - Press `⌘+Shift+↑` or `⌘+Shift+↓` to scroll to the top or bottom of the selected Block.
* **Scroll one line at a time** - “Scroll Terminal output up/down one line” can be configured with a keyboard shortcut in **Settings** > **Keyboard shortcuts** or accessed from the [Command Palette](/terminal/command-palette/).
* When the output of a command is cut off, Warp keeps the [Sticky Command Header](/terminal/blocks/sticky-command-header/) pinned at the top that displays the command the Block corresponds to. Clicking the header will scroll the screen to the start of the Block.
* Windows
* **Mouse or scrollbar** - Scroll using your mouse, trackpad, or the scrollbar.
* **Arrow keys** - Select a Block and use `↑` and `↓` to move between Blocks.
* **Page scrolling** - Press `Page Up` or `Page Down` to scroll by one page.
* **Jump to top or bottom** - Press `Home` or `End` to scroll to the top or bottom of terminal output.
* **Scroll within a selected Block** - Press `Ctrl+Shift+↑` or `Ctrl+Shift+↓` to scroll to the top or bottom of the selected Block.
* **Scroll one line at a time** - “Scroll Terminal output up/down one line” can be configured with a keyboard shortcut in **Settings** > **Keyboard shortcuts** or accessed from the [Command Palette](/terminal/command-palette/).
* When the output of a command is cut off, Warp keeps the [Sticky Command Header](/terminal/blocks/sticky-command-header/) pinned at the top that displays the command the Block corresponds to. Clicking the header will scroll the screen to the start of the Block.
* Linux
* **Mouse or scrollbar** - Scroll using your mouse, trackpad, or the scrollbar.
* **Arrow keys** - Select a Block and use `↑` and `↓` to move between Blocks.
* **Page scrolling** - Press `Page Up` or `Page Down` to scroll by one page.
* **Jump to top or bottom** - Press `Home` or `End` to scroll to the top or bottom of terminal output.
* **Scroll within a selected Block** - Press `Ctrl+Shift+↑` or `Ctrl+Shift+↓` to scroll to the top or bottom of the selected Block.
* **Scroll one line at a time** - “Scroll Terminal output up/down one line” can be configured with a keyboard shortcut in **Settings** > **Keyboard shortcuts** or accessed from the [Command Palette](/terminal/command-palette/).
* When the output of a command is cut off, Warp keeps the [Sticky Command Header](/terminal/blocks/sticky-command-header/) pinned at the top that displays the command the Block corresponds to. Clicking the header will scroll the screen to the start of the Block.
Note
During long-running or full-screen commands, `Page Up`, `Page Down`, `Home`, and `End` are forwarded to the running program. See the full list of scrolling shortcuts on the [Keyboard Shortcuts](/getting-started/keyboard-shortcuts/) page.
[Navigate between Blocks](https://www.loom.com/embed/21ebb0a79c1248a98846cba12a4b7020)
# Block Filtering
Canonical page: [/terminal/blocks/block-filtering/](https://docs.warp.dev/terminal/blocks/block-filtering/)
> Filter Block output by text, regex, or case to focus on specific matching lines.
Filter the output lines of a block in Warp to quickly focus on a subset of the block. You can filter by plaintext, regex, invert, or make your filter case-sensitive. You can also add context lines to view output around matches. Filtering does not delete any output lines, so you can clear the filter to go back to the original output.
## How to filter a block
[Section titled “How to filter a block”](#how-to-filter-a-block)
To apply a filter to a block:
1. Click on the filter icon in the top right corner of a block. A filter editor will appear with a large input field with two buttons on the left and a smaller input field on the right.
2. Type in the input to filter the block in the left input field. Only lines containing text that matches the filter query will be shown.
3. (Optional) Click on the regex, case sensitive search, or invert filter buttons to enable.
4. (Optional) Type a number in the right input field to add context lines around matched lines.
[](/assets/terminal/block_filtering_with_context_lines.mp4)
* macOS
You can also toggle a filter by:
* Using the keybinding `Option+Shift+F` by default to toggle filtering on the selected or latest block
* Selecting `Toggle Block Filter` in the block context menu
* Windows
You can also toggle a filter on/off by:
* Using the keybinding `Alt+Shift+F` to toggle filtering on the selected or latest block
* Selecting `Toggle Block Filter` in the block context menu
* Linux
You can also toggle a filter on/off by:
* Using the keybinding `Alt+Shift+F` to toggle filtering on the selected or latest block
* Selecting `Toggle Block Filter` in the block context menu
Note
Toggling a filter on a block without a filter applied will open the filter editor. If you toggle a filter off, the same filter will be applied if you toggle filtering on again.
[](/assets/terminal/block_filtering_toggle.mp4)
# Block Sharing
Canonical page: [/terminal/blocks/block-sharing/](https://docs.warp.dev/terminal/blocks/block-sharing/)
> Share Blocks with your team as permalinks or embeddable HTML snippets.
Note
This action sends command information to our server and is explicitly opt-in. Read more about privacy at Warp on [our privacy page](https://www.warp.dev/privacy).
Share your blocks with a permalink or HTML embed. You can get started with shared blocks by opening the context menu and copying the command, output, or prompt.
## How to share blocks
[Section titled “How to share blocks”](#how-to-share-blocks)
* macOS
To share your blocks, follow these steps:
1. On a finished block, click the context menu and select **Share…** or select the block and hit `⌘+Shift+S`.
2. A modal will pop up that lets you title your block and customize it by selecting which parts of the block you want to share (e.g. command, output, prompt, etc.).
3. Click either “Create link” or “Get embed” depending on how you want to share your block.
4. The link or embed snippet will be copied to your clipboard.
* Windows
To share your blocks, follow these steps:
1. On a finished block, click the context menu and select **Share…**, or set up a key bind for Share Block in **Settings** > **Keyboard shortcuts**.
2. A modal will pop up that lets you title your block and customize it by selecting which parts of the block you want to share (e.g. command, output, prompt, etc.).
3. Click either “Create link” or “Get embed” depending on how you want to share your block.
4. The link or embed snippet will be copied to your clipboard.
* Linux
To share your blocks, follow these steps:
1. On a finished block, click the context menu and select **Share…**, or set up a key bind for Share Block in **Settings** > **Keyboard shortcuts**.
2. A modal will pop up that lets you title your block and customize it by selecting which parts of the block you want to share (e.g. command, output, prompt, etc.).
3. Click either “Create link” or “Get embed” depending on how you want to share your block.
4. The link or embed snippet will be copied to your clipboard.
Note
If you experience any issues with block sharing, see our known issues for [troubleshooting steps](/support-and-community/troubleshooting-and-support/known-issues/#online-features-dont-work).
[](/assets/terminal/block-sharing-embed.mp4)
## Permalink
[Section titled “Permalink”](#permalink)
Create and share a permalink to your blocks to collaborate with teammates. Here is the [web permalink](https://app.warp.dev/block/vzFATak939iqGWfNh7wsAP) of the block depicted below.
## Embedded blocks
[Section titled “Embedded blocks”](#embedded-blocks)
Create and embed your blocks on web pages to help your readers follow along with technical writing. Readers can interact with an embedded block as they would with a block in Warp, with a context menu and styling. When you click “Get embed”, Warp will copy an `iframe` to your clipboard. Here’s an example `iframe`:
```html
<iframe src="https://app.warp.dev/block/embed/qn0g1CqQnkYjEafPH5HCVT"
title="server script error" style="width: 712px; height: 397px; border:0;
overflow:hidden;" allow="clipboard-read; clipboard-write"></iframe>
```
#### Embedded block example on web page
[Section titled “Embedded block example on web page”](#embedded-block-example-on-web-page)
## Managing shared blocks
[Section titled “Managing shared blocks”](#managing-shared-blocks)
You can unshare a block by navigating to **Settings** > **Shared blocks**. Currently, shared blocks are accessible to anyone with the link.
## Link previews
[Section titled “Link previews”](#link-previews)
Shared permalinks will also display a preview of your code for quick context on each link.
Note
Compatible with any platform that supports Open Graph or Twitter meta tags. For example, Slack, Twitter, Facebook, Telegram, Notion, and more.
[Share and Unfurl a Block Preview](https://www.loom.com/embed/a78147fee8804c00b08a1decbc0d4e72)
# Terminal Block Find
Canonical page: [/terminal/blocks/find/](https://docs.warp.dev/terminal/blocks/find/)
> Search across Blocks from the bottom up, with regex, case-sensitive, and per-Block filtering options.
## What is it
[Section titled “What is it”](#what-is-it)
Find searches for matches in all your Blocks from the bottom up and can even be isolated to a specific Block.
Note
Since command outputs are contained within Blocks, you can still use the input editor when invoking find.
## How to access it
[Section titled “How to access it”](#how-to-access-it)
* macOS
1. Hitting `⌘+F` opens the find view which searches across the terminal (scoped within the current pane).
2. Within the find modal, you can also enable the regex toggle, find on a selected Block, and/or toggle case-sensitive search.
* Windows
1. Hitting `Ctrl+Shift+F` opens the find view which searches across the terminal (scoped within the current pane).
2. Within the find modal, you can also enable the regex toggle, find on a selected Block, and/or toggle case-sensitive search.
* Linux
1. Hitting `Ctrl+Shift+F` opens the find view which searches across the terminal (scoped within the current pane).
2. Within the find modal, you can also enable the regex toggle, find on a selected Block, and/or toggle case-sensitive search.
## How it works
[Section titled “How it works”](#how-it-works)
[](/assets/terminal/find.mp4)
# Sticky Command Header
Canonical page: [/terminal/blocks/sticky-command-header/](https://docs.warp.dev/terminal/blocks/sticky-command-header/)
> Pin the running command at the top of the screen when scrolling through large Block outputs.
Note
For long-running commands that take up the full screen, the sticky header only shows after you start scrolling up. This is to prevent the header from blocking the top part of the output for commands like `git log` that simulate full-screen apps.
## How to access sticky command header
[Section titled “How to access sticky command header”](#how-to-access-sticky-command-header)
* macOS
* Sticky Command Header is enabled by default.
* Toggle Sticky Command Header by going to **Settings** > **Features** > **General** > toggle “Show sticky command header”.
* Toggle by searching for “Sticky Command Header” within the [Command Palette](/terminal/command-palette/) or by pressing `⌘+Ctrl+S`.
* You can also “Toggle Sticky Command Header in Active Pane” with `Ctrl+S`. This won’t disable the feature entirely, only minimize it on the active session.
* Windows
* Sticky Command Header is enabled by default.
* Toggle the Sticky Command Header by going to **Settings** > **Features** > **General** > toggle “Show sticky command header”.
* Toggle by searching for “Sticky Command Header” within the [Command Palette](/terminal/command-palette/) or by setting up a key bind in **Settings** > **Keyboard shortcuts**.
* You can also “Toggle Sticky Command Header in Active Pane” in the Command Palette or by setting up a key bind in **Settings** > **Keyboard shortcuts**. This won’t disable the feature entirely, only minimize it on the active session.
* Linux
* Sticky Command Header is enabled by default.
* Toggle the Sticky Command Header by going to **Settings** > **Features** > **General** > toggle “Show sticky command header”.
* Toggle by searching for “Sticky Command Header” within the [Command Palette](/terminal/command-palette/) or by setting up a key bind in **Settings** > **Keyboard shortcuts**.
* You can also “Toggle Sticky Command Header in Active Pane” in the Command Palette or by setting up a key bind in **Settings** > **Keyboard shortcuts**. This won’t disable the feature entirely, only minimize it on the active session.
## How to use sticky command header
[Section titled “How to use sticky command header”](#how-to-use-sticky-command-header)
* If a Block has a large output ( e.g. `seq 1 1000`), the header of the Block will show on the top of the active Window, Tab, or Pane.
* Click on the Sticky Command Header to quickly jump to the top of the Block.
* While active you can also minimize the Sticky Command Header on the active pane by clicking the UP/DOWN arrow in the middle of the header.
## How sticky command header works
[Section titled “How sticky command header works”](#how-sticky-command-header-works)
[Sticky Command Header Demo](https://www.loom.com/embed/a86967c057e44ab4bee4860ba80538b9)
Toggle active header and Jump to bottom of block demo.
# Command completions overview
Canonical page: [/terminal/command-completions/](https://docs.warp.dev/terminal/command-completions/)
> Warp's main features for command completions and autosuggestions.
1. [Completions](/terminal/command-completions/completions/) will suggest commands, option names, and path parameters for you.
2. [Autosuggestions](/terminal/command-completions/autosuggestions/) will automatically suggest commands as you type based on shell history and possible completions.
## Completions
[Section titled “Completions”](#completions)
[Completions Demo](https://www.loom.com/embed/92594c821ae341f69d5d1c1af56f2c69)
## Autosuggestions
[Section titled “Autosuggestions”](#autosuggestions)
[Autosuggestion Demo](https://www.loom.com/embed/5e87c52ae855486ab88ffb2f89aeaf73)
# Autosuggestions
Canonical page: [/terminal/command-completions/autosuggestions/](https://docs.warp.dev/terminal/command-completions/autosuggestions/)
> Warp will automatically suggest commands as you type based on shell history and possible completions.
## How to access it
[Section titled “How to access it”](#how-to-access-it)
* From the [Command Palette](/terminal/command-palette/), type in “Autosuggestions” to toggle.
Note
**Terminal Tip**
You can change the keybinding for accepting autosuggestions to `Tab`. Configure this in the “Tab key behavior” setting under **Settings** > **Features** > **Terminal Input**. *Note: This will update the keybinding for opening the completions menu to `Ctrl+Space`. You can also enable the “Open completions menu as you type” in **Settings** > **Features** > **Terminal Input** so that the completions menu opens automatically.*
## How to use it
[Section titled “How to use it”](#how-to-use-it)
* macOS
There are several ways to accept autosuggestions, either completely or partially:
* Complete an autosuggestion using the `→` arrow or `Ctrl+F`.
* `Ctrl+E` also completes the autosuggestion when your cursor is at the end of the buffer.
* `Ctrl+→` can be used to partially complete the autosuggestion one component at a time.
* Windows
There are several ways to accept autosuggestions, either completely or partially:
* Complete an autosuggestion using the `→` arrow or `Ctrl+F`.
* `End` jumps to the last character in the Input Editor, then `→` completes the autosuggestion.
* `Ctrl+Shift+→` can be used to partially complete the autosuggestion one component at a time.
* Linux
There are several ways to accept autosuggestions, either completely or partially:
* Complete an autosuggestion using the `→` arrow or `Ctrl+F`.
* `Ctrl+E` jumps to the last character in the Input Editor, then `→` completes the autosuggestion.
* `Ctrl+Shift+→` can be used to partially complete the autosuggestion one component at a time.
## How it works
[Section titled “How it works”](#how-it-works)
[Autosuggestion Demo](https://www.loom.com/embed/5e87c52ae855486ab88ffb2f89aeaf73)
# Tab completions
Canonical page: [/terminal/command-completions/completions/](https://docs.warp.dev/terminal/command-completions/completions/)
> Get fuzzy-matched suggestions for commands, options, and paths by pressing Tab anywhere.
## What is it
[Section titled “What is it”](#what-is-it)
Completions feature fuzzy search capability that provides you with [approximate matches](https://en.wikipedia.org/wiki/Approximate_string_matching) for your queries. If you’re unsure about the exact syntax or spelling, you’ll be provided with suggestions based on your input, even if it’s not an exact match.
## How to access it
[Section titled “How to access it”](#how-to-access-it)
* Type out the beginning of your command, then press `Tab`.
* To search for options and flags, you must type and press `Tab`.
* Forgo `Tab` by enabling “Open completions menu as you type” in **Settings** > **Features** > **Terminal Input**.
## How to use it
[Section titled “How to use it”](#how-to-use-it)
### Completions
[Section titled “Completions”](#completions)
1. Type `git checkout` (note the space) and then press `Tab`
2. A menu will show all of your local branches. You can select one using your mouse or the `UP ↑`/`DOWN ↓` arrow keys
### Completions on aliases
[Section titled “Completions on aliases”](#completions-on-aliases)
* Shell aliases - This is an alias for an entire command. For example, if you have `gc=git checkout` in alias, typing `gc` and hitting `Tab` should give you the same completion options as for `git checkout`.
* Command aliases - This is an alias for a subcommand. For example, this could be setting `git status` to `git st`. With completions support, we could now suggest completions for `git status` even if you typed in `git st`.
Note
**Terminal Tip**\
The “Tab key behavior” setting under **Settings** > **Features** > **Terminal Input** can change the action that `Tab` is bound to. If `Tab` is not bound to open the completions menu, `Ctrl+Space` will be assigned as the default keybinding. *Note: You can also enable the “Open completions menu as you type” in **Settings** > **Features** > **Terminal Input** so that the completions menu opens automatically.*
## How it works
[Section titled “How it works”](#how-it-works)
[Completions Demo](https://www.loom.com/embed/92594c821ae341f69d5d1c1af56f2c69)
### Supported completion specs
[Section titled “Supported completion specs”](#supported-completion-specs)
| Command Name | Level of Support |
| ----------------------- | ---------------- |
| act | Partial |
| adb | Partial |
| afplay | Partial |
| aftman | Partial |
| ag | Partial |
| agrippa | Partial |
| amplify | Partial |
| ansible | Partial |
| ansible-config | Partial |
| ansible-doc | Partial |
| ansible-galaxy | Partial |
| ansible-lint | Partial |
| ansible-playbook | Partial |
| appwrite | Partial |
| arch | Partial |
| asdf | Partial |
| assimp | Partial |
| atlas | Partial |
| autojump | Partial |
| aws | Partial |
| babel | Partial |
| banner | Partial |
| base32 | Partial |
| base64 | Partial |
| basename | Partial |
| basenc | Partial |
| bat | Partial |
| bazel | Partial |
| bc | Partial |
| black | Partial |
| blitz | Partial |
| bosh | Full |
| brew | Full |
| build-storybook | Partial |
| bun | Partial |
| bundle | Partial |
| bw | Partial |
| caffeinate | Partial |
| cargo | Full |
| cat | Partial |
| cd | Partial |
| cdk | Partial |
| checkov | Partial |
| chmod | Partial |
| chown | Partial |
| circleci | Partial |
| clang | Partial |
| clear | Partial |
| clojure | Partial |
| cloudflared | Partial |
| cmake | Partial |
| code | Partial |
| code-insiders | Partial |
| command | Partial |
| composer | Partial |
| conda | Full |
| copilot | Partial |
| cordova | Partial |
| cosign | Partial |
| cot | Partial |
| cp | Partial |
| create-completion-spec | Partial |
| create-next-app | Partial |
| create-nx-workspace | Partial |
| create-react-app | Partial |
| create-react-native-app | Partial |
| create-remix | Partial |
| create-t3-app | Partial |
| create-video | Partial |
| create-web3-frontend | Partial |
| croc | Partial |
| curl | Partial |
| cut | Partial |
| dart | Partial |
| date | Partial |
| dateseq | Partial |
| datree | Partial |
| dbt | Partial |
| dd | Partial |
| defaults | Full |
| degit | Partial |
| deno | Partial |
| deployctl | Partial |
| deta | Partial |
| df | Partial |
| diff | Partial |
| dig | Partial |
| direnv | Partial |
| dirname | Partial |
| django-admin | Partial |
| do | Partial |
| docker | Full |
| docker-compose | Partial |
| doctl | Partial |
| dog | Partial |
| doppler | Partial |
| dotenv | Partial |
| dotnet | Partial |
| dotslash | Partial |
| drush | Partial |
| dtm | Partial |
| du | Partial |
| eb | Partial |
| echo | Partial |
| electron | Partial |
| eleventy | Partial |
| elif | Partial |
| elixir | Partial |
| elm | Partial |
| elm-review | Partial |
| else | Partial |
| emacs | Partial |
| esbuild | Partial |
| eslint | Partial |
| exa | Partial |
| exec | Partial |
| exercism | Partial |
| expo | Partial |
| expo-cli | Partial |
| export | Partial |
| fastlane | Partial |
| fastly | Partial |
| fd | Partial |
| ffmpeg | Partial |
| fig-teams | Partial |
| file | Partial |
| find | Partial |
| firebase | Full |
| fisher | Partial |
| flutter | Full |
| fly | Partial |
| flyctl | Partial |
| fmt | Partial |
| fnm | Partial |
| fold | Partial |
| for | Partial |
| forge | Partial |
| fvm | Partial |
| fzf | Partial |
| fzf-tmux | Partial |
| ganache-cli | Partial |
| gatsby | Partial |
| gcc | Partial |
| gcloud | Partial |
| gh | Full |
| git | Full |
| git-flow | Partial |
| github | Partial |
| gltfjsx | Partial |
| go | Full |
| goctl | Partial |
| googler | Partial |
| goreleaser | Partial |
| gpg | Partial |
| gradle | Partial |
| graphcdn | Partial |
| grep | Partial |
| grex | Partial |
| hardhat | Partial |
| hasura | Partial |
| hb-service | Partial |
| head | Partial |
| helm | Partial |
| heroku | Full |
| hexo | Partial |
| hostname | Partial |
| htop | Partial |
| http | Partial |
| https | Partial |
| httpy | Partial |
| hub | Partial |
| hugo | Partial |
| hx | Partial |
| hyper | Partial |
| id | Partial |
| iex | Partial |
| if | Partial |
| ignite-cli | Partial |
| install | Partial |
| ionic | Partial |
| j | Partial |
| java | Partial |
| jest | Partial |
| join | Partial |
| jq | Partial |
| julia | Partial |
| jupyter | Partial |
| just | Partial |
| keytool | Partial |
| kill | Partial |
| killall | Full |
| kitty | Partial |
| knex | Partial |
| kool | Partial |
| kubecolor | Partial |
| kubectl | Full |
| kubectx | Full |
| kubens | Full |
| laravel | Partial |
| lerna | Partial |
| less | Partial |
| lima | Partial |
| limactl | Partial |
| ln | Partial |
| lp | Partial |
| lpass | Partial |
| ls | Partial |
| lsd | Partial |
| mackup | Partial |
| make | Full |
| man | Full |
| mas | Partial |
| mask | Partial |
| mdfind | Partial |
| meteor | Partial |
| micro | Partial |
| mikro-orm | Partial |
| minikube | Partial |
| mix | Partial |
| mkdir | Partial |
| mkfifo | Partial |
| mknod | Partial |
| mob | Partial |
| molecule | Partial |
| mongocli | Partial |
| mongosh | Partial |
| more | Partial |
| mosh | Partial |
| mv | Partial |
| mvn | Partial |
| mysql | Partial |
| n | Partial |
| nano | Partial |
| nativescript | Partial |
| nc | Partial |
| nest | Partial |
| netlify | Partial |
| networkQuality | Partial |
| newman | Partial |
| next | Partial |
| ng | Full |
| nginx | Partial |
| ngrok | Partial |
| nhost | Partial |
| ni | Partial |
| nl | Partial |
| nocorrect | Partial |
| node | Full |
| noglob | Partial |
| npm | Full |
| npx | Partial |
| nr | Partial |
| nrm | Partial |
| ns | Partial |
| nu | Partial |
| nuxi | Partial |
| nuxt | Partial |
| nvim | Partial |
| nvm | Partial |
| nx | Full |
| nylas | Partial |
| od | Partial |
| oh-my-posh | Partial |
| okta | Partial |
| okteto | Partial |
| omz | Partial |
| onboardbase | Partial |
| op | Partial |
| opa | Partial |
| open | Partial |
| osascript | Partial |
| pageres | Partial |
| pandoc | Partial |
| pass | Partial |
| paste | Partial |
| pathchk | Partial |
| pdfunite | Partial |
| pgcli | Partial |
| php | Partial |
| phpunit-watcher | Full |
| ping | Partial |
| pip | Full |
| pip3 | Partial |
| pipenv | Partial |
| pm2 | Partial |
| pmset | Partial |
| pnpm | Partial |
| pnpx | Partial |
| pod | Partial |
| poetry | Partial |
| pre-commit | Partial |
| preset | Partial |
| prettier | Partial |
| prisma | Partial |
| projj | Partial |
| ps | Partial |
| pscale | Partial |
| psql | Partial |
| publish | Partial |
| pulumi | Partial |
| pushd | Partial |
| pwd | Partial |
| pyenv | Full |
| python | Partial |
| python3 | Partial |
| qodana | Partial |
| quickmail | Partial |
| r | Partial |
| rails | Partial |
| railway | Partial |
| rake | Partial |
| rancher | Partial |
| rbenv | Partial |
| rclone | Partial |
| react-native | Full |
| readlink | Partial |
| redwood | Partial |
| remix | Partial |
| remotion | Partial |
| repeat | Partial |
| rg | Partial |
| rm | Partial |
| rmdir | Partial |
| robot | Partial |
| rollup | Partial |
| rscript | Partial |
| rsync | Partial |
| ruby | Partial |
| rush | Partial |
| rushx | Partial |
| rustc | Partial |
| rustup | Partial |
| sam | Partial |
| scc | Partial |
| scp | Partial |
| screen | Partial |
| sed | Partial |
| sequelize | Partial |
| serve | Partial |
| serverless | Partial |
| sfdx | Partial |
| sftp | Partial |
| shopify | Partial |
| shortcuts | Partial |
| shred | Partial |
| sips | Partial |
| softwareupdate | Partial |
| source | Partial |
| splash | Partial |
| split | Partial |
| spotify | Partial |
| sqlite3 | Partial |
| src | Partial |
| ssh | Full |
| st2 | Partial |
| start-storybook | Partial |
| stat | Partial |
| steadybit | Partial |
| stepzen | Partial |
| stripe | Partial |
| su | Partial |
| subl | Partial |
| sudo | Partial |
| swc | Partial |
| swift | Partial |
| sysctl | Partial |
| tac | Partial |
| tail | Partial |
| tailscale | Partial |
| tailwindcss | Partial |
| tangram | Partial |
| tar | Full |
| task | Partial |
| tccutil | Partial |
| tee | Partial |
| terraform | Full |
| terragrunt | Partial |
| tfenv | Partial |
| tfsec | Partial |
| then | Partial |
| time | Partial |
| tldr | Partial |
| tmux | Full |
| tmuxinator | Full |
| tns | Partial |
| tokei | Partial |
| top | Partial |
| touch | Partial |
| tr | Partial |
| traceroute | Partial |
| trash | Partial |
| trex | Partial |
| trivy | Partial |
| truffle | Partial |
| truncate | Partial |
| trunk | Partial |
| ts-node | Partial |
| tsc | Partial |
| tsh | Partial |
| turbo | Partial |
| twiggy | Partial |
| twilio | Partial |
| typeorm | Partial |
| uname | Partial |
| uniq | Partial |
| until | Partial |
| until | Partial |
| unzip | Partial |
| vale | Partial |
| valet | Partial |
| vapor | Partial |
| vault | Partial |
| vela | Partial |
| vercel | Partial |
| vi | Partial |
| vim | Partial |
| vimr | Partial |
| vite | Partial |
| vite | Partial |
| volta | Partial |
| vr | Partial |
| vsce | Partial |
| vtex | Partial |
| vue | Partial |
| vue | Partial |
| vultr-cli | Partial |
| w | Partial |
| w | Partial |
| wasm-bindgen | Partial |
| wasm-pack | Partial |
| watson | Partial |
| wc | Partial |
| wc | Partial |
| wd | Partial |
| webpack | Partial |
| wget | Partial |
| whence | Partial |
| where | Partial |
| which | Partial |
| while | Partial |
| who | Partial |
| whois | Partial |
| wifi-password | Partial |
| wifi-password | Partial |
| wp | Partial |
| wrangler | Partial |
| wrk | Partial |
| wscat | Partial |
| xargs | Partial |
| xcode-select | Partial |
| xcodebuild | Partial |
| xcodeproj | Partial |
| xcrun | Partial |
| xed | Partial |
| yank | Partial |
| yarn | Partial |
| yo | Partial |
| youtube-dl | Partial |
| z | Partial |
| z | Partial |
| zapier | Partial |
| zapier | Partial |
| zip | Partial |
| zoxide | Partial |
# Command Palette
Canonical page: [/terminal/command-palette/](https://docs.warp.dev/terminal/command-palette/)
> Command Palette is a global search to quickly locate Workflows, Notebooks, keyboard shortcuts, or other actions within Warp.
The Command Palette is Warp’s global search interface for quickly finding and launching Workflows, Notebooks, Prompts, keyboard shortcuts, file searches, settings, and other actions. Open it with a keyboard shortcut, then type or filter results by type to find exactly what you need.
The Command Palette panel.
## How to access it
[Section titled “How to access it”](#how-to-access-it)
* macOS
You can access the Command Palette with the keyboard shortcut `⌘+P`.
* Windows
You can access the Command Palette with the keyboard shortcut `Ctrl+Shift+P`.
* Linux
You can access the Command Palette with the keyboard shortcut `Ctrl+Shift+P`.
## How it works
[Section titled “How it works”](#how-it-works)
* Start typing to search for Workflows, Notebooks, keyboard shortcuts, actions, toggles, etc.
* Activate a specific filter, by clicking on the filter buttons or prepending your search with the following:
* `workflows:` or `w:` will filter for [Workflows](/knowledge-and-collaboration/warp-drive/workflows/).
* `prompts:` or `p:` will filter for [Prompts](/knowledge-and-collaboration/warp-drive/prompts/).
* `notebook:` or `n:` will filter for [Notebooks](/knowledge-and-collaboration/warp-drive/notebooks/).
* `env_vars:` will filter for [Environment Variables](/knowledge-and-collaboration/warp-drive/environment-variables/).
* `files:` will filter for local files.
* `drive:` will filter for [Warp Drive](/knowledge-and-collaboration/warp-drive/).
* `actions:` will filter for Warp-specific actions like settings and features.
* `sessions:` will filter for active sessions with [Session Navigation](/terminal/sessions/session-navigation/).
* `launch_configs:` will filter for [Launch Configurations](/terminal/sessions/launch-configurations/).
[Command Palette Demo](https://www.loom.com/embed/0e6108b295234637a0bb20cc941976e9)
# Terminal comparisons overview
Canonical page: [/terminal/comparisons/](https://docs.warp.dev/terminal/comparisons/)
> Compare Warp's performance and terminal feature support against other popular terminal emulators like iTerm2, Alacritty, and WezTerm.
Warp is a modern terminal built in Rust with GPU rendering, agent support, and a code-editor-style input. Use this section to see how Warp stacks up against other popular terminals on raw performance and feature coverage.
## How Warp differs
[Section titled “How Warp differs”](#how-warp-differs)
* **Open source under AGPL v3** — Warp’s client lives at [`warpdotdev/warp`](https://github.com/warpdotdev/warp). You can read the code, build from source, and contribute. See [Contributing to Warp](/support-and-community/community/contributing/) for the flow.
* **Built-in agents** — Warp ships with the Warp Agent (powered by the Automation Platform) and supports third-party CLI agents like Claude Code, Codex, and Gemini CLI from the same terminal.
* **Modern editing** — Cursor placement, multi-line input, block-based output, and integrated code review work like a text editor instead of a traditional terminal emulator.
* **Cross-platform Rust core** — Warp ships on macOS, Linux, and Windows from a single Rust + GPU-rendered codebase.
## Benchmarks
[Section titled “Benchmarks”](#benchmarks)
* [Performance benchmarks](/terminal/comparisons/performance/) — VTE and Termbench results comparing Warp against Terminal.app, iTerm2, Alacritty, and WezTerm.
# Performance benchmarks
Canonical page: [/terminal/comparisons/performance/](https://docs.warp.dev/terminal/comparisons/performance/)
> This is a short comparison of different terminals and their performance.
## Terminal apps selected for these benchmarks
[Section titled “Terminal apps selected for these benchmarks”](#terminal-apps-selected-for-these-benchmarks)
We chose to benchmark Warp against 4 other terminal emulator applications, based on their popularity as well as language and principles. Here is the list of the applications we chose for this comparison together with the explanation as to why we decided to include it in our comparison:
* Terminal.app - the default terminal app available on macOS;
* iTerm2 - one of the most popular terminal emulators used by macOS users;
* Alacritty & WezTerm - both of those terminals are written in Rust and are well-known for their speed and overall performance, things that Warp is aiming for.
### Versions & settings used during the comparison
[Section titled “Versions & settings used during the comparison”](#versions--settings-used-during-the-comparison)
| Terminal | Version | Terminal size (cols / rows, window is identical pixel-wise) |
| ------------ | ------------------------------ | ----------------------------------------------------------- |
| Warp | v0.2022.04.01.01.37.stable\_03 | 208 cols / 54 rows |
| Terminal.app | Version 2.11 (440) | 188 cols / 72 rows |
| iTerm2 | Build 3.4.15 | 211 cols / 78 rows |
| Alacritty | alacritty 0.10.1 (2844606) | 286 cols / 102 rows |
| WezTerm | 20220319-142410-0fcdea07 | 243 cols / 80 rows |
### About benchmarks
[Section titled “About benchmarks”](#about-benchmarks)
We link the source code of each benchmark used, so you can easily reproduce the tests with other terminal apps. Note that these benchmarks are not exhaustive. Comparing terminal emulators with each other is not an easy task - right now we’re checking how each of the apps behaves when dealing with lots of input and/or output.
Ideally, the benchmarks would also cover the latency (time between pressing a key and the character showing on the screen, but also a delay between the user’s input and communication with the shell). We may include tests that account for that in the future.
## VTE benchmark
[Section titled “VTE benchmark”](#vte-benchmark)
Benchmark code is available in the [Alacritty VTE benchmark repository](https://github.com/alacritty/vtebench) at the specific commit we used in our comparison: `93bcc32b6e0f7560e9b1a5a8b0998c04fbf9b50d`. Results in milliseconds.
### Average time for each of the benchmark tests
[Section titled “Average time for each of the benchmark tests”](#average-time-for-each-of-the-benchmark-tests)
| | Warp avg (ms) | Terminal.app avg (ms) | iTerm avg | Alacritty avg | WezTerm avg |
| -------------------------------- | ------------- | --------------------- | --------- | ------------- | ----------- |
| dense\_cells | 43.88 | 24.91 | 144.84 | 7.25 | 28.15 |
| scrolling | 30.06 | 283.34 | 1257.57 | 31.75 | 687.77 |
| scrolling\_bottom\_region | 117.34 | 257.23 | 1294.25 | 29.1 | 672.67 |
| scrolling\_bottom\_small\_region | 114.52 | 227.75 | 1251 | 25.98 | 669.93 |
| scrolling\_fullscreen | 37.4 | 307.03 | 1565.17 | 37.36 | 1205 |
| scrolling\_top\_region | 120.63 | 209.29 | 2212.2 | 84.42 | 682.6 |
| scrolling\_top\_small\_region | 114.64 | 205.59 | 1216.33 | 21.91 | 663.44 |
| unicode | 66.47 | 34.45 | 93.01 | 16.78 | 1279.25 |
### P90 of the results
[Section titled “P90 of the results”](#p90-of-the-results)
| | Warp p90 | Terminal.app p90 | iTerm p90 | Alacritty p90 | WezTerm p90 |
| -------------------------------- | -------- | ---------------- | --------- | ------------- | ----------- |
| dense\_cells | 52 | 28 | 189 | 8 | 32 |
| scrolling | 32 | 266.76 | 1336 | 32 | 707 |
| scrolling\_bottom\_region | 170 | 243 | 1398 | 30 | 686 |
| scrolling\_bottom\_small\_region | 167 | 224 | 1331 | 30 | 679 |
| scrolling\_fullscreen | 38 | 327 | 1593 | 41 | 1208 |
| scrolling\_top\_region | 178 | 222 | 2243 | 85 | 686 |
| scrolling\_top\_small\_region | 167 | 222 | 1314 | 30 | 666 |
| unicode | 77 | 39 | 90 | 20 | 3883 |
## Termbench
[Section titled “Termbench”](#termbench)
Benchmark code is available in the [Termbench repository](https://github.com/cmuratori/termbench) at the specific commit we used in our comparison: `82afbc69256b4e22de913f0f02f82e0480f3dac5`.
Below you’ll find results for small and regular test sizes. Note that Terminal.app only participated in the small test. Results in seconds.
### Small test sizes
[Section titled “Small test sizes”](#small-test-sizes)
| | Warp small (s) | Terminal.app small (s) | iTerm small (s) | Alacritty small | WezTerm small |
| -------------- | -------------- | ---------------------- | --------------- | --------------- | ------------- |
| ManyLine | 6.7854 | 2.6789 | 8.7057 | 1.2532 | 8.9436 |
| LongLine | 9.0033 | 1.6473 | 9.0849 | 0.8179 | 11.4587 |
| FGPerChar | 1.3716 | 453.9888 | 2.6625 | 0.2788 | 0.6487 |
| FGBGPerChar | 2.8403 | 908.894 | 4.5881 | 0.5931 | 0.7283 |
| overall result | 20.0006 | 1367.209 | 25.0413 | 2.943 | 21.7793 |
### Regular test size
[Section titled “Regular test size”](#regular-test-size)
| | Warp regular (s) | iTerm regular (s) | Alacritty regular (s) | WezTerm regular |
| -------------- | ---------------- | ----------------- | --------------------- | --------------- |
| ManyLine | 113.76 | 132.4975 | 19.8802 | 150.8175 |
| LongLine | 155.0937 | 126.7561 | 12.7859 | 207.3647 |
| FGPerChar | 21.8928 | 39.3352 | 4.2925 | 9.4265 |
| FGBGPerChar | 46.312 | 50.5369 | 8.418 | 13.5142 |
| overall result | 337.0585 | 349.1258 | 45.3767 | 381.1229 |
# Terminal features
Canonical page: [/terminal/comparisons/terminal-features/](https://docs.warp.dev/terminal/comparisons/terminal-features/)
> Below you'll find a table showcasing different terminal features (such as text attribution) and information about which one of those are supported in Warp.
To make it more transparent & useful, we also show the results for 4 other popular macOS terminal emulators.
| Feature | Warp | Terminal.app | iTerm | Alacritty | WezTerm |
| --------------------------------------------------------- | ---- | ------------ | ----- | --------- | ------- |
| 24-bit (true color) | YES | NO | YES | YES | YES |
| Bold | YES | YES | YES | YES | YES |
| Dim | NO | YES | YES | YES | YES |
| Italic | NO | YES | YES | YES | YES |
| Underline | YES | YES | YES | YES | YES |
| Underline (alt) | YES | NO | YES | YES | YES |
| Double underline | NO | NO | NO | NO | YES |
| Double underline (alt) | YES | NO | YES | YES | YES |
| Curly underline | NO | NO | YES | NO | YES |
| Colored underline | NO | NO | NO | NO | YES |
| Blink | NO | YES | NO | NO | NO |
| Reverse | YES | YES | YES | YES | YES |
| Invisible (but copy-paste-able) | NO | YES | NO | YES | NO |
| Strikethrough | YES | NO | YES | YES | YES |
| Overline | NO | NO | NO | NO | YES |
| [Magic string](https://en.wikipedia.org/wiki/Unicode#Web) | YES | YES | YES | YES | YES |
| Emojis | YES | YES | YES | YES | YES |
| Right-to-left | NO | YES | NO | NO | NO |
| Sixel graphics | NO | NO | YES | NO | NO |
Based on the [terminal-testdrive.sh](https://gist.github.com/hellricer/e514d9615d02838244d8de74d0ab18b3).
# Modern text editing overview
Canonical page: [/terminal/editor/](https://docs.warp.dev/terminal/editor/)
> Unlike other terminals, Warp’s input editor operates out of the box like a modern IDE and the text editors we’re used to.
Warp’s input editor works like a modern IDE text editor, with cursor movement, click-to-place, multi-line editing, copy-paste, word selection, and soft wrapping built in. Unlike traditional terminals, you can edit commands the same way you edit code — no memorizing shell-specific shortcuts required.
Note
Text Editor Input also works for [SSH sessions](/terminal/warpify/ssh/).
### Soft wrapping
[Section titled “Soft wrapping”](#soft-wrapping)
Warp supports soft wrapping in the input editor. If an autosuggestion goes off-screen, the input editor will be horizontally scrollable to make it visible. Some operations treat soft-wrapped lines like a logical line (`TRIPLE-CLICK`) while other operations treat soft wrapped lines like visible different lines (`↑`/`↓`, `Shift+↑`/`Shift+↓`).
### Copy on select
[Section titled “Copy on select”](#copy-on-select)
Warp supports copy on select for selectable text within [Blocks](/terminal/blocks/).
* Toggle this feature in **Settings** > **Features** > **Terminal** or search for “Copy on select” in the [Command Palette](/terminal/command-palette/).
### Autocomplete quotes, parentheses, and brackets
[Section titled “Autocomplete quotes, parentheses, and brackets”](#autocomplete-quotes-parentheses-and-brackets)
Warp can automatically complete quotes, brackets, and parentheses like you’re used to in IDEs.
* Toggle this feature in **Settings** > **Features** > **Text Editing** or search for “Autocomplete quotes” in the [Command Palette](/terminal/command-palette/).
## How to use it
[Section titled “How to use it”](#how-to-use-it)
* macOS
| Keyboard binding | Shortcut description |
| ----------------------------------------- | ---------------------------------------------------------------------------- |
| `Escape` | Closes the input suggestions or history menu |
| `Ctrl+L` | Clears the terminal |
| `Ctrl+H` | Backspace |
| `Ctrl+C` | Clear the entire editor buffer |
| `Ctrl+U` | Copy and Clear the current line |
| `⌘+Shift+K` | Clear selected lines |
| `⌘+C`, `⌘+X`, `⌘+V` | Copy, cut, paste |
| `Ctrl+W` / `Option+D` | Cut the word to the left / right of the cursor |
| `Option+Backspace` / `Option+Delete` | Delete the word to the left / right of the cursor |
| `Ctrl+K` | Cut everything to the right of the cursor (copies it to the clipboard) |
| `⌘+Delete` | Delete everything to the right of the cursor (does not affect the clipboard) |
| `Option+←` / `Option+→` | Move to the beginning of the previous / next word |
| `Ctrl+Option+←` / `Ctrl+Option+→` | Move backward / forward by one subword |
| `⌘+←` / `Ctrl+A` / `Ctrl+E` / `⌘+→` | Move the cursor to the start / end of the line |
| `Shift+←` / `Shift+→` | Select the character to the left / right of the cursor |
| `Option+Shift+←` / `Option+Shift+→` | Select the word to the left / right of the cursor |
| `⌘+Shift+←` / `⌘+Shift+→` | Select to the start / end of the line |
| `Shift+↑` / `Shift+↓` | Select everything above / below the cursor |
| `⌘+A` | Select the entire editor buffer |
| `Shift+Enter` `Ctrl+Enter` `Option+Enter` | Insert newline |
| `Ctrl+R` | Command Search |
| `⌘+D` | Split pane |
* Windows
| Keyboard binding | Shortcut description |
| -------------------------------------- | ---------------------------------------------------------------------- |
| `Escape` | Closes the input suggestions or history menu |
| `Ctrl+L` | Clears the terminal |
| `Ctrl+H` | Backspace |
| `Ctrl+C` | Clear the entire editor buffer |
| `Ctrl+U` | Copy and Clear the current line |
| `Ctrl+C`, `Ctrl+X`, `Ctrl+V` | Copy, cut, paste |
| `Ctrl+W` / `Alt+D` | Cut the word to the left / right of the cursor |
| `Ctrl+Backspace` / `Ctrl+Delete` | Delete the word to the left / right of the cursor |
| `Ctrl+K` | Cut everything to the right of the cursor (copies it to the clipboard) |
| `Ctrl+←` / `Ctrl+→` | Move to the beginning of the previous / next word |
| `Home` / `End` | Move the cursor to the start / end of the line |
| `Shift+←` / `Shift+→` | Select the character to the left / right of the cursor |
| `Meta+Shift+B` / `Meta+Shift+F` | Select the word to the left / right of the cursor |
| `Shift+Home` / `Shift+End` | Select to the start / end of the line |
| `Shift+↑` / `Shift+↓` | Select everything above / below the cursor |
| `Ctrl+A` | Select the entire editor buffer |
| `Shift+Enter` `Ctrl+Enter` `Alt+Enter` | Insert newline |
| `Ctrl+R` | Command Search |
| `Ctrl+Shift+D` | Split pane |
* Linux
| Keyboard binding | Shortcut description |
| -------------------------------------- | ---------------------------------------------------------------------- |
| `Escape` | Closes the input suggestions or history menu |
| `Ctrl+L` | Clears the terminal |
| `Ctrl+H` | Backspace |
| `Ctrl+C` | Clear the entire editor buffer |
| `Ctrl+U` | Copy and Clear the current line |
| `Ctrl+C`, `Ctrl+X`, `Ctrl+V` | Copy, cut, paste |
| `Ctrl+W` / `Alt+D` | Cut the word to the left / right of the cursor |
| `Ctrl+Backspace` / `Ctrl+Delete` | Delete the word to the left / right of the cursor |
| `Ctrl+K` | Cut everything to the right of the cursor (copies it to the clipboard) |
| `Ctrl+←` / `Ctrl+→` | Move to the beginning of the previous / next word |
| `Home` / `End` | Move the cursor to the start / end of the line |
| `Shift+←` / `Shift+→` | Select the character to the left / right of the cursor |
| `Meta+Shift+B` / `Meta+Shift+F` | Select the word to the left / right of the cursor |
| `Shift+Home` / `Shift+End` | Select to the start / end of the line |
| `Shift+↑` / `Shift+↓` | Select everything above / below the cursor |
| `Ctrl+A` | Select the entire editor buffer |
| `Shift+Enter` `Ctrl+Enter` `Alt+Enter` | Insert newline |
| `Ctrl+R` | Command Search |
| `Ctrl+Shift+D` | Split pane |
## How it works
[Section titled “How it works”](#how-it-works)
[Text Editor Input Demo](https://www.loom.com/embed/1517049fefc34227bf1abaf19cc7e6ea)
Soft wrapping applied to long lines in the editor.
# Alias Expansion
Canonical page: [/terminal/editor/alias-expansion/](https://docs.warp.dev/terminal/editor/alias-expansion/)
> Warp will automatically expand your aliases as you type in the input editor.
## How to use it
[Section titled “How to use it”](#how-to-use-it)
* macOS
When alias expansion is enabled, type an alias and then hit `Space` to expand the alias.
To insert a space without expanding an alias, the default keybinding is `Option+Space`.
* Windows
When alias expansion is enabled, type an alias and then hit `Space` to expand the alias.
To insert a space without expanding an alias, the default keybinding is `Alt+Space`.
* Linux
When alias expansion is enabled, type an alias and then hit `Space` to expand the alias.
To insert a space without expanding an alias, the default keybinding is `Alt+Space`.
Note
Aliases will not be expanded when the command in the expanded form is the same as the alias itself. e.g. if you have an alias `ls='ls -G'`, `ls` will not be expanded in the input editor.
## How to access it
[Section titled “How to access it”](#how-to-access-it)
Alias expansion is disabled by default. There are two ways to toggle this on and off:
* From Settings: Navigate to **Settings** > **Features** > **Terminal Input** and toggle “Expand aliases as you type”.
* From the [Command Palette](/terminal/command-palette/#how-to-access-it): Search for the “Enable/disable alias expansion” option and hit `Enter`.
## How it works
[Section titled “How it works”](#how-it-works)
[Alias Expansion Demo](https://www.loom.com/embed/2267657c033e482890eea75a8a6c5373)
# Command Inspector
Canonical page: [/terminal/editor/command-inspector/](https://docs.warp.dev/terminal/editor/command-inspector/)
> Command Inspector (also known as Command X-Ray) surfaces documentation for sub-parts of your command, directly in Warp's Input Editor.
## How to access it
[Section titled “How to access it”](#how-to-access-it)
* macOS
Hover over the part of the command you want to inspect with your mouse or press `⌘+Shift+I` to inspect the cursor’s current location.
* Windows
Hover over the part of the command you want to inspect with your mouse or press `Ctrl+Shift+I` to inspect the cursor’s current location.
* Linux
Hover over the part of the command you want to inspect with your mouse or press `Ctrl+Shift+I` to inspect the cursor’s current location.
## How it works
[Section titled “How it works”](#how-it-works)
[Command Inspector Demo](https://www.loom.com/embed/a00259927ada41b2895fd5c4072a3dcc)
# Syntax & Error Highlighting
Canonical page: [/terminal/editor/syntax-error-highlighting/](https://docs.warp.dev/terminal/editor/syntax-error-highlighting/)
> Color-code commands and underline errors in real time as you type in Warp's input editor.
## What is syntax highlighting
[Section titled “What is syntax highlighting”](#what-is-syntax-highlighting)
Warp supports syntax highlighting in the [Input Editor](/terminal/editor/). It colors each part of a command to help differentiate between sub-commands, options/flags, arguments, and variables.
Caution
Newly installed apps or newly created aliases will not trigger syntax highlighting until you open a new Warp session (new window, tab, or pane), even if you `source` the RC files in the current session.
### How to access syntax highlighting
[Section titled “How to access syntax highlighting”](#how-to-access-syntax-highlighting)
When syntax highlighting is enabled, Warp’s [Input Editor](/terminal/editor/) automatically recognizes each part of the command as you type it into the Input Editor, and syntactically highlights them.
### How to enable/disable syntax highlighting
[Section titled “How to enable/disable syntax highlighting”](#how-to-enabledisable-syntax-highlighting)
Syntax highlighting is enabled by default, to toggle it:
* Through the [Command Palette](/terminal/command-palette/), search for the “Syntax Highlighting” option and click it (or press enter) to enable/disable.
* Through **Settings** > **Features** > **Terminal Input**, toggle “Syntax highlighting for commands”.
### How syntax highlighting works
[Section titled “How syntax highlighting works”](#how-syntax-highlighting-works)
[Syntax Highlighting Demo](https://www.loom.com/embed/87b15de13ee9407b98a24f1a31835784)
## What is error underlining
[Section titled “What is error underlining”](#what-is-error-underlining)
Warp highlights errors in commands that are typed within the [Input Editor](/terminal/editor/) e.g. if the binary for the command you’ve typed does not exist.
Caution
Newly installed apps or newly created aliases will trigger error underlining until you open a new Warp session (new window, tab, or pane), even if you `source` the RC files in the current session.
### How to access error underlining
[Section titled “How to access error underlining”](#how-to-access-error-underlining)
When error underlining is enabled, Warp automatically underlines any invalid commands with a dashed red underline.
### How to enable/disable error underlining
[Section titled “How to enable/disable error underlining”](#how-to-enabledisable-error-underlining)
Error underlining is enabled by default, to toggle it:
* Through the [Command Palette](/terminal/command-palette/), search for the “Syntax Highlighting” option and click it (or press enter) to enable/disable.
* Through **Settings** > **Features** > **Terminal Input**, toggle “Error underlining for commands”.
### How error underlining works
[Section titled “How error underlining works”](#how-error-underlining-works)
[Error Underlining Demo](https://www.loom.com/embed/7721e06ed4aa4e1380abae4f5827ef6f)
# Input editor Vim keybindings
Canonical page: [/terminal/editor/vim/](https://docs.warp.dev/terminal/editor/vim/)
> Use input editor Vim keybindings (also known as Vim mode) to edit commands quickly in Warp.
## About Vim keybindings
[Section titled “About Vim keybindings”](#about-vim-keybindings)
The Vi family of programs (including Vim and Neovim) are modal text editors that allow for keyboard-driven text editing. Several shells, including `bash` and `zsh`, implement vi-style keybindings. Warp’s input editor was built natively to support more modern text editing experiences, which means it replaces the shell’s editor capabilities. Warp has its own implementation of Vim keybindings (also known as Vim mode) you can use.
### How to enable Vim keybindings
[Section titled “How to enable Vim keybindings”](#how-to-enable-vim-keybindings)
Note
With `bash` and `zsh`, Warp attempts to detect the shell’s keybinding settings. If a shell vi mode is detected, Warp may suggest enabling Vim keybindings (also known as Vim mode).
To manually toggle Vim keybindings in Warp’s input editor:
* Through the [Command Palette](/terminal/command-palette/), search for “vim keybindings” to find “Enable editing commands with Vim keybindings” (or “Disable editing commands with Vim keybindings” if already enabled).
* Through **Settings** > **Features** > **Text Editing**, toggle “Edit code and commands with Vim keybindings”.
As in `bash` and `zsh`’s vi mode implementations, the editor starts in insert mode. Pressing `Ctrl+C` or `Enter` clears any pending command state.
### Customizing keybindings
[Section titled “Customizing keybindings”](#customizing-keybindings)
At the moment, Warp only supports default Vim keybindings.
One exception is the keyboard shortcut for exiting insert mode, which can be rebound under **Settings** > **Keyboard shortcuts** > **Exit Vim insert mode**, or through the [Command Palette](/terminal/command-palette/) search for “Exit Vim insert mode”.
## Supported keybindings
[Section titled “Supported keybindings”](#supported-keybindings)
Below is a list of the vim functionality implemented in Warp so far.
### Movement
[Section titled “Movement”](#movement)
See [Vim docs: motion](https://vimdoc.sourceforge.net/htmldoc/motion.html) for more information.
#### Basic
[Section titled “Basic”](#basic)
| Command(s) | Description |
| ---------------------------- | --------------------------------------------------- |
| `h`, `j`, `k`, `l` | single-char movement |
| `<space>`, `<backspace>` | single-char movement with line wrap |
| `w`, `W`, `b`, `B`, `e`, `E` | word movement |
| `ge`, `gE` | end of previous word |
| `$` | end of line |
| `0` | beginning of line |
| `^` | first non-whitespace character of line |
| `%` | jump to matching bracket |
| `[`, `]` | prev/next unmatched bracket |
| `_` | beginning of the current line |
| `+` | first non-whitespace character of the next line |
| `-` | first non-whitespace character of the previous line |
#### Multi-line-related
[Section titled “Multi-line-related”](#multi-line-related)
| Command(s) | Description |
| ---------- | ----------------------- |
| `gg`, `G` | jump to first/last line |
### Editing
[Section titled “Editing”](#editing)
| Command(s) | Description |
| ---------- | ----------------------------------------------------------- |
| `r` | replace character under cursor |
| `d`, `D` | delete a range or object |
| `c`, `C` | change a range or object (delete, then go to insert mode) |
| `s`, `S` | substitute (like change, but can only delete at the cursor) |
| `x`, `X` | delete under cursor |
| `y`, `Y` | yank (copy) into the clipboard |
| `p`, `P` | paste from the clipboard |
| `u`, `⌃r` | undo, redo |
| `~` | toggle upper/lowercase under cursor |
| `gu` | lowercase under cursor (`u` in visual mode) |
| `gU` | uppercase under cursor (`U` in visual mode) |
| `J` | join current and following lines |
| `.` | repeat last edit |
See [Vim docs: editing](https://vimdoc.sourceforge.net/htmldoc/editing.html) for more information.
#### Text objects
[Section titled “Text objects”](#text-objects)
| Command(s) | Description |
| ---------------- | ----------------------------------------------------------------------------- |
| `i` | inner (exclude delimiters in text object) |
| `a` | around (include delimiters in text object) |
| `w`, `W` | whitespace-delimited string (word) |
| `"`, `'`, \`\`\` | quote-delimited string |
| `(`, `{`, `[` | parenthesized/bracketed string |
| `l` | current line without leading/trailing whitespace (`il`); entire buffer (`al`) |
See [Vim docs: text objects](https://vimdoc.sourceforge.net/htmldoc/motion.html#text-objects) for more information.
### Search
[Section titled “Search”](#search)
#### Character search
[Section titled “Character search”](#character-search)
| Command(s) | Description |
| ------------------ | ------------------------------------------------------ |
| `t`, `T`, `f`, `F` | find next/prev matching character on line |
| `;` | repeat last character search in the same direction |
| `,` | repeat last character search in the opposite direction |
See [Vim docs: left-right motions](https://vimdoc.sourceforge.net/htmldoc/motion.html#f) for more information.
#### General search
[Section titled “General search”](#general-search)
Unlike Vim, general search commands don’t search within the buffer. Instead, they open Warp’s native command search.
| Command(s) | Description |
| ------------------ | ------------------------ |
| `/`, `?`, `*`, `#` | open Warp command search |
### Mode switching
[Section titled “Mode switching”](#mode-switching)
| Command(s) | Description |
| ---------- | ----------------------------------------------------------------- |
| `i` | insert text before the cursor |
| `I` | insert text before the first non-whitespace character in the line |
| `a` | append text after the cursor |
| `A` | append text at the end of the line |
| `o` | begin new line below the cursor and insert text |
| `O` | begin new line above the cursor and insert text |
| `v` | visual character mode |
| `V` | visual line mode |
See [Vim docs: insert](https://vimdoc.sourceforge.net/htmldoc/insert.html#insert) and [Vim docs: visual mode](https://vimdoc.sourceforge.net/htmldoc/visual.html#visual-mode) for more information.
### Registers
[Section titled “Registers”](#registers)
| Command(s) | Description |
| ---------- | --------------- |
| `"` | register prefix |
Warp currently supports the following registers:
| Register name | Description |
| ---------------- | ---------------------------------------------------------------- |
| `a`–`z`, `A`–`Z` | named registers |
| `+` | system clipboard |
| `*` | system clipboard |
| `"` | unnamed register, containing the text of the last delete or yank |
See [Vim docs: registers](https://vimdoc.sourceforge.net/htmldoc/change.html#registers) for more information.
## Feedback
[Section titled “Feedback”](#feedback)
The best way to report bugs and request features is through Warp’s [GitHub Issues](https://github.com/warpdotdev/Warp/issues) page. Note that the issue or request is for Vim keybindings.
# Command entry overview
Canonical page: [/terminal/entry/](https://docs.warp.dev/terminal/entry/)
> Warp's main features for Command Entry, History, Synchronized Inputs, YAML Workflows, and more.
1. [Command Corrections](/terminal/entry/command-corrections/) provides auto-correct suggestions on previously run commands to catch typos and forgotten flags, and fix general console errors.
2. [Command Search](/terminal/entry/command-search/) is a 3-in-1 panel that allows you to search across Command History, Workflows, Notebooks, and AI Command Search all at once.
3. [Command History](/terminal/entry/command-history/) allows Warp to isolate the history of each shell session to make previously run commands easily accessible.
4. [Synchronized Inputs](/terminal/entry/synchronized-inputs/) allow you to easily run the same command in multiple sessions at the same time.
5. [YAML Workflows](/terminal/entry/yaml-workflows/) are easier to execute and share parameterized and searchable commands within Warp.
## Command Corrections
[Section titled “Command Corrections”](#command-corrections)
[Command Corrections Demo](https://www.loom.com/embed/180e1dc8d1504ec39c00694d9fd71b7c)
## Command Search
[Section titled “Command Search”](#command-search)
[Command Search Demo](https://www.loom.com/embed/21a6f58a33754ee7913edbff6d33d8d1)
## Command History
[Section titled “Command History”](#command-history)
[Command History Demo](https://www.loom.com/embed/8119beca8d794b06859c5dea1b1377bb)
## YAML Workflows
[Section titled “YAML Workflows”](#yaml-workflows)
[](/assets/terminal/yaml_workflows_demo.mp4)
# Command Corrections
Canonical page: [/terminal/entry/command-corrections/](https://docs.warp.dev/terminal/entry/command-corrections/)
> Command Corrections provides auto-correct suggestions on previously run commands to catch typos and forgotten flags, and fix general console errors.
## What is it
[Section titled “What is it”](#what-is-it)
This feature was built on top of the open-source project [nvbn/thefuck](https://github.com/nvbn/thefuck). Here are some examples that the Warp team usually finds Command Corrections useful for:
* Misspelled commands
* `gti checkout myBranchName` -> `git checkout myBranchName`
* `cd ap/sorce/executtor` -> `cd app/source/executor`
* Missing flags
* `git push` -> `git push --set-upstream myBranchName`
* Add permissions
* `./script` -> `chmod +x ./script && ./script`
## How to access it
[Section titled “How to access it”](#how-to-access-it)
* Command Corrections is enabled by default. You can disable Command Corrections by going to **Settings** > **Features** > **Terminal Input** > toggle “Suggest corrected commands”.
* After an incorrect command is run, a panel with the corrected command suggestion appears above the Input Editor. `CLICK` or press the `→` arrow to insert the suggestion.
## How it works
[Section titled “How it works”](#how-it-works)
[Command Corrections Demo](https://www.loom.com/embed/180e1dc8d1504ec39c00694d9fd71b7c)
#### Command correction rules
[Section titled “Command correction rules”](#command-correction-rules)
| Command |
| ------------------------------------------------------------ |
| brew |
| cargo |
| cat |
| cd |
| chmod |
| conda |
| cp |
| docker |
| generic (command agnostic, e.g. misspelling executable name) |
| git |
| go |
| grep |
| java |
| ls |
| mkdir |
| npm |
| pip |
| python |
| sed |
| sudo |
| yarn |
# Command History
Canonical page: [/terminal/entry/command-history/](https://docs.warp.dev/terminal/entry/command-history/)
> Command History helps you quickly find previously run commands.
## What is it
[Section titled “What is it”](#what-is-it)
While running, Warp isolates the history of each shell session e.g. if you have two Split Panes open, commands created in one pane do not populate the history of the other. Warp combines the history upon closing.
Command History also provides rich information like exit code, directory, thread, time to finish running, last run, etc.
Command history with rich metadata.
## How to access it
[Section titled “How to access it”](#how-to-access-it)
* Hitting `↑` in the [Input Editor](/terminal/editor/) brings up your history and performs a prefix search based on input.
* Pressing `Ctrl+R` opens the [Command Search](/terminal/entry/command-search/) panel and initiates a search of your Command History. To navigate the Command Search panel:
* Start typing and Warp will automatically filter using fuzzy search. Warp bolds matching text when filtering with fuzzy search.
## How it works
[Section titled “How it works”](#how-it-works)
[Command History Demo](https://www.loom.com/embed/8119beca8d794b06859c5dea1b1377bb)
# Command Search
Canonical page: [/terminal/entry/command-search/](https://docs.warp.dev/terminal/entry/command-search/)
> Search command history, Workflows, Prompts, and agent conversations with fuzzy matching.
The Command Search panel provides unified search across all your terminal inputs, saved commands, and [Terminal and Agent modes](/agents/local-agents/interacting-with-agents/terminal-and-agent-modes/) conversation history. Use it to quickly find and reuse commands, workflows, or past agent interactions.
Note
Tailor your Command Search experience by toggling off “Show Global Workflows” in **Settings** > **Features** > **Workflows**. When disabled, your search will exclusively encompass YAML and Warp Drive Workflows.
## Quickstart
[Section titled “Quickstart”](#quickstart)
1. Press `Ctrl+R` to open the Command Search Panel
2. Type your search query in the input box
3. Press `Enter` to input the selected command into Warp’s Input Editor
If your shell has rebound `Ctrl+R` to its own history widget — for example **fzf**, **atuin**, or fish’s **PatrickF1/fzf.fish** — Warp hands that keypress off to the shell widget instead of opening Command Search. Open Warp’s Command Search from the Command Palette when you need the unified panel (history, workflows, prompts, and agent conversations) while those shell widgets are installed.
## fzf shortcuts
[Section titled “fzf shortcuts”](#fzf-shortcuts)
For fzf, Warp also hands off these shortcuts at an idle prompt; atuin only receives the `Ctrl+R` handoff.
* `Ctrl+T` - Opens fzf’s file-search widget.
* `⌥+C` (macOS) or `Alt+C` (Windows/Linux) - Opens fzf’s directory-search widget and changes to the selected directory.
## Search filters
[Section titled “Search filters”](#search-filters)
You can filter your search results by prepending your search term with any of the following:
| Filter | Shortcuts |
| ------------------------------------------------------------------- | ------------------------------- |
| Command History | `history:`, `h:`, or `H-TAB` |
| Prompts | `prompts:`, `p:`, or `P-TAB` |
| [Agent Mode](/agents/local-agents/interacting-with-agents/) History | `ai_history:`, `a:`, or `A-TAB` |
Note
When a filter is activated, it will be bolded and italicized in the search panel.
## Additional features
[Section titled “Additional features”](#additional-features)
* You can expand the menu horizontally by dragging the right edge
* The panel supports fuzzy search and ranks results by relevance
## How it works
[Section titled “How it works”](#how-it-works)
[Command Search Demo](https://www.loom.com/embed/21a6f58a33754ee7913edbff6d33d8d1)
# Synchronized Inputs
Canonical page: [/terminal/entry/synchronized-inputs/](https://docs.warp.dev/terminal/entry/synchronized-inputs/)
> Type a command once and sync it to multiple panes simultaneously.
### Synchronized inputs vs. broadcast input
[Section titled “Synchronized inputs vs. broadcast input”](#synchronized-inputs-vs-broadcast-input)
Synchronized inputs in Warp work similarly to “broadcast input” settings in other terminals, but there are some differences.
With Warp’s synchronized inputs, whatever command you enter in one session will sync to the other sessions in its entirety. Whereas, “broadcast input” typically allows you to “broadcast” individual keystrokes, which may be more suitable for editing parts of commands.
## How to access it
[Section titled “How to access it”](#how-to-access-it)
There are two ways to access controls to synchronize inputs:
* [Command Palette](/terminal/command-palette/) in Warp: Search for “synchronize”
* macOS menus for the Warp app: **Edit** > **Synchronize Input**
## How to use it
[Section titled “How to use it”](#how-to-use-it)
* macOS
There are two modes available to scope how input is synchronized and one to stop any synchronization:
* Synchronize All Panes in All Tabs
* Synchronize All Panes in Current Tab `⌘+Option+I`
* Stop Synchronizing Any Panes `⌘+Option+I`
* Windows
There are two modes available to scope how input is synchronized and one to stop any synchronization:
* Synchronize All Panes in All Tabs
* Synchronize All Panes in Current Tab `Ctrl+Alt+I`
* Stop Synchronizing Any Panes `Ctrl+Alt+I`
* Linux
There are two modes available to scope how input is synchronized and one to stop any synchronization:
* Synchronize All Panes in All Tabs
* Synchronize All Panes in Current Tab `Ctrl+Alt+I`
* Stop Synchronizing Any Panes `Ctrl+Alt+I`
When inputs are synchronized, you can start typing in one input editor and that same input will be entered into all of the input editors for all panes in your current tab or all tabs, depending on the scope you selected.
If you are working in an alternative editor mode (like vim), synchronized inputs will only apply to all tabs with that same editor type running.
When you get done, you can select “Stop Synchronizing Any Panes” to end the synchronization.
## How it works
[Section titled “How it works”](#how-it-works)
# YAML Workflows
Canonical page: [/terminal/entry/yaml-workflows/](https://docs.warp.dev/terminal/entry/yaml-workflows/)
> Workflows are an easier way to execute and share commands within Warp.
Caution
You can continue to use YAML-based workflows, but we recommend using new [workflows in Warp Drive](/knowledge-and-collaboration/warp-drive/workflows/) instead for a better editing experience.
## What is it
[Section titled “What is it”](#what-is-it)
Workflows are easily parameterized and searchable by name, description, or command arguments. [Common Workflows](https://github.com/warpdotdev/workflows) sourced by the Warp team and community are readily available within the app. Additionally, you can create and scope Workflows locally or to a Git repository.
## How to use it
[Section titled “How to use it”](#how-to-use-it)
* Open the [Command Search](/terminal/entry/command-search/) or Workflow Search `Ctrl+Shift+R` panel to find Workflows.
* Once inside the menu, start typing in the search bar to filter the existing Workflows. (e.g. git, android, npm, etc.)
* When a Workflow is selected with `Enter`, you can use `Shift+Tab` to cycle through the arguments.
* You can also expand the menu horizontally with the mouse by dragging it on the right edge.
Note
Tailor your [Command Search](/terminal/entry/command-search/) experience by toggling off “Show Global Workflows” in **Settings** > **Features** > **Workflows**. When disabled, your search will exclusively encompass YAML and Warp Drive Workflows.
## How it works
[Section titled “How it works”](#how-it-works)
[](/assets/terminal/yaml_workflows_demo.mp4)
### How is this different from aliases?
[Section titled “How is this different from aliases?”](#how-is-this-different-from-aliases)
Workflows solve some major pain points with aliases, specifically the:
1. need to context switch
1. leave vim, source dotfiles, or reset shell
2. difficulty with attaching documentation
3. inability to easily search or share
4. inability to easily parameterize
## Creating custom workflows
[Section titled “Creating custom workflows”](#creating-custom-workflows)
### How to create a workflow with YAML
[Section titled “How to create a workflow with YAML”](#how-to-create-a-workflow-with-yaml)
You can store local workflows (scoped to your machine) in:
* macOS
```bash
$HOME/.warp/workflows/
```
* Windows
```powershell
$env:APPDATA\warp\Warp\data\workflows\
```
* Linux
```bash
${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/workflows/
```
Or, you can share them with your team by saving them in `{{path_to_git_repo}}/.warp/workflows/`. Local and repository Workflows can be accessed under the “My Workflows” and “Repository Workflows” tab of the Workflows menu, respectively.
See the existing Workflow spec within the [Workflows repo](https://github.com/warpdotdev/Workflows/tree/main/specs) for examples. Additionally, we outline the file format below:
[Workflow File Format](https://github.com/warpdotdev/Workflows/blob/main/FORMAT.md)
The Workflow file format is a [yaml](https://yaml.org/) file and must have either a `.yml` or `.yaml` extension. If you’re new to YAML and want to learn more, see [Learn YAML in Y minutes](https://learnxinyminutes.com/docs/yaml/).
***
**`name`**
The name of the Workflow. Required.
**`command`**
The command that is executed when the Workflow is selected. Required.
**`tags`**
An array of tags that are useful to categorize the Workflow. Optional.
```yaml
tags: ["git", "GitHub"]
```
**`description`**
The description of the Workflow and what it does. Optional.
**`source_url`**
The URL from where the Workflow was originally generated. Used for attribution of the original source. Optional.
**`author`**
The original author of the Workflow. For example, if this Workflow was generated from StackOverflow, the `author` would be the `author` of the StackOverflow post. Used for attribution. Optional.
**`author_url`**
The URL of the original author of the Workflow. For example, if this Workflow was generated from StackOverflow, the `author_url` would be the StackOverflow author’s profile page. Used for attribution. Optional.
**`shells`**
The list of shells where this Workflow is valid. If not specified, the Workflow is assumed to be valid in all shells. This must be one of `zsh`, `bash`, or `fish`.
**`arguments`**
A Workflow can have parameterized arguments to specify pieces of the Workflow that need to be filled in by the user.
You can specify which part of the Workflow command maps to an argument by surrounding it with two curly braces (`{{<argument>}}`).
For example the Workflow command:
```bash
for {{variable}} in {{sequence}}; do
{{command}}
done
```
Includes 3 arguments: `variable`, `sequence`, and `command`.
**`arguments.name`**
The name of the argument. The argument name is used within the command to specify the ranges of the argument. Required.
```yaml
name: Example Workflow
command: echo {{string}}
arguments:
- name: string
description: The value to echo
```
**`arguments.description`**
The description of the argument. Warp surfaces this to help users fill in Workflow arguments. Optional.
**`arguments.default_value`**
The default value for the argument. If specified, the `default_value` replaces the argument name within the command. Optional
***
### Where to save workflows
[Section titled “Where to save workflows”](#where-to-save-workflows)
Local Workflows are scoped to your machine. Repository Workflows are scoped to a Git repository and can be accessed by anyone who has cloned the repo.
* macOS
```bash
# Local Workflow Path
$HOME/.warp/workflows/
# Repository Workflow Path
{{path_to_git_repo}}/.warp/workflows
```
* Windows
```powershell
# Local Workflow Path
$env:APPDATA\warp\Warp\data\workflows\
# Repository Workflow Path
{{path_to_git_repo}}\.warp\workflows
```
* Linux
```bash
# Local Workflow Path
${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/workflows/
# Repository Workflow Path
{{path_to_git_repo}}/.warp/workflows
```
#### Local Workflows
[Section titled “Local Workflows”](#local-workflows)
To start, create a Workflow subdirectory within
* macOS
```bash
mkdir -p $HOME/.warp/workflows/
```
* Windows
```powershell
New-Item -Path "$env:APPDATA\warp\Warp\data\workflows\" -ItemType Directory
```
* Linux
```bash
mkdir -p ${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/workflows/
```
Add your Workflow’s `.yaml` file to this directory; if the file format is valid Warp should automatically load it into the Workflows menu.
`cp ~/path/to/my_awesome_workflow.yaml {{path_to_local_workflow_folder}}`
#### Repository Workflows
[Section titled “Repository Workflows”](#repository-workflows)
You can add a repository Workflow similarly to how you added a local Workflow. Create a Workflows folder in a repository’s root directory and save your `.yaml` file like so:
```plaintext
cd {{repository_path}}
mkdir -p .warp/workflows/
cp ~/path/to/my_awesome_workflow.yaml {{path_to_local_workflow_folder}}
```
#### Global Workflows
[Section titled “Global Workflows”](#global-workflows)
You can contribute Workflows that will be made available to other Warp users by forking the [Workflows repo](https://github.com/warpdotdev/workflows/tree/main/specs) and opening a pull request. See the [Contributing](https://github.com/warpdotdev/workflows#contributing) section for more details.
# Terminal Integrations
Canonical page: [/terminal/integrations-and-plugins/](https://docs.warp.dev/terminal/integrations-and-plugins/)
> Warp's terminal functionality extends and integrates with popular development tools.
## Docker
[Section titled “Docker”](#docker)
Note
Currently, the Docker extension is only available on macOS.
[Warp’s Docker extension](https://hub.docker.com/extensions/warpdotdev/warp) makes it more convenient to open Docker containers in Warp. With the extension, you can click to open any Docker container in a [Warpified subshell](/terminal/warpify/subshells/), without manually running `docker exec` or typing out lengthy container IDs.
Select a container from the list and specify a shell type. Note that only `bash|zsh|fish` are supported shells for Docker containers. Then, select a user (optional) and finally click “Open in Warp” to run commands within the Docker container.
Warp’s extension for Docker lists available containers.
## Raycast
[Section titled “Raycast”](#raycast)
Note
Currently, the Raycast extension is only available on macOS.
Warp + Raycast extension helps you open new windows, tabs, or Launch Configurations with [ease](https://twitter.com/warpdotdev/status/1678432353461637121).
[Warp + Raycast Extension Link](https://www.raycast.com/warpdotdev/warp)
Note
**Terminal Tip**\
Within `Raycast Settings > Extensions > Apps` search for Warp and assign the alias “terminal” so that it will show up on a search.
Warp integration with the Raycast launcher.
## VSCode
[Section titled “VSCode”](#vscode)
* macOS
Press `⌘+Shift+C` while in [VSCode](https://code.visualstudio.com/docs/terminal/basics) to open a new session in Warp.
[](/assets/terminal/vscode_new_session.mp4)
To configure this, navigate to Settings in VSCode and search for `Terminal › External: Osx Exec`.\
\
Change this to `Warp.app` if you’ve installed Warp in the default location. Otherwise, put in the full path to the executable.
* Windows
Press `Ctrl+Shift+C` while in [VSCode](https://code.visualstudio.com/docs/terminal/basics) to open a new session in Warp.
To configure this, navigate to Settings in VSCode and search for `Terminal › External: Windows Exec`.\
\
Change this to `%LOCALAPPDATA%\Programs\Warp\warp.exe` if you’ve installed Warp in the default location for a single user or `%PROGRAMFILES%\Warp\warp.exe` if you’ve installed Warp in the default location for all users. Otherwise, put in the full path to the executable.
* Linux
Press `Ctrl+Shift+C` while in [VSCode](https://code.visualstudio.com/docs/terminal/basics) to open a new session in Warp.
To configure this, navigate to Settings in VSCode and search for `Terminal › External: Linux Exec`.\
\
Change this to `warp-terminal` if you’ve installed Warp with your distribution’s package manager. Otherwise, put in the full path to the executable (e.g. if it is an AppImage).
## JetBrains IDEs
[Section titled “JetBrains IDEs”](#jetbrains-ides)
Note
Currently, the JetBrains IDE configuration is only available on macOS.
Press a keyboard shortcut of choice while in a JetBrains IDE to open a new session in Warp.
To configure this, use the Apple Menu. Click on **Preferences**, go to **External Tools**, and click **Add**. In this menu, put the following information:
* *Name*: Open Warp
* *Program*: `/Applications/Warp.app`
* *Arguments*: `$ProjectFileDir$`
* *Working Directory*: `/Applications`
Then press **OK**. Now you will be able to `Open Warp` from the Apple Menu under `Tools` -> `External Tools`.
[](/assets/terminal/jetbrains_external_terminal_config.mp4)
To attach this configuration to a keyboard shortcut, you must go to the Apple Menu -> `Preferences`. Then go to `Keymap` -> `External Tools`. You will find `Open Warp`. Right-click on it, and select **Add Keyboard Shortcut**. Type your desired shortcut and click save! You’re ready to open Warp with a keyboard shortcut.
[](/assets/terminal/jetbrains_external_window_keymap_config.mp4)
# More features overview
Canonical page: [/terminal/more-features/](https://docs.warp.dev/terminal/more-features/)
> Explore additional Warp terminal features beyond the essentials.
# Accessibility
Canonical page: [/terminal/more-features/accessibility/](https://docs.warp.dev/terminal/more-features/accessibility/)
> Warp's accessibility features include VoiceOver support, voice input, and configurable verbosity.
Note
Currently, these instructions are for macOS only. Warp doesn’t support screen readers on Linux or Windows. We’re tracking screen reader support in [GitHub issue #3847](https://github.com/warpdotdev/Warp/issues/3847).
We recognize the need to improve the experience for those visually impaired, as - to our best knowledge - other terminal emulator apps didn’t do a good job in this area. This doc summarizes what we’ve done so far, how Warp works with VoiceOver, and outlines the main changes from the typical workflow. For the features documentation and its keyboard shortcuts, go to the feature-specific page in the documentation.
**Keep in mind that this is a work-in-progress and the current state is not a final state of accessibility in Warp**.
## How to use Warp with VoiceOver
[Section titled “How to use Warp with VoiceOver”](#how-to-use-warp-with-voiceover)
The best way to start working with Warp & VoiceOver is to install it using Homebrew:
`brew install warp`
This will ensure that you can receive all future updates automatically, without the need to go through a macOS standard drag-and-drop installation process.
From there, Warp should seamlessly work with VoiceOver and start announcing what’s happening on the screen and what actions you can take. This may be a major difference from other apps: Warp makes these announcements on its own, letting you know what’s going on. There’s currently no way to navigate between different UI elements using VO key combinations.
Once installed, it will ask you to log in. Warp also sends telemetry that we use to improve the overall user experience. You can find out more about that in the [privacy section](/support-and-community/privacy-and-security/privacy/).
The login flow will require you to navigate between the app and your browser. The last step before you can start enjoying our new terminal app is filling up the onboarding survey.
The main terminal window is not that different from other terminals - there’s a place to type commands (Command Input) and a list of the previously executed commands and their outputs. Warp groups those together - each command and output create a Block. You can navigate blocks with your keyboard to check the command, learn whether it succeeded, and read the output, as well as copy the command, output, or both for further processing.
A main entry point for discovering new features and actions is our Command Palette, which you can access by pressing `⌘+P`.
## Differences from the regular VoiceOver workflow
[Section titled “Differences from the regular VoiceOver workflow”](#differences-from-the-regular-voiceover-workflow)
As you may notice, typical VoiceOver navigation keys or settings do not currently work in Warp. In short - it’s related to how our UI framework is currently implemented and that as of now we don’t yet offer a keyboard-accessible way to navigate the UI elements.
Instead, whenever you perform an action and/or something happens in the background, Warp announces it to you, letting you know what’s going on and what possible actions you can take. Since it’s a terminal, we care about all user actions being keyboard accessible from the start, so pretty much all our features have the assigned keybindings already. You can adjust the default keybindings by following the [Warp keysets repository](https://github.com/warpdotdev/keysets). You can also always fall back to using cmd-p to check the keybinding or execute the specific action.
### A11y specific actions
[Section titled “A11y specific actions”](#a11y-specific-actions)
Some a11y-specific settings are available through the Command Palette. For example, you can adjust the verbosity level of messages. Open the [Command Palette](/terminal/command-palette/) and type “a11y” to discover related options and their keybindings.
### Voice input
[Section titled “Voice input”](#voice-input)
Warp supports voice input as an alternative way to interact with your terminal. This can be especially helpful for users who prefer or require voice commands over typing. You can use voice input to:
* Issue terminal commands
* Ask questions about command usage
* Perform complex multi-step operations
Voice input can be enabled in **Settings** > **Agents** > **Warp Agent** > **Voice**. For detailed information about voice features and setup, see our [Voice documentation](/agents/local-agents/interacting-with-agents/voice/).
## Future work
[Section titled “Future work”](#future-work)
While not all Warp features are accessible yet, we’ve implemented a process around releasing new features and changes to the main app, to ensure that all new code provides proper a11y announcements.
This is not the ideal and final implementation. We’re happy to hear your thoughts and ideas on how we can improve. The biggest milestone for this work is to add support for navigating the UI elements using the keyboard. Give Warp a try, and please, do not hesitate to [share your feedback](/support-and-community/troubleshooting-and-support/sending-us-feedback/).
# Audible terminal bell
Canonical page: [/terminal/more-features/audible-bell/](https://docs.warp.dev/terminal/more-features/audible-bell/)
> Enable an audible terminal bell in Warp that can be triggered by CLI tools like ping.
Warp allows you to enable an audible terminal bell (disabled by default) that can be triggered by a variety of CLI tools (for example, `ping -a`).
* Enable the audible terminal bell in **Settings** > **Features** > **Terminal**.
* In the [Command Palette](/terminal/command-palette/), “Enable/Disable Audible Terminal Bell”.
# Files, Links, & Scripts
Canonical page: [/terminal/more-features/files-and-links/](https://docs.warp.dev/terminal/more-features/files-and-links/)
> Quickly open links and files or run scripts with your mouse.
## Files & links
[Section titled “Files & links”](#files--links)
Warp supports opening files, folders, and URL links that are within Blocks. Multiple URL protocols are supported e.g. `https`, `ftp`, `file`, etc. Warp can open files and folders in a variety of editors and opens web links directly in your default browser. Warp can also open markdown files directly with a [Markdown Viewer](/terminal/more-features/markdown-viewer/).
Note
Warp also supports iTerm2 and Kitty Image protocols on macOS and Linux. You will need to use a CLI tool to view images, in some cases the tools expect `$TERM=kitty`, so you may need to workaround this by setting `TERM=kitty` before the command. We’re working on updating the popular tools to recognize Warp natively.
Warp parses relative and absolute file paths. Warp also tries to capture line and column numbers attached to the file path, supported formats include:
* `file_name:line_num`
* `file_name:line_num:column_num`
* `file_name[line_num, column_num]`
* `file_name(line_num, column_num)`
* `file_name, line: line_num, column: column_num`
* `file_name, line: line_num, in`
- macOS
1. After hovering over a link, open it directly by holding down `⌘` while clicking it.
2. Clicking a link normally will open a clickable tooltip that says “Open File/Folder/Link”.
3. Right-clicking a link will open a context menu that supports copying the absolute file path or URL to the clipboard.
- Windows
1. After hovering over a link, open it directly by holding down `Ctrl` while clicking it.
2. Clicking a link normally will open a clickable tooltip that says “Open File/Folder/Link”.
3. Right-clicking a link will open a context menu that supports copying the absolute file path or URL to the clipboard.
- Linux
1. After hovering over a link, open it directly by holding down `Ctrl` while clicking it.
2. Clicking a link normally will open a clickable tooltip that says “Open File/Folder/Link”.
3. Right-clicking a link will open a context menu that supports copying the absolute file path or URL to the clipboard.
* You can also Drag and drop a folder or file onto the Warp dock icon to open a new tab in this directory.
* You can also right-click on a folder or file in Finder, then select Services, and “Open new Warp Tab | Window here”.
* Configure the default editor to open files by navigating to **Settings** > **Code** > **Editor and Code Review** > **Choose an editor to open file links**.
* Selecting “Default App” uses your system’s default application for the file type.
#### List of supported editors
[Section titled “List of supported editors”](#list-of-supported-editors)
Non-exhaustive list of editors, please submit new ones on our GitHub, see [Sending Feedback](/support-and-community/troubleshooting-and-support/sending-us-feedback/#sending-warp-feedback).
1. `$EDITOR`
2. Visual Studio Code
3. JetBrains IDEs
* WebStorm
* PhpStorm
* GoLand
* PyCharm
* DataGrip
* DataSpell
* Rider
* RubyMine
4. Zed and Zed Preview
5. Cursor
6. Windsurf
7. Sublime Text
8. Android Studio
[](/assets/terminal/files-links-demo.mp4)
### OSC 8 hyperlinks
[Section titled “OSC 8 hyperlinks”](#osc-8-hyperlinks)
Warp recognizes the OSC 8 escape sequence, so command-line tools can print a short label that links to a longer URL instead of printing the raw URL. When a program emits an OSC 8 hyperlink, Warp renders only the visible text and makes it clickable, the same way it treats auto-detected URLs:
* Hold `⌘` (macOS) or `Ctrl` (Windows/Linux) and click the linked text to open it.
* Copying the block copies the visible text, not the escape sequence or the underlying URL.
Any URL scheme works, including `file://` URLs without a hostname. To try it, print a hyperlink from your shell:
```bash
printf '\033]8;;https://docs.warp.dev\033\\Warp docs\033]8;;\033\\\n'
```
The output shows `Warp docs` as a clickable link. Plain-text URL detection still works, so tools that print full URLs behave as before.
## Scripts
[Section titled “Scripts”](#scripts)
Warp can open `.command` and Unix Executable files from Finder directly.
1. Find a `.command` or shell script you’d like to open in Finder.
2. Right-click and open the script with Warp.
Caution
Make sure the file has the appropriate executable permissions before you can run it in Warp. (e.g. `chmod +x script.command`)
[](/assets/terminal/script-demo.mp4)
# Full-screen apps
Canonical page: [/terminal/more-features/full-screen-apps/](https://docs.warp.dev/terminal/more-features/full-screen-apps/)
> Run Vim, Emacs, and other full-screen apps with configurable mouse reporting and padding.
## Mouse and scroll reporting
[Section titled “Mouse and scroll reporting”](#mouse-and-scroll-reporting)
Warp supports configuring how to handle mouse and scroll events. They can be sent to the currently running app, e.g. `vim`, or kept and handled by Warp.
Note
Mouse reporting must be enabled to also toggle scroll reporting.
Once mouse reporting is enabled, Warp will use ANSI escape sequences to communicate mouse events to the running app.
Note
If you want a mouse event to go to Warp instead (for example, for text selection) without disabling mouse reporting, you can hold the `Shift` key.
### How to access it
[Section titled “How to access it”](#how-to-access-it)
* From **Settings** > **Features** > **Terminal** > **Enable Mouse Reporting**
* Scroll Reporting can be enabled after toggling **Enable Mouse Reporting**
* From the [Command Palette](/terminal/command-palette/), search for “mouse reporting”
* The entry is labeled “Enable mouse reporting” or “Disable mouse reporting” depending on the current setting
* From the macOS Menu, **View** > **Toggle Mouse Reporting**
### How it works
[Section titled “How it works”](#how-it-works)
[Mouse and Scroll Reporting Demo](https://www.loom.com/embed/a918696b002148d3beafd545b233c1be)
## Padding
[Section titled “Padding”](#padding)
Warp supports configuring how much padding surrounds full-screen apps. The default is 0 pixel padding, but this can be changed to a custom padding amount or to match the padding in the block list.
Note
Warp allows you to scale your terminal by fractions of a cell width | height. When your terminal size is not perfectly aligned to a cell width | height, the extra space appears as padding on the right | bottom.
### How to access it
[Section titled “How to access it”](#how-to-access-it-1)
* Go to **Settings** > **Appearance** > **Full-screen Apps** or from the [Command Palette](/terminal/command-palette/) search for “Appearance”
* **Use custom padding in alt-screen** is enabled by default, you can disable it to match the block list padding
* Set the desired uniform padding (px) pixels, which is set to 0px by default
Caution
Some full-screen applications don’t behave well when resizing. If you are experiencing rendering issues with full screen apps, try turning this setting off. This will ensure that full-screen apps don’t need to resize when starting up.
The alt-screen padding setting in appearance preferences.
## Kitty keyboard protocol
[Section titled “Kitty keyboard protocol”](#kitty-keyboard-protocol)
Warp supports the [Kitty keyboard protocol](https://sw.kovidgoyal.net/kitty/keyboard-protocol/) (CSI u progressive enhancement) so full-screen apps can read keystrokes that legacy terminal escape sequences can’t represent — for example, distinguishing `Ctrl+I` from `Tab`, capturing modifier-only key events, or detecting key release events.
When a running app advertises that it supports the protocol, Warp emits the extended escape sequences automatically. No configuration is required.
* **Supported in**: Vim, Neovim, Emacs, tmux, helix, and other modern TUI apps that opt into CSI u.
* **Falls back to legacy encoding** when the running app doesn’t request progressive enhancement, so older programs keep working unchanged.
Note
If a TUI app reports unexpected key events after upgrading Warp, confirm the app itself supports the Kitty keyboard protocol. Most apps require an explicit opt-in (for example, `:set keyprotocol` in Neovim).
# Warp for Linux
Canonical page: [/terminal/more-features/linux/](https://docs.warp.dev/terminal/more-features/linux/)
> Linux-specific features including native Wayland support and crash recovery.
## Native Wayland
[Section titled “Native Wayland”](#native-wayland)
Warp Wayland support can be enabled in **Settings** > **Features** > **System**. Enabling Wayland support may fix issues with blurry text if you have fractional scaling enabled in your window manager.
Caution
When native Wayland is enabled, Global Hotkey support will be disabled. Unlike X11, the Wayland protocol does not expose the configuration necessary to support this feature.
## Wayland crash recovery
[Section titled “Wayland crash recovery”](#wayland-crash-recovery)
When Wayland support is enabled, Warp uses a custom crash recovery process to detect any crashes that may occur when using Wayland. If there’s a crash, Warp will fall back to using X11 to allow you to continue to use the application.
# Markdown Viewer
Canonical page: [/terminal/more-features/markdown-viewer/](https://docs.warp.dev/terminal/more-features/markdown-viewer/)
> Open Markdown files in your terminal, run shell commands, and view rendered Mermaid diagrams.
Warp can be used for both editing and viewing rendered Markdown files in a [split pane](/terminal/windows/split-panes/). Any local file with the `.md` or `.markdown` extension is treated as a Markdown file. Remote files are currently not supported. Turning on **Settings** > **Code** > **Editor and Code Review** > **Open Markdown files in Warp’s Markdown Viewer by default** will make the Markdown viewer default, otherwise Markdown files will open in Warp’s editor.
### Opening a file link within a block
[Section titled “Opening a file link within a block”](#opening-a-file-link-within-a-block)
* macOS
For any link to a Markdown file within a block, you can open the file in Warp by `⌘`-clicking on the link, from the link tooltip, or the right-click context menu on the link.
* Windows
For any link to a Markdown file within a block, you can open the file in Warp by `Ctrl`-clicking on the link, from the link tooltip, or the right-click context menu on the link.
* Linux
For any link to a Markdown file within a block, you can open the file in Warp by `Ctrl`-clicking on the link, from the link tooltip, or the right-click context menu on the link.
Opening a Markdown file via link tooltip.
### Markdown-viewing commands
[Section titled “Markdown-viewing commands”](#markdown-viewing-commands)
If you run a Markdown-viewing command like `cat myfile.md`, Warp will show a banner with a button to open the Markdown file.
The following commands are considered Markdown viewers:
* `cat`
* `glow`
* `less`
### Opening a Markdown file from Finder
[Section titled “Opening a Markdown file from Finder”](#opening-a-markdown-file-from-finder)
From Finder, you can open a Markdown file in Warp from the “Open With” menu that appears when right-clicking on the file.
### Toggling between editor and viewer
[Section titled “Toggling between editor and viewer”](#toggling-between-editor-and-viewer)
You can toggle between the Markdown editor and viewer via the pane overflow menu.
Toggling between editor and viewer.
## Shell commands in Markdown files
[Section titled “Shell commands in Markdown files”](#shell-commands-in-markdown-files)
Warp can run shell commands from Markdown code blocks in your active terminal session. Click the run icon `>_` to insert a command into the terminal input.
Note
The shell command must be in a code block with three backticks ` ``` ` and not inline code for Warp to treat the code like a runnable command.
Markdown shell blocks also support keyboard navigation. There are two ways to enter the keyboard navigation mode:
* macOS
* Clicking on a shell block.
* Pressing `⌘+↑` or `⌘+↓`.
Once a shell block is selected, press `⌘+Enter` to insert it into the terminal input. You can also use `↑`, `↓`, `⌘+↑`, and `⌘+↓` to navigate between shell blocks. While the Markdown file is focused, press `⌘+L` to switch focus back to the terminal without inserting a command.
* Windows
* Clicking on a shell block.
* Pressing `Ctrl+↑` or `Ctrl+↓`.
Once a shell block is selected, press `Ctrl+Enter` to insert it into the terminal input. You can also use `↑`, `↓`, `Ctrl+↑`, and `Ctrl+↓` to navigate between shell blocks. While the Markdown file is focused, press `Ctrl+Shift+L` to switch focus back to the terminal without inserting a command.
* Linux
* Clicking on a shell block.
* Pressing `Ctrl+↑` or `Ctrl+↓`.
Once a shell block is selected, press `Ctrl+Enter` to insert it into the terminal input. You can also use `↑`, `↓`, `Ctrl+↑`, and `Ctrl+↓` to navigate between shell blocks. While the Markdown file is focused, press `Ctrl+Shift+L` to switch focus back to the terminal without inserting a command.
If the command contains any arguments using the curly brace `{{param}}` syntax, they will be treated as Workflow arguments. Learn more about [Workflows](/knowledge-and-collaboration/warp-drive/workflows/).
[](/assets/terminal/run-markdown-file-command.mp4)
In addition, all shell and code blocks have a copy button to quickly copy the block’s text to the clipboard.
Code blocks without a set language, or one of the following languages, are treated as shell commands: `sh`, `shell`, `bash`, `fish`, `zsh`, `warp-runnable-command`.
## Mermaid diagrams
[Section titled “Mermaid diagrams”](#mermaid-diagrams)
Warp renders [Mermaid](https://mermaid.js.org/) diagrams in the markdown viewer. Add a fenced code block with the `mermaid` language tag and Warp converts it to a rendered SVG diagram automatically.
````plaintext
```mermaid
graph LR
A[Start] --> B[End]
```
````
A Mermaid diagram rendered in the Markdown Viewer.
### Switching between raw and rendered
[Section titled “Switching between raw and rendered”](#switching-between-raw-and-rendered)
Each Mermaid block includes a **Raw** and **Rendered** toggle. Use it to switch between the rendered diagram and the original Mermaid source without leaving the viewer.
# Desktop Notifications
Canonical page: [/terminal/more-features/notifications/](https://docs.warp.dev/terminal/more-features/notifications/)
> Receive desktop notifications when long-running commands complete or need your input.
## What is it
[Section titled “What is it”](#what-is-it)
Notifications can be sent when a command completes after a configurable number of seconds or when a running command needs you to enter a password to proceed. For either of these triggers, Warp will only send you a desktop notification if you are using a different app at the time the trigger is fired.
Note
For notifications from coding agents (Warp’s built-in Agent and third-party CLI agents like Claude Code and OpenCode), see [Agent Notifications](/agents/capabilities/agent-notifications/).
## Custom notification hooks (OSC 9 / OSC 777)
[Section titled “Custom notification hooks (OSC 9 / OSC 777)”](#custom-notification-hooks-osc-9--osc-777)
Warp supports pluggable notifications triggered by terminal escape sequences, so scripts and tools can raise desktop notifications without additional dependencies.
* OSC 9 (body only): sends a notification with just a body.
* Format: `ESC ] 9 ; <body> BEL`
* Example (bash/zsh): `printf '\033]9;Build complete\007'`
* OSC 777 (title + body): sends a notification with a title and body.
* Format: `ESC ] 777 ; notify ; <title> ; <body> BEL`
* Example (bash/zsh): `printf '\033]777;notify;Deploy;Success on prod\007'`
Notes:
* Works on macOS, Windows, and Linux where Warp is allowed to show notifications.
* Newlines and semicolons should be avoided or escaped in payloads.
* This feature is enabled by default in current releases of Warp.
## How to access it
[Section titled “How to access it”](#how-to-access-it)
### Notifications
[Section titled “Notifications”](#notifications)
* Notifications are enabled by default and require system permissions to appear.
* If you’ve turned Notifications off before, toggle it back on by going to **Settings** > **Features** > **Session**, or quickly toggle Notifications with the [Command Palette](/terminal/command-palette/).
* Customize Notification triggers for long-running commands or password prompts by going to **Settings** > **Features** > **Notifications**.
Note
On macOS, you will want to **Allow** or **Accept** the request so that Warp can send you desktop notifications. If you accidentally denied it or would like to re-enable Notifications later, check the [troubleshooting guide below](/terminal/more-features/notifications/#troubleshooting-notifications).
## How it works
[Section titled “How it works”](#how-it-works)
[Notifications Demo](https://www.loom.com/embed/65967f43a7fa432b98cf3e94766a8e79)
## Troubleshooting Notifications
[Section titled “Troubleshooting Notifications”](#troubleshooting-notifications)
* macOS
Warp requires two distinct notification settings to work. macOS system settings found in > **System Settings** > **Notifications & Focus** and Warp app settings found in **Settings** > **Features** > **Session** must both be enabled for Notifications to show.\
\
If you have Notifications enabled in the system and Warp, but you still aren’t receiving desktop notifications, try the following:
* Make sure that you are navigated away from Warp when you expect to receive the notification.
* Make sure the **Do Not Disturb** mode is turned off in > **System Settings** > **Notifications** > **Notifications & Focus** > **Focus**.
* Go to > **System Settings** > **Notifications & Focus** > **Notifications** and select Warp in the list. Make sure either banner style or alert style notifications are selected, then quit and restart Warp.
* To get the macOS notification prompt to show again for Warp, run `defaults delete dev.warp.Warp-Stable Notifications`, then restart Warp and toggle on the **Settings** > **Features** > **Receive desktop notifications from Warp**.
* Once all of the above is done, restart macOS to apply the changes, which should restore notifications in Warp.
* Windows
Warp requires two distinct notification settings to work. Windows system settings found in **Settings** > **System** > **Notifications** > **Warp** and Warp app settings found in **Settings** > **Features** > **Session** must both be enabled for Notifications to show.
If you have Notifications enabled in the system and Warp, but you still aren’t receiving desktop notifications, try the following:
* Make sure that you are navigated away from Warp when you expect to receive the notification.
* Make sure the **Do Not Disturb** mode or **Focus** is turned off.
* Go to **System** > **Notifications** and select Warp in the list. Make sure notifications are turned on, then quit and restart Warp.
* Linux
Warp requires two distinct notification settings to work. Linux system settings found in **Settings** > **Notifications** > **Warp** and Warp app settings found in **Settings** > **Features** > **Session** must both be enabled for Notifications to show.
If you have Notifications enabled in the system and Warp, but you still aren’t receiving desktop notifications, try the following:
* Make sure that you are navigated away from Warp when you expect to receive the notification.
* Make sure the **Do Not Disturb** mode (if your distribution supports it) is turned off.
* Go to **Settings** > **Notifications** and select Warp in the list. Make sure notifications are turned on, then quit and restart Warp.
Please [reach out to us](/support-and-community/troubleshooting-and-support/sending-us-feedback/#sending-warp-feedback) if you have any other issues.
# Terminal quit warning
Canonical page: [/terminal/more-features/quit-warning/](https://docs.warp.dev/terminal/more-features/quit-warning/)
> Warp's quit warning feature is a valuable precaution to prevent unintentional data loss or lost progress on long-running jobs.
## What is it
[Section titled “What is it”](#what-is-it)
The quit warning feature ensures that you receive a warning before quitting the app with a running process, allowing you to save your work and avoid any unintended data loss.\
If you quit the app or close a window containing a session with a running process, you’ll see the alert and need to confirm the action before proceeding. If you aren’t sure which processes you have running, there is also an option to show those processes.
## How to access it
[Section titled “How to access it”](#how-to-access-it)
* Open **Settings** > **Features** > **General**, there you can toggle the “Show warning before quitting”.
* You can also toggle the quit warning feature in the [Command Palette](/terminal/command-palette/), by searching for `Quit Warning`.
* If enabled, when you try and close Warp you will see a pop-up window with a few options listed below:
* Yes, quit, which will close all the Warp sessions and running processes.
* Show running processes, which will bring up the [Session Navigation](/terminal/sessions/session-navigation/) panel with a filter for running processes.
* Cancel, which will prevent Warp from closing.
* Don’t ask again, which is a box you can check to disable the quit warning feature.
## How it works
[Section titled “How it works”](#how-it-works)
[Quit Warning Modal Demo](https://www.loom.com/embed/bacb9d1c1e3947dca8365e15231cfcd3)
# Settings Sync
Canonical page: [/terminal/more-features/settings-sync/](https://docs.warp.dev/terminal/more-features/settings-sync/)
> Keep your Warp settings consistent across devices and sessions with cloud-based sync.
## How to toggle settings sync
[Section titled “How to toggle settings sync”](#how-to-toggle-settings-sync)
* You can toggle Settings Sync within the **Settings** > **Account** pane
* Through the [Command Palette](/terminal/command-palette/) by searching for “Settings Sync”
Settings Sync in Account pane.
Settings Sync in Command Palette.
## How settings sync works
[Section titled “How settings sync works”](#how-settings-sync-works)
**Settings Sync** works by syncing the state of most of your Warp settings to our cloud servers.
When you log in to Warp on another device or through the browser with [Session Sharing](/agents/local-agents/session-sharing/), if you have Settings Sync enabled, most of your settings will be the same as they were when you were logged in before.
That means your themes, most features, privacy settings, AI settings, **are all the same everywhere you use Warp**, saving you the time from having to set them up again.
When you first enable Settings Sync, the settings from the computer you enabled it on becomes the default settings for all devices. This is true if you toggle Settings Sync off and on as well - the synced settings are always from **the last device you enabled Settings Sync on**, so toggling effectively causes all of your devices to have settings from the current logged in instance.
Note
Read more about privacy for cloud features in the [privacy overview](https://www.warp.dev/privacy).
### Non-synced settings
[Section titled “Non-synced settings”](#non-synced-settings)
Not all settings are synced, however. Notably, Warp does not sync:
* Custom keybindings (we may in the future). Although, you can set [custom keybinds with a file](/getting-started/keyboard-shortcuts/#custom-keyboard-shortcuts)
* Custom themes (we may in the future)
* Device specific settings (e.g. what editor you prefer using, startup shell)
* Platform-specific settings are synced across devices on the same platform (e.g. your settings for how to interact with the Linux clipboard are synced across all Linux devices, but not on macOS, Windows, or Web).
You can tell when a setting is not synced because it will have a special cloud strikethrough icon in the settings panel.
Indicator showing settings are not synced.
# Text selection
Canonical page: [/terminal/more-features/text-selection/](https://docs.warp.dev/terminal/more-features/text-selection/)
> Use smart selection and rectangular (column) selection to quickly highlight text in Warp.
## Smart selection
[Section titled “Smart selection”](#smart-selection)
**Smart selection** goes beyond the typical double-click selection, which only highlights a single word. Instead, it uses semantic rules to treat common patterns (like URLs or file paths) as one unit, even when separated by punctuation or whitespace.
Using smart selection to select a file path by double clicking.
Double-click on text in the input or block list. The following patterns are recognized:
1. URLs
2. File paths
3. Email addresses
4. IP addresses
5. Floating point numbers, including scientific notation.
You can toggle smart selection on the **Settings** > **Features** > **Terminal** > **Double-click smart selection**. If disabled, you can instead manually select specific punctuation characters to be included within word boundaries.
## Rectangular selection
[Section titled “Rectangular selection”](#rectangular-selection)
**Rectangular selection** lets you highlight text in a clean vertical block (also called *column* or *box* selection). This is especially useful for copying command output, logs, or prefixed text without grabbing unwanted characters.
Using rectangular selection to select by columns in the block output.
Hold the modifier keys while dragging your mouse:
* macOS: `⌘+Option`
* Windows and Linux: `Ctrl+Alt`
# Warp URI Scheme
Canonical page: [/terminal/more-features/uri-scheme/](https://docs.warp.dev/terminal/more-features/uri-scheme/)
> Warp's URI scheme enables you to programmatically open new windows, tabs, launch configurations, or tab configs with ease.
## How to use it
[Section titled “How to use it”](#how-to-use-it)
There are several ways to use the URI scheme:
* Open new window `warp://action/new_window?path=<path_to_folder>`
* Open new tab `warp://action/new_tab?path=<path_to_folder>`
* Open Launch Configuration `warp://launch/<launch_configuration_path>`
* Open Tab Config `warp://tab_config/<name>` — opens the saved [Tab Config](/terminal/windows/tab-configs/) as a new tab in the active window. Append `?new_window=true` to open it in a new window instead. `<name>` is matched case-insensitively against the file stem of the `.toml`, so both `warp://tab_config/my_tab` and `warp://tab_config/my_tab.toml` resolve to `my_tab.toml`.
* Open Settings `warp://settings` — opens the Settings window. See [Settings deep links](#settings-deep-links) for search, widget, and sub-page options.
Note
[Warp Preview](/support-and-community/community/warp-preview-and-alpha-program/) URI scheme begins with `warppreview://`
## Settings deep links
[Section titled “Settings deep links”](#settings-deep-links)
Open the Settings window directly, optionally jumping to a specific page, widget, or search:
* `warp://settings` — open Settings on the default page.
* `warp://settings?q=<query>` — open Settings with the search bar pre-filled.
* `warp://settings?widget=<widget_id>` — open Settings scrolled to a specific setting.
* `warp://settings/appearance` — open the Appearance page (themes, fonts, and more).
* `warp://settings/mcp` — open the MCP servers page. Append `?autoinstall=<name>` to install a gallery MCP server by name.
* `warp://settings/warp_agent` — open the Warp Agent page (inference and API keys).
* `warp://settings/environments` — open the Cloud environments page.
* `warp://settings/platform` — open the Platform page.
* `warp://settings/billing_and_usage` — open the Billing & usage page.
* `warp://settings/teams` — open Team settings. Append `?invite=<email>` to open the invite dialog with the email pre-filled.
## How it works
[Section titled “How it works”](#how-it-works)
Example of Warp [URIs in use in Warp + Raycast Extension](https://github.com/raycast/extensions/blob/74521b70b62355004b0958393a64f9417b1ff3a6/extensions/warp/src/uri.ts).
[Warp + Raycast Extension Demo made using URIs](https://twitter.com/i/status/1678432353461637121)
# Working Directory
Canonical page: [/terminal/more-features/working-directory/](https://docs.warp.dev/terminal/more-features/working-directory/)
> Set a default working directory for new Warp sessions, with options for home directory, previous session, custom path, or per-window/tab/pane configuration.
## What is it
[Section titled “What is it”](#what-is-it)
Warp’s working directory feature is designed to enhance your workflow by enabling you to set up a default directory for new sessions. This feature helps you save time and quickly access your preferred directories when starting new sessions. You have the flexibility to set up a working directory for all new sessions or customize it individually for Windows, Tabs, and Panes, based on your specific needs.
## How to access it
[Section titled “How to access it”](#how-to-access-it)
* Open **Settings** > **Features** > **Session** and go to “Working directory for new sessions”.
* The drop-down for this feature provides several options discussed below:
* Home Directory, is the default option for new sessions and opens new sessions in the currently logged-in user’s home folder `~/`.
* Previous session’s directory, opens new sessions in your active session’s current directory.
* Custom directory, opens new sessions in a file path you specify.
* Advanced, allows you to select from the three options for new sessions in Windows, Tabs, and Panes.
## How to use it
[Section titled “How to use it”](#how-to-use-it)
[](/assets/terminal/working-directory-demo.mp4)
# Sessions overview
Canonical page: [/terminal/sessions/](https://docs.warp.dev/terminal/sessions/)
> Navigate between sessions and automatically restore windows, tabs, and panes when you relaunch Warp.
Warp sessions let you navigate between terminal sessions and automatically restore your workspace when you relaunch the app. Session Navigation helps you quickly switch between active sessions, while Session Restoration preserves your windows, tabs, and panes across restarts.
1. [Session Navigation](/terminal/sessions/session-navigation/) enables you to easily navigate to any session in Warp.
2. [Session Restoration](/terminal/sessions/session-restoration/) automatically restores the window and tabs from your previous session.
For tab layout configuration, see [Tab Configs](/terminal/windows/tab-configs/) and [Launch Configurations (Legacy)](/terminal/sessions/launch-configurations/) under [Windows and Tabs](/terminal/windows/).
## Session Navigation
[Section titled “Session Navigation”](#session-navigation)
[Session Navigation Demo](https://www.loom.com/embed/2147adc6749c4f4ea5da432eadda7995)
## Session Restoration
[Section titled “Session Restoration”](#session-restoration)
[](/assets/terminal/sessions-block_restoration.mp4)
# Launch Configurations (Legacy)
Canonical page: [/terminal/sessions/launch-configurations/](https://docs.warp.dev/terminal/sessions/launch-configurations/)
> Launch Configurations (Legacy) let you save a configuration of windows, tabs, and panes. For new setups, use Tab Configs instead.
Caution
Launch Configurations have been replaced by [Tab Configs](/terminal/windows/tab-configs/). Existing Launch Configurations continue to work, but new features are not being added. For new setups, use [Tab Configs](/terminal/windows/tab-configs/).
## What is it
[Section titled “What is it”](#what-is-it)
You can create Launch Configurations in the app or by adding a YAML file.
## Creating a Launch Configuration
[Section titled “Creating a Launch Configuration”](#creating-a-launch-configuration)
### From the UI
[Section titled “From the UI”](#from-the-ui)
1. Set up the configuration of windows, tabs, and panes you would like to save.
2. Open the [Command Palette](/terminal/command-palette/), and type in `Save New Launch Configuration`.
3. Name the configuration file. The name field cannot be empty.
4. Click the Save configuration button.
Warp saves each tab group’s name, color, collapsed and pinned states, and tab membership.
### With a YAML File
[Section titled “With a YAML File”](#with-a-yaml-file)
* Launch Configurations files are generated when you create them with the UI and can also be created or modified manually.
* See [Launch Configuration YAML file locations, format, and examples](/terminal/sessions/launch-configurations/#launch-configuration-yaml-format).
## Using a Launch Configuration
[Section titled “Using a Launch Configuration”](#using-a-launch-configuration)
* macOS
* From the [Command Palette](/terminal/command-palette/), enter `Launch Configuration` to open and select Launch Configuration.
* Right-clicking the new Tab **+** button to open a menu and select saved Launch Configuration.
* From the macOS menu bar, **File** > **Launch Configurations**, where you can search through and open your saved Launch Configuration.
* Single-window launch configs can be launched into the active window from the launch configuration palette using `⌘+Enter` on macOS.
* Windows
* From the [Command Palette](/terminal/command-palette/), enter `Launch Configuration` to open and select Launch Configuration.
* Right-clicking the new Tab **+** button to open a menu and select saved Launch Configuration.
* Single-window launch configs can be launched into the active window from the launch configuration palette using `Ctrl+Enter` on Windows.
To open a WSL tab with a Launch Configuration, you must first set WSL as your default shell in Warp:
* Go to **Settings** > **Features** > **Session** > **Startup shell for new sessions**.
* Select your desired WSL distribution (e.g., Ubuntu) as the default shell.
After this, any Launch Configuration you open will use WSL as the shell.
* Linux
* From the [Command Palette](/terminal/command-palette/), enter `Launch Configuration` to open and select Launch Configuration.
* Right-clicking the new Tab **+** button to open a menu and select saved Launch Configuration.
* Single-window launch configs can be launched into the active window from the launch configuration palette using `Ctrl+Enter` on Linux.
Tip
**Terminal Tip**\
You can open saved Launch Configurations via Alfred Workflow or [Raycast](/terminal/integrations-and-plugins/#raycast) Extension. See Joe Tannenbaum’s guide to [opening Warp Launch Configurations from Raycast and Alfred](https://blog.joe.codes/open-warp-launch-configurations-from-raycast-and-alfred). Credit to [@joetannenbaum](https://twitter.com/joetannenbaum/status/1633538768866009115)
## How it works
[Section titled “How it works”](#how-it-works)
[Launch Configuration Demo](https://www.loom.com/embed/daa2a9e55c27458c8bbf722d90078880)
## Launch Configuration YAML format
[Section titled “Launch Configuration YAML format”](#launch-configuration-yaml-format)
All Launch Configuration yaml files are stored in the following location:
* macOS
```bash
$HOME/.warp/launch_configurations/
```
* Windows
```powershell
$env:APPDATA\warp\Warp\data\launch_configurations\
```
* Linux
```bash
${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/launch_configurations/
```
Caution
The `cwd:` value in the yaml code must contain an absolute path or `""`. Note that `~` or empty paths will result in the file not being visible on the list of options for Launch Configurations.
### Windows
[Section titled “Windows”](#windows)
Sample configuration that shows how windows are structured in launch configuration files.
```yaml
# Warp Launch Configuration
#
# This configuration has two windows,
# each with one tab in different starting directories.
---
name: Example Windows
windows:
- tabs:
- title: Documents
layout:
cwd: /Users/warp-user/Documents
color: blue
- tabs:
- title: Warp User
layout:
cwd: /Users/warp-user
color: green
```
### Tabs
[Section titled “Tabs”](#tabs)
Here’s a sample configuration that shows how tabs are structured in launch configuration files.
* Use the `title` field to set a custom tab name
* Use the `color` field to set the tab color
* We currently support using the terminal colors (ANSI colors):
`Red | Green | Yellow | Blue | Magenta | Cyan`
The actual color values will be automatically derived from your Warp theme
```yaml
# Warp Launch Configuration
#
# This configuration has two tabs in the same window.
---
name: Example Tabs
windows:
- tabs:
- title: Documents
layout:
cwd: /Users/warp-user/Documents
color: blue
- title: Warp User
layout:
cwd: /Users/warp-user
color: green
```
### Tab groups
[Section titled “Tab groups”](#tab-groups)
Use `tab_groups` on a window to define groups. Set `group` on each tab to the zero-based position of its group in the `tab_groups` list. Tabs without `group` open outside a group.
Each tab group supports:
* **`name`** - The group name.
* **`color`** - One of `black`, `red`, `green`, `yellow`, `blue`, `magenta`, `cyan`, or `white`.
* **`collapsed`** - Whether the group opens collapsed. Defaults to `false`.
* **`pinned`** - Whether the group opens pinned. Defaults to `false`.
grouped-development.yaml
```yaml
---
name: Grouped development
windows:
- tabs:
- title: API
layout:
cwd: /Users/warp-user/Projects/api
group: 0
- title: Tests
layout:
cwd: /Users/warp-user/Projects/api
commands:
- exec: npm test
group: 0
- title: Notes
layout:
cwd: /Users/warp-user/Documents
tab_groups:
- name: Backend
color: blue
collapsed: false
pinned: false
```
Tabs in the same group must be adjacent in the `tabs` list. Warp opens a tab outside a group when its `group` index does not exist or when the same group appears again after a different group or ungrouped tab. Warp does not create groups without member tabs.
### Panes
[Section titled “Panes”](#panes)
Launch Configurations support setting split panes in each tab. Note that Warp also supports nesting split panes in launch configuration files.
```yaml
# Warp Launch Configuration
#
# This configuration is two windows, each with split panes.
# The first window contains a vertically split tab with two panes.
# The second window contains a horizontally split tab,
# with a vertically split tab on the right.
---
name: Example Panes
windows:
- tabs:
- title: Downloads and Warp User
layout:
split_direction: vertical
panes:
- cwd: /Users/warp-user/Downloads
- cwd: /Users/warp-user
color: blue
- tabs:
- title: Desktop, Documents, and Warp User
layout:
split_direction: horizontal
panes:
- cwd: /Users/warp-user/Desktop
- split_direction: vertical
panes:
- cwd: /Users/warp-user/Documents
- cwd: /Users/warp-user
color: green
```
### Active and Focus
[Section titled “Active and Focus”](#active-and-focus)
Sample configuration that shows how a Window and Tab can be activated with a session in focus.
* Use the `active_window_index` and `active_tab_index` fields to set your active Window and Tab.
* Use the `is_focused` field to set which Pane is focused in each tab.
Caution
Note that when you use `- active_tab_index:` the `tabs:` field doesn’t need the `-` prefix, as this can cause syntax issues.
```yaml
# Warp Launch Configuration
#
# This configuration has two tabs, with the second tab active.
# Two vertical split panes in the first tab and the top pane focused.
# Two horizontal split panes in the second tab and the right pane focused.
---
name: Example Active and Focus
active_window_index: 0
windows:
- active_tab_index: 1
tabs:
- title: Tab 1
layout:
split_direction: vertical
panes:
- cwd: /Users/warp-user/Documents
is_focused: true
- cwd: /Users/warp-user/Documents/Projects
- title: Tab 2
layout:
split_direction: horizontal
panes:
- cwd: /Users/warp-user/Downloads
- cwd: /Users/warp-user
is_focused: true
```
### Commands
[Section titled “Commands”](#commands)
Use the `commands` field to define a set of commands to run when a launch configuration is run.
Caution
You may need to use double quotes for commands with special characters. Commands in separate lines are chained together with `&&` when run, as such commands run after `ssh` commands may not execute.
```yaml
# Warp Launch Configuration
#
# This configuration has two windows,
# the first window executes two commands on start,
# the second window has a split pane that executes a command on start.
---
name: Example Commands
windows:
- tabs:
- title: Documents
layout:
cwd: /Users/warp-user/Documents
commands:
- exec: ls
- exec: code .
color: blue
- tabs:
- title: Downloads
layout:
split_direction: vertical
panes:
- cwd: /Users/warp-user/Downloads
commands:
- exec: curl http://example.com -o my.file
- exec: cp my.file my.file2
- cwd: /Users/warp-user
commands:
- exec: ssh user@remote.server.com
color: green
```
# Session Navigation
Canonical page: [/terminal/sessions/session-navigation/](https://docs.warp.dev/terminal/sessions/session-navigation/)
> Quickly navigate to any terminal session across Warp using the Session Navigation palette.
## How to access session navigation
[Section titled “How to access session navigation”](#how-to-access-session-navigation)
1. Open the Session Navigation palette with the [Command Palette](/terminal/command-palette/), click on **session >\_** or type in “sessions:”.
2. Jump to a session by using your mouse or the `↑`/`↓` arrow keys and `Enter`.
3. Refine the session results by searching for sessions by prompt, the currently running command, last run command, and command status (ex: “Running…”, “Completed 10 minutes ago”, “Empty Session”).
Note
Sessions are ordered by recency, so the most recently focused sessions show up first. The Session Navigation palette does not have **PS1** support and can only show Warp’s native prompt.
### Ctrl+Tab behavior
[Section titled “Ctrl+Tab behavior”](#ctrltab-behavior)
`Ctrl+Tab` shortcut defaults to activate the previous / next [Tabs](/terminal/windows/tabs/). You can configure the shortcut to cycle the most recent session, including any [Split Panes](/terminal/windows/split-panes/), in **Settings** > **Features** > **Keys** > **Ctrl+Tab behavior**
## How session navigation works
[Section titled “How session navigation works”](#how-session-navigation-works)
[Session Navigation Demo](https://www.loom.com/embed/2147adc6749c4f4ea5da432eadda7995)
# Session Restoration
Canonical page: [/terminal/sessions/session-restoration/](https://docs.warp.dev/terminal/sessions/session-restoration/)
> Restore your windows, tabs, panes, and recent Blocks automatically when you relaunch Warp.
## What is it
[Section titled “What is it”](#what-is-it)
Session restoration allows you to quickly pick up where you left off in your previous terminal session.
## How to access session restoration
[Section titled “How to access session restoration”](#how-to-access-session-restoration)
* Session Restoration comes enabled by default in Warp.
Note
On Linux, opening windows at a specific position is not supported in Wayland.
* You can disable Session Restoration by going to **Settings** > **Features**, then toggling off **Restore windows, tabs, and panes on startup**.
Caution
Toggling off Session Restoration will not clear the [SQLite database](/terminal/sessions/session-restoration/#session-restoration-database); however, Warp will stop recording new output.
## How session restoration works
[Section titled “How session restoration works”](#how-session-restoration-works)
[](/assets/terminal/sessions-block_restoration.mp4)
#### Session Restoration database
[Section titled “Session Restoration database”](#session-restoration-database)
Warp saves the data from your previous session’s windows, tabs, and panes to a SQLite database on your computer, and every time you quit the app, this data is overwritten by your latest session. You can open the database directly and inspect its full contents like so:
* macOS
```bash
sqlite3 "$HOME/Library/Group Containers/2BBY89MBSN.dev.warp/Library/Application Support/dev.warp.Warp-Stable/warp.sqlite"
```
* Windows
```powershell
sqlite3 $env:LOCALAPPDATA\warp\Warp\data\warp.sqlite
```
* Linux
```bash
sqlite3 "${XDG_STATE_HOME:-$HOME/.local/state}/warp-terminal/warp.sqlite"
```
**How to clear the Session Restoration database**
Sometimes, you may want to prevent a sensitive Block from being saved on your computer, or you may want to clear blocks from a machine entirely.
Note
This interferes with the running session’s ability to save content and may require you to close Warp before running the database removal commands.
Danger
The following guidance is destructive and will delete any sessions and block history.
There are two ways to do this:
* macOS
* Clear the blocks from your running Warp session with `⌘+K`.
* Delete the SQLite file entirely with the following command:
```bash
rm -f "$HOME/Library/Group Containers/2BBY89MBSN.dev.warp/Library/Application Support/dev.warp.Warp-Stable/warp.sqlite"
```
* Windows
* Clear the blocks from your running Warp session with `Ctrl+Shift+K`.
* Delete the SQLite file entirely with the following command:
```powershell
Remove-Item -Force $env:LOCALAPPDATA\warp\Warp\data\warp.sqlite
```
* Linux
* Clear the blocks from your running Warp session with `Ctrl+Shift+K`.
* Delete the SQLite file entirely with the following command:
```bash
rm -f "${XDG_STATE_HOME:-$HOME/.local/state}/warp-terminal/warp.sqlite"
```
# Settings file
Canonical page: [/terminal/settings/](https://docs.warp.dev/terminal/settings/)
> Configure Warp with a plain-text TOML settings file. Learn where it lives, how it works with the Settings panel, and see common configuration examples.
Warp stores your preferences in a plain-text file called `settings.toml`. You can edit it directly in any text editor, check it into version control, or generate it with a script. Changes take effect immediately — no restart required.
The settings file works alongside the graphical Settings panel. Changes you make in either place are reflected in the other.
**Key features:**
* **Hot-reload** — Warp watches `settings.toml` for changes and applies them instantly when you save the file.
* **Error recovery** — If the file contains invalid TOML or an unrecognized value, Warp shows a warning banner and falls back to defaults for the affected settings. Fix the file and the banner clears automatically.
* **Automatic migration** — When you upgrade to a version of Warp that includes the settings file, Warp automatically migrates your existing preferences into `settings.toml`.
* **Bidirectional sync with Settings UI** — Changes in the Warp **Settings** panel (`⌘+,` on macOS, `Ctrl+,` on Linux/Windows) write to `settings.toml`, and hand-edits to the file are reflected in the panel.
* **Agent-powered editing** — Ask Warp’s agent to change settings for you using natural language (for example, “increase my font size to 16”). The bundled `modify-settings` skill handles the file update automatically.
## Opening your settings file
[Section titled “Opening your settings file”](#opening-your-settings-file)
There are several ways to open `settings.toml`:
* In the Warp app, go to **Settings** and click **Open settings file** at the bottom of the panel.
* Open the file directly in any editor at the path listed below for your platform and Warp release channel.
## File location
[Section titled “File location”](#file-location)
Depending on your platform and Warp release channel, `settings.toml` is located at:
* **macOS**
* Stable — `~/.warp/settings.toml`
* Preview — `~/.warp-preview/settings.toml`
* **Linux**
* Stable — `~/.config/warp-terminal/settings.toml`
* Preview — `~/.config/warp-terminal-preview/settings.toml`
* **Windows**
* Stable — `%LOCALAPPDATA%\warp\Warp\config\settings.toml`
* Preview — `%LOCALAPPDATA%\warp\WarpPreview\config\settings.toml`
The JSON schema for `settings.toml` is bundled with the app (read-only) and can be used to enable autocompletion and validation in your editor:
* **macOS**
* Stable — `/Applications/Warp.app/Contents/Resources/settings_schema.json`
* Preview — `/Applications/WarpPreview.app/Contents/Resources/settings_schema.json`
* **Linux**
* Stable — `/opt/warpdotdev/warp-terminal/resources/settings_schema.json`
* Preview — `/opt/warpdotdev/warp-terminal-preview/resources/settings_schema.json`
* **Windows** (user install)
* Stable — `%LOCALAPPDATA%\Programs\Warp\resources\settings_schema.json`
* Preview — `%LOCALAPPDATA%\Programs\WarpPreview\resources\settings_schema.json`
* **Windows** (system install)
* Stable — `%PROGRAMFILES%\Warp\resources\settings_schema.json`
* Preview — `%PROGRAMFILES%\WarpPreview\resources\settings_schema.json`
For the locations of every other Warp file — themes, tab configs, keybindings, logs, the local database, and more — see [File and folder locations](/terminal/settings/file-locations/).
## Settings file format
[Section titled “Settings file format”](#settings-file-format)
The file uses [TOML v1.1](https://toml.io/en/v1.1.0) syntax. Settings are organized into **sections** (TOML tables) that group related options — for example, `[appearance.text]` contains font settings and `[agents.profiles]` contains agent permission settings.
Here is a minimal example showing the structure:
```toml
# Appearance settings
[appearance.text]
font_name = "JetBrains Mono"
font_size = 14.0
line_height_ratio = 1.3
[appearance.themes]
theme = "dracula"
# Terminal behavior
[terminal.input]
syntax_highlighting = true
honor_ps1 = false
# Agent permissions
[agents.profiles]
agent_mode_execute_readonly_commands = true
```
### How sections map to TOML tables
[Section titled “How sections map to TOML tables”](#how-sections-map-to-toml-tables)
Each section in the settings file corresponds to a TOML table header in brackets. Subsections use dot-separated paths:
* `[general]` — Top-level general settings like session restoration and tab placement
* `[appearance]` — Visual settings, with subsections like `[appearance.text]`, `[appearance.themes]`, `[appearance.cursor]`
* `[agents]` — Agent and AI settings, with subsections like `[agents.profiles]`, `[agents.warp_agent.input]`
* `[terminal]` — Terminal behavior settings, with subsections like `[terminal.input]`
For the complete list of every available setting, see [All settings reference](/terminal/settings/all-settings/).
## How settings are applied
[Section titled “How settings are applied”](#how-settings-are-applied)
### Relationship between the Settings panel and the file
[Section titled “Relationship between the Settings panel and the file”](#relationship-between-the-settings-panel-and-the-file)
The Warp Settings panel (`⌘+,` on macOS, `Ctrl+,` on Linux/Windows) and `settings.toml` represent the same underlying configuration. Changing a toggle in the Settings panel writes the new value to `settings.toml`. Editing `settings.toml` by hand updates the Settings panel the next time it reads the file.
### Error banner
[Section titled “Error banner”](#error-banner)
When `settings.toml` has errors, Warp displays a dismissible warning banner at the top of the workspace. The banner includes an **Open settings file** button so you can jump directly to the file and fix the issue. Once you save a corrected file, the banner disappears automatically.
## Common configurations
[Section titled “Common configurations”](#common-configurations)
### Change theme and font
[Section titled “Change theme and font”](#change-theme-and-font)
```toml
[appearance.themes]
theme = "cyber_wave"
[appearance.text]
font_name = "Fira Code"
font_size = 15.0
ligature_rendering_enabled = true
font_weight = "normal"
```
### Configure agent permissions
[Section titled “Configure agent permissions”](#configure-agent-permissions)
```toml
[agents.profiles]
agent_mode_coding_permissions = "always_allow_reading"
agent_mode_execute_readonly_commands = true
agent_mode_command_execution_allowlist = [
"cat(\\s.*)?",
"echo(\\s.*)?",
"find .*",
"grep(\\s.*)?",
"ls(\\s.*)?",
"which .*",
]
```
### Enable Vim keybindings
[Section titled “Enable Vim keybindings”](#enable-vim-keybindings)
```toml
[text_editing]
vim_mode_enabled = true
vim_status_bar = true
```
## Migrating from previous settings
[Section titled “Migrating from previous settings”](#migrating-from-previous-settings)
When you upgrade to a version of Warp that includes the settings file, Warp automatically migrates your existing preferences into `settings.toml`. No action is required — your customizations carry over and the file becomes the source of truth for all settings going forward.
## Troubleshooting
[Section titled “Troubleshooting”](#troubleshooting)
### ”Your settings file contains an error” banner
[Section titled “”Your settings file contains an error” banner”](#your-settings-file-contains-an-error-banner)
This banner appears when `settings.toml` has invalid TOML syntax or an unrecognized value. Click **Open settings file** in the banner to open the file and look for:
* **Missing quotes** — String values must be wrapped in double quotes: `font_name = "Hack"`, not `font_name = Hack`.
* **Missing brackets** — Section headers require square brackets: `[appearance.text]`.
* **Wrong value types** — Check that numbers are numbers (`font_size = 13.0`), booleans are `true`/`false`, and enum values are valid strings.
### Resetting to defaults
[Section titled “Resetting to defaults”](#resetting-to-defaults)
Delete `settings.toml` (or rename it) and restart Warp. Warp falls back to built-in defaults for all settings. The file is re-created the next time you change a setting through the Settings panel.
```bash
# Uncomment the two lines that match your platform and Warp release
# channel, then run them to back up and delete settings.toml.
# Stable (macOS)
# cp ~/.warp/settings.toml ~/.warp/settings.toml.bak
# rm ~/.warp/settings.toml
# Stable (Linux)
# cp ~/.config/warp-terminal/settings.toml ~/.config/warp-terminal/settings.toml.bak
# rm ~/.config/warp-terminal/settings.toml
# Preview (macOS)
# cp ~/.warp-preview/settings.toml ~/.warp-preview/settings.toml.bak
# rm ~/.warp-preview/settings.toml
# Preview (Linux)
# cp ~/.config/warp-terminal-preview/settings.toml ~/.config/warp-terminal-preview/settings.toml.bak
# rm ~/.config/warp-terminal-preview/settings.toml
```
### Settings not applying
[Section titled “Settings not applying”](#settings-not-applying)
Confirm you’re editing the correct file for your platform and Warp release channel (see [File location](#file-location) above). If you run multiple [Warp release channels](/support-and-community/community/warp-preview-and-alpha-program/), each channel has its own settings directory.
## Related pages
[Section titled “Related pages”](#related-pages)
* [All settings reference](/terminal/settings/all-settings/) — Complete list of every available setting with descriptions, types, and defaults
* [File and folder locations](/terminal/settings/file-locations/) — Where Warp stores every config, data, and state file across macOS, Windows, and Linux
* [Customizing Warp](/getting-started/quickstart/customizing-warp/) — Overview of all customization options
* [Custom themes](/terminal/appearance/custom-themes/) — Create and load custom YAML or Base16 themes
* [Keyboard shortcuts](/getting-started/keyboard-shortcuts/) — Customize keybindings
* [Settings Sync (Beta)](/terminal/more-features/settings-sync/) — Sync settings across machines
# All settings reference
Canonical page: [/terminal/settings/all-settings/](https://docs.warp.dev/terminal/settings/all-settings/)
> Complete reference for every setting available in Warp's settings.toml file, organized by section with descriptions, types, defaults, and examples.
This page lists every setting you can configure in [`settings.toml`](/terminal/settings/) organized by TOML section. For an introduction to the settings file, how to open it, and common configuration examples, see [Settings file](/terminal/settings/).
Settings are grouped into sections that correspond to TOML table headers (for example, `[appearance.text]`). Only include the settings you want to change — Warp uses built-in defaults for everything else.
## General
[Section titled “General”](#general)
Top-level settings that control Warp’s startup behavior, session management, and window-level preferences.
**Section**: `[general]`
* `default_session_mode` — The default mode for new terminal sessions. Type: string. Default: `"terminal"`. Options: `"terminal"`, `"agent"`, `"cloud_agent"`, `"tab_config"`, `"docker_sandbox"`.
* `default_tab_config_path` — Path to the tab config used when `default_session_mode` is `"tab_config"`. Type: string. Default: `""`.
* `link_tooltip` — Whether to show a tooltip when hovering over links. Type: boolean. Default: `true`.
* `login_item` — Whether to launch Warp automatically when you log in. Type: boolean. Default: `true`.
* `mouse_scroll_multiplier` — The scroll speed multiplier for mouse scroll events. Type: number. Default: `3.0`.
* `new_tab_placement` — Where new tabs are placed in the tab bar. Type: string. Default: `"after_current_tab"`. Options: `"after_current_tab"`, `"after_all_tabs"`.
* `preserve_input_focus_on_block_selection` — Whether the input box keeps focus when you select a block. Type: boolean. Default: `false`.
* `quit_on_last_window_closed` — Whether to quit Warp when the last window is closed. Type: boolean. Default: `false`.
* `restore_session` — Whether to restore the previous session when Warp starts up. Type: boolean. Default: `true`.
* `should_confirm_close_session` — Whether to show a confirmation dialog when closing a session. Type: boolean. Default: `true`.
* `show_changelog_after_update` — Whether the changelog is shown after an update. Type: boolean. Default: `true`.
* `show_warning_before_quitting` — Whether to show a warning dialog before quitting Warp. Type: boolean. Default: `true`.
* `snackbar_enabled` — Whether to show snackbar notifications. Type: boolean. Default: `true`.
* `user_native_preference` — Whether to prefer the native desktop app or the web app. Type: string. Default: `"not_selected"`. Options: `"not_selected"`, `"web"`, `"desktop"`.
### Undo close
[Section titled “Undo close”](#undo-close)
**Section**: `[general.undo_close]`
* `enabled` — Whether the undo close feature is enabled. Type: boolean. Default: `true`.
* `grace_period` — How long (in seconds) after closing a tab you can still undo the close. Type: integer. Default: `60`.
## Appearance
[Section titled “Appearance”](#appearance)
Visual settings that control how Warp looks, including themes, fonts, cursor, tabs, window, and layout.
**Section**: `[appearance]`
* `spacing` — Controls the spacing between terminal blocks. Type: string. Default: `"normal"`. Options: `"normal"`, `"compact"`.
### Themes
[Section titled “Themes”](#themes)
**Section**: `[appearance.themes]`
* `theme` — The color theme. Type: string. Default: `"dark"`. Options: `"adeberry"`, `"phenomenon"`, `"dark"`, `"dracula"`, `"fancy_dracula"`, `"cyber_wave"`, `"solar_flare"`, `"solarized_dark"`, `"willow_dream"`, `"light"`, `"dark_city"`, `"gruvbox_dark"`, `"red_rock"`, `"jelly_fish"`, `"leafy"`, `"koi"`, `"solarized_light"`, `"snowy"`, `"gruvbox_light"`, `"pink_city"`, `"marble"`, or a custom theme object.
* `system_theme` — Whether to match the system light/dark theme. Type: boolean. Default: `false`.
* `selected_system_themes` — The themes to use for system light and dark modes. Type: object. Default: `{ dark = "dark", light = "light" }`.
To use a custom theme:
```toml
[appearance.themes]
theme = { custom = { name = "My Theme", path = "~/.warp/themes/my-theme.yaml" } }
```
### Text
[Section titled “Text”](#text)
**Section**: `[appearance.text]`
* `font_name` — The monospace font used in the terminal. Type: string. Default: `"Hack"`.
* `font_size` — The size of the monospace font in the terminal. Type: number. Default: `13.0`.
* `font_weight` — The weight of the monospace font. Type: string. Default: `"normal"`. Options: `"thin"`, `"extra_light"`, `"light"`, `"normal"`, `"medium"`, `"semibold"`, `"bold"`, `"extra_bold"`, `"black"`.
* `line_height_ratio` — The line height ratio for terminal text. Type: number. Default: `1.2`.
* `ligature_rendering_enabled` — Whether to render font ligatures in the terminal. Type: boolean. Default: `false`.
* `ai_font_name` — The font used for AI-generated content. Type: string. Default: `"Hack"`.
* `match_ai_font` — Whether the AI font automatically matches the terminal font. Type: boolean. Default: `false`.
* `notebook_font_size` — The font size used in notebooks. Type: number. Default: `14.0`.
* `match_notebook_to_monospace_font_size` — Whether the notebook font size matches the terminal font size. Type: boolean. Default: `true`.
* `use_thin_strokes` — Whether to use thin font strokes on macOS. Type: string. Default: `"on_high_dpi_displays"`. Options: `"never"`, `"on_low_dpi_displays"`, `"on_high_dpi_displays"`, `"always"`.
* `enforce_minimum_contrast` — Whether to enforce minimum contrast for text readability. Type: string. Default: `"only_named_colors"`. Options: `"never"`, `"only_named_colors"`, `"always"`.
### Cursor
[Section titled “Cursor”](#cursor)
**Section**: `[appearance.cursor]`
* `cursor_display_type` — The visual style of the cursor. Type: string. Default: `"bar"`. Options: `"bar"`, `"block"`, `"underline"`.
* `cursor_blink` — Whether the cursor blinks. Type: string. Default: `"enabled"`. Options: `"enabled"`, `"disabled"`.
### Blocks
[Section titled “Blocks”](#blocks)
**Section**: `[appearance.blocks]`
* `show_block_dividers` — Whether to show dividers between terminal blocks. Type: boolean. Default: `true`.
* `show_jump_to_bottom_of_block_button` — Whether to show the jump-to-bottom button in long command output. Type: boolean. Default: `true`.
* `should_show_bootstrap_block` — Whether the bootstrap block is visible in the terminal. Type: boolean. Default: `false`.
* `should_show_in_band_command_blocks` — Whether in-band command blocks are visible. Type: boolean. Default: `false`.
* `should_show_ssh_block` — Whether the SSH connection block is visible. Type: boolean. Default: `false`.
### Tabs
[Section titled “Tabs”](#tabs)
**Section**: `[appearance.tabs]`
* `workspace_decoration_visibility` — When workspace decorations such as the tab bar are visible. Type: string. Default: `"hide_fullscreen"`. Options: `"always_show"`, `"hide_fullscreen"`, `"on_hover"`.
* `tab_close_button_position` — Position of the close button on tabs. Type: string. Default: `"right"`. Options: `"right"`, `"left"`.
* `show_indicators_button` — Whether to show activity indicators on tabs. Type: boolean. Default: `true`.
* `preserve_active_tab_color` — Whether to preserve the active tab’s color when switching tabs. Type: boolean. Default: `false`.
* `directory_tab_colors` — Mapping of directory paths to their tab color assignments, populated when you assign tab colors by directory. Type: object. Default: `{}`.
* `header_toolbar_chip_selection` — Configuration for the header toolbar chips in the vertical tab panel header. Type: string or object. Default: `"default"`.
### Vertical tabs
[Section titled “Vertical tabs”](#vertical-tabs)
**Section**: `[appearance.vertical_tabs]`
* `enabled` — Whether to display tabs vertically instead of horizontally. Type: boolean. Default: `false`.
* `view_mode` — Display mode for the vertical tab bar. Type: string. Default: `"compact"`. Options: `"compact"`, `"expanded"`.
* `primary_info` — The primary information displayed on vertical tabs. Type: string. Default: `"command"`. Options: `"command"`, `"working_directory"`, `"branch"`.
* `compact_subtitle` — Subtitle shown on compact vertical tabs. Type: string. Default: `"branch"`. Options: `"branch"`, `"working_directory"`, `"command"`.
* `display_granularity` — Granularity of rows displayed in the vertical tabs panel. Type: string. Default: `"panes"`. Options: `"panes"`, `"tabs"`.
* `tab_item_mode` — Tab item display mode in vertical tabs. Type: string. Default: `"focused_session"`. Options: `"focused_session"`, `"summary"`.
* `show_details_on_hover` — Whether to show a details sidecar when hovering over a vertical tab. Type: boolean. Default: `true`.
* `show_diff_stats` — Whether to show diff stats on vertical tabs. Type: boolean. Default: `true`.
* `show_pr_link` — Whether to show PR links on vertical tabs. Type: boolean. Default: `true`.
* `use_latest_prompt_as_title` — Whether vertical tab names for agent conversations use the latest user prompt. Type: boolean. Default: `false`.
* `hide_title_bar_search_bar` — Whether to hide the title bar search bar when using the vertical tab layout. Search stays available via the Command Palette and keyboard shortcuts. Type: boolean. Default: `false`.
* `show_panel_in_restored_windows` — Whether restored windows open the vertical tabs panel even if it was closed when the session was saved. Type: boolean. Default: `false`.
### Panes
[Section titled “Panes”](#panes)
**Section**: `[appearance.panes]`
* `focus_pane_on_hover` — Whether panes are focused when hovered over. Type: boolean. Default: `false`.
* `should_dim_inactive_panes` — Whether inactive panes are visually dimmed. Type: boolean. Default: `false`.
### Input position
[Section titled “Input position”](#input-position)
**Section**: `[appearance.input]`
* `input_mode` — The position of the terminal input. Type: string. Default: `"pinned_to_bottom"`. Options: `"pinned_to_bottom"`, `"pinned_to_top"`, `"waterfall"`.
### Full-screen apps
[Section titled “Full-screen apps”](#full-screen-apps)
**Section**: `[appearance.full_screen_apps]`
* `alt_screen_padding` — Controls padding around full-screen terminal applications. Type: string or object. Default: `{ custom = { uniform_padding = 0.0 } }`.
### Icon
[Section titled “Icon”](#icon)
**Section**: `[appearance.icon]`
* `app_icon` — The app icon displayed in the dock. Type: string. Default: `"default"`. Options: `"default"`, `"aurora"`, `"classic1"`, `"classic2"`, `"classic3"`, `"comets"`, `"cow"`, `"glass_sky"`, `"glitch"`, `"glow"`, `"holographic"`, `"mono"`, `"neon"`, `"original"`, `"starburst"`, `"sticker"`, `"warp_one"`.
* `show_dock_icon` — Whether Warp is shown in the macOS Dock and `⌘+Tab` switcher. Type: boolean. Default: `true`. macOS only.
### Window
[Section titled “Window”](#window)
**Section**: `[appearance.window]`
* `override_opacity` — The opacity of the window background, from 1 to 100 percent. Type: integer. Default: `100`.
* `override_blur` — The blur radius applied to the window background. Type: integer. Default: `1`. macOS only.
* `backdrop` — The system backdrop material applied to the window background when opacity is below 100%. Type: string. Default: `"none"`. Options: `"none"` (no material), `"mica"`, `"acrylic"`, `"mica_alt"`. Windows only. In the Warp app, go to **Settings** > **Appearance** > **Window** and choose **Window backdrop**.
* `override_blur_texture` — Deprecated. Prefer `backdrop`. When `backdrop` is unset, a true value migrates to `"acrylic"`. Type: boolean. Default: `false`. Windows only.
* `zoom_level` — The zoom level for the window, as a percentage. Type: integer. Default: `100`.
* `open_windows_at_custom_size` — Whether to open new windows at a custom size instead of the default. Type: boolean. Default: `false`.
* `new_windows_num_columns` — The number of columns for new windows when using a custom size. Type: integer. Default: `80`.
* `new_windows_num_rows` — The number of rows for new windows when using a custom size. Type: integer. Default: `40`.
* `left_panel_visibility_across_tabs` — Whether the left panel visibility is shared across all tabs. Type: boolean. Default: `true`.
## Terminal
[Section titled “Terminal”](#terminal)
Settings that control terminal behavior, input, and event handling.
**Section**: `[terminal]`
* `copy_on_select` — Whether text is automatically copied to the clipboard when selected. Type: boolean. Default: `true`.
* `focus_reporting_enabled` — Whether to forward focus and blur events to full-screen terminal applications. Type: boolean. Default: `true`.
* `mouse_reporting_enabled` — Whether to forward mouse events to full-screen terminal applications. Type: boolean. Default: `true`.
* `scroll_reporting_enabled` — Whether to forward scroll events to full-screen terminal applications. Type: boolean. Default: `true`.
* `maximum_grid_size` — The maximum number of rows in the terminal grid. Type: integer. Default: `50000`.
* `osc52_clipboard_access` — Whether terminal programs can access the system clipboard via OSC 52 escape sequences. Type: string. Default: `"deny"`. Options: `"deny"`, `"write_only"`, `"read_write"`.
* `use_audible_bell` — Whether to play an audible bell sound on terminal bell events. Type: boolean. Default: `false`.
* `show_terminal_zero_state_block` — Whether to show the AI zero-state block in new terminal sessions. Type: boolean. Default: `true`.
### Input
[Section titled “Input”](#input)
**Section**: `[terminal.input]`
* `syntax_highlighting` — Whether syntax highlighting is enabled in the terminal input. Type: boolean. Default: `true`.
* `honor_ps1` — Whether to use your shell’s PS1 prompt instead of the Warp prompt. Type: boolean. Default: `false`.
* `input_box_type_setting` — The terminal input style. Type: string. Default: `"classic"`. Options: `"universal"` (AI-first input), `"classic"` (Terminal-first input).
* `alias_expansion_enabled` — Whether shell alias expansion is enabled in the input. Type: boolean. Default: `false`.
* `command_corrections` — Whether command corrections are suggested for mistyped commands. Type: boolean. Default: `true`.
* `error_underlining_enabled` — Whether command errors are underlined in the input. Type: boolean. Default: `true`.
* `completions_open_while_typing` — Whether the completions menu opens automatically while typing. Type: boolean. Default: `false`.
* `classic_completions_mode` — Whether classic completions mode is enabled. Type: boolean. Default: `false`.
* `warp_completions_enabled` — Whether Warp’s built-in completions are shown for shell commands. When enabled, **Settings** > **Features** > **Terminal Input** also exposes “Open completions menu as you type” as a nested control (the same knob as `completions_open_while_typing`). Type: boolean. Default: `true`.
* `native_shell_completions_enabled` — Whether your shell’s own completions are used for shell commands, alongside Warp’s built-in completions when both are on. Native shell completions are not generated as you type; press `Tab` (or your completions keybinding) to fetch them. Type: boolean. Default: `true`.
* `show_hint_text` — Whether hint text is shown in the terminal input. Type: boolean. Default: `true`.
* `show_terminal_input_message_bar` — Whether the terminal input message bar is shown. Type: boolean. Default: `true`.
* `enable_slash_commands_in_terminal` — Whether slash commands are available in the terminal input. Type: boolean. Default: `true`.
* `at_context_menu_in_terminal_mode` — Whether the @ context menu is available in terminal mode. Type: boolean. Default: `true`.
* `enable_ai_command_search_hash_trigger` — Whether typing `#` at the start of terminal input opens [Command Search](/terminal/entry/command-search/). When disabled, Command Search is still reachable through its keyboard shortcut. Type: boolean. Default: `true`.
* `outline_codebase_symbols_for_at_context_menu` — Whether codebase symbols appear in the @ context menu. Type: boolean. Default: `true`.
* `middle_click_paste_enabled` — Whether middle-click pastes from the clipboard. Type: boolean. Default: `true`.
* `right_click_behavior` — What a bare right-click does in the terminal. Type: string. Default: `"context_menu"`. Options: `"context_menu"` (open the context menu), `"paste"` (paste from the clipboard; `Shift`+right-click opens the context menu instead).
* `extra_meta_keys` — Controls which additional keys are treated as meta keys. Type: object. Default: `{ left_alt = false, right_alt = false }`.
#### Autosuggestions
[Section titled “Autosuggestions”](#autosuggestions)
**Section**: `[terminal.input.autosuggestions]`
* `enabled` — Whether command autosuggestions are shown. Type: boolean. Default: `true`.
* `keybinding_hint` — Whether autosuggestion keybinding hints are displayed. Type: boolean. Default: `true`.
* `show_ignore_button` — Whether the ignore button is shown for autosuggestions. Type: boolean. Default: `false`.
### Smart select
[Section titled “Smart select”](#smart-select)
**Section**: `[terminal.smart_select]`
* `enabled` — Whether double-click smart selection is enabled for URLs, emails, file paths, and identifiers. Type: boolean. Default: `true`.
* `word_char_allowlist` — Characters considered part of a word for double-click selection when smart select is disabled. Type: string. Default: `"-.~/\"`.
## Session
[Section titled “Session”](#session)
Settings that control shell selection and working directory behavior for new sessions.
**Section**: `[session]`
* `startup_shell_override` — The shell to use when Warp starts up. Type: string or null. Default: `null` (uses system default).
* `new_session_shell_override` — The shell to use when opening a new session. Type: string, object, or null. Default: `null` (uses system default). Options: `"system_default"`, `{ executable = "/path/to/shell" }`, `{ custom = "command" }`.
### Working directory config
[Section titled “Working directory config”](#working-directory-config)
**Section**: `[session.working_directory_config]`
* `advanced_mode` — Whether to use separate settings per session source. Type: boolean. Default: `false`.
When `advanced_mode` is `false`, the `[session.working_directory_config.global]` table applies to all session sources. When `true`, you can configure each source independently.
**Section**: `[session.working_directory_config.global]` (also `.split_pane`, `.new_tab`, `.new_window`)
* `mode` — How the working directory is determined. Type: string. Default: `"previous_dir"`. Options: `"home_dir"`, `"previous_dir"`, `"custom_dir"`.
* `custom_dir` — Custom directory path, used when mode is `"custom_dir"`. Type: string. Default: `""`.
```toml
# Use a specific directory for split panes, previous directory for everything else
[session.working_directory_config]
advanced_mode = true
[session.working_directory_config.global]
mode = "previous_dir"
custom_dir = ""
[session.working_directory_config.split_pane]
mode = "custom_dir"
custom_dir = "~/projects"
[session.working_directory_config.new_tab]
mode = "previous_dir"
custom_dir = ""
[session.working_directory_config.new_window]
mode = "home_dir"
custom_dir = ""
```
## Agents
[Section titled “Agents”](#agents)
Settings for Warp’s agents, including model behavior, permissions, knowledge, MCP servers, and voice input.
**Section**: `[agents]`
* `cloud_conversation_storage_enabled` — Whether conversations are stored in the cloud. Type: boolean. Default: `true`.
* `usage_display_mode` — Which unit the terminal agent’s usage entry displays. Applies only to the terminal agent’s settings file; click the usage entry to flip between units. Type: string. Default: `"credits"`. Options: `"credits"` (the same number the desktop app’s usage footer shows), `"cost"` (provider dollar cost).
* `execution_profiles` — The collection of [agent profiles](/agents/capabilities/agent-profiles-permissions/) and their permissions, shared by Agent Mode and the terminal agent. This is a structured object that Warp manages when you create and edit profiles in **Settings** > **Agents** > **Profiles**; edit it through the UI rather than by hand. Type: object. Default: `{}` (Warp’s built-in profiles).
* `custom_endpoints` — Non-secret [custom inference endpoint](/agents/inference/custom-inference-endpoint/) definitions (URL, models, schema). Credentials stay in local secure storage, not in this object. Warp manages the collection from **Settings**; edit it through the UI rather than by hand. Type: object. Default: `{}`.
### Knowledge
[Section titled “Knowledge”](#knowledge)
**Section**: `[agents.knowledge]`
* `rules_enabled` — Whether the agent uses your saved rules during requests. Type: boolean. Default: `true`.
* `warp_drive_context_enabled` — Whether Warp Drive context is included in AI requests. Type: boolean. Default: `true`.
### MCP servers
[Section titled “MCP servers”](#mcp-servers)
**Section**: `[agents.mcp_servers]`
* `file_based_mcp_enabled` — Whether global file-based MCP servers from third-party agents are automatically spawned. Warp-managed global MCP servers auto-spawn regardless of this setting, and project-scoped servers must be started manually. Type: boolean. Default: `false`.
### Profiles (permissions)
[Section titled “Profiles (permissions)”](#profiles-permissions)
**Section**: `[agents.profiles]`
* `agent_mode_coding_permissions` — The file read permission level for the agent. Type: string. Default: `"always_ask_before_reading"`. Options: `"always_ask_before_reading"`, `"always_allow_reading"`, `"allow_reading_specific_files"`.
* `agent_mode_coding_file_read_allowlist` — File paths the agent can read without asking for permission. Type: array of strings. Default: `[]`.
* `agent_mode_execute_readonly_commands` — Whether the agent can auto-execute read-only commands without asking. Type: boolean. Default: `false`.
* `agent_mode_command_execution_allowlist` — Commands the agent can execute without explicit permission (regex patterns). Type: array of strings. Default: `["cat(\\s.*)?", "echo(\\s.*)?", "find .*", "grep(\\s.*)?", "ls(\\s.*)?", "which .*"]`.
* `agent_mode_command_execution_denylist` — Commands the agent must always ask before executing (regex patterns). Type: array of strings. Default: `["bash(\\s.*)?", "fish(\\s.*)?", "pwsh(\\s.*)?", "sh(\\s.*)?", "zsh(\\s.*)?", "curl(\\s.*)?", "eval(\\s.*)?", "exec(\\s.*)?", "source(\\s.*)?", "wget(\\s.*)?", "dig(\\s.*)?", "nslookup(\\s.*)?", "host(\\s.*)?", "ssh(\\s.*)?", "scp(\\s.*)?", "rsync(\\s.*)?", "telnet(\\s.*)?", "rm(\\s.*)?"]`.
### Warp Agent (AI features)
[Section titled “Warp Agent (AI features)”](#warp-agent-ai-features)
**Section**: `[agents.warp_agent]`
* `is_any_ai_enabled` — Controls whether all AI features are enabled. Type: boolean. Default: `true`.
#### Active AI
[Section titled “Active AI”](#active-ai)
**Section**: `[agents.warp_agent.active_ai]`
* `enabled` — Controls whether proactive AI features like suggestions are enabled. Type: boolean. Default: `true`.
* `code_suggestions_enabled` — Controls whether AI code suggestions are enabled. Type: boolean. Default: `true`.
* `intelligent_autosuggestions_enabled` — Controls whether AI-powered intelligent autosuggestions are enabled. Type: boolean. Default: `true`.
* `agent_mode_query_suggestions_enabled` — Controls whether prompt suggestions are shown in Agent Mode. Type: boolean. Default: `true`.
* `git_operations_autogen_enabled` — Whether AI auto-generates commit messages and PR titles and bodies in the code review dialogs. Type: boolean. Default: `true`.
* `rule_suggestions_enabled` — Whether the agent suggests rules to save after responses. Type: boolean. Default: `true`.
* `shared_block_title_generation_enabled` — Controls whether titles are auto-generated when sharing blocks. Type: boolean. Default: `true`.
#### Input
[Section titled “Input”](#input-1)
**Section**: `[agents.warp_agent.input]`
* `ai_auto_detection_enabled` — Controls whether AI automatically detects natural language input. Type: boolean. Default: `true`.
* `ai_command_denylist` — Commands to exclude from AI natural language autodetection. Type: string. Default: `""`.
* `nld_in_terminal_enabled` — Controls whether natural language detection is enabled in the terminal input. Type: boolean. Default: `false`.
* `show_model_selectors_in_prompt` — Whether to show AI model selectors in the input prompt. Type: boolean. Default: `true`.
* `show_agent_tips` — Whether agent tips are displayed in the input. Type: boolean. Default: `true`.
* `include_agent_commands_in_history` — Whether agent-executed commands are included in command history. Type: boolean. Default: `false`.
* `agent_toolbar_chip_selection_setting` — Controls the layout of context chips in the Agent Mode toolbar. Type: string or object. Default: `"default"`.
#### Other
[Section titled “Other”](#other)
**Section**: `[agents.warp_agent.other]`
* `thinking_display_mode` — Controls how agent thinking traces are displayed after streaming. Type: string. Default: `"show_and_collapse"`. Options: `"show_and_collapse"`, `"always_show"`, `"never_show"`.
* `open_conversation_layout_preference` — Whether to open agent conversations in a new tab or a split pane. Type: string. Default: `"new_tab"`. Options: `"new_tab"`, `"split_pane"`.
* `show_conversation_history` — Whether conversation history appears in the tools panel. Type: boolean. Default: `true`.
* `show_agent_notifications` — Whether agent notifications are shown. Type: boolean. Default: `true`.
* `should_show_oz_updates_in_zero_state` — Whether the “What’s new” section is shown in the agent view. Type: boolean. Default: `true`.
* `should_render_use_agent_toolbar_for_user_commands` — Whether to show the “Use Agent” footer for terminal commands. Type: boolean. Default: `true`.
* `cloud_agent_computer_use_enabled` — Whether computer use is enabled for cloud agent conversations. Type: boolean. Default: `false`.
* `agent_attribution_enabled` — Whether the Warp Agent adds an attribution co-author line to commit messages and pull requests it creates. Type: boolean. Default: `true`.
* `auto_handoff_on_sleep_enabled` — Whether Warp automatically hands off local agent conversations to the cloud when your computer is about to sleep (macOS). See [local-to-cloud handoff](/platform/handoff/local-to-cloud/). Type: boolean. Default: `false`.
* `default_prompt_submission_mode` — Default behavior when submitting a new prompt while the agent is still responding. See [Prompt Queueing](/agents/local-agents/interacting-with-agents/prompt-queueing/). Type: string. Default: `"interrupt"`. Options: `"interrupt"`, `"queue"`.
* `long_running_command_submission_mode` — What happens when you submit a prompt while the agent is running an agent-requested long-running command. Only applies when `default_prompt_submission_mode` is `"interrupt"`. See [Prompt Queueing](/agents/local-agents/interacting-with-agents/prompt-queueing/). Type: string. Default: `"queue_until_command_completes"`. Options: `"send_immediately"`, `"queue_until_command_completes"`.
* `orchestration_message_display_mode` — How child-agent message bodies are displayed during [multi-agent runs](/platform/orchestration/multi-agent-runs/). Type: string. Default: `"always_collapse"`. Options: `"show_and_collapse"`, `"always_show"`, `"always_collapse"`.
* `auto_approve_bypasses_command_denylist` — Whether auto-approve and fast forward run commands that match your [command denylist](/agents/capabilities/agent-profiles-permissions/#command-denylist) without asking for confirmation. Denylist rules enforced by your organization through the [Admin Panel](/enterprise/team-management/admin-panel/) are never bypassed. Type: boolean. Default: `true`.
* `should_force_disable_cloud_handoff` — Whether to force-disable [local-to-cloud handoff](/platform/handoff/local-to-cloud/). Type: boolean. Default: `false`.
* `should_force_disable_ampersand_handoff` — Whether to force-disable the `&` prefix that composes a prompt for cloud handoff. Type: boolean. Default: `false`.
### Third-party (CLI agents)
[Section titled “Third-party (CLI agents)”](#third-party-cli-agents)
**Section**: `[agents.third_party]`
* `should_render_cli_agent_toolbar` — Whether to show the CLI agent footer for coding agent commands. Type: boolean. Default: `true`.
* `auto_toggle_composer` — Whether CLI agent Rich Input automatically closes and reopens based on the agent’s blocked state. Type: boolean. Default: `true`.
* `auto_open_composer_on_cli_agent_start` — Whether CLI agent Rich Input automatically opens when a CLI agent session starts. Type: boolean. Default: `false`.
* `auto_dismiss_composer_after_submit` — Whether CLI agent Rich Input automatically closes after the user submits a prompt. Type: boolean. Default: `false`.
* `cli_agent_toolbar_chip_selection_setting` — Controls the layout of context chips in the CLI Agent toolbar. Type: string or object. Default: `"default"`.
* `cli_agent_toolbar_enabled_commands` — Maps custom toolbar command patterns to specific CLI agents. Type: object. Default: `{}`.
* `submit_on_ctrl_enter` — Whether the CLI agent Rich Input editor submits on `Ctrl+Enter` instead of `Enter` (with `Enter` inserting a newline). Type: boolean. Default: `false`.
### Voice
[Section titled “Voice”](#voice)
**Section**: `[agents.voice]`
* `voice_input_enabled` — Controls whether voice input is enabled for AI interactions. Type: boolean. Default: `true`.
* `voice_input_toggle_key` — The key used to toggle voice input. Type: string. Default: `"none"`. Options: `"none"`, `"fn"`, `"alt_left"`, `"alt_right"`, `"control_left"`, `"control_right"`, `"super_left"`, `"super_right"`, `"shift_left"`, `"shift_right"`.
* `voice_input_language` — Preferred spoken language for voice input transcription, as a two-letter ISO 639-1 code (for example, `"es"`). Type: string. Default: `""` (auto-detect).
## Code
[Section titled “Code”](#code)
Settings for Warp’s built-in code editor, file handling, and codebase indexing.
**Section**: `[code]`
### Editor
[Section titled “Editor”](#editor)
**Section**: `[code.editor]`
* `open_file_editor` — The editor used to open files. Type: string or object. Default: `"system_default"`. Options: `"system_default"`, `"warp"`, `"env_editor"`, or an external editor object such as `{ external_editor = "v_s_code" }`. Supported external editors: VS Code (`v_s_code`), VS Code Insiders (`v_s_code_insiders`), PyCharm (`py_charm`), IntelliJ IDEA (`intelli_j`), CLion (`c_lion`), RustRover (`rust_rover`), Sublime Text 4 (`sublime4`), Zed (`zed`), Cursor (`cursor`), Windsurf (`windsurf`), and others.
* `open_code_panels_file_editor` — The editor used to open files from code panels. Type: string or object. Default: `"warp"`.
* `open_file_layout` — The layout used when opening files in the editor. Type: string. Default: `"split_pane"`. Options: `"split_pane"`, `"new_tab"`.
* `prefer_markdown_viewer` — Whether to use the Markdown viewer when opening Markdown files. Type: boolean. Default: `true`.
* `prefer_tabbed_editor_view` — Whether to prefer opening files in a tabbed editor view. Type: boolean. Default: `true`.
* `show_code_review_button` — Whether to show the code review button on tabs. Type: boolean. Default: `true`.
* `auto_open_code_review_pane_on_first_agent_change` — Whether to automatically open the code review pane when the agent makes its first change. Type: boolean. Default: `false`.
* `show_code_review_diff_stats` — Whether to show lines added/removed counts on the code review button. Type: boolean. Default: `true`.
* `show_project_explorer` — Whether the project explorer is shown in the tools panel. Type: boolean. Default: `true`.
* `show_global_search` — Whether global file search is shown in the tools panel. Type: boolean. Default: `true`.
* `show_hidden_files` — Whether hidden files (dotfiles) are shown in the project explorer. Type: boolean. Default: `true`.
* `use_warp_as_default_editor` — Whether Warp is used as the default code editor. Type: boolean. Default: `false`.
* `format_on_save` — Whether the language server automatically formats the file on save. Other LSP features (hover, go-to-definition, references, diagnostics) are unaffected. Type: boolean. Default: `true`.
* `auto_save` — Whether the Warp text editor automatically saves changes as you type and when the editor loses focus. Type: boolean. Default: `false`.
### Indexing
[Section titled “Indexing”](#indexing)
**Section**: `[code.indexing]`
* `agent_mode_codebase_context` — Whether Codebase Context is provided to the agent. Type: boolean. Default: `true`.
* `agent_mode_codebase_context_auto_indexing` — Whether automatic codebase indexing is enabled. Type: boolean. Default: `false`.
## Keys
[Section titled “Keys”](#keys)
Keyboard behavior settings.
**Section**: `[keys]`
* `ctrl_tab_behavior_setting` — Controls the behavior of `Ctrl+Tab`. Type: string. Default: `"activate_prev_next_tab"`. Options: `"activate_prev_next_tab"`, `"cycle_most_recent_session"`.
## Notifications
[Section titled “Notifications”](#notifications)
Settings that control desktop notification behavior.
**Section**: `[notifications]`
* `toast_duration_secs` — How long notification toasts are displayed, in seconds. Type: integer. Default: `8`.
### Preferences
[Section titled “Preferences”](#preferences)
**Section**: `[notifications.preferences]`
* `mode` — Whether notifications are enabled, disabled, or not yet configured. Type: string. Default: `"unset"`. Options: `"unset"`, `"dismissed"`, `"enabled"`, `"disabled"`.
* `is_long_running_enabled` — Whether to notify when a long-running command completes. Type: boolean. Default: `true`.
* `long_running_threshold` — Threshold in seconds for long-running command notifications. Type: integer. Default: `30`.
* `is_agent_task_completed_enabled` — Whether to notify when an agent task completes. Type: boolean. Default: `true`.
* `is_needs_attention_enabled` — Whether to notify when a session needs attention. Type: boolean. Default: `true`.
* `is_password_prompt_enabled` — Whether to notify when a password prompt is detected. Type: boolean. Default: `true`.
* `play_notification_sound` — Whether to play a sound with notifications. Type: boolean. Default: `true`.
## Privacy
[Section titled “Privacy”](#privacy)
Settings that control telemetry, crash reporting, and secret redaction.
**Section**: `[privacy]`
* `telemetry_enabled` — Whether anonymous usage telemetry is collected. Type: boolean. Default: `true`.
* `crash_reporting_enabled` — Whether crash reports are sent. Type: boolean. Default: `true`.
* `custom_secret_regex_list` — Custom regex patterns for detecting and redacting secrets. Type: array of objects. Default: `[]`.
Each item in `custom_secret_regex_list` has the format:
```toml
[[privacy.custom_secret_regex_list]]
pattern = "sk-[A-Za-z0-9]{48}"
name = "OpenAI API key"
```
### Secret redaction
[Section titled “Secret redaction”](#secret-redaction)
**Section**: `[privacy.secret_redaction]`
* `enabled` — Whether secret redaction is enabled to detect and obscure secrets in terminal output. Type: boolean. Default: `false`.
* `hide_secrets_in_block_list` — Whether to hide detected secrets in the block list using asterisks. Type: boolean. Default: `false`.
* `secret_display_mode_setting` — Controls how detected secrets are visually displayed. Type: string. Default: `"strikethrough"`. Options: `"asterisks"`, `"strikethrough"`, `"always_show"`.
## System
[Section titled “System”](#system)
Low-level system and rendering settings.
**Section**: `[system]`
* `prefer_low_power_gpu` — Whether to prefer the integrated (low-power) GPU. Type: boolean. Default: `false`.
* `preferred_graphics_backend` — The preferred graphics backend (Windows). Type: string or null. Default: `null`. Options: `"dx12"`, `"vulkan"`, `"gl"`, `"metal"`, `null`.
* `linux_selection_clipboard` — Whether the Linux primary selection clipboard is used. Type: boolean. Default: `true`.
* `force_x11` — Whether to force X11 instead of Wayland on Linux. Type: boolean. Default: `true` (`false` under WSL).
## Text editing
[Section titled “Text editing”](#text-editing)
Settings that control text editing behavior in the input editor.
**Section**: `[text_editing]`
* `code_editor_line_number_mode` — How line numbers are displayed in code editors. Type: string. Default: `"absolute"`. Options: `"absolute"`, `"relative"`.
* `vim_mode_enabled` — Whether Vim keybindings are enabled. Type: boolean. Default: `false`.
* `vim_status_bar` — Whether the Vim status bar is displayed. Type: boolean. Default: `true`.
* `vim_unnamed_system_clipboard` — Whether the Vim unnamed register uses the system clipboard. Type: boolean. Default: `false`.
* `autocomplete_symbols` — Whether matching symbols like brackets and quotes are auto-completed. Type: boolean. Default: `true`.
## Experimental
[Section titled “Experimental”](#experimental)
Opt-in settings for features that are still being refined.
**Section**: `[experimental]`
* `async_find_enabled` — Use an improved implementation of find that keeps the UI responsive while searching large outputs. Type: boolean. Default: `false`.
## Warp Drive
[Section titled “Warp Drive”](#warp-drive)
Settings for Warp Drive (shared workflows, notebooks, and prompts).
**Section**: `[warp_drive]`
* `enabled` — Whether Warp Drive is enabled. Type: boolean. Default: `true`.
* `sorting_choice` — The sort order for items in Warp Drive. Type: string. Default: `"by_object_type"`. Options: `"by_timestamp"`, `"alphabetical_descending"`, `"alphabetical_ascending"`, `"by_object_type"`.
## Warpify
[Section titled “Warpify”](#warpify)
Settings for Warp features in SSH sessions and subshells.
### SSH
[Section titled “SSH”](#ssh)
**Section**: `[warpify.ssh]`
* `enable_ssh_warpification` — Whether to enable Warp features in SSH sessions. Type: boolean. Default: `true`.
* `enable_legacy_ssh_wrapper` — Has no effect on Warp’s current behavior; retained only for a one-time migration to `enable_ssh_warpification`. Type: boolean. Default: `true`.
* `use_ssh_tmux_wrapper` — Has no effect on Warp’s current behavior now that tmux-based Warpification has been removed in favor of the [SSH extension](/terminal/warpify/ssh/); retained only for a one-time migration. Type: boolean. Default: `false`.
* `reuse_existing_control_master` — Whether the legacy SSH wrapper attaches to an existing SSH `ControlMaster` for the destination host instead of always creating its own. Type: boolean. Default: `false`.
* `ssh_extension_install_mode` — Controls SSH extension installation behavior. Type: string. Default: `"always_ask"`. Options: `"always_ask"` (always prompt before installing), `"always_install"` (auto-install and connect without prompting), `"never_install"` (fall back to the legacy, wrapper-only SSH warpification).
* `ssh_hosts_denylist` — SSH hosts that should not trigger the warpification prompt. Type: array of strings. Default: `[]`.
### Subshells
[Section titled “Subshells”](#subshells)
**Section**: `[warpify.subshells]`
* `added_subshell_commands` — Additional regex patterns for commands that should be recognized as subshells. Type: array of strings. Default: `[]`.
* `subshell_commands_denylist` — Commands that should not trigger the subshell warpification prompt. Type: array of strings. Default: `[]`.
## Workflows
[Section titled “Workflows”](#workflows)
Settings for workflow behavior.
**Section**: `[workflows]`
* `show_global_workflows_in_universal_search` — Whether to show global workflows in universal search results. Type: boolean. Default: `false`.
## Accessibility
[Section titled “Accessibility”](#accessibility)
Settings for screen reader support.
**Section**: `[accessibility]`
* `accessibility_verbosity` — The verbosity level for screen reader announcements. Type: string. Default: `"verbose"`. Options: `"verbose"` (includes help string), `"concise"` (value only).
## Account
[Section titled “Account”](#account)
Settings related to your Warp account.
**Section**: `[account]`
* `is_settings_sync_enabled` — Whether settings are synced across devices via the cloud. Type: boolean. Default: `false`.
## Cloud platform
[Section titled “Cloud platform”](#cloud-platform)
Settings for third-party API key integration and cloud model configuration.
### Third-party API keys
[Section titled “Third-party API keys”](#third-party-api-keys)
**Section**: `[cloud_platform.third_party_api_keys]`
* `aws_bedrock_credentials_enabled` — Whether Warp should use your local AWS credentials for Bedrock-enabled requests. Type: boolean. Default: `false`.
* `aws_bedrock_profile` — The AWS profile name to use for Bedrock credentials. Type: string. Default: `"default"`.
* `aws_bedrock_auto_login` — Whether to automatically run the AWS login command when Bedrock credentials expire. Type: boolean. Default: `false`.
* `aws_bedrock_auth_refresh_command` — The command to run to refresh AWS credentials for Bedrock. Type: string. Default: `"aws login"`.
* `gemini_enterprise_credentials_enabled` — Whether Warp routes eligible requests through your workspace’s Gemini Enterprise Google Cloud project. Requires a workspace admin to configure Gemini Enterprise. Type: boolean. Default: `false`.
* `can_use_warp_credits_with_byok` — Whether Warp credits can be used even when providing your own API key. Type: boolean. Default: `false`.
## Global hotkey
[Section titled “Global hotkey”](#global-hotkey)
Settings for the global activation hotkey and dedicated hotkey window (Quake Mode).
### Toggle all windows
[Section titled “Toggle all windows”](#toggle-all-windows)
**Section**: `[global_hotkey.toggle_all_windows]`
* `enabled` — Whether the hotkey that toggles visibility of all windows is enabled. Mutually exclusive with `global_hotkey.dedicated_window.enabled`. Type: boolean. Default: `false`.
* `keybinding` — The keybinding for the global activation hotkey. Format: modifiers and a key joined by `-`, for example `"cmd-shift-a"` or `"alt-enter"`. Type: string or null. Default: `null`.
### Dedicated window (Quake Mode)
[Section titled “Dedicated window (Quake Mode)”](#dedicated-window-quake-mode)
**Section**: `[global_hotkey.dedicated_window]`
* `enabled` — Whether the dedicated hotkey window is enabled. Mutually exclusive with `global_hotkey.toggle_all_windows.enabled`. Type: boolean. Default: `false`.
**Section**: `[global_hotkey.dedicated_window.settings]`
* `active_pin_position` — Screen edge where the hotkey window is pinned. Type: string. Options: `"top"`, `"bottom"`, `"left"`, `"right"`.
* `hide_window_when_unfocused` — Whether to hide the hotkey window when it loses focus. Type: boolean.
* `keybinding` — Keyboard shortcut to toggle the hotkey window. Type: string or null.
* `pin_screen` — Display to pin the hotkey window to. Type: string or object or null. Options: `"primary"`, `{ external = 1 }`, `null`.
Window size percentages are configured per pin position:
```toml
[global_hotkey.dedicated_window]
enabled = true
[global_hotkey.dedicated_window.settings]
active_pin_position = "top"
hide_window_when_unfocused = true
keybinding = "ctrl-`"
[global_hotkey.dedicated_window.settings.pin_position_to_size_percentages.top]
width = 100
height = 30
[global_hotkey.dedicated_window.settings.pin_position_to_size_percentages.bottom]
width = 100
height = 30
[global_hotkey.dedicated_window.settings.pin_position_to_size_percentages.left]
width = 40
height = 100
[global_hotkey.dedicated_window.settings.pin_position_to_size_percentages.right]
width = 40
height = 100
```
# File and folder locations
Canonical page: [/terminal/settings/file-locations/](https://docs.warp.dev/terminal/settings/file-locations/)
> Reference for where Warp stores config, themes, tab configs, settings, keybindings, logs, and other files on macOS, Windows, and Linux.
This reference lists every directory and file Warp reads or writes on disk, organized by platform and Warp release channel. Use it when you want to back up your config, edit a file directly, debug a missing setting, or symlink Warp’s configuration from another shell (for example, [WSL](#symlinking-warps-config-from-wsl)).
## How Warp organizes files
[Section titled “How Warp organizes files”](#how-warp-organizes-files)
Warp groups its files into three buckets, and the directory each bucket maps to depends on your platform. Knowing the bucket explains why two files that feel related (themes and settings, for example) live in different roots on Windows and Linux but the same root on macOS.
* **Portable user data** - Files you’d want to copy to a new machine, such as themes, tab configs, workflows, and launch configurations.
* **Non-portable config** - Local-only configuration that doesn’t make sense to roam, such as `settings.toml` and `keybindings.yaml`.
* **Non-portable state** - Machine-specific state like logs, the local database, and the Codebase Context index.
In addition, a small set of cross-cutting files always live in your home directory on every platform — currently MCP server config and bundled skills. Both Stable and Preview share the same `~/.warp/` directory for these files (Preview does **not** use `~/.warp-preview/` for MCP config or skills, so installing Preview alongside Stable shares the same MCP servers and skills). Other release channels do use a channel-suffixed directory — for example, `~/.warp-oss/` for OSS. These files sit in the home directory so they’re easy to reference from shell config, version control, or other tools.
## File locations by platform
[Section titled “File locations by platform”](#file-locations-by-platform)
The tables below cover the **Stable** channel. For **Preview**, see [Preview channel paths](#preview-channel-paths).
* macOS
On macOS, Stable keeps every Warp-authored file under `~/.warp/`. Preview uses `~/.warp-preview/` for everything except the cross-platform `~/.warp/` carve-out.
**Portable user data**
* **Themes** - `~/.warp/themes/`
* **Tab configs** - `~/.warp/tab_configs/`
* **Default tab configs** (shipped, user-editable) - `~/.warp/default_tab_configs/`
* **Workflows** (local) - `~/.warp/workflows/`
* **Launch configurations** - `~/.warp/launch_configurations/`
**Non-portable config**
* **Settings file** - `~/.warp/settings.toml`
* **Keybindings** - `~/.warp/keybindings.yaml`
* **User preferences** (legacy) - macOS `defaults` domain `dev.warp.Warp-Stable`
**Non-portable state**
* **Logs** - `~/Library/Logs/warp.log*`
* **Crash reports** - `~/Library/Logs/DiagnosticReports/` (Warp `.ips` files)
* **Database, Codebase Context index, MCP logs** - `~/Library/Group Containers/2BBY89MBSN.dev.warp/Library/Application Support/dev.warp.Warp-Stable/`
**Cross-platform (always in your home directory)**
* **MCP server config** - `~/.warp/.mcp.json`
* **Bundled skills** - `~/.warp/skills/`
* **Agent config** - `~/.agents/`
* Windows
On Windows, Warp follows the platform conventions used by the [`directories`](https://docs.rs/directories) crate, which splits user data across `%APPDATA%` (Roaming) and `%LOCALAPPDATA%` (Local). Themes and tab configs are portable and live in Roaming, while settings, logs, and the local database are machine-specific and live in Local. Two separate `data\` directories exist as a result — one under each root — so check the full path when locating files.
**Portable user data** (`%APPDATA%\warp\Warp\data\`, Roaming)
* **Themes** - `%APPDATA%\warp\Warp\data\themes\`
* **Tab configs** - `%APPDATA%\warp\Warp\data\tab_configs\`
* **Default tab configs** (shipped, user-editable) - `%APPDATA%\warp\Warp\data\default_tab_configs\`
* **Workflows** (local) - `%APPDATA%\warp\Warp\data\workflows\`
* **Launch configurations** - `%APPDATA%\warp\Warp\data\launch_configurations\`
**Non-portable config** (`%LOCALAPPDATA%\warp\Warp\config\`)
* **Settings file** - `%LOCALAPPDATA%\warp\Warp\config\settings.toml`
* **Keybindings** - `%LOCALAPPDATA%\warp\Warp\config\keybindings.yaml`
* **User preferences** (legacy) - Windows Registry key `HKCU:\Software\Warp.dev\Warp`
**Non-portable state** (`%LOCALAPPDATA%\warp\Warp\data\`)
* **Logs** - `%LOCALAPPDATA%\warp\Warp\data\logs\warp.log*`
* **Database, Codebase Context index, MCP logs** - other subdirectories under `%LOCALAPPDATA%\warp\Warp\data\`
* **Cache** - `%LOCALAPPDATA%\warp\Warp\cache\`
**Cross-platform (always in your home directory)**
* **MCP server config** - `%USERPROFILE%\.warp\.mcp.json`
* **Bundled skills** - `%USERPROFILE%\.warp\skills\`
* **Agent config** - `%USERPROFILE%\.agents\`
* Linux
On Linux, Warp follows the [XDG Base Directory Specification](https://specifications.freedesktop.org/basedir-spec/basedir-spec-latest.html). Each path below uses the standard XDG environment variable with its default fallback.
**Portable user data** (`${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/`)
* **Themes** - `${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/themes/`
* **Tab configs** - `${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/tab_configs/`
* **Default tab configs** (shipped, user-editable) - `${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/default_tab_configs/`
* **Workflows** (local) - `${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/workflows/`
* **Launch configurations** - `${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/launch_configurations/`
**Non-portable config** (`${XDG_CONFIG_HOME:-$HOME/.config}/warp-terminal/`)
* **Settings file** - `${XDG_CONFIG_HOME:-$HOME/.config}/warp-terminal/settings.toml`
* **Keybindings** - `${XDG_CONFIG_HOME:-$HOME/.config}/warp-terminal/keybindings.yaml`
**Non-portable state** (`${XDG_STATE_HOME:-$HOME/.local/state}/warp-terminal/`)
* **Logs** - `${XDG_STATE_HOME:-$HOME/.local/state}/warp-terminal/warp.log*`
* **Database, Codebase Context index, MCP logs** - other files under `${XDG_STATE_HOME:-$HOME/.local/state}/warp-terminal/`
* **Cache** - `${XDG_CACHE_HOME:-$HOME/.cache}/warp-terminal/`
**Cross-platform (always in your home directory)**
* **MCP server config** - `~/.warp/.mcp.json`
* **Bundled skills** - `~/.warp/skills/`
* **Agent config** - `~/.agents/`
## Preview channel paths
[Section titled “Preview channel paths”](#preview-channel-paths)
Preview uses a separate set of directories so it never overwrites your Stable config:
* **macOS** - Replace `~/.warp/` with `~/.warp-preview/` and `Warp-Stable` with `Warp-Preview` in the macOS paths above. The cross-platform `~/.warp/` carve-out (MCP config, skills) is shared with Stable and does not get a `-preview` suffix.
* **Windows** - Replace `\warp\Warp\` with `\warp\WarpPreview\` in every path. Logs become `%LOCALAPPDATA%\warp\WarpPreview\data\logs\warp_preview.log*`. The Registry key is `HKCU:\Software\Warp.dev\WarpPreview` (no hyphen — `Warp-Preview` is the macOS bundle identifier, not the Windows app name). The cross-platform `%USERPROFILE%\.warp\` carve-out (MCP config, skills) is shared with Stable.
* **Linux** - Append `-preview` to each `warp-terminal` directory (for example, `~/.config/warp-terminal-preview/settings.toml`). Logs become `${XDG_STATE_HOME:-$HOME/.local/state}/warp-terminal-preview/warp_preview.log*`. The cross-platform `~/.warp/` carve-out (MCP config, skills) is shared with Stable.
## Symlinking Warp’s config from WSL
[Section titled “Symlinking Warp’s config from WSL”](#symlinking-warps-config-from-wsl)
If you run Warp on Windows and also use WSL, you can share Warp’s config with your WSL `$HOME` so that tools running inside WSL can read the same themes, tab configs, settings, MCP servers, and agent config. WSL `$HOME` (typically `/home/<wsl-user>/`) is a separate Linux filesystem from your Windows profile (`%USERPROFILE%`, typically `C:\Users\<Windows-user>\`), so `~/.warp/` and `~/.agents/` inside WSL are **not** automatically the same as the Windows-side directories with those names — every Warp directory you want to share needs its own symlink that points back to the Windows path.
Your WSL Linux username (`$USER`) is also usually different from your Windows account name, so don’t assume `/mnt/c/Users/$USER` resolves to your Windows profile. Resolve `%USERPROFILE%` through `cmd.exe` and convert it with `wslpath` instead, then run the symlinks from a WSL shell:
```bash
# Resolve the Windows %USERPROFILE% (e.g. C:\Users\Alex) into a WSL path
# (e.g. /mnt/c/Users/Alex). Avoids hard-coding the Windows username or
# assuming it matches your WSL $USER.
WIN_HOME=$(wslpath "$(cmd.exe /C 'echo %USERPROFILE%' 2>/dev/null | tr -d '\r')")
# Portable data: themes, tab configs, workflows, launch configurations (Roaming AppData).
ln -s "$WIN_HOME/AppData/Roaming/warp/Warp/data" ~/.warp-windows-data
# Local config: settings.toml, keybindings.yaml (Local AppData).
ln -s "$WIN_HOME/AppData/Local/warp/Warp/config" ~/.warp-windows-config
# Cross-platform carve-outs that live under Windows %USERPROFILE%:
# MCP server config and bundled skills (Windows-side ~/.warp).
ln -s "$WIN_HOME/.warp" ~/.warp
# Agent config (Windows-side ~/.agents).
ln -s "$WIN_HOME/.agents" ~/.agents
```
If `~/.warp` or `~/.agents` already exist in WSL, remove or back them up first — otherwise `ln` will create the link inside the existing directory instead of replacing it. If you prefer to hard-code the Windows username instead of using `wslpath`, find it from WSL with `cmd.exe /C 'echo %USERNAME%' 2>/dev/null | tr -d '\r'` and replace `$WIN_HOME` above with `/mnt/c/Users/<your-windows-username>`.
Note
Warp on Windows does not currently load config from `~/.warp/tab_configs/` or `~/.warp/themes/` — those paths only work on macOS. If you have config files in those home-directory paths from a different machine, copy or symlink them into the Windows `%APPDATA%\warp\Warp\data\` directory before they take effect.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Settings file](/terminal/settings/) - Format, hot-reload behavior, and common examples for `settings.toml`.
* [All settings reference](/terminal/settings/all-settings/) - Every setting available in `settings.toml`, organized by section.
* [Keyboard shortcuts](/getting-started/keyboard-shortcuts/) - How to view and remap shortcuts, including the `keybindings.yaml` file.
* [Tab Configs](/terminal/windows/tab-configs/) - TOML format and schema for tab config files in `tab_configs/`.
* [Custom themes](/terminal/appearance/custom-themes/) - YAML format and image conventions for themes in `themes/`.
* [Uninstalling Warp](/support-and-community/troubleshooting-and-support/logging-out-and-uninstalling/) - Commands for removing all of these files when uninstalling.
# Warpify overview
Canonical page: [/terminal/warpify/](https://docs.warp.dev/terminal/warpify/)
> Warp support for Warpifying, or enabling Warp's features, in local or remote sessions.
1. [Subshells](/terminal/warpify/subshells/), Warp supports enabling Warp features in subshells for bash, zsh, and fish.
2. [SSH](/terminal/warpify/ssh/), Warp’s SSH extension brings the file tree, code editing, code review, and reliable completions to remote macOS and Linux hosts, including a [legacy fallback wrapper](/terminal/warpify/ssh-legacy/) for hosts or settings that skip the extension.
## Subshells
[Section titled “Subshells”](#subshells)
[](/assets/terminal/subshells-demo.mp4)
## SSH
[Section titled “SSH”](#ssh)
[](/assets/terminal/subshell-ssh-demo.mp4)
# SSH with Warp features
Canonical page: [/terminal/warpify/ssh/](https://docs.warp.dev/terminal/warpify/ssh/)
> Use Warp's SSH extension on remote macOS and Linux hosts for a real file tree, code editing, code review, codebase indexing, and reliable completions over SSH.
Warp’s **SSH extension** brings the local Warp experience to remote macOS and Linux hosts. After you opt in on first connect, you get a real file tree backed by the remote filesystem, Warp’s code editor and code review on remote files, codebase indexing for the remote repo, and a coding agent that applies edits with Warp’s native diff tool instead of falling back to `sed`.
[SSH extension demo](https://www.loom.com/embed/466d88a1968842c68f66a3b66b94f146)
## How it works
[Section titled “How it works”](#how-it-works)
When you connect to a remote host and accept the install prompt, Warp installs a small companion server in your home directory on the remote machine. The server runs in the background as your user and communicates with Warp over your existing SSH connection. It doesn’t open any network ports, doesn’t require root, and doesn’t change anything outside your home directory.
The server does the heavy lifting directly on the remote machine: it reads and writes files, watches your repository for changes, runs git commands, and indexes your codebase. Only lightweight, incremental updates stream back to Warp — an edit, a diff, a status change — instead of full file contents round-tripped through shell commands. This keeps the connection fast while features like the file tree, code review, and the Agent’s file tools behave the same as they do locally.
A few properties worth knowing:
* **One server, many sessions** - Multiple SSH sessions and Warp windows connected to the same host share a single server process.
* **Automatic updates** - The extension version tracks your Warp version. When you connect to a host with an outdated extension, Warp automatically installs the matching version.
* **Easy to remove** - Uninstall by deleting the `~/.warp*/remote-server` directory on the remote host.
## What you get over SSH
[Section titled “What you get over SSH”](#what-you-get-over-ssh)
Once the SSH extension is installed on a remote host, most of Warp’s coding features work the same way they do locally. See [Feature support over SSH](/code/ssh-feature-support/) for the full breakdown of what’s included and what isn’t. Headline features include a real file tree backed by the remote filesystem, Warp’s code editor and code review on remote files, codebase indexing for the remote repo, and native code diffs applied through Warp’s built-in diff tool instead of `sed`. Core terminal features like the input editor, blocks, and completions also work the same as they do locally.
## Requirements
[Section titled “Requirements”](#requirements)
The SSH extension has the following requirements on the remote host:
* **Operating system** - Linux or macOS. Windows remote hosts are not supported. The extension is also not available from Warp’s Windows client.
* **Architecture** - `x86_64` (amd64) or `aarch64` (arm64).
* **glibc 2.31 or newer (Linux)** - The prebuilt server binary requires glibc 2.31+ (Ubuntu 20.04 or equivalent). Hosts with an older glibc (for example RHEL/CentOS 7 and 8, Amazon Linux 2, Ubuntu 18.04, Debian 10) or a non-glibc libc (for example Alpine’s musl) are not supported. Warp detects this before installing anything and quietly falls back to the [legacy SSH wrapper](/terminal/warpify/ssh-legacy/).
* **Shell** - `bash` or `zsh` as the remote shell.
* **Home directory and Unix sockets** - The install writes only under `~/.warp*/`, so your home directory must be writable. The server also needs to create Unix domain sockets under your home directory and run as a background process under your user.
* **Outbound HTTPS for install** - The install script downloads the server binary from `app.warp.dev` using `curl` or `wget`, so the host needs outbound HTTPS access to `app.warp.dev`. If neither `curl` nor `wget` is available, Warp uploads the binary over the SSH connection instead.
* **Outbound HTTPS for account-backed features** - Features that use your Warp account, such as codebase indexing and AI-generated commit messages, require the server on the remote host to reach Warp’s servers over HTTPS. The server authenticates with credentials forwarded from your local Warp session over the SSH connection; you never log in on the remote host. Core features like the file tree, file reads and edits, and completions work without any outbound access from the host.
When a host doesn’t meet these requirements, or when [SSH extension install mode](/terminal/settings/all-settings/#ssh) is set to **Never install**, Warp falls back to the [legacy SSH wrapper](/terminal/warpify/ssh-legacy/).
Note
We are actively working on extending support to older glibc versions and more operating systems.
## Installing the SSH extension
[Section titled “Installing the SSH extension”](#installing-the-ssh-extension)
On the first SSH connection to a host that doesn’t already have the SSH extension installed, Warp shows an in-block prompt with two options:
* **Install Warp’s SSH extension** - Recommended. Warp downloads the matching remote server extension for the remote OS and architecture, installs it under `~/.warp/remote-server` (or `~/.warp-preview/remote-server` on Preview builds), launches it, and completes the handshake. Subsequent connections to the same host skip the prompt and reuse the installed binary.
* **Continue without installing** - Skip installing the extension for this connection. The session continues without the SSH extension, so file tree, native file reads, and native code diffs are unavailable until you install. You can reconnect and install at any time.
Warp never installs anything on a remote host without your explicit consent, and the install only writes under `~/.warp*/`.
Note
The extension binary tracks your client’s release channel. Stable Warp installs the extension under `~/.warp/remote-server`, and Preview installs it under `~/.warp-preview/remote-server`, so both channels can coexist on the same remote host.
### Managing the install prompt
[Section titled “Managing the install prompt”](#managing-the-install-prompt)
In the Warp app, go to **Settings** > **Warpify** to control how the prompt behaves:
* **Always ask** (default) - Show the install prompt the first time you connect to each host.
* **Always install** - Skip the prompt and install the extension automatically when it’s missing.
* **Never install** - Skip the prompt and connect to the host without installing the SSH extension.
The same setting can also be changed inline from the install prompt by selecting **Don’t ask me this again** before clicking either button. The underlying TOML key is `warpify.ssh.ssh_extension_install_mode` - see [All settings reference](/terminal/settings/all-settings/#ssh) for the full list of SSH-related settings, including `ssh_hosts_denylist` for hosts you never want to engage Warpification on.
## Legacy: tmux-based Warpification
[Section titled “Legacy: tmux-based Warpification”](#legacy-tmux-based-warpification)
Tmux-based Warpification was an older approach to enabling Warp features in SSH sessions that used [`tmux`](https://github.com/tmux/tmux/wiki) to multiplex commands over your SSH connection. It has been removed in favor of the SSH extension described on this page.
## FAQs
[Section titled “FAQs”](#faqs)
### Will Warpifying a remote SSH session make changes to the remote machine?
[Section titled “Will Warpifying a remote SSH session make changes to the remote machine?”](#will-warpifying-a-remote-ssh-session-make-changes-to-the-remote-machine)
Only with your explicit permission. The SSH extension installs the remote server extension under `~/.warp*/remote-server`. Warp shows you exactly what it’s going to run, and you can always decline and continue using SSH without these features.
### Can I SSH to remote machines that I don’t want to Warpify?
[Section titled “Can I SSH to remote machines that I don’t want to Warpify?”](#can-i-ssh-to-remote-machines-that-i-dont-want-to-warpify)
Yes. Cancel the prompt to continue without Warp features, or add the host to the denylist (**Settings** > **Warpify** > **SSH hosts denylist**) so you’re never prompted again.
### Do I have to manually Warpify every time?
[Section titled “Do I have to manually Warpify every time?”](#do-i-have-to-manually-warpify-every-time)
After you successfully Warpify an SSH connection manually, Warp provides a brief script you can run to append a marker at the end of your shell’s rcfile. This lets Warp know when your remote shell is ready to be Warpified. Place the snippet at the bottom of your rcfile for the best results.
### What shells and operating systems are supported?
[Section titled “What shells and operating systems are supported?”](#what-shells-and-operating-systems-are-supported)
Warp supports macOS and most flavors of Linux as remote hosts. Supported shells are `bash` and `zsh`. Windows remote hosts are not yet supported. See [Requirements](#requirements) for the full list.
### What if Warp fails to detect my SSH session?
[Section titled “What if Warp fails to detect my SSH session?”](#what-if-warp-fails-to-detect-my-ssh-session)
If you’re in a remote SSH session and Warp didn’t detect it, first check that **Settings** > **Warpify** > **Warpify SSH Sessions** is enabled. If it’s already on, Warp likely skipped detection for that particular command. See [What triggers SSH session detection for Warpification?](#what-triggers-ssh-session-detection-for-warpification) for the cases Warp doesn’t detect.
### What triggers SSH session detection for Warpification?
[Section titled “What triggers SSH session detection for Warpification?”](#what-triggers-ssh-session-detection-for-warpification)
With SSH session detection enabled, Warp watches for `ssh` commands whose arguments suggest an interactive session. If you’ve aliased `ssh` or are running it as part of a script, Warp won’t perform SSH session detection.
Once Warp is confident you’ve successfully authenticated (by detecting `Last login:` or something resembling a basic prompt), it prompts you to Warpify the active SSH session.
If SSH session detection doesn’t pick up your session, see [What if Warp fails to detect my SSH session?](#what-if-warp-fails-to-detect-my-ssh-session).
# Legacy SSH wrapper
Canonical page: [/terminal/warpify/ssh-legacy/](https://docs.warp.dev/terminal/warpify/ssh-legacy/)
> Use the legacy SSH wrapper as a fallback when skipping the SSH extension or when it can't run on a remote host.
Note
This is a fallback path. For the current, fully-featured way to use Warp over SSH, see the [SSH extension](/terminal/warpify/ssh/).
The legacy SSH wrapper brings a subset of Warp’s features, such as Blocks, the input editor, and command completions, to a remote session without installing anything on the remote host. Warp falls back to it when [SSH extension install mode](/terminal/settings/all-settings/#ssh) is set to **Never install**, or when a host doesn’t meet the SSH extension’s [requirements](/terminal/warpify/ssh/#requirements).
Caution
Limitations of the legacy SSH wrapper:
* Warp preserves the remote login shell. It adds the enhanced Warp bootstrap to `bash` and `zsh` sessions; other shells continue without those enhancements.
* For zsh, `xxd` is required to bootstrap Warp. Warp creates a temporary ZDOTDIR to bootstrap the shell and removes it once setup finishes.
* For Windows, [Cygwin](https://www.cygwin.com/) is required to bootstrap the SSH wrapper.
* `RemoteCommand` in your SSH config causes the SSH wrapper to fail.
A remote session bootstrapped by the legacy SSH wrapper.
## Implementation
[Section titled “Implementation”](#implementation)
We create a wrapper around `/usr/bin/ssh` to set up supported remote shells for Warp’s feature set. We authenticate normally using `/usr/bin/ssh`, preserve the remote login shell, and enhance `bash` or `zsh` for Warp Blocks and the Input Editor. Other shells continue without the enhanced bootstrap. You can opt out of the wrapper by invoking `command ssh` directly.
* Warp takes over the prompt which enables us to build a modern input editor.
* Warp configures histcontrol to ignore commands with leading spaces. We do this so our bootstrapping code does not clutter the history.
You can see the SSH wrapper by using `which warp_ssh_helper` in zsh, `type warp_ssh_helper` in bash.
*Note:* The SSH wrapper is only *initialized* on your local machine. We don’t currently support bootstrapping nested ssh sessions.
Note
Warp [Completions](/terminal/command-completions/completions/) for ssh show entries in `~/.ssh/config` and `~/.ssh/known_hosts`
## Troubleshooting SSH
[Section titled “Troubleshooting SSH”](#troubleshooting-ssh)
### channel 2: open failed: connect failed: open failed
[Section titled “channel 2: open failed: connect failed: open failed”](#channel-2-open-failed-connect-failed-open-failed)
If you’re seeing these errors, you may have some config on your server (usually in `/etc/ssh/sshd_config`) preventing Warp’s ControlMaster connection from working. In this state, completions that require information from your remote host won’t work and your history also won’t work.
`MaxSessions` must be either commented out or set to at least `2`.
Write access in `/etc/ssh/` typically requires sudo access. After any edits, you’d also need to restart the `sshd` daemon.
### SSH wrapper fails
[Section titled “SSH wrapper fails”](#ssh-wrapper-fails)
There are several [known issues with the SSH wrapper](https://github.com/warpdotdev/Warp/issues?q=is%3Aissue+is%3Aopen+sort%3Acreated-desc+label%3ABugs+label%3ASSH). As a workaround, add `command ssh` to **Settings** > **Warpify** > **Subshells** > **Added commands**, then run `command ssh <user@server>` to connect. Warp then tries to enable features as a [subshell](/terminal/warpify/subshells/) instead of through the SSH wrapper.
[](/assets/terminal/subshell-ssh-demo.mp4)
# Warpify subshells
Canonical page: [/terminal/warpify/subshells/](https://docs.warp.dev/terminal/warpify/subshells/)
> Warpify subshells in bash, zsh, and fish to get Warp features in nested sessions.
## What is a subshell?
[Section titled “What is a subshell?”](#what-is-a-subshell)
Within the context of Warp, a “subshell” is defined as any nested interactive shell session that’s spawned and running within the context of an existing, running shell. This can be a nested session running locally on your machine, a shell session running within a Docker container, or a remote server accessed through SSH. [See more on SSH Warpification](/terminal/warpify/ssh/).
Note that Warp’s definition of a subshell differs from the more common definition of a Unix subshell, which typically refers to any shell process spawned as a child of the interactive shell. For example, in bash, a command wrapped in parentheses is executed in a subshell with its own PID and addressable memory space.
## How to Warpify the subshell
[Section titled “How to Warpify the subshell”](#how-to-warpify-the-subshell)
By default, Warp automatically recognizes the following commands as **subshell-compatible**:
* `bash`, `zsh`, `fish`
* `docker run` and `podman run` (when launching `bash`, `zsh`, or `fish`)
* `docker exec` and `podman exec` (when launching `bash`, `zsh`, or `fish`)
* `poetry shell`
* `pipenv shell`
* `aws-vault exec`
* `flox activate`
* `wsl` (Windows only, to enter a WSL distribution)
* `gcloud compute ssh`, `eb ssh`, and `doctl compute ssh`, recognized through the same SSH-like command detection used for [SSH Warpification](/terminal/warpify/ssh/)
When you run a command that’s subshell-compatible, Warp will prompt you and invite you to “Warpify” the subshell which makes all of the modern IDE features of Warp available in that subshell. The list of subshell-compatible commands is configurable in Subshell settings as described [below](/terminal/warpify/subshells/#configuring-subshell-compatible-commands).
Note
bash, zsh, or fish (3.6 or above) must be set as the default shell within containers and ssh sessions for the Warpification of the subshells to work.
[](/assets/terminal/subshells-demo.mp4)
### Configuring subshell-compatible commands
[Section titled “Configuring subshell-compatible commands”](#configuring-subshell-compatible-commands)
To configure subshell-compatible commands, navigate to **Settings** > **Warpify** > **Subshells**.
#### Adding compatible commands
[Section titled “Adding compatible commands”](#adding-compatible-commands)
You can add any command that spawns a bash, fish, or zsh subshell to ‘Added commands’ to make it eligible for “Warpification.”
Furthermore, you can add regular expressions to the Added commands list. Any commands that match an added regex will be eligible for “Warpification.”
#### Denylisting commands
[Section titled “Denylisting commands”](#denylisting-commands)
Some types of subshells are not compatible, and you may also want to control Warp so it never invites you to “Warpify” the subshells for specific commands. When you add commands to **Denylisted commands**, Warp will never invite you to “Warpify” subshells spawned by those commands.
### Automatically “Warpify” subshells
[Section titled “Automatically “Warpify” subshells”](#automatically-warpify-subshells)
To remember your preferences for a command and bypass the confirmation banner, you can manually paste the appropriate snippet to the end of the RC file corresponding to your subshell (bash, fish, or zsh).
```bash
# For zsh subshells, add to ~/.zshrc.
printf '\eP$f{"hook": "SourcedRcFileForWarp", "value": { "shell": "zsh"}}\x9c'
# For bash subshells, add to ~/.bashrc or ~/.bash_profile.
printf '\eP$f{"hook": "SourcedRcFileForWarp", "value": { "shell": "bash"}}\x9c'
# For fish subshells, add to ~/.config/fish/config.fish.
if status is-interactive
printf '\eP$f{"hook": "SourcedRcFileForWarp", "value": { "shell": "fish"}}\x9c'
end
```
Once added, Warp will automatically “Warpify” subsequent subshell sessions for the corresponding shell on the machine with the newly updated RC file.
Under the hood, this snippet prints a Device Control String ([DCS](https://vt100.net/docs/vt510-rm/chapter4.html)) to be read by Warp, signaling that a subshell session has started and is ready to be “Warpified.” In turn, Warp executes a setup script in the session that enables the full suite of Warp features like blocks, completions, and the input editor.
For this reason, it’s best to ensure the snippet is added to the end of the RC file, so Warp does not attempt to execute the setup script before the shell has finished sourcing your RC file.
To disable automatic integration, remove the snippet from the corresponding RC file.
If you encounter issues in subshell sessions where the RC file is sourced, [file a GitHub issue](https://github.com/warpdotdev/Warp/issues/new/choose).
## Background commands
[Section titled “Background commands”](#background-commands)
Warp runs background commands to power useful features like completions, syntax highlighting, and command corrections. For example, to provide completions for git checkout, Warp runs a background command that lists all git branches in the current repo.
In local subshell sessions, these commands are run in forked shell processes, isolated from your interactive shell session. This is the same implementation used for any non-subshell session.
In remote sessions, however, Warp takes a different approach – while a forked shell process is running on your local machine (where the Warp app is running), your remote session might be running on a server elsewhere. In these cases, Warp takes advantage of the session’s “idle time” – when no command is currently running – to run background commands directly in the session itself. These commands are executed in a non-interactive subshell process to prevent modifications to the session state (they cannot modify an environment variable, for instance).
### Show/hide background blocks
[Section titled “Show/hide background blocks”](#showhide-background-blocks)
By default, blocks for background commands are hidden. To show background command blocks, select ‘Show background blocks’ in the ‘Blocks’ menu of the macOS menu bar.
### Disable background commands in remote sessions
[Section titled “Disable background commands in remote sessions”](#disable-background-commands-in-remote-sessions)
We understand that some developers may want to disable background commands for certain or all environments.
To disable background commands in remote subshell sessions, you can execute the following command in a top-level terminal session:
* macOS
Update the settings defaults located in `dev.warp.Warp-Stable` to include the following name-value pair: `"DisableInBandCommands": "true"`.
```bash
defaults update dev.warp.Warp-Stable DisableInBandCommands true
```
* Windows
Update the settings registry located at `HKCU:\Software\Warp.dev\Warp` to include the following name-value pair: `"DisableInBandCommands": "true"`.
```powershell
Set-ItemProperty -Path "HKCU:\SOFTWARE\Warp.dev\Warp" -Name DisableInBandCommands -Value true
```
* Linux
Update the settings file located at `~/.config/warp-terminal/user_preferences.json` to include the following name-value pair: `"DisableInBandCommands": "true"`.
```bash
cd ~/.config/warp-terminal/
jq '.prefs += {"DisableInBandCommands": "true"}' user_preferences.json > tmp.json && mv tmp.json user_preferences.json
```
This will effectively disable tab completions, syntax highlighting, command corrections, and the git status prompt indicator in remote subshells.
# Windows and tabs overview
Canonical page: [/terminal/windows/](https://docs.warp.dev/terminal/windows/)
> Manage Warp windows, tabs, vertical tabs, split panes, and tab configurations with global hotkeys and reusable layouts.
1. [Tabs](/terminal/windows/tabs/) allow you to organize a window into multiple terminal sessions.
2. [Vertical Tabs](/terminal/windows/vertical-tabs/) replace the horizontal tab bar with a sidebar that shows rich metadata and drag-and-drop management for every tab and pane.
3. [Split Panes](/terminal/windows/split-panes/) allows you to divide a Tab into multiple rectangular *panes*, each of which is a unique terminal session.
4. [Tab Configs](/terminal/windows/tab-configs/) let you define reusable tab setups in a simple TOML file.
5. [Global Hotkey](/terminal/windows/global-hotkey/) is a configurable shortcut that can show/hide a dedicated window or all windows on your chosen desktop regardless of whether the app is focused.
6. [Launch Configurations (Legacy)](/terminal/sessions/launch-configurations/) support saving a configuration of windows, tabs, and panes to open later.
## Tabs
[Section titled “Tabs”](#tabs)
[Tabs Demo](https://www.loom.com/embed/84d15cc7eb5a4a668bb86be9e827f261)
## Split Panes
[Section titled “Split Panes”](#split-panes)
[Split Panes Demo](https://www.loom.com/embed/c1104b51cab848a9bef6792ec4fd8421)
## Global Hotkey
[Section titled “Global Hotkey”](#global-hotkey)
[](/assets/terminal/Dedicated-Window.mp4) [](/assets/terminal/Show-Hide-All-Windows.mp4)
# Configurable toolbar
Canonical page: [/terminal/windows/configurable-toolbar/](https://docs.warp.dev/terminal/windows/configurable-toolbar/)
> Reorder, hide, and move panel toggle buttons between the left and right sides of Warp's header toolbar to match your workflow.
The header toolbar holds the panel toggle buttons for the tabs panel, tools panel, agent management, Code Review, and notifications mailbox. Instead of a fixed layout, you can rearrange these buttons, move them between the left and right sides of the header, or hide the ones you don’t use. The side a button lives on also determines which side of the window its panel opens on, so you can tune Warp’s layout to match how you work.
The configurable toolbar works with both [horizontal tabs](/terminal/windows/tabs/) and [vertical tabs](/terminal/windows/vertical-tabs/).
[Configurable toolbar demo](https://www.loom.com/embed/292d126ecf7148f296fc8685e451790f)
## Key features
[Section titled “Key features”](#key-features)
* **Reorder items within a side** - Drag toolbar chips to change the left-to-right order on either side of the header.
* **Move items across sides** - Drag a chip between the left and right drop zones to move its button (and the panel it opens) to the other side of the window.
* **Hide items you don’t need** - Remove a chip from both sides to hide the button. Removed items become available again, so you can drop them back in later.
* **Side placement drives panel side** - Moving the tools panel, tabs panel, or code review button flips the corresponding panel to open from the same side, with resize handles, borders, and anchored popups following along.
* **Persistent across sessions** - Your layout is saved to settings and survives app restarts.
## Configurable items
[Section titled “Configurable items”](#configurable-items)
The following header buttons can be rearranged or hidden:
* **Tabs panel** - Toggles the [vertical tabs](/terminal/windows/vertical-tabs/) sidebar.
* **Tools panel** - Toggles the panel that contains the project explorer, global search, [Warp Drive](/knowledge-and-collaboration/warp-drive/), and conversation history.
* **Agent management** - Toggles the agent management view for [cloud agents](/platform/managing-cloud-agents/).
* **Code review** - Toggles the [Code Review](/code/code-review/) panel.
* **Notifications mailbox** - Toggles the [agent notifications](/agents/capabilities/agent-notifications/) mailbox.
The search bar and profile avatar are fixed and can’t be repositioned.
An item only appears in the toolbar when its prerequisites are met. For example, the tabs panel button requires [vertical tabs](/terminal/windows/vertical-tabs/) to be enabled, and agent management requires Agent Mode to be enabled. If an item’s prerequisite becomes unavailable later, the button disappears but your saved layout is preserved, so the button reappears once the prerequisite is met again.
## Default layout
[Section titled “Default layout”](#default-layout)
The default layout matches Warp’s standard header:
* **Left** - Tabs panel, tools panel, agent management.
* **Right** - Code review, notifications mailbox.
## Editing the toolbar
[Section titled “Editing the toolbar”](#editing-the-toolbar)
You can open the toolbar editor from the header or from Settings.
### From the header
[Section titled “From the header”](#from-the-header)
Right-click any toolbar button (or any empty space between the buttons and the search bar) and select **Rearrange toolbar items**. The configurator modal opens.
### From Settings
[Section titled “From Settings”](#from-settings)
1. In the Warp app, navigate to **Settings** > **Appearance** > **Tabs**.
2. Click **Edit toolbar**.
## How side placement affects panels
[Section titled “How side placement affects panels”](#how-side-placement-affects-panels)
Moving a button to the opposite side also moves where its panel opens, and Warp flips associated UI to stay readable:
* **Tabs panel** - Opens its sidebar on whichever side its button sits. The hover detail sidecar, action buttons, and right-click menu flip to face the center of the screen.
* **Tools panel** - Opens on the side its button sits. Warp Drive hover previews, kebab menus, and dialogs flip toward the center. The resize handle and border switch to the edge facing the main content.
* **Code review** - Opens on the side its button sits, with a matching resize handle.
* **Agent management** - Replaces the main content area when opened, so side placement only affects the button’s position, not where the view renders.
* **Notifications mailbox** - The popover anchors under its button, and notification toasts appear on the same side as the mailbox button.
When multiple panels are open on the same side, they render in the order their buttons appear in the toolbar. For example, if the left-side order is code review, tabs panel, tools panel, the panels open in that same order from left to right, with the main content to their right.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Vertical tabs](/terminal/windows/vertical-tabs/) - The sidebar toggled by the tabs panel button.
* [Code Review panel](/code/code-review/) - The panel toggled by the code review button.
* [Agent notifications](/agents/capabilities/agent-notifications/) - The mailbox toggled by the notifications button.
* [Managing cloud agents](/platform/managing-cloud-agents/) - The view toggled by the agent management button.
* [Warp Drive](/knowledge-and-collaboration/warp-drive/) - One of the views available in the tools panel.
# Global Hotkey
Canonical page: [/terminal/windows/global-hotkey/](https://docs.warp.dev/terminal/windows/global-hotkey/)
> Show or hide Warp instantly with a global hotkey, including a dedicated Quake-style drop-down window.
Global Hotkey shows or hides Warp instantly from anywhere with a keybinding you configure once, including a dedicated Quake-style drop-down window.
Note
On macOS, [system keyboard shortcuts](https://support.apple.com/en-us/HT201236) like `⌘+Esc`, `` ⌘+` ``, `⌘+Tab`, `⌘+.`, and `⌘+~` need to be [unbound](https://support.apple.com/guide/mac-help/keyboard-shortcuts-mchlp2262/mac) before you can use them in Warp.
Global Hotkey support on Linux depends on your window manager.
Caution
On Linux, the Global Hotkey may not work for some X11 window managers that do not implement [Extended Window Manager Hints](https://en.wikipedia.org/wiki/Extended_Window_Manager_Hints). Some examples include: [sowm](https://github.com/dylanaraps/sowm), [catwm](https://github.com/pyknite/catwm), [Fvwm](https://www.fvwm.org/), [dwm](https://dwm.suckless.org/), [2bWM](https://github.com/venam/2bwm), [monsterwm](https://github.com/c00kiemon5ter/monsterwm), [TinyWM](https://github.com/mackstann/tinywm), [x11fs](https://github.com/sdhand/x11fs), [XMonad](https://xmonad.org/)
## How to access it
[Section titled “How to access it”](#how-to-access-it)
### Dedicated window
[Section titled “Dedicated window”](#dedicated-window)
Dedicated Window lets you customize the window’s pinned position and its width and height ratio relative to your active screen size (also known as Quake Mode).
1. Open **Settings** > **Features** > **Keys** and select “Dedicated hotkey window” from the Global Hotkey dropdown to enable the feature.
2. Configure the keybinding, the window’s position, screen, and relative size or uncheck “Autohides on the loss of keyboard focus” which will cause the dedicated Hotkey Window to stay on top when triggered regardless of mouse or keyboard focus.
Caution
On Linux and Windows, Warp does not support the “Autohides on the loss of keyboard focus” feature.
### Show/hide all windows
[Section titled “Show/hide all windows”](#showhide-all-windows)
Show/Hide All Windows lets you configure a shortcut to show/hide all Warp windows.
1. Open **Settings** > **Features** > **Keys** and select “Show/hide all windows” from the Global Hotkey dropdown to enable the feature.
2. Configure your preferred keybinding.
Caution
On Linux, hidden windows may not appear in your `Alt+Tab` window switcher menu. Furthermore, the ordering of windows beyond the top window may change after toggling.
## How it works
[Section titled “How it works”](#how-it-works)
[](/assets/terminal/Dedicated-Window.mp4) [](/assets/terminal/Show-Hide-All-Windows.mp4)
## Troubleshooting hotkey dedicated window
[Section titled “Troubleshooting hotkey dedicated window”](#troubleshooting-hotkey-dedicated-window)
Review platform-specific instructions for troubleshooting the global hotkey below
* macOS
If the keybinding doesn’t work, go to > **System Settings** > **Privacy & Security** > **Accessibility** and toggle the switch next to **Warp** on.
* Windows
On Windows, there are no known issues with Global Hotkey Dedicated Window. If you find an issue, please [send feedback](/support-and-community/troubleshooting-and-support/sending-us-feedback/) to let us know.
* Linux
The hotkey window may appear on the incorrect monitor under certain window sizes. For example, with GNOME, if the hotkey window is supposed to show on a monitor having the taskbar (GNOME Panel), and the window height is 100%, causing an overlap, the hotkey window may fall back to showing on an external monitor if you have one. Try working around this by setting a window height to a lesser percentage, e.g. 90%.
# Split panes
Canonical page: [/terminal/windows/split-panes/](https://docs.warp.dev/terminal/windows/split-panes/)
> The split panes feature allows you to divide a tab into multiple rectangular panes, each of which is a unique terminal session.
## How to use split panes
[Section titled “How to use split panes”](#how-to-use-split-panes)
* macOS
* Split panes to the right / down with `⌘+D` / `⌘+Shift+D` or in any direction by right-clicking on any Pane.
* Activate the Previous / Next Pane with `⌘+[` / `⌘+]` or by clicking a pane.
* Navigate among split panes with `Option+⌘` plus an arrow key, the active pane will be marked with a triangle in the top corner.
* Toggle Maximize Pane with `⌘+Shift+Enter`.
* Close the active Pane with `⌘+W`.
* You can also drag and drop panes. Click and drag a Pane’s header around a given tab, drag the Pane to the tab bar to move it to another Tab, or make it into a Tab.
* Windows
* Split Panes to the right / down with `Ctrl+Shift+D` / `Ctrl+Shift+E` or in any direction by right-clicking on any Pane.
* Activate the Previous / Next Pane with `Ctrl+Shift+{` / `Ctrl+Shift+}` or by clicking a pane.
* Navigate among Split Panes with `Ctrl+Alt` plus an arrow key, the active pane will be marked with a triangle in the top corner.
* Toggle Maximize Pane with `Ctrl+Shift+Enter`.
* Close the active Pane with `Ctrl+Shift+W`.
* You can also drag and drop panes. Click and drag a Pane’s header around a given tab, drag the Pane to the tab bar to move it to another Tab, or make it into a Tab.
* Linux
* Split Panes to the right / down with `Ctrl+Shift+D` / `Ctrl+Shift+E` or in any direction by right-clicking on any Pane.
* Activate the Previous / Next Pane with `Ctrl+Shift+{` / `Ctrl+Shift+}` or by clicking a pane.
* Navigate among Split Panes with `Ctrl+Alt` plus an arrow key, the active pane will be marked with a triangle in the top corner.
* Toggle Maximize Pane with `Ctrl+Shift+Enter`.
* Close the active Pane with `Ctrl+Shift+W`.
* You can also drag and drop panes. Click and drag a Pane’s header around a given tab, drag the Pane to the tab bar to move it to another Tab, or make it into a Tab.
Note
You can quickly find all the **pane** shortcuts by using the [Command Palette](/terminal/command-palette/). You can also remap the shortcuts to your liking. See [Custom Keyboard Shortcuts](/getting-started/keyboard-shortcuts/#custom-keyboard-shortcuts) for more details.
### Ctrl+Tab behavior
[Section titled “Ctrl+Tab behavior”](#ctrltab-behavior)
`Ctrl+Tab` shortcut defaults to activate the previous / next [Tabs](/terminal/windows/tabs/). You can configure the shortcut to cycle the most recent session, including any split panes, in **Settings** > **Features** > **Keys** > **Ctrl+Tab behavior**.
## How split panes work
[Section titled “How split panes work”](#how-split-panes-work)
[Split Panes Demo](https://www.loom.com/embed/c1104b51cab848a9bef6792ec4fd8421)
[](/assets/terminal/split-panes-dragging-demo.mp4)
# Tab Configs
Canonical page: [/terminal/windows/tab-configs/](https://docs.warp.dev/terminal/windows/tab-configs/)
> Tab Configs let you define reusable tab setups — including directory, startup commands, pane layout, shell, and theme — in a simple TOML file.
Tab Configs let you define reusable tab setups — including directory, startup commands, pane layout, shell, and theme — in a simple TOML file. Select a Tab Config from the `+` menu to open a fully configured tab with a single click.

## How Tab Configs work
[Section titled “How Tab Configs work”](#how-tab-configs-work)
Each Tab Config is a `.toml` file stored in Warp’s `tab_configs` directory. Every file defines a single tab layout with optional pane splits, startup commands, and parameterized inputs. Tab Configs appear in the `+` menu alongside your existing tabs, so you can launch a preconfigured workspace instantly.
The `tab_configs` directory lives in a different location on each platform:
* macOS
`~/.warp/tab_configs/` (Stable) or `~/.warp-preview/tab_configs/` (Preview).
* Windows
`%APPDATA%\warp\Warp\data\tab_configs\` (Stable) or `%APPDATA%\warp\WarpPreview\data\tab_configs\` (Preview).
* Linux
`${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal/tab_configs/` (Stable) or `${XDG_DATA_HOME:-$HOME/.local/share}/warp-terminal-preview/tab_configs/` (Preview).
For the full list of Warp file locations, see [File and folder locations](/terminal/settings/file-locations/).
## Creating a Tab Config
[Section titled “Creating a Tab Config”](#creating-a-tab-config)
### From the UI
[Section titled “From the UI”](#from-the-ui)
1. Click the **+** button in the tab bar to open the new-tab menu.
2. Click **+ New tab config**. Warp creates a new `.toml` file in the `tab_configs` directory and opens it for editing.
### Manually
[Section titled “Manually”](#manually)
1. Create a new `.toml` file in the `tab_configs` directory shown above. Use snake\_case for the file name (e.g., `dev_server.toml`).
2. Define the tab layout using the schema below, then save the file. The new config appears in the `+` menu automatically.
### Save an existing tab as a Tab Config
[Section titled “Save an existing tab as a Tab Config”](#save-an-existing-tab-as-a-tab-config)
You can also capture a tab’s current state as a reusable Tab Config without writing TOML. Right-click any tab in the [vertical tabs](/terminal/windows/vertical-tabs/) panel or horizontal tab bar to open the context menu, then click **Save as new config**. Warp generates a `.toml` file from the tab’s layout, commands, and directory and adds it to the `+` menu.

Saving a tab config.
## Managing Tab Configs
[Section titled “Managing Tab Configs”](#managing-tab-configs)
Saved Tab Configs appear in the `+` menu for quick access. When you hover a Tab Config in the menu, a **sidecar panel** appears alongside it with options to:
* **Edit config** — Open the underlying `.toml` file for manual editing. The editor also shows a footer to invoke the **update tab config** skill, so you can describe changes in natural language and have Warp’s agent apply them.
* **Remove** — Remove the Tab Config from the `+` menu.
* **Make default** — Assign the Tab Config as the default `⌘+T` action for new tabs.
Tab config menu with sidecar options.
## Open a Tab Config from a URL
[Section titled “Open a Tab Config from a URL”](#open-a-tab-config-from-a-url)
You can open a saved Tab Config directly via Warp’s [URI scheme](/terminal/more-features/uri-scheme/). This is useful for browser bookmarks, scripts, and launchers like Raycast or Alfred that need to jump straight into a configured pane layout without going through the `+` menu.
By default, the Tab Config opens as a new tab in the active window. Pass `?new_window=true` (or invoke when no Warp window is open) to open it in a new window instead.
```bash
# Open my_tab.toml as a new tab in the focused window
open "warp://tab_config/my_tab"
# Open it in a brand-new window
open "warp://tab_config/my_tab?new_window=true"
```
`<name>` is matched case-insensitively against the file stem of the `.toml`, so `warp://tab_config/my_tab` and `warp://tab_config/my_tab.toml` both resolve to `my_tab.toml`. Matching uses the filename rather than the `name` field inside the file, because multiple Tab Configs can share the same display name.
If the Tab Config declares `[params.*]` entries, the params modal opens just like launching from the `+` menu. Worktree-style configs that reference `{{autogenerated_branch_name}}` still get a freshly generated branch name on each open.
Note
On Warp Preview, use `warppreview://tab_config/<name>` instead.
## Using skills to manage Tab Configs
[Section titled “Using skills to manage Tab Configs”](#using-skills-to-manage-tab-configs)
Warp includes built-in skills for creating and modifying Tab Configs through natural language:
* **Create Tab Config** — Generate a new Tab Config from a description (e.g., “create a 2x2 grid with one pane running my dev server”).
* **Update Tab Config** — Modify an existing Tab Config by describing the changes you want.
To use these skills, type `/skills` in Agent Mode and select the tab config skill, or use the footer that appears when editing a Tab Config file.
## Tab Config TOML schema
[Section titled “Tab Config TOML schema”](#tab-config-toml-schema)
### Top-level fields
[Section titled “Top-level fields”](#top-level-fields)
* **`name`** (required, string) — display name shown in the `+` menu.
* **`title`** (optional, string) — custom tab title. Supports `{{param}}` template variables.
* **`color`** (optional, string) — tab color. One of: `"black"`, `"red"`, `"green"`, `"yellow"`, `"blue"`, `"magenta"`, `"cyan"`, `"white"`. Actual color values are derived from your Warp [Theme](/terminal/appearance/themes/).
### Pane list
[Section titled “Pane list”](#pane-list)
All panes are defined in a flat `[[panes]]` array. The first entry is the root of the pane tree. Each entry is either a **split node** (branch) or a **leaf node**.
#### Leaf node fields
[Section titled “Leaf node fields”](#leaf-node-fields)
* **`id`** (required, string) — unique identifier for this pane. Use descriptive names like `"editor"` or `"server"`.
* **`type`** (required, string) — `"terminal"` (standard shell), `"agent"` (opens in Agent Mode), or `"cloud"` (cloud mode pane, no local shell).
* **`directory`** (optional, string) — initial working directory. Supports `~` expansion and `{{param}}` template variables.
* **`commands`** (optional, array of strings) — commands to run in sequence when the tab opens.
* **`shell`** (optional, string) — shell executable to use for this pane (e.g. `"pwsh"`, `"zsh"`, `"bash"`, `"fish"`). Only applies to `terminal` and `agent` pane types. If omitted or the specified shell is not installed, the user’s default shell is used.
* **`is_focused`** (optional, bool) — set to `true` on at most one pane to give it initial focus.
Caution
Commands in the `commands` array run in sequence, with each command waiting for the previous one to finish. A long-running or interactive command like `ssh` never returns control to the shell, so any commands listed after it don’t run in the session. To run commands on a remote host, include them in the `ssh` command itself (e.g., `ssh -t user@host 'cd ~/project && exec $SHELL -l'`).
#### Split node fields
[Section titled “Split node fields”](#split-node-fields)
* **`id`** (required, string) — unique identifier for this split.
* **`split`** (required, string) — `"horizontal"` (children arranged left-to-right) or `"vertical"` (children arranged top-to-bottom).
* **`children`** (required, array of strings) — ordered list of child pane `id` values. Must contain at least 2 entries. Order determines visual order.
Note
All children within a split are equally sized. There are no flex or proportion values.
### Parameters
[Section titled “Parameters”](#parameters)
Parameters let users fill in values at open time via a modal prompt. Declare them with `[params.<name>]` tables and reference them in `directory`, `commands`, and `title` using `{{name}}` syntax.
Each parameter has:
* **`type`** (optional, string) — `"text"` (default, freeform input), `"branch"` (Git branch picker), or `"repo"` (repository picker).
* **`description`** (optional, string) — label shown in the fill-in UI.
* **`default`** (optional, string) — default value.
`{{autogenerated_branch_name}}` is a reserved template variable. If a Tab Config references it, Warp generates a unique worktree branch name on each open instead of prompting the user.
## Examples
[Section titled “Examples”](#examples)
### Single pane
[Section titled “Single pane”](#single-pane)
A simple config that opens a terminal in a project directory and starts a dev server:
```toml
name = "Dev Server"
[[panes]]
id = "main"
type = "terminal"
directory = "~/code/my-app"
commands = ["npm run dev"]
```
### Two panes side by side
[Section titled “Two panes side by side”](#two-panes-side-by-side)
An editor and server running in parallel, with the editor focused:
```toml
name = "Editor + Server"
color = "green"
[[panes]]
id = "root"
split = "horizontal"
children = ["editor", "server"]
[[panes]]
id = "editor"
type = "terminal"
directory = "~/code/my-app"
commands = ["nvim ."]
is_focused = true
[[panes]]
id = "server"
type = "terminal"
directory = "~/code/my-app"
commands = ["npm run dev"]
```
### Cross-shell development
[Section titled “Cross-shell development”](#cross-shell-development)
A config that opens two panes side by side, each with a different shell:
```toml
name = "Cross Shell"
color = "cyan"
[[panes]]
id = "root"
split = "horizontal"
children = ["bash_pane", "pwsh_pane"]
[[panes]]
id = "bash_pane"
type = "terminal"
shell = "bash"
directory = "~/code/my-app"
is_focused = true
[[panes]]
id = "pwsh_pane"
type = "terminal"
shell = "pwsh"
directory = "~/code/my-app"
```
### Worktree with parameters
[Section titled “Worktree with parameters”](#worktree-with-parameters)
A parameterized config that creates a new Git worktree on open:
```toml
name = "New Worktree"
title = "{{branch_name}}"
[[panes]]
id = "main"
type = "terminal"
directory = "{{repo}}"
commands = [
"git worktree add -b {{branch_name}} ../{{branch_name}} {{base_branch}}",
"cd ../{{branch_name}}",
]
[params.repo]
type = "repo"
description = "Repository path"
[params.base_branch]
type = "branch"
description = "Base branch to branch from"
[params.branch_name]
type = "text"
description = "New branch name"
default = "my-feature"
```
### Quick worktree setup
[Section titled “Quick worktree setup”](#quick-worktree-setup)
You can also create a worktree-based Tab Config directly from the `+` menu by clicking **New worktree config** and selecting the repo you want your worktree to be from. Warp generates the Tab Config automatically and saves it for future use.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Launch Configurations (Legacy)](/terminal/sessions/launch-configurations/) — the previous session configuration format. Existing configs still work, but Tab Configs are the recommended approach for new setups.
* [Tabs](/terminal/windows/tabs/) — tab management, keyboard shortcuts, and behavior settings
* [Themes](/terminal/appearance/themes/) — customize the colors used by tab color settings
* [Working Directory](/terminal/more-features/working-directory/) — how Warp resolves working directories
* [Third-party CLI agents](/agents/cli-agents/overview/) — use the `"agent"` pane type to open tabs in Agent Mode
* [Warp URI Scheme](/terminal/more-features/uri-scheme/) — open Tab Configs via `warp://tab_config/<name>` deeplinks
# Tabs
Canonical page: [/terminal/windows/tabs/](https://docs.warp.dev/terminal/windows/tabs/)
> Organize terminal sessions with customizable tabs and groups, then pin important tabs and groups at the front of the tab list.
Note
New Tabs will default to the active Tabs’ current [Working Directory](/terminal/more-features/working-directory/) and the actual color values will be automatically derived from your Warp [Theme](/terminal/appearance/themes/).
## How to use Tabs
[Section titled “How to use Tabs”](#how-to-use-tabs)
* macOS
* Right-click on the new Tab button `+` to make a new tab, restore closed tab, or run a saved [Launch Configuration](/terminal/sessions/launch-configurations/).
* Open a new Tab with `⌘+T` or by clicking on the `+` in the top bar.
* Close the current Tab with `⌘+W` or by clicking on the `X` on hover over a Tab.
* Reopen closed tabs with `⌘+Shift+T`.
* Move a Tab to the Left / Right with `Ctrl+Shift+←` / `Ctrl+Shift+→` or by clicking and dragging a Tab.
* Activate the Previous / Next Tab with `⌘+Shift+{` / `⌘+Shift+}` or by clicking a Tab.
* Activate the first through eighth Tabs with `⌘+1` thru `⌘+8`.
* Switch to the last Tab with `⌘+9`.
* Double-click a Tab to rename it.
* Right-clicking on a Tab reveals more options you can explore within the [Command Palette](/terminal/command-palette/) or [Keyboard Shortcuts](/getting-started/keyboard-shortcuts/#all-available-shortcuts).
* Windows
* Right-click on the new Tab button `+` to make a new tab, restore closed tab, or run a saved [Launch Configuration](/terminal/sessions/launch-configurations/).
* Open a new Tab with `Ctrl+Shift+T` or by clicking on the `+` in the top bar.
* Close the current Tab with `Ctrl+Shift+W` or by clicking on the `x` on hover over a Tab.
* Reopen closed tabs with `Ctrl+Alt+T`.
* Move a Tab to the Left / Right with `Ctrl+Shift+←` / `Ctrl+Shift+→` or by clicking and dragging a Tab.
* Activate the Previous / Next Tab with `Ctrl+Page Up` / `Ctrl+Page Down` or by clicking a Tab.
* Activate the first through eighth Tabs with `Ctrl+1` thru `Ctrl+8`.
* Switch to the last Tab with `Ctrl+9`.
* Double-click a Tab to rename it.
* Right-clicking on a Tab reveals more options you can explore within the [Command Palette](/terminal/command-palette/) or [Keyboard Shortcuts](/getting-started/keyboard-shortcuts/#all-available-shortcuts).
* Linux
* Right-click on the new Tab button `+` to make a new tab, restore closed tab, or run a saved [Launch Configuration](/terminal/sessions/launch-configurations/).
* Open a new Tab with `Ctrl+Shift+T` or by clicking on the `+` in the top bar.
* Close the current Tab with `Ctrl+Shift+W` or by clicking on the `x` on hover over a Tab.
* Reopen closed tabs with `Ctrl+Alt+T`.
* Move a Tab to the Left / Right with `Ctrl+Shift+←` / `Ctrl+Shift+→` or by clicking and dragging a Tab.
* Activate the Previous / Next Tab with `Ctrl+Page Up` / `Ctrl+Page Down` or by clicking a Tab.
* Activate the first through eighth Tabs with `Ctrl+1` thru `Ctrl+8`.
* Switch to the last Tab with `Ctrl+9`.
* Double-click a Tab to rename it.
* Right-clicking on a Tab reveals more options you can explore within the [Command Palette](/terminal/command-palette/) or [Keyboard Shortcuts](/getting-started/keyboard-shortcuts/#all-available-shortcuts).
Tip
**Terminal Tip**\
Using your `.zshrc` or `.bashrc` files on macOS or Linux, you can set a new Tab name:
```bash
# Set name, where MyTabName would be whatever you want to see in the Tab ( either a fixed string, $PWD, or something else )
function set_name () {
export WARP_DISABLE_AUTO_TITLE=true
echo -ne "\033]0;MyTabName\007"
}
# Add the function to the environment variable in either Zsh or Bash
if [ -n "$ZSH_VERSION" ]; then
preexec_functions+=(set_name)
elif [ -n "$BASH_VERSION" ]; then
PROMPT_COMMAND='set_name'
fi
```
Learn more about [setting shell tab titles in Windows Terminal](https://learn.microsoft.com/en-us/windows/terminal/tutorials/tab-title#set-the-shells-title).
### Tab Restoration
[Section titled “Tab Restoration”](#tab-restoration)
Tab Restoration enables you to reopen recently closed tabs for up to 60 seconds. Configure this feature in **Settings** > **Features** > **Session** > **Enable reopening of closed sessions**.
### Ctrl+Tab behavior
[Section titled “Ctrl+Tab behavior”](#ctrltab-behavior)
`Ctrl+Tab` shortcut defaults to activate the previous / next Tab. You can configure the shortcut to cycle the most recent session, including any [Split Panes](/terminal/windows/split-panes/), in **Settings** > **Features** > **Keys** > **Ctrl+Tab behavior**.
### Tabs behavior
[Section titled “Tabs behavior”](#tabs-behavior)
See our [Appearance > Tabs Behavior](/terminal/appearance/tabs-behavior/) docs for more tab-related settings.
### How Tabs work
[Section titled “How Tabs work”](#how-tabs-work)
[Tabs Demo](https://www.loom.com/embed/84d15cc7eb5a4a668bb86be9e827f261)
## Tab colors
[Section titled “Tab colors”](#tab-colors)
Color-code tabs to tell projects, environments, or long-running sessions apart at a glance. Colors come from your active [theme](/terminal/appearance/themes/), so they stay readable whichever theme you use.
### Set a tab’s color
[Section titled “Set a tab’s color”](#set-a-tabs-color)
1. Right-click the tab you want to color.
2. Click a color in the color row.
To remove a color, right-click the tab and click the same color again, or pick the default (no color) option.
You can also set the color without leaving the input. Run the [`/set-tab-color`](/agents/capabilities/slash-commands/) Slash Command with the color you want — `red`, `green`, `yellow`, `blue`, `magenta`, `cyan`, or `none` to clear it. For example, `/set-tab-color blue`.
Note
Coloring a tab that belongs to a [group](#tab-groups) sets the group’s color, so every tab in the group changes together.
### Cycle the active tab’s color
[Section titled “Cycle the active tab’s color”](#cycle-the-active-tabs-color)
The **Cycle current tab color** action (`workspace:cycle_active_tab_color`) steps the active tab through the available colors, then back to no color. It has no default shortcut, so reach it from the [Command Palette](/terminal/command-palette/) or bind a key to it in **Settings** > **Keyboard shortcuts**.
Tip
Warp can also color tabs automatically based on their working directory. See `directory_tab_colors` in the [all settings reference](/terminal/settings/all-settings/#tabs).
## Tab groups
[Section titled “Tab groups”](#tab-groups)
Organize related tabs into named, collapsible groups. A tab group keeps its member tabs together in the tab bar, can be given a name and a color, and can be collapsed to hide its members until you need them. Tab groups work in both the horizontal tab bar and the [vertical tabs](/terminal/windows/vertical-tabs/) panel.
### Create a group
[Section titled “Create a group”](#create-a-group)
* Right-click a tab and choose **New group with tab** to start a group from that tab.
* Select multiple tabs first (see [Select multiple tabs](#select-multiple-tabs)), then right-click the selection to group them together.
* Click the **+** new-tab button and choose **New tab group** to create a new group with a new tab.
### Select multiple tabs
[Section titled “Select multiple tabs”](#select-multiple-tabs)
* `Cmd`-click (macOS) or `Ctrl`-click (Windows/Linux) a tab to add it to or remove it from the selection.
* `Shift`-click a tab to select every tab between it and the active tab.
With multiple tabs selected, right-click to group them, move them into an existing group, or remove them from their group in one step.
Note
The active tab is always included in a selection.
### Manage a group
[Section titled “Manage a group”](#manage-a-group)
Right-click a group’s header to:
* **Rename** the group.
* Set a **color** for the group.
* Add a **New tab in group**.
* **Ungroup tabs** to dissolve the group while keeping its tabs.
* Close the tabs in the group.
Right-click an individual tab for **New group with tab**, **Move to group** (to move it into another group), and **Remove from group**.
### Collapse a group
[Section titled “Collapse a group”](#collapse-a-group)
Click a group’s header to collapse or expand it. Collapsed groups hide their member tabs to save space in the tab bar; click the header again to expand.
Note
You can assign keyboard shortcuts for creating a group from the active or selected tabs and for removing tabs from a group in **Settings** > **Keyboard shortcuts**.
## Pin tabs and groups
[Section titled “Pin tabs and groups”](#pin-tabs-and-groups)
Pin frequently used tabs or tab groups to keep them at the front of the tab list. Pinned items form a leading section before unpinned tabs and groups, and you can reorder items within the pinned section. Pinning works in both the horizontal tab bar and the [vertical tabs](/terminal/windows/vertical-tabs/) panel. Warp restores the pinned state when you reopen the window.
### Pin a tab
[Section titled “Pin a tab”](#pin-a-tab)
1. Right-click the tab you want to keep at the front.
2. Click **Pin tab**.
Warp moves the tab to the end of the pinned section.
Note
If the tab belongs to a group, **Pin tab** removes the tab from its group and pins it independently. To keep the group together, pin the group instead.
### Pin a group
[Section titled “Pin a group”](#pin-a-group)
1. Right-click the group’s header.
2. Click **Pin group**.
Warp moves the entire group to the end of the pinned section as one block.
### Unpin a tab or group
[Section titled “Unpin a tab or group”](#unpin-a-tab-or-group)
To return an item to the unpinned section:
* **Tab** - Right-click the pinned tab, then click **Unpin tab**.
* **Group** - Right-click the pinned group’s header, then click **Unpin group**.
Warp moves the item to the beginning of the unpinned section.
Note
You can assign keyboard shortcuts for pinning or unpinning the active tab or group in **Settings** > **Keyboard shortcuts**.
## Move a tab to another window
[Section titled “Move a tab to another window”](#move-a-tab-to-another-window)
You can pull a tab out of the tab bar to reorganize your windows, similar to a web browser:
* **Detach a tab into its own window** — drag a tab out of the tab bar and drop it in empty space to open it in a new window.
* **Move a tab between windows** — drag a tab onto another window’s tab bar to move it there.
The tab keeps its running session, panes, and state as it moves. This works from both the horizontal tab bar and the [vertical tabs](/terminal/windows/vertical-tabs/) panel.
Note
Dragging tabs between windows is available on macOS and Windows.
# Vertical Tabs
Canonical page: [/terminal/windows/vertical-tabs/](https://docs.warp.dev/terminal/windows/vertical-tabs/)
> The vertical tabs panel replaces the horizontal tab bar with a sidebar showing rich metadata, drag-and-drop management, and display options for tabs and panes.
The vertical tabs panel is a sidebar that replaces the traditional horizontal tab bar with a richer, more powerful tab management surface. Instead of a single row of tab titles, the panel displays every tab and pane with contextual metadata — Git branch, working directory, agent conversation status, diff stats, and more. Scan and switch between workstreams without losing context.
Vertical tabs are especially useful when running multiple coding agents side by side, giving you a clear overview of each session’s state without switching tabs.

## Key features
[Section titled “Key features”](#key-features)
### Rich metadata and status
[Section titled “Rich metadata and status”](#rich-metadata-and-status)
* **Pane metadata** - See working directory, Git branch, agent conversation status, diff stats, and PR badges at a glance for every pane.
* **Agent status badges** - Pane icons display a colored badge overlay showing agent state (in progress, done, errored, cancelled, or blocked). [Third-party CLI agents](/agents/cli-agents/overview/) like Claude Code, Codex, and Gemini CLI display their brand icon and color alongside badges.
* **Notification indicators** - An accent-colored dot appears on pane rows with unread agent activity, so you can spot sessions that need attention without switching tabs.
### Display modes and customization
[Section titled “Display modes and customization”](#display-modes-and-customization)
* **Pane or tab view** - Display every split pane as its own row (**Panes**) or show only the focused pane per tab (**Tabs**).
* **Focused session or summary tab item** - When viewing as **Tabs**, choose **Focused session** to show the active pane per tab, or **Summary** to show a condensed multi-line digest of every pane in the tab (commands, working directories, branches, and status badges).
* **Compact and expanded modes** - Choose between a dense single-line view (default) or a detailed multi-line layout with full metadata.
* **Configurable pane titles** - Control which metadata appears first: last command or conversation, working directory, or Git branch.
* **Hover detail sidecar** - Hover any pane row to see full, un-clipped metadata in a floating detail card without changing focus.
### Tab management
[Section titled “Tab management”](#tab-management)
* **Search, drag and drop, and renaming** - Filter panes by title, directory, or branch; reorder tabs or move panes between tabs by dragging; double-click a tab to rename it inline.
* **New tab menu** - Create agent tabs, terminal tabs, cloud agent sessions, worktree configs, and [Tab Configs](/terminal/windows/tab-configs/) from a unified **+** menu.
## Enabling vertical tabs
[Section titled “Enabling vertical tabs”](#enabling-vertical-tabs)
To switch from horizontal tabs to the vertical tabs panel:
1. In the Warp app, navigate to **Settings** > **Appearance** > **Tabs**.
2. Toggle **Use vertical tab layout** on.
The vertical tabs panel appears as a resizable sidebar on the left side of the window. The horizontal tab bar is hidden while vertical tabs are active.

Vertical tab with agent details.
Note
You can also toggle vertical tabs from the [Command Palette](/terminal/command-palette/) by searching for “vertical tab layout.”
## View modes
[Section titled “View modes”](#view-modes)
The vertical tabs panel supports two display densities that you can switch between at any time.
### Compact mode
[Section titled “Compact mode”](#compact-mode)
Compact mode is the default. Each pane row displays an icon and title on one line, with an optional subtitle below it. The subtitle is configurable via the **Additional metadata** setting in the settings popup.
Vertical tabs in compact mode.
### Expanded mode
[Section titled “Expanded mode”](#expanded-mode)
Expanded mode shows each pane row with a title, description (such as the working directory or file path), and metadata (Git branch, diff stats badge, and PR badge when available).

Vertical tabs overview.
### Switching view modes
[Section titled “Switching view modes”](#switching-view-modes)
Click the settings icon (sliders) in the control bar at the top of the vertical tabs panel. In the popup, use the **Density** segmented control to switch between compact and expanded views. The change takes effect immediately.
Vertical tabs settings popup.
## Customizing vertical tabs
[Section titled “Customizing vertical tabs”](#customizing-vertical-tabs)
When vertical tabs are enabled, configure their appearance and behavior from the settings popup (click the sliders icon in the control bar) or from **Settings** > **Appearance** > **Tabs**.
You can also rearrange the panel toggle buttons at the top of the Warp window — including the tabs panel, tools panel, agent management, code review, and notifications mailbox — and move them between the left and right sides of the header. See [Configurable toolbar](/terminal/windows/configurable-toolbar/) for details.
| Setting | Availability | Options | Default |
| ------------------------- | ------------------------------ | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | ---------------------- |
| **View as** | Always | **Panes** — each split pane gets its own row. **Tabs** — one row per tab, controlled further by the **Tab item** setting. | Panes |
| **Tab item** | **View as** is set to **Tabs** | **Focused session** — show the focused pane’s title and metadata. **Summary** — show a condensed digest of every pane in the tab, with command or conversation titles, working directories, branches, and agent status badges (up to three lines, with a `+ N more` overflow row). | Focused session |
| **Density** | Always | **Compact** — smaller rows with title and optional subtitle. **Expanded** — larger rows with title, description, and metadata. | Compact |
| **Pane title as** | Always | **Command / Conversation** — last command, conversation title, or CLI agent session name. **Working Directory** — pane’s working directory. **Branch** — checked-out Git branch. | Command / Conversation |
| **Additional metadata** | Compact mode only | **Branch** **Working Directory** **Command / Conversation** (options depend on the **Pane title as** setting; duplicates are excluded). | Branch |
| **Show** | Expanded mode only | **PR link** — pull request and status for the current branch (requires GitHub CLI). **Diff stats** — lines added/removed. | — |
| **Show details on hover** | Always | On / Off — toggles the hover detail sidecar. | On |
### Automatic metadata
[Section titled “Automatic metadata”](#automatic-metadata)
The following metadata appears automatically and doesn’t require configuration:
* **Git branch** - The currently checked-out branch for the pane’s working directory.
* **Worktree** - The active [Git worktree](/code/git-worktrees/) path, if applicable.
* **Agent status** - A colored badge on the pane icon indicating the agent’s current state (see [Agent status badges](#agent-status-badges) below).
* **Notification dot** - An accent-colored dot on the title row when a pane has unread agent activity.
## Agent status badges
[Section titled “Agent status badges”](#agent-status-badges)
Agent pane icons display a small circular badge overlay in the bottom-right corner that reflects the agent’s current state:
| Status | Icon | Meaning |
| --------------- | ------------- | -------------------------------------------------- |
| **In progress** | Magenta clock | The agent is actively running. |
| **Done** | Green check | The agent’s last turn completed successfully. |
| **Error** | Red triangle | The agent’s last turn completed with an error. |
| **Cancelled** | Gray stop | The user cancelled the agent’s last turn. |
| **Blocked** | Yellow stop | The agent is waiting for user approval to proceed. |
Agent status badges on vertical tabs.
Third-party CLI agents (Claude Code, Codex, Gemini CLI, and others) display their brand icon and color inside the circular pane icon, with the same status badge overlay.
When a pane has unread agent activity, an accent-colored notification dot appears at the right edge of the title row. The dot clears when you focus the pane.
## Managing tabs
[Section titled “Managing tabs”](#managing-tabs)
### Search
[Section titled “Search”](#search)
The control bar at the top of the vertical tabs panel includes a search field. Type to filter the visible tabs and panes by title, working directory, Git branch, PR label, or diff stats. Only matching tabs remain visible while the search query is active.
### New tab menu
[Section titled “New tab menu”](#new-tab-menu)
Click the **+** button in the control bar to open the new tab menu. The menu includes:
* **Agent** - Open a new agent tab.
* **Terminal** - Open a new terminal tab.
* **Cloud agent** - Open a new cloud agent session tab.
* **Tab Configs** - Any [Tab Configs](/terminal/windows/tab-configs/) you’ve created appear as menu items for one-click setup.
* **New worktree config** - Create a new worktree-based Tab Config.
* **New tab config** - Create a new Tab Config from a starter template.
### Drag and drop
[Section titled “Drag and drop”](#drag-and-drop)
Reorder tabs by dragging tab group headers within the panel. To move a pane from one tab to another, drag the pane header over a different tab group in the panel. Warp switches to that tab so you can place the pane using the standard drop targets. Dropping a pane between tab groups creates a new tab at that position.
### Tab renaming
[Section titled “Tab renaming”](#tab-renaming)
Double-click a tab row to rename it inline. Press `Enter` to confirm or `Esc` to cancel.
Note
Renaming applies to tabs only. Individual panes can’t be renamed at this time.
## Hover detail sidecar
[Section titled “Hover detail sidecar”](#hover-detail-sidecar)
Hover any pane row to open a floating detail card anchored to the right side of the panel. The sidecar shows full, un-clipped metadata (complete directory paths, full branch names, and the full conversation or command title) without changing which pane is focused.
Hover detail card for a vertical tab.
The sidecar stays open as you move the cursor from the row into the card. Move away from both the row and the sidecar to dismiss it. Disable this behavior with the **Show details on hover** toggle in the settings popup.
## Keyboard shortcuts
[Section titled “Keyboard shortcuts”](#keyboard-shortcuts)
All existing tab keyboard shortcuts continue to work with vertical tabs. The sidebar layout changes how tabs are displayed, not how you interact with them. See [Terminal tabs](/terminal/windows/tabs/) for the full list of tab shortcuts.
## Related pages
[Section titled “Related pages”](#related-pages)
* [Terminal tabs](/terminal/windows/tabs/) - Horizontal tab bar usage and keyboard shortcuts
* [Split panes](/terminal/windows/split-panes/) - Divide tabs into multiple terminal panes
* [Tab Configs](/terminal/windows/tab-configs/) - Define reusable tab setups in TOML files
* [Git Worktrees](/code/git-worktrees/) - Worktree support that surfaces in vertical tab metadata
* [Tabs behavior](/terminal/appearance/tabs-behavior/) - Tab bar visibility, indicators, and close button settings
* [Third-party CLI agents](/agents/cli-agents/overview/) - Use Claude Code, Codex, Gemini CLI, and other third-party agents with Warp’s utility bar, including brand icons and status badges in the vertical tabs panel